 bugcrowd
@Bugcrowd

Linux users... What's your favorite distro?

Politicians, athletes, journalists, NGOs, companies... They all use corporation-owned social networks to communicate with us. Citizens shouldn't have to hand over their data to companies to read content published by public entities. Public Feeds changes that by making posts of popular accounts freely available. Read more.
Bugcrowd is a crowdsourced security platform. It was founded in 2012, and in 2019 it was one of the largest bug bounty and vulnerability disclosure companies on the internet. Bugcrowd runs bug bounty programs and also offers a range of penetration testing services it refers to as "Penetration Testing as a Service" (PTaaS), as well as attack surface management. More on Wikipedia
The leading provider of crowdsourced cybersecurity solutions purpose-built to secure the digitally connected world...Unleash Ingenuity™
bugcrowd
@Bugcrowd
Linux users... What's your favorite distro?
bugcrowd
@Bugcrowd
In your opinion, what are the top 3 hacking tools that every webapp hacker needs in their arsenal? 🛠️
bugcrowd
@Bugcrowd
Thank you for your time @kuzushi!
And we have another Hive Exchange event coming up!
Join us! 👇
luma.com/ko1b052l
 bugcrowd
@Bugcrowd
UPCOMING EVENT: AWS and Just Eat takeaway.com are joining us in Amsterdam for THE HIVE EXCHANGE.
Connect with infosec professionals and security researchers to explore how offensive security and hacker collaboration accelerate vulnerability detection and strengthen overall defense.
Connect, learn, and have fun!
📍 Amsterdam | 18 November
Request your spot 👇
luma.com/ko1b052l
 bugcrowd
@Bugcrowd
We sat down with Dani Woolf to explore the parallels between chess and preemptive security. Check out the blog to learn how to keep attackers in check ♟️ www.bugcrowd.com/blog/checkmate-what-chess-teaches-us-abo…
bugcrowd
@Bugcrowd
Is that AI agent actually legit, or just another flashy demo?
Watch the on-demand webinar to learn more about evaluating AI testing agents:
event.on24.com/wcc/r/5473529/31E55D6876A6ED6CBDB61A230C0B…
bugcrowd
@Bugcrowd
ASN enumeration is an important yet frequently overlooked recon method.
Finding the ASN can reveal the target's network ranges.
Tools include:
- asnlookup.com
- bgp.he.net
- @Yassineaboukir's ASNlookup
And more!
What tools do you like to use?
 bugcrowd
@Bugcrowd
API Tip 💡
Thank you, @InsiderPhD 🙌
 bugcrowd
@Bugcrowd
Don't hunt alone. Trade tips, swap PoCs, and level up with other researchers who get it. 👇
 bugcrowd
@Bugcrowd
Join our community on Reddit 👇
www.reddit.com/r/Bugcrowd/
bugcrowd
@Bugcrowd
We're hiring! We have a bunch of great career opportunities available globally. Check them out on our careers page and join our awesome team. www.bugcrowd.com/about/careers/
 bugcrowd
@Bugcrowd
403 bypass tricks that (may) still work in 2026 😏
🧵👇
 bugcrowd
@Bugcrowd
T-Mobile just released its Advancing Cybersecurity at T-Mobile Report and it's a must-read! We're proud to play a part in helping T-Mobile on its preemptive security journey.
"Our Bug Bounty program, managed with Bugcrowd, remains one of the telecommunications industry's most impactful programs. To date, our Bug Bounty program has received over 1,400 valid submissions. As the program has matured, submissions have become increasingly sophisticated, reflecting stronger defenses and a higher barrier for potential attacks."
Read the full report here: www.t-mobile.com/news/_admin/uploads/2026/11/Advancing-Cy…
bugcrowd
@Bugcrowd
📣 Calling all hardware hackers! 📣
If you're attending hardwear.io in the Netherlands next week, be sure to find Bugcrowd customer Cisco, who will be handing out hardware for you to test as part of their HardPwn live hacking event. Find out more here:
bugcrowd
@Bugcrowd
TFW you take the day off 😎
 bugcrowd
@Bugcrowd
When designing malware to evade modern Endpoint Detection and Response (EDR) solutions, red teamers must focus on 3 primary components:
🟧 pretexting the software
🟧 hiding the payload
🟧 executing the payload.
The critical 2nd step, hiding the payload, is the focus of this blog: 👇
www.bugcrowd.com/blog/weird-ways-to-hide-shellcode/
 bugcrowd
@Bugcrowd
Actual footage of me catching my first bug. I knew I was this close 🤏.
bugcrowd
@Bugcrowd
It isn't just organizations that benefit from Bugcrowd Live Hacking Events!
Here’s one of Bugcrowd's top hackers Justin Gardner (Rhynorater) talking his experience at our LHEs.
bugcrowd
@Bugcrowd
Prevent getting duped. Hunt XXE bugs in these uncommon places: 👇
bugcrowd
@Bugcrowd
How AI exploit capabilities should actually be measured, and why benchmark scores can be misleading.
Dr. David Brumley breaks it down in his Offensive AI Con 2026 keynote: AI Exploitation, Quantified
Watch the full talk: 👇
www.youtube.com/watch?v=HY4_9o2xPvk
bugcrowd
@Bugcrowd
Hot spots where you can hunt XXE bugs: 👇
bugcrowd
@Bugcrowd
Learn how to verify a blind XXE in under 2 minutes: 👇
bugcrowd
@Bugcrowd
Gather round the campfire as we celebrate Halloween by sharing the ghost stories of past phishing exploits that relentlessly haunt the world to this day. We love Halloween candy, but these phish aren’t so sweet!
Here are the tales:
1) The cursed USB device: An employee plugged a found parking lot USB drive into their computer, unleashing malware that quietly crept through the network and shut down critical systems at Saudi Aramco right before the holidays.
2) The employee impostor: Attackers used Business Email Compromise (BEC) to impersonate executives at Ubiquiti Networks and trick the finance team into sending urgent wire transfers, resulting in over $40 million lost.
3) When a third party brought the poltergeist: A supply chain compromise allowed attackers to inject malicious code into a routine software update at SolarWinds, letting them infiltrate thousands of government and corporate systems worldwide.
Read the rest of the stories (link below) 👇
www.bugcrowd.com/blog/trick-or-treat-5-spooky-phishing-st…
 bugcrowd
@Bugcrowd
More 📬 More 📬 More 📬
bugcrowd
@Bugcrowd
 bugcrowd
@Bugcrowd
Get the bad news while it's still good 🟧
For nearly 15 years, Bugcrowd has helped organizations find vulnerabilities that traditional security tools miss. Now we're taking that ingenuity further.
Today, we're sharing the next chapter of Bugcrowd: our evolution from crowdsourced to preemptive security.
By bringing human hackers and AI together, we're helping security teams discover exposure, validate what attackers can actually exploit, and act before risk becomes impact.
Because finding vulnerabilities is only part of the job. Finding them before attackers do is what changes the outcome.
Our CEO Dave Gerry shares why we're making this shift, what it means for our customers, and where we're headed next.
Read the full story 👇
bgcd.co/3W8ErTL
bugcrowd
@Bugcrowd
Nothing is scarier than these.
What are you dressing up as for Halloween? 👇

 bugcrowd
@Bugcrowd
Everyone wants a bite... 🐛💰
bugcrowd
@Bugcrowd
How can frontier AI models be trained to exploit real-world targets without getting tricked by reward hacking?
Our Chief AI & Science Officer, Dr. David Brumley, explains why traditional cybersecurity benchmarks fail and how redesigning RL environments enables effective training and evaluation of offensive AI capabilities.
Watch the full talk: 👇
www.youtube.com/watch?v=HY4_9o2xPvk
bugcrowd
@Bugcrowd
Are you getting continuous validation, an exploitability/risk score, and predictive intelligence in one place? Watch the on-demand webinar to learn how Bugcrowd can help. event.on24.com/wcc/r/5338391/6F6D2298E5D8365008458C3B8E10…
bugcrowd
@Bugcrowd
You really are famous
 bugcrowd
@Bugcrowd
Come join Bugcrowd's Reddit community, where you can brag about the bugs you found, vent about the ones that got marked as "duplicate," and pretend you're not just refreshing your inbox every five seconds for a bounty.
 bugcrowd
@Bugcrowd
CHALLENGE: This is a quick one. Spot the bug in 12 seconds! ⏲️
Got it? Drop your payloads. 👇
 bugcrowd
@Bugcrowd
➡️ DELETE /api/user/999 → 403 ❌
Try this:
➡️ POST /api/user/999 + X-HTTP-Method-Override: DELETE → 200 ✅
➡️ POST /api/user/999?_method=DELETE → 200 ✅
Gateways/auth middleware often match on verb+path. Frameworks (Laravel _method, Express method-override, Rails) may accept overrides at the router level.
Same for edge rules that only guard GET/POST. Try HEAD/PATCH/OPTIONS too.
 bugcrowd
@Bugcrowd
Attending a live hacking event is a career-defining experience for many hackers! Here’s why:
bugcrowd
@Bugcrowd
"Managing the PHP threat involves striking a balance between the risk of a severe cyberattack and the business impact of downtime." ⚖️
In the wake of PHP2Shell, our CI&SO Nick McKenzie shares a CISO perspective about how security and business leaders made decisions under pressure, what works, and what other CISOs can take into the next critical vulnerability.
www.bugcrowd.com/blog/behind-the-scenes-of-php2shell-what…
bugcrowd
@Bugcrowd
"Won't fix." 😂
bugcrowd
@Bugcrowd
Exactly one week from right now, you could be:
🟠 Meeting CISOs and expert hackers
🟠 Learning how to uncover vulnerabilities faster
🟠 Networking over drinks and dinner
It's your last chance to sign up for the Hive Exchange Nuremberg! Don't miss it 🚀 luma.com/4hngxg09
bugcrowd
@Bugcrowd
You can never go wrong with recon. 🔎
Here are some tactics you can try:
🟠 Scope company domains
🟠 Scope target company acquisitions
🟠 Enumerate ASNs
🟠 Run reverse WHOIS lookups
🟠 Enumerate subdomains
🟠 Analyze open ports
🟠 Check ad/analytics trackers
🟠 Use Shodan to find exposed assets
🟠 Google copyrights, terms of service, and privacy policies
Just make sure to test only in-scope assets. ✅
 bugcrowd
@Bugcrowd
Get a better understanding of why you should stay within scope: 👇
www.bugcrowd.com/blog/understanding-scope-for-higher-payo…
bugcrowd
@Bugcrowd
UPCOMING EVENT: Join us on October 21 for the RSA Conference, where Alistair G, our Director of Red Teaming, will participate as a panelist in the Innovation Showcase: "Countering AI-Powered Fraud Before It Happens."
Register here:
bgcd.co/4yVlDG6
 bugcrowd
@Bugcrowd
How does a top hacker prepare for a Live Hacking Event (LHE)? 😏
Let’s hear it from a pro:
bugcrowd
@Bugcrowd
Got rate-limited. 😩
bugcrowd
@Bugcrowd
“Is bug bounty really legal? 🤔”
Here’s a quick clarification: 👇
bugcrowd
@Bugcrowd
The Nuremberg Hive Exchange agenda just dropped ⬇️ We hope to see you October 28. Reserve your spot today! luma.com/4hngxg09
 bugcrowd
@Bugcrowd
You can now scroll X and Reddit at the same time! ⏬
If you’re interested in:
➡️ Bug bounty
➡️ Security news
➡️ or anything hacking-related
Follow us here and on Reddit! 🔔
Here’s our official subreddit: 👇
www.reddit.com/r/Bugcrowd
 bugcrowd
@Bugcrowd
How to discover and test API endpoints?
Here are some solid tips: 👇
bugcrowd
@Bugcrowd
No target yet? Take your pick here: 🎯
bugcrowd.com/engagements
bugcrowd
@Bugcrowd
Hack and party!🕺
bugcrowd
@Bugcrowd
Are you seeing a 403 when you access this:
GET /api/v2/admin/users ❌
You can try bypassing it by accessing an older API version:
➡️ GET /api/v1/admin/users
➡️ GET /api/admin/users
➡️ GET /api/V2/admin/users
➡️ GET /api/v2/admin/users with X-API-Version: 1
➡️ GET /api/v2.0/admin/users
➡️ GET /api/beta/admin/users
What else will you try? 👇
 bugcrowd
@Bugcrowd
We are continuously reviewing the mechanics of the Bugcrowd Platform to safeguard triage capacity, uphold signal quality across all engagements, and improve the experience for everyone. Read about our latest update here:
www.bugcrowd.com/blog/evolving-our-submission-accuracy-an…
bugcrowd
@Bugcrowd
Stuck on a target? Other hunters have your back.
 bugcrowd
@Bugcrowd
Join our community on Reddit 👇
www.reddit.com/r/Bugcrowd/
bugcrowd
@Bugcrowd
Why should an organization invest in a Live Hacking Event? 🤔
We'll let top hacker Justin Gardner (Rhynorater) explain👇
bugcrowd
@Bugcrowd
The Hive Exchange is coming to Nuremberg during it-sa Expo & Congress! Reserve your spot today luma.com/4hngxg09
 bugcrowd
@Bugcrowd
The average organization sees a 50% increase in critical findings in the six months that follow a live hacking event. These events aren't just about the day-of results...they're the gift that keeps on giving 🎁 www.bugcrowd.com/blog/how-to-choose-the-right-live-hackin…
bugcrowd
@Bugcrowd
📡 BROADCASTING TO THE CROWD
Vinted's bug bounty just went public on Bugcrowd!
Now's your time: bugcrowd.com/engagements/vinted-uab-mbb
 bugcrowd
@Bugcrowd
How does a classic XXE attack work? 🤔
Here’s a simple explanation: 👇
bugcrowd
@Bugcrowd
"If the first batch of findings is garbage, engineering tunes out everything after it."
Read the conversation between our CTO and SVP of Offensive Security about where agentic testing earns its keep and where it still needs a human. 🧵 www.bugcrowd.com/blog/agentic-vs-human-offensive-security…
bugcrowd
@Bugcrowd
CHALLENGE: Spot the bug in 15 seconds! ⏲️
.
.
.
.
.
.
.
.
.
.
.
Drop your payloads. 👇
 bugcrowd
@Bugcrowd
Today is World Tourism Day. #worldtourismday 🌍
Hackers are naturally drawn to places fueled by curiosity, cryptography, and covert history.
Here are 20 spy and intelligence museums worth a detour on your next trip 🧵👇
 bugcrowd
@Bugcrowd
17/ Museum of the Ministry of the Interior (Havana, Cuba): Four decades of Cuban intelligence history and counter-espionage records.
18/ International Spy Museum (Washington, D.C.): A massive facility on the global history and evolution of espionage. 🌐
19/ National Cryptologic Museum (Fort Meade, MD): Near NSA headquarters, showcasing the history of American signals intelligence and cryptography.
20/ SpyScape (New York City): A modern, interactive exploration of codebreaking, intelligence, and surveillance culture.
bugcrowd
@Bugcrowd
Which one are you adding to your list?
Bookmark this for your next trip.
bugcrowd
@Bugcrowd
Join Bugcrowd's Reddit community, ask questions, share tips, share wins, level up your skills together, and connect with hackers who live for the hunt.
 bugcrowd
@Bugcrowd
Check it out 👇🏻
www.reddit.com/r/Bugcrowd/
bugcrowd
@Bugcrowd
Beginners: What skill did you develop that helped you find so many bugs?
Experienced hackers:
 bugcrowd
@Bugcrowd
Your SAST tool flags noise. Savant Forge flags exploits. 🎯
Fuzz testing + symbolic execution = real vulnerabilities, prioritized, with working test cases attached. Savant Forge is built to keep pace with how fast AI is shipping code.
www.bugcrowd.com/blog/savant-forge-automated-offensive-te…
bugcrowd
@Bugcrowd
Being able to drop a critical zero-day without catching a federal charge is a luxury built on decades of pushback.
As governments and corporations finally realized how hackers could help them, they pushed to create exceptions to laws like the CFAA and DMCA. This paved the way for responsible disclosure policies.
Companies started adding "safe harbor" language to protect researchers who report vulns in good faith. Through the work of platforms like Bugcrowd and HackerOne, major tech companies adopted these policies, and eventually governments followed suit.
The more we protect and value ethical hackers, the safer everyone gets. 💯
 bugcrowd
@Bugcrowd
Dig deep into the hacker culture, check out our blog! 👇
www.bugcrowd.com/blog/the-hacker-culture-manual/
bugcrowd
@Bugcrowd
What are some misconceptions regarding data protection laws?
Learning this is important in understanding data/information leakage.
Here’s a short clip to clarify things: 👇
bugcrowd
@Bugcrowd
Watch the full video:
www.youtube.com/watch?v=ZM08KoiBkkI
bugcrowd
@Bugcrowd
These are some of the exciting live hacking event (LHE) stories told by the top hackers: 👇
bugcrowd
@Bugcrowd
Register and be part of LHEs! 👇
login.hackers.bugcrowd.com
bugcrowd
@Bugcrowd
CodeAI has been a Bugcrowd customer for almost a decade. Check out the case study to learn how CodeAI:
➡️ Moved from annual audits to always-on, continuous security testing
➡️ Surfaced vulnerabilities that internal testing missed
➡️ Freed teams from triage responsibilities, enabling investment in a dedicated security engineer.
www.bugcrowd.com/customers/codeai/
 bugcrowd
@Bugcrowd
What is considered “Personal Data”? 🤔
It’s important to know this distinction if you’re hunting for information disclosure bugs.
Here’s a quick explainer: 👇
bugcrowd
@Bugcrowd
Watch the full video:
www.youtube.com/watch?v=ZM08KoiBkkI
bugcrowd
@Bugcrowd
Most of the traffic hitting apps today is mobile. Most security programs still treat mobile like an afterthought.
We put together the Mobile Hacking Resource Kit: the blogs, videos, courses, and tools our community actually uses for iOS and Android pen testing.
Grab it 👇 (2-minute read, no form fill)
 bugcrowd
@Bugcrowd
How it feels to have the 'report and forget' mentality 😏
 bugcrowd
@Bugcrowd
Sent the report. Lost the peace.
 bugcrowd
@Bugcrowd
These are the patterns in the source code of a Windows app that will lead you to sensitive endpoints: 👇
bugcrowd
@Bugcrowd
Watch the full video: 👇
www.youtube.com/watch?v=xyqMBvTrbIA
bugcrowd
@Bugcrowd
✋ When thinking about securing AI agents, consider @davegerryjr's advice. "Treat a new AI agent the way you'd treat a new employee: with limited access, human oversight at decision points, and trust that has to be earned rather than assumed." www.secureworld.io/industry-news/ai-pacing-debate-securit…
bugcrowd
@Bugcrowd
Most hackers scan for bugs. The sharp ones scan for what the company is scared of losing.
Find that, and you find the treasure chest. 💎👇
bugcrowd
@Bugcrowd
Traditional pen testing hasn’t scaled. It was designed as a periodic audit, not a running program. Here are four ways the gap shows up in high-tech and SaaS environments...and what actually closes it. www.bugcrowd.com/blog/four-ways-traditional-pen-testing-f…
bugcrowd
@Bugcrowd
It’s the home stretch... you have one final week to win a physical copy of the Hacker Culture Manual. We're giving out 100 zines to the first hackers to get a non-dupe P1 on a paid bug bounty program between August 21st and September 21st. You also qualify for a copy if you are in the top 25 of the All-Time leaderboard by September 21st.
 bugcrowd
@Bugcrowd
Want to hack an API?
Here are 4 simple steps you can follow: 👇
bugcrowd
@Bugcrowd
Watch the full video: 👇
www.youtube.com/watch?v=wKTlcO-AxBM
bugcrowd
@Bugcrowd
A quick overview of the different types of API: 👇
bugcrowd
@Bugcrowd
Watch the full video: 👇
www.youtube.com/watch?v=wKTlcO-AxBM
bugcrowd
@Bugcrowd
What is an API? What does it look like? 🤔
Here’s a short explainer: 👇
bugcrowd
@Bugcrowd
Watch the full video: 👇
www.youtube.com/watch?v=wKTlcO-AxBM
bugcrowd
@Bugcrowd
CHALLENGE: Spot the bug in 15 seconds! ⏲️
.
.
.
.
.
.
.
.
.
.
.
Got it? Drop your payloads. 👇
 bugcrowd
@Bugcrowd
Part ✌️ of pranking my coworkers by switching the question. Maybe the best piece of cybersecurity advice is actually to never trust the social media manager... 🤭
bugcrowd
@Bugcrowd
How do IDORs occur? 🤔
Here’s a short explainer: 👇
bugcrowd
@Bugcrowd
Watch the full video:
www.youtube.com/watch?v=B_WESrC-wWs
bugcrowd
@Bugcrowd
Our CEO @davegerryjr joined Varney & Co. this morning to explain how malicious actors leverage AI to execute cyberattacks against critical infrastructure, businesses, and other AI systems. Check out the clip here 📺 www.foxbusiness.com/video/6404882622112
bugcrowd
@Bugcrowd
Two years ago, about a third of global companies used generative AI. Now, 80% of companies run autonomous AI agents, not just chatbots. AI security has reset completely. This blog covers six of the biggest changes in AI security. www.bugcrowd.com/blog/whats-changed-in-ai-security-over-t…
bugcrowd
@Bugcrowd
"You're going to start to see agents getting hacked, not people."
Check out this Axios article, where our CEO @davegerryjr spoke about his prediction that agents will start being adversaries and targets. www.axios.com/2026/09/08/ai-agents-bugcrowd-cyberattacks-…
bugcrowd
@Bugcrowd
Nation-state cyber attacks are increasingly targeting commercial companies. This blog dives into attacker economics, the shift to behavior-led detection, and tips for executive readiness. www.bugcrowd.com/blog/attacker-economics-and-targetabilit…
bugcrowd
@Bugcrowd
Bug bounty rewards the relentless
bugcrowd
@Bugcrowd
📢 Last call! You have just 48 hours left to register for a 30-minute fireside chat with Braden Russell and Julian Brownlow Davies about their tips to combine agentic and human security testing. event.on24.com/wcc/r/5473529/31E55D6876A6ED6CBDB61A230C0B…
bugcrowd
@Bugcrowd
Bet everyone remembers their first one
 bugcrowd
@Bugcrowd
Rookie hunters: skip the recon scripts at first. Just use the target app like a regular user.
Say your target is an e-commerce webapp.
Create a real account, complete a product checkout, and note every API call. You'll find endpoints and parameters that an automated crawler misses.
➡️ Record the entire flow with a proxy tool running in the background.
➡️ Note which parameters are incremental (userId, orderId).
➡️ Change IDs, replay requests in a different sequence, skip steps.
Try the same checklist on a login flow, a password reset, or a multi-step form.
Go find that P1. 💰
 bugcrowd
@Bugcrowd
Pranking my coworkers by changing the question 🫣
bugcrowd
@Bugcrowd
/api/user/profile?user_id=12345
Tweaks you can do on this endpoint: 🤔
➡️ user_id=12344
➡️ user_id=-1
➡️ user_id=123′ OR ‘1’=’1
➡️ user_id=12345&user_id=12344
➡️ {“user_id”:[“12345″,”12344”]}
What else will you try? 👇
 bugcrowd
@Bugcrowd
If you’re starting bug bounty from 0, aside from the technical challenges, you’ll probably face mental hurdles. 😩
Here’s @hakluke with some advice to help you overcome them: 👇
bugcrowd
@Bugcrowd
Aaaaaaaaand it's a P1! 💰
bugcrowd
@Bugcrowd
▶️ Have you subscribed to our channel yet?
We have:
✅ Practical bug bounty lessons
✅ CVE breakdowns
✅ Bugcrowd news & events
Check it out! 👇
youtube.com/@Bugcrowd
Some of our BEST content: 👇
bugcrowd
@Bugcrowd
There is a major tradeoff happening in the world of agentic pentesting. In our newest blog, our Chief Technology Officer Braden Russell breaks down how emerging autonomous pentesting tools are testing their technology, how the noise this creates is impacting triage teams, and how Savant Pathseeker is different. www.bugcrowd.com/blog/the-hidden-cost-of-agentic-pentesting/
bugcrowd
@Bugcrowd
OpenAI recently made a call for collective action on cyber defense in an open letter asking leaders across industry and government to make the digital infrastructure we all depend on more secure. Bugcrowd is proud to support this effort and sign the letter calling for urgent, collective action on cyber defense. openai.com/collective-cyberdefense/
bugcrowd
@Bugcrowd
“What matters as much as the volume is what Maryland actually does with it. Every single result is 100% actionable. Bugcrowd isn’t going to hand you a false positive after triage. You cannot get that out of another product or service.” - Steve Kain, Director of Adversary Emulation, Maryland Department of Information Technology (DoIT)
Read the full Maryland DoIT success story to see how the team built a researcher-first program. www.bugcrowd.com/customers/maryland-department-of-informa…
bugcrowd
@Bugcrowd
If you truly want to understand the soul of the hacker community, look at the slang we refuse to let go.
Language is one of the most powerful ways we preserve our culture and bridge the gap between different generations of hackers.
Favorite words like pwned and leet (1337) have survived since the BBS boards of the 1980s, serving as a linguistic thread that connects us to our roots. Even with the arrival of corporate compliance speak, over 90 percent of hackers still feel knowledgeable in hacker culture and lore.
This lore is not just about nostalgia, it’s a shared identity that reminds us why we started hacking in the first place.
So, what’s your favorite h4ck3r word?
 bugcrowd
@Bugcrowd
Dig deep into the hacker culture, check out our blog! 👇
www.bugcrowd.com/blog/the-hacker-culture-manual/
bugcrowd
@Bugcrowd
A few weeks ago was DEFCON, but do you know the story behind it?
Let's look at the rise of DEFCON and live hacking 🧵👇
 bugcrowd
@Bugcrowd
That energy stuck, and the rest is history.
Want more stories like this? Find them in The Hacker Culture Manual (grab it for free!) 👇
bugcrowd
@Bugcrowd
Will a well-written report get you better bounties? 🤔
Absolutely!
Here are some report-writing essentials: 👇
bugcrowd
@Bugcrowd
Watch the full video:
www.youtube.com/watch?v=vN-t9FWdcsA
bugcrowd
@Bugcrowd
You only have 10 seconds to review this. ⏱️
10…
9…
8…
7…
6…
5…
4…
3…
2…
1…
Is this safe for a PostgreSQL setup? Or did you SPOT a bug? 🤔
Share your payloads! 👇
 bugcrowd
@Bugcrowd
This is how a BAC vuln was found. 👇
bugcrowd
@Bugcrowd
Watch the full video:
www.youtube.com/watch?v=zlodGMqAuD8
bugcrowd
@Bugcrowd
Dr. David Brumley has thoughts on what most people miss when it comes to AI. Check out the full webinar to learn more. event.on24.com/wcc/r/5374864/73CA17ADA2FE4464483D0F4F09ED…
bugcrowd
@Bugcrowd
Bugcrowd VRT explained: how P1-P5 & CVSS mapping works. 🤓
Check it out: 👇
bugcrowd
@Bugcrowd
Watch the full video:
www.youtube.com/watch?v=LAyG8dySuMw
bugcrowd
@Bugcrowd
These are the first steps you can take if you're hunting for RCEs. 👨💻
Here’s a mini masterclass: 👇
bugcrowd
@Bugcrowd
Watch the full video: 👇
www.youtube.com/watch?v=1fdKBB9KPRs
bugcrowd
@Bugcrowd
Editing our Black Hat footage to look like a horror movie 😈
bugcrowd
@Bugcrowd
The most effective hack in history was not a fancy technical exploit, it was a congressional testimony.
In 1998, members of L0pht sat in front of the US Senate and told them they could take down the entire internet in 30 minutes. They did this to encourage the government and the public to take digital threats seriously.
At that time, major software companies were showing zero interest in fixing the flaws they were responsibly disclosing.
As these talks concluded, the hackers were hired by corporations and the government.
It wasn't a sellout move, it was an action that established the rules for integrating security into development processes and created internal procedures for resolving issues. They demanded flaws be fixed before products shipped.
This is how hackers pushed for a real change.
 bugcrowd
@Bugcrowd
Dig in deep into the hacker culture, check out our blog! 👇
www.bugcrowd.com/blog/the-hacker-culture-manual/
bugcrowd
@Bugcrowd
A few weeks ago, we released The Hacker Culture Manual. It’s a celebration of hacking; for hackers, by hackers. A compilation of the stories of the people who helped Bugcrowd get where we are today.
Let's dive into one of its chapters: The Unwritten Rules of Hacking – The six laws of hacker culture. 🧵👇
 bugcrowd
@Bugcrowd
Check out the The Hacker Culture Manual (it's free)👇
bugcrowd
@Bugcrowd
The Hacker Culture Manual is here, full of easter eggs, nostalgia, and hidden 1337s.
We're giving out 100 physical copies of the zine to the first hackers to get a non-dupe P1 on a paid bug bounty program between today and September 21st. If you're in the top 25 of the All-Time Leaderboard by September 21st, you'll also get a copy!
In the meantime, here's a digital copy. Happy hacking! www.bugcrowd.com/blog/the-hacker-culture-manual/


 bugcrowd
@Bugcrowd
A hacking approach that everyone can easily follow. 💯
Here's a 2-min crash course. 👇
bugcrowd
@Bugcrowd
Watch the full video:
www.youtube.com/watch?v=Ot8FihzhAjo
bugcrowd
@Bugcrowd
What's the bug that gave you the most bounties? 💰
Share a quick story about how you caught it. 👇
 bugcrowd
@Bugcrowd
It's just missing an energy drink
 bugcrowd
@Bugcrowd
CHALLENGE: Spot the bug in 20 seconds! ⏲️
.
.
.
.
.
.
.
.
.
.
.
Drop your payloads. 👇

bugcrowd reposted
 Nasdaq Exchange
@NasdaqExchange
.@davegerryjr, CEO of @Bugcrowd, visits Nasdaq to discuss the future of crowdsourced cybersecurity and how AI is empowering, not replacing ethical hackers. While AI tackles the grunt work, human creativity remains essential for identifying business logic flaws, connecting vulnerability data, and stopping attackers before they reach sensitive client information.
See the full interview here: www.nasdaq.com/solutions/listings/live-from-marketsite
bugcrowd
@Bugcrowd
Tell us your BEST bug chain (don't name the target!). 👇
 bugcrowd
@Bugcrowd
I just want to verify the bug. 😅
bugcrowd
@Bugcrowd
🛑 DON'T immediately submit your low-impact bugs.
Here’s @zseano with some pro tips on what you should do with them: 👇
bugcrowd
@Bugcrowd
Full video: 👇
www.youtube.com/watch?v=BEaMhs9LmoY
bugcrowd
@Bugcrowd
A classic technique that can still land you bugs in 2026. 😏
bugcrowd
@Bugcrowd
Full video: 👇
www.youtube.com/watch?v=BEaMhs9LmoY
bugcrowd
@Bugcrowd
Testing IDOR is not just swapping IDs in the URL.
If the obvious ?user_id=123 to 124 does not work, explore IDOR in:
🧵👇
 bugcrowd
@Bugcrowd
File names and paths in upload and export endpoints.
A filename field in a multipart upload or an export request like GET /export?file_id=789 can reference another user's file if ownership is not checked server-side.
bugcrowd
@Bugcrowd
Widen your hunt and catch that P1. 🔎🐝
bugcrowd
@Bugcrowd
You have 10 seconds to review this. ⏱️
10…
9…
8…
7…
6…
5…
4…
3…
2…
1…
Did you spot the bug?
Share your payloads! 👇
 bugcrowd
@Bugcrowd
This hacking secret may lead to your first P1. 😏
Spoiler: This may also lead to your first RCE.
Here's a quick watch: 👇
bugcrowd
@Bugcrowd
How to filter out 10,000+ subdomains. 🌐
Spoiler: they used httpx.
Here's a short explainer: 👇
bugcrowd
@Bugcrowd
Happy #internationalcatday!
Let's talk about the infamous "Meow" hackers.
🧵👇
 bugcrowd
@Bugcrowd
How did they do it?
They targeted unprotected Elasticsearch and MongoDB databases that lacked basic password protection.
But instead of deploying ransomware or demanding money, the botnet ran a simple search-and-destroy script that instantly overwrote the data, replacing it with the word: meow followed by random numbers.
bugcrowd
@Bugcrowd
The takeaway of this?
If you leave your database sitting on the edge of the internet desk, someone is eventually going to push it off. 🗑️🐈
bugcrowd
@Bugcrowd
Drop what you're doing and come to Swingers 🐝🏌🏼♂️
The party starts right now! From 4:00–5:30 PM, we have our speaker sessions and book signing. Starting at 6:00 PM, the drinks flow and the mini-golf tournament begins. If you are already in the venue, welcome! If you're on your way, we can't wait to see you 🫶
Let's get it: www.bugcrowd.com/the-hive/
bugcrowd
@Bugcrowd
Things you need to get started in game hacking: 👇
bugcrowd
@Bugcrowd
The business hall closes today, which means your window to sync with our elite offensive security crew at Booth 5532 is rapidly shutting. ☹️
If you haven't stopped by to see how we’re redefining continuous asset visibility and crowdsourced validation, this is it. Grab what's left of the swag, ask your technical questions, and lock in your plans before we transition to the evening festivities. 🕺
 bugcrowd
@Bugcrowd
If you look at your step counter right now, you definitely deserve a break. 👟
Tomorrow afternoon, we’re skipping the business hall exhaustion and heading to Swingers right next door.
The agenda is fully locked and loaded:
🔥 4:00 PM: AI changed the rules
📚 4:30 PM: An exclusive book signing with the industry's finest
☁️ 5:00 PM: Hacking in the age of AI
🍹 6:00 PM: A mini-golf reception with light bites and drinks
Consider this your final warning to get your name on the list before doors open! BIG thanks to @HPE and sponsors @trustvijil, Cytix, @Pi_Security_, and Manifold Security!
Grab your entry pass: www.bugcrowd.com/the-hive/


 bugcrowd
@Bugcrowd
Want to try game hacking? 🎮
Here's a view of what it actually looks like. Take a peek: 👀
👇
bugcrowd
@Bugcrowd
Day 2 energy check, how we doin'?!?! 🙌
Shake off the casino haze and find the familiar orange at Booth 5532. Today we're feeling extra hype after all the positive conversations yesterday (sorry if you're feeling the opposite)
Don't wander the floor aimlessly—come hang out with us 📍

 bugcrowd
@Bugcrowd
Ever heard of account pre-hijacking?
An attacker registers an account using the victim's email BEFORE the victim ever signs up. Later, when the victim uses SSO with that same email, some apps merge them into the attacker's existing account instead of creating a new one.
 bugcrowd
@Bugcrowd
3️⃣ Check if:
a) they get merged into your account
b) attacker's session/password persists
bugcrowd
@Bugcrowd
If the app mishandles the merge, you've got yourself a potential bounty! 💰
bugcrowd
@Bugcrowd
THE DOORS ARE OPEN 🏃🏻♂️
This might not be Black Friday at Walmart, but it is Black Hat, and we do think you need to hurry on over to Booth #5532.
The Bugcrowd team is locked in and ready to show you how we're matching the speed of modern threat actors with scalable crowd-sourced innovation.
We’ll see you soon! 😎
 bugcrowd
@Bugcrowd
This code is up for review.
Can you SPOT the bug? 🔎🐞
How would you exploit? 👇
 bugcrowd
@Bugcrowd
We didn’t fly all the way to Vegas to pass out stickers and play nice 💀
The vendor floor is full of companies using the same buzzwords (yuck). Tomorrow, we’re at Booth 5532 to show you what happens when you orchestrate human ingenuity instead of relying on passive scans.
If you want to see our latest platform updates up close, come see us. And if you want the smaller low-key vibe, meet us at The Hive on Thursday. Or, come to both! 😇
Learn more about Savant Pathseeker: www.bugcrowd.com/products/pathseeker
Track us down and say hi: www.bugcrowd.com/the-hive/
 bugcrowd
@Bugcrowd
Going to DEF CON? Join us and Chainguard to kick off their Bug Bash event, Saturday August 8th at RedTail Sports Bar chainguardbugbash.splashthat.com
 bugcrowd
@Bugcrowd
🌐 Web fundamentals: an essential to learning bug bounty.
Here’s a 2-min explainer: 👇
bugcrowd
@Bugcrowd
Watch the full video:
www.youtube.com/watch?v=tr5xbhmSgO4
bugcrowd
@Bugcrowd
Here’s why you shouldn’t skip web basics: 👇
bugcrowd
@Bugcrowd
Watch the full video:
www.youtube.com/watch?v=tr5xbhmSgO4
bugcrowd
@Bugcrowd
Do you need to spend money to get started in bug bounty? 🤔
Here’s a quick answer! 👇
bugcrowd
@Bugcrowd
Watch the full video:
www.youtube.com/watch?v=XSYzbAKgyUs
bugcrowd
@Bugcrowd
Bug bounty programs have a clear, easily measurable ROI, which makes management conversations simple.
Hear it from one of our clients 👇
bugcrowd
@Bugcrowd
Traditional pentesting gave you depth, but zero scale. Early automated scanners promised scale, but gave you a mountain of false negatives and a false sense of security.
The industry is evolving again, and the narrative is shifting from "AI vs. Human" to Agentic + Crowd.
Bugcrowd's Julian Brownlow Davies just broke down the raw truth about automated pentesting—the massive wins in speed, the dangerous blind spots of pure automation, and why a hybrid approach is the only way to reduce risk.
Oh, and we also dropped a first look at our new agentic pentesting solution, Savant Pathseeker. 😉
Get the answers to the tough questions here: www.bugcrowd.com/blog/frequently-asked-questions-about-au…
bugcrowd
@Bugcrowd
Don't blink now. 👀

 André Baptista
@0xacb
🚨We reported KindaRails2Shell, a critical RCE in Ruby on Rails via Active Storage.
It’s not a one-shot RCE, but the preconditions are kinda common under default configurations.
Patch your applications now!
ethiack.com/info-hub/research/kindarails2shell-rails-rce-…
bugcrowd
@Bugcrowd
The clock is ticking and our guest list is getting tight 👀
Next Thursday, August 6th, The Hive takes over Swingers to deliver the ultimate antidote to conference fatigue.
We’ve packed one evening with AI debates, top-tier author signings, an indoor mini-golf green, and drinks to toast the end of the briefings. 🥳
Not possible without our partner @HPE and sponsors @trustvijil, Cytix, @Pi_Security_, and Manifold Security!
Check out our full itinerary here: www.bugcrowd.com/blog/your-official-hacker-summer-camp-it…
 bugcrowd
@Bugcrowd
See you on the green 😎 ⛳
 bugcrowd
@Bugcrowd
If your library consists entirely of outdated compliance manuals, we need to fix that. Next week at The Hive ✨ August 6th at 4:30 PM ✨ you get immediate access to the industry's sharpest thinkers.
Antonio Bovoso, John Speigel, and Jaye Tillson are hanging out to sign books, chat strategy, and give you some hard-hitting perspectives to take back to your executive board. Come for the insights, leave with an autographed playbook.
Put it on your calendar: www.bugcrowd.com/the-hive/
🤝 🤝 @HPE, @trustvijil, Cytix, @Pi_Security_, Manifold Security
 bugcrowd
@Bugcrowd
The junior missed this flaw.
Can you spot the bug? 🔎🐞
Share your PoCs. 👇
 bugcrowd
@Bugcrowd
We're excited to announce Savant Pathseeker 🟧 💥
For the first time, security teams can run continuous agentic pentesting across every web application and API to get findings with real proof of exploitability.
Bugcrowd is a complete preemptive security platform:
1️⃣ Autonomous testing
2️⃣ Asset discovery
3️⃣ Human-led validation
By combining these three, your team can uncover the full picture of your risk 🔎
www.bugcrowd.com/blog/introducing-savant-pathseeker-agent…
bugcrowd
@Bugcrowd
We teamed up with an incredible lineup of cohosts and sponsors to build The Hive. 🥳
Together, we have designed a dedicated oasis just steps from Black Hat where you can actually escape the sales pitches, sink a few putts, and talk real-world risk strategy with peers who get it.
A massive thank you to our brilliant partners for helping us curate the best room in Vegas on August 6th. We couldn't do this without you, @HPE, @trustvijil, Cytix, @Pi_Security_, and Manifold Security!
See you on the green! ⛳👇
www.bugcrowd.com/the-hive/
 bugcrowd
@Bugcrowd
You’ve chosen your target. What now?
Here are some tips: 👇
bugcrowd
@Bugcrowd
Watch the full video:
www.youtube.com/watch?v=Ot8FihzhAjo&t=3s
bugcrowd
@Bugcrowd
Another day in the office. 💻
bugcrowd
@Bugcrowd
Hacking tip!
Whenever you land on a page that contains a secret in the URL (password reset tokens, email confirmation tokens, or even API keys), jump into your HTTP history in your intercept proxy and search for that token.
It's common to see outbound requests to 3rd-party services that contain secret keys, which is not ideal.
🧵👇
 bugcrowd
@Bugcrowd
Here’s a simple methodology:
1️⃣ request a password reset
2️⃣ open the network tab of your browser dev tools
3️⃣ open the reset link with the secret token
4️⃣ scour the network requests for any 3rd-party requests that contain the token
bugcrowd
@Bugcrowd
The most common place to see it is in the Referer header. Anyone with access to the logs of the server that receives the request (admins, support staff, or anyone who compromised that subdomain) can now steal the tokens
It's also worth checking this on mobile! Sometimes the flow differs a bit.
Go, catch that bug! 💰
bugcrowd
@Bugcrowd
Pop the hood on an AI system and things get complicated fast.
Training data, fine-tuning, context windows, tools, memory, agents. Each layer helps the system do more. Each layer also gives attackers somewhere new to meddle.
The CISO checklist is changing 👇
✅ What trained the model?
✅ What can enter its context?
✅ What tools can it call?
✅ How far can it run without human approval?
Dr. David Brumley breaks down the anatomy of modern AI systems and where the risks live. Read the latest AI lecture: www.bugcrowd.com/blog/ai-lectures-with-dr-brumley-part-2-…
bugcrowd
@Bugcrowd
What happens in Vegas stays on the mini-golf course. The only high-pressure thing here is your short game. ⛳
The Hive Reception kicks off on August 6th at 6:00 PM with light bites, refreshing drinks, and an epic indoor setup just steps away from Black Hat. If the cab line is 30+ minutes to get back to your hotel, you might as well stop by here instead!
Come hang out with new friends, shoot the breeze after a long week on the floor, and see if you can nail a hole-in-one before the night wraps up 😎
Don't forget to register: luma.com/Hivereceptionatbhusa26
Thanks to our partner @HPE and our sponsors @trustvijil, Cytix, @Pi_Security_, and Manifold Security!
 bugcrowd
@Bugcrowd
This code is sent for review. Is there a bug? 🤔
Share your payloads. 👇
 bugcrowd
@Bugcrowd
5 rapidfire bug bounty tips in under 2 minutes. GO 🏃♂️
bugcrowd
@Bugcrowd
Watch the full video:
www.youtube.com/watch?v=Ot8FihzhAjo&t=3s
bugcrowd
@Bugcrowd
🤥 Is your current security dashboard lying to you? Most traditional toolsets are good at generating an endless list of theoretical flaws, but they leave your team drowning in guesswork.
Let’s change how you look at exposure. The Bugcrowd crew is setting up base camp at Booth 5532 from August 4–6 to show you how orchestrating genuine human ingenuity flips the script on modern adversaries.
Swing by, check out our latest platform mutations, and walk away with some legendary swag 🛍️
Put us down as your 1st stop and check out what else we'll be up to: www.bugcrowd.com/the-hive/
 bugcrowd
@Bugcrowd
The most severe exposure lives in the quiet overlap between tech, people, and process. ♾️
A single leaked credential, an overly permissive token, or a subtle change to a deployment pipeline might seem isolated. But a skilled researcher doesn't look at them in isolation. They trace how these minor friction points chain together to create an exploitation path.
If you aren't actively auditing the intersections of your ecosystem, you're missing the actual attack vector. 😌
Uncover the systemic gaps before they become incidents and learn more in our full AMA with Alex from Trustpilot: www.bugcrowd.com/blog/lessons-from-our-ask-me-anything-wi…
bugcrowd
@Bugcrowd
That’s how it works. 💰
Deal?
Register and pick your target here! 👇
bugcrowd.com/engagements
 bugcrowd
@Bugcrowd
Really, the first thing you need to do when you're just starting with bug bounties is to learn how to use the platform really well.
This allows you to find programs that are better suited to you and submit bugs with confidence.
This video is invaluable for anyone starting out. 👇
www.youtube.com/watch?v=Lplbqsm49Qs
bugcrowd
@Bugcrowd
Hackers, register and log in here.
login.hackers.bugcrowd.com
bugcrowd
@Bugcrowd
With Stanford HAI reporting organizational AI adoption at 88%, your workforce is already using these tools whether they're sanctioned or not. 🤷
But before you can secure or govern AI systems, you need to change how you talk about them.
In his latest piece, Dr. David Brumley (Chief AI Officer at Bugcrowd / Professor at CMU) shares the core insights from his recent AI security lecture, outlining the next-level questions security leaders should be asking their vendors:
❓Which exact mechanism is this tool using?
❓Is this a standalone model, or a composite system wired to retrieval, memory, and tools?
Stop letting imprecise language dictate your security roadmap. Read Part 1 of the lecture series here: www.bugcrowd.com/blog/ai-lectures-with-dr-brumley-part-1-…
bugcrowd
@Bugcrowd
4-STEPS to bug bounty 🐞
 bugcrowd
@Bugcrowd
3️⃣ Pick a program
A program is your target, it’s what you’re going to hack.
Register and choose a program here:
bugcrowd.com/engagements
Choosing a program that you’re already familiar with is highly advisable. And bonus points if you regularly use their product. Makes your first hacking experience enjoyable. 🤩
bugcrowd
@Bugcrowd
4️⃣ GO HACK!
Oh, you’re still here? Go catch your first bug! 🔎🐞
bugcrowd
@Bugcrowd
Let’s talk about the tsunami of automated junk code hitting production. 🌊
The cloud-native landscape is mutating by the hour, and standard defense lines are bending under the weight. On August 6th at 5:00 PM, we’re teaming up with AWS Marketplace inside The Hive for a critical deep-dive 👇
Hacking in the Age of AI: What's Changed, What Hasn't. We’re swapping the standard abstract vendor pitches for a gritty, technical look at how elite researchers manipulate shared responsibility at scale.
🎤 Ads Dawson
🎤 @codingo_
Come see how the other side plays the game 😈
Claim your seat: www.bugcrowd.com/the-hive/
Massive thanks to @HPE, @trustvijil, Cytix, @Pi_Security_, and Manifold Security bringing this to life!
 bugcrowd
@Bugcrowd
Time to upgrade your office shelf space 😍🪄
Your brain deserves better than airport fiction on the flight home from Vegas.
On August 6th at 4:30 PM, we’re hosting an exclusive author meet-and-greet inside The Hive. Skip the usual small talk and grab a drink with Antonio Bovoso, John Speigel, and Jaye Tillson.
They’ll be handing out wisdom, answering your burning architecture questions, and signing copies of their latest hot sellers. First come, first signed—so don’t wander in late ⌚️
More details: www.bugcrowd.com/the-hive/
Shoutout to our friends at @HPE, @trustvijil, Cytix, @Pi_Security_, Manifold Security! 🫶
 bugcrowd
@Bugcrowd
The BEST advice for beginner hackers. 👇
bugcrowd
@Bugcrowd
Watch the full video:
www.youtube.com/watch?v=kQkBCaEqujk
bugcrowd
@Bugcrowd
AI has drastically accelerated vulnerability research and exploitation. Because of this speed, the half-life of a security team's baseline skills is now measured in months.
Keeping up requires treating continuous upskilling as a strict operational requirement. Organizations must build protected downtime into their schedules so teams can match the adversary's pace. 💨
Bugcrowd Chief Strategy and Trust Officer Trey Ford shared his perspective with Dice Insights:
"Security leaders need to stop positioning training as professional development and start framing it as operational readiness."
Read more about how AI is shifting security training requirements in this feature: www.dice.com/career-advice/ai-drives-need-for-training-fo…
bugcrowd
@Bugcrowd
Which one are you? 😏
 bugcrowd
@Bugcrowd
Generative tech and automated scanners are spinning up endless alerts, but they lack the business context and creative thinking that only humans possess.
📍 On August 6 at 4:00 PM at The Hive, Teri Robinson, Antonio Bovoso, David Hughes, Dr. Hannarae Lee, and Chenxi Wang are coming together for AI Broke Your Backlog, Now What?
Come learn how top tier security teams are filtering out automated slop, reclaiming their engineering timelines, and leaning into human-led validation to defend what actually matters.
🔗 Save your spot: luma.com/aibrokeyourbacklog
 bugcrowd
@Bugcrowd
Things that deserve a red card: you ignoring this post.
Everyone's favorite time of the year is almost here and we've got things lined up all week long.
🎩 Start your trip by swinging past Booth 5532 at Black Hat USA to talk proactive security and grab the iconic stickers.
🐝 When the business hall clears out on August 6th, skip the networking dinners and meet us at The Hive for speaker panels, book signings, and a competitive round of indoor mini-golf.
🪲 To top it all off, we're heading straight into DEF CON to sponsor Bug Bounty Village, DEF CON.
We just planned your entire week for you, you're welcome 😇
Register for what you're feeling here: www.bugcrowd.com/the-hive/


 bugcrowd
@Bugcrowd
AI has scaled external recon and app discovery, but internal tradecraft remains deeply human. 🧍
This imbalance is exactly why organizations are drowning in a flood of valid, external vulnerability reports.
🙅🏽♂️ Defending against this volume means changing how you prioritize. Attackers don't just look for isolated high-severity exploits; they collect situational awareness and use lower-tier findings to stitch together a full attack path.
Learn the four tiers of attacker decision-making and how to layer human intelligence over machine noise: www.bugcrowd.com/blog/the-ai-slop-era-do-most-vulnerabili…
Watch the 20-minute breakdown with with Julian Brownlow Davies and Alistair G. here: www.youtube.com/watch?v=TmPsNopd2TA
bugcrowd
@Bugcrowd
Bug bounty strategy that can land you MORE bugs. 👇
bugcrowd
@Bugcrowd
Watch the full video:
www.youtube.com/watch?v=kQkBCaEqujk
bugcrowd
@Bugcrowd
The most common public sector security failure is a simple oversight.
When massive portals share infrastructure, data accountability easily slips through the cracks. The fix is complete asset inventory visibility and a trusted channel to report flaws before adversaries find them.
As Bugcrowd’s Chief Strategy and Trust Officer, Trey Ford, points out:
"The job to be done is owning access control across the entire inventory of public-facing assets and treating coordinated disclosure as defensive infrastructure."
Read more on how coordinated disclosure turned three major exposures into fast fixes in this Dark Reading feature: www.darkreading.com/vulnerabilities-threats/vulnerabiliti…
bugcrowd
@Bugcrowd
Did you KNOW that we have a YouTube channel? ▶️
✅ Practical bug bounty tips
✅ CVE breakdowns
✅ Bugcrowd news & events
Check it out! 👇
www.youtube.com/@Bugcrowd
 bugcrowd
@Bugcrowd
Once the suits pack up at Black Hat, the real party starts 🪩😜
Bugcrowd is incredibly proud to head down the Strip and sponsor @BugBountyDEFCON this year. We're showing up to celebrate the incredible researcher community that powers the future of offensive security every single day.
Swing by the village to connect with the Crowd, talk tactics, and immerse yourself in pure hacker culture (only the best thing ever) 👾🎲
 bugcrowd
@Bugcrowd
Solid API testing tips. 👇
bugcrowd
@Bugcrowd
Watch the full video:
www.youtube.com/watch?v=zlodGMqAuD8
bugcrowd
@Bugcrowd
Why going DEEP in a single program is a great game plan for beginners. 💯
@the_IDORminator gives some tips on how to do it.
Here’s his solid advice. 👇
www.bugcrowd.com/blog/zwinks-tips-and-tricks-to-crush-bug…
bugcrowd
@Bugcrowd
 bugcrowd
@Bugcrowd
 bugcrowd
@Bugcrowd
What the cat said 👇
www.reddit.com/r/Bugcrowd/
bugcrowd
@Bugcrowd
Insider info only. 🤫
We’re dropping exclusive content over on our Reddit. Join now to unlock them. 🔓
👉www.reddit.com/r/Bugcrowd/
 bugcrowd
@Bugcrowd
What are the first steps of bug bounty?
✅ Learn the fundamentals
✅ Sign up
✅ Pick a target
What’s next? Run a vuln scanner? 😏 No!
@the_IDORminator explains why this is a bad idea. 👇
www.bugcrowd.com/blog/zwinks-tips-and-tricks-to-crush-bug…
bugcrowd
@Bugcrowd
When you sign up, we don't just dump you a bunch of programs, we guide you through the process and suggest a path based on your current skills.
Here's Brandon Reynolds showing you what it looks like. 🐝
bugcrowd
@Bugcrowd
Sign up here 👇
login.hackers.bugcrowd.com
bugcrowd
@Bugcrowd
As adversaries weaponize AI, cybersecurity training is no longer a professional development perk, it's an absolute requirement for operational readiness ‼️
"The budget investments aren't generosity; they're a calculated response to watching adversaries gain capabilities faster than human learning curves can match," notes Trey Ford, Chief Strategy and Trust Officer at Bugcrowd. "Boards are seeing the cost of not training show up in incident response budgets and breach disclosures."
Read the full Dice Insights piece: www.dice.com/career-advice/ai-drives-need-for-training-fo…
bugcrowd
@Bugcrowd
Shoutout to a very brilliant crew bringing you the BEST event at @BlackHatEvents USA this year 😏🙌
Putting together an event like The Hive takes a village, or at least a highly coordinated collective of security innovators.
A massive thank you to our incredible cohost: @HPE and sponsors: @Pi_Security_ , Cytix, and @trustvijil for helping us build the ultimate space to unwind, chat it up, and sink a few putts after #bhusa.
We couldn't ask for better partners!! See you all on August 6th 🎉
Register early: www.bugcrowd.com/the-hive/
 bugcrowd
@Bugcrowd
There’s IDOR in cookies 🍪
Some apps store object references in cookies rather than URL parameters or request bodies. If an app blindly trusts an object reference in a cookie, it may allow an attacker to read/modify other users' data.
👇🧵
bugcrowd
@Bugcrowd
Here’s a testing methodology:
1️⃣ Login and use your target app like a normal user.
2️⃣ Look for cookies that contain IDs, hashes, or numeric values that might reference objects.
3️⃣ Change these cookie values and observe if you can access or modify other users' data.
bugcrowd
@Bugcrowd
❗ Test both authenticated and unauthenticated scenarios. ALWAYS use multiple accounts for this type of testing.
This can lead to unauthorized modification of other users' data and integrity violations.
Catch those P1s! 💰
bugcrowd
@Bugcrowd
Critical security gaps in Indian government systems have left the private data of millions exposed, highlighting the vulnerabilities of traditional defense measures. 📏
"Securing public sector infrastructure requires continuous, crowdsourced vigilance," notes Bugcrowd CEO @davegerryjr. "When private citizen data is at stake, organizations must proactively discover gaps before malicious actors do."
Explore the full analysis on @DarkReading: www.darkreading.com/vulnerabilities-threats/vulnerabiliti…
bugcrowd
@Bugcrowd
Did you know an innocent smiley face can break LLM safety? It’s all about a vulnerability called Token Segmentation Bias. 👇
 bugcrowd
@Bugcrowd
LLMs don't read words like we do, they break text into pieces called "tokens." When you inject an emoji into the middle of a word (like sens😎itive), it throws the AI's tokenizer completely off track.
To the AI’s safety filters, a malicious prompt suddenly looks completely harmless, but it allows an attacker to make toxic requests or exploits that slip right past the guardrails.
bugcrowd
@Bugcrowd
You can read more about this vulnerability class here👇
medium.com/google-cloud/emoji-jailbreaks-b3b5b295f38b
bugcrowd
@Bugcrowd
Stop what you're doing and ditch those standalone EASM tools. 💅
They find assets, but leave you guessing about actual risk. Today we're changing that with the launch of Savant Vista on the Bugcrowd Platform.
🧭 Track what you own, scan for exposures, and use human ingenuity to validate what's exploitable from one centralized dashboard.
Stop playing catch-up with infrastructure changes.
Learn more 👉 www.bugcrowd.com/blog/introducing-savant-vista-know-what-…
bugcrowd
@Bugcrowd
The Bugcrowd platform has a bunch of features that can make it easier for you to find a program that you enjoy hacking on. One of those features is updating your “Skills and Interests”.
Brandon Reynolds explains how this can help you in choosing the right target.
You can find it in Account Settings > Skills and Interests.
bugcrowd
@Bugcrowd
Me on the 4th of July
 bugcrowd
@Bugcrowd
Today is #worldufoday, a reminder that one of the most famous hacks of all time was conducted by Gary McKinnon, who just wanted to see if the U.S. government was hiding alien technology. 👽
How did he breach NASA (and the DoD)? 👇
 bugcrowd
@Bugcrowd
He wrote a Perl script over a 56k dial-up connection to scan tens of thousands of military computers, hunting for machines where IT administrators had left the default passwords blank. Once he found an open door, he simply installed standard remote desktop software to log in and search for raw, unedited images of spacecraft.
He says he found some, but didn't retain any evidence. 👀
bugcrowd
@Bugcrowd
What do you think? Did you know about the UFO hacker?👇
bugcrowd
@Bugcrowd
The new administration executive order creates an entirely fresh security bargain between the government and the AI industry 🗞️
For cybersecurity leaders, this policy shift sets a clear mandate to prove proactive security measures are in place. Point-in-time audits will no longer cut it. Crowdsourced testing is becoming the standard for validating systemic resilience!
Read the full policy breakdown on Security Buzz: securitybuzz.com/cybersecurity-news/executive-order-barga…
bugcrowd
@Bugcrowd
We got you 😌🤣🐶
bugcrowd
@Bugcrowd
Why taking BABY steps is important when starting.
@the_IDORminator shares some advice on how to approach bug bounty as a total beginner.
A quick 2-min read. 👇
www.bugcrowd.com/blog/zwinks-tips-and-tricks-to-crush-bug…
bugcrowd
@Bugcrowd
The latest federal executive order shifts AI safety from a theoretical debate into an immediate engineering requirement for technical organizations.
Staying ahead of these incoming benchmarks means moving away from static checklist compliance. True preemptive security requires continuous pressure-testing to uncover structural vulnerabilities before code goes live.
Review the strategy and talent pipeline impact on DICE Insights: www.dice.com/career-advice/trump-administrations-ai-order…
bugcrowd reposted
 Bug Bounty Village
@BugBountyDEFCON
We're thrilled to welcome @bugcrowd as a Silver Sponsor of Bug Bounty Village at DEF CON 34! Their ongoing support helps us create a space for hackers to connect, learn, and push boundaries.
#defcon #bugbounty #bbv #bugbountyvillage
bugcrowd
@Bugcrowd
Consider this your official, socially acceptable excuse to duck out of work early✌️🎊
The Hive Exchange with Bugcrowd, @AWS, and @GlobalDots kicks off tomorrow at 2:00pm CEST. If you want to see how a hacker actually deconstructs your defense, stop scrolling and register.
Snag one of the last seats right here: luma.com/qke5k7r8
 bugcrowd
@Bugcrowd
Yaaaa, AI can scan at scale, but it lacks the instinct to exploit business logic.
Bugcrowd Chief Strategy and Trust Officer @treyford notes that specialized human talent remains irreplaceable 👏
"My expectation is bug bounty hunters will achieve a level of specialization where 'this is my niche, this is where I wreck things,' and you will need a group of doctors with skills in specific areas... to get a really comprehensive view of your most sensitive applications and services."
Read the full interview on ISMG: www.govinfosecurity.com/ai-reshapes-bug-bounties-but-huma…
bugcrowd
@Bugcrowd
When vulnerability discovery and exploit development can happen in under 10 hours, annual testing starts to look a little… dusty 🧹🧹
@davegerryjr and @thedavidbrumley discuss why security teams need to move toward continuous validation, red teaming, and active adversary emulation in the age of AI.
If you want to hear the full clip, click here➡️ www.youtube.com/watch?v=9B_m7iyAhn4&t=752s
bugcrowd
@Bugcrowd
Why you should start hunting for access control issues 🎛️
@InsiderPhD shares her insights 👇
bugcrowd
@Bugcrowd
Full video:
www.youtube.com/watch?v=wKTlcO-AxBM
bugcrowd
@Bugcrowd
AI adoption isn't waiting for perfect governance. If your framework only focuses on blocking deployment, you are inadvertently creating a shadow AI problem.
Bugcrowd Chief AI and Science Officer @thedavidbrumley frames the challenge clearly. 💬
"The question is not really 'which AI risk framework is best?' but 'which framework helps [the] organization safely build, deploy, and learn from AI in the real world?'"
True preemptive security doesn't stall innovation. It paves safe, continuous roads for a technology that is already inevitable 💯
See which frameworks bridge the gap in CSO Online: www.csoonline.com/article/4185917/5-ai-risk-management-fr…
bugcrowd reposted
 𝖁𝖆𝖘𝖎𝖑𝖊𝖎𝖔𝖘
@marketingrckstr
🚨 New target alert 🚨@
@Gameforge just launched their #vulnerabilitydisclosureprogram on @Bugcrowd!
Amazing games, great targets to hunt on, all ready for you to explore and break safely.
🧪 Go test it: bugcrowd.com/engagements/gameforge-vdp-ess
#runvdp
 bugcrowd
@Bugcrowd
What does it take to keep stakeholders happy, developers shipping, and massive digital footprints secure, all at the same time? 😵💫
Just Eat takeaway.com calls it flexibility. We call it a classic case of smart offensive security. 🍔✨
Get the inside look at how this decade-long security partnership scales: www.bugcrowd.com/blog/community-spotlight-just-eat-takeaw…
 bugcrowd
@Bugcrowd
Your calendar is looking empty at 10am BST on July 1. Let's change that. 😉
Trustpilot protects its reputation by giving elite researchers free rein to find structural flaws before malicious actors do.
When trust is your product, you have to actively hunt for the gaps your tools miss.
If trust is important to you, which is probably everyone reading this, sign up here: event.on24.com/wcc/r/5376481/75D1C68A9DD9F8FE14C8E88E0F5B…
 bugcrowd
@Bugcrowd
Hunting for your first RCE?
 bugcrowd
@Bugcrowd
Here’s a complete guide to attack pathways and detection methods 👇
www.bugcrowd.com/blog/how-to-find-rce-a-list-of-pathways-…
bugcrowd
@Bugcrowd
From alert(1) to ATO.
Here’s a quick explainer by @InsiderPhD on how to maximize the impact of your reflected XSS.
bugcrowd
@Bugcrowd
Full video ⬇️
www.youtube.com/watch?v=CpV3XDqzYyE
bugcrowd
@Bugcrowd
That alert is about to pop, keep going! ⚠️
 bugcrowd
@Bugcrowd
Security debt has a nasty interest rate. 📈
Startups are great at moving fast. That's the whole point.
But when security gets pushed too far down the roadmap, risk starts compounding in ways that can hit growth, trust, and customer confidence.
Crowdsourced security gives startups a way to bring in outside expertise earlier, without adding unnecessary overhead. ✨
If you're leading security for a tech startup, this guide can help you scale coverage earlier and build the kind of confidence buyers expect.
Read more in the full guide: www.bugcrowd.com/resources/guide/ultimate-guide-to-securi…
bugcrowd
@Bugcrowd
More alerts ≠ more security 🛑
If your security strategy relies on throwing every single automated finding at your engineering team and hoping for the best, we need to talk.
A mature bug bounty program isn't extra homework for your developers. It’s a filter. It brings hacker ingenuity into the loop to separate real threats from background noise.
📣 Don't miss AMA with Trustpilot on July 1!
Move away from guessing games and toward actual risk reduction. Because let’s be honest: assuming makes an 🫏 out of you and... well, you know the rest.
Add it to your calendar: event.on24.com/wcc/r/5376481/75D1C68A9DD9F8FE14C8E88E0F5B…
bugcrowd
@Bugcrowd
The ONLY tip you need if you’re starting from zero.
@the_IDORminator gives solid advice on how you can get STARTED hacking without spending a dime. 😎
Check it out! 👇
www.bugcrowd.com/blog/zwinks-tips-and-tricks-to-crush-bug…
bugcrowd reposted
𝖁𝖆𝖘𝖎𝖑𝖊𝖎𝖔𝖘
@marketingrckstr
Day 1 @owasp global con in Vienna with @Bugcrowd: completed it, mate ✅ Bring on Day 2 💪🏼💪🏼
 bugcrowd
@Bugcrowd
Security dashboards are full.
But full doesn’t mean focused.
Here’s how teams can shift from vulnerability volume to validated risk ⤵
Run a continuous cycle:
🔸 Avoid
🔎 Discover
✅ Validate
👨🔧 Fix
Learn more 🔄: www.bugcrowd.com/blog/from-volume-to-validated-risk-kpis-…
bugcrowd
@Bugcrowd
"We'll fix that in next month's pen test."
Said no secure company, ever. 😶
If you're shipping daily but testing annually, you're leaving a gaping window of exposure for attackers to find first.
Pairing your existing strategy with a continuous bug bounty program isn't an alternative—it’s a pipeline requirement. Protect your deployment velocity and keep your code covered, 24/7/365. 🚀
Upgrade your offensive security strategy. Here's the rundown: www.bugcrowd.com/blog/why-companies-choose-bugcrowd-for-m…
 bugcrowd
@Bugcrowd
A new executive order establishes a voluntary 30-day pre-release review for frontier AI models and directs CISA, the Treasury, and the DOJ to create a cybersecurity clearinghouse to crack down on AI-enabled cybercrime.
It is a delicate balancing act between national security and technological innovation. As Bugcrowd CEO @davegerryjr highlights in the piece, adversaries move faster than bureaucracy, strategic priority is a great first step, but security ultimately comes down to speed. 🔐💨
Learn more from @security_buzz: securitybuzz.com/cybersecurity-news/executive-order-barga…
bugcrowd
@Bugcrowd
Think of a number between 1 and 10. A hacker already knows you picked 7.
Kidding! They're not magicians, but we do need their magic 🪄
Security isn’t a software problem; it’s a perspective problem. You look at a wall and see a barrier. A hacker looks at the same wall and wonders how thick the drywall is 💭
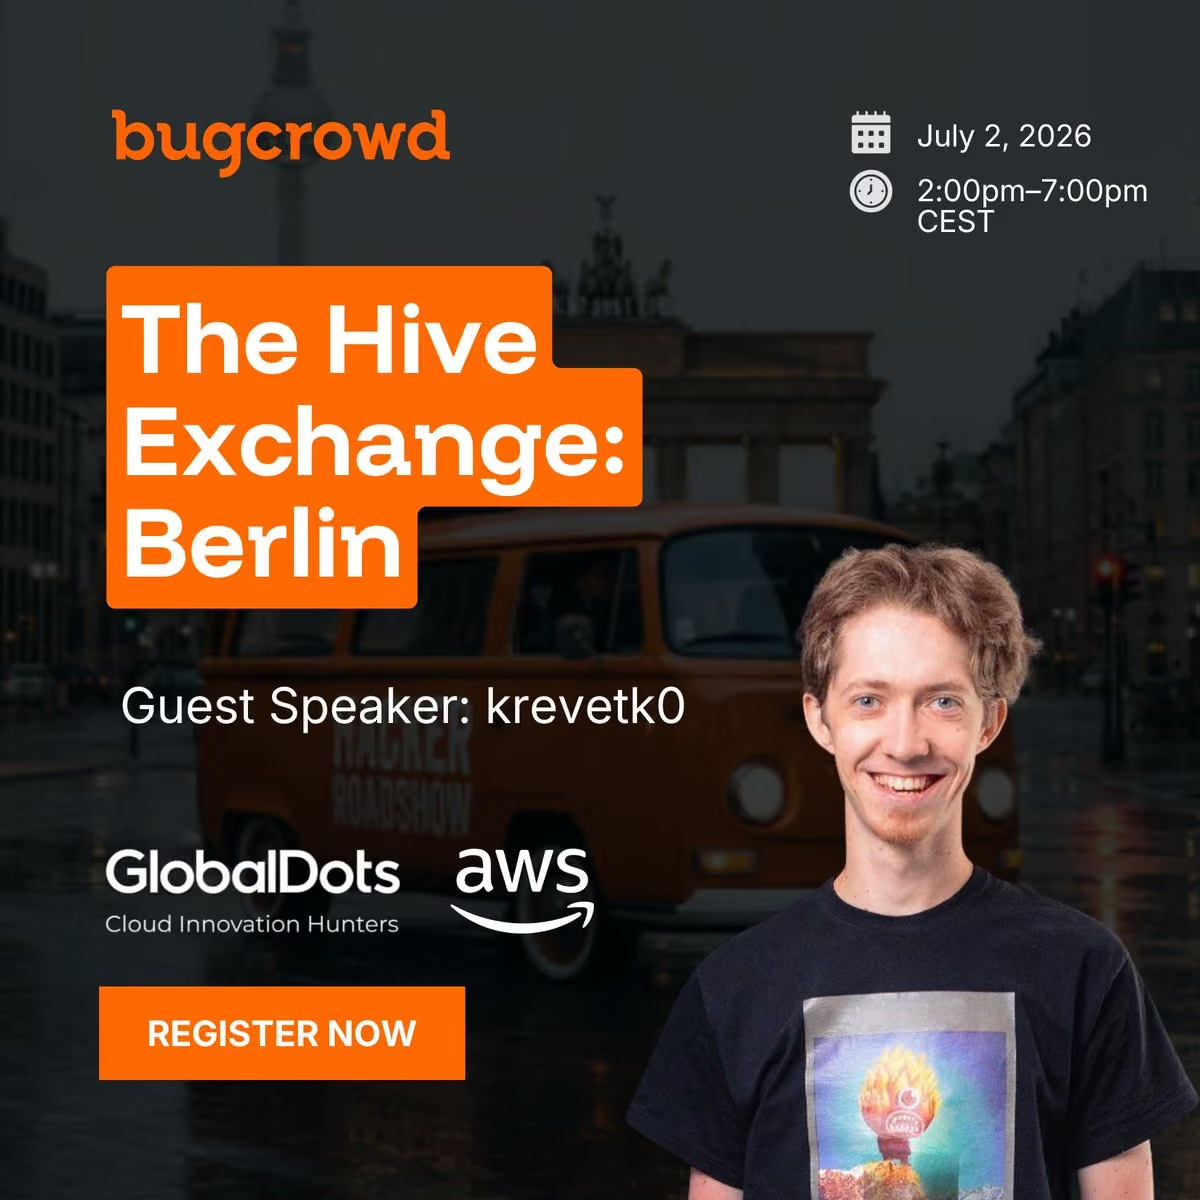
On July 2, we’re putting the builders and the breakers in a room in Berlin to see what happens when those two mindsets collide. The Hive Exchange features Bugcrowd, @AWS, @GlobalDots, and guest speaker krevetk0.
We’re dissecting exactly how a defender’s "perfect logic" turns into a hacker’s favorite target. Come learn how to think upside down.
🍻 Berlin on July 2 from 2:00–7:00pm CEST
🐝 Register: luma.com/qke5k7r8
 bugcrowd
@Bugcrowd
A QUICK rundown of authentication & authorization testing ⚡
Let’s hear it from @InsiderPhD 👇
bugcrowd
@Bugcrowd
Full video:
www.youtube.com/watch?v=wKTlcO-AxBM
bugcrowd
@Bugcrowd
Learning Regex doesn't have to be that scary.
 bugcrowd
@Bugcrowd
Here is a practical guide to Regular Expressions (Regex) for Hackers.👇
www.bugcrowd.com/blog/how-to-regex-a-practical-guide-to-r…
bugcrowd reposted
 kuzushi
@kuzushi
As I am just arriving to the conference, I can now open up a little bit more of the results of some of my research into hacker cognition. Blog post attached :)
bugcrowd
@Bugcrowd
12 out of 15 top-tier hackers ignore standard security methodologies.
🤯
New research into hacker cognition reveals that elite researchers don’t follow rigid checklists when testing a target. Instead, they rely on fast, intuitive pattern recognition built from years of building, breaking, and tinkering.
Compliance scripts find basic bugs. Human intuition stops catastrophic breaches. ✋🌪️
A checklist can't replicate what a diverse crowd natively possesses. Hackers don't come from a single mold, and that is exactly why they see the blind spots your automated tools miss.
The blog by Andrew shows more data behind how hackers actually make decisions: www.bugcrowd.com/blog/experience-vs-methodology-how-hacke…
bugcrowd
@Bugcrowd
The bugs that ruin your weekend aren't the ones on your automated reports. 💀
Scanners love to hand you a mountain of minor alerts, but they miss the giant logic flaws, like a single mobile app integration completely bypassing the need for millions of dollars worth of SSO and MFA.
💰 Bounties and traditional testing keep the baseline secure, but Bugcrowd Red Team as a Service (RTaaS) is how you stop the catastrophic, business-ending attack paths.
Hear the full breakdown from our Director of Red Team Operations on why it’s time to scale up your defensive context ⤵
🎬: www.youtube.com/live/TmPsNopd2TA
bugcrowd
@Bugcrowd
CSO Magazine just published a great breakdown of the frameworks helping security leaders manage algorithmic bias, data poisoning, and prompt injection:
📑 ISO/IEC 42001 👉 Holistic program building
📑 NIST AI RMF 👉 Flexible, maturity-based playbook
📑 ENISA FAICP 👉 EU-focused compliance baseline
📑 ISO/IEC 23894 👉 Lifecycle risk guidance
📑 Google SAIF 👉 Engineering-heavy defense controls
As Bugcrowd’s David Brumley points out in the piece, the goal shouldn't be to halt progress with rigid governance, but to pave safe roads for real-world AI deployment.
Full breakdown: www.csoonline.com/article/4185917/5-ai-risk-management-fr…
bugcrowd
@Bugcrowd
Quick Rule of Thumb💡
Focus on hunting for critical/high-impact bugs and leave the low-severity noise behind. That's where the real impact (and payout) happens, and you'll stumble across lower severity bugs while you're hunting anyway 💰
bugcrowd
@Bugcrowd
July 6th, it's on! 🪲🔥
Three weeks of virtual testing with @chainguard_dev means plenty of time to find some great bugs, rack up points, and get paid.
Skip the FOMO and request your invite: forms.gle/CGJHYCYr88AnPiG29
We’ll follow up with next steps as spots are confirmed.
 bugcrowd
@Bugcrowd
12 out of 15 top-tier hackers ignore standard security methodologies.
🤯
New research into hacker cognition reveals that elite researchers don’t follow rigid checklists when testing a target. Instead, they rely on fast, intuitive pattern recognition built from years of building, breaking, and tinkering.
Compliance scripts find basic bugs. Human intuition stops catastrophic breaches. ✋🌪️
A checklist can't replicate what a diverse crowd natively possesses. Hackers don't come from a single mold, and that is exactly why they see the blind spots your automated tools miss.
The blog by Andrew shows more data behind how hackers actually make decisions: www.bugcrowd.com/blog/experience-vs-methodology-how-hacke…
bugcrowd
@Bugcrowd
🗓️ Upcoming webinar you don't want to miss!!
The security model was built for a world where discovery took time. That world is getting crowded in the rearview 🚘
Join Bugcrowd CEO @davegerryjr and Dr. @thedavidbrumley for Bugmageddon: When AI Breaks the Security Model.
📹 June 25, 11am ET
Register before this becomes a 2027 budget conversation: event.on24.com/wcc/r/5374864/73CA17ADA2FE4464483D0F4F09ED…
 bugcrowd
@Bugcrowd
AI didn’t make every attacker brilliant.
It made “good enough to be dangerous” easier to reach.
At #infosec2026, @davegerryjr and Dr. @thedavidbrumley unpack how AI is changing attacker capability, why the security model is starting to wobble, and where human ingenuity still wins.
Watch: www.youtube.com/live/9B_m7iyAhn4
bugcrowd
@Bugcrowd
How long should you keep going when you haven't found a bug?
Take these useful tips from @monkehack 👇
bugcrowd
@Bugcrowd
Full video:
www.youtube.com/watch?v=U-vfF7ZdFBg
bugcrowd
@Bugcrowd
We’re not talking about hackers, we’re talking WITH THEM!
Berlin, The Hive Exchange is coming your way 🎊🐝
Join Bugcrowd, @AWS, @GlobalDots, and guest speaker krevetk0 for an afternoon with the people seeing security from both sides of the problem.
Defenders bring the architecture. Hackers bring the alternate route. Together, the room gets a lot harder to surprise.
📍 Berlin
📅 July 2, 2026
🕑 2:00pm–7:00pm CEST
Put your name on the list: luma.com/qke5k7r8
 bugcrowd
@Bugcrowd
What are the advantages of learning HTML & JS? 👌
Listen to @InsiderPhD explain.
bugcrowd
@Bugcrowd
Full video ⬇️
www.youtube.com/watch?v=CpV3XDqzYyE
bugcrowd
@Bugcrowd
📫 Special delivery!
An invite for anyone wondering what AI is quietly doing to the exploit timeline.
Two of our leaders, @davegerryjr and @thedavidbrumley, are talking on Bugmageddon: When AI Breaks the Security Model, a conversation on where AI is speeding up vulnerability discovery, where the current model starts to strain, and what security leaders need to rethink next.
📅 June 25, 2026
🕚 11:00am EDT
Click here to sign up: event.on24.com/wcc/r/5374864/73CA17ADA2FE4464483D0F4F09ED…
 bugcrowd
@Bugcrowd
For a global platform like Just Eat takeaway.com, security visibility has to scale with the business.
Across 16 countries, applications, APIs, payment systems, and services, their attack surface is anything but simple.
With Bugcrowd, Just Eat takeaway.com uses a managed bug bounty program to bring ethical hacker expertise into the fold, uncover valuable insights across their technology estate, and improve the path from report submission to remediation. 🫰
Read more in their spotlight: www.bugcrowd.com/blog/community-spotlight-just-eat-takeaw…
bugcrowd
@Bugcrowd
⏭️ Take a look at your 2027 roadmap.
Where does AI show up? Boardroom? Risk register? Product backlog? Attacker playbook?
🎙️ At SydneySEC 2026, Bugcrowd CEO @davegerryjr will unpack how AI is changing vulnerability discovery, exploit development, and offensive security.
If AI is anywhere on your roadmap, you’ll want to park it here for this session. 🚗
Register: aisasecuritydays.com.au/sydneysec
 bugcrowd
@Bugcrowd
If your hands are full of PoCs, payloads, and half-finished writeups…
Ours are full of Bugcrowd swag for you 🎁🧡
Tag a hacker who’s been working hard lately. We’ll randomly pick two of you to each win a Bugcrowd t-shirt!
bugcrowd
@Bugcrowd
Devs implement some protection.
Can you bypass it? 🤔
Share your payload. 👇
 bugcrowd
@Bugcrowd
Everyone has their own unique bug bounty starting story. 📖
@monkehack shares how he started and how bug bounty helped him land a job!
bugcrowd
@Bugcrowd
Full video:
www.youtube.com/watch?v=U-vfF7ZdFBg
bugcrowd
@Bugcrowd
2 truths and a lie: government VDP edition 👀
1️⃣ Good-faith hackers need a safe way to report vulnerabilities
2️⃣ Launching a VDP during an election year can show proactive leadership
3️⃣ Opening a VDP means your team will be flooded with unmanageable reports
If you guessed #3 as the lie, you're correct.
A managed VDP is built to help reduce noise, not add to it 🫣
With scope, rules of engagement, triage, and deduplication built in, state and local governments can create a clear path for responsible disclosure without overwhelming their teams.
See the 3 full myths: www.bugcrowd.com/blog/3-myths-about-vdps-for-state-and-lo…
bugcrowd
@Bugcrowd
EU security teams shouldn’t have to choose between global security expertise and regional data requirements.
With Bugcrowd’s EU data residency option, organizations can access our global crowd and expert support while keeping PII and vulnerability data in the EU.
🔗
bugcrowd
@Bugcrowd
You shouldn’t settle for alert(1) ❌
But, how do you escalate impact?
@hbenja_m shows how to increase the impact of reflected XSS.
Check it out. 👇
bugcrowd
@Bugcrowd
Full video:
www.youtube.com/watch?v=0C9c-4hWi0Q
bugcrowd
@Bugcrowd
Most security teams have plenty of findings. What they need is confidence in what to fix first.
That’s where a mature bug bounty program starts to look different. Not as another stream of tickets, but as a way to bring trusted hacker insight into the places your team needs more visibility 🤏🥽
Join our live AMA to hear how Trustpilot thinks about program maturity, better hacker engagement, and turning vulnerability discovery into business-ready action.
We’ll talk through how the right program helps teams move from more findings to better decisions.
🗓️ July 1
🕙 10:00am BST
Add it to your calendar: event.on24.com/wcc/r/5376481/75D1C68A9DD9F8FE14C8E88E0F5B…
 bugcrowd
@Bugcrowd
Should you turn your bug bounty hunting into your career?
@monkehack gives a quick insight! 🤓
bugcrowd
@Bugcrowd
Full video:
www.youtube.com/watch?v=U-vfF7ZdFBg
bugcrowd
@Bugcrowd
/search?q=<script>alert(1)</script>
You dropped this payload, nothing happened. 😫
Now what?
Check this quick explainer by @InsiderPhD on what to do after sending your failed XSS payload. 😏
bugcrowd
@Bugcrowd
Full video ⬇️
www.youtube.com/watch?v=CpV3XDqzYyE
bugcrowd
@Bugcrowd
📢 Building a successful bug bounty program requires a strong foundation of trust, clear triage processes, and a commitment to continuous testing.
Moving from annual audits to continuous testing lets you find vulnerabilities as code changes. This creates a predictable workflow where external researchers safely report findings, giving developers the clear data needed to fix bugs faster. A win-win for everyone. 🥇
Read the full interview with our CISO & CIO, Nick McKenzie, at Tech Nadu: www.technadu.com/bug-bounty-programs-trust-triage-and-con…
bugcrowd
@Bugcrowd
When you start bug bounty hunting, it can feel like larger companies will be more secure. You'd be surprised!
bugcrowd
@Bugcrowd
Full video:
www.youtube.com/watch?v=U-vfF7ZdFBg
bugcrowd
@Bugcrowd
Preemptive security starts before the attacker has the advantage.
🎙️ Joe Castellanos, Senior Director of Product Management at Bugcrowd, shares how security teams are moving beyond reactive vulnerability management toward continuous, attacker-informed testing.
From shifting testing left in the SDLC to understanding your external attack surface from the outside in, this is a good watch for teams building a program designed to reduce risk earlier.
Watch the full discussion: event.on24.com/wcc/r/5338391/1CC86150BF85DF61FCA9FAE7D4AD…
bugcrowd
@Bugcrowd
As automation and AI continue to accelerate security operations, the role of security researchers is becoming more critical to defensive strategy 🧑💻‼️
While tools can scan code and surface anomalies at a massive scale, they lack the contextual nuance required to validate complex business logic flaws.
Relying entirely on automated triage often results in a flood of false positives that exhausts internal teams. Integrating a human layer ensures that security operations can quickly separate meaningful exposure from background noise. 🤝
Watch the full video interview with our CTO, Braden Russell, at Tech Nadu: www.technadu.com/external-bug-hunters-are-a-critical-huma…
bugcrowd
@Bugcrowd
Securing 7.5B+ transactions while maintaining strict compliance takes incredible agility. 👌
That’s why Moneytree has anchored its offensive security on Bugcrowd for nearly a decade. The secret to their 10-year ROI is our built-in triage engine.
By ensuring only validated, actionable vulnerabilities reach engineering, they reduce risk without sacrificing shipping velocity.
💸 See how this partnership scales: www.bugcrowd.com/blog/community-spotlight-moneytree/
 bugcrowd
@Bugcrowd
Reflected XSS to stored XSS via cache misconfig flaw.
How? 🤔
@hbenja_m explains.👇
bugcrowd
@Bugcrowd
Full video:
www.youtube.com/watch?v=0C9c-4hWi0Q
bugcrowd
@Bugcrowd
Can you SPOT the bug? 🔎🐞
Share your payloads. 👇
 bugcrowd
@Bugcrowd
📈 In 2024, 60% of state and local governments experienced a cyberattack. Public sector security teams face a 148% malware surge and a 300%+ uptick in endpoint security incidents, alongside strict compliance hurdles. Traditional scanners leave gaps because they only find known bugs.
Automated fuzz testing solves this by testing running software to trigger hidden flaws before threat actors do. It’s a fast, repeatable way to meet federal rules like NIST SP 800-53, NIST SSDF, and ED-203A. ✅
With our FedRAMP Moderate Authorization, agencies can deploy these workflows immediately to uncover 25% more defects.
Read the blog here: www.bugcrowd.com/blog/how-fuzz-testing-can-help-secure-th…
bugcrowd
@Bugcrowd
With AI models proving they can successfully exploit software vulnerabilities, the timeline for defenders to patch systems is shrinking rapidly. ⏳
Finding bugs faster creates an overwhelming amount of noise for security teams unless prioritization is automated.
💬 Our CEO, Dave Gerry, highlighted that companies need to rethink their remediation pipelines to move fixes into near-real-time workflows. The focus must shift from simply gathering tickets to automatically prioritizing and acting on the specific vulnerabilities that actually enable exploits.
Get the full strategy breakdown from Infosecurity Magazine: www.infosecurity-magazine.com/news/mythos-gpt-chrome-expl…
bugcrowd
@Bugcrowd
At #infosec2026, we shared the first findings from ExploitBench, a benchmark we launched with Carnegie Mellon University to measure how AI models handle actual exploits.
📊 The data shows that frontier models are rapidly closing the gap with human researchers. In head-to-head testing on Google Chrome vulnerabilities, Anthropic’s Mythos successfully reached the highest tier of exploitation in 21 out of 41 cases, outperforming OpenAI's GPT-5.5.
Review the benchmark results at Infosecurity Magazine: www.infosecurity-magazine.com/news/mythos-gpt-chrome-expl…
bugcrowd
@Bugcrowd
The incredible @monkehack dropping gold nuggets on modern webapp hacking.
Check it out! 👇
bugcrowd
@Bugcrowd
Full video:
www.youtube.com/watch?v=U-vfF7ZdFBg
bugcrowd reposted
 Dave Gerry
@davegerryjr
Security teams already drown in vulnerability data, but they're missing the context that makes the difference between a triaged backlog and an actual decision.
Today, @Bugcrowd announced Savant - the AI fabric of the Bugcrowd Platform - and with it, the ability to deliver actionable results across appsec, bug bounty and vdp, red-teaming or pentest results in a single platform.
You'll see Savant across many of our current products and future releases:
- Savant Vista (formerly Asset View), helps teams understand what’s exposed.
- Savant Triage (formerly AI Triage Assistant), validates and prioritizes findings faster, cutting through noise so teams focus on what’s real.
- Savant Analytics (formerly AI Analytics), surfaces patterns across program data and supports clearer, more confident reporting.
- Savant Match (formerly CrowdMatch), activates the right hackers and connects them to customers for better results over time.
- Savant Forge (formerly Mayhem Code Security), supports autonomous testing for code.
- Savant Probe (formerly Mayhem API Security), supports live API testing.
- Savant Runtime (formerly Mayhem Dynamic SBOM), adds context from running software.
www.bugcrowd.com/blog/savant-bugcrowds-ai-strategy-for-pr…
bugcrowd
@Bugcrowd
Meet Savant: the AI fabric inside Bugcrowd’s platform 🟧
To the customers who trust us, the hackers who power us, and the partners who help extend our impact, we’re excited to introduce Savant!
Savant brings Bugcrowd’s AI features, autonomous agents, human hacker insights, and platform signals under one umbrella, making it clear where AI is used and how it supports the work happening across our platform. ☂️
Bugcrowd’s preemptive security vision comes to life with Savant, and we’re excited to bring our community along for what’s next. 🚀
Learn more from our CEO, @davegerryjr: www.bugcrowd.com/blog/savant-bugcrowds-ai-strategy-for-pr…
bugcrowd
@Bugcrowd
We just launched an EU data residency option to help organizations manage their evolving data sovereignty and compliance needs. 🌍
This update allows customers to store and process their crowdsourced security data entirely within the European Union.
🔒 As data privacy regulations become more localized, having regional control over vulnerability data helps teams meet strict compliance baselines without sacrificing the scale and speed of global security researchers.
Read the full announcement at @DarkReading: www.darkreading.com/cyber-risk/bugcrowd-launches-eu-data-…
bugcrowd
@Bugcrowd
AI slop and copy-paste reports are clogging triage queues across the industry.
It’s frustrating for everyone, but especially for researchers doing quality work that gets buried in the noise.
We get it. And we’re fixing it with Priority Queue Bypass 📨💨
Researchers with a proven track record of accurate, professional submissions on Bugcrowd can skip the standard line, get faster triage, earn a platform badge, and unlock priority access to private invites.
You prioritize quality over volume. It’s about time the platform prioritized you.
Read more: www.bugcrowd.com/blog/introducing-priority-queue-bypass-a…
bugcrowd
@Bugcrowd
Manual recon is important. 💯
@InsiderPhD outlines how she manually browses through an application to get an idea of how requests are handled.
Check it out. 👇
bugcrowd
@Bugcrowd
Full video:
www.youtube.com/watch?v=kYetdP8K2IA
bugcrowd
@Bugcrowd
CISOs know bug bounties find vulnerabilities. The real questions are operational:
❓ Will low-quality reports overwhelm engineering?
❓ How do we scale without slowing down shipping velocity?
❓ How do we shift to continuous testing smoothly?
Join Alex (Trustpilot), Alistair, and Vas (Bugcrowd) on Wednesday, July 1 at 10:00 AM BST for a live, unfiltered 30-minute AMA on the actual mechanics of a successful program.
Save your spot: event.on24.com/wcc/r/5376481/75D1C68A9DD9F8FE14C8E88E0F5B…
 bugcrowd
@Bugcrowd
Got an XSS with little (to zero) impact? 😩
@hbenja_m shares a practical way to escalate your self-XSS into a stored XSS.
More impact!
Check it out. 👇
bugcrowd
@Bugcrowd
Full video:
www.youtube.com/watch?v=0C9c-4hWi0Q
bugcrowd
@Bugcrowd
What EXACTLY is an IDOR? 🤔
@InsiderPhD gives a digestible explanation.
Check it out. 👇
bugcrowd
@Bugcrowd
Full video:
www.youtube.com/watch?v=kYetdP8K2IA
bugcrowd
@Bugcrowd
That’s a wrap on #infosec2026!
Same time next year? ✈️ 🎊


 bugcrowd
@Bugcrowd
☁️ Cloud-native culture is about speed, learning, and adaptability.
But the faster teams ship, the more important it becomes to continuously test what could break.
Writing for CloudTech, Marc Zottner explores how organizations can build high-performing teams by moving past rigid processes, reducing bottlenecks, and learning faster.
Read more: www.cloudcomputing-news.net/news/how-to-thrive-in-a-cloud…
bugcrowd
@Bugcrowd
Security teams are playing with a shorter clock ⏰🏒
AI is speeding up the path from discovery to exploitation. Bugs are being found faster. Exploits are moving faster. The window to respond is getting smaller.
Bugcrowd recently sponsored Black Hat’s webinar, The Changing Face of Bug Hunting, featuring Trey Ford 🎙️
Watch the full discussion to see why security teams need a faster game plan: webinar.connectmeinforma.com/event/register/zZoN1bEOSag4r…
bugcrowd
@Bugcrowd
My weekend plans in a nutshell: 🐞
 bugcrowd
@Bugcrowd
The 19-year streak of stolen passwords as hackers’ top entry point is over 🙅
‼️ Verizon’s new DBIR reveals software vulnerabilities are now the leading root cause of global breaches.
Bugcrowd’s Trey Ford says AI has compressed the window between published vulnerability and active exploit from months to hours.
See what this means for your risk strategy on The Brew News: thebrewnews.com/thebrew-news/world/software-vulnerabiliti…
bugcrowd
@Bugcrowd
How do bug bounty PROS actually approach a target? 🤔
@monkehack shares his thinking when going in at a fresh target. 🎯
Check it out! 👇
bugcrowd
@Bugcrowd
Full video:
www.youtube.com/watch?v=U-vfF7ZdFBg
bugcrowd
@Bugcrowd
Attackers love an unchecked assumption.
In FinTech’s extended enterprise, every product, partner, and system adds another place trust can fail.
🔔 Test early, validate continuously, and close the gaps before attackers get there.
bugcrowd reposted
 bsysop
@bsysop
Spent the last days hacking at the @Bugcrowd event and had an absolute blast.
Big shoutout to Tatiana and the Bugcrowd team for the amazing event, and all the brilliant hackers for the impressive work. 🤟🏻
#bugbounty

 bugcrowd
@Bugcrowd
For 19 years, stolen credentials were the top way attackers got in.
That streak is over.
🚨 The 2026 Verizon DBIR shows vulnerability exploitation has taken the lead, now accounting for 31% of breach entry points. At the same time, AI is shrinking CVE-to-exploit timelines from months to hours.
This matters because annual testing and quarterly assessments were built for a slower world.
Trey Ford breaks down what this shift means for security teams, third-party risk, shadow AI, and the growing need for continuous adversarial coverage ⤵
www.bugcrowd.com/blog/the-economics-of-exploitation-what-…
bugcrowd reposted
Dave Gerry
@davegerryjr
Well, it’s been an interesting 24 hours to watch this play out and there’s been a lot of conversation about using submission data for training. I want to be very clear on Bugcrowd’s position.
Hackers are and continue to be the heart of @Bugcrowd. We are a part of the community and value the work the researcher community does to help customers identify vulnerabilities.
AI is here to stay and will play a large role in cybersecurity going forward. However, that doesn’t change our commitment to the hacker community.
We’ve been exploring ways to bring hackers along for the journey - not replace them with AI - and have been working in conjunction with members of the community, our own team & our Hacker Advisory Board to figure out the right way to incentivize and monetize AI-driven products for the hackers contributing.
We won’t get everything right, but you have our commitment to be transparent as we strive to get this right and chart a path towards a human+AI future.
bugcrowd
@Bugcrowd
What to LOOK for when hunting for IDORs? 👀
@InsiderPhD shares some solid tips and insight on why you shouldn’t be intimidated by unpredictable IDs.
Check it out. 👇
bugcrowd
@Bugcrowd
Full video:
www.youtube.com/watch?v=kYetdP8K2IA
bugcrowd reposted
 Juan Francisco Bolívar
@JFran_cbit
Thanks to @Bugcrowd and Tatiana for the Live Hacking Event in Germany. Great researchers, great collaboration, and memorable moments with @sw33tLie @bsysop @gr3pme.
 bugcrowd
@Bugcrowd
Day 2 at #infosec2026 was absolute 🔥
THANK YOU to everyone who joined the booth conversations at A76 and came through The Hive. The security world is elite 😎
We heard from @davegerryjr and @thedavidbrumley on Bugmageddon moderated by the one and only Ali Al-Sherbaz (yup, cool.) 👏
But the fun didn’t stop there. Julian and Alistair kept the party going with a discussion around the AI slop era.
P.S. Did you hear? 👀
You can watch the speaker sessions whenever, wherever on our YouTube: www.youtube.com/@Bugcrowd/streams


bugcrowd reposted
bugcrowd
@Bugcrowd
European data stays in Europe. But your security program doesn’t have to stay small 🤌
Bugcrowd’s EU Data Residency Option gives European and EU-focused organizations more control over sensitive vulnerability data and PII, while still giving them access to our global Crowd.
Kevin Kersley breaks down what that means for teams under pressure to meet regional requirements and reduce risk faster.
Read the Q&A: www.bugcrowd.com/blog/bugcrowds-new-data-residency-option…
bugcrowd
@Bugcrowd
If you can’t make it to #thehive, don’t spiral. Sometimes traffic, or coffee, or gets in the way.
Just stream it. Bugcrowd is going live on YouTube for our second speaker session in 1 hour: www.youtube.com/live/TmPsNopd2TA
bugcrowd
@Bugcrowd
Be honest 👀 Are you “on your way,” or are you still looking for your #infosec2026 badge?
Either way, Bugcrowd is going live on YouTube for our first speaker session at #thehive in 1 hour: www.youtube.com/live/9B_m7iyAhn4
bugcrowd
@Bugcrowd
What’s making vulnerability volume everyone’s problem right now?
If you guessed AI, you get a gold star. 🫴⭐️
🚨 Today at 12pm, Julian Brownlow Davies and Alistair G. are talking about how to cut through the AI slop and focus on exploitable risk.
➡️ Steps away from Infosec Europe
➡️ Today, 12:00–12:30pm
See it live at The Hive: luma.com/aislop
 bugcrowd
@Bugcrowd
Today at 11am: AI, exploitability, and a very normal little topic called Bugmageddon. 😉
Join Bugcrowd CEO @davegerryjr and Chief AI & Science Officer Dr. @thedavidbrumley at The Hive for a conversation on what happens when AI starts breaking the security models teams depend on.
➡️ The Hive just steps from Infosec Europe
➡️ Today, 11:00–11:30am
Grab your spot: luma.com/Bugmageddon
 bugcrowd
@Bugcrowd
Eight major telecom giants are putting rivalries aside to form a unified cyber defense.
AT&T, Verizon, T-Mobile, and Comcast are among the heavyweights launching the C2 ISAC for rapid threat intelligence sharing.
Bugcrowd CEO @davegerryjr notes this narrows the gap against collaborative adversaries, while Bugcrowd executive @treyford emphasizes that individual carrier budgets can no longer fight full spectrum threats alone.
Details via Tech News World: www.technewsworld.com/story/telecom-heavyweights-circle-w…
bugcrowd
@Bugcrowd
Okayyyyy #infosec2026, we see your good energy!
Let’s keep it going all week at Booth A76 👏
And when you need a break from the show floor hustle, add The Hive to your step count 👣 🐝
Register here >> www.bugcrowd.com/the-hive/
See you tomorrow! 😍


 bugcrowd
@Bugcrowd
May 28th was apparently National Hamburger Day! 🍔 We errr... missed it. But here are some tasty cyber-hamburger facts.
Last year, the world’s biggest burger chain served up a masterclass in why basic security hygiene matters. 🧵👇
 bugcrowd
@Bugcrowd
The "McFlaw" URL Trick. 🍔🔓
Researcher "BobDaHacker" found that the delivery app only ran client-side checks for credit points, no server-side validation! This meant a "Hamburglar" could essentially order food for free.
By just changing a word in a URL (IDOR), they also gained admin rights to marketing portals and potential corporate email access for some, *ahem*, "filet-o-phishing." 🎣
bugcrowd
@Bugcrowd
Anyway, I'm hungry now, brb 🍔
bugcrowd reposted
Dave Gerry
@davegerryjr
We've heard it from customers across the EU for years: they want access to the @Bugcrowd Platform for the global researcher community, world-class triage capability, & AI-augmented and autonomous testing, but the vulnerability data has to stay in-region.
Previously an EU data residency requirement meant they had to choose other niche local providers which met some, but not all of their needs.
On the heels of our FedRAMP authorization, today, we launched the EU Data Residency Option which runs in @awscloud Frankfurt, generally available July 1.
www.bugcrowd.com/press-release/bugcrowd-expands-platform-…
bugcrowd
@Bugcrowd
EU data residency is coming to Bugcrowd 🥳
Bugcrowd’s new EU Data Residency Option helps European and EU-focused organizations keep sensitive vulnerability data and PII on European soil while still tapping into Bugcrowd’s global Crowd, AI-powered platform, and high-fidelity security results.
Built for teams balancing regional compliance, data sovereignty, and faster risk reduction.
See how regional control meets global reach: www.bugcrowd.com/press-release/bugcrowd-expands-platform-…
bugcrowd
@Bugcrowd
Anthropic is expanding access to Claude Mythos, an AI model previously restricted for its advanced bug hunting capabilities. 🔋
By opening access to vetted security teams, organizations can use its codebase mapping to find and fix vulnerabilities before attackers do.
Read more from ISMG: www.govinfosecurity.com/anthropic-expands-public-access-t…
bugcrowd
@Bugcrowd
Are you a student who wants to be a hacker?
Follow these 3 tips from @hbenja_m to kickstart the journey:
1️⃣ Master the Fundamentals: Don't skip networking (TCP/IP) and Linux basics. You can't break what you don't understand.
2️⃣ Get Hands-On: Build your foundation with labs like TryHackMe or PortSwigger. Practice > Theory.
3️⃣ Engage with the Community: Join Discord servers, follow write-ups on Twitter, and learn from others.
 bugcrowd
@Bugcrowd
Read the full story here 👇
www.bugcrowd.com/blog/my-experience-hacking-as-a-student/
bugcrowd
@Bugcrowd
Threat detection glow-up ✨
Turns out, stress-testing your security with real-world attacks is a pretty good way to make it stronger. Who knew? 😉
By simulating Active Directory attacks in a hosted lab, Netwrix found detection gaps, strengthened protections, and boosted threat detection from 70% to 90%.
Key results:
✅ 100% detection of attacks from user and IT admin accounts
✅ Stronger threat detection and response
✅ Faster product releases with higher quality
Read the case study: www.bugcrowd.com/customers/netwrix/
bugcrowd reposted
 TechNadu
@TechNadu
Security teams are not failing because they cannot detect threats. According to Braden Russell, CTO at @Bugcrowd, the real problem is prioritization failure.
🧑💻 "The LLMs and the AI models that are coming out now are just dumping thousands of vulnerabilities."
🧑💻 Broken access control flaws are exploding as developers ship faster and AI accelerates complexity.
🧑💻 External researchers often spot exploitable weaknesses internal teams normalize over time.
#bugbounty #ai #appsec #cybersecurity #devsecops #threatintel #bugcrowd
bugcrowd
@Bugcrowd
✋ HELLO, LONDON! We've arrived. And yes, the show floor is loud. But the attack surface is louder.
This week at Infosecurity Europe, you can find Bugcrowd in two places:
📍 Booth A76 on the show floor
🍯 The Hive just steps away from the action
Stop by and learn about AI-powered testing, exploitability, and how Bugcrowd helps teams bring together human ingenuity, platform intelligence, and continuous testing to find what matters faster.
Booth A76 and The Hive. That’s your new plan. 😉
Get registered here: luma.com/infosec26reception

 bugcrowd
@Bugcrowd
Will you be safe if you deploy this?
SPOT the bug. 🔎
Share your sneaky payloads. 👇
 bugcrowd
@Bugcrowd
How to go from theory to REAL-WORLD hacking? 🤔
Here’s @monkehack with some practical lessons. 🤓
Check it out! 👇
youtube.com/watch?v=U-vfF7ZdFBg
bugcrowd
@Bugcrowd
Zero Trust gets stuck when strategy can’t keep up with the complexity of modern risk.
With 40% of initiatives stalling and only 20% succeeding, Zero Trust has to be tied to business outcomes, not just technical controls.
The programs that move forward connect security to business outcomes, people, and evidence.
Bugcrowd helps teams turn assumptions into proof by continuously testing the places trust can fail. Applications, identities, exposed assets, third parties, and changing attack surfaces 📍
You don’t know until you test.
bugcrowd
@Bugcrowd
AI is revealing that too many of our fortresses were built on unstable foundations in the first place.
For the public sector, the biggest AI security risk is what more noise exposes:
⛓️💥 Brittle legacy systems
🩹 Unpatched weaknesses
🔓 Insecure defaults
🦺 Poor asset visibility
And compliance programs that look better on paper than they hold up in practice.
Kent Wilson discusses the foundational problem here: www.bugcrowd.com/blog/a-foundation-of-quicksand-how-ai-sl…
bugcrowd
@Bugcrowd
AI can surface more vulnerabilities than ever.
Great. Now what? 🙃
Next week at #infosec2026, Julian Brownlow Davies and Alistair G. are taking on the question every security team drowning in findings needs to ask 🏊⤵
Do most vulnerabilities actually matter?
📍 The Hive near Infosec Europe
🗓 Wednesday, 3 June
⏰ 12:00–12:30pm
Save your spot: luma.com/aislop
 bugcrowd
@Bugcrowd
It’s Friday! Your calendar deserves a lil treat for next week 😌🎁
We’re bringing the big AI security questions to The Hive at #infosec2026:
⚡ When does AI break the security model?
Dave Gerry + Dr. David Brumley
Wednesday, 3 June at 11:00–11:30am
🎫: luma.com/Bugmageddon
🐛 In the age of AI slop, do most vulnerabilities actually matter?
Julian Brownlow Davies + Alistair G.
Wednesday, 3 June at 12:00–12:30pm
🎫: luma.com/aislop
Two sessions, one hive, zero boring conversations!
We’ll see you there 🐝: luma.com/infosec26reception


 bugcrowd
@Bugcrowd
🏃♂️💨
bugcrowd
@Bugcrowd
AI is changing how fast security issues can be discovered, but discovery is only one part of the bug bounty lifecycle.
Teams still need trusted researchers, clear validation, and human judgment to understand what is real risk and what is just more backlog.
Bugcrowd’s @treyford joined Black Hat’s “Changing Face of Bug Hunting” webinar to break down what this shift means for the future of security research.
Watch the clip: webinar.connectmeinforma.com/event/register/zZoN1bEOSag4r…
bugcrowd
@Bugcrowd
AI is moving fast. Security models are moving… well, trying their best 😀
Next week at @Infosecurity Europe, Bugcrowd CEO @davegerryjr and Chief AI & Science Officer Dr. @thedavidbrumley are bringing Bugmageddon: When AI Breaks the Security Model to The Hive.
Join us!
🐝 The Hive near Infosec Europe
🗓 Wednesday, 3 June
⏰ 11:00–11:30am
Register: luma.com/Bugmageddon
 bugcrowd
@Bugcrowd
We just launched Reinforcement Learning Environments to let frontier AI labs train models on real vulnerable software instead of synthetic data.
Built on technology from our Mayhem acquisition, it provides open-source environments where AI agents learn to locate and patch actual production flaws.
Our Chief AI and Science Officer, @thedavidbrumley, explains: "You cannot train a model to be good at security by showing it what security looks like, you have to give it real problems to solve and honest feedback on whether it solved them."
Get the details from @SiliconANGLE: siliconangle.com/2026/05/21/bugcrowd-launches-reinforceme…
bugcrowd
@Bugcrowd
Your calendar has an open slot at 11am ET today? Perfect. 🤩
Join Bugcrowd product leaders in a discussion on moving past vuln overload and focusing on validated risk.
Grab your seat before we go live: event.on24.com/wcc/r/5338391/6F6D2298E5D8365008458C3B8E10…
 bugcrowd
@Bugcrowd
To find valid bugs and stop getting those frustrating N/A triages, you need to understand one concept above all others: impact.
In bug bounties, a bug is only valid if it has real security impact. Most hunters nod along at this but never actually internalise it, and it's why their reports get closed.
Here's the simplest way to think about it. Ask yourself: "If an attacker used this bug, what could they actually achieve?" The answer has to be at least one of these:
- They can view information they shouldn't be able to see
- They can change information they shouldn't be able to change
- They can make the service unavailable or unusable
If you can't prove the attacker achieves one of those, the bug doesn't meet the bar and you shouldn't report it. Full stop.
This is where pentesting and bug bounties part ways. In a pentest you'd also flag potential issues and general hygiene findings: cookie flags, SSL/TLS weaknesses, missing security headers, verbose error messages, and so on. None of those have direct impact, but they're worth knowing about and usually worth fixing anyway. A bounty program will just close them as informational.
So before you hit submit, run the test: confidentiality, integrity, or availability. If you can't point to one of the three, you don't have a bug yet.
 bugcrowd
@Bugcrowd
Reminder: Go to bed, bugs can wait. 😴 #bugbounty
 bugcrowd
@Bugcrowd
Reflecting on major infrastructure disruptions reminds the industry that widespread tech reliance creates deep concentration risks.
When a single software update can disrupt transportation, healthcare, and banking globally, resilience has to be designed into systems from the beginning.
Our CEO, @davegerryjr, pointed out that practices like staged rollouts, reliable kill switches, and rigorous pre-deployment testing must become baseline requirements for software running with deep system privileges.
Explore the review at @DarkReading: www.darkreading.com/cyber-risk/broken-dreams-2-decades-cy…
bugcrowd
@Bugcrowd
Better AI outcomes start with better security evidence 🗂️
When signals from code, cloud, assets, and production stay disconnected, teams are left with more findings to interpret. When those signals are validated and connected, AI can help reason over what is exploitable and worth acting on.
Bugcrowd product leaders Justin and Joe will break this down tomorrow!
Sign up ASAP: www.linkedin.com/events/7460349997432176640?viewAsMember=…
 bugcrowd
@Bugcrowd
Frontier AI teams are leveling up their models with Bugcrowd’s new Reinforcement Learning environments. By interacting with real software, AI learns to find, exploit, and patch vulnerabilities through practice.
But AI can’t do it alone. True security still relies on human expertise to build the advanced frameworks and reward structures that teach models how to solve real-world problems.
Our Chief AI and Science Officer, @thedavidbrumley, shares more.
bugcrowd
@Bugcrowd
Now that you don’t need any convincing, we can’t wait to see you there.
Register for The Hive happening June 3 at #infosec2026: luma.com/infosec26reception

 bugcrowd
@Bugcrowd
A recent vulnerability in PraisonAI was actively scanned by attackers within four hours of its public disclosure, proving how fast the threat window closes ⌛️
The flaw stemmed from a common oversight: authentication was disabled by default in a development-grade API server.
Our Chief Strategy and Trust Officer, @treyford, warned that organizations fast-tracking AI agent adoption without auditing network bindings and credential exposures are taking on unquantified risk.
Review the vulnerability breakdown at @CSOonline: www.csoonline.com/article/4171215/praisonai-vulnerability…
bugcrowd
@Bugcrowd
Reflected XSS vs Self-XSS: What's the difference? 🤔
Here’s @InsiderPhD explaining how they work, attack scenarios, and impact.👇
bugcrowd
@Bugcrowd
Our Chief AI and Science Officer, @thedavidbrumley, is asking security researchers to look past the next bug.
Inspired by Richard Hamming, his latest blog explores how great researchers notice when the important problems are changing.
Bug finding may become the plumbing. The real opportunity is what gets built on top of it.
Read more: www.bugcrowd.com/blog/hammings-question-and-the-future-of…
bugcrowd
@Bugcrowd
Introducing ExploitBench, the first benchmark built to measure how AI models move from crashing a vulnerability to exploiting it and gaining full control.
ExploitBench was created to bring clearer data to a growing debate around AI’s role in vulnerability exploitation.
Developed through a collaboration between Bugcrowd Chief AI and Science Officer @thedavidbrumley and Seunghyun Lee, a leading Chrome V8 vulnerability researcher, the benchmark reflects the environments, graders, and reward structures Bugcrowd has spent years building, strengthened by the acquisition of Mayhem Security.
David explains the announcement in depth here: www.bugcrowd.com/blog/ai-benchmarking-report-measuring-th…
bugcrowd
@Bugcrowd
Gadgets: Turning harmless bugs into P1s
Gadgets are low-impact bugs like open redirects or client-side quirks, that seem harmless alone. But when you chain these pieces (Prototype Pollution, cookie injections, etc.), you can build a high-impact exploit that crushes a hardened target.
Let’s learn.
🧵👇
 bugcrowd
@Bugcrowd
Don’t settle for P5s 📉
Open redirects, postMessage misconfigurations, or cookie injections don't do much solo. The trick is always showing impact through a gadget chain. A single low-severity bug is often just the entry point for a critical exploit.
bugcrowd
@Bugcrowd
Tools you need
➡️ DOM Invader (Burp) – traces sources and sinks, finds PP gadgets.
➡️ DOMLogger++ – browser extension for monitoring postMessage traffic.
bugcrowd
@Bugcrowd
Final tips 💰
Don’t report gadgets in isolation. Aim for the full chain:
✅ Open redirect → SSRF → Internal service hit
✅ Cookie injection → Cache poison → Stored XSS
Demonstrate impact end-to-end. Your next big bounty is likely hiding behind a "harmless" P5.
Bag them now! 💸
bugcrowd
@Bugcrowd
Does this look solid to you?
SPOT the bug.🐞
Share your best payloads. 👇
 bugcrowd
@Bugcrowd
If you’re a rookie hunter, your best game plan would be just to navigate your target app like a regular user.
Say your target is a banking webapp.
Instead of immediately running recon scripts, use the app like a normal user: create a real account, complete a full transaction, and note every API call. You’ll discover endpoints and parameters that automated spidering misses.
➡️ Record the entire flow with a proxy tool running in the background.
➡️ Note which parameters are incremental (userId, orderId).
➡️ Change IDs, replay requests in a different sequence, skip steps.
There are a ton of things you can do in every scenario.
Fire up your creativity engine, execute your weird ideas, they might just work (who knows). 🔥
bugcrowd
@Bugcrowd
Some of the best researchers in the world spent their week breaking things so the rest of us don’t have to. 👏
That’s Bug Bash. That’s the Bugcrowd community. And that’s exactly why T-Mobile US and Telstra invited them in.
Thank you to every researcher who made the trip to Australia and brought their best. The people relying on these networks every day are safer because you showed up.
See you at the next one? 😏


 bugcrowd
@Bugcrowd
Inside this box is everything for my favorite activity.


bugcrowd reposted
Dave Gerry
@davegerryjr
Most AI security training stops at detection. That’s pattern matching, not skill.
We just launched RL Environments at @Bugcrowd.
Hundreds of thousands of real open-source vulnerabilities. Find, exploit, patch, audit. The full loop.
Frontier labs are already training on them.
bugcrowd
@Bugcrowd
A customer service inbox isn't a vulnerability disclosure program 🙅♀️🙅
That might sound obvious, until security reports start showing up in places where no one knows who owns them or what to do with them.
Verified Bugcrowd users shared how a structured VDP helps bring order to the process, with:
🔥 Clearer intake
👏 Expert triage
🧽 Cleaner handoffs
💯 Reports teams can move on faster
Read why companies choose Bugcrowd for VDP: www.bugcrowd.com/blog/what-verified-users-say-about-runni…
bugcrowd
@Bugcrowd
Why is reading JavaScript key to finding your FIRST bug (XSS)? 🤔
Here’s @InsiderPhD explaining the significance of reading JavaScript in your bug bounty hunting.
Full video ⬇️
Analysing the DOM to find Reflected XSS
bugcrowd
@Bugcrowd
Today, Bugcrowd is launching Reinforcement Learning environments.
Built for AI developers and supported by our acquisition of Mayhem Security, this new offering gives LLM providers and frontier AI research teams instant access to enterprise-grade infrastructure for model training and optimization.
That means teams can spend less time building platform infrastructure and more time advancing model capability.
All environments are derived exclusively from open-source software. No customer data or security researcher data is used at any stage of the training process.
We’re excited to share what we’ve built and help AI teams move faster with infrastructure designed for this work.
Read the full announcement: www.bugcrowd.com/press-release/bugcrowd-launches-reinforc…

bugcrowd reposted
𝖁𝖆𝖘𝖎𝖑𝖊𝖎𝖔𝖘
@marketingrckstr
Wheels down 🛬 @Bugcrowd #edinburgh #hacker Roadshow babyyyy! 🏴 with @monkehack Let's DO this 👏🏼
 bugcrowd
@Bugcrowd
What vulnerabilities should we fix first? A simple question with a messy answer
AI is helping teams find more issues faster. Now comes the harder part. Deciding which findings are likely to create risk and which ones are just making the queue look dramatic.
Join Julian Brownlow Davies and Alistair G. at The Hive at @Infosecurity Europe for a rapid-fire session on prioritization through an offensive lens 🔎
📅 Wednesday, 3 June
⏰ 12:00–12:30pm
Your remediation queue deserves it: luma.com/aislop
 bugcrowd
@Bugcrowd
Verizon DBIR 2026 found that exploiting software vulnerabilities has overtaken stolen credentials as the top initial access method for the first time in the report’s 19-year history.
For security teams, that changes things.
As Trey Ford, Bugcrowd’s Chief Strategy and Trust Officer, shared with Hackread, this is “not primarily a credential story; it is an economics story.”
When flaws can be researched and weaponized in hours, annual testing isn't enough. Security teams need a more continuous way to validate what matters before attackers get there first.
Read the full article: hackread.com/verizon-dbir-ai-hackers-exploit-vulnerabilit…
bugcrowd
@Bugcrowd
If you’ve ever wanted to pull up a chair with leaders from the Bugcrowd product team, this is your chance (byoc) 💺🪑
On May 28, Justin Kestelyn and Joe Castellanos are breaking down what continuous exposure assessment and validation means for modern security teams.
Register here ⤵
www.linkedin.com/events/7460349997432176640?viewAsMember=…
 bugcrowd
@Bugcrowd
Quick bug bounty TIPS!
➡️ verified=false → true, “true”, "True", "TRUE", 1, "1", “yes”
➡️ /v3/users/1234 → v1, v0, internal, beta, legacy
➡️ quantity=100 → -1, 0, 9999999999, 1.82376931348623157e+308
➡️ role=”user” → “admin”, “”, null, “system”
➡️ /admin → /Admin, /ADMIN, /aDmIn
Try them now! ✅
Do you have something to add? 👇
 bugcrowd
@Bugcrowd
Bug bounty program growing pains?
We can talk about them 🎙️
Featuring:
😎 Ali Abdollahi, Canon EMEA
😎 Matthias Held, Bugcrowd
😎 Vas Kosapanos, Bugcrowd
Today at 10:00am BST 🗓️
Register >> www.linkedin.com/events/7459534008104779776?viewAsMember=…
 bugcrowd
@Bugcrowd
“AI is going to help with a lot of things but we’re never going to replace that human creativity.”
Bugcrowd CEO @davegerryjr spoke with the @FinancialTimes about the rise of AI-generated bug bounty submissions and what it means for the future of security research.
AI can speed up discovery, but security teams still need trusted researchers to turn findings into real risk reduction.
Keep reading: www.ft.com/content/dbec4441-02dc-4053-8500-85677973d324?s…
bugcrowd
@Bugcrowd
When testing a GraphQL target, verifying array batching is one of the first checks. ☑️
Here’s a quick process:
➡️ Intercept a single query.
{"query": "{ user { id } }"}
➡️ Wrap the JSON object in an array and duplicate the query.
[{"query": "{ user { id } }"}, {"query": "{ user { id } }"}]
➡️ If the server returns a JSON array of responses:
[{"data":...}, {"data":...}]
Batch execution is supported.
Now, target high-value mutations like login, submit2FA, passwordReset, or query heavy nested objects to cause an application-level Denial of Service (DoS).
Here’s how you format the brute-force payload for a login mutation. You can easily script this to generate a massive array of credentials:
[
{"query": "mutation { login(username: \"admin\", password: \"admin123\") { token } }"},
{"query": "mutation { login(username: \"admin\", password: \"password1\") { token } }"},
{"query": "mutation { login(username: \"admin\", password: \"qwerty\") { token } }"}
]
Hack GraphQL and catch some P1s. 😎
bugcrowd
@Bugcrowd
If you're seeing this you should join us on Reddit.
reddit.com/r/Bugcrowd
bugcrowd
@Bugcrowd
A louder inbox? No thank you ✋
Everyone is talking about what AI tools like Mythos can find. We need answers to what happens next.
A vulnerability finding doesn’t walk itself into a board meeting and explain business risk. It doesn’t know whether it’s urgent, duplicate, exploitable, or one of 400 things sitting in a very loud inbox.
More discovery creates more responsibility.
Our CEO, @davegerryjr, explains how Bugcrowd helps turn AI acceleration into validated, prioritized action with real people: www.bugcrowd.com/blog/the-role-of-mythos-and-ai-models-in…
bugcrowd
@Bugcrowd
Please remain calm, Bugmageddon has entered the chat 📳
AI is making vulnerability discovery faster, cheaper, and more accessible. Great news for defenders. Great news for attackers. A little chaotic for everyone trying to keep remediation queues under control.
📍🐝 At The Hive at @Infosecurity Europe, Bugcrowd CEO @davegerryjr and Chief AI & Science Officer Dr. @thedavidbrumley will discuss what happens when AI starts moving faster than the security model was built to handle.
Is “Bugmageddon” inevitable? Come find out.
Your finance team can relax, it’s free: luma.com/Bugmageddon
 bugcrowd
@Bugcrowd
Bug bounty hunters are putting AI to work.
Researchers told @WSJ they’re using AI to support everything from recon to analysis and exploitation, with a growing focus on fewer, higher-value findings.
But as Bugcrowd CEO @davegerryjr shared, human insight still plays a critical role in finding deeper, novel vulnerabilities, including “things that people have never seen before.”
Read the full piece: www.wsj.com/pro/cybersecurity/mythos-rewires-the-bug-boun…
bugcrowd
@Bugcrowd
Hacking tip 😎
Don't assume that something is secure just because the feature exists.
We saw a bug recently where an application had custom auth. The user entered their password, if it was correct they had to enter a 6 digit code that was sent to their email address. The endpoint had throttling enabled.
Most hackers would stop there. This one didn't! They worked out that the password step could be skipped completely, and then they worked out that the throttling on the 2FA endpoint was throttled by IP.
They found a full ATO on any account by rotating their IP address on every request and simply brute forcing the 6 digit code.
If you're a hacker, don't assume anything!
bugcrowd
@Bugcrowd
“Rarely do you get to work with hackers, looking closely over their shoulder.”
@Netwrix did exactly that with Bugcrowd 🔥
Through AWS, they brought in ethical hackers to simulate attacks, test product protections, and uncover what traditional validation can miss.
The result? We’ll give you a hint: stronger. 💪
See for yourself in the case study: www.bugcrowd.com/customers/netwrix/
bugcrowd
@Bugcrowd
Good research takes work. It takes validation, clear reproduction steps, and enough context for teams to understand the real impact.
That work shouldn't get buried under speculative submissions or reports that cannot stand up to scrutiny.
Bugcrowd is introducing additional safeguards for Managed Bug Bounty programs to help protect signal quality and keep triage focused on validated findings.
The standard stays the same. Show the impact and make the report useful.
Read the blog to stay updated: www.bugcrowd.com/blog/continuing-our-work-to-reduce-ai-sl…
bugcrowd
@Bugcrowd
Your post-Gartner plans just got cleared for landing ✈️
Join Bugcrowd’s Kent Wilson and team for Tacos & Tailwinds, an evening of tacos, drinks, Potomac views, and plane spotting at Rosa Mexicano in National Harbor.
We’ll also be on hand to talk through Bugcrowd’s FedRAMP Moderate authorization and what it means for agencies looking to bring crowdsourced security into their mission with more confidence.
🗓️ Monday, June 1
⏰ 5:00–7:00pm EDT
🌮 Register here: luma.com/bugcrowdatgartner
 bugcrowd
@Bugcrowd
bugcrowd
@Bugcrowd
Tip of the day:
When you're hacking with AI, it pays to know when deterministic tooling is better than AI.
A good rule of thumb is this:
AI = fuzzy inputs and outputs
Deterministic tools = clear inputs and outputs
For example:
Want a list of subdomains? Use a deterministic tool like subfinder or amass.
Want to "check the list of subdomains to see if any of the hostnames look interesting"? use AI.
The real magic happens when you combine them.
bugcrowd
@Bugcrowd
POV just before you locked in
 bugcrowd
@Bugcrowd
Some vulnerabilities only show up when a real person understands the business logic, chains together signals, and thinks like an attacker.
In our webinar with Schibsted, Gabriel explains why bug bounty programs are a critical layer for finding the deeper exploits automated tools can miss.
Keep up the great work, hackers 👏
Watch the full clip: www.bugcrowd.com/webinar/
bugcrowd
@Bugcrowd
Copy Fail stands out because it stems from a logic flaw in the Linux kernel’s crypto API, making exploit reliability less dependent on timing or distribution-specific behavior.
Bugcrowd researchers told WIRED the same script can work across distributions, making remediation a priority. See what else they had to say: www.wired.com/story/dangerous-new-linux-exploit-gives-att…
bugcrowd
@Bugcrowd
A 9-year-old Linux flaw is drawing urgent attention after researchers confirmed exploitability at scale. 🌎
Bugcrowd’s @thedavidbrumley told @Forbes the issue highlights how routine system functions can create critical weaknesses when mishandled across widely used systems.
The latest on this: www.forbes.com/sites/daveywinder/2026/05/03/update-linux-…
bugcrowd
@Bugcrowd
Don't be this guy
 bugcrowd
@Bugcrowd
AI has made one thing clear ⤵
The future of cybersecurity needs better questions, not louder predictions ✏️
Bugcrowd’s Dr. @thedavidbrumley will speak at SVCC 2026 on June 11 at 8:30am.
Register to attend: www.svcc-svcsi.org
 bugcrowd
@Bugcrowd
Friendly reminder: validate the bugs that AI is finding for you *before* submitting them. 😅
bugcrowd
@Bugcrowd
Preemptive security is becoming a federal priority.
The challenge is execution.
Our latest blog looks at how the Cyber Strategy for America is reframing public sector cybersecurity in the age of AI, and why agencies need scalable ways to identify and remediate critical vulnerabilities faster.
Read our perspective on what it will take to close the gap: www.bugcrowd.com/blog/how-the-federal-government-is-rethi…
bugcrowd
@Bugcrowd
Copy Fail has been added to CISA’s Known Exploited Vulnerabilities catalog. 📙
Bugcrowd’s @thedavidbrumley told @SCMagazine teams should treat this as a “patch right now” situation given the reliability and reach of the public exploit.
🚨 Learn what's at stake:
bugcrowd
@Bugcrowd
Pen testing outcomes depend on what happens after findings are delivered. 📩
In Dark Reading, Bugcrowd’s Trey Ford shared why executive ownership, remediation timelines, and validation are critical to getting more value from security testing.
Dig into the coverage:
bugcrowd
@Bugcrowd
🇬🇧 @Infosecurity Europe plans?
👀 A quick look at our lineup:
🍯 11:00–11:30am
Bugmageddon: When AI Breaks the Security Model
Speakers: Dave Gerry and Dr. David Brumley
Register: luma.com/Bugmageddon
🍯 12:00–12:30pm
The AI Slop Era: Do Most Vulnerabilities Actually Matter?
Speakers: Julian Brownlow Davies and Alistair G.
Register: luma.com/aislop
And yes, you can still find us on the floor.
Come say hey to the Bugcrowd team at booth A76, then swing by The Hive!
Get on the guest list: luma.com/infosec26reception

 bugcrowd
@Bugcrowd
Our ins and outs 🚮
In: exposure anticipation
Out: bug chasing
Security teams need a better way to validate exploitability, reduce backlog chaos, and focus remediation where it counts.
Join leaders from our product team on May 28 as they walk through three integrated layers used by leading security organizations: event.on24.com/wcc/r/5338391/6F6D2298E5D8365008458C3B8E10…
 bugcrowd
@Bugcrowd
The SaaS companies shaping the digital economy are also carrying some of its most important security responsibilities.
Protecting customer data, keeping services available, and staying ahead of emerging risk takes more than static testing. 😅
Learn how Bugcrowd helps SaaS teams solve these challenges: www.bugcrowd.com/blog/five-challenges-to-security-for-saa…
bugcrowd
@Bugcrowd
Can you bypass and run the id command?
There is no validation on user-supplied base64 data which is troublesome.
Try to spot the Bug 🐞👇
 bugcrowd
@Bugcrowd
A top 10 track. 🐐
bugcrowd reposted
 Katie Paxton-Fear
@InsiderPhD
I 100% credit my mum in my tech journey, she an artist and a practical doer person, she taught me how to think outside the box, how to solve problems and the importance of determination and getting back up 💪
bugcrowd
@Bugcrowd
🦾❤️ #bugbounty
 bugcrowd
@Bugcrowd
The Hive is landing at Infosecurity Europe 🐝
After a buzzy day of loud chatter and badge scans, security leaders deserve a place to step away from the floor and chat without the pressure.
We’ll bring the snacks and drinks. You bring the talk and good vibes.
📍 Next stop: the debrief.
Register here: www.bugcrowd.com/the-hive/
 bugcrowd
@Bugcrowd
🦾❤️ #bugbounty
bugcrowd
@Bugcrowd
Looking for a place where you can share bug bounty stories or ask questions?
There's a subreddit for that: r/Bugcrowd
Join the Crowd! 🧡
www.reddit.com/r/Bugcrowd/
 bugcrowd
@Bugcrowd
Social engineering has become operational infrastructure.
Security Boulevard covered industrial-scale scam operations targeting Americans, with Bugcrowd’s Trey Ford explaining why defenders need to look beyond awareness training 🔍
The real test is whether your controls hold up before money moves: securityboulevard.com/2026/05/china-has-its-sights-set-on…
bugcrowd
@Bugcrowd
Attack surfaces keep growing and growing and growing. Your snake plant could learn a thing or two. 🪴
Security teams are being asked to validate more often, prioritize better, and prove value in business terms.
Which leads us to… resilience.
For CISOs, resilience starts with visibility, validation, and evidence to show what’s working, where risk is shrinking, and where more support is needed.
Get the practical takeaways: www.bugcrowd.com/blog/the-cisos-challenge-measuring-secur…
 bugcrowd
@Bugcrowd
Argument parsing is really important, especially when they are used as inputs to other functions or commands.
Spot the Bug 🐞👇
 bugcrowd
@Bugcrowd
“Present since 2017” 🐞🚨
HackRead covered Copy Fail, a Linux kernel flaw that can let a regular user gain root access by exploiting an issue in the cryptographic subsystem’s algif_aead module.
For security teams, this is a patching priority and a reminder.
The bugs that matter aren't always new. Sometimes they are old, reliable, and sitting inside assumptions no one has revisited: hackread.com/linux-kernel-vulnerability-copy-fail-full-ro…
bugcrowd
@Bugcrowd
AI tools are already part of everyday work, approved or not. 🤷
Developers are using ChatGPT, Claude, Gemini, Copilot, and other tools to write code, troubleshoot, summarize, and move faster.
But when every team picks its own AI stack, security leaders are left asking questions like, where is sensitive data going? 🫣
The teams getting this right are starting with visibility 👇
📋 What tools are being used?
📋 What data is being shared?
📋 Which workflows need guardrails?
📋 Where does human review still matter?
bugcrowd reposted
 c4ng4c3ir0
@c4ng4c3ir0
Mês passado terminei em 3° no ranking da @Bugcrowd, saudades de ter disposição pra caçar como nos velhos tempos 😭
 bugcrowd
@Bugcrowd
We went fishing for compliments. 🎣
And verified G2 reviewers had plenty to say.
One theme kept showing up: Bugcrowd helps teams uncover vulnerabilities they may have missed otherwise.
That’s what happens when security testing includes human creativity, validated findings, and programs built around real workflows.
Read more ⭐⭐⭐⭐⭐ reviews: www.bugcrowd.com/blog/why-companies-choose-bugcrowd-for-m…
bugcrowd
@Bugcrowd
Hunt for Admin Panels across all subdomains.
Here’s a one-liner for you to try. 👇
 bugcrowd
@Bugcrowd
hello, nostalgia
bugcrowd
@Bugcrowd
⏰ 30s to find a bug
1️⃣ You can only send a single HTTP request
👇 What’s your payload?
 bugcrowd
@Bugcrowd
By testing their platform against diverse attack scenarios, @Netwrix achieved a perfect 100% detection rate against standard user and admin account threats. 🔒
With Bugcrowd they shipped faster, safer, and with total confidence.
More in the full video → www.youtube.com/watch?v=DkqmfqYjOos
bugcrowd
@Bugcrowd
Agentic AI may change how SOCs triage, investigate, and respond, but faster workflows still need human judgment 👨🔧 👋
CSO Magazine covered how teams can prepare, with Bugcrowd founder @caseyjohnellis noting that SOC roles will adapt ↙️
“Jobs won’t disappear, they’ll adapt. The key is ensuring that SOC professionals are prepared for this shift through ongoing education, training, and tooling.”
Read more: www.csoonline.com/article/4140208/4-ways-to-prepare-your-…
bugcrowd
@Bugcrowd
Schibsted has seen a lot of change since 1839. 🕰️
In our latest AMA, Gabriel Berrios shares how he approaches application security, red teaming, and cybersecurity operations at one of the Nordics’ most established media houses.
Read the recap: www.bugcrowd.com/blog/customer-ama-webinar-recap-schibsted/
Watch the full webinar 🍿: www.bugcrowd.com/webinar/
bugcrowd
@Bugcrowd
Bug bounty life. 😎
 bugcrowd
@Bugcrowd
Logging in is quieter than breaking in. That's the problem.
manufacturing.net covered new threat intelligence showing stolen credential marketplace listings up 72% and identity-based attacks becoming leading entry points for cloud intrusions.
When attackers use valid credentials, the perimeter doesn't look broken. The activity can look normal, the access can look approved, and the risk moves inside the trust model ⚠️
Here's where validation matters: www.manufacturing.net/cybersecurity/article/22965614/stol…
bugcrowd
@Bugcrowd
Is this code really that bad?
Share your payload(s). 👇
 bugcrowd
@Bugcrowd
David Brumley, Chief AI & Science Officer at Bugcrowd, told GovInfoSecurity 💭👇
“Don’t be fooled by the ‘high’, not critical, CVSS score. If your stack runs untrusted code and the isolation story has the word ‘container’ in it without the word ‘microVM,’ ‘gVisor,’ or ‘dedicated host’ right after it, Copy Fail is in your threat model.”
⛔ Don’t assume Linux containers running untrusted code are still safe.
Learn more: www.govinfosecurity.com/linux-copy-fail-flaw-delivers-roo…
bugcrowd reposted
 Maryland Applied Graduate Engineering
@MAGEUMD
National title? ✔️
International title? ✔️
Securing state infrastructure? ✔️
Meet the "RandomHackers," the @MAGEUMD team dominating the #cybersecurity circuit. From @Bugcrowd brackets to global leaderboards, these Terps are unstoppable.
Read more: mage.umd.edu/news/story/terp-tech-warriors-how-ldquorando…

bugcrowd reposted
 Kanhaiya Sharma
@krishnsec
Crossed 14K reputation on @Bugcrowd✅
 bugcrowd
@Bugcrowd
A long time ago, in a shell far, far away… 🌌
A red teamer decided it was time to prove they were ready.
CrowdForce is Bugcrowd’s elite red team, and we’re looking for hackers with the skills to execute the greatest attack simulations, adapt under pressure, and collaborate with some of the smartest minds in offensive security.
Think you’re ready? 🦸
May the force be with you. Learn how to join CrowdForce: www.bugcrowd.com/blog/how-to-join-our-red-team-crowdforce/
bugcrowd
@Bugcrowd
The value of Shodan in bug bounty is often overlooked, if you haven't already you should check it out - especially the advanced operators.
Here's a blog with some quick tips 👇
www.bugcrowd.com/blog/shodan-the-search-engine-for-hackers/
 bugcrowd
@Bugcrowd
Asked the dev to lock this down. Is it secure?
Reply with your answer👇
 bugcrowd
@Bugcrowd
When the new program notifications start hitting the inbox on a Friday afternoon. 🍽️
 bugcrowd
@Bugcrowd
Don't forget to be curious ‼️
Satyam’s spending this year going deeper into hardware, wi-fi, iot, and web3 security while continuing to build, research, and teach along the way.
He’s also looking to work with other hackers on meaningful security projects, sooooo who wants to collab? 👀
Read our latest hacker spotlight: www.bugcrowd.com/blog/hacker-spotlight-meet-satyam-pathania/
 bugcrowd
@Bugcrowd
staying in scope
bugcrowd
@Bugcrowd
Bugcrowd Chief AI and Science Officer @thedavidbrumley is heading to Carnegie Mellon University on Monday for the Agentic AI Evaluation and Governance Workshop.
📌 Hosted by CMU, the Brookings Institution, and UC Berkeley, the workshop brings together leaders working through big AI questions.
Learn more here: mailchi.mp/ce6db5ee926a/save-the-date-may-4th-agentic-ai-…
bugcrowd
@Bugcrowd
The Coast Guard’s new cybersecurity rules for maritime facilities have some universal lessons for every industry.
Trey Ford mentions that these rules get one big thing right: they assume failure. Instead of just trying to keep people out, the focus is on segmentation and secure design so you can spot an adversary before they act. It is a leading indicator for what we can expect to see in other regulated sectors soon.
🔗 Read the full piece in @DarkReading: www.darkreading.com/cybersecurity-operations/coast-guards…
bugcrowd
@Bugcrowd
NIST is changing how they prioritize CVEs in the National Vulnerability Database after a huge surge in submissions.
They are moving to a model that prioritizes vulnerabilities already being exploited in the wild or those affecting critical software. This marks a shift for defenders who used to rely on one complete database for everything. 🖊️
Now, the move is to focus on known exploited vulnerabilities instead of trying to chase every single CVE.
Get the details in Security Magazine: www.securitymagazine.com/articles/102255-nists-new-priori…
bugcrowd
@Bugcrowd
If you want hackers to hunt on your program, make the scope worth hunting.
Broad and clear beats restrictive and confusing every time 🙌
Learn more about how to build a successful program hackers want to hunt on in the full clip: www.bugcrowd.com/webinar/?commid=664468&bt_tok={{lead.id}}&utm_source=x
bugcrowd
@Bugcrowd
Want to win some Bugcrowd stickers?
1️⃣ Join our Reddit: www.reddit.com/r/Bugcrowd/
2️⃣ Reply to this post with an emoji!
The winner will be randomly selected. Good luck!🐞

 bugcrowd
@Bugcrowd
Copy Fail puts a few uncomfortable questions on the table ⤵️
🤔 How much of your isolation story depends on shared-kernel containers?
🤔 How quickly can your team validate a credible exploit?
🤔 Is your disclosure intake ready for more reports that look real, and some that actually are?
CVE-2026-31431 is a Linux kernel LPE affecting major distributions since 2017. A public exploit is already available, and according to Theori (theori.io), AI surfaced the bug in about an hour of scan time.
@thedavidbrumley, our Chief AI & Science Officer, breaks down the bug, the container impact, and why the way it was found is important to know: www.bugcrowd.com/blog/what-we-know-about-copy-fail-cve-20…
bugcrowd
@Bugcrowd
You can’t scan your way out of every startup security risk.
✋ not when teams are moving fast
✋ not when shadow IT creeps in
✋ not when old test environments are still hanging around
✋ not when AI speeds up code and risk at the same time
Startups need coverage that’s as flexible as they are.
This breaks down where automated tools miss the mark and what to do instead: www.bugcrowd.com/blog/how-automated-tools-fall-short-for-…
bugcrowd
@Bugcrowd
The headlines are full of the rivalry between AI giants like Anthropic and OpenAI, but...
There's a bigger conversation happening in security 💬
Trey Ford notes that the bottleneck for most companies isn’t the AI models.
🚧 The hurdle is the human coordination needed to fix the volume of bugs these models are helping find.
For security leaders, focusing on frontier model access might be the wrong priority when the struggle is simply keeping up with remediation.
Check out the analysis in @CRN: www.crn.com/news/security/2026/anthropic-openai-race-obsc…
bugcrowd
@Bugcrowd
How to CRUSH bug bounties in the first 12 months!
The most viewed video on our YouTube channel is a LevelUp talk that @hakluke did on this topic 5 years ago, and it's still relevant!
www.youtube.com/watch?v=AbebbJ3cRLI
bugcrowd
@Bugcrowd
Successful bug bounty programs are usually built on the basics done well 👌
When program teams take the time to explain decisions, stay consistent, and build trust with researchers, the whole program gets stronger.
What’s the biggest thing you look for before hunting on a program? 🎯
Watch the full discussion: www.bugcrowd.com/webinar/

 bugcrowd
@Bugcrowd
Knowing the VRT helps you to submit better bugs. It's a good general guideline for the types of bugs that are typically accepted on programs, and their estimated severity level.
Join @codingo_ and @InsiderPhD to learn more!
www.youtube.com/watch?v=LAyG8dySuMw
bugcrowd
@Bugcrowd
The latest data on Microsoft vulnerabilities shows a 6% drop in total bugs, but the critical flaws have doubled. 📊
Risk is concentrating in the cloud and Office suite, where Azure and Dynamics 365 saw a massive jump in severe findings. With AI speeding up how fast exploits are developed, patching is becoming a much tighter race.
🔎 The focus for teams is shifting away from total bug counts and toward the specific pathways attackers use to move through a network.
Read the breakdown at @SecureWorld: www.secureworld.io/industry-news/microsoft-vulnerabilitie…
bugcrowd
@Bugcrowd
Attackers are currently exploiting a command injection flaw in DVRs to build out a new Mirai-based botnet.
The catch here is that automated scans only tell part of the story. Our Chief Strategy and Trust Officer, @treyford, points out that machine analysis identifies the flaw, but human insight is what explains how an adversary will chain it together to keep access long after the initial alert.
🔔 It’s a good reminder that seeing a bug and understanding the risk are two different things.
The full report is over at Infosecurity Magazine: www.infosecurity-magazine.com/news/mirai-variant-dvr-flaw…
bugcrowd
@Bugcrowd
Everyone says their favorite part about working at Bugcrowd is the people, the culture, the mission...
Interesting.
Pretty sure it’s actually being in these videos. 😜
bugcrowd
@Bugcrowd
A red team is only as strong as its ability to think like the threats you’re actually up against.
Bugcrowd’s RTaaS brings crowdsourced specialization to your unique attack surface, helping uncover deeper weaknesses and validate defenses beyond static testing.
If you’re evaluating red team solutions, this breaks down the pros, cons, and where red teaming delivers the most value: www.bugcrowd.com/blog/the-pros-and-cons-of-red-teaming/
bugcrowd
@Bugcrowd
😮
 TESS
@ArmanSameer95
I earned $94,000 for my submission on @bugcrowd bugcrowd.com/h/{id: "tess"} #ittakesacrowd
bugcrowd reposted
bugcrowd
@Bugcrowd
8 minutes after submitting a P4
 bugcrowd
@Bugcrowd
Is it late where you are? Get some sleep! The bugs will still be there tomorrow.
 bugcrowd
@Bugcrowd
You SSH into your new VPS for the first time. What's your first command?
bugcrowd
@Bugcrowd
🗄️ File name: hackers
Preview available 📂
Our Inside the Mind of a Hacker report explores what thousands of hackers shared about who they are, how they work, and what drives them. Nearly 50% say hacking helped them land a job, proving these skills go far beyond the screen 👀
 bugcrowd
@Bugcrowd
 bugcrowd
@Bugcrowd
Don’t rely on outdated assumptions. Get a fresher view: www.bugcrowd.com/resources/report/inside-the-mind-of-a-ha…
bugcrowd
@Bugcrowd
Without Bugcrowd
( -_- )っ☕
/|\
/ \
With Bugcrowd
( ˶^◡^˶ )っ☕
/|\
/ \
bugcrowd
@Bugcrowd
Bugcrowd and @Carahsoft are partnering to bring crowd-powered security to the public sector. This collaboration makes it easier for government agencies to access our global network of researchers. 🌎
By working together, we are helping organizations stay ahead of threats through proactive, scalable security solutions. 🫸💥🫷
Learn about our new partnership and its impact: intelligencecommunitynews.com/bugcrowd-and-carahsoft-part…
bugcrowd
@Bugcrowd
Popping alert(1) doesn't show REAL impact.
Escalate your XSS by stealing cookies instead👇
Better XSS escalation paths here: www.bugcrowd.com/blog/the-ultimate-guide-to-finding-and-e…
bugcrowd reposted
𝖁𝖆𝖘𝖎𝖑𝖊𝖎𝖔𝖘
@marketingrckstr
Great event @Bugcrowd
 bugcrowd
@Bugcrowd
Well well well, look what day it is 😍
Tonight, GeoCyclone is hosting The Modern Hacker in London, where Bugcrowd CEO @davegerryjr will be sharing what we learned from surveying 2,000 hackers and what those insights mean for security teams trying to keep up with AI, bug bounties, and a rapidly shifting threat landscape.
Free to attend for a topic that could not be more relevant right now. ⏰
🎟️ Registration: luma.com/qmh8uc6e
👨🏻🎓 Student registration: luma.com/ywldg9kk
 bugcrowd
@Bugcrowd
📰 NIST is adjusting how it handles CVE entries as the number of submissions continues to grow.
This shift highlights the need for new ways to manage vulnerability data at scale. As traditional databases face these surges, the focus is moving toward more efficient, automated methods to keep up with the volume of new threats. 🎧
See how the CVE process is changing to meet modern demand: therecord.media/nist-to-limit-work-on-cve-entries-surge
bugcrowd
@Bugcrowd
When they ask what vibes we bring to the function:
bugcrowd reposted
 R4CK4TT&CK
@R4CK4TT4CK
The last Breakfast, but time to get on with life 🦆😓😢
Quick meeting with my local Canva consultant 🤣 then heading into London for a super secret super special Hacker lunch, which I'm even more excited about than tonights @Bugcrowd session with their CEO 😉😎🔥✌️
 bugcrowd
@Bugcrowd
We’ve spent years optimizing for more content, faster output, and lower friction.
🚨 Sloptimism is a reminder that not every system benefits from that. In environments where truth still depends on human verification, speed without proof creates drag, not progress.
That’s what security, open source, academia, and law are all starting to confront now.
@thedavidbrumley, Bugcrowd’s Chief AI and Science Officer, puts language to a problem a lot of teams are already feeling: www.bugcrowd.com/blog/sloptimism-is-breaking-any-system-b…
bugcrowd
@Bugcrowd
Well well well, look what day it is 😍
Tonight, GeoCyclone is hosting The Modern Hacker in London, where Bugcrowd CEO @davegerryjr will be sharing what we learned from surveying 2,000 hackers and what those insights mean for security teams trying to keep up with AI, bug bounties, and a rapidly shifting threat landscape.
Free to attend for a topic that could not be more relevant right now. ⏰
🎟️ Registration: luma.com/qmh8uc6e
👨🏻🎓 Student registration: luma.com/ywldg9kk
bugcrowd
@Bugcrowd
Cybersecurity defense has reached a new stage with the launch of OpenAI’s GPT-5.4-Cyber. 👩🏻🔧
While this model helps strengthen defenses, the challenge is adding these tools to your security stack without creating gaps. We are monitoring how these advancements help teams meet more sophisticated threats. 🕷️
Explore the implications of the latest GPT model here: informationsecuritybuzz.com/openai-expands-cybersecurity-…
 bugcrowd
@Bugcrowd
Customers and hackers in the Bugcrowd platform
 bugcrowd
@Bugcrowd
TFW you locked into a target and it paid off.
 bugcrowd
@Bugcrowd
not your average ctf
bugcrowd
@Bugcrowd
Big shout out to
🥇@codecancare
🥈@mertistaken
🥉Chuck Norris
 bugcrowd
@Bugcrowd
Centralizing vulnerability triage is difficult at current volumes. 🔊
The NIST CVE framework update confirms that priority should come from how a threat functions in practice, not just database notes.
🗯️ Bugcrowd’s @treyford notes that future programs will rely on continuous signals from researchers with sharp instincts rather than slow update cycles.
Tap into what drives remediation: www.darkreading.com/vulnerabilities-threats/nist-revamps-…
bugcrowd
@Bugcrowd
The difference between a good find and a frustrating outcome? Usually this 👇
 bugcrowd
@Bugcrowd
3. Read triage comments carefully
If you disagree with an outcome, lead with clarity instead of friction. The most productive follow-ups explain the risk in a way that helps triage and the customer understand what is actually at stake.
bugcrowd
@Bugcrowd
Check out the full blog to learn more: www.bugcrowd.com/blog/three-common-hacker-mistakes-to-avoid/
bugcrowd
@Bugcrowd
The path for new cybersecurity professionals is evolving. AI now manages repetitive tasks like log scanning, which allows teams to focus on deeper analysis.
Bugcrowd CEO @davegerryjr spoke with the Wall Street Journal about how this shift lets experts use AI to cover more ground. Instead of manual data entry, the modern professional moves quickly into high-level strategy and oversight.
Read more on how AI is elevating the human role in security: www.wsj.com/pro/cybersecurity/entry-level-cyber-workers-a…
 bugcrowd
@Bugcrowd
With trillions moving through it every day, financial services is a major target for attackers. 💲
When financial organizations are attacked, businesses and individuals lose access to critical financial services.
The average breach costs $6 million and can lead to lost trust, added scrutiny, fines, and audits. 💔
Crowdsourced security helps teams bring in specialized expertise on demand, extend internal resources, and support compliance.
A solid next click, honestly: www.bugcrowd.com/blog/5-tips-to-succeed-with-offensive-se…
bugcrowd
@Bugcrowd
Me receiving a bounty for the bug that an AI agent found while I was asleep.
 bugcrowd
@Bugcrowd
Not all bug bounty programs grow into something truly valuable.
🏅 The ones that do usually get a few things right: clear expectations, smart scaling, strong researcher relationships, and a real connection to security outcomes.
On April 23 at 10am BST, Schibsted and Bugcrowd are talking about how!
🎙️ Gabriel Berrios, Matthias Held, and Vas Kospanos
Register here: www.bugcrowd.com/webinar/?commid=664468&bt_tok={{lead.id}}&utm_source=x
 bugcrowd
@Bugcrowd
JWT verification looks solid...
But there's a $10k bug hiding here 💰
Can you spot it? 👀
 bugcrowd
@Bugcrowd
This bug has been popping up more and more in real-world apps.
Can you spot it? 🐞
 bugcrowd
@Bugcrowd
It's been a busy few weeks for the industry. 🗓️
We saw everything from AI exploitation windows to the rise of invisible AI agents. Keeping up with the pace of change is half the battle in modern security! 🏃
Here's some of the most important news and analysis to help you stay ahead of the curve. Grab a coffee and get caught up before the weekend starts.
Read the Daily CyberTech Highlights from last week: cybertechnologyinsights.com/daily-roundup/daily-cybertech…
bugcrowd
@Bugcrowd
Let’s test your 💎 Rails knowledge
@user.update(params.require(:user).permit(:name, :bio, :is_admin))
What’s the bug?
A) Insecure Direct Object Reference
B) Mass assignment leading to privilege escalation
C) Server Side Request Forgery
D) Cross Site Request Forgery
Bonus: Which parameter should never be user-controlled here? 😈
bugcrowd
@Bugcrowd
👋 London, this one’s for the cyber and geopolitics crowd.
On April 23, Bugcrowd CEO @davegerryjr joins GeoCyclone to unpack insights from 2,000+ hackers, from motivations and demographics to how AI is changing offensive security.
A few spots are still open:
🎟️ General admission: luma.com/qmh8uc6e
👨🏻🎓 Student registration: luma.com/ywldg9kk
 bugcrowd
@Bugcrowd
Something that can turn every user into admin 💀
Can you find it?
Bonus: Drop you payload? 👇
 bugcrowd
@Bugcrowd
Ransomware groups are pivoting. As big companies harden their defenses, attackers are moving downstream to target smaller businesses using stolen logins. 📉
Valid credentials provide the path of least resistance to slip past traditional security. If you aren't focused on credential hygiene, you are the next target on their list. 🔑🚪
Explore the shift in ransomware economics: www.securityweek.com/stolen-logins-are-fueling-everything…
bugcrowd reposted
 Satyam Pathania
@satyam72565815
Thanks for the spotlight @Bugcrowd , This is just the start, more to come gg
bugcrowd
@Bugcrowd
Before the talks, the projects, and the growing security community, there was a teenager with a tiny CPU and a lot of curiosity.
In our latest Hacker Spotlight, meet Satyam Pathania, a self-taught researcher, builder, and teacher who believes the best way to learn is to break things, fix them, and share the process honestly 👏
💡 Tip: consistency beats shortcuts every time. Read more: www.bugcrowd.com/blog/hacker-spotlight-meet-satyam-pathania/
bugcrowd
@Bugcrowd
Before the talks, the projects, and the growing security community, there was a teenager with a tiny CPU and a lot of curiosity.
In our latest Hacker Spotlight, meet Satyam Pathania, a self-taught researcher, builder, and teacher who believes the best way to learn is to break things, fix them, and share the process honestly 👏
💡 Tip: consistency beats shortcuts every time. Read more: www.bugcrowd.com/blog/hacker-spotlight-meet-satyam-pathania/
bugcrowd
@Bugcrowd
A haystack isn't a problem. Not knowing where the needle is? 🤷🏻♂️
That's the problem. See how our customers solve it: www.bugcrowd.com/customers/
 bugcrowd
@Bugcrowd
The gap between a bug announcement and exploitation is now less than a day. 🐛⏳
With LangFlow, attackers reverse-engineered an exploit in just 20 hours without any public code. If your patch cycle takes weeks, you are structurally exposed.
As Bugcrowd’s SVP Julian points out, the challenge is no longer just finding the bug. You have to know which ones hit your crown jewels before the clock runs out. ⏰
Read more: www.scworld.com/news/critical-langflow-ai-bug-exploited-w…
bugcrowd
@Bugcrowd
SecLists is a security tester’s best companion.
From usernames and passwords to URLs, payloads, web shells, and sensitive data patterns, it covers almost every recon need.
Use SecLists in your workflow to automate more and find more bugs. 🐞
 bugcrowd
@Bugcrowd
What can we say? Guilty as charged.
bugcrowd
@Bugcrowd
Your team is likely deploying AI agents to handle tasks across your SaaS apps and APIs. The problem is that most security teams have no idea these agents even exist. 🤷
They operate with broad permissions but lack the oversight we give to human identities.
When you can’t see an agent, you can’t secure it. We need to start treating AI as a monitored identity. Before you scale your automation, make sure your visibility can keep up. 👀
Check out why AI agents are becoming the new shadow IT: securityboulevard.com/2026/04/ai-agents-whos-there-what-a…
bugcrowd
@Bugcrowd
Let’s check your database knowledge.
query = "SELECT * FROM users WHERE id = " + userId
Replace string concatenation with ________ to prevent SQLi
A) query = f"SELECT * FROM users WHERE id = {userId}"
B) query = "SELECT * FROM users WHERE id = " + escape(userId)
C) cursor.execute("SELECT * FROM users WHERE id = %s", (userId,))
D) query = "SELECT * FROM users WHERE id = " + str(int(userId))
Bonus: Why are the others still injectable?
bugcrowd
@Bugcrowd
📢 April 16 at 11am ET: www.bugcrowd.com/webinar/?commid=663767&bt_tok={{lead.id}}&utm_source=x&utm_medium=organic_social
Join Bugcrowd, CISA VDP, and public sector security leaders for a Q&A on the impact of FedRAMP Moderate authorization.
Hear from Kent Wilson, Trey Ford, and Shondalyn Smith on what this means for vulnerability disclosure, operational rigor, and proactive security across government and beyond. 🎙️🔥
bugcrowd
@Bugcrowd
The average cost of a breach for financial institutions is $6 million 💸
Crowdsourced security helps financial services organizations bring in specialized expertise on demand, extend internal teams, and support compliance efforts through solutions like bug bounty, penetration testing, and vulnerability disclosure programs.
☝️ In fact, 96% of ethical hackers agree these programs help fill cybersecurity skills gaps.
We’re letting you in on a few secrets in this blog: www.bugcrowd.com/blog/5-tips-to-succeed-with-offensive-se…
bugcrowd
@Bugcrowd
The security world spent a decade obsessed with finding bugs faster. We succeeded, but now we have a massive bottleneck at the finish line. 🏁
AI finds vulnerabilities in seconds, but a human still has to ship the patch. When a maintainer is buried under 40 reports on a Friday, speed of discovery feels like noise.
As Bugcrowd's Trey Ford notes, we optimized the wrong end of the pipe. It is time to value the fix as much as the find. 💯
Read the full analysis: www.darkreading.com/application-security/ai-led-remediati…
 bugcrowd
@Bugcrowd
Broken Object Property Level Authorization (BOPLA) occurs when APIs fail to properly restrict access to specific properties within an object.
Think of it as IDOR, but targeted at individual properties rather than the entire object.
👇🧵
 bugcrowd
@Bugcrowd
✅Mass Assignment example:
POST /api/host/approve_booking
{
"approved": true
}
If an attacker modifies the request to include:
{
"approved": true,
"total_stay_price": "$1"
}
and the API accepts it, business logic can be abused.
bugcrowd
@Bugcrowd
✅Another example:
A platform restricts content using a parameter like:
{
"blocked": true
}
If a user modifies it to:
{
"blocked": false
}
and gains access, property-level authorization is broken.
bugcrowd
@Bugcrowd
👉Test for mass assignment:
- Add unexpected fields in requests
- Modify existing parameters
- Observe changes in behavior
For example, you could add the following field when updating your user profile:
{
"isAdmin": true
}
bugcrowd
@Bugcrowd
Save this for later🔖
What's your take?👇
bugcrowd
@Bugcrowd
When VulnCon winds down, come hang with us! 🤙
We’re bringing the Bugcrowd community to The Canal Club for patio vibes, drinks, bites, and conversations that just might be the highlight of your trip.
We’ll see you tomorrow, April 14, at 6:30pm!
🔗 Register here:
bugcrowd
@Bugcrowd
AI agents are increasingly being used by some users to create a huge volume of low-quality, unverified submissions. We call this “sloptimism,” overly optimistic submissions driving large volumes of speculative or AI-generated reports.
 bugcrowd
@Bugcrowd
Check out this blog to learn how we fixed this👇
www.bugcrowd.com/blog/bugcrowd-policy-changes-to-address-…
bugcrowd
@Bugcrowd
Sure, you 𝙘𝙤𝙪𝙡𝙙 read the whole 50-page Inside the Mind of a Hacker report.
But if hearing the top insights live from Bugcrowd CEO Dave Gerry, while also getting networking and drinks, sounds better... this is your sign 😎
Join us at the GeoCyclone event in London on April 23: luma.com/qmh8uc6e
 bugcrowd
@Bugcrowd
Offensive testing is the theme
Hackers search for bugs upstream
A preemptive approach
The attacker’s reproach
Extends the reach of your security team.
🎤 🫳 🥵
And on that note, happy Friday! If you're into poems, we have plenty: www.bugcrowd.com/blog/10-cybersecurity-poems-for-world-po…
bugcrowd
@Bugcrowd
Broken Object Level Authorization (BOLA) is one of the most critical API vulnerabilities, and it consistently ranks at the top of OWASP API risks.
Occurs when API fails to verify whether a user has permission to access a specific object.
 bugcrowd
@Bugcrowd
Even if IDs are non-sequentials (UUIDs), BOLA can still exist.
Attackers often extract ID from:
- API responses
- Logs
- Public Endpoints
and reuse them across endpoints
bugcrowd
@Bugcrowd
Conclusion:
Authorisation must always be enforced server-side per object.
Obscurity like UUIDs or frontend controls aren't enough.
bugcrowd
@Bugcrowd
The unspoken problem with AI risk:
Security leaders are evaluating AI in black-and-white terms. But AI does not work that way and most tools are not built for the gray areas where real risk shows up.
That leaves teams stuck between slowing AI down or accepting risk they do not fully understand.
Read the full guide on securing AI with confidence: www.bugcrowd.com/blog/ai-security-risks-what-teams-need-t…
bugcrowd reposted
 Tur.js
@Tur24Tur
I just earned $9,000 from a single @Bugcrowd target.
2x P2 Broken Access Control on a 7-year-old public program.
To anyone hunting for bugs don't skip old programs. The surface changes, APIs get updated, new endpoints get deployed Fresh bugs appear on old targets all the time.
#bugbounty #infosec #bugcrowd
 bugcrowd
@Bugcrowd
At this point next week, you've sat through enough presentations. 😌
Come network with the Bugcrowd community at The Canal Club after Vulncon.
Patio, bites, drinks, and people worth meeting! How could you say no?
🗓️ April 14
⏰ 6:30–8:30pm
Register today:
bugcrowd
@Bugcrowd
Quick recon tip for finding potential SSRF targets 🔎
One-liner security header check 👇

bugcrowd reposted
Kanhaiya Sharma
@krishnsec
Last month ranked #1 on the @Bugcrowd leaderboard in 🇮🇳
 bugcrowd
@Bugcrowd
Government agencies saw a 40% spike in targeted attacks last year. Vulnerability submissions to government programs surged 151%. 🚨
The demand for security researcher partnership is growing, and so is the value it delivers.
With Bugcrowd's FedRAMP Moderate Authorization, these three case studies hit different:
📑 CISA VDP
📑 Department of Defense CDAO
📑 Office of the Minnesota Secretary of State
Dive into each here: www.bugcrowd.com/blog/elevating-public-sector-security-in…
bugcrowd
@Bugcrowd
Can any of these actually stop Path Traversal? 🤔
A) filepath = "/uploads/" + filename.replace("../", "")
B) filepath = "/uploads/" + os.path.basename(filename)
C) filepath = "/uploads/" + filename.replace("..", "")
D) if ".." not in filename: return send_file(filepath)
Bonus: Can you bypass them all? 😈
bugcrowd
@Bugcrowd
More access. More coverage. Less reactive security.
Bugcrowd is now partnering with @Carahsoft to expand access to our FedRAMP Moderate authorized platform across federal, state, and local government. 🙌
Through Carahsoft's trusted Government distribution network, public sector teams can access Bugcrowd's leading offensive security capabilities through:
• NASA SEWP V
• OMNIA Partners
• E&I Cooperative Services contracts
• Carahsoft reseller partners
From bug bounty to VDP, pen testing, and red teaming, this partnership helps agencies take a more proactive approach to finding and remediating risk.
See the full announcement to learn what this opens up: www.bugcrowd.com/press-release/bugcrowd-and-carahsoft-par…
bugcrowd reposted
 Carahsoft
@Carahsoft
We have partnered with @Bugcrowd to expand crowdsourced security solutions across the Public Sector. Through our reseller network and key contract vehicles, agencies can access Bugcrowd’s FedRAMP Moderate authorized platform to proactively identify and remediate vulnerabilities:
 bugcrowd
@Bugcrowd
If these questions keep landing in your Slack:
💬 Is our program mature enough?
💬 Are we getting the right value?
💬 What do hackers actually want from us?
💬 How do strong programs scale without getting messy?
Schibsted and Bugcrowd are covering it live on April 23 at 10am BST with Gabriel Berrios, Matthias Held, and Vas Kospanos. 🎙️
Register before someone drops “quick question” in chat again: www.bugcrowd.com/webinar/?%2Bcommid=664468&bt_tok={{lead.ld}&utm_campaign=webinar&utm_source=x&utm_medium=organic_social&utm_content=1775638080
 bugcrowd
@Bugcrowd
You don't make cyber feel more accessible with buzzwords. You do it with people like Tati! 🤩
We’re proud to celebrate Tatiana Uklist for representing Bugcrowd at the UTS Cyber Security Society (CSEC) Women in Cyber Career Panel and sharing a perspective students could genuinely connect with.
Tati brought the kind of honesty and clarity that makes these conversations matter.
Big thanks to UTS Cyber Security Society for hosting such a strong event and to everyone involved in making it happen. 👏


 bugcrowd
@Bugcrowd
Financial services isn’t short on pressure. If you’re in it, you know that.
Security teams are managing a moving attack surface while also answering to regulators, auditors, and the business.
Continuous penetration testing helps close that gap. It gives teams ongoing insight into vulnerabilities, helps prioritize real risk, and supports a stronger compliance story over time. 💪
Explore a testing model built for financial services and built for change. See how crowdsourced security is evolving: www.bugcrowd.com/blog/the-benefits-of-continuous-pen-test…
bugcrowd
@Bugcrowd
As one of Bugcrowd's longest-running customers in Japan, Moneytree has built a program that filters the noise, rewards the right researchers, and keeps their dev team focused on building, not firefighting. 🧱
Nine years in, they're still finding value. And that says something. Read about their journey and why they keep choosing Bugcrowd: www.bugcrowd.com/blog/community-spotlight-moneytree/
 bugcrowd
@Bugcrowd
What's the bug here? How would you exploit it?
 bugcrowd
@Bugcrowd
Strict standards and real security can coexist!
If you work in government security, you’re probably balancing two realities at once: the need to move faster, and the need to meet stricter standards than ever.
Move too slowly? Risk grows.
Move without trust? Nothing moves at all.
It shouldn't have to be one or the other.
Join us on April 16 at 11am ET for a conversation on what Bugcrowd’s FedRAMP Moderate Authorization means for federal agencies and beyond.
Because security standards and access to skilled researchers should work together.
💌 Register: www.bugcrowd.com/webinar/?commid=663767&bt_tok={{lead.id}}&utm_source=x&utm_medium=organic_social
 bugcrowd
@Bugcrowd
Turn your Nmap scan into a clean report in seconds ⚡
1️⃣ Scan with XML output
2️⃣ Convert it to a readable report
Simple flow:
nmap -> xml -> xsltproc -> html
Perfect for documenting recon during bug bounty hunts.
bugcrowd
@Bugcrowd
It looks safe, but is it really? 👀
Can you figure out how this SSRF filter breaks?
Bonus: Drop the payload 👇
 bugcrowd
@Bugcrowd
Your RSVP would look great here 📍
If you’re a CISO, student, government employee, security researcher, or you're finding your way into the industry. ⤵
Join Dr Craig Jarvis' GeoCyclone event on April 23 for The Modern Hacker, featuring Bugcrowd CEO @davegerryjr sharing insights from our latest research based on responses from 2,000+ hackers.
🤝 Bring a friend and sign up here: luma.com/qmh8uc6e
Can't wait! ✈️ 🏴
 bugcrowd
@Bugcrowd
🎖️ Consider this a highly relevant result.
This spring brought 15 new G2 badges for Bugcrowd, including Leader in 3 categories! 👇
We couldn’t do it without the hacker ingenuity powering our platform, the customers who trust us daily, and the partners who help move our mission forward.
On to bigger things with the community that makes it happen. 💫
 bugcrowd
@Bugcrowd

bugcrowd reposted
 Mackenzie Jackson -
@advocatemack
👉 Casey Ellis created @Bugcrowd to legitimize hackers through bug bounty.
𝗡𝗼𝘄 𝗔𝗜 𝗶𝘀 𝗽𝘂𝘁𝘁𝗶𝗻𝗴 𝗿𝗲𝗮𝗹 𝗽𝗿𝗲𝘀𝘀𝘂𝗿𝗲 𝗼𝗻 𝘁𝗵𝗮𝘁 𝗺𝗼𝗱𝗲𝗹.
So… is bug bounty dead?
(Spoiler: no, but it is changing)
This episode actually came from a previous episode.
I spoke with Daniel Stenberg about shutting down the cURL bug bounty program, mainly due to the flood of AI-generated reports they couldn't keep up with.
That raised a bigger question for me:
👉 If this is happening at cURL… what does the future of bug bounty actually look like?
So I wanted the perspective from someone who helped build the space. And for some unknown reason, Casey agreed.
A few things Casey said that stood out:
⚫ Every company already has a vulnerability disclosure program (whether they realise it or not)
⚫ Not every company should run a public bug bounty
⚫ AI isn’t creating a new problem.... it’s massively accelerating an old one
⚫ The real bottleneck is triage, not finding vulnerabilities
⚫ Incentives need to shift (we shouldn’t be rewarding low-quality, automated findings)
The best line of the episode....
“We’re doing stupid things faster with more energy.”
A fascinating episode, really looking forward to the discussion this brings about.
Full episode in comments 👇 available anywhere you get your podcast fix.
bugcrowd
@Bugcrowd
Production is hardened, but staging often isn’t.
Use this one-liner to discover dev and staging environments.

bugcrowd reposted
 SC Media
@SCMagazine
#ai at #rsac2026 shows two paths: smarter defense at scale — or faster, more dangerous attacks, says @Bugcrowd's Braden Russell in this op-ed. The gap between optimism and risk is narrowing fast. #cybersecurity #ciso #infosec #itsecurity www.scworld.com/perspective/rsac-2026-takes-a-sober-look-…
bugcrowd
@Bugcrowd
April Fools is all fun and games until your coworkers dig up what you posted in 2010 😭
A little reminder that what you post on the internet can stick around forever and come back when you least expect it.
Sometimes as a prank. Sometimes as something worse.
bugcrowd
@Bugcrowd
What’s going on here?
Spot the bug. 🐞
 bugcrowd
@Bugcrowd
Bugcrowd recently achieved FedRAMP® Moderate Authorization, showing that strict government security standards and access to the global security research community are fully compatible. 🤝
Join Kent Wilson, VP of Public Sector at Bugcrowd, Trey Ford, Chief Strategy and Trust Officer at Bugcrowd, and Shondalyn Smith from CISA’s VDP for a live Q&A on what this milestone means for federal agencies and beyond. ✨
Date: April 16, 2026
Time: 11am ET
Register >> www.bugcrowd.com/webinar/?commid=663767&bt_tok={{lead.id}}&utm_source=x&utm_medium=organic_social
 bugcrowd
@Bugcrowd
AI is raising the ceiling for defenders and lowering the barrier for attackers at the exact same time.
In his latest SC Media Perspectives piece, Bugcrowd CTO Braden Russell unpacks the biggest AI-driven threat shifts emerging in cyber and why collaboration, transparency, and human creativity will be critical to what comes next. 🚀
Read here: www.scworld.com/perspective/rsac-2026-takes-a-sober-look-…
bugcrowd
@Bugcrowd
We know that feeling 😔
 bugcrowd
@Bugcrowd
State of Maryland CISO James Saunders recognized Abhijeet Kumar (UMD) and Price Kokeh (Stevenson University) at Billington’s State and Local Summit following their roundtable with Steve Kain from MD DoIT alongside our own Johnny Curran III and Roland Hansen!
This is the kind of moment that doesn't always land in the spotlight, but makes a real difference for the community and the industry.
The pipeline from campus to the security community is alive and well 👏


 bugcrowd
@Bugcrowd
This code snippet was prevalent in legacy Node.js applications.
What kind of bug does it bring?
Share your payloads 👇
 bugcrowd
@Bugcrowd
Devs implemented a filter, but is it enough?
Drop your bypass. 👇
 bugcrowd
@Bugcrowd
Common tampering techniques that you should TRY
quantity: 1 ➡️ quantity: -2
isVerified: False ➡️ isVerified: True (or true, TRUE, 1)
GET ➡️ POST, PUT, UPDATE, DELETE, OPTIONS
string ➡️ SUUUUUPEERLOOOONGSTRINGGGGG
Do you have some other tricks? 👇
bugcrowd
@Bugcrowd
The new U.S. National Cyber Strategy is seven pages with big implications 👇
Offensive operations, deregulation of compliance burdens, and AI-driven public-private collaboration at the core of national cyber defense.
The speed gap between human defenders and machine speed adversaries is the defining problem. Closing it requires proactive vulnerability discovery and continuous testing, not annual assessments.
Cyber Technology Insights breaks down what it means for security programs: cybertechnologyinsights.com/ai-security/americas-2026-cyb…
bugcrowd
@Bugcrowd
$1,000,000 in bug bounties came down to one decision:
pick a program and stick with it 👨💻😮💨
HX007, a hacker in the Bugcrowd community, made over $750K on a single program. Not by knowing more than everyone else. By knowing one target better than anyone else.
🔖 The longer you work a program, the more you understand the dev team behind it. Their patterns, their blind spots, the bugs they keep missing. It stops feeling like hunting and starts feeling like collaboration.
When nothing's clicking, HX007 switches to a VDP, racks up some P1s, and comes back with his confidence rebuilt. 💡
More advice from HX007 and why he hunts on Bugcrowd: www.bugcrowd.com/blog/how-i-hacked-my-way-to-a-million-do…

bugcrowd reposted
 XavSecOps
@XavSecOps
Donuts, cyber gems, and elite energy. What a week!
bugcrowd
@Bugcrowd
WE 🧡 THE HIVE
Turns out, creating a quieter space for the right people leads to some pretty great connections and conversations. Here are a few of our favorite highlights from the week:
✨ Each of you who stopped by
✨ Donuts
✨ Braden Russell, Dominique DeVaux Jeffords, George Gerchow, nick terkay, and Deap U. on the mic, chatting about the gaps in your attack surface and how to close them
✨ Trey Ford, Jaye Tillson, and Pranav Vattaparambil speaking about fintech attack surface risk
✨ Kristina Ayanian, Dave Gerry, Ramin Farassat, John Spiegel, and Umesh Shankar discussing AI and cyber insecurity
✨ Our amazing sponsors Hewlett Packard Enterprise, Menlo Security Inc., Unosecur, Amazon Web Services (AWS)
✨ Celebrating together on Wednesday evening
✨ Did we mention donuts?
And of course, we couldn’t do it without the dream team and every Bugcrowder who helped from home! 👏
Global energy. One Bugcrowd community!
That's all... for now ✈️✌️
bugcrowd reposted
𝖁𝖆𝖘𝖎𝖑𝖊𝖎𝖔𝖘
@marketingrckstr
CANNOT freaking wait to host this!
bugcrowd
@Bugcrowd
A hacker finds a vulnerability in your system.
In one version of this story, you find out when it's too late. In another, you find out first, because you invited them in. 📒
Gabriel B. built that second version at Schibsted. Matthias Held has been on the other side of it. They're joining Vasileios Kospanos to talk about what it takes to run a bug bounty program that works: scaling it, sustaining it, and using it to stay ahead.
🎟️ Register for the insights coming your way on April 23 at 10am BST: www.bugcrowd.com/webinar/? commid=664468&bt_tok={{lead.ld}
 bugcrowd
@Bugcrowd
A hacker finds a vulnerability in your system.
In one version of this story, you find out when it's too late. In another, you find out first, because you invited them in. 📒
Gabriel B. built that second version at Schibsted. Matthias Held has been on the other side of it. They're joining Vasileios Kospanos to talk about what it takes to run a bug bounty program that works: scaling it, sustaining it, and using it to stay ahead.
🎟️ Register for the insights coming your way on April 23 at 10am BST: www.bugcrowd.com/webinar/? commid=664468&bt_tok={{lead.ld}
bugcrowd
@Bugcrowd
📡 BROADCASTING TO THE CROWD
@OpenAI's safety bug bounty just went public on Bugcrowd!
Now's your time: bugcrowd.com/engagements/openai-safety

bugcrowd reposted
 Evan Kirstel #B2B #TechFluencer
@EvanKirstel
Third party trust in FinTech is one of the biggest attack surfaces nobody talks about enough. Great panel from @Bugcrowd at The Hive at #rsac
bugcrowd
@Bugcrowd
📢 Trust is critical 📢
This afternoon at coolest spot at #rsac aka The Hive, Trey Ford, Pranav Vattaparambil, and Jaye Tillson talked on how that trust creates exploitable conditions across the extended enterprise in FinTech.
Thank you to our speakers for an incredibly candid conversation, and to everyone who joined us in the room for being part of it. 🎉🎸
One more session tomorrow at 10:30am if you want in. Complete your registration ASAP: www.bugcrowd.com/the-hive/


 bugcrowd
@Bugcrowd
This is a classic mistake. Did you SPOT it? 🐞👀
Drop your answers below👇
 bugcrowd
@Bugcrowd
You wouldn't walk into the gym without a plan and expect results. 🤷🏻♂️
AI adoption works the same way!
In Q3 2025, companies planned to invest an average of $130 million in AI. By Q4, 80% of leaders said security was their biggest barrier to reaching those goals. 🚧
The capabilities that make AI powerful are the same ones that make it exploitable. Jailbreaking, prompt injection, biased outputs, agentic AI making decisions it shouldn't. And they're showing up more than anyone wants to admit.
🏁 Know what you're working with before you go all in. Start here: www.bugcrowd.com/blog/ai-security-risks-what-teams-need-t…
 bugcrowd
@Bugcrowd
As platform ecosystems grow more complex, securing them requires more than standard tooling. 🔨
Bugcrowd's Trey Ford says non-human identities, long-lived credentials, and complex permission architectures create blind spots that automated scanning misses entirely.
The bigger the ecosystem, the harder it is to secure in the ways that matter. 🔐
If your org runs on Salesforce or any sprawling platform ecosystem, this Security Magazine piece is for you: www.securitymagazine.com/articles/102172-why-are-platform…
bugcrowd
@Bugcrowd
Friendly faces, refreshing drinks, and good tunes flowing... talk about a HOMERUN ⚾️
We're all about supporting our local teams, so if you're headed to the Giants game, stop by before and let's raise a toast to a successful RSA Conference and some good baseball!🍻
Last chance to register for The Hive's last inning 😉: www.bugcrowd.com/the-hive/


 bugcrowd
@Bugcrowd
Did you know IDORs have a variant? And it will probably be a P1.
Yes, it’s the Second-Order IDORs. Sometimes called Stored IDORs
Let’s have a mini masterclass🧵👇
 bugcrowd
@Bugcrowd
Tools 🛠️
No tools for this; you can't brute-force this you have to map it.
Two things you need
1️⃣ A pair of test accounts: an attacker (User A) and a victim (User B)
2️⃣ Patience: Test an input, wait for the cron job, check your email, check the webhook, retest.
bugcrowd
@Bugcrowd
Bookmark this for later🔖
Stay elite, map the state logic, and get those P1s. 🚀🔥
bugcrowd
@Bugcrowd
Immaculate vibes this morning with everyone packed in for the final session at The Hive. ☕️🥐
Thank you to @kristinaayanian for moderating, and to @davegerryjr, Ramin Farassat, John Spiegel, and Umesh Shankar for closing out the week with a conversation about AI risk, cyber insecurity, and what it means to lead through uncertainty.
We appreciate everyone who joined us for sessions at The Hive. Now, let's party 🎊🍸
6pm, be there! Registration is still open, but there's only a few spots left: www.bugcrowd.com/the-hive/
Thanks to our sponsors @menlosecurity, @HPE, and Unosecur for making it all happen!


 bugcrowd
@Bugcrowd
Moneytree has processed over 7.5 billion secure transactions. 📈
For nearly a decade, they've trusted Bugcrowd's crowdsourced security model to keep their platform and their customers' financial data protected.
"The Bugcrowd Platform and triage team allows us to filter submissions and remove duplicate vulnerability submissions."
Less noise, more signal, and faster fixes! 👏
See how they built a security program that scales: www.bugcrowd.com/blog/community-spotlight-moneytree/
bugcrowd reposted
 cje
@caseyjohnellis
Day $NEXT of RSAC is underway… Looking forward to catching up with folks, chilling at the @decibelvc Founder Festival, and the @bugcrowd HIVE Reception later on this evening. See you in the village!
www.bugcrowd.com/the-hive/
bugcrowd
@Bugcrowd
Your customers don't see the breaches that never happened.
That's exactly the point 👏👏
 bugcrowd
@Bugcrowd
This one is common in SPAs.
Did you SPOT it already?👀
👇
 bugcrowd
@Bugcrowd
🔺 Ransomware attacks are up 50% year-over-year. Ransom payments are down, meaning defenders are getting better, but attackers are adapting fast.
Cybercriminals are moving beyond phishing into SaaS-based attacks, double extortion, and social engineering IT teams directly.
Bugcrowd's Chief Strategy and Trust Officer Trey Ford says knowing your total attack surface and testing with remediation in mind is foundational. Endpoint visibility, MFA, privileged account management. Still where most breaches start.
🗞️ Bookmark this one for later: www.dice.com/career-advice/ransomware-trends-show-why-cyb…
bugcrowd
@Bugcrowd
FOR ONE DAY ONLY 😱⏰
JK, two days. But with day one coming to a close, you only have one day left to experience The Hive at RSA Conference.
One of the best parts is the connections you can make. Our speaker session tomorrow at 10:30am is not one to skip! Register here and enjoy a cup of coffee on us: luma.com/AIsession
Once you’ve taken that 5-min power nap after the show floor, we’ll be hosting a reception from 6–8pm. Yep, come relax and have some honest convos. We know you want to 🥂😏
‼️ You’ll be entered to win the gift card with registration and attendance.
bugcrowd
@Bugcrowd
📢 Trust is critical 📢
This afternoon at coolest spot at #rsac aka The Hive, Trey Ford, Pranav Vattaparambil, and Jaye Tillson talked on how that trust creates exploitable conditions across the extended enterprise in FinTech.
Thank you to our speakers for an incredibly candid conversation, and to everyone who joined us in the room for being part of it. 🎉🎸
One more session tomorrow at 10:30am if you want in. Complete your registration ASAP: www.bugcrowd.com/the-hive/
bugcrowd
@Bugcrowd
A donut is just a circle with a hole in it. 🍩
Your attack surface is the same, just with higher stakes!
This morning at The Hive, Braden Russell, Dominique DeVaux Jeffords, George Gerchow, Nick Terkay, and Deap Ubhi spent an hour talking about those gaps and how to close them.
Thank you to our speakers for kicking off The Hive the right way, and to everyone who joined us for making it such a great conversation. 🔥
Two more sessions this week if you want in.
🗓️ Today at 3:30pm and tomorrow at 10:30am.
We couldn't save you a donut (sorry), but we can save you a seat, register here: www.bugcrowd.com/the-hive/

 bugcrowd
@Bugcrowd
The White House dropped its National Cyber Strategy this month, and the industry is still unpacking what it means for security professionals.
✅ Offense is now table stakes, AI skills are non-negotiable, and the compliance-heavy era is getting a rethink.
Bugcrowd CEO @davegerryjr says the traditional model of defense is changing. Red-teaming, AI tooling, and threat hunting aren't nice-to-haves anymore. They're becoming standard practice as organizations shift from reacting to attacks to anticipating them.
If you're wondering how federal policy is shaping careers or security programs, this Dice piece breaks it down clearly. 🤓
Check it out: www.dice.com/career-advice/offense-ai-regulation-what-pro…
bugcrowd
@Bugcrowd
Johnny Blaze, Kent Wilson, and NASS Tech Talks—OH MY ⚡️
Maryland's VDP is setting the bar for state-level security transparency.
We recently had the pleasure of hearing from Steven Kain, DoIT leader behind Maryland's VDP, on what setting the bar looks like across agencies, apps, and election security. 🤝🤝
 bugcrowd
@Bugcrowd
The calendar has been circled for weeks. The people showing up to this? They're your people. 😍
Starting tomorrow at #rsac, you can find the Bugcrowd team at The Hive, just steps away from the Moscone Center.
We have donuts, big conversations with familiar names, and a reception to celebrate it all.
If you haven't signed up yet, head to the links below to register for sessions and The Hive Reception ⤵
🍩 Donut Miss the Holes in Your Attack Surface: luma.com/DonutBrunch
🤝 Trust Is the Attack Surface: luma.com/PeerExchange
🦾 Mitigating Adverse AI Outcomes: luma.com/AIsession
💃 The Hive Reception: luma.com/hivereception
 bugcrowd
@Bugcrowd
This isn't a webinar you'll have open in one tab while answering emails in another.
Bugcrowd and @hackthebox_eu are bringing the "Inside Offensive Security" roadshow to London, and we want you in the room.
🗓️ March 24, 2026
📍 AWS London
Security leaders will discuss how organizations close critical skill gaps, how external vulnerability discovery changes the game, and what offense-informed defense looks like when it's working.
🤝 networking with the people worth knowing
🍻 happy hour (yes, really)
🛍️ exclusive swag
Space is limited. If you're in London and this is your world—register now: resources.hackthebox.com/inside-offensive-security-what-r…{}&utm_campaign=EMEA_roadshow&utm_source=x&utm_medium=organic_social
 bugcrowd
@Bugcrowd
Did you spot it in a glance? 👀
What does your payload look like? 👇

bugcrowd reposted
 Owais
@syaedowais
P1 on @Bugcrowd
 Domino's Pizza UK
@Dominos_UK
starts with P and we all love it
bugcrowd
@Bugcrowd
When they ask about my weekend plans
Me:
 bugcrowd
@Bugcrowd
Check out all our open programs👇
bugcrowd.com/engagements?category=bug_bounty&page=1&sort_…
bugcrowd
@Bugcrowd
The struggle of security researchers in 2026.
 bugcrowd
@Bugcrowd
Just to name a few.
Want to go deeper on a specific topic? Our blog is packed with resources and guides to support your boardroom conversations: www.bugcrowd.com/blog/
 bugcrowd
@Bugcrowd
You survived the show floor. Reward yourself accordingly 🐝🥂
We’re hosting a low-key reception just steps from the conference with good drinks, good people, and conversation that feels a lot better than shouting over expo hall carpet 🤭
🌉 Come hang! Your better after-hours plan is right here at The Hive: luma.com/hivereception
We’re grateful to our sponsors, @HPE, @menlosecurity, and Unosecur, for helping bring this event to life! 🎉
 bugcrowd
@Bugcrowd
🔥
 Sharik Khan
@4non_Hunter
I just published a new #article on Medium.
How I Earned $76,000 Bounty From a Single Program on @Bugcrowd .
#bugbounty #bugcrowd #cybersecurity #ethicalhacking @Hacker0x01 @yeswehack @intigriti
anonhunter.medium.com/how-i-earned-76-000-from-a-single-p…
bugcrowd
@Bugcrowd
AI-generated phishing attacks have reportedly increased by 14X, with a significant impact on the manufacturing sector. 🧑🏭
The surge indicates a shift in how attackers are leveraging LLMs to scale their operations. By automating the creation of realistic lures, threat actors can target specific industries with much higher frequency.
This trend emphasizes the need for defensive strategies that can account for the rapid iteration of social engineering tactics. Read more at manufacturing.net: www.manufacturing.net/cybersecurity/article/22962434/aige…
bugcrowd
@Bugcrowd
AI might be moving faster than your org chart. 👥
When innovation outpaces accountability, risk ownership can get messy. We’re heading to RSAC to discuss how to fix the gap between AI-driven exposure and fragmented controls.
The Panel:
🎙️ @kristinaayanian (Moderator, @Nasdaq)
🎙️ @davegerryjr, (CEO at #bugcrowd)
🎙️ Umesh Shankar (CVP Engineering, Microsoft AI)
🎙️ Ramin Farassat (CPO, Menlo Security Inc.)
🎙️ John Spiegel (CTO Security, Hewlett Packard Enterprise)
💌 RSVP: luma.com/AIsession
Made possible with support from our event partners: @HPE, @menlosecurity, and Unosecur. 🔥
 bugcrowd
@Bugcrowd
✍️ World Poetry Day in cyber?
Yeah, we know. A little absurd.
Now that our social media manager tried to rhyme, please head to the blog because this felt like a crime 🥴: www.bugcrowd.com/blog/10-cybersecurity-poems-for-world-po…
Happy #worldpoetryday from Bugcrowd and our talented Director of Content Marketing 🌟🧡
bugcrowd
@Bugcrowd
Tired of standard XSS payloads getting blocked by strict sanitizers and CSPs?
Enter DOM Clobbering.
Here's how it works 🧵👇
 bugcrowd
@Bugcrowd
The Fundamentals 📚
When a browser parses a webpage, it maps the structure to a DOM tree. Thanks to legacy specifications, injecting HTML elements with an id or name attribute automatically creates a global property on the window and document objects.
bugcrowd
@Bugcrowd
How it Works ⚙️
If an application relies on a global variable (like window.config), we can overshadow or "clobber" it.
By injecting <a id=config name=url href='malicious.js'></a>, the engine maps this to window.config.url. When an existing "script gadget" evaluates that variable, it executes our payload instead.
bugcrowd
@Bugcrowd
Going Deep 🕳️
Clobbering isn't limited to a flat namespace.
By abusing the authoritative relationships of HTML <form> elements, we can clobber three levels deep. Injecting <form id=x><output id=y>Payload</output></form> successfully overwrites window.x.y.value.
bugcrowd
@Bugcrowd
Bug Bounty Significance 💰
This technique bypasses robust sanitizers by disabling their internal logic loops (like the classic html-janitor bypass). It escalates low-severity HTML injection straight to critical Stored XSS.
bugcrowd
@Bugcrowd
Tools of Efficiency 🛠️
DOM Invader: standard dynamic scanners fail at discovering this because aggressive clobbering instantly breaks site functionality. Use DOM Invader in Burp Suite, but remember you must manually toggle the "DOM clobbering" setting on and reload the browser context to start finding these data flows.
Stay 1337, DOM clobber! 👊🔥
bugcrowd reposted
𝖁𝖆𝖘𝖎𝖑𝖊𝖎𝖔𝖘
@marketingrckstr
Last year's hacker roadshow was GREAT! @Bugcrowd took security professionals and ethical hackers on the road and the reception has been phenomenal.
In 2026 @hackthebox_eu Box hops on the orange bus, and we start in London next week! Sign up here resources.hackthebox.com/inside-offensive-security-what-r…
 bugcrowd
@Bugcrowd
data = pickle.loads(user_cookie)
Replace pickle.loads with ________ to prevent RCE
A) pickle.loads(user_cookie, fix_imports=False)
B) json.loads(user_cookie)
C) yaml.load(user_cookie)
D) eval(user_cookie)
Hint: One of these is even WORSE than pickle 😈
Bonus: RCE payloads for each!
bugcrowd
@Bugcrowd
Verification is harder when risk is shared across vendors, partners, and platforms 💨
At The Hive during #rsac, Bugcrowd is hosting a conversation for security leaders focused on how FinTech teams assess vendor exposure, inherited risk, and partner dependencies in complex environments.
Featuring @treyford at Bugcrowd, Jaye Tillson at @HPE, and Pranav Vattaparambil at Unosecur. 🎙️
🛟 Save your seat before it’s full: luma.com/PeerExchange
Good conversations need good company. Thanks to our sponsors for helping make this one happen: Hewlett Packard Enterprise, @menlosecurity, Unosecur!
 bugcrowd
@Bugcrowd
📢 The White House has released a National Cyber Strategy that places a priority on offensive operations.
Bugcrowd CEO Dave Gerry observes that the current document serves as a high-level messaging framework. While it aligns with national needs, the specific details regarding timing, funding, and execution plans will likely follow in subsequent executive orders or legislation. 📜
For the cybersecurity industry, the focus now turns to how different agencies will be tasked with executing these high-level goals. Full story at Dark Reading: www.darkreading.com/cybersecurity-operations/white-house-…
bugcrowd
@Bugcrowd
Catch Tatiana Uklist from Bugcrowd on the Women in Cybersecurity Careers Panel hosted by the UTS Cyber Security Society 💼
It’s always inspiring to see conversations like this create more visibility, representation, and guidance for the next generation of talented folks in cyber!

 bugcrowd
@Bugcrowd
New research highlights how connecting Salesforce with third-party applications and APIs can inadvertently expand an organization’s attack surface.
Trey Ford points out that trust relationships are becoming a focal point for attackers. Compromising a single trusted integration can create a ripple effect of risk across the entire ecosystem.
Enterprise teams are encouraged to audit guest user permissions and enforce a policy of least-privilege access for all public API connections.
Read more in CSO Magazine: www.csoonline.com/article/4143667/overly-permissive-guest…
bugcrowd
@Bugcrowd
Coverage reports can look great while exposure quietly stacks up in the background. 😅
That’s the thread behind our upcoming brunch session at The Hive on attack surface gaps and exploit paths across modern stacks. This is a working discussion for buyers and security leaders who want tighter validation.
Moderated by Braden Russell at Bugcrowd, with field perspectives from Dominique DeVaux Jeffords at @TMobile, George Gerchow at Bedrock Data, Nick Terkay at Unosecur, and Deap Ubhi at @AWS.
🍩 Donuts included
📍 The Hive
If you know someone who’d love this session, bring them along. Registration is required, so tag them below 👇
🎟️> luma.com/DonutBrunch
Big appreciation for our sponsors: @HPE, @menlosecurity, and Unosecur! 🙌
 bugcrowd
@Bugcrowd
This GraphQL resolver looks secure... right? 🤔
Spot the vulnerability 👇
 bugcrowd
@Bugcrowd
2,000 hackers, one report, and plenty to talk about 😍
Join Bugcrowd CEO Dave Gerry at GeoCyclone in London for an insightful chat.
If you haven't signed up yet, now’s the time: luma.com/qmh8uc6e
Already registered? Scroll through our Inside the Mind of a Hacker report for a sneak peek at the discussion: www.bugcrowd.com/resources/report/inside-the-mind-of-a-ha…
 bugcrowd
@Bugcrowd
🚨 Overly permissive guest settings in Salesforce are coming under scrutiny as a primary vector for data exposure.
It’s an ecosystem challenge. Bugcrowd’s Chief Strategy and Trust Officer, Trey Ford, notes that the risk is often tied to third-party integrations and non-human identities (NHI). When credentials are long-lived and poorly monitored, they can grant unintended access to core systems.
Organizations should review integration account access patterns and apply IP limits to harden their usage of SaaS platforms.
Full report at Dark Reading: www.darkreading.com/application-security/overly-permissiv…
bugcrowd
@Bugcrowd
Public sector security teams are being asked to do more with less.
More systems to protect. More complexity to manage. More pressure to move quickly, stay compliant, and prove resilience against threats. 📋
That’s why crowdsourced security is becoming a more important part of the conversation.
Here's what matters 🧵👇
 bugcrowd
@Bugcrowd
FedRAMP changes the conversation
👉 Bugcrowd’s FedRAMP Moderate Authorization helps agencies move forward with greater trust in platform security and data protections.
bugcrowd
@Bugcrowd
📩 Download the Ultimate Guide to Offensive Security Testing in the Public Sector: www.bugcrowd.com/resources/guide/ultimate-guide-to-crowds…
bugcrowd
@Bugcrowd
The White House recently released the Cyber Strategy for America, elevating cybersecurity to a first-order national security priority.
Bugcrowd CEO @davegerryjr breaks down the strategy and identifies the shifts required to move from compliance to proactive resilience.
✒️ Closing the speed gap: Outpacing bureaucracy to match adversary speed.
✒️ Intelligence sharing: Enabling real-time public and private sector collaboration.
✒️ Preemptive discovery: Shifting focus from response to finding vulnerabilities first.
✒️ Scaling security: Using FedRAMP Moderate to help federal agencies modernize.
Read more: www.bugcrowd.com/blog/breaking-down-the-cyber-strategy-fo…
 bugcrowd
@Bugcrowd
Bam Adebayo just dropped a historic 83 points in a single game. 🏀
Think you can match that stat line?
On Bugcrowd, 83 points in a day isn’t a dream.
Time to hunt.
Check public programs here: 👇
www.bugcrowd.com/bug-bounty-list/
 bugcrowd
@Bugcrowd
os.system('ping ' + userInput)
Replace os.system with ________ to make it safe
A) exec()
B) eval()
C) subprocess.call([...])
D) shell_exec()
Drop your answer! Most pick wrong 😈
Bonus: Give payloads for each.
bugcrowd
@Bugcrowd
Classic download functionality but big impact.
Can you find any 🐞?
 bugcrowd
@Bugcrowd
This is a big step forward for federal agencies looking to modernize security without compromising trust. 📈
Bugcrowd’s FedRAMP Moderate Authorization brings crowdsourced offensive security to the public sector in a way that supports both mission speed and security rigor!
Learn how this expands what agencies can do with Bugcrowd: www.bugcrowd.com/blog/bugcrowds-fedramp-authorization-fre…
 bugcrowd
@Bugcrowd
Did you look for SSRF in URL-based parameters?
Archive → grep → test
Try this one-liner 👇
 bugcrowd
@Bugcrowd
Looks like it only allows jpg, png, gif.
What’s wrong here?
 bugcrowd
@Bugcrowd
Federal agencies have always faced a two-part struggle: a massive talent gap and 6–12 month wait times for security tool authorization. Bugcrowd just solved both!
By achieving FedRAMP® Moderate Authorization, we’re giving regulated teams a shortcut to high-velocity defense.
💨 Zero lag
🔐 Data sovereignty
🌍 Elite talent
As our VP of Global Public Sector, Kent Wilson, puts it: "We are providing federal teams a disciplined, vetted, and secure environment to proactively defend their mission-critical assets with absolute confidence."
You no longer have to sacrifice innovation for compliance. Read the TechPark piece: ai-techpark.com/bugcrowd-achieves-fedramp-moderate-author…
bugcrowd
@Bugcrowd
✋ Before Q2 hits, your leadership team should be having this AI risk conversation. And we’re making it easy at RSAC!
On March 25 at 10:30am, we’re sitting down with security and technology leaders to dig into the tough questions: AI-driven exposure, fragmented controls, and who owns risk when things get messy.
Grab your seat while spots are still available: luma.com/AIsession
Panel lineup ⤵
🎙️ @kristinaayanian (@Nasdaq) moderating
🎙️ @davegerryjr, Bugcrowd CEO
🎙️ Ramin Farassat, @menlosecurity CPO
🎙️ John Spiegel, @HPE CTO for Security
🎙️ Umesh Shankar, @MicrosoftAI CVP Engineering
The smartest way to start your RSAC day, thanks to our friendly sponsors at Unosecur, HPE, and Menlo Security! ☀️🙌
 bugcrowd
@Bugcrowd
If RSA Conference had a bingo card this year, “AI” would fill half the squares. 🔲
But the important conversation isn’t about new tools, it’s about the security assumptions AI is quietly breaking.
Bugcrowd’s @treyford shared three that likely won’t survive 2026.
And if you're responsible for securing legacy systems or critical infrastructure, the third one is especially important to understand: 👇
www.bugcrowd.com/blog/three-ai-security-assumptions-that-…
 bugcrowd
@Bugcrowd
Just because you can blast 10k req/s doesn’t mean you should.
Rate-limit your Nuclei scans.
Hunt responsibly. 👮
 bugcrowd
@Bugcrowd
🗞️ Agentic AI is quickly becoming part of the SOC. IDC predicts 45% of organizations will have autonomous agents operating at scale by 2030.
But deploying AI isn’t enough. Teams need to prepare for how work will change. Bugcrowd Founder @caseyjohnellis explains:
“Jobs won’t disappear, they’ll adapt. The key is ensuring that SOC professionals are prepared for this shift through ongoing education, training, and tooling.”
✍️ 4 takeaways for SOC leaders:
1️⃣ Analysts will shift from operators to AI supervisors
2️⃣ SOCs need new roles for AI governance and investigation design
3️⃣ Playbooks must evolve into AI-driven workflows and guardrails
4️⃣ AI decisions must stay explainable and auditable
Learn more: www.csoonline.com/article/4140208/4-ways-to-prepare-your-…
bugcrowd
@Bugcrowd
Looks fine at first glance… right?
Spot the bug 👇
 bugcrowd
@Bugcrowd
Bugcrowd has seen a sharp rise in what we’re calling “AI slop” submissions: high-volume reports with thin evidence, templated write-ups, and little to no validation.
That’s not how real vulnerability research works.
Bugcrowd has always been built on human ingenuity and high-signal findings, so we’re introducing updated submission policies to reduce speculative AI-generated reports and keep the focus where it belongs: validated vulnerabilities that create real impact.
These updates include enforcement against submission farming, automated pipelines, and repeated invalid submissions.
Read the full update from @treyford ↓
www.bugcrowd.com/blog/bugcrowd-policy-changes-to-address-…

bugcrowd reposted
 Crowd Funded Psyop
@kaorrosi
5%. There is no doubt that we need more women in the cyber field. That's honestly one of my main motivations for learning! I want to be able to help guide other women into the field and keep learning and growing together. Alot of women have messaged me saying me posting about my learning journey inspired them to start careers in the field and I hope all other women pursuing their technical careers and/or passions make sure to share their journey too and take up space here because you are the inspiration for me and so many others.
bugcrowd
@Bugcrowd
✊🚪 Knock knock. It’s Bugcrowd’s HackHer Network with a reminder for anyone needing a sign to keep going.
Women make up 5% of the hacking community, but we're changing that.
Ignore the people who discourage you. The world is literally waiting for what you bring to the table. 👏
Read more: www.bugcrowd.com/blog/international-womens-day-spotlight-…
 bugcrowd
@Bugcrowd
✊🚪 Knock knock. It’s Bugcrowd’s HackHer Network with a reminder for anyone needing a sign to keep going.
Women make up 5% of the hacking community, but we're changing that.
Ignore the people who discourage you. The world is literally waiting for what you bring to the table. 👏
Read more: www.bugcrowd.com/blog/international-womens-day-spotlight-…
bugcrowd
@Bugcrowd
Cisco just dropped patches for 48 firewall vulnerabilities, including two CVSS 10s.
It sounds like a lot, but our Chief AI & Science Officer, @thedavidbrumley, says the "batching" is actually a good sign for coordinated defense. Here's a quick breakdown ⤵
⚠️ Perimeter risk: Firewalls are the front door. If an attacker gets through, they've bypassed your entire defense.
🏎️ AI speed: 1-day vulnerabilities are being weaponized faster than ever. AI makes it easier for attackers to reason through disclosed code and turn it into an exploit.
📦 The move: These are being actively exploited. If you haven’t patched yet, do it now.
Full details here: hackread.com/cisco-patches-firewall-vulnerabilities-cvss-…
bugcrowd
@Bugcrowd
Open Redirects are everywhere, you just have to look at the right spot.
It could be as simple as waybackurls + a simple grep.
Try it on your next target 👀

bugcrowd reposted
R4CK4TT&CK
@R4CK4TT4CK
Don't forget to take a break from hax & touch a little grass 2day✌️#hacktheplanet 💙
 bugcrowd
@Bugcrowd
Me when I see all the new bug bounty programs on Bugcrowd
 bugcrowd
@Bugcrowd
Check them out👇
bugcrowd.com/engagements?category=bug_bounty&page=1&sort_…
bugcrowd
@Bugcrowd
AI won't replace the human intuition needed to find bugs, but it will amplify the hackers who use it.
If you are new to this, start small with n8n to remove friction from your workflow.👇
 bugcrowd
@Bugcrowd
Start with simple building blocks to automate the repetitive tasks:
1️⃣CVE Monitoring: Get instant alerts for new PoCs (like the React2Shell RCE) sent to your phone.
2️⃣Scope Management: Use bbscope and AI to track Bugcrowd asset changes in real-time.
3️⃣Background Recon: Run subdomain enumeration while you sleep and wake up to a filtered list of new targets.
bugcrowd
@Bugcrowd
The goal is to automate the repetitive "boring" parts so you can save your mental energy for manual exploration
Read the complete guide to automating your hacking with n8n here👇 www.bugcrowd.com/blog/tips-to-automate-your-hacking-using…
bugcrowd
@Bugcrowd
Catch us chillin' at The Hive during RSA. 🐝
Don’t wait to register! Save your spot 🛟: www.bugcrowd.com/the-hive/
bugcrowd
@Bugcrowd
👨🏻🔬 New research into vulnerabilities within Anthropic’s Claude Code proves that while AI tools can surface complex flaws, they still require expert human intuition to validate and weaponize the findings.
For the Crowd, these models are becoming the ultimate "force multiplier" to bypass the noise and focus on high-impact, creative exploits. 🐛
Read the breakdown: www.mbtmag.com/cybersecurity/article/22961480/new-researc…
bugcrowd
@Bugcrowd
The difference between a "Blocked" notification and a $5,000 bounty. 💸
 bugcrowd
@Bugcrowd
🚨 AI coding assistants are changing the "untrusted code" threat model. New research into Anthropic’s Claude Code (now patched) showed that simply cloning a repository could lead to full system takeover.
The risk has shifted from running malicious code to merely opening a malicious project. By abusing "Hooks" and configuration files, attackers could execute shell commands and exfiltrate API keys before a user even saw a trust prompt.
As we automate the developer workflow, we’re turning operational metadata into an execution layer. If you're using agentic AI tools, the repository is now part of your attack surface. 🛬
Technical breakdown: devops.com/security-flaws-in-anthropics-claude-code-risk-…
bugcrowd
@Bugcrowd
Let’s STOP ignoring WebSockets
There are P1s to be found.
Here we go.👇🧵
 bugcrowd
@Bugcrowd
Toolkit 🛠️
You can't hack what you can't see. Here’s the toolkit to enhance your hunting: 👇
1. Burp Suite: The WebSockets History tab and Repeater are your best friends. Intercept, modify, and drop frames.
2. STEWS: A lethal tool for automated WS endpoint discovery and vulnerability fingerprinting.
3. Wscat: Perfect for quick, lightweight CLI testing and raw connection probing.
bugcrowd
@Bugcrowd
Save this for later.🔖
Keep hunting, and bag those P1s. 🚀
bugcrowd
@Bugcrowd
Empowered women empower… the whole grid 📡✨
This International Women’s Day, we’re shouting out the HackHer Network! Since launching in 2025, this community has grown to members across 30 countries, connecting on hacking, research, career advice, and more. 🌎
From mentorship in Discord to breaking APIs with the best in the business, these hackers are living this year’s theme: #givetogain.
Finding your path in cyber is easier when you aren’t walking it alone. Come meet your new teammates like Katie, Olufela, Brigitte, and so many more 💜
Read their stories here and celebrate the women around you on March 8 (and every other day of the year): www.bugcrowd.com/blog/international-womens-day-spotlight-…
 bugcrowd
@Bugcrowd
The hacker's psyche is finally being declassified. 🔓
Professional hacking represents a sophisticated fusion of team-based creativity and critical risk. At GeoCyclone on April 23, Bugcrowd CEO @davegerryjr is tracking the seismic shift in the new reality of security research.
We’re bringing the data from 2,000+ hackers to the stage:
🤝 72% now work in teams
🦾 74% say AI has fundamentally increased the value of their work
⚠️ 65% are finding bugs they can’t report, and we need to talk about why
It’s time to align our policies with how the world’s best researchers actually work. Grab your FREE ticket before they’re gone: luma.com/qmh8uc6e
See you in the city! 🌃
 bugcrowd
@Bugcrowd
Singapore just revealed "Operation Cyber Guardian," an 11-month silent battle to oust the China-linked APT group UNC3886 from its four major telcos.
The attackers used zero-day exploits and rootkits to maintain persistence without disrupting service, a classic espionage play. As Bugcrowd’s @treyford points out in Dark Reading, this success story highlights a major lesson: intelligence sharing only works when the infrastructure is responsive enough to act on it.
Tight public 🤝 private coordination prevented what could have been a massive regional disruption.
Full story: www.darkreading.com/cyberattacks-data-breaches/singapore-…
bugcrowd
@Bugcrowd
Every trusted integration extends your attack surface 🔓➡️
We’re hosting a peer exchange at The Hive focused on supply chain and ecosystem exposure across financial platforms, with discussion centered on how leaders are pressure testing trust assumptions.
Featured speakers:
🎙️ @treyford, Bugcrowd
🎙️ Jaye Tillson, @HPE
🎙️ Pranav Vattaparambil, Unosecur
Step away from the #rsac floor a little early, and stop into The Hive on March 24 at 3:30pm.
🐝 Register here >> luma.com/PeerExchange
Thanks to HPE, @menlosecurity, and Unosecur for sponsoring! 🤝
 bugcrowd
@Bugcrowd
Low-key the biggest news of the week: Bugcrowd is officially FedRAMP® Moderate Authorized! 🥁
Government-grade trust meets the power of the Crowd. Kent Wilson and @treyford walk through why this matters and how we hardened the platform to meet the highest federal standards.
Let’s get into it > www.bugcrowd.com/blog/bugcrowds-fedramp-authorization-fre…
 bugcrowd
@Bugcrowd
It’s time to tackle postMessage!
Let’s not miss on those big P1s again. Time to upskill!
Here’s a mini masterclass🧵👇
bugcrowd
@Bugcrowd
Top Vulnerabilities:
1️⃣ Missing Origin Validation: The receiving script completely forgets to check event.origin and blindly accepts malicious payloads from ANY attacker-controlled domain.
2️⃣ Wildcard Leaks: The sender uses * as the target (window.postMessage(secretToken, '*')), broadcasting sensitive OAuth tokens or PII to any iframe that happens to be listening.
3️⃣ Weak Regex / indexOf Bypasses: Devs try to be secure by checking if(event.origin.indexOf('trusted.com') !== -1). Attackers simply register attacker-trusted.com or trusted.com.evil.net, completely bypassing the flawed logic.
bugcrowd
@Bugcrowd
Toolkit 🛠️
Here is the elite toolkit for dominating web messages👇
1️⃣DOM Invader (Burp Suite): The absolute GOAT. It automatically intercepts, monitors, and injects canary payloads into web messages to find dangerous sinks.
2️⃣DOMLogger++ (@kevin_mizu): This tool really shines when you need to trace complex data flows deep within a heavily obfuscated application.
3️⃣Chrome DevTools: Your native best friend. Pop open the "Global Listeners" tab in the Sources panel to manually audit message handlers.
bugcrowd
@Bugcrowd
Save for later🔖
Focus deep, trace the sinks, and get those P1s. 🚀
bugcrowd
@Bugcrowd
Hacker fomo is real, but you're worrying about the wrong thing. AI won't automate the "finding", but it will automate the "boring."
Stop wasting manual cycles. @aituglo breaks down the "start small" automation stack:
🚫 Stop over-optimizing: use simple nodes, not complex scripts
👀 Smart monitoring: use bbscope + AI to filter why new endpoints actually matter
👯♂️ Assistant, not pilot: use the Shift plugin in Caido to turn AI into a traffic analyst
You think, AI does. Read more: www.bugcrowd.com/blog/tips-to-automate-your-hacking-using…
bugcrowd
@Bugcrowd
📢 "The goal isn’t to find every bug; it’s to find the ones that actually matter to the business."
Bugcrowd CEO @davegerryjr joined BizcastNH to discuss the shift toward preemptive security. The conversation dives into how the crowdsourced model scales alongside rapid AI adoption, and why "checking the box" on security is no longer a viable strategy for modern enterprises. ☑️
Listen to the full interview for a look at where the industry is headed and how Bugcrowd is evolving to meet the next generation of vulnerabilities.
Listen here: www.podbean.com/media/share/pb-x34y6-1a53793
bugcrowd
@Bugcrowd
Why choosing a suitable target matters?
For a beginner, It will really be a rocky hacking adventure when you’re traversing an unfamiliar target.
But not when hacking a known program. Since you already know how the app works, navigating through is much smoother. And having an initial idea where sensitive features are, you already have a valuable intel on where to focus on thus making your bug bounty debut seamless and pleasurable.
Less friction, added fun.
Pick the program that fits you. 👇
www.bugcrowd.com/bug-bounty-list/
bugcrowd
@Bugcrowd
Bugcrowd has achieved FedRAMP® Moderate Authorization. ✅
Our Platform now meets 300+ NIST SP 800-53 controls, enabling federal agencies to deploy offensive security testing at scale.
Read the full announcement ➡️ www.bugcrowd.com/press-release/bugcrowd-achieves-fedramp-…
 bugcrowd
@Bugcrowd
The U.S. Treasury just released a new AI Risk Management Framework and Lexicon for the financial sector. 📑
As @thedavidbrumley has noted, moving from "aspirational statements" to practical, risk-based governance is the only way to deploy these models safely.
The framework adapts NIST standards specifically for the financial lifecycle, focusing on how third-party dependencies and model drift are monitored. In a sector where trust is the primary currency, clear guardrails are overdue. ⏰
Read more: www.americanbanker.com/news/treasury-issues-new-ai-risk-t…
bugcrowd
@Bugcrowd
Time to talk about GraphQL.
While everyone else is fuzzing REST endpoints like it's 2016, the top hunters are tearing apart GraphQL APIs.
It is a modern "Goldmine" for information disclosure and logic bugs.
If you see /graphql and ignore it, you are losing money.
Let's dig in.🧵👇
 bugcrowd
@Bugcrowd
🏁
Don't just look at the query the website makes. Look at the Schema to see what queries the website could make.
Happy Hunting. 🕹️
bugcrowd
@Bugcrowd
✅BONUS:
Even if Introspection is disabled, the game isn't over. Look at the error messages. GraphQL is notoriously verbose. If you guess a field name like secretField, the error might say "Did you mean 'secretField_v2'?" The "Suggestions" feature often leaks the schema for you.
bugcrowd
@Bugcrowd
For leaders at Atlassian, the ability to "rapidly mix and match" security services is what keeps their roadmap moving without compromising on safety. It’s about achieving technical assurance at the speed of business.
See how Bugcrowd’s flexible delivery model helps enterprise teams stay ahead of the curve. 📈
See the proof in our latest case studies: www.bugcrowd.com/customers/atlassian/
 bugcrowd
@Bugcrowd
One-liner command to try 👇
You can test for XSS across all endpoints at once.
 bugcrowd
@Bugcrowd
Ever wonder why Prompt Injection is still the #1 risk on the OWASP LLM Top 10?
Most people think it’s just about making an AI say something "edgy."
The reality for hackers? It’s the "master key" that opens the door to high-impact exploit chains across the entire application stack. 🗝️
👇
 bugcrowd
@Bugcrowd
The real pain point is that Prompt Injection rarely operates alone.
It’s a force multiplier for:
🔶LLM02/05: Forcing the disclosure of sensitive data or executing malicious HTML, JS, and SQL through poor output handling.
🔶LLM06: Exploiting "Excessive Agency" to hijack internal APIs for billing, user management, or infrastructure control.
bugcrowd
@Bugcrowd
If you’re only looking for a jailbreak, you’re missing the P1.
Real impact happens when you chain injection with agency and insecure output. ⛓️
Master the methodology and learn how to secure the next generation of AI apps.
Check out our full guide to the hidden threat of Prompt Injection here👇
www.bugcrowd.com/blog/a-guide-to-the-hidden-threat-of-pro…
bugcrowd
@Bugcrowd
POV: You just found the best plan for the weekend
👉bugcrowd.com/engagements
 bugcrowd
@Bugcrowd
💭 Imagine this: You log in to Bugcrowd and instead of a flood of data, you feel... momentum.
We’ve overhauled the Security Inbox to kill operational drag. Now, it’s your command center for turning vulnerabilities into resolutions at high speed.
Scale from 10 to 10,000 bugs without adding headcount. The new experience is live for all customers, log in and feel the difference. ⚡️
→ www.bugcrowd.com/blog/meet-the-new-security-inbox-faster-…
 bugcrowd
@Bugcrowd
The exploitation of the React2Shell flaw by LLM-generated malware marks a pivotal shift in the threat landscape 🏞️
We are officially entering the era of AI vs. AI. When malware can be generated and iterated on by Large Language Models, static defenses aren't enough. This shift underscores the need for a Crowd that knows how to use these same tools to find and patch flaws before they can be weaponized.
See how AI is changing the exploit game: securityboulevard.com/2026/02/exploited-react2shell-flaw-…
bugcrowd
@Bugcrowd
If you need to slip away from RSA to The Hive for a sugar rush, feel free to steal these excuses for your boss:
🔓 I'm performing a gap analysis on a dozen glazed donuts.
🍩 I have a "donut miss" situation.
☕️ Brunch is the only way to remediate my low blood sugar.
🗓️ I’ve got a 10:30 AM appointment with the CPO at Bugcrowd.
🏦 I'm heading to a session on FinTech supply chains.
📊 I’m analyzing "Next-Gen Supply Chain Threats" at The Hive.
💲 I’m attending a Nasdaq-moderated panel on fragmented risk.
My social battery needs a hard reboot.
Your boss is probably already in line for a donut anyway. See you at The Hive!
Register now (we have limited capacity): www.bugcrowd.com/the-hive/
 bugcrowd
@Bugcrowd
AI agents are the shiny new toy in security, but can they actually land you a P1? 🕵️♂
@hbenja_m went down the rabbit hole, moving from classic Bash scripts to a multi-agent CrewAI setup for OSINT and bug hunting. The result was a wild ride through automated report generation, a mountain of false positives, and a crucial lesson: ⤵
AI is an amplifier of skill, not a substitute for it 👌
Read this before your LLM hallucinates another P5: www.bugcrowd.com/blog/what-i-learned-building-ai-agents-f…
bugcrowd
@Bugcrowd
Next up: Hacking OAuth (Open Authorization) 🔓
You see "Log in with Google/GitHub" everywhere.
To a user, it’s convenience.
To a hacker, it’s a direct path to Account Takeover (ATO).
If you understand the flow, you can steal the tokens to the kingdom without ever touching a password.
Let's get into it. 🧵👇
 bugcrowd
@Bugcrowd
BONUS:
Always check the scope parameter. Sometimes apps ask for read_only access, but if you manually change the scope in the URL to admin or write, the backend might just accept it and give you elevated privileges. It's a classic privilege escalation hidden in plain sight.
bugcrowd
@Bugcrowd
Takeaway🏁
Validate the redirect. Check the state. Get paid.
Happy Hunting.🐞
bugcrowd
@Bugcrowd
DORA. NIS2. PCI-DSS. SOC 2. The EU AI Act.
The list keeps growing 📜
The pressure doesn’t shrink 😅
Staying compliant today means navigating overlapping requirements, reporting obligations, testing mandates, and real consequences for getting it wrong.
We put together a guide to major cybersecurity compliance requirements to help security leaders cut through the noise and understand:
🧮 What each framework actually requires
🔀 Where they overlap
☑️ What regulators expect in practice
🔐 How to approach compliance without lowering your security bar
 bugcrowd
@Bugcrowd
Threat-Led Testing:
Bugcrowd Red Team as a Service simulates real-world adversaries, measures detection and response, and delivers the kind of threat-led validation regulators increasingly expect.
bugcrowd
@Bugcrowd
Reporting:
From executive summaries to detailed findings and attestations, Bugcrowd delivers reporting that satisfies auditors without creating last-minute fire drills for your team.
bugcrowd
@Bugcrowd
AI Security Testing:
As AI systems face increased regulatory scrutiny, Bugcrowd provides bias testing, robustness validation, and AI penetration testing aligned with emerging compliance standards.
bugcrowd
@Bugcrowd
If compliance is on your roadmap this year, download the guide: www.bugcrowd.com/resources/guide/a-guide-to-major-cyberse…
bugcrowd
@Bugcrowd
A massive data leak has exposed the personal information of global leaders and executives, proving no one is off-limits ‼️
High-value targets require high-value defense. This leak is a stark reminder that an organization's attack surface extends far beyond its corporate firewall and into the personal digital lives of its leadership. 📲
See the impact of the leak: www.securitymagazine.com/articles/102129-global-leaders-e…
bugcrowd
@Bugcrowd
Singapore’s major telcos recently fended off state-sponsored attacks through a massive, coordinated intelligence-sharing effort.
📢 Intelligence sharing only works when it’s a two-way street. Trey Ford, our Chief Strategy & Trust Officer, notes that while many call for public-private partnerships, Singapore is proving that a tight relationship between government and industry creates a formidable response.
Read Trey's full commentary in Dark Reading: www.darkreading.com/cyberattacks-data-breaches/singapore-…
bugcrowd
@Bugcrowd
For most, it’s just boring enterprise XML. For a bug hunter? It’s a gateway to Full Account Takeover (ATO) and massive P1 payouts.
If you're skipping the SAML handshake, you're walking past "free" money.
Let’s break it down 👇
 bugcrowd
@Bugcrowd
The Toolkit 🛠️
Don't do this manually, save your energy for the exploit.
Use the SAML Raider (Burp Suite Extension): The "all-in-one" tool that detects SAML messages, manages certificates, and provides pre-built XSW attack templates.
Install it. Use it. Love it.
bugcrowd
@Bugcrowd
The Takeaway:
SAML implementations are notoriously complex and in security, complexity breeds bugs.
Go find them.
Happy Hacking! 🐞
bugcrowd
@Bugcrowd
Thinking like an attacker is not about running tools. It is about challenging assumptions most teams never question 🙋♂️
In this session, Bugcrowd’s Alistair G. pulls back the curtain on how modern red teams plan, adapt, and pressure test real environments.
If you want a clearer view of how adversaries actually operate, this is worth your time!
Happening soon 👉 www.bugcrowd.com/webinar/?commid=661860&bt_tok={{lead.id}}
 bugcrowd
@Bugcrowd
Behind every effective red team engagement is a lot of creative, slightly uncomfortable thinking. 💭
Join Bugcrowd’s Alistair G. for a straight look at how real adversary emulation works, including how elite operators plan simulations and where defenders most often slip.
🗓️ Coming up on Feb 26: www.bugcrowd.com/webinar/?commid=662258&bt_tok={{lead.id}}"
 bugcrowd
@Bugcrowd
The "DockerDash" incident is a wake-up call regarding the risks of blind trust in AI integrations within DevOps environments 🚨
AI is accelerating development, but it’s also creating unmapped attack surfaces. Securing the "Dark Side" of AI trust requires human-in-the-loop testing to catch the logic flaws that automated scanners miss.
Get the full story on DockerDash: securitybuzz.com/cybersecurity-news/dockerdash-exposes-th…
bugcrowd
@Bugcrowd
Why have one hacker when you can have the whole squad? 🏘️
If your program blocks team submissions, you're missing:
🛠️ Shared custom tooling
🧠 Combined technical depth
⛓️ Coordinated attack chains
⚡ Lightning-fast validation
@sw33tLie, @bsysop, and @_godiego__ went from solo to squad, and the results speak for themselves.
Is your program built for the modern Crowd, or are you still stuck in solo mode? 🐺🚀
 bugcrowd
@Bugcrowd
 bugcrowd
@Bugcrowd
 bugcrowd
@Bugcrowd
Check the blog: www.bugcrowd.com/blog/hacker-spotlight-meet-an-elite-hack…{TIMESTAMP_EPOCH}
bugcrowd
@Bugcrowd
Can you spot the bug before an attacker does? 👀
Bonus: Suggest the correct fix.
 bugcrowd
@Bugcrowd
There’s a reason @davegerryjr was named NH Tech Alliance's 2025 Entrepreneur of the Year. 🎖️
In his latest appearance on BizCast NH, Dave explains how Bugcrowd is scaling from San Francisco to New Hampshire and across the globe. It’s a look at how we’re driving a worldwide security revolution while staying deeply rooted in the NH tech community.
His philosophy: Service-first security. By combining the precision of autonomous testing with the ingenuity of a global crowd of researchers, Bugcrowd meets customers exactly where they are.
It’s not all technical ✋ Dave also shares some personal advice, like how being your authentic self is one of the most important things you can do in life and business.
🎧 Listen now: www.podbean.com/ew/pb-x34y6-1a53793
bugcrowd
@Bugcrowd
Skip the sales pitch and grab a donut instead 🍩🤭
We’re kicking off RSAC 2026 at The Hive with a brunch for security leaders. Our first session, “Donut Miss the Holes in Your Attack Surface,” tackles the reality of an attack surface that’s expanding faster than you can map it.
From AI-driven risk to API sprawl, we’re hosting a chat about what's working in the real world.
Space is limited and subject to approval, so don't leave a hole in your schedule. Sponsored by our incredible partners at @HPE! 🥰
🎫 Request to join the brunch: luma.com/DonutBrunch
 bugcrowd
@Bugcrowd
One man's "vibe" is another man's five-figure bounty.
 bugcrowd
@Bugcrowd
Want to know how vulnerable are vibe-coded apps?
Read this👇
www.bugcrowd.com/blog/hacking-vibe-coded-apps/
bugcrowd
@Bugcrowd
Ransomware-as-a-Service (RaaS) and AI are lowering the barrier to entry for cybercrime, leading to a 30% increase in new ransomware groups. 📈
As the threat landscape shifts, the advantage goes to those who can scale their defense as fast as the attackers. AI isn't just a tool for the "bad guys"—it’s a force multiplier for the Crowd.
📰 Read more on the evolving threat: securityboulevard.com/2026/02/ai-and-raas-alter-threat-la…
bugcrowd
@Bugcrowd
Is AI making hackers better? (🤫 Spoiler: Yes)
In 2023, only 21% of hackers thought AI added value, now it's 74%. Hackers are using AI to automate the boring stuff and focus on creative exploits.
For security teams, this means:
⏩ Faster findings
💰 More testing for your budget
🌐 Broader coverage
📊 Higher-quality reports
Check out the full Inside the Mind of a Hacker data: www.bugcrowd.com/blog/three-years-of-ai-innovation-and-ha…
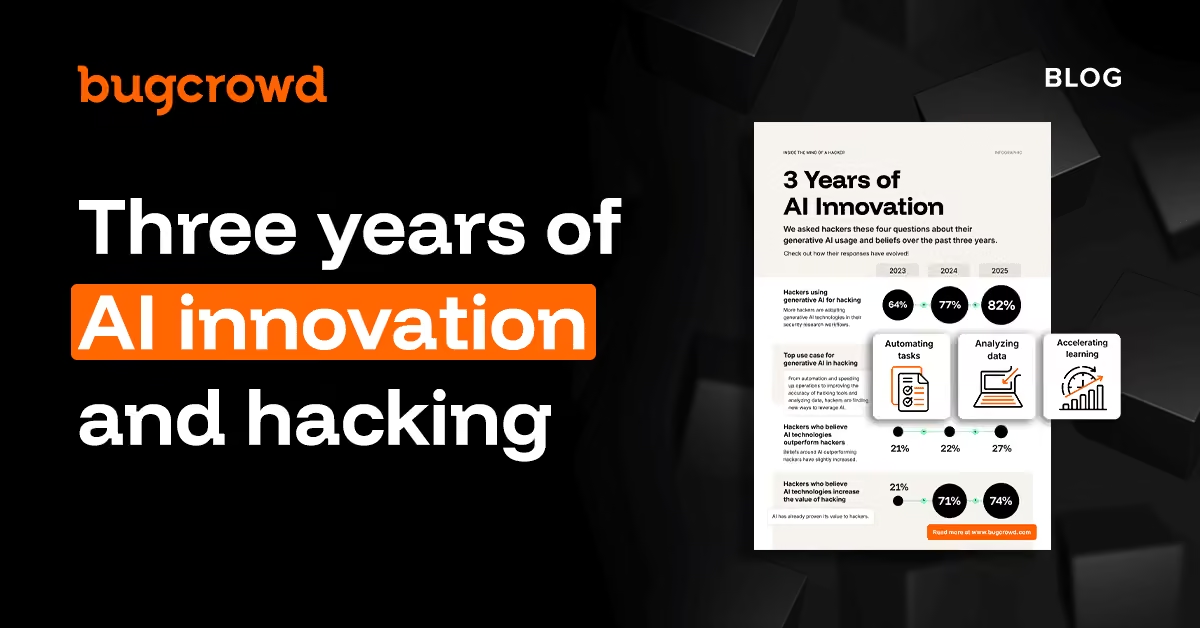 bugcrowd
@Bugcrowd
“AI red teaming” is getting thrown around a lot right now. But not everything labeled red teaming… is red teaming 🫢
On @DtSR_Podcast, Julian breaks down the difference between real, covert red team operations that are structured, controlled, and intentionally steered. He also calls out how the term is being stretched in today’s AI conversations.
As AI testing evolves, precision in language matters. So does rigor.
Full conversation with Rafal, James, and Jim ⤵
Listen 🎧: www.buzzsprout.com/2153215/episodes/18498795
Watch ▶️: youtube.com/live/aNz-qPmWf7g
bugcrowd
@Bugcrowd
Bug bounty is one of the few fields with asymmetric upside: low entry barriers, but an infinite financial ceiling.
🚫No degree or extensive certs. No interviews or resumes.
Just you, your proxy, and your grit.
The Classic Path to Payouts: Basic Web Ops → 1 Specialized Bug Class → Deep Recon → High-Impact Payouts.
✅ The Secret: Don't be a generalist. Master one high-impact bug class (like IDORs or Logic Flaws). Being the specialist who finds what others miss is the fastest way to your first P1.
Master one. Hunt deep. Get paid.
bugcrowd
@Bugcrowd
To a dev, it’s a security layer. To a hunter, it’s the difference between a $5,000 P1 and a "N/A" report.
If you aren't analyzing Content Security Policy (CSP) headers, you’re leaving bounties on the table.
Here’s the breakdown. 🧵👇
bugcrowd
@Bugcrowd
The Trickster’s Eye: Where it fails 🫣
This is where we get paid. CSP is notoriously hard to implement correctly. Look for these "lazy" configurations:
⚠️ unsafe-inline: Allows inline scripts (kills the main protection against XSS).
⚠️ unsafe-eval: Allows dangerous functions like eval().
⚠️ wildcards (*): Allowing data from anywhere.
⚠️ Missing base-uri: Can lead to base tag hijacking.
A weak CSP is often worse than no CSP, it provides a false sense of security while leaving the doors unlocked.
bugcrowd
@Bugcrowd
✅The Takeaway: Don't just find the injection; find the bypass.
Learn to read the policy, identify the whitelisted domains you can abuse (like JSONP endpoints), and turn that "blocked" error into a successful PoC.
Happy Hunting. 💸
bugcrowd
@Bugcrowd
A sad story in 4 acts 🚬
 bugcrowd
@Bugcrowd
What does it actually mean to think like an attacker during a red team engagement? 🚨🫰
In this webinar, Bugcrowd’s red team experts walk through the mindset and methodology behind real adversary emulation, including how operators plan simulations, apply creative pressure, and expose hidden weaknesses that scanners miss.
⏩ If you are building or refining a red team program, save your spot now: www.bugcrowd.com/webinar/?commid=662258&bt_tok={{lead.id}}
 bugcrowd
@Bugcrowd
🚙🚨 Volvo Group North America is among the companies impacted by a breach tied to an HR outsourcing provider. Third party risk continues to show up as first party damage.
Your attack surface includes vendors, partners, and connected services whether you like it or not. Continuous testing across that ecosystem helps catch weak links early ⛓️💥
If you're managing supplier risk, check out the full story: www.manufacturing.net/cybersecurity/article/22960518/volv…
bugcrowd
@Bugcrowd
Vibes are great for playlists 🎧🕺
Slightly less great for secure code.
AI can crank out working apps fast, but speed without scrutiny creates risk. Ryan Syed tested vibe-coded output from multiple models and reviewed the vulnerabilities that came with it!
To vibe or not to vibe?? Read the full piece to find out: www.bugcrowd.com/blog/hacking-vibe-coded-apps/
bugcrowd
@Bugcrowd
Ever wonder how red teamers actually think when they are planning an attack simulation? 🎭
Join our upcoming session with Bugcrowd’s red team leadership for a behind the scenes look at the mindset, creativity, and controlled chaos that drives effective adversary emulation. 🚨🫰
You'll learn how elite red teams plan engagements, where defenders commonly slip, and how crowdsourced red teaming adds depth and scale!
🗓 February 26: www.bugcrowd.com/webinar/?commid=661860&bt_tok={{lead.id}}
 bugcrowd
@Bugcrowd
The conference show floor is like a 5-mile hike through a forest of buzzwords 🥾🌳🥵
The Hive is where you find the clearing. It’s a dedicated space near RSAC to breathe, reset your bearings, and have conversations with peers who own the same high-stakes outcomes you do.
🎟️ The lineup: 3 sessions, 1 low-key reception, and a limited guest list. Take a look at our speakers and get your name on the list ASAP 👇:
🍩 Tuesday, March 24 at 10:30am featuring: Braden Russell, Dominique DeVaux Jeffords, and George Gerchow!
🤑 Tuesday, March 24 at 3:30pm featuring: ☁️ Trey Ford and Jaye Tillson!
🦾 Wednesday, March 25 at 10:30am featuring: Kristina Ayanian, Dave Gerry, Amir Ben-Efraim, and John Spiegel!
🐝 Wednesday, March 25 at 6pm: The Reception!
Space is limited, and approval is required. Don't leave your week (and calendar) to chance! Register here >>> www.bugcrowd.com/the-hive/
Shoutout to our incredible sponsor, @HPE!
 bugcrowd
@Bugcrowd
Register here: luma.com/DonutBrunch
 bugcrowd
@Bugcrowd
Register here: luma.com/PeerExchange
 bugcrowd
@Bugcrowd
Register here: luma.com/AIsession
 bugcrowd
@Bugcrowd
 bugcrowd
@Bugcrowd
Bugcrowd CEO @davegerryjr is joining GeoCyclone in London this April 🇬🇧
Security and geopolitics leaders will be in the room to examine what’ shaping today’s threat landscape 🌍
The discussion: The Modern Hacker, AI, and Bug Bounties 💬👏
Drawing from insights gathered from 2,000 hackers worldwide, Dave will share what we’re seeing across the community, how AI is influencing offensive behavior, how motivations are shifting, and what that means for organizations defending complex, real-world environments.
Thanks to Dr Craig Jarvis for letting us be part of the event!
🗓️ April 23! Sign up here:
luma.com/qmh8uc6e
bugcrowd
@Bugcrowd
If you’re still just swapping id=123 for id=124, you’re fighting for duplicates.
In 2026, IDORs are about broken business logic, not just incrementing integers.
Here is the methodology elite hunters use to find P1s. 👇
 bugcrowd
@Bugcrowd
5️⃣ The "Race-to-IDOR"
Classic pattern:
- Request A checks authorization
- Request B changes ownership
- Request A completes
Try using parallel requests, delayed responses, and modified replays.
bugcrowd
@Bugcrowd
✅ The Takeaway: IDORs aren't a bug; they are a failure of Contextual Awareness.
The system knows who you are, but it forgets what you own.
Stop thinking, "Can I change this ID?"
Start thinking, "Where does the system assume ownership without verifying it?"
Happy hunting. 🐞
bugcrowd
@Bugcrowd
Industry forecasts expect CVE disclosures to cross 50,000 in 2026. Transparency is good. Alert overload is not 🚫
More CVEs do not automatically equal more risk, but poor prioritization definitely does. Teams that validate real world exploitability are in a much better spot than teams chasing every alert the same way. ✅
See what the forecast means for us as defenders: www.secureworld.io/industry-news/first-forecast-cves-surp…
bugcrowd
@Bugcrowd
It's PHP Time! ⏰
Find the 🐞👇
 bugcrowd
@Bugcrowd
📰 A newly reported Docker AI flaw shows how malicious image metadata can trigger unintended actions through prompt injection patterns.
Bugcrowd’s @thedavidbrumley highlights this as a growing AI risk area that traditional AppSec tools often miss. If your AI stack trusts inputs too easily, attackers will take advantage.
AI features move fast. Guardrails and real world testing should move faster. Read the coverage: www.govinfosecurity.com/docker-ai-bug-lets-image-metadata…
bugcrowd
@Bugcrowd
Every false positive eats up reviewer time, and when enough of them pile up, even strong bounty programs start to feel the strain 🫨
That is what happened with cURL after a surge of AI generated vulnerability reports that sounded convincing but led to no real findings. Bug bounties work because of trust, proof, and reproducible results, not guess and submit.
Read why quality control is becoming a survival skill for modern bug bounty programs: www.bugcrowd.com/blog/hacker-opinion-piece-how-lazy-hacki…
bugcrowd
@Bugcrowd
Financial services is a top target right now.
📊 97% of US banks had a third party breach
📈 Attacks up 109% YoY
💸 Avg breach cost $6M
Attackers go after vendors, APIs, partners, and internal access, not just the perimeter.
Our new crowdsourced security guide for financial services shows how teams are closing the gaps.
Get it → www.bugcrowd.com/resources/guide/crowdsourced-security-fo…
 bugcrowd
@Bugcrowd
What if your inbox felt like a command center instead of a flood zone? 👀
Security teams don’t need more data; they need more momentum. Inspired by how teams use the Bugcrowd Platform every day, we’ve redesigned the Security Inbox to act as your mission control:
✅ Zero Friction: Custom filters to cut the noise.
✅ High Speed: Triage and collab in one view.
✅ Scale: Handle high volumes without the overhead.
Learn how to accelerate your workflow with it here: www.bugcrowd.com/blog/meet-the-new-security-inbox-faster-…
 bugcrowd
@Bugcrowd
Passing ≠ protected. 😯
Attackers don’t test against your audit framework, they probe your entire attack surface.
That’s why more teams pair compliance with crowd-powered testing and AI-assisted validation.
See how teams like yours validate risk with Bugcrowd 🚀:
bugcrowd
@Bugcrowd
Vulnerability volume is climbing fast, with forecasts showing published CVEs could top 50,000 in 2026. That is a lot of disclosed weaknesses and a lot of pressure on already busy security teams. 🗓️
The challenge is knowing what to fix first and how quickly to act while attackers operate at machine speed. As Bugcrowd’s @treyford notes, the real question is whether patching and response can keep up.
More volume means smarter prioritization matters even more. Get the full breakdown here: www.scworld.com/news/published-cves-could-hit-record-brea…
bugcrowd
@Bugcrowd
Just a reminder: burnout is real and common in cybersecurity.
Signs to watch for:
> Exhaustion
> Brain fog
> Irritability
> Anxiety
If you start to feel these, it's a sign to take a break.
The bugs can wait.
Your health is more important
bugcrowd
@Bugcrowd
You don’t need 20 tabs for recon. You just need a pipe.
Here’s the one-liner 👇
subfinder → httpx → gau → grep
Turn passive recon into real findings.
 bugcrowd
@Bugcrowd
What made you fall in love with bug bounty hunting? 👀
1️⃣ The first big payout
2️⃣ The creative "puzzle-solving"
3️⃣ 90s hacker movies
4️⃣ The rush of the first alert(1)
Drop your story below! 👇
bugcrowd
@Bugcrowd
Severity scores don't always predict real world risk ⚠️
In this campaign, attackers leveraged Microsoft Office vulnerabilities that were not just top of the chart criticals to establish access and move forward.
Bugcrowd’s @treyford highlights the gap this exposes. Many teams prioritize only the highest scores, but targeted attackers often chain medium and high vulnerabilities with social engineering to get results. One trusted click can open the door.
👉 Full coverage from @SCMagazine:
www.scworld.com/news/microsoft-office-bugs-exploited-by-r…
bugcrowd
@Bugcrowd
That “AI installer” download might be installing more than features 🍎
macOS users are being hit by Python based infostealers disguised as AI tools. Familiar theme, real compromise risk.
Bugcrowd’s @treyford warns this trend shows why teams need a continuous offensive view of their technology estate, especially as attackers use AI powered capabilities to gain footholds.
Continuous testing helps catch what branding and trust signals miss. Read the full story from HackRead:
hackread.com/macos-users-python-infostealers-posing-ai-in…
bugcrowd
@Bugcrowd
Emotionally attached. ♥️
bugcrowd
@Bugcrowd
Going to #rsa? We can sweeten your day, just a few blocks away 🍯
RSA Conference is coming up quick! Your future self and your tired feet will thank you for adding The Hive to your schedule ☝️
Because the show floor can be a lot. Noise, crowds, constant buzz. The Hive is your reset spot. Come chill, grab something good, and talk security in a space built for conversation. 🐝
Take a look at what’s happening at The Hive →
www.bugcrowd.com/the-hive/
Thanks to our sponsor, @HPE!🫸💥🫷
 bugcrowd
@Bugcrowd
Will AI replace pen testers? Not so fast 🙅
AI is accelerating security testing, but trust, oversight, and validation still matter a lot 🙌
Bugcrowd Chief AI and Science Officer @thedavidbrumley puts it like this: AI is here and it is already improving the speed and scale of testing. The win is not human versus AI. It is human plus AI!
Faster signal, less exposure time, better decisions.
If you are evaluating where AI fits into your testing strategy, this @DarkReading piece will help ⤵:
www.darkreading.com/cybersecurity-operations/ai-supplant-…
bugcrowd
@Bugcrowd
If this trio isn’t on your radar yet, you’re about to wonder why. That feeling right now? FOMO.
Meet sw33tLie, bsysop, and godiego 👉 friends who hack as a team. Ideas get challenged, paths get chained, and “that’s probably nothing” quickly turns into “ok that’s definitely something.”
If you want to see how team-driven hacking exposes weaknesses faster and from more angles, start here. They’re also a pretty fun crew to learn from. 😏
Meet the team and see how they work: www.bugcrowd.com/blog/hacker-spotlight-meet-an-elite-hack…
bugcrowd
@Bugcrowd
👋 @bsysop
👋 @sw33tLie
👋 @_godiego__
bugcrowd
@Bugcrowd
Want to start hunting for WCP bugs?
Understand these 4 core concepts first 👇
 bugcrowd
@Bugcrowd
4️⃣ Cache Rules & TTL
- Cache Rules: Instructions telling CDNs/Load Balancers what to store, for how long, and for whom.
- TTL (Time To Live): How long a response stays in cache before expiring. (Longer TTL = greater impact if the cache is poisoned).
- Cache-Control: Watch for public + long max-age. These are prime targets for web cache poisoning.
✅Quick Tip: If you're hunting for bugs, look for X-Cache: Hit. It confirms the server is serving you the stored version!
bugcrowd
@Bugcrowd
Ready to hunt for WCP bugs? 🎯
Save this for your next session!
bugcrowd
@Bugcrowd
Your environment doesn’t sit still, with new APIs, integrations, and exposure popping up all the time.
Meanwhile your pen test report is already aging 🏚️🧓🏻
Our Ultimate Guide to Penetration Testing breaks down what testing looks like when uptime, trust, and regulators are all in the room at the same time.
📢 This is exactly why continuous validation is becoming the new normal. Check it out for yourself: www.bugcrowd.com/resources/ebooks/the-ultimate-guide-to-p…
bugcrowd
@Bugcrowd
The threat model is getting blurry, which is a problem. We need to see clearly. Quick plug: go get your eyes checked 🤓
Nation state activity and cybercrime are overlapping more than ever, which makes attacker behavior harder to predict and harder to contain.
Bugcrowd founder @caseyjohnellis explains the shift toward hybrid threat models where motivation, tooling, and intent can change mid campaign. That unpredictability means orgs cannot rely on static testing or checklist compliance.
When motives shift, visibility matters more than assumptions 🆑
→ This is a good read from @SecurityWeek: www.securityweek.com/cyber-insights-2026-cyberwar-and-ris…
bugcrowd
@Bugcrowd
The groundhog might have seen its shadow, but that doesn’t mean you can’t do a little spring cleaning. 🌷
In case you didn’t know, today is Clean Out Your Computer Day, which is important for good tech hygiene or something like that 😌
Here’s a cleanup list so easy even your dog could do it (make sure to give them treats if they do it for you) 🧵👇
 bugcrowd
@Bugcrowd
🧹 Empty downloads folder
🧹 Delete duplicate files and random screenshots
🧹 Uninstall apps you don’t use anymore
🧹 Clear your desktop clutter
🧹 Organize loose files into folders
🧹 Empty your trash / recycle bin
🧹 Remove unused browser extensions
🧹 Update your software and restart your machine
🧹 Back up anything you’d be sad to lose
✋ Close all your tabs and go touch grass
bugcrowd
@Bugcrowd
You don't wan´t to miss this data👀
5 things about the modern hackers and why it matters. 👇
 bugcrowd
@Bugcrowd
5️⃣ AI has become the keystone:
- The majority of elite hackers now rely on AI.
- It is used primarily to automate recon, analyze code, and conduct instant research.
✅Why it matters: Hacking now runs at machine speed, 24/7. It's a race of momentum.
bugcrowd
@Bugcrowd
Today, security isn't about Humans vs. AI. It’s about Humans + AI working toward a more secure future.
Organizations that understand how hackers think, collaborate, and adapt will be the ones that stay ahead of the curve.
👉 Dive deeper here
www.bugcrowd.com/blog/inside-the-mind-of-a-hacker-2026/
bugcrowd
@Bugcrowd
Big global events = big attack surfaces ❄️🏟️
The Winter Olympics attracts athletes, fans, 𝒂𝒏𝒅 attackers.
In this piece, security leaders break down how orgs can stay resilient during high visibility moments. Bugcrowd’s Trey Ford highlights a simple but often overlooked control: people.
Continuous security testing plus employee awareness creates layered defense, not just perimeter confidence. 🤝
Real security posture comes from:
✔️ Continuous testing
✔️ Validated findings
✔️ Humans who know what to question
Smart, practical guidance from @securitymag here:
www.securitymagazine.com/articles/102115-how-to-protect-o…
bugcrowd
@Bugcrowd
Today's the day! 🎉
The Bugcrowd crew including Maria, Gary, and Kye will be at CISO Sydney and ready to chat about security, Bugcrowd, your biggest questions, and possibly your favorite color.
We’re a friendly bunch, so come say hi and don’t be shy 👋
➡️

bugcrowd reposted
 tal
@RelentlessT7
After a hard work of Triaging!!! @Bugcrowd #saynotoburnout
 bugcrowd
@Bugcrowd
Somewhere out there, a hacker is reading this right now 👀🌎
Actually… a lot of them are!
Here are the top 10 countries hackers are located in, according to Bugcrowd’s 2026 Inside the Mind of a Hacker Report:
bgcd.co/4qYX8DG
Sound off if we missed you ⤵
bugcrowd
@Bugcrowd
My priorities are exactly where they need to be.
 bugcrowd
@Bugcrowd
Check out our programs👇
bugcrowd.com/engagements?category=bug_bounty&sort_by=prom…
bugcrowd
@Bugcrowd
Did you spot it?
If this passed review, the bug isn’t the upload.👀
Reply with your answer👇
 bugcrowd
@Bugcrowd
Huddle up 🏈😃
No matter how the big game ends, the real winners are the teams who run Mayhem all year long 🏆


 bugcrowd
@Bugcrowd
🚌 In coverage of Australia’s review of Chinese electric buses, Bugcrowd founder @caseyjohnellis highlights that the real risk in connected vehicles isn’t cinematic remote takeovers.
It’s data exfiltration, surveillance, ransomware, and fleet-wide compromise 📹🔐
As Ellis notes, modern vehicle networks make dramatic physical takeovers less likely, but the underlying digital risks are often underestimated.
@DarkReading breaks down why these concerns matter beyond transportation: www.darkreading.com/cyber-risk/chinese-electric-buses-aus…
bugcrowd
@Bugcrowd
Your answer says a lot about how you hunt. 👀
Drop your answer below👇
 bugcrowd
@Bugcrowd
Bugcrowd is sponsoring CISO Sydney, and Maria Ter Meer, Kye Gaviglio, and Gary Tolmatsky are making the trip to meet security leaders and practitioners in person 👋🥳
Come say hi, test our thinking, and talk about how continuous testing holds up in the real world. Bonus points if coffee is involved 😈
See you there: ciso-syd.coriniumintelligence.com
 bugcrowd
@Bugcrowd
🗣️ Bugcrowd Senior VP of Offensive Security & Strategy Julian Brownlow Davies explains, modern offensive security goes beyond point-in-time testing. It combines human ingenuity, automation, red teaming, and bug bounty programs to continuously validate how real attackers operate.
That shift 👉 from episodic testing to intelligence-led validation 👈 is defining where offensive security is headed next.
@SecurityWeek explores what that evolution means for defenders: www.securityweek.com/cyber-insights-2026-offensive-securi…
bugcrowd
@Bugcrowd
At Bugcrowd, we take security seriously 👔
Ourselves? Slightly less so.
We don’t usually post the bloopers. But like any good testing process, the messier moments happen before the results. 😏
Here’s a rare look behind the scenes. You’re welcome. Please don’t get used to this.
It’s the same philosophy behind RTaaS: test early, iterate often, and fix things before it matters ⬇️:
www.bugcrowd.com/products/rtaas/
bugcrowd
@Bugcrowd
Want to discover a modern app’s attack surface? 🔍
Most of it lives in JavaScript.
Katana helps uncover what traditional crawlers miss by crawling what actually runs in the browser, not just static links.
Why Katana is useful:
✅ Extracts endpoints from JS bundles
✅ Handles client-side rendering
✅ Finds routes passive recon misses
✅ Easy to chain into automation
Check it out 👉 github.com/projectdiscovery/katana
 bugcrowd
@Bugcrowd
♨️ Hot tip: don’t wait for permission to belong.
Brandon Prince, better known in the community as syntax, started at BSides Philly by volunteering, moving chairs, building badges, and spinning music. Years later, he was on stage telling stories 🎙️
There’s no “right” way to get involved, just show up!
Hacking since the mid-’90s. Now a Tech Engagement Manager at Bugcrowd. This is one hacker spotlight you don’t want to scroll past 📜: www.bugcrowd.com/blog/the-value-in-making-mistakes-one-ha…
 bugcrowd
@Bugcrowd
As autonomous AI-powered attacks become more realistic, long-standing security gaps will surface fast. 🚨
According to Bugcrowd Chief Strategy and Trust Officer Trey Ford, this shift may finally force organizations to take basics like MFA seriously.
💭👉 “Sadly, I think some of these [AI-powered attacks] will be what motivates those changes,” Ford told CRN.
AI raises the bar on fundamentals. Gaps become impossible to ignore. Read more on this in @CRN's full analysis: www.crn.com/news/security/2026/how-autonomous-ai-cyberatt…
bugcrowd
@Bugcrowd
📙 New data from Bugcrowd’s Inside the Mind of a Hacker 2026 report shows AI adoption surging across the global ethical hacker community, changing how vulnerabilities are discovered, validated, and prioritized.
Understanding these workflows is critical for organizations trying to stay ahead of increasingly capable adversaries.
See how @SCMagazine breaks down the findings 🔗:
www.scworld.com/brief/ai-adoption-surges-among-ethical-ha…
bugcrowd
@Bugcrowd
Yes, you’re seeing this right. And yes, you’re invited. 🥳
@Chime is turning up the rewards this February. Double bounties on valid P1s all month long ‼️
Security is core to Chime’s mission of bringing financial peace of mind to everyone. Your research helps keep millions of members safe and their money secure.
→ Start digging for those bugs: bugcrowd.com/engagements/chime
 bugcrowd
@Bugcrowd
AI-generated actors are surging, but as they move into the mainstream, so do the risks. Scammers are now using these "perfect" personas to scale fraud with terrifying efficiency.
👇🧵
 bugcrowd
@Bugcrowd
The risks:
🔶Hyper-Realistic Scams: Fraudsters are using AI personas to build "emotional rapport" at scale, leading to highly effective romance and investment scams.
🔶Deepfake Endorsements: We’ve seen "Taylor Swift" cookware giveaways; now, AI-cloned influencers are used in real-time video calls to push fraudulent products.
🔶Identity Kits: Scammers are pairing AI faces with synthetic IDs and voices to bypass traditional verification, making "seeing is believing" a thing of the past.
bugcrowd
@Bugcrowd
How to stay safe:
✅ Check the URL: Scammers mimic brands but miss the details (e.g., retailer.com vs retailer-deals.net).
✅ Verify the Source: Real influencers don’t usually ask for crypto or urgent wire transfers in DMs.
✅ Look for Glitches: Watch for unnatural blinking, mismatched lip-syncing, or weird finger/hand movements in videos.
The future is human-augmented, but the risks are purely digital. Stay skeptical
bugcrowd
@Bugcrowd
Your triage workflow just got a serious upgrade 🔥
Meet Bugcrowd’s new Security Inbox. Built to help teams move faster without sacrificing accuracy.
→ AI-powered triage to move fast and stay precise
→ Saved views for instant focus on what matters
→ Split-view layouts to review details without losing context
→ Automated ticketing to trigger action at the right moment
Because speed only matters if it’s right. Live now for all Bugcrowd customers.
Read the full blog: www.bugcrowd.com/blog/meet-the-new-security-inbox-faster-…
bugcrowd
@Bugcrowd
One thing we hear over and over from this community: “Consistency pays off.” 💪
How long have you been in the game? No wrong answers.
bugcrowd
@Bugcrowd
A new year brings a new calendar full of events. First up: #rsac!
Bugcrowd will be headed to #sanfrancisco this March, and there’s already a little buzz. That’s all we’re saying for now 🌉🤫
Anywhoooo, which type of con-goer are you gonna be this year?
📝 The note-taker (notes app fighting for its life)
🎤 The interviewer (“wait 🤳 can you say that again?")
📸 The documentarian (if no pics, did it even happen?)
🔋 The prepared one (hydrated, charged, unstoppable)
🍯 The sweet strategist (snacks is your strategy)
>>> Tell us below!
 bugcrowd
@Bugcrowd
Spot the bug 👇
Looks like user preferences, but it's not👀
 bugcrowd
@Bugcrowd
👨🏻🔬 According to Bugcrowd’s Inside the Mind of a Hacker 2026 report, more than 80% of ethical hackers are already using AI to accelerate research, identify patterns, and work more efficiently.
For security teams, this changes the baseline. Attackers are evolving faster, and defenders need insight into how modern hackers actually operate, not how we think they do!
Read @InfosecurityMag's coverage of the data shaping today’s hacker workflows: www.infosecurity-magazine.com/news/over-80-of-ethical-hac…
bugcrowd
@Bugcrowd
At @CactusCon 14, Bugcrowd will be on the ground discussing how organizations combine expert triage, trusted hackers, and continuous testing to reduce risk faster and with confidence. 🏜️
🗓️ February 6 & 7
Hunter Kurtz, Brandon Prince, and Dom Radeka will be there to talk realities behind the programs!
🔗🔗 www.cactuscon.com
 bugcrowd
@Bugcrowd
From financial services to global enterprises, every organization is vulnerable.
Every. Single. One. ☝️
That’s why Bugcrowd's 2026 Inside the Mind of a Hacker Report is your new BFF. We surveyed 2,000 hackers, and they’re showing exactly how they think, adapt, and operate today.
As @davegerryjr, CEO of Bugcrowd, puts it, this report uncovers the human side of modern threats.
Take a look 👀⤵
www.bugcrowd.com/resources/report/inside-the-mind-of-a-ha…
bugcrowd reposted
bugcrowd
@Bugcrowd
Want to iterate on Nuclei templates faster? ⚡
AI can draft templates directly from vulnerability descriptions.
It won’t replace reasoning, but it will remove YAML friction and speed up detection.
Check it out👇
cloud.projectdiscovery.io/templates
 bugcrowd
@Bugcrowd
AI isn't just a trend, it’s the new standard. 82% of hackers have already integrated AI into their workflow, moving from experimentation to 24/7 automation.
The race is on.
 bugcrowd
@Bugcrowd
Why the shift?
74% of hackers say AI has increased their value. By automating "the boring stuff," they can focus on high-level creative problem-solving.
Top use cases:
✅ Instant code analysis
✅ Automated recon scripts
✅ Real-time research
bugcrowd
@Bugcrowd
Get the full breakdown in our latest report: Inside the Mind of a Hacker 2026.👇
www.bugcrowd.com/resources/guides/inside-the-mind-of-a-ha…
bugcrowd
@Bugcrowd
Protect it at all costs.
 bugcrowd
@Bugcrowd
With ticket scams, fake apps, and phishing campaigns ramping up around events like the 2026 Winter Olympics, the advice is still surprisingly simple. 😌↓
As @treyford puts it: if it sounds too good to be true, it probably is! 💯
Attackers rely on urgency, hype, and trust gaps. Awareness remains one of the most effective defenses 🏂
Read more in Secure World Magazine: www.secureworld.io/industry-news/cyber-threats-milano-cor…
bugcrowd
@Bugcrowd
Manual recon doesn’t scale, especially for hidden URLs.
This one-liner surfaces endpoints you didn’t know existed. 👇
 bugcrowd
@Bugcrowd
Inside the Mind of a Hacker is a Bugcrowd staple, and this year’s edition reflects a threat landscape that never slows down. 🏃🏻♂️💨
Security isn’t static. Attackers adapt in real time, and with AI in the mix, they’re moving faster, operating continuously, and learning as they go. 🚌
🤨 If you’re especially interested in how AI is showing up in hacker workflows, skip ahead to Chapter 3 (though we’d definitely recommend reading the whole thing).
📙 Download your copy here: www.bugcrowd.com/resources/report/inside-the-mind-of-a-ha…
bugcrowd
@Bugcrowd
Most people miss this one 👀
Spot the bug 🐞
⭐Bonus: what’s the impact?
 bugcrowd
@Bugcrowd
One submission a day keeps the blues away 😌
🐛💰: bugcrowd.com/user/sign_up
bugcrowd reposted
 Ben Sadeghipour
@NahamSec
Just got my hands on @Bugcrowd’s 2026 Inside the Mind of a Hacker Report, the original hacker survey where hackers like me share who they are , where we’re hacking from, what motivates us, and how we are leveraging AI! Check it out for yourself 👉🏼 www.bugcrowd.com/resources/report/inside-the-mind-of-a-ha…
 bugcrowd
@Bugcrowd
Security alignment doesn’t break down at the controls level, it breaks down at the communication level. ☎️⛓️💥
As @treyford notes, cyber risk committees create space for business leaders to actively participate in risk trade-offs, investment decisions, and acceptance of exposure. That alignment shouldn’t start at QBRs—it should be continuous and intentional. 🔁
The goal is to have clarity around what matters, why it matters, and what’s needed next. Learn more in Secure World Magazine: www.secureworld.io/industry-news/decoding-ciso-cfo-discon…
bugcrowd
@Bugcrowd
Information sharing has always been part of security—but trust is the real limiter. ⚓️
According to @treyford, formal, government-backed channels tend to create implicit trust between organizations. The most valuable insights often come from candid conversations between peers sharing real failures, staffing challenges, and live incident response lessons.
That kind of trust is hard to automate, but critical as threats move faster. 🙌
SecurityWeek's full piece: www.securityweek.com/cyber-insights-2026-information-shar…
bugcrowd
@Bugcrowd
Think you know Python? Try this one👇
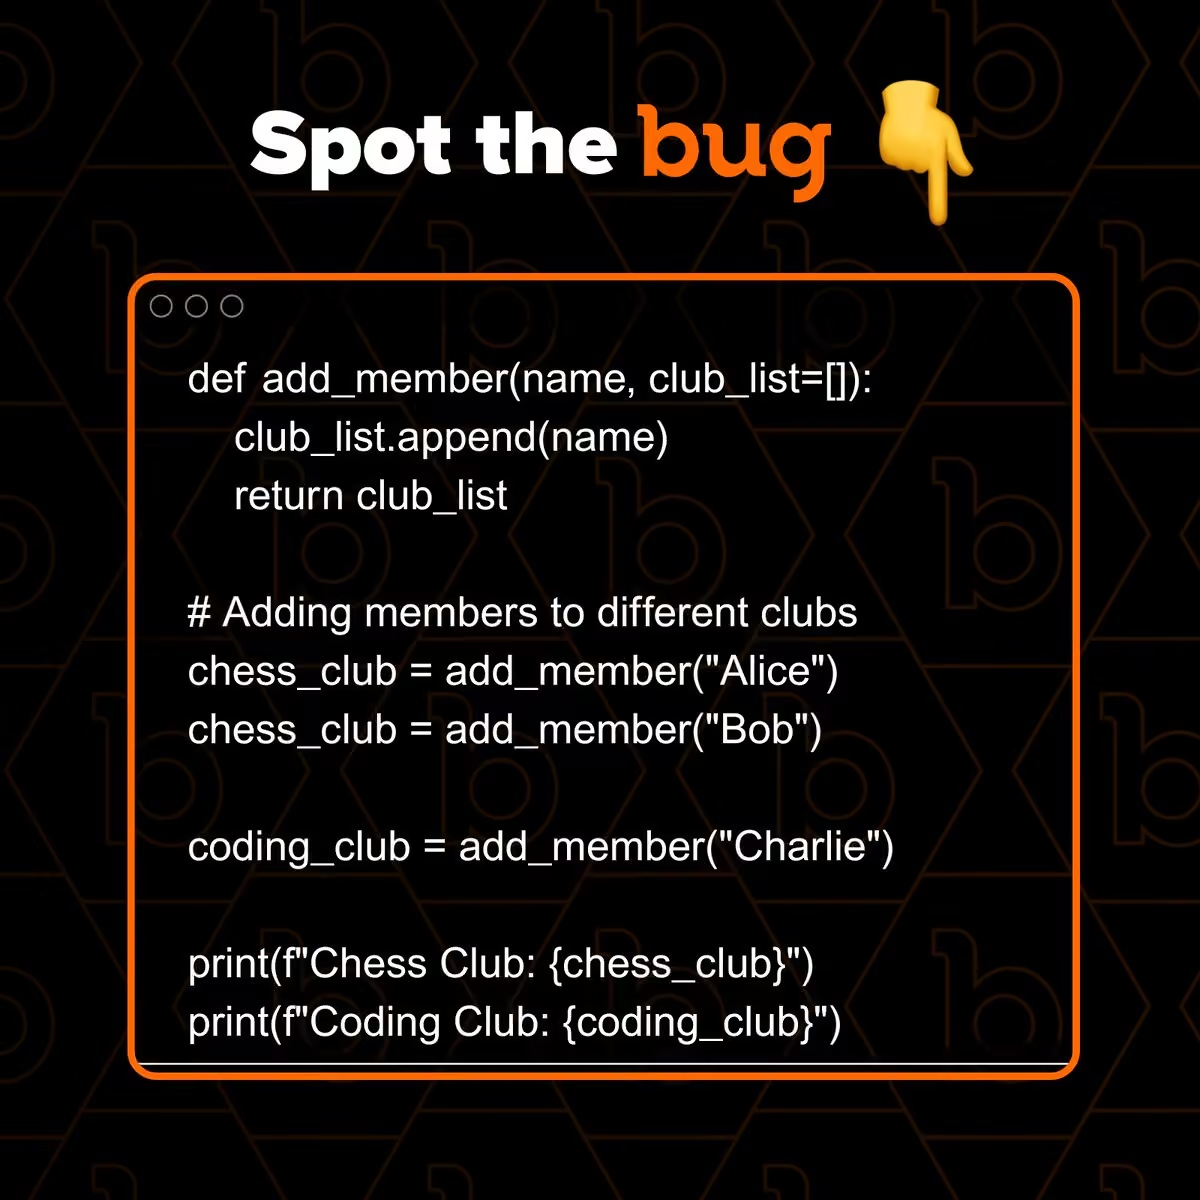
bugcrowd reposted
 Bishal Shrestha
@bishal0x01
Thank you @Bugcrowd for this cool swag!
 bugcrowd
@Bugcrowd
You can’t predict the security landscape. But you don’t have to navigate it alone!
Security has never been a solo sport. The Crowd works in teams, combining different skills and perspectives to cover what one person can’t. 🏔️
👥 See why human collaboration still matters when AI is part of the toolset: www.bugcrowd.com/resources/report/inside-the-mind-of-a-ha…
#bugcrowd #itmoah

bugcrowd reposted
bsysop
@bsysop
@Bugcrowd Inside the Mind of a Hacker is out! 🚀🔥
Honored to be featured alongside @_godiego__ and @sw33tLie 🔥
Check it out 👇www.bugcrowd.com/resources/report/inside-the-mind-of-a-ha…
#bugbounty #bugcrowd #insidethemindofhacker
 bugcrowd
@Bugcrowd
📲 1 new message: Bugcrowd’s Inside the Mind of a Hacker Report just dropped and it’s SO GOOD.
↪ That’s exactly what your group chat is about to look like—especially when you see that 98% of hackers say they’re proud of the work they do. 🧡
Not to toot our own horn, but this year’s edition is that good 💁♀️
And yes, wishes are being granted because this report pulls insights from 2,000+ hackers, sharing what motivates them, how they work, and how they’re using AI 🤯🤯
Ok ok ok, we’ll let you get into it now. Don’t forget to tell us what your fave part is!
Download your copy (it’s freeeeeeee 😍): www.bugcrowd.com/resources/report/inside-the-mind-of-a-ha…
 bugcrowd
@Bugcrowd
What is the most 'out-of-the-box' bypass you’ve ever found that actually worked?
👇👀
bugcrowd
@Bugcrowd
Being scammed can leave you feeling powerless 😥
For Chinedu Nkem, it sparked something else entirely—a decision to learn how attacks happen and help protect others from the same experience. ❤️🔥
As part of that journey, he spent the day learning from Ciarán “monke” Cotter, one of Ireland’s top bug bounty hunters and an ethical hacker with Bugcrowd.
Lots of powerful lessons and moments came out of that day, thanks to Chinedu! It’s all in here: www.bugcrowd.com/blog/lifechanging-lectures-my-day-with-a…
 bugcrowd
@Bugcrowd
You, me, we—us. We all still need human judgment to assess risk 🧑🧑🧒🧒
AI can speed things up, but deciding what poses real business risk still comes down to human insight.
🎙️→ That’s exactly what Julian Brownlow Davies, SVP of Offensive Security & Strategy at Bugcrowd, talked about on the @DtSR_Podcast, how human creativity and experience, paired with AI, is what actually moves security forward.
🎧 Full podcast episode: www.buzzsprout.com/2153215/episodes/18498795
Bugcrowd is sharing more on this tomorrow in a BIGGG way 👀⏰
bugcrowd
@Bugcrowd
🗞️ As governments evaluate the risk of connected electric buses, the concern isn’t dramatic Hollywood-style takeovers. It’s quieter threats like data exfiltration, surveillance, ransomware, and fleet-wide compromise.
As @caseyjohnellis explains, these risks reflect broader IoT realities: complex systems, sensitive data, and attackers looking for scale, not spectacle. 💡
Full analysis in Dark Reading: www.darkreading.com/cyber-risk/chinese-electric-buses-aus…
bugcrowd
@Bugcrowd
POV: You just found our Engagement Page with lots of bug bounty programs.😼
Check it out👇
bugcrowd.com/engagements?category=bug_bounty&page=1&sort_…
 bugcrowd
@Bugcrowd
🃏 Tricking the Cache: Deception, poisoning, and the techniques that still surprise teams.
All with Benjamín Muñoz → youtu.be/04k7O7fwFmo
bugcrowd
@Bugcrowd
If you’re evaluating new approaches to security testing, we have something that might help. 🕵️♀️
Financial services teams face constant regulatory pressure while attack surfaces continue to grow. Leading organizations use Bugcrowd to complement audits and internal testing with continuous, crowdsourced security! 🙌
Learn why continuous testing is becoming the standard in financial services: www.bugcrowd.com/blog/navigating-financial-services-regul…
bugcrowd
@Bugcrowd
Reply with your answer👀👇
 bugcrowd
@Bugcrowd
In a recent Security Boulevard article, Bugcrowd Founder @caseyjohnellis shares why ethical paths matter 💭
“Providing a white-hat outlet for young people with these skills helps them understand legal and ethical boundaries.”
Hacking groups are recruiting younger talent, and arrests alone won’t stop it. Reducing attacker incentives is key. More insights:
securityboulevard.com/2026/01/were-hiring-hacking-groups-…
bugcrowd
@Bugcrowd
🧼 Identifying vulnerabilities early keeps security programs clean, leading to reduced exposure and clearer prioritization.
See how security teams describe their results: www.bugcrowd.com/customers/
 bugcrowd
@Bugcrowd
How can a hacker take over an account with just one link?
That's the power of Cross-Site Scripting (XSS).
In this episode, we'll demystify this common vulnerability and show you exactly how to find and report it as a bug bounty hunter.
You'll learn:
📙 The crucial difference between Reflected vs. Self-XSS and which one is a reportable bug.
📙 How to outsmart common filters and get your malicious script to run.
📙 Where to focus your efforts to find XSS bugs that others miss.
Mastering XSS is a powerful skill for any bug bounty hunter.
Watch the full video here 👇
youtu.be/-MsjH-Ypekk
bugcrowd
@Bugcrowd
A technical issue alone does not = risk.
Clear business impact is what makes a bug bounty report actionable 🎬
Here’s how to ensure that impact is understood: www.youtube.com/watch?v=vN-t9FWdcsA&t=2s
bugcrowd
@Bugcrowd
NASA recently recognized an independent researcher who responsibly disclosed four vulnerabilities, all fixed before they were exploited.
The story highlights why strong vulnerability disclosure programs matter, not just for finding issues, but for building trust with the global research community. 👏
Read more, including perspective from Bugcrowd’s @treyford: securityboulevard.com/2026/01/turkish-security-researcher…
bugcrowd
@Bugcrowd
Bugcrowd's excited to join NASS Winter Con this year. ❄️
State leaders face growing pressure to keep critical systems secure, available, and trustworthy. We’re looking forward to conversations around strengthening defenses for citizen-facing services and election infrastructure! 🏢
Connect with Johnny Curran and Brendan Campbell from our team, January 28–31: www.nass.org/events/nass-2026-winter-conference
 bugcrowd
@Bugcrowd
Want to uncover a target's hidden attack surface? 🔎
GAU (GetAllURLs) is a must-have.
It fetches known URLs from AlienVault, Wayback Machine, and Common Crawl—letting you find parameters, sensitive files, and forgotten endpoints without sending a single request to the target.
Why it’s a P1 goldmine:
✅ Hidden Endpoints: Finds old APIs and documentation.
✅ Parameter Mining: Perfect for finding potential XSS/SQLi entry points.
✅ Passive Recon: Discovery at scale without triggering WAFs.
Check it out👉 github.com/lc/gau
 bugcrowd
@Bugcrowd
🧣 Warm up your skills. The Fireblocks Web Managed Bug Bounty is now public!
Enterprise-grade digital asset infrastructure with real-world targets and ongoing testing. Yaaaa, we’re talking to you, blockchain hackers. 🧱
With rewards up to $12K, the program is live and accepting submissions: bugcrowd.com/engagements/fireblocks-mbb-og
 bugcrowd
@Bugcrowd
Credential exposure rarely stays small.
Reports show ESA email credentials ended up on the dark web, leading to hundreds of GBs of data loss. This is how identity issues turn into real exposure.
The full coverage: www.space.com/space-exploration/esa-email-credentials-on-…
bugcrowd
@Bugcrowd
Security teams aren’t being measured by speed alone anymore.
Here’s what will define security performance in 2026, according to Bugcrowd’s Senior Vice President of Offensive Security and Strategy, Julian Brownlow Davies 👇
 bugcrowd
@Bugcrowd
 bugcrowd
@Bugcrowd
Get the full predictions on our blog: www.bugcrowd.com/blog/2026-cybersecurity-predictions/{TIMESTAMP_EPOCH}
bugcrowd reposted
 Sam Houston
@samhouston
Oh we lived and died by canva back then
Also I have tons of photos on Google Photos


 bugcrowd
@Bugcrowd
Attackers are already using AI to move faster, blend in, and scale attacks.
This post breaks down what that looks like in practice, using real patterns security teams and researchers are seeing now.
🧯 Faster phishing, malware, and recon
🧯 Deepfakes and voice cloning are harder to spot
🧯 Static defenses fall behind adaptive threats
🤿 Dive in: www.bugcrowd.com/blog/ai-is-the-new-magical-master-key-ho…
 bugcrowd
@Bugcrowd
OAuth device code phishing is increasing, especially against M365 accounts, by abusing trusted authentication flows. 🎣
These attacks succeed by blending in and relying on user action rather than technical exploits.
Share with your friends responsible for identity security or user awareness: securityboulevard.com/2025/12/surge-of-oauth-device-code-…
bugcrowd
@Bugcrowd
Vibe coding is great until you realize your AI is a "yes-man" that prioritizes vibes over security audits.
 bugcrowd
@Bugcrowd
Check out this blog to learn how to better approach vibe coding without leaving the door wide open👇
www.bugcrowd.com/blog/your-code-has-vibes-my-exploits-hav…
bugcrowd
@Bugcrowd
🏋️♀️ As AI moves into OT environments, many systems are being pushed beyond what they were built to secure.
The article highlights the growing tension between modernization and resilience in critical infrastructure where uptime comes first.
This is a valuable perspective for anyone working at the intersection of AI, OT, and critical systems: securitybuzz.com/cybersecurity-news/ai-is-moving-into-ope…
bugcrowd
@Bugcrowd
Pen testing demand is up. Budgets are not.
Buyers are stuck choosing between expensive consulting or low-value, point-in-time tests. ⚖️
Bugcrowd PTaaS delivers expert-led testing on demand, so teams can test more often, focus on real risk, and stay within budget.
Learn how >> www.bugcrowd.com/products/pen-test-as-a-service/
bugcrowd
@Bugcrowd
Looking for your first bug? Start with IDORs.
Insecure Direct Object References (IDORs) are a type of broken access control vulnerability and a perfect starting point for beginners. They're logic flaws, not technical exploits, which means they don't require deep expertise to find.
In this video, you'll learn:
📙 What IDORs are and how they work.
📙 The two-account testing method.
📙 Where to look for them.
📙 Why IDORs are great for beginners
IDORs can range from low to critical severity, so mastering them is a great way to start building your bug bounty portfolio.
Watch this video for a step-by-step guide to finding your first IDOR vulnerability. 👇
youtu.be/kYetdP8K2IA
bugcrowd
@Bugcrowd
Financial services organizations are constant targets due to the sensitive data they hold and their expanding attack surfaces.
As regulations evolve, teams must balance compliance with uninterrupted operations. 🔄
Learn how financial services leaders use Bugcrowd to reduce risk across critical assets and meet evolving security expectations: www.bugcrowd.com/blog/navigating-financial-services-regul…
bugcrowd
@Bugcrowd
AI is changing how attacks are built, tested, and reused.
Experts point to AI lowering the barrier for attackers while raising the bar for defenders. Faster reconnaissance, smarter phishing, and adaptive tooling are becoming standard faster than many teams are ready for.
Trying to understand what AI actually changes in day to day security work is what we're all doing, so this is a read for you (yes, you 🫵): techinformed.com/ai-cybersecurity-threats-2026-what-exper…
bugcrowd
@Bugcrowd
🤝 Place your bets. How many seconds until AI is mentioned?
Julian Brownlow Davies joins the @DtSR_Podcast to talk red teaming, third-party testing, and why security decisions still come down to judgment.
🎧 Episode 688 is live and the perfect listen on your lunch:
bugcrowd
@Bugcrowd
2026 in security through the eyes of Bugcrowd’s Chief Strategy and Trust Officer, @treyford 🔮
 bugcrowd
@Bugcrowd
 bugcrowd
@Bugcrowd
Read how our leadership team is thinking about what comes next: www.bugcrowd.com/blog/2026-cybersecurity-predictions/{TIMESTAMP_EPOCH}
bugcrowd reposted
bugcrowd reposted
bugcrowd reposted
R4CK4TT&CK
@R4CK4TT4CK
Name the film, & TY for tye Trucker Cap @Bugcrowd 🥰
www.linkedin.com/posts/michaelrack_dear-bugcrowd-thank-yo…
bugcrowd
@Bugcrowd
This is how we imagine your New Year’s resolutions look:
📝 hack on bugcrowd 3x a week
📝 write reports so clean triage sheds a tear
📝 give the social media manager a break (pls no more swag dms)
📝 follow the proper steps for support on subs and account issues
📝 crack the top 100 on the leaderboard by year’s end
Manifesting bugs, bounties, and better reports ✨
 bugcrowd
@Bugcrowd
Some threats are loud. Others are quietly being built years in advance 👀
From quantum computing to nation state activity and dark AI, this article explores how the threat landscape is scaling faster than most defenses. Automation and sophistication are increasing, while the line between experimentation and exploitation continues to blur.
If your planning horizon stops at the next quarter, this article is a useful reset: techinformed.com/cybersecurity-predictions-2026-quantum-t…
bugcrowd
@Bugcrowd
Attacks on operational technology and supply chains continue to rise, stretching the attack surface across IoT devices, pipelines, and water systems.
According to @davegerryjr, CEO of Bugcrowd, critical infrastructure will remain a top target in 2026, especially where hardware security and legacy systems intersect.
If you work anywhere near infrastructure, supply chains, or systems that cannot afford downtime, read the full article: www.scworld.com/feature/critical-infrastructure-facing-cy…
bugcrowd
@Bugcrowd
We’ve all been there. An unexpected pop quiz. Nobody likes an unwanted test 😭
Quarterly security assessments are the same. They’re a snapshot. Threats don’t follow schedules.
Bugcrowd RTaaS delivers continuous, adaptive attack simulations that reflect how attackers actually operate.
👉 Book a Red Teaming session: www.bugcrowd.com/try-bugcrowd/
 bugcrowd
@Bugcrowd
Need to map an entire network range? 👀
Angry IP Scanner is the tool you need. It’s lightweight, fast, and works on any OS.
What it does:
✅ Scans fast: Uses multithreading to check IP ranges in seconds.
✅ Finds details: Grabs hostnames, MAC addresses, and open ports.
✅ Flexible: Export your results to CSV or TXT for your report.
Whether you're hunting for hidden dev servers or just auditing your home Wi-Fi, this is a must-have for the toolkit.
Learn more here👇
www.bugcrowd.com/glossary/angry-ip-scanner/
bugcrowd
@Bugcrowd
3, 2, 1... 0 👀🎉
The wait’s officially over. Bugcrowd is thrilled to announce the acquisition of @MayhemSec!
This marks a strategic investment in the power of combining human ingenuity with AI. It underscores our dedication to progressing cybersecurity innovation for customers and hackers.
See how we’re building the industry’s first adaptive security platform: www.bugcrowd.com/blog/bugcrowd-acquires-mayhem-security-r…
#bugcrowd #ingenuityunleashed #mayhemsecurity
bugcrowd
@Bugcrowd
Want to get to grips with @Burp_Suite?
@insiderPhD has created this Burp Suite guide that you need to check out!
What's covered?
🪲 Setting up
🐛 Key features
🐞 Tips for beginners
Watch now! 👇
www.youtube.com/watch?v=ltgfOgN1GIo
bugcrowd
@Bugcrowd
@Masonhck3571, Application Security Engineer here at Bugcrowd, gave a great presentation at the @NatUniv of San Diego last night! 👏
We love engaging with students about the opportunities and possibilities in #bugbounty and #cybersecurity. 📚

 bugcrowd
@Bugcrowd
5 major companies, 1 epic panel 🔥
Our VP of Operations, @codingo_, joined an elite panel at Bug Bounty Village @defcon with leaders from @yeswehack, @synack, @Hacker0x01, and @intigriti.
What an honor to shape the future of #cybersecurity with our new besties! 🫶📈
 bugcrowd
@Bugcrowd
🤩🤩🤩
bugcrowd
@Bugcrowd
How are your #iot skills? Put them to the test with @BitdefenderBOX #bugbounty program: bgcd.co/2CLNV8Y
 bugcrowd
@Bugcrowd
New @BitdefenderBOX public #bugbounty program now live on @Bugcrowd! See program details here: bugcrowd.com/bitdefenderbox2 #ittakesacrowd #outhackthemall
 bugcrowd
@Bugcrowd
[Spotlight] Help improve the security of @SecureDrop, report bugs to their bug bounty: bgcd.co/1MR4BOc
 bugcrowd
@Bugcrowd
Check out Bugrowd's new ongoing bug bounty programs! bgcd.co/1FwnVcy


 Edinburgh Napier University Security Society


 Abdelhy khaled🦅


