Politicians, athletes, journalists, NGOs, companies... They all use
corporation-owned social networks to communicate with us. Citizens
shouldn't have to hand over their data to companies to read content
published by public entities. Public Feeds changes that by making posts
of popular accounts freely available.
Read more.
HashiCorp
HashiCorp, Inc. is an American software company and subsidiary of IBM based in San Francisco, California. IBM completed its acquisition of HashiCorp on 27 February 2025 in a transaction valued at US$6.4 billion. HashiCorp provides tools and products that enable developers, operators and security professionals to provision, secure, run and connect cloud-computing infrastructure. It was founded in 2012 by Mitchell Hashimoto and Armon Dadgar. The company name HashiCorp is a portmanteau of co-founder last name Hashimoto and Corporation. More on Wikipedia
AI can help infrastructure teams break out of the operational loop. 🔁
Join HashiCorp experts Cole Morrison and Kyle Ruddy at @awscloud re:Invent to see how AI can work through infrastructure iterations while engineers step back in when a real decision needs them.
See the pattern in action with Terraform, Vault, Kubernetes, Amazon Bedrock, AgentCore, and more. ibm.co/6016EnriY
AI is changing how developers manage infrastructure, but how do you automate more without sacrificing security and control?
Join HashiCorp at @AWScloud re:Invent for two technical sessions:
🔹 COP347-S | AI at full speed without crashing See how Terraform, Vault, Kubernetes, Amazon Bedrock, AgentCore, and @IBM Concert connect infrastructure automation, security, and application context across hybrid environments.
🔹 DVT218-S | Let AI drive the infrastructure loop Explore how AI can handle routine infrastructure iterations so engineers can spend less time troubleshooting and more time building.
Two sessions. Real-world use cases. More automation, less operational overhead. ibm.co/6011Enyj9
AI agents are moving fast. Enterprise security and governance need to keep up.
As organizations scale agentic AI, they need a way to establish identity, control access, and maintain visibility across a growing ecosystem.
🔐 HashiCorp Vault uses @IBM Agent Identity to give each agent a governed identity 🛡️ Vault extends secrets management to AI agents with least-privilege access and real-time revocation for unauthorized actions 🔎 @IBMwatsonx Orchestrate is designed to unify agent discovery, containment, and evaluation across @awscloud Bedrock, @Microsoft Foundry, and @Google Gemini
The goal: move from simply deploying AI agents to governing and securing them at scale. ibm.co/6016EVIug
With the acquisition of AuthMind, IBM is expanding HashiCorp Vault’s approach to securing the agent lifecycle, helping organizations protect credentials and secrets not only when they are issued, but as agents use them across applications, tools and data. ibm.co/6018EnKbO
Combined with IBM Concert’s application and infrastructure context, teams can focus remediation on proven risk instead of chasing every vulnerability. ibm.co/6016EV7om
Terraform and @IBM Concert are better together 💜 🤝
IBM Concert Protect helps organizations discover vulnerabilities and determine which findings represent real-world exposure. Terraform provides the infrastructure context and governed execution layer needed to take the next step.
Together, they connect discovery → prioritization → remediation, helping teams translate vulnerability insights into policy-driven, controlled infrastructure changes across complex environments. ibm.co/6013En1oF
Enterprise identity and access models are evolving for the agentic era.
🍎 Join us in New York City with HashiCorp Field CTO Steve Wilson for an executive discussion and private roundtable exploring how autonomous agents, non-human identities, and machine-speed access are reshaping enterprise security.
Learn how organizations can align identity, access, runtime security, and governance to scale agentic AI securely. ibm.co/6013EVf21
AI agents are introducing a new infrastructure operating model: one where machines can reason about infrastructure and take action alongside humans.
Join us in this webinar to explore how Terraform can support governed, autonomous infrastructure with trusted infrastructure context, controlled workflows, guardrails, and lifecycle management.
Learn what it takes to move from human-driven automation toward autonomous operations. ibm.co/6014EVf1k
This release advances secure, resilient connectivity for modern applications while introducing new building blocks for agentic workloads.
What’s new:
• Expanded API Gateway support for HTTP/2, gRPC, external authorization, and processing • Localized DNS to improve application resilience during certain control-plane disruptions • Native nftables support for transparent proxy traffic redirection • Hybrid post-quantum TLS key exchange and FIPS 140-3 Enterprise builds • Agentic runtime fabric (beta) for governing connectivity between AI agents, MCP servers, and inference models
See what’s new in Consul 2.1.0 and what to consider before upgrading. ibm.co/6010EV74e
Bring it to booth #1022 at @AWScloud re:Invent. HashiCorp and @IBM experts will be there to talk through your hybrid cloud challenges and explore what comes next. ibm.co/6013EV2cc
AI development introduces more credentials across models, cloud infrastructure, databases, and developer tooling. That makes managing the full secrets lifecycle increasingly important.
With Vault and Vault Radar, teams can:
🔎 Discover unmanaged secrets across code, Git history, and collaboration tools 🔐 Bring replacement credentials under centralized secrets management 🔄 Sync Vault-managed secrets to supported platforms without embedding them back into source code ⏱️ Reduce reliance on long-lived credentials with dynamic or short-lived secrets where supported
Secret discovery identifies the exposure. Secrets management helps prevent it from becoming the same problem again. ibm.co/6015EVf0V
Your cloud strategy should move your business forward. 📈
Schedule a one-on-one meeting with HashiCorp experts at @AWScloud re:Invent to explore how your team can deliver infrastructure faster, reduce security risk, and better control cloud costs. Bring your priorities, and we'll talk through practical next steps toward your business goals. ibm.co/6016EV22C
Finding exposed secrets is only the first step. How quickly can your organization actually remediate them?
Secrets remediation maturity looks at how effectively you close the gap between detection and risk reduction, from remediation speed and ownership to audit readiness.
Answer eight questions to see where your organization stands and identify your next steps. ibm.co/6019EVIOx
The Terraform policy agent is now generally available, helping teams convert existing Sentinel and OPA policy libraries into Terraform policy without manually rebuilding every policy. 🎉
The agent uses a staged conversion workflow to:
📋 Interpret the intent and requirements of existing policies 🛠️ Generate HCL-based Terraform policies and corresponding tests 🔎 Validate resources and attributes against Terraform provider schemas 🧪 Run tests and report passed and failed scenarios 👀 Keep humans in the loop before policies are enforced
Experience a faster, reviewable path for bringing existing governance logic into Terraform workflows. ibm.co/6016EVfia
HashiCorp Vault Enterprise is now available as a fully managed service on @IBM Cloud. 🔐
IBM Cloud Secrets Manager Vault Dedicated combines Vault Enterprise capabilities with dedicated, single-tenant IBM Cloud infrastructure, IBM-managed operations, and enterprise support.
The result: a simpler path to enterprise-grade secrets management and machine identity, with less responsibility for deploying and managing the underlying service.
For organizations modernizing security operations, governing hybrid environments, or securing AI initiatives, this brings Vault Enterprise to IBM Cloud through a fully managed experience. ibm.co/6015EV2j5
Visit @IBM booth #1022 for live Terraform, Vault, and HCP demos designed to help teams accelerate infrastructure delivery, secure access, and simplify AWS operations.
Connect with HashiCorp experts, explore practical solutions for your environment, and plan your visit: ibm.co/6017EV2kB
Cryptographic risk doesn’t stop at secrets and encryption. 🔐
As hybrid and multi-cloud environments grow more complex, security teams need visibility and governance across the full lifecycle of cryptographic assets.
Join us for episode 2 of our webinar security series to explore how organizations can:
• Discover cryptographic assets across environments • Assess and reduce cryptographic risk • Strengthen secrets and key management with Vault • Build a more continuous approach to cryptographic governance • Prepare for emerging post-quantum threats
📅 Tuesday, November 17 | 12 p.m. ET ➡️ Register here: ibm.co/6017EVN3d
Shorter certificate lifecycles and evolving cryptographic standards are raising the bar for PKI management. 👀
Vault 2.2 helps organizations modernize their approach with automated public certificate lifecycle management, centralized visibility and governance, and new capabilities for crypto-agility and post-quantum readiness. ibm.co/6014EVIOO
AI agents can move infrastructure operations at machine speed. The challenge is doing it without sacrificing control.
Scaling agentic infrastructure operations requires trusted context, standardized workflows, and governance built into every action.
⚡ Move faster with AI-driven operations grounded in trusted infrastructure context 🔐 Reduce risk by embedding security and compliance policies directly into workflows 🔎 Scale with confidence while maintaining visibility, governance, and human oversight
Move faster without leaving security, compliance, or control behind with Terraform. ibm.co/6013EVI3N
Infrastructure automation changed how organizations provision and manage infrastructure. Now, AI agents are changing who, or what, operates it.
The next challenge is autonomy: How do you enable agents to act safely within defined guardrails?
Giving agents infrastructure access isn’t enough. They need trusted context to understand their environment, governed workflows to turn decisions into action, and continuous governance to maintain trust and control as infrastructure evolves.
Three fundamental barriers stand in the way. Find out what they are: ibm.co/6015EVxbX
Looking to standardize infrastructure automation across your organization?
Whether you're exploring infrastructure as code for the first time or looking to scale existing practices, Terraform provides a consistent workflow for provisioning and managing infrastructure across cloud, hybrid, and on-premises environments.
Choose the path that's right for you: ✅ Learn with on-demand and live sessions ✅ Build hands-on skills in workshops ✅ Apply what you've learned with a free trial ✅ Connect with experts to explore your next steps
Missed HashiConf at @IBM TechXchange? We’ve got you covered. 🎥 Catch up on the latest Vault, Terraform, and IBM integration announcements, hear directly from HashiCorp experts, and see new capabilities in action in the session recordings. ibm.co/6011EVxw5
Infrastructure automation and managing infrastructure at scale were top of mind for us at HashiConf at @IBM TechXchange. 💭
Keep the conversation going in this webinar with Jacob Plicque, Sr. Technical Product Marketing Manager at HashiCorp. Dive deeper into how Terraform and HCP can automate infrastructure, networking, security, and applications at scale. 🤩 ibm.co/6015EVsAU
Catch up on the biggest Terraform, Vault, Boundary, and agentic AI announcements from the week:
• Terraform advances infrastructure lifecycle management for the agentic era: ibm.co/6015EVl8B • Strengthen security for agentic AI with new Vault, Verify, Boundary, and Secure Hub capabilities: ibm.co/6016EVl88 • Vault Enterprise 2.2 advances identity security, PKI, and crypto-agility: ibm.co/6017EVl8D • Announcing the public preview of Secure Hub: Govern Vault at scale: ibm.co/6015EVl8B • Read about all announcements: ibm.co/6018EVl8E
Explore the highlights and see what’s next for infrastructure and security. 👇
Terraform provides the foundation for agentic infrastructure lifecycle management. Swipe through to see how Terrform can connect trusted context, governed self-service, and infrastructure intelligence for autonomous operations. 👉 ibm.co/6013EVYa5
Catch up on the biggest Terraform, Vault, Boundary, and agentic AI announcements from the week:
• Terraform advances infrastructure lifecycle management for the agentic era: ibm.co/6010EVsBp • Strengthen security for agentic AI with new Vault, Verify, Boundary, and Secure Hub capabilities: ibm.co/6011EVsBV • Building self-service into Terraform: Introducing Terraform Developer Portal: ibm.co/6012EVsBn • Vault Enterprise 2.2 advances identity security, PKI, and crypto-agility: ibm.co/6013EVsBX • Announcing the public preview of Secure Hub: Govern Vault at scale: ibm.co/6014EVsBk • Read about all announcements: ibm.co/6015EVsBZ
Explore the highlights and see what’s next for infrastructure and security.
AI agents are moving fast. Enterprises need the visibility and control to move with confidence.
Announced at IBM TechXchange, @IBM Agent Identity gives every AI agent a governed identity, while HashiCorp Vault provides scoped, short-lived credentials so agents can securely access the systems they need. IBM watsonx Orchestrate brings third-party agents into one control plane to help teams discover, secure, and evaluate them at scale. 🔐
Learn how IBM and HashiCorp are helping make agentic AI ready for the enterprise. ibm.co/6012EVYxm
Terraform Developer Portal is now in public preview ✨🥳
Getting infrastructure shouldn’t require a scavenger hunt through modules, workspaces, and organizational standards. 🔎
Terraform Developer Portal (TDP) brings governed self-service directly into HCP Terraform, giving platform teams a way to define approved infrastructure patterns that developers and agents can easily consume.
What’s new in Vault? With updates for identity security, crypto agility, IBM Power integration, and Secure Hub, read how to create centralized visibility and governance across Vault environments in our blog 👉 ibm.co/6018EVYUC
Just announced at HashiConf at IBM TechXchange: new Terraform capabilities for the agentic era, including Terraform policy, intent-driven workflows for @IBM Z and LinuxONE, and Terraform Developer Portal. Explore what’s new. 👉 ibm.co/6012EVYsm
Do you have spooky secrets still lurking in your hybrid cloud environments? 👻 HashiCorp can help keep your cloud estates safe from threats in the darkness. 🔦
What happens when you connect vulnerability detection, infrastructure intelligence, and AI-assisted automation?
In this demo, @IBM Concert Protect identifies a vulnerability, Infragraph traces it back to the underlying infrastructure and Packer image, and IBM Bob works with HCP Terraform to deploy the updated infrastructure. The result: the vulnerability is remediated and verified.
See the workflow in action 👇 Then read more about announcements from HashiConf at IBM TechXchange. ibm.co/6011EVlES
Boundary 1.1 is now generally available, expanding access security to agentic identities, improving administrative for enterprise scale, and enhancing external integration.
Boundary also introduces an MCP server, currently in public preview, which is used to help reduce administrative tasks and facilitate agentic access. 🔐
Read more about what's new in Boundary from HashiConf at @IBM TechXchange. ibm.co/6010EViMA
The Boundary MCP server is now in public preview. Simplify management and troubleshooting on the control plane while securely connecting AI agents to infrastructure on the data plane. The result is easier integration with less complexity for teams adopting agentic workflows. ✅
Still have room in your HashiConf at @IBM TechXchange agenda? Add these sessions to your schedule:
🔐 Securing AI agents with Boundary [TEC-3140] 🛡️ Post-quantum cryptography with Guardium and Vault [LAB-2345] 🏗️ From golden image to golden path: Standardize infrastructure delivery [DMO-5581] 🤖 First-look live demo: Build, govern, and scale infrastructure in the agentic era [DMO-6016] 🔑 End-to-end cryptographic lifecycle management with Guardium, Vault and transparent data encryption [LAB-4073]
Explore the full session catalog and build your agenda. ibm.co/6010EVigy
HashiCorp Vault and @IBM Agent Identity integrate with @NVIDIA OpenShell secure runtime software, the foundation of the NVIDIA OpenShell Architecture.
Together, they pair a protected environment for agents to run in with a verified identity and short-lived credentials for every agent, so each action can be traced, limited and reviewed. Read more: ibm.co/6018EVYJi
Now in public preview, Secure Hub gives teams centralized visibility across their Vault environments, making it easier to monitor operational health, understand usage, and manage security resources from one place.
Learn how Secure Hub helps you govern Vault at scale. ibm.co/6019EVYgd
Enhanced search with Terraform policy is now in public preview. Discover unmanaged infrastructure, evaluate resources against policy, and bring them under Terraform management through one integrated workflow.
Gain greater visibility and make it easier to reduce risk across your infrastructure estate. 👀 Learn what’s new in Terraform and agentic infrastructure lifecycle management. ibm.co/6015EVY6T
Terraform intent-driven workflows are now in private preview for @IBM Z and LinuxONE. 🔎
Bring discovery, rehearsal, and simulation into Terraform workflows so teams can explore and validate changes before applying them to mission-critical infrastructure.
Learn what’s new for infrastructure lifecycle management for the agentic era. ✨ ibm.co/6012EViB8
The Terraform Developer Portal is now in public preview. 🚀
Extend HCP Terraform with governed self-service, giving developers and AI agents an easy way to find and use approved infrastructure patterns through the tools and interfaces where they already work. Move faster while maintaining consistent standards and control.
Read about all new Terraform announcements made at HashiConf at @IBM TechXchange. ibm.co/6011EVcC7
The remote MCP server for Terraform is now in public preview. 🙌
Connect AI agents to HCP Terraform without requiring developers to install or maintain an MCP server locally. This makes it easier to bring governed infrastructure workflows into AI-powered development experiences. 🔌
Learn what’s new for agentic infrastructure lifecycle management. ibm.co/6018EV9h0
Announced at HashiConf at @IBM TechXchange, this release gives AI agents secure identities, automatically renews credentials, and advances quantum-ready encryption.
It also deepens integration across the IBM ecosystem, including support for Vault on IBM Power, while improving usability, automation, and operational visibility. Oh, and dark mode. 🌙
The opening general session at HashiConf at @IBM TechXchange is starting shortly.
Tune in to explore how agents are changing the way applications are built and work gets done across the enterprise. 🌐
Expect live demos, real-world examples, and a first look at the latest from IBM and HashiCorp, plus practical insights into bringing these technologies together to turn agentic potential into enterprise impact. Watch here: ibm.co/6015EVihZ
Soon we'll be welcoming the HashiCorp community to Atlanta for a week packed with product sessions, technical deep dives, hands-on labs, and opportunities to connect with peers.
Safe travels, and we'll see you at HashiConf at @IBM TechXchange! 👋 🛫
Just 3 days until HashiConf at @IBM TechXchange! 🎉
That means you have 3 more days to make plans with your friends attending, build your agenda, and finish packing. 👀
We can't wait to welcome practitioners, industry leaders, and HashiCorp enthusiasts from around the world for a week of learning, connection, and community.
Your application needs a secret to get its secrets. 🤫
Vault 2.2 introduces vTPM Support for Linux VMs, replacing distributed bootstrap secrets with authentication tied to an enrolled virtual TPM. See what changes for your on-prem workloads. ibm.co/6013EVke1
There are plenty of ways to experience HashiConf at IBM TechXchange. 👋
🤔 Can’t make it to Atlanta? Register for the livestream and catch HashiConf from wherever you are: Register for the livestream
Tune in to select sessions to learn: ⏭️ What’s next for the enterprise tech stack 📚 Which skills developers will need over the next two years in the age of AI 🌐 How to make agents work effectively across enterprise hybrid cloud environments What it takes to build responsible AI systems
Joining us in Atlanta? Build your agenda now to make the most of your time at TechXchange: Build your agenda ibm.co/6017EVr9R
Vault 2.2 helps teams adopt, operate, and scale security with confidence.
Explore a more intuitive user experience, smarter upgrade planning, expanded feature adoption automation, and consistent security practices across @IBM and hybrid environments. ibm.co/6011EVTyH
Enterprise trust is evolving with AI, agent identity, and the shift to quantum-safe security.
Ahead of HashiConf at @IBM TechXchange, explore how HashiCorp Vault and IBM Cryptography Manager can help uncover cryptographic risk, automate lifecycle management, and prepare for a quantum-safe future. ibm.co/6016EVuZo
Planning to certify at HashiConf at IBM TechXchange? Start with our curated roadmap of exam objectives, learning content, and supporting resources.
Looking for a smarter way to study? Feed the exam content list into @IBM Bob and prompt it to generate practice questions based on the exam objectives. It's a great way to turn the exam blueprint into an interactive study session. 🤖
The future of intelligent operations is taking shape ahead of HashiConf at @IBM TechXchange. 🚀
In this interview with @theCUBE, Outbound CTO, IBM Automation Tyler Lynch explores how AI agents, infrastructure context, and financial accountability come together to drive business outcomes, including how HCP Terraform powered by Infragraph can provide a shared view of infrastructure dependencies and help teams understand the impact of change.
Get a preview of the conversations shaping IBM TechXchange 2026, then join us at the event to explore what’s next for AI and infrastructure. ibm.co/6016EVrhI
Building enterprise AI means building for a world that keeps changing. 🏗️
Across data, models, infrastructure, and hybrid environments, there’s no single blueprint. Real-world practitioner experience can help organizations navigate that complexity and move from experimentation to operational reality.
See what’s ahead at HashiConf at @IBM TechXchange with VP of Enterprise Software, Bruno Aziza, in this interview with @theCUBE. ibm.co/6011Ep7zW
Vault 2.2 automates public certificate lifecycle management, modernizes PKI, and improves crypto-agility and post-quantum readiness. See how to reduce risk and simplify security across the autonomous hybrid cloud. ☁️ ibm.co/6012EVuTm
Vault 2.2 brings SCIM to GA and strengthens non-human identity controls, helping teams automate lifecycles, enforce least privilege, and securely govern human, machine, and AI agent identities at scale. ibm.co/6017EVJzR
The future of intelligent operations is taking shape ahead of HashiConf at @IBM TechXchange. 🚀
In this interview with @theCUBE, HashiCorp Field CTO Tyler Lynch explores how AI agents, infrastructure context, and financial accountability come together to drive business outcomes, including how HCP Terraform powered by Infragraph can provide a shared view of infrastructure dependencies and help teams understand the impact of change.
Get a preview of the conversations shaping IBM TechXchange 2026, then join us at the event to explore what’s next for AI and infrastructure. ibm.co/6014EVyCo
Vault 2.2, now generally available, secures AI identities, automates secrets and certificates, advances post-quantum readiness, and standardizes security across enterprise environments. ibm.co/6016EVGDk
AI won’t make the hybrid world less complex. The opportunity is learning how to master it.
As AI agents operate across data, applications, and infrastructure, enterprises need to rethink how they approach access, oversight, and operational control.
IBM VP Bruno Aziza explores what it takes to orchestrate AI for the hybrid enterprise.
Read more and watch the full interview to get a sneak peek of what you'll hear at HashiConf at @IBM TechXchange. ibm.co/6013Ep71D
Banking security is no longer just about managing human access.
As cloud, automation, and AI reshape financial services, applications, workloads, services, and AI-enabled systems all need secure access to critical resources.
How can financial institutions maintain control, compliance, and auditability as operations move at machine speed?
Learn how to secure access across cloud, AI, and hybrid environments. 🔐 ibm.co/6015EVD6h
A multibillion-dollar global retailer strengthens its industry foothold through self-service and automation with HCP Terraform. See how Skechers did it: ibm.co/6010EpQF4
Discover how Terraform MCP Server helps AI agents make better infrastructure decisions using trusted organizational context and guardrails with these four real-world AI infrastructure patterns. ibm.co/6014EpQ0n
In @theCUBE’s AI Operating Model series in partnership with IBM, technology leaders unpack what it takes to move from experimentation to enterprise-scale production, from agentic workloads and hybrid infrastructure to data sovereignty, identity, automation, and continuous governance.
🎥 Get a sneak peek of what to expect at HashiConf at IBM TechXchange with IBM VP Bruno Aziza as he explores how organizations can operationalize AI while navigating rapid model change and growing agent scale. ibm.co/6014EpAFM
Managing infrastructure at scale doesn't have to mean more operational toil. Learn how Benchling transformed its Terraform workflows, centralized governance, and saved an estimated 8,000 developer hours across its engineering organization. ibm.co/6010EpQm4
Lab-based exams will be offered on Monday, October 26 only. Availability is limited, so register before October 24. All other exams are available on a walk-in basis during the conference.
AI agents are reshaping how infrastructure is managed, but autonomy without governance creates new operational risks.
To scale autonomous infrastructure with confidence, organizations need seven foundational layers:
1️⃣ Infrastructure as code: Standardize how infrastructure is defined and provisioned. 2️⃣ Source of truth: Establish a unified view of infrastructure state and dependencies. 3️⃣ Policy enforcement: Embed governance directly into infrastructure workflows. 4️⃣ Agentic workflows: Enable AI agents to operate within governed, auditable processes. 5️⃣ Self-service: Provide approved infrastructure patterns on demand. 6️⃣ Visibility & observability: Deliver continuous insight into infrastructure state, risk, and cost. 7️⃣ Lifecycle management: Continuously optimize infrastructure to improve efficiency, control costs, and reduce operational overhead.
Together, these capabilities provide the consistency, visibility, and control required to scale autonomous infrastructure operations across hybrid and multi-cloud environments. Learn more: ibm.co/6015EpQYN
AI agents can now provision, modify, and manage infrastructure at machine speed. Your operating model needs the governance, visibility, and control to keep up.
Build the foundation for autonomous infrastructure: ibm.co/6016EpQcm
Learn how intent-driven workflows introduce a new interaction model for Terraform for Z and LinuxONE, helping organizations modernize infrastructure operations through guided, repeatable agentic workflows. ibm.co/6016EptF4
There's a ton to explore at HashiConf at IBM TechXchange besides just product sessions. Make sure to put time aside in your conference schedule to check out our activations:
🏁 RoboRally A community favorite is back. Flex your competitive side as you challenge Developer Advocates on our robot racetrack in the HashiConf Zone.
🥳 LAN Party Take a seat at one of our retro computers and jump into a game with the people around you. It’s a throwback to the days when getting together to game meant actually getting together.
🔦 Lightboard videos in the Sandbox Studio See technical concepts come to life in the Sandbox Studio. Watch experts break down complex ideas using a digital lightboard, turning technical topics into visual stories that are easier to understand.
Securing the agentic enterprise starts with identity.
Every enterprise is racing to put AI agents into production, but almost none of them have decided who’s accountable when an agent does something wrong. Vault 2.1 gives platform and security teams a way to answer that question before they get asked in an incident review. Read more: ibm.co/6013Epwjd
Infrastructure leaders are rethinking how they scale securely.
At the Frankfurt stop of the Agentic Runtime Security Exchange, hear real-world stories from Ömer Korkmaz of Delivery Hero, Giancarlo Longobardi of Deutsche Börse, and Daniel Neumann of LeanIX on building secure, scalable, and compliant infrastructure with Terraform and Vault.
🇩🇪 Join us to learn how leading organizations are approaching automation, governance, and security as they scale their infrastructure and prepare for the next generation of AI-driven operations. ibm.co/6015Eprd5
A community favorite is back. Flex your competitive side as you challenge HashiCorp Developer Advocates on our robot racetrack in the HashiConf Zone. 🏁 🏎️
Learn more about what's happening at HashiConf at @IBM TechXchange, and make sure to get your ticket if you haven't already! ibm.co/6015EpP1V
Terraform 1.16 adds destroy-time Actions and reusable imports in child modules, keeping more infrastructure lifecycle operations in Terraform. ibm.co/6015ET2Tt
New and exciting changes are coming to HashiCorp certifications! Discover what's next for developers and infrastructure engineers in this webinar.
We'll discuss the up-leveling of our existing lab-based certification exams for Vault and Terraform to a new Advanced category, and how it makes way for our new Terraform exam, coming this fall.
📆 Wednesday, September 30 | 1 p.m. ET Register now: ibm.co/6018ETAce
Two communities. One big week. HashiConf is now part of @IBM TechXchange, with more ways to build, secure, and deploy infrastructure at scale. ✨
Join developers, security teams, and IT leaders to sharpen your skills, get hands-on with new releases, connect with experts, and learn from your peers.
FYI, Early bird pricing for HashiConf at IBM TechXchange is ending soon. Register today to get the best pricing possible for your ticket. 👀 ibm.co/6014ET2c8
AI agents are changing infrastructure operations. Learn the foundation needed to scale autonomy with confidence and what’s ahead at HashiConf and @IBM TechXchange 2026. ibm.co/6011ET2kB
If you're still deciding what to add to your HashiConf at @IBM TechXchange agenda, here are a few of our picks ⬇️
• Designing a production-grade Vault architecture on IBM Z and @RedHat OpenShift [TEC-3413] • Deploy regulated AI workloads with Vault and Terraform policy-as-code [LAB-2990] • Securing AI agents with Boundary [TEC-3140] • Applying zero trust principles to Red Hat Ansible Automation Platform with Vault [TEC-3038] • Securing AI agents at scale: Vault, Terraform & @IBMwatsonx Orchestrate [LAB-2479]
With two dedicated session tracks of hybrid cloud management and security & governance, and over 100 HashiCorp product sessions, there's something for every practitioner.
Modernizing zero trust. Governing AI agents at runtime. Scaling agentic AI securely.
As AI agents gain access to enterprise systems and data, organizations need new approaches to security and governance.
Join @IBM and HashiCorp experts, Field CTOs, and industry peers to discuss how leading organizations are managing identity, access, and trust in the age of agentic AI.
Terraform provider for @GoogleCloud 8.0 is now GA, with expanded infrastructure discovery workflows, modernized defaults, and updates to keep the provider aligned with how Google Cloud services are evolving. ibm.co/6017ETfeX
Agentic AI introduces autonomous agents that can make decisions, access systems, and take action with minimal human intervention.
But without the right identity, access, and governance controls, AI innovation can outpace security.
🇩🇪 Join industry peers and HashiCorp Field CTO, Anna McDougall, in Frankfurt to discuss how organizations are securing agentic AI deployments, addressing non-human identity challenges, and building the foundation for responsible AI scale. ibm.co/6012ETFQn
Hybrid infrastructure, multi-cloud environments, and AI-driven operations are changing the requirements for privileged access.
Learn how modern approaches can reduce risk, strengthen governance, and simplify secure access at scale.
Watch this webinar to learn how to: 🙅♀️ Eliminate broad network access and reduce dependence on long-lived credentials 💪 Improve auditability and support compliance with session monitoring and RDP session recording 👩💻 Simplify secure access across multi-cloud and Kubernetes environments while maintaining consistent security controls ✅ Prepare for emerging identity and governance challenges as AI agents become operational actors
70 HashiCorp sessions. 35 HashiCorp hands-on labs. 105 total opportunities to learn more about Terraform, Vault, AI operations, hybrid cloud, identity security and more. 🥳
Attend sessions at HashiConf and IBM TechXchange like... 💸 FinOps and cloud cost discipline 🛠️ Day 2 operations with Terraform and Vault 🔐 Securing AI agents and machine identities ☁️ Running AI workloads across hybrid cloud environments 🛡️ Quantum readiness 🌳 IT efficiency and sustainability
HCP Terraform is making policy as code easier to adopt with a native pre-written policy experience. Browse and select pre-written, HashiCorp-managed policies directly in a policy-set workflow without manually sourcing or authoring every policy. Read more ➡️
The full HashiConf at @IBM TechXchange agenda is now live!
With more than 70 HashiCorp sessions and 35 hands-on labs, you'll have plenty of opportunities to deepen your product knowledge, connect with HashiCorp experts, and gain practical skills you can apply with your team.
You'll also have access to 1,000+ sessions and activities across five technical tracks at IBM TechXchange, making it easy to customize your experience and explore the topics that matter most to you.
Turn infrastructure intent into governed Terraform action on @IBM Z and LinuxONE. New intent-driven workflows guide teams through Terraform tasks to help mainframe operators adopt consistent infrastructure-as-code practices with confidence. Read more ➡️ ibm.co/6018ETV5Q
Let's geek out together at HashiConf at @IBM TechXchange! 🤓
This year's session topics include: 💼 Day 2 operations with Terraform and Vault 🌱 IT efficiency, resilience, and sustainability ✅ Quantum readiness 💰 FinOps and cloud cost discipline Identity security and managing AI agents
Head to our website to get more info on session content and get your tickets. ibm.co/6015ET8Fc
Identity security is top of mind for lots of developer teams and organizations, so make sure you have this session on your list to attend at HashiConf at IBM TechXchange.
Swipe and see how Grupo Madero built identity resilience with IBM Verify, and then learn more at HashiConf:
Gain deeper visibility into your HCP Terraform-managed estate. Pull operational metrics from a single Prometheus-compatible endpoint into the visualization tools you already use. Read more ➡️ ibm.co/6019ETBxU
Discover how teams at American Honda Motor Inc used Terraform, Vault, @RedHat Ansible, and FinOps tooling to drive cost accountability across complex @awscloud environments in this session at HashiConf at @IBM TechXchange.
Your HashiConf conference pass is waiting for you! Register now: ibm.co/6016ErMKC
Agentic AI is changing how software interacts with infrastructure. Security models need to evolve with it.
Join us in Singapore with Technical Field Strategy Director, Oscar Medina, for a hands-on workshop exploring how to secure AI agents with trusted identities, just-in-time access, authorization guardrails, and governance controls.
Learn practical approaches for building secure, scalable agentic systems in enterprise environments.
Amid India’s regulatory wave, a common security control set is emerging. See how Vault, Boundary, and Consul help organizations implement it. ibm.co/6012EryBK
✅ 70 HashiCorp sessions. ✅ 35 HashiCorp hands-on labs. ✅ 105 total opportunities to learn more about Terraform, Vault, AI operations, hybrid cloud, identity security and more. 🥳
👀 Find the right sessions for you at HashiConf. Get a sneak peek at the agenda and register today: ibm.co/6016ErwLM
Secrets management doesn't have to be complicated. 👀
Join our Vault Quickstart workshop and learn how to securely store, access, and manage secrets across your infrastructure.
You'll learn Vault best practices, security lifecycle management core concepts, and how to manage the full lifecycle of secrets, certificates, passwords, and keys.
Your mainframe may be modernizing. Is your access model keeping up? Learn how HashiCorp Boundary brings identity-based access, just-in-time credentials, and centralized visibility to mainframe environments. Read the blog ➡️ ibm.co/6017Eru5S
Enhanced native support for agentic identity access management is now generally available in HashiCorp Vault. Read on to learn more ➡️ ibm.co/6015Eru55
Innovation is driven by the people challenging what's possible. 💭
At the @awscloud Ambassador Global Summit, Dr. Rahul Gaikwad, HashiCorp's first AWS Ambassador and a Staff Resident Solutions Architect at @IBM, presented "When Infrastructure Fixes Itself!", showcasing how Agentic AI and HCP Terraform can help organizations build self-healing infrastructure and more autonomous cloud operations.
Rahul specializes in AI, cloud architecture, DevOps, and platform engineering, helping enterprises build scalable, automated cloud platforms. He holds a Ph.D. in AIOps and is recognized for his contributions to technology, research, and the global cloud community.
His presentation received the Best Presenter Award, and he was also recognized as an Agentic AI L300 Expert and AWS Ambassador Golden Jacket All-Star.
Congratulations to Rahul on these accomplishments and for helping advance the conversation around the future of cloud operations. 👏
HashiCorp Validated Designs now make it easier to find field-tested guidance for deploying, operating, and using HashiCorp products in production. Read the blog ➡️ ibm.co/6014ErPLE
Provisioning is just the beginning. What happens next?
Many @awscloud environments are built with infrastructure as code, but operational challenges often emerge after deployment. Infrastructure drift, secrets sprawl, fragmented workflows, and governance gaps can introduce complexity as environments scale. Explore how organizations are approaching AWS lifecycle management from Day 0 provisioning through Day 2 operations and beyond. ibm.co/6018ErMnr
Stream HCP Vault Dedicated Audit logs to Microsoft Sentinel, and deploy the pipeline with Terraform. No native connector needed — just a generic HTTP sink and an Azure Function that forwards logs into Log Analytics. Full walkthrough: ibm.co/6016ERh9Y
This session with Ritesh Hegde will show a real production outage and how it reveals the risks of infrastructure drift and long-lived credentials.
Learn how Terraform and Vault work together to detect drift, automate operations, and secure infrastructure with short-lived AWS credentials and zero secrets left behind.
Register for HashiConf at IBM TechXchange conference 2026: ibm.co/6015ERhP5
Secrets management doesn't have to be complicated. 👀
Join our Vault Quickstart workshop and learn how to securely store, access, and manage secrets across your infrastructure.
You'll learn how Vault best practices, security lifecycle management core concepts, and how platform teams can enable workflows to protect sensitive data with a system of record and manage the full lifecycle of secrets, certificates, passwords, and keys.
As AI adoption accelerates, managing privileged access is becoming more complex. 😵💫
Learn how to modernize access management across hybrid cloud and AI environments, reduce reliance on long-lived secrets, and strengthen security posture.
Cloud adoption is only as strong as the foundation it's built on.
Join us to learn how platform, infrastructure, and security teams are creating scalable cloud foundations with automation, policy, and self-service. Get practical insights you can apply across your cloud environment. You'll learn:
✅ A deeper understanding of cloud infrastructure and the Terraform ecosystem ✅ Best practices for infrastructure lifecycle management ✅ Advanced features like policy as code, state management, and collaboration workflows ✅ How platform teams enable developers across business units
Make the most of your conference experience with certification testing on-site at HashiConf at @IBM TechXchange! 🤓
Each HashiConf attendee can take up to two certification exams at no additional cost, making it easier to validate your skills and advance your career. 💯
HashiCorp certification offerings include: 📝 Terraform Associate (004) 📝 Terraform Authoring & Operations Professional with AWS 📝 Vault Associate (003) 📝 Vault Operations Professional
Manage credential risk across core, digital systems, and payment at scale. 💸
Banks are not starting from zero, exposure is already known.
The focus is shifting to how remediation is operationalized across systems without disrupting critical services.
Establish visibility with Vault Radar, automate credential workflows with Vault, and apply policy-driven controls across hybrid and cloud environments. ibm.co/6017Eu0sT
Come learn something you'll actually use at HashiConf at @IBM TechXchange 😉 ✨ Join sessions on:
💸 FinOps and cutting cloud costs 🛠️ Day 2 operations with Terraform and Vault 🔐 Securing AI agents and machine identities ☁️ Running AI workloads across hybrid cloud environments
Grab your ticket now and lock in early bird pricing: ibm.co/6018Eu02C
Looking for ways to level up on your HashiCorp product skills?
Check out some of our upcoming webinars and workshops and choose the best sessions for you ⬇️
🛣️ Paved path for agents: Platform engineering an observable AI stack on AKS with HCP Terraform: August 18 Dynamic provider credentials with HCP Terraform and Vault on AWS: August 19 🔎 Detect, prevent, and remediate secret sprawl with Vault Radar and AWS: Monday, August 24 🤫 From secrets to sessions: Modernizing privileged access for hybrid cloud and AI: September 9 🧢 HCP Terraform and Red Hat Ansible workshop: September 10
What happens after exposed credentials are discovered? Financial institutions are evaluating how to move from credential discovery to repeatable remediation processes across applications, infrastructure, payment systems, and cloud environments. How is your organization approaching the challenge? Explore more: ibm.co/6011Eu0iF
How do you maintain control as agentic AI scales across your organization?
Join security leaders and technology executives at the HashiCorp Agentic Runtime Security Exchange for peer discussions on the future of AI-enabled infrastructure security.
Upcoming locations include: 🇮🇳 Mumbai | 13 August 🇹🇭 Bangkok | 20 August 🇯🇵 Tokyo | 26 August 🇮🇩 Jakarta | 10 September 🇺🇸 Chicago | 16 September 🇺🇸 Minneapolis | 17 September
See more cities in the series and register now: ibm.co/6015ER1Ol
The best infrastructure ideas aren't built in isolation.
Join thousands of practitioners at HashiConf at @IBM TechXchange to learn how teams are scaling platform engineering, securing infrastructure, managing secrets, and automating cloud operations with Terraform, Vault, and more. ✨
See what fellow builders are creating. Register today. ibm.co/6013ER1M7
Curious about what you'll hear at HashiConf at @IBM TechXchange conference 2026? We just released some of featured sessions and speakers on our website, like:
• Bridging IT automation and FinOps to drive cloud cost discipline at scale • From deployed to governed: Day 2 operations with Terraform & Vault with SPH Media Pte Ltd. • Vault, SPIFFE, and the identity crisis of AI agents • AI agents all the way down: Enforcing and tracking agent identity and delegation
Get more details about these sessions and start building your agenda now. Full agenda coming soon: ibm.co/6013EuaIW
Still rotating local account passwords manually? Learn how Vault Enterprise manages local OS credentials as secrets, enabling automated rotation and centralized credential management across large server fleets. 🌐
AI coding agents now author Terraform, open changes, and trigger runs at machine speed. That loop was built for a human author.
HCP Terraform is the managed control plane that governs every agent-authored run, anchoring context, enforcing policy, scoping identity, and keeping an audit trail. Learn more: ibm.co/6018EuSqo
Terraform Stacks are a feature intended to simplify infrastructure provisioning and management at scale, providing a built-in way to scale without complexity. This blog covers the challenges Terraform Stacks solve, their benefits, use cases, how they work, their features, and future roadmap. ibm.co/6018EumLg
Every workload in your Consul service mesh trusts a CA, but is it one your security team governs?
🚀 Consul now integrates with CyberArk Workload Identity Manager to issue and auto-rotate mesh certificates, anchoring trust in PKI you already audit and control. Read how it works: ibm.co/6011Eum2J
Official Helm charts for the Boundary controller and worker are now available, bringing Kubernetes-native deployment to both self-managed and HCP Boundary environments. Read more ➡️ ibm.co/6015EujbR
Infrastructure data silos make it difficult to understand what's happening across hybrid and multi-cloud environments, driving complexity, risk, and cost. 🤔
HCP Terraform powered by Infragraph helps teams gain greater visibility into their infrastructure. Learn more:
Agentic AI systems are creating an explosion of non-human identities, many of them over-privileged and secured with static credentials.
That combination introduces new risks, from credential leakage to unauthorized access at machine speed.
In this webinar, HashiCorp and AWS experts Nicholas Jackson, David Mills, and Nic Gumina will discuss: • Why traditional IAM and perimeter security struggle in agentic architectures • How dynamic, short-lived credentials reduce risk • What identity-first security looks like for autonomous agents • How to apply zero trust principles across modern AI systems
Terraform AzureRM 5.0 is now generally available, with more control over Resource Provider registration, opt-in Azure preflight validation, and the removal of long-deprecated resources and properties. Review the upgrade guide before moving from 4.x. ➡️ ibm.co/6014EuuPA
New in Terraform Stacks: Automate approved Day 2 workflows with Terraform actions, and adopt Stacks more confidently with a clearer, lower-risk path for migrating existing workspaces. Learn more ➡️ ibm.co/6016EP7ln
Infrastructure teams can deploy cloud resources in minutes, but understanding the financial impact often takes weeks.
Discover how Terraform and Cloudability bridge that gap in this blog. You’ll learn:
💰 What the cost visibility gap really means 🩹 Common FinOps pain points 👀 How to bring cost visibility into the Terraform workflow 💸 The benefits of integrated cost governance 💪 Post-deployment optimization and cost management strategies
Infrastructure challenges are rarely unique to one team.
At this HashiCorp User Group meetup in Singapore, practitioners share real-world lessons, implementation strategies, and experiences building and operating cloud infrastructure at scale.
If you're working with Terraform, platform engineering, or cloud automation, this discussion offers practical insights from peers in the field. See talks like:
🛠️ Engineering "Invisible" platforms with Crossplane and Score 🤖 Terraform at scale: Architecture, automation, and AI-assisted @awscloud delivery Enable zero trust for service connectivity across hybrid cloud with Consul
As AI accelerates software development, the challenge is preventing, prioritizing, and remediating leaked credentials. Learn how HCP Vault Radar can help. ibm.co/6014EuzIa
Terraform is helping platform teams scale with confidence through new capabilities like workspaces and Stacks restore, monorepo support for Stacks, and registry tagging with project registry view. ibm.co/6013EuKCh
AI agents are beginning to participate directly in infrastructure operations — from provisioning resources and responding to incidents to executing remediation workflows.
But most infrastructure operating models weren't designed for environments where changes occur at machine speed. ⚡️
Learn about the foundational layers required to scale autonomous infrastructure without sacrificing governance, visibility, and control. ibm.co/6014EPI8G
Don't hesitate to get your early bird ticket to HashiConf at @IBM TechXchange! 🐣
If you've been thinking about getting a ticket, now is the perfect time to buy. These prices won't be around for long, so get your conference pass at the cheapest rate while you still can. 👀
AI coding assistants like Claude Code, GitHub Copilot, IBM Bob, and others can help you write Terraform faster, but they are only as good as the context they have.
In this video, Bryan Krausen shows how the Terraform MCP server helps fix that.
You'll see how MCP gives your coding assistant live access to Terraform Registry documentation, provider docs, modules, and policies so it can generate more accurate Terraform code with fewer hallucinations. ibm.co/6013EPwvV
AI can generate infrastructure. The harder problem is ensuring it follows your organization's standards.
The Terraform MCP Server provides AI agents with authoritative context from Terraform workflows, modules, policies, and infrastructure configurations, helping improve decision quality and reduce operational risk.
This post walks through four real-world patterns teams are using today:
• AI-guided no-code infrastructure consumption • Self-service deployments using approved registry modules • Policy-aware workflows with Sentinel and OPA • Enterprise-scale orchestration with Terraform Stacks
See how practitioners are building governed AI-assisted infrastructure workflows with Terraform. ibm.co/6019EPwkX
Get the latest benchmark insights into HashiCorp Vault Enterprise on HashiCorp Validated Designs for AWS, highlighting how KV, SSH, and PKI workloads perform as concurrency increases. ➡️ ibm.co/6014EPe5y
Encryption is only as strong as its keys. Explore the public beta of Vault Kubernetes key management for centralized encryption at rest. Learn more ➡️ ibm.co/6011EPwld
Platform engineers often manage hundreds or thousands of servers across various data centers. Manually logging into each system to update local account passwords is time-consuming, difficult to scale, and creates security risks.
In this demo, learn how the Vault Enterprise local account password rotation plugin closes this gap by treating local OS credentials as managed secrets within Vault. Teams can automate password rotation for local accounts using the same workflows they already use to manage database credentials or cloud IAM roles. ibm.co/6013EPDtv
The post-quantum era is coming, but migration isn't the first step.
Before organizations can adopt post-quantum cryptography, they need visibility into where cryptographic assets exist, what they protect, and which systems face the greatest risk.
Learn why discovery, prioritization, and crypto agility are critical to building a successful post-quantum strategy. ibm.co/6019EPwZU
Many organizations rely on multiple secrets management tools, which can cause secret sprawl across different systems, files, and repositories. As secrets become harder to manage, teams often rely on long-lived static credentials that increase security risk.
In this demo, learn how to get started with secrets sync and replace static credentials with short-lived access in AWS Secrets Manager. ibm.co/6012EPwkG
HCP Terraform powered by Infragraph uses a query interface to allow users to view and search through their data. It enables users to build queries to gain insights about their infrastructure estate through low code and JSON queries with future support for NL2Q.
Teams are already using Infragraph queries to answer critical operational questions in seconds. Read more: ibm.co/6017EOFpW
Join thousands of practitioners, developers, and IT leaders at HashiConf at @IBM TechXchange this October in Atlanta. See what's next for cloud infrastructure and security. 👀
The super early bird rate won't be available for much longer. Get your ticket at it's lowest rate now. ibm.co/6012EOFMK
Audit logs alone may not satisfy compliance requirements. 🚫
Organizations often need visibility into not just logins, but also the commands and actions performed during a user session.
Boundary supports RDP and SSH session recording, helps deter malicious behavior, expedite the remediation of a breach, and helps organizations meet compliance by recording all user activity during RDP and SSH sessions. Watch it in action: ibm.co/6013EOhoD
Resilient recording framework. Stronger auditability. Less operational pain. See how Boundary helps teams maintain trusted, durable records of privileged activity. ibm.co/6011EOFyl
Building AI on @Microsoft Azure? Make sure your infrastructure can keep up. 🏁
Join Kerim Satirli for a technical session on building secure, scalable foundations for AI workloads with Azure. Learn how infrastructure as code and automated security practices can help platform teams standardize deployments, enforce governance, and reduce operational complexity.
What you'll learn: • Key considerations for AI-ready infrastructure on Azure • How infrastructure as code simplifies provisioning and operations • Approaches for consistent security and governance across environments • Best practices for secrets, access, and compliance management • Ways to streamline operations and support AI growth at scale
Automate user and group provisioning on HCP with SCIM to reduce manual overhead, improve security, and keep access in sync with your identity provider. Learn more ➡️ ibm.co/6011EOFEP
HCP Terraform powered by Infragraph connects directly to your cloud and infrastructure sources to map out relationships and surface insights. Today, you can leverage connectors across environments like AWS and Azure, bringing together infrastructure, configuration, and state data into a unified graph view.
Learn more about Infragraph now in limited availability: ibm.co/6012EOcaK
What if your Terraform plan could tell you more than what's visible at first glance? 🔎
In this video, you'll learn how Terraform MCP and LLM reviews can help uncover production-breaking changes before deployment. See how teams can shift DevOps left, reduce risk, and build secure, modern infrastructure faster. ibm.co/6016EOcjk
HashiConf at @IBM TechXchange conference 2026 will be here sooner than you think!
Super early bird pricing won't be around much longer, so don't miss your chance to get tickets while prices are at their lowest. Register today! ibm.co/6016EOioE
How do you secure autonomous infrastructure while enabling innovation?
The HashiCorp Agentic Runtime Security Exchange Series is an exclusive forum for enterprise leaders navigating the realities of agentic AI, non-human identities, governance, and auditability.
Join peer-level discussions led by HashiCorp Field CTOs to exchange ideas, compare approaches, and help shape what's next.
See the next events and register to attend a city near you: ibm.co/6017EOigz
🇦🇺 Canberra, Australia | 28 July 🇹🇭 Bangkok, Thailand | 20 August 🇻🇳 Hanoi, Vietnam | 24 September
Plus, be on the lookout for events in Mumbai, Stockholm, Bengaluru, and more coming soon!
AI initiatives are accelerating infrastructure sprawl across Azure environments. Learn how Terraform helps platform teams discover unmanaged resources, reduce drift, and establish continuous governance so cloud and AI workloads remain secure, visible, and under control.
The enterprises pulling ahead aren’t just experimenting with AI. They’re operationalizing it.
@IBM and HashiCorp are helping organizations tackle one of the defining challenges of the AI era: operationalizing AI, data, and agents across fragmented hybrid environments while maintaining governance, resilience, flexibility, and control.
AI is rapidly becoming the new interface for infrastructure, but LLMs are non-deterministic systems. Without access to trusted organizational context, AI agents can generate inconsistent, non-compliant, or misleading infrastructure recommendations.
In this blog, we explore four real-world ways engineering teams are using the Terraform MCP Server to help AI agents make better infrastructure decisions:
✅ Testing and validating no-code modules ✅ Building compliant environments from approved modules in the Private Module Registry ✅ Accelerating governance workflows with Sentinel or OPA ✅ Scaling landing zones and multi-environment deployments with Terraform Stacks
The real value of MCP isn’t helping AI do more, it’s helping AI make better decisions by grounding it in trusted infrastructure context. ibm.co/6019EOPRW
Access paths that align with your organization’s infrastructure — from global to project boundaries, target aliases bring structure, simplify access, and help Boundary scale without friction. ibm.co/6014EOznK
Boundary 1.0 expands compliance with RDP session recording, improves usability with grants builder, and increases scale with scoped aliases. Also, let’s have a peak at how Boundary can help secure AI agent access as we prepare for a new agentic era. ibm.co/6017EOzVZ
Cluster DR (public preview) for HCP Vault Dedicated gives teams a faster failover path for cluster-level failures, service instability, and security response scenarios, extending resilience beyond infrastructure-only recovery. ibm.co/6016EO8DY
AI is changing the interface to operations, not the lifecycle itself. In an agentic world, infrastructure and security lifecycle management become one operating model built for safe automation.
See how to build out Agentic Lifecycle Management for your organization.
Secrets detection is no longer the problem. Scalable remediation is.
Teams can now identify exposed secrets across code, pipelines, and developer environments with high accuracy, but many still struggle to operationalize remediation, creating a growing gap between visibility and risk reduction.
This e-book breaks down how to close that gap and build a remediation strategy that actually scales.💡
⬇️ Download it to learn how to:
• Align security and development teams for accelerated secrets remediation • Measure remediation progress with metrics tied to real risk reduction • Build scalable, audit-ready remediation workflows across environments • Prioritize high-impact exposures using secrets correlation to reduce attack surface
What's new with Terraform + Ansible? From the Terraform Ansible Collection 2.0 powered by pyTFE to an enhanced Terraform actions experience, we're continuing to simplify infrastructure automation across the entire lifecycle. ibm.co/6012E3qA6
tfctl is the first dedicated CLI for HCP Terraform and Terraform Enterprise, giving engineers and AI agents safe, full-coverage access to the platform API. Check out our blog to learn more ➡️ ibm.co/6014E3qMk
Join this upcoming session on June 18 to understand what sets Professional-level certifications apart and how to approach the lab-based exam environment with confidence.
Hear directly from Gary Larizza, Software Developer at IBM, and get your questions answered live.
In this session, you’ll: • Learn what makes Professional exams unique • Get an overview of the hands-on lab environment • Ask your questions and get expert guidance
Want to use SPIFFE without turning your first step into a full runtime migration? See how to leverage HashiCorp Vault as both an identity issuer and an identity broker to manage the complete SPIFFE authentication and authorization lifecycle, with clear guidance on where SPIRE fits. ibm.co/6013E3ZuX
How do you secure and govern autonomous infrastructure without slowing innovation? 💭
The HashiCorp Agentic Runtime Security Exchange Series brings together enterprise leaders for discussions on the realities of agentic AI and non-human identities. 🗣️
Led by HashiCorp Field CTOs, each session is designed for peer exchange. No pitches. No fluff. Just practical conversations on what comes next.
Interested in attending? See the next few global sessions and sign up for an event near you: ibm.co/6011EM0o3
🇻🇳 Hanoi, 23 June with Jerome Walter 🇳🇱 Amsterdam, 23 June with Christian Schwarz 🇯🇵 Tokyo, 26 June with Seigo Kawamura 🏴 London, 25 June with Richard Bennet
Terraform MCP Server 1.0 is now GA. Connect AI assistants like GitHub Copilot, IBM Bob, and Claude Code to Terraform workflows to reduce manual effort, minimize context switching, and deliver infrastructure faster — with consistency and security built in. ibm.co/6017E3utt
HCP Packer now supports enforced provisioners — helping platform and security teams maintain image integrity and compliance across downstream image builds. ibm.co/6011E3zs5
Offensive AI has evolved from assisted scripting to autonomous exploit engineering. When models like Claude Mythos can chain zero days in hours, static secrets are liabilities. Learn how to design a zero trust defense using Vault Radar and Vault. ibm.co/6015E3zal
Delhi NCR enterprise technology leaders are navigating a new reality with agentic AI and non-human identities. 🤔
Join the HashiCorp Agentic Runtime Security Exchange Series for a session focused on securing and governing autonomous infrastructure without slowing innovation.
Led by HashiCorp Field CTO, Jerome Walter, this Delhi NCR gathering is designed for peer exchange. Practical discussions. Real challenges. No pitches. Register here: ibm.co/6011EM0qJ
The HashiCorp certification program helps thousands of practitioners validate their skills each year. 💡
Ready to take the next step with the Vault Professional exam? 🤔
Whether you’ve recently earned your Associate badge or are already managing Vault in production, this session will help you prepare with confidence.
Join exam expert, Karla Gabriel, to: • Break down advanced exam objectives • Explore recommended study resources • Learn how to avoid common pitfalls • Get your questions answered live
Preparing for a professional-level HashiCorp certification? 🤔
Join this upcoming session with @IBM and HashiCorp experts to get a clear understanding of what to expect from the exam experience, including the lab-based format, key focus areas, and practical tips for success. 💯
You’ll hear directly from Bridget Egan, Senior Product Certification Manager from the exam development team and get answers to your top questions so you can approach certification with confidence.
If you’re working with Terraform or Vault and looking to validate your expertise, this session is designed to help you take the next step. ibm.co/6013EM0LX
Learn how Boundary, when paired with Vault, allows your organization to adopt continuous identity and runtime controls that enable teams to securely implement and use agentic AI workflows at scale. ibm.co/6018EM4G0
From AI that talks to AI that acts, security needs to evolve fast. 🏃♀️
Join us in Delhi NCR on June 19 for the Agentic Runtime Security Exchange and connect with HashiCorp Field CTOs and peers tackling AI governance, runtime security, and scaling agentic systems in production.
Infrastructure is getting more complex as organizations scale AI and hybrid cloud.
HCP Terraform powered by Infragraph is designed to bring clarity back.
It creates a real-time infrastructure graph that connects infrastructure, applications, services, and ownership into a single system of record.
With unified context across environments, teams can: • Understand relationships across their stack • Make faster, more informed decisions • Power automation and policy with greater precision • Prepare for agent-driven workflows
This is a step toward more intelligent infrastructure operations. Explore the latest updates: ibm.co/6016EM0dK
HCP Terraform now supports project-level run tasks — giving teams more flexible governance controls between organization and workspace controls. ibm.co/6015EMaP9
Join HashiCorp in Palo Alto for an exclusive, peer-driven conversation on securing the future of AI. ✨
The Agentic Runtime Security Exchange brings together enterprise leaders to explore how to govern, secure, and scale agentic AI, without slowing innovation.
📍 Palo Alto 📅 June 11
Connect with peers and HashiCorp Field CTOs to discuss: • Modernizing zero trust for non-human identities • Governing AI agents at runtime • Scaling agentic AI with visibility and control
Generative AI is transforming how teams build and operate cloud infrastructure, rapidly drafting Terraform configurations, proposing remediation plans, and clarifying complex systems.
But success with AI will not be defined by code generation volume. Instead, it will hinge on making accurate, safe infrastructure and security changes throughout the entire lifecycle.
See how to manage AI operations with full agentic lifecycle management: ibm.co/6010EMiZE
Join us ahead of AWS Summit New York City for an exclusive reception hosted by IBM Apptio and IBM HashiCorp.
We’re bringing together partners, AWS sellers, and industry leaders for curated networking and focused conversations on how teams are simplifying cloud complexity and driving real outcomes across AI, infrastructure, and cost management. Register now: ibm.co/6012EMeRa
Vault 2.0 introduces beta SCIM support, making it easier for operators to connect identity lifecycle workflows to Vault. The result: less manual provisioning and identities that stay in sync with your existing user and group systems. ibm.co/6014EMnye
Consul 2.0 is now generally available with multi-port service mesh enhancements, @CyberArk Workload Identity Manager integration, cluster-wide rate limits, and improved API gateway auto-scaling support. ibm.co/6018EMwzg
Banco Bradesco already had automation, but it was fragmented across workflows, teams, and approvals.
By turning Terraform into a control plane for platform engineering, they: • Standardized workflows across 20+ teams • Coordinated provisioning, validation, and post-deploy steps in one flow • Scaled a catalog of 500+ reusable modules
The impact? 👉 Delivery time dropped from 80 days to 5
Agentic AI is changing how software behaves, but traditional identity and access models weren’t built for autonomous, non-human actors operating at runtime. In this webinar, join IBM and HashiCorp experts to learn how to secure agentic AI workloads and...
✅ Understand why traditional IAM breaks down for agentic AI ✅ Identify new identity, secrets, and access gaps at runtime ✅ Enforce least-privilege, dynamic access for AI agents ✅ Secure machine-to-machine and agent-to-infrastructure interactions ✅ Enable safe, scalable AI across hybrid and multicloud environments
AI agents are moving fast, but how are you controlling what resources they can access? 🚨
Whether you're just exploring, running experimental agents in a sandbox, or already have agentic workflows assisting with live tasks in production, the requirements remains the same: securely connecting non-human identities to critical infrastructure with governance and access controls fully built in.
At HashiCorp, we are actively shaping the future of Boundary to secure AI agents and we are looking for early adopters to help us build the right guardrails. 🔎
Want to help shape our roadmap and get on the shortlist for the Boundary Agentic Security Beta Program? To sign up, take our quick survey ➡️ ibm.co/6012EM6Fu
Don’t miss your chance to submit your session proposal for HashiConf at IBM TechXchange 2026. ⏰ The deadline is Friday, May 22 at 11:59 PM EST.
Share your story to help fellow practitioners learn, problem-solve, and leave with implementable skills they can apply immediately in their hybrid cloud environments. ☁️
If you have a real-life use case, implementation story, or technology deep dive that shows how HashiCorp products are being used by technical end users across our clients, partners and community, submit your story now! 📖 ✨ ibm.co/6018EHc2p
Encrypting small payloads with Vault is easy. Scaling that model to massive artifacts and streaming data? Not so much. This post walks through a better approach: envelope encryption with Vault. ibm.co/6012EM6e8
🚀 Struggling with slow, inconsistent infrastructure delivery? Terraform + Ansible can help you automate faster, safer, and at scale.
Join HashiCorp product experts Matthew Packer and Bikash Mainali to learn how teams are: ✅ Automating multi‑cloud provisioning with Terraform ✅ Applying secure, standardized configs using Ansible ✅ Reducing errors by removing manual steps ✅ Simplifying Day 2 ops across hybrid environments
Azure hub-and-spoke networking is now generally available for HCP Vault Dedicated, expanding options for customers to seamlessly and securely connect to Vault as they continue to advance their cloud security maturity. ibm.co/6014EzA8Q
Agentic AI turns software into autonomous actors, but it also introduces an explosion of non‑human identities that are often over‑privileged and protected by static credentials.
As attacks like prompt injection and credential leakage happen at machine speed, NHIs are becoming the primary enterprise attack surface. This webinar explains why legacy IAM falls short for agentic AI and how zero‑trust identity secures autonomous agents while enabling innovation. ibm.co/6016EzuKI
HashiConf at @IBM TechXchange tickets are out now at super early bird pricing. Join us for a few days of hands-on labs, strategic keynotes, product announcements, and hybrid cloud and security learnings. Get your conference pass today:
LAB3 helps teams implement more advanced Vault capabilities to strengthen connectivity, governance, and automation.
See how they... ✅ Automated secrets management with Vaultdriven rotation and access controls ✅ Cut credential exposure windows to minutes or hours instead of months or years ✅ Accelerated delivery with preapproved templates and embedded guardrails
Learn how they implement security modernization for clients: ibm.co/6019Ezi79
Most companies aren’t failing at AI — they’re stuck in pilots. Learn why powering the agentic enterprise means turning real-time intelligence into coordinated action at scale. ➡️ ibm.co/6010EzmUO
Terraform 1.15 introduces flexible module management through variable support in source attributes, explicit deprecation warnings for configurations, native Windows ARM64 support and enhanced testing capabilities. Read more ➡️ ibm.co/6014EzcVe
AI agents need more than access; they need an identity. Vault now provides native IAM for agents to deliver least privileged access. 🔒 ibm.co/6018EzcDp
Terraform Enterprise 2.0 introduces new capabilities for managing infrastructure at scale, including Stacks, automated identity management with SCIM 2.0, project-level notifications, workspace migration workflows, and more. Read the blog ➡️ ibm.co/6015Eze9f
IBM Vault 2.0 delivers UI enhancements for better feature discoverability and product usability and reporting improvements for transparency and forecasting support. Learn more ➡️ ibm.co/6013Ezezx
Security and compliance issues don’t usually fail teams because they’re hard to find. They fail because they’re found too late, after CI/CD and deployment. ‼️
Learn how DevOps teams are embedding security and policy earlier in the development workflow, so risks are addressed as code is written, not after systems are live in this webinar. Register here: ibm.co/6019EzuEt
Attending @RedHat Summit this week? Our experts would love to chat with you about all things Terraform and Vault. Learn how to accelerate delivery without compromising security at our booth, 124!
Introducing identity security — evolved. IBM Vault Enterprise 2.0 moves LDAP static roles to a centralized rotation manager. Eliminate high-privilege bind accounts with self-managed flows and gain granular control over your automated secret lifecycle. ibm.co/6013EzKa1
If your automation relies on static API keys, passwords, or SSH keys, your risk surface is growing.
This webinar shows how to eliminate secret sprawl in Ansible Automation Platform by adopting a zero trust approach with HashiCorp Vault. You will see how workload identity, dynamic secrets, and least-privilege access work together to secure automation without slowing teams down. ibm.co/6017EKCz5
Trying to get an accurate snapshot of your cloud landscape can be elusive. After consolidating data from different ecosystems, workflows, and applications, data is already out-of-date.
HCP Terraform powered by Infragraph regularly updates assets through direct connections into every ecosystem, so you can get the unified infrastructure truth your platform teams are seeking. See this in action with Infragraph in public preview now. ibm.co/6016EKIUo
Dynamic credentials are essential for securing access to critical infrastructure. Read this post to learn how Boundary and Vault integrate with Windows AD DS to secure RDP connections, and get step-by-step instructions on testing out a POC. ibm.co/6017EKCs1
If you have a great story to tell for fellow developers and security professionals, we'd love to hear from you. 🤩 This is your chance to showcase real‑world implementations, deep technical insights, and the innovations shaping the future of cloud, automation, and AI‑driven infrastructure. ☁️
Submit your HashiCorp story for HashiConf at IBM TechXchange by May 22 at 11:59 PM EST. ibm.co/6013EKQRL
A centralized, event-driven knowledge graph, HCP Terraform powered by Infragraph provides the unified visibility that keeps the focus where it belongs: empowering organizations to secure and optimize infrastructure. ✨
Connect all workflows, data, and applications across your full estate with Infragraph, now in public preview: ibm.co/6017EKCJt
This is where IBM HCP Terraform powered by Infragraph shines, enhancing visibility to help platform teams streamline operations and automate remediation.
Eligible customers can get started in public preview today:
Do you know how much access one non-human identity has in your organization? Hear from HashiCorp Field CTO, Jake Lundberg, as he discusses how teams can link NHIs back to human workflows and control their boundaries. Watch the IBM Security Intelligence podcast episode:
Struggling to manage secrets at scale in Kubernetes or @RedHat OpenShift? Discover why the Vault Secrets Operator (VSO) is the new gold standard for secure automated secret delivery and lifecycle management that empowers both platform teams and developers alike.
Don't let local accounts be a security blind spot! Vault Enterprise 2.0 automates password rotation for RHEL & Ubuntu via SSH. Replace shared "admin" passwords with unique, audited credentials to stop lateral movement and secure the last mile. ibm.co/6018EKQy2
Secure SSH without the operational drag of static keys. Explore a new Vault-based approach for short-lived SSH certificates, RBAC, and consistent access across on-prem, hybrid, and multi-cloud environments — and Boundary for seamless just-in-time access at scale.
HashiCorp is happy to announce the launch of a new Partner Premier tier tag available in the Terraform Registry that will help ensure extended benefits for Terraform end users and customers. Learn more ➡️ ibm.co/6017EKX7S
Secret detection is only the starting point. The real security value comes from what teams can do next. This blog explores how Vault Radar helps teams move from discovery to remediation through Vault correlation and secrets import, webhooks, reporting, and traceability.
Powering over 80 million transactions each month, Riverty delivers flexible payments, debt collection, and smart accounting solutions while constantly pushing to innovate.
Learn how they achieved faster infrastructure deployment and quicker ticket resolution with self-service IaC with Terraform and Vault. ibm.co/6016EKirK
When Skechers needed to modernize its infrastructure, the multibillion-dollar retailer turned to HashiCorp to deliver self-service and automation. Find out how Skechers is putting its best foot forward.
Hear how HCP Terraform propelled the Fortune 500 retailer’s cloud journey forward by helping to streamline its infrastructure provisioning, standardize deployment practices, shift left on FinOps and security, and speed up application delivery. ibm.co/6016EKELE
Learn how to automate public CA workflows, unify your PKI lifecycle, and secure your internal workflows with @IBM Vault's new public certificate integration. ibm.co/6017EKTV1
SOCs don't start investigations by watching videos – they start with alerts. See how pairing Boundary session recordings with kernel-level audit events from Elastic Auditbeat gives security teams real-time SIEM detection plus full forensic context for every privileged session.
HashiConf at IBM TechXchange registration is now live. Secure a super early bird ticket and connect with developers, security professionals, and IT leaders shaping the future of hybrid cloud. 😎 ☁️ ibm.co/6017EJ4ZH
Terraform and AWS have just released a set of pre-written Sentinel policies designed to help get you started with ISO 27001 compliance. ibm.co/6019EKOMt
Banco Bradesco transformed infrastructure delivery by uniting policy as code and platform orchestration, reducing time to provision while improving compliance. Read the full story ➡️ ibm.co/6011EKJ5d
IBM Think is the place to be for leaders shaping the future of enterprise IT.
If you’ll be there, meet with HashiCorp executives and experts to discuss how we help organizations securely manage infrastructure and scale across hybrid cloud environments.
Learn how Ariso. ai uses the Vault transit secrets engine to deliver tenant-isolated envelope encryption with sub-millisecond performance at scale. ibm.co/6011EJV3N
If you’re attending, come find HashiCorp at booth 124 to chat with our team about modern infrastructure management, security, and automation across hybrid and multi-cloud.
Want guaranteed time with our experts? Book a customer meeting onsite here: ibm.co/6016EJtak
IBM Think is where important conversations about the future of enterprise infrastructure and security happen.
If you’re attending, connect with HashiCorp executives and experts to discuss how organizations can bring greater consistency, security, and automation to their hybrid cloud operations.
Schedule time to meet with the HashiCorp team at the event: ibm.co/6012EJt0n
Solve security and scalability problems through an “as code” approach to infrastructure and security lifecycle management. Learn how Terraform can help you manage secrets as code. ibm.co/6012EJVMa
As AI agents take on work, trust can’t stop at login. Learn how agentic AI reshapes identity and access — and what must change as autonomy scales. ibm.co/6014EJUL0
Vault Enterprise 2.0 is now generally available, delivering new capabilities to help organizations secure, scale, and simplify secrets management across modern infrastructure.
Strengthen identity-based access, improve credential lifecycle automation, and enable high-performance encryption for emerging workloads, while continuing to enhance usability and integrations across your ecosystem. ibm.co/6014EJUPs
Eliminate secret zero and enable “secretless” workloads with Vault and workload identity federation. Replace static credentials with short-lived access and enforce zero trust. ibm.co/6016EJVKQ
With native OIDC integration in AFT, you can enable secure, dynamic credentials with a single flag — no manual IAM setup, no secrets. Learn more: ibm.co/6017EJOF7
Security risks grow as teams adopt more cloud, CI/CD, and SaaS tools. Static secrets scattered across environments make breaches more likely and harder to manage.
Watch this on-demand webinar to learn how HashiCorp Vault helps centralize secrets, enforce access controls, and reduce risk across your organization. ibm.co/6016EJEKk
Engineers are being tasked to build AI, but they're not identity experts. Tyler Lynch, Field CTO, explains how agentic runtime security, dynamic credentials, OAuth2, and IDP flows protect AI agents from risks like prompt injection. Learn how to secure non‑human identities and cloud workloads. 🚀 ibm.co/6015EyRWU
How are organizations today trying to tackle agentic AI and the risk of non-human identities? HashiCorp Field CTO Jake Lundberg discusses these issues and more in this episode of the IBM Security Intelligence podcast. Watch the full episode: ibm.co/6011EJJZJ
We are excited to welcome Ricardo Martins as our new Field CTO for the LATAM at HashiCorp. Ricardo joins us with over 20 years of experience leading technology, data, and digital platform teams.
Ricardo specializes in converting complex tech stacks (cloud, microservices, CI/CD) into tangible business growth. Welcome to the team, Ricardo!
Ticket-driven cloud ops won’t get you to AI. LAB³ uses HashiCorp to help enterprises unify infrastructure, security, and networking into a single workflow — accelerating delivery, reducing risk, and building a foundation for next-gen architectures. Read more:
Most secure remote access feels like visiting a bank teller every time you need to buy a coffee. That’s why we built HashiCorp Boundary. And the differentiating feature we lead with when we talk about it? Transparent sessions. Security shouldn’t require users to change how they work.
Transparent Sessions embeds access controls directly into the workflows people already use. No extra hoops. No friction. Just instant, secure access to infrastructure — the way it should be.ibm.co/6018EHc3q
When “cloud” still meant tickets and manual processes, LAB3 set out to change the model. Watch how the global platform engineering leader uses HashiCorp to help enterprises modernize their cloud foundations, reduce provisioning time, and unlock real cloud velocity.
Setting up AWS access for HCP Terraform shouldn’t come with IAM tax or bootstrapping toil – here’s how HashiCorp and AWS make it easier. ibm.co/6010EytVe
Scanning of @awscloud S3 buckets is now available as a public beta in HCP Vault Radar. This new capability will help you find all of those unmanaged secrets exposed in application data and backups so you can get them under control. Learn more about how to find exposed unmanaged secrets. www.youtube.com/watch?v=GOcXL8jWJ18
HCP Terraform now supports IP allowlists at both the organization and agent level, enabling organizations to define trusted IP ranges and enforce stronger network security when managing infrastructure in private environments. ibm.co/6012EytTY
Teams are under constant pressure to move faster, and developers want to ship applications quickly. But even with automation, approvals can stack up and security controls can slow everything down. 🐌
HashiCorp helps align developers, platform, and security teams with shared workflows, automated guardrails, and built‑in security—keeping delivery fast, consistent, and secure. Watch to learn more: ibm.co/6019EDdmx
Building AI agents is exciting, but securing them is critical. 🔐 ☁️
HashiCorp, Langflow, Prisma, and AWS EKS show how to protect AI workloads with secure workflows, seamless secrets management, and identity‑based access baked in.
We’re excited to welcome Satyan Nair as a Field CTO to HashiCorp.
Satyan brings over 25 years of leadership experience in driving enterprise digital transformation and technology execution strategy.
Deeply passionate about the convergence of product, platform, and infrastructure engineering, Satyan specializes in building high-performance engineering cultures and establishing robust governance frameworks. Welcome to the team! 🙌
Today marks a significant milestone for HashiCorp.
From the start, @armon has been instrumental in shaping not just our products, but also how organizations tackle cloud infrastructure and security at scale. His technical expertise and forward-thinking vision have been crucial to the company we’ve become. We truly appreciate the positive impact he’s made on our culture, customers, community, and teams over the past 13 years.
Bevel Work used Terraform to automate factory building in Factorio, wiring mods into Archon for external control, resource gathering, and production flows.
As hybrid cloud environments expand, traditional perimeter security isn’t enough. 🙅
We help organizations embed zero trust into their operating model with identity‑based access, automated workflows, and consistent security across every cloud.
In this hands-on tutorial, we demonstrate how to install the DigiCert Vault plugin and use HashiCorp Vault to issue TLS certificates from DigiCert. ibm.co/6010EDiRn
Platform teams are being asked to do more: support more apps, more developers, and more clouds. 😮💨
The Infrastructure Cloud provides a unified, automated foundation that standardizes workflows and accelerates delivery across the organization. Read the whitepaper:
Please join us in welcoming Blair Newman as one of HashiCorp’s newest Field CTOs! 🙌
Blair is a globally recognized technology executive known for advancing edge AI, distributed intelligence, and multi‑cloud operating models. He’s helped organizations across highly regulated industries scale AI‑native architectures and turn complex systems into business outcomes.
We’re excited to have Blair’s expertise helping HashiCorp customers navigate the next wave of cloud and AI innovation. Welcome to the team!
Cloud complexity is only growing faster as organizations introduce AI in their workflows. But complexity can quickly slow developer teams down.
Learn how a unified approach to Infrastructure and Security Lifecycle Management (ILM and SLM) can help enterprises accelerate delivery, reduce friction, and innovate securely across every environment. ibm.co/6012ED9eq
Attackers don’t need zero-days when identity is wide open. 😳
Join Bob Kalka and Jake Lundberg from IBM and HashiCorp for a deep dive into the attack patterns from the 2026 X-Force Threat Intelligence Index and how modern identity and secrets management shut them down.
You’ll learn how to implement dynamic secrets, enforce least-privilege, secure AI workloads, and strengthen session protection across your environment. Reserve your spot and transform identity into your most resilient layer of defense here. ibm.co/6016EyEuC
Learn why legacy IAM methodologies cannot be applied to agentic AI and how to enforce operational and security best practices in this new era of agentic identity. ibm.co/6019EyEJR
“Developers always take the easy path. So if you make the easiest way the right way, then you have the right outcome.”— Suneer Pallitharammal Mukkolakal, Lead Platform Engineer, World Bank
That mindset powered the World Bank’s shift from 5‑day manual provisioning to a 30‑minute self‑service platform that now manages 27,000 cloud resources and supports 1,700 applications across AWS, Azure, and GCP — all built on golden paths with HCP Terraform.
When the easiest path is the secure, compliant, best‑practice path, teams move faster and smarter.
👉 Explore how they made the right path the easy path. ibm.co/6013EDgiT
Many enterprises believe they’ve modernized just by moving to the cloud, but long ticket queues, manual secrets management, and inconsistent IaC keep teams stuck at “fake speed to market.”
By standardizing on Terraform, Vault, and Consul, LAB3 helps clients cut provisioning time by 70%, reduce operational overhead by 30–50%, and unify delivery across clouds. See how LAB3 accelerates cloud modernization: ibm.co/6016EyDPw
The VSCode scanning plugin is now generally available for HCP Vault Radar. By integrating secret scanning directly into VSCode, Vault Radar makes secure coding easy and automated. Learn more about how to find exposed unmanaged secrets. ibm.co/6013ED5fl
With Security Lifecycle Management (SLM), you can help your teams strengthen your security posture and maintain compliance without slowing innovation.
Explore HashiCorp's approach to zero trust, enhanced compliance posture, and proactive risk management in our Do Cloud Right video series. Watch now: ibm.co/6016EDezu
Atruvia supports 900+ financial institutions across Germany — and needed to modernize the infrastructure behind millions of banking transactions.
But provisioning was still slow and ticket-driven: clusters took 3 months, and network setup took weeks.
So, Atruvia rebuilt around infrastructure as code, using Terraform + GitOps workflows (Terraform Enterprise + GitLab) and Vault for centralized secrets management in CI/CD.
The impact? ✅ Provisioning dropped from 3 months to 2 hours ✅ Network setup went from weeks to 15 minutes ✅ Developers gained fast, compliant self-service instead of “ticket ops”
What are the considerations when deploying AI Agents? In this video, Bob Kalka and Tyler Lynch explain how agentic AI, non-human identities, IAM gaps, and runtime security risks shape real-world deployments. Learn how accountability, least privilege, and zero trust keep agentic AI secure. ibm.co/6017EHcXB
Learn how ariso.ai uses the Vault transit secrets engine to deliver tenant-isolated envelope encryption with sub-millisecond performance at scale. ibm.co/6013EHckN
Building secure, compliant infrastructure on Day 1 is critical. But environments change or are forgotten over time, creating a huge security risk. Learn how Terraform and Packer help you construct Day 2 guardrails that protect your organization from falling victim to unknown vulnerabilities. ibm.co/6019EHcRt
Terraform Enterprise 1.2 is now GA: bring brownfield resources under management with UI-driven search and import, get centralized workspace visibility with Explorer (now GA), and improve reliability with new diagnostics and Day 2 operations. ibm.co/6012EHi0M
Kubernetes teams need a safer way to deliver secrets without storing them in etcd. With Vault Enterprise 1.21, the Vault Secrets Operator now supports a CSI-based workflow that delivers secrets directly to pods at runtime.
Watch this session to learn how the new CSI driver works, why it improves security, and how to start adopting it in your environment. ibm.co/6015EHipd
What would you do with 8,000 reclaimed developer hours? 🤔
Benchling found out firsthand after transforming how it manages infrastructure with Terraform. By shifting away from laptop-based Terraform runs and centralizing execution and governance, the team eliminated massive operational toil — in an environment spanning 165,000+ cloud resources and 350 workspaces. ibm.co/6017EDjBc
HCP Vault Radar has come a long way since GA launch. And 2025 marked a major leap forward in how teams detect, remediate, and prevent secret sprawl. 🔐
From expanding visibility across code, cloud, and collaboration tools to deepening integrations that meet developers where they work, this year’s advancements strengthened the bridge between security and speed. Read the Vault Radar team's reflections and priorities going into 2026. ibm.co/6016EDbYm
HCP Vault Dedicated is now available in additional AWS and Azure regions, expanding options for resilient, high-performance secrets management across global infrastructure environments. ibm.co/6014EHDmu
Visiting @Google Cloud Next? Come to booth 2809 to learn how HashiCorp + Google Cloud help organizations automate infrastructure, secure cloud environments, and accelerate platform engineering. ⚙️✨ ibm.co/6019EDXxB
HashiConf is taking place at @IBM TechXchange 2026 to bring developers, engineers, operators, and practitioners together for deep‑dive learning across AI, automation, hybrid cloud, and emerging tech.
We’re looking for technical talks that share real-world implementations, use cases, and deep dives with HashiCorp products.
Have a story to tell? Submit your session proposal by May 22 at 11:59 PM EST.
Atruvia AG cut cluster provisioning from 3 months to 4 hours, reduced network setup from weeks to 15 minutes, and standardized compliant pipelines across hybrid environments — all while powering infrastructure for 900+ banks across Germany. Learn more: ibm.co/6013EDXyl
HashiCorp Boundary makes a clean break with traditional PAM and VPNs — unlike its other secure remote access competitors. Learn how Boundary stands above the rest in ease-of-use. ibm.co/6018EDnvA
GEICO cut $300M+ in cloud spend by shifting from network‑centric security to an identity‑driven model — simplifying infrastructure, reducing complexity, and building a foundation for future AI workloads. 🛠️
Working in silos = fragmented tooling, rising cloud costs, and greater complexity 🤯
Learn how a modern proactive operations model that’s optimized for cost and built on automated workflows can work for your organization in our Do Cloud Right video series:
Autonomous agents are driving explosive growth in non-human identities (NHIs), most of which are over-privileged and protected by static credentials. Traditional IAM and perimeter security simply weren’t built for this.
Join this webinar to learn how zero-trust identity, including ephemeral credentials, OBO authorization, and full auditability — secures autonomous agents without slowing innovation. ibm.co/6019EDz7T
To every speaker who shared their journey. To every attendee who tuned in across time zones. To our MCs and production teams who powered 24 hours of learning. To everyone who filled the chat with questions, insights, and encouragement, Thank you.
This event is powered by community, for the community.
The #hashitalks stream doesn’t stop, and neither does our community.
We continue to follow the sun as community speakers from all over the world share advanced workflows, infrastructure patterns, and lessons learned across hybrid and multi-cloud environments.
Let us know where are you tuning in from? Drop your city In the chat at hashi.co/hashitalks-2026
We’ve made it to the half point of this 8th edition of the annual 24-hour #hashitalks 🎉
Meet the next set of MCs who will guide us through sessions featuring global voices who are building, experimenting, and leading with HashiCorp tools from this midpoint to the close of the event.
In just one year, HashiCorp Vault Radar expanded visibility across the cloud, correlating @awscloud Secrets Manager data, scanning S3, and integrating directly into developer workflows.
See how Radar is redefining how enterprises detect, remediate, and govern secrets at scale.
Vault certificates and secrets inventory reporting (beta) is now available in HCP Vault Dedicated, delivering centralized visibility into secrets and certificates to help security teams strengthen governance and avoid the audit scramble. ibm.co/6013DclWT
This is the idea behind HashiCorp Agent Skills: an open library of domain-specific context designed to make AI assistance more trustworthy for platform and infrastructure engineers.
If you’re curious how this works in practice, we’ve shared more details here:
Make the easy way, the secure way. ✅ With Boundary transparent sessions quietly running in the background, developers can securely access their target resources without changing the tools or the way they work. 🪄 www.hashicorp.com/pt/blog/transparent-sessions-now-ga-in-…
I asked the @HashiCorp speakers to use Project Bob to help build their demos for @IBMDeveloper Day: #ai Demystified. Moderate success using it to review #terraform code, but I really needed it to edit the video for me. 😅
88% of web application attacks involve stolen credentials.
HCP Vault Radar is now generally available and helps you detect exposed secrets, prioritize risks, and securely import them into Vault for centralized management.
Bevel Work used Terraform to automate factory building in Factorio, wiring mods into Archon for external control, resource gathering, and production flows.
Cloud security is complicated in a regulated industry. Learn how Duke Energy built a developer platform that abstracts infrastructure tasks from developers, enhances security, and accelerates innovation. ibm.co/6014DnnIg
What if you could pair-program with a HashiCorp engineer every day?
Someone who generates Terraform and Packer code that follows official style conventions, applies best practices, and understands how your providers and modules are structured.
That’s the kind of confidence we’re aiming to give platform and infrastructure engineers with HashiCorp Agent Skills: an open library of domain-specific context designed to make AI assistance more reliable in real infrastructure workflows.
A credential committed to a repo doesn’t stay there. It moves through CI/CD, builds, images, logs, and shared artifacts. By the time it’s detected, it often exists across environments and trust boundaries. ibm.co/6013DBYVB
During the October 2025 AWS us-east-1 disruption, HCP Vault Dedicated maintained full data plane availability across regions and clouds. This blog breaks down the architecture, the control plane impact, and the resilience lessons we’re applying going forward. ibm.co/60138hekZ
Expedia had GPU-heavy jobs running for 24+ hours and expensive compute sitting idle.
Instead of buying more capacity, they stitched together what they already had into a shared compute platform that now runs production workloads at scale.
New Stacks support, smarter governance tools, and improvements for secure, air-gapped AI workflows. Plus practical tips for using Terraform, Vault, and Consul MCP servers more effectively. ibm.co/60178Lx8R
The idea that Linux is “secure by default” no longer holds up against modern attacks built on stolen credentials, misconfigurations, and standing privileges.
In our latest blog, Krishnan Ramachandran breaks down:
• The real Linux threat landscape in 2026 • Why credential-based attacks now dominate breaches • The business impact of downtime, ransomware, and audit failure • The strategic pillars CISOs need to reduce blast radius and eliminate standing risk • What immutable, identity-first Linux security actually looks like in practice
If you’re responsible for securing Linux environments at scale — across cloud, AI, and hybrid infrastructure — read our blog to learn about the concrete practices you need to put in place to defend against threats to your Linux systems.
Expedia had GPU-heavy jobs running for 24+ hours and expensive compute sitting idle.
Instead of buying more capacity, they stitched together what they already had into a shared compute platform that now runs production workloads at scale.
Are you still manually invoking Lambda functions, creating invalidation requests for CloudFront’s cache, or running Ansible playbooks outside of your core Terraform provisioning workflow?
Use Terraform actions — now GA — to unify and automatically trigger all of these fragmented Day 2 workflows in Terraform.
Are you still manually invoking Lambda functions, creating invalidation requests for CloudFront’s cache, or running Ansible playbooks outside of your core Terraform provisioning workflow?
Use Terraform actions — now GA — to unify and automatically trigger all of these fragmented Day 2 workflows in Terraform.
Do cloud right, and zero trust stops being a slogan.
It becomes an operating model.
One where access is earned, temporary, and provable, whether the requester is a human or a machine. Watch our full breakdown here: youtu.be/S2zsmIqMhYU
Learn how Terraform Actions built for the AWS provider can trigger dynamic automation workflows in your environment, all with just one Terraform apply. www.youtube.com/watch?v=269PPRbCj_g&t=1s
The Terraform engineering team has been focused on reducing friction for platform teams by improving how infrastructure is standardized, shared, and scaled.
Latest updates across HCP Terraform and Terraform Enterprise include:
◼️ Stack component configurations (GA) ◼️Workspace-to-Stacks migration (Beta) ◼️Native monorepo support for module publishing (GA) ◼️Self-hosted agent support for module testing (GA) ◼️Terraform search and import (GA)
Expedia had GPU-heavy jobs running for 24+ hours and expensive compute sitting idle.
Instead of buying more capacity, they stitched together what they already had into a shared compute platform that now runs production workloads at scale.
🚨#hashitalks: España is now live. Join the livestream to hear real-world stories, demos, and use cases on HashiCorp tools from the community in #spain. Explore the full schedule of talks and speakers here 👉 hashi.co/hashitalks-espana
GEICO was on track for $300M+ in annual cloud spend when they discovered a way to fix their network security issues and save money on cloud at the same time. Read on to learn how they set themselves up for success in the AI era. ibm.co/601189Km7
In many enterprises, AI ambitions are running into a formidable roadblock: Hybrid cloud complexity. Here's an analogy: some organizations are trying to use hybrid cloud like one rider riding two horses — unless you're extremely skilled, you're going to fall off. What they they should be building is a harness and a carriage to use both effectively.
Learn why having a hybrid cloud plan matters in 2026 and how a unified lifecycle management approach can turn hybrid cloud infrastructure into a catalyst for faster, more impactful innovation.
☁️ Hybrid cloud, explained: What it is, what it isn’t, and why having a plan matters in 2026 ibm.co/601189JdL
If you’ve heard of Amazon VPC Lattice, it’s a useful method for connecting HashiCorp Vault to resources like Amazon RDS. If you’re interested in the architectural patterns and setup, start here. www.hashicorp.com/en/blog/patterns-for-connecting-vault-t…
▶️ Watch Benchling's evolution from decentralized Terraform usage to a unified, modular, and automated infrastructure-as-code approach: www.youtube.com/watch?v=b8HS0TIW-2w
Non-human identities (service accounts, API keys, OAuth tokens, certificates, and machine credentials) now vastly outnumber human users, yet we're still managing them with approaches designed for people. This has to stop. www.hashicorp.com/en/blog/the-future-of-secrets-and-ident…
AGL had already started using HashiCorp Terraform Enterprise to automate some infrastructure.
That early work became the foundation for a complete rebuild.
Using infrastructure as code, teams created a shared library of tested modules that anyone could use to provision consistent, secure environments in minutes.
Modernizing your engineering stack is the key to unlocking developer productivity and faster innovation. But legacy drag can hamper your progress. Learn how one large financial institution took on the challenge and succeeded. www.hashicorp.com/en/blog/5-lessons-for-enabling-self-ser…
As companies look to build a solid foundation for their AI workloads, hybrid cloud strategies are undergoing major transformation. From self-service provisioning to ground-up security, automation will divide the leaders from the stragglers. www.hashicorp.com/en/blog/new-year-new-cloud-strategy-5-s…
Riverty processes payments at a global scale, but legacy provisioning and manual secrets slowed them down. By adopting HCP Terraform and Vault, they cut deployment time by 90% and eliminated the risk of expired credentials.
Looking ahead to 2026, we’re focused on the people who make the HashiCorp community what it is.
The HashiCorp Ambassador program is now open for nominations and applications. If you or someone you know has been creating, teaching, mentoring, or supporting others, this is a great way to recognize that impact. www.hashicorp.com/en/ambassador
At HashiConf 2025, we introduced Project Infragraph, a unified infrastructure knowledge graph that gives AI full context of your systems, security, and ownership.
Manage all of your infrastructure in one place. It’s easier said than done, but Terraform search is another step toward making this goal more achievable.
HashiCorp’s SE team has a deep fellowship with their customers because they use our products the same way our customers do.
Hear how our SEs built a self-service demo platform powered by HCP Terraform to standardize demo setup, cut provisioning time from hours to minutes, and influence $20M+ in ACV. www.hashicorp.com/en/blog/infrastructure-as-demos-a-terra…
New in Terraform: organization-level control over user API tokens.
Teams can now enable or disable user token use across their Terraform orgs to improve visibility, enforce least privilege, and simplify access management.
The Vault Secret Store CSI (SSCSI) provider is now certified by @RedHat.
OpenShift customers can now mount secrets from Vault directly into ephermeral volumes – never stored in etcd – with security, lifecycle, and supportability jointly validated by Red Hat and hashiCorp.
California’s Department of Health Care Services serves millions of residents every day.
With HashiCorp Terraform Cloud, DHCS modernized its legacy infrastructure, cutting provisioning time by 70%, improving availability, and laying the foundation for 200 future applications.
A leading global insurer reclaimed 42,000+ admin hours per year and cut risk by 14% by modernising its infrastructure with automation and policy as code.
The Terraform engineering team has been focused on reducing friction for platform teams by improving how infrastructure is standardized, shared, and scaled.
Latest updates across HCP Terraform and Terraform Enterprise include: ◼️ Stack component configurations (GA) ◼️ Workspace-to-Stacks migration (Beta) ◼️ Native monorepo support for module publishing (GA) ◼️ Self-hosted agent support for module testing (GA) ◼️ Terraform search and import (GA)
The Terraform engineering team has been focused on reducing friction for platform teams by improving how infrastructure is standardized, shared, and scaled.
Latest updates across HCP Terraform and Terraform Enterprise include: ◼️ Stack component configurations (GA) ◼️ Workspace-to-Stacks migration (Beta) ◼️ Native monorepo support for module publishing (GA) ◼️ Self-hosted agent support for module testing (GA) ◼️ Terraform search and import (GA)
California’s Department of Health Care Services serves millions of residents every day.
With HashiCorp Terraform Cloud, DHCS modernized its legacy infrastructure, cutting provisioning time by 70%, improving availability, and laying the foundation for 200 future applications.
As HCP Terraform continues to evolve, we want to share clarity around upcoming Free tier changes. This post outlines the move away from legacy Free plans, how Free usage is measured, and what teams should know moving forward for the Free tier. www.hashicorp.com/en/blog/continuing-hcp-terraform-s-enha…
Excited to collaborate with GitHub on their new Custom Agents for Copilot.
The Terraform-focused custom agent helps teams ship infrastructure faster and more securely by codifying best practices, enforcing standards, and eliminating boilerplate.
Identity security isn’t just about people anymore.
As non-human identities continue to grow across pipelines, workloads, and AI systems, the need for consistent identity governance is becoming critical.
KuppingerCole named HashiCorp, an IBM company, a leader in all four categories of its 2025 Leadership Compass for Non-Human Identity Management.
At HashiConf 2025, we introduced Project Infragraph, a unified infrastructure knowledge graph that gives AI full context of your systems, security, and ownership.
Most companies made it to the cloud. Very few are getting the full value.
Why? Fragmented tooling, misconfigurations, wasted spend, and operating models that were never designed for today’s scale.
This talk explores what’s broken, why reactive approaches don’t work anymore, and how a unified, lifecycle-based model can turn cloud from a cost center into a competitive advantage. www.hashicorp.com/en/do-cloud-right-explained
New in Terraform: organization-level control over user API tokens.
Teams can now enable or disable user token use across their Terraform orgs to improve visibility, enforce least privilege, and simplify access management.
In @Armon Dadgar’s end-of-year reflection, he visits the themes we heard consistently from customers this year, and how those insights shaped our strategy across infrastructure lifecycle automation, identity-led security, and platform integration. www.hashicorp.com/en/blog/hashicorp-year-in-review-2025-l…
It’s clear static SSH keys aren’t built for scale. So how do enterprises start rethinking their SSH access workflows for the challenges in modern IT environments?
▶️ Watch Benchling's evolution from decentralized Terraform usage to a unified, modular, and automated infrastructure-as-code approach: www.youtube.com/watch?v=b8HS0TIW-2w
Developers want to move fast and innovate. Business leaders want the same thing, with one caveat: don’t put the business at risk. But how do you increase agility without compromising security? Robert Scully from WPP says the answer is to create a developer platform. Check out what he has to say. www.hashicorp.com/en/blog/a-cloud-engineering-lead-s-7-le…
At HashiConf 2025, we introduced Project Infragraph, a unified infrastructure knowledge graph that gives AI full context of your systems, security, and ownership.
AI isn’t breaking cloud. It’s exposing how broken our cloud operations already were.
Silos, tool sprawl, and fragmented policies keep teams stuck reacting instead of building. And with non-human identities scaling faster than we can govern them, “fix it later” no longer works.
The companies pulling ahead are unifying platforms, automating guardrails, and giving developers a faster, safer path to ship.
Cloud gets easier when the foundation is unified — and that’s what makes it ready for AI.
New in Terraform: organization-level control over user API tokens.
Teams can now enable or disable user token use across their Terraform orgs to improve visibility, enforce least privilege, and simplify access management.
Agentic AI is reshaping enterprise software and exposing massive security gaps as NHIs surge.
Learn how HashiCorp and IBM apply zero trust principles such as dynamic credentials, auditing, PKI, and more to secure autonomous systems before threats become incidents.
Why do so many AI projects stall before reaching production?
In this recent Sip and Sync with Azure, HashiCorp shares how to tackle last-mile challenges in AI deployments.
From dynamic credential management to solving the “confused deputy” problem, discover how HashiCorp and @Microsoft Azure are enabling secure, scalable, and auditable AI workflows.
Are you still manually invoking Lambda functions, creating invalidation requests for CloudFront’s cache, or running Ansible playbooks outside of your core Terraform provisioning workflow?
Wrapping up re:Invent with a look at what’s resonating most with customers — from AWS’s new DevOps Agent service to how HashiCorp can bring identity, consent, and Terraform consistency into agentic workflows. Tyler breaks down where agentic interfaces and infrastructure automation are heading next.
Last month, during #ibmtechxchange, I sat down with @HashiCorp CTO, @Armon to discuss HashiCorp joining @IBM and the changing nature of infrastructure in the AI era. My POV, Armon's thinking frames wrt core tenants of the infrastructure are spot on!
Armon breaks down the full picture of non-human identity and why many organizations struggle with visibility and governance.
From discovering unmanaged secrets with Radar to issuing just-in-time credentials with Vault to securing system-to-system access with Boundary and Consul, he shares how HashiCorp helps teams bring order to NHI.
A leading global insurer reclaimed 42,000+ admin hours per year and cut risk by 14% by modernising its infrastructure with automation and policy as code.
California’s Department of Health Care Services serves millions of residents every day.
With HashiCorp Terraform Cloud, DHCS modernized its legacy infrastructure, cutting provisioning time by 70%, improving availability, and laying the foundation for 200 future applications.
The Kiro AI-powered IDE, built by AWS, introduced “powers” extensions this week at re:Invent. HashiCorp is a powers launch partner with the launch of our Terraform power extension for Kiro. www.hashicorp.com/en/blog/hashicorp-is-a-kiro-powers-laun…
Our community is strongest when practitioners share what they’ve learned along the way. Jasmine talks about why your story matters and how you can get involved through HashiTalks 2026 or your local HashiCorp User Group.
Wrapping up re:Invent with what resonated most with customers.
Tyler shares how teams are exploring AWS’s new DevOps Agent service alongside HashiCorp tools like Project Infragraph, MCP servers, and identity delegation to bring informed consent into agentic workflows. He also highlights how Terraform Actions can keep automation consistent and predictable as teams adopt these new patterns.
At HashiConf 2025, we introduced Project Infragraph, a unified infrastructure knowledge graph that gives AI full context of your systems, security, and ownership.
Using AWS Kiro, the team has cut Terraform provider development from 40 hours to as little as 4. Paul breaks down how this works and what he’ll be covering in his re:Invent session on Friday.
What is HashiCorp doing with MCP servers? Jacob breaks down how Vault, Consul, and Terraform MCP servers help teams onboard faster and use AI with their public and private registries.
Using AWS Kiro, the team has cut Terraform provider development from 40 hours to as little as 4. Paul breaks down how this works and what he’ll be covering in his re:Invent session on Friday.
Servus vom HashiCorp Stand auf der AWS re:Invent 👋
Ihr seid heute auch in Vegas unterwegs? Dann kommt vorbei am HashiCorp Stand. Noch nicht überzeugt? Dann hört von HashiCorps Field CTO Steffen Wagner warum es sich lohnt, doch vorbeizuschauen.
New in Terraform: organization-level control over user API tokens.
Teams can now enable or disable user token use across their Terraform orgs to improve visibility, enforce least privilege, and simplify access management.
Melissa walks through the open Ambassador nominations and the CFP for HashiTalks, our 24-hour event where practitioners around the world share what they’re building.
Armon and Deepak caught up at re:Invent to look back at the early days of containers and infrastructure as code, and talk about how AI and agent-driven automation are changing the way builders work. They also dig into recent AWS updates and where cloud operations are headed next.
Armon and Deepak caught up at re:Invent to look back at the early days of containers and infrastructure as code, and talk about how AI and agent-driven automation are changing the way builders work. They also dig into recent AWS updates and where cloud operations are headed next.
From chaining infrastructure stages to securing Kubernetes workflows, learn how HashiCorp helps you run agentic AI with confidence. Learn what you can takeaway from this session from Kyle Ruddy and Cole Morrison at AWS re:Invent. www.hashicorp.com/en/lp/aws-re-invent-2025
Gen AI is speeding everything up, but it also makes governance and security even more important.
In this clip, Cole shares why AI is just another workload running on your cloud, and how standardized modules and policy as code help teams move faster without losing control.
This year at re:Invent, our team is highlighting a few updates we’re especially excited about. Mike shares three of them, including a major Terraform AWS provider milestone, new Sentinel policies to support compliance and security, and a great lineup of HashiCorp speakers throughout the week.
Ready to hit the jackpot in the cloud? 🎰 With HashiCorp, you’ll win big through Infrastructure and Security Lifecycle management — delivering faster, more secure cloud operations. 💸 ☁️ Check out our booth at @awscloud re:Invent, 439 to learn more. www.hashicorp.com/en/lp/aws-re-invent-2025
Non-human identities now outnumber human users by up to 50x — and security teams are feeling the impact. 😅
@KuppingerCole just named HashiCorp a leader in non-human identity management, recognizing our strengths in automation, dynamic credentialing, and zero trust access controls.
If you’re looking to get ahead of AI- and automation-driven identity sprawl, this report is a must-read.
Vegas loves a gamble, but your cloud doesn’t. ♦️♣️
Stop by at the HashiCorp booth at @AWS re:Invent for booth demos, see our sponsored sessions on stage, and connect with us at CUT and CHICA this week to win big with hybrid cloud automation. 💸 www.hashicorp.com/en/lp/aws-re-invent-2025
🌍 The #hashitalks 2026 Call for Proposals is open.
Our annual 24-hour community event is back and we want to hear your HashiCorp story. If you’ve learned something, solved something, or built something with HashiCorp tools, tell the community.
“We’re in the cloud, but we’re not using the cloud.”
That candid admission from a senior IT leader at a large insurance company reflects a common challenge: lifting and shifting legacy systems won’t deliver cloud’s full potential—or prepare teams for AI.
As multi-cloud grows, identity is becoming one of the hardest challenges for security teams. Human, machine — it all matters.
Join Ricardo Martinez at re:Invent as he shares how unified policies and continuous visibility can help teams secure identities across every environment.
The Terraform AWS Provider just surpassed 5 billion downloads — and it tells a bigger story than adoption alone.
Cloud environments are now multi-cloud, hybrid, distributed, and dynamic. Provisioning is only the first step. Security, governance, and operational consistency are what make IaC sustainable at enterprise scale.
Cloud migration shouldn’t mean cloud waste. One insurer nearly burned $100M a year—until a 3-step blueprint cut costs to ~$800/day. If your cloud spend is climbing, these steps can help you rein it in fast. Read the breakdown 💵 www.hashicorp.com/en/blog/how-to-reduce-cloud-waste-it-bo…
Learn how Fannie Mae automates cloud compliance at scale with Terraform Sentinel—managing 450+ policies across 700+ workspaces. Get their proven 5-stage process for implementing policy as code in highly regulated environments. www.hashicorp.com/en/blog/fannie-mae-process-for-developi…
Losing engineering talent is a serious business risk at this critical turning point in the technology space. Don’t let poor infrastructure and frustrating processes drive your top talent away. Instead, invest in modern tools and automation to improve developer experience and capitalize on this moment. www.hashicorp.com/en/blog/developer-attrition-developer-e…
Writing policy as code from scratch can be time-consuming. That’s why HashiCorp and AWS co-developed a library of pre-written Sentinel policies, designed to help you meet CIS benchmarks faster and enforce compliance at scale.
✅ Reduce setup time ✅ Strengthen cloud governance ✅ Move from speed or security → to speed and security
Explore the policy library in the Terraform registry.
Losing engineering talent is a serious business risk at this critical turning point in the technology space.
Don’t let poor infrastructure and frustrating processes drive your top talent away. Instead, invest in modern tools and automation to improve developer experience and capitalize on this moment. www.hashicorp.com/en/blog/developer-attrition-developer-e…
In this session, Jacob Plicque breaks down the latest updates designed to streamline workflows, improve scale, and strengthen security across cloud and on-prem environments.
Short talks. Real takeaways. Join our 15-minute tech talks at the top of every hour at the HashiCorp booth. See some of the sessions below 👇 and view the full agenda of booth sessions. www.hashicorp.com/en/lp/aws-re-invent-2025
Getting security feedback early and often in the development lifecycle is less expensive and disruptive than late-stage checks and manual security audits. Learn about the strategies and tools that can give you insights on how secure your secrets are from design to production.
With built-in support for SPIFFE, Vault further extends capabilities to issue, rotate, and validate workload identities and credentials, enabling customers to implement zero trust practices in an automated, simplified manner. www.hashicorp.com/en/blog/spiffe-securing-the-identity-of…
✅Eliminated CI/CD maintenance overhead ✅Enabled self-service infrastructure for all engineers ✅Standardized governance and compliance ✅Supported growth from 3 to 75 engineers and from 2 to 90+ workspaces
Learn how Terraform Actions built for the Microsoft @Azure provider can trigger dynamic automation workflows in your environment, all with just one Terraform apply. ⚡ youtu.be/brrHH8ts6fo
🚨 #hashitalks: Japan is live now! Hear from seven speakers on how they’re solving real-world challenges in #japan with HashiCorp tools. Join the livestream at: hashi.co/hashitalks-japan
🎤 The #hashitalks 2026 Call for Proposals is now open. Whether you’re new to public speaking or a seasoned professional, this virtual 24-hour global event is the stage to share your real-world HashiCorp stories. Submit your talk → hashi.co/hashitalks-2026
▶️ Watch Benchling's evolution from decentralized Terraform usage to a unified, modular, and automated infrastructure-as-code approach: www.youtube.com/watch?v=b8HS0TIW-2w
As more enterprises scale across AWS accounts and teams, some clear patterns have emerged about what separates secure, efficient operations from the rest.
🔹 Standardization is security. Using Terraform and Sentinel to enforce baselines across AWS accounts helps teams reduce drift and stay compliant by default.
🔹 Zero trust works best when it’s invisible. Vault enables short-lived credentials and policy-driven access that strengthens security without slowing developers down.
🔹 Automation is the real accelerator. Packer and HCP Terraform make it easier to build reusable templates, streamline onboarding, and keep environments consistent across teams.
Each of these practices helps teams scale safely on AWS by making secure and compliant operations part of their everyday workflows.
If you’re heading to AWS re:Invent, stop by Booth 439 to connect with the HashiCorp team and learn how we’re helping organizations simplify infrastructure and security lifecycle management on AWS. www.hashicorp.com/en/lp/aws-re-invent-2025
Make the easy way, the secure way. ✅ With Boundary transparent sessions quietly running in the background, developers can securely access their target resources without changing the tools or the way they work. 🪄 www.hashicorp.com/pt/blog/transparent-sessions-now-ga-in-…
Addressing the complexities of modern cloud environments requires proactive risk management, an enhanced compliance posture, and advanced zero trust cloud practices. ☁️
By asking these key questions we've gathered, gain a better understanding of how your team is currently managing risk across your multi-cloud estate and determine where you need to focus efforts. Use our list of 15 questions as a guide. ✨ 🔭 www.hashicorp.com/de/blog/15-questions-to-ask-your-cloud-…
Terraform provider for @GoogleCloud 7.0 is now GA.
This release adds new security-first features, including ephemeral resources, write-only attributes, and stronger validation logic for safer, more predictable deployments. Read more: www.hashicorp.com/en/blog/terraform-provider-for-google-c…
Heading to AWS re:Invent? Visit Booth 439 to see how HashiCorp and AWS are shaping the future of cloud infrastructure together. www.hashicorp.com/en/lp/aws-re-invent-2025
HCP Waypoint actions now support @github Actions workflows in private beta). Trigger CI/CD pipelines and Day 2+ ops from Waypoint — no YAML edits required. Simplify self-service + governance for platform teams.
AWS re:Invent is back — and this year, HashiCorp’s presence is bigger and more hands-on than ever. From live technical showcases to expert-led breakout sessions, discover how automation and security come together to help you build confidently on @awscloud. 🥳 🤝
58% of software engineering leaders say developer experience is critical to the C-suite at their organizations.
Now is your chance to get buy-in for a DevEx program, and this cheat sheet — with 13 best practices and dozens of practical resource links — will show you a proven blueprint for building that program.www.hashicorp.com/en/on-demand/13-proven-best-practices-t…
The risks of secret sprawl aren't just about breaches. They extend into significant hidden expenses that quietly drain resources and impact velocity 📉
- Developer time: Hours lost manually handling secrets or investigating exposures. - Management overhead: Complex, decentralized processes lead to wasted effort. - Firefighting: Reactive responses to incidents pull teams away from innovation. - Brand risk: Erosion of trust, delayed deals, and churn.
A single leaked secret can trigger days of downtime, even without a full breach, consuming engineering resources. Our ebook details these operational and financial burdens, and how avoid them: www.hashicorp.com/en/on-demand/the-cost-of-secret-sprawl
LPL Financial shares how it reengineered its cloud delivery model by eliminating ClickOps and scaling automation with Terraform and @awscloud.
Explore how automation became a strategic enabler, driving faster delivery, stronger reliability, and enterprise-wide efficiency across their organization. Watch the full session: www.youtube.com/watch?v=_a7q7O-HYn8
👀 Attending AWS re:Invent? Visit HashiCorp at booth #439 for sessions on infrastructure and security lifecycle management that help you build faster, strengthen security, and optimize how you run on AWS. 🏃♀️➡️ www.hashicorp.com/en/lp/aws-re-invent-2025
We've helped many companies succeed in their cybersecurity tool consolidation efforts and reduce costs. Learn some of the high-level strategies we've picked up over the years for tool sprawl consolidation and optimization efforts. www.hashicorp.com/blog/how-to-start-consolidating-your-cy…
Project infragraph will help organizations connect the dots in complex cloud environments to solve major visibility and remediation challenges. Learn more about our vision for AI. www.hashicorp.com/en/blog/building-intelligent-infrastruc…
🚨 #hashitalks: India is live now! Hear from 12 speakers from across the community on how they’re solving real-world challenges with HashiCorp tools. Tune in and learn something new → hashi.co/hashitalks-india
Visibility makes large-scale decisions and audits easier. See how SPH Media built a custom Terraform dashboard that made a huge impact on efficiency, security, compliance, and cost-effectiveness. www.hashicorp.com/en/blog/sph-media-shares-its-custom-hcp…
It’s clear static SSH keys aren’t built for scale. So how do enterprises start rethinking their SSH access workflows for the challenges in modern IT environments?
Open source secret scanners are a great start and work well for uncomplicated environments, but as organizations grow, so does complexity. From context-aware detection to automated remediation, Vault Radar helps you go beyond “finding secrets” to fully managing them.
Why do so many AI projects stall before reaching production?
In this recent Sip and Sync with Azure, HashiCorp shares how to tackle last-mile challenges in AI deployments.
From dynamic credential management to solving the “confused deputy” problem, discover how HashiCorp and @Microsoft Azure are enabling secure, scalable, and auditable AI workflows.
Tune in this Thursday, Oct 30, for #hashitalks: India. The fifth edition of this virtual event will feature real-world use cases, live demos, and community-powered sessions on #terraform, #vault, Boundary & more. ✨ From first-time builders to seasoned pros, there’s something for everyone. 🔗 hashi.co/hashitalks-india
Hybrid and multi-cloud environments are now the norm, but complexity doesn’t have to be. To stay competitive, businesses need to worry less about where services live and more about delivering customer value.
Join us in our next webinar to: ✅ Standardize workflows and service management across all environments ✅ Drive consistency with shared modules and golden images ✅ Support complex workloads like AI with platform-agnostic orchestration and service discovery ✅ Unify secrets and access management to simplify and secure hybrid deployments
The simple reality is that most organizations think they’re secure, right until the moment they’re proven wrong.
We’ve put together a list of 10 questions every business and technical leader should be asking their cloud and platform teams right now to reduce risk.
Learn how Terraform Actions built for the Ansible Automation Platform (AAP) provider can trigger dynamic automation workflows from Ansible, all with just one Terraform apply. www.youtube.com/watch?v=6Btyq31la1E
Too often in hybrid cloud environments, early warning signs of trouble are ignored. Companies wait to act. And what started as an isolated problem quickly becomes an operational nightmare.
The most common red flags include: 🚩 Constantly buying tools but nothing actually changes 🚩 Your cloud bill always surprises you 🚩 Security slows down everything — or gets bypassed 🚩Your cloud feels more complex, not less
“Since implementing Vault, I haven’t received a single notification that a secret has expired.” – Pavel Ozerov, Technical Program Manager, Riverty
With HCP Terraform and Vault, Riverty modernized its hybrid cloud, reducing approval cycles by 80% and turning infrastructure into a self-service capability. 💳 See how they’re powering payments with automation and trust 💳:
Help shape the next major innovation in the HashiCorp Cloud Platform, a unified resource graph, codenamed Project infragraph, designed to transform how enterprises understand and act on their cloud environments. www.hashicorp.com/en/project-infragraph-private-beta
Project infragraph is HashiCorp's long-term vision for AI. Hear how organizations can get visibility across infrastructure, applications, and services with Project infragraph. www.hashicorp.com/en/blog/building-intelligent-infrastruc…
Learn how Terraform Actions built for the AWS provider can trigger dynamic automation workflows in your environment, all with just one Terraform apply. ⚡ www.youtube.com/watch?v=269PPRbCj_g
Infrastructure challenges only get harder after deployment.
That's where Terraform actions bring real value. By standardizing more of your Day 2 workflows within the Terraform pipeline, you can confidently manage infrastructure over time without the manual overhead.
A perfect example? Pairing Ansible with Terraform actions for seamless, automated infrastructure and configuration management.
Multi-cloud security is complex. Are you asking the right questions? We've compiled 15 essential questions to strengthen your cloud security posture and ensure compliance across your entire infrastructure. www.hashicorp.com/blog/15-questions-to-ask-your-cloud-sec…
New in HCP Terraform and Terraform Enterprise: Org-level user token control. Easily manage or disable user API tokens to improve security and streamline permissions.
With the right guardrails in place, platform teams gain consistency and visibility across environments. That means AI-assisted code can accelerate delivery without sacrificing reliability.
Secret sprawl is a growing attack surface. As secrets spread across repos, clouds, and teams, the chance of leakage rises — and compliance gets harder.
You can’t protect what you can’t see. Automated scanning finds leaked or unmanaged credentials across source code, repos, wikis, S3, Terraform, ticketing systems, and more — then prioritizes by risk.
Vault, HCP Vault, and HCP Vault Radar bring these patterns together so organizations can reduce risk, meet compliance requirements, and eliminate operational overhead from ad-hoc secrets handling.
AI has the potential to make the cloud maturity gap even wider, according to the 2025 Cloud Complexity Report.
The majority (56%) of “transformative” organizations plan to use AI-driven automation to help deliver greater cloud success. That means:
👉 Optimizing all their cloud environments 👉 Accelerating innovation without jeopardizing security 👉 Strengthening infrastructure to turn it into a competitive advantage
Meanwhile, those in the “tactical” stage continue to struggle with:
🛑 Highly-manual, reactive, and inconsistent processes 🛑 Siloed IT environments and internal teams 🛑 Misalignment between infrastructure operations and broader business goals.
Secret exposure isn’t just a “security team” problem. It’s an everyone problem.
Here are 4 proactive methods to prevent the exposure of credentials, API tokens, and other sensitive data — helping teams avoid costly breaches before they happen:
🔒 Credential injection with Boundary + Vault Eliminate manual credential handling with just-in-time, task-scoped access.
🔒 Proactive scanning with HCP Vault Radar Detect, remediate, and prevent plaintext secrets from entering your repos or pipelines.
🔒 Secure-by-design modules with Terraform + Vault Pull secrets dynamically from Vault instead of hard-coding them into configurations.
🔒 Workload identity & dynamic credentials Use short-lived, OIDC-based credentials with Terraform and Vault to remove the need for static keys entirely.
Riverty processes payments at a global scale, but legacy provisioning and manual secrets slowed them down. By adopting HCP Terraform and Vault, they cut deployment time by 90% and eliminated the risk of expired credentials.
Ready to reduce risk and complexity? Part 2 of our cybersecurity consolidation series breaks down how to get started, from auditing your tools to building a platform-first strategy. www.hashicorp.com/en/blog/how-to-start-consolidating-your…
It’s clear static SSH keys aren’t built for scale. So how do enterprises start rethinking their SSH access workflows for the challenges in modern IT environments?
We’re live! 🚀 #hashitalks: Africa is back for its 6th edition. From first-time speakers to seasoned experts, the HashiCorp community in Africa is taking the stage to share stories, hands-on demos, and use cases centered around HashiCorp tools. Join the livestream 👉
Why do so many AI projects stall before reaching production?
In this recent Sip and Sync with Azure, HashiCorp shares how to tackle last-mile challenges in AI deployments.
From dynamic credential management to solving the “confused deputy” problem, discover how HashiCorp and @Microsoft Azure are enabling secure, scalable, and auditable AI workflows.
“We’re in the cloud, but we’re not using the cloud.” That’s what a senior IT leader at a leading insurance company stated.
Automating the old processes and lifting & shifting old apps into the cloud will not fully unlock its benefits. And it doesn’t establish a robust infrastructure platform to enable modernization initiatives like AI.
HashiCorp’s 2025 Cloud Complexity Report is here. Learn from over 1,100 IT, DevOps, platform, and software engineering leaders about the top challenges of managing multi-/hybrid cloud environments today, and what you can do to overcome them. www.hashicorp.com/en/blog/how-do-you-overcome-cloud-compl…
There’s no need to build your own manual approval customizations for your Terraform and @ServiceNow workflow. The ServiceNow Service Catalog for Terraform now includes a clean, native approval workflow for extra control and governance without the extra maintenance.
Ready to reduce risk and complexity? Part 2 of our cybersecurity consolidation series breaks down how to get started, from auditing your tools to building a platform-first strategy. www.hashicorp.com/en/blog/how-to-start-consolidating-your…
Many organizations continue to struggle under increasingly complex hybrid and multi-cloud environments.
But “transformative” organizations are empowering developers with self-service capabilities, delivering consistent security and governance, and continually optimizing resources to make infrastructure into a competitive advantage. .
European customers now have local access to HCP Terraform and HCP Waypoint. With data stored in the EU, reduced latency, and built-in compliance support, platform teams can move faster while staying secure.
Mitchell Hashimoto, one of our co-founders, just made a surprise appearance alongside Armon Dadgar! It’s a special moment celebrating how far we’ve come and the journey ahead.
The next era of infrastructure automation is here.
At HashiConf 2025, we shared our vision for intelligent operations — powered by AI and built on a unified resource knowledge graph called Project infragraph.
As AI reshapes how teams build and secure infrastructure, Project infragraph will provide the trusted data and context that AI agents need to take action with confidence.
🚀 Kick off Day 2 at HashiConf with HashiCorp Co-Founder and CTO Armon Dadgar as he explores the future of infrastructure as code in an AI-driven world.
He’ll be joined by Brendan Burns, Corporate Vice President at Microsoft, and Tyler Jacobsen, Director of Cloud Operations and Engineering at Adobe, for a dynamic conversation packed with industry insights, real-world perspectives, and a forward-looking view of what’s next in cloud infrastructure.
Provision. Configure. Operate. All in one workflow.
Managing infrastructure across hybrid and multi-cloud environments is only getting more complex.
That’s why we’re bringing Terraform and @RedHat Ansible Automation Platform closer together with Terraform actions, now in public beta.
By combining Terraform’s infrastructure provisioning with Ansible’s configuration management, teams can: ✅ Automate Day 0–2+ operations ✅ Eliminate drift and manual inventory updates ✅ Trigger event-driven workflows across both platforms
✔️ Terraform Stacks GA ✔️ AI-powered productivity with the Terraform MCP server ✔️ Packer SBOM storage and package visibility
At #hashiconf, we’re unveiling new Terraform + Packer features to help teams manage infrastructure at scale with greater speed, security, and efficiency.
Our bags are packed and we're ready to go. See you in San Francisco! If you can't make it this year, watch select HashiConf sessions live on LinkedIn and hashiconf.com on September 25 and 26. 📽️
🚀 Discover the GitHub MCP Registry: A simpler way to bring Terraform into AI workflows
GitHub’s new MCP Registry makes it easier than ever for developers to discover and add official MCP servers — including HashiCorp’s Terraform MCP server — directly into their workflows with a single click.
The MCP Registry creates a trusted home for MCP servers, helping teams: ✅ Reduce friction ✅ Accelerate provisioning ✅ Build on an open, interoperable ecosystem
Will you be heading to Hashiconf in SF in 2 weeks?
If you DM me a taco 🌮 and you are in SF during @HashiConf - I have a fun invite for you. The invite is for more than food 😬
Last year we got to speak with people from Bank of America and many other security leaders and practitioners at the conference so when they reached out for this yeae - I had to say Yes! 🙌🏾
@HashiCorp folks have been kind enough to invite @CloudSecPod to their annual conference. ❤️
Big news from HashiCorp: We just launched The Stack, our completely redesigned blog, built for the next era of cloud..
For years, our blog has been a place to share updates about our products and features. But technology businesses need more. Today’s cloud and infrastructure landscape is bigger, faster, and far more complex than ever before. You’re not just looking for release notes — you’re looking for guidance, inspiration, and proven paths to outcomes.
That’s the purpose of The Stack: to bring together insights, strategy, and stories that help practitioners, technical leaders, and business decision-makers do cloud right.
🔍 Why The Stack matters: As organizations adopt platform engineering, hybrid/multi-cloud strategies, AI, and heightened security demands, the conversation has shifted. Technology leaders need trusted resources that meet them where they are — not just in the weeds of a single product, but across the entire infrastructure lifecycle.
The Stack represents this shift. It’s not just a blog refresh; it’s our commitment to becoming your go-to hub for insights, strategy, and stories that help you navigate this ever-changing terrain.
Here’s what’s new: ✨ A sleek, white-on-black design that reflects our modern brand 🗂️ An ‘Explore topics’ menu for quick navigation by interest area 📺 A dedicated video section for those who’d rather watch than read 💡 Highlighted quotes and stories from real customers scaling with HashiCorp 📚 Author pages and tags that make diving deep easier than ever
Whether you’re solving today’s infrastructure problems or planning for tomorrow’s strategy, The Stack has you covered.
In hybrid-cloud environments, non-human identities (NHIs) outnumber humans 50:1, often lingering with unchecked access.
In this session at HashiConf, learn how Vault’s PKI automation and privilege management can help you contain the threat with David Mills and Vinithra Varadharajan.
Explore the benefits of HashiCorp Terraform and @RedHat Ansible integrations for hybrid cloud automation. Join this session at HashiConf to learn...
👀 The latest integrations between HCP Terraform and Ansible Automation Platform 🤝 How Ansible and Terraform work together to simplify Infrastructure Lifecycle Management
This session will show how to evolve from manual, insecure workflows to centralized, secure secrets management with HashiCorp Vault and Red Hat OpenShift. Learn workflows like:
✅ Securing app workloads with ephemeral secrets via VSO and the Secrets Store CSI Driver ✅ Hardening the platform with upcoming KubeKMS support for etcd encryption ✅ Strengthening OpenShift Service Mesh with Vault and cert-manager ✅ Securing quay.io with short-lived tokens via Vault and ESO
The cost of secret sprawl isn’t just measured in breaches. It shows up in lost time, slower delivery, compliance failures, and the erosion of customer trust.
The right frameworks reverse that trend before it’s too late...
We surveyed 1,100 infrastructure, security, and platform leaders around the world.
▪️98% said they’re facing cloud cost challenges. ▪️97% said they’re struggling with their cloud infrastructure. ▪️86% said managing security and compliance is one of their top challenges.
These aren’t isolated problems. They’re symptoms of cloud complexity.
Moneybox share how they evolved their infrastructure, transforming from a DIY environment into a scalable, resilient cloud-native platform. Dive into their journey of innovation and discover the real impact of efficient infrastructure strategy in fintech.
But that’s not all! This story is just a glimpse of what’s possible with HashiCorp. Whether you're planning your next migration, striving for greater agility, or enhancing reliability, HashiConf 2025 is where it all comes to life.
🧑🎓 Learn from leaders across GitHub, World Bank, Microsoft, GEICO, and more
🤝 Join hands-on sessions, real-world case studies, and live labs
🏆 Get certified on HashiCorp tech like Terraform, Vault, or Consul
How does a 180-year-old telecom defend against nation-state actors?
BT Group's Security Director for Networking shares several lessons from their HashiCorp transformation: Start with a gateway product, make security frictionless, and plan for quantum-ready infrastructure.
Join the Women in Tech lunch at HashiConf to hear from VPs, founders, and product leaders on systems they’ve built, broken, and rebuilt to create lasting impact, followed by guided networking to connect with women and allies across the community.
🚀 Automation that thinks. Infrastructure that adapts.
Join Bruno Aziza, VP of Data & AI Strategy at IBM, and Anubhav Mishra, Sr. Director of Product Management at HashiCorp, as they dive into how HashiCorp’s Infrastructure Cloud is evolving with IBM’s Data and AI strategy. See all sessions at HashiConf here. www.hashicorp.com/en/conferences/hashiconf/agenda
Go from manual ClickOps to scalable infrastructure as code (IaC) on Azure with AI in this session with Microsoft's Mark Gray.
This HashiConf session will demonstrate how AI-powered tools like Copilot in Azure and VS Code can streamline HashiCorp Terraform adoption and ongoing management. 🤖
Learn what’s next for @HashiCorp and @IBM, including our latest product updates and how joining IBM has unlocked new possibilities for customers. Catch it all in the opening keynote featuring Armon Dadgar and Hicham Mourad from @RedHat.
Last chance to get your HashiConf tickets before General Admission pricing ends. Get your conference pass now before prices increase. See you in San Francisco! 🌁 www.hashicorp.com/en/conferences/hashiconf/register
AWS GameDay at HashiConf is a hands-on, solo exercise designed for technical professionals to sharpen their skills by solving real-world cloud challenges. Experience a fast moving cloud infrastructure scenario where every decision counts.
Is security just insurance, or can it reduce risk and developer toil in measurable ways? 💭 In this session, Prerit Munjal will share how Vault, Boundary, and Consul helps define risk footprints, speed up remediation, and automate security—while improving developer experience with the organization.
Stay secure, resilient, and cost-efficient with automated policy checks in your provisioning pipelines that prevent misconfigurations, enforce compliance, and drastically reduce manual reviews (and tickets!); all without slowing your dev team down.
🤖 Learn how to deploy AI apps with Terraform the easy way with HashiCorp Ambassador & Principal Architect at Microsoft, Mark Tinderholt. In this HashiConf session, you will build a RAG chat app using Azure OpenAI, AI Search, and Terraform, all managed with HCP Terraform Stacks.
Plus, see a live demo, explore best practices, and discover how to scale and secure AI workloads in Azure with ease.
Terraform Provider for Google Cloud 7.0 is now GA!
This release brings new security-first features like ephemeral resources and write-only attributes, helping you manage sensitive data more safely in your Terraform workflows.
Many teams start with ad hoc adoption, but scaling success means shifting to centralized, automated practices. Our free assessment helps you see what’s next.
At HashiConf, Trajce Golomeov of Air France will share the company's biggest IT transformation: the evolution of legacy systems into an automated IaC platform.
By integrating Terraform Enterprise, Red Hat Ansible Automation Platform, and Vault Enterprise, Air France streamlined workflows, enforced security, and ensured scalability across hybrid and cloud infrastructure. 📊
John Weigand and Benjamin Lykins share real-world experience from working with HashiCorp customers to share best practices for optimizing run capacity, integrating with tools like Vault and CI/CD, and setting guardrails that don’t slow developers down.
The goal of every platform team is to enable developer self-service without compromising security or stability.
Learn how Waypoint and Terraform allow you to create golden workflows that let developers provision infrastructure safely with no deep operations expertise required. Speed meets compliance. www.hashicorp.com/en/blog/how-to-enable-developer-self-se…
How do you find and bring secrets under centralized management? Hear from HashiCorp Ambassador Ned Bellavance on HashiCorp Vault Radar's secrets scanning capabilities 🕵️♀️ www.hashicorp.com/en/products/vault/hcp-vault-radar
🇮🇩✨ We are live for the 2nd edition of #hashitalks: Indonesia. Join the HashiCorp community for a day of inspiring talks, real-world stories, and hands-on insights about HashiCorp tools and products from local experts & practitioners. 🎥 Tune in here: hashi.co/hashitalks-indonesia
Hear from HashiCorp Ambassador Lachlan White on Waypoint actions and how it can empower your developer community 💪 www.hashicorp.com/en/products/waypoint
Starting with Terraform Community Edition, @moneyboxteam undertook a phased migration of critical systems to HCP Terraform, enabling them to efficiently and securely scale their infrastructure. This blog post explores how their strategy delivered early efficiency gains, gradual integration, and critical business goals. www.hashicorp.com/blog/5-lessons-from-moneybox-s-terrafor…
Is the HashiCorp Vault Secrets operator insecure? Let's clear that up. Bryan Krausen, HashiCorp Ambassador shares why these common understandings exist and debunks confusion in this blog post. krausen.io/blog/
Want to know what's new with HashiCorp Terraform? Join Jacob Plicque at HashiConf, as we dive into recent updates designed to improve workflows, enhance scalability, and strengthen security across your cloud and on-premises environments. 🌐
We're honored to receive the WINergy Award from @wiz_io! Thank you, Wiz, for the recognition and for your partnership in shaping the future of cloud security. 🤝
In this hands-on lab at HashiConf, learn how to run AI workloads with ease. Led by Tu Nguyen, you’ll learn how to deploy a Nomad cluster with clients in AWS, GCP, and Azure, then run an AI job using Ollama and Granite to summarize a large dataset. 😮
Stop secret sprawl with @awscloud + HCP Vault Radar.
HCP Vault Radar scans AWS services (S3, Parameter Store, Secrets Manager) plus code repos and collaboration tools to detect unmanaged secrets, PII, and more—before they become a breach.
Built on the HashiCorp Cloud Platform, Vault Radar integrates with AWS to give teams real-time visibility and automated remediation. go.aws/3Jfi9t6
We are LIVE for Day 2 of #hashitalks: Securely Building. This is the first-ever event for the HashiCorp community of developers, builders, & security pros shaping the future of infrastructure, app delivery, & secure workflows. 🎤 Hear amazing speakers share their HashiCorp tools expertise! 👉 Watch live: hashi.co/securely-building
Your secrets just might be streaking across the internet in nothing but an S3 tag 🫣
Learn how HashiCorp Vault Radar surfaces unmanaged secrets in your repos and environments so you can rotate and revoke credentials before they cause trouble. www.hashicorp.com/en/products/vault/hcp-vault-radar
Hear from Trust Bank in the HashiDays Singapore keynote on how they think of infrastructure automation and infrastructure-as-code ⬇️ Watch the full fireside chat here: www.youtube.com/watch?v=3XuG52bGWj4&t=5s
HCP Terraform offers multiple workflows, but choosing the right one is key to efficient infrastructure management. 🔑 This HashiConf session led by Ting Li will dive deep into three core Terraform workflows — CLI-driven, VCS-driven, and API-driven — exploring their use cases, pros/cons, and best practices.
Software supply chain attacks are skyrocketing—66% exploit compromised codebases and 87% of container images contain critical vulnerabilities. Learn how HCP Packer provides comprehensive build provenance to secure your artifacts and maintain compliance throughout the image lifecycle. www.hashicorp.com/en/blog/software-provenance-why-visibil…
Compliance isn’t a checkbox, but a continuous journey. In today’s cloud-first world, dynamic infrastructure makes policy enforcement harder with every change.
📆 Join us on August 20 to learn how platform teams can shift from point-in-time audits to continuous compliance using The Infrastructure Cloud, powered by HashiCorp Cloud Platform. ☁️
#hashitalks: Securely Building is LIVE! Our first-ever event for developers, builders & security professionals shaping the future of infrastructure, app delivery, and secure workflows is happening NOW. 💡 Hear how the HashiCorp community uses HashiCorp tools in real-world projects—live! 🎥 Watch here: hashi.co/securely-building
Updating and distributing SSH keys across a fleet of machines without proper automation is time-consuming and error-prone. Learn how HashiCorp Vault and @RedHat Ansible Automation Platform work together to simplify secure SSH access to remote hosts. www.hashicorp.com/en/blog/managing-ansible-automation-pla…
Business Track sessions at HashiConf focus on how business leaders can make their developer teams more productive, strengthen security, and get the biggest ROI on cloud investments. 💸
Build your IDP, empower your devs. 📈 Platform teams are extending Terraform workflows with HCP Waypoint to unlock self-service. Now, with GA of Waypoint actions, Day 2+ ops like deploys and rollbacks are just a click away.
With @ Bharath Ram Ramanathan and @ Tejitha Raju, join us to see how HCP Terraform + HCP Waypoint simplify app delivery and boost team velocity.
Get ready for HashiConf! Plan which sessions you want to attend by viewing our full lineup of deep dive technical sessions and business-focused content.
Hear the World Bank's success story with HashiCorp Terraform and how they accelerated cloud transformation and revolutionized their platform engineering teams at HashiConf. 🌥️
Staff Software Engineer, Suneer Pallitharammal Mukkolakal, will share how the World Bank achieved an 80x improvement in deployment speed, increased security, and consistency. ⏩
Here are 10 questions every business and technical leader should be asking their cloud and platform teams right now to reduce risk, build software confidently, and stay audit-ready by default. www.hashicorp.com/en/blog/10-key-questions-about-designin…
🎤 #hashitalks: Brasil is LIVE! Tune in now for a full day of inspiring talks, real-world stories, and expert insights on HashiCorp tools straight from the vibrant HashiCorp community in Brazil! 👉 Watch the livestream: hashi.co/hashitalks-brasil
Every HashiConf ticket includes a free product certification exam which you can take on-site! 📝
Whether you're looking to validate your skills in Terraform, Vault, or Consul, this is your chance to earn a recognized credential during the conference.
Discover how Trust Bank became Singapore's fastest-growing digital bank, capturing 20% of the population in just two years and realizing a remarkable time-to-value of credit card account opening in under three minutes using HashiCorp Terraform and infrastructure-as-code.
The full agenda for HashiConf is out now! 🥳 Check out all sessions on the Cloud Engineering Tracks and Business Tracks to plan out your conference schedule 📆
Security and compliance shouldn’t just be a cost center — they should be a competitive advantage. In this session with Samuel Arogbonlo, see how HashiCorp Vault, Terraform, and Boundary automates compliance, makes audits painless, security scalable, and breaches less likely.
Quantum computing is fast approaching, and with it comes a serious cybersecurity challenge. The threat of quantum-enabled attacks is real and requires immediate preparation. Prioritize and protect your most sensitive data from quantum threats with a smart, scalable cryptography strategy. www.hashicorp.com/en/blog/prioritizing-data-for-post-quan…
Security and compliance shouldn’t just be a cost center, they should be an advantage. In this session with Samuel Arogbonlo, see how HashiCorp Vault, Terraform, and Boundary automates compliance, makes audits painless, security scalable, and breaches less likely.
What does it really mean to be secure in the cloud? Explore 10 critical questions every leader should be asking to reduce risk, enforce compliance, and build a stronger security foundation.
Explore @GitHub's nine-year journey with HashiCorp Vault from open-source to enterprise in this session at HashiConf led by Eleonore Carpentier. Learn how GitHub scaled Vault with BCDR, Autopilot, ChatOps, and more to support global operations.
Have your AI and LLM tools experienced hallucinations? 😵💫 These hallucinations can pose risks to organizations when using it for infrastructure as code development.
In this HashiConf session, Welly Siauw will share how to build reliable AI workflows by grounding LLMs with execution feedback, turning them into effective orchestrators of your development tools.
HCP Terraform just added another layer of security to state and plan files: Hold Your Own Key (HYOK). Get full visibility into your state and plan files without exposing any secrets in plain text. www.hashicorp.com/en/blog/hcp-terraform-introduces-hold-y…
Non-human identities outnumber humans, and they’re creating new security gaps teams aren’t ready for. In this blog, we unpack why NHIs matter, how secrets management fits in, and why platform + security collaboration is key. 👇 www.hashicorp.com/en/blog/what-are-non-human-identities-n…
Pre-approved “golden” Terraform modules are the backbone of secure, compliant provisioning. But how do you make sure developers follow the rules and use them? This is where Sentinel can be your organization’s compliance guardrails. www.hashicorp.com/blog/enforce-private-module-registry-us…
Save the date! We're bringing together cloud leaders from across the DACH region for a full day of real stories, fresh perspectives, and honest conversations from platform teams, cloud leaders, and experts who are shaping the future of cloud. ☁️
Join HashiCorp and partner Datadog to learn how to integrate Datadog dashboards with HCP Vault, helping you secure, monitor, and audit your secrets management at scale.
🚀 How does Skechers support 100% year-over-year e-commerce growth across 180 countries?
With a lean team, Skechers automated infrastructure provisioning and strengthened governance across both AWS and Azure. This enabled them to standardize deployments, reduce manual effort, and deliver infrastructure faster, all while maintaining control and minimizing risk at scale.
Cloud maturity shows how well your enterprise scales cloud practices. The higher it is, the bigger the benefits — less waste, lower costs, faster delivery, stronger security, and better talent retention. 📊
As internal uses for AI like R&D, code generation, and marketing grow, organizations are now moving quickly to build customer-facing agents. How can leaders be prepared to mitigate the risks that come with this new wave of AI? www.hashicorp.com/en/blog/before-you-build-agentic-ai-und…
Is your organization using too many cloud tools? Using too many tools from multiple vendors can slow your developer teams down and hurt the developer experience. 📉
💭 Hear more customer insights like these at HashiConf this September in San Francisco. Register now:
Cloud adoption is now the norm, but many organizations still struggle to realize real business value, facing challenges such as cloud waste, tool sprawl, and lost time-to-market. ⌛
Join this virtual webinar to learn how enterprises are moving from reactive, fragmented cloud programs to strategic and outcome-driven cloud operations. ☁️ events.hashicorp.com/JulDoCloudRight
Ready to reduce risk and complexity? Part 2 of our cybersecurity consolidation series breaks down how to get started, from auditing your tools to building a platform-first strategy. www.hashicorp.com/en/blog/how-to-start-consolidating-your…
Join hosts Sarah Polan and Christian Reilly as they chat with Gayatri Prakash, GM for Security and Compliance at @CloudBees. Learn key insights on managing risk in cloud adoption, from budgeting to collaboration. hashi.co/42deEsr
HashiCorp is thrilled to announce inclusion in the @ServiceNow App Store, along with a new integration that enables operators and practitioners to easily access credentials stored in HashiCorp #vault from ServiceNow. hashi.co/3oF3YkK
Terraform received a 2018 Modern Infrastructure Impact Award for private/hybrid cloud management from @datacentertt, with special note of its infrastructure as code approach. hashi.co/2GB82ud

 HashiCorp, an IBM Company
@HashiCorp













 Rosemary Wang


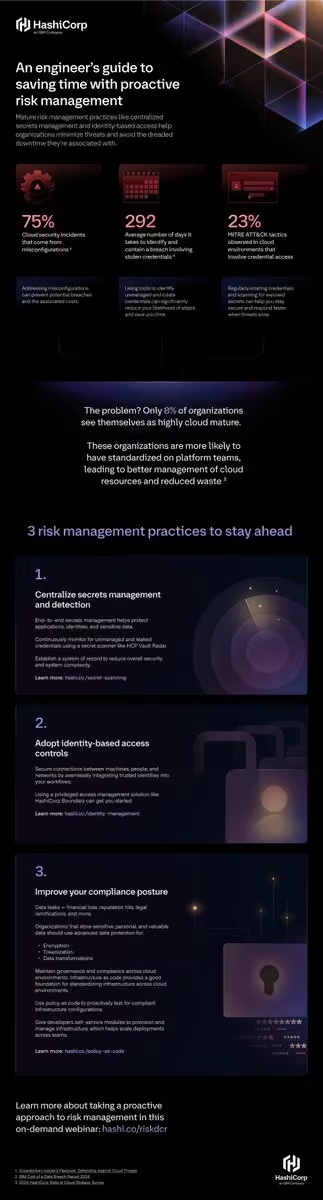




 Sarbjeet Johal






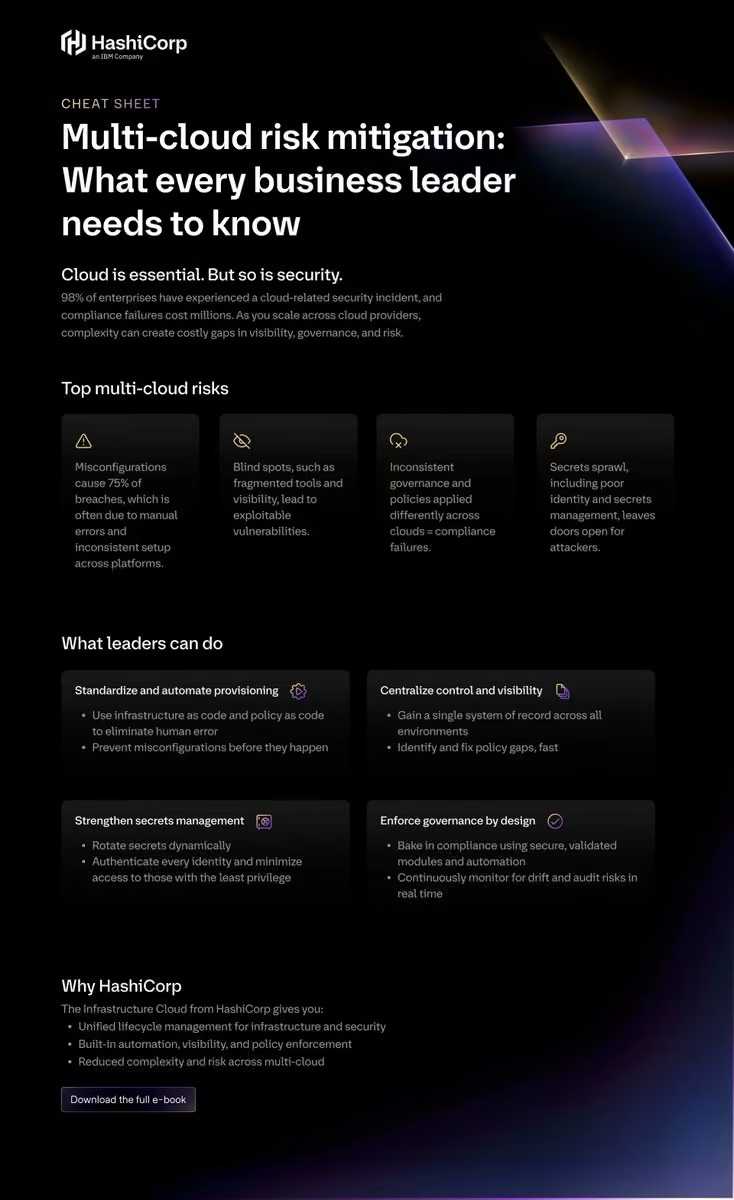








 HashiConf


 Ashish Rajan 🤴🏾