Congrats to all!
And that's a wrap! Congratulations to the Austin, TX, #cyber912 winners Devil's Data Decryptors from @DukeU, runners up Cyber Super Girls from @Stanford, and 3rd place finishers Binary Bandits from @HQAirUniversity!
Politicians, athletes, journalists, NGOs, companies... They all use corporation-owned social networks to communicate with us. Citizens shouldn't have to hand over their data to companies to read content published by public entities. Public Feeds changes that by making posts of popular accounts freely available. Read more.
Jason Healey is an American senior research scholar and adjunct professor at the School of International and Public Affairs, Columbia University. He is also a senior fellow with the Cyber Statecraft Initiative at the Atlantic Council, where he was the program's founding director. He has published many academic articles, essays, and books on the topic of cyber security and has advised on security measures for corporate, government, and military institutions. He has been identified as the first historian of cyber conflict. More on Wikipedia
Congrats to all!
And that's a wrap! Congratulations to the Austin, TX, #cyber912 winners Devil's Data Decryptors from @DukeU, runners up Cyber Super Girls from @Stanford, and 3rd place finishers Binary Bandits from @HQAirUniversity!
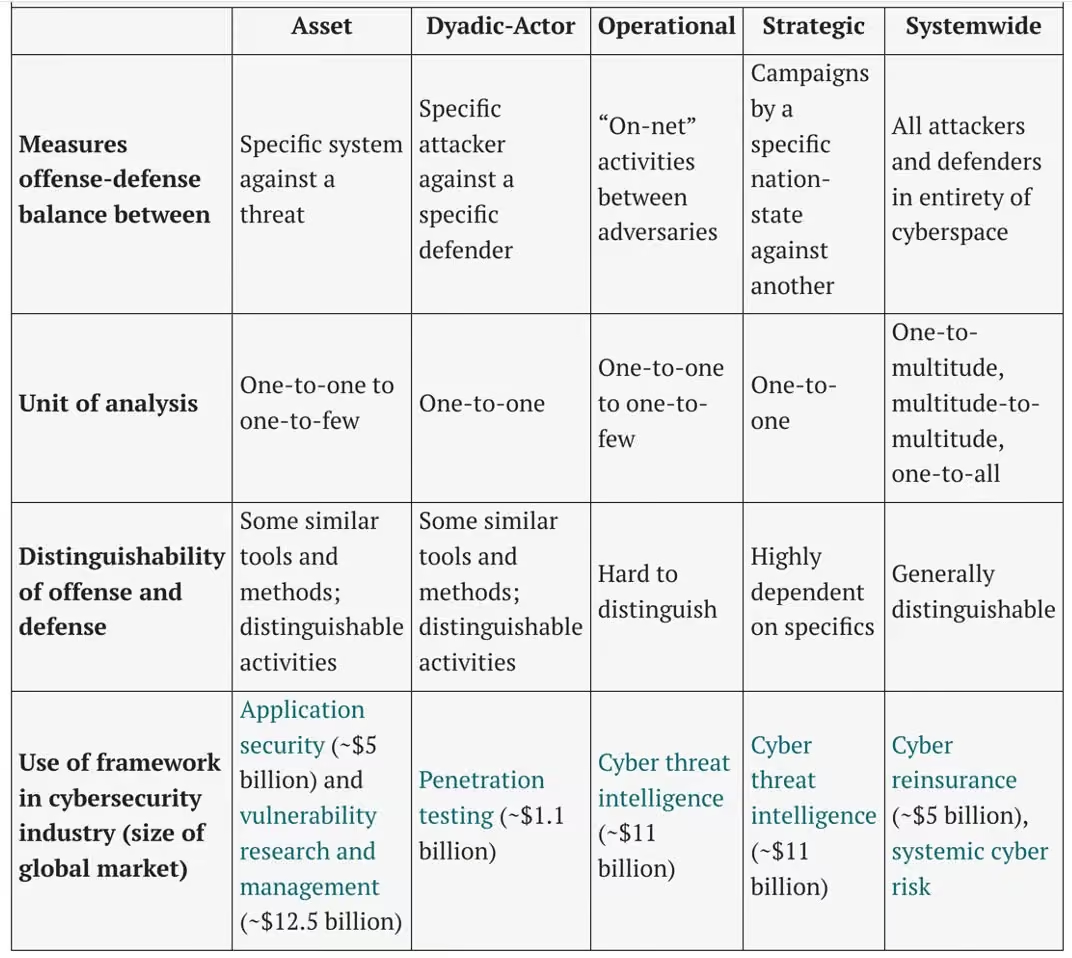
Is defense winning? How would we know if we are shifting advantages away from cyber adversaries to defenders?
This talk summarizes an initial framework and indicators to start answering the question.
youtu.be/wNXMQ-ficOc
Jay Healey reposted
Compete in #cyber912 from anywhere in the world at our flagship competition in Washington DC! Last year a virtual team, Cornfidential 🌽 from @UofIllinois placed third after a challenging final round.
My new piece @WarOnTheRocks - a framework to categorize and better understand the why, where, when of offensive cyber in warfare
warontherocks.com/2025/01/understanding-cyber-effects-in-…
The framework also highlights how much warfare drives innovation in cyber operations. When this research began in 2019, prior to Russia’s invasion, most of these cells would have been blank, just theoretical. No longer...
As crises and conflicts between cyber powers become more frequent, offensive cyber operations will continue to be used in surprising ways.
warontherocks.com/2022/01/preparing-for-inevitable-cyber-…
Jay Healey reposted
The venerable Summer Workshop on the Analysis of Military Operations and Strategy (SWAMOS), convened by @SIWPSColumbia, is now accepting applications for 2025. Further details in flyer
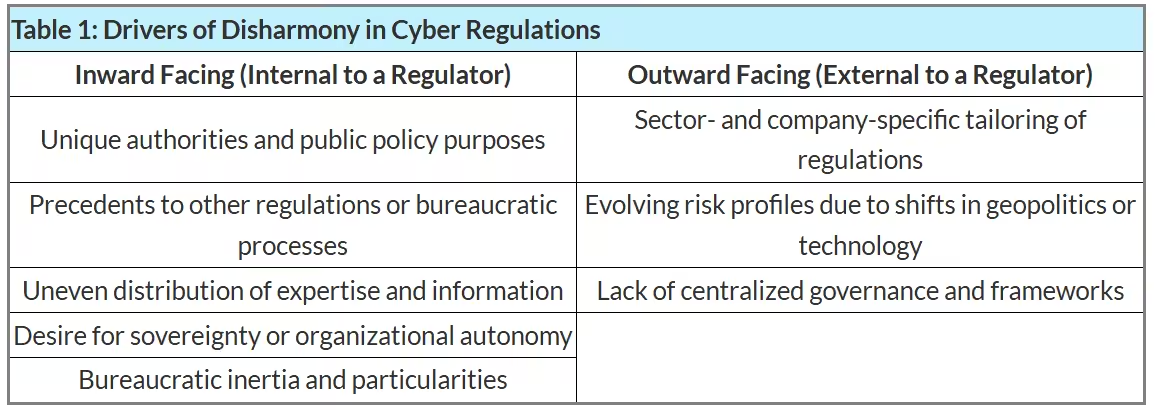
Inward-facing drivers of disharmony are internal to each regulator (like unique authorities or precedent).
Outward-facing more about the environment (such as tailoring risks to specific companies or sectors)
Read the article here: www.lawfaremedia.org/article/drivers-of-disharmony-in-u.s…
The inward-facing drivers pretty much always are negative, causing duplication & hurting security outcomes
Outward-facing often beneficial, leading to tailoring of controls to specific companies or sectors, or shifting risks
And thanks to @DabSamuel1 for all his hard work co-authoring and to @GoogleCloudSec and @Microsoft for their support
To harmonize cyber regulations, researchers and USG must first understand *disharmonies* & their causes
New article @lawfare on 5 inward-facing and 3 outward drivers of disharmony of cyber regulations
www.lawfaremedia.org/article/drivers-of-disharmony-in-u.s…
Great analysis and read!
Just look at the lights: Assad’s territory was growing poorer as opposition’s economy advanced | @Nrg8000 | www.aspistrategist.org.au/just-look-at-the-lights-assads-…
Jay Healey reposted
Upcoming @ColumbiaIGP & @SIWPSColumbia Rapid Response webinar: Experts will discuss the fall of Assad, the future of Syria, and the geopolitical implications for the region.
🌐 Wednesday, December 11
🌐 4:30 p.m. ET
With speakers: Jon B. Alterman, @JeromeDrev, @KimGhattas, & @ColumbiaSIPA’s Lisa Anderson
Register to watch it live: columbiauniversity.zoom.us/webinar/register/4717327209385…
Jay Healey reposted
What do you mean you haven't registered for #cyber912 Paris yet? 😮
The in-person event at @UnivParis8 is almost here! Registration closes December 13th, so don’t miss out. 🔒 Secure your spot and join us on January 29-31, 2025! form.jotform.com/242664845064159
Thanks to @CISAJen and team @CISAgov for visiting @ColumbiaSIPA this week to discuss all things cyber and infrastructure -- and for singing jingles for "We Can Secure Our World"
www.youtube.com/watch?v=tljH5y4bneI
Here at @SIWPSColumbia we had 30+ students, like Carina Kaplan and Christine McNeill ...
And great faculty and staff, including my deputy Erva Kan, @CartierBeth, Neal Pollard, Simha Sethumadhavan, and Rachel Cummings
And had time for a short visit here in Suite 1337 (yes, really) at SIPA
Super well deserved by this amazing research team!
This week the @CSS_ETHZurich was awarded the "Excellence in Cybersecurity Research Award" during the Global Cybersecurity Conference (@swisscyberinst) in Zurich.
Congrats to @CyberMyri, @eubenincasa, @JScurrell, @Maxwsmeets, @LenMaschmeyer, Clemence Poirier, and Sarah Wiedemar.
Biggest surprise for me in @ColumbiaSIPA New York Cyber Task Force in 2016, for a more defensible cyberspace at scale
In DC, the conversation always, "the cloud is great, but..."
In NYC, @philvenables @hashtag_cyber & others: "the cloud is great & just see what's next!"
Thoughts on cloud security and careers in cybersecurity.......
Jay Healey reposted
.@GovKathyHochul on protecting New York from cyber threats: “It is happening in real-time. So I view this as just an important part of my responsibility as the governor of New York.”
Watch her @ColumbiaIGP Spotlight Interview with Secretary @HillaryClinton during @SIPACyber’s Cyber Conference on Cyber Regulation and Harmonization: www.youtube.com/live/ltI0iNNeovQ?t=8323
Jay Healey reposted
Paris, croissants, and cybersecurity? Oui, it's happening! Join us in Paris on January 29-31, 2025, for #cyber912 with @geode_science and @UnivParis8. Register now and kick off your new year with some serious cyber strategy! form.jotform.com/242664845064159
This will be such an amazing course!
The internet is evolving faster than most nations can adapt. Professors @camillefrancois and Jen Weedon are diving into how we can maintain the safety of ourselves and our institutions amidst this rapid change.
doc.sis.columbia.edu
Great article by @VirpratapVS to classify cyber incidents in the Cyber Power Matrix dataset to my decade-old spectrum of state responsibility.
Nicely done, @IISS_org!
www.iiss.org/cyber-power-matrix/the-six-degrees-of-cyber-…
Final panel @ColumbiaSIPA conference on regulating cybersecurity
Moderated by Harry Krejsa!
Day 2 of @ColumbiaSIPA conference on cyber regulation and harmonization!
Kicking off with @KembaWalden former acting @ONCD im conversation with former dean Merit Janow, non chair of Mastercard
www.youtube.com/live/8BENyUNYt54
Jay Healey reposted
Today, NCD Coker spoke at @ColumbiaSIPA’s Conference on Cyber Regulation and Harmonization. He underscored the need to streamline well-meaning regulations to provide more security for the American people and more clarity & efficiency for American companies
www.whitehouse.gov/oncd/briefing-room/2024/11/13/remarks-…
First panel kicking off for @ColumbiaSIPA conference on cyber regulation and harmonization!
And our former (maybe future?) adjunct faculty Colin Ahern, chief cyber officer @newyorkstate
And expertly moderated by my co-instructor this semester, Evan Wolff, Crowell & Moring
Next up: regulatory harmonization for the finance sector!
Moderated by Neal Pollard @ColumbiaSIPA !!!
Last panel for today: regulating AI for cybersecurity...
With Art Lindo @federalreserve kicking off...
Jay Healey reposted
Starting soon: I’m chatting with Anne Neuberger about cyber security and regulation harmonization. Then right after, Secretary @HillaryClinton interviews @GovKathyHochul.
Watch live starting at 10:45 am ET: x.com/i/broadcasts/1zqKVYMvVPpxB
Next up: a conversation with Keren Yarhi-Milo @ColumbiaSIPA and Anne Neuberger
Starting on first 100 days for incoming administration
Follow on the livestream!
Hope you can join tomorrow and Thursday on the
@ColumbiaSIPA livestream!
Day 1, 13 November: www.youtube.com/live/ltI0iNNeovQ
Day 2, 14 November: www.youtube.com/live/8BENyUNYt54
Join us at @ColumbiaSIPA for our Conference on Cyber Regulation and Harmonization!
Featuring a spotlight interview by Secretary Hillary Clinton @ColumbiaIGP w/ @GovKathyHochul
Dates: 13-14 November
Register through www.eventbrite.com/e/conference-on-cyber-regulation-and-h…
Hope you can join tomorrow and Thursday on the
@ColumbiaSIPA livestream!
Day 1, 13 November: www.youtube.com/live/ltI0iNNeovQ
Day 2, 14 November: www.youtube.com/live/8BENyUNYt54
On 13-14 November, join us at @ColumbiaSIPA for a can't miss cyber-regulation conference
Featuring a spotlight interview by Secretary Hillary Clinton @ColumbiaIGP w/ @GovKathyHochul
Plus Harry Coker @oncd, Merit Janow, @KembaWalden46, & many more!
www.eventbrite.com/e/conference-on-cyber-regulation-and-h…
Yep: important for understanding "brandishing" cyber capabilities to scare a rival
Argument often oversimplified: "use a capability & adversary patches, making it useless"
In reality, old vulns may remain useful enough for long enough time to brandish
www.lawfaremedia.org/article/lingering-power-cyber-brandi…
The U.S. and its Five Eyes intelligence partners have released a list of 2023's most exploited vulnerabilities:
MOVEit and Log4Shell *still* in the top 15.
www.cisa.gov/sites/default/files/2024-11/aa24-317a-2023-t…
Jay Healey reposted
Join us at @ColumbiaSIPA for our Conference on Cyber Regulation and Harmonization!
Featuring a spotlight interview by Secretary Hillary Clinton @ColumbiaIGP w/ @GovKathyHochul
Dates: 13-14 November
Register through www.eventbrite.com/e/conference-on-cyber-regulation-and-h…
Kickoff panel on 13 November for @ColumbiaSIPA cyber regulation conference!
State of cyber regulation: Colin Ahern @NYGov , Chris Hetner @NACD, Nick Leiserson @ONCD, and Evan Wolff @Crowell_Moring
Register online or watch livestream (link to come)
www.eventbrite.com/e/conference-on-cyber-regulation-and-h…
Day 2, 14 November, of the @ColumbiaSIPA cyber-regulation features 9:45am panel on regulating healthcare cybersecurity
Check out this all-star lineup:
@beauwoods, @iamthecavalry;
Drew Hanchett, @HealthNYGov;
Ari Schwartz, @VenableLLP;
@CartierBeth, the moderator!
Closing panel: 14 November, 11:15am, on smart cyber regulation for the energy transition!
We got the best for this:
@JasonBordoff of @ColumbiaUEnergy;
Sean Ewart, Assistant Secretary for Energy @newyorkstate;
Michele Guido, @SouthernCompany; and
@HarryKrejsa, @cmist_cmu
On 13-14 November, join us at @ColumbiaSIPA for a can't miss cyber-regulation conference
Featuring a spotlight interview by Secretary Hillary Clinton @ColumbiaIGP w/ @GovKathyHochul
Plus Harry Coker @oncd, Merit Janow, @KembaWalden46, & many more!
www.eventbrite.com/e/conference-on-cyber-regulation-and-h…
And thanks to our amazing partners and co-sponsors!
@NYGov , @ColumbiaIGP, @CUSEAS, @DSI_Columbia, @Google Cloud, @Microsoft, @jpmorgan, @VenableLLP, and @Kyndryl
We still have sponsorship slots left ... DM me if interested!
Jay Healey reposted
Our panel on the Sigma Wargames and the Johnson administration's decisions to escalate in Vietnam is now online! @LTGHRMcMaster @MarkMoyar @HooverInst @HooverArchives
www.youtube.com/watch?v=BipfLfrdm6Y
Adversary offensive cyber to disrupt logistics is longstanding DoD concern ... back to "Dutch hackers" hitting DoD logistics, Desert Shield/Storm in 1991
Within 10 years, focus shifted to Taiwan scenario since TRANSCOM connects to logistics companies using unclassified networks
"An adversary might use cyber capabilities to disrupt the flow of logistics into a military theater," writes Jason Healey. tnsr.org/2024/08/cyber-effects-in-warfare-categorizing-th…
This is offensive cyber operations in the category of "before hostilities"
Alongside attacking information, networks, and IT systems as well as undermining trust in institutions or eroding morale ... generally shaping the strategic environment for victory without fighting
"Another way to exploit information is by stealing technological advantages that are useful to the battlefield," writes Jason Healey. tnsr.org/2024/08/cyber-effects-in-warfare-categorizing-th…
The other two main categories in the Framework of Cyber Operations In Warfare are
During Hostilities: Before Battle or in the Rear Echelon
(Phases 2 and 3)
and
During Hostilities: Battle
Jay Healey reposted
What's better than a Paris Olympics? 🤔 a Paris #cyber912 of course 🇫🇷. Registration is LIVE for #cyber912 Paris held January 29-31 in partnership with @geode_science.
Register to compete or judge here: form.jotform.com/242664845064159
Amazing to teach with this crew!
@ColumbiaSIPA class, Cybersecurity: Technology, Policy, and Law taught by Charles Carmakal @Mandiant, Evan Wolff @Crowell_Moring & me ... and we had @robknake join for the night!
The student team was presenting on their findings from the 2014 hack of Sony Pictures.
Charles worked part of that investigation and Rob was able to share how the White House coordinated the response and called out the North Koreans.
Jay Healey reposted
The deadline for our spring term is tonight at 11:59pm ET. Don't miss your chance to be a part of next year's cohort of future global leaders.
apply.sipa.columbia.edu/apply/
As a J-Term student, Janvi Manek MIA '25 found her place on campus among an intimate cohort of students and friends.
The application deadline for SIPA's spring term (J-term) entry is October 15.
apply.sipa.columbia.edu/apply/
Just came across this para from Bob Jervis and me @TXNatSecReview
A "Balkanized" internet: not just split by national borders but cursed by long and selective memories of past insults
tnsr.org/2020/09/the-escalation-inversion-and-other-oddit…
"Within 15 years of the invention of powered flight, nearly all of the doctrinal missions of an air force had been not just discovered but integrated under a single commander in battle: Billy Mitchell at the 1918 battle of Saint-Mihiel"
Jason Healey introduces a novel analytical framework to assess offensive cyber operations based on the circumstances of their use across the different phases of war. tnsr.org/2024/08/cyber-effects-in-warfare-categorizing-th…
1st cyber conflict was 1986 (Cuckoo's Egg) & 1st offense-defense cyber unit working for combatant command was 1995 (609th IWS)
We're 40 years in & still floundering on doctrine and thinking about offensive cyber operations...
USAF for example has for decades wanted to normalize cyber, but flip every few years on what "normal" means
Is cyber like intelligence or space? A strategic capability able to affect anywhere on earth or a tactical capability to aid the battle?
www.airandspaceforces.com/article/from-cybernetics-to-cyb…
That led to flip flops of cyber being assigned to AIA, AFSPC, strategic air forces, ACC and back again...
Yes, this might sound super basic. But the article puts this, and a 14 other categories of offensive cyber operations in warfare into perspective.
With this framework, easier to compare OCO on, near, and far from the battlefield
"Techniques to exploit information could include stealing an adversary's battleplan or trying to understand the location of its tactical assets." tnsr.org/2024/08/cyber-effects-in-warfare-categorizing-th…
Look forward to diving into this new work from Vir and @IISS_org!
Feels like every sentence of this para has big lessons for understanding cyber conflict
From "Hawkish Biases and Group Decision Making" (International Organization 76, Summer 2022, pp. 513–48) www.cambridge.org/core/journals/international-organizatio…
Regulation is the most complex, politically sensitive cybersecurity measure ever undertaken by the US
The most important step @ONCD can take is starting a cyber-regulation strategy & creating a new office to drive smart regulation and harmonization
www.darkreading.com/vulnerabilities-threats/what-white-ho…
Government mandates touch at the heart of the role of government in a free society -- far more inherently political than other cybersecurity initiatives
Decisions and tradeoffs must be made by principals of the NSC and NEC
ONCD has subordinate strategy and dedicated office for cyber workforce
Time to do the same for regulation and harmonization, a more complex and politically sensitive topic!
My first article for @DarkReading -- hope you enjoy ... and thanks to the team there...
Looking forward to Cyber Beacon this year @NDU_EDU
www.eventbrite.com/e/cyber-beacon-2024-learning-from-the-…
A fun, wide-ranging talk on intelligence past and future!
NEW PODCAST 📢
In the third video edition of The Sydney Dialogue Summit Sessions, @Jason_Healey and Admiral Michael Rogers (Ret'd) discuss all things intelligence.
The conversation explores Michael's career in intelligence, how signals intelligence has changed over time, whether AI will result in a substantial shift, and much more!
👀 Watch the episode now ➡️ www.youtube.com/watch?v=kYLvmedoAco
Jay Healey reposted
The Vice Chairman visited @Columbia @ColumbiaSIPA in New York City for discussions on international relations & regional conflicts - diplomacy & working with our Allies & partners is the basis for our global power & collective security.
If you haven't read it, go buy Offensive Cyber Operations by @ILDannyMoore
I'd been working on this framework since 2019 but hadn't included attacks on trust, which are a major feature in that book
I had to add two additional columns to the framework but so much better!
"Offensive cyber operations that take place before battle or in the rear echelon can also be used to erode trust in weapons systems or physical infrastructure." tnsr.org/2024/08/cyber-effects-in-warfare-categorizing-th…
Buy your copy here!
It's been on the curriculum @ColumbiaSIPA for two years, for the course on fundamentals of cyber conflict I teach w/ @GregRattray_
www.amazon.com/Offensive-Cyber-Operations-Understanding-I…
Looking forward to this report! The draft was excellent. If you follow submarine cables, you'll want to read this!
Much of offense cyber in battle similar to other capabilities: hacking drones instead of EW or shotgun
Where OCO could be radically different is ability to disrupt or commandeer at scale - affecting *all* targets w/same vuln
Jason Healey distinguishes between an operation that is intended to attack the information or system itself and an operation that is attacking the trust that the other side places in the information or system - or both. tnsr.org/2024/08/cyber-effects-in-warfare-categorizing-th…
Doing so is likely both extraordinarily hard & highly uncertain
But not impossible, especially with sufficient prep time and in the hands of a commander willing & able to take the risk and integrate cyber
Jay Healey reposted
Meet tomorrow's global leaders, our 2024-25 @ColumbiaIGP Student Scholars! These students will engage with our Faculty Advisory Board and IGP Carnegie Distinguished Fellows this year in pursuit of understanding and solving the world’s toughest problems. Onward!
Get to know them here: igp.sipa.columbia.edu/students/igp-student-engagement
@HillaryClinton | @YarhiMilo | @ColumbiaSIPA
This will be a fascinating event!
Come join us on October 8th as we explore declassified documents from the Sigma wargames--the games that warned the US that Vietnam would be a costly, bloody quagmire, but were ultimately ignored. Why? @LTGHRMcMaster @MarkMoyar @HooverInst @Stanford @HooverArchives #archives
This is a great read! Like everything else from Kim it is thoughtful, balanced, factual, and well-cited...
Our faculty member @KimberlyMarten (@BarnardCollege) published an article in @TWQgw on Russia-Israel Relations since the attacks on Oct. 7, 2023 harriman.columbia.edu/kimberly-marten-in-the-washington-q…
My favorite example: "In an exercise in the mid-1990s," the 609th Info Warfare Squadron, "the first combined offense-defense cyber unit stole the blue-force’s Air Tasking Order within two hours, giving them perfect knowledge of the next day’s raids."
"Techniques to exploit information could include stealing an adversary's battleplan or trying to understand the location of its tactical assets." tnsr.org/2024/08/cyber-effects-in-warfare-categorizing-th…
Jay Healey reposted
Very exciting news from @ColumbiaSIPA!
We’re updating our curriculum to respond to a changing world.🌎
Read about the enhancements here: www.sipa.columbia.edu/news/introducing-columbia-sipas-enh…
Starting in Fall 2025, Columbia SIPA is launching an enhanced curriculum designed to take global policy education to the next level.
At a time when other schools are adding one-off programs or ancillary studies, we’re addressing change comprehensively to meet the evolving needs of students, the workforce, and our world.
Learn more ⬇️
www.sipa.columbia.edu/news/introducing-columbia-sipas-enh…
Pagers on fire? Don't forget "Hackers can turn your printer into a flaming death bomb"!!!
Salvatore Stolfo and Ang Cui @CUSEAS in 2011 used unsigned firmware to steal info from printers & even burn paper being printed
www.youtube.com/watch?v=njVv7J2azY8
Original @MSNBC article was balanced: nbcnews.com/technolog/exclusive-millions-printers-open-de……
But headlines got more unhinged over time...
Ang continues the fight for embedded-device security @redballoonsec !!!
x.com/redballoonsec
If pager explosion is cyber (I'm skeptical), highlights sometimes overlooked reason why offense has so many advantages:
Common-mode vulnerabilities
Single offensive operation can hit multitude of targets, EVERY vulnerable device at once
www.lawfaremedia.org/article/understanding-offenses-syste…
Too often, analysis treats OCO as one-on-one: Stuxnet or Sony, a single attack vs single target
Most impactful attacks are usually one-on-multitude: Morris Worm, SQLSlammer, NotPetya
Unless we specifically code for & analyze one-on-multiple, we'll miss these larger dynamics
"Sickos can wreak death and destruction from thousands of miles away!"
👀
"Overheating" lends itself to explanation of offensive cyber
"New shipment" lends itself to supply-chain insertion of explosives, detonated remotely
"The affected pagers were from a new shipment that the group received in recent days, people familiar with the matter said. A Hezbollah official said hundreds of fighters had such devices, speculating that malware may have caused the devices to heat up and explode. The official said some people felt the pagers heat up and disposed of them before they burst." www.wsj.com/world/middle-east/hundreds-of-hezbollah-opera…
Someday soon, maybe today, someone like @drbvaler will throw playground insults at your work
On that **same day** may you be lucky enough to have have the most cyber-savvy head-of-state @IlvesToomas call out the same article as a must-read...
Here's leadup to this quote. So much of our experience w/offensive cyber happened when states didn't invade for territorial gain
Russia's full invasion of Ukraine has given examples of new kinds of offensive cyber. More great-power crises likely to drive more OCO innovation
"If conflicts between cyber powers become more frequent, offensive cyber operations will continue to be used in surprising ways." tnsr.org/2024/08/cyber-effects-in-warfare-categorizing-th…
So much of my work is developing frameworks
EVERY scholar & practitioner has some part of the right answer. Good frameworks allow us to understand who is most right under which circumstances
Cyber is new. Something can be both MYTH & TRUTH in different situations over time
Jason Healey distinguishes between an operation that is intended to attack the information or system itself and an operation that is attacking the trust that the other side places in the information or system - or both. tnsr.org/2024/08/cyber-effects-in-warfare-categorizing-th…
Jay Healey reposted
.@Jason_Healey knows his stuff. DO read
www.lawfaremedia.org/article/measuring-policy-effectivene…
The main advancement of the paper is this framework for offensive cyber in wartime
Too many disagreements about if and how cyber will matter in warfare are because we aren't precise about the where, what, and why ...
Thanks to the great TNSR editors and the reviewers
Jason Healey takes a look at the past and future of offensive cyber operations. tnsr.org/2024/08/cyber-effects-in-warfare-categorizing-th…
"Risk = Hazard + Outrage ... the most important equation in risk management"
Phil put me onto the great work of psandman.com in 2002 & I've been a devout follower since...
6 Truths of Cyber Risk Quantification
"If the cost of doing the risk analysis exceeds the cost of implementing the control then just implement the damn control."
www.philvenables.com/post/6-truths-of-cyber-risk-quantifi…
Jay Healey reposted
Hey, future global leaders! @ColumbiaSIPA applications for Fall 2025 are now open.
Join us in New York City at the world’s most global public policy school. Apply here: apply.sipa.columbia.edu/apply/
Applications for Fall 2025 are now open. Your chance to join the next generation of global leaders in New York City starts today!
Apply here:
apply.sipa.columbia.edu/apply/
Thrilled to have moderated an excellent panel on hybrid threats for @ASPI_org #thesydneydialogue
With @Braze_Baiba, @JamesAppathurai, @rajepant1 and help of @Alex_Caples1 @BartHoogeveen @BassiJustin
"Greater exposure of naval battles [makes them] faster, more decisive, more one-sided, and more sensitive to differences in materiel than battle outcomes on land."
My colleague Steve Biddle @SIWPSColumbia based on all 573 known naval battles, 1649-1988
www.tandfonline.com/doi/full/10.1080/09636412.2024.2363533
I got to read an embargoed copy and just WOW. The quality and quantity of data and analysis is amazing...
LOL. Hoody froody froo
@SMBCComics
www.smbc-comics.com/comic/tongue
Kicking off with @ONCD Harry Coker!
Next @defcon fireside keynote @thedarktangent and @CISAJen ...with Jen making cocktails
Big point: calling them "vulnerabilities" diffuses responsibility from those who write bad code. We should call them defects to make it clear exactly what they are and who is responsible.
I WANTS!!!
Trying to get your hands on this year’s @ONCD #badge? Find us on GitHub to become an Open Source Software Security Plankholder! #challenge
Keynote fireside kicking off @defcon with @thedarktangent and Anne Neuberger NSC...
Jeff looking comfy in his grandpa la-z-boy
Why yes, new @OnitsukaTiger just for @BlackHatEvents and @defcon ...
Policy workshop kicking off @BlackHatEvents with Lauryn @ONCD, Nand CTO @CIA, Daniel @McKinsey, Hans @enisa_eu
Co-hosting with @AmitElazari and her great team at Open Policy Group!
Fabulous questions from the audience on policy, AI, and national strategies...
Phew ... That amazing feeling when you first practice your 40-minute @BlackHatEvents presentation ... and it finishes w/plenty of time for Q&A
Going to Black Hat and want to talk policy? A few great events (1/3)
**Policy Track Meetup -- Wednesday, 7 August, 10:20am to 11am, Breakers C. I'll be co-hosting with the Policy track for an informal meetup and networking!
Hope to see you there!
One of the clearest examples is Mean Time to Detect
MTTD is a direct measure of whether defenders are better at finding than adversaries are at hiding) which has decreased markedly over time, even when controlling for ransomware
(sources: @Mandiant @VZDBIR)
If you've ever felt frustrated that it seems we're not making progress, that we're falling farther behind, then this talk is for you
With frameworks like this, we as defenders can track how we're doing ... and learn that in many areas we're doing better than you may think!
Jackie's work is amazing! Apply to join the team doing smart, informative (and super cool) work...
I'm looking for an intern for our wargaming and crisis simulation initiative! Help us build the archive, run wargames, and contribute to groundbreaking research on national security. @HooverInst @Stanford
www.hoover.org/hoover-student-fellowship-program
Teller Window blog of @NewYorkFed published a summary of the FRBNY-@ColumbiaSIPA conference on Cyber Risk to Financial Stability!
Thanks to @VirpratapVS, Trish Mosser, & Christine McNeill
tellerwindow.newyorkfed.org/2024/08/01/conference-on-cybe…
Can't wait to see what @SecureAerospace has in store for us this year!
We appreciate every opportunity to talk about our mission to Build-Inspire-Promote.
We created a short video thanks to the cinematic expertise of @cyberpilot22, @cybertestpilot & @therealBantha.
We take our mission seriously...just not ourselves.
Enjoy!
What questions do you have for Director Harry Coker, @ONCD?
I'll be moderating his fireside chat at @defcon on Saturday, 10 August, at 1pm in Track 1. Let me know what's on your mind!
Jay Healey reposted
📆 July 31 online: We host: Moving Cyber Regulatory Harmonization from Concept to Reality www.rstreet.org/events/moving-cyber-regulatory-harmonizat… with a recorded keynote @SenGaryPeters, our @Brandon_J_Pugh, @Jason_Healey @ColumbiaSIPA, Vincent Voci @USChamber, Elizabeth Irwin - @WhiteHouse
Jay Healey reposted
🔴 LIVE NOW: A Rapid Response State of the Race analysis, with experts discussing the US presidential election.
x.com/i/broadcasts/1ynJODQkmnVxR
@ColumbiaSIPA Dean Keren @YarhiMilo
@TimNaftali
@CNN Anchor @AbbyDPhillip
@Dr_CMGreer
@ProfSaunders
Robert Shapiro
Jay Healey reposted
We’re in the middle of an unprecedented election season.
Join @ColumbiaIGP for a Rapid Response State of the Race analysis with @ColumbiaSIPA Dean Keren @YarhiMilo, Faculty Scholar and CNN Presidential Historian @TimNaftali, @CNN Anchor @AbbyDPhillip, and @Columbia professors @Dr_CMGreer, @ProfSaunders, & Robert Shapiro.
Watch it live: twitter.com/i/broadcasts/1ynJODQkmnVxR
Dear Style Guides: Always capitalize "Internet" when referring to the first single internetwork to connect humanity
We capitalize Earth to distinguish it from mere earth
Removing the capital "I" demotes the Internet to just another resource we’re going to exploit till it sucks
Honored to join this event to help newbies and others looking to connect!
TL;DR -- In any tightly interconnected, highly interdependent system, like the Internet, cascading failures can come from any direction. Most failure modes cannot be known in advance and only become known after failures
It is a Charles Perrow Day. A book written in 1984 that I cited in my 1995 thesis.
Though CRWD failure isn't an attack, such dynamics are one reason why system-wide, offense has easier time than defense
This time it was CRWD, but there are an uncountable number of other common mode vulnerabilities (see Heartbleed)
www.lawfaremedia.org/article/understanding-offenses-syste…
Thanks Vir! So glad we could write this together...
Jay Healey reposted
Join me and @PrincetonSPIA Dean @AmaneyJamal tomorrow, July 18 at 1pm ET as we discuss how to foster constructive conversations on campuses about the Israel-Hamas War.
Register here: events.ceip.org/thecampusandtheisraelhamaswar
@Aarondmiller2 @CarnegieEndow
Jay Healey reposted
🗓️ JOB REMINDER 🗓️
Interested in a leadership opportunity at ASPI as the new Director of @ASPI_CTS?
This senior executive role will lead an impactful team in addressing emerging security challenges across the Indo-Pacific 🌏
Don't miss out! Apply now ➡️ www.aspi.org.au/jobs-at-ASPI/director_CTS_2024
Thanks for sharing! #hammercon rocks...
Hear @Jason_Healey "Framework to Understand Offensive Cyber Operations in Warfare" at #hammercon 2024.
www.youtube.com/watch?v=x4FRgBSmqfQ
Cool resource, thanks GCA!
We’ve added 300 free tools in a “Threat Taming Tool Collection (T3C)” within ACT to help organizations combat cybersecurity incidents, even if they can’t afford a commercial #threatintelligence service.
Visit: globalcyberalliance.org/act-threat-taming-tool-collection/
#civilcyberdefense
Looking forward to being there!
We've got a great line-up of confirmed speakers for OODAcon 2024 to include keynotes with Ambassador Nathaniel Fick and Thomas P.M. Barnett, PhD who wrote the Pentagon's New Map book.
Other confirmed speakers include: James N. Miller, Amr Awadallah, Will Hurd, Al Tarasiuk, Guillaume Verdon, Kristin Del Rosso, Molly Just-Behr, katharina mcfarland, Dara Ladjevardian, Johnny Sawyer, Simone Syed, and Andrew Côté.
Topics on the agenda include:
Cyber Diplomacy for Cyber & AI Safety
Beyond Human Limits: Charting the Future of AI Innovation
Materializing Tomorrow: Advances and Challenges in Materials Science
Disruption as a Catalyst: Tech Innovations That Will Solve Global Challenges
China – Current Threats and Emerging Risks
The Age of Exponential Blockchain Disruption
Cross Domain Innovation – Driving Deep Tech Convergence
Touching the Void: Persona Based AI and the New Age of Expertise
The Cybersecurity Dilemma: Board Expectations for Managing Cyber Risk
Annual Global Threat Brief
The Net Assessment for the Future
Navigating the Future: Strategic Insights and Global Trends from America’s New Map
Register today and join us in Reston VA on November 6, 2024.
www.oodaloop.com/oodacon-2024/
Jay Healey reposted
when I am meeting people who express an interest in digital investigations, their main q's regard our Digital Sherlocks program. where can they apply? and when?
answers - RIGHT HERE: form.jotform.com/241615280405146
and RIGHT NOW! (by July 3)
Only 3 days left to apply to the #digitalsherlocks 2024 cohort! Learn open-source investigative techniques, geolocation, and so much more directly from our experts and connect with other OSINT practitioners from around the world.
DEADLINE JULY 5 🚨form.jotform.com/241615280405146
Thanks for sharing! Natsec-linked ransomware seem likely to challenge large-n datasets in international relations. Code as criminal or natsec?
Since 2014, some % of RU-linked ransomware has some natsec purpose, even if just shitstirring. And now this China example...
We knew some ransomware attacks are a cover for nation-state espionage but not much has been written about it. Here's good research from @RecordedFuture & @SentinelOne about Chinese APT that deploys ransomware in last stage of spy op for purposes of financial gain/distraction/erasing evidence of spying www.sentinelone.com/labs/chamelgang-attacking-critical-in…
OSINTers, apply now for this coolest of programs!
Want to be a part of world’s largest series of free, online trainings dedicated to those focused on combatting dis- and misinformation through OSINT techniques?
Apply for the next cohort of Digital Sherlocks!
Applications are open until July 5th!
dfrlab.org/training/
Got a new rack to organize my challenge coins ... a great addition to the office!
Looking forward to reading this!
🚨 NEW REPORT 🚨 In “Reasonable” Cybersecurity in Forty-Seven Cases: The Federal Trade Commission’s Enforcement Actions Against Unfair and Deceptive Cyber Practices, Isabella Wright and Maia Hamin crunch the numbers on FTC cyber enforcement actions.
dfrlab.org/2024/06/12/forty-seven-cases-ftc-cyber/
Congrats Camille!
Congrats to Professor and @ColumbiaIGP affiliated faculty member @camillefrancois MIA '13 on joining @YGLvoices — a 3-year program aligned with the @wef that accelerates the impact of leaders working to shape a more inclusive and sustainable future.
Love how this article dives right in!
"Simply put, software will never be perfect. Efforts to develop bug-free software are complicated by many factors... So, for software developers and policymakers, the question then becomes, 'How good is good enough'?"
Another great entry in the @lawfare #securitybydesign project
www.lawfaremedia.org/article/standards-of-care-and-safe-h…
Jay Healey reposted
Another great @ColumbiaSIPA KENT Global Leadership Program @JGuehenno, with particular focus on #technology this year, including a new simulation I ran of inter-state negotiations in-person & online including #cyber attacks. Thanks @UNDPPA MSU @Jason_Healey @ipinst for mentoring!
To learn more, check out this awesome @ColumbiaDEFRAG event on WarGames with @CISAJen , @webjedi, @MattDevost & Maj Gen Huyck (who was driven to become a comp-sci major b/c of the movie and then became the head of operations for NORAD)!
www.youtube.com/watch?v=iqx6STDYJ7c
CYBERCOM can trace its roots to Ronald Reagan watching this movie and then asking the Joint Chiefs what tf was going on.
Jay Healey reposted
Our team is committed to securing the nation’s cyber and physical infrastructure. Learn more about how you can give back to our nation: cisa.gov/careers
Jay Healey reposted
Cyber careers come in many shapes & sizes! Multidisciplinary teams will thrive at #cyber912 San José, CR 🤹
📣 Register before June 12th to compete in English or Spanish: form.jotform.com/241206162269149
@ufidelitas_cr @StateCDP @MITREcorp @OAS_official @LAC4_EUCN @manager_cluster
Jay Healey reposted
Since our launch in October 2023, it’s been quite the year for IGP!
🌐 24 major events with over 13,000 attendees
🌐 23 policy roundtables & skills workshops
🌐 14 Inaugural Carnegie Distinguished Fellows
🌐 36 Student Scholars from across @Columbia
🌐 Policy work that will help to address some of the world’s most pressing challenges
And we’re just getting started.
Read more about our BIG inaugural year: igp.sipa.columbia.edu/inaugural-year
Jay Healey reposted
It’s been quite a year for @ColumbiaIGP!
In its inaugural year, we held 24 major events with over 13k attendees and hosted 14 Inaugural Carnegie Distinguished Fellows & 36 Student Scholars from across @Columbia.
And we’re just getting started!
igp.sipa.columbia.edu/inaugural-year
Congrats on a great gig! You'll be as amazing there as you did to build out @SIPAcyber and support @SIPA_DCG!
Not quite sure why this headline that F-35 software will need frequent updates is written to be so alarmist...
www.airandspaceforces.com/f-35-tr-3-software-patches/
Jay Healey reposted
It’s been a remarkable inaugural year for IGP.
We brought people together across geographic, political, and ideological divides. We inspired new ideas and built the foundation for policy work to address some of today’s most pressing challenges.
Take a look back at our inaugural year - there’s more to come!
igp.sipa.columbia.edu/inaugural-year
Jay Healey reposted
Looking for a paid and remote internship this fall?
Apply to join our team and support programming at the intersection of cybersecurity and geopolitics!
www.atlanticcouncil.org/job-opportunity/cyber-statecraft-…
Jay Healey reposted
With the White House pressuring corporate America to take cybersecurity more seriously, the Justice Department is ramping up its use of a Civil War-era law to hold federal contractors accountable for cyber failures.
My new story for @TheRecord_Media: therecord.media/doj-corporate-cybersecurity-false-claims-…
Ignore Brandon's disagreeability here: his point #2 deserves attention. The research's statistical significance was p=.07, well above normal
That is, despite the size of the effect, most studies would not be comfortable this was not a false positive
Why? 1) Its not peer reviewed yet. 2) read pg 14 carefully, the results are not statistically sig which is odd since this is a large sample. 3) while interesting this says nothing about your fantasy of cyberwar. There is plenty of attention focused on ransomware.
Feels like we should be talking about this more:
"In-hospital mortality for patients already hospitalized at a ransomware-attacked hospital increases between 1.28 and 1.87% – representing a 35.9-55.3% relative increase when compared to pre-attack mean"
papers.ssrn.com/sol3/papers.cfm?abstract_id=4579292
Jay Healey reposted
Feels like we should be talking about this more:
"In-hospital mortality for patients already hospitalized at a ransomware-attacked hospital increases between 1.28 and 1.87% – representing a 35.9-55.3% relative increase when compared to pre-attack mean"
papers.ssrn.com/sol3/papers.cfm?abstract_id=4579292
Long past time to put "but no one has died yet" arguments behind us
Can't wait for a prosecutor to go after ransomware bastards on charges for involuntary manslaughter
Jay Healey reposted
Congratulations to the winners of this year's #prescup🏆 Cybersecurity Competition! Our ceremony at the White House was a tribute to the talent, dedication and service of those who work everyday to protect us in our increasingly digital world. www.whitehouse.gov/oncd/briefing-room/2024/05/20/cisa-and…
Jay Healey reposted
‼️123‼️software manufacturers have now signed our Secure by Design Pledge, w/50 companies signing on since our launch at RSA just 2 weeks ago! If your company is committed to #securebydesign principles, take the pledge & join the revolution! Learn more at: cisa.gov/securebydesign/pledge
Jay Healey reposted
“We are in a war that Putin has said out loud is against us, the United States of America. He calls Ukraine our proxies and this is an active war on inflaming division here.”
Sean Penn on the War in Ukraine during our recent Spotlight Interview with Secretary @HillaryClinton and IGP Carnegie Distinguished Fellow Robert O'Brien.
Jay Healey reposted
Did you know Hack the Capitol 7.0 is introducing its first every Workforce Development Day? On May 29, HtC will a full day of hands-on training on securing critical infrastructure for college students and military veterans.
Register now! securityandtechnology.org/hack-the-capitol-7-0/
Jay Healey reposted
Great GS-9 entry level job @ONCD for cybersecurity policy
There's only two days left to apply, so hurry!
www.usajobs.gov/job/790769000
Jay Healey reposted
None of us will change the world this week. But each of us has a chance to use whatever talent and wisdom we have…to work with other people to build a more cooperative future.
— @IanBremmer to SIPA’s Class of 2024
Jay Healey reposted
This is the future of global leadership 🌎
Graduation 🎓🎓🎓 @ColumbiaSIPA
Another great student here @ColumbiaSIPA. Seamus Boyle excelled, specializing in cyber and won Cyber 9/12!
His capstone worked @GregRattray_ to assess success of Cyber Defense Assistance Collaborative for Ukraine...
Check out his profile!
www.linkedin.com/in/seamus-boyle-5b60051b3/
Jay Healey reposted
Join @iamthecavalry & a chorus of serious players from National Security / Public Safety - Moscone South 301, 1:15-4:00
Come play a game with @iamthecavalry in this #rsac 2024 partner seminar. Participants will "time-hop" to problem solve an exercise that assumes elevated disruptions and hybrid warfare on US soil in 2027. Learn more. www.rsaconference.com/usa/agenda/session/Getting Serious …
We'll leave this job opening for the SIPA Cyber coordinator for another week or so!
Please apply as we have a lot to build here, from more cyber courses our cyber regulation lab, and a lot more in between...
Come join us to help build our @SIPAcyber program here @ColumbiaSIPA!
We're hiring a new coordinator and would love to have you on the team: cyber regulations, financial stability, cyber conflict, dialogues with Asia, Cyber 9/12 and more!
opportunities.columbia.edu/jobs/coordinator-sipa-cyber-pr…
Great insight here from Phil on defending forward & deterrence, which includes
Futility,
Dependency, and
Counter-productivity
Ten Laws of Security and their Security Implications.
10.Venables’ Law. Attackers have bosses and budgets too.
www.philvenables.com/post/security-and-ten-laws-of-techno…
Here's the link to Phil's original post on deterrence
"If we can constantly raise our baseline defenses by reducing the cost of control and in turn raise the costs to attackers we increase deterrence by making many types of attacks futile"
www.philvenables.com/post/cyber-deterrence-a-simple-persp…
Jay Healey reposted
Huge thank you to our federal and private sector partners who came to our White House Convening on Good Paying Cyber Jobs and making meaningful commitments that will ensure a strong cyber workforce! www.whitehouse.gov/oncd/briefing-room/2024/04/29/press-re…
For those that don't know, Vir has been the soul and the heartbeat of SIPA Cyber. I'm in charge but he's run it all, building our program to what it is today.
So glad he chose our team to work with and look forward to working with him in years to come...
Jay Healey reposted
Spread the word. Piss off RFK Jr by forwarding his all over the place. It's based on data released this week by @WHO .
Come join us to help build our @SIPAcyber program here @ColumbiaSIPA!
We're hiring a new coordinator and would love to have you on the team: cyber regulations, financial stability, cyber conflict, dialogues with Asia, Cyber 9/12 and more!
opportunities.columbia.edu/jobs/coordinator-sipa-cyber-pr…
Jay Healey reposted
Loved joining @lawfare to chat about why I think the US needs a Cyber Force! I discuss arguments underlying the report @MarkCMontgomery and I recently published, which you can read here: www.fdd.org/analysis/2024/03/25/united-states-cyber-force/. @ColumbiaSIPA @SIPAcyber @SIWPSColumbia
On Lawfare Daily, @EugeniaLostri spoke to @eborghard about her report making the case for establishing a U.S. Cyber Force, the types of problems the cyber mission faces, different ways in which they can be addressed, and more. www.lawfaremedia.org/article/lawfare-daily-the-case-for-a…
Jay Healey reposted
On April 19, we’ll debate and discuss the system of protecting sensitive security information and ensuring the public’s right to know what officials do in their name.
Tune in to the Jervis Conference, presented by @SIWPSColumbia, @ColumbiaIGP, @ColumbiaSIPA, @iserp_columbia, & @PublicDeclass: youtube.com/live/JIXKt2tDaJI
@BlackHatEvents Asia kicking off with @thedarktangent!!!
And the keynote by David Koh, Singapore CSA
Jay Healey reposted
Love this. I’d go even further to say that any sizable org, say, Fortune 500 that has open source risks on their radar now or previously and isn’t a member of @openssf or providing other support needs to ask themselves a few serious questions.
CISA's @aevavoom and @jackhcable say the XZ Utils supply-chain incident highlights need for more investment: "Companies consuming open source software must contribute back — either financially or through developer time — to ensure a sustainable ecosystem." www.cisa.gov/news-events/news/lessons-xz-utils-achieving-…
Jay Healey reposted
“In 2024, there will be fakes, some will be deep, most will be shallow and the simplest manipulations will travel the furthest on the internet.”
Clint Watts (@selectedwisdom), General Manager of @Microsoft’s Threat Analysis Center, says audio deep fakes are the ones we should be most worried about.
Jay Healey reposted
“Sometimes discomfort is a sign that you are growing.”
Secretary @HillaryClinton speaking to admitted students about the importance of embracing political disagreement in both the classroom and the situation room.
Jay Healey reposted
New —> The Commerce Department is preparing to prohibit US companies and persons from using Kaspersky anti-virus software, citing national security concerns that the company has dismissed as unfounded, w/ @ZcohenCNN, @Phil_Mattingly & @evanperez www.cnn.com/2024/04/09/politics/biden-administration-amer…
Jay Healey reposted
Last week, we invited admitted students to join us on campus for a series of events and panels introducing what academic and social life is like here at SIPA.
We can't wait to see so many of these students again this fall!
Love this second point, one which @ILDannyMoore makes so well in "Offensive Cyber Operations" -- OCO don't have to defeat a weapons system if defeating trust in it is an easier target
To be more specific:
1. Our average senior leader doesn't understand what it will mean to have networked devices in combat nor how to manage the associated cyber risks.
2. Making troops mistrust machines won't be that hard, so the cognitive domain aspect of this needs more exploration as well.
Jay Healey reposted
Welcome to SIPA! IGP Carnegie Distinguished Fellow Ambassador John J. Sullivan spoke with newly admitted students during this year’s @ColumbiaSIPA Admitted Students Day.
Watch his full conversation with @SIWPSColumbia’s V. Page Fortna here: www.youtube.com/watch?v=vBxtc6kZm8c
Good article @MarkAPomerleau on latest AF organizational advancement/confusion on cyber
The latest step of 25+ years of "what is cyber" & trying to "normalize" w/in AF
Compare w/my history from 2019 in @ASForcesMag
defensescoop.com/2024/04/05/elevation-air-forces-cyber-af…
www.airandspaceforces.com/article/from-cybernetics-to-cyb…
The work of Sally White is amazing...
I cover AF so deeply because I lived the history. Sally goes so much farther, with deep research of the history, with analysis, across all the services
tnsr.org/2023/01/the-organizational-determinants-of-milit…
Likewise Craig Wiener's "Penetrate, Exploit, Disrupt, Destroy: The Rise of Computer Network Operations as a Major Military Innovation" has a lot of the really deep history. Really well researched...
www.semanticscholar.org/paper/Penetrate%2C-Exploit%2C-Dis…
Sorry, I don't have the handles for Michael, Sally, or Craig ... if anyone knows them, please tag them into the conversation!
Just asked @philvenables about this. We report $$$ and ### of 0days but don't have a valid economic model for what either means
Does more, more expensive 0days really equate to defensive success? Or just more offense demand or changing tech stack?
x.com/Jason_Healey/status/1773072550005731357
I dunno, could be a demand signal with multiple interested entities driving up the price as much as a supply crunch...
Tremendous thanks to Ann of Microsoft for this engaging discussion, now out on the Afternoon Cyber Tea podcast...
podcasts.apple.com/us/podcast/nurturing-trust-in-cybersec…
Jay Healey reposted
Congratulations @NIST for awarding cooperative agreements to build the cyber workforce of tomorrow! Grants to 18 education and community organizations across 15 states, worth $3.6 million. This is tremendous progress investing in our nation's cyber workforce.
#icymi: @NIST announced a new Notice of Funding Opportunity to support Regional Alliances & Multistakeholder Partnerships to Stimulate cybersecurity education & workforce development & anticipates awarding an additional 15 awards of up to $200,000. www.nist.gov/news-events/news/2024/03/ramp-your-program-a…
Jay Healey reposted
Come work with me @internetsociety in Washington DC, and help bring the Internet to everyone, empowering communities and protecting people globally: Senior Policy and Advocacy Expert (DC-Remote) internetsociety.bamboohr.com/careers/253
Jay Healey reposted
Don't forget to register! #eca24
Core cybersecurity capabilities provide the foundations for a positive online experience.
Join @HeliKlaar from the @GlobalCyberAlln at #eca24 for an in-depth discussion on the role of the common good cyber initiative.
Jay Healey reposted
Happy Admitted Students’ Day, future Seeples! 💙
I loved meeting and welcoming our newly admitted SIPA students to campus today. We had a full day of events, networking, and speakers. Head to @ColumbiaSIPA’s accounts to see more!
Happy Admitted Students Day!
Students are arriving from around the world to learn more about what their lives will look like at SIPA — starting with a fireside chat between Dean @YarhiMilo and Professor @HillaryClinton!
I got to meet 20+ of our admitted students. Amazing group of future colleagues!
Happy Admitted Students Day!
Students are arriving from around the world to learn more about what their lives will look like at SIPA — starting with a fireside chat between Dean @YarhiMilo and Professor @HillaryClinton!
Jay Healey reposted
Want to work for @CyberStatecraft? Apply now for these two open positions! Opportunity to do meaningful work on cyber + capacity building with some of the best people in the field. Don't miss it - apply before May 3, 2024!
www.atlanticcouncil.org/job-opportunity/associate-directo…
www.atlanticcouncil.org/job-opportunity/assistant-directo…
Jay Healey reposted
GCHQ wins the Internet for today.
Jay Healey reposted
Let’s take SW we can’t make trustworthy/reliable near anywhere… & put it everywhere… & on internet… incl safety critical infra
Jay Healey reposted
On Saturday, ONCD hosted a fantastic Women in Cyber webinar to close out #womenshistorymonth. Nearly 800 people from 34 countries joined! We had inspiring conversations with the next generation of girls and women in cyber. Did you miss it? Here's a recap! www.whitehouse.gov/oncd/briefing-room/2024/04/01/readout-…
Thanks for having me on the show @securityweekly!
Great discussion on "are we winning?" and indicators if cyberspace is indeed becoming more defensible, as called for by @ONCD
www.youtube.com/watch?v=G64QUiKp3Kk
Jay Healey reposted
Know who to trust for facts and well informed opinions on maritime issues, including the Francis Scott Key Bridge disaster. See @johnkonrad and @gcaptain for context like: gcaptain.com/ship-lost-control-before-hitting-baltimore-b…
Jay Healey reposted
📢UPDATE - We are rescheduling our Women in Cyber Webinar to Saturday, March 30. Although it will be a week later, we are excited to celebrate women's history month and empower the next generation of women and girls in cyber.
Interesting ideas I'd not seen before from @johnnysaks130, like drawing on Work Opportunity Tax Credit for SMBs to hire cyber talent to fight ransomware...
In "Behind the Rise of Ransomware" @johnnysaks130 explores historical factors that have contributed to the rise of ransomware and lays out ideas for how the US government can start to tackle this problem.
www.atlanticcouncil.org/in-depth-research-reports/issue-b…
Jay Healey reposted
I love seeing our @ColumbiaSIPA students thriving & breaking down barriers!
Bonnie Ewart-Fisher MIA ’25 is working as a Research Assistant with @SIPACyber, collating resources to increase the number of women in the cybersecurity field. Well done, Bonnie!➡️www.sipa.columbia.edu/admissions/blog/researching-resourc…
Cyber Resilience & Collaboration, our new exec ed course, 7 to 9 June, here @Columbia
Led by @GregRattray_ & me, this course is for private & public sector cyber leaders, military, & govt officials
Deep dives on cyber risks, governance, & collaboration
www.sipa.columbia.edu/sipa-education/executive-education/…
Jay Healey reposted
"We are living in science fiction times, and our fate is in your hands."
IGP Fellow @MariaRessa on the responsibility SIPA students have to make the greatest impacts they can on the most pressing issues of our time:
www.sipa.columbia.edu/news/science-fiction-times
Jay Healey reposted
Did you just get accepted to SIPA? Here's some tips from current students on how to make the most of your time here 🧵
Jay Healey reposted
We asked 5 Cyber 9/12 alumni if they could participate in 9/12 again, would they?
Gabriel Cajiga said “I would definitely do it again!”
Learn what @francesschroe, @grantversfeld, @NitanshaBansal and Tionge Mughogho have to say: dfrlab.org/2024/02/28/the-5x5alumni-perspectives-on-cyber…
The MattGPT by @MattDevost "trained on Matt's writing, interviews, and over 1000 hand-curated reference documents" is totally worth the time to try...
www.oodaloop.com/archive/2023/11/10/the-new-era-of-person…
altzero.ai
Thanks to @CarpeDiemCyber, the @GlobalCyberAlln team, and the other contributing organizations and sponsors of #commongoodcyber!
There is no bigger gap in #cybersecurity than making sure that the entire effort to support the public good in cyber is funded, says @CarpeDiemCyber, our President & CEO. See the full interview #commongoodcyber
globalcyberalliance.org/interview-philip-reitinger-first-…
Jay Healey reposted
Don’t miss this incredible opportunity for cyber experts who want to impact policy! Apply for @AspenPolicyHub's spring and summer 2024 policy programs by 3/7 at 11:59pm PT. Learn more and apply here 👇: www.aspentechpolicyhub.org/announcing-science-and-technol…
Nat-sec impact of Change Healthcare disruption are pretty stunning
NSC deputies committee has been meeting DAILY, according to @johnnysaks130
All from one ransomware attack at a single point of failure...
www.politico.com/newsletters/weekly-cybersecurity
The Health team @washingtonpost has a good piece on what it means for individuals and their access to medicine & procedures
www.washingtonpost.com/wellness/2024/03/05/change-healthc…
And impact to the military and retirees, as it affects tricare
newsroom.tricare.mil/News/TRICARE-News/Article/3684541/ch…
Jay Healey reposted
🔴LIVE NOW
Women Powering the Economy: A Fireside Chat with @SecRaimondo and @StaceyAbrams, moderated by @OlatiJ.
Watch it here: x.com/i/broadcasts/1mrGmyWplDQGy
Jay Healey reposted
.@CyberStatecraft is accepting applications from prospective teams for three #cyber912 competitions--one in Geneva (virtual), one in Paris (in-person), and one in New York City (in-person).
Learn more and register here! www.atlanticcouncil.org/programs/digital-forensic-researc…
Jay Healey reposted
🔴Watch LIVE as we launch our new Women’s Initiative with a series of panel discussions addressing some of today’s most pressing issues affecting women and girls.
x.com/i/broadcasts/1mrGmyWplDQGy
Jay Healey reposted
We need and deserve trust & transparency in our digital infrastructure… with increasing stakes… - incl #sbom
Gonna keep saying it every time I read it.
The @JonKBateman report @CNASdc on Russia's wartime use of cyber in Ukraine is a really rewarding and balanced piece...
carnegieendowment.org/2022/12/16/russia-s-wartime-cyber-o…
Jay Healey reposted
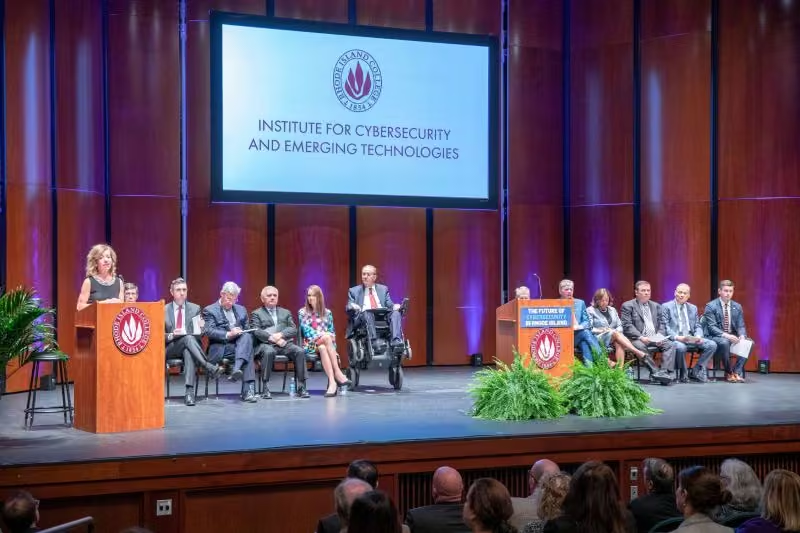
The Institute is hiring a Director. We're looking for someone to help set the direction of the organization as we endeavor to prepare Rhode Island College students for the cybersecurity jobs of the 21st century.
Learn more below and share this post with your network!
Join our team as our new Director! If you're passionate about protecting digital landscapes and working with students, this is a great opportunity.
🔍 Check out the job posting and apply here: employment.ric.edu/postings
👥 Share this post with your network!
This Tomcat RIO who became an Iraqi POW went onto a career in cyber!
Callsign "Rat", he was assigned with a squadron mate to the new Joint Task Force-Computer Network Defense to run the watch in the first cyber J3
#cyberhistor
#otd 1991, an F-14 from VF-103 became the only U.S. Navy Tomcat to be lost to hostile fire when it was shot down by an Iraqi missile. The pilot was recovered in the first combat search and rescue mission behind enemy lines since Vietnam, but the RIO was held as a POW for 6 weeks.
Jay Healey reposted
Be sure to tune in this afternoon ⬇️
Join @ColumbiaIGP for a major convening on the future of Ukraine.
We’ll discuss the ongoing battle around NATO assistance, the role of the West in rebuilding the country, and what’s needed for long-term peace & economic recovery for the Ukrainian people.
x.com/i/broadcasts/1ynJOyrydblKR
Jay Healey reposted
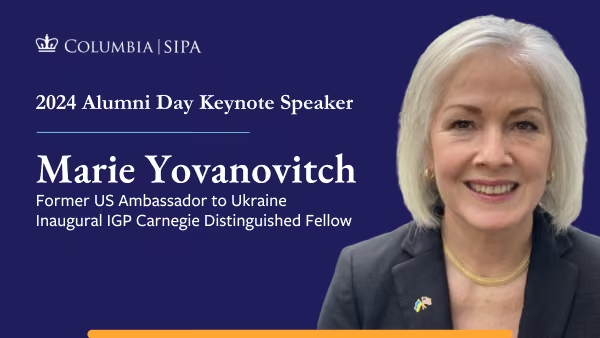
We're proud to announce Marie Yovanovitch, an Inaugural Carnegie Distinguished Fellow at @ColumbiaIGP and former U.S. Ambassador to Ukraine, as the Keynote Luncheon speaker at Alumni Day on Saturday, April 20, 2024.
www.sipa.columbia.edu/alumni/community/alumni-day-and-reu…
Epic event of Future of Ukraine, @ColumbiaIGP @ColumbiaSIPA
With @HillaryClinton @ianbremmer @KimberlyMarten Amb Yovanovich, Amb Markarova, @VelshiMSNBC @YarhiMilo, & many more!
7 February, noon to 2:30pm
igp.sipa.columbia.edu/events/future-ukraine
Come join us at SIPA to take your career, thinking, and professional network to the next level!
Ready to launch a career in public service? SIPA applications are due FEBRUARY 5. Apply today:
apply.sipa.columbia.edu/apply/
Jay Healey reposted
That's a wrap for #cyber912 Austin 2024, but don't worry, there are many more Cyber 9/12's to register for!
Washington, DC, Mar 15-16!
Geneva, CH, Apr 4-5!
Paris, FR, Apr 24-26!
You can find all the links and registration closing dates on our website:
www.atlanticcouncil.org/programs/digital-forensic-researc…
Great event yesterday with @camillefrancois & an amazing panel!
Addressing AI threats to electoral integrity “is going to have to be a partnership between the Federal government, private sector, working with local governments to figure out what the challenges and the issues are…”
Nevada Secretary of State @CiscoAguilar in conversation with Dr. @Alondra Nelson, @JuliaAngwin, and @ColumbiaSIPA’s @CamilleFrancois.
Watch the full convo: www.youtube.com/watch?v=DeDmap3EStg
The Samantha Jennings-Jones Memorial Scholarship is now open for applications.
Sam was a treasured colleague at @ONCD and we all hope her legacy will continue.
www.iamcybersafe.org/s/samantha-jennings-jones-memorial-s…
Jay Healey reposted
Join the @AtlanticCouncil's @DFRLab and @CyberStatecraft as they launch the Congressional Cyber and Digital Policy Program. Registration is now open and linked below to learn more: dfrlab.org/policy/cyber-statecraft-initiative/congression…
Jay Healey reposted
Scholars @SIWPSColumbia again invite interested junior faculty & Ph.D. students to apply to the Summer Workshop on the Analysis of Military Operations & Strategy (SWAMOS), directed by my colleagues Prof Richard Betts & Stephen Biddle, & held @Cornell in summer ‘24. Details below
Jay Healey reposted
No matter how much one supports cybersecurity maturity for defense of DIB, publishing a 230+ page document for comment on the Friday before the Christmas weekend, closing on Boxing Day, is not how to ensure robust feedback. & this merely cements industry distrust of .gov regulatory rulemaking in other contexts.
Jay Healey reposted
"This has been a momentous year – for SIPA, for the world, for humanity. As 2023 draws to a close, I continue to be inspired by the intellectual energy and passion of our community. Nurture that spirit. It is what makes us SIPA."
— Dean @yarhimilo
Congrats to our cyber J-termers!
From this month's J-Term reception 🎉
Congratulations to the classes of October 2023 and February 2024. We're so proud of you and the journey you've taken here at SIPA. We can't wait to see what you do next 🎓
Great to see @ColumbiaSIPA @SIPAcyber alum Camila in her scholarship with @FSISAC!
Building a diverse talent pool is a business imperative. FS-ISAC is committed to increasing the number of women in cybersecurity. The application for our Women in Cyber scholarship for the 2024-25 academic year is now open until 17 March, 2024. Learn more: www.fsisac.com/scholarships?hss_channel=tw-270908634
Jay Healey reposted
Big Congrats to Harry Coker, our new National Cyber Director. Go Team Cyber!
www.politico.com/news/2023/12/12/coker-confirmed-as-next-…
Jay Healey reposted
We're delighted to welcome Mr. Harry Coker, Jr. as our next National Cyber Director. Full statement: www.whitehouse.gov/oncd/briefing-room/2023/12/12/oncd-wel…
Didn't understand the @craignewmark fascination with pigeons until a small flock of seven (these three plus another four behind, on the sill) decided to come visit us each night to bed down...
Craig: we get it now!
Thanks to @maurertim for stopping by @ColumbiaSIPA to speak with students about his incredible journey, careers in cyber, and of course working in the NSC on democracy and technology!
ICYMI here's some of the amazing work he did there:
www.whitehouse.gov/briefing-room/statements-releases/2023…
In remembrance of Steve Katz, the world's first CISO...
I got to know Steve in 2001, only a few years after he started his role at Citi. Many of us got to hear him recount that early history at a dinner marking the 20th anniversary of the FS-ISAC
www.inforisktoday.com/steve-katz-worlds-first-ciso-dies-i…
Apply now to be a postdoc research scholar at Saltzman Institute of War & Peace Studies @ColumbiaSIPA!!!
www.siwps.org/programs/call-for-applications-postdoctoral…
Applications open for Hinman fellows @SilveradoPolicy "for graduate students ... pursuing public policy careers ... who would not otherwise have the financial means to spend a summer" in DC
Get to work & learn w/ the great @Eco2Sec & @DAlperovitch!
silverado.org/hinmanfellowship/
Not to one-up the beautiful, sunny landscapes photos which @johnmccumber and @MerrittBaer take of the view from their windows...
But here in NYC, we get crews filming naked dudes throwing away stuff
The National Cybersecurity Strategy calls for cyber regulation
But the terms are confusing .... What do we mean by performance-based or principles-based regulation?
A thread, based on my recent piece @lawfare to make sense of it all
www.lawfaremedia.org/article/which-cyber-regulations-fit-…
Performance-based regulations are micro-ends
Only useful when the actual outcomes can be measured, which is super-hard for cybersecurity!
Best for sectors where entities are similar and stable, where tech doesn’t change too quickly
Recovery-time objectives are one of the few performance-based regulations, such as the 2-hour target set by financial regulators in 2003 in the Sound Practices Letter of 2003
occ.gov/news-issuances/bulletins/2003/OCC2003-14a.pdf
Performance-based makes more sense for stable, less-mature sectors like water & wastewater. Checklists and specifics are a good place to start the risk-management journey
Other sectors should get management- and principles-based which are more general and easier to harmonize
Either way, both regulators and regulated entities need to be more precise about what they actually is best ... and be cautious with shorthand like "performance-based" which may suggest different things to different people
end//
In case that's all gobbledygook:
0343 is job classification for non-tech Management and Program Analysts
2210 is for technical IT specialists. You should have computer security experience or education
The final number (like 9/11/12) is the grade/pay scale: GS-9, GS-11, GS-11
New jobs at NRMC @CISAgov!
GS-0343-13: www.usajobs.gov/job/760725400
GS-2210-9/11/12 (permanent): www.usajobs.gov/job/762371000
GS-2210-9/11/12 (term): www.usajobs.gov/job/762370900
GS-2210-12/13 (permanent): www.usajobs.gov/job/762371100
GS-2210-13/14 (permanent): www.usajobs.gov/job/762371200
New jobs at NRMC @CISAgov!
GS-0343-13: www.usajobs.gov/job/760725400
GS-2210-9/11/12 (permanent): www.usajobs.gov/job/762371000
GS-2210-9/11/12 (term): www.usajobs.gov/job/762370900
GS-2210-12/13 (permanent): www.usajobs.gov/job/762371100
GS-2210-13/14 (permanent): www.usajobs.gov/job/762371200
Come join us tonight uptown for the launch of "Bridging the Trust Gap" on improving trust between pubic and private sectors for cybersecurity
New report from New York Cyber Task Force @ColumbiaSIPA comes out tonight!
www.sipa.columbia.edu/global-research-impact/initiatives/…
New report from New York Cyber Task Force @ColumbiaSIPA comes out tonight!
www.sipa.columbia.edu/global-research-impact/initiatives/…
Embarrassed our literature review missed this great 2020 article on using Cyber Kill Chain to assess impact of AI
Of course, in all things cyber and AI, @CSETGeorgetown was there first: @BuchananBen, John Bansemer, and others
Articles on AI cybersecurity are often just opinion pieces arguing an "arms race" or benefit to either defenders or attackers
My new @ASPI_CTS article more comprehensively analyzes AI's advantages to defense & offense using NIST CSF & Cyber Kill Chain
www.aspistrategist.org.au/the-impact-of-artificial-intell…
New job for a program and management analyst at National Risk Management Center @CISAgov
It's GS-13 ($112k to $145k) to suitable for grad students re-entering the works force!
www.usajobs.gov/job/760725400
Apply soon for this GS-13 job @CISAgov National Risk Management Center!
Working in the Chief of Staff's office, you'll learn everything about the mission of NRMC...
www.usajobs.gov/job/759661600
Honored to join @DAlperovitch being awarded the Outstanding American by Choice to recognize achievements of naturalized U.S. citizens, presented by Secretary Mayorkas, himself a naturalized American
Congrats to Dmitri, @Eco2Sec, & whole team at @SilveradoPolicy & @alperovitch
Join us uptown for launch of the next report from the NY Cyber Task Force!
Join @ColumbiaSIPA on 11/20 for the launch of 'Bridging the Trust Gap', a report by the NYCTF. The event will feature a conversation with Colin Ahern, Chief Cyber Officer for the State of New York, as well as a panel discussion on the report. (1/3)
nyctf-sipa.eventbrite.com
Great initiative on norms for routing security!
A kind of collaboration like that we have reached to take on the @RoutingMANRS Secretariat with @internetsociety is at the heart of all the work GCA is doing with #cybersecurity issues in the #internet names, numbers and #routing space. 🌐✒️ globalcyberalliance.org/achieving-greater-heights-manrs/
Jay Healey reposted
Amazing opportunity to work in the information operations analysis space here. Great team, great mission. What are you waiting for?
We are #hiring! The @Mandiant Information Operations (IO) team is looking for a IO Data Scientist. Join our industry leading team! You will get to work with some wonderfully talented people and have an opportunity to drive huge impact on a major problem facing society!
Jay Healey reposted
Just watched @MarkHertling's 2012 Ted Talk on obesity as a national security issue. Wow. If you're interested in the military obesity crisis, check it out: www.youtube.com/watch?v=sWN13pKVp9s. To see how the problem is just getting worse, check out our data: www.americansecurityproject.org/white-paper-combating-mil…
OH at Air Force-Navy tailgate:
"I became a SEAL to serve the country, shoot guns, and blow stuff up. Then I encountered DTS..."
Want to help secure America's elections?
New job posting @CISAgov to lead the Election Infrastructure Subsector Risk Management Agency!
Job closes tomorrow though!
www.usajobs.gov/job/755721800
Articles on AI cybersecurity are often just opinion pieces arguing an "arms race" or benefit to either defenders or attackers
My new @ASPI_CTS article more comprehensively analyzes AI's advantages to defense & offense using NIST CSF & Cyber Kill Chain
www.aspistrategist.org.au/the-impact-of-artificial-intell…
And how AI assists offense, using Cyber Kill Chain...
It'd be better to use ATT&CK here, but that's far more complex than Cyber Kill Chain, much more than I could use in a 1200-word article...
Infosec twitter can miss a lot of OT, like this interesting story on fire alarms moving to the cloud
Mostly covers benefits, but a bit on security. Wish it'd mentioned DDoS impact, but still worthwhile read
www.securityinfowatch.com/alarms-monitoring/fire-life-saf…
Incredible role @ColumbiaSIPA open now for practitioner-academics to be the Shelby Cullom Davis Professor to teach international diplomacy and US Foreign Policy & direct the storied International Fellows Program
academic.careers.columbia.edu
So, does your neighborhood also get topped up with liquid nitrogen?
Great insights from Ukraine’s energy minister @TheEconomist -- cyber is a worse threat than kinetic b/c it can paralyze the whole system, not just individual parts
www.economist.com/europe/2023/10/02/ukraine-prepares-for-…
Often ignored by those saying offense doesn't have advantage:
Issues like common-mode failures allow a single one-to-multitude attack to affect a great many targets at once
www.lawfaremedia.org/article/understanding-offenses-syste…
If you haven't read "You'll See This Message When It Is Too Late," really recommend it for policy, economic, and legal insights to fix cybersecurity at scale
@josephinecwolff did a great job with it and thrilled to say we've added it to the syllabus here at @ColumbiaSIPA!
Jay Healey reposted
SIPA students are tomorrow’s global leaders and policy makers.
Sound like your future goals? Our 2024 application is now open!
How to apply: www.sipa.columbia.edu/admissions/applying-sipa/how-apply
Jay Healey reposted
🚨Less than ONE WEEK left to secure your spot in the NYC #cyber912 Strategy Challenge being held Oct 13-14.
🗓️ Deadline: Sept 20 @ 11:59pm
📍@ColumbiaSIPA
📄Register: nyc-cyber912.eventbrite.com
cc: @CyberStatecraft @SIPA_DCG
New jobs at National Risk Management Center @CISAgov!
GS 13-14 for a data scientist: www.usajobs.gov/job/749053600
GS 12-13 admin officer in the Chief of Staff's office: www.usajobs.gov/job/747958900
Excited for first course co-teaching w/ Evan Wolff @Crowell_Moring & Charles Carmakal @Mandiant
Just one of the exciting cyber courses here @ColumbiaSIPA!
Thanks for the great conversation @ASPI_org @BassiJustin!
Looking forward to my next trip to Canberra...
🚨 NEW PODCAST 🚨
This week on the ASPI pod, @BassiJustin speaks to cyber security expert @Jason_Healey about the history of cyberspace & conflict, implications on security & society, and why cyber needs to be at the heart of national security.
Listen ➡️ soundcloud.com/user-415599049/cyber-conflict-competition-…
Jay Healey reposted
🎂Happy 1-year anniversary, Blueprint for Ransomware Defense! Last year, @CISecurity’s Community Defense Model v2 estimated that Blueprint Safeguards would protect against 70% of ransomware attack techniques. To celebrate, IST put this claim to the test.
securityandtechnology.org/blog/putting-the-blueprint-for-…
Great opening @CISACyber National Cyber Risk Management Center for a direct-hire GS 9 through 12 to perform risk assessments, develop cyber risk indicators
Closes 5 September so apply quickly!
www.usajobs.gov/job/745055700
Wargames is @KembaWalden46's fave hacker flick!
Yours too?
Check out this amazing event @ColumbiaSIPA talking Wargames with @CISAJen, @webjedi, @MattDevost, and Maj Gen Kevin Huyck, then head of ops (J3) for NORAD!
www.youtube.com/watch?v=iqx6STDYJ7c
Jay Healey reposted
🔥Fantastic fireside keynote this morning at #blackhat2023 with @KembaWalden46, expertly moderated by @Jason_Healey. Go Team Cyber!
Jay Healey reposted
To Help you figure out what's where @defcon and how to walk between them
More help at The One! at defcon.outel.org downloadable html,pdf,Google Calendar
and
reddit Mega Info - reddit.com/r/Defcon/comments/tx7tg2/mega_def_con_info_for…
Please RT
have fun! #defcon #defcon31
Jay Healey reposted
We are officially two weeks away - and the #defcon31 schedule is HERE! You may now begin your planning. Find out who's doing what and where! We've also thrown together a few useful at-a-glance schedules for @DEFCONPolicy - check them out below!
defcon.org/html/defcon-31/dc-31-schedule.html
So cool...
Hey grads and students interested in #infosecjobs check out this open opportunity for internships (unpaid, boo) at State Department's office of Cyberspace & Digital Policy!
openopps.usajobs.gov/internships/5684
Send me any questions you have for @KembaWalden46 of @ONCD!
I'll be moderating the fireside chat with her and will try to include what you all want to hear about...
Check out the amazing group of keynote speakers #bhusa has lined up this year including @Fox0x01, @CISAJen, @KembaWalden46, @VZhora, @Jason_Healey, and @lilyhnewman. Presentation details here. www.blackhat.com/us-23/briefings/schedule/index.html
Jay Healey reposted
To all my fellow financial sector geeks tracing and analysing cybersecurity developments in the field:
The European Supervisory Authorities launched a public consultation on the first batch of policy products under DORA.
www.esma.europa.eu/press-news/esma-news/esas-consult-firs…
Calling all (senior) analysts!
NRMC advertising for a senior-executive Associate Director for Analytic Capabilities to join @cisa
www.usajobs.gov/job/739080500
Been in a great streak with Wordle lately...
Jay Healey reposted
Jay Healey reposted
Calling all comics and graphic novel enthusiasts! On 8/1, join us for a discussion w/ @Columbia scholars about the influence of comics in America and the authors and artists who shaped the medium. Free and open to the public. #columbiasummer summer.sps.columbia.edu/events/comics-and-graphic-novels-…
Jay Healey reposted
Two vacancies within the cybersecurity governance group we are a part of - please share and help us find new colleagues!
- Assistant Professor Cybersecurity Governance, with a specialization in international cybersecurity
- Assistant Professor in Cyber Security Governance
1/2
JOB!
This GS-13 communications analyst position in NRMC @CISAgov is a good fit for a recent graduate!
You'd be helping NRMC leadership on speeches, presentations. Good way to learn a range of topics & get your foot in the door
www.usajobs.gov/job/738517300
Me from February 2022:
US government must use three Es:
Encourage those actors which have the means to improve defenses at scale but may lack the will
Enable those with the will but not the means; and
Enforce with regulations when the first two options fail
Developing a national cyber strategy is a complicated process but as @emmacs26 says, "the US has a tendency to put cyber in its own box—to miss the forest for the trees."
Read more from her, @Jason_Healey, @JoshRovner1, @CamilleEsq, and @HeliKlaar here.
www.atlanticcouncil.org/content-series/the-5x5/the-5x5-wh….
Jay Healey reposted
Congratulations to V. Page Fortna, the new Director of the Arnold A. Saltzman Institute of War and Peace Studies! @SIWPSColumbia
And thank you to Peter Clement for serving as Interim Director during the 2022-23 academic year.
www.sipa.columbia.edu/v-page-fortna-new-director-saltzman…
Excellent product by @CyberStatecraft on the National Cybersecurity Strategy of the Biden-Harris administration
As a drafter of the NCS & early implementation plan, here’s a thread with additional background…
1/
The 2023 National Cybersecurity Strategy (NCS) implementation planned has dropped.
@CyberStatecraft marked up the implementation plan, examining how the administration's vision will become reality and “rebalancing responsibility” in cyberspace. 🧵👇 dfrlab.org/2023/07/18/national-cybersecurity-strategy-imp…
This would have been hard for any administration to manage – even more so for the Trump NSC which decided to remove the position of cyber coordinator
www.nytimes.com/2018/05/15/technology/white-house-cyberse…
8/
To put that in context, the Biden team -- @KembaWalden & Anne Neuberger - operate with cabinet secretaries or depsecs
The senior Trump NSC cyber official, a senior director, would work at undersecretary level
9/
Thanks for following and thanks to my former @ONCD colleagues for this great implementation plan!
12/
Wasn't sure if I'd mention this, but the implementation plan had been led at @ONCD by the amazing Sam Jennings-Jones
She was an amazing colleague, tragically killed by a speeding driver in April. We miss you Sam...
www.legacy.com/us/obituaries/washingtonpost/name/samantha…
13/13
Sweet! @CUNY advertising for an Assistant Professor of Policy Cyber Security
www.linkedin.com/jobs/view/3661404066
Another @CISAgov GS-15 position! Assistant Chief of Staff at NRMC...
Position closes on 20 July
www.usajobs.gov/job/736866100
Multiple GS-15 branch chief vacancies at @CISAgov National Risk Management Center!
Risk Prioritization
Solutions Engineering
Emerging Risks
Initiatives
Critical Infrastructure
Hurry, this closes TODAY!
www.usajobs.gov/job/735434900
Jay Healey reposted
We're excited to announce registration is open for this years' NYC #cyber912 Competition. Join us at @ColumbiaSIPA on 13-14 October 2023!
More info: sipa.columbia.edu/cyber912
Team Registration: nyc-cyber912.eventbrite.com
Multiple GS-15 branch chief vacancies at @CISAgov National Risk Management Center!
Risk Prioritization
Solutions Engineering
Emerging Risks
Initiatives
Critical Infrastructure
Hurry, this closes TODAY!
www.usajobs.gov/job/735434900
Amazing day here at SIPA Cyber, @ColumbiaSIPA as it's the first day in the office for Erica Lonergan our new assistant professor!
Welcome home Erica!
Amazing day here at SIPA Cyber, Columbia | SIPA, as it's the first day in the office for Erica Lonergan our new assistant professor!
Welcome home Erica! www.linkedin.com/feed/update/urn:li:share:708452284638264…
Sweet! Students and recent grads: can't recommend this enough!
cc: @SIPA_DCG @SIPAcyber
Come intern with the Bureau of Cyberspace and Digital Policy!
Welcome to the team @ColumbiaSIPA, Maria!
NEWS: @MariaRessa is joining @ColumbiaSIPA as a distinguished fellow in 2023 and a professor of professional practice in 2024.
She will be researching and teaching about the role of artificial intelligence in democracy.
@Columbia
"In Mr Putin’s world, powerful leaders do not let people off and they do not ask for help from the junior dictator next door."
The meaning of Prigozhin’s short-lived mutiny from TheEconomist www.economist.com/leaders/2023/06/25/the-meaning-of-prigo…
Oooga! Oooga!
Love intelligence? Love history?
Maybe you'd love being a historian @NSAGov? Of course you would!
apply.intelligencecareers.gov/job-description/1210277
My 2nd article on national cyber strategy!
It's been 50 years since 1st report finding we need to bake security in, not bolt it on.
Defenders have made huge strides; unfortunately attackers; strides have made huger
The NCS might just break this 50 year losing streak
On March 2, the Biden administration released its new National Cybersecurity Strategy, calling for long-term investment in cyber defense by the federal government and major technology companies. @jason_healey evaluates the strategy: www.lawfareblog.com/national-cybersecurity-strategy-break…
"Cybersecurity Policy" comes in four main flavors. The NCS includes policies across all four:
"Each of us" - USG cybersecurity
"Them" (adversaries) - disruption
"All of us" - regulation
"Everything" - s/w liability, securing tech foundations of the Internet
My favorite quote on this 50-year attacker advantage comes from, as usual, Dan Geer:
"Whether in detection, control, or prevention, we are notching personal bests, but all the while the opposition is setting world records."
geer.tinho.net/geer.rsa.28ii14.txt
Congrats to the new Catherine Hinman Memorial Fellows!
And thanks to @Eco2Sec @DAlperovitch and the whole @SilveradoPolicy team for this great initiative
silverado.org/news/meet-silverado-s-2023-catherine-hinman…
Want to be more like Gen Scowcroft?
Come study with us @Columbia!
On this date in 1967, Brent Scowcroft is awarded his Ph.D. in Public Law and Government, now Political Science, from Columbia University. Learn more about General Scowcroft and his legacy: www.atlanticcouncil.org/brent-scowcroft/
Substantial continuity over 25 years ... not always a good thing. If problems are familiar & worse, new strategies need to mix it up!
Article compares White House strategies: promise/peril of cyberspace, role of markets, public-private partnerships, & countering adversaries
On May 22, 1998, the Clinton admin published the White House’s first-ever national cyber policy. Twenty-five years and several cyber strategies later, many underlying cyber problems facing the US today are worse than they were in then, from @jason_healey:
www.lawfareblog.com/twenty-five-years-white-house-cyber-p…
By contrast, Biden strategy asserts at least 5 times that markets have failed! Therefore...
"Regulation can level the playing field, enabling healthy competition without sacrificing cybersecurity or operational resilience"
www.whitehouse.gov/wp-content/uploads/2023/03/National-Cy…
Regulation is one of the few cyber topics w/ a partisan split
Republican administrations either argue that new regulations make the problem worse or fail to mention them at all
Democratic administrations acknowledge markets might fail, or they have and regulation is needed
New article up at The Lawfare Institute on 25 years of White House cyber policies. This is part 1 of 2, with another coming out next week.
Twenty-five years ago, on May 22, 1998, the Clinton administration published the White Hous…www.linkedin.com/feed/update/urn:li:share:707041335664544… www.lawfaremedia.org/twenty-five-years-white-house-cyber-…
Really looking forward to reading this economics article on cyber impact on state & local governments
Like others from these authors, they have access to unique data sets (like government financing costs) for interesting insights
papers.ssrn.com/sol3/papers.cfm?abstract_id=4465071
"Cyberattacks translate to roughly $1.77 billion in mark-to-market losses to investors [in state and local debt] on the $870 billion in outstanding bonds affected by external data breaches between2010and 2019."
Incredible finding:
"Total government expenditures increase substantially and permanently in the aftermath of data breaches
"For example, within a year of data breaches, total expenditures jump by 2.8% and continue rising to up to roughly 5% three years after the event"
First batch of briefings just dropped @BlackHatEvents!
Excited to be on the review board for my third year...
www.blackhat.com/us-23/briefings/schedule/index.html?elq_…
Complexity & systems thinking is one of biggest gaps of scholars of international relations -- and possibly military -- on cyber.
Can often treat "Internet" as one thing rather than hugely complex system "operating most of the time in failure mode"
Security and Complexity 🧵
Complexity is not necessarily the enemy of security. Bad design is. All useful things are complex at some level of abstraction. To wish the complexity away is to fail to apply good design to deal with it.
1/19
NRMC using it's direct hire authority @CISACyber to bring on GS-13s and GS-14s with cyber/IT background ($112,015 - $172,075)
Cyber-related policy, research, analysis, and project management
Apply now to join the great team at NRMC!
www.usajobs.gov/job/725334200
Next up at #hammercon -- @HostileSpectrum on CCO and future conflict
The military role in the 1980’s “war on drugs” was challenging. Just read “Sum of All Fears” to get a sense.
Here’s the path to some POTUS ordering USCYBER against Mexican drug cartels:
Those same advantages make it useful for a very wide range of POTUS priorities it hasn't been used for yet
IF POTUS already has decided to use the military against drug cartels, why wouldn't cyber be an easy and early choice?
Likewise, if some POTUS wanted to invoke the Insurrection Act to use the military to quell protests they didn't like, then @US_CYBERCOM might find itself being used against US citizens labeled "enemies of the state"
www.defenseone.com/ideas/2020/09/could-trump-deploy-us-cy…
Exceptional interview @bgroothuis at @TheRecord_Media @AlexMartin! Has it all: subject matter knowledge, process, details, and unique insights.
Thanks to @josephmenn for the tip in the WaPo Cyber 202
therecord.media/interview-with-bart-groothuis-eu-cybersec…
This always seemed nearly foreordained to me
Almost every new general-purpose technology has preferentially advantaged the offense over the defense
Only a very few -- encryption, cloud -- have boosted defense over offense
Artificial intelligence is helping criminal hackers more than it is helping defenders. It is going to change the battlefield just when things were getting less terrible. Free version of my story at the Post: www.washingtonpost.com/technology/2023/05/11/hacking-ai-c…
Not a bad idea, just not time for it yet.
Too many unanswered questions, most importantly should it be an "information service" for info ops, mis/disinfo, network and computing systems
Many believe it's time for an independent uniformed cyber service. Here's what it could look like. @MarkAPomerleau breaks it down: scoopmedia.co/430yR43
Perhaps Cyber Command was wrong model in 2010, compared to an "Information Command," considering challenges since from China, Russia
Imagine if we'd created a major Battleship Command in 1935. Cool idea but wrong technology & not matched to the future strategic challenge
So for those following defacements and info ops:
If you were coding a database including war-related Russia or Ukraine webpage defacements ...
(a) Default assumption each defacement is an cyber-enabled info op OR
(b) Default assumption defacement is mere nuisance?
Jay Healey reposted
Attending #defcon31? Curious to support gathering hackers and policymakers at @DEFCONpolicy? Check out our "call for support" application here! As a policy-attaché, you can spend a few hours helping bridge the hacker and policy maker divide
form.jotform.com/231257054126045
So @josephmenn - can you confirm this please?
Seems like commander of CNMF saying @US_CYBERCOM has "43 [members] currently deployed" for forward operations to Ukraine...
Or does that mean "in support of" Ukraine but maybe in Poland?
Additional reporting @zebatweets on same RSA event seems to confirm Army MG Hartman saying @US_CYBERCOM deployed 43 individuals TO UKRAINE
Given blowup over leak that US special ops is in Ukraine, kinda surprised this isn't getting walked back ASAP
www.reuters.com/technology/us-deploys-more-cyber-forces-a…
BTW, not sure Russia would agree US hunt forward ops on Ukrainian networks is purely defensive, any more than they'd accept that US infantry on the ground, finding Russians hiding in forests and trenches would be particularly defensive
Curious how Texeira got so much varied material, whether it was through hunting, gathering, or salvaging?
If salvaged, Texeira collected the information from the office, such as after it was legitimately disposed of into a “burn bag”
Junior personnel get tasked to incinerate such bags full of disposed secrets, so he might've just snuck papers out
Salvaging seems less likely, given some of what's been disclosed so far, but it does explain the huge range of codeword material
Texeira may not have had legitimate access, he just gleaned through burn bags when no one was looking
Coolest job I've posted in ages!
Who'd like to be a historian at US Cyber Command!
Work with Michael Warner, the command historian to help document the history of cyber conflict and the command. We must professionalize the study…www.linkedin.com/feed/update/urn:li:share:705490027334486… www.usajobs.gov/job/720908500
Coolest job I've posted in ages!
Historian at @US_CYBERCOM !!!
Work with Michael Warner, the command historian to help document the history of cyber conflict and the command
www.usajobs.gov/GetJob/ViewDetails/720908500
A great showing of students, alumni, and NYC-area cyber experts!
Last night, SIPA Cyber (with @Jason_Healey) hosted its last Uptown Cyber Social of the Spring '23 semester.
Thank you to everyone in the NYC cyber community who came out!
Problem: "missingness" of cyber data on cyber & international relations
One solution: Literature from financial stability. Papers by economists from the Fed system look at likelihood, impact of major cyber incidents
These economists have far less missing data, as they can rely on private, supervisory data from banks, payment systems
For example
www.newyorkfed.org/research/staff_reports/sr1022
Where else can we have a economic analysis with real data that finds a 40% increase in potential impact of a cyber attack on a key sector (wholesale payments) during COVID to show how cyber and financial risks are correlated
Absolute gold...
In addition to those directly hit by NotPetya, Fed economists found an additional $7.3 billion downstream loss to their customers...
Who knew?
NotPetya had long-term effects as customers switched trading relationships to those not directly affected by cyber attacks...
Major benefit of papers by Fed economists is they can use confidential loan data to see the major role of banks, as NotPetya victims (and their customers) drew down their credit lines
Completely adds new color to understanding of this attack (cc @a_greenberg)
Jay Healey reposted
Couldn't make it in person? Join online!
@ColumbiaSIPA and @NewYorkFed present the State of the Field Conference on Cyber Risk to Financial Stability, exploring the impact of deglobalization on cyber risks and financial stability.
columbiauniversity.zoom.us/webinar/register/WN_49vCjCY3Tl…
Jay Healey reposted
Don't miss this exciting conversation about the future of cyber risks and financial stability. We look forward to having you join us!
Register for virtual or in-person attendance here: www.eventbrite.com/e/2023-state-of-the-field-conference-o…
Jay Healey reposted
On the panel will be Former CFTC Chairman @giancarloMKTS, @NewYorkFed's Danny Brando, @FSISAC's Steven Silberstein, U.S. regulatory strategist Naveen Zaidi, and moderator @Jason_Healey.
Jay Healey reposted
Panel 3 of the conference is a forward-looking assessment of risks will explore the impact of deglobalization on cyber risks and financial stability across geopolitics, national security, and finance.
Jay Healey reposted
Tomorrow, join @ColumbiaSIPA and @NewYorkFed for the State of the Field Conference on Cyber Risk to Financial Stability.
Scholarships for the Intelligence and National Security Foundation (INSF) ... deadline coming up on 14 April! my.reviewr.com/s2/site//2023_INSF_Scholarship_Application
Want to learn more about ICANN or DNS and how the Internet really works? Check out this ICANN 101 webinars... icann-community.atlassian.net/wiki/pages/viewpage.action?…
Want to learn more about ICANN or DNS and how the Internet really works? Check out this ICANN 101 webinars...
community.icann.org/display/IFBVP/ICANN+for+Beginners+Vir…
Scholarships for the Intelligence and National Security Foundation (INSF) ... deadline coming up on 14 April!
my.reviewr.com/s2/site//2023_INSF_Scholarship_Application
Please join in person @ColumbiaSIPA or online for 14 April conference on cyber risk to financial stability, in partnership w/ @NewYorkFed
SIPA produced much of the initial research on this important field, like the general framework, below...
capco.com/Capco-Institute/Journal-53-Operational-Resilien…
Earlier SIPA research explored how cyber risks were different from typical financial stability risks (eg, an intelligent, motivated opponent)
Also how cyber campaigns might EXACERBATE or INITIATE a financial crisis
www.brookings.edu/wp-content/uploads/2018/10/Healey-et-al…
My new piece up at @CFR_org
Assessments of Russian cyber attacks re Ukraine capabilities have missed a crucial lesson from fifteen years ago: cyber power requires soft power
www.cfr.org/blog/ukrainian-cyber-war-confirms-lesson-cybe…
Ukrainian cyber defenses have been inspired, but also reinforced by cyber defense assistance from dozens of companies and the governments
Much of that defensive boost would not have been on offer if Ukraine had a loathsome or tyrannical regime
www.crdfglobal.org/news/crdf-global-becomes-platform-for-…
Little would be on offer, for example, for Iran. Obviously, there are important lessons here for Taiwan.
So assessments that simply assess that "#cyberdefense is possible so cyber during wartime isn't likely to be effective" may only be true for states with friends and allies
My new piece on #cyber power and #ukrainerussiawar at Council on Foreign Relations.
Cyber experts, policymakers, and practitioners are striving to understand how cyber capabilities have been used since the Russian invasion of Ukra…www.linkedin.com/feed/update/urn:li:share:704903877600155… www.cfr.org/articles/ukrainian-cyber-war-confirms-lesson-…
The agenda just dropped for our annual conference with @NewYorkFed on cyber risk to financial stability!
Join @ColumbiaSIPA & @NewYorkFed for our 4th annual conference on Cyber Risk to Financial Stability!
This is the major global conference on how cyber risks will affect financial stability and macroprudential regulation
In-person at SIPA and hybrid options...
Do you still use cyber in wartime if you can physically destroy a target?
Senior DoD official in @MorningCybersec says yes, of course, cc @johnnysaks130
Many scholars take opposite view: why both using cyber once bombs start flying
www.politico.com/newsletters/weekly-cybersecurity/2023/04…
For example, here's @eborghard @Shawn_Lonergan et al...
www.washingtonpost.com/politics/2022/03/07/putins-invasio…
Neither side is clearly right: it all depends on the conditions
What vulnerabilities, how important is the topic, what capabilities, how much time to prepare, how long does the target need to be down?
Please join the Columbia | SIPA and Federal Reserve Bank of New York for our Fourth Annual State-of-the-Field Conference on Cyber Risk to Financial Stability on 14 April 2023!
This is the major global conference on how cyber risks…www.linkedin.com/feed/update/urn:li:share:704721196123886… www.eventbrite.com/e/2023-state-of-the-field-conference-o…
Join @ColumbiaSIPA & @NewYorkFed for our 4th annual conference on Cyber Risk to Financial Stability!
This is the major global conference on how cyber risks will affect financial stability and macroprudential regulation
In-person at SIPA and hybrid options...
Great conference just opened up their CFP!
Starting to look for a great idea to submit...
#callforpapers for our 2023 Conference on International Cybersecurity, this time taking War and Peace as our theme, focusing on conflict, behaviour and diplomacy in cyberspace: www.thehagueprogram.nl/news/2023-conference-on-internatio… #cyberwarpeace2023
Amazing event coming up next week!
Join Secretary @HillaryClinton and @SpeakerPelosi for a conversation at @Columbia on global politics, national security, and the backsliding of democracy
Monday, April 3
12:30-2 pm
Hosted by @ColumbiaSIPA and Dean Keren @YarhiMilo
Sign up to watch live: www.eventbrite.com/e/spotlight-interview-speaker-emerita-…
Very cool jobs @CISAgov NRMC!
GS-2210-15 IT Cybersecurity Specialist; closes 3/30/2023 (Hiring Manager: AD Harrington)
www.usajobs.gov/job/713161400
GS-0343-13 Management and Program Analyst; closes 3/31/2023 (Hiring Manager: Sarah Ellis)
www.usajobs.gov/job/714167800
Deputy Assistant Director; closes 3/31/2023: USAJOBS - Job Announcement (Hiring Manager: AD Harrington)
www.usajobs.gov/job/713560600
Would love to take this class! It'll be some lucky students...
Want to be Inside the Situation Room with Secretary @HillaryClinton?
She and Dean Keren @YarhiMilo are co-teaching a new course on foreign policy decision-making at @Columbia this fall.
Learn more: www.sipa.columbia.edu/situationroom
Jay Healey reposted
Great history to capture and appreciate the effort it took to pull this together. This incident helped frame a lot of issues that would be key lessons learned to drive improvements in future responses.
nsarchive.gwu.edu/briefing-book/cyber-vault/2023-02-28/so…
ICYMI, we just passed the 25th anniversary of SOLAR SUNRISE, the first major named cyber campaign, and one of the most consequential ever!
It was the first to lead to a coordinated US government response by the FBI (and its new N…www.linkedin.com/feed/update/urn:li:share:704401989998310… nsarchive.gwu.edu/briefing-book/cyber-vault/2023-02-28/so…
Cyber threat #intelligence has a longer history than many realize.
Twenty years ago, I built this #cti indications and warning matrix for Goldman Sachs and larger FS-ISAC on whether the upcoming US invasion of Iraq would be likely to lead to major #cybe…www.linkedin.com/feed/update/urn:li:share:704401377811119…
Sooo, wonder how that frustration may play out against USCYBER hunt forward operations to eject Russian military operators from Ukrainian systems...
There is general sentiment, @CNA_org experts said, of resentment that the U.S. has such tools to conduct surveillance and reconnaissance.
“Sooner or later, that pent up anger was going to erupt and Russians would respond in one way or another.”
www.c4isrnet.com/unmanned/2023/03/15/downing-of-mq-9-reap…
Yesterday's @EricSchmittNYT piece touches this so elegantly: Predator incident is first known **physical** contact between US-Russian militaries
In cyber, the militaries are in, well, more constant contact: intelligence & "defensive" hunt forward ops
www.nytimes.com/2023/03/14/us/politics/russia-us-drone-bl…
Such a mismatch between the consensus view of the entire Intelligence Community (per the ATA) and international-relations academics, many of whom don't believe cyber capabilities can be escalatory or particularly effective in wartime
www.intelligence.gov/annual-threat-assessment
No, cyber may not win the war, but as Betts wrote in 1982, the goal of surprise is to "keep the victim reeling when his plans dictate he should be reacting"
warontherocks.com/2022/01/preparing-for-inevitable-cyber-…
ICYMI, check out documents on SOLAR SUNRISE at
@NSArchiveCyber
It's the 25th anniversary of this early intrusion, the 1st to get a coordinated US government response: FBI, DoD, White House
SUNRISE drove DoD to create world's 1st cyber command, JTF-CND, just 10 months later
25 years ago this month, in February 1998,the United States suffered a series of cyber intrusions that would later be named #solarsunrise. The series of government system intrusions took place over a period of three weeks, from February 1-26, 1998 (1/17).
Several early cyber experts - @MattDevost, Neal Pollard - were involved in the response, helping shape their early careers...
Really humbling to have my thoughts on "Russia and Ukraine, One Year Later" listed along these amazing scholars...
www.sipa.columbia.edu/news/russia-and-ukraine-one-year-later
This quote from @jonrlindsay was about naval & land combat, but has major implications for cyber as well.
Missed shots still land somewhere and they change the political makeup of cyber conflict...
From Information Technology and Military Power: www.jonrlindsay.com/information-technology-and-military-p…
So proud at what ONCD achieved with this strategy ... and what's coming next with the implemenation!
Sorry I couldn't be there in person...
Incredibly excited to have launched @POTUS's National Cybersecurity Strategy at @CSIS. The strategy is a tool to deliver a safer, equitable and more resilient cyberspace for all Americans.
Come join the White House cyber team!
Entry(ish)-level position for a GS9/11 at ONCD for cyber policy! WOW!
www.usajobs.gov/job/709514400
Jay Healey reposted
Jay Healey reposted
Jay Healey reposted
In honor of #blackhistorymonth, we celebrate some members of our talented leadership team, including our Acting Director @KembaWalden46, and recommit to the Administration’s goal of building a more diverse cyber workforce. Representation matters.
These cyber history lessons from 2011 still hold pretty well...
Great Cybersecurity 202 followup about @CISAJen @CISACyber on “secure-by-design” (by @timstarks)
**Insecurity by design is a 50-year old problem.** Excerpt below from Andersen report of 1972
Glad CISA is taking this on!
www.washingtonpost.com/politics/2023/02/06/how-cisa-plans…
Here's the link to the Anderson report...
(Misspelled as Andersen in the original tweet...)
csrc.nist.gov/csrc/media/publications/conference-paper/19…
Love the use of "sustainable" cybersecurity, borrowing from the language of environmentalism
We need more sustainable cyber practices so that when they are our age, our grandkids and their grandkids will have an Internet as awesome as the one we have today!
.@CISAJen and Eric Goldstein discuss sustainable cybersecurity—and explain how the U.S. government and the private sector can make cyberspace safer for everyone.
www.foreignaffairs.com/united-states/stop-passing-buck-cy…
Jay Healey reposted
“I think the best thing about being a SIPA student is that you have such a wide range of opportunities that you can choose from.” — Ambar Pagan MPA ’24
Learn more about SIPA's student community: www.sipa.columbia.edu/communities-connections
Not a funny take on #chinaspyballoon but remember that overflying denied airspace was pretty much the primary original mission of the U-2 and SR-71...
Great cyber policy jobs at Treasury!
www.usajobs.gov/job/702809000
Right that @CISACyber @CISAJen want to hold companies responsible for cybersecurity
One way to scale this policy, as I wrote in 2014, is to convince key, activist shareholders -- Warren Buffett, CalPers -- to vote their shares to improve security
www.usnews.com/opinion/blogs/world-report/2014/05/05/warr…
If USG can convince investors like Warren Buffett to take cybersecurity seriously ("We'll use NIST CSF in all my companies and won't buy any companies that doesn't take cybersecurity seriously") we can make more progress than going to individual boards one-by-one...
This 2014 article finished by saying "we don't need regulation, but innovation" which is no longer true, especially for minimum cybersecurity baselines for critical infrastructure entities...
Software liability is center of attention, so definitely study Jane Chong's series @lawfareblog in 2013 (tipped by @RosenzweigP)
Especially if you compare software to auto safety, it's a must read!
www.lawfareblog.com/bad-code-whole-series
This series is great background to better understand the new @ForeignAffairs article by @CISAJen @CISACyber
www.foreignaffairs.com/united-states/stop-passing-buck-cy…
Not just a brilliant example of sports journalism, but just brilliant journalism!
www.nytimes.com/interactive/2023/02/01/sports/football/br…
I have questions...
Added to the curriculum at @ColumbiaSIPA!
Glad it's back in stock...
Looking forward to reading "TikTok v. Trump and the Uncertain Future of National Security-based Restrictions on Data Trade" on gaps in US toolboc
I’ve struggled a bit since data can be simply bought, so what threat is there in just the flag of ownership?
jnslp.com/2022/12/16/tiktok-v-trump-and-the-uncertain-fut…
Reworking my syllabus on "Foundations of Cyber Conflict" and @peterwsinger @allanfriedman still is a unique book on so many basics!
Would love an updated version!
www.amazon.com/Cybersecurity-Cyberwar-Everyone-Needs-Know…
CUNY Baruch College looking for tenure track professor, with a specialization in international cybersecurity and global security!
Thanks to @adschina for the tip...
cuny.jobs/new-york-ny/assistant-professor-of-policy/BE46D…
Just got a major article rejected by a journal. Sigh. Happens to everyone! Don't let it get you down!
In an odd command relationship, once created in December 1998, JTF-CND would report *directly* to DepSecDef Hamre
After leaving DoD, Hamre joined @CSIS as president and CEO, a position he still holds
Yet, DoD didn’t have long to apply any lessons learned. As Deputy Defense Secretary John Hamre described, “Everything we learned in Eligible Receiver, we relearned in Solar Sunrise” – an incident that arose only a few months later. (14/16)
Happy to say we've been in touch with both Mike and Keith, who have additional material to share! More to come...
The NSA red team was led by Navy Captain Michael Sare, while Keith Abernethy served as the Chief Targeting Officer. (12/16)
Lt Gen John "Soup" Campbell was an F-16 pilot who later became the world's first joint cyber commander, in charge of the JTF-CND in December 1998. Now with @IridiumComm
Col Dusty Roads came to J-39 having flown F-117s. He next was the first cyber J3, at the JTF-CND
#er97 was organized by the JCS, especially the J39 and people like Lt Gen Soup Campbell and Dusty Rhoads. At its conclusion, the DoD had to brief the exercise president that DoD would not be able to fight a war, if required. (11/16)
Thrilled to be working w/ @tgrossman_ @Monahan_cyber on the history of cyber conflict and update Fierce Domain!
To start, here's a thread to celebrate the 50th anniversary of the major JCS cyber exercise, Eligible Receiver 97!
Twenty-five years ago, a DoD-led joint cybersecurity exercise sounded the alarm of the growing threat faced by ICT. Eligible Receiver #er97 is the most influential wargame ever. (1/16)
ICYMI: Alex Klimberg has a great article "Of Ships and Cyber: Transposing the Incidents at Sea Agreement" for @CSIS_Tech
Lots of past work on INCSEA on cyber but Alex goes article by article to better develop the idea
www.csis.org/analysis/ships-and-cyber-transposing-inciden…
I also really like his intro:
"Amid the geopolitical crises caused by Russia’s February 2022 invasion of Ukraine, it may seem wildly optimistic-or even bad diplomacy-to consider future arms-control scenarios for cyber operations. However, good policy needs to prepare ..."
Sweet tenure-track job at @UofNH for an assistant or associate professor of intelligence studies!
cc @karlgrindal
www.higheredjobs.com/faculty/details.cfm?JobCode=178203617
Yeah, here's the slide I used at CyberNext last week for @CyAlliancePrez. The only way to tell the difference in cyber workforce recommendations from 2000 vs 2022 is the language used (infosec vs cyber)
One of the most depressing things you can do is to read old cyber strategies & note how many recommendations are still applicable (and yet to be fulfilled). Take a gander at the 2003 one for example.
This isn't a shot at any new policies, just that we must address why these solid ideas didn't get implemented (or were but didn't move the needle) to do better this time!
Here's the answers...
Can't wait for this amazing event with Shane and Camille!
Tune into @ColumbiaDEFRAG next Tuesday, 13 December at 6pm!
@camillefrancois will talk with @ShaneHuntley about 'Hacking Google' and the 12-year history of @Google Threat Analysis Group!
www.eventbrite.com/e/defrag-presents-hacking-google-with-…
Jay Healey reposted
In March, #cyber912 competitors responded to a scenario examining a cyberattack impacting critical infrastructure in the midst of the 2022 World Cup in 🇶🇦. You can read the scenario, as well as award-winning recommendations from competitors here:
www.atlanticcouncil.org/content-series/cyber-9-12-project…
Reupping this really important piece @johnnysaks130 @MorningCybersec @NSA_CSDirector
Better title might've been "NSA cyber director: fight against ransomware shows limits of counteroffensive 'defending forward'"
www.politico.com/newsletters/weekly-cybersecurity/2022/11…
Joyce: despite NSA, @US_CYBERCOM “standing organization ... focused exclusively on pursuing ransomware" it is at least back to "historical norms"
Assuming this organization is using unique Title 10, 50 authorities such as direct action against REvil
www.zdnet.com/article/us-cyber-command-head-confirms-dire…
Despite being back to "historical norms", "Joyce was adamant the nation’s cyber warriors are already doing enough" and would not surge more resources to counter-ransomware
Shouldn't ransomware gangs be an easy test for Defending Forward?
A standing NSA-USCYBER organization had an important but ultimately limited impact vs ransomware
Do they have a better shot against better organized and resourced teams at SVR, GRU, RGB, MSS?
[BTW, this isn't meant to be snarky. Am I missing a reason why DF against state-backed APTs are more likely to be effective? Are ransomware groups, for example, more decentralized and harder to disrupt?]
I'd suspect state-backed APTs should be far harder: more driven, more disciplined, better resourced
DF might disrupt *particular operations* but APT's middle names is "persistent" for a reason
At a minimum, this seems strong refutation against the simple formulation like Sen Romney's the "only effective way to stop [cyber attacks] is to attack back ... the best defense is a good offense"
Sen Romney: "only effective way to stop [cyber attacks] is to attack back ... the best defense is a good offense"
It's been 1739 days since @US_CYBERCOM announced "defend forward." Time for DoD to produce unclas evidence that offense is a good defense
thehill.com/policy/cybersecurity/3740758-wray-tells-lawma…
One *major* negative of my hot take here: Of course, Defending Forward is a Title 50 role for USCYBER, not for the Title 10ing NSA
So Joyce's comments especially about NSA resourcing not nearly as germane as something from across Ft Meade...
And of course Joyce never even mentioned "defending forward" or counteroffensive in his interview...
Not an argument used much before or since.
In 2015, Admiral Rogers testified that just as building the triad w/ "robust" C2 helped nuclear stability, nations building major cyber commands would be ultimately stabilizing
irp.fas.org/congress/2015_hr/031915rogers.pdf
Major respect for mainland Chinese students here @Columbia for standing against the Communist Party
Big gathering last night...
Sen Romney: "only effective way to stop [cyber attacks] is to attack back ... the best defense is a good offense"
It's been 1739 days since @US_CYBERCOM announced "defend forward." Time for DoD to produce unclas evidence that offense is a good defense
thehill.com/policy/cybersecurity/3740758-wray-tells-lawma…
Happy to believe it is stopping major campaigns. But that's different from being "the best defense" or delivering security & stability
DoD defeated a lot of Taliban campaigns as well. Doesn't mean we were ever turning the corner...
nsarchive.gwu.edu/document/16475-united-states-cyber-comm…
What's not fair is the suggestion "if we were in a SCIF, we could tell you it's working"
If your only evidence is classified, then you may definitely be frustrating adversaries but you are likely not winning, which should be more obvious
Compared to traditional war zones, DoD has less "information asymmetry."
Any substantial decrease/increase in adversary operations *should be* pretty apparent (after a lag) especially for the most worrying attacks: those which are most widespread, brazen, disruptive
In terms of the NY Cyber Task Force, counteroffensive ops vs ransomware doesn't provide LEVERAGE
Outputs scale linearly with the inputs: x of effort returns (or maybe 2 or 3x). If offense were best defense, it would scale exponentially, x gives x^2
sipa.columbia.edu/sites/default/files/embedded-media/NYCT…
Exponential scaling isn't just theoretically possible: the best defensive innovations -- encryption, auto update, NIST CSF, creation of ISACs & CISOs -- all were likely exponential
Over the past 50 years, DEFENSE-AT-SCALE is usually the best defense
Derp. Thanks to a colleague for the correction. Exponential growth is 2^x not x^2...
Great point on escalation @MorningCybersec @johnnysaks130
@NSA_CSDirector sees "decline" “in [adversary] willingness to use large-scale vulnerabilities” like NotPetya, WannaCry
(1) Possible taboo against them & (2) harder now, as need to chain exploits
www.politico.com/newsletters/weekly-cybersecurity/2022/11…
Interested in the cyber parallels of this piece by @Mipeck1:
"Initially, Russia's jamming offensive was devastating ... [but doomed by] poor planning, lack of coordination, & general indifference by Russian commanders toward getting the details right"
www.businessinsider.com/russian-ew-campaign-in-ukraine-un…
Wow, stunning thread here from Toomas...
Some PR advice for Russian liberals: (a thread)
1. Stop being so self-absorbed. Don’t talk about a “Marshall Plan” for Russia when those who would pay for it read daily accounts of new atrocities in Ukraine
2. Don’t call Westerners Nazis when they do want Russians to travel 1/n
Such a mismatch:
International relations theorists: ransomware is not much a natsec threat
Reality: Over half of UK COBRA meetings are on ransomware. Not half of all *cyber* meetings, half of ALL
therecord.media/ransomware-incidents-now-make-up-majority…
Yes, many of those meetings were for a sprint for solutions
BUT according to @AlexMartin's sources: despite sprint, still "no light at the end of the tunnel" even w/ UK military working w/ US partners on **offensive ops** in response -- a clear indicator of natsec importance
Just had @AlexMartin clarify that "sprints" were different cross-departmental meetings than crisis-management COBRA
Puts the mismatch into even sharper relief: one-to-multitude attacks like ransomware need to be central to IR theories, not an add on
www.lawfareblog.com/understanding-offenses-systemwide-adv…
The completely unchoreographed, candid poses of Michael Novak (artistic director @paultaylordance) & Steve Biddle (@SIWPSColumbia) while discussing themes of war in the arts, after performance of stunning anti-war ballet, The Green Table (Kurt Joos, 1932)
I want reference this photo whenever I hear about diversity gap in cybersecurity. Just an amazing group from every kind of background
Programs like #cyber912 are amazing at identifying, training, mentoring diverse talent!
Great open position for risk management at National Risk Management Center @CISAgov
Now open for GS-14!
www.usajobs.gov/job/685969900
Rust is critical way to eliminate entire classes of attack, shifting advantage to defenders not just at one organization (like a firewall) but across the entire system
Good summary on Rust and use in Android, h/t @DaveKSecure
www.wired.com/story/rust-secure-programming-language-memo…
"And if the attackers are themselves an all-star team, then few organizations in the world have much chance."
Through innovations like memory-safe languages that eliminate entire classes of attack, defenders can reverse this decades-long trend across the entire system
As tweeted earlier this week, it has been 50 years since these trends were first documented
It's been FIFTY YEARS this month that the Anderson Report of 1972 documented that security must be "designed into a system from its inception" as "there is little chance it can be made secure by retrofit"
Jay Healey reposted
It’s #cyber912 Week at @ColumbiaSIPA! @SIPA_DCG is excited to return the US competitions to an in-person format this Friday and Saturday!
Better yet, I was wearing the matching hoodie from 2018!
It's been FIFTY YEARS this month that the Anderson Report of 1972 documented that security must be "designed into a system from its inception" as "there is little chance it can be made secure by retrofit"
This 50-year old Anderson report also assessed "there are essentially no costs for finding at least one exploitable vulnerability and then designing an attack around it"
These statements highlight offense system-wide advantage over defense
Any particular org or state might have idiosyncratic advantages but for 50 years, factors like lack of built-in security & inexpensive exploitable vulns mean the system favors offense
www.lawfareblog.com/understanding-offenses-systemwide-adv…
This point is missed by most scholarship: cyber campaigns are getting progressively worse decade after decade
Accordingly, there is a higher risk of extreme events which might exceed states' resilience or willingness to tolerate
If defensive adaptation can match the intensification of offense, then its no big deal
If adaptation falls behind (say by deploying IOT, ICS) then defense will be overwhelmed and policymakers will feel need to respond/retaliate
Great to work w/ @VirpratapVS on how cyber escalation risks vary w/ tensions in geopolitics and cyberspace
Academic & policy work too often assumes **constant level** of cyber & geopolitical tension
Can ignore how cyber conflict has different escalation risks during crises
Looks like this link isn't active ... @ccdcoe @piret_ccdcoe can you help?
In the meantime, mirrored here: www.cybersecitalia.it/wp-content/uploads/2022/05/Horizon_… [PDF]
And because geopolitical & cyber tensions are worsening, escalation ratchets higher past what "pressure release" can adapt
Likewise, when cyber tensions are high (that is, feel states keenly feel the risk of existential crises from online threats), chances are higher that a purely cyber campaign will spark a larger geopolitical crisis
However, if tensions are low, then the use of cyber capabilities will not escalate and can definitely de-escalate as @JoshRovner1 and others have described
Best example is US 2019 cyber attack on IRGC after their shootdown of RQ4-A & mining of tankers
If cyber & geopolitical tensions are already high, then further cyber conflict further escalates, possibly creating (or even exacerbating a crisis into war)
Our work expands on my @TXNatSecReview paper with Bob Jervis, to explore four mechanisms on how cyber capabilities can stabilize or destabilize geopolitics
Wrote this in 2014. Still true?
Totally loving/borrowing this quote from @woodyatpch. Just strikes so many great notes:
"To the degree that I’ve learned about cybersecurity, it’s because I started when it was simple and I’ve never really looked away"
Worth reading the full interview!
medium.com/authority-magazine/cyber-defense-bill-woodcock…
Have or getting a Ph.D. in Political Science, Public Policy, or a cyber-related field?
Come join us at @ColumbiaSIPA as a tenure-track assistant professor!
apply.interfolio.com/113150
This position is still open!
@ColumbiaSIPA is hiring a tenure-track assistant professor in the overlap of cybersecurity international relations
Hope you'll apply and we'll be colleagues soon!
A packed house of @ColumbiaSIPA cyber students, alumni, and NYC-area cyber professionals!
Thanks to @elenakvochko and to all who joined and support our amazing students @SIPA_DCG!
Last night, SIPA Cyber (w @Jason_Healey) hosted its first Uptown Cyber Social of the Fall '22 semester. Fantastic to see the NYC cyber community grow bigger and stronger!
Thank you to @SAP @elenakvochko_ for their continued support!
📸: @AurelianMohan
Jay Healey reposted
It's #cybersecurityawareness Month, and we all have a part to play in securing cyberspace for all Americans. Follow along this month to meet some of our nation's cyber heroes – from all walks of life – working with us to protect our communities online #seeyourselfincyber
We argue Ukrainian IT Army acting opposite to the norms like-minded states have pushed for 2 decades.
"Responsible state behavior" has been that offensive cyber ops should be directed by govts, conducted by govt forces, using govt C2, against military or dual-use targets
‘Patriotic Hacking’ Is No Exception
New from @Jason_Healey and Olivia Grinberg @SIWPSColumbia for @lawfareblog
www.lawfareblog.com/patriotic-hacking-no-exception
Ukrainian hactivists - regardless of how much we may empathize with them or agree with their aim - generally take the opposite approach:
Civilian govt leadership, open to everyone, against not just dual-use but purely civilian targets
If you want to know more on this topic, check out the great work by @iiyonite !!
Hey all, if you following @ncdinglis for news on national cyber, be sure to also check out @KembaWalden46, the principal deputy ONCD!
Google may not know me as well as it thinks...
"Bob Jervis made important contributions to research on cyber conflict because he knew that, although it was fought using new kinds of tools, it was still conflict"
Honored to share reminiscences & contributions from Bob @SIWPSColumbia
tnsr.org/roundtable/remembering-robert-jervis/
"The cyber academics who he kept closest — such @HostileSpectrum with his encyclopedic memory of who hacked whom — were those with long careers as practitioners, rich with knowledge beyond what was printed in journals"
Bob "always had a special, abiding sympathy for decision-makers" so pointing out failures was "less an accusation than a warning against self-deception and an admonition to keep a look out for one-sided perspectives and motivated reasoning"
Honored to be on the list of Cybersecurity Visionaries for the CyberScoop 50 Awards @CyberScoopNews
www.cyberscoop.com/cyberscoop50/vote/
Another great poli-sci tenure-line position, @AmericanU with the brilliant @JoshRovner1
Only a few years ago, PhDs were getting advice to avoid cyber until after they'd secured tenure. The field changed so fast!
apply.interfolio.com/112538
And these photos seem to show some docs with White House logos and headers, meaning they fall under the more-stringent Presidential Records Act and not Federal Records Act.
The image is actually quite telling. The secret/top secret documents found in Trump's office have a "TK" classification which stands for TALENT KEYHOLE aka secret intelligence from spy satellites and planes.
Come join us to compete in-person in NYC here at Columbia!!!
Registration is now open for the NYC #cyber912 competition, returning in-person to @ColumbiaSIPA Nov. 4-5! More info here: cglink.me/2e9/r1653460
This is a smart and well-written proposal. Just the title itself gets across the main point while the proposed solution is reasonable. Love the solid references to best practice in every point.
Top-notch policy writing.
Jay Healey reposted
On 21-22 July, @Jason_Healey and SIPA Cyber led a contingent of @ColumbiaSIPA students to engage with members of the cybersecurity community in Washington DC.
Take a look at how the trip went as captured by one of its student participants.
www.sipa.columbia.edu/news/program-takes-students-and-rec…
An update from @SIWPSColumbia on Bob Jervis:
The SIWPS team of Olivia, Eric, & Courtney "archived the entire contents of Bob's office, over 2,000 volumes and counting - and that is before adding his books in 1302" (the conference room)
A bittersweet update: in this podcast, Francis Gavin, @ColinKahl, @MiraRappHooper, @derekchollet reminisce about Bob's office stacked w/books
@SIWPSColumbia is cataloging every book of Bob's: title, location on shelves, amount of annotation. Already 1000 books done w/1000s left
How are you de-toxing and catching up on email post BH and DC?
Me: @RiversideParkNY
Jay Healey reposted
📢 Join @DEFCONPolicy @defcon this year. Check out our upcoming sessions below: 📢
Because in NYC, you can just walk down the street and hear Nathan and the Zydeco Cha Chas ...
@LincolnCenter Oasis
A bittersweet update: in this podcast, Francis Gavin, @ColinKahl, @MiraRappHooper, @derekchollet reminisce about Bob's office stacked w/books
@SIWPSColumbia is cataloging every book of Bob's: title, location on shelves, amount of annotation. Already 1000 books done w/1000s left
Beautiful Manhattan sunset...
One reason to study cyber at @ColumbiaSIPA: the amazing connections between students & alumni!
Just completed summer DC trip w/ 18 students, recent alum, & even a just-admitted student to talk careers with alumni & others around DC
Check out this awesome group!
Thanks to @CyAlliancePrez @CyberAlliance for the great conversation -- including with fabulous but off-camera @C_Painter!
And super special thanks to @elenakvochko and @sap for the support to make it happen!
I booked to take my seat (and all your chips)!
Seventeen years after I last worked here, happy to be back at the White House, on part-time detail from @CISAgov, to help @ONCD draft the nation's next cyber strategy.
I'll still be working @ColumbiaSIPA with @VirpratapVS on research & events on cyber conflict and business and systemic cyber risk as well as the great students @SIPA_DCG!
Just finished a debate @eborghard @CFR_org where we agreed the difficulty using cyber against weapon systems in wartime, esp at scale
Plausible counterexample: RU or UA find an 0day for DJI drones, patch their own, then disable or commandeer all drones of the other side
Strikes me as realistic exploit (though they'd need to solve access issue of how to affect enough drones)
A neat hack that could substantially impact the course of the war by blinding a fair amount of the other sides ISR assets
Jay Healey reposted
Looks like someone's back after the cryptocurrency market imploded...
What an out-of-date practice question for a cert:
'The President's Critical Infrastructure Protection Board's "National Strategy to Secure Cyberspace" report outlines which of the following?'
That strategy was from 2003 ...
More important than what USCYBER meant saying "we've done offense against Russia on behalf of the Ukrainians" is what Russia heard
They probably know about it & don't care about the words
They just *might* care deeply. Just imagine GRU machismo & response to status challenge
Still think this is worth a LOT of attention
1) Even routine intel collection ops can be more escalatory during crises
During the Cuban Missile Crisis, the USSR launched MiGs to intercept a routine U-2 flight which veered into Siberia
Smart take from @brysonbort
We already knew Cyber Command was engaging in cyber ops to support Ukraine. People think it’s news because when they hear OCO (offensive cyber operations) they think it means CNA (computer network attacks) and not CNE (computer network exploitation)
Was this U2 overflight intentional provocation or signal by the White House? The start of a SAC raid? Just a coincidence?
The US scrambled interceptors – armed w/ nuke air-to-air missiles – to protect the U2. WWIII might have started by mistake
www.vanityfair.com/news/2008/06/missile_crisis_excerpt200806
2) Even routine persistent engagemenst are more dangerous during crises
Also during the Cuban Missile Crisis, US anti-sub forces launched practice depth charges -- with actual explosives -- against Russian subs to force them to surface
Will Putin, the afraid, dying, paranoid KGB veteran shrug off USCYBER disrupting his forces?
Or will this confirm his paranoia that the USA is behind all of this and needs to be taught a lesson?
Probably he won’t. Probably there won’t be any escalation.
But understanding the risks has less to do with the actual cyber operations & more about the geopolitics, the psychology, and the growing likelihood of mistake & miscalculation
Jay Healey reposted
2021-22 highlights: General John W. Raymond of the U.S. Space Force keynoted the annual NY Cyber 9/12 Strategy Challenge at SIPA. SIPA News: www.sipa.columbia.edu/news/taking-cyber-stars
This is massive (but hinted at in previous reporting by @SangerNYT & others)
Biden: "We will not be directly engaged in this conflict"
Except, that is, in cyberspace
Cannot ignore the escalatory potential of direct military actions vs Russia, even if "just" online
🚨
Scoop: In an exclusive interview with Sky News, General Paul Nakasone confirmed that Cyber Command has conducted offensive operations in support of Ukraine.
news.sky.com/story/us-military-hackers-conducting-offensi…
Ever blow up the 10th time your spouse or kid does something, when it was fine the first 9 times?
Maybe they ignored the warning signs you were losing patience, maybe you just got a bad night's sleep
Cyber attackers & defenders aren't rational actors
How Putin (or some low-level commander of a GRU cyber unit) respond may have less to do with cyber itself than emotions like fear, pride, anger. Patriotism and regime survival
We're in uncharted political psychology territory
Conti's ransomware assault on Costa Rica should be mandatory case study on offensive cyber coercion
If a small state can be bullied for ransom (even if they're resisting) another might be bullied to, say, veto more sanctions on Russian or shun Taiwan
www.reuters.com/world/americas/latest-cyberattack-costa-r…
If you have to try to finish a paper I'm NYC on a Friday afternoon, there are worse ways...
Sweet job opening at @CISAgov in the National Risk Management Center for a GS-14 supervisory analyst to "identify cyber/physical infrastructure threats and risks"
www.usajobs.gov/job/652498300
The job closes after the first 100 applicants, so don't wait to apply!
Jay Healey reposted
For the sake of comedy, I refuse to learn the context behind this statement.
Watching porn at work is unacceptable, says UK PM Johnson www.reuters.com/world/uk/watching-porn-work-is-unacceptab…
RSVP for this amazing event, Cyber Risk to Financial Stability w/ @NewYorkFed
Eric Goldstein of @CISAgov
@JohnHultquist of @Mandiant
Phil Venables
Tammy Hornsby-Fink of @federalreserve
@woodyatpch of @PCHglobal
@jwwelburn of @RANDCorporation
Anna Kovner of @NewYorkFed
& more!
Register for the 3rd Annual State-of-the-Field Conference on #cyberrisk to #financialstability by @ColumbiaSIPA and @NewYorkFed being held on 4/28 and 4/29.
Check out the agenda here❗️
www.sipa.columbia.edu/ideas-lab/techpolicy/2022-state-fie…
Sign up here!🔽
columbiauniversity.zoom.us/webinar/register/WN_RjxUKMDhRl…
Join us 28-29 April, our 3rd annual on Cyber Risks to Financial Stability in partnership w/ @NewYorkFed w/
Eric Goldstein @CISAgov
@JohnHultquist
@philvenables
Tammy Hornsby-Fink @federalreserve
@woodyatpch
@jwwelburn
Anna Kovner @NewYorkFed
& more!
www.sipa.columbia.edu/ideas-lab/techpolicy/2022-state-fie…
Love this assessment by @maddiestone in today's WaPo Cyber 202 by @Joseph_Marks_ : "58 zero days [is] less than 20% of the total number ... exploited in 2021"
www.washingtonpost.com/politics/2022/04/20/even-most-comp…
Reminds me of our VEP analysis in 2016.
Unlikely NSA is retaining 100s or 1000s of 0days each year when there are only a few hundred total from all sources
jia.sipa.columbia.edu/online-articles/healey_vulnerabilit…
Not sure I still stand by original assessment that NSA only keeps "single digit" number of 0days, but definitely that it is smaller than many feared at the time
Jay Healey reposted
Akhilesh Variar (@ColumbiaSIPA) and @dannymuradw (SIPA+@qmss_columbia) presented their ongoing work around "CYsyphus" - the Cybersecurity Policy Recommendation Tool during #datascienceday2022
Learn more about the project here:
www.sipa.columbia.edu/ideas-lab/techpolicy/cysyphus-cyber…
"Defending forward" vision was launched 4 years ago: April 2018
Isn't that long enough to know if it worked "to render most malicious cyber and cyber-enabled activity inconsequential ... & contest dangerous adversary activity before it impairs our national power"?
As @nejenkins argued in 2019, we should have seen a decrease by now, if impact of not operating persistently was so strong
Not clear that DF/PE has caused escalation, but it's a better fit to the curve than what was promised
ccdcoe.org/uploads/2019/06/Art_07_Rough-and-Ready.pdf
As I argued in 2017 & again in @lawfareblog, PE/DF always needed
1) @US_CYBERCOM to give clear criteria and timeline for success & failure
2) Political throttle for POTUS
3) Defined sunset when authorities expire if they're not clearly working
www.lawfareblog.com/soldiers-statesmen-and-cyber-crises-c…
ICYMI: Must-watch panel @ColumbiaDEFRAG on WarGames (1983) with an absolutely amazing panel @CISAJen, @LanceWeiler, Maj. Gen. Kevin Huyck (@USNorthernCmd), @webjedi, @MattDevost
www.youtube.com/watch?v=iqx6STDYJ7c
Jay Healey reposted
So excited to *compete* in @CyberStatecraft's #cyber912 today! @BelferCyber grad students (Ghost In the Shellcode) are coming in with a power team of women in cyber security and I'm here for it 🤩
Jay Healey reposted
27 years ago, the paper discussed:
Information warfare
Human factors
Ransomware
Bug bounties
Creation of CISA
Hackers as a national resource
Autonomous military constructs
Increasing attacker costs
Deregulation of encryption
Cyber damage assessments
www.oodaloop.com/archive/2020/05/14/cyberwar-was-coming/
Jay Healey reposted
Cyberspace may be a domain of military operations, but it is not predominantly so. Civil-military relations in the United States must adapt to new demands or cyberspace may be irretrievably diminished.
From @Jason_Healey: www.lawfareblog.com/soldiers-statesmen-and-cyber-crises-c…
DoD has advanced capabilities but cannot fix the internet at scale (as does Microsoft, Google), directly thwart adversaries at scale (CrowdStrike, Mandiant), share intel at scale (@CyberAlliance), or reinforce core infrastructure during attacks at scale (Cloudflare, Verizon)
The private sector is the supported command (a phrase I think I came up with first, in 2012), or to switch the analogy, akin to the host nation in COIN
[Separately, this requires a new mindset of Defense Support to the Private Sector]
digitalcommons.usmalibrary.org/aci_ja/164/
Inspired by Dick Betts @SIWPSColumbia, my latest at @lawfareblog: "Soldiers, Statesmen and Cyber Crises: Cyberspace and Civil-Military Relations"
[Sorry for the gendered language, but it is a reference to Dick's classic book]
www.lawfareblog.com/soldiers-statesmen-and-cyber-crises-c…
Subjective control cannot be a blank check written once, at the beginning of the persistent engagement, to last forever, an online version of the 2001 Authorization to Use Military Force
4) US military culture can discount and misunderstand the role of private-sector entities, which don’t just own most of the domain but are the most powerful actors
"Grey space" = someone else's property, paid for with their own money, for their own purposes and information
Jay Healey reposted
#cyber912 might be virtual this year but that just means you can tune in for *more* programming. RSVP below!
Join us March 25 for a virtual discussion, part of our 2022 DC #cyber912 Strategy Challenge.
Tune in for a panel with @Megantron__47, @wendynather, Kiersten Todt of @CISA, and Morgan Adamski of @NSAcyber exploring the role of public-private collaboration.
www.atlanticcouncil.org/event/beyond-hope-as-a-strategy/
Cyber is weird reason #3,428
In the Cold War, we mostly knew what NATO was developing, deploying, and operating but USSR was a closed book
In cyber conflict, other than broad force structure, we know far more about what adversary government APTs are up to than our own
Scary paragraph (and article) by George Beebe @CFTNI
nationalinterest.org/feature/raging-toward-abyss-russia-2…
Not comforting that Putin's own generals probably don't know if he's serious about tactical nuclear weapons either...
Thanks to the amazing @JordanKlara @CyberpeaceInst for joining our class on cyber conflict @ColumbiaSIPA!
We've focused the class squarely on Ukraine & Klara discussed the basics of CPI, how civilians are affected by cyber conflict, & intl law!
Made a for of a bottle of Johnny Blue w/ Stuart Gottlieb @SIWPSColumbia yesterday on the persistence of sanctions:
By March 2026, is NordStream 2
Jay Healey reposted
Safa Sahwan Edwards @AtlanticCouncil on workforce development www.makingspacepledge.org/21-women-in-cybersecurity-you-n… @jumokedada #womenshistorymonth #cybersecurity #makingspaceincyber #cyberbase
Wait, when did @Columbia get those?
These headlines always cause a split second of confusion for those of us working @SIWPSColumbia
Hope it has more classrooms, corner offices and conference space
First Columbia Ballistic Missile Submarine Begins to Take Shape - USNI News
news.usni.org/2022/03/08/first-columbia-ballistic-missile…
Of course, as soon as this went live, I asked "what would @DAlperovitch think?" & realized I needed to add to the piece:
"Russia needs to be stopped, actions have to be taken & the West can't be paralyzed by escalation concerns in the face of slaughter & tyranny"
"There are multiple ways cyber conflict around the Ukrainian invasion might escalate into a direct conflict between Russia and NATO, possibly as a result of either side’s offensives."
@Jason_Healey in @WarOnTheRocks warontherocks.com/2022/03/preventing-cyber-escalation-in-…
Called it...
US won't help Ukraine w/ boots on the ground or no-fly zone for direct combat with Russia
But assistance w/cyber capabilities maybe more tempting:
- Disrupt Russian military C2 in Ukraine?
- Determine OOB, locations to pass to Ukraine?
- Target conscripts, commanders w/messages?
More realistic to me isn't a no-fly zone, but a Kyiv Airlift, of aircraft bringing food & humanitarian supplies to the capitol, if it gets surrounded
Might be pressure for such an airlift ... and for those aircraft to have NATO fighter & SEAD escort
Why no major Russia cyber onslaught? Here’s a thread on various reasons we’ve heard
Not sure if this list by @VirpratapVS & me improves on the four in excellent article @ciaranmartinoxf (ease, effectiveness, escalation, ethics) but just in case...
www.lawfareblog.com/cyber-realism-time-war
Keeping UA Internet up to exploit access may have been the plan, but seems at the moment to be a bad choice w/little obvious gains in cyber or disinfo/propaganda
If this was the case, it could change soon to be more disruptive ...
Or maybe (seems unlikely) the UA Internet is up b/c RU is collecting so much intelligence
9) Overestimated Russian capabilities
Maybe RU cyber just isn't that good at scale outside of grey-zone shenanigans? After all, no aspects of RU army, air force are impressive
Again, not sure I buy this fully
GRU was good enough to cause havoc many other times...
10) Out of capabilities
Just as the Russian Air Force used most of their PGMs in Syria & were unprepared to take on the UA integrated air defenses, maybe RU cyber just doesn't have the Schlitz left to achieve?
Defer here to @HostileSpectrum & others but suspect even if true, there'd be enough soft targets in UA
11) Ride the Bear shirtless!
This one was from Emily, a @ColumbiaSIPA student who thought Putin maybe wanted to posture, using the most masculine, military approach possible
Don't know how much it explains, but if you substituted "Trump" for "Putin" I find myself nodding a bit...
Personally, none of these are nearly enough, for me anyhow, to explain Russian behavior
Even if those who think cyber nearly worthless in wartime are absolutely correct (which is entirely possible) ...
Why didn't Russia even try it when they were so active since 2014?
Regardless of which you or I think is true...
We probably need to split our explanations into (a) why so little in Ukraine and (b) why essentially nothing against the West
Why so little in Ukraine? I come down on some mix of almost all of these but especially why bother, effective defense, and onslaught might come later (#2, #5, #6)
This is no more than a guess, heavily influenced by my prior expectations and research
This is just one week into a new era of international relations. Let's keep our eyes & minds open
There are lot of other academics, practitioners I ought to have cited here
Apologies to those I missed! As you find these, please reply with the best references so people can read the areas of agreement & disagreement
US won't help Ukraine w/ boots on the ground or no-fly zone for direct combat with Russia
But assistance w/cyber capabilities maybe more tempting:
- Disrupt Russian military C2 in Ukraine?
- Determine OOB, locations to pass to Ukraine?
- Target conscripts, commanders w/messages?
US likely to be in .ru networks not least to understand RU capability
And US may already providing OOB, locations just using imagery, so not crazy to provide it from cyber
OSINT gives plenty of other plausible sources, so less issue about IGL
And if US is already in those Russian C2 systems for intelligence purposes, relatively trivial to disrupt them, if the order were given...
Seems pretty escalatory to me, but to forestall a massacre, I can imagine decisionmakers at least wanting the option to consider
Less reflexively against this Ukraine outsourcing hacking than others but...
This is an incredibly dangerous moment for Europe. De-escalation and peace will be hard enough on their own without outsourced hacking to worry about.
Any real damage may come from Ukrainian cyber crime groups ... or Western cybersecurity professionals who decide to answer the call
Either group could be pretty dangerous foes
The bulk of the outsourced attacks will likely just be script-kiddie defacements, DDoS, and disruptions.
These will do little other than increase the chance that Putin will see no reason not to continue to escalate his own cyber offensive
Jay Healey reposted
There are less than 2 hours till "Shall We Play A Game?" commences.
Registration will close at 7pm.
www.eventbrite.com/e/defrag-presents-wargames-shall-we-pl…
Join @CISAJen @LanceWeiler @MattDevost, Maj. Gen. Kevin A. Huyck (@USNorthernCmd), @webjedi and @Jason_Healey on *2/24 @ 7:30pm EST* for an interactive event around WarGames (1983).
Part of the @ColumbiaDEFRAG by @ColumbiaDSL and @ColumbiaSIPA
www.eventbrite.com/e/defrag-presents-wargames-shall-we-pl…
Register for this awesome event tomorrow night!
We'll be discussing WarGames, and exploring a WarGames-themed interactive board, with amazing hackers and officials!
📢"Shall We Play a Game?" Join us 2/24 for a discussion of the impact of the motion picture WarGames w/ @CISAJen, @LanceWeiler, Maj. Gen. Kevin A. Huyck (
@USNorthernCmd) @MattDevost, @webjedi & @Jason_Healey & interactive elements.
Register ➡️ www.eventbrite.com/e/defrag-presents-wargames-shall-we-pl…
A country under threat of military invasion is getting DDoSed
They're victims, defenders who could be doing a lot of other things, suffering yet again
Missing time w/ their families, struggling w/out enough resources, yet again
STFU if this isn't serious enough attack for you
Have some empathy, please
Spare your derision
Let's feel lucky this is only as bad as it's gotten so far and hope this is as bad as it gets
Jay Healey reposted
This looks great! Should be fun while helping the community connect for some virtual bonding.
Join @CISAJen @LanceWeiler @MattDevost @webjedi and @Jason_Healey on Feb 24 at 7:30pm Eastern for an interactive event, Shall We Play A Game. A part of DEFRAG: Hacked Film Festival by @ColumbiaDSL @ColumbiaSOA and @ColumbiaSIPA
www.eventbrite.com/e/defrag-presents-wargames-shall-we-pl…
WarGames isn't just about hacking but NORAD & Global Thermonuclear War
So @ColumbiaDEFRAG are thrilled to announce Maj Gen Kevin Huyck & Brig Gen Eric DeLange are joining this event
They run Operations & Cyberspace Operations for @NORADCommand!!!
Join @CISAJen @LanceWeiler @MattDevost @webjedi and @Jason_Healey on Feb 24 at 7:30pm Eastern for an interactive event, Shall We Play A Game. A part of DEFRAG: Hacked Film Festival by @ColumbiaDSL @ColumbiaSOA and @ColumbiaSIPA
www.eventbrite.com/e/defrag-presents-wargames-shall-we-pl…
There have been other events about WarGames ... but have any had top officials from both @CISAgov & @NORADCommand?
Plus @MattDevost, @LanceWeiler & @webjedi!
This is exactly why we created DEFRAG: freakin' epic events to learn about hackers, computer security, & society & tech
None of you got to go to the premiere of WarGames...
So join this virtual, interactive event, the coolest event on this awesome movie since 1983!
Thanks to @DAlperovitch for visiting my class on cyber conflict @ColumbiaSIPA to talk Ukraine, cyber conflict, and cyber threat intelligence!
Jay Healey reposted
𝙻𝚘𝚐𝚘𝚗: 𝙰𝚛𝚖𝚊𝚐𝚎𝚍𝚍𝚘𝚗
𝙸𝙳𝙴𝙽𝚃𝙸𝙵𝙸𝙲𝙰𝚃𝙸𝙾𝙽 𝙽𝙾𝚃 𝚁𝙴𝙲𝙾𝙶𝙽𝙸𝚉𝙴𝙳 𝙱𝚈 𝚂𝚈𝚂𝚃𝙴𝙼
--𝙲𝙾𝙽𝙽𝙴𝙲𝚃𝙸𝙾𝙽 𝚃𝙴𝚁𝙼𝙸𝙽𝙰𝚃𝙴𝙳--
#𝚂𝚑𝚊𝚕𝚕𝚆𝚎𝙿𝚕𝚊𝚢𝙰𝙶𝚊𝚖𝚎?
Soooo smoooooth!
Look what I found! AD&D computer games from the late 1980s, with disks!
My first official paychecks...
Washing dishes at @Friendlys in 1986
Jay Healey reposted
The pandemic brought about a push into virtual learning and the adoption of e-proctoring systems.
@camillefrancois highlights the issues faced by these platforms, including silently training facial recognition systems and bias towards students of color.
Jay Healey reposted
Last year, @Twitter and @Hacker0x01 held a challenge at @defcon to tackle bias within their algorithms for photos.
@CyberSemantics calls out the positives of that bounty program, including the openness in showing the results.
OMG love this "challenge lock" from the 1800s, a bounty which went uncollected for decades
Great insights from @ystvns and @_Ryan_Ellis on bug-bounty programs as a one-sided labor market which favors the big companies
Saltzman and @TechPolicySIPA will host "Debugging Bug Bounties in Cyberspace: from Vulnerability Discovery to Algorithmic Harms Redress" this Friday, Feb. 4 at 2:00 P.M. EST. Panelists include Ryan Ellis, @camillefrancois, @CyberSemantics, and @ystvns. columbiauniversity.zoom.us/webinar/register/WN_Zm97iZL2Sj…
Turns out, using bug bounties as a model can help us understand and tackle, algorithmic harms
In this case, the Twitter bias bounty...
Jay Healey reposted
Let's start with definitions from @AJLUnited
Algorithmic Harms: when an actor, uses algorithmic systems to automate classification, recommendations as a process that harms people by compromising opportunities, violating rights, social stigma, physical safety, etc.
Jay Healey reposted
Up now, @camillefrancois and @CyberSemantics discuss a report they coauthored at @AJLUnited
www.ajl.org/bugs
Jay Healey reposted
.@ystvns right now re: the recs from new report: datasociety.net/library/bounty-everything-hackers-and-the…
Jay Healey reposted
Starting NOW!
@ystvns + @_Ryan_Ellis & @camillefrancois + @CyberSemantics w Matt Goerzen will examine the state of bug bounty programs and what we can learn from them to address #algorithmic harms.
events.columbia.edu/cal/event/eventView.do?b=de&calPath=%…
Great insights from @ystvns and @_Ryan_Ellis on bug-bounty programs as a one-sided labor market which favors the big companies
Saltzman and @TechPolicySIPA will host "Debugging Bug Bounties in Cyberspace: from Vulnerability Discovery to Algorithmic Harms Redress" this Friday, Feb. 4 at 2:00 P.M. EST. Panelists include Ryan Ellis, @camillefrancois, @CyberSemantics, and @ystvns. columbiauniversity.zoom.us/webinar/register/WN_Zm97iZL2Sj…
I'd love to find a history-minded co-author to update Fierce Domain. So much has happened since it was published.
Hit me up in DM or email if interested...
For more on this history, check out the history book, A Fierce Domain, from @karlgrindal & me
There's a whole chapter on SOLAR SUNRISE by someone who was then a rising star, @maurertim, now a senior counselor for the secretary of DHS
www.amazon.com/dp/B00E00QSN4?btkr=1
DEFRAG: WarGames is coming!
𝙶𝚁𝙴𝙴𝚃𝙸𝙽𝙶𝚂 𝙿𝚁𝙾𝙵𝙴𝚂𝚂𝙾𝚁 𝙵𝙰𝙻𝙺𝙴𝙽.
𝚂𝙷𝙰𝙻𝙻 𝚆𝙴 𝙿𝙻𝙰𝚈 𝙰 𝙶𝙰𝙼𝙴?
Jay Healey reposted
In cyber conflict, like other forms of conflict, the further back you look the more universal truths you can discover, which makes history that that captured in A Fierce Domain so very relevant to defenders and policy makers today. See thread:
OTD in 1998: SOLAR SUNRISE began. AFCERT detected major intrusions seeming tracing in part to the Middle East during a major buildup against Saddam Hussein's Iraq.
DEPSECDEF briefed POTUS this might be a digital Pearl Harbor. It was Makaveli and Stimpy, 2 teens from California
OTD in 1998: SOLAR SUNRISE began. AFCERT detected major intrusions seeming tracing in part to the Middle East during a major buildup against Saddam Hussein's Iraq.
DEPSECDEF briefed POTUS this might be a digital Pearl Harbor. It was Makaveli and Stimpy, 2 teens from California
I was the AF/XOIWD action officer to set it up, w/ Dusty Rhoads, Bob Lamb, Arnold Abraham
Then joined as the 2nd person PCS'd to a Cyber J2 shop, under @bobgourley
There were 25 of us at first, starting in aluminum trailers behind DISA on Arlington Hill
For more on this history, check out the history book, A Fierce Domain, from @karlgrindal & me
There's a whole chapter on SOLAR SUNRISE by someone who was then a rising star, @maurertim, now a senior counselor for the secretary of DHS
www.amazon.com/dp/B00E00QSN4?btkr=1
Starting shortly!
🗓️ Thursday 1/27 at 12pm
Join @Jason_Healey (@ColumbiaSIPA) and @LanceWeiler (@ColumbiaSOA) as they discuss the origins of @ColumbiaDEFRAG and what you can look forward to through 2022!
x.com/i/spaces/1mnGednbNgrKX
If you love hacker movies, join this Twitter Space discussion tomorrow!
Even better, if your friends think hacking (and hackers) are exactly how it looks in the movies, have them join!
@LanceWeiler & I discuss @Columbia's Hacked Film Festival
Be sure to sign up for Thursday's Space with @Jason_Healey and @LanceWeiler. If you've been curious about @ColumbiaDEFRAG, you won't want to miss this! x.com/i/spaces/1mnGednbNgrKX
Thinking on defending forward and persistent engagement has advanced since my "memo to POTUS" of May 2018. Still pretty much stand by my assessment & recommendations for the NSC
www.thecipherbrief.com/column_article/memo-potus-respondi…
Sorry to hear @BobKolasky is leaving NRMC ... but excited to see what his experience and insight will bring to the risk-management industry!
Jay Healey reposted
This weekend, the Strauss Center and @AtlanticCouncil’s @CyberStatecraft are excited to kick off another @UTAustin edition of the renowned cybersecurity policy competition: #cyber912! To find more details about this event: www.strausscenter.org/events/cyber-9-12-strategy-challenge/
BTW, the "mayo that goes on every sandwich" is something I tell students, that cyber goes with most every topic
Regardless of their interest or their strengths before they got to @ColumbiaSIPA, there is a cyber angle to it
Their job is to (1) take what they know and who they are, (2) learn enough about the Internet, tech, & cyber, to (3) pivot to who they want to be and what they want to do
Our job -- all of ours -- is to help them, not gatekeep
The @SIWPSColumbia has been assembling tributes to our late, beloved colleague Bob Jervis. You can find them here:
www.siwps.org/programs/in-memoriam-robert-jervis/
Hope @FSISAC, ARC watching Ukraine
Putin couldn't use cyber to disrupt Western finance b/c of RU dependence
That restraint weakens if US sanctions cut RU off from SWIFT & the international dollar economy
If RU can't play the game, little to lose from just flipping the table
Michelle Cantos (now @FireEye) and I explored four Russian options for Ukraine in 2015 for @ccdcoe
ccdcoe.org/uploads/2018/10/Ch17_CyberWarinPerspective_Hea…
Theories on cyber dynamics - esp escalation - MUST incorporate how leaders & practitioners actually think & respond
Some leaders (Nakasone) less aggressive than others: then-deputy commander USCYBER: "we cannot .. cede any territory to these adversaries"
www.youtube.com/watch?v=DFHU7B0FoUA&t=1843s
If the next USCYBER commander is more like Stewart than Nakasone, expect a lot more action and less concern about nuances of PE & DF
(and a lot more references to Curtis LeMay, at least from me)
@DAlperovitch & others expect another Russian invasion of Ukraine w/in weeks
Russia is already
(1) beginning cyber ops & positioning for worse,
(2) suggesting it will reduce ransomware attacks on US in exchange for free hand in Russia
Some academics argue cyber isn't useful for coercion & not strategically relevant
Others (me included) argue that will change when states are really serious over the stakes, as Russia is over Ukraine
Unfortunately, we're likely to settle this soon
If Putin busted REvil to get a free hand in Ukraine from Biden, seems he believes in natsec value in conducting (& withholding) disruptive cyber ops
This instance, he'll likely be wrong at least w/the US. Would he be w/EU or smaller prize than Ukraine?
Jay Healey reposted
Jervis spent his life studying individual character and his, a colleague and former student recalls, was "sublime: gifted, generous, and joyful." warontherocks.com/2022/01/robert-jervis-a-remembrance/
Anyone in twitterland used to work at NORAD, especially in cyber defense?
There's seeming consensus states can't brandish cyber capabilities. Once you reveal your capability, it becomes powerless
But (1) if your adversary can do it once, decisionmakers will reasonably fear they can do it again
And (2) in IRL brandishing power decreases gradually
Capability built on log4j would have limited (but still non-zero) brandishing power:
Patched quickly, during a period of geopolitical stress, & was still just a vulnerability and not a campaign
Brandishing based on SolarWinds, say rebooting all computers of all 18k affected orgs at a specific time, might be powerful & long-lasting
Access was exceptionally deep & broad. Even after remediation, USG couldn't be sure they can't be open to a repeat
Does offense have the advantage over defense in cyberspace?
We talk past each other as the question is actually "under what conditions?" one may have the advantage
New piece @lawfareblog describes 5 different perspectives for cyber o-d comparisons
www.lawfareblog.com/understanding-offenses-systemwide-adv…
Five different levels to analyze cyber offense & defense advantage.
When you take a stand on whether O has the advantage, or D does, or that it can't be measured or is meaningless ... be specific about which you mean...
Asset framework is the original way to compare offense & defense, the root of the Ware Report of 1970 and NSA's Rainbow Series of manuals for Trusted Computing
Still around today in appsec and security testing
Dyadic actor framework compares a specific actor against a specific defender. I associate this w/ @rebeccamslayton's research
Examples:
Sandworm vs a control center of the Ukrainian grid
Herb Lin versus a cat
www.latimes.com/opinion/story/2021-11-07/op-ed-what-a-hou…
@HerbLinCyber -- sorry, forgot to tag you on this one...
Edited out of the original paper was an important point that @jfslowik picked up on:
Dyadic-actor framework is not just a specific attacker against a specific defender
Also includes whatever outside support either is able to bring to bear alongside their organic capabilities
Systemwide cyber offense-defense balance might be measurable (or least magnitude, direction of balance & trend might be estimated):
1) scale achievable in one-to-multitude attacks
2) surplus profits of cybercrime
3) relative difficulty of hiding versus detection and ejection
Oops, forgot
4) Relative difficulty of patching compared to exploiting
Thanks to many for helping me think about offense-defense!
@jonrlindsay @rebeccamslayton @HostileSpectrum for thoughtfully reviewing drafts
Steve Biddle for advice on ODT & framing my argument
@jfslowik @drbvaler who I knew would savage this if it wasn't good or balanced enough
Not saying any of those fine folks will actually AGREE with the final product, but still...
Whether YOU agree or disagree, check out the links to read their contributions!
Complexity depends on a lot of factors we haven't gotten nuanced about
As log4j shows, defenders have a lot to deal with
Attackers needn't worry about complexity as much if they don't care much who they target or how precisely, when they have their effect, or remaining secret
If attackers care deeply about who they target, when, for what effect, and for how long then complexity is a major issue, especially against a well-defended target
This ties in I think with @LenMaschmeyer's trilemma:
direct.mit.edu/isec/article/46/2/51/107693/The-Subversive…
In case you missed the new paper on cyber offense-defense that Santa brought down the @lawfare chimney...
Does offense have the advantage over defense in cyberspace?
We talk past each other as the question is actually "under what conditions?" one may have the advantage
New piece @lawfareblog describes 5 different perspectives for cyber o-d comparisons
www.lawfareblog.com/understanding-offenses-systemwide-adv…
GEN Alexander: Fort Meade is the center of cybersecurity excellence. Let us defend you!
CEO Alexander: Public & private must work together. Collective defense!
Even JPMorgan is highlighting the need for #collectivedefense.
"The public and private sectors must work together to fortify our business and government activities against this threat." www.cnn.com/2021/12/16/business/cyber-security-hacking-jp…
Jay Healey reposted
It's happening!!! Registration for our tenth annual #cyber912 is open. Check out the link below to register your team or lend your expertise as a judge.
Registration for the 2022 DC Cyber 9/12 Strategy Challenge on March 25-26 is open! While you're enjoying time with family and loved ones over the holidays, take a second to think about building your #cyber912 dream team.
More here:
www.atlanticcouncil.org/cyber912
Internet should always be capitalized. It is a single innovation we take for granted.
Before the Internet, there were thousands of smaller internets. The Internet connected all of them.
Jay Healey reposted
The deadline for the 2022-2023 @ObamaFoundation Scholars Program is approaching! Submit your application by December 22 at 5pm ET. worldprojects.columbia.edu/application-information
For USG, this is really encouraging!
@DawnCappelli says their IT team "are looking at our application inventory, looking at the GitHub site @CISAgov put together"
Also "we have SBOMs, that's been a big issue since [EO 14028] came out — that a lot of companies don't have them"
A week ago, news of the #log4j reverberated throughout the security community. Where do #cisos even begin? We asked @DawnCappelli CISO from @ROKAutomation and member of SC Media sister organization, Cybersecurity Collaborative, to share her experiences.
www.scmagazine.com/analysis/leadership/a-cisos-timeline-p…
Twice in one article, a call-out by a major CISO to the important role of government, both for operational risk reduction by @CISAgov and @WHNSC cyber policy!
I'm not a natural academic. I got to Columbia SIPA not quite knowing what was involved in being a "scholar." I could have no better role model than Bob whose curiosity and brilliance was only outshone by his kindness.
We're sorry to share the news that our longtime faculty member Robert Jervis, the Adlai E. Stevenson Professor of International Politics, died yesterday (December 9) after a battle with lung cancer. We will share more information in coming days.
It is my greatest professional pride that he not only valued my thoughts and saw me as a colleague but that we published several pieces together.
My great shame is that I didn't rush our final paper together, the culmination of four years researching the dynamics of cyber conflict. As recently as last week, I thought we'd have more time together.
A former student just wrote this wonderful sentence: “We will all feel his loss, and as a former RA, I can also say we’ll miss his supreme ability to discern if there were cookies anywhere in the International Affairs Building.”
Jay Healey reposted
We're sorry to share the news that our longtime faculty member Robert Jervis, the Adlai E. Stevenson Professor of International Politics, died yesterday (December 9) after a battle with lung cancer. We will share more information in coming days.
Bob Jervis' wife has allowed us to share this wonderful summary of his life which affected so many of us. This has so much of his whimsy in it, I imagine him helping to shape it
Though he could be a devoted dinosaur, using a dictophone & sometimes a typewriter, Bob Jervis grasped the relevance of technology - especially cyber - to the study of international relations
He dove in to see how it was an extension of, or demanded modifications to, his ideas
So overdue.
Better yet, explain why USCYBER conducted this as a Title 50 military mission against civilian criminals, rather than the FBI ...
U.S. Military Has Acted Against Ransomware Groups, General Acknowledges www.nytimes.com/2021/12/05/us/politics/us-military-ransom…
Advantages of USCYBER are obvious: capability, maybe deterrence v. Russia
But real dangers too: Mission creep over time lowers the bar for military counterattack, distracts USCYBER from missions only it can do
And it can suck away resources and attention from other agencies and other ways to defend...
"Escalation" is not a real danger here
USG cannot allow disruptions on pipelines and hospitals, then fret about escalatory risk if it disrupts the attackers
US disruptions would have to be especially savage, or US-Russia war very near, to be a concern
Fascinating to read about the nuclear anti-air defense for New York City, including on Rockaway Beach (which still has the bunkers)
If you saw the short piece on #cyber912 by @markyarm in the @NewYorker and want to learn more ...
Check out this article @ColumbiaSIPA, written by the two students who organized the event for 120+ students & developed the compelling cyber-space scenario!
www.sipa.columbia.edu/news/taking-cyber-stars
Thanks @markyarm for covering our #cyber912 Strategy Challenge here @ColumbiaSIPA in @NewYorker!!!
@SIPA_DCG students developed a mean but accurate space-cyber scenario and held a great competition for 30+ university teams, w/ @CyberStatecraft
www.newyorker.com/magazine/2021/11/29/the-general-of-the-…
Thanks @Mandiant for the great conversation on cyber conflict and systemic cyber risk!
We are serving up a fresh episode of Eye on Security! Hear from @Jason_Healey at @ColumbiaSIPA on how #cyber policy has evolved over the years.
🎧: mndt.info/3ln2qZV
This panel starting shortly!
STOP SAYING there are no agreed-to cyber norms!
Join @techpolicySIPA Wednesday, 1 December, at noon Eastern, for a panel to discuss the incredible progress
"2021: Year of the Cyber Norms" w/ Michele Markoff @State_Cyber, @JanNeutze, @caminokav
columbiauniversity.zoom.us/webinar/register/WN_092SD-khRd…
STOP SAYING there are no agreed-to cyber norms!
Join @techpolicySIPA Wednesday, 1 December, at noon Eastern, for a panel to discuss the incredible progress
"2021: Year of the Cyber Norms" w/ Michele Markoff @State_Cyber, @JanNeutze, @caminokav
columbiauniversity.zoom.us/webinar/register/WN_092SD-khRd…
Just as important, we'll dive into what states and non-states must do to ENFORCE all these great new-ish norms!
Jay Healey reposted
Wondering how to pass the time this Thanksgiving? Might we recommend watching Blackhat (2015)?
Totally unrelated, join @ColumbiaDEFRAG on November 30 at 7pm, as we discuss 'Blackhat' - the movie that hackers love to hate!
columbiauniversity.zoom.us/webinar/register/WN_lszDBUECT3…
Come join @MattDevost @MeganStifel tomorrow night to talk Blackhat (and other hackers films)!
Put some camp in your Thanksgiving. Watch Blackhat with your family then sign up for our event Tuesday, Nov 30, 7pm Eastern where we'll be talking with @MattDevost about his experiences advising the filmmakers. Should be fun! columbiauniversity.zoom.us/webinar/register/WN_lszDBUECT3…
Unsophisticated, mass-targeted attacks are common, just not often by states for geopolitical purposes
In great-power competition, expect them to be more likely, more dangerous, & more likely to be coercive as states spend more energy and take more risk to coerce one another
Thanks so much to @argvee for covering so many amazing cybersecurity topics with our students from @ColumbiaSIPA @ColumbiaCompSci @ColumbiaLaw!
"Cybersecurity: Tech, Policy, & Law," that I teach w/ Evan Wolff @Crowell_Moring brings together students from across campus
This year students are learning about four of the "great hacks" -- Sony, NotPetya, SolarWinds, and Colonial -- and proposing recommendations
And thanks to Heather I learned about the amazing Hilda Faust, a pioneering woman in cybersecurity and exploitation
Check out her induction into the @NSAGov hall of fame...
www.marywood.edu/connect/class-notes/Hilda/Mathieu/NSAHonors
Jay Healey reposted
Thanks for letting us support your great work.
Hats off to @kairozukigou for adding her experience and perspective to create an outstanding scenario!
And thanks to our sponsors for making the competition possible!
@BlueVoyant
@NYCCyberCommand
NextPeak (@GregRattray_)
@redballoonsec (esp @angcui)
@BlackHatUSA
@SecureAerospace (esp @cyberpilot22)
Thanks @markyarm for covering our #cyber912 Strategy Challenge here @ColumbiaSIPA in @NewYorker!!!
@SIPA_DCG students developed a mean but accurate space-cyber scenario and held a great competition for 30+ university teams, w/ @CyberStatecraft
www.newyorker.com/magazine/2021/11/29/the-general-of-the-…
And thanks to our sponsors for making the competition possible!
@BlueVoyant
@NYCCyberCommand
NextPeak (@GregRattray_)
@redballoonsec (esp @angcui)
@BlackHatUSA
@SecureAerospace (esp @cyberpilot22)
Okay, so I LOVE ska covers. The cover of Bad Guy by @Interruptweets is pretty awesome...
www.youtube.com/watch?v=gmRy-JW5aps
I'd put it up there with @PartyLikeItsSKA version of Timber which I've seen live many times
www.youtube.com/watch?v=fIrMR1oEuIM
Thanks @HerbLinCyber for writing this great book!
So glad it didn't cover just NC3 but the whole nuke enterprise. And of course all written with your typical clarity...
Beautiful cloudy view above Manhattan and @Columbia
Thrilled that the amazing @camillefrancois will be teaching students @ColumbiaSIPA on tracking disinformation campaigns on social media.
Learn more about her and her course in this great article: www.sipa.columbia.edu/news/an-optimist-mind
.@DHSgov hiring fairs coming up, including for @CISAgov and cyber jobs!
June 2, 4-6 pm ET: Professionals, Students, & Recent Grads
June 15, 4-6 pm: Veterans
June 29, 2-4 pm: Individuals w/ Disabilities
September 14, 6-8 pm: Students & Recent Grads
www.dhs.gov/homeland-security-careers/hiring-event
How's your week going? Mine? Thanks for asking...
I published two separate articles with Bob Jervis!
Overclassification and its Impact on Cyber Conflict and Democracy: mwi.usma.edu/overclassification-and-its-impact-on-cyber-c…
How to reverse three decades of escalating cyber conflict: www.atlanticcouncil.org/blogs/new-atlanticist/how-to-reve…
Look at what I've kept around for 15 years...
Time to review (and maybe repurpose one of my cyber classes...)
Rather, the news of the NSA disclosure highlights *continuity * -- that despite the hawkishness of US on cyber and secrecy of the new PPD-20, the Trump administration of 2020 is still following its stated priority of 2017
Great short video of the New York #cyber912 here at @ColumbiaSIPA, featuring CJ Dixon @SIPA_DCG ... Thanks to @AtlanticCouncil @TomBossert, other speakers and sponsors!
Absolutely right: @RGB_Lights worried about significant risk of miscalculation of states trending from exploitation to disruption. Calls out Triton specifically...
Surprised & disappointed NSA kept Cisco 0days in arsenal for years. Seems to go against nearly every WH criteria www.whitehouse.gov/blog/2014/04/28/heartbleed-understandi…
On public panel discussion tomorrow, bringing @defcon to DC w/ @beauwoods @spacerog @lorrietweet @AtlanticCouncil goo.gl/dFPsy3
Sad. 'Non-kinetic effects' rather than desperate need for defense dominates cyber section of new Air Force strategy, goo.gl/i2HVSD
So we've been saying "electronic Pearl Harbor" for 20+ of 70+ years since the *real* Pearl Harbor - we clearly don't understand cyber power
In Ukraine, Russia playing a game US forgot a decade ago, info ops. US switched to sexier CYBER, goo.gl/QoPe6t @AtlanticCouncil
We overlook soft power in cyber. Estonia won 2007 b/c seen as charismatic victim of aggression. US bleeding soft power from NSA revelations