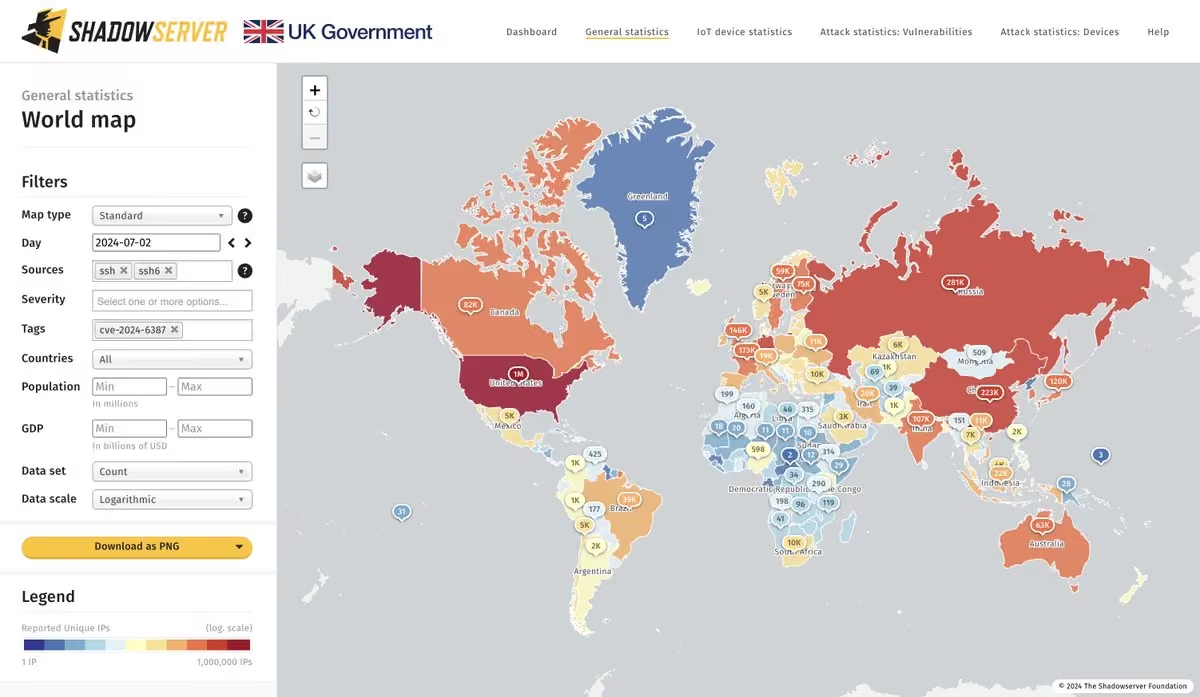
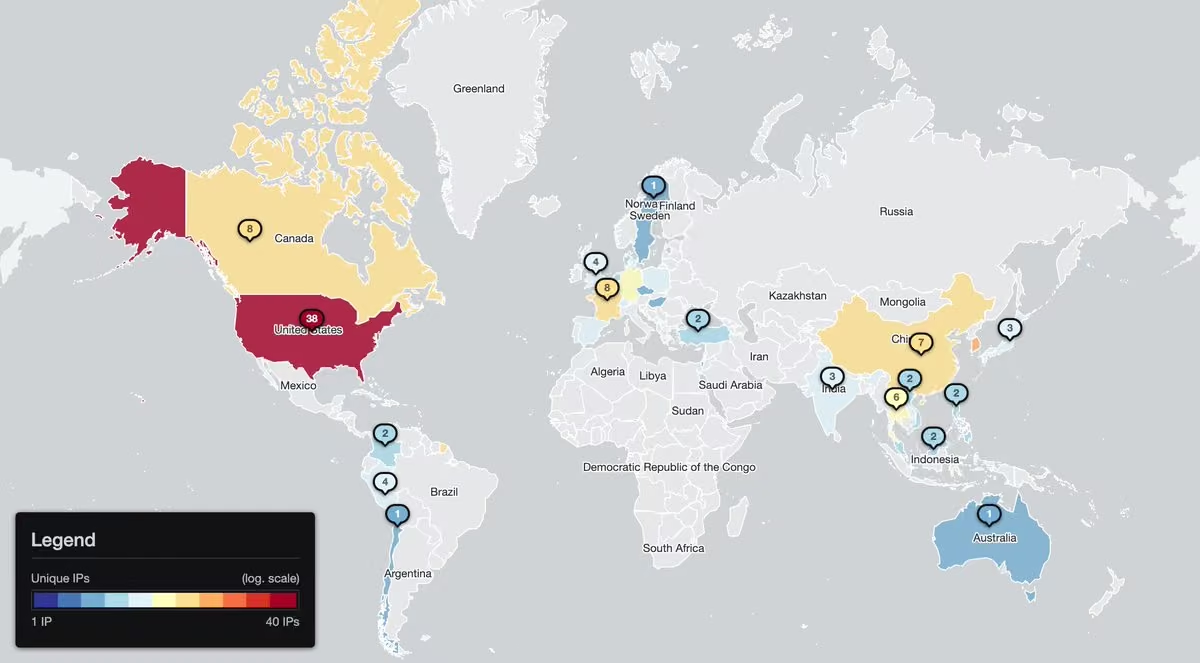
We have added ARTEX, CyberStrike, PentestCode, VXControl & other agentic AI attack frameworks to our daily device fingerprinting and reporting. Currently over 3800 unique IPs seen daily. IP data shared in www.shadowserver.org/what-we-do/network-reporting/device-…
Dashboard Map view: dashboard.shadowserver.org/statistics/iot-devices/map/?da…
Shadowserver Foundation
Shadowserver Foundation is a nonprofit security organization that gathers and analyzes data on malicious Internet activity (including malware, botnets, and computer fraud), sends daily network reports to subscribers, and works with law enforcement organizations around the world in cybercrime investigations. Established in 2004 as a "volunteer watchdog group," it liaises with national governments, CSIRTs, network providers, academic institutions, financial institutions, Fortune 500 companies, and end users to improve Internet security, enhance product capability, advance research, and dismantle criminal infrastructure. Shadowserver provides its data at no cost to national CSIRTs (by geo code) and network owners (according to their network space). More on Wikipedia
-
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver

-
The Shadowserver Foundation
@Shadowserver
We have added ARTEX, CyberStrike, PentestCode, VXControl & other agentic AI attack frameworks to our daily device fingerprinting and reporting. Currently over 3800 unique IPs seen daily. IP data shared in www.shadowserver.org/what-we-do/network-reporting/device-…
Dashboard Map view: dashboard.shadowserver.org/statistics/iot-devices/map/?da…
The Shadowserver Foundation
@Shadowserver
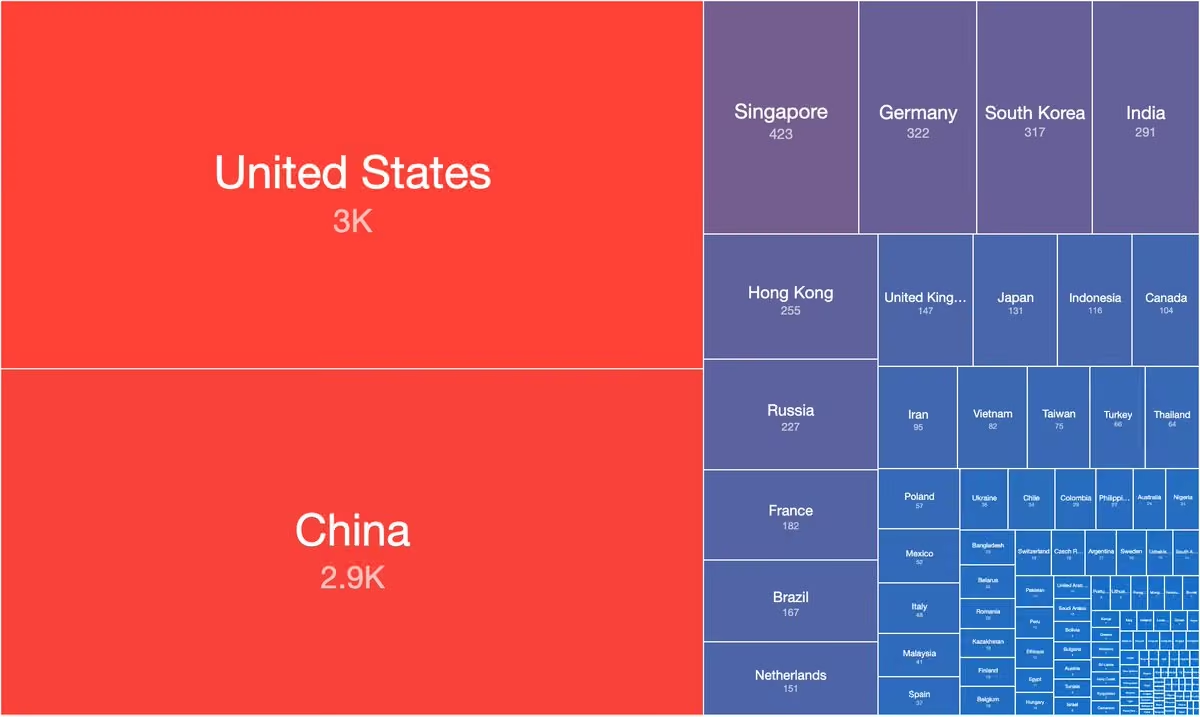
Tree Map view:
dashboard.shadowserver.org/statistics/iot-devices/tree/?d…
Trends over time, broken down by framework:
dashboard.shadowserver.org/statistics/iot-devices/time-se…
If you get an alert about infrastructure you are not expecting in your network/constituency make sure to investigate. Events shared with severity set to "high"
The Shadowserver Foundation
@Shadowserver
-
The Shadowserver Foundation
@Shadowserver
Happy to continue to support our international partners in "Season 4" of Operation Endgame, this time successfully targeting the Gootloader, CastleRAT, and StealC cybercrime-as-a-service families
www.europol.europa.eu/media-press/newsroom/news/64-millio…
www.justice.gov/opa/pr/gootloader-malware-disrupted-inter…Post not available here, view on X
The Shadowserver Foundation
@Shadowserver
New Season 4.0 Episode 1 GootLoader “Thumbs Up?” video added to the Operation Endgame website:
www.operation-endgame.com/videos/S04E01_THUMBSUP.mp4
www.operation-endgame.com
The Shadowserver Foundation
@Shadowserver
Additional international LE partner announcements:
www.politie.nl/nieuws/2026/november/12/11-internationale-…
www.linkedin.com/posts/fbicyberbranch_today-as-part-of-op…
x.com/fbicyberbranch/status/2120972344491454941
www.bka.de/DE/Presse/Listenseite_Pressemitteilungen/2026/…
politi.dk/national-enhed-for-saerlig-kriminalitet/nyhedsl…
FBI Cyber Branch
@FBICyberBranch
Today, as part of Operation Endgame, the FBI and our partners announced the disruption of the malware and botnet known as Gootloader. Since 2018, Gootloader malware infected more than 25,000 computers worldwide and was used in ransomware attacks against at least 44 U.S.-based victims, resulting in millions of dollars in losses.
As part of the coordinated international operation, @FBIDenver and partners removed the Gootloader malware from over 100 computer servers and seized the U.S. domain names used by criminals to deliver and control the malware. Private-sector partner The Shadowserver Foundation assisted with identifying infections, victim notification, and remediation.
www.justice.gov/opa/pr/gootloader-malware-disrupted-inter… -
The Shadowserver Foundation
@Shadowserver
We’re honored to be appointed as an Implementing Agent for NATO’s Defence Capacity Building Initiative to help partners strengthen cybersecurity capabilities!
Read more: www.shadowserver.org/news/shadowserver-selected-to-natos-… -
The Shadowserver Foundation
@Shadowserver
Refrigeration incidents: We still track around 170 Danfoss AK-SM8xxA Series CVE-2025-41452/CVE-2025-41451 vulnerable instances & 136 CVE-2025-41450 in our Vulnerable HTTP reporting: www.shadowserver.org/what-we-do/network-reporting/vulnera…
World Map view: dashboard.shadowserver.org/statistics/combined/map/?date_…
The Shadowserver Foundation
@Shadowserver
If you receive alerts from us (and not running a honeypot) make sure to take your systems off the public Internet!
nvd.nist.gov/vuln/detail/cve-2025-41450
nvd.nist.gov/vuln/detail/cve-2025-41451
nvd.nist.gov/vuln/detail/cve-2025-41452 -
The Shadowserver Foundation
@Shadowserver
We are also sharing vulnerable Ahsay AhsayCBS CVE-2026-105134 instances. We are aware of the vulnerability being used in ransomware attacks - so despite only 22 currently remaining vulnerable - if you receive an alert from us please investigate, filter traffic and update!
The Shadowserver Foundation
@Shadowserver
IP data in our Vulnerable HTTP reporting: www.shadowserver.org/what-we-do/network-reporting/vulnera…
We would like to thank @ValidinLLC for the collaboration in our scanning.
Tree map view: dashboard.shadowserver.org/statistics/combined/tree/?date…
World map view: dashboard.shadowserver.org/statistics/combined/map/?date_…
Patch: www.ahsay.com/en/company/announcements/patch-cve-105133-1… -
The Shadowserver Foundation
@Shadowserver
Shadowserver is honored to be a 2026 @SANSInstitute Difference Makers Awards finalist! If you appreciate our work, please support us with your vote! go.sans.org/Nb9PSd
-
The Shadowserver Foundation
@Shadowserver
We are currently tracking over 1000 GitLab instances vulnerable to CVE-2026-97229 (on @CISACyber KEV) and over 11300 instances vulnerable to CVE-2026-110264 (out of around 39K GitLab instances we see daily).
Tree Map Dashboard stats (both vulns) dashboard.shadowserver.org/statistics/combined/tree/?date…
The Shadowserver Foundation
@Shadowserver
IP data in our Vulnerable HTTP reporting tagged 'cve-2026-97229' or 'cve-2026-110264': www.shadowserver.org/what-we-do/network-reporting/vulnera…
World Map view: dashboard.shadowserver.org/statistics/combined/map/?date_…
Tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
Patch info:
docs.gitlab.com/releases/patches/patch-release-gitlab-19-… -
The Shadowserver Foundation
@Shadowserver
PHP Attacks Update: As others, we have been observing a lot of AI slop PHP attempts against our honeypot sensors the last week, but so far no confirmed exploitation.
We have refrained from CVE-2026-109618/619 tagging in scans, due to lack of reliable, safe large scale methods.
The Shadowserver Foundation
@Shadowserver
Instead we have opted for reporting out End of Life instances, which is hopefully the more actionable approach at this stage. We added 'eol-php' to the Vulnerable HTTP reporting. Tagging is based on: endoflife.date/php (anything older than 8.2)
The Shadowserver Foundation
@Shadowserver
You can track unique IPs (not hostnames) running EOL PHP at dashboard.shadowserver.org/statistics/combined/tree/?date…
Make sure to update those systems! -
The Shadowserver Foundation
@Shadowserver
Copeland/Dixwell XWEB refrigeration web controller incidents: As in the case of Danfoss, for a long time we have been sharing exposed Copeland XWEB Pro & Evo panels in Device ID reporting. We see around 1200 instances daily - these should of course not be publicly accessible.
The Shadowserver Foundation
@Shadowserver
Data shared in shadowserver.org/what-we-do/network-reporting/device-iden…
World Map view:
dashboard.shadowserver.org/statistics/iot-devices/map/?da…
Tree Map view:
dashboard.shadowserver.org/statistics/iot-devices/tree/?d…
Exposure tracker: dashboard.shadowserver.org/statistics/iot-devices/time-se…
See also @CERT_FR cert.cyber.gouv.fr/alerte/CERTFR-2026-ALE-012/
Additional info: claroty.com/team82/research/chilling-discoveries-unpackin… -
The Shadowserver Foundation
@Shadowserver
Danfoss refrigeration incidents: We are sharing exposed instances for a long time in our Device ID reporting, daily. For Danfoss AK-SM800A we still see at least 365 unique instances daily (drop from over 550 last few days) exposed. These need to be taken off the public Internet!
The Shadowserver Foundation
@Shadowserver
Data shared in www.shadowserver.org/what-we-do/network-reporting/device-…
World Map view: dashboard.shadowserver.org/statistics/iot-devices/map/?da…
Tree map view: dashboard.shadowserver.org/statistics/iot-devices/tree/?d…
Exposure tracker:
dashboard.shadowserver.org/statistics/iot-devices/time-se…
Background: claroty.com/team82/research/freeze-the-controller-defrost…
We are working on possible CVE tagging too -
The Shadowserver Foundation
@Shadowserver
We have started reporting out (daily) MikroTik instances with exposed proprietary services, such as WinBox & Bandwidth Test server (btest): www.shadowserver.org/what-we-do/network-reporting/accessi…
Around 2.6M exposed instances shared daily. Top: Brazil, Indonesia, USA.
Tree map stats: dashboard.shadowserver.org/statistics/combined/tree/?date…
The Shadowserver Foundation
@Shadowserver
These should not be publicly accessible on the Internet due to potential vulnerabilities, such as the recent CVE-2026-67277 nvd.nist.gov/vuln/detail/cve-2026-67277
You can find all our MikroTik detections in Device ID report www.shadowserver.org/what-we-do/network-reporting/device-… (around 3M daily): dashboard.shadowserver.org/statistics/iot-devices/time-se…
The Shadowserver Foundation
@Shadowserver
For MikroTik with SSH enabled, check out our Accessible SSH reporting (www.shadowserver.org/what-we-do/network-reporting/accessi…), with the tag 'mikrotik' dashboard.shadowserver.org/statistics/combined/time-serie… - just over 119K seen daily currently
Background: cert.pl/en/posts/2026/09/vulnerabilities-in-mikrotik-rout… -
The Shadowserver Foundation
@Shadowserver
Still 218 instances of N-able N-central seen unpatched to CVE-2026-86218 pre-auth RCE that is exploited in the wild & on @CISACyber KEV. Top: US (141)
Stats - World Map view: dashboard.shadowserver.org/statistics/combined/map/?date_…
Tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
IP data in Vulnerable HTTP reporting tagged 'cve-2026-86218': www.shadowserver.org/what-we-do/network-reporting/vulnera…
218 out of 1399 seen in total. This is one week after exploitation activity was first reported publicly.
Patch info: documentation.n-able.com/N-central/Release_Notes/GA/Conte…
Background on incidents: www.huntress.com/blog/n-able-vulnerability-exploitation -
The Shadowserver Foundation
@Shadowserver
We shared a one-off share of over 400 compromised PaperCut NG/MF instances (via CVE-2026-81578/CVE-2026-82078) observed by @GreyNoiseIO. IP data in our Compromised Website reporting for 2026-09-11, tagged 'papercut-compromise'.
Dashboard Tree Map stats: dashboard.shadowserver.org/statistics/combined/tree/?date…
The Shadowserver Foundation
@Shadowserver
Compromised Website Report: www.shadowserver.org/what-we-do/network-reporting/comprom…
Thank you to @GreyNoiseIO for the share! Background with info about the AI-orchestrated campaign behind the compromises (includes IOCs): www.greynoise.io/blog/ai-orchestrated-campaign-against-pa… -
The Shadowserver Foundation
@Shadowserver
Since 2026-09-04 we are scanning/reporting daily unpatched versions of Plex Media Server in response to an advisory issued by Plex forums.plex.tv/t/important-security-update-for-plex-media… for v1.43.2 & earlier. Over 36K instances found still unpatched! Top affected: US (16K)
World Map: dashboard.shadowserver.org/statistics/combined/map/?date_…
The Shadowserver Foundation
@Shadowserver
No CVEs have been issued meaning the vulnerabilities are essentially invisible to the security community limiting an effective response.
We tag the raw IP data shared 'vulnerable-plex' in Vulnerable HTTP reporting: www.shadowserver.org/what-we-do/network-reporting/vulnera…
Tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
Running an outdated Plex Media Server? Patch!
Dashboard Tree Map view: dashboard.shadowserver.org/statistics/combined/tree/?date… -
The Shadowserver Foundation
@Shadowserver
We added MikroTik SSH identification to our daily scans on 2026-09-04, in response to MikroTik's patches mikrotik.com/supportsec/september-2026-vulnerability. As discovered by @CERT_Polska_en cert.pl/en/posts/2026/09/vulnerabilities-in-mikrotik-rout… unpatched MikroTiks can be compromised, if device supports remote access using SSH protocol
The Shadowserver Foundation
@Shadowserver
At least 122,500 MikroTik devices with SSH accessible found per 24 hour scan window on 2026-09-05 (no vulnerability check).
IP data shared daily in Accessible SSH reporting www.shadowserver.org/what-we-do/network-reporting/accessi… tagged 'mikrotik' & Device Identification reports: www.shadowserver.org/what-we-do/network-reporting/device-…
The Shadowserver Foundation
@Shadowserver
Exploitation is reported in the wild.
Review for compromise and patch! -
The Shadowserver Foundation
@Shadowserver
PaperCut MF/NG incidents: At least 204 instances found on 2026-08-31 still vulnerable to CVE-2026-82078/CVE-2026-81578 RCE that is exploited in the wild. Make sure to check for compromise & patch. Top affected: US (60).
Dashboard World Map view stats: dashboard.shadowserver.org/statistics/combined/map/?date_…
The Shadowserver Foundation
@Shadowserver
Daily IP data now in our Vulnerable HTTP reporting, tagged 'cve-2026-82078' & 'cve-2026-81578': www.shadowserver.org/what-we-do/network-reporting/vulnera…
Tree map view: dashboard.shadowserver.org/statistics/combined/tree/?date…
NVD entry:
nvd.nist.gov/vuln/detail/cve-2026-82078
nvd.nist.gov/vuln/detail/cve-2026-81578
Patch info: www.papercut.com/kb/Main/security-bulletin-27-aug-2026-ur…
The Shadowserver Foundation
@Shadowserver
Make sure to install Emergency Patch (Release 3) - but assume compromise.
Background on PaperCut incidents: www.huntress.com/blog/papercut-actively-exploited
Detection based on Nuclei template by darses - github.com/projectdiscovery/nuclei-templates/pull/17025
#cybercivildefense -
Post not available here, view on X
The Shadowserver Foundation
@Shadowserver
Daily IP data now in our Vulnerable HTTP reporting, tagged 'cve-2026-82078' & 'cve-2026-81578': www.shadowserver.org/what-we-do/network-reporting/vulnera…
Tree map view: dashboard.shadowserver.org/statistics/combined/tree/?date…
NVD entry:
nvd.nist.gov/vuln/detail/cve-2026-82078
nvd.nist.gov/vuln/detail/cve-2026-81578
Patch info: www.papercut.com/kb/Main/security-bulletin-27-aug-2026-ur…
The Shadowserver Foundation
@Shadowserver
Make sure to install Emergency Patch (Release 2) - but assume compromise.
Detection based on Nuclei template by darses - github.com/projectdiscovery/nuclei-templates/pull/17025
Background on PaperCut incidents: www.huntress.com/blog/papercut-actively-exploited -
The Shadowserver Foundation
@Shadowserver
We are scanning & reporting daily on vulnerable Microsoft Exchange CVE-2026-62911 (Authentication Bypass by Capture-replay) instances in our Vulnerable Exchange reporting: www.shadowserver.org/what-we-do/network-reporting/vulnera…
At least 21899 IPs seen unpatched 2026-08-31, top US (6.2K) & Germany (5.1K)
The Shadowserver Foundation
@Shadowserver
Dashboard World Map view stats: dashboard.shadowserver.org/statistics/combined/map/?date_…
Dashboard Tree Map stats: dashboard.shadowserver.org/statistics/combined/tree/?date…
NVD entry: nvd.nist.gov/vuln/detail/cve-2026-62911
MS advisory: msrc.microsoft.com/update-guide/vulnerability/CVE-2026-62911
Daily IP data tagged 'cve-2026-62911'
See also @ncsc_nl advisory: www.ncsc.nl/alerts/ernstige-kwetsbaarheden-in-microsoft-e… -
The Shadowserver Foundation
@Shadowserver
We are scanning/reporting Gitea instances vulnerable to CVE-2026-60004 (code injection), with 8393 IPs found vulnerable on 2026-08-27. This vulnerability is exploited in the wild and on @CISACyber KEV. Top affected: China, Germany, US
Dashboard view:
dashboard.shadowserver.org/statistics/combined/map/?date_…
The Shadowserver Foundation
@Shadowserver
IP data shared in our Vulnerable HTTP reporting tagged 'cve-2026-60004': www.shadowserver.org/what-we-do/network-reporting/vulnera…
Patch Tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
Exploit code is public.
Gitea advisory: blog.gitea.com/release-of-1.27.1/
NVD entry: nvd.nist.gov/vuln/detail/cve-2026-60004 -
The Shadowserver Foundation
@Shadowserver
Alert! Zimbra compromises associated with CVE-2026-73570 exploitation are spreading. 274 instances seen compromised in our scans for exploitation artifacts on 2026-08-22. Top: US (41 IPs). Detection in collaboration with @CERT_Polska_en
Public Dashboard: dashboard.shadowserver.org/statistics/combined/map/?date_…
The Shadowserver Foundation
@Shadowserver
Data in Compromised Website reporting tagged 'zimbra-compromised' with detail set to 'Artifact from probable CVE-2026-73570 compromise' www.shadowserver.org/what-we-do/network-reporting/comprom…
Compromised Zimbra tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
We also see at least 8200 CVE-2026-73570 unpatched instances (note this does not mean exploitable as the vuln is in a non default config) dashboard.shadowserver.org/statistics/combined/tree/?date…
Check for compromise & update: wiki.zimbra.com/wiki/Zimbra_Security_Advisories
CVE-2026-73570 is on @CISACyber KEV www.cisa.gov/known-exploited-vulnerabilities-catalog?fiel… -
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
Using ELK & interested in automating ingestion of our threat intel for your network/constituency via our API?
We have introduced an ECS logging script for our intelligence reports. This script uses Redis to queue events for Logstash.
Check it out at github.com/The-Shadowserver-Foundation/api_utils/tree/mai… -
The Shadowserver Foundation
@Shadowserver
RondoDox botnet now also trying to exploit the new GeoServer 0-day, as seen in our sensors. We see over 1500 exposed instances worldwide (exposed population, not a vulnerability check). Patch info: geoserver.org/announcements/vulnerability/2026/08/14/geos…
Tree Map Dashboard stats: dashboard.shadowserver.org/statistics/iot-devices/tree/?d…
The Shadowserver Foundation
@Shadowserver
IP data in our Device ID reporting (exposure, not vulnerability check): shadowserver.org/what-we-do/network-reporting/device-iden…
Public POC available and being used. Check for compromise and patch.
#cybercivildefense -
The Shadowserver Foundation
@Shadowserver
RondoDox botnet now also trying to exploit the new GeoServer 0-day, as seen in our sensors. We see over 1500 exposed instances worldwide (exposed population, not a vulnerability check). Patch info: geoserver.org/announcements/vulnerability/2026/08/14/geos…
Tree Map Dashboard stats: dashboard.shadowserver.org/statistics/iot-devices/tree/?d…
The Shadowserver Foundation
@Shadowserver
IP data in our Device ID reporting (exposure, not vulnerability check): www.shadowserver.org/what-we-do/network-reporting/device-…
Public POC available and being used.
Check for compromise and patch. -
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
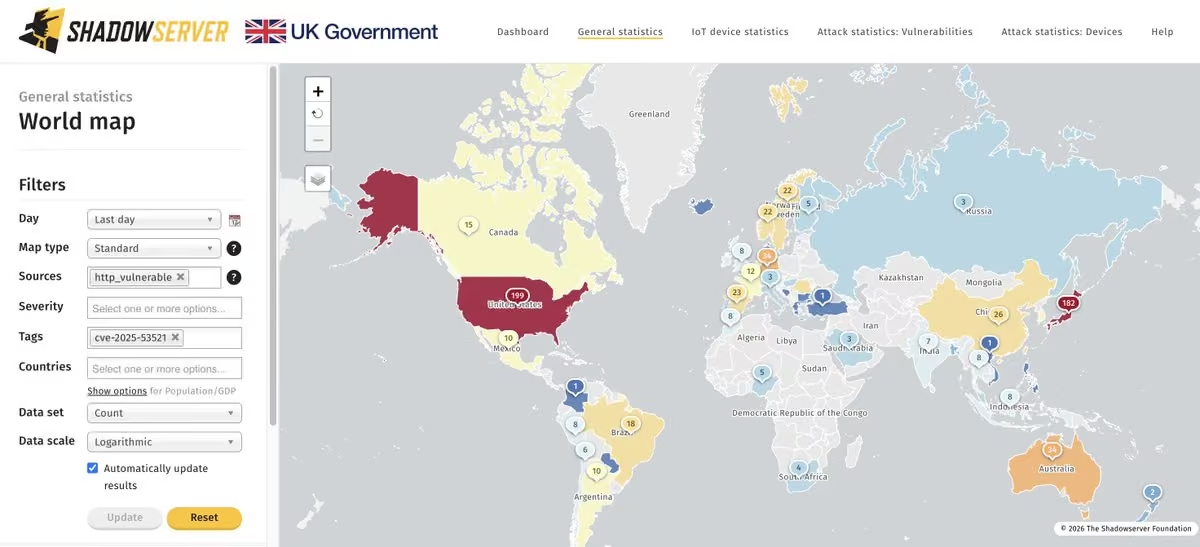
We are scanning & reporting F5 BIG-IP APM CVE-2025-53521 instances thanks to collaboration with the @ncsc_nl SRT. 10 months after vuln disclosure, we still see over 850 IPs vulnerable to potential RCE. Top affected: US with 199 & Japan 182. IP data in Vulnerable HTTP reporting.
-
The Shadowserver Foundation
@Shadowserver
We are also scanning & reporting Metabase IPs likely unpatched to CVE-2026-72898 SQLi, which is exploited in the wild & on @CISACyber KEV. 2171 unpatched (version check) instances seen 2026-08-15. Top US (603), Germany (278)
Dashboard World Map stats: dashboard.shadowserver.org/statistics/combined/map/?date_…
The Shadowserver Foundation
@Shadowserver
IP Data in our Vulnerable HTTP reporting tagged 'cve-2026-72898' : www.shadowserver.org/what-we-do/network-reporting/vulnera… (since 2026-08-11)
NVD entry: nvd.nist.gov/vuln/detail/CVE-2026-72898
Metabase advisory & patch info: github.com/metabase/metabase/security/advisories/GHSA-vwf… -
The Shadowserver Foundation
@Shadowserver
We are scanning & reporting F5 BIG-IP APM CVE-2025-53521 instances thanks to collaboration with the @ncsc_nl SRT. 10 months after vuln disclosure, we still see over 850 IPs vulnerable to potential RCE. Top affected: US with 199 & Japan 182. IP data in Vulnerable HTTP reporting.
The Shadowserver Foundation
@Shadowserver
This vulnerability is known to be exploited in the wild and on @CISACyber KEV www.cisa.gov/known-exploited-vulnerabilities-catalog?fiel…
@F5 Advisory: my.f5.com/manage/s/article/K000156741
Check your reports for IPs tagged 'cve-2025-53521'!
Public Dashboard World Map: dashboard.shadowserver.org/statistics/combined/map/?date_…
The Shadowserver Foundation
@Shadowserver
Vulnerable HTTP Report: www.shadowserver.org/what-we-do/network-reporting/vulnera…
-
The Shadowserver Foundation
@Shadowserver
You can also track CVE-2026-59310 & CVE-2026-59309 vulnerable VMware vCenter instances in our daily Vulnerable HTTP reporting since July 30th: www.shadowserver.org/what-we-do/network-reporting/vulnera…
Tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
World Map: dashboard.shadowserver.org/statistics/combined/tree/?date…
The Shadowserver Foundation
@Shadowserver
Thanks to collaboration with @quirso_de we are sharing the VMware vCenter CVE-2026-59310 Exploitation Victim Special Report www.shadowserver.org/what-we-do/network-reporting/vmware-…
Check compromised IPs for your network/constituency & remediate! File prefix: 2026-08-13-special
See: medium.com/@quirso_de/active-exploitation-of-cve-2026-593… -
The Shadowserver Foundation
@Shadowserver
Thanks to collaboration with @quirso_de we are sharing the VMware vCenter CVE-2026-59310 Exploitation Victim Special Report www.shadowserver.org/what-we-do/network-reporting/vmware-…
Check compromised IPs for your network/constituency & remediate! File prefix: 2026-08-13-special
See: medium.com/@quirso_de/active-exploitation-of-cve-2026-593…
The Shadowserver Foundation
@Shadowserver
The Shadowserver Foundation
@Shadowserver
Public Dashboard link: dashboard.shadowserver.org/statistics/combined/map/?date_… (choose source 'special' on 2026-08-13 for other visuals)
-
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
Excited to announce our Central and Eastern Europe (CEE) Critical Community Infrastructure (CCI) Project, focused on improving the #cybersecurity of essential public-serving organizations (made possible with support from @Googleorg)
Find out more:
www.shadowserver.org/news/shadowserver-critical-community… -
The Shadowserver Foundation
@Shadowserver
We shared a Dysphoria Botnet Special Report on 2026-08-12 with over 296,000 devices compromised globally: www.shadowserver.org/what-we-do/network-reporting/dysphor…
Check reports with the 2026-08-12-special prefix for your network or constituency.
Dashboard stats: dashboard.shadowserver.org/statistics/combined/map/?date_…
The Shadowserver Foundation
@Shadowserver
Dysphoria targets IoT devices and its primary function appears to be for use in DDoS-attacks. Recently the botnet has gotten residential proxy functionality.
More details on Dysphoria at blog.xlab.qianxin.com/dysphoria/ -
The Shadowserver Foundation
@Shadowserver
Excited to announce our Central and Eastern Europe (CEE) Critical Community Infrastructure (CCI) Project, focused on improving the #cybersecurity of essential public-serving organizations (made possible with support from @Googleorg)
Find out more:
www.shadowserver.org/news/shadowserver-critical-community… -
The Shadowserver Foundation
@Shadowserver
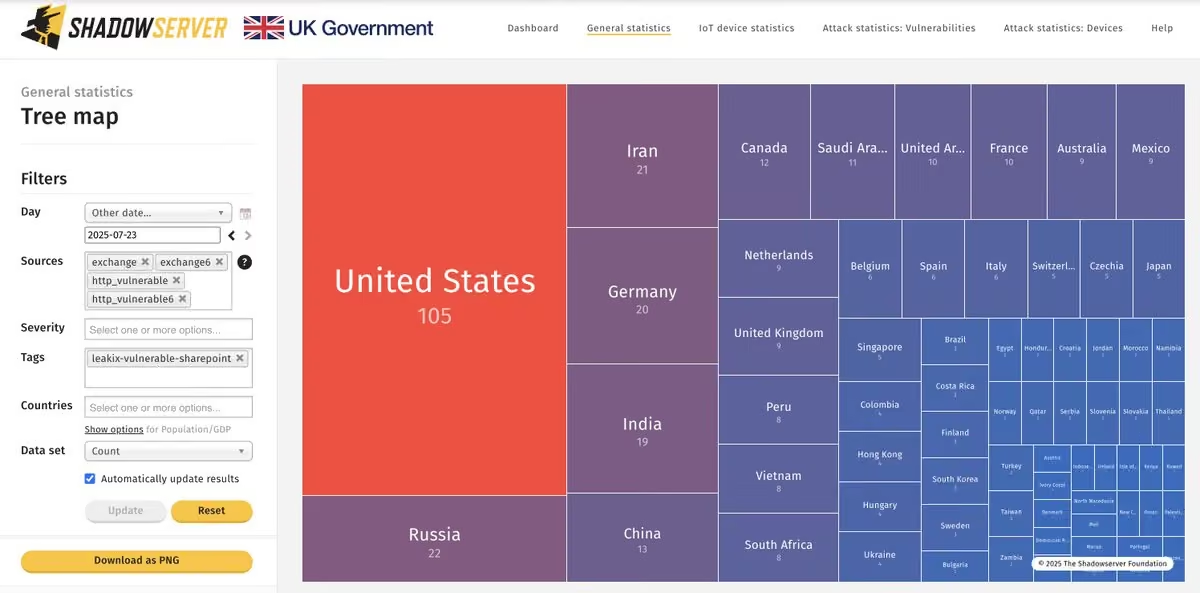
Still seeing substantial amounts of Microsoft SharePoint unpatched instances that have been added to @CISACyber Known Exploited Vulnerability catalog last few weeks. This includes CVE-2026-50522, CVE-2026-56164, CVE-2026-58644 with 878 IPs (1585 FQDNs) unpatched on 2026-07-23
The Shadowserver Foundation
@Shadowserver
Data for these is shared in our Vulnerable HTTP reporting with the appropriate CVE tags: www.shadowserver.org/what-we-do/network-reporting/vulnera…
Dashboard World Map: dashboard.shadowserver.org/statistics/combined/map/?date_…
Dashboard Tree Map: dashboard.shadowserver.org/statistics/combined/tree/?date…
Tracker: dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation
@Shadowserver
We’re excited to welcome Backblaze to the Shadowserver Alliance as a Bronze Tier Partner!
@backblaze is a premier, high-performance cloud storage platform. www.backblaze.com
With our Alliance Partners, we’ll make the Internet more secure & raise the bar on cybersecurity!
The Shadowserver Foundation
@Shadowserver
Join the Alliance and become part of the community: www.shadowserver.org/partner/
-
The Shadowserver Foundation
@Shadowserver
Great to partner with @cybersafehq in supporting #cybergirls in Kenya, and be able to assist them in gaining real-world #cybersecurity experience.
Cybersafe Foundation
@cybersafehq
Cybersecurity talent needs room to practise.
Through this partnership, CyberSafe Foundation and The Shadowserver Foundation are helping five members of our CyberGirls Alumni community in Kenya move closer to real-world cyber experience.
Thank you, @Shadowserver .
#cybergirls -
The Shadowserver Foundation
@Shadowserver
We shared out ~2000 unique IPs exposing secrets that are known to have been harvested by a threat actor. IP data in our Compromised Website report: www.shadowserver.org/what-we-do/network-reporting/comprom… for your network/constituency with the 'stolen-key' tag (dated 2026-07-02). Check your reports!
The Shadowserver Foundation
@Shadowserver
Thank you to our anonymous partner for the contribution!
-
The Shadowserver Foundation
@Shadowserver
We are scanning for SimpleHelp CVE-2026-48558 vulnerable instances since 2026-06-16. We see 439 unpatched in our 2026-07-01 scan. Most (268) found in the US.
Raw IP data in www.shadowserver.org/what-we-do/network-reporting/vulnera… for your network/constitiuency
Dashboard World Map view: dashboard.shadowserver.org/statistics/combined/map/?date_…
CISA Cyber
@CISACyber
🛡️ We added SimpleHelp authentication bypass vulnerability CVE-2026-48558 to our Known Exploited Vulnerabilities Catalog. Visit go.dhs.gov/Z3Q & apply mitigations to protect your org from cyberattacks. #cybersecurity #infosec
The Shadowserver Foundation
@Shadowserver
We also recently collaborated with @ValidinLLC for additional domain based detections, thank you!
-
The Shadowserver Foundation
@Shadowserver
We have improved our Oracle E-Business Suite fingerprinting by adding domain based scans in collaboration with @ValidinLLC. Around 950 exposed instances now seen globally (no vulnerability assessment). CVE-2026-46817 attempts have been observed in the wild by @DefusedCyber
The Shadowserver Foundation
@Shadowserver
IP data for your network/constituency shared in our Device ID reporting (device_vendor Oracle device_model Oracle E-Business Suite)
World Map view of exposed EBS instances (no vulnerability assessment): dashboard.shadowserver.org/statistics/iot-devices/map/?da…
CVE-2026-46817 NVD entry: nvd.nist.gov/vuln/detail/CVE-2026-46817
The Shadowserver Foundation
@Shadowserver
Patch info from Oracle: www.oracle.com/security-alerts/cspumay2026.html
-
The Shadowserver Foundation
@Shadowserver
Yesterday we reported out an additional dataset found on the #fortibleed threat actors systems in a one-off Special Report - www.shadowserver.org/what-we-do/network-reporting/fortibl…. The data was shared with us by @spycloudco & covers 35000 new IPs not previously reported.
The Shadowserver Foundation
@Shadowserver
The report also contains over 1000 IPs where the threat actor ran credential sniffing in June.
Check out SpyCloud's analysis here: spycloud.com/blog/what-spycloud-found-inside-the-fortible…
Thank you to SpyCloud for the collaboration!
If you receive an alert from us, make sure to verify the data!
The Shadowserver Foundation
@Shadowserver
Global Stats:
Dashboard World Map view: dashboard.shadowserver.org/statistics/combined/map/?date_…
Dashboard Tree Map view: dashboard.shadowserver.org/statistics/combined/tree/?date… -
The Shadowserver Foundation reposted
VulnCheck
@VulnCheckAI
On the THREATCON1 Podcast, Piotr Kijewski (@Shadowserver) breaks down AI-generated vuln reports, fake exploits and “research” that fails in the real world.
Could AI misinformation become its own threat vector?
Watch: www.youtube.com/watch?v=2E1Tn1zhgIQ&list=PLxJm4O47cW3WFm5…
Listen: podcasts.apple.com/us/podcast/episode-19-inside-shadowser…This media couldn't be displayed. See it on the original post. -
The Shadowserver Foundation
@Shadowserver
More Operation Endgame #cybercrime disruption success this week, with a new one-off StealC Historical Bot Special Report run overnight (2026-06-24), continuing our support for international LE partners:
www.shadowserver.org/news/stealc-historical-bot-infection…Post not available here, view on X
The Shadowserver Foundation
@Shadowserver
StealC Historical Bot Special Report technical details and sample data available here (dated 2026-06-24):
www.shadowserver.org/what-we-do/network-reporting/critica…
The Shadowserver Foundation
@Shadowserver
As with SocGholish Compromised WordPress Sites Special Report run last week (2026-06-18), if you receive a StealC alert from us or your service provider/national CSIRT, please follow remediation advice and change passwords immediately!
-
The Shadowserver Foundation
@Shadowserver
Last week we added scanning for Joomla JCE editor extension CVE-2026-48907 vulnerable instances. This RCE vulnerability is exploited in the wild & on @CISACyber KEV. 4840 vulnerable instances seen 2026-06-22 down from 5146 on 2026-06-19. Top affected: US
dashboard.shadowserver.org/statistics/combined/map/?date_…
The Shadowserver Foundation
@Shadowserver
Raw IP data shared in our Vulnerable HTTP reporting www.shadowserver.org/what-we-do/network-reporting/vulnera… tagged 'cve-2026-48907' filtered by network/constituency
Dashboard Tree Map view: dashboard.shadowserver.org/statistics/combined/tree/?date…
Patch info: www.joomlacontenteditor.net/news/jce-security-update-and-… -
The Shadowserver Foundation
@Shadowserver
We shared a one-off "FortiBleed" dataset of compromised Fortinet devices in our Compromised Website Report www.shadowserver.org/what-we-do/network-reporting/comprom… thanks to collaboration with @socradar!
Stats:
Dashboard World map view:
dashboard.shadowserver.org/statistics/combined/map/?date_…
Dashboard Tree map view:
dashboard.shadowserver.org/statistics/combined/tree/?date…
The Shadowserver Foundation
@Shadowserver
IP data tagged 'fortibleed' in www.shadowserver.org/what-we-do/network-reporting/comprom… with timestamp set to 2026-06-18
SOCRadar FortiBleed checker: socradar.io/free-tools/fortibleed
Background: socradar.io/blog/fortibleed-fortinet-firewalls-compromised/ -
The Shadowserver Foundation
@Shadowserver
New one-off SocGholish Compromised #wordpress Sites Special Report run today, in continued support of international LE partners in Operation Endgame #cybercrime disruption:
www.shadowserver.org/news/socgholish-compromised-wordpres…
Great work once again everyone involved 👏
The Shadowserver Foundation
@Shadowserver
1,441,695 credentials covering period 2023-05-17 to 2026-05-25, from 1,134,542 domains hosted on 271,176 unique IP addresses, across 7,550 different ASNs in 187 countries/territories globally.
Report technical details available here (dated 2026-06-18):
www.shadowserver.org/what-we-do/network-reporting/critica…
The Shadowserver Foundation
@Shadowserver
WordPress site users/admins (plus their friends and colleagues):
Please read the defensive guidance provided, check your sites and remediate any signs of compromise immediately. -
The Shadowserver Foundation
@Shadowserver
Happy to once again support LE partners in disruption of the AudiA6 service, allegedly responsible for $389 million USD in cryptocurrency money laundering:
www.justice.gov/usao-edpa/pr/two-charged-connection-crypt…
www.secretservice.gov/newsroom/releases/2026/06/two-charg…
www.europol.europa.eu/media-press/newsroom/news/ransomwar… -
The Shadowserver Foundation
@Shadowserver
Heads up! New report going out daily: the Initial Access Broker Report www.shadowserver.org/what-we-do/network-reporting/initial… on compromised hosts likely under control of IABs
Data thanks to collaboration with anonymous researchers & @spycloudco - thank you!
Check your free daily reports from us! -
The Shadowserver Foundation
@Shadowserver
We are observing a large amount of Ivanti Sentry CVE-2026-10520 exploitation attempts based on the public PoC today. We see 19 vulnerable instances in our own scans, with at least 2 backdoored (thanks to @NCA_KSA for the tip!). However, all remaining likely compromised too.
Post not available here, view on X
The Shadowserver Foundation
@Shadowserver
Compromised IP data shared in our Compromised Website reporting tagged as 'ivanti-sentry,injected-code,backdoor'. See: www.shadowserver.org/what-we-do/network-reporting/comprom…
Advisory/patch: hub.ivanti.com/s/article/Security-Advisory-Ivanti-Sentry-…
The Shadowserver Foundation
@Shadowserver
Map has a typo in the date, should of course be 2026-06-10
-
The Shadowserver Foundation
@Shadowserver
Shadowserver is excited to share its cybersecurity insights and actionable recommendations in a report aimed at helping ECOWAS stakeholders make West Africa more secure!
Read the report & accompanying fact sheets in English, French & Portuguese at www.shadowserver.org/news/shadowserver-report-provides-cy…
The Shadowserver Foundation
@Shadowserver
Direct links (full report) -
English: www.shadowserver.org/wp-content/uploads/2026/06/SSF001-EC…
French: www.shadowserver.org/wp-content/uploads/2026/06/SSF001-EC…
Portuguese: www.shadowserver.org/wp-content/uploads/2026/06/SSF001-EC…
Direct links (fact sheet) -
English: www.shadowserver.org/wp-content/uploads/2026/06/SSF001-EC…
French: www.shadowserver.org/wp-content/uploads/2026/06/SSF001-EC…
Portuguese: www.shadowserver.org/wp-content/uploads/2026/06/SSF001-EC… -
The Shadowserver Foundation
@Shadowserver
We added scanning of Automatic Tank Gauge (ATG) systems to our Accessible ICS reporting with 1061 IPs seen on 2026-06-05 (on port 10001/tcp).
This is after weeding out vast majority which appear to be honeypots (including ports 8001/9001). Vast majority exposed are in the US.
The Shadowserver Foundation
@Shadowserver
IP data in www.shadowserver.org/what-we-do/network-reporting/accessi… (tagged 'atg')
Dashboard World Map view: dashboard.shadowserver.org/statistics/combined/map/?date_…
These should not be publicly exposed - read why at www.cisa.gov/resources-tools/resources/cisa-and-partners-… from @CISACyber
The Shadowserver Foundation
@Shadowserver
See also: www.bitsight.com/blog/critical-vulnerabilities-discovered…
-
The Shadowserver Foundation
@Shadowserver
Very happy to support @CrowdStrike and @Google in disruption of the Glassworm botnet, which features 4x C2 channels, and targets developers via open-source supply chains:
www.crowdstrike.com/en-us/blog/inside-crowdstrike-takedow…Post not available here, view on X
The Shadowserver Foundation
@Shadowserver
Daily aggregated country level statistics available via our public Dashboard:
Graph
dashboard.shadowserver.org/statistics/combined/time-serie…
Heatmap
dashboard.shadowserver.org/statistics/combined/tree/?date…
Worldmap
dashboard.shadowserver.org/statistics/combined/map/?date_…
The Shadowserver Foundation
@Shadowserver
Check your network logs and endpoint telemetry for connections to benign "lighthouse" IP address 164.92.88[.]210 - any activity suggests Glassworm infections, which require immediate remediation
-
The Shadowserver Foundation
@Shadowserver
We published a "Shadowserver-in-a-box" platform based on IntelMQ + ELK that can ingest, process and visualize our threat/vulnerability/victim data feeds. Available as a VM or Docker image for free download. Use it for training or in production!
github.com/The-Shadowserver-Foundation/trainingPost not available here, view on X
The Shadowserver Foundation
@Shadowserver
Development was supported by the cyber capacity building project under the ECOWAS-G7 partnership for cybersecurity, the “Joint Platform for Advancing Cyber Security” (JPAC) in West Africa.
@ecowas_cedeao @G7 @EU_Commission @GermanyDiplo @giz_gmbh
The Shadowserver Foundation
@Shadowserver
The project was launched by the ECOWAS Commission in collaboration with Germany’s G7 presidency in 2022, commissioned by the German Federal Foreign Office & the European Union Commission in 2023 & implemented by Deutsche Gesellschaft für Internationale Zusammenarbeit (GIZ) GmbH.
-
The Shadowserver Foundation
@Shadowserver
We are scanning & reporting daily Wazuh CVE-2026-30893 (CVSS 9.9) vulnerable instances, with over 3500 IPs seen unpatched on 2026-05-10. See advisory & update to latest version: github.com/wazuh/wazuh/security/advisories/GHSA-m8rw-v4f6… ...
Worth keeping your security platforms up to date!
The Shadowserver Foundation
@Shadowserver
IP data for your network/constituency shared in Vulnerable HTTP reporting, tagged 'cve-2026-30893: www.shadowserver.org/what-we-do/network-reporting/vulnera…
Public Dashboard tree map view: dashboard.shadowserver.org/statistics/combined/tree/?date…
NVD entry: nvd.nist.gov/vuln/detail/CVE-2026-30893
#cybercivildefense -
The Shadowserver Foundation
@Shadowserver
We are tagging CVE-2026-6973 Ivanti EPMM instances seen in our daily scans. 362 IPs seen unpatched on 2026-05-10, down from 562 IPs on 2026-05-08 when we first added the detection. See Ivanti advisory for details - hub.ivanti.com/s/article/May-2026-Security-Advisory-Ivant…
CVE-2026-6973 is on @CISACyber KEV.
The Shadowserver Foundation
@Shadowserver
Raw IP data in our Vulnerable HTTP reporting www.shadowserver.org/what-we-do/network-reporting/vulnera… tagged 'cve-2026-6973'
Public Dashboard tree map overview of vulnerable instances:
dashboard.shadowserver.org/statistics/combined/tree/?date…
CVE-2026-6973 patch tracker:
dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
Attention! cPanel/WHM CVE-2026-41940 attacks ongoing, with at least 44K IPs likely compromised & seen scanning our honeypots on 2026-04-30. Follow latest guidance to track for compromise & patch: support.cpanel.net/hc/en-us/articles/40073787579671-Secur…
See Public Dashboard for stats: dashboard.shadowserver.org/statistics/honeypot/device/tre… -
The Shadowserver Foundation
@Shadowserver
Attention! cPanel/WHM CVE-2026-41940 attacks ongoing, with at least 44K IPs likely compromised & seen scanning our honeypots on 2026-04-30. Follow latest guidance to track for compromise & patch: support.cpanel.net/hc/en-us/articles/40073787579671-Secur…
See Public Dashboard for stats: dashboard.shadowserver.org/statistics/honeypot/device/tre…Post not available here, view on X
The Shadowserver Foundation
@Shadowserver
You can find likely newly compromised instances in our honeypot based reports with cPanel set in the device_vendor of the attacking device
- Darknet Events Report www.shadowserver.org/what-we-do/network-reporting/honeypo…
- Honeypot HTTP Scanner Events Report
www.shadowserver.org/what-we-do/network-reporting/honeypo…
The Shadowserver Foundation
@Shadowserver
- Honeypot Brute Force Events Report
www.shadowserver.org/what-we-do/network-reporting/honeypo…
You can also find exposed cPanel/WHM instances in our Device ID reporting with ~650K IPs seen hosting dashboard.shadowserver.org/statistics/iot-devices/time-se… -
The Shadowserver Foundation
@Shadowserver
We are scanning/reporting daily Zimbra Collaboration Suite instances vulnerable to CVE-2025-48700, that can allow unauthorized access to sensitive information. This vulnerability is exploited in the wild and on @CISACyber KEV. We see over 10.5K IPs unpatched 2026-04-23.
The Shadowserver Foundation
@Shadowserver
IP data in Vulnerable HTTP reporting: www.shadowserver.org/what-we-do/network-reporting/vulnera…
See wiki.zimbra.com/wiki/Security_Center for patch info.
Dashboard World Map view: dashboard.shadowserver.org/statistics/combined/map/?date_…
Dashboard Tree Map view: dashboard.shadowserver.org/statistics/combined/tree/?date…
CVE-2025-48700 Tracker: dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation reposted
ZA Network Operators Group
@ZA_NOG
At #iweek2026, Andy Chadwick from @Shadowserver joined us to share how their nonprofit foundation provides world-class threat intelligence at no cost to network operators and ISPs.
-
The Shadowserver Foundation
@Shadowserver
We are also scanning & reporting Microsoft SharePoint CVE-2026-32201 (Improper input validation in SharePoint allows an unauthorized attacker to perform spoofing over a network). This vulnerability is known exploited in the wild & on @CISACyber KEV. 1370 IPs seen unpatched.
The Shadowserver Foundation
@Shadowserver
IP data shared in Vulnerable HTTP reporting: shadowserver.org/what-we-do/network-reporting/vulnerable-…
Dashboard World Map view: dashboard.shadowserver.org/statistics/combined/map/?date_…
Dashboard Tree Map view: dashboard.shadowserver.org/statistics/combined/tree/?date…
CVE-2026-32201 tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
Numbers down from 2026-04-15 when we found 1745 unpatched.
The Shadowserver Foundation
@Shadowserver
This is a version based scan.
Microsoft Advisory: msrc.microsoft.com/update-guide/en-US/vulnerability/CVE-2… -
The Shadowserver Foundation
@Shadowserver
Thank you to Precursor Security for becoming a Shadowserver Alliance Silver Tier Partner!
@PrecurSec delivers pen testing, 24/7 managed SOC, and more. precursorsecurity.com
Together with our Alliance Partner community, we’ll make the Internet more secure. -
The Shadowserver Foundation
@Shadowserver
We are now scanning daily for CVE-2026-34197 (Apache ActiveMQ Improper Input Validation Vulnerability) which has recently been added to @CISACyber KEV.
6364 IPs seen vulnerable on 2026-04-19 based on a version check.
Dashboard Tree Map view:
dashboard.shadowserver.org/statistics/combined/tree/?date…
The Shadowserver Foundation
@Shadowserver
IP data shared in our Accessible ActiveMQ reporting www.shadowserver.org/what-we-do/network-reporting/accessi…
For Dashboard viewing, select sources 'activemq' and 'cve-2026-34197'
ActiveMQ Security advisory: activemq.apache.org/security-advisories.data/CVE-2026-341…
Background with details from @Horizon3ai horizon3.ai/attack-research/disclosures/cve-2026-34197-ac…
The Shadowserver Foundation
@Shadowserver
CISA KEV entry: www.cisa.gov/known-exploited-vulnerabilities-catalog?fiel…
NVD CVE entry: nvd.nist.gov/vuln/detail/CVE-2026-34197 -
The Shadowserver Foundation
@Shadowserver
We added CVE-2026-35616 scans based on the vulnerability detector developed by @bishopfox bishopfox.com/blog/api-authentication-bypass-in-forticlie….
Over 60 IPs still assessed as vulnerable: dashboard.shadowserver.org/statistics/combined/tree/?date…
Data shared daily in our Vulnerable HTTP reporting: www.shadowserver.org/what-we-do/network-reporting/vulnera…
The Shadowserver Foundation
@Shadowserver
Heads up FortiClient EMS users! CVE-2026-35616 (new) & CVE-2026-21643 - both unauthenticated RCE observed to be exploited in the wild! We fingerprint about 2000 instances globally, see public Dashboard: dashboard.shadowserver.org/statistics/iot-devices/time-se…
Top affected: US & Germany dashboard.shadowserver.org/statistics/iot-devices/map/?da… -
The Shadowserver Foundation
@Shadowserver
We’re excited to announce that @cybercentre_ca has increased its annual Shadowserver Alliance Partnership tier from Gold to Diamond! Thank you @cybercentre_ca for your generous support and for being a valuable and trusted partner in making the Internet more secure.
The Shadowserver Foundation
@Shadowserver
Become an Alliance Partner today: www.shadowserver.org/partner/
-
The Shadowserver Foundation
@Shadowserver
We have also added CVE-2026-2699 tagging to our scans, which now detect unpatched Progress ShareFile instances. 120 IPs seen on 2026-04-06: dashboard.shadowserver.org/statistics/combined/time-serie…
CVE-2026-2699 Tree Map view: dashboard.shadowserver.org/statistics/combined/tree/?date…
IP data in Vulnerable HTTP reporting: www.shadowserver.org/what-we-do/network-reporting/vulnera…
The Shadowserver Foundation
@Shadowserver
We added Progress ShareFile fingerprinting to our scans & reports with 784 unique IPs seen exposed on 2026-04-02. @watchtowrcyber recently disclosed details behind an RCE CVE-2026-2699 & CVE-2026-2701 exploit chain affecting ShareFile. Make sure to apply the latest patch!
-
The Shadowserver Foundation
@Shadowserver
Heads up FortiClient EMS users! CVE-2026-35616 (new) & CVE-2026-21643 - both unauthenticated RCE observed to be exploited in the wild! We fingerprint about 2000 instances globally, see public Dashboard: dashboard.shadowserver.org/statistics/iot-devices/time-se…
Top affected: US & Germany dashboard.shadowserver.org/statistics/iot-devices/map/?da…
The Shadowserver Foundation
@Shadowserver
Raw IP data shared in our Device ID reporting www.shadowserver.org/what-we-do/network-reporting/device-…
If you receive data from us on exposed instances, check for compromise & patch!
Patch info:
CVE-2026-35616 (0day reported by @DefusedCyber): fortiguard.fortinet.com/psirt/FG-IR-26-099
CVE-2026-21643: fortiguard.fortinet.com/psirt/FG-IR-25-1142 -
The Shadowserver Foundation
@Shadowserver
We added Progress ShareFile fingerprinting to our scans & reports with 784 unique IPs seen exposed on 2026-04-02. @watchtowrcyber recently disclosed details behind an RCE CVE-2026-2699 & CVE-2026-2701 exploit chain affecting ShareFile. Make sure to apply the latest patch!
The Shadowserver Foundation
@Shadowserver
Raw IP data in Device ID reporting, with device_vendor set to Progress & device_model to ShareFile: www.shadowserver.org/what-we-do/network-reporting/device-…
Thank you to @ValidinLLC for the collaboration!
Dashboard World Map view: dashboard.shadowserver.org/statistics/iot-devices/map/?da…
Dashboard Tree Map view:
dashboard.shadowserver.org/statistics/iot-devices/tree/?d…
The Shadowserver Foundation
@Shadowserver
Top affected: US, Germany
Patch: docs.sharefile.com/en-us/storage-zones-controller/5-0/sec…
Note: we are just sharing exposed population, there is no vulnerability assessment
Background: labs.watchtowr.com/youre-not-supposed-to-sharefile-with-e…
CVE-2026-2699 NVD entry: nvd.nist.gov/vuln/detail/CVE-2026-2699
CVE-2026-2701 NVD entry:
nvd.nist.gov/vuln/detail/CVE-2026-2701 -
The Shadowserver Foundation
@Shadowserver
F5 BIG-IP APM CVE-2025-53521 impact has recently been updated from a DoS to RCE (see: my.f5.com/manage/s/article/K000156741) & added to @CISACyber KEV.
We are fingerprinting & sharing F5 BIG-IP APM instances - over 17.1K IPs seen on 2026-03-31 globally. This is just a population assessment.
The Shadowserver Foundation
@Shadowserver
IP data is shared in our Device ID reporting www.shadowserver.org/what-we-do/network-reporting/device-… with device_vendor set to 'F5', device_model set to 'BIG-IP APM'
Dashboard Tree Map view: dashboard.shadowserver.org/statistics/iot-devices/tree/?d…
Dashboard World Map view:
dashboard.shadowserver.org/statistics/iot-devices/map/?da…
Top affected: US, Japan
The Shadowserver Foundation
@Shadowserver
If you have APM running on your services/network make sure you are patched & review for any compromise
NVD entry: nvd.nist.gov/vuln/detail/CVE-2025-53521 -
The Shadowserver Foundation
@Shadowserver
We’re excited to welcome @KPN to the Shadowserver Alliance as a bronze tier partner!
KPN is a leading telecommunications and IT provider in the Netherlands. www.kpn.com/algemeen/english
Together we will raise the bar on cybersecurity to make the Internet more secure.
The Shadowserver Foundation
@Shadowserver
Become a Shadowserver Alliance partner today: www.shadowserver.org/partner/
-
The Shadowserver Foundation
@Shadowserver
IIS EOL tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
Over 511 000 End-of-Life Microsoft IIS instances seen in our daily scans, out of those over 227 000 instances that are beyond the official Microsoft Extended Security Updates (ESU) period. We now tag those 'eol-iis' and 'eos-iis' respectively in our Vulnerable HTTP reports.
-
The Shadowserver Foundation
@Shadowserver
Over 511 000 End-of-Life Microsoft IIS instances seen in our daily scans, out of those over 227 000 instances that are beyond the official Microsoft Extended Security Updates (ESU) period. We now tag those 'eol-iis' and 'eos-iis' respectively in our Vulnerable HTTP reports.
The Shadowserver Foundation
@Shadowserver
Raw IP data shared in www.shadowserver.org/what-we-do/network-reporting/vulnera… filtered by recipient network/constituency
Top countries running outdated IIS instances: China & USA
EOL IIS Dashboard World Map view: dashboard.shadowserver.org/statistics/combined/map/?date_…
EOS (beyond ESU) IIS Dashboard World Map view: dashboard.shadowserver.org/statistics/combined/map/?date_…
The Shadowserver Foundation
@Shadowserver
More on associated risks & on reducing attack surface from EOL devices from @CISACyber www.cisa.gov/resources-tools/resources/reducing-attack-su…
MS IIS lifecycle: learn.microsoft.com/en-us/lifecycle/products/internet-inf…
MS Extended Security Update program (ESU) learn.microsoft.com/en-us/lifecycle/products/internet-inf… -
The Shadowserver Foundation
@Shadowserver
We added Microsoft SharePoint CVE-2026-20963 (post-auth deserialization RCE) to our scanning & daily feeds. 1109 IPs found running vulnerable instances worldwide (close to 1900 FQDNs) on 2026-03-19, with 510 IPs in the US.
Dashboard World Map: dashboard.shadowserver.org/statistics/combined/map/?date_…
The Shadowserver Foundation
@Shadowserver
Vulnerable IPs (tagged 'cve-2026-20963') shared daily in our Vulnerable HTTP reporting: www.shadowserver.org/what-we-do/network-reporting/vulnera…
CVE-2026-20963 is known exploited in the wild and on @CISACyber KEV: www.cisa.gov/known-exploited-vulnerabilities-catalog?sear…
Check for compromise.
Microsoft Advisory: msrc.microsoft.com/update-guide/vulnerability/CVE-2026-20963
The Shadowserver Foundation
@Shadowserver
CVE-2026-20963 Dashboard Tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
Dashboard Tree Map view: dashboard.shadowserver.org/statistics/combined/tree/?date… -
The Shadowserver Foundation
@Shadowserver
We added a feed of IPs/websites with ClickFix/ClearFake injected code in our Compromised Website reporting, tagged as 'clickfix'. Visitors of the website get tricked to install malware when injected JavaScript executes. If you receive an alert review for root cause of compromise!
Post not available here, view on X
The Shadowserver Foundation
@Shadowserver
Compromised Website Report (now with ClickFix data!): www.shadowserver.org/what-we-do/network-reporting/comprom…
Dashboard World Map view of infected IPs:
dashboard.shadowserver.org/statistics/combined/map/?date_…
Dashboard Tree Map view of infected IPs:
dashboard.shadowserver.org/statistics/combined/tree/?date…
The Shadowserver Foundation
@Shadowserver
657 instances shared for 2026-03-14. We expect to increase the volume of the feed in the future!
We would like to thank our Alliance partners and @ValidinLLC for the collaboration making this possible!
Background on investigating ClickFix/ClearFake: www.atea.no/siste-nytt/it-sikkerhet/investigating-a-clear… -
The Shadowserver Foundation
@Shadowserver
Great to support our international LE and private sector partners in Tycoon 2FA phishing-as-a-service #cybercrime disruption:
www.shadowserver.org/news/tycoon-2fa-phishing-as-a-servic…
New nCSIRT-only Tycoon 2FA Domains Special Report run 2026-03-04 (historical C2/panel/infra domains)
The Shadowserver Foundation
@Shadowserver
Operation successfully coordinated by @Europol, via EC3 Cyber Intelligence Extension Programme (CIEP). Civil legal action by @MicrosoftDCU
Millions of phishing emails, 96K victims globally
Key domains seized/sinkholed/suspended, thousands of criminal users potentially impacted
The Shadowserver Foundation
@Shadowserver
nCSIRT-only Tycoon 2FA Domains Special Report run 2026-03-04 (historical C2/panel/infra domains) link: www.shadowserver.org/what-we-do/network-reporting/info-ty…
-
The Shadowserver Foundation
@Shadowserver
Another Iran Internet blackout, this time due to the war, visualized on our Public Dashboard - drop to near zero on 2026-03-01: dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
Iran Internet blackout visualized on our Public Dashboard - drop to near zero exposure after 2026-01-08 in scan and sinkhole telemetry:
Scan results: dashboard.shadowserver.org/statistics/combined/time-serie…
Sinkhole results:
dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation
@Shadowserver
We are continuing to expand our n8n RCE vulnerability scanning - most recently adding CVE-2026-27495 (CVSS 9.4) tagging as well. You can track our various n8n scan results here for the most well known critical vulns: dashboard.shadowserver.org/statistics/combined/time-serie…
Top affected: US, Germany & France.
The Shadowserver Foundation
@Shadowserver
IP data on vulnerable instances is tagged 'n8n' & with a cve tag (like cve-2026-27495) in our Vulnerable HTTP reporting - www.shadowserver.org/what-we-do/network-reporting/vulnera…
Latest n8n critical RCE vulns (all covered with above tag):
github.com/n8n-io/n8n/security/advisories/GHSA-wxx7-mcgf-…
github.com/n8n-io/n8n/security/advisories/GHSA-vpcf-gvg4-…
github.com/n8n-io/n8n/security/advisories/GHSA-jjpj-p2wh-…
The Shadowserver Foundation
@Shadowserver
If you receive an alert from us, please patch.
World Map view of all n8n vulnerable instances we track: dashboard.shadowserver.org/statistics/combined/map/?date_… -
The Shadowserver Foundation
@Shadowserver
We are scanning & reporting IceWarp CVE-2025-14500 (CVSS 9.8, pre-auth command injection RCE) instances. 1278 IPs seen 2026-03-01 (version based check).
Patch info: support.icewarp.com/hc/en-us/community/posts/400409800987…
IP data in www.shadowserver.org/what-we-do/network-reporting/vulnera…
Dashboard World Map view: dashboard.shadowserver.org/statistics/combined/map/?date_…
The Shadowserver Foundation
@Shadowserver
If you receive an alert from us, please update!
NVD entry: nvd.nist.gov/vuln/detail/cve-2025-14500
Background: www.zerodayinitiative.com/advisories/ZDI-25-1072/ -
The Shadowserver Foundation
@Shadowserver
Cisco SD-WAN incidents: we are sharing information on identified Cisco SD-WAN instances in Device ID reporting - www.shadowserver.org/what-we-do/network-reporting/device-…
We see over 5.5K Cisco SD-WAN IPs (control plane) (dashboard.shadowserver.org/statistics/iot-devices/tree/?d…), & over 270 management interfaces (dashboard.shadowserver.org/statistics/iot-devices/tree/?d…)
The Shadowserver Foundation
@Shadowserver
We are also sharing SSH port 830 data in our Accessible SSH reporting - this includes potential NETCONF instances www.shadowserver.org/what-we-do/network-reporting/accessi…
Around 90K SSH instances seen exposed, but this includes generic SSH population (NETCONF uses SSH).
Background: www.ncsc.gov.uk/news/exploitation-cisco-catalyst-sd-wans -
The Shadowserver Foundation
@Shadowserver
Thanks to collaboration with the Canadian Centre for Cyber Security @cybercentre_ca we can share more comprehensive information on FreePBX instances running webshells, with still over 900 IPs seen compromised.
Dashboard Victim overview (Tree map) dashboard.shadowserver.org/statistics/combined/tree/?date…
The Shadowserver Foundation
@Shadowserver
IP data in our Compromised Website report, tagged 'freepbx-compromised' - www.shadowserver.org/what-we-do/network-reporting/comprom…
Compromised FreePBX tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
These compromises are likely via CVE-2025-64328
Additional background from @Fortinet: www.fortinet.com/blog/threat-research/unveiling-the-weapo… -
The Shadowserver Foundation
@Shadowserver
Massive increase in sources attempting Ivanti EPMM CVE-2026-1281 exploitation, with over 28.3K source IPs seen on 2026-02-09. IP data on attackers shared in our www.shadowserver.org/what-we-do/network-reporting/honeypo… (with vulnerability_id set to CVE-2026-1281). 20.4K IPs seen from US networks.
The Shadowserver Foundation
@Shadowserver
We have started to report webshells (or other exploitation artifacts) found on Ivanti EPMM devices, likely compromised via CVE-2026-1281. 56 IPs found on 2026-02-06
Data in www.shadowserver.org/what-we-do/network-reporting/comprom…
Tree Map view: dashboard.shadowserver.org/statistics/combined/tree/?date…
Thank you to @NCA_KSA for the heads up!
The Shadowserver Foundation
@Shadowserver
Tracker: dashboard.shadowserver.org/statistics/honeypot/vulnerabil…
Tree Map view: dashboard.shadowserver.org/statistics/honeypot/vulnerabil… -
The Shadowserver Foundation
@Shadowserver
Running End-of-Life devices or apps is a major security risk. @CISACyber has recently released a Directive on the topic: www.cisa.gov/news-events/directives/bod-26-02-mitigating-…
It's worth mentioning we share many End-of-Life devices/apps in our daily reporting, tagged 'eol'.
See: dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
Over 57.5K IPs seen tagged with 'eol' in our exposed web service reporting alone! IP data shared for example in
www.shadowserver.org/what-we-do/network-reporting/vulnera…
Dashboard World Map view: dashboard.shadowserver.org/statistics/combined/map/?date_…
Dashboard Tree Map view: dashboard.shadowserver.org/statistics/combined/tree/?date… -
The Shadowserver Foundation
@Shadowserver
We have started to report webshells (or other exploitation artifacts) found on Ivanti EPMM devices, likely compromised via CVE-2026-1281. 56 IPs found on 2026-02-06
Data in www.shadowserver.org/what-we-do/network-reporting/comprom…
Tree Map view: dashboard.shadowserver.org/statistics/combined/tree/?date…
Thank you to @NCA_KSA for the heads up!
The Shadowserver Foundation
@Shadowserver
If you receive an alert from us, please review the security advisory and guidance from Ivanti at hub.ivanti.com/s/article/Security-Advisory-Ivanti-Endpoin… including the Exploitation Detection RPM Package co-developed by Ivanti & @ncsc_nl
-
The Shadowserver Foundation
@Shadowserver
For the last few days, we have been sharing SolarWinds Help Desk CVE-2025-40551 RCE vulnerable IPs (version check based) - ~170 seen. This vuln is now on @CISACyber KEV. Data in Vulnerable HTTP reports: www.shadowserver.org/what-we-do/network-reporting/vulnera…
Dashboard Tree Map view: dashboard.shadowserver.org/statistics/combined/tree/?date…
The Shadowserver Foundation
@Shadowserver
See advisory and patch info from SolarWinds: solarwinds.com/trust-center/security-advisories/cve-2025-…
If you receive an alert from us, make sure to review for compromise.
NVD entry: nvd.nist.gov/vuln/detail/CVE-2025-40551
Thank you to @ValidinLLC for collaboration on the scan. -
The Shadowserver Foundation
@Shadowserver
We are scanning & reporting out exposed OpenClaw/Clawdbot/Moltbot instances, with ~25K seen on 2026-02-02. We report these out in our Device Identification reporting, with vendor set to OpenClaw for all cases: www.shadowserver.org/what-we-do/network-reporting/device-…
World Map view: dashboard.shadowserver.org/statistics/iot-devices/map/?da…
The Shadowserver Foundation
@Shadowserver
Most instances are across various cloud providers.
Our reporting is for awareness purposes.
OpenClaw has had various security risks highlighted recently (such as for example www.wiz.io/blog/exposed-moltbook-database-reveals-million… & CVE-2026-25253 (1-Click RCE via Authentication Token Exfiltration)
The Shadowserver Foundation
@Shadowserver
Dashboard Tree Map view: dashboard.shadowserver.org/statistics/iot-devices/tree/?d…
OpenClaw exposure tracker (for past data, select vendor Moltbot on the Dashabord):
dashboard.shadowserver.org/statistics/iot-devices/time-se… -
The Shadowserver Foundation
@Shadowserver
Spike in Ivanti EPMM CVE-2026-1281 RCE exploitation attempts seen by our sensors last 24 hours from at least 13 source IPs. In our scans, we see ~1600 exposed instances worldwide (no vulnerability assessment). Top exposed: Germany
Ivanti hotfix guidance: forums.ivanti.com/s/article/Security-Advisory-Ivanti-Endp…
The Shadowserver Foundation
@Shadowserver
IP data on exposed instances is shared in Device ID (device_vendor Ivanti, device_model EPMM ): www.shadowserver.org/what-we-do/network-reporting/device-…
Dashboard World Map view of exposed instances: dashboard.shadowserver.org/statistics/iot-devices/map/?da…
Dashboard Tree Map geo breakdown of exposed instances: dashboard.shadowserver.org/statistics/iot-devices/tree/?d…
The Shadowserver Foundation
@Shadowserver
CVE-2026-1281 has been added to @CISACyber Known Exploited Vulnerability catalog: www.cisa.gov/news-events/alerts/2026/01/29/cisa-adds-one-…
Additional background from @watchtowrcyber : labs.watchtowr.com/someone-knows-bash-far-too-well-and-we… -
The Shadowserver Foundation
@Shadowserver
CVE-2026-24858, a Fortinet authentication bypass vulnerability affecting multiple Fortinet products with FortiCloud SSO enabled has been added by @CISACyber to the KEV catalog.
We share exposed Fortinet instances with FortiCloud SSO enabled daily in our feeds (~10 000 seen)
The Shadowserver Foundation
@Shadowserver
We added fingerprinting of Fortinet devices with FortiCloud SSO enabled to our Device Identification reporting (at least 25K IPs seen globally). While not necessarily vulnerable to CVE-2025-59718/CVE-2025-59719 if you get a report from us regarding exposure, please verify/patch!
The Shadowserver Foundation
@Shadowserver
Numbers have gone down from 25 000+ seen when we first started reporting in mid-Dec 2025.
We share data on Fortinet devices with FortiCloud SSO enabled in our Device ID reporting: www.shadowserver.org/what-we-do/network-reporting/device-…
Fortinet Advisory: www.fortiguard.com/psirt/FG-IR-26-060
The Shadowserver Foundation
@Shadowserver
@CISACyber Advisory: www.cisa.gov/news-events/alerts/2026/01/28/fortinet-relea…
Public Dashboard Tree Map view: dashboard.shadowserver.org/statistics/iot-devices/tree/?d…
Public Dashboard Exposure Tracker: dashboard.shadowserver.org/statistics/iot-devices/time-se… -
The Shadowserver Foundation
@Shadowserver
We added SmarterTools SmarterMail CVE-2026-23760 RCE to our daily Vulnerable HTTP scans. Around 6000 IPs globally found likely vulnerable based on our version check. We also see exploitation attempts in the wild.
CVE-2026-23760 Geo Treemap View: dashboard.shadowserver.org/statistics/combined/tree/?date…
The Shadowserver Foundation
@Shadowserver
Tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
Please update to the latest build (9518 as of time of writing) www.smartertools.com/smartermail/release-notes/current
Background: labs.watchtowr.com/attackers-with-decompilers-strike-agai… -
The Shadowserver Foundation
@Shadowserver
Regarding CVE-2026-24061 in GNU InetUtils telnetd: while we are not scanning for it explicitly (due to current lack of ability to check in a safe way, we share - and have for years - data on exposed instances in our Accessible Telnet Report: www.shadowserver.org/what-we-do/network-reporting/accessi…
~800K exposedPost not available here, view on X
The Shadowserver Foundation
@Shadowserver
Dashboard Tree Map view of telnet exposure (no vulnerability assessment): dashboard.shadowserver.org/statistics/combined/tree/?date…
Like others, we also see exploitation attempts in the wild at scale.
The Shadowserver Foundation
@Shadowserver
We have been tweaking the scan the last few days to better weed out non-telnet protocols. Some honeypots may remain.
Telnet should not be publicly exposed, but often is especially on legacy iot devices.
CVE-2026-24061 info & patch: seclists.org/oss-sec/2026/q1/89 -
The Shadowserver Foundation
@Shadowserver
We are scanning & reporting out SmarterMail hosts vulnerable to CVE-2025-52691 RCE (CVSS 10).
8001 unique IPs likely vulnerable on 2026-01-12 (out of 18783 exposed). Note Exploit PoCs are public.
Tree Map view: dashboard.shadowserver.org/statistics/combined/tree/?date…
Raw IP data in www.shadowserver.org/what-we-do/network-reporting/vulnera…
The Shadowserver Foundation
@Shadowserver
NVD entry: nvd.nist.gov/vuln/detail/CVE-2025-52691
Singapore CSA (@CSAsingapore ) advisory: www.csa.gov.sg/alerts-and-advisories/alerts/al-2025-124/
CVE-2025-52691 Tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
SmarterMail exposure tracker (no vulnerability assessment):
dashboard.shadowserver.org/statistics/iot-devices/time-se…
The Shadowserver Foundation
@Shadowserver
Update to latest SmarterMail version (Build 9413 and later): www.smartertools.com/smartermail/release-notes/current
-
The Shadowserver Foundation
@Shadowserver
Iran Internet blackout visualized on our Public Dashboard - drop to near zero exposure after 2026-01-08 in scan and sinkhole telemetry:
Scan results: dashboard.shadowserver.org/statistics/combined/time-serie…
Sinkhole results:
dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation
@Shadowserver
You can also track different scan results for recent n8n vulns (not just CVE-2026-21858 but also CVE-2025-68668, CVE-2025-68613, CVE-2026-21877) on Dashboard:
dashboard.shadowserver.org/statistics/combined/time-serie…
dashboard.shadowserver.org/statistics/combined/map/?date_…
IP data shared in Vulnerable HTTP reporting: www.shadowserver.org/what-we-do/network-reporting/vulnera…
The Shadowserver Foundation
@Shadowserver
Scan results for n8n CVE-2026-21858 (CVSS 10.0 RCE) for 2026-01-09: 105,753 vulnerable instances by unique IP found - out of 230,562 IPs with n8n we see that day.
Dashboard Tree Map view: dashboard.shadowserver.org/statistics/combined/tree/?date…
IP data in Vulnerable HTTP reports: www.shadowserver.org/what-we-do/network-reporting/vulnera… -
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
Scan results for n8n CVE-2026-21858 (CVSS 10.0 RCE) for 2026-01-09: 105,753 vulnerable instances by unique IP found - out of 230,562 IPs with n8n we see that day.
Dashboard Tree Map view: dashboard.shadowserver.org/statistics/combined/tree/?date…
IP data in Vulnerable HTTP reports: www.shadowserver.org/what-we-do/network-reporting/vulnera… -
The Shadowserver Foundation
@Shadowserver
Scan results for n8n CVE-2026-21858 (CVSS 10.0 RCE) for 2026-01-09: 105,753 vulnerable instances by unique IP found - out of 230,562 IPs with n8n we see that day.
Dashboard Tree Map view: dashboard.shadowserver.org/statistics/combined/tree/?date…
IP data in Vulnerable HTTP reports: www.shadowserver.org/what-we-do/network-reporting/vulnera…
The Shadowserver Foundation
@Shadowserver
Thank you to @ValidinLLC for the collaboration on the scan!
Dashboard World Map view:
dashboard.shadowserver.org/statistics/combined/map/?date_…
CVE-2026-21858 Tracker:
dashboard.shadowserver.org/statistics/combined/time-serie…
Advisory with patch info: github.com/n8n-io/n8n/security/advisories/GHSA-v4pr-fm98-…
NVD entry: nvd.nist.gov/vuln/detail/CVE-2026-21858
The Shadowserver Foundation
@Shadowserver
Note this is a version based scan. If you receive an alert from us make sure to update!
Vulnerability details: www.cyera.com/research-labs/ni8mare-unauthenticated-remot… -
The Shadowserver Foundation
@Shadowserver
We added Fortinet SSL-VPN CVE-2020-12812 to our daily Vulnerable HTTP Report: www.shadowserver.org/what-we-do/network-reporting/vulnera…
After 5 1/2 years since being published still over 10K Fortinet firewalls remain unpatched. Vuln actively exploited as recently highlighted by Fortinet: www.fortinet.com/blog/psirt-blogs/product-security-adviso…
The Shadowserver Foundation
@Shadowserver
CVE-2020-12812 is also on @CISACyber KEV.
Dashboard World Map view: dashboard.shadowserver.org/statistics/combined/map/?date_…
Dashboard Tree Map view:
dashboard.shadowserver.org/statistics/combined/tree/?date…
Original Fortinet advisory from July 2020: www.fortiguard.com/psirt/FG-IR-19-283 -
The Shadowserver Foundation
@Shadowserver
MongoBleed update: We added MongoDB CVE-2025-14847 tagging today that is version based. This results in 74,854 possibly unpatched versions (out of 78,725 exposed today). IP data on vulnerable instances shared in our Open MongoDB Report: www.shadowserver.org/what-we-do/network-reporting/open-mo…
Post not available here, view on X
The Shadowserver Foundation
@Shadowserver
Advisory & patch details on CVE-2025-14847 can be found at jira.mongodb.org/browse/SERVER-115508
If you receive an alert from us, check for compromise!
Upgrade to 8.2.3, 8.0.17, 7.0.28, 6.0.27, 5.0.32, or 4.4.30.
The Shadowserver Foundation
@Shadowserver
Note FPs on CVE-2025-14847 tagging may be possible due to backporting patches without bumping versions.
IP data on exposed instances is shared daily since Feb 2015!
To view exposed info on Dashboard select source 'scan' 'scan6' & tag 'mongodb' dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation
@Shadowserver
Great to again provide technical support to Interpol & international LE partners, this time on Operation Sentinel:
www.interpol.int/en/News-and-Events/News/2025/574-arrests…
Undertaken as part of African Joint Operation against Cybercrime (AFJOC) project, funded by UK FCDO, & EU/Council of Europe GLACY-e project -
The Shadowserver Foundation
@Shadowserver
Attention! We are scanning & reporting WatchGuard Firebox devices unpatched to CVE-2025-14733 (Out of Bounds Write Vulnerability, unauthenticated RCE, CVSS 9.8). Nearly 125 000 IPs found (2025-12-20): dashboard.shadowserver.org/statistics/combined/tree/?date…
WatchGuard Advisory: www.watchguard.com/wgrd-psirt/advisory/wgsa-2025-00027
The Shadowserver Foundation
@Shadowserver
We share daily IP data in our Vulnerable ISAKMP Report, tagged 'cve-2025-14733': www.shadowserver.org/what-we-do/network-reporting/vulnera…
CVE-2025-14733 is reported exploited in the wild & on @CISACyber KEV: www.cisa.gov/known-exploited-vulnerabilities-catalog?fiel…
If you receive a report from us, check for signs of compromise as well
The Shadowserver Foundation
@Shadowserver
Most affected (most unpatched IPs): US (38.3K), Germany (14K), Italy (12.3K)
CVE-2025-14733 World Map View: dashboard.shadowserver.org/statistics/combined/tree/?date…
CVE-2025-14733 Tracker: dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation
@Shadowserver
We have identified 120 Cisco Secure Email Gateway/ Cisco Secure Email and Web Manager likely vulnerable to CVE-2025-20393 (over 650 fingerprinted exposed). CVE-2025-20393 is exploited in the wild, with no patch available. Follow Cisco recommendations at sec.cloudapps.cisco.com/security/center/content/CiscoSecu…
The Shadowserver Foundation
@Shadowserver
Data shared in our Vulnerable HTTP Report, tagged 'cve-2025-20393': www.shadowserver.org/what-we-do/network-reporting/vulnera…
Dashboard Tree Map view (CVE-2025-20393): dashboard.shadowserver.org/statistics/combined/tree/?date…
The Shadowserver Foundation
@Shadowserver
We also shared fingerprinted instances in our Device Identification Report (device_vendor Cisco, device_model "Cisco Secure Email Gateway" or "Cisco Secure Email and Web Manager")
www.shadowserver.org/what-we-do/network-reporting/device-…
#cybercivildefense #cybersecuritynews -
The Shadowserver Foundation
@Shadowserver
We added fingerprinting of Fortinet devices with FortiCloud SSO enabled to our Device Identification reporting (at least 25K IPs seen globally). While not necessarily vulnerable to CVE-2025-59718/CVE-2025-59719 if you get a report from us regarding exposure, please verify/patch!
The Shadowserver Foundation
@Shadowserver
Dashboard World Map: dashboard.shadowserver.org/statistics/iot-devices/map/?da…
Dashboard Tree Map overview:
dashboard.shadowserver.org/statistics/iot-devices/map/?da…
Exposure tracker:
dashboard.shadowserver.org/statistics/iot-devices/time-se…
Device ID Report:
www.shadowserver.org/what-we-do/network-reporting/device-…
Fortinet Advisory:
fortiguard.fortinet.com/psirt/FG-IR-25-647
See also: arcticwolf.com/resources/blog/arctic-wolf-observes-malici… -
The Shadowserver Foundation
@Shadowserver
Second Rhadamanthys Historic Bot Victims Special Report run overnight (dated 2025-12-15):
92M stolen data items from 567K victim IPs across 228 countries
Additional data shared by LE partners under Operation Endgame
Updated blog:
www.shadowserver.org/news/rhadamanthys-historical-bot-inf…
Check your reports! -
The Shadowserver Foundation
@Shadowserver
Using ELK & interested in automating ingestion of our threat intel for your network/constituency via our API?
We have introduced an ECS logging script for our intelligence reports. This script uses Redis to queue events for Logstash.
Check it out at github.com/The-Shadowserver-Foundation/api_utils/tree/mai… -
The Shadowserver Foundation
@Shadowserver
Update on React Server Components CVE-2025-55182: over 165K IPs & 644K domains with vulnerable code found on 2025-12-08 after scan targeting improvements!
See: dashboard.shadowserver.org/statistics/combined/tree/?date…
Check for compromise & patch!
Thank you to @ValidinLLC & @leak_ix for the collaboration!
The Shadowserver Foundation
@Shadowserver
React Server Components (CVE-2025-55182) RCE findings so far on 2025-12-05. 77664 IPs found vulnerable (based on @assetnote methodology).
IP data is being shared in our Vulnerable HTTP reports: www.shadowserver.org/what-we-do/network-reporting/vulnera…
Dashboard geo breakdown: dashboard.shadowserver.org/statistics/combined/tree/?date…
The Shadowserver Foundation
@Shadowserver
Free vulnerable IP data shared daily with 201 National CSIRTs (covering 175 countries & territories) & 10000+ other subscribed organizations worldwide in www.shadowserver.org/what-we-do/network-reporting/vulnera…
World map of vulnerable IPs:
dashboard.shadowserver.org/statistics/combined/map/?date_…
CVE-2025-55182 tracker: dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation
@Shadowserver
Like others we are seeing attacks attempting to exploit React CVE-2025-55182 at scale, incl. botnet related activity. How successful have these attacks been? You can get a view here, where we track compromised host with Next.js attacking our sensors: dashboard.shadowserver.org/statistics/honeypot/device/tim…
The Shadowserver Foundation
@Shadowserver
Attacks from bot compromised Next.js assets spiked on 2025-12-05 from the usual 100 IP baseline to close to a 1000.
Data on attacking compromised Next.js instances is shared in our Vulnerable HTTP Report www.shadowserver.org/what-we-do/network-reporting/vulnera… & Compromised IoT Report www.shadowserver.org/what-we-do/network-reporting/comprom… -
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
React Server Components (CVE-2025-55182) RCE findings so far on 2025-12-05. 77664 IPs found vulnerable (based on @assetnote methodology).
IP data is being shared in our Vulnerable HTTP reports: www.shadowserver.org/what-we-do/network-reporting/vulnera…
Dashboard geo breakdown: dashboard.shadowserver.org/statistics/combined/tree/?date… -
The Shadowserver Foundation
@Shadowserver
React Server Components (CVE-2025-55182) RCE findings so far on 2025-12-05. 77664 IPs found vulnerable (based on @assetnote methodology).
IP data is being shared in our Vulnerable HTTP reports: www.shadowserver.org/what-we-do/network-reporting/vulnera…
Dashboard geo breakdown: dashboard.shadowserver.org/statistics/combined/tree/?date…
The Shadowserver Foundation
@Shadowserver
World map: dashboard.shadowserver.org/statistics/combined/map/?date_…
CVE-2025-55182 Tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
React security advisory: react.dev/blog/2025/12/03/critical-security-vulnerability…
Next.js advisory: github.com/vercel/next.js/security/advisories/GHSA-9qr9-h…
NVD entry: nvd.nist.gov/vuln/detail/CVE-2025-55182
Assetnote detection methodology: slcyber.io/research-center/high-fidelity-detection-mechan… -
The Shadowserver Foundation
@Shadowserver
Excited that our collaboration with @VulnCheckAI (www.vulncheck.com) continues to grow as we welcome them as a new Shadowserver Alliance Partner -Silver tier!
We look forward to enhancing our joint efforts to help network defenders globally with vulnerability management.
The Shadowserver Foundation
@Shadowserver
Become a Shadowserver Alliance Partner: www.shadowserver.org/partner/
-
The Shadowserver Foundation
@Shadowserver
We shared out 10,449 entries (e-mails) affected by the JSONFormatter and CodeBeautifier leak discovered by @watchtowrcyber (see labs.watchtowr.com/stop-putting-your-passwords-into-rando…).
Data shared in a our Compromised Account Report www.shadowserver.org/what-we-do/network-reporting/comprom… (search for 2025-11-26 & compromised_account prefix)
The Shadowserver Foundation
@Shadowserver
Data is filtered by domain ccTLD for National CSIRTs. For all other subscribers it will be filtered by the domain linked to your subscription.
The Shadowserver Foundation
@Shadowserver
If you receive data from us based on IP/CIDR or ASN filtering only, please consider adding your domain to our filters. This will increase coverage of our reports to you.
If you wish to do so, please contact us via www.shadowserver.org/contact/ with details of your subscription -
Post not available here, view on X
The Shadowserver Foundation
@Shadowserver
Data is filtered by domain ccTLD for National CSIRTs. For all other subscribers it will be filtered by the domain linked to your subscription.
The Shadowserver Foundation
@Shadowserver
If you receive data from us based on IP/CIDR or ASN filtering only, please consider adding your domain to our filters. This will increase coverage of our reports to you. If you wish to do so, please contact us via www.shadowserver.org/contact/ with details of your subscription
-
The Shadowserver Foundation
@Shadowserver
Operation Endgame Season 3 Episode 2: Interlude released in time for Thanksgiving, recapping some of the #cybercrime disruption successes achieved so far, by partners working together internationally. Happy holidays - looking forward to future episodes!
www.operation-endgame.com -
The Shadowserver Foundation
@Shadowserver
We have been sharing Monsta FTP CVE-2025-34299 (pre-auth RCE) vulnerable instances for the last few weeks. Unfortunately, we still see over 780 IPs vulnerable (version based check) instances daily. Most affected: US & Slovakia: dashboard.shadowserver.org/statistics/combined/time-serie…
dashboard.shadowserver.org/statistics/combined/tree/?date…
The Shadowserver Foundation
@Shadowserver
Big thanks to @ValidinLLC on vhost identification collaboration!
Data in Vulnerable HTTP: www.shadowserver.org/what-we-do/network-reporting/vulnera…
More about Monsta FTP CVE-2025-34299 from @watchtowrcyber labs.watchtowr.com/whats-that-coming-over-the-hill-monsta…
Make sure to check for signs of compromise and patch: www.monstaftp.com/notes/ -
The Shadowserver Foundation reposted
LondonCyber
@LondonCyber
Proud to support #operationendgame 3.0! Our partner @Shadowserver helped uncover 86M stolen data items from 525K victims across 226 countries, disrupting cybercrime at scale #cybersecurity #botnettakedown 🌐
The Shadowserver Foundation
@Shadowserver
Proud to once again support our LE partners in Operation Endgame Season 3
86M stolen data items from 525K victim IPs across 226 countries included in our new Rhadamanthys Historic Bot Victims Special Report, run overnight 2025-11-12
More details:
www.shadowserver.org/news/rhadamanthys-historical-bot-inf… -
The Shadowserver Foundation
@Shadowserver
Proud to once again support our LE partners in Operation Endgame Season 3
86M stolen data items from 525K victim IPs across 226 countries included in our new Rhadamanthys Historic Bot Victims Special Report, run overnight 2025-11-12
More details:
www.shadowserver.org/news/rhadamanthys-historical-bot-inf…
The Shadowserver Foundation
@Shadowserver
Latest Operation Endgame S03E01 video "STICKY FINGERS":
www.operation-endgame.com
Europol Press Release:
www.europol.europa.eu/media-press/newsroom/news/end-of-ga…
Rhadamanthys Historic Bot Victims Special Report technical details:
www.shadowserver.org/what-we-do/network-reporting/rhadama… -
The Shadowserver Foundation
@Shadowserver
Don’t take BADCANDY from strangers ... We still see around 15 000 Cisco IOS XE devices backdoored with the implant - and frequent re-infection campaigns.
You can track those here: dashboard.shadowserver.org/statistics/combined/time-serie…
Geo breakdown of implanted Cisco IOS XE: dashboard.shadowserver.org/statistics/combined/tree/?date…
Australian Signals Directorate
@ASDGovAu
We've released a new advisory on the BADCANDY 🍬 implant that continues to haunt vulnerable Cisco IOS XE devices.
Read the full advisory to learn more about this threat in Australia and what you can do to remove and mitigate the implant 👉 cyber.gov.au/about-us/view-all-content/alerts-and-advisor…
The Shadowserver Foundation
@Shadowserver
Free IP data shared daily with National CSIRTs worldwide & subscribed impacted network owners in our Compromised Website report (tagged badcandy) www.shadowserver.org/what-we-do/network-reporting/comprom…
Act!
Background on CVE-2023-20198/CVE-2023-20273 & BadCandy implant (2 yrs back):
blog.talosintelligence.com/active-exploitation-of-cisco-i… -
The Shadowserver Foundation
@Shadowserver
We added CVE-2025-40778 BIND9 tagging (potential susceptibility to cache poisoning) to our DNS scans: www.shadowserver.org/what-we-do/network-reporting/dns-ope…
We found nearly 8898 unpatched DNS open resolvers on 2025-10-30, down to 6653 on 2025-11-01: dashboard.shadowserver.org/statistics/combined/tree/?date…
Patch info: kb.isc.org/docs/cve-2025-40778
The Shadowserver Foundation
@Shadowserver
Results are based on versions returned.
CVE-2025-40778 Public Dashboard tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
NVD entry: nvd.nist.gov/vuln/detail/CVE-2025-40778
#cybercivildefense -
The Shadowserver Foundation
@Shadowserver
Attention - Microsoft WSUS CVE-2025-59287 incidents! We are observing exploitation attempts based on a published POC. We have also began fingerprinting exposed WSUS instances (ports 8530/8531) with at least 2800 seen on 2025-10-25 (not necessarily vulnerable).
The Shadowserver Foundation
@Shadowserver
IP data is being shared in our Device ID reporting www.shadowserver.org/what-we-do/network-reporting/device-… with device_vendor set to Microsoft & device_model set to Windows Server Update Services (Open).
Geo distribution (World Map):
dashboard.shadowserver.org/statistics/iot-devices/map/?da…
Tree map view:
dashboard.shadowserver.org/statistics/iot-devices/tree/?d…
The Shadowserver Foundation
@Shadowserver
This vulnerability is on @CISACyber KEV: www.cisa.gov/known-exploited-vulnerabilities-catalog?fiel…
NVD: nvd.nist.gov/vuln/detail/CVE-2025-59287
Microsoft Advisory: msrc.microsoft.com/update-guide/vulnerability/CVE-2025-59287
HawkTrace writeup:
hawktrace.com/blog/CVE-2025-59287-UNAUTH
Huntress writeup: www.huntress.com/blog/exploitation-of-windows-server-upda…
Eye Security writeup: research.eye.security/wsus-deserialization-exploit-in-the… -
The Shadowserver Foundation
@Shadowserver
We are now sharing daily IP data on WatchGuard Fireware OS IKEv2 Out-of-Bounds Write CVE-2025-9242 vulnerable instances, with over 71 000 seen on 2025-10-18. Data shared in our Vulnerable ISAKMP reportings - www.shadowserver.org/what-we-do/network-reporting/vulnera…
Top affected: US with 23.2K instances
The Shadowserver Foundation
@Shadowserver
To search for statistics in our Public Dashboard, set source to isakmp_vulnerable, isakmp_vulnerable6 and use the 'cve-2025-9242' tag.
Geo breakdown (world map):
dashboard.shadowserver.org/statistics/combined/map/?date_…
Geo breakdown (tree map): dashboard.shadowserver.org/statistics/combined/tree/?date…
Tracker:
dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
For background and detection methodology (version based), please read: labs.watchtowr.com/yikes-watchguard-fireware-os-ikev2-out… (thanks @watchtowrcyber !)
Patch information from WatchGuard is here: www.watchguard.com/wgrd-psirt/advisory/wgsa-2025-00015
#cybercivildefense -
The Shadowserver Foundation
@Shadowserver
Proud to support our Law Enforcement partners in another successful cybercrime disruption:
Operation SIMCARTEL
Great work everyone involved 👏
www.europol.europa.eu/media-press/newsroom/news/cybercrim… -
The Shadowserver Foundation
@Shadowserver
Regarding F5 network compromise (see my.f5.com/manage/s/article/K000154696):
We are sharing daily IP data on F5 exposures in our Device Identification report www.shadowserver.org/what-we-do/network-reporting/device-… (device_vendor set to F5).
~269K IPs seen daily, nearly half in US.
Geo breakdown: dashboard.shadowserver.org/statistics/iot-devices/tree/?d…
The Shadowserver Foundation
@Shadowserver
Follow guidance from @CISACyber & @NCSC UK to identify (for example, using our reporting) and harden F5 assets:
www.cisa.gov/news-events/directives/ed-26-01-mitigate-vul…
www.ncsc.gov.uk/news/confirmed-compromise-f5-network
The Shadowserver Foundation
@Shadowserver
You can track F5 related exposure on our Public Dashboard here: dashboard.shadowserver.org/statistics/iot-devices/time-se…
-
The Shadowserver Foundation
@Shadowserver
Oracle E-Business Suite incidents: We have added CVE-2025-61882 scanning & reporting with 576 potential vulnerable IPs found on 2025-10-06. Top affected: United States.
IP data in www.shadowserver.org/what-we-do/network-reporting/vulnera…
World map view of likely vulnerable instances: dashboard.shadowserver.org/statistics/combined/map/?date_…
The Shadowserver Foundation
@Shadowserver
Tree map: dashboard.shadowserver.org/statistics/combined/tree/?date…
Tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
If you receive an alert from us, please assume compromise (see also @CISACyber KEV list)
Patch info from Oracle:
www.oracle.com/security-alerts/alert-cve-2025-61882.html
Background: www.ncsc.gov.uk/news/active-exploitation-vulnerability-af…
Please let us know of any FPs
The Shadowserver Foundation
@Shadowserver
We are also in the process of expanding Oracle E-Business Suite exposure, which you can track here: dashboard.shadowserver.org/statistics/iot-devices/time-se…
-
The Shadowserver Foundation
@Shadowserver
You can track CVE-2025-20333 & CVE-2025-20362 vulnerable (unpatched) Cisco ASA/FTD instances here - dashboard.shadowserver.org/statistics/combined/time-serie…
Around ~45K vulnerable seen on 2025-10-04
The Shadowserver Foundation
@Shadowserver
Attention!
Cisco ASA/FTD CVE-2025-20333 & CVE-2025-20362 incidents: we are now sharing daily vulnerable Cisco ASA/FTD instances in our Vulnerable HTTP reporting:
shadowserver.org/what-we-do/network-reporting/vulnerable-…
Over 48.8K unpatched IPs found on 2025-09-29. Top affected: USA
dashboard.shadowserver.org/statistics/combined/map/?date_… -
The Shadowserver Foundation
@Shadowserver
Attention!
Cisco ASA/FTD CVE-2025-20333 & CVE-2025-20362 incidents: we are now sharing daily vulnerable Cisco ASA/FTD instances in our Vulnerable HTTP reporting:
shadowserver.org/what-we-do/network-reporting/vulnerable-…
Over 48.8K unpatched IPs found on 2025-09-29. Top affected: USA
dashboard.shadowserver.org/statistics/combined/map/?date_…
The Shadowserver Foundation
@Shadowserver
dashboard.shadowserver.org/statistics/combined/tree/?date…
Cisco advisories with patch info:
CVE-2025-20333: sec.cloudapps.cisco.com/security/center/content/CiscoSecu…
CVE-2025-20362: sec.cloudapps.cisco.com/security/center/content/CiscoSecu…
More info:
@CISACyber Emergency Directive EDD-25-03: Identify and Mitigate Potential Compromise of Cisco Devices: www.cisa.gov/news-events/directives/ed-25-03-identify-and…
The Shadowserver Foundation
@Shadowserver
-
The Shadowserver Foundation
@Shadowserver
Last week we released a new daily report type, "Badsecrets Report": www.shadowserver.org/what-we-do/network-reporting/badsecr… (default severity: HIGH)
It identifies the use of known or very weak cryptographic secrets across a variety of web frameworks/platforms. 12168 IPs seen (2025-09-14) using "bad" secrets!
The Shadowserver Foundation
@Shadowserver
To identify these “bad” secrets, we use the badsecrets library from @BlackLanternLLC - github.com/blacklanternsecurity/badsecrets
Please review github.com/blacklanternsecurity/badsecrets?tab=readme-ov-… for a list of currently supported checks.
Background: blog.blacklanternsecurity.com/p/introducing-badsecrets
The Shadowserver Foundation
@Shadowserver
Dashboard links:
World map distribution of IPs:
dashboard.shadowserver.org/statistics/combined/map/?date_…
Tree map view: dashboard.shadowserver.org/statistics/combined/tree/?date…
Tracker:
dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation
@Shadowserver
FreePBX CVE-2025-57819 (CVSS 10.0) incidents: 6620 unpatched instances seen 2025-08-29, at least 386 compromised.
Dashboard links:
Vulnerable (unpatched): dashboard.shadowserver.org/statistics/combined/map/?date_…
Compromised:
dashboard.shadowserver.org/statistics/combined/map/?date_…
Check for compromise, patch - community.freepbx.org/t/security-advisory-please-lock-dow…
The Shadowserver Foundation
@Shadowserver
Raw IP data shared daily for your constituency in our Vulnerable HTTP reporting www.shadowserver.org/what-we-do/network-reporting/vulnera… tagged 'cve-2025-57819'
and
Compromised Website reporting www.shadowserver.org/what-we-do/network-reporting/comprom… tagged 'freepbx-compromised'
CVE-2025-57819 tracker :
dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
Compromised FreePBX tracker:
dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation
@Shadowserver
Citrix NetScaler CVE-2025-7775 patch rate as seen in our scans:
dashboard.shadowserver.org/statistics/combined/time-serie…
Now down from 28.2K to 12.4K. Europe patching at a faster rate than North America ...
(you can toggle overlapping/stacked time series on our Dashboard to compare)
The Shadowserver Foundation
@Shadowserver
ALERT: On 2025-08-26 over 28.2K Citrix instances were unpatched to CVE-2025-7775 RCE. There is exploitation in the wild confirmed by @CISACyber KEV.
Patch info from Citrix: support.citrix.com/support-home/kbsearch/article?articleN…
Top affected: US, Germany
Dashboard geo breakdown: dashboard.shadowserver.org/statistics/combined/tree/?date… -
The Shadowserver Foundation
@Shadowserver
ALERT: On 2025-08-26 over 28.2K Citrix instances were unpatched to CVE-2025-7775 RCE. There is exploitation in the wild confirmed by @CISACyber KEV.
Patch info from Citrix: support.citrix.com/support-home/kbsearch/article?articleN…
Top affected: US, Germany
Dashboard geo breakdown: dashboard.shadowserver.org/statistics/combined/tree/?date…
The Shadowserver Foundation
@Shadowserver
IP data is being shared in our Vulnerable HTTP reporting www.shadowserver.org/what-we-do/network-reporting/vulnera… (tagged 'cve-2025-7775')
If you receive an alert from us investigate for compromise
You can track CVE-2025-7775 patching progress on our Dashboard at: dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation
@Shadowserver
We added a new daily scan report type, Accessible GPRS Tunneling Protocol (GTP) services listing IPs with publicly exposed GTP-C (Core) hosted on port 2123/UDP & GTP-U (User) 2152/UDP.
Report format: www.shadowserver.org/what-we-do/network-reporting/accessi…
Dashboard World map view: dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
Breakdown by GTP type (2025-08-19):
GTP-C-v2 with ~255K IPs seen: dashboard.shadowserver.org/statistics/combined/tree/?date…
GTP-C-v1 with ~14K IPs seen:
dashboard.shadowserver.org/statistics/combined/tree/?date…
GTP-U with ~18K IPs seen:
dashboard.shadowserver.org/statistics/combined/tree/?date…
These services should not be exposed to the public Internet.
#cybercivildefense -
The Shadowserver Foundation
@Shadowserver
Since July 30th we are seeing an increase in scans coming from ~2200 compromised Cisco Small Business RV series routers , Linksys LRT series, & Araknis Networks (AN-300-RT-4L2W). Top affected: US but also many others.
IP data on these scans shared in www.shadowserver.org/what-we-do/network-reporting/honeypo…Post not available here, view on X
The Shadowserver Foundation
@Shadowserver
Relevant Dashboard Attacking Devices trends, with device model breakdown:
Cisco: dashboard.shadowserver.org/statistics/honeypot/device/tim…
Linksys:
dashboard.xn--shado-2u3bawserver.org/statistics/honeypot/device/time-series/?date_…
Araknis:
dashboard.shadowserver.org/statistics/honeypot/device/tim…
The Shadowserver Foundation
@Shadowserver
Tree map breakdown by country (2025-08-15):
Cisco:
dashboard.shadowserver.org/statistics/honeypot/device/tre…
Linksys:
dashboard.shadowserver.org/statistics/honeypot/device/tre…ľ––
Araknis:
dashboard.shadowserver.org/statistics/honeypot/device/tre… -
The Shadowserver Foundation
@Shadowserver
We added version based N-able N-central RMM CVE-2025-8875 & CVE-2025-8876 detection to our daily scans. 1077 IPs unpatched IPs seen on 2025-08-15. Both CVEs recently added to @CISACyber KEV.
Top affected: US, Canada, Netherlands, UK
Dashboard map view: dashboard.shadowserver.org/statistics/combined/map/?date_…
The Shadowserver Foundation
@Shadowserver
IP data shared in Vulnerable HTTP report tagged 'cve-2025-8875' & 'cve-2025-8876'): www.shadowserver.org/what-we-do/network-reporting/vulnera…
If you receive an alert from us review for signs of compromise & patch
Patch info from N-able: status.n-able.com/2025/08/13/announcing-the-ga-of-n-centr…
Dashboard tree map: dashboard.shadowserver.org/statistics/combined/tree/?date…
The Shadowserver Foundation
@Shadowserver
Dashboard CVE-2025-8875/8876 tracker link:
dashboard.shadowserver.org/statistics/combined/time-serie…
#cybercivildefense -
The Shadowserver Foundation
@Shadowserver
Still a large number of unpatched Citrix NetScaler devices likely vulnerable to CVE-2025-5777 (3312 seen) & CVE-2025-6543 (4142 seen). Both vulns are on @CISACyber KEV.
The Dutch @ncsc_nl has recently released an update related to CVE-2025-6543 activity: www.ncsc.nl/actueel/nieuws/2025/07/22/casus-citrix-kwetsb…
The Shadowserver Foundation
@Shadowserver
We see exploitation attempts related to both vulnerabilities in our sensors.
Data on vulnerable IPs shared in our Vulnerable HTTP reporting: www.shadowserver.org/what-we-do/network-reporting/vulnera… tagged 'cve-2025-5777' & 'cve-2025-6543'.
Citrix advisories:
support.citrix.com/support-home/kbsearch/article?articleN…
The Shadowserver Foundation
@Shadowserver
Dashboard links:
Tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
World map:
dashboard.shadowserver.org/statistics/combined/map/?date_…
Tree map: dashboard.shadowserver.org/statistics/combined/tree/?date… -
The Shadowserver Foundation
@Shadowserver
We added VMware ESXi CVE-2025-41236 (CVSS 9.3) version based detection to our daily scans. First added 2025-07-19 with 17,238 IPs found. Latest scan (2025-08-10) detects 16,330 unpatched IPs, which is a slow patch rate.
Top affected: France, China, US, Germany
The Shadowserver Foundation
@Shadowserver
Data in Vulnerable HTTP reporting tagged 'cve-2025-41236'
Dashboard tree map: dashboard.shadowserver.org/statistics/combined/tree/?date…
Dashboard world map: dashboard.shadowserver.org/statistics/combined/map/?date_…
CVE-2025-41236 tracker:
dashboard.shadowserver.org/statistics/combined/time-serie…
Broadcom advisory: support.broadcom.com/web/ecx/support-content-notification…
NVD entry: nvd.nist.gov/vuln/detail/CVE-2025-41236 -
The Shadowserver Foundation
@Shadowserver
We added Microsoft Exchange CVE-2025-53786 detection to our daily scans (version based). See @CISACyber Emergency Directive 25-02: www.cisa.gov/news-events/directives/ed-25-02-mitigate-mic…
Over 28K IPs unpatched (2025-08-07). Top affected: US, Germany, Russia
Dashboard world map: dashboard.shadowserver.org/statistics/combined/map/?date_…
The Shadowserver Foundation
@Shadowserver
IP data tagged 'cve-2025-53786' shared for your networks/constituencies in our Vulnerable Exchange Server reporting: www.shadowserver.org/what-we-do/network-reporting/vulnera…
Dashboard tree map:
dashboard.shadowserver.org/statistics/combined/tree/?date…
CVE-2025-53786 tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
NVD entry: nvd.nist.gov/vuln/detail/CVE-2025-53786
The Shadowserver Foundation
@Shadowserver
MS advisory: msrc.microsoft.com/update-guide/vulnerability/CVE-2025-53786
#cybercivildefense -
The Shadowserver Foundation
@Shadowserver
We added version based SonicWall SMA100 CVE-2025-40596 detection to our daily scans - at least 3200 IPs seen still unpatched! Top affected: US, Japan, Germany
Dashboard map: dashboard.shadowserver.org/statistics/combined/map/?date_…
NVD entry: nvd.nist.gov/vuln/detail/CVE-2025-40596
SonicWall advisory: psirt.global.sonicwall.com/vuln-detail/SNWLID-2025-0012
The Shadowserver Foundation
@Shadowserver
IP data tagged 'cve-2025-40596' in our Vulnerable HTTP reporting: www.shadowserver.org/what-we-do/network-reporting/vulnera…
CVE-2025-40596 tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
#cybercivildefense -
The Shadowserver Foundation
@Shadowserver
PaperCut CVE-2023-2533 was recently added to the @CISACyber KEV catalog. We added version based detection of unpatched IPs with 129 seen on 2025-08-03.
dashboard.shadowserver.org/statistics/combined/tree/?date…
We also scan for CVE-2023-39143 & CVE-2023-27350. Data in Vulnerable HTTP: www.shadowserver.org/what-we-do/network-reporting/vulnera…
The Shadowserver Foundation
@Shadowserver
If you receive an alert from us, check for compromise and update your PaperCut instance to the latest version
www.papercut.com/kb/Main/CommonSecurityQuestions/ -
The Shadowserver Foundation
@Shadowserver
We’re excited to welcome SURFcert to the Shadowserver Alliance as a Bronze Tier Partner!
Together with SURFcert and fellow Alliance Partners, we’re making the Internet more secure for all.
Read more about SURFcert: www.surf.nl/en
The Shadowserver Foundation
@Shadowserver
Become a Shadowserver Alliance Partner today: www.shadowserver.org/partner/
-
The Shadowserver Foundation
@Shadowserver
SharePoint situational update: In collaboration with @ValidinLLC & @certbund we improved vhost & version detection of SharePoint instances, resulting in ~17K IPs observed exposed. 840 with CVE-2025-53770 - version based detection only. At least 20 with webshells.
Post not available here, view on X
The Shadowserver Foundation
@Shadowserver
Compromised SharePoint data in Compromised Website report (tag is sharepoint-compromised)
www.shadowserver.org/what-we-do/network-reporting/comprom…
The Shadowserver Foundation
@Shadowserver
Public Dashboard links:
CVE-2025-53770 tracker:
dashboard.shadowserver.org/statistics/combined/time-serie…
CVE-2025-53770 vulnerable breakdown:
dashboard.shadowserver.org/statistics/combined/tree/?date…
Compromised SharePoint (IPs only, not vhosts or orgs):
dashboard.shadowserver.org/statistics/combined/tree/?date… -
The Shadowserver Foundation
@Shadowserver
Emerging threats are countered most effectively when IR teams can share technical indicators to improve detection - helping identify, notify & remediate more victims.
Great example: CVE-2025-25257 & FortiWeb shells. @NCA_KSA & @cybercentre_ca both helped protect victims globallyPost not available here, view on X
The Shadowserver Foundation
@Shadowserver
If you receive free daily network reports from us about vulnerable/compromised devices and can share feedback on technical artifacts, you can also help improve detection and protection for everyone. Join us and become a part of a collaborative, virtuous defensive circle
The Shadowserver Foundation
@Shadowserver
Double kudos to @NCA_KSA for sharing additional compromised FortiWeb webshell paths over the past 2 weeks - further improving the quality and quantity of critical free daily cyber threat intelligence that we can provide to everyone 👏
Subscribe & Protect:
www.shadowserver.org/what-we-do/network-reporting/ -
The Shadowserver Foundation
@Shadowserver
Thanks to a scan conducted by @leak_ix, we have shared SharePoint IPs confirmed vulnerable to CVE-2025-53770, CVE-2025-53771.
424 SharePoint IPs found on 2025-07-23. One-off data in our Vulnerable HTTP report - www.shadowserver.org/what-we-do/network-reporting/vulnera…
Tree map: dashboard.shadowserver.org/statistics/combined/tree/?date…
The Shadowserver Foundation
@Shadowserver
Data tagged ‘leakix-vulnerable-sharepoint’.
More information & guidance on the SharePoint incidents:
- research.eye.security/sharepoint-under-siege/
- msrc.microsoft.com/blog/2025/07/customer-guidance-for-sha…
- www.microsoft.com/en-us/security/blog/2025/07/22/disrupti… -
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
Alert: SharePoint CVE-2025-53770 incidents! In collaboration with @eyesecurity & @watchtowrcyber we are notifying compromised parties. Read: research.eye.security/sharepoint-under-siege/
~9300 Sharepoint IPs seen exposed daily (just population, no vulnerability assessment): dashboard.shadowserver.org/statistics/iot-devices/tree/?d… -
The Shadowserver Foundation
@Shadowserver
Alert! We are scanning for unpatched CrushFTP instances vulnerable to CVE-2025-54309. This vulnerability is exploited in the wild - www.crushftp.com/crush11wiki/Wiki.jsp?page=CompromiseJuly…
We see 1040 instances unpatched on 20th July. Top countries affected: US, Germany, Canada
dashboard.shadowserver.org/statistics/combined/map/?date_…
The Shadowserver Foundation
@Shadowserver
We share IP data tagged 'cve-2025-54309' in our Vulnerable HTTP report www.shadowserver.org/what-we-do/network-reporting/vulnera…
Affected versions:
All version 10 below 10.8.5.
All version 11 below 11.3.4_23.
Geo tree map breakdown: dashboard.shadowserver.org/statistics/combined/tree/?date…
CVE-2025-54309 tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
If you receive an alert from us make sure to review for compromise and update!
-
The Shadowserver Foundation
@Shadowserver
Alert: SharePoint CVE-2025-53770 incidents! In collaboration with @eyesecurity & @watchtowrcyber we are notifying compromised parties. Read: research.eye.security/sharepoint-under-siege/
~9300 Sharepoint IPs seen exposed daily (just population, no vulnerability assessment): dashboard.shadowserver.org/statistics/iot-devices/tree/?d…
The Shadowserver Foundation
@Shadowserver
IP data of exposed instances in our Device Identification report (device_model will be set to SharePoint): www.shadowserver.org/what-we-do/network-reporting/device-…
More updates to follow. -
The Shadowserver Foundation reposted
LondonCyber
@LondonCyber
🚨 BREAKING 🚨
Supported by @Shadowserver, the @Europol-led Operation Eastwood dismantles pro-Russian cybercrime group ‘NoName057(16), behind DDoS attacks on Ukraine 🇺🇦 and allies.
🔒 100+ systems shut down
👮♀️ Arrests in 🇫🇷&🇪🇸
🎯 6 Russian nationals wanted
The Shadowserver Foundation
@Shadowserver
Proud to support our international LE partners in @Europol /@Eurojust coordinated Operation Eastwood - another successful public/private partnership cyber threat disruption!
Europol
@Europol
🚨 Operation Eastwood targets pro-Russian cybercrime network NoName057(16) and shuts down over one hundred criminal servers in global operation.
Read more in our press release ⤵️
www.europol.europa.eu/media-press/newsroom/news/global-op… -
The Shadowserver Foundation
@Shadowserver
Proud to support our international LE partners in @Europol /@Eurojust coordinated Operation Eastwood - another successful public/private partnership cyber threat disruption!
Europol
@Europol
🚨 Operation Eastwood targets pro-Russian cybercrime network NoName057(16) and shuts down over one hundred criminal servers in global operation.
Read more in our press release ⤵️
www.europol.europa.eu/media-press/newsroom/news/global-op… -
The Shadowserver Foundation
@Shadowserver
We are sharing Fortinet FortiWeb instances compromised with webshells likely via CVE-2025-25257. We see 77 cases on 2025-07-15, down from 85 on 2025-07-14. CVE-2025-25257 exploitation activity observed since Jul 11th.
Tree map overview (compromised): dashboard.shadowserver.org/statistics/combined/tree/?date…Post not available here, view on X
The Shadowserver Foundation
@Shadowserver
IP data on compromised instances shared in our Compromised Website report tagged 'fortiweb-compromised': www.shadowserver.org/what-we-do/network-reporting/comprom…
IP data on exposed instances is in our Device ID report: www.shadowserver.org/what-we-do/network-reporting/device-… (device model is set to FortiWeb Management Interface)
The Shadowserver Foundation
@Shadowserver
Fortinet advisory: fortiguard.fortinet.com/psirt/FG-IR-25-151
-
The Shadowserver Foundation
@Shadowserver
Since start of July we are seeing Wing FTP Server CVE-2025-47812 RCE exploitation attempts. We are fingerprinting exposed Wing FTP Server instances to establish the potentially vulnerable population.
We see ~2000 IPs exposed (no vulnerability checks): dashboard.shadowserver.org/statistics/iot-devices/map/?da….
The Shadowserver Foundation
@Shadowserver
Tree map view of Wing FTP Server population: dashboard.shadowserver.org/statistics/iot-devices/tree/?d…
IP data on Wing FTP Server population is shared in our Device Identification reporting www.shadowserver.org/what-we-do/network-reporting/device-…
The Shadowserver Foundation
@Shadowserver
If running an older version please make sure to check for signs of compromise & update to version 7.4.4 of Wing FTP Server www.wftpserver.com/download.htm
Please note vulnerability details are public -
The Shadowserver Foundation
@Shadowserver
Numbers steadily going down but still a lot out there ...
mRr3b00t
@UK_Daniel_Card
Compromised Fortigates.... by country.....
-
The Shadowserver Foundation
@Shadowserver
Live Flax Typhoon Raptor Train botnet sinkholing data now available through @shadowserver free daily Sinkhole Event and Sinkhole HTTP Event network reports:
www.shadowserver.org/what-we-do/network-reporting/sinkhol…
events tagged as "raptor-train"
Remediate current infections!
The Shadowserver Foundation
@Shadowserver
Current daily Flax Typhoon Raptor Train country level sinkhole statistics available on our public Dashboard:
dashboard.shadowserver.org/statistics/combined/time-serie…
Tree map:
dashboard.shadowserver.org/statistics/combined/tree/?date…
World map:
dashboard.shadowserver.org/statistics/combined/map/?date_…
The Shadowserver Foundation
@Shadowserver
Links to Raptor Train nCSIRT advisories, Indicators of Compromise and remediation guidance available here:
www.shadowserver.org/what-we-do/network-reporting/raptor-… -
The Shadowserver Foundation
@Shadowserver
New Special Report run in collaboration with LE partners on historical Flax Typhoon Raptor Train botnet infections:
www.shadowserver.org/what-we-do/network-reporting/raptor-…
Filename prefix: 2025-07-07-special
732545 events, 179539 IPs, 2750 ASNs, 143 countries
Check your reports for historical compromises
The Shadowserver Foundation
@Shadowserver
Country level statistics for one-off Special Report on historical Flax Typhoon Raptor Train botnet infections available via @shadowserver public Dashboard:
Treemap:
dashboard.shadowserver.org/statistics/combined/tree/?date…
World map:
dashboard.shadowserver.org/statistics/combined/map/?date_… -
The Shadowserver Foundation
@Shadowserver
We are scanning for Citrix NetScaler CVE-2025-5777 (since 19/06) & CVE-2025-6543 (since 27/06) vulnerabilities.
1289 & 2100 IPs still seen unpatched as of 2025-06-29. Top: US & DE
Tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
Advisories:
support.citrix.com/support-home/kbsearch/article?articleN…
The Shadowserver Foundation
@Shadowserver
IP data shared in our Vulnerable HTTP report - www.shadowserver.org/what-we-do/network-reporting/vulnera…
Tree map view of CVE-2025-5777: dashboard.shadowserver.org/statistics/combined/tree/?date…
Tree map view of CVE-2025-6543:
dashboard.shadowserver.org/statistics/combined/tree/?date… -
The Shadowserver Foundation reposted
LondonCyber
@LondonCyber
🇬🇧 Cyber Resilience Programmes joined #opserengeti2 kick-off in Seychelles with @INTERPOL_Cyber, @AFRIPOLOfficial & @Shadowserver.
🎯 Focus: High-impact cyber threats in Africa incl. BEC, phishing, DDoS & darknet crime.
#cybercrime
INTERPOL_Cyber
@INTERPOL_Cyber
Operation Serengeti 2.0 kicks off in Seychelles! #interpol, African nations & global partners unite to fight cybercrime through stronger regional cooperation, strategic planning, capacity building & intelligence sharing - a bold step for Africa’s digital security. #afjoc #fcdo
-
The Shadowserver Foundation
@Shadowserver
Shadowserver, a member of the Common Good Cyber secretariat, is proud to help launch the Common Good Cyber Fund announced today. Special thanks to the UK and Canada for investing in the Fund and continuing to provide their steadfast support.
commongoodcyber.org/news/common-good-cyber-fund-announcem…
The Shadowserver Foundation
@Shadowserver
-
The Shadowserver Foundation
@Shadowserver
For the last few days, we are reporting out Roundcube CVE-2025-49113 vulnerable instances (allows remote code execution by authenticated users). Roundcube vulnerabilities have been frequently used for targeted attacks by possible state actors. We see ~84K unpatched worldwide.
The Shadowserver Foundation
@Shadowserver
Make sure to update to versions 1.6.11 or 1.5.10: roundcube.net/news/2025/06/01/security-updates-1.6.11-and…
Public exploit PoC is available.
Dashboard map view: dashboard.shadowserver.org/statistics/combined/map/?date_…
CVE-2025-49113 tracker:
dashboard.shadowserver.org/statistics/combined/time-serie…
IP data in our Vulnerable HTTP report: www.shadowserver.org/what-we-do/network-reporting/vulnera…
The Shadowserver Foundation
@Shadowserver
NVD entry (CVSS 9.9 from MITRE): nvd.nist.gov/vuln/detail/CVE-2025-49113
-
The Shadowserver Foundation
@Shadowserver
We are happy to support our LE partners!
www.justice.gov/usao-edva/pr/us-government-seizes-approxi… -
The Shadowserver Foundation
@Shadowserver
We have shared a Special Report on IPs infected with Latrodectus malware during 2025-04-26 to 2025-05-20. This is one of the results of the continued international Law Enforcement action called Operation Endgame Season 2.0
Over 44K infected IPs seen: dashboard.shadowserver.org/statistics/combined/map/?date_…
The Shadowserver Foundation
@Shadowserver
Check your reports! IP data shared with '2025-05-28-special' file prefix for your constituency.
Please see the Special Report page on Latrodectus Historical infections: www.shadowserver.org/what-we-do/network-reporting/icedid-…
Operation Endgame Season 2.0 (announced 23rd May 2025): www.europol.europa.eu/media-press/newsroom/news/operation…
The Shadowserver Foundation
@Shadowserver
Data can be viewed on our Dashboard by selecting the source 'special' with the date 2025-05-28.
Dashboard tree map country breakdown: dashboard.shadowserver.org/statistics/combined/tree/?date… -
The Shadowserver Foundation reposted
OEA Ciberseguridad
@OEA_Cyber
🌐 @OEA_Cyber llevó a cabo la Reunión Regional de Comunidades de Ciberseguridad en América Latina y el Caribe, junto a @Shadowserver, @FIRSTdotOrg, @lacnic, @ITU, y @CCNCERT en el marco de las Jornadas #sticpanamÁ 🤝 Un espacio clave para alinear esfuerzos, identificar desafíos comunes y fortalecer la colaboración regional. Como actor de articulación estratégica, desde #csirtamericas seguimos apostando por la cooperación como pilar de la resiliencia digital en las Américas. #ciberseguridad #cooperaciónRegional
-
The Shadowserver Foundation
@Shadowserver
You can also track CVE-2025-4427 exploitation attempts as seen by our honeypot sensors on our Dashboard: dashboard.shadowserver.org/statistics/honeypot/vulnerabil…
The Shadowserver Foundation
@Shadowserver
We are also scanning for Ivanti EPMM instances likely vulnerable (unpatched) to CVE-2025-4427 which can be chained with CVE-2025-4428 for RCE.
First scans found 940 instances (2025-05-15), down to 798 (2025-05-18).
Geo breakdown: dashboard.shadowserver.org/statistics/combined/tree/?date… -
The Shadowserver Foundation
@Shadowserver
We are also scanning for Ivanti EPMM instances likely vulnerable (unpatched) to CVE-2025-4427 which can be chained with CVE-2025-4428 for RCE.
First scans found 940 instances (2025-05-15), down to 798 (2025-05-18).
Geo breakdown: dashboard.shadowserver.org/statistics/combined/tree/?date…
The Shadowserver Foundation
@Shadowserver
IP data in www.shadowserver.org/what-we-do/network-reporting/vulnera… tagged as 'cve-2025-4427'.
Detection is based on non-intrusive check provided by @watchtowrcyber
CVE-2025-4427 tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
If you receive an alert, please make sure to review for any compromise - CVE-2025-4427/CVE-2025-4428 are exploited in the wild.
Patch info from Ivanti: forums.ivanti.com/s/article/Security-Advisory-Ivanti-Endp…
Background on vulnerabilities: labs.watchtowr.com/expression-payloads-meet-mayhem-cve-20… -
The Shadowserver Foundation reposted
CERT
@certlv
cert.lv un @Shadowserver – veiksmīga sadarbība jaunā kvalitātē! 🌐🤝 Esam kļuvuši par Shadowserver “Bronze Tier” partneri! Tas ir vēl viens mērķtiecīgs solis, lai stiprinātu kiberdrošību Latvijā un veicinātu globālo sadarbību. 🛡️🇱🇻
The Shadowserver Foundation
@Shadowserver
We’re excited to announce that @certlv (cert.lv - National CSIRT of Latvia) has joined the Shadowserver Alliance as a Bronze Tier Partner!
Together we will raise the bar on cybersecurity.
Read more about cert.lv: cert.lv/en/ -
The Shadowserver Foundation
@Shadowserver
We’re excited to announce that @certlv (cert.lv - National CSIRT of Latvia) has joined the Shadowserver Alliance as a Bronze Tier Partner!
Together we will raise the bar on cybersecurity.
Read more about cert.lv: cert.lv/en/
The Shadowserver Foundation
@Shadowserver
Become a Shadowserver Alliance partner today: www.shadowserver.org/partner/
-
The Shadowserver Foundation
@Shadowserver
We are sharing ScreenConnect instances likely vulnerable to CVE-2025-3935 (CVSS 8.1, versions 25.2.3 & earlier versions may be susceptible to a ViewState code injection).
Patch info: www.connectwise.com/company/trust/security-bulletins/scre…
685 instances still unpatched on 2025-05-07:
dashboard.shadowserver.org/statistics/combined/map/?date_…
The Shadowserver Foundation
@Shadowserver
CVE-2025-3935 Tracker - dashboard.shadowserver.org/statistics/combined/time-serie…
IP data tagged 'cve-2025-3935' in our Vulnerable HTTP report www.shadowserver.org/what-we-do/network-reporting/vulnera… -
The Shadowserver Foundation
@Shadowserver
The dashboard has been built thanks to UK FCDO funding (@LondonCyber) and holds 2 years worth of aggregated Shadowserver data for all to explore!
The Shadowserver Foundation
@Shadowserver
Check out our latest Dashboard updates that now highlight compromised devices & post-exploitation frameworks/C2s discovered in scans, as well as various functionality improvements:
dashboard.shadowserver.org
As a reminder we have 76 languages supported! -
The Shadowserver Foundation
@Shadowserver
We are sharing SysAid instances likely vulnerable to CVE-2025-2775, CVE-2025-2776, CVE-2025-2777 (XXEs) any of which combined with CVE-2025-2778 allows for RCE.
77 IPs found unpatched so far (version check).
Install updates from SysAid (from March!) documentation.sysaid.com/docs/24-40-60
The Shadowserver Foundation
@Shadowserver
IP data for your network shared in our Accessible HTTP www.shadowserver.org/what-we-do/network-reporting/accessi… & Accessible SSL www.shadowserver.org/what-we-do/network-reporting/accessi… reports with 'sysaid-vulnerable' tag.
Starting tomorrow data will be in our Vulnerable HTTP report with 'cve-2025-2775' tag www.shadowserver.org/what-we-do/network-reporting/vulnera…
The Shadowserver Foundation
@Shadowserver
We would like to thank @watchtowrcyber for the collaboration. Background: labs.watchtowr.com/sysowned-your-friendly-rce-support-tic…
-
The Shadowserver Foundation
@Shadowserver
Check out our latest Dashboard updates that now highlight compromised devices & post-exploitation frameworks/C2s discovered in scans, as well as various functionality improvements:
dashboard.shadowserver.org
As a reminder we have 76 languages supported! -
The Shadowserver Foundation
@Shadowserver
Attention! We are sharing SAP NetWeaver instances vulnerable to CVE-2025-31324 unauth upload (CVSS 10.0). 454 IPs found vulnerable on 2025-04-26. If you receive an alert from us, make sure to check for signs of compromise (incl. webshells).
World Map: dashboard.shadowserver.org/statistics/combined/map/?map_t…
The Shadowserver Foundation
@Shadowserver
Patch info from SAP: me.sap.com/notes/3594142
Data in www.shadowserver.org/what-we-do/network-reporting/vulnera…
Top affected - US 149, India 50, Australia 37: dashboard.shadowserver.org/statistics/combined/tree/?day=…
CVE-2025-31324 tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
Background details on CVE-2025-31324: redrays.io/blog/critical-sap-netweaver-vulnerability-cve-… -
The Shadowserver Foundation reposted
WACREN
@WACREN
In the #cybersecurity session at #wacren2025, panel members shared rich perspectives and agreed on the nexus and cooperation needed between nCSIRTs, NREN #csirts, academic institutions and policymakers and every player in-between. #trustbrokerafrica is well positioned to enable this as articulated by @OmoOaiya. Thanks to @CsirtOpen (Don Stikvoort), @ecowas_cedeao (Folake Olagunju), @Shadowserver (Piotr Kijewski), @NRD__CS (Dr. Vilius Benetis) and CINERI 🇸🇳for joining the panel.
-
The Shadowserver Foundation reposted
Identity Digital Inc
@IdentityDig
📣 We have exciting news to share! Identity Digital has joined the @Shadowserver Foundation to combat malicious activity and neutralize emerging threats.
This partnership represents a decisive step forward in proactively protecting users from increasingly sophisticated online threats. 🤝🛡️
Learn more: www.businesswire.com/news/home/20250415301851/en/Identity…
#cybersecurity #domains -
The Shadowserver Foundation
@Shadowserver
We’re excited to announce that @IdentityDig has joined the Shadowserver Alliance as a Bronze Tier Partner!
Together we will work to make the Internet safer and more secure.
Read more about Identity Digital: www.identity.digital/company
The Shadowserver Foundation
@Shadowserver
Become a Shadowserver Alliance partner today: www.shadowserver.org/partner/
-
The Shadowserver Foundation
@Shadowserver
Urgent: Check your Compromised Website Report for critical events tagged “fortinet-compromised” and follow @Fortinet's mitigation advice on compromised devices:
www.fortinet.com/blog/psirt-blogs/analysis-of-threat-acto…
Data available from 2025-04-11+
www.shadowserver.org/what-we-do/network-reporting/comprom…
The Shadowserver Foundation
@Shadowserver
Detected compromised Fortinet devices:
dashboard.shadowserver.org/statistics/combined/tree/?day=…
dashboard.shadowserver.org/statistics/combined/map/?map_t…
dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
National CSIRT advisories:
www.cisa.gov/news-events/alerts/2025/04/11/fortinet-relea…
www.cyber.gov.au/about-us/view-all-content/alerts-and-adv…
www.cert.govt.nz/advisories/malicious-activity-due-to-pre… -
The Shadowserver Foundation
@Shadowserver
Ivanti Connect Secure CVE-2025-22457 (stack-based buffer overflow allowing for unauth RCE): we see over 5113 instances unpatched in our scan for 2025-04-06. This vulnerability has been observed exploited in the wild and is on @CISACyber KEV.
World Map: dashboard.shadowserver.org/statistics/combined/map/?map_t…
The Shadowserver Foundation
@Shadowserver
IP data shared in our Vulnerable HTTP report tagged 'cve-2025-22457'. As part of work on tagging this vuln, we improved our fingerprinting of Ivanti Connect Secure with a little help from some friends!
www.shadowserver.org/what-we-do/network-reporting/vulnera…
CVE-2025-22457 tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
Ivanti advisory and patch info: forums.ivanti.com/s/article/April-Security-Advisory-Ivant…
Note that according to Ivanti, the vulnerability was patched in a Feb 11, 2025 release. However, a large set of what is affected are older Pulse Connect Secure 9.x (end-of-support as of December 31, 2024) without a patch. -
The Shadowserver Foundation
@Shadowserver
We are observing CrushFTP CVE-2025-2825 exploitation attempts based on publicly available PoC exploit code. You can track attempts on our Dashboard at dashboard.shadowserver.org/statistics/honeypot/vulnerabil…
Still 1512 unpatched instances vulnerable to CVE-2025-2825 seen on 2025-03-30
dashboard.shadowserver.org/statistics/honeypot/vulnerabil…
The Shadowserver Foundation
@Shadowserver
We are sharing unpatched CrushFTP instances likely vulnerable to CVE-2025-2825 (CVSS 9.8) that may allow unauthenticated remote attackers to bypass authentication via HTTP(S) requests. We see ~1800 unpatched instances worldwide, with over 900 in the US.
dashboard.shadowserver.org/statistics/combined/map/?map_t…
The Shadowserver Foundation
@Shadowserver
CrushFTP versions 10.0.0 through 10.8.3 and 11.0.0 through 11.3.0 are affected. Make sure to check for signs of compromise and update: crushftp.com/crush11wiki/Wiki.jsp?page=Update
-
The Shadowserver Foundation
@Shadowserver
We are sharing unpatched CrushFTP instances likely vulnerable to CVE-2025-2825 (CVSS 9.8) that may allow unauthenticated remote attackers to bypass authentication via HTTP(S) requests. We see ~1800 unpatched instances worldwide, with over 900 in the US.
dashboard.shadowserver.org/statistics/combined/map/?map_t…
The Shadowserver Foundation
@Shadowserver
IP data shared in our Vulnerable HTTP report, tagged 'cve-2025-2825': www.shadowserver.org/what-we-do/network-reporting/vulnera…
CrushFTP versions 10.0.0 through 10.8.3 & 11.0.0 through 11.3.0 are affected. Make sure to update: www.crushftp.com/crush11wiki/Wiki.jsp?page=Update
Tree map geo breakdown: dashboard.shadowserver.org/statistics/combined/tree/?day=…
The Shadowserver Foundation
@Shadowserver
CVE-2025-2825 tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
Switch on automatic updates if possible! -
The Shadowserver Foundation
@Shadowserver
For the last few days we are also scanning & reporting out exposed Ingress NGINX Controller for Kubernetes (Admission Controller feature). These may possibly be also vulnerable to CVE-2025-1974 & other recently disclosed vulnerabilities.
We see around 4000 IPs exposed.Post not available here, view on X
The Shadowserver Foundation
@Shadowserver
Vulnerable HTTP report: www.shadowserver.org/what-we-do/network-reporting/vulnera…
Device Identification (device model is set to Kubernetes Admission Controller): www.shadowserver.org/what-we-do/network-reporting/device-…
Dashboard tree map view: dashboard.shadowserver.org/statistics/combined/tree/?day=…
Dashboard tracker:
dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
Patch info: kubernetes.io/blog/2025/03/24/ingress-nginx-cve-2025-1974/
Background: www.wiz.io/blog/ingress-nginx-kubernetes-vulnerabilities -
The Shadowserver Foundation
@Shadowserver
We are excited to welcome Arctic Security @ArcticSecurity to the Shadowserver Alliance (Silver tier)!
We look forward to this partnership to raise the bar on cybersecurity.
Learn more about Arctic Security: www.arcticsecurity.com
The Shadowserver Foundation
@Shadowserver
Become a Shadowserver Alliance Partner today: www.shadowserver.org/partner/
-
The Shadowserver Foundation
@Shadowserver
We are scanning & reporting out VMware ESXi CVE-2025-22224 vulnerable instances ("a malicious actor with local admin privileges on a virtual machine may exploit this to execute code as virtual machine's VMX process running on host").
Nearly 41.5K found vulnerable on 2025-03-04.
The Shadowserver Foundation
@Shadowserver
IP data shared in our Vulnerable HTTP report, tagged 'cve-2025-22224' : www.shadowserver.org/what-we-do/network-reporting/vulnera…
Dashboard tree map breakdown: dashboard.shadowserver.org/statistics/combined/tree/?day=…
Track patching progress here: dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
This vulnerability is known to be exploited in the wild and on @CISACyber KEV: www.cisa.gov/known-exploited-vulnerabilities-catalog
Patch info from Broadcom: support.broadcom.com/web/ecx/support-content-notification… -
The Shadowserver Foundation
@Shadowserver
We started scanning for IoT devices compromised by the Eleven11bot DDoS botnet, with ~86.4K discovered on 2025-03-02. IP data is shared daily in our Compromised IoT report www.shadowserver.org/what-we-do/network-reporting/comprom…
Top affected: US (24.7K), UK (10.8K).
Dashboard map view: dashboard.shadowserver.org/statistics/combined/map/?map_t…
The Shadowserver Foundation
@Shadowserver
For background, please see Nokia Deepfield Emergency Response Team (ERT) announcement: infosec.exchange/@deepfield/114086567369833954
The Shadowserver Foundation
@Shadowserver
Dashboard breakdown by US state:
dashboard.shadowserver.org/statistics/combined/map/region… -
The Shadowserver Foundation
@Shadowserver
We are scanning for & reporting Nakivo Backup & Replication CVE-2024-48248 (arbitrary file read) vulnerable instances in our Vulnerable HTTP report: www.shadowserver.org/what-we-do/network-reporting/vulnera….
~208 vulnerable instances seen 2025-02-26
Dashboard map view: dashboard.shadowserver.org/statistics/combined/tree/?day=…
The Shadowserver Foundation
@Shadowserver
Data is tagged 'vulnerable-nakivo-backup' since 2025-02-13 thanks to @watchtowrcyber.
We have also added the 'cve-2024-48248' tag as well starting today.
If you run Nakivo, make sure to update your instance to the latest version! (vulnerability was silently patched 2024-11-04).
The Shadowserver Foundation
@Shadowserver
For an in-depth analysis of the vulnerability, please read the @watchtowrcyber blog at labs.watchtowr.com/the-best-security-is-when-we-all-agree…
-
The Shadowserver Foundation
@Shadowserver
We started scanning & reporting out Ivanti Connect Secure CVE-2025-22467 vulnerable (unpatched) instances in our daily feeds. ~2850 IP seen unpatched worldwide in our daily scans.
Top affected: US (852) & Japan (384)
Dashboard world map view: dashboard.shadowserver.org/statistics/combined/map/?map_t…
The Shadowserver Foundation
@Shadowserver
CVE-2025-22467 is stack-based buffer overflow in Ivanti Connect Secure before version 22.7R2.6 allows a remote authenticated attacker to achieve remote code execution.
This is a version based check.
See advisory from Ivanti on this & other vulns: forums.ivanti.com/s/article/February-Security-Advisory-Iv…
The Shadowserver Foundation
@Shadowserver
We share IP level data on CVE-2025-22467 in our Vulnerable HTTP report for your network/constituency: www.shadowserver.org/what-we-do/network-reporting/vulnera…
Not receiving our free daily feeds? Subscribe here: www.shadowserver.org/what-we-do/network-reporting/get-rep… -
The Shadowserver Foundation
@Shadowserver
At last week’s UN #oewg on ICT, @Shadowserver and @GlobalCyberAlln represented @CommonGoodCyber on a panel discussing “Cybersecurity for the Common Good: Strengthening Nonprofits Engagement in a Permanent UN Mechanism on ICT Security” hosted by @EU_ISS
The Shadowserver Foundation
@Shadowserver
Read more about Common Good Cyber: commongoodcyber.org
-
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
Excited to publish our 2024 Highlights of the Year in Review, covering improvements to public benefit services, response to emerging threats/vulnerabilities, reporting to nCSIRTs & system defenders globally, LE support & cyber capacity building efforts
www.shadowserver.org/news/shadowserver-2024-highlights-of… -
The Shadowserver Foundation
@Shadowserver
We are excited to collaborate with @WACREN and Deutsche Gesellschaft für Internationale Zusammenarbeit (GIZ) GmbH on our joint project to strengthen the cyber resilience, situational awareness and incident response of the West African research & education sector!
WACREN
@WACREN
WACREN, @Shadowserver and Deutsche Gesellschaft für Internationale Zusammenarbeit (GIZ) are collaborating on a project to strengthen Africa’s research & education sector against cyber threats! 🌍🔐 The project will enhance real-time response and catalyse decision-making in NREN and national African #csirts across the WACREN region! More info here - wacren.net/en/news/wacren-in-a-new-project-to-strengthen-… 🚀 📢 First training at #wacren2025 in Dakar! Stay tuned! 🔗 #cybersecurity #africa
-
The Shadowserver Foundation reposted
WACREN
@WACREN
WACREN, @Shadowserver and Deutsche Gesellschaft für Internationale Zusammenarbeit (GIZ) are collaborating on a project to strengthen Africa’s research & education sector against cyber threats! 🌍🔐 The project will enhance real-time response and catalyse decision-making in NREN and national African #csirts across the WACREN region! More info here - wacren.net/en/news/wacren-in-a-new-project-to-strengthen-… 🚀 📢 First training at #wacren2025 in Dakar! Stay tuned! 🔗 #cybersecurity #africa
-
The Shadowserver Foundation reposted
LondonCyber
@LondonCyber
We are proud to partner with one of the best cyber defenders, continuing to keep the internet safe for us all and making cybersecurity accessible. @Shadowserver
The Shadowserver Foundation
@Shadowserver
Excited to publish our 2024 Highlights of the Year in Review, covering improvements to public benefit services, response to emerging threats/vulnerabilities, reporting to nCSIRTs & system defenders globally, LE support & cyber capacity building efforts
www.shadowserver.org/news/shadowserver-2024-highlights-of… -
The Shadowserver Foundation
@Shadowserver
Excited to publish our 2024 Highlights of the Year in Review, covering improvements to public benefit services, response to emerging threats/vulnerabilities, reporting to nCSIRTs & system defenders globally, LE support & cyber capacity building efforts
www.shadowserver.org/news/shadowserver-2024-highlights-of…
The Shadowserver Foundation
@Shadowserver
We would like to take this opportunity to thank all of our supporters, particularly the United Kingdom’s Foreign, Commonwealth and Development Office (UK FCDO @LondonCyber), Craig Newmark @craignewmark, all of our Shadowserver Alliance partners and all other donors & sponsors
The Shadowserver Foundation
@Shadowserver
Become an Alliance partner today: www.shadowserver.org/partner/
-
The Shadowserver Foundation
@Shadowserver
Not only new vulnerabilities are exploited in the wild. At the start of Feb, @CISACyber added CVE-2018-19410 Paessler PRTG Network Monitor Local File Inclusion Vulnerability (CVSS 9.8) to its KEV list.
We scan/report vulnerable IPs daily, with 2149 found on 2025-02-15.
The Shadowserver Foundation
@Shadowserver
Top affected: Bangladesh (600), Indonesia (252) & Brazil (250)
Dashboard World map view: dashboard.shadowserver.org/statistics/combined/map/?map_t…
CVE-2018-19410 tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
IP data shared daily for your network/constituency in our Vulnerable HTTP report: www.shadowserver.org/what-we-do/network-reporting/vulnera…
The Shadowserver Foundation
@Shadowserver
If you receive a report from us with a vulnerable instance, make sure to check for signs of compromise and update to the latest version: www.paessler.com/prtg/history/stable
-
The Shadowserver Foundation
@Shadowserver
Many Palo Alto CVE-2025-0108 attempts seen since 4 am UTC 2024-02-13 in our honeypots, with 19 source IPs seen attempting the use of a recent PoC published for this vulnerability (with a few creative exceptions)
Patch info: security.paloaltonetworks.com/CVE-2025-0108
The Shadowserver Foundation
@Shadowserver
Please make sure to take your management interface off the public Internet ...
You can track exposure of PAN-OS mgmt interfaces here (~3500 seen exposed): dashboard.shadowserver.org/statistics/iot-devices/time-se…
The Shadowserver Foundation
@Shadowserver
Please note we share info on exposed Palo Alto mgmt interfaces (IPs filtered for your network/constituency) daily in our Device Identification report: www.shadowserver.org/what-we-do/network-reporting/device-…
-
The Shadowserver Foundation
@Shadowserver
We are excited to welcome CERT Orange Polska @CERT_OPL as a new Shadowserver Alliance partner (Bronze tier)!
We look forward to raising the bar on cybersecurity together.
Read more about CERT Orange Polska: cert.orange.pl
The Shadowserver Foundation
@Shadowserver
Become a Shadowserver Alliance partner today: www.shadowserver.org/partner/
-
The Shadowserver Foundation
@Shadowserver
A Mirai botnet is attempting exploitation in the wild using a new (at least to us) set of CVEs. Includes:
- Tenda CVE-2024-41473
- Draytek CVE-2024-12987
- HuangDou UTCMS V9 CVE-2024-9916
- Totolink CVE-2024-2353 CVE-2024-24328 CVE-2024-24329
- (likely) Four-Faith CVE-2024-9644
The Shadowserver Foundation
@Shadowserver
Just a few IPs involved so far, as seen by our honeypot sensors.
As a reminder we share IPs we see involved in HTTP scans/exploitation attempts in your network/constituency in our Honeypot HTTP Scanner Events report: www.shadowserver.org/what-we-do/network-reporting/honeypo…
The Shadowserver Foundation
@Shadowserver
Tagging for the above CVEs has been added to our system and going forwards detections should be available (if activity is seen) at dashboard.shadowserver.org/statistics/honeypot/vulnerabil…
-
The Shadowserver Foundation reposted
PIRegistry
@PIRegistry
On #saferinternetday, we reaffirm our commitment to a safer Internet year-round. By fighting DNS abuse, tackling CSAM, and partnering with @IWFhotline and @Shadowserver, we’re working to keep the web safe. Learn more at pir.org/news-insights/pir-making-the-internet-safer-all-y…
-
The Shadowserver Foundation
@Shadowserver
We are excited to welcome @PIRegistry Public Interest Registry (PIR) as a new Shadowserver Alliance partner (Bronze tier).
We look forward to raising the bar on cybersecurity together!
Read more about PIR: pir.org
The Shadowserver Foundation
@Shadowserver
Become a Shadowserver Alliance partner today: www.shadowserver.org/partner/
-
The Shadowserver Foundation
@Shadowserver
Since 2025-02-05 we are reporting daily GFI Kerio Control firewall instances vulnerable to CVE-2024-52875 which can (possibly) be leveraged for RCE. Data shared in www.shadowserver.org/what-we-do/network-reporting/vulnera…
We see 12,229 unpatched instances on 2025-02-09 worldwide: dashboard.shadowserver.org/statistics/combined/map/?map_t…
The Shadowserver Foundation
@Shadowserver
We are also seeing CVE-2024-52875 related scan activity in our honeypot sensors.
Make sure to check for any signs of compromise if you receive an alert from us and patch: gfi.ai/products-and-solutions/network-security-solutions/…
CVE-2024-52875 Dashboard Tracker (scan results): dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation
@Shadowserver
Large increase in web login brute forcing attacks against edge devices seen last few weeks in our honeypots, with up to 2.8M IPs per day seen with attempts (especially Palo Alto Networks, Ivanti, SonicWall etc). Over 1M from Brazil. Source IPs shared in shadowserver.org/what-we-do/network-reporting/honeypot-ht…
The Shadowserver Foundation
@Shadowserver
Geo breakdown - 2025-01-27: dashboard.shadowserver.org/statistics/combined/tree/?day=…
HTTP Scan/Attack Tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
HTTP attacks by src device. Only in cases where we can map src IP to a device. Note it may be a device behind the identified device that is involved:
dashboard.shadowserver.org/statistics/honeypot/device/tim…
The Shadowserver Foundation
@Shadowserver
If you receive an alert from us about an IP in your constituency seen attacking please investigate and reach out to us with your findings
-
The Shadowserver Foundation
@Shadowserver
Added 4in6 & 6in4 scans to our Open IP-Tunnel reporting (hosts that accepted unauthenticated packets from an arbitrary source, which can be abused for DoS/other attacks) www.shadowserver.org/what-we-do/network-reporting/open-ip…
~150K 4in6 open tunnels found (most in Germany)
~1.07M 6in4 open tunnels found
The Shadowserver Foundation
@Shadowserver
Now sharing open IP tunnel hosts in a new daily Open IP-Tunnel report www.shadowserver.org/what-we-do/network-reporting/open-ip…
These hosts accept tunnelling packets such as IPIP, GRE without authenticating the source IPv4 or IPv6 addr, which can be abused for DoS/other attacks
~436K GRE & ~66K IPIP IPs found
The Shadowserver Foundation
@Shadowserver
4in6 open tunnel map (2025-01-28:
dashboard.shadowserver.org/statistics/combined/map/?map_t…
6in4 open tunnel map (2025-01-28):
dashboard.shadowserver.org/statistics/combined/map/?map_t…
4in6 open tunnel tracker:
dashboard.shadowserver.org/statistics/combined/time-serie…
6in4 open tunnel tracker:
dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
Background and more details:
github.com/vanhoefm/tunneltester -
The Shadowserver Foundation
@Shadowserver
For the last few days we are sharing SimpleHelp CVE-2024-57727 (path traversal vulnerability) instances in our Vulnerable HTTP report: www.shadowserver.org/what-we-do/network-reporting/vulnera…
For patch info from SimpleHelp please see simple-help.com/kb---security-vulnerabilities-01-2025
We see around 580 vulnerable
dashboard.shadowserver.org/statistics/combined/tree/?day=…
The Shadowserver Foundation
@Shadowserver
For background on CVE-2024-57727 and other vulnerabilities please see www.horizon3.ai/attack-research/disclosures/critical-vuln…
-
The Shadowserver Foundation
@Shadowserver
We are sharing backdoored Ivanti Connect Secure devices that *may* have been compromised as part of a CVE-2025-0282 exploitation campaign (but also we believe may include older or other activity).
379 new backdoored instances found on 2025-01-22:
dashboard.shadowserver.org/statistics/combined/tree/?day=…
The Shadowserver Foundation
@Shadowserver
Data shared daily in our Compromised Website report www.shadowserver.org/what-we-do/network-reporting/comprom… tagged 'backdoor;ivanti-connect-secure'
Dashboard tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
Make sure to investigate your Ivanti Connect Secure instance if you receive an alert from us! @CISACyber mitigation advice is a good start www.cisa.gov/cisa-mitigation-instructions-cve-2025-0282
Thank you to @CERTFI for the insights and detection methods! -
The Shadowserver Foundation
@Shadowserver
We are sharing daily results of Fortinet CVE-2024-55591 (auth bypass) vulnerable instances in our Vulnerable HTTP report - www.shadowserver.org/what-we-do/network-reporting/vulnera…
CVE-2024-55591 is known to be exploited in the wild & on @CISACyber KEV.
Around 50K found vulnerable: dashboard.shadowserver.org/statistics/combined/map/?map_t…
The Shadowserver Foundation
@Shadowserver
Our test is based on the methodology published by @watchtowrcyber github.com/watchtowrlabs/fortios-auth-bypass-check-CVE-20… - thank you!
CVE-2024-55591 vulnerability tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
Fortinet advisory: www.fortiguard.com/psirt/FG-IR-24-535
Make sure to check for signs of compromise!
The Shadowserver Foundation
@Shadowserver
Additional background: arcticwolf.com/resources/blog/console-chaos-targets-forti…
-
The Shadowserver Foundation
@Shadowserver
Sharing rsync instances vulnerable to CVE-2024-12084 RCE (version check only) in our updated daily Accessible Rsync report: www.shadowserver.org/what-we-do/network-reporting/accessi…
17,475 instances found vulnerable (out of population of 146,844) on 2025-01-16. Top affected: US (5K)
dashboard.shadowserver.org/statistics/combined/map/?map_t…
The Shadowserver Foundation
@Shadowserver
Please note even though the report severity is by default MEDIUM, IPs tagged as CVE-2024-12084 have severity level set to CRITICAL
Post not available here, view on X
The Shadowserver Foundation
@Shadowserver
We also enhanced the report with an IPv6 version - 1002 found vulnerable out of a population of 7636 on 2025-01-16.
To view stats, you can select 'rsync' and/or 'rsync6' as source and select the cve-2024-12084 tag on the Dashboard.
The Shadowserver Foundation
@Shadowserver
Thank you @scannell_simon and @maximilianhils for the collaboration!
-
The Shadowserver Foundation
@Shadowserver
Now sharing open IP tunnel hosts in a new daily Open IP-Tunnel report www.shadowserver.org/what-we-do/network-reporting/open-ip…
These hosts accept tunnelling packets such as IPIP, GRE without authenticating the source IPv4 or IPv6 addr, which can be abused for DoS/other attacks
~436K GRE & ~66K IPIP IPs found
The Shadowserver Foundation
@Shadowserver
Geo breakdown (GRE/GRE6):
dashboard.shadowserver.org/statistics/combined/tree/?day=…
Geo breakdown (IPIP/IP6IP6):
dashboard.shadowserver.org/statistics/combined/tree/?day=…
The Shadowserver Foundation
@Shadowserver
These vulnerabilities were discovered by Angelos Beitis and Mathy Vanhoef @vanhoefm the DistriNet Reseach Unit at KU Leuven University in Belgium. Thank you for the collaboration!
You can find more details on the vulnerabilities at: github.com/vanhoefm/tunneltester -
The Shadowserver Foundation
@Shadowserver
Current Ivanti Connect Secure CVE-2025-0282 scanning results: around 800 exposed unpatched devices (IPs) seen as of 2025-01-12 (drop from around 2000 seen 2025-01-09)
CVE-2025-0282 vulnerability tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
We have started reporting unpatched Ivanti Connect Secure instances likely vulnerable to the new known to be exploited in the wild CVE-2025-0282.
We see 2048 likely vulnerable instances worldwide on 2024-01-09. Top: US
Dashboard overview by country: dashboard.shadowserver.org/statistics/combined/tree/?day=… -
The Shadowserver Foundation
@Shadowserver
We have started reporting unpatched Ivanti Connect Secure instances likely vulnerable to the new known to be exploited in the wild CVE-2025-0282.
We see 2048 likely vulnerable instances worldwide on 2024-01-09. Top: US
Dashboard overview by country: dashboard.shadowserver.org/statistics/combined/tree/?day=…
The Shadowserver Foundation
@Shadowserver
Vulnerable IP data is shared daily for your network/constituency in our shadowserver.org/what-we-do/network-reporting/vulnerable-… tagged 'cve-2025-0282'
If you receive an alert from us, make sure to follow
@CISACyber mitigation instructions: cisa.gov/cisa-mitigation-instructions-cve-2025-0282
Ivanti patch info: forums.ivanti.com/s/article/Security-Advisory-Ivanti-Conn…
The Shadowserver Foundation
@Shadowserver
Thank you to @watchtowrcyber for the insights and collaboration
-
The Shadowserver Foundation
@Shadowserver
We have started notifying about hosts running POP3/IMAP services without TLS enabled, meaning usernames/passwords are not encrypted when transmitted. We see around 3.3M such cases with POP3 & a similar amount with IMAP (most overlap).
It's time to retire those!Post not available here, view on X
The Shadowserver Foundation
@Shadowserver
Note that regardless whether TLS is enabled or not service exposure may enable password guessing attacks against the server.
You can find POP3 and IMAP servers that use TLS in our Accessible POP3 www.shadowserver.org/what-we-do/network-reporting/accessi… &
Accessible IMAP www.shadowserver.org/what-we-do/network-reporting/accessi… reports
The Shadowserver Foundation
@Shadowserver
UPDATE: After feedback from various National CSIRTs & mail server operators (thank you!), we have identified a number of potential false positives in data being shared. We have suspended the vulnerable POP3/IMAP reports & are working on improvements before restarting reporting
-
The Shadowserver Foundation
@Shadowserver
UPDATE: After feedback from various National CSIRTs & mail server operators (thank you!), we have identified a number of potential false positives in data being shared. We have suspended the vulnerable POP3/IMAP reports & are working on improvements before restarting reporting
The Shadowserver Foundation
@Shadowserver
We have started notifying about hosts running POP3/IMAP services without TLS enabled, meaning usernames/passwords are not encrypted when transmitted. We see around 3.3M such cases with POP3 & a similar amount with IMAP (most overlap).
It's time to retire those! -
The Shadowserver Foundation
@Shadowserver
The @DTC_NL funded CR4NGO consortium (which we are a part of) recently released the "Cyber Resilience for NGOs: A Collective Intelligence Effort” report. You can read more about the project & report at:
www.humanityhub.net/cyber-resilience-for-ngos/
www.humanityhub.net/wp-content/uploads/2024/11/Cyber-Resi…
www.humanityhub.net/wp-content/uploads/2024/12/Cyberweerb…
The Shadowserver Foundation
@Shadowserver
Thank you to our project partners @HumanityHub @CyberpeaceInst & connect2trust.nl for the collaboration and the continued efforts to strengthen the cyber resilience of Dutch NGOs and beyond!
-
The Shadowserver Foundation
@Shadowserver
For the last few days we are scanning & sharing IPs of Cleo Harmony/VLTrader/LexiCom CVE-2024-50623/CVE-2024-55956 vulnerable file transfer instances. These RCE vulnerabilities are being exploited in the wild.
We see around 930 vulnerable in our daily scans. Majority in US.
The Shadowserver Foundation
@Shadowserver
IP data shared in our Vulnerable HTTP Report: www.shadowserver.org/what-we-do/network-reporting/vulnera…
Make sure to review also for compromise if you receive a report from us!
Dashboard tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
Map:
dashboard.shadowserver.org/statistics/combined/map/?map_t…
Patch to version 5.8.0.24: support.cleo.com/hc/en-us/articles/28408134019735-Cleo-Pr…
The Shadowserver Foundation
@Shadowserver
(note we currently tag cve-2024-55956 as cve-2024-12632. cve-2024-12632 is now rejected as a duplicate of cve-2024-55956. We will replace it with cve-2024-55956)
-
The Shadowserver Foundation
@Shadowserver
We are seeing large numbers of sources scanning for RDP services - especially port 1098/TCP (!) - in our honeypot sensors last 2 weeks (up to 740 000 (!) distinct source IPs daily, incl up to 405 000 from Brazil).
Tracker: dashboard.shadowserver.org/statistics/honeypot/device/tim…
Map: dashboard.shadowserver.org/statistics/honeypot/device/map…Post not available here, view on X
The Shadowserver Foundation
@Shadowserver
We observe many MikroTik routers behind the probes, but these could be other devices/residential proxies behind the routers
dashboard.shadowserver.org/statistics/honeypot/device/tim…
The Shadowserver Foundation
@Shadowserver
We share data on the source IPs doing the scans in our Honeypot RDP Scanner Events report www.shadowserver.org/what-we-do/network-reporting/honeypo…
The file name for that report is event4_honeypot_rdp_scan -
The Shadowserver Foundation
@Shadowserver
We are happy to support the Hanover Police Department @Polizei_H, the Verden Public Prosecutor's Office, @Europol & other LE agencies in the takedown of "Manson Market". Hats off to all involved in the operation!
www.presseportal.de/blaulicht/pm/66841/5924114
www.europol.europa.eu/media-press/newsroom/news/fraudulen…
The Shadowserver Foundation
@Shadowserver
cc @EC3Europol @PolicieCZ @PolicjaCBZC @Politie @LPDWien @krp_poliisi
-
The Shadowserver Foundation
@Shadowserver
Great to have our cybersecurity capacity building work in the Indo-Pacific featured in UK Gov's CSSF Annual Report. Continuing to strengthen our valued partnership with @FCDOGovUK & help secure the Internet for all.
LondonCyber
@LondonCyber
The Conflict Stability and Security Fund (CSSF) Annual Report 2023-2024 is live: www.gov.uk/government/publications/conflict-stability-and…
The Fund transformed the UK's response to conflict, transnational threats, and hostile state activity overseas. Check out our work on #cyber under transnational threats. -
The Shadowserver Foundation reposted
National Cybersecurity Alliance
@StaySafeOnline
@ShadowServer is a nonprofit threat detection agency that scans the internet daily for harmful info.
Join us Dec. 12 to learn more about how to access and utilize these reports for your organization or your clients’ organizations.
www.staysafeonline.org/programs/events/how-to-protect-you…
#staysafeonline -
The Shadowserver Foundation reposted
Help Net Security
@helpnetsecurity
How the Shadowserver Foundation helps network defenders with free intelligence feeds - www.helpnetsecurity.com/2024/12/05/piotr-kijewski-shadows… - @Shadowserver @piotrkijewski #internet #network #automation #threatintelligence #incidentresponse #cybersecurity #ciso #itsecurity #cybersecuritynews #securitynews
-
The Shadowserver Foundation
@Shadowserver
We are excited to welcome Nihon Cyber Defence as a new Shadowserver Alliance partner (Bronze tier).
We look forward to raising the bar on cybersecurity together!
Read more about Nihon Cyber Defence: nihoncyberdefence.co.jp/en/
The Shadowserver Foundation
@Shadowserver
Shadowserver Alliance details: www.shadowserver.org/partner/
-
The Shadowserver Foundation
@Shadowserver
Heads-up! Thanks to collaboration with @NCA_KSA
we are now scanning & reporting Palo Alto Networks devices COMPROMISED as a result of a CVE-2024-0012/CVE-2024-9474 campaign.
Found ~2000 instances compromised on 2024-11-20:
dashboard.shadowserver.org/statistics/combined/map/?map_t…
Top affected: US & India
The Shadowserver Foundation
@Shadowserver
We are sharing IP data tagged 'panos-compromised' in our daily Compromised Website report, filtered by your network/constituency shadowserver.org/what-we-do/network-reporting/compromised…
We appreciate feedback on any IoCs you may find as a result of investigations based on our reporting
unit42.paloaltonetworks.com/cve-2024-0012-cve-2024-9474/ -
The Shadowserver Foundation
@Shadowserver
We have started to report Palo Alto Networks devices still vulnerable to CVE-2024-0012 in our Vulnerable HTTP reports (filtered by network/constituency of recipient): www.shadowserver.org/what-we-do/network-reporting/vulnera…
~2700 found vulnerable on 2024-11-20: dashboard.shadowserver.org/statistics/combined/tree/?day=…
Top affected: US & India
The Shadowserver Foundation
@Shadowserver
Thanks to @watchtowrcyber for the insights.
Please check for compromise if you receive a report from us for your device.
Patch info: security.paloaltonetworks.com/CVE-2024-0012
security.paloaltonetworks.com/CVE-2024-9474 -
The Shadowserver Foundation
@Shadowserver
We see CVE-2024-0012 exploitation attempts since Nov 18th. We are now also observing CVE-2024-9474.
IoCs: unit42.paloaltonetworks.com/cve-2024-0012-cve-2024-9474/
Check for signs of compromise and patch:
security.paloaltonetworks.com/CVE-2024-0012
security.paloaltonetworks.com/CVE-2024-9474
For additional background - labs.watchtowr.com/pots-and-pans-aka-an-sslvpn-palo-alto-…
The Shadowserver Foundation
@Shadowserver
CVEs have now been assigned:
unit42.paloaltonetworks.com/cve-2024-0012-cve-2024-9474/
security.paloaltonetworks.com/CVE-2024-0012
security.paloaltonetworks.com/CVE-2024-9474
6642 IPs found exposed on 2024-11-17 (down from around 11K): dashboard.shadowserver.org/statistics/iot-devices/time-se…
As a reminder, IP data is shared in our Device ID report daily: www.shadowserver.org/what-we-do/network-reporting/device-…
The Shadowserver Foundation
@Shadowserver
Palo Alto Networks has now updated their advisory security.paloaltonetworks.com/PAN-SA-2024-0015 saying they have "observed threat activity exploiting an unauthenticated remote command execution vulnerability against a limited number of firewall management interfaces which are exposed to the Internet."
The Shadowserver Foundation
@Shadowserver
Palo Alto published an advisory on 2024-10-08 warning of a claim of an RCE via the PAN-OS management interface. While no exploitation activity has yet been observed, we added fingerprinting for exposed PAN-OS mgmt interfaces in our Device ID report.
We see around 11K IPs exposed -
The Shadowserver Foundation
@Shadowserver
CVEs have now been assigned:
unit42.paloaltonetworks.com/cve-2024-0012-cve-2024-9474/
security.paloaltonetworks.com/CVE-2024-0012
security.paloaltonetworks.com/CVE-2024-9474
6642 IPs found exposed on 2024-11-17 (down from around 11K): dashboard.shadowserver.org/statistics/iot-devices/time-se…
As a reminder, IP data is shared in our Device ID report daily: www.shadowserver.org/what-we-do/network-reporting/device-…
The Shadowserver Foundation
@Shadowserver
Palo Alto Networks has now updated their advisory security.paloaltonetworks.com/PAN-SA-2024-0015 saying they have "observed threat activity exploiting an unauthenticated remote command execution vulnerability against a limited number of firewall management interfaces which are exposed to the Internet."
The Shadowserver Foundation
@Shadowserver
Palo Alto published an advisory on 2024-10-08 warning of a claim of an RCE via the PAN-OS management interface. While no exploitation activity has yet been observed, we added fingerprinting for exposed PAN-OS mgmt interfaces in our Device ID report.
We see around 11K IPs exposed -
The Shadowserver Foundation
@Shadowserver
Based on recent advisory by @CISACyber @ASDGovAu @cybercentre_ca @NCSC @CERTNZ on "2023 Top Routinely Exploited Vulnerabilities" we added 3 2023 CVEs to our daily reports
Atlassian CVE-2023-22515
PaperCut MF/NG CVE-2023-27350
OwnCloud CVE-2023-49103
www.cisa.gov/news-events/cybersecurity-advisories/aa24-317a
The Shadowserver Foundation
@Shadowserver
These can be found (in addition to others from that list) in our Vulnerable HTTP report www.shadowserver.org/what-we-do/network-reporting/vulnera…
You can track all our CVE related scans from that report on our Dashboard at dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation
@Shadowserver
Palo Alto Networks has now updated their advisory security.paloaltonetworks.com/PAN-SA-2024-0015 saying they have "observed threat activity exploiting an unauthenticated remote command execution vulnerability against a limited number of firewall management interfaces which are exposed to the Internet."
The Shadowserver Foundation
@Shadowserver
Palo Alto published an advisory on 2024-10-08 warning of a claim of an RCE via the PAN-OS management interface. While no exploitation activity has yet been observed, we added fingerprinting for exposed PAN-OS mgmt interfaces in our Device ID report.
We see around 11K IPs exposed
The Shadowserver Foundation
@Shadowserver
We see a drop in exposed PAN-OS Management Interfaces (down by around 2K from previously shared observations), currently at 8726 IPs Get these Interfaces off public Internet access NOW!
PAN-OS Management Interface tracker: dashboard.shadowserver.org/statistics/iot-devices/time-se… -
The Shadowserver Foundation
@Shadowserver
We observed a 0day exploit in the wild used by a botnet targeting GeoVision EOL devices. The pre-auth command injection vulnerability was verified in collaboration with TWCERT & GeoVision & assigned CVE-2024-11120 (CVSS 9.8)
twcert.org.tw/en/cp-139-8237-26d7a-2.html
NVD: nvd.nist.gov/vuln/detail/CVE-2024-11120
The Shadowserver Foundation
@Shadowserver
If you run a vulnerable EOL version, please remove from the Internet and replace it.
We currently track around 17K GeoVision devices (see our device id report for GeoVision devices on your network) of all versions and will be working to identify the vulnerable cases.
The Shadowserver Foundation
@Shadowserver
Geo map view of exposed GeoVision devices (population only, no vulnerability assessment) dashboard.shadowserver.org/statistics/iot-devices/map/?da…
-
The Shadowserver Foundation
@Shadowserver
We have observed D-Link NAS CVE-2024-10914 /cgi-bin/account_mgr.cgi command injection exploitation attempts starting Nov 12th. This vuln affects EOL/EOS devices, which should be removed from the Internet: supportannouncement.us.dlink.com/security/publication.asp…
We see ~1100 exposed.
dashboard.shadowserver.org/statistics/iot-devices/tree/?d…
The Shadowserver Foundation
@Shadowserver
We share IP data on exposed D-Link NAS instances for your network/constituency in our Device ID reports (vendor D-Link, type: nas): www.shadowserver.org/what-we-do/network-reporting/device-…
D-Link NAS exposure tracker dashboard.shadowserver.org/statistics/iot-devices/time-se…
NVD entry: nvd.nist.gov/vuln/detail/CVE-2024-10914 -
The Shadowserver Foundation
@Shadowserver
We started seeing Citrix Virtual Apps and Desktops CVE-2024-8068/CVE-2024-8069 PoC based attempts at around 16:00 UTC today, shortly after publication.
While there is discussion on whether these are remotely exploitable without auth, we urge you to update your installations NOW
The Shadowserver Foundation
@Shadowserver
Citrix security advisory and update information: support.citrix.com/s/article/CTX691941-citrix-session-rec…
watchTowr disclosure: labs.watchtowr.com/visionaries-at-citrix-have-democratise… -
The Shadowserver Foundation
@Shadowserver
Palo Alto published an advisory on 2024-10-08 warning of a claim of an RCE via the PAN-OS management interface. While no exploitation activity has yet been observed, we added fingerprinting for exposed PAN-OS mgmt interfaces in our Device ID report.
We see around 11K IPs exposedPost not available here, view on X
The Shadowserver Foundation
@Shadowserver
IP data is now shared daily in our Device ID report www.shadowserver.org/what-we-do/network-reporting/device-…
Palo Alto Networks security alert advisory security.paloaltonetworks.com/PAN-SA-2024-0015
How to Secure the Management Access of Your Palo Alto Networks Device: live.paloaltonetworks.com/t5/community-blogs/tips-amp-tri…
The Shadowserver Foundation
@Shadowserver
PAN-OS Management Exposure by US state:
dashboard.shadowserver.org/statistics/iot-devices/map/?da… -
The Shadowserver Foundation
@Shadowserver
We have observed some interest in rocket.chat CVE-2024-39713 in our sensors. This is a Server-Side Request Forgery (SSRF) vuln which could for example lead to some level of access to internal systems.
We added a population scan for exposed IPs (1781 IPs found)
The Shadowserver Foundation
@Shadowserver
IP data shared in: www.shadowserver.org/what-we-do/network-reporting/device-…
Dashboard exposure tracker of rocket.chat IPs (no vuln assessment): dashboard.shadowserver.org/statistics/iot-devices/time-se…
Dashboard tree map view of rocket.chat instances broken down by country (2024-11-10): dashboard.shadowserver.org/statistics/iot-devices/tree/?d…
The Shadowserver Foundation
@Shadowserver
Make sure to upgrade to the latest release: github.com/RocketChat/Rocket.Chat
-
The Shadowserver Foundation
@Shadowserver
Using ELK & interested in automating ingestion of our threat intel for your network/constituency?
We have added support for Elasticsearch Custom Logs integration for our free daily reports API. Check it out at github.com/The-Shadowserver-Foundation/api_utils/tree/mai… -
The Shadowserver Foundation
@Shadowserver
We are excited to welcome watchTowr @watchtowrcyber as a new Shadowserver Alliance partner (Bronze tier).
We look forward to raising the bar on cybersecurity together!
Read more about watchTowr: watchtowr.com
The Shadowserver Foundation
@Shadowserver
Alliance partnership details: shadowserver.org/partner/
-
The Shadowserver Foundation
@Shadowserver
URGENT: We just ran a Special Report about FortiManager devices targeted/compromised in Sept 22nd mass compromise using CVE-2024-47575:
www.shadowserver.org/what-we-do/network-reporting/fortine…
Check your reports & assume compromise, unless extensive analysis shows otherwise.
The Shadowserver Foundation
@Shadowserver
IP data in a file shared with a 2024-10-24-special prefix.
If you need assistance, please reach out to Fortinet’s support (or your reseller) clearly communicating the observed IOCs.
See Fortinet advisory: www.fortiguard.com/psirt/FG-IR-24-423 -
The Shadowserver Foundation
@Shadowserver
We added SolarWinds Web Help Desk CVE-2024-28987 (Hardcoded Credential Vulnerability) to our daily scan tagging & free feeds. We see around 190 vulnerable instances. Top affected: USA
Dashboard: dashboard.shadowserver.org/statistics/combined/map/?map_t…
We first saw exploitation activity in our sensors Oct 7th.
CISA Cyber
@CISACyber
🛡️ We added #microsoft, #mozilla & #solarwinds vulnerabilities, #cve-2024-30088, CVE-2024-9680 & CVE-2024-28987 to our Known Exploited Vulnerabilities Catalog. Visit go.dhs.gov/Z3Q & mitigations to protect your org from cyberattacks. #cybersecurity #infosec
The Shadowserver Foundation
@Shadowserver
IP data shared in vulnerable HTTP report: www.shadowserver.org/what-we-do/network-reporting/vulnera…
Note the vulnerable instances are likely unreported, as we do NOT tag any 12.8.3 versions as vulnerable due to the fact we are currently unable to distinguish this version from the (patched) 12.8.3 HF2 remotely.
The Shadowserver Foundation
@Shadowserver
SolarWinds advisory (Aug 22nd) and patch info: www.solarwinds.com/trust-center/security-advisories/cve-2…
-
The Shadowserver Foundation
@Shadowserver
We are excited to announce our partnership with @pausetake9. This new campaign will strengthen America’s CyberSecurity by forming communities of cyber defenders. Protect your private information and the nation.
Learn more at pausetake9.org. #take9 @craignewmark -
The Shadowserver Foundation
@Shadowserver
Now sharing daily feeds of SolarWinds Serv-U IPs likely vulnerable to CVE-2024-45711 (directory traversal vulnerability where remote code execution is possible depending on privileges given to authenticated user).
2598 IPs found on 2024-10-19, top: US.
dashboard.shadowserver.org/statistics/combined/tree/?day=…
The Shadowserver Foundation
@Shadowserver
IP data in www.shadowserver.org/what-we-do/network-reporting/vulnera…
CVE-2024-45711 vulnerability tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
Patch info from SolarWinds (16th Oct): www.solarwinds.com/trust-center/security-advisories/cve-2…
Breakdown by US state of likely vulnerable instances:
dashboard.shadowserver.org/statistics/combined/map/region… -
The Shadowserver Foundation reposted
craig newmark
@craignewmark
We must support those organizations that support cybersecurity for the common good and #cybercivildefense, like @Shadowserver, which would cost tens of millions of dollars to replicate. commongoodcyber.org/news/interview-piotr-kijewski-replica… @CommonGoodCyber
-
The Shadowserver Foundation reposted
Omo Oaiya
@OmoOaiya
🎉 The #tbaiv event wraps up! The intensive week equipped cybersecurity professionals with #sim3 Auditor certification skills. This is a huge step forward in strengthening #african teams. Thanks to @BeninFgi, @asinbenin, @CsirtOpen & @Shadowserver for making it happen! #cotonou
-
The Shadowserver Foundation reposted
Common Good Cyber
@CommonGoodCyber
Our new interview with @Shadowserver highlights a perfect example of why #commongoodcyber is so crucial.
“Replicating Shadowserver on a similar scale would probably cost tens of millions of dollars.”
commongoodcyber.org/news/interview-piotr-kijewski-replica… -
The Shadowserver Foundation
@Shadowserver
We are now reporting in our feeds Fortinet IPs still likely vulnerable to CVE-2024-23113 (format string pre-auth RCE). This vulnerability is known to be exploited in the wild.
87,390 IPs found on 2024-10-12 scan. Top: US (14K), Japan (5.1K), India (4.8K)
dashboard.shadowserver.org/statistics/combined/map/?map_t…
The Shadowserver Foundation
@Shadowserver
We are sharing daily feeds of vulnerable IPs in our Vulnerable HTTP report: shadowserver.org/what-we-do/network-reporting/vulnerable-…
You can track CVE-2024-23113 vulnerable instances over time on our Dashboard: dashboard.shadowserver.org/statistics/combined/time-serie…
Patch details from Fortinet (Feb 8th, 2024): fortiguard.com/psirt/FG-IR-24-029 -
The Shadowserver Foundation
@Shadowserver
We are scanning for & reporting Zimbra IPs likely vulnerable to CVE-2024-45519 (CVSS 9.8 RCE, NVD entry: nvd.nist.gov/vuln/detail/CVE-2024-45519)
Over 19.6K unpatched instances seen on 2024-10-04.
Top: Germany (1.6K), US (1.6K), Russia (1.5K).
Country tree map: dashboard.shadowserver.org/statistics/combined/tree/?day=…
The Shadowserver Foundation
@Shadowserver
IP data shared in our daily feeds in www.shadowserver.org/what-we-do/network-reporting/vulnera… with 'cve-2024-45519' tag)
Please note CVE-2024-45519 can be exploited via the SMTP service (our version check itself is web based) and that postjournal is NOT enabled by default (which is not verified in our scans).
The Shadowserver Foundation
@Shadowserver
As the vulnerability has been confirmed exploited in the wild by @CISACyber and added to their KEV catalog (www.cisa.gov/known-exploited-vulnerabilities-catalog), please check for any signs of compromise as well if using postjournal.
Upgrade to the latest versions of Zimbra: wiki.zimbra.com/wiki/Security_Center -
The Shadowserver Foundation
@Shadowserver
You can track Ivanti Endpoint Manager CVE-2024-29824 exploitation attempts (by unique attacking source IP) as seen by our sensors on our public Dashboard, for example:
dashboard.shadowserver.org/statistics/honeypot/vulnerabil…
CISA Cyber
@CISACyber
🛡️ We added an #ivanti Endpoint Manager SQL injection vulnerability, #cve-2024-29824, to our Known Exploited Vulnerabilities Catalog. Visit go.dhs.gov/Z3Q & apply mitigations to protect your org from cyberattacks. #cybersecurity #infosec
The Shadowserver Foundation
@Shadowserver
CVE-2024-29824 exploitation attempts by unique destinations (sensors)
dashboard.shadowserver.org/statistics/honeypot/vulnerabil… -
The Shadowserver Foundation
@Shadowserver
We shared a one-off Special report on vulnerable CUPS instances www.shadowserver.org/what-we-do/network-reporting/vulnera… - data tagged cups;cve-2024-47176
107 289 instances seen on 2024-09-27 (based on a scan from an external party). Top affected US (over 20K), Germany (nearly 13K).
dashboard.shadowserver.org/statistics/combined/map/?map_t…
The Shadowserver Foundation
@Shadowserver
Background: www.evilsocket.net/2024/09/26/Attacking-UNIX-systems-via-…
-
The Shadowserver Foundation reposted
LondonCyber
@LondonCyber
We are proud to support @shadowserver at @commongoodcyber from the Hague, acting within a likeminded community to defend cyberspace and ensure the internet remains a safe cyber place for all!
#beyond125_thehague #commongoodcyber #cybercivildefense
Common Good Cyber
@CommonGoodCyber
Heli Tiirma-Klar, Distinguished Fellow from The German Marshall Fund, and Kathryn Jones, Head of Cyber Strategy & Engagement @FCDOGovUK, exchange views on cybersecurity trends, and related geographical disparities and challenges. #beyond125_thehague🧵
-
The Shadowserver Foundation
@Shadowserver
Thanks to collaboration with @NCA_KSA we now detect Samsung Techwin NVR Web Viewer devices compromised with a webshell (backdoor). Data added to our free daily Compromised Website Report from 2024-09-26:
www.shadowserver.org/what-we-do/network-reporting/comprom…
Events tagged as "samsung-techwin-nvr-web-viewer"
The Shadowserver Foundation
@Shadowserver
Statistics about compromised publicly exposed devices are available on our Dashboard (~600 devices initially).
Treemap of devices per country:
dashboard.shadowserver.org/statistics/combined/tree/?day=…
Tracking of compromised devices over time:
dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
If you receive a report about a compromised device, please investigate immediately. Look for webshell file named "update.php" in the "/root/webviewer/" directory.
-
The Shadowserver Foundation
@Shadowserver
Large increase in queries on 631/UDP seen in our sensors due to recent CUPS RCEs disclosure. These include callback attempts.
We are exploring possible non-invasive scanning options for the recent RCEs. Please note we scan daily for exposed IPP printer services (631/TCP).
The Shadowserver Foundation
@Shadowserver
IP data on exposed printer instances on port 631/TCP in our Open IPP report: www.shadowserver.org/what-we-do/network-reporting/open-ip…
Dashboard tree map view (2024-09-26): dashboard.shadowserver.org/statistics/combined/tree/?day=…
The Shadowserver Foundation
@Shadowserver
Background on recent CUPS RCEs: www.evilsocket.net/2024/09/26/Attacking-UNIX-systems-via-…
-
The Shadowserver Foundation
@Shadowserver
We are seeing an increase in attacks against various AI/LLM platforms. This includes Gradio CVE-2024-4325 SSRF (since end of June), CVE-2024-1561 path traversal (start of July). Tags for these are now visible on our Dashboard & tracked moving forward.
dashboard.shadowserver.org/statistics/honeypot/vulnerabil…
The Shadowserver Foundation
@Shadowserver
Gradio exposure (no vulnerability assessment): over 1000 IPs seen worldwide. Top: US (397), China (237), Germany (52). Shared in our Device ID report: shadowserver.org/what-we-do/network-reporting/device-iden…
Geo breakdown: dashboard.shadowserver.org/statistics/iot-devices/map/?da…
Lastest Gradio patched releases: gradio.app/changelog
The Shadowserver Foundation
@Shadowserver
Other AI/LLM/Chatbot platform CVE attempts we track include for example NextChat CVE-2023-49785, LiteLLM CVE-2024-6587, Ollama CVE-2024-37032, dirk1983/chatgpt CVE-2024-27564
Expect more to come ... -
The Shadowserver Foundation
@Shadowserver
We are releasing a new daily IP feed of compromised IoT devices discovered in our non-HTTP scans, attacks against sensors we map to devices. Includes compromised SSH instances obtained via collaboration with external sources.
www.shadowserver.org/what-we-do/network-reporting/comprom…
dashboard.shadowserver.org/statistics/combined/map/?map_t…
The Shadowserver Foundation
@Shadowserver
This complements our other reports such as the Compromised Website report with HTTP based detection (see www.shadowserver.org/what-we-do/network-reporting/comprom…) which also contains IoT devices, as well as our sinkhole and honeypot based reports.
The report will be expanded with new detections in the future. -
The Shadowserver Foundation
@Shadowserver
We added VMware vCenter Server CVE-2024-38812 (heap-overflow vulnerability in implementation of the DCERPC protocol, CVSS 9.8 RCE) to our scans. 1159 unpatched instances found 2024-09-19, of those 446 have DCERPC service exposed, so likely exploitable
dashboard.shadowserver.org/statistics/combined/map/?map_t…
The Shadowserver Foundation
@Shadowserver
Data in Vulnerable HTTP report: www.shadowserver.org/what-we-do/network-reporting/vulnera… tagged cve-2024-38812 & additionally vcenter-dcerpc-exposed when DCERPC service found accessible remotely
See patch information from Broadcom: support.broadcom.com/web/ecx/support-content-notification… -
The Shadowserver Foundation
@Shadowserver
End of last week we sinkholed a number of domains associated with the Android Vo1d malware that infects Android-based TV boxes. Over 580K infected devices on 2024-09-15. Top infected is Brazil with over 203K, but wide range of countries impacted.
Stats: dashboard.shadowserver.org/statistics/combined/map/?map_t…
The Shadowserver Foundation
@Shadowserver
IP data is shared in www.shadowserver.org/what-we-do/network-reporting/sinkhol… as infection: android.vo1d tag:android.vo1d
Background on the discovery by Doctor Web, with technical info & IoCs: news.drweb.com/show/?i=14900&lng=en&c=9 -
The Shadowserver Foundation
@Shadowserver
As a periodic reminder: Shadowserver is also present on a number of other social media platforms.
Mastodon: infosec.exchange/@shadowserver/
LinkedIn: www.linkedin.com/company/the-shadowserver-foundation/
BlueSky: bsky.app/profile/shadowserver.bsky.social
You can also track developments on our GitHub: github.com/The-Shadowserver-Foundation -
The Shadowserver Foundation reposted
AUSCERT
@AusCERT
World-renowned speaker Piotr Kijewski presented at AUSCERT2024, offering an in-depth overview of how Shadowserver operates as a large-scale information collection and sharing project, working closely with the global Internet defender community.
Watch:
www.youtube.com/watch?v=7fSD5ecB1Ck&list=PLrirtPWcnfasXf-… -
The Shadowserver Foundation
@Shadowserver
Great research from @watchtowrcyber on dangers of expired domain names, happy to support by sinkholing.
Events reported from 2024-09-11 in our free daily event4_sinkhole network reports (www.shadowserver.org/what-we-do/network-reporting/sinkhol…) as:
type:sinkhole infection:non-authoritative-whois and tag:mobi
watchTowr
@watchtowrcyber
In August, watchTowr Labs hijacked parts of the global .mobi TLD - and went on to discover the mayhem that we could cause.
Enjoy....
labs.watchtowr.com/we-spent-20-to-achieve-rce-and-acciden…
The Shadowserver Foundation
@Shadowserver
First daily reports will be received tomorrow.
If you have code/systems still using the expired whois.dotmobiregistry.net to make WHOIS queries for the .mobi top level domain (TLD), please update immediately to use the correct authoritative WHOIS server whois.nic.mobi. -
The Shadowserver Foundation reposted
TEAM CYMRU
@teamcymru
We are thrilled to announce our new partnership with @Shadowserver In a world where cybersecurity threats are ever-evolving, there’s strength in numbers. #together, we are stronger. #shadowserver #teamcymru #cybersecurity #partnership
www.shadowserver.org/partner/ -
The Shadowserver Foundation
@Shadowserver
We are excited to welcome the Digital Trust Center (@DTC_NL) of the Netherlands as a new Shadowserver Alliance partner (Silver tier).
We look forward to raising the bar on cybersecurity together and helping make businesses more resilient to cyber threats!
The Shadowserver Foundation
@Shadowserver
Read more about DTC: www.digitaltrustcenter.nl
Alliance partnership details: shadowserver.org/partner/ -
The Shadowserver Foundation
@Shadowserver
Multiple CVEs discovered in Zyxel devices recently, including critical severity RCEs:
www.zyxel.com/global/en/support/security-advisories/zyxel…
We have improved exposed Zyxel device model detection in our Device ID scans
Over 65K firewalls identified by model - dashboard.shadowserver.org/statistics/iot-devices/map/?da…
The Shadowserver Foundation
@Shadowserver
If you receive Device ID reports on exposed Zyxel devices from us (see www.shadowserver.org/what-we-do/network-reporting/device-…) make sure to verify if your version is vulnerable & update per advisory
Note: these are population scans of exposed devices (no vulnerability check)
dashboard.shadowserver.org/statistics/iot-devices/visuali… -
The Shadowserver Foundation
@Shadowserver
We are excited to welcome Rabbi Rob & Lauren Thomas and Team Cymru @teamcymru as a new Shadowserver Alliance partner (Bronze tier).
We look forward to raising the bar on cybersecurity together!
Read more about Team Cymru: team-cymru.com
The Shadowserver Foundation
@Shadowserver
Alliance partnership details: shadowserver.org/partner/
-
The Shadowserver Foundation
@Shadowserver
We started seeing some Progress WhatsUp Gold CVE-2024-6670 (CVSS 9.8) SQLi exploit attempts against our honeypot sensors that match recently published PoC (/NmConsole/Platform/PerformanceMonitorErrors/HasErrors endpoint)
Progress advisory & patch info: community.progress.com/s/article/WhatsUp-Gold-Security-Bu… -
The Shadowserver Foundation
@Shadowserver
7777 Botnet infection breakdown by US state:
dashboard.shadowserver.org/statistics/combined/map/region…
(Tip: select source 'compromised-iot' and tag '7777' to view various 7777 Botnet stats on the Dashboard)
The Shadowserver Foundation
@Shadowserver
Starting tomorrow (2024-08-30) we will be sharing IoT devices compromised by 7777 botnet (IP data in Accessible Telnet report, tagged '7777' www.shadowserver.org/what-we-do/network-reporting/accessi…)
We see 9616 compromised IPs in our 2024-08-29 scan.
Top affected - US (1834), Russia (1197), Bulgaria (953) -
The Shadowserver Foundation
@Shadowserver
Starting tomorrow (2024-08-30) we will be sharing IoT devices compromised by 7777 botnet (IP data in Accessible Telnet report, tagged '7777' www.shadowserver.org/what-we-do/network-reporting/accessi…)
We see 9616 compromised IPs in our 2024-08-29 scan.
Top affected - US (1834), Russia (1197), Bulgaria (953)
The Shadowserver Foundation
@Shadowserver
Scan data is based on indicators published in www.bitsight.com/blog/7777-botnet-insights-multi-target-b…
Stats will be available on the Dashboard on 2024-08-30 under
dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation
@Shadowserver
According to @CISACyber SolarWinds CVE-2024-28986 is actively exploited
We added Internet exposed SolarWinds Web Help Desk instances to our daily Device ID reports -www.shadowserver.org/what-we-do/network-reporting/device-…
812 found on 2024-08-18, 527 in the US
Exposure by country: dashboard.shadowserver.org/statistics/iot-devices/map/?da…
CISA Cyber
@CISACyber
🛡️ We added #solarwindsweb Help Desk vulnerability, #cve-2024-28986, to our Known Exploited Vulnerabilities Catalog. Visit go.dhs.gov/Z3Q & apply mitigations to protect your org from cyberattacks. #cybersecurity #infosec
The Shadowserver Foundation
@Shadowserver
Note: we do not make a vulnerability assessment on the exposed devices
SolarWinds advisory: support.solarwinds.com/SuccessCenter/s/article/WHD-12-8-3…
If you receive information from us about an exposed instance please make verify it is patched (and if not investigate also for signs of compromised)
The Shadowserver Foundation
@Shadowserver
Exposure by US State:
dashboard.shadowserver.org/statistics/iot-devices/map/reg… -
The Shadowserver Foundation
@Shadowserver
CVE-2024-7593: We are sharing Ivanti vTM devices exposed on the Internet in our Device ID report www.shadowserver.org/what-we-do/network-reporting/device-… (no vulnerability assessment)
Only 31 found 2024-08-17, but today we observed an exploit attempt based on the public PoC.
Dashboard: dashboard.shadowserver.org/statistics/iot-devices/tree/?d…
The Shadowserver Foundation
@Shadowserver
Patch info from Ivanti: forums.ivanti.com/s/article/Security-Advisory-Ivanti-Virt…
-
The Shadowserver Foundation
@Shadowserver
We have added a list of our daily threat/vulnerability/exposure reports sorted by severity to our GitHub github.com/The-Shadowserver-Foundation/report_schema/blob…
Hopefully makes it easier to track!
Make sure to use our API for automatically ingesting these reports & more - github.com/The-Shadowserver-Foundation/api_utils/wiki -
The Shadowserver Foundation
@Shadowserver
We are also scanning & reporting out Cisco Smart Software Manager On-Prem CVE-2024-20419 (CVSS 10.0 rated) vulnerable instances. Advisory published in July & now updated by Cisco with info on a PoC available.
We see (only) over 40 instances vulnerable - dashboard.shadowserver.org/statistics/combined/tree/?day=…
The Shadowserver Foundation
@Shadowserver
We share daily reports by IP (filtered by network/constituency) in our Vulnerable HTTP report - www.shadowserver.org/what-we-do/network-reporting/vulnera…
Cisco Advisory with update information: sec.cloudapps.cisco.com/security/center/content/CiscoSecu… -
The Shadowserver Foundation
@Shadowserver
We see over 6000 IPs with Cisco Smart install feature exposed to the Internet. We share IPs daily in our feeds - www.shadowserver.org/what-we-do/network-reporting/accessi…
You can track worldwide, country, province/state level exposure of Cisco Smart Install on our Dashboard, for example: dashboard.shadowserver.org/statistics/combined/map/?map_t…
CISA Cyber
@CISACyber
🛡️Recently we’ve observed malicious cyber actors acquire systems configuration files by leveraging protocols or software on devices like the legacy #cisco Smart Install feature. View best practices for Cisco device configuration at cisa.gov/news-events/alerts/2024/08/08/best-practices-cis….
The Shadowserver Foundation
@Shadowserver
Make sure to block external access and disable Smart Install on your devices!
Dashboard tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
Per State exposure in the United States:
dashboard.shadowserver.org/statistics/combined/map/region… -
The Shadowserver Foundation
@Shadowserver
Let's adequately fund cybersecurity nonprofits. The Internet depends on it!
Please read: www.compiler.news/lets-adequately-fund-cybersecurity-nonp…
#commongoodcyber #cybercivildefense -
The Shadowserver Foundation
@Shadowserver
Using Progress WhatsUp Gold? Starting Aug 1st, we see /NmAPI/RecurringReport CVE-2024-4885 exploitation callback attempts (so far 6 src IPs). Note:PoC is public!
See Progress advisory: community.progress.com/s/article/WhatsUp-Gold-Security-Bu…
Track CVE-2024-4885 attacks on our Dashboard: dashboard.shadowserver.org/statistics/honeypot/vulnerabil…
The Shadowserver Foundation
@Shadowserver
Please note that the Dashboard shows attacks only from when the tagging was added, so for CVE-2024-4885 on Aug 6th. This means IPs from Aug 1st till Aug 5th will not be shown.
-
The Shadowserver Foundation
@Shadowserver
You can track likely vulnerable GeoServer instances on our Dashboard, for example CVE-2024-36401 (over 6200) : dashboard.shadowserver.org/statistics/combined/time-serie…
You can also see an increase in compromised GeoServer instances attacking our honeypot sensors (see attached image): dashboard.shadowserver.org/statistics/honeypot/device/tim…
SANS.edu Internet Storm Center
@sans_isc
A Survey of Scans for #geoserver Vulnerabilities: @shadowserver FTW isc.sans.edu/diary/31148
The Shadowserver Foundation
@Shadowserver
IP level data on vulnerable instances shared in our daily Vulnerable HTTP report filtered by network/constituency - www.shadowserver.org/what-we-do/network-reporting/vulnera…
IP level data on compromised devices scanning our honeypot sensors is in the Honeypot HTTP Scanner Report : www.shadowserver.org/what-we-do/network-reporting/honeypo… -
The Shadowserver Foundation
@Shadowserver
For clarity: these are potentially vulnerable as this is a remote version check only for patch status. We do not have detection of any workarounds in place nor do we check whether other pre-conditions of exploitability exist (domain-joined ESXi hypervisors).
The Shadowserver Foundation
@Shadowserver
We have started sharing exposed VMware ESXi vulnerable to CVE-2024-37085 (authentication bypass). While rated only CVSS 6.8 by Broadcom, this vuln has been reported by Microsoft as exploited in the wild by ransomware operators.
We see 20 275 instances vulnerable on 2024-07-30. -
The Shadowserver Foundation
@Shadowserver
We have started sharing exposed VMware ESXi vulnerable to CVE-2024-37085 (authentication bypass). While rated only CVSS 6.8 by Broadcom, this vuln has been reported by Microsoft as exploited in the wild by ransomware operators.
We see 20 275 instances vulnerable on 2024-07-30.Post not available here, view on X
The Shadowserver Foundation
@Shadowserver
Microsoft blog with background details - www.microsoft.com/en-us/security/blog/2024/07/29/ransomwa…
The Shadowserver Foundation
@Shadowserver
Please note: this is based on a version check. We do not check for a workaround.
-
The Shadowserver Foundation
@Shadowserver
We are sharing CVE-2024-36401 vulnerable GeoServer instances in our daily feeds.
Our version based check uncovers 6635 likely vulnerable instances on 2024-07-24
Dashboard: dashboard.shadowserver.org/statistics/combined/map/?map_t…
CVE-2024-36401 is known to be exploited in the wild & on @CISACyber KEV list.
The Shadowserver Foundation
@Shadowserver
Top affected: US (985), China (929) & Germany (517).
Data in www.shadowserver.org/what-we-do/network-reporting/vulnera… tagged cve-2024-36401
Tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
Make sure to check for signs of compromise & update: github.com/geoserver/geoserver/security/advisories/GHSA-6…
-
The Shadowserver Foundation
@Shadowserver
CISA added GeoServer CVE-2024-36401 to its Known Exploited Vulnerability Catalog www.cisa.gov/news-events/alerts/2024/07/15/cisa-adds-one-…
We first observed CVE-2024-36401 "POST /geoserver/wfs" exploitation July 9th in our sensors. Check for signs of compromise & patch github.com/geoserver/geoserver/security/advisories/GHSA-6… -
The Shadowserver Foundation
@Shadowserver
We are observing Apache HugeGraph-Server CVE-2024-27348 RCE "POST /gremlin" exploitation attempts from multiple sources. PoC code is public since early June. If you run HugeGraph, make sure to update: lists.apache.org/thread/nx6g6htyhpgtzsocybm242781o8w5kq9
NVD entry: nvd.nist.gov/vuln/detail/CVE-2024-27348
The Shadowserver Foundation
@Shadowserver
Looking back some of these started June 6th, but attempts increased last week. Overall we have seen 8 src IPs to date.
-
The Shadowserver Foundation reposted
National Crime Agency (NCA)
@NCA_UK
The NCA has coordinated global action against illicit software which has been used by cybercriminals for over a decade to infiltrate victims’ IT systems and conduct attacks.
FULL STORY ➡️ www.nationalcrimeagency.gov.uk/news/national-crime-agency… -
The Shadowserver Foundation reposted
Europol
@Europol
⚠️Law enforcement teamed up with the private sector to stop criminals abusing Cobalt Strike to carry out attacks.
An action led by @NCA_UK & coordinated from Europol HQ resulted in the takedown of 593 IP addresses linked to criminal activity.
Details ⤵️
www.europol.europa.eu/media-press/newsroom/news/europol-c… -
The Shadowserver Foundation
@Shadowserver
We are reporting out OpenSSH servers potentially vulnerable to CVE-2024-6387 RCE (“regreSSHion”): shadowserver.org/what-we-do/network-reporting/accessible-…
~4.5M hosts possibly vulnerable 2024-07-02 (out of over 23.5M seen)
dashboard.shadowserver.org/statistics/combined/map/?map_t…
Details: qualys.com/2024/07/01/cve-2024-6387/regresshion.txt
NVD: nvd.nist.gov/vuln/detail/CVE-2024-6387
The Shadowserver Foundation
@Shadowserver
As this scan is version based both false positives and false negatives are possible. Backporting by various distributions is also possible which makes version based assessment less reliable.
Make sure you have an updated OpenSSH version: openssh.com/txt/release-9.8
The Shadowserver Foundation
@Shadowserver
(Apologies: we had to delete a previous tweet with wrong map and dashboard link)
-
The Shadowserver Foundation
@Shadowserver
Same botnet now also targeting Netis MW5360 routers with a CVE-2024-22729 CVSS 9.8 command injection RCE
NVD entry: nvd.nist.gov/vuln/detail/CVE-2024-22729
The Shadowserver Foundation
@Shadowserver
We have started observing Zyxel NAS CVE-2024-29973 RCE exploitation attempts by a Mirai-like botnet in our sensors. Zyxel has released patches for this and other vulnerabilities (though affected products are EOL)
zyxel.com/global/en/support/security-advisories/zyxel-sec…
Review for signs of compromise and patch! -
The Shadowserver Foundation
@Shadowserver
Running Redis in the cloud? P2Pinfect malware has been making the rounds recently infecting vulnerable Redis installations: www.cadosecurity.com/blog/from-dormant-to-dangerous-p2pin…
As a reminder, we scan for open Redis installations & now see over 40K daily (with no auth in place): dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
Vast majority of vulnerable Redis servers are on networks of major cloud providers. Sadly, these numbers are steadily going up. If you run Redis please read redis.io/docs/latest/operate/oss_and_stack/management/sec… & ensure adequate access controls!
We share IP data in Open Redis report: www.shadowserver.org/what-we-do/network-reporting/open-re… -
The Shadowserver Foundation
@Shadowserver
Very shortly after vulnerability details were published today we started observing Progress MOVEit Transfer CVE-2024-5806 POST /guestaccess.aspx exploit attempts. If you run MOVEit & have not patched yet - please do so now: community.progress.com/s/article/MOVEit-Transfer-Product-…
NVD: nvd.nist.gov/vuln/detail/CVE-2024-5806
The Shadowserver Foundation
@Shadowserver
Background on CVE-2024-5806: labs.watchtowr.com/auth-bypass-in-un-limited-scenarios-pr…
You can track Progress MOVEit Transfer exposed instances here: dashboard.shadowserver.org/statistics/iot-devices/time-se…
IP Data shared daily in www.shadowserver.org/what-we-do/network-reporting/device-…
(please note this is a population count, not on a vulnerability assessment) -
The Shadowserver Foundation
@Shadowserver
We have started observing Zyxel NAS CVE-2024-29973 RCE exploitation attempts by a Mirai-like botnet in our sensors. Zyxel has released patches for this and other vulnerabilities (though affected products are EOL)
zyxel.com/global/en/support/security-advisories/zyxel-sec…
Review for signs of compromise and patch!
The Shadowserver Foundation
@Shadowserver
... and consider a replacement for these now unsupported devices!
NVD entry: nvd.nist.gov/vuln/detail/CVE-2024-29973
Vulnerability/exploit details are public. -
The Shadowserver Foundation
@Shadowserver
MS CVE-2024-30080 update: You can track increased interest in MSMQ services as seen by our honeypot sensors dashboard.shadowserver.org/statistics/combined/time-serie…
While we have not seen actual exploitation more details about the CVSS 9.8 RCE vulnerability have been made public making exploitation more likely.
The Shadowserver Foundation
@Shadowserver
Critical Microsoft Message Queuing (MSMQ) Remote Code Execution (RCE) vulnerability CVE-2024-30080
~256,000 publicly exposed devices:
dashboard.shadowserver.org/statistics/combined/time-serie…
dashboard.shadowserver.org/statistics/combined/tree/?day=…
Check our free Accessible MSMQ Service Report & patch immediately:
www.shadowserver.org/what-we-do/network-reporting/accessi…
The Shadowserver Foundation
@Shadowserver
Microsoft advisory - msrc.microsoft.com/update-guide/vulnerability/CVE-2024-30080
-
The Shadowserver Foundation
@Shadowserver
We are scanning/sharing VMware vCenter CVE-2024-37079 & CVE-2024-37078 vulnerable instances. 1220 unpatched instances found on 2024-06-20. Note these are only remotely exploitable if DCERPC is also exposed (486 cases).
dashboard.shadowserver.org/statistics/combined/map/?map_t…
Patch: support.broadcom.com/web/ecx/support-content-notification…
The Shadowserver Foundation
@Shadowserver
IP data shared daily (tagged cve-2024-37079) for filtered for your network/constituency in our vulnerable HTTP report - www.shadowserver.org/what-we-do/network-reporting/vulnera…
Hosts with DCERPC exposed (thus exploitable) are also tagged 'vcenter-dcerpc-exposed' -
The Shadowserver Foundation
@Shadowserver
We are very happy to welcome Trivest AG as a new Shadowserver Alliance partner (Bronze tier).
We look forward to raising the bar on cybersecurity together!
Read more about Trivest AG: www.trivest.at
Alliance partnership details: shadowserver.org/partner/ -
The Shadowserver Foundation
@Shadowserver
We are also scanning for SolarWinds Serv-U Directory Transversal Vulnerability CVE-2024-28995. As of 2024-06-15, 942 (492 in US) exposed instances found vulnerable. This is down from 1191 when we first started scanning/reporting.
dashboard.shadowserver.org/statistics/combined/map/?map_t…
dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
With exploit details made public last week, we also started seeing first attempts in our honeypot sensors.
Patch info: www.solarwinds.com/trust-center/security-advisories/cve-2…
Data shared in www.shadowserver.org/what-we-do/network-reporting/vulnera… -
The Shadowserver Foundation
@Shadowserver
Critical Microsoft Message Queuing (MSMQ) Remote Code Execution (RCE) vulnerability CVE-2024-30080
~256,000 publicly exposed devices:
dashboard.shadowserver.org/statistics/combined/time-serie…
dashboard.shadowserver.org/statistics/combined/tree/?day=…
Check our free Accessible MSMQ Service Report & patch immediately:
www.shadowserver.org/what-we-do/network-reporting/accessi…
The Shadowserver Foundation
@Shadowserver
Unauthenticated attackers could send a specially crafted malicious MSMQ packet to publicly exposed devices, causing RCE (CVSS:3.1 score 9.8/10, rated "CRITICAL")
For mitigation advice see:
msrc.microsoft.com/update-guide/vulnerability/CVE-2024-30080 -
The Shadowserver Foundation
@Shadowserver
As part of Operation Endgame we shared a second one-off Special Report on SystemBC bot infections:
shadowserver.org/what-we-do/network-reporting/systembc-hi…
Dashboard map view:
dashboard.shadowserver.org/statistics/combined/map/?map_t…
Details on Operation Endgame coordinated by @EC3Europol:
www.europol.europa.eu/media-press/newsroom/news/largest-e…
The Shadowserver Foundation
@Shadowserver
Data in files with prefix 2024-06-11-special, shared on 2024-06-12. Check your e-mail reports or download via API
-
The Shadowserver Foundation
@Shadowserver
As part of Operation Endgame we shared a second one-off Special Report on IcedID/Latrodectus bot infections:
shadowserver.org/what-we-do/network-reporting/icedid-latr…
Dashboard map view:
dashboard.shadowserver.org/statistics/combined/map/?map_t…
Details on Operation Endgame coordinated by @EC3Europol:
www.europol.europa.eu/media-press/newsroom/news/largest-e…
The Shadowserver Foundation
@Shadowserver
Data in files with prefix 2024-06-10-special, shared on 2024-06-11. Check your e-mail reports or download via API
-
The Shadowserver Foundation
@Shadowserver
Attention! We see multiple IPs testing PHP/PHP-CGI CVE-2024-4577 (Argument Injection Vulnerability) against our honeypot sensors starting today, June 7th. Vulnerability affects PHP running on Windows.
Patches released June 6th: www.php.net
Exploit PoC is public.
The Shadowserver Foundation
@Shadowserver
Details: devco.re/blog/2024/06/06/security-alert-cve-2024-4577-php…
Note currently verified as exploitable on installation with the following locales:
- Traditional Chinese (Code Page 950)
- Simplified Chinese (Code Page 936)
- Japanese (Code Page 932 -
The Shadowserver Foundation
@Shadowserver
We are observing Progress Telerik Report Server CVE-2024-4358 auth bypass exploitation attempts in our honeypot sensors starting 5th June. We have also started reporting out vulnerable versions seen in our scans (89 seen on 5th June out of 95 exposed).
dashboard.shadowserver.org/statistics/combined/tree/?day=…
The Shadowserver Foundation
@Shadowserver
If you receive an alert from us, make sure to check for signs of compromise & update. See docs.telerik.com/report-server/knowledge-base/registratio… for update or mitigation guidance
Exploit PoC is public.
Data on vulnerable instances shared in www.shadowserver.org/what-we-do/network-reporting/vulnera… tagged "telerik" & "cve-2024-4358" -
The Shadowserver Foundation
@Shadowserver
As part of Operation Endgame we shared an initial one-off Special Report on SystemBC bot infections: www.shadowserver.org/what-we-do/network-reporting/systemb…
Dashboard map view: dashboard.shadowserver.org/statistics/combined/map/?map_t…
Details on Operation Endgame coordinated by @EC3Europol: www.europol.europa.eu/media-press/newsroom/news/largest-e…
The Shadowserver Foundation
@Shadowserver
Data in files with 2024-05-31-special prefix, shared on 2024-06-01. Check your e-mail reports or download via API.
-
The Shadowserver Foundation
@Shadowserver
As part of Operation Endgame we shared an initial one-off Special Report on IcedID/Latrodectus bot infections:
www.shadowserver.org/what-we-do/network-reporting/icedid-…
Dashboard map view: dashboard.shadowserver.org/statistics/combined/map/?map_t…
Details on Operation Endgame coordinated by @EC3Europol: www.europol.europa.eu/media-press/newsroom/news/largest-e…
The Shadowserver Foundation
@Shadowserver
Data in files with 2024-05-30-special prefix, shared on 2024-06-01. Check your e-mail reports or download via API.
-
The Shadowserver Foundation
@Shadowserver
Heads up! As part of Operation Endgame we are sharing Smokeloader malware infections in our daily sinkhole reports.
Current Dashboard world map view: dashboard.shadowserver.org/statistics/combined/map/?map_t…
Details on Operation Endgame coordinated by @EC3Europol : www.europol.europa.eu/media-press/newsroom/news/largest-e…
The Shadowserver Foundation
@Shadowserver
Data shared in www.shadowserver.org/what-we-do/network-reporting/sinkhol… filtered by network of the recipient
Data tagged as infection:smokeloader -
The Shadowserver Foundation
@Shadowserver
Attention: We are sharing current 911 SOCKS5 Proxy infections daily in our sinkhole reports. For more details behind the recent disruption led by the US Department of Justice see: www.justice.gov/opa/pr/911-s5-botnet-dismantled-and-its-a…
Dashboard world map view of current infections: dashboard.shadowserver.org/statistics/combined/map/?map_t…
The Shadowserver Foundation
@Shadowserver
Data shared in shadowserver.org/what-we-do/network-reporting/sinkhole-ht… and shadowserver.org/what-we-do/network-reporting/sinkhole-ev… filtered by network of the recipient
tagged as infection: 911-socks5-proxy -
The Shadowserver Foundation
@Shadowserver
As a reminder, you can also track the top vulnerabilities daily that we see being used for exploitation attempts against our honeypot sensors:
dashboard.shadowserver.org/statistics/honeypot/vulnerabil…
(sorted by unique source IPs seen)
The Shadowserver Foundation
@Shadowserver
You can now track Check Point CVE-2024-24919 attack activity on our Dashboard at dashboard.shadowserver.org/statistics/honeypot/vulnerabil…
In the last 72 hours, 26 src IPs seen attempting exploitation.
Make sure to check for compromise and update! Advisory and hot fix details - support.checkpoint.com/results/sk/sk182336
The Shadowserver Foundation
@Shadowserver
You can also view the latest anomalies seen in CVE related attacks by selecting the "Anomaly" category:
dashboard.shadowserver.org/statistics/honeypot/vulnerabil…
You can also switch from the Top 100 by changing the value in the limit field from the default 100. -
The Shadowserver Foundation
@Shadowserver
You can now track Check Point CVE-2024-24919 attack activity on our Dashboard at dashboard.shadowserver.org/statistics/honeypot/vulnerabil…
In the last 72 hours, 26 src IPs seen attempting exploitation.
Make sure to check for compromise and update! Advisory and hot fix details - support.checkpoint.com/results/sk/sk182336
The Shadowserver Foundation
@Shadowserver
(CVE tagging deployed 2024-05-31). We also saw first attempts 30th April
-
The Shadowserver Foundation reposted
U.S. Department of Justice
@TheJusticeDept
911 S5 Botnet Dismantled and Its Administrator Arrested in Coordinated International Operation
Botnet Infected Over 19M IP Addresses to Enable Billions of Dollars in Pandemic and Unemployment Fraud, and Access to Child Exploitation Materials
🔗: www.justice.gov/opa/pr/911-s5-botnet-dismantled-and-its-a… -
The Shadowserver Foundation reposted
Europol
@Europol
🚨Largest ever operation against botnets hits dropper malware ecosystem.
Operation Endgame, coordinated from Europol headquarters, has led to four arrests and the takedown of over 100 servers worldwide.
More information in our press release⤵️
www.europol.europa.eu/media-press/newsroom/news/largest-e… -
The Shadowserver Foundation reposted
craig newmark
@craignewmark
Two years in, the #cybercivildefense initiative is building momentum towards better #cybersecurity for everyone. Join us on Wednesday, May 29 to celebrate the second anniversary, with @CLTCBerkeley, @Shadowserver, @GlobalCyberAlln, and more! Register: www.aspendigital.org/event/building-momentum-two-years-of…
-
The Shadowserver Foundation
@Shadowserver
As of end of last week, we are sharing IPs of PlugX infected machines in our daily sinkhole reports thanks to collaboration with @sekoia_io www.shadowserver.org/what-we-do/network-reporting/sinkhol…
Background at blog.sekoia.io/unplugging-plugx-sinkholing-the-plugx-usb-…
Dashboard stats for 2024-05-06 (~9K hosts daily): dashboard.shadowserver.org/statistics/combined/map/?map_t… -
The Shadowserver Foundation
@Shadowserver
Coming to #rsac? Please join us at the Cyber Nonprofits Reception Tuesday, May 7th 6PM-7:30PM to chat with us and others on the role nonprofits play in making the Internet more secure for everyone. All are welcome! #rsac2024 #cybersecurity
-
The Shadowserver Foundation
@Shadowserver
We are happy to contribute once more with our malware & honeypot statistical data to the @VerizonBusiness Data Breach Investigations Report 2024 report!
Download at www.verizon.com/business/resources/reports/dbir/
#vzdbir -
The Shadowserver Foundation
@Shadowserver
The @Interpol_Cyber 10th Africa Working Group Meeting on Cybercrime for Heads of Units (#10awgc) is ongoing & full on in Abuja. Be in no doubt, cybercrime is taken seriously. Trust & cooperation being forged across #africa! Honoured to contribute #cybersecurity @INTERPOL_HQ
INTERPOL_Cyber
@INTERPOL_Cyber
Great discussions at #10awgc! @INTERPOL_HQ, Law enforcement & partners like @GroupIB & @Shadowserver in combating Africa's cyber threats. Collaboration is key to effectively combating cybercrime! #cybersecurity #africa
-
The Shadowserver Foundation reposted
INTERPOL_Cyber
@INTERPOL_Cyber
Great discussions at #10awgc! @INTERPOL_HQ, Law enforcement & partners like @GroupIB & @Shadowserver in combating Africa's cyber threats. Collaboration is key to effectively combating cybercrime! #cybersecurity #africa
-
The Shadowserver Foundation
@Shadowserver
We are also sharing both vulnerable & compromised Qlik Sense instances daily now:
Dashboard tracker (vulnerable): dashboard.shadowserver.org/statistics/combined/time-serie…
Dashboard tracker (compromised): dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
Attention: we are sharing a one-off special report on Cactus ransomware group campaign targeting Qlik Sense (data viz & business intelligence tool): shadowserver.org/what-we-do/network-reporting/critical-vu…
2894 IPs found vulnerable to CVE-2023-48365
91 IPs found compromised by Cactus ransomware group
The Shadowserver Foundation
@Shadowserver
IP data in our vulnerable HTTP report www.shadowserver.org/what-we-do/network-reporting/vulnera… & compromised website report - www.shadowserver.org/what-we-do/network-reporting/comprom…
-
The Shadowserver Foundation
@Shadowserver
Congratulations @CraigNewmark on receiving the Cyber Philanthropist of the Year Award in recognition of outstanding contributions to cybersecurity and policy through #cybercivildefense!
www.youtube.com/watch?v=V8IRjWiOQy4 -
The Shadowserver Foundation
@Shadowserver
Attention: we are sharing a one-off special report on Cactus ransomware group campaign targeting Qlik Sense (data viz & business intelligence tool): shadowserver.org/what-we-do/network-reporting/critical-vu…
2894 IPs found vulnerable to CVE-2023-48365
91 IPs found compromised by Cactus ransomware group
The Shadowserver Foundation
@Shadowserver
Data for 2024-04-24
Data shared by @foxit & @DIVDnl - thank you for the collaboration!
More details on data and Qlik Sense attacks at: blog.fox-it.com/2024/04/25/sifting-through-the-spines-ide…
You can also accessible track Qlik devices on our Dashboard (no vulnerability assessment): dashboard.shadowserver.org/statistics/iot-devices/time-se…
The Shadowserver Foundation
@Shadowserver
If you receive an alert from us, make sure to investigate for signs of compromise (even if just identified as vulnerable only)
See also original reporting on Cactus ransomware targeting Qlik by @AWNetworks arcticwolf.com/resources/blog/qlik-sense-exploited-in-cac… -
The Shadowserver Foundation
@Shadowserver
We are now sharing CrushFTP CVE-2024-4040 (CrushFTP VFS Sandbox Escape Vulnerability) vulnerable instances. At least 1400 vulnerable on 2024-04-24. CVE-2024-4040 is currently exploited in the wild & on @CISACyber KEV.
Top affected: US, Germany, Canada
dashboard.shadowserver.org/statistics/combined/tree/?day=…Post not available here, view on X
The Shadowserver Foundation
@Shadowserver
Scan is version based.
NVD entry: nvd.nist.gov/vuln/detail/CVE-2024-4040
Track remediation progress with our Dashboard: dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
It's important to stress that this vulnerability enables authentication bypass for administrator account access and full remote code execution! See @rapid7 analysis: www.rapid7.com/blog/post/2024/04/23/etr-unauthenticated-c…
-
The Shadowserver Foundation
@Shadowserver
Attention: Now sharing Palo Alto GlobalProtect instances that we tag as CVE-2024-3400 vulnerable (without the "possible-" prefix). Scanning based on confirming existence of files left behind by exploits.
6634 vulnerable IPs found on 2024-04-20: dashboard.shadowserver.org/statistics/combined/map/?map_t…
The Shadowserver Foundation
@Shadowserver
We are sharing Palo Alto GlobalProtect instances that we believe are possibly vulnerable (there may be mitigations in place) to CVE-2024-3400:
Data in Vulnerable HTTP report shadowserver.org/what-we-do/network-reporting/vulnerable-…
22, 542 possibly vulnerable IPs found on 2024-04-18: dashboard.shadowserver.org/statistics/combined/map/?map_t…
The Shadowserver Foundation
@Shadowserver
Palo Alto GlobalProtect CVE-2024-3400 detailed analysis now public & we started to see attack attempts as of ~14 UTC today (connectivity callback tests). See: security.paloaltonetworks.com/CVE-2024-3400 for patch info/mitigation
We plan to start reporting out potentially vulnerable instances soon
The Shadowserver Foundation
@Shadowserver
Data in Vulnerable HTTP report (we chose not to classify these yet as compromised as this cannot be confirmed by us): shadowserver.org/what-we-do/network-reporting/vulnerable-…
Nevertheless best to assume compromise.
Patch info: security.paloaltonetworks.com/CVE-2024-3400
Thanks to @NCA_KSA for the detection tip! -
The Shadowserver Foundation
@Shadowserver
We are sharing Palo Alto GlobalProtect instances that we believe are possibly vulnerable (there may be mitigations in place) to CVE-2024-3400:
Data in Vulnerable HTTP report shadowserver.org/what-we-do/network-reporting/vulnerable-…
22, 542 possibly vulnerable IPs found on 2024-04-18: dashboard.shadowserver.org/statistics/combined/map/?map_t…
The Shadowserver Foundation
@Shadowserver
Palo Alto GlobalProtect CVE-2024-3400 detailed analysis now public & we started to see attack attempts as of ~14 UTC today (connectivity callback tests). See: security.paloaltonetworks.com/CVE-2024-3400 for patch info/mitigation
We plan to start reporting out potentially vulnerable instances soon
The Shadowserver Foundation
@Shadowserver
Scanning based on ETag/Last-Modified header mappings github.com/noperator/panos-scanner (+additions)
-
The Shadowserver Foundation
@Shadowserver
Great @metpoliceuk led multi-agency success against LabHost fraudsters. Proud to assist another example of LE tenacity - successful public/private/3rd sector partnership in action. Thanks all involved (and our sponsors: your generosity enabled our role)
news.met.police.uk/news/law-enforcement-infiltrates-fraud… -
The Shadowserver Foundation
@Shadowserver
Palo Alto GlobalProtect CVE-2024-3400 detailed analysis now public & we started to see attack attempts as of ~14 UTC today (connectivity callback tests). See: security.paloaltonetworks.com/CVE-2024-3400 for patch info/mitigation
We plan to start reporting out potentially vulnerable instances soon
The Shadowserver Foundation
@Shadowserver
In the meantime you can find information about accessible Palo Alto GlobalProtect (no vulnerability assessment) in our Device ID report - www.shadowserver.org/what-we-do/network-reporting/device-…
Around 156K instances seen per day
dashboard.shadowserver.org/statistics/iot-devices/map/?da…
The Shadowserver Foundation
@Shadowserver
Read more on earlier exploitation at
www.volexity.com/blog/2024/04/12/zero-day-exploitation-of…
unit42.paloaltonetworks.com/cve-2024-3400/ -
The Shadowserver Foundation
@Shadowserver
We have also started sharing out D-Link NAS CVE-2024-3273 vulnerable instances. Around ~2400 vulnerable instances found on 2024-04-11: dashboard.shadowserver.org/statistics/combined/map/?map_t…
Data shared in vulnerable HTTP report - shadowserver.org/what-we-do/network-reporting/vulnerable-…
The Shadowserver Foundation
@Shadowserver
You can also track D-Link CVE-2024-3273 exploitation attempts (includes attempts to propagate Mirai-like botnets) on our Dashboard. For example this query shows the current D-Link related CVEs being exploited dashboard.shadowserver.org/statistics/honeypot/vulnerabil…
(select CVE-2024-3273 tag to view those only)
The Shadowserver Foundation
@Shadowserver
We have started to see scans/exploits from multiple IPs for CVE-2024-3273 (vulnerability in end of life D-Link Network Area Storage devices). This involves chaining of a backdoor & command injection to achieve RCE.
D-Link announcement: supportannouncement.us.dlink.com/security/publication.asp… -
The Shadowserver Foundation
@Shadowserver
We are proud to release #commongoodcyber report together with @CyberAlliance @CyberpeaceInst @FIRSTdotOrg @GlobalCyberAlln @IST_org @theGFCE @ChertoffGroup & @CommonGoodCyber
Read on our joint effort to solve underfunding of cybersecurity non-profits at: commongoodcyber.org/news/launch-of-common-good-cyber-dc-w…
Common Good Cyber
@CommonGoodCyber
Launched in Feb 2024 with the support of @CyberAlliance @CyberpeaceInst @FIRSTdotOrg
@GlobalCyberAlln @IST_org @Shadowserver @theGFCE @ChertoffGroup,
#commongoodcyber will establish sustainable funding solutions for critical #cybersecurity
orgs. 🔻
commongoodcyber.org/news/launch-of-common-good-cyber-dc-w… -
The Shadowserver Foundation
@Shadowserver
You can also track D-Link CVE-2024-3273 exploitation attempts (includes attempts to propagate Mirai-like botnets) on our Dashboard. For example this query shows the current D-Link related CVEs being exploited dashboard.shadowserver.org/statistics/honeypot/vulnerabil…
(select CVE-2024-3273 tag to view those only)
The Shadowserver Foundation
@Shadowserver
We have started to see scans/exploits from multiple IPs for CVE-2024-3273 (vulnerability in end of life D-Link Network Area Storage devices). This involves chaining of a backdoor & command injection to achieve RCE.
D-Link announcement: supportannouncement.us.dlink.com/security/publication.asp…
The Shadowserver Foundation
@Shadowserver
151 source IPs attempting CVE-2024-3273 exploitation last 72 hours.
We will be sharing out IPs of CVE-2024-3273 vulnerable devices in our Vulnerable HTTP report tomorrow (www.shadowserver.org/what-we-do/network-reporting/vulnera…) -
The Shadowserver Foundation reposted
EURid
@EUregistry
We are pleased to announce our partnership with @Shadowserver 🙌🔐With this collaboration, we aim to advance internet security and ensure a safer online environment for users worldwide 🌐 Read more about the partnership efforts: eurid.eu/en/news/eurid-becomes-a-partner-of-the-shadowser…
#doteu #partnership #cybersecuritynews -
The Shadowserver Foundation
@Shadowserver
We have started to see scans/exploits from multiple IPs for CVE-2024-3273 (vulnerability in end of life D-Link Network Area Storage devices). This involves chaining of a backdoor & command injection to achieve RCE.
D-Link announcement: supportannouncement.us.dlink.com/security/publication.asp…
The Shadowserver Foundation
@Shadowserver
Exploit & PoC details are public. As there is no patch for this vulnerability, these devices should be taken offline/replaced or at least have their remote access firewalled.
We are sharing IP data on exposed devices in our Device Identification report: www.shadowserver.org/what-we-do/network-reporting/device-… -
The Shadowserver Foundation
@Shadowserver
We are now scanning/reporting Ivanti Connect Secure instances vulnerable to CVE-2024-21894 (heap overflow potentially leading to RCE) & others described in forums.ivanti.com/s/article/SA-CVE-2024-21894-Heap-Overfl…
~16 500 likely vulnerable (~4.6K in US): dashboard.shadowserver.org/statistics/combined/map/?map_t…
Data in: www.shadowserver.org/what-we-do/network-reporting/vulnera… -
The Shadowserver Foundation
@Shadowserver
Excited to team up with the @HumanityHub, @CyberpeaceInst, connect2trust.nl in a new @DTC_NL funded project to produce a national level assessment of the cyber threat landscape for NGOs in the Netherlands!
www.shadowserver.org/news/non-profit-consortium-launches-… -
The Shadowserver Foundation
@Shadowserver
We are very happy to welcome the @EUregistry EURid as a new Shadowserver Alliance partner (Bronze tier).
We look forward to raising the bar on cybersecurity together!
Read more about EURid: eurid.eu
Alliance partnership details: www.shadowserver.org/partner/ -
The Shadowserver Foundation
@Shadowserver
We have started scanning/reporting Fortinet FortiClient EMS CVE-2023-48788 (pre-auth SQL Injection) vulnerable instances.
130 vulnerable found on 2024-03-23
Top: US with 30 IPs
Dashboard geo breakdown: dashboard.shadowserver.org/statistics/combined/tree/?day=…
Fortinet Advisory: www.fortiguard.com/psirt/FG-IR-24-007
The Shadowserver Foundation
@Shadowserver
Please note detailed vulnerability analysis and PoC is public.
Note we only do a version check on the web interface, exploitation requires access to FmcDaemon on tcp/8013
Data shared in our Vulnerable HTTP report www.shadowserver.org/what-we-do/network-reporting/vulnera… -
The Shadowserver Foundation
@Shadowserver
Today we started sharing data on IPs vulnerable to the novel "Loop DoS" attack discovered by @CISPA. Data is based on DNS, NTP & TFTP protocol scans.
Over 167 500 vulnerable instances found on 2024-03-20.
Stats: dashboard.shadowserver.org/statistics/combined/map/?map_t…
Data shared in: www.shadowserver.org/what-we-do/network-reporting/high-lo…
Christian Rossow (@rossow@infosec.exchange)
@chrossow
We @CISPA discovered that attackers could trigger infinite message loops at the application layer between servers of popular protocols such as DNS, FTP, or NTP. To trigger such an infinite loop, attackers just have to send a single (!) IP-spoofed trigger message. 1/4
The Shadowserver Foundation
@Shadowserver
Data will be shared daily go forwards
DNS ~ 73K, NTP ~80K, TFTP, ~16K
Loop DoS tracker (with protocol breakdown) dashboard.shadowserver.org/statistics/combined/time-serie…
Advisory with mitigation steps: docs.google.com/document/d/1KByZzrdwQhrXGPPCf9tUzERZyRzg0…
The Shadowserver Foundation
@Shadowserver
Big Thanks @chrossow Yepeng (Eric) Pan @CISPA for the collaboration!
-
The Shadowserver Foundation
@Shadowserver
With detailed vulnerability/exploit analysis now published, we have started to observe Fortinet CVE-2024-21762 exploitation attempts executing callbacks as of March 17th UTC. These are currently coming from one IP hitting FortiGate devices.
Investigate for compromise & update!
The Shadowserver Foundation
@Shadowserver
We have added improvements to our Fortinet FortiOS/FortiProxy scans for CVE-2024-21762 vulnerable instances - nearly 150K (!) found on 2024-02-06: dashboard.shadowserver.org/statistics/combined/map/?map_t…
Advisory info: www.fortiguard.com/psirt/FG-IR-24-015
Note: this vulnerability is known to be exploited in the wild
The Shadowserver Foundation
@Shadowserver
Fortinet advisory: www.fortiguard.com/psirt/FG-IR-24-015
We still see over 133 000 vulnerable instances, so a potentially large attack surface dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation
@Shadowserver
We are scanning & sharing VMware ESXi instances which have vulnerabilities that could allow a malicious actor with local admin privileges to escape sandbox protections - www.vmware.com/security/advisories/VMSA-2024-0006.html
Tagged as "cve-2024-22252". Based on version checks, we see ~16.5K vulnerable.
The Shadowserver Foundation
@Shadowserver
Make sure to update your instances!
IP data shared daily in our vulnerable HTTP report - www.shadowserver.org/what-we-do/network-reporting/vulnera…
Dashboard world map view:
dashboard.shadowserver.org/statistics/combined/map/?map_t…
Dashboard tree map view:
dashboard.shadowserver.org/statistics/combined/tree/?day=… -
The Shadowserver Foundation
@Shadowserver
We have added improvements to our Fortinet FortiOS/FortiProxy scans for CVE-2024-21762 vulnerable instances - nearly 150K (!) found on 2024-02-06: dashboard.shadowserver.org/statistics/combined/map/?map_t…
Advisory info: www.fortiguard.com/psirt/FG-IR-24-015
Note: this vulnerability is known to be exploited in the wild
The Shadowserver Foundation
@Shadowserver
IP Data shared daily in our Vulnerable HTTP report: www.shadowserver.org/what-we-do/network-reporting/vulnera…
CVE-2024-21762 vulnerability tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
Thank you @Gi7w0rm & @leak_ix for the support!
The Shadowserver Foundation
@Shadowserver
150 000 found on 2024-03-06 of course (not 2024-02-06)
-
The Shadowserver Foundation
@Shadowserver
We are also scanning & reporting JetBrains TeamCity instances likely vulnerable to CVE-2024-27198/CVE-2024-27199. As of 2024-03-06 1182 instances still possibly vulnerable (patch plugin mitigation may be in place for some of these). Top affected: US (298) & Germany (188)
The Shadowserver Foundation
@Shadowserver
If running JetBrains TeamCity on-prem - make sure to patch for latest CVE-2024-27198 (remote auth bypass) & CVE-2024-27199 vulns NOW!
We started seeing exploitation activity for CVE-2024-27198 around Mar 4th 22:00 UTC. 16 IPs seen scanning so far.
blog.jetbrains.com/teamcity/2024/03/additional-critical-s…
The Shadowserver Foundation
@Shadowserver
IP data shared in our Vulnerable HTTP report (filtered by constituency): shadowserver.org/what-we-do/network-reporting/vulnerable-…
World map (Dashboard): dashboard.shadowserver.org/statistics/combined/map/?map_t…
Vulnerable instance tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
JetBrains advisory: blog.jetbrains.com/teamcity/2024/03/additional-critical-s… -
The Shadowserver Foundation
@Shadowserver
If running JetBrains TeamCity on-prem - make sure to patch for latest CVE-2024-27198 (remote auth bypass) & CVE-2024-27199 vulns NOW!
We started seeing exploitation activity for CVE-2024-27198 around Mar 4th 22:00 UTC. 16 IPs seen scanning so far.
blog.jetbrains.com/teamcity/2024/03/additional-critical-s…
The Shadowserver Foundation
@Shadowserver
Details on the new vulnerabilities discovered by @Rapid7 can be found at www.rapid7.com/blog/post/2024/03/04/etr-cve-2024-27198-an…
-
The Shadowserver Foundation
@Shadowserver
IntelMQ is a solution for Internet defenders for collecting & process security feeds using a message queuing protocol.
Happy to support the latest release of (3.3.0) - now with dynamic configuration to decouple our feed schema changes from IntelMQ releases github.com/certtools/intelmq -
The Shadowserver Foundation
@Shadowserver
You can now also track ConnectWise ScreenConnect CVE-2024-1709 exploitation attempts (by unique source IPs attacking) as seen by our sensors on our Dashboard -dashboard.shadowserver.org/statistics/honeypot/time-serie…
The Shadowserver Foundation
@Shadowserver
We've improved the scanning/detection for vulnerable instances of ConnectWise ScreenConnect (CVE-2024-1709/CVE-2024-1708) - we now see over 8200 vulnerable instances (on 2024-02-21).
CVE-2024-1709 is widely exploited in the wild - 643 IPs seen attacking to date by our sensors. -
The Shadowserver Foundation
@Shadowserver
We've improved the scanning/detection for vulnerable instances of ConnectWise ScreenConnect (CVE-2024-1709/CVE-2024-1708) - we now see over 8200 vulnerable instances (on 2024-02-21).
CVE-2024-1709 is widely exploited in the wild - 643 IPs seen attacking to date by our sensors.
The Shadowserver Foundation
@Shadowserver
Data has so far been shared tagged as "vulnerable-screenconnect" but will now be tagged "cve-2024-1709" starting from today's scans, now that a CVE has been assigned: www.shadowserver.org/what-we-do/network-reporting/vulnera…
World map: dashboard.shadowserver.org/statistics/combined/map/?map_t…
Tree map: dashboard.shadowserver.org/statistics/combined/tree/?day=…
The Shadowserver Foundation
@Shadowserver
CVE-2024-1709 is also now on the @CISACyber KEV list - cisa.gov/known-exploited-vulnerabilities-catalog
Vendor advisory connectwise.com/company/trust/security-bulletins/connectw…
If you receive an alert from us on your instances assume compromise -
The Shadowserver Foundation
@Shadowserver
Last week we also started sharing RoundCube CVE-2023-43770 vulnerable servers. This vulnerability was recently added to @CISACyber Known Exploited Vulnerabilities (KEV) catalog.
As of 2024-02-20 we still see ~39K instances vulnerable. Investigate for any breaches & update!
The Shadowserver Foundation
@Shadowserver
Latest RoundCube release news and updates - roundcube.net/news/
IPs shared in shadowserver.org/what-we-do/network-reporting/vulnerable-…
Dashboard World Map: dashboard.shadowserver.org/statistics/combined/map/?map_t…
CVE-2023-43770 tracker: dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation
@Shadowserver
Please note: with the PoC now public we are already picking up the initial exploit request in our honeypot sensors ... check for signs of compromise (new users added) and patch!
The Shadowserver Foundation
@Shadowserver
~3800 vulnerable ConnectWise ScreenConnect instances (authentication bypass using an alternate path or channel (CVSS 10) & path traversal (CVSS 8.4)) www.connectwise.com/company/trust/security-bulletins/conn…
IP data in:
www.shadowserver.org/what-we-do/network-reporting/vulnera…
~93% instances of ScreenConnect seen on 2024-02-20 still vulnerable:
The Shadowserver Foundation
@Shadowserver
Using ScreenConnect? ConnectWise has released a security bulletin regarding critical vulnerabilities (incl. a CVSS 10 RCE): www.connectwise.com/company/trust/security-bulletins/conn…
You can track accessible instances on our Dashboard: dashboard.shadowserver.org/statistics/iot-devices/map/?da…
~4300 accessible daily (no vulnerability assessment) -
The Shadowserver Foundation
@Shadowserver
~3800 vulnerable ConnectWise ScreenConnect instances (authentication bypass using an alternate path or channel (CVSS 10) & path traversal (CVSS 8.4)) www.connectwise.com/company/trust/security-bulletins/conn…
IP data in:
www.shadowserver.org/what-we-do/network-reporting/vulnera…
~93% instances of ScreenConnect seen on 2024-02-20 still vulnerable:
The Shadowserver Foundation
@Shadowserver
Using ScreenConnect? ConnectWise has released a security bulletin regarding critical vulnerabilities (incl. a CVSS 10 RCE): www.connectwise.com/company/trust/security-bulletins/conn…
You can track accessible instances on our Dashboard: dashboard.shadowserver.org/statistics/iot-devices/map/?da…
~4300 accessible daily (no vulnerability assessment)
The Shadowserver Foundation
@Shadowserver
Dashboard World Map link: dashboard.shadowserver.org/statistics/combined/map/?map_t…
-
The Shadowserver Foundation
@Shadowserver
Using ScreenConnect? ConnectWise has released a security bulletin regarding critical vulnerabilities (incl. a CVSS 10 RCE): www.connectwise.com/company/trust/security-bulletins/conn…
You can track accessible instances on our Dashboard: dashboard.shadowserver.org/statistics/iot-devices/map/?da…
~4300 accessible daily (no vulnerability assessment)
The Shadowserver Foundation
@Shadowserver
Accessible instances shared in our Device Identification report: www.shadowserver.org/what-we-do/network-reporting/device-…
We will also be adding vulnerable instances to our Vulnerable HTTP report going out tomorrow (2024-02-21): www.shadowserver.org/what-we-do/network-reporting/vulnera… -
The Shadowserver Foundation reposted
BleepingComputer
@BleepinComputer
LockBit ransomware disrupted by global police operation - @serghei
www.bleepingcomputer.com/news/security/lockbit-ransomware…
www.bleepingcomputer.com/news/security/lockbit-ransomware… -
The Shadowserver Foundation
@Shadowserver
Lots of scanning activity past week (especially on 2024-02-16 & 2024-02-19) checking for Ivanti CVE-2024-21887 RCE, with thousands of src IPs involved.
Ivanti attacks by CVE (by IP): dashboard.shadowserver.org/statistics/honeypot/time-serie…
We still see over 800 vulnerable instances: dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation reposted
Common Good Cyber
@CommonGoodCyber
Meet our speakers for the 'Illustration of the Problem' panel attempting to build a shared understanding of the funding challenges in the #cybersecurity landscape.
↘️
commongoodcyber.org/introducing-the-speakers-for-our-firs…
@kierstentodt
@ONCD
@Shadowserver
@Columbia
@MITREcorp
@joshcorman -
The Shadowserver Foundation
@Shadowserver
Over the weekend we started reporting Microsoft Exchange versions vulnerable to CVE-2024-21410. On 2024-02-17 around 97K vulnerable or possibly vulnerable where the latter means a vulnerable version but may have mitigation applied. Microsoft guidance: msrc.microsoft.com/update-guide/vulnerability/CVE-2024-21410
The Shadowserver Foundation
@Shadowserver
Data shared in our Vulnerable Exchange Server report - www.shadowserver.org/what-we-do/network-reporting/vulnera…
Count of vulnerable instances on 2024-02-17: 28.5K
Count of possibly vulnerable instances on 2024-02-17: 68.5K
Please note this vulnerability is on the CISA KEV - www.cisa.gov/known-exploited-vulnerabilities-catalog
The Shadowserver Foundation
@Shadowserver
Top 20 countries most affected: dashboard.shadowserver.org/statistics/combined/visualisat…
-
The Shadowserver Foundation
@Shadowserver
We are proud to have assisted (along with partners) in the US DoJ & FBI-led disruption of the Moobot malware botnet comprised of SOHO routers utilized by APT 28/Fancy Bear: www.justice.gov/opa/pr/justice-department-conducts-court-…
Data on infections shared in Sinkhole HTTP Events report: www.shadowserver.org/what-we-do/network-reporting/sinkhol…
The Shadowserver Foundation
@Shadowserver
Tagged as "moobot".
Over 3500 infected initially (2024-01-27). Current numbers: over 2350 infected, US highest.
Geo breakdown: dashboard.shadowserver.org/statistics/combined/tree/?day=…
Infection tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
Interested in whether your network/contituency is impacted? You can subscribe to our FREE daily threat intelligence feeds and secure your network infrastructure - www.shadowserver.org/what-we-do/network-reporting/get-rep…
-
The Shadowserver Foundation
@Shadowserver
We are scanning & sharing JetBrains TeamCity CVE-2024-23917 vulnerable instances (CVSS 9.8 authentication bypass RCE in versions < 2023.11.3). 1052 vulnerable on 2024-02-14.
Top: US (332) & Germany (120).
Patch: www.jetbrains.com/privacy-security/issues-fixed/
World Map: dashboard.shadowserver.org/statistics/combined/map/?map_t…
The Shadowserver Foundation
@Shadowserver
IP data in www.shadowserver.org/what-we-do/network-reporting/vulnera…
This is out of 1805 seen exposed on 2024-02-14
See: dashboard.shadowserver.org/statistics/iot-devices/time-se…
Please note previous CVE-2023-42793 was exploited by state actors. Can we avoid a repeat please? www.cisa.gov/news-events/cybersecurity-advisories/aa23-347a -
The Shadowserver Foundation
@Shadowserver
Code execution attempts for CVE-2023-47218 aimed at '/cgi-bin/quick/quick.cgi' appeared shortly after @rapid7 disclosure. Currently limited to 'id' & '/etc/passwd' checks from a couple of IPs - as seen in our sensors ... Make sure to patch your QNAP www.qnap.com/en/security-advisory/qsa-23-57
Stephen Fewer
@stephenfewer
QNAP have patched an unauthenticated command injection vuln we reported, CVE-2023-47218, affecting QTS and QuTS Hero based systems. Vuln is in a component quick.cgi, which helps configure uninitialized systems. Read our disclosure here: www.rapid7.com/blog/post/2024/02/13/cve-2023-47218-qnap-q…
-
The Shadowserver Foundation
@Shadowserver
We have added improvements to our Ivanti Connect Secure VPN scans to better detect unpatched versions vulnerable to CVE-2024-22024 (~3900 found) & CVE-2024-21887 (~ 1000 found). IP data shared in www.shadowserver.org/what-we-do/network-reporting/vulnera…
CVE-2024-22024 geo breakdown: dashboard.shadowserver.org/statistics/combined/map/?map_t… -
The Shadowserver Foundation
@Shadowserver
We are very excited to welcome @csis_cyber as a new Shadowserver Alliance partner (Bronze tier).
We look forward to raising the bar on cybersecurity together!
Read more about CSIS Security Group at csis.com
More about the Alliance: shadowserver.org/partner/ -
The Shadowserver Foundation
@Shadowserver
Ivanti Connect Secure CVE-2024-22024 activity: we started seeing exploitation attempts to '/dana-na/auth/saml-sso.cgi' Feb 9th, around 8 UTC, shortly after PoC publication. These are primarily callback tests. 47 IPs seen to date.
See Ivanti advisory: forums.ivanti.com/s/article/CVE-2024-22024-XXE-for-Ivanti…
The Shadowserver Foundation
@Shadowserver
Track CVE-2024-22024 exploitation (and other Ivanti product targeted attacks) - dashboard.shadowserver.org/statistics/honeypot/time-serie…
(note tag for CVE-2024-22024 was added 2024-02-10 so Dashboard does NOT display 2024-02-09 attack stats) -
The Shadowserver Foundation
@Shadowserver
As of 2024-02-09 we are also scanning & reporting Ivanti Connect Secure instances that show signs of compromise as described by @orangecyberdef in Journey to the core of the DSLog backdoor: www.orangecyberdefense.com/fileadmin/general/pdf/Ivanti_C…
Data in: www.shadowserver.org/what-we-do/network-reporting/comprom…
2024-02-09 scan: 141 instances
The Shadowserver Foundation
@Shadowserver
There is little IP overlap with previously reported implants/webshells
The Shadowserver Foundation
@Shadowserver
World map:
dashboard.shadowserver.org/statistics/combined/map/?map_t…
Tracker: dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation
@Shadowserver
Honoured by UK Deputy Prime Mininster @OliverDowden kind words during speech yesterday:
www.gov.uk/government/speeches/deputy-prime-minister-oliv…
Support the #pallmallprocess declaration:
www.gov.uk/government/publications/the-pall-mall-process-…
Cabinet Office
@cabinetofficeuk
Today @OliverDowden spoke at the first conference on proliferation and malicious use of cyber intrusion tools.
The UK is committed to working with like-minded nations on this issue including through our new initiative, the Pall Mall Process. @francediplo -
The Shadowserver Foundation
@Shadowserver
Proud to be part of joint 🇬🇧 🇫🇷 led #pallmallprocess, with many great partners, to tackle the proliferation and misuse of commercial #cyber intrusion tools
Will Middleton
@WillMiddletonUK
Delighted to launch the Pall Mall Process in London this morning - a joint UK-France multi-stakeholder initiative to tackle the proliferation and misuse of commercial cyber intrusion tools. #pallmallprocess @LondonCyber
-
The Shadowserver Foundation
@Shadowserver
Thrilled to receive much needed support to enhance our free public benefit services, and 🇬🇧 showing leadership for non-profit #cybersecurity funding. Looking forward to more cybersecurity capacity building globally, and helping to better secure the Internet together #ukcssf
LondonCyber
@LondonCyber
The 🇬🇧 is enhancing our strategic partnerships with non-profit organisations. We are proud to announce a £1m uplift to @Shadowserver to expand access to early warning systems, and provide cyber security support to those impacted by cyber-attacks #ukcssf
-
The Shadowserver Foundation reposted
LondonCyber
@LondonCyber
The 🇬🇧 is enhancing our strategic partnerships with non-profit organisations. We are proud to announce a £1m uplift to @Shadowserver to expand access to early warning systems, and provide cyber security support to those impacted by cyber-attacks #ukcssf
-
The Shadowserver Foundation
@Shadowserver
We are sharing 153 Ivanti Connect Secure instances still known vulnerable to CVE-2024-21893/CVE-2024-21887 (as of late 2024-02-05 UTC) in a one-off special report - www.shadowserver.org/what-we-do/network-reporting/vulnera…
Make sure to act if you receive an alert from us (also assume compromise!)
The Shadowserver Foundation
@Shadowserver
Security update info from Ivanti: www.ivanti.com/blog/security-update-for-ivanti-connect-se…
CISA guidance: www.cisa.gov/news-events/alerts/2024/01/30/updated-new-so… -
The Shadowserver Foundation
@Shadowserver
We observed CVE-2024-21893 exploitation using '/dana-na/auth/saml-logout.cgi' on Feb 2nd hours before @Rapid7 posting & unsurprisingly lots to '/dana-ws/saml20.ws' after publication. This includes reverse shell attempts & other checks. To date, over 170 attacking IPs involved
Stephen Fewer
@stephenfewer
We have published our AttackerKB @rapid7 analysis for CVE-2024-21893, an SSRF vulnerability in the SAML component of Ivanti Connect Secure, that has recently been exploited in the wild, allowing attackers bypass the mitigation for an earlier exploit chain. attackerkb.com/topics/FGlK1TVnB2/cve-2024-21893/rapid7-an…
The Shadowserver Foundation
@Shadowserver
As of today you can also track CVE-2024-21893 exploitation on our Dashboard at dashboard.shadowserver.org/statistics/honeypot/monitoring…
Ivanti products exploitation attempts by CVE over time (now includes CVE-2024-21893, note tag added 2024-02-03):
dashboard.shadowserver.org/statistics/honeypot/time-serie…
The Shadowserver Foundation
@Shadowserver
Patch info: www.ivanti.com/blog/security-update-for-ivanti-connect-se…
CISA Alert & Guidance - www.cisa.gov/news-events/alerts/2024/01/30/updated-new-so… -
The Shadowserver Foundation
@Shadowserver
As an INTERPOL Gateway Partner we congratulate @INTERPOL_HQ @INTERPOL_Cyber on this effort and we’re happy we could support the actions. We applaud such coordinated efforts to tackle global cybercrime!
www.interpol.int/en/News-and-Events/News/2024/INTERPOL-le…
INTERPOL
@INTERPOL_HQ
⚡️ Dismantling the infrastructure behind phishing, banking malware, and ransomware attacks:
🌐 55 countries
🔎 1,300 malicious servers identified
🚨 31 arrests
🚔 70 additional suspects
www.interpol.int/en/News-and-Events/News/2024/INTERPOL-le… -
The Shadowserver Foundation reposted
CISA Cyber
@CISACyber
🚩 Threat actors are actively exploiting #ivanti Connect Secure and Policy Secure Gateways vulnerabilities. Read more and apply @CISAgov’s NEW recommended mitigations at cisa.gov/news-events/alerts/2024/01/30/new-mitigations-de… #cybersecurity #infosec
-
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
Around 45K exposed Jenkins instances vulnerable to CVE-2024-23897 (Arbitrary file read vulnerability through the CLI can lead to RCE). If you run Jenkins & receive an alert from us make sure to read Jenkins advisory: www.jenkins.io/security/advisory/2024-01-24/
World map: dashboard.shadowserver.org/statistics/combined/map/?map_t… -
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
Heads up! We are sharing out a second Special Report on Compromised SSH hosts detected through leakage of malicious public SSH keys placed on them by attackers: www.shadowserver.org/what-we-do/network-reporting/comprom…
This time 10020 compromised hosts found. Top countries US (3K), China (2.9K), Singapore (423)
The Shadowserver Foundation
@Shadowserver
We are sharing out a Special Report on Compromised SSH hosts detected through leakage of malicious public SSH keys placed on them by attackers: www.shadowserver.org/what-we-do/network-reporting/comprom…
3327 compromised hosts detected on IPv4/IPv6 using this methodology.
For background: rushter.com/blog/public-ssh-keys/ -
The Shadowserver Foundation
@Shadowserver
Heads up! We are sharing out a second Special Report on Compromised SSH hosts detected through leakage of malicious public SSH keys placed on them by attackers: www.shadowserver.org/what-we-do/network-reporting/comprom…
This time 10020 compromised hosts found. Top countries US (3K), China (2.9K), Singapore (423)
The Shadowserver Foundation
@Shadowserver
We are sharing out a Special Report on Compromised SSH hosts detected through leakage of malicious public SSH keys placed on them by attackers: www.shadowserver.org/what-we-do/network-reporting/comprom…
3327 compromised hosts detected on IPv4/IPv6 using this methodology.
For background: rushter.com/blog/public-ssh-keys/
The Shadowserver Foundation
@Shadowserver
If you receive a report from us on compromised IPs in your network/constituency make sure to investigate (check for wider compromise) & remediate!
Tree map view attached with country breakdown.
Data shared in collaboration with an external partner. -
The Shadowserver Foundation
@Shadowserver
Around 45K exposed Jenkins instances vulnerable to CVE-2024-23897 (Arbitrary file read vulnerability through the CLI can lead to RCE). If you run Jenkins & receive an alert from us make sure to read Jenkins advisory: www.jenkins.io/security/advisory/2024-01-24/
World map: dashboard.shadowserver.org/statistics/combined/map/?map_t…
The Shadowserver Foundation
@Shadowserver
Data on vulnerable instances shared in www.shadowserver.org/what-we-do/network-reporting/vulnera… (filtered for your network/constituency), tagged cve-2024-23897
-
The Shadowserver Foundation
@Shadowserver
Currently 28 Fortra GoAnywhere MFT instances we believe vulnerable to attacks from the public Internet (CVE-2024-0204). However 770 unpatched instances can be still be found (SSH banner check) - 2024-01-25 scans.
Vulnerable (potentially exploitable): dashboard.shadowserver.org/statistics/combined/tree/?day=…
The Shadowserver Foundation
@Shadowserver
Still unpatched: dashboard.shadowserver.org/statistics/combined/tree/?day=…
The Shadowserver Foundation
@Shadowserver
Data on vulnerable (exploitable due to admin panel exposure) instances is shared in our Vulnerable HTTP report (tagged cve-2024-0204): shadowserver.org/what-we-do/network-reporting/vulnerable-…
Data on unpatched instances shared in our Accessible SSH report (tagged cve-2024-0204): shadowserver.org/what-we-do/network-reporting/accessible-…
The Shadowserver Foundation
@Shadowserver
Fortra Advisory: www.fortra.com/security/advisory/fi-2024-001
-
The Shadowserver Foundation
@Shadowserver
Track Atlassian CVE-2023-22527 (and other CVE) attacks on our Dashboard (by unique source IPs attempting exploitation), for example: dashboard.shadowserver.org/statistics/honeypot/time-serie…
Updated daily.
The Shadowserver Foundation
@Shadowserver
We are seeing Atlassian Confluence CVE-2023-22527 pre-auth template injection RCE attempts since 2024-01-19. Over 600 IPs seen attacking so far (testing callback attempts and 'whoami' execution). Vulnerability affects out of date versions of Confluence: confluence.atlassian.com/security/cve-2023-22527-rce-remo…
The Shadowserver Foundation
@Shadowserver
(please note we first started seeing CVE-2023-22527 attacks on 2024-01-19, but tagging was added 3 days later on 2024-01-22 and these earlier attempts are not reflected on the chart)
-
The Shadowserver Foundation
@Shadowserver
Unsurprisingly lots of Fortra GoAnywhere MFT CVE-2024-0204 related exploit attempts (based on public PoC exploit) happening. Over 120 IPs seen so far ... However, we think unlikely these will be successful on larger scale as not many admin portals exposed (only ~50, most patched)
The Shadowserver Foundation
@Shadowserver
Fortra advisory and patch info: www.fortra.com/security/advisory/fi-2024-001
NVD entry: nvd.nist.gov/vuln/detail/CVE-2024-0204 -
The Shadowserver Foundation
@Shadowserver
Running GitLab? We are sharing instances vulnerable to CVE-2023-7028 (Account Takeover via Password Reset without user interactions) - 5379 instances found worldwide (on 2024-01-23). Top: US (964) & Germany (730)
Check for signs of compromise and patch: about.gitlab.com/releases/2024/01/11/critical-security-re…
The Shadowserver Foundation
@Shadowserver
IP Data shared in our Vulnerable HTTP Report (filtered by your network/constituency): shadowserver.org/what-we-do/network-reporting/vulnerable-……
Dashboard World Map: dashboard.shadowserver.org/statistics/combined/map/?map_t… -
The Shadowserver Foundation
@Shadowserver
As of 2024-01-18 we are scanning for NextGen Healthcare Mirth Connect appliances vulnerable to CVE-2023-43208 (pre-auth RCE). We see 441 vulnerable (2024-01-22 scan). Data shared in www.shadowserver.org/what-we-do/network-reporting/vulnera…
Make sure to upgrade to latest version: github.com/nextgenhealthcare/connect/wiki/Upgrading -
The Shadowserver Foundation reposted
craig newmark
@craignewmark
Introducing the #commongoodcyber to secure the Internet for all through sustainable funding for cybersecurity in the public interest. Join the workshop at National Press Club, D.C., on Feb 26-27th: www.commongoodcyber.org #cybercivildefense @CommonGoodCyber
-
The Shadowserver Foundation reposted
Common Good Cyber
@CommonGoodCyber
We are a collaborative effort led by @GlobalCyberAlln, @CyberAlliance, @CyberpeaceInst, @FIRSTdotOrg, @IST_org, and @Shadowserver to fortify the Internet's foundations, ensuring availability and security for generations to come.
Join us on Feb 26-27 in DC: commongoodcyber.org/events/ -
The Shadowserver Foundation
@Shadowserver
2024-01-21 results update: 372 Ivanti Connect Secure VPN compromised with credential stealers
Tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
Tree map (country breakdown):
dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
Latest numbers: 276 credential stealer compromised Ivanti Connect Secure VPN (2024-01-20 results) after some scan fixes (thanks to @Gi7w0rm for helping with that discovery)
Tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
Tree map with Geo results: dashboard.shadowserver.org/statistics/combined/tree/?day=…
The Shadowserver Foundation
@Shadowserver
Additional IPs compromised with credential stealers injected into vulnerable Ivanti Connect Secure VPN devices now shared daily in our Compromised Website report www.shadowserver.org/what-we-do/network-reporting/comprom…
168 compromised IPs found in our scans on 2023-01-19: dashboard.shadowserver.org/statistics/combined/tree/?day=… -
The Shadowserver Foundation
@Shadowserver
We are seeing Atlassian Confluence CVE-2023-22527 pre-auth template injection RCE attempts since 2024-01-19. Over 600 IPs seen attacking so far (testing callback attempts and 'whoami' execution). Vulnerability affects out of date versions of Confluence: confluence.atlassian.com/security/cve-2023-22527-rce-remo…
The Shadowserver Foundation
@Shadowserver
If you have exposed Atlassian Confluence instances make sure they are up to date (and if not check for signs of compromise!)
11,1K accessible: dashboard.shadowserver.org/statistics/iot-devices/time-se…
Info on exposed Atlassian Confluence instances in our Device Identification report: www.shadowserver.org/what-we-do/network-reporting/device-… -
The Shadowserver Foundation
@Shadowserver
Latest numbers: 276 credential stealer compromised Ivanti Connect Secure VPN (2024-01-20 results) after some scan fixes (thanks to @Gi7w0rm for helping with that discovery)
Tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
Tree map with Geo results: dashboard.shadowserver.org/statistics/combined/tree/?day=…
The Shadowserver Foundation
@Shadowserver
Additional IPs compromised with credential stealers injected into vulnerable Ivanti Connect Secure VPN devices now shared daily in our Compromised Website report www.shadowserver.org/what-we-do/network-reporting/comprom…
168 compromised IPs found in our scans on 2023-01-19: dashboard.shadowserver.org/statistics/combined/tree/?day=… -
The Shadowserver Foundation
@Shadowserver
Additional IPs compromised with credential stealers injected into vulnerable Ivanti Connect Secure VPN devices now shared daily in our Compromised Website report www.shadowserver.org/what-we-do/network-reporting/comprom…
168 compromised IPs found in our scans on 2023-01-19: dashboard.shadowserver.org/statistics/combined/tree/?day=…
The Shadowserver Foundation
@Shadowserver
Total for 2023-01-19: 550 IPs still compromised (includes GIFTEDVISITOR variant webshells) - dashboard.shadowserver.org/statistics/combined/time-serie…
Recovery guidance from Ivanti - forums.ivanti.com/s/article/Recovery-Steps-Related-to-CVE…
The Shadowserver Foundation
@Shadowserver
2024-01-19 is of course the correct date ;)
-
The Shadowserver Foundation
@Shadowserver
Lots of exploitation of Ivanti Connect Secure VPN CVE-2023-46805 & CVE-2024-21887 seen by our sensors. Assume compromise on exposed endpoints if you have not applied the mitigation. You can track Ivanti CVE exploitation attempts on our Dashboard:
dashboard.shadowserver.org/statistics/honeypot/time-serie…
The Shadowserver Foundation
@Shadowserver
You can track latest trends in CVE exploitation on our Dashboard at dashboard.shadowserver.org/statistics/honeypot/monitoring…
-
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
In collaboration with @Volexity we have added daily scans & reports of compromised Ivanti Connect Secure VPN instances. Data shared in our Compromised Website report, tagged "ivanti-connect-secure".
609 IPs found on 2023-01-16: www.shadowserver.org/what-we-do/network-reporting/comprom…
dashboard.shadowserver.org/statistics/combined/tree/?day=…
Volexity
@Volexity
.@Volexity provides an update on its Ivanti Connect Secure VPN report concerning chained exploitation of CVE-2024-21887/CVE-2023-46805. Based on new data, 1700+ devices have been compromised following widespread exploitation. Details: www.volexity.com/blog/2024/01/15/ivanti-connect-secure-vp…
#dfir #threatintel -
The Shadowserver Foundation
@Shadowserver
We are proud to have our team members contribute to these discussions and publication! #cybercivildefense
Download "Generative A.I. Regulation and Cybersecurity: A Global View of Policymaking" at
www.aspendigital.org/wp-content/uploads/2024/01/Aspen-Dig…
Aspen Digital
@AspenDigital
Our #aspencyber Global Group has analyzed current regulatory efforts and limitations at the intersection of #generativeai x #cybersecurity. The resulting guidance for #governments around the 🌎🌍🌏 across liabilities, safeguards, and standards is out now: www.aspendigital.org/report/generative-ai-regulation-and-…
-
The Shadowserver Foundation
@Shadowserver
Another odd increase in BadCandy Cisco IOS XE implants seen in our daily scans. If you receive a report on your network on a Cisco device, we would appreciate feedback! (IP data shared in www.shadowserver.org/what-we-do/network-reporting/comprom…)
dashboard.shadowserver.org/statistics/combined/time-serie…
Geo breakdown: dashboard.shadowserver.org/statistics/combined/tree/?day=…
The Shadowserver Foundation
@Shadowserver
After a steady drop for over a month, Cisco IOS XE implants have increased between 2023-11-30 and 2023-12-02. Now at 23.5K instances. Large increases in Mexico & Chile. Possible new campaign?
dashboard.shadowserver.org/statistics/combined/time-serie…
(background: blog.talosintelligence.com/active-exploitation-of-cisco-i…) -
The Shadowserver Foundation
@Shadowserver
In collaboration with @Volexity we have added daily scans & reports of compromised Ivanti Connect Secure VPN instances. Data shared in our Compromised Website report, tagged "ivanti-connect-secure".
609 IPs found on 2023-01-16: www.shadowserver.org/what-we-do/network-reporting/comprom…
dashboard.shadowserver.org/statistics/combined/tree/?day=…
Volexity
@Volexity
.@Volexity provides an update on its Ivanti Connect Secure VPN report concerning chained exploitation of CVE-2024-21887/CVE-2023-46805. Based on new data, 1700+ devices have been compromised following widespread exploitation. Details: www.volexity.com/blog/2024/01/15/ivanti-connect-secure-vp…
#dfir #threatintel -
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
We are very excited to support the Dominican Republic National Cyber Security Center (@CNCSRD) their newly launched automatic notification service for vulnerabilities & exposure in cyberspace, serving public & private entities in the Dominican Republic!
cncs.gob.do/gobierno-lanza-servicio-de-alerta-automatica-… -
The Shadowserver Foundation
@Shadowserver
Data on vulnerable Ivanti Connect Secure devices now available on our Dashboard, for example
World map: dashboard.shadowserver.org/statistics/combined/map/?map_t…
Tree map:
dashboard.shadowserver.org/statistics/combined/tree/?day=…
Tracker:
dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
Scanning for vulnerable Ivanti Connect Secure (CVE-2023-46805 & CVE-2024-21887) instances has been added to our daily scan list. 6809 found vulnerable for 2024-01-15 scans using methodology from @watchtowrcyber - labs.watchtowr.com/welcome-to-2024-the-sslvpn-chaos-conti…)
More details: www.shadowserver.org/what-we-do/network-reporting/vulnera… -
The Shadowserver Foundation
@Shadowserver
Scanning for vulnerable Ivanti Connect Secure (CVE-2023-46805 & CVE-2024-21887) instances has been added to our daily scan list. 6809 found vulnerable for 2024-01-15 scans using methodology from @watchtowrcyber - labs.watchtowr.com/welcome-to-2024-the-sslvpn-chaos-conti…)
More details: www.shadowserver.org/what-we-do/network-reporting/vulnera…
The Shadowserver Foundation
@Shadowserver
These are instances that we believe have NOT applied the mitigation provided by Ivanti: forums.ivanti.com/s/article/KB-CVE-2023-46805-Authenticat…
IP data will start being reported out tomorrow (2024-01-16) along with Dashboard stats updates.
Subscribe for free data for your network: www.shadowserver.org/what-we-do/network-reporting/get-rep… -
The Shadowserver Foundation
@Shadowserver
We are very excited to support the Dominican Republic National Cyber Security Center (@CNCSRD) their newly launched automatic notification service for vulnerabilities & exposure in cyberspace, serving public & private entities in the Dominican Republic!
cncs.gob.do/gobierno-lanza-servicio-de-alerta-automatica-… -
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
If you are searching for exposed Ivanti Connect Secure appliances in your network/constituency, you can get a daily breakdown of these (amongst other devices) in our device identification report: www.shadowserver.org/what-we-do/network-reporting/device-…
(vendor is set to "Pulse Secure")
Over 17.1K exposed
Volexity
@Volexity
.@Volexity detected an incident where it discovered a threat actor chained 2 #0days in Ivanti Connect Secure, CVE-2023-46805/CVE-2024-21887, to achieve RCE, modifying components of the software to backdoor the device.
www.volexity.com/blog/2024/01/10/active-exploitation-of-t…
#dfir #threatintel #memoryforensics -
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
We are starting regular reporting of ransomware victims (published by ransomware actors on their public data leak sites) to National CSIRTs & LE agencies subscribed to our daily feeds - www.shadowserver.org/what-we-do/network-reporting/ransomw…
Enabled as part of EU ISF MISP-LEA project: misp-lea.org -
The Shadowserver Foundation reposted
MISP (@misp@misp-community.org)
@MISPProject
Bridging the Gap: Introducing MISP Airgap for Secure Environments
🔗 www.misp-project.org/2024/01/12/MISP-airgap.html/
🔗 github.com/MISP/misp-airgap
#misp #opensource #airgap #threatintelligence #infosecurity
@circl_lu @Shadowserver -
The Shadowserver Foundation
@Shadowserver
If you are searching for exposed Ivanti Connect Secure appliances in your network/constituency, you can get a daily breakdown of these (amongst other devices) in our device identification report: www.shadowserver.org/what-we-do/network-reporting/device-…
(vendor is set to "Pulse Secure")
Over 17.1K exposed
Volexity
@Volexity
.@Volexity detected an incident where it discovered a threat actor chained 2 #0days in Ivanti Connect Secure, CVE-2023-46805/CVE-2024-21887, to achieve RCE, modifying components of the software to backdoor the device.
www.volexity.com/blog/2024/01/10/active-exploitation-of-t…
#dfir #threatintel #memoryforensics
The Shadowserver Foundation
@Shadowserver
Note these are just population results, not vulnerability checks!
Ivanti Connect Secure exposure tracker - dashboard.shadowserver.org/statistics/iot-devices/time-se…
Geo breakdown:
dashboard.shadowserver.org/statistics/iot-devices/tree/?d… -
The Shadowserver Foundation
@Shadowserver
We are starting regular reporting of ransomware victims (published by ransomware actors on their public data leak sites) to National CSIRTs & LE agencies subscribed to our daily feeds - www.shadowserver.org/what-we-do/network-reporting/ransomw…
Enabled as part of EU ISF MISP-LEA project: misp-lea.org -
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
We are expanding our honeypot sensor feeds to include reporting of IPs scanning or exploiting IKEv2 (Internet Key Exchange) services: www.shadowserver.org/what-we-do/network-reporting/honeypo…
May include Zyxel CVE-2023-28771, a CVSS 9.8 RCE
IKEv2 scanner tracker (~800 src IPs/day): dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation
@Shadowserver
We are expanding our honeypot sensor feeds to include reporting of IPs scanning or exploiting IKEv2 (Internet Key Exchange) services: www.shadowserver.org/what-we-do/network-reporting/honeypo…
May include Zyxel CVE-2023-28771, a CVSS 9.8 RCE
IKEv2 scanner tracker (~800 src IPs/day): dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
We are expanding our honeypot sensor based feeds to include reporting of IPs scanning or exploiting Android Debug Bridge (ADB) services, a common target for botnets & other threat actors: www.shadowserver.org/what-we-do/network-reporting/honeypo…
ADB attack tracker (~700 src IPs daily): dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
We have started sharing IPs scanning or attempting to exploit RocketMQ services (for example, exploiting CVE-2023-33246, a CVSS 9.8 RCE) based on our honeypot sensors: www.shadowserver.org/what-we-do/network-reporting/honeypo…
RocketMQ scanner tracker (~400 src IPs on a given day): dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
SSH Terrapin attack: 60.1% vulnerable on IPv6 vs 50.8% on IPv4
You can track these by selecting ssh or ssh6 on our time series chart as the source, cve-2023-48795+ as the tag
SSH IPv6 CVE-2023-48795:
dashboard.shadowserver.org/statistics/combined/time-serie…
SSH IPv4 CVE-2023-48795:
dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
We are sharing SSH CVE-2023-48795 (Terrapin attack) vulnerable instances found in our IPv4/IPv6 scans in our Accessible SSH report: www.shadowserver.org/what-we-do/network-reporting/accessi…
Nearly 11M instances (by unique IP) found vulnerable (~52%).
Background on the vulnerability: terrapin-attack.com -
The Shadowserver Foundation
@Shadowserver
We have started sharing IPs scanning or attempting to exploit RocketMQ services (for example, exploiting CVE-2023-33246, a CVSS 9.8 RCE) based on our honeypot sensors: www.shadowserver.org/what-we-do/network-reporting/honeypo…
RocketMQ scanner tracker (~400 src IPs on a given day): dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
We are sharing SSH CVE-2023-48795 (Terrapin attack) vulnerable instances found in our IPv4/IPv6 scans in our Accessible SSH report: www.shadowserver.org/what-we-do/network-reporting/accessi…
Nearly 11M instances (by unique IP) found vulnerable (~52%).
Background on the vulnerability: terrapin-attack.com -
The Shadowserver Foundation
@Shadowserver
We are expanding our honeypot sensor based feeds to include reporting of IPs scanning or exploiting Android Debug Bridge (ADB) services, a common target for botnets & other threat actors: www.shadowserver.org/what-we-do/network-reporting/honeypo…
ADB attack tracker (~700 src IPs daily): dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
There are over 6000 accessible ADB instances that these scanners/attackers are searching for: dashboard.shadowserver.org/statistics/combined/time-serie…
We report out accessible ADB instances (ie. what the attackers are searching for) here: shadowserver.org/what-we-do/network-reporting/accessible-…
Make sure to block external access to ADB! -
The Shadowserver Foundation
@Shadowserver
SSH Terrapin attack: 60.1% vulnerable on IPv6 vs 50.8% on IPv4
You can track these by selecting ssh or ssh6 on our time series chart as the source, cve-2023-48795+ as the tag
SSH IPv6 CVE-2023-48795:
dashboard.shadowserver.org/statistics/combined/time-serie…
SSH IPv4 CVE-2023-48795:
dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
We are sharing SSH CVE-2023-48795 (Terrapin attack) vulnerable instances found in our IPv4/IPv6 scans in our Accessible SSH report: www.shadowserver.org/what-we-do/network-reporting/accessi…
Nearly 11M instances (by unique IP) found vulnerable (~52%).
Background on the vulnerability: terrapin-attack.com -
The Shadowserver Foundation
@Shadowserver
We are sharing SSH CVE-2023-48795 (Terrapin attack) vulnerable instances found in our IPv4/IPv6 scans in our Accessible SSH report: www.shadowserver.org/what-we-do/network-reporting/accessi…
Nearly 11M instances (by unique IP) found vulnerable (~52%).
Background on the vulnerability: terrapin-attack.com
The Shadowserver Foundation
@Shadowserver
World map: dashboard.shadowserver.org/statistics/combined/map/?map_t…
Tree map with geo breakdown:
dashboard.shadowserver.org/statistics/combined/tree/?day=… -
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
We have seen quite a few scans using PoC published for Apache OFBiz CVE-2023-49070 (CVSS 9.8 pre-auth RCE) patched start of Dec 2023: issues.apache.org/jira/browse/OFBIZ-12812
That patch apparently failed to remove root cause of the issue so update again for CVE-2023-51467! www.openwall.com/lists/oss-security/2023/12/26/3
SonicWall
@SonicWall
🚨 SonicWall Capture Labs threat research team discovers critical Apache OFBiz zero-day - AuthBiz (CVE-2023-51467)
Read more ➡️ blog.sonicwall.com/en-us/2023/12/sonicwall-discovers-crit… -
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
Our daily free feeds in Common Event Format? No problem! We have published a CEF logging script for you to use. Check out github.com/The-Shadowserver-Foundation/api_utils/tree/mai…
Feedback welcome!
Also if you use Elasticsearch or Splunk, have a look at our support there too ...
The Shadowserver Foundation
@Shadowserver
Using Splunk or Elasticsearch? We have released a Splunk Modular Input Add-On for indexing our daily feeds & ECS logging script to make it easier to integrate with our reports API.
Splunk integration: github.com/The-Shadowserver-Foundation/api_utils/tree/mai…
Elasticsearch integration: github.com/The-Shadowserver-Foundation/api_utils/tree/mai… -
The Shadowserver Foundation
@Shadowserver
We have seen quite a few scans using PoC published for Apache OFBiz CVE-2023-49070 (CVSS 9.8 pre-auth RCE) patched start of Dec 2023: issues.apache.org/jira/browse/OFBIZ-12812
That patch apparently failed to remove root cause of the issue so update again for CVE-2023-51467! www.openwall.com/lists/oss-security/2023/12/26/3
SonicWall
@SonicWall
🚨 SonicWall Capture Labs threat research team discovers critical Apache OFBiz zero-day - AuthBiz (CVE-2023-51467)
Read more ➡️ blog.sonicwall.com/en-us/2023/12/sonicwall-discovers-crit… -
The Shadowserver Foundation
@Shadowserver
Our daily free feeds in Common Event Format? No problem! We have published a CEF logging script for you to use. Check out github.com/The-Shadowserver-Foundation/api_utils/tree/mai…
Feedback welcome!
Also if you use Elasticsearch or Splunk, have a look at our support there too ...
The Shadowserver Foundation
@Shadowserver
Using Splunk or Elasticsearch? We have released a Splunk Modular Input Add-On for indexing our daily feeds & ECS logging script to make it easier to integrate with our reports API.
Splunk integration: github.com/The-Shadowserver-Foundation/api_utils/tree/mai…
Elasticsearch integration: github.com/The-Shadowserver-Foundation/api_utils/tree/mai… -
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
We are sharing out a Special Report on Compromised SSH hosts detected through leakage of malicious public SSH keys placed on them by attackers: www.shadowserver.org/what-we-do/network-reporting/comprom…
3327 compromised hosts detected on IPv4/IPv6 using this methodology.
For background: rushter.com/blog/public-ssh-keys/ -
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
Heads-up! New free daily report now going out on post-exploitation frameworks (includes Cobalt Strike, Sliver and over a dozen others) observed in daily scans:
www.shadowserver.org/what-we-do/network-reporting/post-ex…
Currently over 1200 unique IPs reported daily.
Country distribution: dashboard.shadowserver.org/statistics/combined/map/?map_t… -
The Shadowserver Foundation
@Shadowserver
Heads-up! New free daily report now going out on post-exploitation frameworks (includes Cobalt Strike, Sliver and over a dozen others) observed in daily scans:
www.shadowserver.org/what-we-do/network-reporting/post-ex…
Currently over 1200 unique IPs reported daily.
Country distribution: dashboard.shadowserver.org/statistics/combined/map/?map_t…
The Shadowserver Foundation
@Shadowserver
You can also track the various framework families on our Dashboard (updated once per day):
dashboard.shadowserver.org/statistics/combined/time-serie…
(for related Dashboard searches use 'beacon' as source)
Data shared as part of EU Internal Security Fund MISP-LEA project: misp-lea.org @circl_lu -
The Shadowserver Foundation
@Shadowserver
We are sharing out a Special Report on Compromised SSH hosts detected through leakage of malicious public SSH keys placed on them by attackers: www.shadowserver.org/what-we-do/network-reporting/comprom…
3327 compromised hosts detected on IPv4/IPv6 using this methodology.
For background: rushter.com/blog/public-ssh-keys/
The Shadowserver Foundation
@Shadowserver
Top countries affected: US (535), Germany (486), Netherlands (333).
If you receive such a report for your network/constituency, make sure to investigate!
Note: Data sourced through an external trusted partner. -
The Shadowserver Foundation reposted
Nonprofit Cyber
@NonprofitCyber
Explore the pledges of our members
@CRESTadvocate @GlobalCyberAlln @IST_org @Shadowserver to the Accra Call👉gc3b.org/accra-call-pledges/.
@theGC3B
#cyberresilience
#accracall
#techforgood -
The Shadowserver Foundation
@Shadowserver
Still over 230 vulnerable instances in the United States alone on 2023-12-13: dashboard.shadowserver.org/statistics/combined/map/?map_t…
IP data shared daily for your network/constituency in our free feeds since 2023-09-29 - www.shadowserver.org/what-we-do/network-reporting/vulnera… -
The Shadowserver Foundation
@Shadowserver
We still see nearly 800 JetBrains TeamCity unpatched instances worldwide unfortunately: dashboard.shadowserver.org/statistics/combined/time-serie…
You can also track CVE-2023-42793 attacks by source here:
dashboard.shadowserver.org/statistics/honeypot/time-serie…
If you receive an alert from us, make sure to investigate for signs of compromise
The Shadowserver Foundation
@Shadowserver
We are reporting JetBrains TeamCity CI/CD CVE-2023-42793 vulnerable instances (critical authentication bypass). 1296 unique IPs found vulnerable on 2023-09-30. Data shared in our Vulnerable HTTP report www.shadowserver.org/what-we-do/network-reporting/vulnera…
Patch information - blog.jetbrains.com/teamcity/2023/09/cve-2023-42793-vulner…
The Shadowserver Foundation
@Shadowserver
Vulnerable instances shared daily in our Vulnerable HTTP report: www.shadowserver.org/what-we-do/network-reporting/vulnera…
CVE-2023-42793 has been observed also used by Russian Foreign Intelligence Service (SVR) actors: www.gov.pl/attachment/f111510e-f9b6-40e7-b3f0-7cae28c8ff38
www.cisa.gov/news-events/cybersecurity-advisories/aa23-347a -
The Shadowserver Foundation
@Shadowserver
We have started to see attempts to use PoC exploit code published for Apache Struts CVE-2023-50164 CVSS 9.8 RCE in our sensors (a few src IPs). Make sure to update your Struts installs ...
Apache Security Bulletin: cwiki.apache.org/confluence/display/WW/S2-066
NVD entry: nvd.nist.gov/vuln/detail/CVE-2023-50164 -
The Shadowserver Foundation
@Shadowserver
Great to be at #gc3b23 to endorse the official launch of the #accracall - encouraging global action to improve #cyberresilience and promoting #cybercapacitybuilding that supports broader development goals, more effectively serving the needs and priorities of developing countries
The Shadowserver Foundation
@Shadowserver
Shadowserver pledges free #cyberthreatintelligence to help improve #cyberresilience globally, and provide qualitative and quantitative data for #cybercapacitybuilding impact evaluation
www.shadowserver.org/what-we-do/network-reporting/
dashboard.shadowserver.org
The Shadowserver Foundation
@Shadowserver
Read the full details of the #gc3b23 #accracall and find out how you can join 50 leading countries and organizations in this new global effort at:
gc3b.org/news/read-the-full-accra-call-for-cyber-resilien… -
The Shadowserver Foundation
@Shadowserver
We are sharing Qlik Sense instances observed in scans in our daily Device ID report (no vuln assessment!) - www.shadowserver.org/what-we-do/network-reporting/device-…
4525 IPs seen on 2023-12-09.
Qlik Sense CVE-2023-41265 & CVE-2023-41266 were recently added to @CISACyber known exploited vulnerabilities list.
The Shadowserver Foundation
@Shadowserver
Qlik tracker: dashboard.shadowserver.org/statistics/iot-devices/time-se…
Check for signs of compromise & upgrade - community.qlik.com/t5/Official-Support-Articles/Critical-…
See also CVE-2023-48365 patch: community.qlik.com/t5/Official-Support-Articles/Critical-…
These vulnerabilities were reported by @AWNetworks to be used for deploying Cactus ransomware arcticwolf.com/resources/blog/cve-2023-41265-cve-2023-412… -
The Shadowserver Foundation
@Shadowserver
After a steady drop for over a month, Cisco IOS XE implants have increased between 2023-11-30 and 2023-12-02. Now at 23.5K instances. Large increases in Mexico & Chile. Possible new campaign?
dashboard.shadowserver.org/statistics/combined/time-serie…
(background: blog.talosintelligence.com/active-exploitation-of-cisco-i…)
The Shadowserver Foundation
@Shadowserver
Thank you @NCA_KSA for the notice!
-
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
At least 539 Unitronics PLC instances (port 20256/tcp) still publicly exposed worldwide (2023-12-02 scan). Unitronics PLC instances have been targeted recently as part of attacks against Water & Wastewater systems. (see @CISACyber @WaterISAC alert: www.cisa.gov/news-events/alerts/2023/11/28/exploitation-u…)
-
The Shadowserver Foundation
@Shadowserver
At least 539 Unitronics PLC instances (port 20256/tcp) still publicly exposed worldwide (2023-12-02 scan). Unitronics PLC instances have been targeted recently as part of attacks against Water & Wastewater systems. (see @CISACyber @WaterISAC alert: www.cisa.gov/news-events/alerts/2023/11/28/exploitation-u…)
The Shadowserver Foundation
@Shadowserver
IP data shared in our Accessible ICS report: www.shadowserver.org/what-we-do/network-reporting/accessi…
Unitronics PLC exposure tracker: dashboard.shadowserver.org/statistics/combined/time-serie… (note drop between 2023-12-01 & 2023-12-02 scan results due to honeypots being removed from results)
Country breakdown: dashboard.shadowserver.org/statistics/combined/tree/?day=…
The Shadowserver Foundation
@Shadowserver
See also: www.cisa.gov/news-events/cybersecurity-advisories/aa23-335a for additional details, including mitigation advice and IoCs
@NCSC UK statement following exploitation of Unitronics PLCs: www.ncsc.gov.uk/news/ncsc-statement-following-exploitatio… -
The Shadowserver Foundation
@Shadowserver
Note as of 2023-12-02 our sensors are seeing CVE-2023-49103 scans/exploitation attempts that utilize a modified request that makes vulnerable docker installations of ownCloud exploitable in a default configuration.
See @rapid7 blog for more details: www.rapid7.com/blog/post/2023/12/01/etr-cve-2023-49103-cr…
The Shadowserver Foundation
@Shadowserver
Not surprisingly given ease of exploitation we have started seeing OwnCloud CVE-2023-49103 attempts. This is a CVSS 10 disclosure of sensitive credentials & configs in containerized deployments. Please follow ownCloud advisory mitigation steps:
owncloud.com/security-advisories/disclosure-of-sensitive-…
The Shadowserver Foundation
@Shadowserver
CVE-2023-49103 exploitation tracker: dashboard.shadowserver.org/statistics/honeypot/time-serie…
-
The Shadowserver Foundation
@Shadowserver
We have also started scanning & sharing F5 BIG-IP instances that remain vulnerable to CVE-2023-46747. 382 vulnerable instances found on 2023-11-29. This vulnerability is actively exploited & on @CISACyber KEV list. Assume compromise if you receive a report from us!
The Shadowserver Foundation
@Shadowserver
Not surprisingly given its inclusion in the Nuclei scanner, since Oct 30th we are seeing F5 BIG-IP CVE-2023-46747 attempts in our honeypot sensors. Make sure to review your system for signs of compromise and patch before more threat actors jump in: my.f5.com/manage/s/article/K000137353
The Shadowserver Foundation
@Shadowserver
Thank you to sicra.no for the collaboration!
IP data shared in Vulnerable HTTP report: www.shadowserver.org/what-we-do/network-reporting/vulnera…
Vulnerable instance tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
NVD entry: nvd.nist.gov/vuln/detail/CVE-2023-46747
F5 advisory: my.f5.com/manage/s/article/K000137353 -
The Shadowserver Foundation
@Shadowserver
We are sharing ownCloud instances we see in our scans (no vuln assessment, only accessibility) in our Device Identification report www.shadowserver.org/what-we-do/network-reporting/device-…
Currently over 11K IPs being reported out (we are also working on adding additional fingerprints)
dashboard.shadowserver.org/statistics/iot-devices/map/?da…
The Shadowserver Foundation
@Shadowserver
Not surprisingly given ease of exploitation we have started seeing OwnCloud CVE-2023-49103 attempts. This is a CVSS 10 disclosure of sensitive credentials & configs in containerized deployments. Please follow ownCloud advisory mitigation steps:
owncloud.com/security-advisories/disclosure-of-sensitive-…
The Shadowserver Foundation
@Shadowserver
Please also note other reported ownCloud vulnerabilities with CVSS > 9:
owncloud.com/security-advisories/webdav-api-authenticatio…
owncloud.com/security-advisories/subdomain-validation-byp… -
The Shadowserver Foundation
@Shadowserver
Not surprisingly given ease of exploitation we have started seeing OwnCloud CVE-2023-49103 attempts. This is a CVSS 10 disclosure of sensitive credentials & configs in containerized deployments. Please follow ownCloud advisory mitigation steps:
owncloud.com/security-advisories/disclosure-of-sensitive-… -
The Shadowserver Foundation
@Shadowserver
We are excited to welcome @cybercentre_ca as a new Shadowserver Alliance partner (Gold tier). We look forward to raising the bar on cybersecurity together!
Read more about the Canadian Centre for Cyber Security: www.cyber.gc.ca -
The Shadowserver Foundation
@Shadowserver
You can track top exploited vulnerabilities as seen by our sensors on our Dashboard: dashboard.shadowserver.org/statistics/honeypot/monitoring…
Track CVEs exploited over time (you can select particular vendors or src/dst of attacks by country): dashboard.shadowserver.org/statistics/honeypot/time-serie…
By vendor attacked: dashboard.shadowserver.org/statistics/honeypot/time-serie…
Dark Reading
@DarkReading
CISA's Known Exploited Vulnerabilities catalog shouldn't be your only source of threat intelligence. @RobLemos digs into why. Exploited Vulnerabilities Can Take Months to Make KEV List informatech.co/47mvBCB #drtheedge
-
The Shadowserver Foundation
@Shadowserver
We are sharing out Microsoft Exchange Servers that have reached end-of-life (ie, end of extended support, with no security updates issued).
Still nearly 20K IPs found (!). Top countries: US & Germany.
Country breakdown:
dashboard.shadowserver.org/statistics/combined/map/?map_t…
The Shadowserver Foundation
@Shadowserver
IPs shared in Vulnerable Exchange Report for your constituency, tagged "eol"
www.shadowserver.org/what-we-do/network-reporting/vulnera…
Tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
Definitely worth upgrading or considering alternatives
MS Fixed Lifecycle Policy - learn.microsoft.com/en-us/lifecycle/policies/fixed
See also: endoflife.date/msexchange -
The Shadowserver Foundation
@Shadowserver
Significantly more visibility into Socks5Systemz proxy botnet infections now - over 245K infections on 2023-11-22. IPs shared in Sinkhole HTTP Event report: www.shadowserver.org/what-we-do/network-reporting/vulnera…
dashboard.shadowserver.org/statistics/combined/time-serie…
If you receive an alert investigate your systems!
#cybercivildefense
The Shadowserver Foundation
@Shadowserver
We are sharing out Socks5Systemz proxy botnet infected IPs in our free daily SInkhole HTTP Event reports www.shadowserver.org/what-we-do/network-reporting/sinkhol….
Over 36K IPs seen infected 2023-11-12.
Thank you @Bitsight for the collaboration!
Socks5Systemz Infection tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
Country Socks5Systemz infection breakdown:
dashboard.shadowserver.org/statistics/combined/tree/?day=… -
The Shadowserver Foundation
@Shadowserver
We are scanning for CVE-2023-43177 vulnerable CrushFTP instances. Over 700 likely vulnerable (out of 4161 total found so far). This pre-auth RCE vuln was patched in August: www.crushftp.com/crush10wiki/Wiki.jsp?page=Update
If you receive a CVE-2023-43177 vulnerable report from us make sure to patch!
The Shadowserver Foundation
@Shadowserver
Minimum safe version according to CrushFTP is now 10.5.6.
Shared in: www.shadowserver.org/what-we-do/network-reporting/vulnera…
NVD entry: nvd.nist.gov/vuln/detail/CVE-2023-43177
Please note that technical details on how to exploit this vulnerability have been published.
Dashboard tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
We appreciate feedback on any of the vulnerable CrushFTP findings - if you believe a report was an FP please let us know!
-
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
Over a month after Citrix advisory publication NetScaler CVE-2023-4966 exploitation attempts continue to be one of the most common attacks seen by our honeypot sensor network.
dashboard.shadowserver.org/statistics/honeypot/time-serie…
If you are running NetScaler & did not patch initially assume compromise.
The Shadowserver Foundation
@Shadowserver
Sharp increase in queries for "/oauth/idp/.well-known/openid-configuration" endpoint associated with Citrix NetScaler CVE-2023-4966 (leaking of session tokens) observed by our honeypot sensors. This is after recent @assetnote www.assetnote.io/resources/research/citrix-bleed-leaking-… publication.
-
The Shadowserver Foundation
@Shadowserver
Over a month after Citrix advisory publication NetScaler CVE-2023-4966 exploitation attempts continue to be one of the most common attacks seen by our honeypot sensor network.
dashboard.shadowserver.org/statistics/honeypot/time-serie…
If you are running NetScaler & did not patch initially assume compromise.
The Shadowserver Foundation
@Shadowserver
Sharp increase in queries for "/oauth/idp/.well-known/openid-configuration" endpoint associated with Citrix NetScaler CVE-2023-4966 (leaking of session tokens) observed by our honeypot sensors. This is after recent @assetnote www.assetnote.io/resources/research/citrix-bleed-leaking-… publication.
The Shadowserver Foundation
@Shadowserver
NVD entry: nvd.nist.gov/vuln/detail/CVE-2023-4966
Citrix advisory: support.citrix.com/article/CTX579459/netscaler-adc-and-ne…
LockBit ransomware attribution www.bleepingcomputer.com/news/security/lockbit-ransomware…
The Shadowserver Foundation
@Shadowserver
We share free daily IP data for your network/constituency on:
1) All seen Citrix NetScaler devices in our Device Identification report: www.shadowserver.org/what-we-do/network-reporting/device-…
2) Vulnerable Citrix NetScaler devices we can identify:
www.shadowserver.org/what-we-do/network-reporting/vulnera… -
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
We are reporting Microsoft Exchange Server CVE-2023-36439 vulnerable IPs (post-auth RCE). Over 63K vulnerable worldwide. Patch released Nov 14th - msrc.microsoft.com/update-guide/vulnerability/CVE-2023-36439
IP data for your constituency in www.shadowserver.org/what-we-do/network-reporting/vulnera…
Dashboard tracker - dashboard.shadowserver.org/statistics/combined/time-serie… -
The Shadowserver Foundation
@Shadowserver
We are reporting Microsoft Exchange Server CVE-2023-36439 vulnerable IPs (post-auth RCE). Over 63K vulnerable worldwide. Patch released Nov 14th - msrc.microsoft.com/update-guide/vulnerability/CVE-2023-36439
IP data for your constituency in www.shadowserver.org/what-we-do/network-reporting/vulnera…
Dashboard tracker - dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
Vulnerable IP breakdown (world map) - dashboard.shadowserver.org/statistics/combined/map/?map_t…
Vulnerable IP breakdown (tree map) - dashboard.shadowserver.org/statistics/combined/tree/?day=…
NVD entry: nvd.nist.gov/vuln/detail/CVE-2023-36439 -
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
To make it easier for orgs to consume & prioritize on our daily reports we are introducing report & event severity levels. Each report/event will have a severity level assigned.
Announcement: www.shadowserver.org/news/introducing-report-severity-lev…
Report to severity level mappings:
github.com/The-Shadowserver-Foundation/report_schema/blob… -
The Shadowserver Foundation
@Shadowserver
We are sharing out Socks5Systemz proxy botnet infected IPs in our free daily SInkhole HTTP Event reports www.shadowserver.org/what-we-do/network-reporting/sinkhol….
Over 36K IPs seen infected 2023-11-12.
Thank you @Bitsight for the collaboration!
Socks5Systemz Infection tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
Background: www.bitsight.com/blog/unveiling-socks5systemz-rise-new-pr…
-
The Shadowserver Foundation
@Shadowserver
Track exposed SysAid instances on our Dashboard dashboard.shadowserver.org/statistics/iot-devices/time-se… (over 100 exposed)
Track exposed Juniper J-Web interfaces at dashboard.shadowserver.org/statistics/iot-devices/time-se…
IP Data shared for free for your network/constituency daily in our Device Identification report www.shadowserver.org/what-we-do/network-reporting/device-…
CISA Cyber
@CISACyber
⚠️Security Alert: 6 #vulnerabilities have been added to the #kev. Prioritize remediation!
🚨#cve-2023-47246 #sysaid
🚨CVE-2023-36844/45 #juniperos
🚨CVE-2023-36846/47/51 #juniperos
#cybersecurity #infosec
go.dhs.gov/oDm
The Shadowserver Foundation
@Shadowserver
We first warned of the Juniper J-Web exploitation attempts (using the now KEV listed vulns) in Aug 2023: x.com/Shadowserver/status/1696512418036486246
Additional background: www.bleepingcomputer.com/news/security/cisa-warns-of-acti…
The Shadowserver Foundation
@Shadowserver
Since 25th August we are seeing exploitation attempts from multiple IPs for Juniper J-Web CVE-2023-36844 (& friends) targeting /webauth_operation.php endpoint. Same day an exploit POC was published. This involves combining lower severity CVEs to achieve pre-auth RCE.
-
The Shadowserver Foundation reposted
The Shadowserver Foundation
@Shadowserver
Using Splunk or Elasticsearch? We have released a Splunk Modular Input Add-On for indexing our daily feeds & ECS logging script to make it easier to integrate with our reports API.
Splunk integration: github.com/The-Shadowserver-Foundation/api_utils/tree/mai…
Elasticsearch integration: github.com/The-Shadowserver-Foundation/api_utils/tree/mai… -
The Shadowserver Foundation
@Shadowserver
New entry in @CISACyber KEV list: CVE-2023-29552 is being abused for amplification DDoS attacks. You can find externally accessible SLP services in your constituency in our free daily reports since Feb 2023.
IP data shared in Accessible SLP report www.shadowserver.org/what-we-do/network-reporting/accessi…
SecurityWeek
@SecurityWeek
CISA Says SLP Vulnerability Allowing Amplified DoS Attacks Exploited in the Wild www.securityweek.com/cisa-says-slp-vulnerability-allowing…
The Shadowserver Foundation
@Shadowserver
Dashboard tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
www.cisa.gov/news-events/alerts/2023/04/25/abuse-service-…
The Shadowserver Foundation
@Shadowserver
You can also track the actual reflected DDoS attacks abusing SLP on our Dashboard too (relatively few versus other services such as DNS or NTP): dashboard.shadowserver.org/statistics/combined/time-serie…
-
The Shadowserver Foundation reposted
Nonprofit Cyber
@NonprofitCyber
We're proud to announce #worldmorethanapasswordday on November 10 and the release of the Common Guidance on Passwords with the support of 90 signatories from 20 countries.
Read our press release: nonprofitcyber.org/nonprofit-cyber-launches-world-more-th…
Join the global movement! -
The Shadowserver Foundation
@Shadowserver
Using Splunk or Elasticsearch? We have released a Splunk Modular Input Add-On for indexing our daily feeds & ECS logging script to make it easier to integrate with our reports API.
Splunk integration: github.com/The-Shadowserver-Foundation/api_utils/tree/mai…
Elasticsearch integration: github.com/The-Shadowserver-Foundation/api_utils/tree/mai…
The Shadowserver Foundation
@Shadowserver
We appreciate testing, feedback and improvement suggestions!
-
The Shadowserver Foundation
@Shadowserver
UPDATE: Cisco IOS XE Web UI CVE-2023-20198 version 3 BadCandy implant detection scans up and running (hat tip @leak_ix). Total implant detections at around 26.5K unique IPs.
Dashboard tracker: dashboard.shadowserver.org/statistics/combined/time-serie…
World map:
dashboard.shadowserver.org/statistics/combined/map/?map_t…
The Shadowserver Foundation
@Shadowserver
UPDATE: Cisco IOS XE Web UI CVE-2023-20198 version 2 BadCandy implant detection has dropped sharply 2023-11-03: dashboard.shadowserver.org/statistics/combined/time-serie…
Note on 2023-11-02 Cisco updated their threat advisory on CVE-2023-20198/BadCandy with observations of a version 3:
blog.talosintelligence.com/active-exploitation-of-cisco-i…
The Shadowserver Foundation
@Shadowserver
Reminder: all compromised IP data for your network/constituency (free subscription needed) is shared for free daily in our Compromised Website report: www.shadowserver.org/what-we-do/network-reporting/comprom…
-
The Shadowserver Foundation
@Shadowserver
We are excited to welcome @CERT_at as a new Shadowserver Alliance partner (Bronze tier). We look forward to raising the bar on cybersecurity together!
Read more about the Austrian National CERT: cert.at
More about the Alliance: shadowserver.org/partner/ -
The Shadowserver Foundation
@Shadowserver
We are also scanning & reporting VMware vCenter CVE-2023-34048 (CVSS 9.8 RCE) IPs. On 2023-11-04, 1402 instances without patches. Out of these 741 have DCERPC accessible (not firewalled) which means they are remotely exploitable! www.shadowserver.org/what-we-do/network-reporting/vulnera…
dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
VMware advisory & patches (released 2023-10-25) www.vmware.com/security/advisories/VMSA-2023-0023.html
NVD entry: nvd.nist.gov/vuln/detail/CVE-2023-34048 -
The Shadowserver Foundation
@Shadowserver
UPDATE: Cisco IOS XE Web UI CVE-2023-20198 version 2 BadCandy implant detection has dropped sharply 2023-11-03: dashboard.shadowserver.org/statistics/combined/time-serie…
Note on 2023-11-02 Cisco updated their threat advisory on CVE-2023-20198/BadCandy with observations of a version 3:
blog.talosintelligence.com/active-exploitation-of-cisco-i…
The Shadowserver Foundation
@Shadowserver
Over 2200 unique IPs seen with CVE-2023-20198 attempts on 2023-11-03 in our honeypot sensors (many different actors now probing)
dashboard.shadowserver.org/statistics/honeypot/monitoring… -
The Shadowserver Foundation
@Shadowserver
Took a while but the fiber is finally fixed, so we should be fully back ...
The Shadowserver Foundation
@Shadowserver
Attention: A fiber cable cut has impacted some of our services, which includes access to our APIs (including our reports API) and public Dashboard amongst others. We are working with our provider to fix the issue ASAP and restore our full services.
-
The Shadowserver Foundation
@Shadowserver
Count for 2023-11-02: 3580 vulnerable to CVE-2023-46604 out of 8931 seen (increase due to us scanning additional ports)
dashboard.shadowserver.org/statistics/combined/time-serie…
The Shadowserver Foundation
@Shadowserver
We are scanning & reporting out Apache ActiveMQ instances vulnerable to CVE-2023-46604, a deserialization of untrusted data RCE. 3329 vulnerable brokers found out of 7249 accessible (2023-10-30).
Data in new daily Accessible ActiveMQ Service report: www.shadowserver.org/what-we-do/network-reporting/accessi… -
The Shadowserver Foundation
@Shadowserver
36 IPs seen last 24 hours testing for Atlassian Confluence CVE-2023-22518 critical RCE. POST requests to '/json/setup-restore.action' & '/confluence/json/setup-restore.action' endpoints & file upload based check. Make sure to check your Confluence instance and patch.
The Shadowserver Foundation
@Shadowserver
PoC code is now public.
Patch information from Atlassian: confluence.atlassian.com/security/cve-2023-22518-improper…
We scan for exposed Atlassian Confluence instances & report these in our Device Identification Report www.shadowserver.org/what-we-do/network-reporting/device-…
We see around around 24K exposed (not necessarily vulnerable)
The Shadowserver Foundation
@Shadowserver
Dashboard tracker for exposed instances - dashboard.shadowserver.org/statistics/iot-devices/time-se…
-
The Shadowserver Foundation
@Shadowserver
Attention: A fiber cable cut has impacted some of our services, which includes access to our APIs (including our reports API) and public Dashboard amongst others. We are working with our provider to fix the issue ASAP and restore our full services.
-
The Shadowserver Foundation
@Shadowserver
Not surprisingly given its inclusion in the Nuclei scanner, since Oct 30th we are seeing F5 BIG-IP CVE-2023-46747 attempts in our honeypot sensors. Make sure to review your system for signs of compromise and patch before more threat actors jump in: my.f5.com/manage/s/article/K000137353
-
The Shadowserver Foundation
@Shadowserver
We are scanning & reporting out Apache ActiveMQ instances vulnerable to CVE-2023-46604, a deserialization of untrusted data RCE. 3329 vulnerable brokers found out of 7249 accessible (2023-10-30).
Data in new daily Accessible ActiveMQ Service report: www.shadowserver.org/what-we-do/network-reporting/accessi… -
The Shadowserver Foundation
@Shadowserver
Sharp increase in queries for "/oauth/idp/.well-known/openid-configuration" endpoint associated with Citrix NetScaler CVE-2023-4966 (leaking of session tokens) observed by our honeypot sensors. This is after recent @assetnote www.assetnote.io/resources/research/citrix-bleed-leaking-… publication.
-
The Shadowserver Foundation
@Shadowserver
To make it easier for orgs to consume & prioritize on our daily reports we are introducing report & event severity levels. Each report/event will have a severity level assigned.
Announcement: www.shadowserver.org/news/introducing-report-severity-lev…
Report to severity level mappings:
github.com/The-Shadowserver-Foundation/report_schema/blob… -
The Shadowserver Foundation
@Shadowserver
We are reporting JetBrains TeamCity CI/CD CVE-2023-42793 vulnerable instances (critical authentication bypass). 1296 unique IPs found vulnerable on 2023-09-30. Data shared in our Vulnerable HTTP report www.shadowserver.org/what-we-do/network-reporting/vulnera…
Patch information - blog.jetbrains.com/teamcity/2023/09/cve-2023-42793-vulner… -
The Shadowserver Foundation
@Shadowserver
Since 25th August we are seeing exploitation attempts from multiple IPs for Juniper J-Web CVE-2023-36844 (& friends) targeting /webauth_operation.php endpoint. Same day an exploit POC was published. This involves combining lower severity CVEs to achieve pre-auth RCE.
-
The Shadowserver Foundation
@Shadowserver
Happy to collaborate with @circl_lu on new EU ISF funded MISP-LEA project to establish a @MISPProject instance dedicated to law enforcement agencies. Shadowserver will contribute ransomware & C2 infrastructure tracking to support LEA investigations.
More: www.misp-lea.org -
The Shadowserver Foundation
@Shadowserver
We are thrilled to announce the official launch of our new Shadowserver Alliance enabling us to sustain & scale up delivery of no cost cybersecurity & threat intelligence services to Internet defenders & LE worldwide! Join here: shadowserver.org/sponsor
www.shadowserver.org/news/shadowserver-alliance-launch