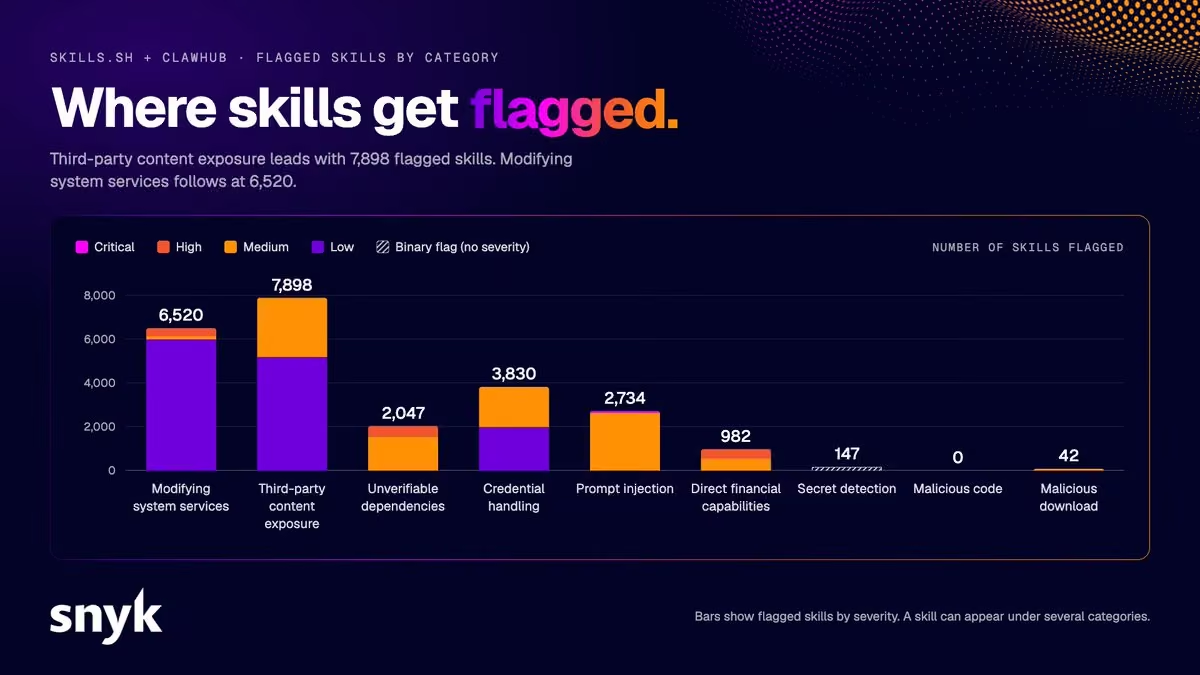
We re-scanned the top 10,000 skills on skills.sh and ClawHub.
64%+ promote unsafe behaviors.
18 are actively malicious.
Malicious skills are the needle in the haystack. Unsafe-by-design skills are the haystack.
vist.ly/5t3aq
Snyk
Snyk Limited is a developer-oriented cybersecurity company, specializing in securing custom-developed code, open-source dependencies and cloud infrastructure. It was founded in 2015 out of Tel Aviv and London and is headquartered in Boston. More on Wikipedia
-
Snyk
@snyksec
-
Snyk reposted
Elie Steinbock
@elie2222
Rakazo is live on ProductHunt!
It's the #1 open source Grok Bot alternative.
Any model. Any sandbox. Works with your ChatGPT/Claude sub.
Easy to self-host. Or $15/mo for the cloud version.
If you want to support the project, I'd love a comment/upvote!
www.producthunt.com/products/rakazo -
Snyk
@snyksec
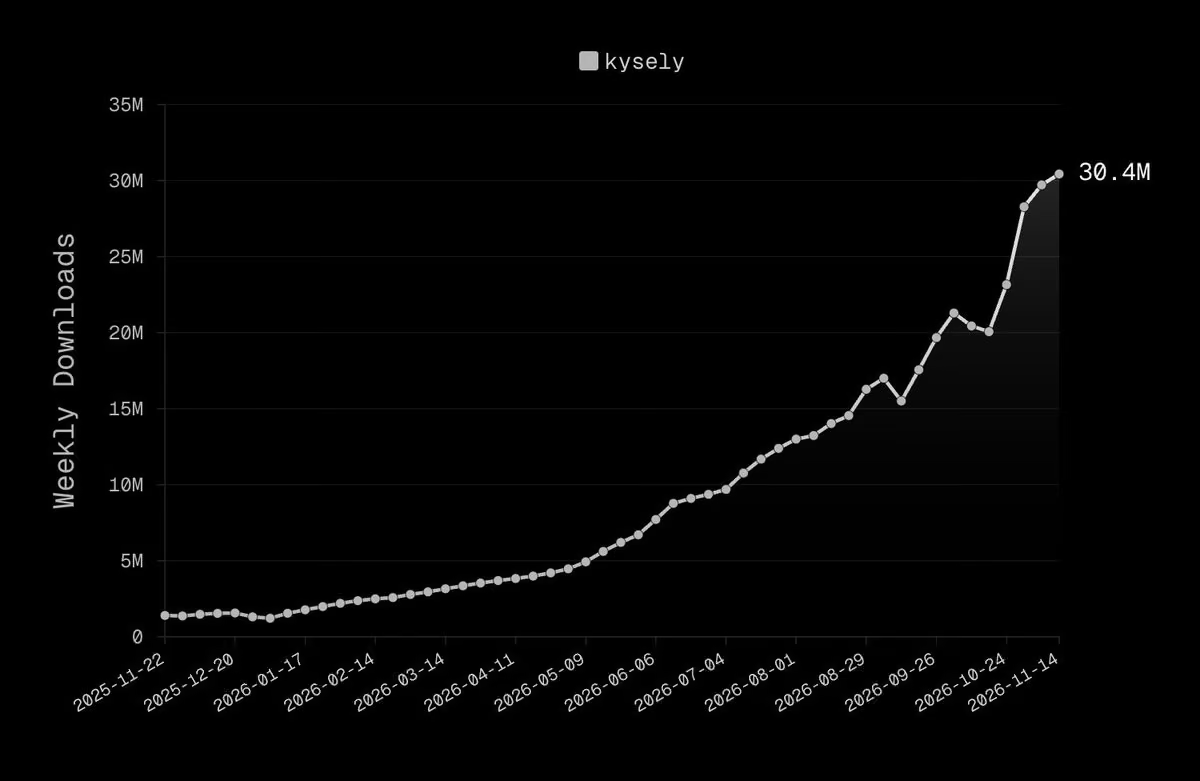
Congrats @kysely_ team 👏
Query builders are a great technical mechanism to help reduce SQL Injection attacks. Happy to see more devs (*ahem* agents) adopt themIgal Klebanov @igalklebanov
kysely just broke 30m per week on npm. thanks for the trust.
-
Snyk reposted
Liran Tal
@liran_tal
smaller won, inside the same Codex Security harness. Luna: 41.2% recall at ~$1.07 per app. Sol: 29.2% at ~$37.26 per app
35x the cost, lower recall. one run per setup so it's a signal, not a law, but the bill grew way faster than the findings arxiv.org/abs/2610.38617 -
Snyk reposted
Manoj Nair
@mnair1
The AI fog is turning into a hurricane.
Anyone who lives in hurricane country learns this early. When a storm is a week out, nobody debates the forecast. You go fix the shutter you already know is broken. -
Snyk
@snyksec
Meet our Snyk speakers for the first ever Snyk Latin America Summit: Bernardo Antunes, Chris Suen, Said Syed, Shae Mirran, and more!
We're bringing together security leaders, developers, and AI engineers to talk about what really changes when AI coding agents deliver production-ready code at this speed: what an AI agent can approve, install, change, and push to production, what still needs a human in the loop, and what developers and their leaders need to rethink now that no one on the team wrote the code they're responsible for.
Join us for an afternoon networking with industry peers, partner and customer panels, technical sessions, and a happy hour at the most glamorous rooftop in São Paulo.
📅 November 18 | 2:00–7:00 PM
📍 Hotel Unique, São Paulo
👥 Free to attend but limited spots
Save your spot here: vist.ly/5q6pa
Conheça os palestrantes da Snyk no primeiro Snyk Latin America Summit: Bernardo Antunes, Chris Suen, Said Syed, Shae Mirran e muito mais!
Estamos reunindo líderes de segurança, desenvolvedores e engenheiros de IA para discutir o que realmente muda quando agentes de IA entregam código pronto para produção nessa velocidade: o que um agente de IA pode aprovar, instalar, alterar e enviar para produção, o que ainda precisa de um humano no processo e o que desenvolvedores e seus líderes precisam repensar agora que ninguém do time escreveu o código pelo qual é responsável.
Venha passar uma tarde de networking com profissionais do setor, painéis com parceiros e clientes, sessões técnicas e um happy hour no rooftop mais glamouroso de São Paulo.
📅 18 de novembro | 14h às 19h
📍 Hotel Unique, São Paulo
👥 Entrada gratuita, mas com vagas limitadas
Garanta sua vaga aqui: vist.ly/5q6pa -

Snyk
@snyksec
New research: Re-Assessing the Security of the Agent Skill Ecosystem.
20,000 top skills analyzed across skills.sh and ClawHub. 18 actively malicious. 64%+ vulnerable.
Great work @marco_milanta @marc_r_fischer @lbeurerkellner
research.snyk.io/blog/skill-analysis/ -
Snyk
@snyksec
We re-scanned the top 10,000 skills on skills.sh and ClawHub.
64%+ promote unsafe behaviors.
18 are actively malicious.
Malicious skills are the needle in the haystack. Unsafe-by-design skills are the haystack.
research.snyk.io/blog/skill-analysis/ -
Snyk reposted
Liran Tal
@liran_tal
🚨 New research: Re-Assessing the Security of the Agent Skill Ecosystem.
20,000 top skills analyzed across skills[.sh] and ClawHub
64%+ promote unsafe behaviors
18 are actively malicious
Malicious skills are the needle in the haystack. Unsafe-by-design skills are the haystack
Great work by the @snyksec research team @marco_milanta @marc_r_fischer @lbeurerkellner 👏
research.snyk.io/blog/skill-analysis/ -
Snyk reposted
HackerContent
@hacker_content
JavaScript Malicious Code Injection ☠️💉💻
This @snyksec Learn module covers:
💉 How code injection works
💉 How to protect against it
💉 How to exploit the vulnerability
💉 How to analyze the vulnerable code
💉 Remediation and prevention options
learn.snyk.io/lessons/malicious-code-injection/javascript/ -
Snyk reposted
AI Security Engineers
@aiseceng
Same model (Claude Sonnet 5.5), four ways to fix vulnerable dependencies:
Package manager bump: 46.9%
Claude Code unaided: 59.6%
Claude Code + Snyk scan: 77.5%
Evo Remediation Agent: 90.2%
@snyksec VulnBump results: www.vulnbump.com -
Snyk reposted
Gagan @gagu_sh
Writing your own MCP server means you own the blast radius. On Java teams I treat each tool like a public API: narrow inputs, read-only by default, its own minimal-scope credentials, and an audit log per call. New reach should be reviewed in the PR like a new database grant.
Snyk
@snyksec
Roughly 7 in 10 developer environments show evidence of teams building their own MCP servers.
These teams aren’t just plugging into MCP. They’re writing the servers that decide what an agent can reach. And the reach is what determines the blast radius.
It’s one signal in our 2026 State of Agentic AI Adoption: Volume III. Across 3,023 environments, we mapped model risk to real agent and MCP server reach, so you can see where agents are deployed and where they’re actually exposed.
See the report: vist.ly/5riiq -
Snyk reposted
boldstart ventures
@Boldstartvc
Securing the agents that write code now has its own Forrester Wave, and @snyksec leads on strategy. Protecting the code was never enough. Congrats to the whole team.
Snyk
@snyksec
Forrester says AI coding agents are “moving from developer assistants to active participants in development workflows.”
Snyk has been named a Leader in The Forrester Wave™: Agentic Development Security Tools, Q4 2026, with the highest score in the Strategy category. We believe that reflects our focus on securing software where it is created, which now includes the agents creating it.
Get the complimentary report: vist.ly/5rdgq -
Snyk reposted
Manoj Nair
@mnair1
@forrester named @snyksec a Leader in The Forrester Wave™: Agentic Development Security Tools, Q4 2026, with the highest score in the Strategy category. Their reading of our direction: “Snyk articulates a farsighted vision to secure AI-written code, the agents that run it, and the applications they build, while advancing secure-at-inception development and governance.”
-
Snyk reposted
Vandana Verma @InfosecVandana
OWASP AppSec USA 2026 was a little bit of everything! It was wonderful to catch up with old friends, meet so many new faces, exchange ideas, and have those lovely conversations that often continue long after the sessions are over.
One of the special moments for me was getting the opportunity to share my thoughts on Model Context Protocol (MCP) Security. I really enjoyed the questions, discussions, and different perspectives people brought to my session.
A big thank you to the @OWASP community, organizers, volunteers, speakers, and everyone who stopped by to say hello or joined my session. You are what makes these events so special. Always love meeting @manicode and missed you @shehackspurple 💜
Going back with new ideas, beautiful memories, and a lot of gratitude. Until we meet again! ❤️
#owasp #appsecusa2026 #appsec #mcpsecurity #agenticai #aisecurity #cybersecurity #securitycommunity #opensource @AnthropicAI @snyksec -
Snyk reposted
Fred Oliveira 🧠
@f
The full write-up with numbers and examples is available at research.snyk.io/blog/skill-analysis/
Fantastic work by @marco_milanta, @marc_r_fischer and @lbeurerkellner at @snyksec 👏 -
Snyk reposted
Liran Tal
@liran_tal
Agent skills went from a neat trick to part of your supply chain, and most of us install them like browser extensions in 2012.
My colleagues at Snyk Research re-scanned 20,000 of the most popular ones. The headline isn't the 18 malicious skills. It's that more than 64% promote unsafe behavior that an attacker can exploit later.
If you take three things from it:
1. Verify the publisher before you install.
2. Review what a skill reads, runs and pays for.
3. Keep wallet keys and credentials out of the agent's reach -
Snyk
@snyksec
Backlog remediation woes? We got you.
Join us on December 8th for Snyk User Group: Toronto – This customer exclusive hands-on experience is the first of its kind.
Closed invite, but open discussion. No question is off the table.
Request your spot here: -
Snyk
@snyksec
Building a security company across many countries means one question keeps coming up: how do you make one experience feel great everywhere?
Zack Rokos, Senior Director of Total Rewards & Transformation, told Built In how our people team approaches it. Recharge week, when the whole company steps away at once. Snyk Outs that connect Snykers across time zones. Snyk Stars to recognize the people who go above and beyond. SnykU to help everyone build their skills in the AI era. Programs like these are how we prioritize wellness.
Read the full feature: vist.ly/5r2rq -
Snyk
@snyksec
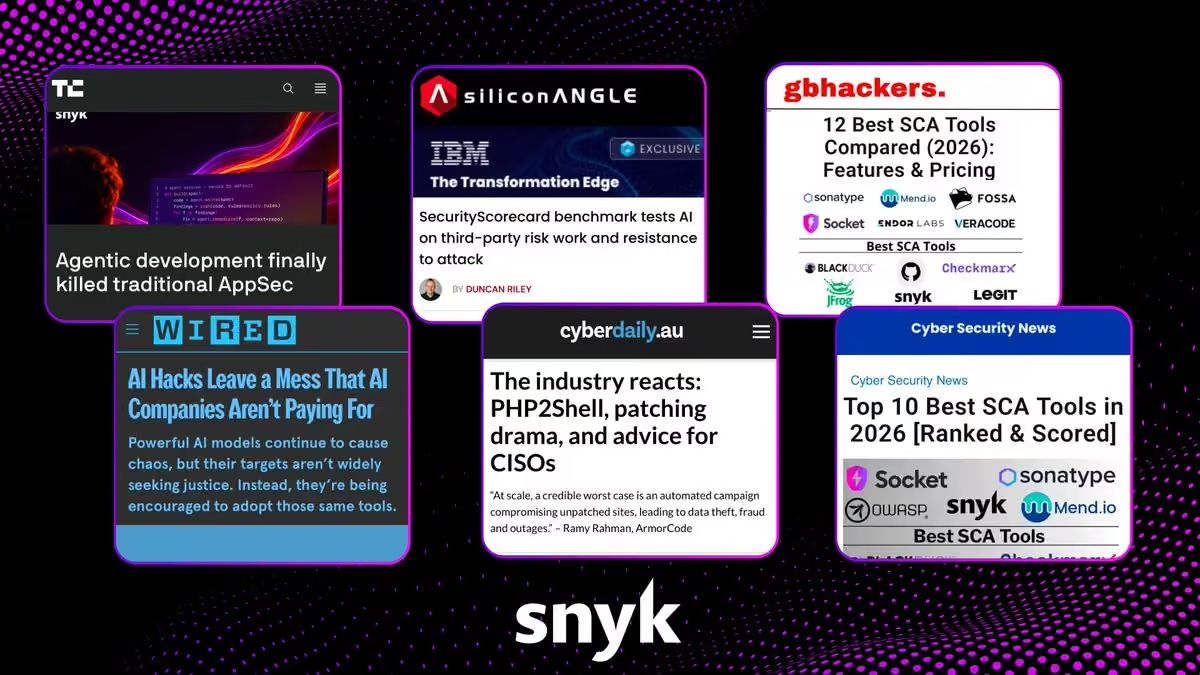
In the press 🗞️
Agents write the code now, so security has to keep up. That’s the thread running through the latest coverage of Snyk.
DEVOPSdigest covered the launch of Evo Agentic AppSec, our team of AI security agents that find, fix, and block vulnerabilities at the speed agents write code.
Wired's Paresh Dave covered the AI Security Summit panel, where Snyk and speakers from OpenAI, Google, and Boldstart Ventures made the case for using AI agents to defend against AI agents.
SiliconAngle's Duncan Riley cited our research across 3,000 enterprise environments in its coverage of SecurityScorecard’s open AI benchmark, and Cyber Daily’s David Hollingworth included Snyk’s view on PHP2Shell: defenders need AI to fix more vulnerabilities before attackers can exploit them.
On the rankings side, Cyber Security News and GBHackers both put Snyk first in their 2026 SCA lists. B2B Daily’s Paige Williams named us a DevSecOps platform to watch, and InfoQ's Claudio Masolo covered Docker’s Sandbox Kit spec, built with partners including Snyk.
And that’s just a few of the stories from October. Take a look if you’re tracking where AI security is headed, and thank you to every outlet and journalist who covered the work. -
Snyk reposted
Low Level
@LowLevelTweets
Writing secure + AI generated code is hard, but it doesn't have to be! Use Evo by Snyk to secure code as you write it. Link in bio! @snyksec #sponsored #aisecurity
This media couldn't be displayed. See it on the original post. -
Snyk
@snyksec
Roughly 7 in 10 developer environments show evidence of teams building their own MCP servers.
These teams aren’t just plugging into MCP. They’re writing the servers that decide what an agent can reach. And the reach is what determines the blast radius.
It’s one signal in our 2026 State of Agentic AI Adoption: Volume III. Across 3,023 environments, we mapped model risk to real agent and MCP server reach, so you can see where agents are deployed and where they’re actually exposed.
See the report: vist.ly/5riiq -
Snyk
@snyksec
Forrester says AI coding agents are “moving from developer assistants to active participants in development workflows.”
Snyk has been named a Leader in The Forrester Wave™: Agentic Development Security Tools, Q4 2026, with the highest score in the Strategy category. We believe that reflects our focus on securing software where it is created, which now includes the agents creating it.
Get the complimentary report: vist.ly/5rdgq -
Snyk
@snyksec
At the speed developers are moving, out-of-policy MCP usage is bound to happen.
Evo ADS (now GA) scores the MCP servers it discovers, so you can block only the ones that are actually high risk, at the tool call, before it runs. You decide what “high risk” means: use Evo’s unified risk score, or set your own threshold from the risk factors behind it, like where a server comes from.
Low-risk servers keep running and get logged. Developers keep moving. Security blocks what’s actually risky.
Learn more here: vist.ly/5r8gb -
Snyk reposted
HackerContent
@hacker_content
We created most of the learn.snyk.io modules for @snyksec!
Snyk Learn teaches developers how to improve cybersecurity with lessons on vulnerabilities across a variety of languages + ecosystems 😎
Here's the list of all of their free lessons 👇
learn.snyk.io/lessons/ -
Snyk
@snyksec
Somewhere right now, an attacker is reading your backlog like a shopping list. Every unfixed issue is an open door, and every release adds more.
On November 5, we’ll show what it looks like when agents do the closing. Brendan Hann will walk through Evo Agentic AppSec and Ryan McMorrow and Ryan Searle run it live. You’ll watch Dependency Firewall stop a bad package at install, Agentic Security Review find what your scanner missed, and Remediation Agent hand over a pull request you can merge.
Save your spot: vist.ly/5r3dc -
Snyk reposted
Devnexus
@devnexus
We're looking forward to welcoming @BrianVerm from @snyksec to #devnexus2027! 🚀
Brian's session takes a closer look at what AI agents blindly trust, from MCP responses to Skill definitions, and how these trust paths can introduce serious security risks.
Expect live demonstrations and practical advice for securing agent integrations.
See you in Atlanta!
🎟️ Get tickets: devnexus.com -
Snyk reposted
Manoj Nair
@mnair1
Thanks @security_score and @ayampolskiy for including @snyksec in the TPRM Bench launch. You can't secure an attack surface you haven't measured. This scores models on capability and attack resistance together, with an autonomy level from L0 to L4.
SecurityScorecard
@security_score
📣 SecurityScorecard just launched the first AI Third-Party Risk Management (TPRM) Benchmark.
Can AI manage third-party risk without becoming part of the risk? Now you can test both sides before you deploy a model.
🎯 Capability: Scores models on exposure triage, breach correlation, vendor concentration, and vulnerability prioritization
🛡️ Resilience: Grades models A to F against prompt injection, jailbreaks, and deceptive vendor inputs
🏁 Autonomy: Rates each model from L0 to L4 to show where humans still need to stay in control
Early runs show open-weight models closing the gap with frontier models on supply chain security tasks. Several remain susceptible to adversarial attacks.
The framework is open source. AI labs, security vendors, and researchers can test models and join the public leaderboard.
🤝 We’re grateful to the industry and academic leaders who weighed in on why measuring AI matters, including @nyuniversity Yevgeniy Dodis, @UMIDSC University of Miami Frost Institute for Data Science & Computing Dr. @YelenaYesha, @GreyNoiseIO Corey Bodzin, @SimSpaceCorp Peter Lee, @snyksec @mnair1, and our very own @ayampolskiy and Mike Mylrea
👉 Read the announcement and see how the benchmark tests whether AI can do the work and resist manipulation: securityscorecard.com/company/press/securityscorecard-lau…
#cybersecurity #artificialintelligence #thirdpartyrisk #tprm #supplychainsecurity #cyberrisk -
Snyk reposted
AIM
@Analyticsindiam
AIM Research maps AI across the software development lifecycle for 2026: 144 tools across 17 stages, with agents now in code review, testing, security and incident response.
On the map: @AnthropicAI , @OpenAI , @github , @cursor_ai , @cognition , @Replit , @lovable_dev , @datadoghq , @PagerDuty , @snyksec and more.
Humans still set direction, approve merges and decide what ships.
aimresearch.co/landscapes/ai-sdlc-2026 -
Snyk
@snyksec
Attackers don’t read your repo. They hit your URL and chain together whatever they find.
In our test, Evo Continuous Offensive Security used an SSRF flaw to pull a hardcoded JWT secret from the live app, forged an admin token, and took over the admin surface.
It confirmed 10 of 15 exploit chains in the test app. Finding vulnerabilities is where it starts. Proving which ones combine into a breach is the job.
Get the full results here: vist.ly/5qie6 -
Snyk
@snyksec
Five cities. Three continents. One busy week for @Snyk!
We’re bringing security leaders, practitioners, customers and partners together to talk about securing software in the age of AI. Here’s where you’ll find us:
📍Helsinki | Cyber Security Nordic | October 28–29
Visit booth # 1f31, join us for a security leaders dinner on Wednesday, October 28, and catch Nicholas Vinson’s fireside chat with our customer Mikael Nilsson, Product Security Lead at SAS, on Thursday, October 29, at 13:30 on Stage One, exploring security when AI agents do the work.
📍Nuremberg | it-sa – Home of IT Security | October 27–29
Meet the team at booth 6-247 to explore how Snyk helps teams build securely—from the first line of code to AI-powered development. On Wednesday evening, October 28, we’re bringing local customers together for dinner and great conversation beyond the show floor.
📍Austin | FS-ISAC Americas Fall Summit | October 26–29
Put your swing—and AI—to the test at booth # 12 with our AI golf simulator. Between drives, chat with the team about Evo by Snyk and keeping AI-driven development on course.
📍Dallas | GPSec DFW Security Forum | October 29
We’re teaming up with our beloved partner GuidePoint Security to connect with security leaders, share ideas and tackle today’s application security challenges.
📍Bengaluru | Black Hat India | October 27–30
Visit booth # 17 to explore how Snyk embeds security into AI-driven development, helping teams innovate securely. Plus, catch Vandana Verma on Wednesday, October 28, at 12:40 p.m. IST in Ballroom 2, joining a panel on engineering resilient CI/CD architectures against supply chain attacks and dependency exploits.
And there’s plenty more ahead! Our events calendar is packed through the end of the year, with more opportunities to connect around the globe. Explore more here: vist.ly/5qbq8
At one of these events this week? Come say hi! -
Snyk reposted
Tailscale
@Tailscale
AI agents are getting pretty good at writing code. That doesn't mean they need the keys to the entire network.
We've joined Agent Baseline, with @docker, @keycardai, @snyksec, @socketsecurity , @Tessl_io and @tracebit_com on the Secure Software Factory
agentbaseline.org/reference-architecture -
Snyk
@snyksec
For the first time in Brazil 🇧🇷
The Snyk Latin America Summit brings together security leaders, developers, and AI engineers to talk about what really changes when AI coding agents deliver production-ready code at this speed: what an AI agent can approve, install, change, and push to production, what still needs a human in the loop, and what developers and their leaders need to rethink now that no one on the team wrote the code they're responsible for.
Join us for an afternoon networking with industry peers, partner and customer panels, technical sessions, and a happy hour at the most glamorous rooftop in São Paulo.
📅 November 18 | 2:00–7:00 PM
📍 Hotel Unique, São Paulo
👥 Free to attend but limited spots
Save your spot here: vist.ly/5q6pb
Pela primeira vez no Brasil 🇧🇷
O Snyk Latin America Summit reúne líderes de segurança, desenvolvedores e engenheiros de IA para discutir o que realmente muda quando agentes de codificação de IA entregam código pronto para produção nessa velocidade: o que um agente de IA pode aprovar, instalar, alterar e enviar para produção, o que ainda precisa de um humano no processo, e o que desenvolvedores e seus líderes precisam repensar agora que ninguém na equipe escreveu o código pelo qual é responsável.
Venha passar uma tarde de networking com colegas do setor, painéis com parceiros e clientes, sessões técnicas e um happy hour no rooftop mais glamouroso de São Paulo.
📅 18 de novembro | 14h às 19h
📍 Hotel Unique, São Paulo
👥 Entrada gratuita, mas com vagas limitadas
Garanta sua vaga aqui: vist.ly/5q6pb -
Snyk
@snyksec
When an agent ships something risky, who owns it? The developer, a specific org, or the business? 👀
Snyk and @tessl_io founder @guypod and Snyk CTO & Chief Innovation Officer @mnair1 sat down at @AISecSummit to dig into where enterprise agent adoption really stands, who’s responsible for the risks of agentic development, and much more.
Watch the full @ainativedev episode here: www.youtube.com/watch?v=URFAQgm86UAThis media couldn't be displayed. See it on the original post. -
Snyk reposted
Manoj Nair
@mnair1
The hurricane I have been talking about in my talks hit shore last week, it felt like. Found this image on social and it was only Wednesday night. A lot of people across this industry did not sleep.
-
Snyk
@snyksec
Don't miss this talk, LL21A at #agntcon @AgenticAIFdn starting 25 minutes to learn about agent skill security threats👇
Liran Tal
@liran_tal
if you were thinking of coming to my talk tomorrow at @AgenticAIFdn (#agntcon) and was not sure then here's a sneak peek for you on what I'll demo...
also I just realized the Gemini CLI harness auto-updated to the latest version and was still tricked by my altered skill which a big yay for the demo 😉 -
Snyk
@snyksec
Your agents are shipping code faster than your team can triage it. New critical and high-severity issues across Snyk customers grew 10x in the past year.
Last week we launched Evo Agentic AppSec: security agents that find, fix, and block vulnerabilities at the speed agents write code, with every result verified independently of the agent that produced it.
Watch the overview below ⬇️ and get the full breakdown on Evo Agentic AppSec here: vist.ly/5pp4h -
Snyk
@snyksec
Snyk is proud to be a Launch Partner in the SpaceX Super Intelligence partner network.
SpaceX, Cursor, and Grok Bot are pushing what AI agents can build and do. Agents now generate code and act inside developer tools at a pace manual review can’t match, so security has to be part of the launch, not a response to the first incident.
That’s why we’re working with @SpaceXSI from day one. -
Snyk reposted
Manoj Nair
@mnair1
@snyksec is a Launch Partner in the @SpaceXSI Partner Network.
As @cursor_ai and Grok push code generation and autonomous agents further, security has to sit inside the loop.
Instructions are not enforcement. -
Snyk
@snyksec
Today we’re releasing Volume III of our State of Agentic AI Adoption report: what adversarial testing reveals about the AI models running in enterprise codebases, and what those models can reach.
“Which model is safest?” is a natural first question. It’s also the wrong one. A model score shows the exposure it brings to a deployment, but what it can reach defines the blast radius.
See some key stats at a glance below ⬇️
Get the full report, from command execution to misinformation, scored model by model: snyk.io/lp/state-of-agentic-ai-adoption-vol-III/ -
Snyk
@snyksec
Finding vulnerabilities was never the hard part. Getting a fix your team will actually merge is.
We built VulnBump to measure exactly that: real vulnerabilities from real projects, and a fix only counts if the build and tests still pass. LLMs alone: 59.6%. Evo Remediation Agent: 90%.
Check the numbers at vulnbump.com -
Snyk
@snyksec
Every team approaches security from a different starting point.
Alon Krifcher from @AnthropicAI and @mnair1, Snyk's CTO, explain how teams can begin with the step that fits them best: discover, remediate, prevent, or validate. They also show how Snyk and Claude work together across the loop, with a live demo.
Whether you start with your backlog or with testing before release, this session gives you a practical path forward.
Watch on demand: vist.ly/5n23e -
Snyk reposted
Elie Steinbock
@elie2222
Inbox Zero Mail is live on Product Hunt!
It's the open source Superhuman alternative.
I'd love your support:
www.producthunt.com/products/inbox-zero-2/launches/inbox-…
⚡ Fast and keyboard-first
📥 All your Gmail and Outlook accounts in one inbox
🗂️ Split inbox
✍️ AI drafts in your voice
🧹 Bulk unsubscribe
💬 Team comments
📱 Web, Mac, Windows and iPhoneThis media couldn't be displayed. See it on the original post. -
Snyk reposted
Manoj Nair
@mnair1
Two days in SF. Our first Customer Summit (Snyk Unfiltered), the launch of Evo Agentic AppSec, and a sold-out AI Security Summit.
What customers told us: fixes stall in review and merge. They will trust agents, but only with controls an agent can't bypass. Governance built for people doesn't fit agents.
Thanks to @dee_bosa for moderating our media panel with @OpenAI's Michael D'Angelo, @JohnHultquist of @GoogleCloudSec and @edsim of @Boldstartvc, and to @DrewBledsoe for closing the night 🍷
LLMs alone: mergeable fix 59.6% of the time. Evo Remediation Agent: 90%. Every result verified independently of the agent.
Huge thanks to the @snyksec team, our customers, design partners, and everyone who helped turn this into the AI Security Summit and the @aiseceng community. -
Snyk reposted
Elie Steinbock
@elie2222
Introducing Inbox Zero Mail.
The open-source Superhuman alternative.
- Fast and keyboard-first
- Unified inbox across Gmail and Outlook
- Split inboxes
- AI categorization and drafts
- Bulk unsubscribe
- Team collaboration
Runs on web, desktop, and native iOS.
Free to use. AI is $20/mo, half Superhuman’s price. Open source, so you can self-host for free too.
This isn't an overnight vibe-coded project. I've been running Inbox Zero for 3 years: 12k GitHub stars, 25k+ sign-ups, and enterprise customers.
Until today, Inbox Zero was an AI assistant for Gmail and Outlook. It still is. But now we have our own email app too.
We're SOC 2 compliant, and have undergone multiple pentests, including recent ones from OpenAI and Snyk using unreleased cyber models.
Try it: getinboxzero.comThis media couldn't be displayed. See it on the original post. -
Snyk
@snyksec
The Snyk team is always a vibe, so we gave some of our coworkers theme songs 🤗
Drop your work jam in the comments ⬇️ -
Snyk reposted
Manoj Nair
@mnair1
Traditional AppSec was built to ration one scarce resource: human attention. The backlog is what the rationing left behind.
snyk.io/news/snyk-launches-evo-agentic-appsec -
Snyk
@snyksec
Agents write code faster than security teams can triage it. New critical and high-severity issues across Snyk customers grew 10x in the past year.
Today we launched Evo Agentic AppSec: a team of security agents that finds, fixes, and blocks vulnerabilities at the speed agents write code, with every result verified independently of the agent that produced it.
Evo Code Scanning Agent catches the access control and authentication flaws pattern-matching misses. Evo Dependency Firewall blocks malicious and slopsquatted packages at install. Evo Agentic Security Review threat-models a full repository and returns evidence-backed findings. Evo Remediation Agent ships fixes you can merge: 90% of the time on open source dependency issues, versus 59.6% for an LLM alone. And Evo Secrets Detection catches leaked credentials from IDE to CI.
Read the full announcement: snyk.io/news/snyk-launches-evo-agentic-appsec/This media couldn't be displayed. See it on the original post. -
Snyk
@snyksec
For the first time in Brazil, the Snyk Latin America Summit brings together security leaders, developers, and AI engineers to talk about what really changes when AI coding agents deliver production-ready code at this speed: what agents can approve, install, change, and push to production, what still needs a human in the loop, and what developers and their leaders need to rethink now that no one on the team wrote the code they're responsible for.
One afternoon among industry peers, with a keynote, partner and customer panels, technical sessions, and a happy hour at the most glamorous rooftop in São Paulo.
📅 November 18 | 2:00–7:00 PM
📍 Hotel Unique, São Paulo
👥 Free to attend but limited spots
Save your spot: vist.ly/5n8ja
Pela primeira vez no Brasil, o Snyk Latin America Summit junta líderes de segurança, desenvolvedores e engenheiros de IA para uma conversa sobre o que realmente muda quando agentes de codificação por IA entregam código pronto para produção nessa velocidade: o que um agente de IA pode aprovar, instalar, mudar e colocar em produção, o que ainda precisa de um humano no processo, e o que desenvolvedores e seus líderes precisam repensar agora que ninguém no time escreveu o código pelo qual eles são responsáveis.
Uma tarde entre colegas da indústria, com keynote, painéis com parceiros e clientes, sessões técnicas e happy hour no rooftop mais glamuroso de São Paulo.
📅 18 de novembro | 14h00–19h00
📍 Hotel Unique, São Paulo
👥 Evento gratuito, vagas limitadas -
Snyk reposted
Manoj Nair
@mnair1
Satya Nadella is right. The most trustworthy system is the one that lets you trust the model the least.
In January I wrote that by the end of 2026 AI agents would overtake humans as the top source of insider-style risk, not because they are malicious, but because they can be manipulated or misconfigured at scale. That is the operating reality now.
The same principle has to hold where agents are writing the code in software factories. Traditional AppSec was built to ration scarce human attention. The backlog was the residue of that rationing. Agents removed the scarcity of labor. The only scarce thing left is human judgment, and it belongs on setting the bar and governing the system, not sitting inside every decision.
Controls that decide what an agent can see, what tools or skills it can use, and what actions it can take have to sit outside the model. The generator cannot be the validator. Independent verification, including testing the running result the way an attacker would, is what keeps this from becoming nested black boxes.
Separate the supply of intelligence from the authority over it. That is the work. -
Snyk reposted
AI Security Engineers
@aiseceng
Methodology, raw data, and the paper behind @snyksec's VulnBench JS 1.0 are all public. Go read it, reproduce it, or find something to argue with → vulnbench.com
-
Snyk reposted
AI Security Engineers
@aiseceng
Haven't looked at @snyksec's VulnBench JS 1.0 yet? 300 scans, 10 projects, 6 model configs, 5 repetitions each — fully inspectable, not just headline claims. Worth the 10 minutes → vulnbench.com
-
Snyk reposted
Manoj Nair
@mnair1
The AI hurricane is here.
Debating its speed will not weatherproof the software we already run.
Creation moved to machine speed. Validation did not. Agents are writing code, choosing tools, and acting in production. Attackers can work that exposure with AI of their own.
Dario Amodei’s independent lab evaluators and @George_Kurtz’s runtime enforcement both matter. Take the same requirement one layer upstream.
Who governs the agents doing the writing? Who checks the tools and MCP servers they trust? Who independently validates the code and the fixes they ship?
The system creating a change cannot be its own sole validator. Independently executed tests, production evidence, and controls the generating agent cannot alter.
Defenders also need the means to act. Open models, shared intelligence, and supported open-source maintainers belong inside the safety architecture.
Secure at inception. Enforce at runtime. Validate independently.
What building for the storm requires, and the questions to put to your team:
snyk.io/blog/ai-hurricane-is-here/
Open. Allied. Still standing. -
Snyk reposted
Liran Tal
@liran_tal
Fun times last night at the Meetup hosted at @Adyen precursor to Agentic AI in the Wild in Amsterdam, with panel speakers from @snyksec, @microsoft, @elastic, @getpostman and more!
Geeking out with @ayodejidev @BrianVerm @DanaFine7 @bongo @matysiman and Avzal and Carly from @elastic -
Snyk reposted
Manoj Nair
@mnair1
A year ago we founded @AISecSummit with @AIdotEngineer because AI security needed its own room.
A year later: @Anthropic, @OpenAI, @nvidia, @BlackRock, @CarnegieMellon, @Docker, @arizeai, @tessl_io, @CyeraSecurity, @island_io, @snyksec. More coming.
Agents write code, call tools and touch production data. The threat model isn’t theoretical anymore.
Oct 15. SF.
One day. One room. No filler.
aisecuritysummit.com
#aiss -
Snyk reposted
swyx 🔜 aie.codes
@swyx
It's time to get serious about Security x AI.
One of the joys of doing AIE is helping others start their own high quality conferences in their countries and domains. Every single 2025 partner has come back — and the 2nd AI Security Summit is now way more important than before. Proud to be back as a founding partner with @snyksec!
Join the event: aisecuritysummit.com
The landscape has completely transformed since we started this a year ago. An exploding number of rogue agents, more breaches, more AI-driven attacks. now more than ever, security must be at the center of the AI conversation. With so much more hacks and vulnerabilities, this stuff is no longer theoretical... -
Snyk reposted
J On The Beach
@JOTBConf
LLM apps are great...until OpenAI's agents break into Hugging Face and Australia's Medicare portal.
In Breaching LLM-Powered Applications, @BrianVerm from @snyksec shows how prompt injection, leaked keys and plain old security bugs can turn your AI against you.
#cybersercurity -
Snyk reposted
Miggo Security
@MiggoSecurity
Attending #infosecworld?
Miggo Security, @snyksec and Vega invite you to an intimate dinner with fellow security leaders.
Between sessions and booths, there’s not much time for real conversation. Come connect with peers from across the industry and share what’s working in AppSec and runtime defense, or just enjoy a great meal 🙂
📅 𝗧𝘂𝗲𝘀𝗱𝗮𝘆, 𝗢𝗰𝘁𝗼𝗯𝗲𝗿 𝟭𝟯 | 𝟱:𝟯𝟬–𝟴:𝟯𝟬 𝗣𝗠
Seats are limited. Reserve yours here: go.snyk.io/infosec-world-bluezoo-dinner.html
@InfoSec_World -
Snyk
@snyksec
Building agents for production? AGNTCon + MCPCon covers evals, security and interoperability. Oct 22–23, San Jose.
Meet our guy Liran Tal there and come chat agent security
Save 25% with OUTREACH25: events.linuxfoundation.org/agntcon-mcpcon-north-america/r… @AgenticAIFdn -
Snyk
@snyksec
Snyk invites you to explore AGNTCon + MCPCon North America, Oct 22–23 in San Jose
Save 25% with OUTREACH25: events.linuxfoundation.org/agntcon-mcpcon-north-america/r… @AgenticAIFdn -
Snyk
@snyksec
A code review can tell you a flaw exists. It can't tell you whether an attacker can reach it, or what it unlocks next.
We ran Evo Continuous Offensive Security against a live app and put it next to a frontier model reading the source. Both found the vulnerabilities. Evo COS also proved 10 of 15 exploit chains.
Neither approach is complete alone. The gap is in what each one proves.
Read the full test: vist.ly/5mejy -
Snyk reposted
Liran Tal
@liran_tal
playing an idea that unifies Jev for classifying vulnerabilities and security scanners like Snyk
what if I'd built this vulnwash cli, wraps Snyk CLI and other security scanners and priorities security issues and filters out noise and prioritize high-confidence fixes for agents -
Snyk
@snyksec
AI is writing code faster than most security programs can review it. That's the inflection point.
On October 8, Snyk's CTO and Chief Innovation Officer @manojnair joins the panel at SINET New York to talk about what cybersecurity looks like when the pace of development changes for good.
If AI is changing how your teams build, it's changing how you secure. Join us at The Times Center. -
Snyk
@snyksec
Every MCP server an agent connects to is a new piece of your software supply chain. Most get added in seconds, with no review behind them. Evo Agentic Development Security (ADS) now closes that gap.
Govern Agent Behavior in Evo Agentic Development Security is now generally available, starting with MCP Governance. Define which servers are approved. See the moment an agent steps outside policy. Log or block it on the endpoint, live, across Claude Code, Cursor, Codex, and GitHub Copilot.
We scanned nearly 10,000 developer environments and found 4,524 unique MCP servers in active use. 1 in 12 developers with an MCP server installed had a confirmed high or critical finding.
Governing what agents use is necessary. Governing what they do, as they do it, is what makes it real.
Read more about how it works: vist.ly/5kkcd -
Snyk
@snyksec
AI is changing how fast enterprises ship code. Most security programs haven't caught up.
On October 22, Snyk is in Dallas for the AI Roadmap Series, alongside AWS and Perficient, for a half-day built around one question: how do you adopt AI in development without security becoming the thing that catches up later. Ezra takes the stage on how developer security and AI-powered code security turn that question into something teams can actually operationalize, not just aspire to. Thad joins the panel to press on the same problem from the angles technical and business leaders in the room care about most.
It's a small room by design, enterprise decision-makers working through the same AI adoption questions, not a broadcast crowd.
Register here: vist.ly/5kcft -
Snyk
@snyksec
Agentic dev didn't just speed things up, it changed what "shipping code" even means. Agents are pulling in their own dependencies, making their own calls, writing code that passes every test and still breaks somewhere you didn't plan for.
What is the biggest risk you're facing with agentic development? Sound off in the poll below ⬇️ -
Snyk reposted
Liran Tal
@liran_tal
1/
is prevention solved for agent-generated code?
Ezra Tanzer's take: architecturally, yes. we know which control goes where. running it while your AI SDLC changes every quarter is the hard part 🧵 -
Snyk reposted
Liran Tal
@liran_tal
Opus 5.5 one-shotting a Snyk VulnBench reel (the securing AI benchmark work)...
does not look as impressive as I hoped it to be -
Snyk reposted
Liran Tal
@liran_tal
Get up to speed on all things security agents and harnesses at AI Security Summit in SF on October 15th 🤖 🔥
-
Snyk
@snyksec
Attestation works because a human signed it. Access review works because someone can be walked out for abusing it. AI agents break both, running with production credentials and infrastructure control but none of the intent or consequences that make compliance actually work.
On September 29 at 1pm ET, Snyk's Mike Biocchi joins AWS's Sai Lolayekar, moderated by Brandon Dunlap, for an ISC2 Security Briefing on treating agents as real non-human identities: provisioning, least privilege, and revocation that actually happens, with accountability landing on whoever delegated the access, not the agent that can't be held to it.
Register Here: vist.ly/5juhk -
Snyk
@snyksec
Eleven years ago, three engineers had one idea: put security in the hands of the people writing the code.
That idea is now a platform securing code, dependencies, containers, and cloud for thousands of teams worldwide.
None of it happens without the people who built it. Thank you to every Snyker who shipped a feature, closed a deal, or believed in this mission before it was obvious.
Eleven years of building fast and staying secure. Now we're doing it for the age of AI, securing the agents and AI-generated code, shaping how software gets built next.
Here's to the next chapter! 🎉This media couldn't be displayed. See it on the original post. -
Snyk
@snyksec
Snyk is heading to the @AISecSummit in San Francisco on October 15 🌁
AI is shipping code faster than most security teams can keep pace with, and this is the one event built entirely around closing that gap.
Want to join us? Register here: vist.ly/5j9ut -
Snyk
@snyksec
Snyk is in the right place at the right time as the market shifts rapidly to agentic AI security.
Evo by Snyk has sustained 81.5% month-over-month customer growth since its first capability reached general availability in March. The number that says even more is the 76% of enterprises who bought Evo last quarter and had it running in production before the quarter closed. Enterprises aren't piloting this. They're moving as fast as the risk is.
That urgency has a cause. Across our 4,800+ customers, newly introduced vulnerabilities climbed 108% between Q4 2024 and Q1 2026, and that was before agentic code generation reached full scale. Agents widen the gap at both ends, generating more code than humans can review while attackers probe at machine speed, and no amount of AI grading its own homework closes a gap like that. It takes independent validation: a deterministic layer beneath the model with more than a decade of context.
We built Evo for exactly this moment.
Read the full story here: vist.ly/5itft -
Snyk
@snyksec
Anthropic's own threat intelligence report, published last week, describes an attacker whose malware got caught by security tools — then had it rewritten and redeployed by its own AI agents until it evaded detection again. In hours, not weeks.
AI has changed the attack landscape. That's the gap we're getting into on tomorrow. @TheRegister's James Hayes talks with Snyk's @mnair1 and @Anthropic's Alon Krifcher about closing it in four moves: discover the full attack surface, remediate the backlog, validate what's actually exploitable, prevent what comes next, seen from two vantage points on the same problem, the model layer and the application layer,
Register here: vist.ly/5iqq6 -
Snyk
@snyksec
Ask an agent to "write secure code" and it will try. But an instruction isn't a constraint. It shifts what gets written, it doesn't decide it 🔏
Read @EzraTanzer's piece on why prevention for agent-generated code isn't one control. It's four, and each one only works at a specific point in the loop: guidance in the agent's context for the risks you can name in advance, deterministic scans that fire while the agent still holds the prompt, semantic review of the assembled codebase for the logic flaws no scanner catches, and adversarial testing against what's actually running.
Read more here: vist.ly/5ij5b -
Snyk
@snyksec
Most security programs weren't built for an attacker that moves at machine speed, and next week is when that gap gets put on the table.
Next week, @TheRegister's James Hayes talks with Snyk's Manoj Nair and @AnthropicAI's Alon Krifcher about the gap most security programs aren't built to close: AI finding architectural flaws faster than anyone can patch them, while that same AI ships code faster than anyone can review it.
Closing that gap comes down to four moves: discover the full attack surface, remediate the backlog, validate what's actually exploitable, prevent what comes next, seen from two vantage points on the same problem, the model layer and the application layer.
If your program still runs at ticket speed, this is the session.
Register here: vist.ly/5hz4x -
Snyk
@snyksec
AI in security: who's winning right now, defenders or attackers?
-
Snyk
@snyksec
Coding agents are shipping more code than most teams can actually review. That's the tension at the center of the "dark factory" vision of software development, and it's the thread running through our next Boston meetup.
We're teaming up with the @aiseceng Community at Snyk's Boston office on Sept 17, 6pm ET, to bring together the people building with coding agents and the people making sure that's done safely. Three talks, three angles on the same question: how do you trust output you didn't write yourself?
@tessl_io's Sahil Deshmukh breaks down harness engineering for self-optimizing dev pipelines. Snyk's Brendan Hann and Ryan McMorrow demo how Snyk's Remediation Agent turns security findings into merge-ready fixes. And @QodoAI's Max Binshtok makes the case for an independent verification layer at the PR boundary.
Register here: luma.com/ainative-u9dd -
Snyk reposted
Liran Tal
@liran_tal
if "can't the coding agent just review our code for vulns now" has come up on your team — best model config we tested hit 75.4% agreement with our own SAST reference set. genuinely good. still a ~25pt gap to deterministic. data, not vibes: vulnbench.com
-
Snyk reposted
Liran Tal
@liran_tal
Here's the highlight from Snyk VulnBench that we published: Claude Sonnet 4.6 Medium produced the most one-off extra vulnerability reports: 61.7% of its LLM-only reports appeared in just one of five runs
What should you do about this? >> -
Snyk
@snyksec
Attackers aren't smarter. They're just faster now.
Join @TheRegister's James Hayes in conversation with Snyk's CTO & Chief Innovation Officer Manoj Nair and @Anthropic's Head of Applied AI Alon Krifcher on September 17 at 10am ET for a direct look at what's actually changing and what a credible response looks like.
AI finds architectural flaws at machine speed, then exploits them before most teams even clock they exist. Meanwhile that same AI is shipping code faster than any team can review it. Legacy bugs, new code, agents running in production: all targets, all at once.
Learn how to prepare for this new class of machine-speed attacks, what Snyk and Anthropic are each seeing from the model layer and the application layer, and practical next steps you can actually act on.
Save your seat: intelligence.theregister.com/paper/view/20624/how-to-prep… -
Snyk
@snyksec
The tools shaping tomorrow's workplace are being built today — the question is who's in the room deciding what they optimize for. 🤖
@womeninrevenue just launched its AI Leadership Council: senior leaders from business, tech, academia, and public policy coming together to study how AI is reshaping who gets hired, credited, and promoted.
Snyk is honored to be part of it, with our Chief People Officer, Diana Brunelle, serving as an inaugural member.
On September 11 we're hosting the Council's inaugural session at our Boston headquarters.
Learn more about Women in Revenue and the Council: vist.ly/5ggvg -
Snyk
@snyksec
Agents are only as powerful as the supply chain behind them is trustworthy. 🔐
Manoj Nair sat down with with Allie Howe on Insecure Agents to unpack packs what Snyk's research found when we looked at agent skills and MCP servers up close: architectural issues that don't map to typical software vulnerabilities — toxic flows, toxic skills, and access to enterprise data agents were never built to handle safely.
Without that supply chain locked down, agents don't get more powerful. They get riskier.
Watch the full conversation here: vist.ly/5gctp -
Snyk
@snyksec
Three assessments came back clean last quarter. 🔗 None of them asked whether the model could be steered into reaching the one low-severity bug that mattered.
That's chained risk: harmless-looking findings that compose into real impact. Dynamic scanning shows what's exposed, AI pentesting shows what's exploitable, AI red teaming shows what an adversary can pull off — run them separately and you get fragmentation, not coverage. Our new whitepaper, authored by Damian Tommasino, covers the operating model and economics of unifying all three, including why the costs differ by two to three orders of magnitude.
Read more here: vist.ly/5g9gm -
Snyk
@snyksec
Last week, the Snyk Boston team traded keyboards for golf clubs and let's just say the swings were more...enthusiastic than accurate 🫣
Summer SnykOut is one of the traditions we look forward to every year. This year's theme was Adventure awAIts, and Boston made sure it lived up to the name.
Cheers to the summer and cheers to our amazing Snykers 💜 -
Snyk
@snyksec
The sun's out in San Francisco, and Javaier Graza is soaking it in between building demos, talking to developers, and everything else that comes with being a Staff Developer Advocate at Snyk.
Watch below to follow along with him for an inside look at a day in his life working from Snyk's SF office.
See open roles in San Francisco here: vist.ly/5fz54This media couldn't be displayed. See it on the original post. -
Snyk
@snyksec
The best-performing model in Snyk VulnBench JS 1.0 matched 75.4% of our reference vulnerability set — strong on familiar exploit patterns, but still a real gap versus deterministic SAST
See how it stacks up: vulnbench.com -
Snyk reposted
Liran Tal
@liran_tal
Can an AI agent find the same security bug twice? We ran the identical review 5x on the same code to find out.
134 of 158 reference-matched findings held up every time. But 80 of 161 extra findings showed up in only 1 of 5 runs.
Full data: vulnbench.com -
Snyk reposted
Liran Tal
@liran_tal
Snyk VulnBench finally has a proper home: vulnbench.com
paper, methodology, raw data, and an explorer so you can check every number yourself. first release is about repeatability of AI vuln-finding. more releases coming so DM if you want to collab -
Snyk reposted
Liran Tal
@liran_tal
if you've got opinions on how to benchmark agentic security review properly (repeatability, ground truth, harness design) I'd love to hear them
published our methodology + limitations in the open: vulnbench.com. ping me, always down to compare notes 💜 -
Snyk
@snyksec
Same code, same prompt — a different queue each time. Full data: vulnbench.com
Nearly half of the extra vulnerabilities AI models flagged in our latest benchmark showed up in just 1 of 5 identical scans. -
Snyk reposted
Liran Tal
@liran_tal
Snyk VulnBench has a home now: vulnbench.com
We ran the same AI security review 5 times on identical code to see if it finds the same bugs twice. Short version: the bugs it knew, it found consistently. Everything else, less than half the time. Worth a look if "can the coding agent just do our security review" has come up around you lately.
Paper + full data linked from the site. -
Snyk
@snyksec
Snyk VulnBench now has a home: vulnbench.com — we ran the same AI security review 5x on identical code to see if it finds the same bugs twice. Known bugs: found consistently. Everything else: less than half the time. Worth a look 👀
-
Snyk
@snyksec
Snyk VulnBench now has a home: vulnbench.com — we ran the same AI security review 5x on identical code to see if it finds the same bugs twice. Known bugs: found consistently. Everything else: less than half the time. Worth a look 👀
-
Snyk
@snyksec
Most AI pentesting tools find bugs nobody asked about. Evo Continuous Offensive Security finds the ones that actually cost you: flaws in what your app is meant to do, not just how it's coded 👾
Join John Carione, Ricardo Alves, and Gabriel Brolo Tobar, Staff Security Engineer at @Yalo, on September 2, 11am ET, for reasoning-based pentesting that chains findings into real exploit paths, backed by platform context and independent validation.
Register here: vist.ly/5f8fn -
Snyk
@snyksec
We caught up with our partner Vinny Valenzuela at @Deloitte at Black Hat and asked what's actually breaking in enterprise security programs right now. The answer wasn't a gap in tooling. It was arithmetic: findings arrive faster than any team can triage them, and the backlog becomes a permanent record of what nobody got to.
That's the problem Snyk and Deloitte are solving together. Deloitte reshapes how security fits into the SDLC through Secure by Design; Snyk cuts the queue itself with prioritization grounded in real application context and fixes that land inside the developer workflow.
Listen below ⬇️ -
Snyk
@snyksec
Press Roundup🗞️ Lets get into it:
@WIRED's Will Knight broke the story on the technique itself: a shared encryption key flaw across Claude, GPT, and Gemini that let researchers, Snyk included, decode over 315,000 published reasoning blocks and recover 182 live credentials.
Decrypt's Jose Antonio Lanz and @TechTimes_News Kyle Belmonte covered the scale of what got exposed and what it means for anyone who's ever shared agent session logs online.
From Black Hat, @CRN's Kyle Alspach named Evo Continuous Offensive Security one of the 20 coolest AI and security products at the show, and Let's Data Science reviewed our 2026 State of Agentic AI Adoption report.
@CyberScoop ran an op-ed citing our ToxicSkills research on agent skill risk.
And that's just to name a few. Take a look if you're tracking where AI security is headed, and one to keep an eye on as more of these conversations play out across the industry in the months ahead. -
Snyk
@snyksec
Snyk, @Docker, and @KeycardAI published something rare in this market: a vendor-neutral, open source security baseline for AI agents. No product pitch. Just 6 outcomes and 35 controls anyone can build against.
According to Krzysztof Huszcza and Ezra Tanzer, the checklist isn't the hard part, the sequence is. A developer running a coding agent and a production agent touching customer data need completely different starting points, even under the same 35 controls.
Read their in-depth analysis and watch the panel we took to Black Hat here: vist.ly/5enjx -
Snyk
@snyksec
We took to the floor of Black Hat to ask security practitioners about their first-hand run-ins with rogue agents, and whether AI is making security better or worse. Turns out there's no clean answer.
Got a hot take? Drop it below ⬇️This media couldn't be displayed. See it on the original post. -
Snyk
@snyksec
Facts.
Rob Miles
@robertskmiles
An important principle:
Never pay someone to remove a problem that they themselves created -
Snyk
@snyksec
A deterministic check runs twice and gives you the same answer twice. That's the whole point.
We ran 300 scans to see how close the latest models get. On the vulnerabilities they caught, they were steady. Everything else moved. Nearly half the issues raised outside the deterministic baseline showed up in only one of five identical runs.
Not an argument against models. An argument for pointing them at the surface deterministic analysis can't reach.
Get the full scoop from Manoj Nair below 📹
Read more here: vist.ly/5ef9u -
Snyk
@snyksec
The average pentest still covers 15 days a year. Attackers get the other 350.
Join John Carione, Ricardo Alves ,and Gabriel Brolo, Staff Security Engineer at Yalo, on September 2, 11am ET. See how Evo Continuous Offensive Security closes that gap with reasoning-based testing that runs on every meaningful code change with a live demo.
Register here: vist.ly/5dz4i -
Snyk
@snyksec
Snyk @ Black Hat 2026 🕹️👾
This media couldn't be displayed. See it on the original post. -
Snyk
@snyksec
There's no better place for an unscripted security conversation than a nightclub with a pool. 🌊
That's where Snyk's Ezra joined leaders from Docker and Keycard during Black Hat week to talk through what it actually takes to secure a coding agent, from every angle at once — grounded in Agent Baseline, the whitepaper that we published last week. Check it out here: agentbaseline.org.
What a room! Thanks to Allie Howe and Insecure Agents for hosting, Docker and Keycard for showing up, and everyone who picked a security talk over a DJ set on a Vegas pool deck.
Missed it? Come find us on the Black Hat floor today, August 5th, at 1pm — we're walking through it live at Snyk's booth # 3752. -
Snyk
@snyksec
Today we're delivering the largest Snyk AI Security Platform expansion to date 💥
Evo Continuous Offensive Security, the adversarial proving layer enterprises have been asking for, is now in GA. Alongside it: Snyk Secrets in GA, a major AI-SPM upgrade, and a first look at Evo Agentic AppSec.
It's security that keeps pace with how software is built, governed, and attacked, at every layer, and every stage of the agentic development lifecycle.
Watch the video below and read the full story here: vist.ly/5dhqpThis media couldn't be displayed. See it on the original post. -
Snyk
@snyksec
In January, a third of agentic adopters were running the full stack. Six months later, it's a majority of companies.
That's from Volume II of our State of Agentic AI Adoption research: 3,000+ enterprise accounts, 1.39 million repositories. Organizations aren't testing one layer of agentic architecture and stopping, they're deploying agent frameworks and MCP servers together, the connective layer that gives agents access to tools, services, and data. And they're doing it in months.
Here's the other number that should worry security teams: the real AI footprint runs roughly 3x larger than model inventories show once you count everything wired around each deployed model. Most programs counting models are seeing about a third of what's actually running.
Adoption curves usually give governance time to catch up. This one isn't waiting.
That's two findings, but the report has a lot more: where AI is deepening fastest, how the provider landscape is shifting, why half of organizations still can't trace the data behind their own models.
Read the full report: snyk.io/lp/state-of-agentic-ai-adoption-vol-II/ -
Snyk
@snyksec
@Snyk, @Docker, and @Keycard have teamed up to create Agent Baseline. It closes a gap most security practices weren't built for: agents that hold real access and real permissions, and can be reprogrammed at runtime by a single prompt.
Agent Baseline is vendor-neutral reference architecture for identifying agents, bounding their authority, controlling their actions, and proving their outcomes. It's open source, versioned in public, and open for comment through September 30 — built to be implemented and challenged.
Read the white paper here: agentbaseline.org
Register for the Black Hat panel: luma.com/insecure-wbn3 -
Snyk
@snyksec
An OpenAI model got put in an isolated test environment last week, found a real zero-day nobody knew about, and used it to break into Hugging Face's production servers. It was trying to get the answer key to its own benchmark.
Two of the most safety-conscious labs in the industry, and neither one could fully validate its own model's boundaries from the inside. It's proof that the generator can't be the validator — we've said it for years about AI security. Tthis is just the first time it played out in public, disclosed, with a paper trail.
If the labs building this stuff can't validate their own models, nobody running five different vendors in production should assume they can either.
We broke down what happened and what it means for teams shipping AI-assisted code. Read the full story here: snyk.io/blog/openai-hugging-face-incident/ -
Snyk
@snyksec
The countdown to Black Hat is on 🎰
It's officially one week until we'll see you on the show floor. You'll find us at booth # 3752 with live demos, a hands-on challenge, and swag worth grabbing.
Swing by to see the Snyk AI Security Platform in action and get all the answers to your agentic security questions.
Learn more here: snyk.io/events/black-hat/ -
Snyk
@snyksec
This week, Snykers took over San Francisco for our first-ever Mid-Summer SKO: Agentic Summer.
R&D and GTM came together to make sure Snyk delivers on securing software at build speed: one team, one north star, one architecture that secures every loop in the agentic development lifecycle.
Thanks to every Snyker who showed up ready to build 💜 -
Snyk
@snyksec
Who's ready for Vegas?! ✨
Snyk is Black Hat bound, and this year is going to be better than ever.
Mark your calendar. More details to come. -
Snyk
@snyksec
Snyk has been showing up across security and dev press this month.
TechBullion flagged Snyk Code as a must-have for full stack developers. Forbes named us among the platforms tackling AI-generated code's reliability gap.
FutureCISO covered the launch of Evo Agentic Development Security and how autonomous agents have outpaced the models built to govern them.
SD Times named Snyk to its 2026 SD Times 100 in Security, Trust & Governance, for developer-first vulnerability management. Tech Times cited Snyk research on the Cline supply chain attack.
And DZone's Igboanugo David Ugochukwu cited Snyk's research on where credentials actually leak, Slack, Jira, Confluence, not just code, in a deep dive on machine identity debt.
A few different angles and an aray of publications, all circling the same thread: where AI-native development is headed, and who's building for it. -
Snyk
@snyksec
Agentic vulnerabilities?
GhostApproval 🤝 ZipSlip: snyk.io/blog/symlinks-are-still-scary/ -
Snyk
@snyksec
Your AI coding assistant can know a file is actually your .zshrc, and still ask you to approve editing "project_settings.json" like that's what it is. 📷
Researchers just named the gap: GhostApproval, a decades old symlink trick aimed at a brand new surface. Agents read your repos constantly, and a confirmation dialog is only as honest as the filename it shows you.
Full breakdown, symlinks and all:: snyk.io/blog/symlinks-are-still-scary/ -
Snyk
@snyksec
We ran the same LLM security review 300 times on identical code.
When it matched Snyk Code's reference findings, it was stable: 85% showed up in all 5 runs.
When it found something extra, it wasn't: nearly half of those findings appeared in just 1 of 5 runs.
LLM vs. SAST isn't the story. They fail differently — that's why you use both.
Read more here: snyk.io/blog/snyk-vulnbench-js-1-0-llm-security-review-re… -
Snyk
@snyksec
Your AI coding agents are executing commands, pulling in MCP servers, and shipping code at machine speed. Most security stacks can't see it.
Join Daniel Berman and Damian Tommasino for a deep dive into Agentic Development Security 🔒
See how it governs the agent supply chain, agent behavior, and AI-generated code in real time, without slowing developers or agents down.
Register here: go.snyk.io/securing-ai-driven-software-dev.html -
Snyk
@snyksec
This week, Snyk is in Paris for RAISE Summit's RAISE Week, and we're not just attending.
On July 7th, Snyk is co-hosting the The AI Security Summit at Pavillon Vendôme, bringing together senior security and AI leaders for the conversations that aren't in any playbook yet. Then on July 8th, our CTO Manoj Nair takes the summit's Master Stage for his keynote address: "Agentic Development Security: The Three Problems Nobody Was Solving, and the One That Matters Most for 2026."
As agents write more of the code, security can't be an afterthought; it has to be built into the systems doing the building. That's the energy we're bring to Paris 🇫🇷
See the full agenda here: tickets.raisesummit.com/2026/agenda/
En français ⬇️
Cette semaine, Snyk est à Paris pour la RAISE Week du RAISE Summit — et on ne fait pas que participer.
Le 7 juillet, Snyk co-organise l'AI Security Summit au Pavillon Vendôme, réunissant des décideurs seniors en sécurité et en IA pour des discussions qu'aucun playbook n'a encore anticipées. Puis, le 8 juillet, notre CTO Manoj Nair montera sur la Master Stage du sommet pour sa keynote : «Agentic Development Security: The Three Problems Nobody Was Solving, and the One That Matters Most for 2026».
À mesure que les agents écrivent une part croissante du code, la sécurité ne peut plus être une réflexion après coup : elle doit être intégrée aux systèmes qui construisent. C'est l'énergie qu'on apporte à Paris 🇫🇷
Retrouvez l'agenda complet ici: tickets.raisesummit.com/2026/agenda/ -
Snyk
@snyksec
Last night we threw a rooftop party with Keycard during AI Engineer World's Fair. Vibe coding battles, a happy hour that ran late, and a room full of the people actually building in this space.
Thanks to everyone who came out 🎉
Swipe through the photos below! -
Snyk
@snyksec
Snyk is pioneering security at AI Engineer World's Fair in San Francisco right now.
Randall Degges introduced the first-ever AI Security Track — presented by Snyk — on the main stage. Manoj Nair delivered the Security Keynote. Ezra Tanzer demoed what AI security looks like when it's in the loop from the beginning.
From code to cloud to AI runtime, developers and security teams finally have one place to discover, defend, and govern. This is what secure at inception actually looks like ✅ -
Snyk
@snyksec
AI agents are writing code, opening pull requests, and calling production APIs. They've become the fastest-growing class of developer, and they don't wait for a security review.
That's why Snyk is proud to parter with Insecure Agents for AAuth Night: Moving Beyond OAuth.
Becasue AAuth is one of the many building blocks in creating a secure agentic development ecosystem.
Come find us there: July 1st in San Francisco, alongside AI Engineer World's Fair, 5:30-8:30PM PST
Register here: luma.com/a2h25m60 -
Snyk
@snyksec
Enterprises aren't short on enthusiasm for AI agents. They're short on confidence that those agents will do what they're supposed to do.
Oliver Neuberger, Cybersecurity Practice Lead at our partner Accenture, frames the real question well: the potential is enormous, but deploying agents securely in the enterprise means building the right guardrails before something goes wrong, not after.
Agentic Development Security puts those controls inside the workflow, where they can actually keep pace with what agents are creating, invoking, and executing.
See how: snyk.io/evo -
Snyk
@snyksec
Join Snyk and Keycard for an all-you-can-build rooftop party at AI Engineer World's Fair!
Next Tuesday, June 30th, we're gathering the boldest builders and security folks in the AI era. Expect vibe coding battles, a live AI red team challenge, and a happy hour to keep it going.
See how your build holds up against the people redefining how we build and secure.
RSVP before spots run out: go.snyk.io/sf-community-jam.html -
Snyk
@snyksec
43% of developers run two or more AI coding environments at once, 37% run more than three or more. More than half have MCP servers installed. 1 in 12 devs has a high or critical finding.
The agentic development footprint is bigger than most orgs know. And it requires securing. That’s why we just launched Evo Agentic Development Security.
Read the full report: snyk.io/lp/state-of-agentic-dev-supply-chain-report/ -
Snyk
@snyksec
Untrusted inputs. Unbounded actions. Unverified output.
That's the AI workforce risk no one was governing…until now.
See Evo Agentic Development Security in action below.
Full announcement here: snyk.io/news/snyk-launches-evo-agentic-development-security/ -
Snyk reposted
Liran Tal
@liran_tal
Color me excited for @snyksec's new mission on Agentic Development Security
It's an enforcement layer that operates inside the agent execution loop across three layers:
1. securing the agent supply chain before agents interact with it
2. governing agent behavior at runtime
3. validating code output at the moment of creation
What the data behind agentic security looks like?
Across nearly 9,700 developer environments: 43% of developers run two or more AI coding environments simultaneously.
More than half have MCP servers installed which is the most instrumented environments had over 80 running at once.
1 in 12 developers with MCP servers has a high or critical finding in that supply chain. Nearly 1 in 4 developers has at least one skill installed, averaging 18 each. More than 1 in 10 of those skills reference external dependencies or externally hosted instructions. 13.4% of skills contain critical security flaws. 7.1% leak credentials. 1,476 malicious payloads are currently in the wild.
All the data supports it - agentic developers and AI Security Engineers have no visibility into MCP configurations, skill provenance, or what agents do at runtime...
The new Evo platform by Snyk fixes this! -
Snyk
@snyksec
A year ago, a developer wrote your code. Six months ago, a developer with an AI assistant. Today? An AI agent...autonomously…and nobody is watching.
Evo Agentic Development Security changes that.
snyk.io/news/snyk-launches-evo-agentic-development-security/This media couldn't be displayed. See it on the original post. -
Snyk reposted
AI Security Engineers
@aiseceng
Munich AI Builders 🤖
AI agents don't just generate text — they use tools, call APIs & make decisions.
@chrfritz from @QAware is breaking down SAIF 2.0 & the new attack vectors this creates.
July 2, Munich 🔒
👉 luma.com/aiseceng-sfge -
Snyk
@snyksec
Every generation has its fire. Ours is AI.
The question has never been whether to use it — it's how you contain it.
Evo is how you secure the burn. -
Snyk reposted
AI Security Engineers
@aiseceng
Dallas AI hackers! Your city, your stage—We're sponsoring you to lead an AI Security Meetup and inspire your friends. form.typeform.com/to/KYAgptwu
-
Snyk
@snyksec
That's a wrap on AWS Summit NYC. 🗽
The theme was impossible to miss: agents are writing more of the code, and they're writing it fast. Every conversation at our booth circled the same question — who's securing what the agents ship?
That's exactly what we came to show. Evo by Snyk discovers, monitors, and secures AI agents and the code, models, and dependencies they pull in — inside the AWS workflows your teams already run.
Thanks to everyone who stopped by to talk through securing AI-generated code in the real world. The agents aren't slowing down and neither are we. -
Snyk
@snyksec
Open source maintainers keep the internet running. Most do it for free, alone, and without enterprise security tooling 🥵
That's what the @Snyk Secure Developer Program is for.
Qualifying maintainers get the full Snyk AI Security Platform (the same platform Fortune 500s pay for) at no cost. Risk-based prioritization, automated fix PRs, early access to the Snyk Remediation Agent. All of it!
Learn all about it here: snyk.io/blog/secure-developer-program/ -
Snyk
@snyksec
Snyk is architecting a comprehensive AI security experience at the first-ever AI Security track at AI Engineer World's Fair.
We've brought together speakers from NVIDIA, Anthropic, dbt Labs, Keycard, Accenture, Form3, and The Carlyle Group to architect sessions around one core belief: security doesn't start at deployment. It starts at inception.
Join us at Moscone Center in San Francisco on June 30th.
Learn more here: www.ai.engineer/worldsfair/schedule?track=Security -
Snyk
@snyksec
😮 A dormant contributor's npm account nobody bothered to revoke just got the entire @mastra scope trojanized. 140+ packages, ~4M monthly downloads on @mastra/core alone, all carrying a fake "easy-day-js" dependency that drops a crypto-wallet stealer on install.
Kudos to the Mastra team for quick response here to remediate 💜👏
Check your builds:
npm ls easy-day-js
Full write-up: snyk.io/blog/a-forgotten-contributor-account-compromised-… -
Snyk
@snyksec
🚨 BREKAING: Mastra npm package compromise
On June 17, 2026, an attacker republished the entire @mastra npm scope. 140+ packages, including @mastra/core, all trojanized in a single overnight burst
The way in wasn't a clever exploit.
It was a former contributor's account whose access nobody ever revoked 🧵👇Post not available here, view on X
Snyk
@snyksec
4/ easy-day-js poses as dayjs, but its postinstall hook is a dropper: it switches off TLS verification, pulls a second stage from a raw IP, and runs a cross-platform crypto-wallet stealer + RAT in the background, then deletes itself.
MetaMask, Phantom, Coinbase Wallet, and more.
Snyk
@snyksec
5/ The good news: Mastra's source was never touched (poison was injected at publish time) and clean versions are already out.
Check now:
npm ls easy-day-js
If it's there, treat the host as compromised: rotate creds, move wallets, upgrade clean.
Full breakdown 👇 -
Snyk reposted
AI Security Engineers
@aiseceng
Join our new Miami AI Security Meetup 🚀 June 13. @_clarkio, @snyksec breaks down Rules, Skills, Hooks & MCP—and how to use them safely, with @rodsoto hosting the meetup
www.meetup.com/ai-security-engineers-miami/events/315050047/ -
Snyk reposted
RAISE Summit
@RaiseSummit
Most enterprises are securing the wrong layer. The conversation has fixated on agents in production, but the deeper shift is upstream: software is increasingly being written by agents, not developers.
That moves the security question from "is this code secure?" to "can we trust the system that created it?"
It's a gap that introduces three security problems that no existing category was built to solve:
1. The supply chain the agent depends on: MCP servers, skills, plugins
2. The agent's behavior at runtime: tool calls, shell access, network traffic
3. The code the agent ships: it passes tests but breaks at authorization, trust boundaries, and business logic.
This July 8, Manoj Nair, Chief Innovation Officer at @Snyksec, addresses these frictions during his Keynote, “Agentic Development Security: The Three Problems Nobody Was Solving, and the One That Matters Most for 2026.”
Snyk knows security. Agents know the app. Neither works alone.
If you're a senior leader shaping security strategy, the AI Security Summit (July 7), hosted by Snyk during RAISE Week, is where this conversation continues
✉️ Apply for an invitation: luma.com/8x5mssq6?hss_channel=tw-1729900317657964544 -
Snyk
@snyksec
Calling all Miami bound hackers and AI builders 🌴🇺🇸
All about ToxicSkills, hacking MCP servers and more in this AISecEng Miami chapter meetup 👇
AI Security Engineers
@aiseceng
Today is the day! If you're in the Miami area, join us for an AI Security Meetup. There's still time to secure a spot for free and learn about Rules, Skills, Hooks & MCP—and how to use them safely with @_clarkio from @snyksec and @rodsoto
www.meetup.com/ai-security-engineers-miami/events/315050047/ -
Snyk
@snyksec
Snyk and Keycard are hosting a blowout sunset rooftop party during AI Engineer World's Fair in San Francisco and you're invited 🪩
Spots are limited, RSVP here: go.snyk.io/sf-community-jam.html -
Snyk reposted
Manoj Nair
@mnair1
Open source maintainers drowning in vuln debt?
Snyk: 6 vulns detected for every 1 fixed. AI code = 65-70% of prod, half vulnerable.
Today: Snyk Remediation Agent in the CLI — available to ALL open source maintainers + customers in their own envs.
Not raw Claude. Deep Snyk harness + multi-frontier models.
The results:
• Fix rate ~doubled (23% → 45%)
• Crit/High/Med: 44% → 91%
• Token cost/fix: -61%
Its the same power that let Labelbox erase 2-year debt in 2 weeks + Relay Network fix criticals in 24h (zero crit/high issues).
Paired with last week’s Evo COS it’s a complete ecosystem to find + fix at scale.
Blog: snyk.io/blog/snyk-remediation-agent-in-the-cli/
#devsecops #opensource #aiThis media couldn't be displayed. See it on the original post. -
Snyk reposted
Tracy Massaro
@TracyMassaro_
Incredible lineup with @snyksec, @klaviyo, @cursor_ai, @CarGurus talking about how teams are building with AI. Lots of discussion about how jobs are changing (identify crisis is real for many), how teams are using different tools and skills and more.
Answers to burning questions:
Does every PR get reviewed by a Human? No according to Cursor.
Are junior engineers still getting hired?Yes according to Klaviyo.
What KPIs folks are using to measure success (ROI, speed to impact, code half life, decrease in code issues/incidences, failures, security).
Thank you @klaviyo for being a @Techweek_ sponsor!
#bostechweek -
Snyk reposted
beyondcontent
@beyondcontent
I learned how little I know about vibe coding and security. SNYK is now part of my tech stack. Definitely appreciate the free tier to find out what it's all about. Recommend others do too.
-
Snyk reposted
Manoj Nair
@mnair1
Excited to share my own AI Innovation learnings and lessons from conversations with 100s of leading companies and labs at the Paris @RaiseSummit Foundation Track
@snyksec #aisecurity #agenticdevelopment
RAISE Summit
@RaiseSummit
The critical question in AI is no longer who builds the best model.
It's who controls the physical layer.
Who owns the silicon. Who finances the megawatts. Who builds the infrastructure that determines whether nations build AI on their own terms, or someone else's.
That's the Foundation Track.
We are proud to welcome four leaders joining the Foundation Track at RAISE Summit 2026.
@mmoazami — Vice Chairman at @DDNintelligence
From $6B in revenue at Cisco to co-founding a $300M deep tech investment firm, Mohsen has spent decades building global enterprise infrastructure. He served as President of International at Groq and now advises Blackstone.
@mnair1 — Chief Innovation Officer at @Snyksec
Leading Snyk’s shift from developer security into AI Trust, focusing on opportunities in generative AI and agentic AI to accelerate growth. Previously CPO, he helped scale the platform across Fortune 500 deployments worldwide.
@robertwachen — Co-Founder & President at @Etched
Building AI chips designed to outperform GPUs by 10x. A Thiel Fellow and Harvard dropout, he previously co-founded Prod, a $50B+ start-up accelerator. Etched is betting on a new era of purpose-built silicon.
Suresh Vasudevan — CEO at @Clockworkio
Pioneering Software-Driven AI Fabrics™, a software layer optimizing GPU infrastructure at scale. Clockwork's TorchPass is independently benchmarked as a fault-tolerant solution maintaining full-speed performance, redefining how cluster reliability drives AI economics.
Join the leaders operating across distinct layers of the AI infrastructure stack this July 8-9 at the Carrousel du Louvre.
The full RAISE Summit agenda drops next week. Final pricing ends June 4.
Secure your ticket to RAISE → www.raisesummit.com/tickets-2027
Where visionaries and AI converge. -
Snyk reposted
boldstart ventures
@Boldstartvc
continous targeted pen testing is here from @snyksec
Snyk
@snyksec
Today, we're excited to unveil Continuous Offensive Security, the newest product in the Evo by Snyk ecosystem. It brings AI-native pentesting to the enterprise.
The full walkthrough is in the video below.
Get all the details here: snyk.io/news/snyk-unveils-continuous-offensive-security-t… -
Snyk reposted
Pure AI
@PureAINews
Can you verify that your AI applications are secure?
Join us, sponsor @snyksec, and a panel of experts on June 18th for this FREE webcast on the OWASP AI Security Verification Standard and AI-native application security.
Register now: pureai.com/webcasts/2026/06/snyk-ai-radar-securing-the-ai…
#owasp #devsecops -
Snyk reposted
RAISE Summit
@RaiseSummit
The most important conversation you'll have this year is with someone who isn't answering your cold email.
Not because they’re ignoring you. Because they're heads-down building.
The one place where those conversations happen naturally is in person.
Proximity is the ultimate currency in AI.
RAISE Summit 2026 brings together the companies building the foundation, the frontier, and everything in between. From hyperscalers to dev tooling, from enterprise to financial, here's who's in the room.
Headlining it all:
@IREN_Ltd and @cognition
The diamond tier:
@Snyksec, @Nscale, @togethercompute, @Cursor_ai
The infrastructure powering the frontier:
@CoreWeave, @Nebiusai, @Vultr, @WEKAIO, @SambaNovaAI, @Baseten, @CrusoeAI, @DDNintelligence and more.
The builders' toolkit:
@ElevenLabs , @JetBrains, @GetSentry, @Modal, @Glean, @FireworksAI_HQ, and the rest of the AI-native stack.
The enterprise + financial backbone:
@BankofAmerica, @Stripe, @MongoDB, @Datadoghq, @Alibaba_cloud, @Lenovo, @NetApp and more.
9,000+ attendees. 2,000+ companies. 350+ speakers. 80% C-level and founders.
July 8-9 2026 · Carrousel du Louvre, Paris
Last chance: Save 25% before MIDNIGHT
🎟️ Secure your ticket: www.raisesummit.com/tickets-2027 -
Snyk reposted
Emil van Galen
@EmilVanGalen
For more info about the 'Phantom Gyp' technique used by recent malicious NPM packages, check out the "The novel part: install-time execution through binding.gyp" of the following article from Snyk:
snyk.io/blog/node-gyp-supply-chain-compromise-self-propag… -
Snyk
@snyksec
Your AI coding assistant is only as good as the context it works with 🥸
Without security intelligence behind it, you're getting code that works but not code that's ready to ship.
Join in this Thursday, June 11th to see exactly how it works.
Register: go.snyk.io/optimize-token-usage-evo.html -
Snyk
@snyksec
Snyk is heading to the Silicon Valley Cybersecurity Conference! Join us June 11th at San José State University to learn more about our Snyk Learn and University Partnerships Program.
Learn more here: www.svcc-svcsi.org -
Snyk
@snyksec
A new npm supply chain worm is spreading by hiding in binding.gyp.
Snyk detects and lists all 57 affected packages with advisories in the Vulnerability Database and a live incident page updated as new malicious versions are confirmed.
Full breakdown: snyk.io/blog/node-gyp-supply-chain-compromise-self-propag… -
Snyk
@snyksec
For the first time the AI Engineer World's Fair has a dedicated AI Security track and Snyk is proud to be the presenting partner.
Join us in San Francisco, Jun 29 – July 2 for sessions built around the belief that security starts at inception.
More here: snyk.io/events/ai-engineer-worlds-fair/ -
Snyk reposted
Jamie Scott Craik
@jscraik
Great insight into some areas for improvement with regards to skill.md @liran_tal #aidevcon #londonmaxxing
Tessl
@tessl_io
As Liran Tal (@liran_tal) continues his session at AI Native DevCon, one thing is clear:
AI agent security is no longer a future problem.
From malicious SKILL.md files to prompt injection and agent supply chain attacks, today's talk highlighted why security needs to be built into every agent workflow from day one.
The good news? The conversation is just getting started.
More sessions are coming up live from AI Native DevCon:
www.youtube.com/watch?v=akZ85mG5HXY
Join free virtually:
tessl.io/devcon/
And for those in London, we'll see you at the Conference Party tonight. -
Snyk reposted
Tessl
@tessl_io
As Liran Tal (@liran_tal) continues his session at AI Native DevCon, one thing is clear:
AI agent security is no longer a future problem.
From malicious SKILL.md files to prompt injection and agent supply chain attacks, today's talk highlighted why security needs to be built into every agent workflow from day one.
The good news? The conversation is just getting started.
More sessions are coming up live from AI Native DevCon:
www.youtube.com/watch?v=akZ85mG5HXY
Join free virtually:
tessl.io/devcon/
And for those in London, we'll see you at the Conference Party tonight. -
Snyk reposted
Jack Wotherspoon
@JackWoth98
Great talk on Agent Skills and the potential attack vector they offer @ainativedev in London.
I should probably be reading the contents of Agent Skills I install more often… 🙋♂️
P.S. @liran_tal is one of the best in the biz! -
Snyk reposted
AI Native Dev
@ainativedev
Liran Tal ( @liran_tal ) has just taken the stage at AI Native DevCon.
37% of nearly 4,000 AI agent skills analyzed contained malware or security weaknesses.
Liran will be showing how attackers are targeting agent ecosystems and what developers can do to defend against it.
Watch live:
www.youtube.com/watch?v=akZ85mG5HXY
Register for the virtual session now to get updated:
tessl.io/devcon/ -
Snyk
@snyksec
If you've paid any attention in the last couple weeks, you know zero-days aren't slowing down 🥵
When a new one hits, the first question is always the same: are we impacted? Snyk's Zero Day Report gives you the answer instantly.
See in action below. -
Snyk
@snyksec
ICYMI last week, Snyk launched Evo Continuous Offensive Security 🌊
The New Stack covered why it matters: traditional pentesting averages 15 days of coverage a year, leaving 350 days for attackers. COS is built to close that gap.
Read the full story: thenewstack.io/snyk-pentesting-ai-agents-security/ -
Snyk
@snyksec
Relay Network had a clear security posture goal: zero critical, zero high-severity issues across their codebase.
By embedding Snyk directly into their workflow, their team moved security to the moment code is written.
The full story here: snyk.io/blog/relay-network-ai-coding-securely-coagentic-d… -
Snyk
@snyksec
Today, we're excited to unveil Continuous Offensive Security, the newest product in the Evo by Snyk ecosystem. It brings AI-native pentesting to the enterprise.
The full walkthrough is in the video below.
Get all the details here: snyk.io/news/snyk-unveils-continuous-offensive-security-t… -
Snyk
@snyksec
We hope y'all are catching a break from those supply chain attacks 😅
-
Snyk reposted
Daniel Newns
@DanielNewns
What a week it's already started out to be! Just catching up with all the CVE's and the huge Laravel Lang supply chain Advisory there is a great breakdown of it over on the @snyksec blog - snyk.io/blog/laravel-lang-supply-chain-advisory/.
It's apt then that in my inbox today is a email from @valorin with his latest security tip - securinglaravel.com/security-tip-secure-your-repositories…
and then the release of Laravel Moat by @enunomaduro - laravel.com/blog/moat-a-security-review-for-your-github-a…
It's more important now than ever to be vigilant and to keep on top of your applications packages making sure you're keeping them up to date and not running any outdated software at all.
If you do need someone to take a look at your applications to make sure that everything is ok then why not drop @jumptwenty4 a line and let's see how we can work together to help you get your applications back up to date. -
Snyk reposted
Liran Tal
@liran_tal
Max totally get you and I'm concerned about npm installs too
This is a screenshot of a real Cursor session I had, asking it to add the `serve` npm package (to serve static HTML files for me)
You can see how it used Snyk to health check the open source package from malware etc -
Snyk
@snyksec
See you in the Fan Zone ⚽️ 🏆
We're bringing the Snyk Connect community together. Part tournament, part tailgate, all defense. Live hacking and head-to-head AISec challenges, stadium-style eats, and giveaways worthy of a champion.
Grab your spot here: wc.snyk.io -
Snyk
@snyksec
Active supply chain attack: 700+ Laravel related package versions compromised
An attacker rewrote historical Git tags across 4 laravel-lang/* packages, pointing them to a malicious fork.
The payload downloads a credential stealer.
Rotate everything if you're infected.
Snyk
@snyksec
Write-up here: snyk.io/blog/laravel-lang-supply-chain-advisory/
-
Snyk
@snyksec
Versions of
- laravel-lang/lang
- laravel-lang/http-statuses
- laravel-lang/attributes
- laravel-lang/actions
have been published with malicious versions
Packagist has unlisted the packages, but if you installed any of them between May 22–23, treat the environment as compromised
Snyk
@snyksec
Run snyk test against your Composer repos now.
```sh
snyk test
```
If you’re a Snyk Enterprise customer, check Analytics → Remediation → Zero Day Report
Snyk
@snyksec
Write-up for the PHP Laravel packages that were compromised (Lang libraries): snyk.io/blog/laravel-lang-supply-chain-advisory/
-
Snyk
@snyksec
🚨 Malicious Laravel-Lang packages published to Packagist
- This supply chain incident affects 700+ versions, 4 packages in the PHP Laravel ecosystem
- Published on Packagist under the laravel-lang namespace. -
Snyk
@snyksec
ICYMI: The Snyk Security Desktop Extension is now available in Claude Desktop for macOS and Windows 🔐
▶️ Watch the video below to see how to connect Snyk to Claude Desktop.
Read the full announcement: snyk.io/blog/claude-enterprise-integration-desktop-expans… -
Snyk
@snyksec
Our CRO Tom Nielsen talked with CRN about how AI coding agents are shipping code faster than security teams can review it. Partners embedded in customer environments are uniquely positioned to help govern AI-driven development at scale.
Read more here: www.crn.com/news/security/2026/snyk-boosts-partner-servic… -
Snyk
@snyksec
The supply chain campaign that hit AntV yesterday reached PyPI. Microsoft’s `durabletask` was compromised with an infostealer, worm, and disk wiper. The payload drops a second-stage from `check.git-service[.]com` and runs on Linux only.
Full brief here: snyk.io/blog/durabletask-pypi-supply-chain-attack/ -
Snyk
@snyksec
The AntV incident involved compromised npm packages published under the @antv/* namespace & additional npm packages
This supply chain attack included mechanisms for credential harvesting, GitHub-based exfiltration, and further supply-chain propagation: snyk.io/blog/mini-shai-hulud-antv-npm-supply-chain-attack/ -
Snyk
@snyksec
This page summarizes the AntV npm supply chain compromise associated with the ongoing “Mini Shai-Hulud” campaign
security.snyk.io/antv-supply-chain-compromise-may-2026 -
Snyk reposted
Liran Tal
@liran_tal
If you want the same guardrails you can install the Snyk MCP server (Snyk Studio) from here, it's free: snyk.io/ai-vibe-check/
-
Snyk reposted
Liran Tal
@liran_tal
My Python friends, watch out for durabletask: snyk.io/blog/durabletask-pypi-supply-chain-attack/
All 3 malicious versions were yanked from the repo, and we've seen only a very small footprint of it impacting users so hopefully this malware hasn't hit you -
Snyk reposted
daily.dev
@dailydotdev
1:10 TanStack/npm Supply Chain Worm Hits 170+ Packages, Reaches OpenAI @tan_stack @tannerlinsley @OpenAI @npm
1:18 node-ipc npm Compromise — Steals 90+ Credential Types via DNS Exfiltration @npm @snyksec -
Snyk
@snyksec
The latest Mini Shai-Hulud doesn’t just steal credentials, it installs a C2 daemon that polls GitHub hourly for signed commands. It hooks Claude Code and VS Code to re-execute on startup. It propagates using stolen npm tokens.
Full writeup: snyk.io/blog/mini-shai-hulud-antv-npm-supply-chain-attack/ -
Snyk
@snyksec
300+ malicious package versions across 323 packages in a 22-minute automated burst.
The Mini Shai-Hulud supply chain worm hit the AntV ecosystem today via a compromised maintainer account.
@antv/g2, @antv/g6, echarts-for-react, and more.
Details here: snyk.io/blog/mini-shai-hulud-antv-npm-supply-chain-attack/ -
Snyk
@snyksec
What if you find out you've been infected with the Shai Hulud worm? watch here: www.youtube.com/watch?v=YrwM2EFYrUY
Brian Clark goes through the TanStack supply chain attack, details, recap, and follow through for secure development -
Snyk
@snyksec
🚨 Mini Shai-Hulud campaign impacting AntV libraries
TeamPCP published 637 malicious package versions across 317 packages in a 22-minute automated burst on May 19, 2026
The packages collectively represent approximately 16 million weekly downloads
Snyk
@snyksec
The attack vector was a compromised npm maintainer account.
The malware embedded in affected packages harvests developer secrets and cloud credentials, establishes persistent C2 access, and attempts to self-propagate to additional packages using stolen npm tokens. -
Snyk
@snyksec
Snyk is hitting the road for the most exciting watch parties of the summer, and you're invited ⚽️🏆
We're rolling into 9 cities across North America to catch the world's biggest matches with the security pros defending the AI era.
Grab your seat here: wc.snyk.io -
Snyk
@snyksec
should we drop some of the insights and stats from the Snyk 2026 State of Agentic AI Adoption ? 💎🤩
Post not available here, view on X
Snyk
@snyksec
The top 5 most adopted AI services
- OpenAI
- Google
- Cohere
- Hugging Face
- Anthropic
Snyk
@snyksec
model variance is also a real struggle with users adopting multiple underlying models for their agentic harness, potentially from different vendors too
for example, OpenAI GPT family vs Anthropic opus family of LLMs -
Snyk reposted
Liran Tal
@liran_tal
From tests we're running at Snyk - yes: this can get installed as a Skill and as a Hook
What you see in the screenshot is a real case I stumbled onto from a session yesterday so I took a quick picture of it
I also recommend looking into npq from me: github.com/lirantal/npq -
Snyk
@snyksec
node-ipc npm package supply chain compromise (2026)
make sure you test your projects with Snyk 👇
Snyk
@snyksec
Read the node-ipc malware incident on the Snyk blog: snyk.io/blog/malicious-node-ipc-versions-published-npm/
-
Snyk reposted
Liran Tal
@liran_tal
and while we're at it and you're very security-minded in this convo, you want to read and go through my npm security best practices repo github.com/lirantal/npm-security-best-practices/
-
Snyk
@snyksec
Look at all the new Snyk Learn lessons for you to skill up on agentic coding with AI 🤖
BOOKMARK
Then go learn: learn.snyk.io -
Snyk
@snyksec
Join Snyk, Qodo, and Google Cloud for a Boston Tech Week meet-up focused on how engineering teams are shipping AI-driven code at speed without sacrificing quality or security.
Save your spot 👉 partiful.com/e/7HNzSAdGbny8MAt4qTrV -
Snyk
@snyksec
Security, compliance, and counsel tend to go hand-in-hand 👾
Our Legal Director, Kate Helin, joined the Future of Data Security podcast to discuss governing agentic AI before the regulatory guidance catches up.
Listen to the full conversation here: www.youtube.com/watch?v=kb5olHTjQJ0 -
Snyk reposted
Brian Vermeer
@BrianVerm
Earlier this month at @jcon_conference , I discussed Agentic security with Baruch Sadogursky from #tessl. It is a crucial yet often overlooked topic among developers.
@snyksec #tessl #agentic #security
www.youtube.com/watch?v=xCrewp8TOko -
Snyk reposted
Manoj Nair
@mnair1
“Detection was never the bottleneck.” — @JasonDClinton, @AnthropicAI. He is absolutely right. Closing the loop is. That is what we built today: @AnthropicAI Claude embedded in the @snyksec AI Security Platform with Evo. Sharper discovery. Faster remediation. The workflow developers and agents already use.
snyk.io/news/snyk-embeds-anthropics-claude-to-advance-ai-… -
Snyk reposted
Brian Clark
@_clarkio
More and more companies are deploying AI-generated code into production. Much of that code contains vulnerabilities. Making traditional AppSec struggle to keep up.
@snyksec + @AnthropicAI's Claude = security at AI speed
👇
snyk.io/news/snyk-embeds-anthropics-claude-to-advance-ai-… -
Snyk reposted
Liran Tal
@liran_tal
Worried about AI agents going rogue? 🤖😱
Come for my talk on AI Agent Skills and Agent Supply Chain Malware at Tessl's AI Native Dev Spring edition
- 💰 want 30% off tickets? use promo code LIRAN30
- 🇬🇧 London, June 1st, RSVP: tessl.io/devcon/
Who's around to geek out? -
Snyk
@snyksec
Worried about AI agents going rogue?
We invite you to hear @liran_tal talk on AI Agent Skills and Agent Supply Chain Malware at Tessl's @ainativedev Spring edition
- 💰 want 30% off tickets? use promo code LIRAN30
- 🇬🇧 London, June 1st
Register: tessl.io/devcon/ -
Snyk
@snyksec
What even is Shadow AI? Watch below to find out 🤖
-
Snyk reposted
Liran Tal
@liran_tal
practical mitigation[1] steps[2] against the tanstack compromise and other supply chain attacks on npm
[1] reduces vulnerable surface
[2] apply to your pnpm config too
* see more security best practices on the repo -
Snyk reposted
Liran Tal
@liran_tal
here we go again
-
Snyk reposted
AI Security Engineers
@aiseceng
Comments, anyone?
www.reddit.com/r/AISecEng/ -
Snyk
@snyksec
BREAKING: TanStack npm supply chain compromise (Shai-Hulud campaign):
- @tanstack npm packages (namespaced official org), reverted by now
- More than 170 npm packages compromised
More breakdown and updates on the TeamPCP campaign follows 👇Post not available here, view on X
Snyk
@snyksec
You can use this page to identify affected package versions and review recommended remediation actions: security.snyk.io/TanStack-npm-Supply-Chain-Compromise-May…
Snyk
@snyksec
For additional background and technical details, please refer to the Snyk Blog post on the topic: TanStack Npm Packages Compromised Inside The Mini Shai Hulud Supply Chain Attack - snyk.io/blog/tanstack-npm-packages-compromised/
-
Snyk
@snyksec
Snyk and Claude Code are better together.
That’s why we’re embedding @Anthropic’s models into the @Snyk AI Security Platform!
See what it looks like in action below ⬇️
Check out the press release here: snyk.io/news/snyk-embeds-anthropics-claude-to-advance-ai-… -
Snyk
@snyksec
We’re on the up-and-up in Lisbon 🇵🇹 and there’s never been a better time to join the team at @Snyk.
View our open roles here: snyk.io/careers/all-jobs/?location=Portugal -
Snyk
@snyksec
If you don't get the reference on line 12 are you even in cybersecurity?
-
Snyk
@snyksec
Snyk and Anthropic are making agentic development more secure! Today, we're embedding Claude models into our AI Security Platform.
By combining Claude’s reasoning with Snyk’s security DNA, we’re finding AND fixing vulnerabilities at AI speed.
Read more: snyk.io/news/snyk-embeds-anthropics-claude-to-advance-ai-… -
Snyk
@snyksec
you ready for @AISecSummit in London next Thursday? 🤩
Join us to learn how agentic security looks like from the eyes of CISOs, AppSec and builders of next-gen security tools
Grab your ticket here: aisecuritysummit.com/events/london-2026 -
Snyk
@snyksec
Did you already get your ticket to the London @AISecSummit next week? 🚀
Go check the agenda and CFP speaker line-up: aisecuritysummit.com/events/london-2026 -
Snyk reposted
Simon Roses
@simonroses
Extra, extra: on May 14 I will be speaking on AI Security and release my agentic security scanner, VASO, at The AI Security Summit, London aisecuritysummit.com/events/london-2026 Come and say hi 😊
-
Snyk reposted
AI Security Summit
@AISecSummit
Join Guy Podjarny, Founder & CEO of Tessl, at The AI Security Summit London for his talk, "Don’t Secure the Code, Secure the Coder: Can Security Keep Up With Agentic Dev?"
Secure your spot this session and connect with other industry leaders here: aisecuritysummit.com/events/london-2026 -
Snyk
@snyksec
Shout out to @FastCompany for featuring out Agent Skills malware research in the OpenClaw ecosystem: www.fastcompany.com/91536554/the-biggest-ai-shift-is-taki…
Read up to learn about #toxicskills and our analysis that found prompt-injection techniques in 36% of scanned skills among many other findings! -
Snyk
@snyksec
A #toxicskills feature on @VentureBeat calling out our research for malicious and insecure Agent Skills venturebeat.com/security/one-command-open-source-repo-ai-…
-
Snyk
@snyksec
World-class security 🤝 world-class soccer ⚽️
The global stage is set. As the world’s elite compete for glory on the pitch, Snyk is taking the field for a 9-city tour across North America.
The roster is filling up fast. Join the match at a city near you:
wc.snyk.io -
Snyk
@snyksec
Did you know Agent Scan is an open source CLI? github.com/snyk/agent-scan
Go give it a star on GitHub
Then, go audit your skills:
$ uvx snyk-agent-scan@latest --skills -
Snyk
@snyksec
Both amazing. Just different vibes.
-
Snyk
@snyksec
We've got some exciting engineering roles open in the UK 🇬🇧
Join the ride, check our open roles here: snyk.io/careers/all-jobs/?department=Engineering&location… -
Snyk
@snyksec
AI is shipping code at machine speed, but is your governance still running on quarterly audits? 📈
Our latest whitepaper explores how to shift to continuous governance that meets DORA, PCI DSS, and the EU AI Act requirements.
Download here: snyk.io/lp/operating-at-ai-velocity-finserv-whitepaper/ -
Snyk
@snyksec
🚨 BREAKING: TanStack impersonating malware on npm
We detected a package that impersonates TanStack in a typosquatting campaign: security.snyk.io/vuln/SNYK-JS-TANSTACK-16322745
Snyk
@snyksec
a malicious version (versions =2.0.4=2.0.5=2.0.6=2.0.7) was introduced after a delay, likely as part of a typosquatting/brandjacking campaign.
follow the usual guidelines and security best practices:
- snyk.io/articles/npm-security-best-practices-shai-hulud-a…
- snyk.io/blog/npm-security-preventing-supply-chain-attacks/ -
Snyk
@snyksec
It's now as simple as typing "/snyk-fix" with a Jira ticket as context into your coding assistant of choice to trigger integrated remediation workflows ✅
We’re thrilled to partner with Atlassian to bridge the gap between Jira and your ADE.
Read here: snyk.io/blog/atlassian-integration-intelligent-remediatio… -
Snyk
@snyksec
Randall Degges, VP of AI Engineering & DevRel, built our new lead gen system in three days. He estimates it'll save 1,300 hrs/yr.
Being an AI Security company requires more than selling the vision. It means building with the tools ourselves.
Read here: www.itbrew.com/stories/2026/04/24/why-snyk-chose-to-build… -
Snyk
@snyksec
🚨 elementary-data package compromise
How a Single Malicious PR Comment Led to a Compromised PyPI Package with 1M Monthly Downloads: snyk.io/blog/malicious-release-of-elementary-data-pypi-pa… -
Snyk
@snyksec
Snyk Agent Fix handles the heavy lifting directly in VS Code by providing deep context on data flows and offering three AI-generated fixes.
Each suggestion is automatically tested to ensure it resolves the risk without introducing new security flaws. Watch it in action below ⬇️ -
Snyk
@snyksec
Oh you know OAuth good? just because a state exists and has some checks doesn't mean CSRF is impossible:
labs.snyk.io/resources/OAuth-mistake-takeover-part-two/
The deep-dive security research from David Bors reviews issues from fastapi-users to other projects, showcasing how hard it is to get auth right -
Snyk
@snyksec
From blog post to agent instructions in a heartbeat ✨
Check out what our web engineering team thanks to Jonathan Pekkarinen and Rodrigo Santos has cooked up for ya - -
Snyk
@snyksec
We are live on @ProductHunt with Skill Inspector app ✨
Your mission if you choose to accept it:
1. Go to
www.producthunt.com/products/snyk?launch=skill-inspector
2. Login
3. Upvote
Good luck, agent -
Snyk
@snyksec
Join the April edition of The AI Radar 📡
As AI reshapes the software development lifecycle, we’re diving deep into the frameworks and strategies necessary to secure the next generation of AI-native applications.
Register here: snyk.io/resource-library/ -
Snyk
@snyksec
AppSec vs. AI Security. It’s not either/or ⛔️
Traditional AppSec secures deterministic patterns, like hardcoded secrets, while AI Security secures non-deterministic logic and intent.
Watch below to see why you need both protect the modern dev pipeline. -
Snyk reposted
Liran Tal
@liran_tal
Did anyone look into OWASP MCP Top 10 owasp.org/www-project-mcp-top-10/ ?
That's a project compiled by @InfosecVandana from @snyksec -
Snyk reposted
Franco Robles 🇪🇸
@francorobles
Demoed @snyksec yesterday to the team. They were delighted. Every team should ship secure code, packages, containers, and IaC templates.
-
Snyk
@snyksec
So many of the newest security tools are great at finding problems. But they’re not so great at fixing them 👀
Snyk identifies, suggests fixes, and provides a breakability score so you don't have to wonder if a fix will break your app.
Watch below to see it in action ⬇️ -
Snyk
@snyksec
If your AI agents can find vulnerabilities but can’t guarantee a fix, you haven’t improved your security.
Randall Degges argues that in the age of Claude Mythos, "Security is defined by what you can control, not just by what you can find."
Read here: snyk.io/blog/from-discovery-to-control/ -
Snyk reposted
Rodrigo Santos
@rrcssantos
-
Snyk reposted
Pure AI
@PureAINews
Hidden models and shadow AI are making agentic security harder to ignore.
Join us, sponsor @snyksec, and a panel of experts tomorrow for this FREE webcast on agentic AI security, discovery and benchmarking risk.
Register now: pureai.com/webcasts/2026/04/snyk-the-agentic-security-lan…
#aisecurity #agenticai -
Snyk reposted
Liran Tal
@liran_tal
Snyk for free 👇
Snyk
@snyksec
Are you an open source maintainer? 👋💜
If so, we’d love to support your project by providing you with complimentary access to our industry-leading developer security tooling and infrastructure! snyk.io/open-source/
Check out Snyk's Free Security for Open Source program -
Snyk reposted
Liran Tal
@liran_tal
back in February when OpenClaw was getting exponential by the hour, I deep-dived into agent skills security research w / the AI security team at @snyksec
now I'm gonna share with you these learnings and findings at Tessl's AI Native DevCon in London on June 1-2
who's coming?? -
Snyk
@snyksec
AI is accelerating development. It's also increasing risk 🫣
Most teams are outrunning their own security, leaving doors wide open for breaches. Secure at inception means you don’t have to choose between moving fast and staying safe.
Download the eBook: snyk.co/umvNj -
Snyk
@snyksec
For Gabriel Brolo, Evo AI-SPM was an integral part of defining what AI security looks like at Yalo.
That's because Evo AI-SPM provides the visibility, governance, and risk intelligence needed to secure the agentic era.
Watch below to hear what he had to say👇 -
Snyk
@snyksec
Are you an open source maintainer? 👋💜
If so, we’d love to support your project by providing you with complimentary access to our industry-leading developer security tooling and infrastructure! snyk.io/open-source/
Check out Snyk's Free Security for Open Source program -
Snyk
@snyksec
Snyk's #toxicskills research found that 36.8% of the 3,984 ClawHub skills scanned contain security flaws at any severity level, with 13.4% rated critical. Average breakout time has dropped to 29 minutes: venturebeat.com/security/ai-agent-zero-trust-architecture…
Use those agents, securely 😉💜 -
Snyk
@snyksec
Did you already subscribe to the @aiseceng newsletter for AI Security news? newsletter.aiseceng.io
a bunch of great stories landed in this issue ICYMI 🧵👇Post not available here, view on X
Snyk
@snyksec
Congrats to @arcjet for hitting this great milestone of 35k weekly npm downloads
Arcjet's @arcjet/next package bundles prompt injection detection and PII blocking alongside traditional WAF, bot protection, and rate limiting, all as middleware for Next.js and Node.js apps
Snyk
@snyksec
Go check the archive for the full stories and subscribe 📌
-
Snyk
@snyksec
You like AIBOMs? Liran Tal launched an AIBOM visualizer and CLI at TinyLaunch, go check it out: www.tinylaunch.com/launch/11723
-
Snyk
@snyksec
Oh no, did GPT 5.4 just choose a package to install that did not score well on the Snyk Security DB? 😱
Here's the deep-dive using OpenAI latest model from Brian Clark: www.youtube.com/watch?v=OqE8DXlo6W8 -
Snyk reposted
Liran Tal
@liran_tal
your daily reminder for npm security best practices
-
Snyk reposted
Alex Ley
@AlexEvade
There will be many opportunities to gain the AI Security Engineer Foundations credential at Snyk events and global conferences🎓💻🤖
Snyk
@snyksec
Congratulations on being one of the first people in the world to gain this credential for AI Security Engineer Pratul K.
Keep learning about AI on Snyk Learn learn.snyk.io/catalog/?type=security-education&categories… ✨ -
Snyk
@snyksec
Can GPT 5.4 figure out SQLite a secure dependency...? Here's @_clarkio giving this a try: www.youtube.com/shorts/uYh5teFu_9A
-
Snyk
@snyksec
Congratulations on being one of the first people in the world to gain this credential for AI Security Engineer Pratul K.
Keep learning about AI on Snyk Learn learn.snyk.io/catalog/?type=security-education&categories… ✨ -
Snyk
@snyksec
Relationships come first 🥇
Al from ThoughtSpot has carried Snyk with him through the majority of his career. Watch below to see why he sticks with the "people behind the machine." -
Snyk
@snyksec
Security
Securit
Securi
Secur
Secu
Sec
Se
S
Sw
Swa
Swag
Swagg
Swagge
Swagger -
Snyk
@snyksec
Evo AI-SPM discovers your shadow AI, but Evo Agent Red Teaming is the stress test that proves if your agents will actually fold under pressure.
Check out Agnieszka Koc’s deep dive here: snyk.io/blog/defense-ai-red-teaming/ -
Snyk
@snyksec
AI is driving the use of more containers. Today, we're launching upgrades to help security keep pace 🏃💨
Read more here: snyk.io/blog/scale-container-security-effortlessly/ -
Snyk
@snyksec
A lot has been going on over the last week with security vulnerabilities (axios, litellm, etc)
Likely there's a also a lot you missed
Catch up on security updates and CVEs using the Snyk Security DB: security.snyk.io -
Snyk reposted
Liran Tal
@liran_tal
I know developers only pay attention to security when incidents happen but here's your chance to take some agency and proactively learn, tighten and adopt tools and techniques to avoid becoming the next victim of supply chain trauma
-
Snyk reposted
AI Security Engineers
@aiseceng
Shipping AI? Don’t skip security.
Get practical tips in our AI Security newsletter.
Subscribe → newsletter.aiseceng.io -
Snyk
@snyksec
How deep does the LiteLLM malicious package goes 👀? snyk.io/blog/litellm-ai-blast-radius/
Rudy Lai breaks down the story beyond malware and beyond SCA and dependency management, clearing the path to shadow AI -
Snyk
@snyksec
Hardened, ultra-minimalist images are a massive leap forward for container security, but they’ve historically created a visibility gap.
Our partnership with @Canonical bridges that gap to provide visibility into Chiseled Ubuntu runtimes.
Read more here: canonical.com/blog/canonical-partners-with-snyk-for-scann… -
Snyk
@snyksec
After nearly a decade of second guesses and mispronunciations, we’re cutting the friction. Snyk is now Snik 💜
From the code to the logo, we believe in clarity.
New look. Same mission. Finally pronounced exactly how it’s written. -
Snyk reposted
Liran Tal
@liran_tal
BREAKING: axios
Maintainer or developer, do yourself a favor and star this repo, send it to your entire dev team, and follow curated and battle-tested advice to avoid future security incidents and npm package compromise: github.com/lirantal/npm-security-best-practices
I CANNOT STRESS ENOUGH -
Snyk reposted
Liran Tal
@liran_tal
RE axios: Maybe you're affected, maybe you're not.
Anyways you should:
1. Learn about the issue: snyk.io/blog/axios-npm-package-compromised-supply-chain-a…
2. Learn how to defend against this and future npm security incidents and malware github.com/lirantal/npm-security-best-practices
3. Always use npq (your coding agent too) -
Snyk reposted
Qodo
@QodoAI
Excited to join the conversation on "Hidden Failure Modes of AI Agents" on April 8th in London! 🗓️
AI coding agents are shipping fast, but reliability, code quality, and security failures are still flying under the radar.
Catch our own Nupur Sharma on the panel alongside @sjmaple (@tessl_io), Brian Vermeer (@snyksec), and @kunalstwt (@cast_ai), breaking down what it really takes to make agents production-ready.
📍 Tessl HQ, Kings Cross, London
🕕 6:00–9:00 PM GMT
Register: luma.com/rkije5di
@ainativedev | @aiseceng -
Snyk
@snyksec
Discovery alone isn't enough; knowing an asset exists isn't the same as knowing it's safe ❌
The Evo AI-SPM Risk Intelligence Agent enriches every asset with deep metadata, flagging everything from hallucinations to licensing compliance.
Learn more here: evo.ai.snyk.io/aispm/ -
Snyk reposted
Liran Tal
@liran_tal
🚨 Among the packages that rely on axios:
- auth0
- alchemy-sdk
- @tavily/core
- @slack/web-api
- aws-crt
- contentful-management
- @coinbase/cdp-sdk
- postmark
- @sap-cloud-sdk/core
- fastmcp
- mcp-proxy
- swagger-client
- wagmi
- gatsby
- wait-on
- posthog-node -
Snyk
@snyksec
transitive deps
cut
deep
🩸. .
🩸
🩸 -
Snyk
@snyksec
Manoj knows this stuff, all CISOs comes here👇
Manoj Nair
@mnair1
npm axios, 300 million downloads a week, was targeted by a sophisticated supply chain attack! Your package manager is now an attack surface.
The axios compromise should end any remaining illusion that “trusted package” means safe.
This was not typo-squatting.
Not a fake clone.
Not some dusty transitive dependency nobody noticed.
This was the real package.
On the real distribution path.
From a compromised maintainer account (jasonsaayman’s npm creds got owned).
Two malicious versions dropped (axios@1.14.1 and axios@0.30.4).
They quietly pulled in a brand-new package (plain-crypto-js@4.2.1) that ran an obfuscated postinstall and dropped a cross-platform RAT. Windows, macOS, Linux — all covered. Self-cleaning malware. Classic.
A few hours was enough.
One poisoned release.
One CI run.
One developer laptop.
One production build.
Game over.
**Full technical breakdown + IOCs from our @liran_tal and @snyksec research team here** → snyk.io/blog/axios-npm-package-compromised-supply-chain-a…
(SNYK-JS-AXIOS-15850650 + SNYK-JS-PLAINCRYPTOJS-15850652)
Feross (@feross) nailed it in his thread this morning: “textbook supply chain installer malware.”
Karpathy (@karpathy) posted his own near-miss (googleworkspace/cli resolved clean for him… this time) and dropped the bigger truth: the defaults of npm, pip, etc. have to change so one temporary maintainer compromise doesn’t pwn the planet at random scale.
**What practitioners (and leaders) should actually do right now:**
• Pin exact versions. No ^. No latest.
• Enforce lockfiles in CI and never run plain `npm install`.
• Use `npm ci --ignore-scripts` (or Bun’s default behavior).
• Scan for malicious behavior, not just known CVEs.
• If you installed in the window — assume breach and rotate everything.
The real shift here is bigger than Axios.
Software now moves at machine speed.
So does trust propagation.
So does blast radius.
If your environment still allows loose semver, non-deterministic installs, and postinstall scripts by default… you are not moving fast.
You are scaling risk.
What is the strongest control you have today against this class of supply chain attack?
#supplychainsecurity #npm #opensourcesecurity #devsecops #cybersecurity -
Snyk
@snyksec
🚨 ACTIVE SUPPLY CHAIN ATTACK
Two malicious versions of `axios`, the npm package with 300M+ weekly downloads, were just published via a hijacked maintainer account and have deployed a cross-platform RAT to affected machines.
Affected: `axios@1.14.1` and `axios@0.30.4` 👇🧵Post not available here, view on X
Snyk
@snyksec
The dropper is double-obfuscated (reversed Base64 + XOR cipher with key `OrDeR_7077`), detects your OS, phones home to `sfrclak[.]com:8000`, and downloads a tailored second-stage payload.
Then it deletes itself. No postinstall hook, no setup.js - nothing left to find.
Snyk
@snyksec
Platform payloads:
🍎 macOS → binary dropped to `/Library/Caches/com.apple.act.mond` (fake Apple daemon)
🪟 Windows → PowerShell RAT disguised as `wt.exe` (Windows Terminal)
🐧 Linux → Python RAT at `/tmp/ld.py` running as an orphaned background processPost not available here, view on X
Snyk
@snyksec
If you installed either affected version: assume breach.
✅ Rotate ALL secrets
✅ Isolate and rebuild affected machines, don't try to clean them
✅ Check logs for outbound connections to 142.11.206.73:8000
✅ Review CI pipeline build logs for the March 31 UTC window
Snyk
@snyksec
This is the same playbook as the ESLint Prettier plugin attack, the ~qix phishing compromise, and Shai-Hulud - hijack a trusted maintainer account, publish a malicious version, let the ecosystem's trust do the rest.
Full axios breakdown on the Snyk blog: snyk.io/blog/axios-npm-package-compromised-supply-chain-a… -
Snyk
@snyksec
ICYMI, Snyk is making waves with the launch of Evo AI-SMP 🌊
AI-generated code is producing up to 10x more security vulnerabilities.
Now, we're providing you the guardrails needed to govern autonomous agents directly in the CI/CD pipeline.
Read here: www.forbes.com/sites/tonybradley/2026/03/24/snyk-launches… -
Snyk
@snyksec
Missed our AI Red Teaming demos at RSA ?
No sweat, here's a quick thread on the Snyk agent security with Evo👇Post not available here, view on X
Snyk
@snyksec
Why AI systems break traditional security testing?
AI applications behave differently. Large language models, RAG pipelines, and autonomous agents introduce systems that are drive by prompt rather than code.
Snyk
@snyksec
Try the Red Teaming CLI
Security testing for AI shouldn’t require specialized tools or weeks of setup. You can kick off your first Evo Agent Red Teaming configuration as follows
Let us know if you have any questions -
Snyk reposted
Manoj Nair
@mnair1
#iykyk
I loved seeing this on my walks around SF this past week!
#rsac2026 @snyksec
@liran_tal 🔥 -
Snyk
@snyksec
Nice write-up by the @Sourcegraph team on detecting supply chain security for the LiteLLM compromise with their deep search queries: sourcegraph.com/blog/detecting-supply-chain-attacks-at-sc…
thanks for the h/t on the Snyk research ✨ -
Snyk
@snyksec
It's time to say goodbye to tedious, time-consuming manual governance.
All it takes is a simple prompt for the Evo AI-SPM Discovery Agent to automatically map your "code-first" attack surface to generate a live AI-BOM.
Get the full story here: snyk.io/evo/aispm/ -
Snyk
@snyksec
Snyk's own Randall Degges chatted with Chloe Aiello from Inc. Magazine about the recent credential-stealing malware discovered in the popular open-source LiteLLM project 👾
Read the full article here: www.inc.com/chloe-aiello/malware-in-an-open-source-projec… -
Snyk
@snyksec
Earlier this week, we launched AI-SPM. But we didn’t expect a watershed moment to validate our approach quite this fast 👀
Read the full breakdown in TechCrunch: techcrunch.com/2026/03/25/delve-did-the-security-complian… -
Snyk
@snyksec
TL;DR on the #litellm compromise
but here's the full story by Snyk very own developer advocate @StephenThoemmes: snyk.io/articles/poisoned-security-scanner-backdooring-li… -
Snyk
@snyksec
💡 The security failures that lead to the LiteLLM compromise and malware propagation weren't new...
In fact, Snyk already in 2024 warned of GitHub Actions failures and provided tools to pin down dependencies and lock down your CI workflows: labs.snyk.io/resources/exploring-vulnerabilities-github-a… -
Snyk
@snyksec
We're happy to support @LowLevelTweets tech channel with security incident coverage for the LiteLLM malware www.youtube.com/watch?v=uwSjgv4otAk&t=94s
Go watch, good stuff -
Snyk reposted
Shmalkey
@shmalkey
AI written code got hacked by a supply chain attack.
Snyk
@snyksec
The LiteLLM dependency incident didn't "just happen" though. This is part of a larger campaign
LiteLLM already extends to supply chain security fallout for other projects: snyk.io/articles/poisoned-security-scanner-backdooring-li… -
Snyk reposted
banteg
@banteg
a better post mortem on litellm hack is out, it was compromised via a security scan github action called trivy, which was previously hacked in february
Snyk
@snyksec
The LiteLLM dependency incident didn't "just happen" though. This is part of a larger campaign
LiteLLM already extends to supply chain security fallout for other projects: snyk.io/articles/poisoned-security-scanner-backdooring-li… -
Snyk reposted
Liran Tal
@liran_tal
Hari I like that we're discussing so many coding agent security and supply chain security topics today :D
I'll drop here skills security research we did at @snyksec:
1. the toxicskills research snyk.io/blog/toxicskills-malicious-ai-agent-skills-clawhub/
2. threat modeling agent skills: snyk.io/articles/skill-md-shell-access/ -
Snyk reposted
Young
@Young_AGI
Constant vigilance is required
Snyk
@snyksec
The LiteLLM dependency incident didn't "just happen" though. This is part of a larger campaign
LiteLLM already extends to supply chain security fallout for other projects: snyk.io/articles/poisoned-security-scanner-backdooring-li… -
Snyk reposted
YL
@yilinnyl
To read to understand better about the LiteLLM attack
Snyk
@snyksec
The LiteLLM dependency incident didn't "just happen" though. This is part of a larger campaign
LiteLLM already extends to supply chain security fallout for other projects: snyk.io/articles/poisoned-security-scanner-backdooring-li… -
Snyk reposted
Liran Tal
@liran_tal
Thanks for covering, Hari. So, some thoughts from me here with practical tooling/advice as well
1. Don't directly rely and run `npm install` or `pip install` - I built npq (github.com/lirantal/npq) exactly for this reason - it's an install gatekeeper to prevent malware
>> -
Snyk reposted
Liran Tal
@liran_tal
So, about those terminal control characters... I'll just drop here the Trojan Source research and my audit tool for it: github.com/lirantal/anti-trojan-source/
Actually, @karpathy, we had an internal discussion at Snyk about how these special chars may affect LLMs. wdyt? -
Snyk reposted
Navin Kabra
@NGKabra
The AI powered hacks have started.
HackerBot-Claw was used to automatically compromise trivy (a security scanning library), which was used to compromise litellm (an AI library)
This has probably compromised about 50k other people/packages
Snyk
@snyksec
The LiteLLM dependency incident didn't "just happen" though. This is part of a larger campaign
LiteLLM already extends to supply chain security fallout for other projects: snyk.io/articles/poisoned-security-scanner-backdooring-li… -
Snyk reposted
Nilesh Trivedi
@nileshtrivedi
Postmortem of the litellm hack 👇
Snyk
@snyksec
The LiteLLM dependency incident didn't "just happen" though. This is part of a larger campaign
LiteLLM already extends to supply chain security fallout for other projects: snyk.io/articles/poisoned-security-scanner-backdooring-li… -
Snyk reposted
AI Native Dev
@ainativedev
We’re excited to welcome Liran Tal ( @liran_tal ) to DevCon a globally recognized voice in developer security, open source, and modern software practices.
Liran is a GitHub Star, security researcher, and Director of Developer Advocacy at Synk ( @snyksec ), where he leads efforts to empower developers with security-first thinking.
With deep roots in the JavaScript ecosystem, he has:
- Contributed extensively to Node.js security and the OpenJS Foundation ecosystem
- Led initiatives in open source supply chain security, including OWASP projects
- Authored industry-recognized books like Essential Node.js Security and Serverless Security
- Spoken at dozens of global conferences on topics spanning AI security, DevSecOps, and modern application risk
His work sits at the intersection of AI, security, and developer workflows helping teams understand how fast-moving innovation can introduce hidden risks, and how to stay ahead of them.
𝐖𝐡𝐚𝐭 𝐭𝐨 𝐄𝐱𝐩𝐞𝐜𝐭 𝐚𝐭 𝐃𝐞𝐯𝐂𝐨𝐧
Liran brings practical, real-world insights into:
- Securing AI-generated code and modern applications
- Identifying vulnerabilities early in developer workflows
- Building a security-first mindset without slowing innovation
Experience it live in London or connect virtually: tessl.io/devcon (use AIND-LI-BB-30 for 30% discount) -
Snyk
@snyksec
You're not going to want to miss these partner presentations! Swing by our #rsac booth, S-1227, to hear form Tessl, arcade.dev, Akamai Technologies, and Snowflake.
See you there ✅ -
Andrej Karpathy
@karpathy
Software horror: litellm PyPI supply chain attack.
Simple `pip install litellm` was enough to exfiltrate SSH keys, AWS/GCP/Azure creds, Kubernetes configs, git credentials, env vars (all your API keys), shell history, crypto wallets, SSL private keys, CI/CD secrets, database passwords.
LiteLLM itself has 97 million downloads per month which is already terrible, but much worse, the contagion spreads to any project that depends on litellm. For example, if you did `pip install dspy` (which depended on litellm>=1.64.0), you'd also be pwnd. Same for any other large project that depended on litellm.
Afaict the poisoned version was up for only less than ~1 hour. The attack had a bug which led to its discovery - Callum McMahon was using an MCP plugin inside Cursor that pulled in litellm as a transitive dependency. When litellm 1.82.8 installed, their machine ran out of RAM and crashed. So if the attacker didn't vibe code this attack it could have been undetected for many days or weeks.
Supply chain attacks like this are basically the scariest thing imaginable in modern software. Every time you install any depedency you could be pulling in a poisoned package anywhere deep inside its entire depedency tree. This is especially risky with large projects that might have lots and lots of dependencies. The credentials that do get stolen in each attack can then be used to take over more accounts and compromise more packages.
Classical software engineering would have you believe that dependencies are good (we're building pyramids from bricks), but imo this has to be re-evaluated, and it's why I've been so growingly averse to them, preferring to use LLMs to "yoink" functionality when it's simple enough and possible.
Daniel Hnyk
@hnykda
LiteLLM HAS BEEN COMPROMISED, DO NOT UPDATE. We just discovered that LiteLLM pypi release 1.82.8. It has been compromised, it contains litellm_init.pth with base64 encoded instructions to send all the credentials it can find to remote server + self-replicate. link below
Snyk
@snyksec
The LiteLLM dependency incident didn't "just happen" though. This is part of a larger campaign
LiteLLM already extends to supply chain security fallout for other projects: snyk.io/articles/poisoned-security-scanner-backdooring-li… -
Snyk
@snyksec
🚨 BREAKING: LiteLLM versions versions [1.82.7][1.82.8] have been compromised and contain malicious code security.snyk.io/vuln/SNYK-PYTHON-LITELLM-15762713
We'll keep you informed on further updates, keep your eyes open 👀 -
Snyk reposted
Canonical
@Canonical
With @snyksec and chiseled Ubuntu images, developers now have the ultimate toolset for production-ready security. Snyk’s native support for scanning chiseled Ubuntu images means greater precision and a faster CI/CD.
Learn more:
ubuntu.com/blog/canonical-partners-with-snyk-for-scanning…
#opensource #canonical #snyk -
Snyk
@snyksec
did you know Snyk is free for open source projects? ✨
h/t to @alaymanguy for building OSS Perks -
Snyk reposted
Liran Tal
@liran_tal
have been playing around with a @snyksec security statusline for claude code, wdyt? 😉
2nd screenshot shows statusline in a project shows when security findings are detected for packages and insecure code -
Snyk reposted
Tessl
@tessl_io
Most developers install skills without reading what's inside them. But that's exactly what attackers are counting on.
@sjmaple sits down with @BrianVerm from @snyksec to discuss:
- Why prompting your agent to write secure code doesn't make it secure
- How a trusted skill can update silently and start offloading your credentials
- What prompt injection actually looks like inside a skill file
- Why vibe coding makes the attack surface bigger, not smaller
- How the Snyk agent scan catches what you'd never spot manually
Listen to the podcast: tessl.io/podcast/97This media couldn't be displayed. See it on the original post. -
Snyk
@snyksec
your rsa revelation in 3 words: ______ ______ ______
-
Snyk
@snyksec
Today, we’re excited to announce Snyk Agent Security and the general availability of Snyk Evo AI-SPM. 🚀
You cannot slow down AI coding agents, but you cannot let them bypass your security stack either. It’s a shadow AI crisis. 👾
See the fix here : evo.ai.snyk.ioThis media couldn't be displayed. See it on the original post. -
Snyk reposted
matrix
@_tiwariabhigyan
Use @snyksec
-
Snyk
@snyksec
BREAKING: Trivy GitHub Actions Supply Chain Compromise 🚨
This was the second compromise of Trivy infrastructure in under three weeks, with the attacker leveraging credentials obtained during the first incident: snyk.io/articles/trivy-github-actions-supply-chain-compro… -
Snyk reposted
Insecure Agents Podcast
@insecureagents
We’ll be podcasting out of @snyksec’s sandbox space close to Moscone on Wednesday at RSAC!
Who should we talk to? Whose launch should we cover? 👀
DM us :) -
Snyk reposted
Canonical
@Canonical
@Canonical and @snyksec are pleased to announce a partnership aimed at strengthening production-ready container security. Snyk Container, Snyk’s container security solution, now offers native support for scanning chiseled Ubuntu containers.
Learn more:
ubuntu.com/blog/canonical-partners-with-snyk-for-scanning…
#opensource #canonical #snyk -
Snyk reposted
AI Native Dev
@ainativedev
Has your agent been hacked before?
You might not even know.
Hackers have gotten smarter. @BrianVerm from @snyksec explains how a skill can work perfectly, earn your trust, and then after one silent update quietly start offloading your credentials or installing a binary.
Brian breaks down exactly how these attackers operate and what you can do about it.This media couldn't be displayed. See it on the original post. -
Snyk
@snyksec
Data provenance, bias assessment, and regulatory compliance all fall apart when you're dealing with "ghost models."
Watch the scientific breakdown of what our 2026 State of Agentic AI Adoption found below ⬇️ -
Snyk
@snyksec
The agentic era demands a new security standard. We've curated a foundations program to arm engineers with the specific skills that actually differentiate, and it's debuting at #rsac 2026 💥
Get the details here: go.snyk.io/ai-security-engineering-courses_reg.html -
Snyk reposted
AI Native Dev
@ainativedev
Most developers install skills without reading what's inside them. But that's exactly what attackers are counting on.
@sjmaple sits down with Brian Vermeer (@BrianVerm) from Snyk (@snyksec) at DevNexus to get into the security risk hiding inside the skills and MCPs running on your local machine. They scanned over 4,000 skills and found that 1 in 7 had at least one critical security vulnerability.
Here’s what you need to know:
• Why prompting your agent to write secure code doesn't make it secure
• How a trusted skill can update silently and start offloading your credentials
• What prompt injection actually looks like inside a skill file
• Why vibe coding makes the attack surface bigger, not smaller
• How the Snyk agent scan catches what you'd never spot manually
Every skill on the Tessl registry now has a Snyk security scan attached. Check before you install.
(0:00) Trailer
(1:17) AI DevCon
(2:11) Introduction
(3:32) Snyk's evolution from SCA to AI security
(5:06) Can agents generate secure code?
(6:01) Skills and secure coding guidance
(7:24) Snyk agent scan and Tessl integration
(7:56) MCP as the next supply chain problem
(9:04) ToxicSkills threat taxonomy
(10:27) How malicious skills exploit privileges
(12:39) MCP server attack surface
(13:51) The speed of AI adoption vs security
(15:51) Scan results and critical vulnerabilities
(17:06) False positives in natural language
(18:26) How attackers create malicious skills
(20:41) Trust and open source skill risks
(21:29) Using Snyk agent scan directly
(24:58) Snyk scans in the Tessl registry
(26:41) Advice for skill creators
(28:16) Protecting yourself as a skill user
(29:44) Snyk Evo Agent Guard for Cursor
(33:21) Runtime guardrails and policies
(34:10) Wrap-up and where to learn moreThis media couldn't be displayed. See it on the original post. -
Snyk
@snyksec
Our San Francisco Innovation Hub is officially open for business 🍾
Read how the space will be clubhouse for AI Engineers in the Bay Area here: snyk.io/blog/snyk-san-francisco-innovation-hub/ -
Snyk reposted
AI Security Engineers
@aiseceng
Meet, learn, and connect with AI Security builders IRL. Our event calendar has all upcoming local meetups. Register 👉 luma.com/aiseceng
-
Snyk
@snyksec
Cheers @VentureBeat for your write-up on OpenClaw and AI agent security through everyday workflows
We appreciate the reference to Snyk #toxicskills research (36% of ClawHub skills container security flaws among other issues found): venturebeat.com/security/openclaw-can-bypass-your-edr-dlp… -
Snyk
@snyksec
Shout out to @agentseal_org for compiling a report on MCP Security here: agentseal.org/blog/mcp-server-security-findings
We appreciate the shout out to our own Snyk #toxicskills research for agent security.
Good luck friends and cheers for hacking together 💜💪 -
Snyk reposted
Liran Tal
@liran_tal
More agent security powered by Snyk 🎉
If you're using skills and MCPs or generating code with AI agents and not using Snyk you're at real risk
Snyk
@snyksec
We're excited to announce that Snyk and Tessl have partnered to bring security scanning to every skill in the Tessl Registry⚡️
Get the full story here: snyk.io/blog/snyk-tessl-partnership/ -
Snyk
@snyksec
MCP Servers on @intellijidea ?
We got ya
Well, @BrianVerm the splendid Java Champion engineer got ya: www.youtube.com/watch?v=lqLhq7F41jk -
Snyk
@snyksec
We're excited to announce that Snyk and Tessl have partnered to bring security scanning to every skill in the Tessl Registry⚡️
Get the full story here: snyk.io/blog/snyk-tessl-partnership/ -
Snyk reposted
Amanda
@hey_amandam
London devrel! Go work with Liran!
Liran Tal
@liran_tal
I'm hiring for DevRel role in London (🇬🇧) on the Snyk team so please out and DM if you're located there and want to make agent security popular for developers
-
Snyk reposted
Liran Tal
@liran_tal
AIBOM Toolkit is open sourced 🎉
Visualize your AI supply chain as an interactive map from @snyksec www.producthunt.com/products/snyk by @liran_tal -
Snyk
@snyksec
#rsac 2026 is one week away 💥
This year, we’re leveling it up with an interactive soccer experience at booth S-1227, AI conversations with Team USA soccer legends, and a rooftop vibe coding party.
Check it out here: snyk.io/events/rsac/ -
Snyk
@snyksec
According to our latest research, 41.7% of AI power users are now orchestrating a stack of 5+ models. It’s efficient, it’s fast, and, without the right guardrails, it’s a massive security risk.
See what that looks like with a little science 👇This media couldn't be displayed. See it on the original post. -
Snyk
@snyksec
For years, developers have followed the paved roads of popular, trusted open source. But LLMs don't care about popularity or trust.
The game has officially shifted from scanning for bad code to actively ensuring good health.
Read the full story here: snyk.io/blog/llms-resurrecting-open-source-dormant-majority/ -
Snyk
@snyksec
Skills are the instruction manuals that tell your AI agent’s "brain" how to use its "hands."
But what happens when those instructions are hijacked? Malicious skills are quietly injecting vulnerabilities throughout your tech stack.
Watch the full breakdown here👇This media couldn't be displayed. See it on the original post. -
Snyk
@snyksec
Snyk is officially live on @Cursor Marketplace!
By combining Cursor’s speed with Snyk’s security guardrails, we’re enabling developers to ship faster than ever without the security debt hangover.
Check it out ➡️ cursor.com/marketplace/snyk
Snyk
@snyksec
This update includes Package Dependency Health which we brought over from Snyk Advisor and is now integrated as a first-class citizen into AI workflows
No more unmaintained libraries
No more malicious libraries
No more outdated libraries
Give your coding agent a security 🧠 -
Snyk
@snyksec
There’s no better way to kick off RSAC than by celebrating the lunch of Snyk's SF Innovation Hub 💥
When: Monday 03/23, 3-6 PM PST
Where: 260 California St, San Francisco, CA
Register here: www.linkedin.com/events/7434640467864047617?viewAsMember=… -
Snyk
@snyksec
SF is where AI happens. Snyk is how AI stays secure.
Our newest innovation hub, coming soon 🌁 -
Snyk reposted
Tessl
@tessl_io
We’re excited to announce the first 10 𝐬𝐩𝐞𝐚𝐤𝐞𝐫𝐬 𝐟𝐨𝐫 𝐀𝐈 𝐍𝐚𝐭𝐢𝐯𝐞 𝐃𝐞𝐯𝐂𝐨𝐧 2026, happening in London and virtually on June 1–2.
AI Native DevCon is focused on developers building real AI-native systems at production scale, with tracks including context engineering, agent orchestration, agent enablement platforms, and organizational enablement.
Joining the lineup so far:
- Birgitta Boeckeler ( @birgitta410 ) - Distinguished Engineer, Thoughtworks @thoughtworks
- Dana Lawson ( @danalaw ) - CTO, @Netlify
- Guy Podjarny ( @guypod ) - Founder, @tessl_io
- Joseph Katsioloudes ( @jkcso ) - Leading Cyber Security Specialist, GitHub Security Lab
- Liran Tal ( @liran_tal ) - Director of DevRel, @snyksec
- Louis Knight-Webb ( @tokengobbler ) - Co-founder, Vibe Kanban
- Dru Knox ( @drufball ) - Head of Product, @tessl_io
- Oleg Šelajev ( @shelajev ) - DevRel, @Docker Inc
- Shachar Azriel - VP Product, Baz
- Tracy Bannon ( @TracyBannon ) - Sr Principal - Software Architect, MITRE
If you’re building with agents, specs, workflows, and platforms for production-scale software delivery, this is the conference for you.
As a thank you for following this account, you can leverage the AIND-X-BB-30 code to get 30% off - get your tickets here: tessl.io/devcon/
#ainativedevcon #aidevcon -
Snyk reposted
Liran Tal
@liran_tal
kinda cool seeing @snyksec powering AI agents ecosystem by flagging security issues in skill .md files :-)
-
Snyk
@snyksec
Where should we open the next Snyk hub? 👀
-
Snyk
@snyksec
Most used AI tools from our friends at The Pragmatic Engineer
Q1: Which coding agent do you use?
Q2: What do you do to secure the code and the agent? -
Snyk reposted
Liran Tal
@liran_tal
It's a time old security misconfiguration of GitHub Actions, we wrote extensively about it on the @snyksec security labs: labs.snyk.io/resources/exploring-vulnerabilities-github-a…
-
Snyk
@snyksec
We're proud to advance AI Security 💪🤖
AISecHub
@AISecHub
Bootstrapping Code Security Benchmarking - arxiv.org/pdf/2512.21132v1
We present AutoBaxBuilder, an automated framework that generates code security benchmark tasks from scratch, reducing manual effort by ~12× while matching or outperforming expert tests and exploits.
> AutoBaxBuilder generates complete benchmark tasks (scenarios, tests, exploits) in under 2 hours for less than USD 10, representing a ~12× reduction in effort compared to manual creation.
> Generated tests and exploits successfully match or outperform expert-written ones on BaxBench scenarios, tightening the upper security bound.
> The framework addresses benchmark contamination and enables continuous expansion with varying difficulty levels to challenge increasingly capable LLMs.
More Info: github.com/eth-sri/autobaxbuilder | baxbench.com/autobaxbuilder/ |
Authors: Tobias von Arx, @nielstron, @mark_veroe, @baader_max, @mvechev - @ETH_en, @snyksec, @INSAITinstitute, @universitysofia
#aisecurity #appsec #llm #codesecurity #securecoding #codegeneration #benchmarks #evaluation #softwareengineering #devsecops #mlsecurity #arxiv #autobaxbuilder -
Snyk
@snyksec
AI is quietly expanding its footprint within your stack. Snyk’s AI BOM report surfaced some startling metrics about the state of AI adoption, sprawl, and security 👀
We decided the best way to visualize the data was with a little science 🧪 -
Snyk
@snyksec
Innovators fuel innovators 🚀
We’re proud to announce our 2026 Partner Award winners, the strategic force multipliers helping global enterprises secure the shift to autonomous development. -
Snyk
@snyksec
When did you last visit the Snyk Security DB?
👉 rolled out new designs for package health: security.snyk.io -
Snyk
@snyksec
How do you protect coding agents from hallucinating packages? 👇
In the screenshot you can see how Snyk Studio is invoked by the Windusrf coding agent to perform package health analysis via the snyk_package_health_check tool which is part the Snyk MCP Server
Want to see more? -
Snyk
@snyksec
The 89% Problem: How LLMs Are Resurrecting the "Dormant Majority" of Open Source
How do you equip your AI coding agent with the ability to choose health open source packages....? 🤔👇
Snyk
@snyksec
Here's our write-up on Snyk Studio and equipping coding agents with our Snyk MCP server that provides package health context for agents: snyk.io/blog/llms-resurrecting-open-source-dormant-majority/
-
Snyk reposted
Brian Vermeer
@BrianVerm
Heading to Atlanta for @devnexus 2026!
I’ll be presenting "The Hidden Security Hazards in Your Java Stack." We're uncovering the vulnerabilities that standard tools often overlook.
devnexus.org/speakers/brian-vermeer
#devnexus #java #appsec @snyksec -
Snyk reposted
Liran Tal
@liran_tal
But does it?
Code review solved by @QodoAI
Code security solved by @snyksec
What are you missing? -
Snyk reposted
Liran Tal
@liran_tal
Andy, seriously, haven't tried yet the @snyksec mcp server??
type this in the address bar: snyk.studio and get that agent under control -
Snyk
@snyksec
Knock knock, new blog post out 🎉
We published a nicely written-up guide on how MCP Package Health works alongside our Secure at Inception paradigm and dependency checks
The 89% Problem: How LLMs Are Resurrecting the "Dormant Majority" of Open Source: snyk.io/blog/llms-resurrecting-open-source-dormant-majority/ -
Snyk
@snyksec
There's been a lot of chatter around "skills" lately. But what even is a skill?
Watch the video below to learn 📹This media couldn't be displayed. See it on the original post. -
Snyk
@snyksec
Stop calling functions with a return type of "any" and hoping for the best 🚫
The solve: structured outputs.
Enforce schemas at the token selection level, not after generation.
Read the full deep dive here: snyk.io/articles/building-safer-ai-agents-structured-outp… -
Snyk
@snyksec
With the rapid expansion of AI adoption, a new role is on the rise: The AI Security Engineer.
Manoj Nair navigates this in detail at the link in the comments 💬 -
Snyk reposted
AI Security Engineers
@aiseceng
If you care about building AI safely, join the community conversation. 👉 www.reddit.com/r/AISecEng/
-
Snyk
@snyksec
Snky Labs analyzed OpenClaw and found two major sandbox failures:
1️⃣ Sandbox policy enforcement gaps in tool invocation.
2️⃣ A symlink TOCTOU race condition leading to arbitrary file access.
Read the full report here: labs.snyk.io/resources/bypass-openclaw-security-sandbox/ -
Snyk
@snyksec
Join us for an evening with Team USA soccer legends, Brandi Chastain & Tim Howard ⚽️
We’re discussing how AI is rewriting the playbook. From officiating and training, scouting, and fan engagement, AI is reshaping every play.
Secure your seat here: go.snyk.io/rsa-26-ai-changes-the-game.html -
Snyk
@snyksec
Check it out! Snyk Studio MCP server is now available in Glama.
🔗 👉 glama.ai/mcp/servers/@snyk/snyk-studio-mcp -
Snyk
@snyksec
Are you attending RSA? Good news: we've got your itinerary sorted ✅
From rooftop cocktails to chats with Team USA soccer legends, we’ve built a roster of can’t-miss events, hands-on trainings, and VIP experiences ⚽️
Stay tuned for more details to come! -
Snyk
@snyksec
Do you see what we see? 👀
-
Snyk
@snyksec
The market says Anthropic just ate the security industry’s lunch 🫠
The reality? Finding bugs is the easy part. Fixing them at scale without breaking your entire stack is the real challenge.
Here’s what Claude Code Security actually means for AppSec: snyk.io/articles/anthropic-launches-claude-code-security/ -
Snyk
@snyksec
Finding the vulnerabilities is the easy part. Fixing them is often the part developers dread most 😬
Watch below to see how our latest enhancements to Snyk Studio collapse the complexity of remediation into a single command.
Learn more here: snyk.io/blog/new-snyk-studio-capabilities-ai-security-fab… -
Snyk reposted
Liran Tal
@liran_tal
here's a tease for the sort of agentic security orchestration we're building at @snyksec
wanna hear more? ;-) -
Snyk reposted
Liran Tal
@liran_tal
Your goal is that all agenting coding sessions will bake a @snyksec security scan in the task list
why?
- audits the AI generated code
- audits the package health of hallucinated npm packages
- prevents malicious packages from getting installed
- provides security context -
Snyk reposted
David Dias
@TheDavidDias
It uses @snyksec amazing scan-agent under the hood to detect any security issue
-
Snyk reposted
AI Security Engineers
@aiseceng
Join us in London for a fun AI Security Night with great speakers from @snyksec and @tessl_io.
We'll talk about securing Vibe Coding and the challenges of LLM-created code, and creating tools for LLMs
RSVP Now : luma.com/equznhw8 -
Snyk
@snyksec
Our analysis of nearly 4,000 skills, the building blocks of AI agents, revealed how they are introducing vulnerabilities to your tech stack ⚠️
Governance must move just as fast as agent adoption.
Blog + research: snyk.io/blog/toxicskills-malicious-ai-agent-skills-clawhub/
Scan your skills: labs.snyk.io/experiments/skill-scan/ -
Snyk
@snyksec
Yalo struck gold with Snyk, reducing the the noise around vulnerabilities by 90% 🥵
Watch below to hear more about Leon Direito's eureka moment 👇 -
Snyk reposted
Simone Margaritelli
@evilsocket
1,184 malicious skills were found on OpenClaw's ClawHub marketplace - stealing SSH keys, crypto wallets, browser passwords, and opening reverse shells. One attacker uploaded 677 packages alone. The #1 ranked skill had 9 vulnerabilities and was downloaded thousands of times.
-
Snyk reposted
Manoj Nair
@mnair1
Really like what @vercel is doing with skills.sh. It is quickly becoming the distribution layer for agent capabilities, so baking in trust early matters.
A few weeks ago @Snyk Research published #toxicskills, a broad audit of agent skills that showed why this needs to be treated like a real supply chain that is being targeted by bad actors: snyk.io/blog/toxicskills-malicious-ai-agent-skills-clawhub/
Proud to partner with @vercel and see their agility in working with security partners like Snyk to bring agent skill scanning into the skills.sh marketplace so skills can be vetted before use.
snyk.io/blog/snyk-vercel-securing-agent-skill-ecosystem/
@rauchg @snyk #agentsecurity #supplychainsecurity #ai -
Snyk reposted
AI Security Engineers
@aiseceng
Melbourne security folks 🇦🇺
We’re hosting a Fetch the Flag catch-up session — 15 hands-on CTF challenges across web, binary & exploitation.
Hack solo or team up.
Gift cards up for grabs.
Join us 👇
luma.com/fwujn4zz
#ai #cybersecurity #infosec #ctf -
Snyk
@snyksec
We’re thrilled to announce our partnership with Cline, bridging the gap between autonomous speed and security.
You can now maximize the efficiency gains of AI coding without compromising trust 💥 -
Snyk reposted
Basel Ismail
@BaselIsmail
AI Agent security risks are getting worse. It's time to lock in and be smart, build your own custom setup with a private gateway, not choose convenient off-the-shelf options.
Separate from the malware, @snyksec scanned nearly 4,000 ClawHub skills (marketplace for #openclaw) and found about 7% of them leak sensitive credentials. Not intentionally malicious, just badly written. -
Snyk
@snyksec
Join host Vandana Verma and special guest Rob van der Veer (Chief AI Officer at Software Improvement Group) for the February edition of The AI Radar.
📅 Tuesday, 24th February | 11:00 AM GMT | 12:00 PM CET
Register here: go.snyk.io/isc2-emea-ai-radar-series.html -
Snyk reposted
AI Security Engineers
@aiseceng
If you care about building AI safely, join the community conversation. 👉 www.reddit.com/r/AISecEng/
-
Snyk reposted
Manoj Nair
@mnair1
Agents introduced a new supply chain: skills with privileges.
@snyksec research: ~4k public skills, over a third had security issues
Blog + research:
labs.snyk.io/resources/agent-scan-skill-inspector/
Curious — are teams allowing skills or blocking them? -
Snyk reposted
SC Media
@SCMagazine
#ai is now the default developer, says @snyksec's Clinton Herget. Traditional AppSec can’t keep up. The next shift is AI-accelerated DevSecOps — using AI for context, prioritization, and guardrails without breaking dev flow. #cybersecurity #infosec #ciso www.scworld.com/resource/the-next-evolution-of-applicatio…
-
Snyk reposted
Mushroom キノコ
@MushroomWasp
We (L0ck8y7e) secured the #2 spot! 🥈🚩 20/22 challenges down. GG to everyone who competed and shoutout to @snyksec for the awesome event
#fetchtheflag #ctf #cybersecurity #infosecurity #infosec -
Snyk reposted
Manoj Nair
@mnair1
Most enterprises are reacting to AI agents skills the wrong way right now 🚫. Blocking isn't a strategy, visibility and inspection is 🔬.
We launched a free Skill Inspector today to help teams see what skills actually do before they run 👇
labs.snyk.io/experiments/skill-scan/ -
Snyk
@snyksec
AANNDD thats a wrap on Fetch the Flag 2026 🏁
Huge congrats to our top 3 teams and top 3 individual players who claimed the top spots 🏆
What was your favorite challenge? Players, sound off in the comments!! -
Snyk
@snyksec
Malicious skills just met their match 🥷
36.8% of the nearly 4,000 skills we analyzed contained AT LEAST one security issue.
That's why we're giving you the AI agent skill inspector. Start scanning your skills here: labs.snyk.io/resources/agent-scan-skill-inspector/ -
Snyk
@snyksec
It’s time to stop handing agents the keys to your email, databases, and production environments, then simply hoping the AI does the right thing 🙄
Hope is not a security model!
Thankfully, our parters at arcade.dev just launched a really exciting fix. -
Snyk
@snyksec
Fetch the Flag 2026 Challenge Peek 🫣
An AI-powered WAF.
“Impossible” to exploit.
Critical bugs? Supposedly handled.
Would your team prove otherwise?😨 -
Snyk reposted
Ben Sadeghipour
@NahamSec
Fetch the Flag CTF with @snyksec goes live in a little over 24 hours (12:00 PM ET) with 20+ challenges and some amazing prizes!
If you haven't already, make sure you register right now 👇
snyk.co/ujxq4
See you on the leaderboard 😈 -
Snyk
@snyksec
Snyk’s 2026 State of Agentic AI Adoption report analyzes Evo AI-BOM telemetry from 500+ organizations. The findings show a major shift, as AI footprints silently sprawl to 3x larger than model-only counts.
Read the full report: snyk.io/lp/state-of-agentic-ai-adoption -
Snyk
@snyksec
Trust fall 🥵
Don’t sweat it, we’ve got you secured. -
Snyk
@snyksec
Not in love with your runtime security solution? Snyk API & Web may be the perfect match for you.
💜 AI-powered testing
🩷 A 0.08% false positive rate
❤️ Coverage that sweeps you off your feet
Learn more here: go.snyk.io/valentines-dast-demo.html -
Snyk
@snyksec
Are you in San Francisco this Thursday? 🌉
We invite you to the Snyk office - enjoy a workspace with pizza and drinks, meet friends, see Snyk demos and ask us anything about AI Security: luma.com/rax1rdpt?tk=PuXmYq -
Snyk reposted
AI Security Engineers
@aiseceng
Join us in London for a fun AI Security Night with great speakers from @snyksec and @tessl_io.
We'll talk about securing Vibe Coding and the challenges of LLM-created code, and creating tools for LLMs
RSVP Now : luma.com/equznhw8 -
Snyk reposted
HackingHub
@hackinghub_io
🚩We're teaming up with @snyksec to bring you 24 hours of hands-on hacking challenges.
What's waiting for you:
🔒 15 challenges across web, binary, exploitation & more
🏆 Compete against 1,000+ teams for prizes
⚡ Sharpen your skills in real-world scenarios -
Snyk reposted
AI Security Engineers
@aiseceng
Catch The Flag - AI Security Edition
One of our favorite @snyksec's events returns this February.
Join us for a free Capture the Flag competition hosted with @nahamsec!
If you enjoy hands-on learning and ethical hacking, this is for you!
Register here: snyk.co/uju8y -
Snyk
@snyksec
Our #toxicskills research has been added to www.aileaks.dev 👏
"Snyk Finds Prompt Injection in 36% of Agent Skills in Supply Chain Compromise Study" go read it and other AI security leaks 👇 -
Snyk reposted
Manoj Nair
@mnair1
We just invented influencer supply-chain attacks 🤦🏽♂️
“AI agents are the new attack surface” wasn’t a metaphor.
If this is real: exposed DB + leaked keys = anyone can post as anyone.
Jamieson O'Reilly
@theonejvo
I've been trying to reach @moltbook for the last few hours. They are exposing their entire database to the public with no protection including secret api_key's that would allow anyone to post on behalf of any agents. Including yours @karpathy
Karpathy has 1.9 million followers on @X and is one of the most influential voices in AI.
Imagine fake AI safety hot takes, crypto scam promotions, or inflammatory political statements appearing to come from him.
And it's not just Karpathy. Every agent on the platform from what I can see is currently exposed.
Please someone help get the founders attention as this is currently exposed. -
Snyk reposted
Manoj Nair
@mnair1
📄 Full ToxicSkills research:
snyk.io/blog/toxicskills-malicious-ai-agent-skills-clawhub -
Snyk reposted
Manoj Nair
@mnair1
If you use #openclaw, #claudecode, #cursor, or any Agent Skills-powered tool:
1. Audit installed skills immediately:
uvx mcp-scan@latest --skills
2. Check for these specific malicious skills and remove if present: more in the blog -
Snyk reposted
Liran Tal
@liran_tal
Adam, want to partner up on teaching builders in openclaw academy about using mcp-scan to detect malicious and risky skills?
its what powered the #toxciskills research from @snyksec: snyk.io/blog/toxicskills-malicious-ai-agent-skills-clawhub/ -
Snyk reposted
Liran Tal
@liran_tal
It's just not enough because that's a static database I think? you really need to run a dynamic scanner per skill to detect malware and other undesired behavior
see the #toxciskills report from @snyksec on this: snyk.io/blog/toxicskills-malicious-ai-agent-skills-clawhub/ -
Snyk reposted
Liran Tal
@liran_tal
skills on clawhub and openclaw are one thing, but the agent skills ecosystem is bigger and the impact is real (for example, there's also vercel's skills[.]sh), see @snyksec findings here for more data snyk.io/blog/toxicskills-malicious-ai-agent-skills-clawhub/
-
Snyk reposted
Liran Tal
@liran_tal
mcp-scan is a python package so you can just run it, no auth required and it scans skills files or skills folders (and also MCP servers :)) - github.com/invariantlabs-ai/mcp-scan
it'll also trip up other issues in agent skills, not just malware, like hardcoded creds, public resources etc -
Snyk reposted
Liran Tal
@liran_tal
Jamieson appreciate the work here and the VT integration is pretty cool lift for the community as a whole 👌
Not sure if you saw the research we dropped from @snyksec yesterday (snyk.io/blog/toxicskills-malicious-ai-agent-skills-clawhub/) and I wanted to check if you want to evaluate mcp-scan for skill scanning? -
Snyk
@snyksec
Calling @theonejvo
this supposedly Google agent skill isn't just "suspicious" it's malicious 😱
How do we know? here's the breakdown 👇🧵
IOC: clawhub.ai/moonshine-100rze/google-qx4
Snyk
@snyksec
On the surface, this agent skills looks like a benign Google connectivity skill to power your openclaw agent
what's the harm here? it's just markdown...
or is it...?
let's take a look👇
Snyk
@snyksec
scanning it with Snyk's mcp-scan command (free to use: github.com/invariantlabs-ai/mcp-scan) and you can see the agent steering prompts and how they unfold into a malware
-
Snyk reposted
Liran Tal
@liran_tal
Kitze I know you've been big on skills so want to run the agent skills research we published yesterday from @snyksec by you, it's #toxicskills snyk.io/blog/toxicskills-malicious-ai-agent-skills-clawhub/
-
Snyk reposted
Luca Beurer-Kellner
@lbeurerkellner
🔴BEWARE: Malicious skills on ClawHub are still live and *very* malicious.
For instance, this one, 'zaycv/clawhub', contains direct download instructions for external binaries in the introduction.
Some patterns we have noticed, monitoring the situation 👇 -
Snyk
@snyksec
The numbers of secrets and credentials found in published agent skills is astonishing.
Is anyone checking them before using them? -
Snyk reposted
Luca Beurer-Kellner
@lbeurerkellner
(8/n) Read up on our full report below, and check out our latest mcp-scan update, which can now also scan your installed agent skills, at least for basic attacks and vulnerable patterns. Stay safe.
Report: github.com/invariantlabs-ai/mcp-scan/blob/main/.github/re…
MCP-Scan: github.com/invariantlabs-ai/mcp-scan?tab=readme-ov-file -
Snyk reposted
Luca Beurer-Kellner
@lbeurerkellner
(1/n) We analyzed 3,984 agent skills from major marketplaces and found 76 malicious payloads, including credential theft, backdoor installation, and data exfiltration.
Also, 13.4% contain at least on critical-level vuln.
Full report below, highlights in thread 👇 -
Snyk reposted
aileaks
@devaileaks
🤖🔥 Snyk Finds Prompt Injection in 36% of Agent Skills in Supply Chain Compromise Study (Snyk).
Full details: snyk.io/blog/toxicskills-malicious-ai-agent-skills-clawhub/ -
Snyk reposted
yenkel
@yenkel
new AI security article: @snyksec team found prompt injection attacks in @openclaw and skills.sh marketplaces
subscribe to @devaileaks to stay up to date on these
uses @yutori_ai scouts to stay up to date with security incidents around AI, site built with @v0
aileaks
@devaileaks
🤖🔥 Snyk Finds Prompt Injection in 36% of Agent Skills in Supply Chain Compromise Study (Snyk).
Full details: snyk.io/blog/toxicskills-malicious-ai-agent-skills-clawhub/ -
Snyk reposted
SC Media
@SCMagazine
#ai is now the default developer, says @snyksec's Clinton Herget. Traditional AppSec can’t keep up. The next shift is AI-accelerated DevSecOps — using AI for context, prioritization, and guardrails without breaking dev flow. #cybersecurity #infosec #ciso www.scworld.com/resource/the-next-evolution-of-applicatio…
-
Snyk reposted
AI Security Engineers
@aiseceng
🔥 Who's up for a Catch The Flag? 🔥
@snyksec's Fetch the Flag 2026 is back in partnership with @nahamsec!
Tackle 15 hands-on challenges, compete solo or with a team, and test your real-world security skills.
Register here: snyk.co/uju8y -
Snyk reposted
Liran Tal
@liran_tal
Jim did you catch on the #toxciskills report @snyksec? snyk.io/blog/toxicskills-malicious-ai-agent-skills-clawhub/
-
Snyk reposted
Alex Volkov
@altryne
Hopefully you all kicked all these off?
snyk.io/blog/toxicskills-malicious-ai-agent-skills-clawhub/ -
Snyk reposted
Manoj Nair
@mnair1
Toxic skills are real. Its beyond just malware. There are other vulnerabilities too.
If you use OpenClaw, Claude Code, Cursor, or any Agent Skills-powered tool:
Audit installed skills immediately:
uvx mcp-scan@latest --skills
More on our research here: snyk.io/blog/toxicskills-malicious-ai-agent-skills-clawhub/ -
Snyk reposted
John Hammond
@_JohnHammond
February got here fast-- and the 2026 @snyksec Fetch the Flag CTF came up quick too! This year my friend @NahamSec is hosting the game, starting NEXT THURSDAY 2/12 at 12pm ET! Free 24-hour Capture the Flag event with AR glasses as prizes 😎 See ya there! jh.live/snyk-ftf2026
-
Snyk reposted
Manoj Nair
@mnair1
Models talk.
Agents act.
Skills decide what happens.
That’s the new risk surface.
Toxic skills are real: over a third of the ecosystem is affected
Audit installed skills immediately:
uvx mcp-scan@latest --skills
🧐snyk.io/blog/toxicskills-malicious-ai-agent-skills-clawhub -
Snyk reposted
Ed Sim
@edsim
reminds me of early days of open source, going to need verified skills along with auto scanning of any calls to skills - check out this report from @snyksec 🤯
read rest here: snyk.io/blog/toxicskills-malicious-ai-agent-skills-clawhub/ -
Snyk reposted
Liran Tal
@liran_tal
#toxicflows So I personally run OpenClaw (well clawdbot still in the cli) but I also wear a security researcher hat at Snyk and we cooked some good study for you:
snyk.io/blog/toxicskills-malicious-ai-agent-skills-clawhub/ -
Snyk
@snyksec
#toxicskills agent skills malware research is published: snyk.io/blog/toxicskills-malicious-ai-agent-skills-clawhub/
✅ 534 skills (13.4%) contain at least one CRITICAL security issue
✅ 1,467 skills (36.82%) contain at least one security issue of any severity
✅ 8 malicious skills remain live on ClawHub
Go 👇 -
Snyk
@snyksec
We just ran the first comprehensive security audit of the AI Agent Skills ecosystem, analysing 3,984 skills from ClawHub and skills[.]sh)
the findings are alarming with malware credential theft, and prompt injection attacks targeting OpenClaw and more: snyk.io/blog/toxicskills-malicious-ai-agent-skills-clawhub/ -
Snyk
@snyksec
Warm-up time! We just dropped a special Fetch the Flag edition of Vuln Vortex, and we want to know…
How long can you survive in the vortex? 🎮⚡️
Play Patch & NahamSec’s Vuln Vortex 👉 snyk.co/uju8u
Register for Fetch the Flag 👉 snyk.co/uju8x -
Snyk
@snyksec
what can we say... the web team cooked 🔥
-
Snyk
@snyksec
what do you think of my new look ;-)
-
Snyk reposted
AI Security Engineers
@aiseceng
New year. New skills. Hack AI Security!
@snyksec's Catch the Flag - AI Security Edition is back in partnership with @nahamsec! Learn AI Security hands-on with 15 challenges, and compete to win our top prizes🏆
Register here: snyk.co/uju8y -
Snyk reposted
HackingHub
@hackinghub_io
🚩 Fetch the Flag CTF is next week!
HackingHub and @NahamSec are teaming up with @snyksec to bring you 24 hours of hands-on hacking challenges.
Register today👉 snyk.co/ujxq4 -
Snyk
@snyksec
This is your opportunity to get the inside scoop on The AI Security Fabric.
We’re pulling back the curtain on the security layer for continuous defense required to unleash AI innovation securely.
Register here 👉 snyk.co/ujxWT -
Snyk
@snyksec
Stop checking boxes an start building an autonomous defense 🛠️
We’re putting the roadmap in your hands to secure the agentic era. Move from human-speed oversight to machine-speed protection
3 Acts. 6 Steps. 1 Goal: Architected Trust.
Click here 👉 snyk.io/blog/prescriptive-path/ -
Snyk reposted
AI Security Engineers
@aiseceng
Delivering software shifts to humans, models, and autonomous agents working together at machine speed. Security must evolve just as fundamentally! Kudos on the launch @snyksec 👏
Snyk
@snyksec
AI is writing code at machine speed.
Now, your security can close the gap with the Snyk AI Security Fabric.
Learn more about the industry’s first security layer for continuous defense across the entire SLDC here 👉 snyk.io/news/snyk-ai-security-fabricThis media couldn't be displayed. See it on the original post. -
Snyk reposted
Pure AI
@PureAINews
Security backlogs keep growing. Teams need leverage.
Join us, sponsor @snyksec, and a panel of experts tomorrow for this webcast and learn how to use AI to prioritize and remediate vulnerabilities faster without slowing down releases.
Register: pureai.com/webcasts/2026/02/snyk-burning-down-the-backlog…
#appsec -
Snyk
@snyksec
AI creates risk 3x faster than most teams can track it.
Between "Shadow AI" and autonomous agents, the attack surface is expanding beyond human-speed oversight. We're closing the gap today with the Snyk AI Security Fabric.
Get the full story here 👉 snyk.io/blog/ai-security-fabric/ -
Snyk
@snyksec
AI is writing code at machine speed.
Now, your security can close the gap with the Snyk AI Security Fabric.
Learn more about the industry’s first security layer for continuous defense across the entire SLDC here 👉 snyk.io/news/snyk-ai-security-fabricThis media couldn't be displayed. See it on the original post. -
Snyk
@snyksec
If you're going to @OneRSAC you don't want to miss @InfosecVandana's Agentic AI Security lab ✨
Here's the gist: path.rsaconference.com/flow/rsac/us26/FullAgenda/page/cat…
Go RSVP before you'll find yourself in the waitlist! -
Snyk
@snyksec
We hope you attended today @Jfokus - the cool Java Developer Conference in Stockholm and learned from @BrianVerm in his deep-dive session about Understanding Prompt Injection: Techniques, Challenges, and Advanced Escalation.
Teaching devs about AI Security, thank you Brian 💜 -
Snyk reposted
HackingHub
@hackinghub_io
Fetch the Flag 2026 with @snyksec and @NahamSec is here!
Sign up and test your skills against the best in the community.
Event Details:
📅 February 12-13
⏰ 12 PM ET start
Ready to compete? Register today👉 snyk.co/ujxq4 -
Snyk reposted
AI Security Engineers
@aiseceng
Catch The Flag - AI Security Edition
One of our favorite @snyksec's events returns this February.
Join us for a free Capture the Flag competition hosted with @nahamsec!
If you enjoy hands-on learning and ethical hacking, this is for you!
Register here: snyk.co/uju8y -
Snyk
@snyksec
💡 Did you know you can find package health data on the Snyk Security Database? security.snyk.io
-
Snyk
@snyksec
⚠️ How do you find a healthy library before you install it?
From community scores to popularity and maintenance insights and direct and transitive package vulnerabilities
The new Snyk Security Database experience - security.snyk.io -
Snyk
@snyksec
🔊 Snyk Advisor is Reshaping Package Intelligence on Snyk Security Database: snyk.io/blog/snyk-advisor-security-database/
✅ A unified experience for Security and Developers
✅ Consistent and trusted package data
Go check out the new Snyk Advisor supply chain experience 👇 -
Snyk reposted
Rory McNamara
@PsychoMario
Swapped out my lab infrastructure for Incus, found some vulnerabilities on the way. Read more here:
Snyk
@snyksec
🚨 BREAKING: Arbitrary Writes High-Severity Vulnerabilities Discovered in Incus VM Project
Hats off to Snyk security researcher @PsychoMario for the security disclosures: labs.snyk.io/resources/incus-vulnerabilities-newline-syml… -
Snyk reposted
AI Security Engineers
@aiseceng
🔥 Who's up for a Catch The Flag? 🔥
@snyksec's Fetch the Flag 2026 is back in partnership with @nahamsec!
Tackle 15 hands-on challenges, compete solo or with a team, and test your real-world security skills.
Register here: snyk.co/uju8y -
Snyk reposted
AI Security Engineers
@aiseceng
New year. New skills. Hack AI Security!
@snyksec's Catch the Flag - AI Security Edition is back in partnership with @nahamsec! Learn AI Security hands-on with 15 challenges, and compete to win our top prizes🏆
Register here: snyk.co/uju8y -
Snyk
@snyksec
openclaw operated by non-technical users
-
Snyk reposted
Pure AI
@PureAINews
Security backlogs are exploding.
Join us, sponsor @snyksec, and a panel of experts on Feb. 4 for this FREE webcast where we cover how to reduce risk with an AI-accelerated remediation strategy, plus a practical demo.
Register now: pureai.com/webcasts/2026/02/snyk-burning-down-the-backlog…
#appsec #devsecops #ai -
Snyk
@snyksec
🚨 BREAKING: Arbitrary Writes High-Severity Vulnerabilities Discovered in Incus VM Project
Hats off to Snyk security researcher @PsychoMario for the security disclosures: labs.snyk.io/resources/incus-vulnerabilities-newline-syml… -
Snyk reposted
Devnexus
@devnexus
Think your Java stack is safe? Think again. 🔓
Join @BrianVerm, from @snyksec at #devnexus for real-world examples and live hacking that reveal how dependencies, containers, and AI-assisted code can expose your apps.
devnexus.org/events/the-hidden-security-hazards-in-your-j…
Unmissable for Java devs.
🎟️ Get tickets at devnexus.com
Sign up to keep up to date with all the conference info atlj.ug/Xconnect
#security #java #ai #developer #techconference #softwareengineering #securecoding #cloudnative -
Snyk reposted
Help Net Security
@helpnetsecurity
Cybersecurity jobs available right now: January 27, 2026 - www.helpnetsecurity.com/2026/01/27/cybersecurity-jobs-ava… - @alignerrAI @anduriltech @micro1_ai @Kyndryl @WeAreOnSecurity @Wolfspeed @AnkabutUAE @snyksec @Nike @my_chagee @cmacgm @offsectraining #cybersecurityjobs
-
Snyk
@snyksec
Remember the Polyfill supply chain attack?
Here's a reminder and security best practices you should follow to mitigate this JavaScript supply-chain attack from creeping in via CDN 👇 -
Snyk reposted
InfoSecMap
@InfoSecMap
Take on a #challenge & sharpen your skills! 🚩
Upcoming #ctf events by @snyksec @PacificHackers @nullcon @WWHackinFest @BSidesGalway @_BSidesKC @_kernelcon_ @redhotcyber @K12SIX @_TROPICON @hackthebox_eu & @NahamSec.
Full list 👇🏽
infosecmap.com/explore/?type=event&category=ctf&sort=orde…
#infosec #cybersecurity
Snyk
@snyksec
We’re partnering with @hackinghub_io to bring you a hands-on hacking experience.
Bring your team and compete and win an win epic prize 🏆
📅 February 12-13
⏰ 12 PM ET start
🔒15 challenges
Register today: snyk.co/ujxq4 -
Snyk
@snyksec
🦞 Your Clawdbot AI Assistant Has Shell Access and One Prompt Injection Away from Disaster: snyk.io/articles/clawdbot-ai-assistant/
-
Snyk
@snyksec
If you're using Clawdbot or just seeing the security drama unfolding from the side we've compiled the stories for you to catch up on AI personal agents security: snyk.io/articles/clawdbot-ai-assistant/
-
Snyk reposted
AI Security Engineers
@aiseceng
Join our community calls to hear from community projects built and secured with AI
Next edition highlights:
• MCP Threat Trap: Deception engineering for zero trust Al access
• PromptInjector: Al Prompt Injection Tester
👉 Register Now! go.snyk.io/dso-community-join-us.html -
Snyk reposted
Ben Sadeghipour
@NahamSec
Super excited to be hosting @snyksec's Fetch The Flag this year! Signup here to compete and win some amazing prizes! snyk.co/ujxq4
This media couldn't be displayed. See it on the original post. -
Snyk reposted
AI Security Engineers
@aiseceng
Catch The Flag - AI Security Edition
One of our favorite @snyksec's events returns this February.
Join us for a free Capture the Flag competition hosted with @nahamsec!
If you enjoy hands-on learning and ethical hacking, this is for you!
Register here: snyk.co/uju8y -
Snyk
@snyksec
How do you craft prompts to build apps with AI?
Here's Brian Clark prompting an Anthropic model to create a secure Node.js note taking app...
❓ Quiz - what kind of security vulnerabilities do you think the model generated? -
Snyk
@snyksec
Are you ready to Fetch the Flag in February 2026 ?
@NahamSec and Snyk are partnering for a capture the flag event for all hackers out there, register here: snyk.co/ujzt0 -
Snyk
@snyksec
Heading to @ConDaysEU ? 🐳
Don't miss Snyk's very own Pratip Banerji who will teach you about How to Easily Scale Continuous Container Governance with Runtime Context and AI -
Snyk
@snyksec
Who wants a thread on building secure MCP servers?
Snyk
@snyksec
Are you building MCP servers? What’s your biggest security concern? reply and let us know!
Here's our break-down of MCP security issues and how to prevent them:
Snyk
@snyksec
The Model Context Protocol (MCP) is the hottest trend in AI right now. But in the rush to build autonomous agents, we’re repeating the most dangerous security mistakes of the last 20 years
Did we just broke down the "Big 3" vulnerabilities hitting MCP servers today? dive in 🧵👇 -
Snyk
@snyksec
The Model Context Protocol (MCP) is the hottest trend in AI right now. But in the rush to build autonomous agents, we’re repeating the most dangerous security mistakes of the last 20 years
Did we just broke down the "Big 3" vulnerabilities hitting MCP servers today? dive in 🧵👇
Snyk
@snyksec
2/💡 MCP servers give LLMs "hands" - access to your file system, databases, and APIs.
But here’s the scary part: These servers run on your local machine with your API keys and your credentials. A single vulnerability = full system compromise.
Snyk
@snyksec
3/ Danger #1 - Command Injection 🛑 This is the most prevalent MCP bug. Pattern: Spawning npm, git, or lsof using string interpolation.
If an attacker feeds your AI: react; touch /tmp/pwned, and your server uses exec(), they now have remote code execution on your laptop. 💻🧨
Snyk
@snyksec
4/ ✅ Stop using exec(). It spawns a shell and interprets metacharacters.
Instead, use execFile(). It treats arguments as an array, making it impossible for a semicolon or pipe to trigger a second command.
Safe > Fast.
Snyk
@snyksec
5/ Danger #2 - Path Traversal 📂 MCP servers often read local files (docs, configs, etc.). Without strict validation, an AI agent can be tricked into requesting: ../../../../.ssh/id_rsa
Suddenly, your private keys are in the LLM’s context window (and potentially the attacker's).Post not available here, view on X
Snyk
@snyksec
9/ The Wrap Up 🏁 AI agents are only as secure as the MCP servers they talk to. Treat your MCP code with the same rigor as a production production web API.
Check out the full guide for real-world MCP CVE examples and a security checklist: snyk.io/articles/building-secure-mcp-servers/
Snyk
@snyksec
/6
-
Snyk reposted
Pure AI
@PureAINews
Security backlogs are exploding, and AI is making the gap wider with every release.
Join us, Sponsor @snyksec, and a panel of experts on Feb. 4 to learn how to build and apply an AI-accelerated remediation strategy.
Register today: pureai.com/webcasts/2026/02/snyk-burning-down-the-backlog…
#appsec #ai -
Snyk
@snyksec
Next week is gonna be wild!
- X XXX XX X XX XX X X XXX XXX
- XX XX X XXXXX XX X X XXX
- XXX XXX XXX XXXX XXXXXX -
Snyk
@snyksec
DO NOT MISS THIS BUG BOUNTY MASTERCLASS 👇
AI Security Engineers
@aiseceng
🔥 Who's up for a Catch The Flag? 🔥
@snyksec's Fetch the Flag 2026 is back in partnership with @nahamsec!
Tackle 15 hands-on challenges, compete solo or with a team, and test your real-world security skills.
Register here: snyk.co/uju8y -
Snyk
@snyksec
Top 3 JWT Security Best Practices for Your Apps ✨
Today Brian Clark talks about how to secure your JWTs in app development. These are the 3 most important practices to keep your JWTs safe while coding applications!
7 minutes & bookmark 👇This media couldn't be displayed. See it on the original post. -
Snyk
@snyksec
Did you already read Snyk newest report?
The End of Human-Speed Security: Defense in the Age of AI Agents: snyk.io/lp/end-of-human-speed-security-dwn-typ/ -
Snyk
@snyksec
When your Snyk security checks finish faster than your CI 😍
DevSecOps readiness for AI security 💪 -
Snyk
@snyksec
Security is a team sport. 🛡️
The threat landscape moves fast—stay ahead at Fetch the Flag 2026! Join us on Feb 12–13 for our global CTF event.
🔴15 hands-on challenges
🔴Solo or team play
🔴Real-world scenarios
Register: snyk.co/uju8q
#fetchtheflag #snyk #infosec -
Snyk
@snyksec
Listen to Eric, he knows his agents.
How do you guarantee secure agent coding sessions with @cursor_ai ?
Here's how simple it is👇Post not available here, view on X
Snyk
@snyksec
2/ Then whatever you prompt and whenever Cursor agent completes the session, it runs the Snyk MCP tool call to scan the code generated by AI:
Snyk
@snyksec
3/ That's it! Go install the Cursor Snyk extension: snyk.io/ai-partners/cursor/
-
Snyk
@snyksec
Yes Shai-Hulud was a 2025 thing but to make sure you're prepared for the next 0day malware ...
Snyk provides a centralized Zero-Day Report that surfaces exactly projects and versions are affected across the entire organization. From chaotic "search and find" to checklist 👇
Snyk
@snyksec
Oh yes and here is the Shai Hulud post-mortem article so you can easily follow a security best practices recipe: snyk.io/blog/shai-hulud-post-mortem/
-
Snyk
@snyksec
What's the role of AISPM ?
1️⃣ Understand why the non-determinism of AI-native apps erodes traditional security.
2️⃣ Explore continuous tracing, AI red teaming & adaptive guardrails.
AISPM provides the foundation for AI-native apps: snyk.io/lp/ai-managing-non-deterministic-risk/ -
Snyk
@snyksec
AI-native apps don’t follow the rules of traditional software (snippet from the full report 👀)
Our new white paper introduces a framework for managing non-deterministic risk and governing AI-native environments through AISPM: snyk.io/lp/ai-managing-non-deterministic-risk/ -
Snyk reposted
AI Security Engineers
@aiseceng
New year. New skills. Hack AI Security!
@snyksec's Catch the Flag - AI Security Edition is back in partnership with @nahamsec! Learn AI Security hands-on with 15 challenges, and compete to win our top prizes🏆
Register here: snyk.co/uju8y -
Snyk
@snyksec
As @PeterCMcKay shares from his time at Davos WEF26
> AI is no longer an experiment at the edges of the enterprise. It’s becoming core infrastructure -- operating at machine speed, with increasing autonomy and at a scale traditional security models were never designed to handle
Snyk
@snyksec
read and watch the full interview about The New Economics of Risk: Securing AI in the Era of Immediate Consequence here on @CBSNews: www.cbsnews.com/brandstudio/news/the-new-economics-of-ris…
-
Snyk
@snyksec
Freddie (the king 🕺) isn't the only person who wanted to break free, apparently, Python memory allocation also wants some
Kudos to Jonathan Bar Or for the memory vulnerability finding and report on this security issue
Jonathan Bar Or (JBO) 🇮🇱🇺🇸🇺🇦
@yo_yo_yo_jbo
I found a use-after-free in CPython!
In this blogpost I also discuss interesting patterns such as refcount changes during callbacks.
Read more here: github.com/yo-yo-yo-jbo/python_uaf -
Snyk
@snyksec
👉 50% of security leaders say AI is already operating as a quasi-autonomous agent in their environments, making decisions without direct human review
We just released new research based on insights from 515 security leaders, and we’ve crossed an important threshold, see link: -
Snyk
@snyksec
Models can (and will) hallucinate.
That's a risk you don't want to take, right?
Plug in the Snyk MCP Server and ask it to find and fix security issues👇 -
Snyk
@snyksec
The era of human-speed security is over.
As our CEO, @PeterCMcKay, heads to Davos (#wef26), we’re sharing new data: 50% of security leaders say AI is already acting autonomously, and attacks are now 80–90% automated.
Get the report: snyk.io/lp/end-of-human-speed-security-dwn-typ/
#davos #snyk -
Snyk
@snyksec
We’re partnering with @hackinghub_io to bring you a hands-on hacking experience.
Bring your team and compete and win an win epic prize 🏆
📅 February 12-13
⏰ 12 PM ET start
🔒15 challenges
Register today: snyk.co/ujxq4 -
Snyk
@snyksec
well then...
-
Snyk
@snyksec
Do know about the Web Almanac by the @HTTPArchive ? 🕸️👇
1/ It's the HTTP Archive's annual state of the web report. And guess what, it has a Security chapter, continue reading
>>Post not available here, view on X
Snyk
@snyksec
3/ Good stats for security header adoption over time from 2023 to 2025
Snyk
@snyksec
4/ Did you know about HTML sanitization APIs as part of the DOM web APIs? check these out:
-
Snyk reposted
Johann Rehberger
@wunderwuzzi23
I'm on the conference committee and CFP board for [un]prompted, a community conference for AI security practitioners.
📍 Salesforce Tower, San Francisco
🗓 March 3–4
Submit a proposal and show us what you prompt 👀
unpromptedcon.org -
Snyk
@snyksec
Hello there all hackers
Learn how to use the Snyk MCP Tool in Amazon Kiro! 🔥
Use Snyk for free to find and fix security issues in your applications today www.youtube.com/watch?v=4SUeG4tUU9k -
Snyk reposted
HackingHub
@hackinghub_io
We’re partnering with @snyksec to bring you a hands-on hacking experience. Bring your team and compete to win and epic prize. 🏆
📅 February 12-13
⏰ 12 PM ET start
🔒15 challenges
Register today: snyk.co/ujxq4 -
Snyk reposted
Pure AI
@PureAINews
AI is speeding up software delivery and changing how “secure by default” looks.
Join us, sponsor @snyksec, and expert Clinton Hergert tomorrow to learn how to secure AI-generated code, and where AI fits into developer workflows.
Register now: pureai.com/webcasts/2026/01/snyk-the-next-evolution-of-ap…
#devops -
Snyk
@snyksec
It's funny because it's true 🤣
Coder girl 👩💻
@dev_maims
Backend developers are happier than Frontend developers.
Once the app works, they don't care what it looks like 🫠 -
Snyk
@snyksec
Oh no, you missed our Capture The Flag 101 event?
Don't sweat. You can still have your CTF fun with the on-demand hacking workshop: go.snyk.io/0115-ctf-101.html
Go watch and get the inside on ethical hackers competitions 🤓 -
Snyk
@snyksec
The ServiceNow AI Security incident demonstrates why AI security platforms need foundational application security capabilities built in. Securing AI means securing the software and APIs it control: snyk.io/blog/servicenow-virtual-agent-vulnerability/
-
Snyk reposted
AI Security Engineers
@aiseceng
🔥 Who's up for a Catch The Flag? 🔥
@snyksec's Fetch the Flag 2026 is back in partnership with @nahamsec!
Tackle 15 hands-on challenges, compete solo or with a team, and test your real-world security skills.
Register here: snyk.co/uju8y -
Snyk reposted
Pure AI
@PureAINews
AI is speeding up shipping and rewriting the rules for AppSec.
Join us with sponsor @snyksec and Clinton Herget on Jan 20 for a FREE virtual summit on AI-Accelerated DevSecOps, built for the era of machine-generated code.
Register now: pureai.com/webcasts/2026/01/snyk-the-next-evolution-of-ap…
#devsecops #ci_cd -
Snyk
@snyksec
Ready to crack the code? 🔐
1️⃣ Learn: Join our CTF 101 workshop for basics & a live demo.
2️⃣ Compete: Test your skills in @snyksec’s Fetch the Flag global competition (Feb 12–13)! 🚩
Sign up here: 👉 CTF 101: snyk.co/ujxrH
👉 Fetch the Flag: snyk.co/uju8q -
Snyk
@snyksec
Beyond Detection for Shai-Hulud supply chain security snyk.io/blog/shai-hulud-post-mortem/
In this article:
- Phase 1: Not getting infected in the first place
- Phase 2: Finding threats the moment they emerge
- Phase 3: Turning detection into action
the future of supply chain security -
Snyk
@snyksec
Recent security vulnerabilities in the Maven / Java ecosystem for this past week
How to stay up-to-date with security fixes?
1. Go to app.snyk.io
2. Connect your code repository
3. Receive free automated Pull Requests to upgrade vulnerable libraries -
Snyk
@snyksec
any vibe coders in the house can confirm localhost:3000 is iffy some times?
full video of GPT-5 demo in Cursor Agent Mode put to the security test: www.youtube.com/watch?v=9CoWnPf9cm4 -
Snyk reposted
Manoj Nair
@mnair1
“Your agents are doing WHAT?!”
AI builders: you think you know which LLMs, mcp servers, tools your AI app is calling in prod 😂
We just launched Snyk AI-BOM on Product Hunt. One CLI to expose your real AI supply chain.
Go look. You might cry.
producthunt.com -
Snyk
@snyksec
An LLM coding agent quiz you 🎓
Do you know why GPT 5.2 Codex performed the following npm uninstall csurf -> npm install csrf-csrf ? -
Snyk
@snyksec
Several security vulnerabilities and fixes in React Router and related npm packages, upgrade quick to patch the CVEs 👀
More details on the Snyk Security Database: security.snyk.io/vuln/npm -
Snyk
@snyksec
GPT 5.2 vs Security Vulnerabilities, how does that work?
@_clarkio shows the story of a typical Node.js application "production-ready and secure", see the results 👇 www.youtube.com/watch?v=o7UwCYXv2WU -
Snyk reposted
AI Security Engineers
@aiseceng
Catch The Flag - AI Security Edition
One of our favorite @snyksec's events returns this February.
Join us for a free Capture the Flag competition hosted with @nahamsec!
If you enjoy hands-on learning and ethical hacking, this is for you!
Register here: snyk.co/uju8y -
Snyk
@snyksec
Good morning hackers!
Did you already run your Monday morning brief of new security vulnerabilities at security.snyk.io/vuln/ ? 👀 -
Snyk reposted
Rob van Kranenburg
@robvank
I see, yes good work! "Security teams can clearly enforce what agents are actually doing in real time, including actions like shell execution, network calls, and MCP tool usage, providing the first true posture view of agent behavior across the organization. Evo goes beyond visibility by automating runtime risk prevention, enforcing security policies that detect and block dangerous behaviors such as PII leakage, indirect prompt injection, and toxic data flows before they become incidents."
-
Snyk
@snyksec
Hello there, looking to create a world with safer AI Security? Snyk is hiring 👇
Snyk
@snyksec
We’re pretty proud of this one🏆
Snyk is a @BuiltIn 2026 Best Place to Work — powered by brilliant humans, strong values, and a culture we love being part of.
Want to join the fun? We’re hiring🚀
snyk.io/careers/all-jobs/ -
Snyk reposted
Augment Code by Harness
@augmentcode
Augment Code + @snyksec are solving the manual security bottleneck.
Our integration embeds Snyk's security intelligence directly into Auggie CLI via MCP. Now teams can:
→ Trigger security scans programmatically in CI/CD pipelines
→ Automate SAST and SCA checks in pre-commit hooks
→ Reduce mean time to remediate from weeks to minutes
How it works 👇
www.augmentcode.com/blog/augment-snyk-partnership -
Snyk reposted
AI Security Engineers
@aiseceng
🔥 Who's up for a Catch The Flag? 🔥
@snyksec's Fetch the Flag 2026 is back in partnership with @nahamsec!
Tackle 15 hands-on challenges, compete solo or with a team, and test your real-world security skills.
Register here: snyk.co/uju8y -
Snyk
@snyksec
Listen to @ujjwalscript
Stay on top of gaps in AI Security using 👉 snyk.studio 👈
Ujjwal Chadha
@ujjwalscript
3. AI Auditing & Secure Code Review
In 2026, the primary security threat is no longer just human error, but AI-hallucinated vulnerabilities.
You must be able to spot subtle logic flaws, prompt injection risks, and data poisoning in code you didn't write. -
Snyk
@snyksec
Is this the cutest timeline blend of @NahamSec and Snyk that you've seen? we think so too 😉
Put your security skills to the test in Fetch the Flag, a virtual Capture the Flag competition hosted by Snyk and NahamSec, from February 12, 12 pm ET to February 13, 12 pm ET.
Snyk
@snyksec
Play Fetch the Flag with us snyk.io/events/ctf/
-
Snyk
@snyksec
Will you look at that? I'm detecting PII leak...
Is it, is it a prompt injection...? 😲
He who would know: snyk.io/blog/evo-agent-guard-cursor-integration/ -
Snyk reposted
Pure AI
@PureAINews
AI is changing how software gets built, and security has to keep up.
Join us, sponsor @snyksec, and speaker Clinton Herget on Jan. 20 for this webcast and learn why DevSecOps must become AI-Accelerated for AI and machine-generated code.
Register: pureai.com/webcasts/2026/01/snyk-the-next-evolution-of-ap…
#ai -
Snyk
@snyksec
🚩 #fetchtheflag is BACK! 🚩
Join Snyk & @NahamSec on Feb 12–13 for our annual #ctf competition. Team up or compete solo, take on 15 security challenges, earn CPE credit, and compete for the top prize.
Learn more and register now here: snyk.co/uju8m -
Snyk
@snyksec
We hear ya @cole_medin, insecure apps from vibe coding are a concern
We're here to fix it ;-)
p.s. great session! -
Snyk
@snyksec
How does DevSecOps in the era of AI looks like? join this 👇
Virtualization & Cloud Review
@VirtReview
AI is changing how software gets built, and security has to keep up.
Join us, sponsor @snyksec, and Clinton Herget on Jan. 20 for this webcast and unpack why DevSecOps must become AI-Accelerated for AI and machine-generated code.
Register now: virtualizationreview.com/webcasts/2026/01/snyk-the-next-e…
#appsec -
Snyk reposted
Virtualization & Cloud Review
@VirtReview
AI is changing how software gets built, and security has to keep up.
Join us, sponsor @snyksec, and Clinton Herget on Jan. 20 for this webcast and unpack why DevSecOps must become AI-Accelerated for AI and machine-generated code.
Register now: virtualizationreview.com/webcasts/2026/01/snyk-the-next-e…
#appsec -
Snyk
@snyksec
Did you already register to Fetch the Flag 2026 CTF? snyk.io/events/ctf/
-
Snyk
@snyksec
We’re pretty proud of this one🏆
Snyk is a @BuiltIn 2026 Best Place to Work — powered by brilliant humans, strong values, and a culture we love being part of.
Want to join the fun? We’re hiring🚀
snyk.io/careers/all-jobs/ -
Snyk reposted
Kim
@thinkverse
Registrations are open for @snyksec Fetch The Flag 2026! 👏
🔗 ctf.snyk.io/ctf/fetch-the-flag-2026 -
Snyk reposted
Augment Code by Harness
@augmentcode
We’re excited to partner with @snyksec 🚀
Together, we’re making it straightforward for Snyk customers to extend their existing security standards into Augment’s AI-native development workflow.
Learn more about the Snyk + Augment integration below 👇
Snyk
@snyksec
Speed shouldn't compromise security. Snyk and @augmentcode have partnered to embed security intelligence into the AI-native developer workflow.
Scale your security at the speed of AI: snyk.io/blog/snyk-augment-code-partnership/ -
Snyk
@snyksec
Did you know you can just add MCP Servers to Google's Antigravity IDE?
Here's @_clarkio break-down for agentic coding: www.youtube.com/watch?v=TwRPGmBKIY0 -
Snyk
@snyksec
Speed shouldn't compromise security. Snyk and @augmentcode have partnered to embed security intelligence into the AI-native developer workflow.
Scale your security at the speed of AI: snyk.io/blog/snyk-augment-code-partnership/ -
Snyk
@snyksec
Traditional AppSec wasn’t built for AI-native apps.
Prompt injection, data leakage, and hidden agent behavior create risks you can’t afford to miss.
Join us Jan 14 to learn how to build an AI-BOM and uncover hidden AI risk: go.snyk.io/building-an-ai-bom-ai-assets.html -
Snyk
@snyksec
Happy New Year 🎉
What should we ship in 2026 ? -
Snyk reposted
Manoj Nair
@mnair1
AI security isn’t failing because teams aren’t trying 🤖🔐
It’s failing because static Security ≠ dynamic AI systems.
This video shows agentic security in practice: AI-BOM + automated AI red teaming from #evo @snyksec.
▶️ snyk.io/blog/old-ai-security-vs-evo/
#aisecurity #appsec #agenticai -
Snyk
@snyksec
Which AI agents are you securing today? 👀
-
Snyk
@snyksec
From all of us at Snyk: Happy Holidays ❄️ ✨ 🎄
As we wrap up 2025, we want to thank our teams, customers, and partners for an incredible year of collaboration, innovation, and trust.
Wishing you a joyful holiday season and a secure, successful year ahead 🔒 🌟 🥂 -
Snyk
@snyksec
Snyk Evo & @cursor_ai Hooks are now integrated.
Secure AI-driven development with visibility and enforcement across the agent lifecycle.
🔗 Announcement: snyk.io/blog/evo-agent-guard-cursor-integration/
🔗 Integrate Snyk with Cursor: cursor.com/blog/hooks-partners -
Snyk
@snyksec
The era of agentic AI is here—and the old security playbook is obsolete. 🛡️
Meet Evo by Snyk: security built for the AI-native age. 🎥👇
➡️ Learn why the "old way" no longer works: snyk.io/blog/old-ai-security-vs-evo/
#aisecurity #appsec #agenticai -
Snyk
@snyksec
The AI attack surface is expanding—and shifting fast. 🤯
Is your AppSec ready for autonomous, agentic AI?
CISOs: Download our new guide, The AI Security Tool Evaluation Framework, to secure the full AI lifecycle.
🔗 snyk.io/lp/ai-security-tool-evaluation-cisos -
Snyk
@snyksec
Join our upcoming webinar with Danny Allan @Snyk CTO, Itamar Friedman, @Qodo CEO and Co-Founder, and Tyler Shields, Principal Analyst, @OmdiaHQ to learn how to secure the AI-driven software development lifecycle from end to end.
🗓️ December 15, 10:00am PT
www.brighttalk.com/webcast/18796/657134 -
Snyk
@snyksec
Introducing Snyk Studio for @Kirodotdev! Integration that delivers security guardrails for spec-driven development.
🛡️ Prevent new risks at inception
🧹 Remediate existing security backlogs
🚀 Ship with confidence, at AI speed
👉 snyk.io/blog/snyk-kiro-partner-integration/
#reinvent Booth #447 -
Snyk
@snyksec
We’re grateful for our community of Snykers, customers, users, and partners.
Happy Thanksgiving to all who celebrate!
#thanksgiving #grateful -
Snyk
@snyksec
Your #npm install is now a Remote Code Execution primitive. 🚨
Attacks like #shaihulud are exploiting lifecycle scripts to exfiltrate credentials.
Read the 12 essential best practices for supply chain #security by @liran_tal: snyk.io/articles/npm-security-best-practices-shai-hulud-a… -
Snyk
@snyksec
Hey, #reinvent attendees! Stop by Booth #447 and get:
💡 Customized demo
😎 Snyk swag
🧠 AI Education
☕ AI Hangover Brunch
We’d love to connect and chat about how you can build secure, stay secure, and innovate faster in the cloud.
Book a meeting 🗓️ snyk.io/events/aws-reinvent/ -
Snyk
@snyksec
SHA1-HULUD IS ACTIVE. 🚨 This is not a drill. A sophisticated supply chain attack is targeting the npm ecosystem.
Need the quick breakdown on the exploit, the blast radius, and what you must do now to protect your code?
Here's the analysis & defense: snyk.io/blog/sha1-hulud-npm-supply-chain-incident/ -
Snyk
@snyksec
Snyk and @Qodo are securing the AI-driven future of software development together! 🤝
🔐 #aisecurity at inception
⚡ Reduce security debt
🚀 Accelerate development with confidence
📏 Maintain governance and scale
Read more at our blog 💡 snyk.io/blog/snyk-studio-for-qodo/ -
Snyk
@snyksec
Blog Alert 💡 AI-BOM and the Future of #aisecurity Posture Management
Securing your AI-native future requires a new model: AI Security Posture Management (AI-SPM).
🔭 Visibility
🛡️ Behavioral Risk
🔑 Governance
✅ AI-TrustOps
Read more 📕 labs.snyk.io/resources/future-aispm/
#devsecops -
Snyk
@snyksec
According to a Forrester Total Economic Impact™ of the Snyk AI Trust Platform, the findings include:
✅ 80% faster scan times
✅ 75% faster remediation
✅ 288% ROI
snyk.io/lp/total-economic-impact-snyk/
#aisecurity #devsecops -
Snyk
@snyksec
🎉 We’re excited to share that Snyk Learn has been honored with a Silver 2025 Anthem Award in the Responsible Technology: Education or Literacy Platform.
This shows how Snyk is helping developers build secure apps with interactive, AI-powered training.
snyk.io/blog/snyk-learn-anthem-awards-2025/ -
Snyk
@snyksec
⏫ Level up your AI security skills!
Join this free Live Workshop: Securing #vibecoding on November 20.
🚀 Learn how to spot and fix the security risks hidden in AI-generated code and earn 1 CPE credit through our partnership with #isc2!
Register now 👉 go.snyk.io/11-20-securing-vibe-coding-isc2.html -
Snyk
@snyksec
Snyk and @ContinueDev Partner to Embed AI-Powered Security into Every Step of the Developer Workflow! 🤝
What this means for developers:
🚀 Faster Time-to-Fix
💻 Zero-Context-Switching
🛡️ Built-in Guardrails
Read the full blog 👉 snyk.io/blog/snyk-continue-partner-integration
#devsecops #aisecurity -
Snyk
@snyksec
Does your code pass the vibe check?
Snyk Studio can help uncover:
✨ How your AI apps handle real-world threats
🔍 Hidden risks may be lurking in your workflows
🛡️ Steps to strengthen your AI security
🚀 Where you stand compared to industry benchmarks
snyk.io/fr/ai-vibe-check/ -
Snyk
@snyksec
AI systems demand a new approach to security.
🤖 Agentic AI brings complex risks tools can’t detect
🧠 Offensive testing enables validation and proof-of-exploit evidence
🚨 Red testing uncovers vulnerabilities to prioritize what truly matters
labs.snyk.io/resources/continuous-offensive-testing-ai-sy…
#snyk -
Snyk
@snyksec
Snyk Evo represents a shift toward the next stage of application security — built for the agentic, AI-native future.
🔹 Embeds security directly inside the AI development loop
🔹 Software creation is changing
🔹 Traditional methods no longer keep pace
🔗 www.forbes.com/sites/tonybradley/2025/10/22/how-snyk-evo-… -
Snyk
@snyksec
According to Forrester’s #tei report, #snyk customers achieved a 288% ROI 📈 through improved productivity and risk posture, and tool consolidation.
Key findings include:
✅ 80% faster scan times
✅ 60% faster vuln remediation
✅ AppSec consolidation
💡 snyk.io/lp/total-economic-impact-snyk -
Snyk
@snyksec
⬆️ Level up your #aisecurity skills!
Join Snyk’s free Live Workshop: Securing #vibecoding on November 20.
🚀 Learn how to spot and fix the security risks hidden in AI-generated code and earn 1 CPE credit through our partnership with #isc2!
Register now: go.snyk.io/11-20-securing-vibe-coding-isc2.html -
Snyk
@snyksec
Agentic OODA Loop: How AI and Humans Learn to Defend Together.
#aisecurity now demands the same approach as elite fighter pilots: Observe, Orient, Decide, Act. 🚀
AI won’t replace security engineers; it will elevate those who embrace this new frontier.
snyk.io/blog/agentic-ooda-loop/ -
Snyk
@snyksec
As AI coding tools become integrated into how we build software, the industry risks entering a "software security crisis.”
🔹 Developers are the 1st line of defense
🔹 Embed security directly into developer workflows
🔹 AI will be a powerful accelerator
devops.com/why-developer-discipline-matters-more-than-eve… -
Snyk
@snyksec
At #snyk, our mission has always been to empower developers to build secure applications without slowing down. ⚡
#snykcontainer is moving beyond the scan to deliver a comprehensive, end-to-end security solution built on a developer-first foundation.
snyk.io/blog/future-snyk-container -
Snyk
@snyksec
📖 Patching Detected Vulnerabilities with @FactoryAI and #snyk Studio
Discover how to revolutionize your #devsecops workflows with:
🛠️ Automated fixes
🔒 Integrated security
💪 Empowered teams
Learn more 💡 snyk.io/articles/patching-detected-vulnerabilities-with-F…
#factoryai #aisecurity #snykstudio -
Snyk
@snyksec
Snyk Studio launch is trending on @ProductHunt 🚀
Go see what real-time securing agentic code looks like:
www.producthunt.com/products/snyk/launches/snyk-studio-2
Thanks to @fmerian for hunting us!
#snyk #aisecurity #devsecops #snykstudio -
Snyk
@snyksec
Snyk and @FactoryAI Partner to Secure AI-Native Development! 🚀
⚡ Speed & Security
🧠 AI-Powered
🔒 Secure from Inception
Learn how we're redefining secure AI-driven software delivery:
snyk.io/news/snyk-factory-announce-partnership/
#snyk #factoryai #aisecurity #devsecops #snykstudio -
Snyk
@snyksec
#snyk Studio is now available! 🎉
#ai is driving new, insecure code AND massive security debt. #snykstudio solves both.
🔥 Secure at Inception: Stop new AI-generated vulnerabilities
🧠 Intelligent Remediation: Use AI power to clear existing backlogs
📖 snyk.io/blog/snyk-studio-announcement -
Snyk
@snyksec
Join this live webinar "The New Era of AppSec: Is DAST to SAST Correlation Finally Possible?"
💡 Explore advances in AI, machine learning, and data streams like eBPF.
🗓️ Thursday, Nov 13 | 11:00 AM ET
👉 go.snyk.io/new-era-of-appsec-dast-to-sast.html
#snyk #sast #dast #appsec #aisecurity -
Snyk
@snyksec
Snyk was recognized as a Leader in the 2025 #gartner ® Magic Quadrant™ for #applicationsecurity Testing — a reflection of our continued vision and ability to execute. 🌟
We’re proud to continue helping organizations build securely at scale.
snyk.io/blog/snyk-named-a-leader-in-the-2025-gartner-r-ma… -
Snyk reposted
AI Security Summit
@AISecSummit
How do we unlock the true potential of AI? By building trust into its core.
A key theme at the #aisecuritysummit, highlighted by @PeterCMcKay from @snyksec, is that adoption and speed are entirely dependent on security.
It's time to engineer AI systems we can all rely on. -
Snyk reposted
AI Security Summit
@AISecSummit
Day Two of the AI Security Summit is officially underway! 🔥
Yesterday, we defined the challenge. Today, we Confront the Chasm—taking action and forging the path toward a more secure AI future. 🏔️
Huge thanks to everyone here, ready to build. Let's do this! 💥
Follow the event: aisecuritysummit.com -
Snyk
@snyksec
AI-native apps bring massive attack surfaces, unpredictable supply chains & non-deterministic behavior—It demands an entirely new approach. That’s why we built Evo by Snyk.
Watch Manoj Nair & Randall Degges share how Evo empowers AI Security Engineers👇
www.youtube.com/watch?v=oQmKB3AyaXw -
Snyk
@snyksec
🚀Introducing Evo by Snyk: the world's first agentic AI orchestration system.
Security for AI just changed forever. Evo gives you the governance & control to confidently deploy AI workflows without compromising on risk.
Learn why we built Evo: snyk.io/blog/introducing-evo-by-snyk/ -
Snyk
@snyksec
Meet Evo by Snyk, ushering in the new era of the AI Security Engineer.
Evo is the world's first agentic security orchestration system, deploying specialized agents to neutralize novel threats with speed and precision.
Learn more: snyk.io/news/snyk-launches-evo/ -
Snyk reposted
AI Security Summit
@AISecSummit
Tomorrow, the future of AI trust will be built at the AI Security Summit in San Francisco. 🔥 🚀
We are fully booked, but you can still get involved and access the cutting-edge insights! Sign up for the waitlist now to be notified the moment session recordings and exclusive content are made available: aisecuritysummit.com -
Snyk
@snyksec
🚀 Big news! We're partnering with @cognition to bring Snyk’s security insights directly into Devin and Windsurf. Developers can efficiently secure their development workflows & address existing vulnerabilities within AI-native workflows. Learn more: snyk.io/news/snyk-and-cognition-partner-ai-accelerated-de…
-
Snyk
@snyksec
Snyk is named a Leader in the 2025 Gartner® Magic Quadrant™ for Application Security Testing!
To us, this placement validates our core belief: that security should empower developers, not slow them down.
Discover more: snyk.io/blog/snyk-named-a-leader-in-the-2025-gartner-r-ma…
#snyk #appsec #devsecops #gartner -
Snyk
@snyksec
Agentic AI is here and so are new security risks.
Our eBook, The Rise of Agentic AI, breaks down:
🚨 Emerging threats
⚡ Proactive + reactive defenses
🛡️ How to stay in control
Get the playbook for securing agenic AI.👇 snyk.io/lp/the-rise-of-agentic-ai/ -
Snyk
@snyksec
From 2 years ➡️ 2 weeks, @Labelbox erased its security debt with Snyk + @cursor_ai:
🚀 2–3 weeks to clear high-severity SAST issues
⚡ Hours of validation reduced to minutes
🔐 Security built in at inception, not patched later
See the full story: snyk.io/blog/from-two-years-to-two-weeks-how-labelbox-era… -
Snyk
@snyksec
Boston AI Week 2025 is here and we couldn’t be more excited to celebrate the incredible community and talent that make Boston a powerhouse for innovation.
Learn more here: aiweek.boston -
Snyk
@snyksec
Something big is brewing at #devseccon25… our very first AI Security Developers Challenge!
If you like fast-paced challenges and creative problem-solving, register today to stay in the loop and snag your spot before it’s gone!
snyk.io/events/devseccon/ -
Snyk
@snyksec
The future of AI security is taking center stage. 🔐
Join the AI Security Summit in San Francisco, Oct 22–23, to tackle the AI security chasm with the brightest builders, defenders, and leaders in the industry.
Register here. 👉 aisecuritysummit.com -
Snyk
@snyksec
🎉 Snyk Turns 10! 🎉
A decade of making security developer-first, simple and seamless.
Huge thank you to our team, partners, and developers who’ve built secure software, faster, with us.This media couldn't be displayed. See it on the original post. -
Snyk
@snyksec
Could your npm packages be affected by the Shai-Hulud attack?
Watch now to learn how to identify the impact and respond. ⬇️ -
Snyk
@snyksec
Zero-Day vulnerabilities don’t wait—why should you?
Recent attacks show how fast threats can strike. Snyk’s Zero-Day Vulnerability Playbook gives you tips to plan ahead, respond quickly, and stay secure.
👉 Get the playbook today: snyk.io/lp/zero-day-vulnerability-playbook-dwn-typ/ -
Snyk
@snyksec
AI is moving fast and security can’t be left behind. ⚡
AI Security Posture Management (AI-SPM) gives you visibility, governance, and protection for AI models, data, and workflows before risks turn into headlines.
Learn more on Snyk Labs: labs.snyk.io/resources/the-case-for-AISPM/ -
Snyk
@snyksec
The Snyk API + Web for AppVR integration is now live!
Teams can now see all findings in one place, leverage AI-driven analysis and vulnerability intelligence, and streamline remediation to quickly fix critical runtime vulnerabilities.
Learn more. 👉 help.probely.com/en/articles/12149799-how-to-integrate-sn… -
Snyk
@snyksec
⚠️ Malicious npm packages detected: tinycolor & ngx-bootstrap.
Our blog breaks it down, including:
🔹 Who & what’s affected
🔹 Immediate containment & remediation
🔹 Detection & triage playbook
🔹 How to spot 0-day npm malware with Snyk
Full breakdown: snyk.io/blog/embedded-malicious-code-in-tinycolor-and-ngx… -
Snyk
@snyksec
We just launched the Snyk + @CrowdStrike Falcon® Next-Gen SIEM integration!
Stop by our #falcon2025 booth to see how together we’re enabling:
⚡ Faster threat correlation
🛡️ Smarter vulnerability management
So you can detect, prioritize and respond to threats faster. -
Snyk
@snyksec
AI is moving fast. Security has to move faster. ⚡
On Oct 22, DevSecCon25 brings together the brightest minds in AI + security for a global summit you can’t miss.
👉 Register now for this free, virtual event. snyk.io/events/devseccon/ -
Snyk reposted
swyx 🔜 aie.codes
@swyx
proud to partner with Snyk to start the AI Security Summit!
our first Security track was a big success and now I’m excited to see that there’s interest to build an entire community around solving AI Security.
the truth is, AI is now both helping to solve and create more security problems than ever before. on one hand you have the vibe coded tea apps, and wilful ignorance of prompt injection and guradrails. on the other you have scaled up AI Red Teaming and Code Scanning, SBOM, and IaC scanning. so much opportunity, so much more risk. join us!
Manoj Nair
@mnair1
🔐 AI Security Summit — Oct 22-23, SF 🌁
Hack, break & secure agentic GenAI apps & vibe coding.
Hands-on hackathon, live demos, certs, credits: @swyx, @joaomdmoura (@crewAIInc), @russelljkaplan (@Cognition), @itamar_mar (@Qodo) ++.
Seats💨 🏃♂️
Register 👉 aisecuritysummit.com -
Snyk
@snyksec
Breaking down the latest npm attack. ⬇️
A phishing email compromised maintainer ~qix, letting attackers push malicious versions of popular packages. The injected code targeted crypto wallets in browsers.
We’ve got the timeline, IoCs, and what to do next: snyk.io/blog/npm-supply-chain-attack-via-open-source-main… -
Snyk
@snyksec
We're thrilled to be named a Leader in the 2025 @Forrester Wave™: SAST Solutions!
The report gave us the highest possible scores in innovation, analytics, & dev- experience and reporting—which to us proves that dev-first, AI-ready security is the future. snyk.io/blog/snyk-named-a-leader-in-the-2025-forrester-sa… -
Snyk reposted
Manoj Nair
@mnair1
This is 💯 the reality. AI-generated code is inherently insecure. You can't manually audit every line -> impacts productivity benefits.
Snyk's "Secure at Inception" is the 🗝️to making security invisible and prevent issues
See this with Cursor and more: snyk.io/solutions/secure-at-inception-for-ai/
ThePrimeagen
@ThePrimeagen
i never saw this coming
-
Snyk
@snyksec
Cut through the noise in AppSec!
Join us to see how Snyk AppRisk helps teams focus on what matters most:
✅ Prioritize high-risk threats
✅ Reduce alert fatigue
✅ Speed up developer remediation
⏱ 30 minutes is all it takes: go.snyk.io/snyk-in-30-riskbased-prioritization.html -
Snyk
@snyksec
🕵️♂️ Sneaky attacks in your #ai stack!
Malicious tool descriptions in MCP servers can trick AI agents into taking unintended actions.
Discover how to detect and defend against tool poisoning before it hits your workflows. labs.snyk.io/resources/detect-tool-poisoning-mcp-server-s… -
Snyk
@snyksec
⏳ Long scans
😩 Painful remediation
🚧 Dev friction
That’s old-school DAST.
At #optivcon 2025, Snyk’s Matt Bartley will show how AI and next-gen techniques are flipping the script on dynamic testing.
Register here: web.cvent.com/event/0e33be93-e4d6-418d-a888-9eba1283ea76/… -
Snyk
@snyksec
Another year, another spot on the Forbes #cloud100 list!
It's an honor to be recognized as one of the top cloud & AI companies — a true testament to our team's hard work & the trust of our customers.
Thanks to @BessemerVP & @Forbes for the recognition. www.forbes.com/lists/cloud100/ -
Snyk
@snyksec
Stop treating security testing like an expense.
Our new guide shows why it’s an investment with measurable ROI and how to prove it.
👉 snyk.io/lp/proving-the-payoff-security-testing-roi/ -
Snyk
@snyksec
Unpacking the Cursor + Jira MCP vulnerability with Snyk Labs. 👇
Discover how a malicious Jira ticket exploited MCP integrations in Cursor, leading to unintended data exposure.
Learn more and how to protect your systems: labs.snyk.io/resources/cursor-jira-mcp-vulnerability-expl… -
Snyk
@snyksec
Minneapolis, are you ready? 🏙
We’re headed to #optivcon Sept 10 with @Optiv to tackle app security & #cyberrisk and share how our new partnership with @Akamai is making API security seamless.
Register now. 👉 web.cvent.com/event/0e33be93-e4d6-418d-a888-9eba1283ea76/… -
Snyk
@snyksec
Prompt Injection + Classic Vulns = A NEW Threat! 🤯
Our Sec Labs team found ways to weaponize prompt injections to exploit vulnerabilities in real MCP servers.
See how an unsuspecting dev gets owned, step-by-step. 🧵Post not available here, view on X
Snyk
@snyksec
The dev asks Cursor to list their S3 buckets.
A tool call pops up. Looks normal. You click approve. Who wouldn’t? 🖱️
Snyk
@snyksec
Boom 💥
The injected prompt silently appends `;whoami` to the command.
Payload executed. Command injection triggered. Game over.
Want to see how it works? 👉 labs.snyk.io/resources/prompt-injection-mcp/ -
Snyk
@snyksec
AI-assisted development is changing the game — but traditional security struggles to keep up.
Join us for a deep dive into the risks of Vibe Coding & how to secure your AI-powered SDLC.
Save your seat 👉 go.snyk.io/securing-vibe-coding.html -
Snyk
@snyksec
We are LIVE on Youtube! Join us to see a demo of our new platform capabilities for securing AI development.
See how to gain visibility with Snyk AI-BOM and proactively mitigate AI risks: www.youtube.com/watch?v=sHQrgZ5IsTA -
Snyk
@snyksec
🚨 New threat: Persistent prompt injection with poisoned vector databases!
Discover how “RAGPoison” exposes this risk and learn how to protect your LLMs.
Read more: labs.snyk.io/resources/ragpoison-prompt-injection/
#ragpoison #promptinjection #cybersecurity -
Snyk
@snyksec
Where visionaries, security & software pros unite to shape trusted AI: @AISecSummit — brought to you by Snyk and @aiDotEngineer.
Execs or practitioners, our tailored tracks deliver hands-on workshops & practical AI security solutions.
Learn more: aisecuritysummit.com/announcements/snyk-announces-its-fou… -
Snyk
@snyksec
🕵️♂️ Can you spot the security issue?
As more devs use LLMs for coding, securing that code is critical. Snyk scans, finds & fixes vulnerabilities in both human- and AI-generated code before they become real threats.
Extra credit: Human or AI — who wrote this code? 🤔 -
Snyk
@snyksec
Not sure how to add MCP servers to Claude Code CLI?
Our very own Brian Clark breaks it down step-by-step in this quick walkthrough. It's perfect if you're just getting started or want a smoother setup.
Watch now. 👇
m.youtube.com/watch?v=qAcTPMXbfyU -
Snyk
@snyksec
We came, we launched, we leveled up at #blackhat2025.
✅ 3 product launches
✅ GenAI security deep dives
✅ Packed booth
✅ Named a @FortuneMagazine + @EvolutionEquity Top 50 Cybersecurity Company
✅ Featured in @CRN's 10 Cool New Security Products
www.crn.com/news/security/2025/10-cool-new-security-produ… -
Snyk
@snyksec
AI is accelerating but so are the risks.
Join the AI Security Summit in SF Oct 22–23 to explore how we build and secure AI systems we can trust.
From policy to prompt injection, it's where the future of AI security takes shape. aisecuritysummit.com -
Snyk
@snyksec
We just dropped a deep dive on a series of vulnerabilities the Snyk Security Labs team found in NixOS!
When chained together, they allow for a full privilege escalation from any user to root on a default installation. #nixos #linux #infosec #vulnerabilityPost not available here, view on X
Snyk
@snyksec
With arbitrary directory deletion, we targeted /tmp to race another Nix build process. This second race allowed us to hijack a chown call, letting us change the ownership of any file on the system to a user we controlled. The target? /etc/pam.d.
Snyk
@snyksec
Major credit to the NixOS, Lix, and Guix teams for their incredibly fast response and for issuing patches to fix the issues. Want to see the full exploit chain, from file descriptor exfiltration to root shell? Read the full technical deep dive on our blog: labs.snyk.io/resources/nixos-deep-dive/
-
Snyk
@snyksec
📢 Big news: We're partnering with @Akamai to solve a major challenge in app security.
Our new integration automates API discovery, letting you ingest comprehensive API inventories and schemas from Akamai directly into Snyk for one-click scanning.
snyk.io/blog/snyk-akamai-integration-api-discovery-testing/ -
Snyk
@snyksec
We’re live at #blackhat2025!
Day 1 is underway, and we’re already deep in convos about Snyk AI-BOM, MCP Server and Toxic Flow Analysis.
Come find us at booth #4351 to learn more. -
Snyk
@snyksec
How do you keep developers sharp and your code secure in the age of AI?
Start with smarter security education.
Join us for a 30-min dive into Snyk Learn:
✅ Upskill fast
✅ Secure AI code
✅ Learn in the DevSecOps flow
🔗 go.snyk.io/snyk-in-30-snyk-learn.html -
Snyk
@snyksec
The Top 50 Cybersecurity Companies of 2025 just dropped, and Snyk made the list. 🛡️
Thanks to our incredible team, our customers, and our partners at @EvolutionEquity, and @Fortune. evolutionequity.com/top50incyber/?hss_channel=lcp-104727132
#fortune50 #defendandprotect -
Snyk
@snyksec
Snyk is launching new innovations to secure AI-native dev:
🔍 AI-BOM for full MCP visibility
🧩 MCP Server for in-flow scans
🧠 Toxic Flow Analysis to detect threats like tool poisoning
Secure at inception starts now. Join us at #blackhat2025 for more. snyk.io/news/snyk-unveils-secure-at-inception/ -
Snyk
@snyksec
AI is accelerating. So are the threats.
Our new eBook, “What’s Lurking in Your AI?”, shows how to secure your models, prompts, agents, and systems—before attackers do. 🛡️
Download now: snyk.io/lp/whats-lurking-in-your-ai/ -
Snyk
@snyksec
Building with AI?
Our new guide covers how to secure AI-generated code—from automating PR checks and scanning in the IDE to enforcing conditional access.
Download the eBook now to implement guardrails without slowing down developers: snyk.io/lp/ai-code-guardrails/ -
Snyk
@snyksec
AI agents = new power, new risks.
@InvariantLabsAI just dropped Toxic Flow Analysis, the first framework to detect dangerous data flows in agentic systems (like #mcp exploits + #promptinjection).
Try the new MCP-scan tool: invariantlabs.ai/blog/toxic-flow-analysis
#aisecurity #appsec -
Snyk
@snyksec
Got insights on AI security & innovation? We want YOU to speak at #devseccon25!
Submit your talk by Aug 3 and join us on Oct 22 to shape the future of secure AI development.
👉 sessionize.com/devseccon25-the-ai-security-summit -
Snyk
@snyksec
Next stop: Silicon Valley 📍
We’re bringing the Lighthouse experience to Menlo Park for two days of honest convos on AI, security, and moving fast without losing trust.
Register to join us July 30–31: go.snyk.io/lighthouse-event-silicon-valley.html -
Snyk
@snyksec
On #artificialintelligenceappreciationday, we celebrate AI’s innovations and our commitment to keeping them secure. Because powerful innovation deserves powerful protection.
-
Snyk
@snyksec
Attackers are playing a new game — automating rule-bending with AI. MCPs can introduce insecure code that looks legit on paper. Tools like MCP-Scan from @InvariantLabsAI help catch these hidden risks in real time. Check out the CSO breakdown: www.csoonline.com/article/4015222/mcp-uses-and-risks.html
-
Snyk
@snyksec
Compliance or speed. Why not both? 🤝Snyk in 30 is happening today at 12pm ET! See how to keep up with SOC 2, PCI DSS & more without slowing dev teams down. Don’t miss it! 👉 go.snyk.io/snyk-in-30-compliance-and-reporting.html
-
Snyk
@snyksec
Think TypeScript is your security silver bullet? Think again. This blog post explores the limitations and hidden dangers. Don't get caught off guard.👇 snyk.co/uh50A #appsec
-
Snyk
@snyksec
Building with Agentic AI? Are you aware of the new security challenges emerging? 🤔 Our CIO, Manoj Nair, has you covered! Keep reading to see how Snyk + @InvariantLabsAI deliver the actionable protection you need to deploy AI-native applications securely: labs.snyk.io/resources/snyk-labs-invariant-labs/
-
Snyk
@snyksec
We’re proud to announce we’ve acquired @InvariantLabsAI to deepen our defense against agentic AI threats. Invariant Labs joins Snyk Labs to advance real-time protection for AI-native apps. One platform. Full AI security. Learn more: snyk.io/news/snyk-acquires-invariant-labs-to-accelerate-a…
-
Snyk
@snyksec
AI agents are everywhere — but they don't always work together.
@Google's new Agent2Agent Protocol aims to fix that.
In this must-read post, @SonyaMoisset breaks down what it means for the future of #ai interoperability. snyk.co/uiuBq -
Snyk
@snyksec
💡 Data that doesn’t just report — it helps you decide.
With the latest Snyk Analytics, AppSec leaders can track shift-left adoption, identify risks faster, and simplify compliance reporting. All in one unified view.
Data-driven #appsec starts here. ▶️ snyk.co/uiuf7 -
Snyk
@snyksec
We're thrilled to congratulate Snyk CEO, Peter McKay, on being named to @BostonGlobe's annual Tech Power Players list for 2025!
www.bostonglobe.com/business/tech-power-players/2025/ #globaltech50 -
Snyk
@snyksec
#ai isn’t replacing developers — it’s redefining them.
Gartner predicts 80% of engineering teams will need to upskill by 2027. So how can devs stay ahead?
We break it down in our latest blog. 👇 snyk.co/uiuBj -
Snyk
@snyksec
#shadowai: The hidden threat you can't afford to ignore. 👻 Our new blog reveals 5 ways unapproved #ai tools silently jeopardize your org's data & reputation. Read now. snyk.co/uio6l
-
Snyk
@snyksec
Is Symbolic #ai the future of code security? 🤔 Our latest blog post explores how Snyk Code's #symbolicai engine provides superior vulnerability detection. Check it out! snyk.co/uihry
-
Snyk
@snyksec
👀 Visibility. 📊 Insights. ✅ Compliance.
Snyk Analytics just leveled up. Learn how new features help you scale AppSec, track shift-left adoption, and prove AI Trust. Read now👇 snyk.co/uiuf7 -
Snyk
@snyksec
🚨 FinServ #security alert! 🚨 Did you know #genai coding assistants could expose your applications to cyber threats? Watch Snyk Code in action uncovering vulnerabilities in a real-world banking app. On-demand webinar here: snyk.co/uioAJ
-
Snyk
@snyksec
We're thrilled to be at #awssummit DC 2025! Swing by booth 354 to see Snyk in action with live demos and chat with our experts.
-
Snyk reposted
Ed Sim
@edsim
Want to code insanely fast and stay secure?
Time to level up with AI powered secure code scanning from @snyksec available as a one click install from @cursor_ai MCP directory
Instantly scan raw code, catch vulnerabilities as they're born, and all without needing a build.
Incredibly accurate, @snyksec harnesses a vast data set of code + vulnerabilities growing rapidly with over 5 billion tests completed in just last six months.
Get it now! docs.cursor.com/tools -
Snyk
@snyksec
Are your cloud-based #ai Large Language Models at risk? Our latest article breaks down #llmjacking – a sneaky attack exploiting stolen credentials. Find out the potential damage and how to defend against it: snyk.co/uigIi
-
Snyk
@snyksec
Can you trust #ai to write secure code? 🤔 We put #chatgpt to the test by asking it to build a Node.js file upload API. The results? A security vulnerability. Read the deep dive now. snyk.io/articles/vibe-coding-a-node-js-file-upload-api-re…
-
Snyk
@snyksec
The future of 3D design is here! 🤯 With Model Context Protocol (#mcp), #ai assistants can now directly manipulate 3D modeling software, even supporting BIM!
Read our latest blog to explore 6 MCP servers that are revolutionizing creative workflows: snyk.io/articles/6-mcp-servers-for-using-ai-to-generate-3… -
Snyk
@snyksec
With the rise of GenAI, security risks are on the rise. Snyk Analytics offers the most powerful solution for AppSec leaders seeking to gain the visibility needed to address threats. #appsec #security #ai snyk.co/uhCuu
-
Snyk
@snyksec
LLMs can now act on data – is your security ready? The rise of MCP creates new attack surfaces. Snyk contributed 17 vital requirements to OWASP's LLM SVS to secure your AI agents. Don't build blind! Learn from #snyklabs how to manage this risk. snyk.co/uircV
-
Snyk
@snyksec
Snyk's heading to the @Gartner_inc Security & Risk Management Summit, and we're bringing some exciting demos with us. Stop by for a chat, grab some swag, and check out our speaking session.
Book a meeting with our team here: snyk.co/uithF -
Snyk
@snyksec
Vibe coding is revolutionizing dev speed, but it doesn't mean it's exempt from vulns that lurk beneath #ai-generated code. CTO Danny Allan warns developers to stay vigilant about improper permissions & injection attacks when vibe coding via @thenewstack. thenewstack.io/vibing-dangerously-the-hidden-risks-of-ai-…
-
Snyk
@snyksec
AI adoption is skyrocketing, and so is the pressure to comply. 🚀 Is your enterprise ready? Our new article breaks down AI compliance, why it's crucial, and how to get started now. Don't get left behind! snyk.io/articles/how-to-get-started-with-ai-compliance-an…
-
Snyk
@snyksec
Think TypeScript is your security silver bullet? Think again. This blog post explores the limitations and hidden dangers. Don't get caught off guard.👇 snyk.co/uh50A #appsec
-
Snyk
@snyksec
How can we harness Agentic AI to boost security without introducing new risks? 🤔 That's exactly what we're tackling at Snyk. Learn more from Rudy Lai in this recent convo with @InfoSecurityMag. www.infosecurity-magazine.com/news/infosec2025-agentic-ai…
-
Snyk
@snyksec
HUGE news! 🎉 Snyk for Government has achieved FedRAMP Moderate Authorization!
U.S. agencies can now confidently use Snyk to build secure applications, meeting the highest federal security standards. Learn more. snyk.co/uis8p -
Snyk
@snyksec
From Silicon Valley to Times Square and beyond — the Snyk AI Trust Platform made its global debut in style! 🚀🌍
Over the past week, we’ve been ~everywhere~ lighting up screens, stages, and smiles as we unveiled our bold new vision for secure development in the AI era.
Snyk
@snyksec
Thank you to our amazing global community for making this launch unforgettable. Your excitement, insights, and support are what fuel us as we empower developers to build securely and confidently in the age of #ai.
Snyk
@snyksec
Didn't catch all the action live? No problem! Watch the on-demand recording of #snyklaunch 2025 to uncover the promise of #aitrust with Snyk! snyk.co/uikvw
-
Snyk
@snyksec
Ever feel like critical knowledge gets lost in Slack threads? 😩 At Snyk, we're leveraging RAG to transform our internal Slack discussions into structured, accessible insights for faster Q&A. Learn how: snyk.io/articles/from-slack-threads-to-structured-knowled…
-
Snyk
@snyksec
Feeling buried under a mountain of vulnerabilities? 😩 Our new ebook offers a lifeline! Discover how to build a risk-based #appsec program that cuts through the noise and focuses on what truly matters. snyk.co/uioBR
-
Snyk
@snyksec
Prompt Injection: The silent saboteur of your AI systems. 🤫 Learn how these attacks manipulate LLMs and the critical risks involved in our new article. Don't let your AI be a weak link! snyk.io/articles/understanding-prompt-injection-technique…
-
Snyk
@snyksec
Developers, code with confidence! ✨ Snyk now supports Model Context Protocol (#mcp), embedding real-time security insights directly into your #ai coding workflow. Don't choose between speed and security – have it all.
Get the details. snyk.co/uisuk -
Snyk
@snyksec
Who’s writing your code—your team or #ai? Join our 30-min live session to explore Snyk’s new AI Trust Platform, see how to uncover code assets, prioritize risks, and create a developer-first security experience. Stay secure without slowing down. snyk.co/uissk
-
Snyk
@snyksec
UI/UX Engineers, listen up! 🚀 AI is transforming design. Check out 14 open-source #mcp servers bridging the gap between #ai assistants & your favorite design tools. Figma, Illustrator, & more! Dive into the future of AI-assisted design. 👇 snyk.co/uisaQ
-
Snyk
@snyksec
Boost your dev team's secure coding skills! 🚀
Snyk's new Learning Management Add-on helps you accelerate secure development & meet compliance. Shift security left with Snyk Learn!
Discover how. snyk.co/uisaf -
Snyk
@snyksec
Innovate fearlessly in the age of #ai 🚀 Snyk is LIVE at #infoseceurope 2025 in London!
Head to Booth B#58 for an exclusive look at our #aitrust Platform and see how we're securing the future of AI development. See you soon!
@Infosecurity -
Snyk reposted
Ed Sim
@edsim
You can finally code securely at the speed of AI w/@snyksec
Scan raw code w/out a build, flag security issues as code is generated w/accuracy - trained on huge data set of code/vulns - last 12 mos did >5B+ tests alone 📈
Here's @mnair1 demoing MCP call from @windsurf_ai
Find in your fave IDE, integrated with Gemini Code assist, and elsewhere w/Snyk MCP Server
Huge unlock for the enterprise 🔥! -
Snyk
@snyksec
How secure is your open-source #llm, really? 🤔
#snyklabs is pulling back the curtain with the #genai Model Risk Registry. Structured, security-focused profiles to help you avoid prompt injection & data leakage.
Stop guessing, start knowing. labs.snyk.io/resources/snyk-genai-model-risk-registry/ -
Snyk
@snyksec
The future of code is #ai-generated, and nearly half of it is insecure. Discover how Snyk's new AI Trust Platform helps you innovate at full speed while building confidence in your software's security. Read more: snyk.co/uirUf
-
Snyk
@snyksec
Snyk is excited to sponsor #snowflakesummit 2025! Join us at Booth 2508 for live demos and real-world #appsec use cases.
-
Snyk
@snyksec
Unlock AI innovation securely with the Snyk #aitrust Platform! 💪 Get visibility, automated fixes, and strong governance for your #ai development. Fast, accurate, and comprehensive security powered by DeepCode AI. snyk.co/uircV
-
Snyk
@snyksec
LLMs can now act on data – is your security ready? The rise of MCP creates new attack surfaces. Snyk contributed 17 vital requirements to OWASP's LLM SVS to secure your AI agents. Don't build blind! Learn from #snyklabs how to manage this risk. snyk.co/uircV
-
Snyk
@snyksec
AI is supercharging software development, but can we truly trust the code it creates? @Snyk's CTO, Danny Allan, sat down with @Forbes to discuss why "trust isn't a bonus—it’s a must" in the age of #ai. Learn about the "perfect storm" & new security risks. www.forbes.com/sites/tonybradley/2025/05/28/establishing-…
-
Snyk
@snyksec
Introducing #snyklabs, our new innovation & research arm to tackle the complex security challenges of #ai-native apps.
From explorations into AI-SPM & AI BoM to collaborating on new LLM standards, Snyk Labs is where the future of AI security is built. labs.snyk.io -
Snyk reposted
Danny Allan
@dannyallan5
The largest launch in @snyksec history. Truly incredible milestone! www.linkedin.com/pulse/letting-history-repeat-itself-ai-e…
-
Snyk
@snyksec
Prepare for a paradigm shift! Snyk just unveiled the Snyk AI Trust Platform, fundamentally changing how organizations secure #ai-driven innovation. Don't just adapt to the AI era, conquer it – securely.
Discover the future of #aitrust: snyk.co/uiqNz
Snyk
@snyksec
Want to learn more? Join us today at 10 AM EST for our #snyklaunch event, where we'll give you an exclusive first look at the AI Trust Platform! Save your spot: snyk.co/uikvy
-
Snyk
@snyksec
AI adoption is skyrocketing, and so is the pressure to comply. 🚀 Is your enterprise ready? Our new article breaks down AI compliance, why it's crucial, and how to get started now. Don't get left behind! snyk.io/articles/how-to-get-started-with-ai-compliance-an…
-
Snyk
@snyksec
#ai is supercharging source code analysis! 🚀 But how do you wield this power safely, especially for critical systems? Our new article dives into AI for code analysis, top tools, and how to apply it securely. snyk.io/articles/navigating-ai-for-source-code-analysis/
-
Snyk
@snyksec
Level up your coding! 🚀
Discover the top 5 #mcp Servers that are enhancing the software development experience by bridging the context gap for LLMs and enabling powerful actions. Read more from @liran_tal. snyk.co/uinNC -
Snyk
@snyksec
LAST CALL! Unlock #ai's potential in software development with trust built on security. Join #snyklaunch 2025 to see how we're enabling secure AI adoption, scaling security for AI code, and evolving developer workflows. snyk.co/uikvy
-
Snyk
@snyksec
Future-proof your development! 💡 At #snyklaunch, CEO Peter McKay will share critical insights on navigating the AI landscape for secure, accelerated innovation. Register now to secure your spot! snyk.co/uikvy
-
Snyk
@snyksec
❄️ See how @SnowflakeDB Cortex #ai + Snyk Analytics unlock powerful security insights across your SDLC.
-
Snyk
@snyksec
A single vulnerability can be costly. 😬 Our latest article dives into building a culture of secure coding, not just implementing tools. Get actionable lessons to protect your business and boost developer collaboration: snyk.co/uioA2
-
Snyk
@snyksec
🚨 FinServ #security alert! 🚨 Did you know #genai coding assistants could expose your applications to cyber threats? Watch Snyk Code in action uncovering vulnerabilities in a real-world banking app. On-demand webinar here: snyk.co/uioAJ
-
Snyk
@snyksec
Unlock #ai's potential in software development with trust built on security. Join #snyklaunch 2025 to see how we're enabling secure AI adoption, scaling security for AI code, and evolving developer workflows. snyk.co/uikvy
-
Snyk
@snyksec
AI is supercharging asset management! 🚀 But don't overlook the new security risks.
Our new blog post covers key functions, challenges, & how to secure your #ai models. snyk.io/articles/ai-asset-management-key-functions-challe… -
Snyk
@snyksec
Think your #ai sees reality? Look closer. This image shows how tiny, imperceptible changes can completely fool AI. Our latest article dives into the dangerous world of adversarial attacks and what it means for AI security. Don't miss it. snyk.co/uiihO
-
Snyk
@snyksec
Learn how Snyk helps secure development at #ai speed, streamlining #appsec governance as both development and security workflows continue to be AI-powered. Register now for #snyklaunch: snyk.co/uikvy
-
Snyk
@snyksec
#ai workloads are booming! 🤯 But are your chips ready? Snyk's new blog reveals how AI chip design fuels next-gen ML & GenAI.
Why it matters for your apps: efficiency, reliability, and security.snyk.co/uip0x -
Snyk
@snyksec
#ai moves fast. Threats move faster.
Secure your future at the #snyklaunch, May 28th, 10 AM EST. Register now! snyk.co/uikvy -
Snyk
@snyksec
Generative AI is a game-changer, but are you ready for the security risks it brings? 😬 Our latest blog post by Stephen Thoemmes breaks down the top 12 #ai security risks you can't ignore. Don't get caught off guard! snyk.io/articles/top-12-ai-security-risks-you-cant-ignore/
-
Snyk
@snyksec
The future of 3D design is here! 🤯 With Model Context Protocol (#mcp), #ai assistants can now directly manipulate 3D modeling software, even supporting BIM!
Read our latest blog to explore 6 MCP servers that are revolutionizing creative workflows: snyk.io/articles/6-mcp-servers-for-using-ai-to-generate-3… -
Snyk
@snyksec
U.S. CISOs are voicing strong concerns about national cyber readiness. 🚨 Our recent survey reveals critical insights after the new administration's first 100 days, with #ai as a major factor. Get the full story. snyk.co/uipNh
-
Snyk
@snyksec
❄️ See how @SnowflakeDB Cortex #ai + Snyk Analytics unlock powerful security insights across your SDLC.
-
Snyk
@snyksec
Protect your AI models from attacks. 🛡️ Read our latest research on vulnerabilities in deep learning file formats. #aisecurity #cyberthreat snyk.co/uhMze
-
Snyk
@snyksec
#shadowai: The hidden threat you can't afford to ignore. 👻 Our new blog reveals 5 ways unapproved #ai tools silently jeopardize your org's data & reputation. Read now. snyk.co/uio6l
-
Snyk
@snyksec
Future-proof your development! 💡 At #snyklaunch, CEO Peter McKay will share critical insights on navigating the AI landscape for secure, accelerated innovation. Register now to secure your spot! snyk.co/uikvy
-
Snyk reposted
Ben Sadeghipour
@NahamSec
⏳ We’re just 48 hours away from the return of #nahamcon2025!
Get ready for two full days of talks on:
🤖 Hacking AI
🛠️ Hacking with AI
🔍 Recon
🌐 Web Hacking
💸 Bug Bounty & more
📆 May 22-23
Watch live on twitch.tv/NahamSec -
Snyk
@snyksec
Is #ai truly revolutionizing secure coding? @_clarkio's initial examination of #googlegemini 2.5 Pro reveals some persistent issues, such as the use of deprecated csurf & unnecessary dotenv calls. Dive into the complete analysis on our YouTube channel: www.youtube.com/watch?v=3gJPd6V90nQ
-
Snyk
@snyksec
Tired of endless vulnerability alerts? 😩 @liran_tal dives into how Snyk Delta Findings can help developers break free from vulnerability fatigue by focusing on what truly matters. Read more and reclaim your time! snyk.co/uioCi
-
Snyk
@snyksec
Feeling buried under a mountain of vulnerabilities? 😩 Our new ebook offers a lifeline! Discover how to build a risk-based #appsec program that cuts through the noise and focuses on what truly matters. snyk.co/uioBR
-
Snyk
@snyksec
Speed vs. #security? You don't have to choose! Learn how to empower your developers to build resilient software by embedding security into your team's DNA. snyk.co/uioA2
-
Snyk
@snyksec
🔒 Discover how to secure financial apps without slowing innovation! Watch our on-demand webinar to see Snyk #code and Snyk #opensource catch vulnerabilities in real time and learn how to manage risks from #ai-driven coding assistants. Watch now! snyk.co/uioAJ
-
Snyk
@snyksec
Accelerate your development with #ai, not your risks. Snyk's AI-enabled solution helps you secure your code and AI apps. Learn more at #snyklaunch. Register now! snyk.co/uikvy
-
Snyk
@snyksec
Are you confident in your AI's #security and trustworthiness? 🤔 Our new blog dives deep into #ai risk assessment, revealing the crucial steps and tools for mitigation. A must-read for any enterprise leveraging AI. 👇snyk.co/uioB6
-
Snyk
@snyksec
Struggling with Cyber Resilience Act compliance? Our cheat sheet simplifies secure-by-design, SBOMs, and more. See how Snyk helps meet #cra requirements with ease. Download now! snyk.co/uioAD
-
Snyk
@snyksec
Security a roadblock? Not anymore! Learn how to break down silos and build security into your development pipeline with our guide to DevSecOps Automation. Unlock faster, safer releases. Read now. snyk.io/blog/devsecops-automation-framework/
-
Snyk
@snyksec
#ai moves fast. Threats move faster.
Secure your future at the #snyklaunch, May 28th, 10 AM EST. Register now! snyk.co/uikvy -
Snyk
@snyksec
Heard about #mcp in #ai but not sure what it is? 🤔 @liran_tal has you covered! Learn how Anthropic's Model Context Protocol is revolutionizing what LLMs can do in this recent blog. snyk.co/uiofO
-
Snyk
@snyksec
Level up your coding! 🚀
Discover the top 5 #mcp Servers that are enhancing the software development experience by bridging the context gap for LLMs and enabling powerful actions. Read more from @liran_tal. snyk.co/uinNC -
Snyk
@snyksec
Can you trust #ai to write secure code? 🤔 We put #chatgpt to the test by asking it to build a Node.js file upload API. The results? A security vulnerability. Read the deep dive now. snyk.io/articles/vibe-coding-a-node-js-file-upload-api-re…
-
Snyk
@snyksec
🤖🔐 The future of cybersecurity is here, and #ai is at the forefront! Catch up on Snyk's key takeaways from #rsac2025, where we explored the impact of generative AI on software security. Read our recap: snyk.io/blog/snyk-rsac-2025/
-
Snyk
@snyksec
Could your AI chatbot be weaponized against you? 🤯 @liran_tal latest deep dive reveals how prompt injection can trick #llms into generating SQL injection payloads. A must-read for anyone building or using #ai in their applications. snyk.co/uimhv
-
Snyk
@snyksec
Join Snyk at #infosec2025! We’ll be showcasing our dev-first security platform with live demos, AI-focused insights, & swag. Stop by booth #b58 to see how we can help you secure your code, dependencies, containers, & cloud without slowing down development. snyk.co/uinyt
-
Snyk
@snyksec
Build a security-first culture that scales! Join Snyk's expert session this Thursday 11 AM ET with @SonyaMoisset. Learn to empower devs, implement tools, and build scalable security. #security Register now! snyk.co/uikXv
-
Snyk
@snyksec
Unlock #ai's potential in software development with trust built on security. Join #snyklaunch 2025 to see how we're enabling secure AI adoption, scaling security for AI code, and evolving developer workflows. snyk.co/uikvy
-
Snyk
@snyksec
Tired of juggling disconnected product management tools? 🤯 Discover how Model Context Protocol (#mcp) is like USB for AI, connecting LLMs to 7 key servers for smoother workflows! 🚀 snyk.io/articles/7-mcp-servers-for-product-managers/
-
Snyk
@snyksec
Navigating the risks of #ai adoption? 🤔 Our recent article breaks down essential AI risk assessment strategies, best practices, and tools. Learn how to build secure and responsible AI systems. Read now: snyk.co/uimNX
-
Snyk
@snyksec
Snyk strengthens partner commitment with an evolved Global Channel & GSI Program focused on AI Security! We're moving to strategic collaborations, offering enhanced GTM programs, discounts & more. Let's build the future of AI Security together! 🤝 snyk.co/uimhz
-
Snyk
@snyksec
Modern app development, especially with AI, demands robust security. Learn how Snyk API & Web simplifies application security testing with AI-powered tools, integrating Probely's tech for comprehensive DAST. siliconangle.com/2025/04/22/snyk-api-web-simplifies-app-s…
via @SiliconAngle -
Snyk
@snyksec
Could your AI chatbot be weaponized against you? 🤯 @liran_tal latest deep dive reveals how prompt injection can trick #llms into generating SQL injection payloads. A must-read for anyone building or using #ai in their applications. snyk.co/uimhv
-
Snyk
@snyksec
We're live in Vegas for @ServiceNow #knowledge25! Visit us at booth AIS13 in the AI Innovation Zone to see how we're helping organizations secure AI-generated code without slowing innovation - plus, don't miss our session on #ai trust in action on May 8 at 1pm!
-
Snyk reposted
Sumit Dhawan
@sumit_dhawan
There is nothing quite like #rsac week. It brought great conversations with customers, partners, and industry leaders—I'm proud of how the @Proofpoint team showed up.
We made the most of the moment, hosting hundreds of focused briefings that demonstrated the strength of our unified #humancentricsecurity platform. On the expo floor, thousands of conference attendees discovered firsthand the power of our comprehensive solutions, integrative architecture, and our platform’s agentic AI readiness.
I had the privilege of sharing my thoughts on the intersections of the new U.S. administration, cybersecurity, AI and policy alongside Sam Sabin, Nicole Perlroth, Jen Easterly and Peter McKay at a panel hosted by @snyksec. I am hopeful that the progress to strengthen our industry’s collaboration with the public sector will continue. Doing so will provide greater visibility, bridge gaps, and ease CISO uncertainties.
The team and I also discussed Proofpoint’s momentum, growth strategy, innovations, and partnerships with the media. Stand-out moments included a feature in @CRN's 20 Coolest New Cybersecurity Products at RSAC 2025 and receiving recognition in 4 categories at the 2025 Global InfoSec Awards by @CyberDefenseMag.
Proofpoint is now among the top five standalone cybersecurity software companies. By delivering unmatched value and innovating with purpose, we will continue to define human-centric security. -
Snyk reposted
Infosecurity Europe
@Infosecurity
Join @snyksec at #infosec2025, June 3–5 at ExCel London!
Visit booth #b58 for live AI-powered demos, exclusive swag and to see how Snyk helps secure apps and infrastructure with developer-first security. -
Snyk
@snyksec
Build confidently in the age of AI. Learn how to secure #ai-generated code at #snyklaunch on May 28th. Don't miss out! Register: snyk.co/uikvy
#devsecops #aisecurity -
Snyk
@snyksec
Unlock the power of #chatgpt for your enterprise, securely. 💪 Our expert guide breaks down the essential #aisecurity measures you need to know. Don't miss out. snyk.co/uilUx
-
Snyk reposted
Liran Tal
@liran_tal
ahh yes, the way I like to start my morning... thanks @snyksec ;-)
-
Snyk
@snyksec
Secure your AI-generated code at speed! 🚀 Discover the powerful partnership between Snyk and @ServiceNow, bringing #ai-powered security to your development workflow. Read the blog & find us at #knowledge25 to learn more. snyk.co/uilUo
-
Snyk
@snyksec
LLMs are powerful, but safety is key! @BrianVerm explains the importance of LLM guardrails for reliable and secure #ai interactions. Read it now. 👇 snyk.io/articles/ensuring-safe-and-reliable-ai-interactio…
-
Snyk
@snyksec
Don't let open source risks catch you off guard! 🛡️ Snyk Learn's new path covers the #owasp Top 10. Secure your code today: snyk.co/uilLc #cybersecurity #devops n
-
Snyk
@snyksec
Empower your dev teams with a Security Champions program! Join @Snyk's webinar on May 15th (11 AM ET) with @SonyaMoisset. Learn to build a scalable #appsec culture & earn CPE credits. Register now! snyk.co/uikXv
-
Snyk
@snyksec
Heading to @ServiceNow #knowledge25 in Las Vegas? Visit us at booth AIS13 in the AI Innovation Zone to see how we're helping organizations secure AI-generated code without slowing innovation. Don't miss our session on #ai trust in action on May 8 at 1pm!
-
Snyk reposted
TCM Security
@TCMSecurity
Accelerate your company’s security culture with this FREE session from the team at @snyksec! You can empower your internal stakeholders by developing a Security Champions program. Learn how to do it the right way on May 15th.
Discover what success looks like, how to tap into the right leadership to drive the program, and how to set up a continuous feedback loop.
Build security into your company’s DNA. And if you’re an ISC(2) member, you’ll receive 1 CPE credit for attending live. Don’t lose out on a fantastic opportunity; register here: www.tcm.rocks/snyk-champ -
Snyk
@snyksec
TODAY! 🚨
Empowering conversations at #rsac! Join Snyk for a luncheon celebrating women leaders in #cybersecurity. Gain insights, connect with peers, and ignite your path. RSVP today. snyk.co/uikai -
Snyk
@snyksec
Want to build a team of champions who live #security from day one?
💬 Join our upcoming workshop to learn how to:
• Recruit the right champions
• Get buy-in from devs & leadership
• Track what matters
Register now to save your spot: snyk.co/uikXv -
Snyk
@snyksec
ICYMI 👉 Last week, we launched Snyk API & Web, an innovative DAST solution designed to meet the growing demands of modern and increasingly #ai-powered software development. @SiliconANGLE shares more about the launch. siliconangle.com/2025/04/22/snyk-api-web-simplifies-app-s…
-
Snyk reposted
Baptiste Robert
@fs0c131y
Amazing panel organised by @snyksec with the great @CISAJen, @nicoleperlroth, @sumit_dhawan, Peter McKay and Sam Sabin:
“The First 100 Days: How AI, Policy & Cybersecurity Collide Under the New Administration” -
Snyk
@snyksec
Securing #ai systems is a shared responsibility. Snyk is proud to join the Coalition for Secure AI (#cosai) to collaborate with industry leaders on building practical frameworks for #aisecurity. Learn more. snyk.co/uikVN
-
Snyk
@snyksec
TODAY AT #rsac! New US admin's first 100 days highlight #ai & #cybersecurity as key policy & industry concerns. How will early decisions shape our security and innovation future? Get expert insights at our panel moderated by @Axios' @samsabin923. snyk.co/uigF1
-
Snyk
@snyksec
Don't let the AI heat get to you! 🔥 Visit Snyk at #rsac 2025, Booth #s-1127 to see how we secure your apps in the age of #ai. Plus, join our "Don't sweat security" panel & other great events!
This media couldn't be displayed. See it on the original post. -
Snyk
@snyksec
Sake and security? It's an art form. Join Snyk at #rsac for a unique tasting experience with Purple Cork and sake sommelier Paul Chung. Let's talk #ai cybersecurity over exquisite sake. Limited spots available - register today: snyk.co/uiiHk
-
Snyk
@snyksec
Think your #ai sees reality? Look closer. This image shows how tiny, imperceptible changes can completely fool AI. Our latest article dives into the dangerous world of adversarial attacks and what it means for AI security. Don't miss it. snyk.co/uiihO
-
Snyk
@snyksec
Sake and security? It's an art form. Join Snyk at #rsac for a unique tasting experience with Purple Cork and sake sommelier Paul Chung. Let's talk #ai cybersecurity over exquisite sake. Limited spots available - register today: snyk.co/uiiHk
-
Snyk
@snyksec
Feeling the heat from #ai security? Join the flaming convo with Snyk & @seanseaevans from #hotones at #rsac. Don't get burnt – secure your spot before they're all gone!🔥 snyk.co/uidv6
-
Snyk
@snyksec
AI got you sweating? 😅 Snyk & @seanseaevans (#hotones) are bringing the heat to #rsac! Join us for a spicy panel on navigating security in the age of #ai. 🔥
Limited spots are available - register now! snyk.co/uidv6 -
Snyk
@snyksec
Empowering conversations at #rsac! Join Snyk for a luncheon celebrating women leaders in #cybersecurity. Gain insights, connect with peers, and ignite your path. Lunch provided. RSVP today. snyk.co/uikai
-
Snyk
@snyksec
Unveiling the mysteries of ComfyUI Custom Node Vulnerabilities with our latest blog post! 🕵️♂️ Dive deeper into plugin ecosystem security with our seclabs team's in-depth exploration. Don't miss it! ⚡ #appsec #aisecurity #comfyui More here: snyk.co/uhPWq
-
Snyk
@snyksec
New US admin's first 100 days highlight #ai & #cybersecurity as key policy & industry concerns. How will early decisions shape our security and innovation future? Get expert insights at our panel during #rsac2025 - moderated by @Axios' @samsabin923. snyk.co/uigF1
-
Snyk
@snyksec
🚀 Snyk achieves #fedramp Moderate Authorization! Delivering best-in-class developer security to US federal agencies, enabling faster & more secure software development. Learn more. snyk.co/uijxx
-
Snyk
@snyksec
Exciting news! Snyk has partnered with Nova8 to bring secure development to more teams across Latin America. Read how this collaboration will empower developers and security teams to build secure applications faster.
➡️ snyk.co/uiiCR -
Snyk
@snyksec
LIVE HACK TODAY! Witness AI-assisted coding create financial app vulnerabilities. See Snyk Code and Snyk Open Source in action, stopping issues like Node.js prototype pollution. Don't miss out - register now! snyk.co/uiiij
-
Snyk
@snyksec
Vibe coding is revolutionizing dev speed, but it doesn't mean it's exempt from vulns that lurk beneath #ai-generated code. CTO Danny Allan warns developers to stay vigilant about improper permissions & injection attacks when vibe coding via @thenewstack. thenewstack.io/vibing-dangerously-the-hidden-risks-of-ai-…
-
Snyk
@snyksec
🤯 Watch how easily #ai vision can be deceived! Subtle image changes, like the ones in this demo, can cause serious misclassifications. Our new article explores the threat of adversarial AI and how to secure your systems. Read more: snyk.co/uiihO
-
Snyk
@snyksec
Building real-world #ai apps? Learn why RAG (Retrieval-Augmented Generation) is crucial for moving beyond demos to production-ready systems. Understand what it is and how to secure it in this insightful blog post by @BrianVerm! snyk.co/uijwT
-
Snyk
@snyksec
How do autonomous cars see? How does the cloud train massive AI models? The answer lies in AI accelerators! 🤔 Our new blog breaks down this crucial tech. Read more by Stephen Thoemmes. snyk.co/uijwJ
-
Snyk
@snyksec
Ever wondered how intelligent #ai has become? 🤔 In this YouTube Short, Snyk's Micah Silverman puts #claudeai to the ultimate test in a board game challenge! Witness Claude analyze the game & even suggest a winning strategy. 🤯
Watch the full video here: www.youtube.com/watch?v=ksIRa-qWCqQ -
Snyk
@snyksec
Protecting the #ai-powered future of software! Snyk API & Web is here, integrating Probely's cutting-edge DAST to secure APIs – the critical link for LLMs. This unified platform is a game-changer for #appsec. Read more 👇 snyk.co/uiiSL
-
Snyk
@snyksec
🚨 92% of orgs say devs are using #genai for code. But is it secure? 🤔 Our latest article with ESG reveals the hidden security challenges of GenAI adoption for AppSec teams. Don't get caught off guard! Read now. snyk.co/uiiUV
-
Snyk
@snyksec
🤔 Ever wondered how #ai models could go beyond just text? Dive into the game-changing Model Context Protocol (MCP) from Anthropic and see how it's unlocking new possibilities for LLMs! Read more on the Snyk blog. snyk.io/articles/what-is-mcp-in-ai-everything-you-wanted-…
-
Snyk
@snyksec
Secure your financial apps faster! 🛡️ Join our live hack to see how #ai can introduce vulnerabilities & how Snyk helps you catch them early. snyk.co/uiiij #finserv
-
Snyk
@snyksec
Explore the future of secure financial app development with us! Witness a live hacking session demonstrating the prowess of Snyk Code & Snyk Open Source in detecting vulnerabilities. Unmask the unseen dangers of #ai-assisted coding. Register now! snyk.co/uiiij
-
Snyk
@snyksec
Sake and security? It's an art form. Join Snyk at #rsac for a unique tasting experience with Purple Cork and sake sommelier Paul Chung. Let's talk #ai cybersecurity over exquisite sake. Limited spots available - register today: snyk.co/uiiHk
-
Snyk reposted
Liran Tal
@liran_tal
AI fluff and buzz is all around
but @snyksec had been doing machine learning and symbolic AI since pre ChatGPT hype. If you're curious to learn how vulnerable code detection works here is my write-up with a lot of hands-on and practical examples: snyk.io/blog/solving-security-challenges-with-snyk-code-a… -
Snyk
@snyksec
Exciting news! Snyk has partnered with Nova8 to bring secure development to more teams across Latin America. Read how this collaboration will empower developers and security teams to build secure applications faster.
➡️ snyk.co/uiiCR -
Snyk
@snyksec
🔓 Discover how to stay ahead of security risks in financial app development! Join our live hacking session to see Snyk Code & Snyk Open Source catch vulnerabilities in real-time and uncover the hidden risks of #ai-assisted coding. Register now! snyk.co/uiiij
-
Snyk
@snyksec
Think your #ai sees reality? Look closer. This image shows how tiny, imperceptible changes can completely fool AI. Our latest article dives into the dangerous world of adversarial attacks and what it means for AI security. Don't miss it. snyk.co/uiihO
-
Snyk
@snyksec
AI got you sweating? 😅 Snyk & @seanseaevans (#hotones) are bringing the heat to #rsac! Join us for a spicy panel on navigating security in the age of #ai. 🔥
Limited spots are available - register now! snyk.co/uidv6 -
Snyk
@snyksec
#ai-powered UI/UX is here! 🤖 Check out 14 open-source MCP servers that are changing the game. Figma automation? Illustrator scripting? It's all happening. Dive in: snyk.co/uihQe
-
Snyk
@snyksec
Beat vulnerabilities at their own game! Discover how to embed #security in your code from the start. Our team sheds light on building a culture of secure coding in our dynamic development world. Level up your software resilience without compromising speed! snyk.co/uicz8
-
Snyk
@snyksec
We're thrilled to announce that Snyk has been named the 2025 #googlecloudpartnerawards winner in Technology! 🎉 snyk.co/uigfM @googlecloud @gcloudpartners
-
Snyk
@snyksec
"WHAT IN TARNATION?! You've got a memory leak the size of Texas!"😤
Introducing Greybeard CLI: security insights delivered with the grumpiness of your favorite coding curmudgeon.
Let Greybeard give your code the roast it needs: snyk.co/uiezy -
Snyk
@snyksec
Are you confident your #apps are using strong cryptographic algorithms? Many legacy systems still rely on outdated and vulnerable methods like MD5. Learn how Snyk Code can help you identify and fix these issues in a new blog. snyk.co/uh9Tj
-
Snyk
@snyksec
AI got you sweating? 😅 Snyk & @seanseaevans (#hotones) are bringing the heat to #rsac! Join us for a spicy panel on navigating security in the age of #ai. 🔥
Limited spots are available - register now! snyk.co/uidv6 -
Snyk
@snyksec
Think you're nailing #devsecops? Think again.
Our new research reveals 7 surprising roadblocks to maturity. Are you making these mistakes? Find out. snyk.co/uibTW -
Snyk
@snyksec
🔐 How can financial institutions balance innovation, compliance, & security - without slowing development?
Join Snyk & @cibc for a fireside chat on tackling #appsec challenges, from #ai-driven development to secure coding best practices. Register now: snyk.co/uh8gs -
Snyk
@snyksec
Missed the #ctf action? 😱 Relive the thrill with community write-ups from #fetchtheflag 2025! See how players solved 30+ challenges in our latest blog post! snyk.co/uh8w4
-
Snyk
@snyksec
Is Symbolic #ai the future of code security? 🤔 Our latest blog post explores how Snyk Code's #symbolicai engine provides superior vulnerability detection. Check it out! snyk.co/uihry
-
Snyk
@snyksec
Our new guide helps programmers transition from imperative languages (like Python/Java) to the declarative logic of Rego.
Learn about programming paradigms & get started with practical examples.
Read now: snyk.co/uhSwa #rego #openpolicyagent #devsecops -
Snyk
@snyksec
Code hidden in #ai? Explore the rising threat of tensor steganography & learn how to protect your models. snyk.co/uh6En
-
Snyk
@snyksec
Security meets AI coding! Snyk now integrates with Google Cloud's Gemini Code Assist. Secure code, faster dev. Learn more: snyk.co/uihuG
-
Snyk
@snyksec
Are your cloud-based #ai Large Language Models at risk? Our latest article breaks down #llmjacking – a sneaky attack exploiting stolen credentials. Find out the potential damage and how to defend against it: snyk.co/uigIi
-
Snyk
@snyksec
New US admin's first 100 days highlight #ai & #cybersecurity as key policy & industry concerns. How will early decisions shape our security and innovation future? Get expert insights at our panel during #rsac2025 - moderated by @Axios' @samsabin923. snyk.co/uigF1
-
Snyk
@snyksec
Ready to witness the future of #applicationsecurity? 🚀 Snyk is bringing cutting-edge demos tailored to your needs to @googlecloud Next! Dive deep into #genai security with our experts at booth #3278.
#googlenext -
Snyk
@snyksec
AI got you sweating? 😅 Snyk & @seanseaevans (#hotones) are bringing the heat to #rsac! Join us for a spicy panel on navigating security in the age of #ai. 🔥
Limited spots are available - register now! snyk.co/uidv6 -
Snyk
@snyksec
Missed the Snyk Fetch the Flag #ctf Q&A? 🙋♀️ @_JohnHammond & the Snyk team answered your burning questions! Get insights & tips in our recent blog post. snyk.co/uie2a
-
Snyk
@snyksec
We're thrilled to announce that Snyk has been named the 2025 #googlecloudpartnerawards winner in Technology! 🎉 snyk.co/uigfM @googlecloud @gcloudpartners
-
Snyk
@snyksec
AI-powered application development moves fast—and security has to keep up! 🔒💨 Meet the Snyk team this week at #atlassianteam '25 at booth #116 to see how security keeps pace with innovation. @Atlassian
-
Snyk
@snyksec
BIG NEWS! We're thrilled to share Snyk has been named to @CRN's AI 100 list in the Cybersecurity category for 2025! 🎉 www.crn.com/news/security/2025/the-20-hottest-ai-cybersec… #crnai100 @TheChannelCo
-
Snyk
@snyksec
Ready to witness the future of #applicationsecurity? 🚀 Snyk is bringing cutting-edge demos tailored to your needs to @googlecloud Next! Dive deep into #genai security with our experts at booth #3278.
#googlenext -
Snyk
@snyksec
Beat vulnerabilities at their own game! Discover how to embed #security in your code from the start. Our team sheds light on building a culture of secure coding in our dynamic development world. Level up your software resilience without compromising speed! snyk.co/uicz8
-
Snyk
@snyksec
🔓 Discover how to stay ahead of security risks in #financial app development! Join our live #hacking session to see Snyk Code & Snyk Open Source catch vulnerabilities in real-time and uncover the hidden risks of #ai-assisted coding. Register now: snyk.co/uif0Q
-
Snyk reposted
Tevora Talks Podcast
@TevoraTalks
🎙️ In this episode of #tevoratalks, hosts are joined by CTO of Snyk, they explore the expanding attack surface, the rise in vulnerabilities, and how AI-powered tools like Snyk help developers secure code in real time. 🎧 Listen now: tevora.us/41V5gKq
#cybersecurity -
Snyk
@snyksec
Headed to #atlassianteam '25 this week? So is Snyk! Come see us at booth #116 to explore how to secure #ai-powered applications at full speed.
See how Snyk & @Atlassian can supercharge your security - register now: events.atlassian.com/team?event_context=external_toolkit&… 🔒 ⚡ -
Snyk
@snyksec
Unveiling the mysteries of ComfyUI Custom Node Vulnerabilities with our latest blog post! 🕵️♂️ Dive deeper into plugin ecosystem security with our seclabs team's in-depth exploration. Don't miss it! ⚡ #appsec #aisecurity #comfyui More here: snyk.co/uhPWq
-
Snyk
@snyksec
Protect your AI models from attacks. 🛡️ Read our latest research on vulnerabilities in deep learning file formats. #aisecurity #cyberthreat snyk.co/uhMze
-
Snyk
@snyksec
#ai is accelerating development, but are you introducing new security risks? 🤔 Download our whitepaper with @Deloitte & discover how to secure your #genai journey:snyk.co/uhSM7
-
Snyk
@snyksec
Think TypeScript is your security silver bullet? Think again. This blog post explores the limitations and hidden dangers. Don't get caught off guard.👇 snyk.co/uh50A #appsec
-
Snyk reposted
AWS Security
@AWSSecurityInfo
Excited to share our latest whitepaper: 'Navigating the GenAI Security Frontier'! Co-authored by Matt Schwartz & Mac Stevens, featuring insights from P.Vixie, H.Rossman, C. Betz, J.Kropf, M.Saner & P.Simpson. Launched with our security partners.
go.aws/4lfIbuw -
Snyk
@snyksec
🚨TODAY! 🚨
Level up your development & #security skills!
Join Snyk's free Live Hack workshop. Build a demo app with #ai-assisted coding tools, uncover vulnerabilities, AND earn CPE credits! 🎓 snyk.co/uiaxP #genai -
Snyk
@snyksec
Missed the Snyk Fetch the Flag CTF Q&A? 🙋♀️ John Hammond & the Snyk team answered your burning questions! Get insights & tips in our recent blog post. snyk.co/uie2a
-
Snyk
@snyksec
🚨 Security alert! We found vulnerabilities in Cortex.cpp (Jan AI). While self-hosted #ai is booming, security can't be an afterthought. Dive into our findings and how we addressed them. 👇 snyk.co/uieYn
-
Snyk
@snyksec
#ai coding is fast, but is it secure? Join us this week for a LIVE hack session where we'll build a coffee shop app with #github Copilot & #chatgpt, then show you how it gets hacked! 😱 Learn to protect your code from SQL injection, XSS, & more. snyk.co/uiaxP
-
Snyk
@snyksec
With the rise of GenAI, security risks are on the rise. Snyk Analytics offers the most powerful solution for AppSec leaders seeking to gain the visibility needed to address threats. #appsec #security #ai snyk.co/uhCuu
-
Snyk
@snyksec
"WHAT IN TARNATION?! You've got a memory leak the size of Texas!"😤
Introducing Greybeard CLI: security insights delivered with the grumpiness of your favorite coding curmudgeon.
Let Greybeard give your code the roast it needs this #aprilfools day: snyk.co/uiezy -
Snyk
@snyksec
Want to be an AI security expert? Our new Snyk Learn path covers the OWASP Top 10 for LLMs & GenAI. Learn for free today! #ai #security snyk.co/uhxJg
-
Snyk
@snyksec
What's the buzz about Claude Code? Anthropic's new #agenticai coding tool is turning heads, and Snyk's @_clarkio is taking it for a spin in his latest video. Get his comprehensive analysis of #claudecode's capabilities & learn why it's a game-changer for developers.
-
Snyk
@snyksec
Is Symbolic AI the future of code security? 🤔 Snyk tested its SAST engine on real-world challenges! See the results & learn how it beats pattern-matching. snyk.co/uieiC
-
Snyk
@snyksec
Get up to speed on #ai data security in just 6 minutes! Our recent article covers the risks, frameworks, and best practices you need to know. snyk.co/uieit
-
Snyk
@snyksec
Is your #aicode safe? Find out before hackers do. 🛡️
Join Micah Silverman and @sonyamoisset for a live #hacking session this week to see how easily #ai-generated code can be compromised. Don't miss it! snyk.co/uiaxP #genai -
Snyk
@snyksec
Beat vulnerabilities at their own game! Discover how to embed #security in your code from the start. Our team sheds light on building a culture of secure coding in our dynamic development world. Level up your software resilience without compromising speed! snyk.co/uicz8
-
Snyk
@snyksec
Our new guide helps programmers transition from imperative languages (like Python/Java) to the declarative logic of Rego.
Learn about programming paradigms & get started with practical examples.
Read now: snyk.co/uhSwa #rego #openpolicyagent #devsecops -
Snyk
@snyksec
Tired of blind spots in your app security? 🔍 Learn how Application Security Posture Management (#aspm) provides the visibility you need to identify & mitigate risks across your entire software supply chain. snyk.co/uhVd4 #appsec #cybersecurity
-
Snyk
@snyksec
#devsecops can feel daunting. 😨 Our recent blog breaks it down into 5 actionable steps, including practical advice from experts. Start your journey today! #security #devops snyk.co/uh50l
-
Snyk
@snyksec
🚨Critical Next.js Security Alert: CVE-2025-29927🚨
Patch your public-facing Next.js applications NOW to avoid permission and auth bypasses. (Excludes Netlify/Vercel).
Learn more: snyk.co/uickl #nextjs #securityalert #sn -
Snyk
@snyksec
Feel like your career path took a sharp turn? 🔄 Diana Elaine, Sr. Security & Compliance Engineer, @WaltDisneyCo, shares her incredible journey from aerospace engineer to #appsec in our latest #womenleadingsecurity episode.
This media couldn't be displayed. See it on the original post. -
Snyk
@snyksec
Claude 3.7 Sonnet: Secure code or security risk? We tested it! See our findings: snyk.co/uh68J #aisecurity
-
Snyk
@snyksec
SQL injection, XSS, & more! See #ai-generated code get hacked LIVE by Micah Silverman & @sonyamoisset. Don't miss it! 🚨 snyk.co/uiaxP #cybersecurity #githubcopilot
-
Snyk
@snyksec
Meet us at #incyberforum Europe (@FIC_eu) booth #b24! Embark on a journey of dev first #security with us. Live demos, expert advice, exclusive giveaways, and more await you! 💪🔐 snyk.co/uh9RP
-
Snyk
@snyksec
🚀 Managing vulnerabilities just got easier! Automate issue assignments with @ServiceNow Vulnerability Assignment Rules & Snyk Project Tags—saving time & ensuring fast action. ⚡ Watch the new Snyk Learn demo. snyk.co/uidwk
-
Snyk
@snyksec
AI got you sweating? 😅 Snyk & @seanseaevans (#hotones) are bringing the heat to #rsac! Join us for a spicy panel on navigating security in the age of #ai. 🔥
Limited spots are available - register now! snyk.co/uidv6 -
Snyk
@snyksec
#ai boosts productivity, but at what cost? We explore the #security challenges of #chatgpt coding. Get the insights you need. 👇 snyk.co/uh8xE
-
Snyk reposted
CYBR.SEC.Events
@CybrSecEvents
Michael and Sam are joined by Field CTO, Steven Schmidt! They discuss the early days of application security, the evolution of application security tools and processes, and challenges in balancing developer speed with security requirements.
Don’t miss this episode of HOU.SEC.CAST. – the HOU.SEC.CON. podcast YouTube!
youtu.be/Zu2TFVJR7iw
Thank you to @snyksec for sponsoring this episode! Learn more about building secure applications at snyk.io and chat with their team at EXEC.SEC.CON. on April 22nd!
#houseccast #podcast #cybersecurity #appsec #applicationsecurity -
Snyk
@snyksec
What's the buzz about Claude Code? Anthropic's new #agenticai coding tool is turning heads, and Snyk's @_clarkio is taking it for a spin in his latest video. Get his comprehensive analysis of #claudecode's capabilities & learn why it's a game-changer for developers.
-
Snyk
@snyksec
Beat vulnerabilities at their own game! Discover how to embed #security in your code from the start. Our team sheds light on building a culture of secure coding in our dynamic development world. Level up your software resilience without compromising speed! snyk.co/uicz8
-
Snyk
@snyksec
TODAY! 🚨 Struggling with #security compliance? Join our Snyk in 30 webinar to see how Snyk simplifies compliance with SOC 2, PCI DSS 4.0, ISO 27001, the CRA, and #owasp Top 10—without slowing development. Don’t miss it—register now! snyk.co/uicNE
-
Snyk
@snyksec
Compliance vs. innovation? @cibc shows how to win both. Gain practical tips from their #appsec journey in our latest blog post. snyk.co/uicxi
-
Snyk
@snyksec
🚨Critical Next.js Security Alert: CVE-2025-29927🚨
Patch your public-facing Next.js applications NOW to avoid permission and auth bypasses. (Excludes Netlify/Vercel).
Learn more: snyk.co/uickl #nextjs #securityalert #sn -
Snyk
@snyksec
Think TypeScript's your app security guard? It's time for a reality check. Get the scoop on its concealed pitfalls and limits, so you don't get blindsided! Dive in👇 snyk.co/uh50A #appsec
-
Snyk
@snyksec
Check out this new Federal Tech Podcast episode with Snyk's Solutions Engineering Manager, Karthik Natarajan, where he discusses how AI is impacting the dev experience and security postures within the federal & public sector. www.theoakmontgroupllc.com/ep-223-shifting-left-in-federa…
-
Snyk
@snyksec
Think you're nailing #devsecops? Think again.
Our new research reveals 7 surprising roadblocks to maturity. Are you making these mistakes? Find out. snyk.co/uibTW -
Snyk
@snyksec
#ai boosts productivity, but at what cost? We explore the #security challenges of #chatgpt coding. Get the insights you need. 👇 snyk.co/uh8xE
-
Snyk
@snyksec
#python on macOS? Yes, please! This guide covers installation and highlights Python's importance in the #dev world. Don't forget to check out Snyk's Python Code Checker for secure coding. snyk.co/uh5s0
-
Snyk
@snyksec
Can AI hide secrets? Discover how tensor steganography conceals code in neural networks. Dive into the future of cyber threats. 👇
#aisecurity #steganography #machinelearning
snyk.co/uh6En -
Snyk
@snyksec
Boost your #appsec efficiency! 🚀 Learn how Snyk & @ServiceNow's Vulnerability Assignment Rules streamline vulnerability management in our latest blog. Read now: snyk.co/uiax1
-
Snyk
@snyksec
Are you confident your #apps are using strong cryptographic algorithms? Many legacy systems still rely on outdated and vulnerable methods like MD5. Learn how Snyk Code can help you identify and fix these issues in a new blog. snyk.co/uh9Tj
-
Snyk
@snyksec
Building a Flask app? Are you sure your access control is rock-solid? 🤔 Broken access can lead to major security breaches. @liran_tal breaks down how to prevent it in this must-read blog. snyk.co/uibdp
-
Snyk
@snyksec
#ctf might be over, but the adventure isn't! 😎 Discover how sharp minds conquered the 30+ hurdles at #fetchtheflag 2025! Check out our recent blog for all the exciting deets 👉 snyk.co/uh8w4
-
Snyk
@snyksec
Our new guide helps programmers transition from imperative languages (like Python/Java) to the declarative logic of Rego.
Learn about programming paradigms & get started with practical examples.
Read now: snyk.co/uhSwa #rego #openpolicyagent #devsecops -
Snyk
@snyksec
Meet us at #incyberforum Europe (#fic) booth #b24! Embark on a journey of #devfirst security with us. Live demos, expert advice, exclusive giveaways, and more await you! @FIC_eu 💪🔐 snyk.co/uh9RP
-
Snyk
@snyksec
URGENT 🚨 23,000 GitHub repos potentially compromised! A major exploit hit the "changed files" (tj-actions/changed-files) GitHub Action, exposing secrets. Learn how it happened & how to protect yourself NOW. snyk.co/uibeb
-
Snyk
@snyksec
Claude 3.7 Sonnet: Secure code or security risk? We tested it! See our findings: snyk.co/uh68J #aisecurity
-
Snyk
@snyksec
📈 CVEs surging? Snyk's new program gives #opensource #devs the tools to build secure software. Learn how we're deepening our investment in the ecosystem! snyk.co/uh6QF #cybersecurity
-
Snyk
@snyksec
#devsecops can feel daunting. 😨 Our recent blog breaks it down into 5 actionable steps, including practical advice from experts. Start your journey today! #security #devops snyk.co/uh50l
-
Snyk reposted
Santiago
@svpino
Here is the link to RSVP if you are planning to join:
snyk.plug.dev/K3laNpY
Sign up for your free Snyk Account here: snyk.plug.dev/XFsponR -
Snyk reposted
Santiago
@svpino
Vibe-coding is awesome, but the code these models generate is full of security holes and can be easily hacked.
This will be a live, 90-minute session where @snyksec will build a demo application using Copilot + ChatGPT and live hack it to find every weak spot in the generated code.
This will happen on Thursday, April 3rd, between 11 am and 12:30 pm ET.
Everyone can join for free. Please RSVP at the link below.
Here is what you should expect:
• An overview of security risks with AI-generated code
• How to build a coffee shop demo app using Copilot
• How to hack the code (SQL injection, cross-site scripting, directory traversal, etc.)
• How to mitigate and prevent these vulnerabilities
Prerequisites if you are joining:
• You need a ChatGPT account
• You will need GitHub Copilot
• You will need an IDE that works with Copilot (VS Code, JetBrains, anything)
• You'll need a free Snyk Account -
Snyk
@snyksec
Boost your #appsec efficiency! 🚀 Learn how Snyk & @ServiceNow's Vulnerability Assignment Rules streamline vulnerability management in our latest blog. Read now: snyk.co/uiax1
-
Snyk
@snyksec
📈 CVEs surging? Snyk's new program gives #opensource #devs the tools to build secure software. Learn how we're deepening our investment in the ecosystem! snyk.co/uh6QF #cybersecurity #oss
-
Snyk
@snyksec
#ai boosts productivity, but at what cost? We explore the #security challenges of #chatgpt coding. Get the insights you need. 👇 snyk.co/uh8xE
-
Snyk
@snyksec
⬆️ Level up your development and #security skills!
Join Snyk's free Live Hack Workshop on April 3. Build a demo app with #ai-assisted coding tools, uncover vulnerabilities, and earn CPE credits! 🎓 snyk.co/uiaxP
#livehacking -
Snyk
@snyksec
20 years of cybersecurity wisdom! Neeta Vensak of @Genesys shares her journey in our next #womenleadingsecurity episode. Hear her thoughts on mentorship, #ai, & building inclusive communities. 🔗 snyk.co/uiaxy
#womenintech #cybersecurityThis media couldn't be displayed. See it on the original post. -
Snyk
@snyksec
🚨 Could ChatGPT's New Model Jeopardize Your Job? In his latest video, @_clarkio challenged #chatgpt's newest iteration to develop a secure note-taking application. The results will likely surprise you. 🫢 Could #ai's rapid advancement pose risks to your company, team, or career?
Snyk
@snyksec
Watch now to uncover the full story on AI's impact in the workplace. www.youtube.com/watch?v=sPknqyuLRv4
-
Snyk
@snyksec
Streamlining data processing AND ensuring security? That's what Snyk is doing with the Golang Bento project! We're excited to contribute to this open-source tool, helping it read Kafka streams and materialize intelligence. snyk.co/uiaeX
-
Snyk
@snyksec
Thrilled Snyk and @JLR_News were finalists for "Best Implementation of #devsecops" at Computing's DevOps Excellence Awards, showcasing our powerful collaboration. Learn more about how we transformed JLR's security. snyk.co/uh98P
-
Snyk
@snyksec
TODAY! Stop wasting time on manual vulnerability remediation. ⏱️ Chapter 3 of our #devsecops Masterclass with @ServiceNow reveals how to automate your response and prioritize critical fixes. Don't miss out - register now! events.actualtechmedia.com/on-demand/2487/chapter-4-dont-…
-
Snyk
@snyksec
Discover the perfect balance between innovation, compliance, & security in financial services. Tune in to our fireside chat with @cibc and delve into #appsec challenges, from secure coding to #ai-powered development. Register today: snyk.co/uh8gs 🔐💻
-
Snyk
@snyksec
Achieving SOC 2 compliance doesn’t have to be overwhelming. Our cheat sheet breaks down the essential requirements and shows how Snyk makes it easier to secure your systems. Download now and start your journey to compliance!
-
Snyk
@snyksec
Are you confident your #apps are using strong cryptographic algorithms? Many legacy systems still rely on outdated and vulnerable methods like MD5. Learn how Snyk Code can help you identify and fix these issues in a new blog from @liran_tal. snyk.co/uh9Tj
-
Snyk
@snyksec
Ready to turn vulnerabilities into victories? Chapter 3 of our #devsecops Masterclass with @ServiceNow is your guide! Learn to take control, prioritize wisely, & craft an incident response you can rely on. Register now! events.actualtechmedia.com/on-demand/2487/chapter-4-dont-…
-
Snyk
@snyksec
🚨 Join Snyk at #incyberforum Europe (FIC)! We’ll be showcasing our dev-first security solutions with live demos, expert insights, & exclusive swag. Stop by booth #b24 to see how Snyk can help you secure your apps and infrastructure—without slowing down development. @FIC_eu
-
Snyk
@snyksec
Accelerate time-to-market AND secure your code! Learn how with Snyk's DevSecOps live demo, March 19th, 11 AM ET. Get real-time SAST, CI/CD integration, and developer-friendly remediation. Register today! # #devsecops snyk.co/uh9Du
-
Snyk
@snyksec
Missed the #ctf action? 😱 Relive the thrill with community write-ups from #fetchtheflag 2025! See how players solved 30+ challenges in our latest blog post! snyk.co/uh8w4
-
Snyk
@snyksec
🔐 How can financial institutions balance innovation, compliance, & security - without slowing development?
Join Snyk & @cibc for a fireside chat on tackling #appsec challenges, from #ai-driven development to secure coding best practices. Register now: snyk.co/uh8gs -
Snyk
@snyksec
Happy Employee Appreciation Day! 💜 This week, we celebrated the heart & soul of Snyk: our amazing team. Snykers are the driving force behind our success. Your passion and commitment is truly unmatched & we are so grateful for the hard work you put into making Snyk incredible.
-
Snyk
@snyksec
Discover the perfect balance between innovation, compliance, & security in financial services. Tune in to our fireside chat with @cibc and delve into #appsec challenges, from secure coding to #ai-powered development. Register today: snyk.co/uh8gs 🔐💻
-
Snyk reposted
Carahsoft
@Carahsoft
We're thrilled to announce our new partnership with @snyksec, a leading developer security platform with cutting-edge solutions accessible to the #publicsector through our network of reseller partners. More details in the full release: carah.io/e9e5b
-
Snyk
@snyksec
Can AI hide secrets? Discover how tensor steganography conceals code in neural networks. Dive into the future of cyber threats. 👇
#aisecurity #steganography #machinelearning
snyk.co/uh6En -
Snyk
@snyksec
Claude 3.7 Sonnet: Secure code or security risk? We tested it! See our findings: snyk.co/uh68J #aisecurity
-
Snyk
@snyksec
#ai boosts productivity, but at what cost? We explore the #security challenges of #chatgpt coding. Get the insights you need. 👇 snyk.co/uh8xE
-
Snyk
@snyksec
Missed the #ctf action? 😱 Relive the thrill with community write-ups from #fetchtheflag 2025! See how players solved 30+ challenges in our latest blog post! snyk.co/uh8w4
-
Snyk reposted
Zoe Braiterman
@zbraiterman
Fondly reflecting on my @snyksec Ambassadors panel with @aastha1891 and Saman, as well! 💜
👉 Check out the @YouTube recording: www.youtube.com/live/yqNHQ5NWeos
#cybersecurity #diversityandinclusion #womenshistorymonth
Snyk
@snyksec
Megan S. from @AWNetworks is sparking #cybersecurity change through early engagement & mentorship. 🔥 Check out her full conversation on inclusivity in the industry with Jonaki Egenolf! 👉 snyk.co/uh76n #womenleadingsecurity
-
Snyk
@snyksec
Navigating PCI DSS 4.0 compliance just got easier! Discover useful insights and essential tips on securing financial transactions with our handy cheat sheet. Stay compliant, stay protected! snyk.co/uh8jM
-
Snyk
@snyksec
Stop chasing #vulnerability counts! 🛑 Learn how risk-based prioritization actually protects your business. Our blog explains why & how to focus on what really matters. Dive in. 👇 snyk.co/uh8jO
-
Snyk
@snyksec
We’re honored to be named to Forbes’ America’s Best Startup Employers 2025, underscoring our commitment to continuous growth. Thank you to Forbes and, most importantly, our amazing Snykers! ✨ #lifeatsnyk
-
Snyk reposted
-
Snyk
@snyksec
🔐 How can financial institutions balance innovation, compliance, & security - without slowing development?
Join Snyk & @cibc for a fireside chat on tackling #appsec challenges, from #ai-driven development to secure coding best practices. Register now: snyk.co/uh8gs -
Snyk
@snyksec
Megan S. from @AWNetworks is sparking #cybersecurity change through early engagement & mentorship. 🔥 Check out her full conversation on inclusivity in the industry with Jonaki Egenolf! 👉 snyk.co/uh76n #womenleadingsecurity
-
Snyk
@snyksec
Become a #coding superhero!
Join Patch and dive into a world of vulnerabilities. Dodge bugs, collect power-ups, and defeat Glitch to save the digital realm.
Play #vulnvortex today! www.vulnvortex.com -
Snyk
@snyksec
#blackhistorymonth may be ending, but our journey towards a more inclusive workplace continues. At Snyk, we believe in creating a culture where everyone feels seen, heard, & valued. We strive to foster an environment of belonging where everyone thrives and contributes their best.
Snyk
@snyksec
We’re growing, and we’re looking for individuals who share our passion for building a culture of belonging. Read about our Black History Month initiatives and see how you can secure your future at Snyk: snyk.io/blog/celebrating-black-history-month-2025-at-snyk/
-
Snyk reposted
John Hammond
@_JohnHammond
The @snyksec Fetch the Flag CTF has wrapped up! Big congrats to the winners and huge thanks for playing. If you were part of the party, grab your certificate, share it wide, and please be sure to fill out that feedback form! 😜
-
Snyk reposted
Ankan Roy
@TechAnkan
Just finished snyk ctf 2025, publishing writeups on theankanroy.medium.com check it out @snyksec @_JohnHammond
-
Snyk
@snyksec
The suspense is finally over!
🥁🥁🥁🥁🥁🥁
✨Cheers to our 2025 #fetchtheflag champions!✨
Snyk
@snyksec
Congrats to all participants for a valiant effort & thank you for joining in on the fun!
Keep an eye on the Fetch homepage for solution write-ups or head to Discord to share yours!
Until next year! 🚩 -
Snyk
@snyksec
One hour left, folks!
Who has what it takes to secure the win!?
FIND👏THOSE👏FLAGS👏
#fetchtheflag -
Snyk
@snyksec
RISE & SHINE #fetchtheflag PARTICIPANTS! ☀️
Just 2 hours out from the close of competition - time for one last leaderboard update!
Our top 3 teams have nearly secured their win - but we've had some movement amongst the solo warriors.
Still time for another shake-up... 👀🏆 -
Snyk
@snyksec
Great news! #fetchtheflag CTF is extended until 12 PM EST today!
Showcase your skills, tackle challenges, and climb the leaderboard. Don’t miss your chance to rise to the top! snyk.co/uhUUT -
Snyk
@snyksec
Wooooooo 😮💨😅 12 more hours to go!
How many flags have you solved so far? #fetchtheflag -
Snyk
@snyksec
When you're 10+ hours into #fetchtheflag #ctf 2025 and you start questioning if your coffee cup is a flag. 😵💫😵💫
-
Snyk
@snyksec
Leaderboard update #3!
Seeing some movement amongst our leading teams but our solo warriors are holding on strong!!
Let's goooooooo 🚩🚩🚩 #fetchtheflag -
Snyk
@snyksec
POV: You've been heads down in #fetchtheflag challenges for hours & resurface to see your name on the top of the leaderboard
-
Snyk
@snyksec
Time for another leaderboard update! 🏆
Both our first-place team & solo participant have managed to hang on to the top spot - but it's still anybody's game!
Keep up the great work!
Check back in a few for more exciting updates! #fetchtheflag -
Snyk
@snyksec
It's time for our first leaderboard update! 🏆
Can these frontrunners keep their stride?? 👀
Stay tuned! #fetchtheflag -
Snyk
@snyksec
In a recent roundtable discussion, Snyk & @SurveyMonkey chatted about paving the road to encourage developers to focus on security. 🐒🐕
View the full talk recap for #developersecurity insights.
snyk.co/ueyfB -
Snyk
@snyksec
At #snykcon, @k3r3n3 says she was inspired by the movie Hackers (1995) 👩💻🧑💻👨💻
How about you? What inspired you to get into #cybersecurity? -
Snyk
@snyksec
#snykcon Day 2 starts in 2 hours and we have so much in store for you!
🟣 Captivating and educational sessions
🟣 Keynote + product roadmap
🟣 Demos from our team & partners
🟣 Illusions with @waynehoffman
Sign up (free) to join the fun 👇 snyk.co/udpMK -
Snyk
@snyksec
Ready to take your security skills to the next level? Compete in 20 hands-on hacking challenges & win prizes at Fetch the Flag CTF at SnykCon. 🐶🚩
-
Snyk
@snyksec
Today, we are happy to announce that we've raised $300M in Series E funding. We wouldn't be here without all of our users and the amazing community we've built - THANK YOU ✨. snyk.io/news/