UCL are hiring a Lecturer/Associate Professor in Systems and Networks, deadline 18 January 2027. Further details and application link can be found at www.ucl.ac.uk/about/work-at-ucl/search-jobs/details?nPost⦠(this position includes a market supplement in addition to the pay range listed on the page)
Steven Murdoch
Steven James Murdoch is Professor of Security Engineering in the Computer Science Department, University College London. His research covers privacy-enhancing technology, Internet censorship, and anonymous communication, in particular Tor. He is also known for discovering several vulnerabilities in the EMV bank chipcard payment system (Chip and PIN) and for creating Tor Browser. More on Wikipedia
-
Steven Murdoch
@sjmurdoch
-
Steven Murdoch
@sjmurdoch
I spoke to the FT about the latest Microsoft outage. www.ft.com/content/025b2769-bca8-4a74-b9f5-5d7ad7da32c7
-
Steven Murdoch reposted
UCL InfoSec
@uclisec
āPhishing at the Front Desk: Usable Security in Luxury Hotelsā by Tania Maynard-Browne, a post on Benthamās Gaze. www.benthamsgaze.org/2026/11/11/phishing-at-the-front-desā¦
-
Steven Murdoch reposted
Iceman
@herrmann1001
-
Steven Murdoch
@sjmurdoch
Many misconceptions circulate about thermal communication. These are covert channels, which allow small secrets to be sent between colluding parties. They can also (sometimes) be turned into side channels where small secrets are leaked to a malicious observer. š§µ
Steven Murdoch
@sjmurdoch
However, neither is sufficient to break out of a sandbox, because doing so requires the malicious party to control code outside the sandbox, not just leak information. Itās reasonable to worry about covert/side channels to protect secrets, but they arenāt necessary for sandboxes.
-
Steven Murdoch
@sjmurdoch
Itās #nationalcodingweek next week, so I've published a resource on using the BBC @microbit_edu to play a game that explores how radio waves travel, get blocked by/reflected off obstacles, and the challenges of measuring strong signals that can overload sensors.
Steven Murdoch
@sjmurdoch
The game is a treasure hunt for a hidden radio transmitter, using a signal-strength meter. The only requirements are a browser and a few micro:bits. It includes a lesson plan and worksheet for in-depth exploration, plus a quick start to just play the game. www.benthamsgaze.org/2026/09/08/a-radio-treasure-hunt-forā¦
-
Steven Murdoch
@sjmurdoch
With the availability of LLMs we can now apply ridiculous levels of polish to trivial problems. In this vein, hereās a tool to optimise the reverse-sear of a steak when your thermometer canāt be left in the oven by fitting a three-parameter physical model to measurements.
Steven Murdoch
@sjmurdoch
The tool is at sjmurdoch.github.io/reverse-sear/ with source at github.com/sjmurdoch/reverse-sear/. It is 100% Claude Code generated so take any claim with a pinch of salt (but the first steaks it helped cook were delicious). For the science behind reverse-searing, see www.seriouseats.com/reverse-seared-steak-recipe
Steven Murdoch
@sjmurdoch
It even has a @quint_lang model of the UI, which helped identify one bug in the UI flow and one bug in Apalache. Again itās a ridiculous level of rigour for a trivial application but a helpful learning experience in a low stakes scenario. github.com/apalache-mc/apalache/issues/3479
-
Steven Murdoch
@sjmurdoch
I spoke to The Guardian about Claudeās content watermarking. As long as it only modifies how the existing random number generator works, it should have no measurable effect on quality. www.theguardian.com/technology/2026/aug/17/claude-watermaā¦
Steven Murdoch
@sjmurdoch
Incidentally my first academic paper was on watermarking, as applied to game bots. The covert communication allowed a team to coordinate a better outcome than any individual player could achieve. murdoch.is/papers/ih04connect-4.pdf
-
Steven Murdoch
@sjmurdoch
A prompt thatās been very helpful at getting Claude to improve a user-facing app with minimal interaction from me has been to ask it to do a cognitive walkthrough with a given persona. Itās not great at coming up with good personas (IME) but if you give it one it can run with it.
Steven Murdoch
@sjmurdoch
This is 100% Claude Code generated; somewhat tested but not reviewed. Your mileage may vary. Confirm with the official app before planning your journey (in particular, the route planner doesnāt know opening hours). scottiesinthecity.co.uk/app
-
Steven Murdoch
@sjmurdoch
Are you trying to complete the @MaggiesCentres Scotties in the City art trail in Glasgow? I made a route planner to find an optimised path to get as many as you can, given a starting point and distance/time limit. sjmurdoch.github.io/glasgow-scotties/
Steven Murdoch
@sjmurdoch
This is 100% Claude Code generated; somewhat tested but not reviewed. Your mileage may vary. Confirm with the official app before planning your journey (in particular, the route planner doesnāt know opening hours). scottiesinthecity.co.uk/app
Steven Murdoch
@sjmurdoch
The same principle will likely work for other @wildinart events so feel free to adapt the code if you are interested. github.com/sjmurdoch/glasgow-scotties/
-
Steven Murdoch reposted
Bart Preneel
@bpreneel1
Today Anthropic announced a set of cryptanalytical results developed by Claude Mythos Preview (www.anthropic.com/research/discovering-cryptographic-weakā¦) a š§µ 1/11
-
Steven Murdoch
@sjmurdoch
National COVID-19 figures couldnāt tell a department whether to hold a seminar next week. So from 2020 to 2022 I collected UCLās daily case counts and turned them into an early-warning chart. Iāve now archived all of it plus 168 newsletters for context. www.benthamsgaze.org/2026/07/26/ucls-response-to-the-coviā¦
Steven Murdoch
@sjmurdoch
And a demo of what the dataset makes possible: an interactive chronology of 347 dated events, plotting UCLās decisions against national restrictions and its own case curve, each with a verbatim quote from the source it came from. sjmurdoch.github.io/uclcovid-timeline/timeline.html
-
Steven Murdoch
@sjmurdoch
I spoke to @SMaurizi for a @ComputerWeekly article on smartphone security, particularly how @GrapheneOS can protect journalistsā data. www.computerweekly.com/feature/Journalist-Richard-Medhursā¦
-
Steven Murdoch
@sjmurdoch
I was interviewed for Computerphile on my analysis of hidden messages within the GPS signals and what message they might carry (and to whom). youtu.be/2Q6OvYjOJi0
Steven Murdoch
@sjmurdoch
(apologies for the whoops about the GPS bit rate ā itās only 50 bps not 500 bps)
-
Steven Murdoch reposted
Steven Murdoch
@sjmurdoch
The corrected and expanded article on my exploration of GPS special messages is available at sjmurdoch.github.io/gps-special-messages/. Additionally, this is now mobile-friendly and accompanied by detailed footnotes, allowing results to be verified against the published dataset. 5/
-
Steven Murdoch
@sjmurdoch
Since the original publication of my Inside GNSS article on hidden messages within the GPS signal (The Empty Field That Wasnāt: GPS, OTAD and Two Decades of Encrypted Broadcasts), there have been a few developments and updates. š§µ 1/
Post not available here, view on X
Steven Murdoch
@sjmurdoch
The corrected and expanded article on my exploration of GPS special messages is available at sjmurdoch.github.io/gps-special-messages/. Additionally, this is now mobile-friendly and accompanied by detailed footnotes, allowing results to be verified against the published dataset. 5/
Steven Murdoch
@sjmurdoch
Finally, there is one message which on first inspection appears to be a plaintext leak: ā+81H DAYSā. However, analysis suggests that it is more likely just a coincidence. The discussion forum is open and Iād welcome comments on this or other findings. github.com/sjmurdoch/gps-special-messages/discussions/5 6/6
-
Steven Murdoch
@sjmurdoch
My article on hidden messages within GPS signals was featured on @404mediaco. www.404media.co/the-u-s-military-quietly-turned-gps-into-ā¦
Steven Murdoch
@sjmurdoch
It was also covered in the @WIRED Security Newsletter www.wired.com/story/security-news-this-week-crypto-funded⦠and discussed on Hacker News news.ycombinator.com/item?id=48411799
-
Steven Murdoch
@sjmurdoch
I spoke to The Guardian about Anthropicās call for mechanisms to slow the development of frontier AI capabilities. www.theguardian.com/technology/2026/jun/05/anthropic-urgeā¦
-
Steven Murdoch
@sjmurdoch
For the tl;dr, I wrote a summary of my analysis of the GPS Special Message ānumber stationā, including entropy measurement, duplicated strings, a mysterious new āTEXTā prefix, and the systemās relationship with military key distribution. www.benthamsgaze.org/2026/06/02/the-quiet-numbers-stationā¦
Steven Murdoch
@sjmurdoch
For 19 years, GPS satellites have secretly broadcast a ānumbers stationā in their public signals. We decoded 12M messages: a 2011 flash where 31 of 32 satellites flipped in hours, āghostā substrings repeating years apart, and a āTEXTā prefix spreading now. lsc-pagepro.mydigitalpublication.com/publication/?i=86527ā¦
-
Steven Murdoch
@sjmurdoch
For 19 years, GPS satellites have secretly broadcast a ānumbers stationā in their public signals. We decoded 12M messages: a 2011 flash where 31 of 32 satellites flipped in hours, āghostā substrings repeating years apart, and a āTEXTā prefix spreading now. lsc-pagepro.mydigitalpublication.com/publication/?i=86527ā¦
Steven Murdoch
@sjmurdoch
The source code is available on Github, and the data is on Zenodo. Iād welcome follow-up analysis. github.com/sjmurdoch/gps-special-messages
-
Steven Murdoch reposted
Steven Murdoch
@sjmurdoch
Claude Opus 4.7 is out, and Iāve been interfacing it with the National Rail Live Departure Boards API. I leave you with a poem inspired by the current departures from St Pancras station.
-
Steven Murdoch
@sjmurdoch
Claude Opus 4.7 is out, and Iāve been interfacing it with the National Rail Live Departure Boards API. I leave you with a poem inspired by the current departures from St Pancras station.
-
Steven Murdoch
@sjmurdoch
MCP gives AI tools access to powerful capabilities but is notorious for heavy token use. AXI is a promising token-efficient alternative but it relies on predicting typical tool usage. I've proposed a modification where tools self-tune through an OODA loop. github.com/kunchenguid/axi/pull/29
-
Steven Murdoch
@sjmurdoch
Tried Claude with a higher level planning task rather than coding assistance. It wrote a good migration plan for an aging web app, but not a great one. It got itself in a cyclic dependency mess and missed that dependencies were unused. It fixed those after being pointed out.
-
Steven Murdoch reposted
Alexandre Bartel
@software_ses
Congratulations Sabine for a successful PhD defense! Sabine's work focuses on Control Flow Integrity, a defense mechanism designed to protect programs from control-flow hijacking attacks.
www.umu.se/en/news/advanced-security-technology-rarely-us⦠-
Steven Murdoch
@sjmurdoch
I think itās not just me, but JavaScript web development stacks are needlessly complex and fragile. After many attempts, even Gemini gives up trying to build a one-file npm+Parcel TypeScript project.
-
Steven Murdoch reposted
Weird World
@WeirdIsTheWorld
For a long time, people thought Joy (played by Jaime Pressly) from My Name Is Earl looked like Margot Robbie, but Robbie hadnāt even made her Hollywood debut when the show originally aired...
-
Steven Murdoch
@sjmurdoch
Reuters were accused of acting illegally in guessing the URL of an unreleased report in 2002. I didnāt hear anything after the initial reports so presume it was quietly dropped or settled. blog.citp.princeton.edu/2002/10/31/intentia-vs-reuters-slā¦
Ed Conway
@EdConwaySky
The person who first downloaded the OBR's document at 11:35 on Budget day (I'm guessing someone at Reuters, given they first reported it) had already guessed the web address and tried and failed to download it 32 times so far that day(!)
-
Steven Murdoch
@sjmurdoch
UCL Computer Science are hiring Section Managers to support the development and delivery of teaching, research, and strategy within their section. Iāll be leading the Foundational Computer Science section, where the InfoSec group is based. www.ucl.ac.uk/work-at-ucl/search-ucl-jobs/details?jobId=3ā¦+
-
Steven Murdoch reposted
Anthony Finkelstein
@profserious
Very few people seem to understand university finances and, distressingly, this includes many academics and most policymakers. This is an attempt to condense the key points you need to know. open.substack.com/pub/profserious/p/understanding-universā¦
-
Steven Murdoch reposted
paymentvillage
@paymentvillage
Payment Village at DEF CON 33:
- NFC, BLE, Android, POS, ATMs
- Workshops + live research
- Huge CTF with harder challenges
Built by last year's volunteers. We're bigger than ever. And itās all hands-on!
paymentvillage.substack.com/p/inside-def-con-33-whats-hapā¦
#defcon #ctf #infosec #payments -
Steven Murdoch reposted
UCL InfoSec
@uclisec
ā$5 Wrench Attacks: When Cryptocurrency Crime Get Physicalā, a post on Benthamās Gaze by Marilyne Ordekian discussing when XKCD comics become reality ā www.benthamsgaze.org/2025/07/22/5-wrench-attacks-when-cryā¦
-
Steven Murdoch
@sjmurdoch
I am recruiting mental-health experts (clinical psychologists and psychiatrists) for an in-person workshop in London to discuss a mobile app for mental health care. Participants will receive £500+expenses for their time. If you might be interested please email s.murdoch@ucl.ac.uk
-
Steven Murdoch reposted
EFF
@EFF
In memoriam: Cryptome co-founder John L. Young, who died March 28 at age 89 in New York City, was one of the early, under-recognized heroes of the digital age. www.eff.org/deeplinks/2025/05/memoriam-john-l-young-cryptā¦
-
Steven Murdoch
@sjmurdoch
Has anyone seen mehdiop[.]com showing up as a hijacked search engine? I donāt see other people discussing it.
-
Steven Murdoch reposted
UCL InfoSec
@uclisec
On our new paper published at IEEE Security and Privacy @IEEESSP ā āA Privacy Framework for Research Using Social Media Dataā, a summary by Kyle Beadle www.benthamsgaze.org/2025/05/15/a-privacy-framework-for-rā¦
-
Steven Murdoch
@sjmurdoch
AI-based scam checkers are gaining popularity but I would be cautious in following their advice unless the company is willing to stand behind it. For example, Metro Bank makes bold claims but the fine print absolves them of any responsibility for errors. www.metrobankonline.co.uk/ways-to-bank/i-want-some-informā¦
Steven Murdoch
@sjmurdoch
Nationwide offers the only service Iām aware of that backs up their advice with a guarantee. I donāt know how it works but I suspect that if AI is involved, thereās human verification of decisions. www.nationwide.co.uk/help/fraud-and-security/scam-protectā¦
-
Steven Murdoch
@sjmurdoch
I have an open PhD position at @uclisec on applying traffic-analysis resistance techniques to protect industrial control systems. Full funding is available for home-fee status students (deadline 15 April). www.ucl.ac.uk/security-crime-science/project-proposals
-
Steven Murdoch reposted
Adam Wagner KC
@AdamWagner1
Important judgment from the Investigatory Powers Tribunal in the case relating to the UK government's reported attempt to obtain "backdoor" encrypted data from Apple devices. Apple is challenging that attempt.
The tribunal rejected the Home Secretary's application that even the "bare details" of the case would be kept secret, on open justice grounds.
Judicial Office
@JudiciaryUK
The judgment in Apple -v- Secretary of State for the Home Department is now available on the judicial website:
www.judiciary.uk/judgments/apple-inc-v-secretary-of-state⦠-
Steven Murdoch reposted
Open Rights Group
@OpenRightsGroup
Saddling small sites with the same duties as huge platforms means many will shutdown in a hammer blow to net plurality.
We'll be left with the Sophieās choice of monopoly services.
URGENT: The government must change the Online Safety Act #saveoursites š action.openrightsgroup.org/save-our-sites-write-your-mp -
Steven Murdoch reposted
Open Rights Group
@OpenRightsGroup
šØ APPLE WITHDRAWS ENCRYPTION TECH FROM UK šØ
The @ukhomeofficeās actions have deprived millions of Britons from accessing a security feature.
UK citizens will be at higher risk of their personal data falling into the hands of criminals and predators.
www.bbc.co.uk/news/articles/cgj54eq4vejo -
Steven Murdoch reposted
Open Rights Group
@OpenRightsGroup
Encryption IS online safety
Keeping data secure is key when hackers are skilled at unpicking accounts.
So why does the government want to make us unsafe by ordering a backdoor to Apple encrypted services?
Sign to save encryption this #saferinternetday.
you.38degrees.org.uk/petitions/keep-our-apple-data-encrypted -
Steven Murdoch
@sjmurdoch
Why is it still possible to write a date where the day of the week doesnāt match the day of the month? This doesnāt need AI; a regular expression would do. I want a big red underline if I ever write āThursday 5 Februaryā. Has someone patented this and spoiled it for everyone?
-
Steven Murdoch reposted
profdeibert
@RonDeibert
Hey everyone.
We're hiring a Systems and Security Technical Lead @citizenlab
Come join us! It's an extraordinary place with extraordinary people ... and *extraordinary* security risks!
Never a dull day, I can promise you that!!
jobs.utoronto.ca/job/Toronto-Systems-and-Security-Technic⦠-
Steven Murdoch reposted
Fabio Pierazzi
@fbpierazzi
[1/4] Opportunity to Apply for a Fully-Funded "UK Home Studentship" for a PhD at @uclcs and @uclisec (deadline: Feb 21, 2025)
(Please note that this opportunity is open only to candidates eligible for "UK Home" fees.) -
Steven Murdoch
@sjmurdoch
The government is reviewing the legal presumption that electronic evidence is reliable. I was one of several experts to comment on this news. www.computerweekly.com/news/366618322/Review-of-legal-rulā¦
-
Steven Murdoch
@sjmurdoch
Itās worth noting that the TikTok ban doesnāt itself target TikTok but instead makes app stores and hosting providers liable for distributing TikTok. I can see why intermediaries are the focus but this seems to set a different precedent than imposing liabilities on TikTok itself.
Steven Murdoch
@sjmurdoch
But, as far as I can tell, the law doesnāt stop ISPs from carrying traffic for a banned app. Could TikTok reinvent themselves as a webapp hosted outside the US? Thereās a gap between what webapps can do as compared to a native app but the gap is shrinking. www.congress.gov/bill/118th-congress/house-bill/7521/text
-
Steven Murdoch
@sjmurdoch
My take on the AI Action Plan ā good: encouraging APIs and standardisation; bad: focus on dataset release rather than controlled access (anonymisation has a poor track record for rich data); concerning: prioritisation of novelty over doing the right thing. www.gov.uk/government/publications/ai-opportunities-actioā¦
-
Steven Murdoch
@sjmurdoch
I spoke to @fattoquotidiano on whether British police have the capability to extract data from a @GrapheneOS phone without the passcode. As far as is publicly disclosed, Cellebrite canāt break the protection but less is known about competing forensics tools.
Stefania Maurizi
@SMaurizi
Today we at @fattoquotidiano run an article on an unprecedented case: British journalist,@richimedhurst, could face years in prison for refusing to hand over his passwords to the police.
[English]
www.ilfattoquotidiano.it/in-edicola/articoli/2025/01/02/b⦠-
Steven Murdoch reposted
UCL InfoSec
@uclisec
Funded opportunity for a PhD studentship on Trustworthy Machine Learning in the UCL InfoSec Research Group. Further details are in the thread below (application deadline 28 January).
Fabio Pierazzi
@fbpierazzi
[1/5] #opportunity to Apply for a Fully-Funded PhD in Trustworthy ML for Malware Detection at @uclcs
Deadline: Jan 28, 2025
Are you passionate about ML and Systems Security? Are you curious to understand root causes performance decay of ML-based malware detection over time? -
Steven Murdoch reposted
Open Rights Group
@OpenRightsGroup
Open Rights Group is hiring š
Our Operations Manager is going on maternity leave in March 2025. We're looking for someone who can ensure that ORG continues to run smoothly behind the scenes.
Apply now.
ā° Closes 17 December at 9am
šļø 14 months FT
ā”ļø app.beapplied.com/apply/xvezlyczeg -
Steven Murdoch
@sjmurdoch
Bug report: a temporary reduction of UK cyber threat to zero through co-ordinated action by adversaries will result in premature termination of the NCSC. CVE pending, CVSS score 9.0 (Critical) CVSS:3.1/AV:N/AC:H/PR:N/UI:N/S:C/C:H/I:H/A:H š
NCSC UK
@NCSC
Today weāve published our 2024 Annual Review ā our roundup of this past yearās cyber security threats and trends, and a look to the road ahead.
Check out the highlights š§µor read the full report š
www.ncsc.gov.uk/collection/ncsc-annual-review-2024 -
Steven Murdoch reposted
UCL Computer Science
@uclcs
Join our MSc Open Days in January:
š Virtual Open Day: 22 Jan (12:00 or 5:00 UK time)
šļø In-Person Open Day: 25 Jan
Discover our 17 MSc programmes, opportunities with industry, scholarships, meet staff, students and alumni & more.
š Register now: www.ucl.ac.uk/engineering/computer-science/postgraduate-m⦠-
Steven Murdoch reposted
Open Rights Group
@OpenRightsGroup
Tomorrow at 1pm GMT FIPR the foundation for information policy research are holding an expert panel on the topic of #e2ee and chat controls. You can sign up to watch it online at www.eventbrite.co.uk/e/scrambling-for-safety-online-tickeā¦
-
Steven Murdoch reposted
David MarugƔn
@RadioHacking
Mucha gente me ha preguntado si en EspaƱa funciona algo como el NOAA Weather Radio de EE.UU. La respuesta es NO. AquĆ dependemos de #esalert, pero en la Ćŗltima #dana algunas personas dicen que NO recibieron las alertas. Esto no es un fallo del sistema: hay móviles no compatibles, sin cobertura o mal configurados. Es-Alert es muy Ćŗtil, pero quizĆ”s podrĆa complementarse. šØš§ļøš»
En EE.UU., NOAA Weather Radio (NOAA es algo similar a nuestra AEMET) emite alertas en radios y televisores, independientes de internet o móviles. ĀæCómo podrĆamos implementar algo similar en EspaƱa, aprovechando lo que ya tenemos? AquĆ algunas ideas "locas", por si algĆŗn polĆtico lo lee y se mueve:
1ļøā£ Radio FM con RDS:
Las radios de coche y hogar ya usan el sistema RDS (Radio Data System), que permite enviar mensajes de emergencia . Un aviso por inundación, por ejemplo, podrĆa activarse automĆ”ticamente en todas las radios FM de la región afectada.
2ļøā£ Radio DAB (Digital Audio Broadcasting):
La infraestructura #dab ya estĆ” presente en muchas ciudades de EspaƱa. Estas emisoras podrĆan configurarse para emitir alertas automĆ”ticas con mensajes en los receptores compatibles. DAB es obligatorio en coches desde hace algunos aƱos.
3ļøā£ Televisión (TDT):
Las cadenas de TV podrĆan emitir alertas breves mediante subtĆtulos o interrupciones automĆ”ticas, como se hace en EE.UU. con el Emergency Alert System (EAS). AsĆ, cualquier persona viendo TV recibirĆa el aviso en tiempo real. No solo para catĆ”strofes, tambiĆ©n para avisos de Seguridad Nacional y otros.
šÆ Algunas Ventajas:
Cobertura total: Radios FM/DAB y la TDT llegan a zonas rurales o sin cobertura móvil.
Redundancia: Funciona incluso cuando fallan internet o las redes móviles.
Bajo coste: Aprovecha infraestructuras existentes como emisoras de radio comerciales, RNE y canales de TV.
Todo estĆ” inventado. En EE.UU., NOAA Weather Radio funciona y es accesible, confiable y salva vidas. Ya digo que son ideas mĆas "locas", pero... en EspaƱa ĀæPodrĆamos conseguir algo asĆ? #radio #emergencias š»šŗšØ -
Steven Murdoch reposted
UCL Engineering
@UCLEngineering
āCard not receivedā fraud - where cards are intercepted in the post - is rare, but the losses incurred are increasing.
Steven Murdoch (@uclcs) says that if criminals can intercept post, then it is possible they can apply for account details to change.
www.theguardian.com/money/2024/nov/04/expecting-a-new-cre⦠-
Steven Murdoch reposted
The Inner Temple
@TheInnerTemple
It's your last chance to book your spot to our 22 October event 'The Use of Electronic Evidence and the Law' where we will discuss the reliability of electronic evidence š»š±
šļø 22 October, 6pm
šIn person and online
šļø Book: nrtm.pl/3N7gcxB -
Steven Murdoch
@sjmurdoch
Along with Sir Peter Fraser, I'll be speaking at the Inner Temple on the reliability of electronic evidence. The event is open to the public, so if you're interested in the topic, you can join in person or online.
The Inner Temple
@TheInnerTemple
Learn more about the role of computer-generated evidence in legal disputes š»š± We will be discussing the potential impact of computer bugs on the reliability of electronic evidence.
šļø 22 October, 6pm
šIn person and online
šļø Book: nrtm.pl/3N7gcxB -
Steven Murdoch
@sjmurdoch
I've written about how the legal system might better handle electronic evidence, but computer systems could also be designed to facilitate the production of reliable evidence. I discussed these ideas at the CANS Workshop murdoch.is/talks/
-
Steven Murdoch reposted
Paul Amery
@newmoneyreview
#cybercriminals and those #policing #payments are in a never-ending, high-tech game of cat and mouse
Listen in to the latest @newmoneyreview #podcast for more ā¬
My guest is @sjmurdoch, professor of security engineering at @ucl and head of @uclisec
newmoneyreview.com/index.php/2024/09/30/the-cat-and-mouse⦠-
Steven Murdoch
@sjmurdoch
There are divergences developing in the liability for push payment fraud. The UK is moving from sender bank to 50:50 sender/receiver. US proposals went from receiver to the same 50:50 model as the UK. The EU is the sending bank, but social network websites might have to pay, too.
-
Steven Murdoch
@sjmurdoch
While a failure in CrowdStrike Falcon took down critical infrastructure in July, the widescale harm was due to Microsoftās market share and design choices in Windows. I spoke to CBC News about kernel-mode software and competition lawās role in the fiasco. youtu.be/s4hoEjRh1Eo
-
Steven Murdoch
@sjmurdoch
Both the UK and EU are putting in place measures to protect victims of Authorised Push Payment fraud. This time last year, the UK had the stronger proposals, but now they have switched as the EU expands protections and the UK waters them down š§µ
Post not available here, view on X
Steven Murdoch
@sjmurdoch
This roughly matches the UKās original proposal. However, in response to banking industry lobbying, the UKās Payment Systems Regulator now proposes to allow banks to refuse to reimburse the first Ā£100, and the customer be liable for losses above Ā£85,000. www.psr.org.uk/news-and-updates/latest-news/news/psr-confā¦
Steven Murdoch
@sjmurdoch
Interestingly, the EU proposal introduces liability for āelectronic communications service providersā. The banking industry has been lobbying for years to get (primarily) Facebook to cover the cost of reimbursements. Thereās no UK proposal for this (so far).
-
Steven Murdoch
@sjmurdoch
Deep neural networks outperform traditional methods in a wide range of applications, but their opacity can hide malicious behaviour. @mavroudisv writes about his work at the @turinginst on efficiently detecting backdoors in deep reinforcement learning. www.benthamsgaze.org/2024/08/07/mitigating-deep-reinforceā¦
Vasilios Mavroudis
@mavroudisv
š¤ Excited to announce our upcoming talk at @BlackHatEvents on Deep Reinforcement Learning Backdoors!
š§ Deep Reinforcement Learning is revolutionizing industries but what happens when these AI agents are compromised? š¤
www.blackhat.com/us-24/briefings/schedule/
šØ Our talk will dive into the emerging threat of backdoors in DRL. We'll show how malicious actors can embed hidden functionality in RL models, posing significant risks. This isn't just a future concernāit could be happening now!
See you at #blackhat2024 #bhusa !
šļø August 7, 2:30pm
š South Seas AB, Level 3 -
Steven Murdoch
@sjmurdoch
The views of security experts on Pavel Durovās arrest seem contradictory: criticising Telegram but tentatively defending Durov. The underlying reason is concern of what precedent the arrest might set for how secure messaging platforms work š§µ
Post not available here, view on X
Steven Murdoch
@sjmurdoch
concern is that Franceās action will lead to encrypted messengers to be treated the same way as social networks, and be expected to apply content-based controls and disclose user content. Such requests are impossible to comply with unless their security is substantially weakened.
Steven Murdoch
@sjmurdoch
I think experts are worried about whether the test for criminal complicity shifts from knowingly facilitating illegal activities to choosing to design a messaging application with the principle of data-minimisation and implementing strong security through modern encryption.
-
Steven Murdoch
@sjmurdoch
At @STN_Airport, notorious for an unpleasant experience (long queues, too few seats, routes forcing passengers through shops, ā¦) someone decided that the real problem is the signs saying āWait for gateā and should instead be āRelaxā.
Steven Murdoch
@sjmurdoch
If you want to take the direct route to your gates and avoid the crowded shopping area, youāll be charged Ā£10 per person for the privilege.
-
Steven Murdoch
@sjmurdoch
Magnetic stripe payment cards are being phased out, however more secure (but complex) technologies are not necessarily better for fraud victims. I spoke to CBC Radio about why this might be. www.cbc.ca/listen/live-radio/1-1414/clip/16088571
-
Steven Murdoch
@sjmurdoch
Can I just express my frustration that even if you pay for IEEE Digital Library access, you donāt get access to the current IEEE (Euro) Security and Privacy proceedings because the IEEE Computer Society want to be paid separately. They really arenāt making friends this way.
-
Steven Murdoch
@sjmurdoch
I spoke to @chrisbaraniuk for a @BBCNews article on the uncertain future of the magnetic stripe, featuring how I managed to lock myself out of my hotel room (!). www.bbc.com/news/articles/c51yd4j4lnvo
Steven Murdoch
@sjmurdoch
Iām pleased the article managed to include one of the more subtle points ā better security features arenāt always better for fraud victims.
-
Steven Murdoch reposted
REPHRAIN National Research Centre
@REPHRAIN1
š¢ Our response to @Ofcom's consultation on āProtecting Children from Harms Onlineā is out now!
Written in collaboration with @PolicyBristol , you can find our full response at bpb-eu-w2.wpmucdn.com/blogs.bristol.ac.uk/dist/1/670/fileā¦
#childsafety #onlineharms #digitalsafety #protectingchildren #rephrain -
Steven Murdoch reposted
PETS
@PET_Symposium
PETS/PoPETs is run by volunteers and we're looking for more people to participate. Please fill out this form if you'd like to help out!
forms.gle/wAadQRZWXLyDAQJA8 -
Steven Murdoch reposted
Stephen Snyder
@StephenProducer
Excellent explanation of the #crowdstrike disruption to Windows machines everywhere
@sjmurdoch speaks with @TheWorld's @CarolHills, tells how it happened and why it's likely to happen again
6-minute listen
theworld.org/segments/2024/07/19/crowdstrike-cleanup -
Steven Murdoch
@sjmurdoch
Todayās a good day to be extra-nice to your sysadmins. If your organisation uses Crowdstrike, they will have to visit, in person, every single Windows PC. Automation doesnāt work if your computers wonāt boot. Maybe get them something nice for Sysadmin Day next week.
-
Steven Murdoch reposted
PETS
@PET_Symposium
If you're not joining us in Bristol, you can watch FOCI via the livestream at www.youtube.com/watch?v=noesJ2GfU9s ! #pets24
-
Steven Murdoch reposted
UCL Computer Science
@uclcs
@sjmurdoch quoted in this BBC article on generating random numbers and why this is important for cybersecurity:
The search for the random numbers that run our lives www.bbc.com/future/article/20240704-the-search-for-the-ra⦠via @BBC_Future
@uclisec -
Steven Murdoch reposted
PETS
@PET_Symposium
Registration will be open until July 15. If you tried to register over the past few days and the link didn't work, please try again. Sorry for the glitch! Please share!
petsymposium.org/2024/registration.php
#pets24 -
Steven Murdoch reposted
UCL Computer Science
@uclcs
@sjmurdoch quoted in this article about the #postofficeinquiry evidence of Gareth Jenkins from #fujitsu:
@uclisec
ComputerWeekly
@ComputerWeekly
Experts shocked by āextraordinaryā claim made by Post Office IT expert witness www.computerweekly.com/news/366590300/Experts-shocked-by-ā¦
-
Steven Murdoch
@sjmurdoch
I spoke to @Karlfl from @ComputerWeekly about Gareth Jenkinsā extraordinary statement at the @PostOffInquiry ā āI don't think I was in a position to say that Horizon was working correctly at the timeā ā despite declaring that the statement was accurate. www.computerweekly.com/news/366590300/Experts-shocked-by-ā¦
-
Steven Murdoch reposted
Students' Union UCL
@TheUnionUCL
Today is the last day to apply to vote via post in the #generalelection š©
Not sure where you'll be on 4 July? Sort your vote now and make sure you have your say, no matter where you are in the world š
ā°Be quick, you have until 5pm today!
www.gov.uk/apply-postal-vote -
Steven Murdoch reposted
PETS
@PET_Symposium
Want to present a poster at PETS? Here's the call for proposals:
petsymposium.org/2024/cfposters.php
We're evaluating submissions on a rolling basis, with a deadline of July 10.
#pets24 -
Steven Murdoch reposted
Electoral Commission
@ElectoralCommUK
āIf you havenāt registered to vote by midnight on Tuesday 18 June, you will not be able to vote in the general election on 4 Julyā You have 5 days leftš³ļø Register to vote: www.gov.uk/register-to-vote
-
Steven Murdoch reposted
PETS
@PET_Symposium
We have a program!
petsymposium.org/2024/program.php
#pets24 #privacy -
Steven Murdoch reposted
Electoral Commission
@ElectoralCommUK
Check if you have an accepted form of photo ID: www.electoralcommission.org.uk/voting-and-elections/voterā¦
Donāt have an accepted form of ID?
For England, Scotland, or Wales: Apply for free voter ID by 5pm on 26 June.
For Northern Ireland: Apply for an Electoral Identity Card by 11:59pm on 26 June. -
Steven Murdoch
@sjmurdoch
Itās the pre-election period so civil servants (including research funders) are restricted in what they say publicly. This, however, doesnāt apply to academics (despite revoked guidance from RCUK still circulating). @dkernohan summarises the situation. wonkhe.com/blogs/do-you-have-a-voice-in-the-election-campā¦
-
Steven Murdoch
@sjmurdoch
Thereās a lot to unpick from Paula Vennellsā testimony, but one is the acceptance that there were no bugs in Horizon. In reality, this should be a massive red flag that IT are delusional and/or lines of communication are so dysfunctional that nothing you hear can be trusted.
Nick Wallis
@nickwallis
JB you tell us time and time again that you have been told time and time again that there were no bugs in H. isn't this world-changing info for you
PV yes it was information that changed - but i was told they were incidents which had been dealt with and they were red-herrings and none of it affected the JFSA cases
JB answer my direct question. you had been told for six years there were no bugs. now you were told there were bugs, and your reaction was they don't matter?!
PV I said in my statement there were always glitches in the system - egg timer, blue screens etc
JB [interrupts] let's go back to your WS -
Steven Murdoch reposted
Ben Goldacre
@bengoldacre
STUDENTS: REGISTER TO VOTE RIGHT NOW!
The law is as follows.
1. You can register at home AND at your term-time address, if that's more convenient for you.
2. You can CHOOSE on the day where to vote.
3. But you can ONLY legally vote in ONE place on the day. -
Steven Murdoch reposted
UCL Computer Science
@uclcs
Delighted to announce we have been awarded Athena Swan Gold status!āļø
We are first computer science department in the UK to achieve this honour. While there's much work to be done, we're excited about our progress and the journey ahead.
Find out more:
www.ucl.ac.uk/computer-science/news/2024/may/ucl-computer⦠-
Steven Murdoch reposted
REPHRAIN National Research Centre
@REPHRAIN1
Check out our funding call!
We're looking for project proposals researching online harms and privacy - details on our website!
rephrain.ac.uk/strategic-funding-calls
#rephrain -
Steven Murdoch reposted
REPHRAIN National Research Centre
@REPHRAIN1
Apply for a stipend to attend Privacy Enhancing Technologies Symposium 2024 (PETS2024)!
Further details can be found here: petsymposium.org/2024/stipends.php
#rephrain -
Steven Murdoch reposted
Lorenzo Cavallaro
@lcavallaro
š¢PostDoc on Trustworthy AI for Systems Security on Code Representation Learning @uclisec @uclcs @ucl collab w. Suman Jana @Columbiaš¢
Excited on (AI + program analysis) for security? www.ucl.ac.uk/work-at-ucl/search-ucl-jobs/details?nPostinā¦
Appetite? See S2Lab papers + arxiv.org/abs/2308.03312 (ICML 2024) RTš -
Steven Murdoch
@sjmurdoch
Interested in what weāve been working on at @uclisec? Thereās now a list of group publications available on our website. sec.cs.ucl.ac.uk/publications/
Steven Murdoch
@sjmurdoch
For those curious about the technology, the back end is in @rustlang using the Rocket framework, which collects and de-duplicates the publication records through the profiles.ucl.ac.uk API. The front end is (one line of) @htmx_org code.
-
Steven Murdoch reposted
The Tor Project
@torproject
The @PET_Symposium is inviting nominations for the 2024 Caspar Bowden Award for Outstanding Research in Privacy Enhancing Technologies! šļø The deadline for submissions is May 10th. š© Nominations & more info: petsymposium.org/award/cfn.php
PETS
@PET_Symposium
You are invited to submit nominations for the 2024 Caspar Bowden Award for Outstanding Research in Privacy Enhancing Technologies!
Any paper that has appeared in any peer reviewed venue between April 1, 2022 and March 31, 2024 is eligible.
1/2 -
Post not available here, view on X
Steven Murdoch
@sjmurdoch
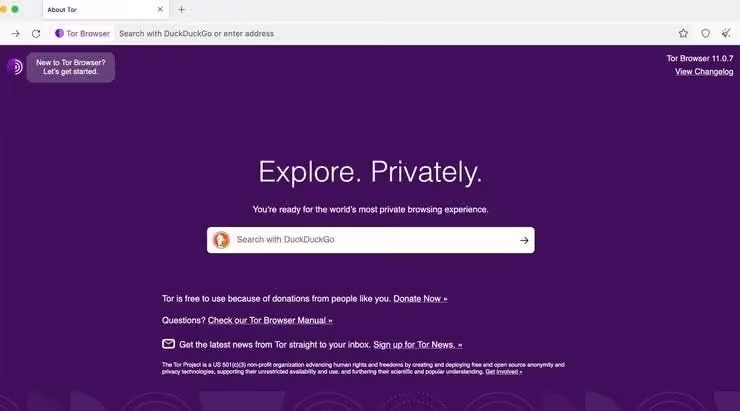
Another dark web myth is that it recommends people view disturbing content. Hereās the Tor Browser start page. It doesnāt suggest anything. You need to know its address to view a dark web site (onion service). There are onion service search engines but these are not offered here.
-
Steven Murdoch
@sjmurdoch
Those watching #mrbatesvsthepostoffice might have the impression that the mistakes made have been recognised and learned from. Thatās sadly not the case. Hereās a former Post Office investigatorās closing statement, referring to a subpostmaster whose conviction was overturned.
-
Steven Murdoch
@sjmurdoch
Iāve had to do plenty of IT security compliance training and itās universally bad. The problem is that the productās main goal is to show that everyone did it ā so the focus is on reporting dashboards, increasing engagement, range of languages, and cost ā not quality. 1/2
Steven Murdoch
@sjmurdoch
A good rule of thumb is that if the training warns about public wifi (a negligible risk for most people), then itās bad. If it doesnāt advise people to use a password manager thatās another red flag (password managers are far better than reusing passwords). 2/2
-
Post not available here, view on X
Steven Murdoch
@sjmurdoch
Detailed statistics circulate inside the industry, and Iāve seen leaked details, but banks have generally agreed to not compete on security, even when there are huge differences between them. Neo-banks have sometimes tried to break ranks but without much success. 2/3
-
Steven Murdoch
@sjmurdoch
The Turing Insitute has published a report on the end-to-end encryption and online safety debate. It proposes ways to encourage more productive discussions on the topic and while this might not create universal consensus, it could foster better understanding between stakeholders.
The Alan Turing Institute
@turinginst
š The āsecurity vs #privacyā argument in the #encryption debate is flawed and preventing meaningful progress
āļø In a new blog, CETaS researcher Sam Stockwell makes the case for why we need a new multistakeholder approach to keep people safe online www.turing.ac.uk/blog/new-and-inclusive-approach-privacy-⦠-
Steven Murdoch
@sjmurdoch
Itās far from a secret but not widely known that safety critical systems often have no cryptography because the complexity and key-management would introduce risks. Combined with fail-safe behaviour, this results in denial-of-service attacks being relatively easy to execute. 1/2
Lukasz Olejnik
@lukOlejnik
This radio-stop signal in Poland IS NOT a cyberattack. Do not call it as such. No security boundaries are bypassed, no breaking of any IT systems involved. Please keep to the facts. Thank you. www.bbc.com/news/world-europe-66630260
-
Steven Murdoch
@sjmurdoch
Privacy-enhancing technologies research is important, but a lot is building tools for companies to maintain their business practices while granting users a little bit of privacy. Iām more interested in PETS that allow people to unilaterally assert their privacy, e.g. Tor š§µ 1/3
Naomi Brockwell priv/acc
@naomibrockwell
Saying:
"we need to rely on politicians to repeal x law and y law, without this we'll never have real privacy"
is a defeatist attitude.
You can start reclaiming your own privacy now, by learning how to use privacy technology that already exists šŖ
Steven Murdoch
@sjmurdoch
One of the few places where this idea was explored is the @hdinetwork āSurveillance Resistanceā theme (Alan Munro & @m_j_chalmers). The paper resulting from my work on this theme will be appearing at the 2024 @PET_Symposium. 2/3
-
Steven Murdoch
@sjmurdoch
I run two Tor nodes in universities (UCL and Cambridge) and Iām very happy to support the @eff and @torproject, working together in setting up more.
EFF
@EFF
Universities are the perfect place to run a Tor relay. Let's get more universities to do it. www.eff.org/deeplinks/2023/08/announcing-tor-university-cā¦
-
Post not available here, view on X
Steven Murdoch
@sjmurdoch
It is so complex to allow for prolonged offline operation in the case of communications failure. I would not at all be surprised if such communication failures are more rare than failures resulting from certificate screwups.
-
Steven Murdoch
@sjmurdoch
Building a web app in Rust was an overall good experience. The result was fast and (presumably) safe. Getting code to compile was painful at times but once it did was generally correct. I hope the former will improve as I build up experience but the latter is impressive.
-
Post not available here, view on X
Steven Murdoch
@sjmurdoch
Many expected the blue tick would be viewed with embarrassment in some circles as an āI paid Elon $8ā badge. Now itās a āmaybe this person is importantā badge too. This is good news for people who want to look important but not so good for those assessing account credibility. 2/2
-
Post not available here, view on XPost not available here, view on X
Steven Murdoch
@sjmurdoch
Vote by mail is permitted in the UK, but ballots must be received by election day to be counted. In the US, it is common to allow ballots to be received a week after election day (as long as they are postmarked before election day). When elections are close, this matters. 3/
Steven Murdoch
@sjmurdoch
In the UK, if someone claims that somebody else has voted using their identity, they can still vote but their vote will be kept separate. If these votes would not make a difference, it is ignored, but if the election is close, the fraudulent ballot needs to be pulled out. 4/
-
Post not available here, view on X
Steven Murdoch
@sjmurdoch
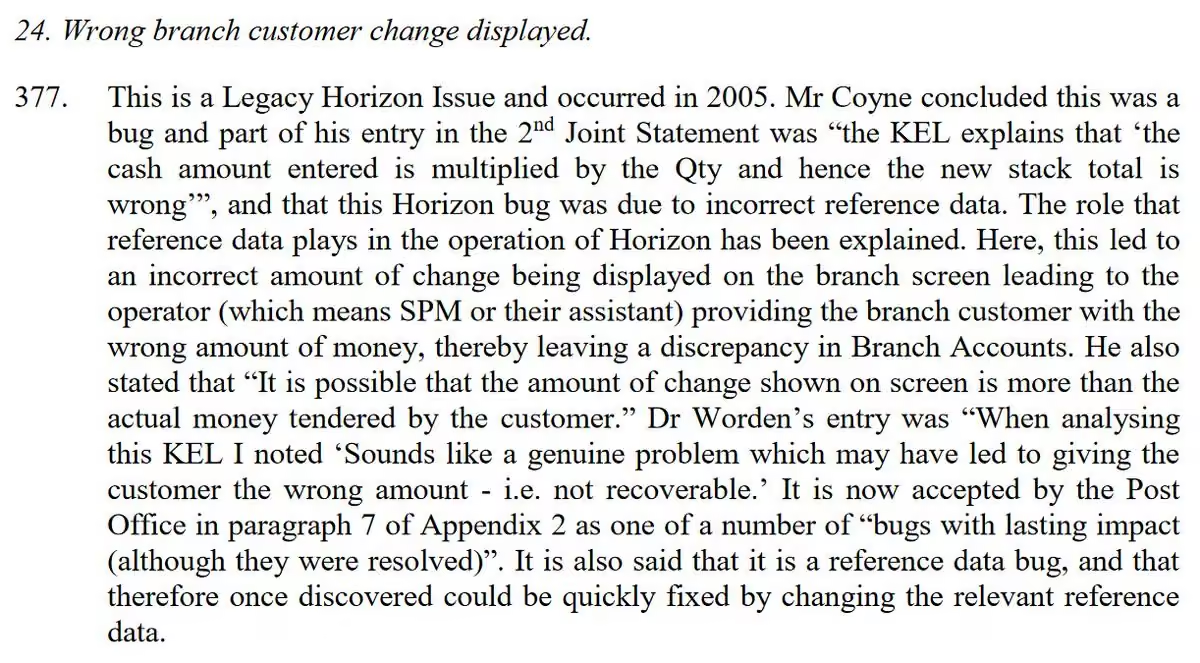
Reference Data controlled how Horizon operated but was separate from the Horizon code. The Reference Data was not subject to the same level of change control as the code, so was quicker to update. This makes sense if the DSL is sufficiently constrained as to eliminate errors. 2/
Steven Murdoch
@sjmurdoch
However, it looks like the DSL was so powerful as to enable the violation of double-entry accounting requirements. Consequently, reference data errors could and did result in subpostmasters encountering shortfalls. For example (from the Horizon Judgement) 3/
-
Post not available here, view on X
Steven Murdoch
@sjmurdoch
In his report, Jonathan Swift QC characterised the Post Office statement as āincompleteā. I assume because it only talked about altering existing transactions and not about adding new transactions that alter balances. 2/
-
Post not available here, view on X
Steven Murdoch
@sjmurdoch
For example, as Levy & Robinson said, ādetails matterā, particularly over which harms are intended to be mitigated. The solutions needed and the environment in which they operate critically depends on what problem they are supposed to address. 2/
Steven Murdoch
@sjmurdoch
And one issue Iāve mentioned before ā the focus on client-side scanning is detracting attention and resources from safer and more readily accepted approaches for which progress could be made. 3/
Post not available here, view on X
Steven Murdoch
@sjmurdoch
Most importantly, having an ongoing dialogue is helpful in facilitating progress. Technology or policy developed in secret and then dropped from the sky is liable to have flaws and meet an unwelcome reception. Events like this workshop should be encouraged. /end
-
Post not available here, view on X
Steven Murdoch
@sjmurdoch
I worry that those advocating for end-to-end security to be compromised are drawing attention and resources away from far less controversial child-protection methods (both technical and non-technical) that could mitigate serious harm while preserving security and privacy. 2/
Steven Murdoch
@sjmurdoch
If end-to-end security is here to stay (and there is good reason for it to be so), we should be investing in research on child-protection measures that are compatible with it rather than engaging in endless debates about restricting it. āPolitics is the art of the possibleā /end
-
Post not available here, view on X
Steven Murdoch
@sjmurdoch
I was an expert witness in this appeal, so wonāt be commenting further, but Iām sure others are more than capable of giving their opinion, e.g. @jennifercobbe @mikarv @DouweKorff @WebDevLaw @cyberleagle @lukOlejnik @PaulbernalUK @neil_neilzone @lilianedwards @MissIG_Geek
Steven Murdoch
@sjmurdoch
...and yes, I do know this decision is of the First-tier Tribunal (General Regulatory Chamber) and not the Information Rights Tribunal, but I think more people would recognise the term Information Rights than General Regulatory Chamber.
-
Post not available here, view on X
Steven Murdoch
@sjmurdoch
Although the human-readable part of the passport would show āSex: Xā in this case, the standard for the machine readable part only permits the sex field to be M, F or unspecified/omitted (the < character).
-
Steven Murdoch
@sjmurdoch
If the discussion on the Online Safety Bill at the @uclisec event got you interested in learning more, I recommend this podcast where @WebDevLaw talks to @jilliancyork and @kkomaitis, particularly on the provisions relating to age verification and legal-but-harmful content.
-
Steven Murdoch
@sjmurdoch
This is bad but the reigning champion of unethical phishing simulation is a fake email from HR asking for your home address DURING A LARGE ROUND OF REDUNDANCY NOTIFICATIONS!
šyāØ
@ki_bydesign
Got a email from my job saying all employees get a $30 gas card to alleviate high gas prices (we are required to drive clients around). Why when I went to sign up it sent me another email saying I was phished by my tech department as a tester and then got assigned training???š„²š
-
Steven Murdoch
@sjmurdoch
And many thanks to @emilianoucl for all heās done as head of research group, especially as the pandemic has made it a particularly challenging period.
UCL InfoSec
@uclisec
Congratulations to @sjmurdoch, new Head of the InfoSec Research Group (sec.cs.ucl.ac.uk)!
-
Post not available here, view on X
Steven Murdoch
@sjmurdoch
This example illustrates the harm caused by the UK libel regime. It allows powerful individuals and organisations to avoid scrutiny due to the eye-watering costs of defending a defamation accusation, even when itās in the public interest.
-
Post not available here, view on X
Steven Murdoch
@sjmurdoch
Thanks to @michaelpmagrath from @OneSpan for drawing this development to my attention.
-
Steven Murdoch
@sjmurdoch
Two more days for you to submit feedback on how to evaluate client-side scanning technologies for CSAM prevention and detection. Please send these to the @REPHRAIN1 team by Friday 8 April.
REPHRAIN National Research Centre
@REPHRAIN1
Weāve released our Scoping the evaluation of CSAM prevention and detection tools in the context of E2EE environment for public consultation!
The document and guidelines for feedback can be found on our website at rephrain.ac.uk - details below!
#rephrain