Burp AT can go through Scanner findings in your project, investigate them, and help validate the results.
You can also send requests from Burp AT to Repeater or Intruder for further testing.
Burp Suite
Burp Suite is a proprietary software tool for security assessment and penetration testing of web applications. It was initially developed in 2003–2006 by Dafydd Stuttard to automate his own security testing needs, after realizing the capabilities of automatable web tools like Selenium. Stuttard created the company PortSwigger to flagship Burp Suite's development. A community, professional, and enterprise version of this product are available. More on Wikipedia
-
Burp Suite
@Burp_Suite
This media couldn't be displayed. See it on the original post. -
Burp Suite
@Burp_Suite
Do you actually apply new research in your pentests?
Read the whitepaper ✅
Understand the whitepaper 🤷♂️
Revisit the basics 📖
Read whitepaper again ✅
Solve the labs 🏆
Mastery achieved 🥷 ☠️
But do you apply this to your next engagement?
Now, @PortSwiggerRes is bringing their research and methodology into Burp AT as a growing library of skills, with new techniques available to your agents as soon as they’re published.
Find out more 👇 👇
Burp Suite
@Burp_Suite
Read the blog post: portswigger.net/burp/burp-at/research-skills
Try Burp AT: portswigger.net/burp/burp-at -
Burp Suite
@Burp_Suite
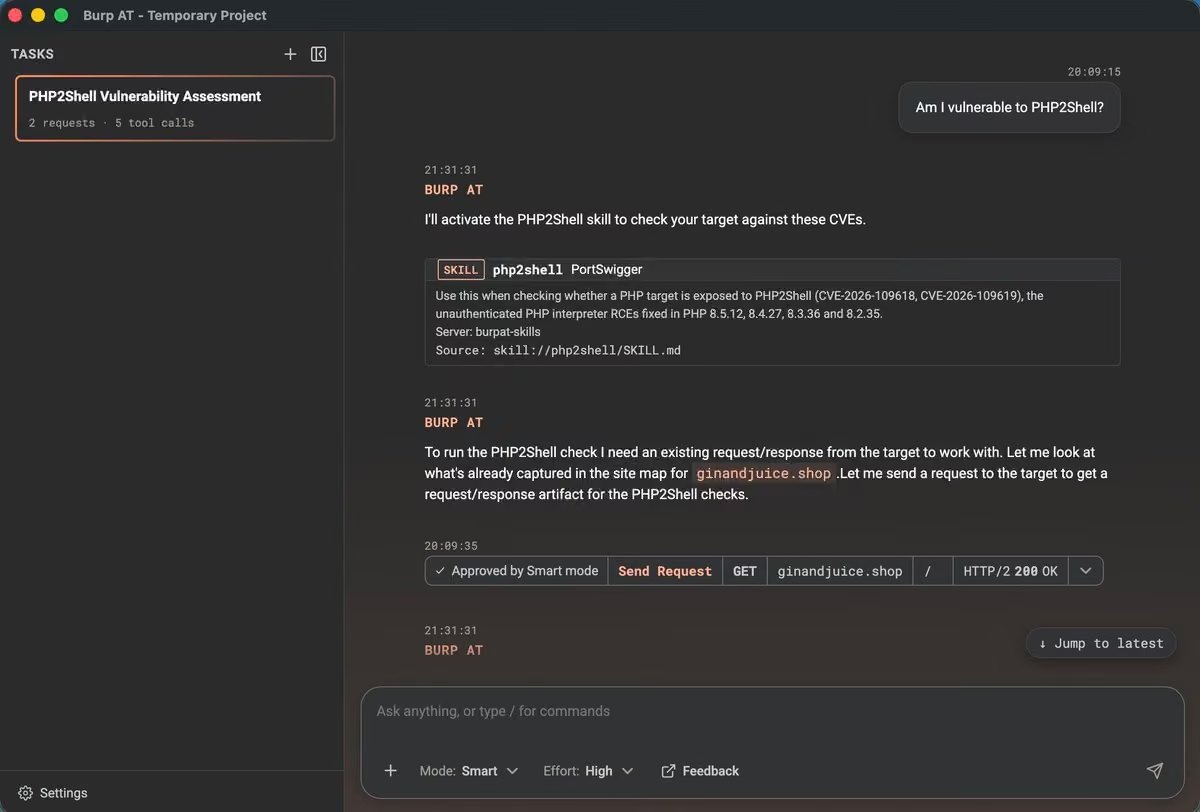
We're in a whole new era of security testing. Just take a look at this video of Burp AT hunting down PHP2Shell.
This is true human hacker augmentation, the perfect combo of human intelligence and AI for offensive security work. It can draw on relevant traffic, issues, and discoveries already in the Burp project and interface that you already know.This media couldn't be displayed. See it on the original post. -
Burp Suite
@Burp_Suite
One of the biggest problems with most of the current AI-assisted hacking products is that auditing what the agent actually did is very difficult.
Burp AT saves agent requests and tool activity in your project so that you can easily review the work behind a skill's conclusion.
More details 👇
portswigger.net/burp/burp-at -
Burp Suite
@Burp_Suite
Here's Gareth Heyes using Burp AT to bypass CSP and exfiltrate credentials.
Gareth Heyes \u2028
@garethheyes
Help your 'self' to some credentials.
Content-Security-Policy: default-src 'none'; form-action 'self';
Learn how to bypass this CSP and exfiltrate credentials using a Burp AT skill. Link to blog post 👇 -
Burp Suite
@Burp_Suite
Watch Burp AT turn a boring header injection finding becomes a critical desync vulnerability!
Tom Stacey shows a Burp AT skill work from the initial finding through validation and exploitation. Write-up here 👇
portswigger.net/research/making-http-header-injection-cri… -
Burp Suite
@Burp_Suite
Burp AT brings a whole new level of automation to your favorite intercept proxy!
We are very excited to see what you'll do with it.
Tom Stacey
@t0xodile
Burp scanner now detects request-header injection, and Burp AT contains a researcher-crafted skill that weaponises it into a high-impact PoC with a single prompt! It'll even do CRLF-Powered Tunnelling if full desync exploitation isn't viable. Read below for full details:
-
Burp Suite
@Burp_Suite
Want agents that can apply the latest techniques from @PortSwiggerRes on your behalf?
This marks the beginning of an exciting new approach where we can ship new and updated skills to Burp AT at any time in a matter of minutes. The next time you start an agent, it automatically picks up the changes without any explicit updates required at your end. This means Burp AT agents stay up-to-date with the latest output from @albinowax, @garethheyes, @zakfedotkin, and @t0xodile on your behalf.
Look out for more PortSwigger Research skills coming soon.
Find out more about Burp AT: portswigger.net/burp/burp-at
Tom Stacey
@t0xodile
Burp scanner now detects request-header injection, and Burp AT contains a researcher-crafted skill that weaponises it into a high-impact PoC with a single prompt! It'll even do CRLF-Powered Tunnelling if full desync exploitation isn't viable. Read below for full details:
-
Burp Suite
@Burp_Suite
You can now schedule autonomous tests with Burp AT across your application estate.
Investigate more applications, more deeply and more often, with scope enforced by Burp and your team able to steer or stop tests.
portswigger.net/burp/burp-at/enterprise/announcement -
Burp Suite
@Burp_Suite
At #owasp Global AppSec USA today? Find PortSwigger at booth G14 for live Burp AT demos, AppSec conversations, and your vendor passport stamp. Plan your visit: portswigger.net/blog/heading-to-san-francisco-meet-portsw…
-
Burp Suite
@Burp_Suite
Heading to #owasp Global AppSec USA? Meet PortSwigger at booth G14, 5–6 Nov in San Francisco. See Burp AT live, talk AppSec, and get a first look at something new for AppSec teams. portswigger.net/blog/heading-to-san-francisco-meet-portsw…
-
Burp Suite
@Burp_Suite
🔎 📰 There are now multiple ways you can detect PHP2Shell using the Burp Suite ecosystem: Pro, DAST, and Burp AT. For details, check out the link in the comments 👇
Burp Suite
@Burp_Suite
PHP2Shell x Burp Suite: Detection in your hands within a day of disclosure: portswigger.net/blog/php2shell-x-burp-suite-detection-in-…
-
Burp Suite
@Burp_Suite
Your next idea doesn’t have to wait. 💬
Queue your next prompt while Burp AT is working. Queued prompts run one at a time, in order, once the current work finishes.
Keep up with your own train of thought while testing.
Get started with Burp AT 👉 portswigger.net/burp/burp-at?ps_source=x&ps_medium=social…
#burpat -
Burp Suite
@Burp_Suite
When testing for vulnerabilities as dangerous as PHP2Shell, you need you need agentic AI that combines capable reasoning with enforced boundaries. You need Burp AT.
Try PortSwigger's new PHP2Shell skill in Burp AT today! share.portswigger.net/tryburpat -
Burp Suite
@Burp_Suite
Burp AT works best when it knows what you know. 📄
Upload scoping docs, previous reports and API specs to a task so it starts from your context, not a blank slate.
Discover Burp AT: portswigger.net/burp/burp-at?ps_source=x&ps_medium=social…
Your context. Your control.
#burpat -
Burp Suite
@Burp_Suite
🚨 PHP2Shell detection is now available in Burp Suite Professional & Burp Suite DAST.
Most of the web is powered by PHP, which means most of the web is vulnerable to these critical unauthenticated remote code execution flaws (CVE-2026-109618 / 109619). You can already detect it in Burp Suite using:
🟧 ActiveScan++ v2.0.13 (portswigger.net/bappstore/3123d5b5f25c4128894d97ea1acc4976)
🟧 Bambda scan checks (github.com/PortSwigger/bambdas/tree/main/CustomScanChecks)
🟧 BChecks (github.com/PortSwigger/bchecks)
Start scanning for the vulnerability now → portswigger.net/bappstore/3123d5b5f25c4128894d97ea1acc4976 -
Burp Suite
@Burp_Suite
How is AI changing the way you pentest?
We’ve just launched our new survey, Pentesting in the age of AI, and we’d love your take on the tools you use, what’s working and where human judgement still matters.
⏱️ The main section takes about 5 minutes.
🎁 Complete the optional section to enter a prize draw for one of five $100 Amazon vouchers.
Share your experience by completing the survey below👇
conjointly.online/study/674513/igr6lluyhztpflk2sgpk -
Burp Suite
@Burp_Suite
Spotted something interesting in Repeater? 🔎
Send the request to Burp AT from Repeater, Intruder, Logger or Organizer and hand over the investigation without starting from scratch.
You decide what it picks up. You're in control.
Get started 👉 portswigger.net/burp/burp-at?ps_source=x&ps_medium=social…
#burpat -
Burp Suite
@Burp_Suite
Repeat the same steps on every engagement? 🧩
Turn them into a custom skill once and Burp AT follows your methodology every time.
Your methodology. Your control.
Learn more 👉 portswigger.net/blog/burp-at-whats-new-since-black-hat
#burpat -
Burp Suite
@Burp_Suite
Got a hunch you can’t get past a WAF? 🎯
Set an outcome with /goal and leave Burp AT to crack on. It works until it gets there, decides it can’t, or hits a limit.
You set the goal. You stay in control.
Read more 👉 portswigger.net/blog/burp-at-whats-new-since-black-hat
#burpat -
Burp Suite
@Burp_Suite
You're in control with Burp AT.
The latest update makes sure Burp AT works your way:
📖 Custom skills for your methodology
🎯 /goal to keep it working until it gets there
💡 Requests, issues and docs as context
🚧 Reject, redirect or approve tool calls
#burpat
Burp Suite
@Burp_Suite
Read more about what's landed in Burp AT in this new blog post👇
portswigger.net/blog/burp-at-whats-new-since-black-hat -
Burp Suite
@Burp_Suite
“Burp AT integrates seamlessly with Burp’s existing tooling and functionality, instead of being just another chat interface to an LLM.”
Burp AT vs Juice Shop, Safe Mode on, no hints: 3 unintended RCEs and a critical handlebars CVE (CVSS 9.2).
@ElliottSaysWhat, web app pentester at Leidos, shares what to feed it, how to steer it and what it cost.
brandon-t-elliott.github.io/achieving-rce-in-unintended-w… -
Burp Suite
@Burp_Suite
“Asking Burp AT to analyze my progress based on the proxy history/sitemap/scans and suggest next steps forward worked pretty well.”
- DEBAR, security tester.
Burp AT, Burp's new agentic solution, works natively with your Burp project, meaning it knows your engagement, and you stay in control.
Get started with Burp AT 👉 portswigger.net/burp/burp-at?ps_source=x&ps_medium=social… -
Burp Suite
@Burp_Suite
How do you test how powerful an AI testing tool is?
@0xTib3rius built his own target: a bespoke vulnerable app, source code never published, with three known, tricky paths to RCE. Then he tried Burp AT.
Burp AT found a fourth within minutes.
#burpat
Burp Suite
@Burp_Suite
An unintended route to RCE, caused by a misconfiguration in the database server. Not something he planted.
Burp AT found it within minutes.
The paths you planned for are one thing. The one nobody planned for is the one that matters on a real engagement.
Burp Suite
@Burp_Suite
Burp AT is now available for Burp Suite Professional users.
Configure your workflow and see what it finds beyond your known vulnerabilities.
Try Burp AT for free today👇portswigger.net/burp/burp-at?ps_source=x&ps_medium=social… -
Burp Suite
@Burp_Suite
Can AI do novel security research?
Today at @OffensiveAIcon - 'The HTTP Terminator: Chasing AI Autonomous Research Cascade' by @albinowax
#offensiveaicon #burpatPost not available here, view on X
Burp Suite
@Burp_Suite
Groundbreaking research like this feeds straight into the tools we build. Burp AT, our agentic AI for human-in-the-loop pentesting, draws on a library of specialist skills created by the PortSwigger Research team, James included.
Burp Suite
@Burp_Suite
#burpat tests with the same methodology you see on stage or read about in this new innovative research; new skills land regularly to put this testing power directly in your hands.
See how PortSwigger Research powers Burp AT 👇
portswigger.net/burp/burp-at?ps_source=x&ps_medium=social… -
Burp Suite
@Burp_Suite
Want to hack HTTP/3 in Burp Suite? Now you can…
Tom Stacey
@t0xodile
Turbo Intruder 2 has landed! You can now surpass 100,000 RPS over WiFi using the new HTTP/3 engine, test HTTP/3 exclusive targets with the Burp adapter, and deploy new research-grade race condition techniques! Check out the post below for full details:
Post not available here, view on X
Burp Suite
@Burp_Suite
As an added bonus, the new HTTP/3 engine also enables you to try some of the awesome new race condition techniques recently dropped by Mohammad Amin Nasiri, Efstratios Chatzoglou, Georgios Kambourakis.
Burp Suite
@Burp_Suite
Check it out and let us know what you think!
-
Burp Suite
@Burp_Suite
Two very different tests. One strong verdict.
@C0d3Cr4zy used Burp AT to explore SQLi and test an app behind a WAF. It found the vulnerable input, validated an auth bypass and connected the evidence.
“It works very well as a pentester’s copilot.”
How are you using #burpat? -
Burp Suite
@Burp_Suite
Burp Champion @fshiga used Burp AT to work through a complete attack chain in 3 hours:
Enumeration + initial access → SQLi privilege escalation → sensitive file access via SSRF
Days of manual analysis compressed into one morning.
How far could #burpat take your next test? -
Burp Suite
@Burp_Suite
4 minutes. 21 tool calls. Broken access control uncovered. 🔎
But the best part? @zahideroglu stayed in control, while Burp AT kept to scope and asked before acting.
Got a Burp AT story? Share it with #burpat for a chance to win exclusive swag. -
Burp Suite
@Burp_Suite
One prompt. 9 minutes. A lot of ground covered.
Read how Burp Champion Mohammad Abu Yahya used Burp AT for the first time.
What could Burp AT do for you in 9 minutes? Share your story with #burpat for a chance to win exclusive swag.
Full article 👉 medium.com/@m8a8a8y/gave-burp-at-a-website-it-found-sql-i… -
Burp Suite
@Burp_Suite
“Burp AT re-wrote the book.”
Mario Contestabile used Burp AT to investigate potential IDOR and XSS findings in seconds, while keeping testing decisions firmly in his hands.
Share your best Burp AT story with #burpat for a chance to win exclusive swag. We want to hear yours too! -
Burp Suite
@Burp_Suite
Competition time!
Share your best story of Burp AT in action with the hashtag #burpat, for a chance to win exclusive swag. Burp AT is in a free public beta for all Pro users, so now is the perfect time to try it. For more info: portswigger.net/burp/burp-at -
Burp Suite
@Burp_Suite
66,000 lines of minified JS. The kind of thing you might write off on a timeboxed engagement.
Ray Huygen pointed Burp AT at it and carried on testing. It came back with a route to confidential whistleblower reports behind a bruteforceable 6-digit code. Full story below 👇
Burp Suite
@Burp_Suite
How Burp AT helped expose whistleblower reports via a critical vuln that was overlooked for years: portswigger.net/blog/how-burp-at-helped-expose-whistleblo…
-
Burp Suite reposted
Clint Gibler
@clintgibler
Agentic AI for human-led pentesting. Built natively into Burp Suite, Burp AT works with Burp’s proven tools, project context, and Skills from @PortSwigger Research, while keeping scope, judgment, and conclusions in human hands.
Learn more: portswigger.net/blog/introducing-burp-at -
Burp Suite reposted
PortSwigger
@PortSwigger
New research: CSS: the bomb inside your inbox 💣
Debuting at Black Hat USA today, @garethheyes shows how "safe" CSS in Gmail, Outlook, Fastmail, ProtonMail, Yahoo & AOL Mail becomes a serious attack surface - no JavaScript required.
#bhusa #blackhatusa -
Burp Suite reposted
PortSwigger
@PortSwigger
We're ready for you BHUSA Day 2 🎩
What a day one - incredible to meet so many of you, and even better to hear how many are already using Burp AT.
Huge congrats to our own @PortSwiggerRes @albinowax and @t0xodile, who took the stage to present brand new research. -
Burp Suite reposted
PortSwigger
@PortSwigger
🚨 New from @PortSwiggerRes's James Kettle @albinowax
At #blackhatusa today: can AI invent genuinely new attack techniques, not just find known bugs?
Yes - and it compromised banks, government infrastructure, and an airport along the way. -
Burp Suite reposted
PortSwigger
@PortSwigger
The PortSwigger stand at @BSidesLV is now LIVE 📍
Two days, lots to see. Here's what's waiting for you… -
Burp Suite
@Burp_Suite
Burp AT brings agentic AI to human-led pentesting, with Burp’s proven tools, project context, and purpose-built skills.
portswigger.net/blog/introducing-burp-at -
Burp Suite reposted
Rana Khalil 🇵🇸
@rana__khalil
Really exciting to see Burp Suite stepping into the world of agentic AI! 😃
As someone who spends a lot of time using Burp during web and API pentests (and is also building our own internal AI tools at work to integrate with Burp) it’s amazing to see this initiative released by @PortSwigger!
What makes Burp AT especially interesting is the approach: AI agents that can leverage Burp’s capabilities, project context, and purpose-built pentesting skills, while keeping the human tester in control.
The fact that these skills are developed by PortSwigger researchers, the same researchers whose work we constantly learn from through the PortSwigger blog and Web Security Academy, makes this even more exciting. 🔥
Looking forward to experimenting with Burp AT and seeing what’s possible!
Burp Suite
@Burp_Suite
Introducing Burp AT.
Agentic AI for human-led pentesting, with Burp Suite’s proven tools, your project context, and purpose-built skills.
Now live in public beta for Burp Suite Professional users.
portswigger.net/blog/introducing-burp-at -
Burp Suite reposted
Stephen Rees-Carter
@valorin
This is pretty freaking impressive!
I asked it to find me a suspected PII leak in an activity log, but didn't tell it where to find the logs, or how to log in (or give it MFA!)...
5 minutes later, it found password hashes and exposed TOTP secrets. 🤯
Burp Suite
@Burp_Suite
Introducing Burp AT.
Agentic AI for human-led pentesting, with Burp Suite’s proven tools, your project context, and purpose-built skills.
Now live in public beta for Burp Suite Professional users.
portswigger.net/blog/introducing-burp-at -
Burp Suite
@Burp_Suite
Introducing Burp AT.
Agentic AI for human-led pentesting, with Burp Suite’s proven tools, your project context, and purpose-built skills.
Now live in public beta for Burp Suite Professional users.
portswigger.net/blog/introducing-burp-atPost not available here, view on X
Burp Suite
@Burp_Suite
Those boundaries are enforced by Burp, outside the model.
Agents can propose actions, but they cannot execute anything Burp does not permit. Their requests and tool activity are recorded in the project, leaving evidence you can inspect and reproduce.
Burp Suite
@Burp_Suite
This is the first phase of Burp AT.
Hand agents the investigations you rarely get time to finish. Explore more of the target while retaining control of scope, judgment and conclusions.
Available now in public beta:
portswigger.net/blog/introducing-burp-at -
Burp Suite reposted
El Mago
@soyel_mago
En tiempos donde el triage de reportes en #bugbounty se volvió un poco "lento" debido al aumento de volumen de reportes causado por la #ai, es sumamente valioso aportar claridad a la reproducción del hallazgo para acelerar el proceso. Ahí es donde entra @Burp_Suite Organizer, no lo conoces?, no lo usaste? te dejo un video que hice hace poco!
📺 www.youtube.com/watch?v=QN2riHwb1Oo
Thanks to the @PortSwigger for building such a great feature! -
Burp Suite reposted
key
@VulkeyChen
Our team's open-source project HaE (Highlighter And Extractor), meticulously crafted and refined over eight years of continuous iteration, has been honored with the Most Nominated Award at the Burp Extensibility Awards 2026(portswigger.net/blog/burp-extensibility-2026-awards-talks…).Thanks to the @Burp_Suite @BApp_Store team for all their efforts!
"Highlighter And Extractor acts like a smart filter, immediately drawing my eyes to the requests that matter most. It feels like having an extra pair of eyes watching the traffic for me. The rule-based automation - the ability to write custom regex rules and have Burp automatically highlight and extract data - is a game-changer."
github.com/gh0stkey/HaE -
Burp Suite reposted
Federico Dotta
@apps3c
As part of @Burp_Suite Extensibility Month initiatives, last week I gave a talk titled “Restoring testability: Handling complex scenarios in Burp Suite with a custom extension”.
Video, slides and code can be found here:
hnsecurity.it/blog/restoring-testability-slides-code-video/ -
Burp Suite reposted
Anvil Secure
@anvil_secure
A short clip from Andrea's ByteBanter talk on the @PortSwigger Discord yesterday ✨
ByteBanter is an awesome @Burp_Suite extension that uses BurpAI to generate context-aware Intruder payloads.
Full recording + 2026 Burp Suite Extension Awards nomination link below 🏆
#appsec #burpsuite #pentesting -
Burp Suite
@Burp_Suite
🏆 Nominations for the 2026 Burp Suite Extension Awards close THIS TUESDAY ⚠️
Week 3 of Extensibility month is almost wrapped - here's what happened, what's still to come, and how to get your nomination in before it's too late 👇Post not available here, view on X
Burp Suite
@Burp_Suite
⚠️ Last chance: 2026 Burp Suite Extension Awards
Nominations close Tuesday 26 May at 9:00 AM EDT (2:00 PM BST).
Nominate the extensions that saved your time, sharpened your workflow, or helped you crack something tricky - and enter a prize draw for a Burp Extensibility t-shirt 👕
You can nominate as many extensions as you want - simply fill out the form!
🗳️ forms.gle/59Gtz68nwMpSRmmi7
Burp Suite
@Burp_Suite
🏗️ Wed 27 May | 11:00 AM EDT (4:00 PM BST)
Build to learn: How PortSwigger uses Burp extensions to prototype ideas - Tom SL
Three internal extension experiments: one that became a product feature, one that didn't make it, and one still finding its feet.
If you've ever had an idea for an extension but weren't sure it was worth building, this one's for you.
Catch it live on the Burp Suite Discord 🎬
Burp Suite
@Burp_Suite
Who will be taking home the 2026 Burp Suite Extension Awards?
Find out next Friday 🏆
discord.gg/portswigger -
Burp Suite reposted
Anvil Secure
@anvil_secure
Looking forward to this one! 🚀
Andrea Braschi will be presenting his @Burp_Suite extension, ByteBanter, live on the @PortSwigger Discord on May 20.
You can also nominate ByteBanter for the 2026 Burp Suite Extension Awards.
Event + nomination links below 👇
#appsec #burpsuite -
Burp Suite
@Burp_Suite
Week 2 of Extensibility month on the Burp Suite Discord is wrapping up 🧩
Here's what we covered this week - and next week is busy 👇Post not available here, view on X
Burp Suite
@Burp_Suite
🎋 Fri 22 May | 11:00 AM EDT (4:00 PM BST)
Adventures in Bambda Automation with Claude Code - Tib3rius
Custom scan check bambdas are powerful. Writing them by hand is tedious. Tib3rius shares his experiments using Claude Code to automate Bambda generation, validation, and testing - the wins, the failures, and the workflows that stuck.
Catch it live on the Burp Suite Discord 👇
discord.com/events/1159124119074381945/1504507670202155008
Burp Suite
@Burp_Suite
All of this is happening live on the Burp Suite Discord next week!
Come join us 🗣️
discord.gg/portswigger -
Burp Suite reposted
HN Security
@hnsec
As part of #burpextensibilitymonth initiatives, our Research Lead and #burpambassador @apps3c is joining @PortSwigger on @discord later today for “Restoring testability: Handling complex scenarios in Burp Suite with a custom extension”.
Don’t miss it!
discord.com/events/1159124119074381945/1499761261750128670 -
Burp Suite
@Burp_Suite
🚀 Want to build your own Burp Suite extensions?
As part of Burp Extensibility Month, we’re sharing Burp Ambassador Federico Dotta's (@apps3c) 10-part guide to extending Burp Suite with the Montoya API.
Start here 👇
hnsecurity.it/blog/extending-burp-suite-for-fun-and-profi…
#burpsuite #burpextensibilityPost not available here, view on X
Burp Suite
@Burp_Suite
🎤 Federico is also joining us on Discord this Thursday for:
**Restoring testability: Handling complex scenarios in Burp Suite with a custom extension**
He’ll explore how custom extensions can help with encryption, request signing, token handling, custom formats, WAF controls, and more.
Burp Suite
@Burp_Suite
🏆 Don’t forget to nominate your favourite extensions for the **2026 Burp Suite Extension Awards** 🌟
Then join us on Discord for the talk, discussion, and more Extensibility Month updates 👇
Nominations: docs.google.com/forms/d/e/1FAIpQLSdU_LfyN-q0G6DqN7i_SjUse…
Discord: discord.gg/portswigger
#bapps #burpsuite -
Burp Suite
@Burp_Suite
One week into Extensibility Month, and the Burp Suite Discord has been busy 👀
🏆 Extension Awards launched
🔥 70+ nominations already in
🎤 First event wrapped: "Intro to Extensibility in Burp"
And we’re only just getting started 👇🧵
Burp Suite
@Burp_Suite
🏆 The 2026 Burp Suite Extension Awards are open!
Want the chance to win some exclusive Burp swag? Nominate the Burp extensions that:
✅ Saved you time
✅ Improved your workflow
✅ Helped solve a tricky problem
✅ Became essential to your setup
Nominations close 26 May at 09:00 EDT (14:00 BST)
Submit your vote here:
docs.google.com/forms/d/e/1FAIpQLSdU_LfyN-q0G6DqN7i_SjUse…
Burp Suite
@Burp_Suite
Next week for Extensibility Month on Discord 👇
📥 Submitting extensions to the BApp Store
📝 Writing your Burp extension
🗣️ “Restoring Testability: Handling Complex Scenarios in Burp Suite with a Custom Extension” with Burp Ambassador, @apps3c
🆕 Deep dive on Swapper with the author, Dave Blandford
Join us on Discord as we continue celebrating Burp Suite extensibility and the community building around it.
discord.gg/portswigger -
Burp Suite reposted
Federico Dotta
@apps3c
To celebrate the @Burp_Suite Extensibility Month, the tenth article of the series "Extending Burp Suite for fun and profit - The Montoya way" is out! The topics of this tenth part is "Burp AI"!
Stay tuned for a new extension on the topic on @BApp_Store!
hnsecurity.it/blog/extending-burp-suite-for-fun-and-profi… -
Burp Suite reposted
HN Security
@hnsec
To kick off his collaboration with @PortSwigger as a Burp Suite Ambassador, our Research Lead @apps3c just published the 10th article on the creation of extensions for @Burp_Suite. Topic: Burp #ai!
hnsecurity.it/blog/extending-burp-suite-for-fun-and-profi… -
Burp Suite
@Burp_Suite
Welcome to Burp Extensibility Month!
#burpextensibility #burpsuite #bappsPost not available here, view on X
Burp Suite
@Burp_Suite
Highlights include:
⭐ Sessions from new Burp Ambassadors
⭐ Custom extensions for complex testing scenarios
⭐ Bambda generation deep dives
⭐ Zak Fedotkin on vibecoding Burp extensions @zakfedotkin
Burp Suite
@Burp_Suite
Join the PortSwigger Discord to take part in the conversations and events 👇
discord.com/invite/portswigger
See you there! 👋 -
Burp Suite reposted
Dave
@hackr1ot
SWAPPER - The pure regex match/replace extension for Burp Suite @PortSwigger. Making testing easier!
portswigger.net/bappstore/0077e9930f0147679b6c5ddbedac52be -
Burp Suite
@Burp_Suite
🚀 Extensibility Month is launching on the PortSwigger Discord!
Join us for a month of events, resources, and community discussion all about creating, sharing, and getting more from Extensibility in Burp Suite.
#burpsuite #burpextensibilityPost not available here, view on X
Burp Suite
@Burp_Suite
Highlights include:
✨ Our new Burp Ambassadors, @apps3c and @0xTib3rius, present sessions covering creating custom extensions for complex testing scenarios and a Bambda generation framework.
🔬 A deep dive with PortSwigger researcher @zakfedotkin on vibecoding Burp extensions.
Burp Suite
@Burp_Suite
Join the PortSwigger Discord server to get involved, share extensibility resources, attend events, and chat with others building with Burp!
discord.gg/portswigger -
Burp Suite reposted
PortSwigger
@PortSwigger
Meet the Burp Ambassadors: @rana__khalil 🌍
Rana Khalil is a security educator and founder of Rana Khalil’s Academy.
Her mission: make web app testing accessible to more people.
#burpambassador #burpsuite -
Burp Suite reposted
James Kettle
@albinowax
We've launched a new @WebSecAcademy topic on exploiting AI-powered security scanners! Learn how to use indirect prompt injection to steal data, cause damage & trigger exploit chains!
-
Burp Suite reposted
PortSwigger
@PortSwigger
Meet the Burp Ambassadors: @0xTib3rius 🇺🇸
Tib3rius is a professional pentester and well-known content creator - you’ve probably seen his livestreams or training content. 👀
#burpambassador #burpsuite #pentesting -
Burp Suite reposted
PortSwigger
@PortSwigger
Meet the Burp Ambassadors: @apps3c 🇮🇹
Federico Dotta is an offensive security researcher with a deep focus on Burp Suite extensibility.
#burpambassador #burpsuite #burpextensibility #bapps -
Burp Suite reposted
PortSwigger
@PortSwigger
Meet the Burp Ambassadors: @hapi_hacker 🇺🇸
Corey Ball brings 15+ years of experience in IT & cybersecurity, with a sharp focus on API security.
#burpambassador #burpsuite -
Burp Suite reposted
PortSwigger
@PortSwigger
Meet the Burp Ambassadors: @soyelmago 🇦🇷
Alan Levy is a Buenos Aires-based security consultant, content creator, and founder of @BugBountyArg.
He’s also behind LATAM’s first online bug bounty conference: BountyMagicCon.
#burpambassador #burpsuite -
Burp Suite reposted
PortSwigger
@PortSwigger
Introducing the official Burp Ambassador Program! 🧡
@0xTib3rius @rana__khalil @apps3c @hAPI_hacker @soyel_mago
#burpambassador #burpsuite -
Burp Suite reposted
PortSwigger
@PortSwigger
PortSwigger X Meta 🤝
We’ve partnered with Meta Bug Bounty, bringing together Meta’s bug bounty programme with Burp Suite and the Web Security Academy! 🚀 #burpsuite #meta #bugbounty #appsec -
Burp Suite reposted
SendSafely
@SendSafely
Continuing our monthly Security Spotlight series, and this time we're showing some love to Burp DAST by @PortSwigger
Our security team has used Burp tooling for years. Daily and weekly automated scans, high-accuracy findings, and minimal false positives. It just works the way you want a scanner to work.
Full post: blog.sendsafely.com/security-spotlight-how-we-use-burp-da… -
Burp Suite
@Burp_Suite
Have you ever found a high-value HTTP request, continued testing, and then lost track of it among dozens of open Repeater tabs?
Stop keeping 50 Repeater tabs open.
Burp Suite has a built-in Organizer. You can send interesting requests there, add custom text notes, and keep your workspace perfectly clean while you continue your hunt.
Stay organized.
Available in Community and Pro 👇
portswigger.net/burp/documentation/desktop/tools/organizer -
Burp Suite
@Burp_Suite
Client-side attack surfaces are expanding fast.
Are you keeping up?
Burp Suite Pro’s Scanner doesn't just look at backend server flaws. Its built-in JavaScript analysis engine automatically crawls and audits complex JS to uncover hidden client-side vulnerabilities while you test.
That’s how you stay ahead.
For a better view of Burp Pro features: 👇
portswigger.net/burp/documentation/scanner/auditing -
Burp Suite
@Burp_Suite
Modern apps don’t fail in obvious places anymore. SPAs, client-side logic, and APIs are where real bugs hide.
Burp Scanner helps you get credible signal faster, so you spend less time triaging noise and more time proving impact.
What makes the difference isn’t just coverage, it’s the research and control behind it:
🔶 Research-led detection: vulnerability logic informed by decades of @PortSwiggerRes, so checks reflect ground-breaking, real-world exploitation techniques.
🔶 API-aware scanning: assess OpenAPI, GraphQL, and SOAP APIs from real definition files for deeper, structured coverage.
🔶 Browser-powered crawling + JS analysis: reach modern SPAs and client-side attack surfaces that traditional crawlers miss.
🔶 Extensible & reusable: create custom scan checks to codify edge cases or new vulns, extensions built by the community for a myriad of use-cases, turning one-off discoveries into repeatable testing standards. -
Burp Suite
@Burp_Suite
Are you testing for authorization bypass or header-based access controls?
It can be tedious to manually edit every request, but you don't have to.
Try using Match & Replace in Burp Suite to automate request modifications on the fly.
Add headers, swap tokens, or tweak parameters across all traffic.
Set the rule once, and let Burp handle it. -
Burp Suite
@Burp_Suite
Learn about NoSQL Injection vulnerabilities!
In this NoSQL course, you will learn how to:
🔶Types of NoSQL
🔶NoSQL syntax and operators
🔶Exploting NoSQL injection to extract data
🔶 Timing-based injection
…and more
Check it out 👇
portswigger.net/web-security/learning-paths/nosql-injection -
Burp Suite
@Burp_Suite
Pentester Julen Garrido Estévez put Burp AI in Repeater to the test and was impressed by how quickly it delivered functional PoCs. 📈
In real-world lab scenarios, well-crafted prompts enabled reliable vulnerability detection in under a minute, with minimal requests and low credit usage.
Read about it here 👇
portswigger.net/blog/functional-pocs-in-less-than-a-minute -
Burp Suite
@Burp_Suite
Workflow tip for the Burp Suite power users 💪
Are you analyzing a parameter in Repeater that gets reflected in the response? Stop manually scrolling to find your payload.
Enable the "Auto-scroll to match when text changes" toggle in the Repeater tab. It instantly snaps to your reflected input every time you hit send.
Massive time saver during intense XSS or injection hunting.
Do you have a favorite Burp Suite trick? Share them below. 👇 -
Burp Suite
@Burp_Suite
Burp Suite keeps getting better because of the amazing community that supports it.
In February:
• 4 new BApp extensions released
• 12 updates to existing extensions
If you’re scaling testing across teams, Burp needs to work the way your team works.
Extensibility is not a bonus feature. It is how mature teams standardize workflows, encode expertise, and adapt Burp Suite to real-world environments.
Here’s what released this month 👇
Burp Suite
@Burp_Suite
• Burp Suite keeps evolving around real-world workflows. Here are the significant updates from February:
• MCP Server adds new feature: MCP tools for Burp Collaborator
• Autorize adds new feature: Multi-user comparison and viewer visibility controls
• Hackvertor adds new feature: WebSocket message editing
• Burp Variables adds new feature: auto-update variables from regular expressions
• Copy Request Response adds new feature: Configurable header omission and copy formatting
• levo.ai Burp integration, InQL - GraphQL Scanner, SAML Raider: bug fixes and improvements
Burp Suite
@Burp_Suite
If you’re scaling testing across teams or extending Burp to fit real-world workflows, check out the BApp Store.
Extensions are how you and your team can:
• Extend manual workflows
• Share repeatable logic
• Enhance Burp Suite with custom functionality tailored to your workflows
Join the discussion in Discord 👇
discord.gg/portswigger
Explore the full list on the BApp Store:
portswigger.net/bappstore -
Burp Suite reposted
Behi
@Behi_Sec
Complete list of tools currently worth using for bug hunting:
Burp Suite -
Burp Suite
@Burp_Suite
Finish the exploit chain:
1. Open redirect on login
2. OAuth token leaked via referrer
3. ??? -
Burp Suite
@Burp_Suite
One of the most underrated API testing techniques:
Review the naming schema of discovered endpoints and just... guess what others might be.
If /api/user/update-name exists, try /api/user/update-role.
You'd be surprised how often this works! -
Burp Suite
@Burp_Suite
3 hours later...
-
Burp Suite
@Burp_Suite
Describe the moment you found your first real bug using Burp.
Where were you? What was the vuln? How did it feel? -
Burp Suite
@Burp_Suite
If you use Repeater to manually validate findings, this will save you serious time.
In this post, Adarsh Kumar breaks down his exact workflow and how he accelerates exploit confirmation without killing accuracy.
Great read!
portswigger.net/blog/how-i-sped-up-exploit-validation-in-… -
Burp Suite
@Burp_Suite
There's a whole community of people who use Burp Suite every day, just like you.
If you're not in it, you should be 👇
discord.gg/portswigger -
Burp Suite
@Burp_Suite
Getting a pingback on Burp Collaborator might just be the best feeling in the world.
-
Burp Suite
@Burp_Suite
If you don't read this, you're missing out on a curated list of the BEST web hacking techniques from 2025.
Big shout out to the incredible cybersecurity community doing this research 💪
portswigger.net/research/top-10-web-hacking-techniques-of… -
Burp Suite
@Burp_Suite
Time for a critical vulnerability discovery story. 📖
Gather around folks. Based on a true story - some details changed for anonymity.
A pentester (let's call him Jerry) was testing a critical application, it was controlling a gigantic water processing plant for a major global city. He sat down on the first day of testing and was greeted with a custom SSO sign-in page. He fired up Burp Suite, enabled interception, and walked through the login flow.
He got most of the way through the SSO flow without seeing anything overly suspicious. The login looks as though it has been successful, but he notices one last POST request pop up in proxy intercept before he's redirected to /dashboard. It's being sent to /login and it just has a JSON body {"user_id":"pentest@example[.].com"}. No password, no auth token, just an email.
He switches "pentest@" to "admin@" and is greeted with full admin privileges. All before morning tea.
After some further testing, he realised that you didn't even need the SSO flow, anyone could just send a POST request with the email of the user they wish to authenticate as, and the response would contain be a session token for that user. 👌
The moral of the story: sometimes, the most critical vulnerabilities are so obvious that most people don't even bother to check for them. 80% of pentesting is just validating assumptions! -

Burp Suite
@Burp_Suite
Finish the sentence:
{"isAdmin":" -
Burp Suite
@Burp_Suite
While we're on the topic of GraphQL testing, let's talk about error hints.
Some GraphQL servers suggest valid fields on bad queries. In Repeater, send an invalid GraphQL query (e.g. referencing a non-existent field) and inspect the error response. If it suggests alternatives, you can mine schema info.
Use those hints (or tools like clairvoyance) to reconstruct the schema.
github.com/nikitastupin/clairvoyance -
Burp Suite
@Burp_Suite
One way to get Burp to map a REST API is by letting a real client do the browsing. Proxy a mobile or web app and watch the HTTP history.
Often, just by doing this, you'll find undocumented sensitive or vulnerable operations buried in the proxy logs.
But if we're looking for undocumented/sensitive enpoints... here's what works even better.
Review the naming schema of the API endpoints and simply guess what some others might be.
For example, if "/api/user/update-name" is an endpoint, why not try "/api/user/update-password"? -
Burp Suite
@Burp_Suite
GraphQL introspection made easy: once you identify a GraphQL endpoint, send a request to Burp Repeater and use the GraphQL tab. Right-click in the request pane → GraphQL → Set introspection query, then click Send.
The server’s JSON response will contain the full schema if introspection is allowed 🤞
Now you can right-click the response and “Save GraphQL queries to site map” so you can attack specific queries (e.g. with Intruder)! -
Burp Suite
@Burp_Suite
APIs can be painful to test if you don't have the right tools.
Thankfully, Burp can parse all major API definitions to automatically discover and scan API endpoints. 👌
portswigger.net/burp/documentation/desktop/running-scans/… -
Burp Suite
@Burp_Suite
Traditional crawlers really struggle with modern applications.
Burp Suite Professional scans applications using a built-in browser that handles JavaScript-heavy apps and SPAs like a real user.
Client-side routing, dynamic content, and state changes are fully covered! -
Burp Suite
@Burp_Suite
Vulnerabilities don’t always show up in responses.
Burp Suite Professional includes OAST tools like Collaborator to detect blind and asynchronous vulnerabilities that don’t return direct responses.
More details 👇
portswigger.net/burp/pro -
Burp Suite
@Burp_Suite
This Burp Suite Professional extension "AI Prompt Fuzzer" automates prompt injection fuzzing for anyone working with LLMs in production.
This extension helps with customizable payloads, AI-assisted analysis, and even an AI vs AI mode to simulate attacks end-to-end.
Perfect for finding LLM vulnerabilities before they’re exploited!
👉 Link: portswigger.net/bappstore/d3d1f3c9427e453193eb5deb3b6c115a -
Burp Suite
@Burp_Suite
Scanning accurately for broken access controls has generally not been possible in the past. By leveraging AI, however, we can suddenly scan for BAC vulnerabilities without drowning in false positives.
Check it out 👇 -
Burp Suite reposted
PortSwigger
@PortSwigger
2025’s web hacking shift: side-channels became a core exploitation primitive.
Which technique are you going to use in your next test?
See the #1 web hacking technique of 2025 below ⬇️
portswigger.net/research/top-10-web-hacking-techniques-of… -
Burp Suite
@Burp_Suite
🔧 Planned maintenance on Web Security Academy – Thursday 12 Feb
Labs and certification exams will be unavailable from 9:00–12:00 GMT (4:00–7:00 EST).
Please do not start a certification exam shortly before this window.
⚠️ Exams started close to the maintenance period may be interrupted and you may lose your exam token.
We recommend waiting until after maintenance has completed before starting an exam. -
Burp Suite
@Burp_Suite
-
Burp Suite
@Burp_Suite
Have you ever met a web app pentester who doesn't know Burp?
-
Burp Suite
@Burp_Suite
I just watched Burp AI find a bug, validate it, and craft a PoC.
2026 is wild! Thanks for the demo @NahamSec 👇
www.youtube.com/watch?v=8ox3s15n-Yc -
Burp Suite
@Burp_Suite
We've all done it.
Change the default proxy interception state in ⚙️ > Proxy > Default Proxy interception state -
Burp Suite
@Burp_Suite
🚀 January BApp Store update
You’ve been busy! Four new Burp Suite extensions launched this month:
🆕 Proxy Rotate
🆕 API Workflow Manager
🆕 GraphQL Security Tester (with Burp AI)
🆕 BubblePop (bubble.io ElasticSearch Decryptor)
Huge thanks to the authors 👏
Burp Suite
@Burp_Suite
💫 17 BApp updates shipped:
GAP, Param Miner (x2), PwnFox for Chromium, DNS Exfilnspector, InQL, ReportLM, Piper, Trusted Domain CORS Scanner, PyCript, Response Overview, Hackvertor, Highlighter & Extractor, Kerberos Authentication, SAML Raider, Autorize, gRPC-Web Coder.
Burp Suite
@Burp_Suite
🤔 Curious to explore what the community’s been building?
Browse the above extensions and other community-created extensions in the BApp Store: portswigger.net/bappstore
Have you built an extension? Submit it via the GitHub Extension Portal: github.com/PortSwigger/extension-portal
And if you want to chat, share ideas, or get feedback, join the conversation on the PortSwigger Community Discord: discord.com/invite/portswigger -
Burp Suite
@Burp_Suite
A screenshot of the exact point where you decided to lock in. 😎
-
Burp Suite
@Burp_Suite
Watch BurpAI find and exploit a Server Side Template Injection bug.
Video by @0xTib3rius, for the full video check out 👇
www.youtube.com/watch?v=eQBD2-k9V7sThis media couldn't be displayed. See it on the original post. -
Burp Suite
@Burp_Suite
Authenticated vulnerability scans made easy… Let Burp AI handle the login flow for active scans!
-
Burp Suite
@Burp_Suite
Burp AI does things that you *could* do manually, but they're just quicker and easier with AI assistance. Here's a quick example!
-
Burp Suite
@Burp_Suite
Modern auth flows (SSO, MFA) are complex and often create blind spots for automated scanners.
Burp AI’s recorded login sequences ensure your automated scans actually stay authenticated. You can't secure what you can't see.
Ensure continuous coverage across your entire enterprise estate. 🔐
Here’s @0xTib3rius showing how it’s done 👇
www.youtube.com/watch?v=lHby1dFjJiM -
Burp Suite
@Burp_Suite
Reminder: make sure you're detecting React2Shell!
Follow our video tutorial 👇
www.youtube.com/watch?v=LeRRJYb0ub0 -
Burp Suite
@Burp_Suite
Hacking tip: Run "Explore Issue" on scanner hits. 🎯
Burp AI might just strike gold from one of your low-sev findings.
More info 👇
portswigger.net/burp/ai -
Burp Suite
@Burp_Suite
It's easy to feel imposter syndrome as a hacker when you don't find bugs, but remember this.
You're looking for something that shouldn't even exist in the first place, and might not exist! It's a tough game! -
Burp Suite
@Burp_Suite
Excited to meet your new pentesting buddy?
Say hello to Burp AI 👋
Here’s what your new buddy can do:
🟪 Provide AI-powered HTTP request/response analysis
🟪 Uncover hidden attack vectors
🟪 Validate findings for you
...and much more!
Everything you need all within arm’s reach.
Find out how to activate your FREE AI credits 👇
portswigger.net/burp/ai -
Burp Suite
@Burp_Suite
Create AI-driven extensions tailored to your custom workflows, speeding up the testing process. 🏃♂️
Your Extensions can directly send prompts to the LLM for:
1️⃣ Automatically analyze HTTP traffic
2️⃣ Generate security reports
3️⃣ Suggest payloads and workflows
4️⃣ Give explanation for complex issues
Check out the docs 👇
portswigger.net/burp/documentation/desktop/extend-burp/ex… -
Burp Suite
@Burp_Suite
We're seeing a lot of folks using Burp AI as an idea generator, to push through roadblocks during testing.
When you're out of ideas, try prompting it with a vague suggestion like "try to exploit this" and see what happens. -
Burp Suite
@Burp_Suite
Tired of manually documenting every pentest step? 📝
Try "Document My Pentest", an AI-powered BurpSuite Pro extension that auto-generates clear, accurate notes based on your testing activity from Proxy and Repeater.
👉 Check it out: BApp Store > Search > “Document My Pentest”
OR
👉 Link: portswigger.net/bappstore/bc746627d8494445bf91988e2e20ede1 -
Burp Suite
@Burp_Suite
Hacking can be tedious work.. 😩
Let Burp AI do the heavy lifting 💪
🟪 AI-powered Repeater
🟪 On-the-fly explanations
🟪 Auto validation of Scanner findings
And much more!
Get access 👇
portswigger.net/burp/ai -
Burp Suite
@Burp_Suite
Struggling to turn leads into working PoCs without wasting time or credits?
Pentester Julen Garrido Estévez (@b3xal) shows how the right prompt structure helps you:
• focus the AI where it matters
• reduce noise & hallucinations
• get reliable PoCs quickly
This guest post breaks it down 👇
portswigger.net/blog/functional-pocs-in-less-than-a-minute -
Burp Suite
@Burp_Suite
Burp Suite DAST now supports Postman environment files, so variables merge automatically with your collection before scanning.
Less prep, fewer mistakes, better coverage. -
Burp Suite
@Burp_Suite
Have you tried Shadow Repeater?
It's an AI-powered Extension for Burp Repeater that auto-mutates requests, does intelligent fuzzes in the background, and surfaces surprising findings to Burp Organizer, helping to uncover bypasses and hidden attack paths faster.
Learn more 👇 -
Burp Suite
@Burp_Suite
What tools and techniques actually moved the needle for you in 2025?
Today is your last chance to nominate them for the Top 10 (new) Web Hacking Techniques of 2025 ⬇️
PortSwigger Research
@PortSwiggerRes
Nominations for the Top 10 (new) Web Hacking Techniques of 2025 are now live! Review the submissions & make your own nominations here: portswigger.net/research/top-10-web-hacking-techniques-of…
-
Burp Suite
@Burp_Suite
Just in case Burp AI isn't powerful enough - you can also use the Montoya API to bake AI features into Burp Suite extensions. So much power! ⚡
Here's @_JohnHammond with his thoughts. -
Burp Suite reposted
Norman Wexler
@normanbyte3
Thanks @albinowax and @PortSwigger for adding command palette in Burp. Its a lifesaver...no need to touch the mouse now.
-
Burp Suite
@Burp_Suite
Discover how AI is integrated into the Hackvertor extension, enabling testers to quickly create custom tags that automatically send selected data to an LLM, along with a predefined prompt.
Link to the full video: www.youtube.com/watch?v=Flg0wOmgbDo
Docs: portswigger.net/bappstore/65033cbd2c344fbabe57ac060b5dd100This media couldn't be displayed. See it on the original post. -
Burp Suite
@Burp_Suite
Grasp the untapped side of web app hacking, WebSockets security vulnerabilities!
WebSockets use an initial HTTP request to create long-lived, bidirectional connections for real-time applications. Since they handle user actions and sensitive data, WebSockets are vulnerable to nearly all the same security issues as regular HTTP communication.
For the COMPLETE guide, check out our FREE course with hands-on labs!
In this course, you’ll learn:
🔶 Understand WebSocket fundamentals
🔶 Common vulnerabilities in WebSockets
🔶 Server-side exploitation techniques
🔶 Apply practical testing and mitigation
..and so much more!
Click here for access 👇
portswigger.net/web-security/learning-paths/websockets-se… -
Burp Suite
@Burp_Suite
ICYMI: scan freeze windows are now available in Burp Suite DAST.
No more babysitting. No more manual pause and resume.
See it in action below: -
Burp Suite
@Burp_Suite
Finding web application vulnerabilities with AI? Yes.
Here’s @Cyb3rMaddy demonstrating the power of Burp AI 🟪✨
www.youtube.com/watch?v=pDjveb2LfEo -
Burp Suite
@Burp_Suite
Can Burp AI create a PoC for us?
Yes.
Here's the full video: www.youtube.com/watch?v=8ox3s15n-Yc -
Burp Suite
@Burp_Suite
Humans 🤝 machines
-
Burp Suite
@Burp_Suite
Just want to check something.
What's a feature of Burp Suite that you know exists, but you don't use it because you have never really learned how it works properly? -
Burp Suite
@Burp_Suite
Burp AI's "Explore Issue" doesn't just guess what security issues your web app has. With a single click, it confirms the existence of a vulnerability, creates PoCs, and spells out exact exploitation steps.
The feature takes you from suspicious issue to a valid vulnerability in seconds. -
Burp Suite
@Burp_Suite
Burp AI 👉 SQLmap… all in seconds.
We found an SQL injection vulnerability. Instead of rebuilding the request, Burp AI generated the exact SQLmap command with every header included. 🤯
Watch! -
Burp Suite
@Burp_Suite
Troubleshooting authenticated scanning shouldn’t be hard.
The new recorded login editor in Burp Suite DAST shows each login step clearly, so it’s easier to understand and update when the flow changes.
Fix selectors and steps directly in the UI, without editing or reuploading JSON.
Check out the video: -
Burp Suite reposted
Gareth Heyes \u2028
@garethheyes
Bypass CSP in a single click using my new Custom Action, powered by @renniepak's excellent CSP bypass project.
-
Burp Suite
@Burp_Suite
Hidden parameters are not hidden anymore!
Burp AI can review the context of the endpoint and generate a wordlist of likely parameters to check with intruder.
No guessing. No luck. No search. Just AI-powered goodness. -
Burp Suite
@Burp_Suite
Are you stuck staring at obfuscated Javascript?
Let Burp AI’s Explainer break down the logic so you can focus on solving the challenges.
Watch us crack CTF challenges with it. -
Burp Suite
@Burp_Suite
Turning requests into Python scripts just got effortless.
Burp AI allows you to build full PoCs with headers, payloads, everything included.
Perfect when you need to repeat an attack or automate testing in seconds. -
Burp Suite
@Burp_Suite
New in Burp Suite DAST this winter:
• Simpler auth scanning
• Stronger API workflows
• Configurable scan freeze windows
Check it out here 👉 portswigger.com/burp/dast/winter-2025-update?ps_medium=so… -
Burp Suite
@Burp_Suite
There are 2 ways to detect React2Shell in Burp Suite Pro.
ActiveScan++, or a custom Bambda.
ActiveScan++: Simply install the latest version, and React2Shell will automatically be detected during active scans: portswigger.net/bappstore/3123d5b5f25c4128894d97ea1acc4976
Bambda: This is a more targeted approach. Download the Bambda and install via extensions > Bambda library: github.com/PortSwigger/bambdas/blob/main/CustomScanChecks…
More details here: portswigger.net/blog/how-to-detect-react2shell-with-burp-… -
Burp Suite reposted
PortSwigger
@PortSwigger
PortSwigger researcher @zakfedotkin just dropped a bunch of novel SAML auth bypasses live at @BlackHatEvents #bheu
Check out the blog post The Fragile Lock: Novel Bypasses For SAML Authentication 👇 -
Burp Suite
@Burp_Suite
Nobody likes writing reports. Let me show you how to go from issue to report in seconds with Burp AI + ReportLM.
Less time reporting, more time hacking. -
Burp Suite reposted
PortSwigger
@PortSwigger
It’s the first morning of FOST in Paris, and we're having a great time meeting so many members of the API community.
Come along to Booth A27 for a Burp Suite DAST demo, meet the team, and pick up some PortSwigger swag, including exclusive Burp t-shirts and coins.
Plus we’re raffling off a pair of Orange AirPods Max - attend the workshop or booth demo and you’ll be entered!
#fost #portswigger #burpsuite #dast #apidays -
Burp Suite
@Burp_Suite
Burp AI feels like a senior tester in your corner, suggesting angles, validating exploits, and helping you think through complex problems.
If you've got Burp Professional, you've got 10,000 free Burp AI credits.
Give it a go! 🚀 -
Burp Suite reposted
Tom Shelton-Lefley
@TomLefley
In the next version of @Burp_Suite, sharing findings with your teammates is as simple as sending them a link to open!
Aaron Boodman
@aboodman
In honor of @jarredsumner, everyone should do a "In the next version of $product" post today.
Show me what's coming for your product in the simplest writing possible. -
Burp Suite
@Burp_Suite
We’ve published a full guide on detecting React2Shell using Burp Suite.
Both Burp Suite Professional and Burp Suite DAST now support updated ActiveScan++ v2.0.8 checks for Next.js, plus optional targeted Bambda tests for deeper investigation.
Full breakdown: -
Burp Suite
@Burp_Suite
This is so cool! Watch as Burp AI automatically bypasses filters to get SSRF.
Bypassing these filters was typically a laborious manual process, not anymore! -
Burp Suite
@Burp_Suite
Stopping scans manually because of maintenance windows? That ends now.
Coming next week in Burp Suite DAST: scan freeze windows - automated pause periods that fit the way you work.
No more babysitting. No more manual stops. -
Burp Suite
@Burp_Suite
Join Burp AI developers, Dan and Pete, as they walk us through the new agentic AI functionality in Burp Suite Professional's Repeater.
Nice hats.
www.youtube.com/watch?v=g06bdpAL5mQ -
Burp Suite
@Burp_Suite
Fun fact: The first version of Burp featured actual burping sounds that you couldn't turn off.
We have come a long way. -
Burp Suite
@Burp_Suite
Did you know that we have 2 other accounts that you can follow? 👀
@PortSwigger and @WebSecAcademy -
Burp Suite
@Burp_Suite
This choice says a lot about you. Which are you?
- Temporary project in memory
- New project on disk -
Burp Suite
@Burp_Suite
While pentesting we often face unfamiliar technologies.
With the help of the Burp AI Explainer feature, you can get an understanding of what you're looking at in seconds!
Read our documentation to understand more 👇
portswigger.net/burp/documentation/desktop/tools/repeater… -
Burp Suite
@Burp_Suite
What happens when you give Burp AI the bare minimum details and just let it hack by itself? Let's find out with @0xTib3rius.
www.youtube.com/watch?v=1-NkCSW-IUU -
Burp Suite
@Burp_Suite
An AI to help you bypass website vulnerabilities? Burp AI proves it can be done!
Watch hacker @0xTib3rius show you exactly how he used it👇This media couldn't be displayed. See it on the original post. -
Burp Suite
@Burp_Suite
Can Burp AI hack a website?
@CyberMaddy dives into the world of AI-driven ethical hacking, exploring how Burp AI performs in Repeater when tasked with finding web vulnerabilities like SQL injection, cross-site scripting (XSS), and insecure configurations.
Watch her video now👇 -
Burp Suite
@Burp_Suite
"Burp AI can bring up a new generation of hackers faster and more effectively."
In his new article, @hAPI_hacker explores how Burp AI:
🔬 Analyzes requests and adapts when attacks fail.
💬 Explains findings in clear language.
💪 Enhances human decision-making.
👉 -
Burp Suite
@Burp_Suite
Still recording logins for your scans manually? 😱
Leave the recording process to Burp AI and watch the magic happen 👀 ⬇️ -
Burp Suite
@Burp_Suite
Want to report a scanner finding, but feel like writing it up is too tedious? 😔
Install the ReportLM extension and get Burp AI to do it for you! 👇 -
Burp Suite
@Burp_Suite
Tip: to get more success finding those SSRF vulnerabilities, you can configure your own Collaborator instance and use it inside Burp!
Here's a full guide on how to do it ⬇️
portswigger.net/burp/documentation/collaborator/server/pr… -
Burp Suite reposted
hAPI_hacker
@hAPI_hacker
Launching The Hab by @hapilabs_ai, a content hub for research, reflections, and real talk about cybersecurity.
✍ 1 Blog / month commitment
🎯 Fun, authentic, slightly unhinged
🤖 No AI slop, guaranteed
First up: "Hacking with Burp AI in the Chesspocalypse"
I explore our place in cybersecurity with our new best frenemy, AI. Then I put this approach into practice with @PortSwigger Burp AI as a pentest training asset. -
Burp Suite
@Burp_Suite
Using the Hackvertor extension, but looking for a quick and convenient way to make your own custom tags?
Just ask Burp AI! Zero coding knowledge needed 😉 -
Burp Suite
@Burp_Suite
What's your favorite Burp AI-powered extension?
Comment below 👇 -
Burp Suite
@Burp_Suite
What does IDOR stand for? Incorrect answers only! 😉 ⬇️
-
Burp Suite
@Burp_Suite
Haven't updated Burp Suite in a while? Here's a short summary of what's new in versions 2025.10 and 2025.10.1
- Updated default HTTP history filter to include less irrelevant requests
- Made the site map more readable, with HTTP methods color-coded
- Simpler data export from tables: right-click a column header, and copy it straight to your clipboard
- Made recorded logins more accurate and reliable
- Bug fixes & performance improvements
Read the full release notes here 👇
portswigger.net/burp/releases -
Burp Suite
@Burp_Suite
Not sure about subscribing to Burp Suite Professional yet?
Get a 30-day trial for free and find out hands-on why Burp Suite Professional is the best tool for the job 👇
portswigger.net/burp/pro/trial -
Burp Suite
@Burp_Suite
“At Microsoft, Burp Suite is what you use. It’s not up for consideration.”
Read the full testimonial on why Microsoft chose Burp Suite here: portswigger.net/customer-stories/microsoft-case-study -
Burp Suite reposted
PortSwigger
@PortSwigger
The PortSwigger team are out in full force (and full orange) at OWASP AppSec Global US today - come say hi at booth S3!
We’re armed with tons of swag, and we’re raffling off AirPods Max 🎧 to anyone who attends a Burp Suite DAST demo!
#appsecdc #owasp #appsecglobalus -
Burp Suite
@Burp_Suite
Burp AI 🤝 Burp Intruder
Generate and run Intruder attacks just by prompting Burp AI. It will make a quick list of payloads that you can run straight away or fine tune through Intruder. -
Burp Suite
@Burp_Suite
We have been loving watching folks make videos of their Burp AI use cases! There are loads of interesting use cases that we didn't even think of.
-
Burp Suite reposted
PortSwigger
@PortSwigger
Heading to OWASP AppSec DC this week? Make sure to stop by booth S3. 🇺🇸
✅ Live demos of Burp Suite DAST
✅ Exclusive swag pictured here
✅ A chance to win a brand-new pair of orange AirPods Max
And yes – Burp Suite creator @DafyddStuttard be there too!
Come chat with our team, and see how Burp Suite DAST can transform your security maturity.
#owaspappsecdc #appsec #devsecops -
Burp Suite
@Burp_Suite
We got really sick of making Clickjacking PoCs...
It's so tedious... Framing the page, lining up the buttons..
Sooo we got Burp AI to do it for us 🎉 get a working HTML page right from your Repeater tab! -
Burp Suite
@Burp_Suite
It’s time you can stop asking: “Where is this error message coming from?!”. 🤷♂️
Use the Burp AI ‘Explainer’ feature on error messages to get an explanation of what it means and where it could be originating from. -
Burp Suite
@Burp_Suite
Generating CSRF PoCs is a bit tricky... Not anymore!
CSRF PoC generation could not be easier with Burp AI: just prompt it through repeater and receive a ready-to-go CSRF payload in no time! -
Burp Suite reposted
PortSwigger
@PortSwigger
Ekoparty day one, and we're sponsoring both @BugBountyArg and @BugBountyGirlsC 🇦🇷 👾
PortSwigger Research's @tincho_508 shared, 'Don’t get hacked while you hack: detecting prompt injection in the wild', and it's been great meeting the Burp community.
We’ve got yerba mate gourds, t-shirts, and stickers to give away - come say hi!
#ekoparty #burpontour2025 -
Burp Suite reposted
PortSwigger
@PortSwigger
We’re heading to OWASP Global AppSec DC on November 6–7 🇺🇸
We’ll be running live demos of Burp Suite DAST, showing how it helps you scale your security program, all within the same Burp Suite ecosystem you're already using.
Stop by booth S3, grab some swag, and see Burp Suite DAST in action!
#appsecdc #burpsuite #dast #owasp -
Burp Suite
@Burp_Suite
Been stuck on this one lab you can’t solve? Maybe Burp AI can help!
Here’s an example of how you can detect a SQL Injection vulnerability and gain valuable insight using Burp Suite’s powerful AI. -
Burp Suite
@Burp_Suite
Yeeeeah you could manually figure out a payload for DOM XSS... or you could just ask Burp AI to do it for you.
This media couldn't be displayed. See it on the original post. -
Burp Suite reposted
James Kettle
@albinowax
HTTP is supposed to be stateless, but sometimes... it isn't! Some servers create invisible vulnerabilities by only validating the first request on each TCP/TLS connection. I've just published a Custom Action to help you detect & exploit this - here's a narrated demo:
This media couldn't be displayed. See it on the original post. -
Burp Suite reposted
PortSwigger
@PortSwigger
Burp on Tour continues! 🇦🇷
Next stop: @ekoparty in Buenos Aires, where we’re proud to be sponsoring @BugBountyArg this week.
Find us from Wednesday onwards, we’ll be talking about all things Burp Suite and Burp AI.
#ekoparty #burpontour2025 #burpsuite #burpai -
Burp Suite
@Burp_Suite
This might be the craziest demo I've seen for Burp AI yet! 🧠
Watch how @NahamSec used Burp AI to craft specific usernames, identify an exploitable user, and confirm a PII leak, even when the response was in a different language! 👇This media couldn't be displayed. See it on the original post. -
Burp Suite
@Burp_Suite
Want more context on something while testing? 🤔
Burp AI's Explainer delivers instant, security-focused explanations for anything you select.
Want to learn more? Read this 👇
portswigger.net/blog/welcome-to-the-next-generation-of-bu… -
Burp Suite
@Burp_Suite
Why spend time manually converting JSON to XML to test for XXE?
Just ask Burp AI in Repeater: it handles the transformation and delivers the exploit. @NahamSec demonstrates this massive shortcut for finding complex, overlooked bugs. 👇This media couldn't be displayed. See it on the original post. -
Burp Suite reposted
Peter Logan
@authpeterlogan
Love seeing AI integrated into pentesting workflows 🔥 Burp AI looks like a real game changer for recon and automation.
#cybersecurity #appsec #burpsuite #aiforgood #ethicalhacking -
Burp Suite
@Burp_Suite
Using Burp AI as a Pentester – tomorrow, 4pm BST (11am EDT)
Join @t0xodile, pentester & security researcher, as he shows how the new Burp AI can:
✅ Streamline your workflow
✅ Give you fresh insights into assessments
✅ Level up your pentesting in practical, hands-on ways
👉 discord.com/events/1159124119074381945/1414987895395323924 -
Burp Suite reposted
Gareth Heyes \u2028
@garethheyes
Last chance to catch "Splitting the Email Atom: Exploiting Parsers to Bypass Access Controls" at @NDC_Conferences Manchester. Join me and see just how wild the email RFCs really are.
portswigger.net/research/talks?talkId=34 -
Burp Suite
@Burp_Suite
Is Burp AI going to steal @NahamSec's job?
Nope - but it does make an excellent sidekick!
Check out his full Burp AI demo here 👉 www.youtube.com/watch?v=8ox3s15n-Yc -
Burp Suite
@Burp_Suite
3 words 👉 Reduce false positives. 😌
Burp AI can automatically audit broken access control vulnerabilities to reduce false positives. -
Burp Suite
@Burp_Suite
AI is not going anywhere...F
Couldn't have said it better ourselves @_JohnHammond!
Full video 👉 www.youtube.com/watch?v=v-McepNOrTQ -
Burp Suite
@Burp_Suite
Join Katie Warren, Product Manager of Burp AI, this Monday (4pm BST, 11am EDT) on the PortSwigger Discord as she shares the journey of bringing AI into Burp.
✅ Critical considerations that shaped Burp AI
✅ Balancing trust, efficiency, and workflow
✅ How AI is transforming AppSec
Previously presented at HAC NYC, this updated talk comes with fresh insights.
👉 discord.com/events/1159124119074381945/1414908823801434124 -
Burp Suite
@Burp_Suite
In case you haven't heard, Burp AI is here.
It's an in-tool AI assistant for pentesters. It lives in Repeater so you don’t have to context-switch. Prompt it in natural language to explain what you're seeing, suggest payload ideas, or triage suspicious responses. Think of it as a second set of expert eyes. It can automate repetitive checks (e.g., XSS validation), generate varied payloads, and analyze responses, saving hours of manual grind.
We can't wait to see how y'all use it! -
Burp Suite
@Burp_Suite
HackerOne report: AI-assisted security testing in 2025
AI is now mainstream in web security testing. But humans still drive the impact. The best results come from a hybrid approach of human-driven, AI-assisted testing.
That’s exactly why we built Burp AI: to accelerate the grind while keeping you fully in control inside Burp Suite Professional.
In our new post, we unpack:
- Why adoption is surging and what it changes day-to-day.
- Where AI is useful for security professionals, and where it's not.
- How human-in-the-loop Burp AI fits your workflow: you choose context, steer prompts, validate output
Already on Burp Suite Professional? You've got 10,000 free AI credits to try it for yourself.
Read the post: portswigger.net/blog/the-future-of-pentesting-is-human-x-… -
Burp Suite
@Burp_Suite
There are a lot of sloppy AI integrations out there, but Burp AI is one that will actually improve your hacking workflow. It's insanely good.
Don't believe us? Maybe you'll believe @_JohnHammond! 👇This media couldn't be displayed. See it on the original post. -
Burp Suite
@Burp_Suite
Bug bounty legend @NahamSec just put Burp AI to the test.
See how it helps turn hunches into evidence faster, right inside Burp Suite Professional 👇
#appsec #bugbounty #burpsuite
Burp Suite
@Burp_Suite
🎥 Watch the demo: www.youtube.com/watch?v=8ox3s15n-Yc
-
Burp Suite
@Burp_Suite
Introducing WebSocket Turbo Intruder
WebSockets are everywhere, but testing them has always been a pain…until now. PortSwigger researcher, Zakhar Fedotkin, replays his Black Hat Arsenal talk on his new Burp Suite extension: WebSocket Turbo Intruder.
Discover how to:
🔍 Fuzz WebSockets at scale and uncover deep protocol-level bugs others miss
⚡ Automate complex, multi-step attacks with ease—even without deep scripting skills
#blackhat #burpsuite #websockets #websecurity
👇
Burp Suite
@Burp_Suite
If you’ve been ignoring WebSockets because the tooling wasn’t there, this is your chance to explore a powerful new attack surface.
Check out the recording of Zak's Discord event: www.youtube.com/watch?v=q-TWZ24A7dw
Get it from the BApp Store now: portswigger.net/bappstore/ba292c5982ea426c95c9d7325d9a1066 -
Burp Suite
@Burp_Suite
Don't miss the exclusive Burp AI in Repeater demo on the PortSwigger Discord – tomorrow, 4pm BST (11am EDT)
✅ Generate payloads
✅ Explain tricky APIs
✅ Accelerate your testing — all while keeping you in control
👉 discord.com/events/1159124119074381945/1410980132394500116 -
Burp Suite reposted
PortSwigger
@PortSwigger
We’re launching new agentic capabilities in Burp AI, and you’re invited to a special Discord event series!
Come along to see the new update in action, hear directly from the team behind it, and learn how to supercharge your testing with AI.
Here’s what’s coming up 👇 -
Burp Suite reposted
Tom Stacey
@t0xodile
Been messing around with this in personal projects a lot! Effectively a little testing assistant sat with you checking things in the background while you do the fun stuff.
I’ve even been impressed by its ability to find and understand relatively novel techniques!
Burp Suite
@Burp_Suite
Meet your agentic AI partner in Burp Suite ✨
Your on-demand AI pentest co-pilot has landed in Repeater in Burp Suite Professional.
Get ready for smarter, faster, more accurate testing. 🧵
#burpai #agentic #burpsuiteprofessional -
Burp Suite
@Burp_Suite
Meet your agentic AI partner in Burp Suite ✨
Your on-demand AI pentest co-pilot has landed in Repeater in Burp Suite Professional.
Get ready for smarter, faster, more accurate testing. 🧵
#burpai #agentic #burpsuiteprofessional
Burp Suite
@Burp_Suite
Even the best testers burn time on repetitive checks, or need a second opinion.
Now in Repeater, with prompts, Burp AI helps you…
✅ Spot leads to investigate
✅ Automate repetitive tests
✅ Bypass filters and input sanitization
✅ Demonstrate impact beyond a p.o.c
Burp Suite
@Burp_Suite
This is just the start of what Burp AI can do.
Read more about these brand-new capabilities 👉
portswigger.net/blog/welcome-to-ai-pentesting-add-on-dema…
Burp Suite
@Burp_Suite
Wondering how active pentesters and AppSec experts are using this new agentic functionality in Burp Suite Professional? Here’s a few examples…
Burp Suite
@Burp_Suite
Want to see Burp AI in action? Join us live on Discord:
🗓️ 30 Sept – All new, super-charged Burp AI demo
🗓️ 13 Oct – The journey to Burp AI (Katie Warren)
🗓️ 15 Oct – Using Burp AI as a pentester (Thomas Stacey)
Join the PortSwigger Discord to attend 👉 discord.com/invite/portswigger -
Burp Suite reposted
Dafydd Stuttard
@DafyddStuttard
It's 6 years since we launched the Web Security Academy. Instead of a 3rd edition of The Web App Hacker's Handbook, we created a learning platform that is actively maintained, interactive, and free.
Reaching 10 million labs launched in the past year is a huge milestone!
Web Security Academy
@WebSecAcademy
🚀 Big milestone: over 10 mil labs have been launched on the Academy in the past year!
That’s 10,000,000 opportunities to learn, hack, and level up.
Here’s to pushing the boundaries of application security together!
#websecurityacademy #portswigger #burpsuite -
Burp Suite reposted
Yousef
@iYousefAlotaibi
Hello pentesters!
Did you check this new crazy feature in Burp Suite AI?
Your jobs will be easier with it. 🙂 -
Burp Suite reposted
Harshad shah
@harshad_hacker
▶️ 𝐇𝐚𝐜𝐤𝐞𝐫𝐬 𝐒𝐡𝐨𝐫𝐭𝐬: Burp AI in Repeater
🖇️ Stream from here:
New Update 2025
👉🏻 Hack Smarter in 2025 @PortSwigger
youtube.com/shorts/zgbQRbq7l4M via @YouTube
#cybersecuritytraining #bugbounty -
Burp Suite reposted
PortSwigger
@PortSwigger
🚨 HTTP/1.1 must die. But what does James Kettle’s latest desync research mean in for pentesters and bug bounty hunters in practice?
Pentester and researcher, Tom Stacey (@t0xodile), gives his perspective 👇 -
Burp Suite reposted
Web Security Academy
@WebSecAcademy
🚀 Big milestone: over 10 mil labs have been launched on the Academy in the past year!
That’s 10,000,000 opportunities to learn, hack, and level up.
Here’s to pushing the boundaries of application security together!
#websecurityacademy #portswigger #burpsuite -
Burp Suite reposted
d4d
@zakfedotkin
Dive into WebSocket Turbo Intruder 2.0 - fuzz at scale, automate complex multi-step attacks, and exploit faster.
The blog post is live! Read it here:
portswigger.net/research/websocket-turbo-intruder-nbsp-un… -
Burp Suite reposted
PortSwigger
@PortSwigger
Big news: PortSwigger x HackerOne 🚀
We’re excited to announce our partnership with @Hacker0x01 on the new Hacker Milestone Rewards Program!
#burpsuiteprofessional #hackerone #hackermilestoneprogram -
Burp Suite reposted
HackerOne
@Hacker0x01
🎉 Hey researchers! Big news → HackerOne + @PortSwigger = rewards made for YOU.
We’re celebrating Burp Suite users who hit major milestones on HackerOne with a new rewards program built around your impact.
Check it out: www.hackerone.com/blog/hackerone-portswigger-hacker-miles… -
Burp Suite
@Burp_Suite
24 million websites compromised. 🧵
PortSwigger's Director of Research, James Kettle (@albinowax), & AppSec expert John Hammond (@_JohnHammond) reveal the fatal flaws in HTTP/1.1 that attackers are abusing right now.
#http1mustdiePost not available here, view on X
Burp Suite
@Burp_Suite
The proof? 💰
@albinowax’s research alone uncovered $350,000+ in bug bounties from these flaws.
For attackers (and bug bounty hunters), this isn’t theory, it’s cash on the table.
Burp Suite
@Burp_Suite
It’s time to move on from outdated protocols.
▶️ Watch the full video: www.youtube.com/watch?v=n3Bw8CASnHE -
Burp Suite reposted
Gareth Heyes \u2028
@garethheyes
I discovered how to use CSS to steal attribute data without selectors and stylesheet imports! This means you can now exploit CSS injection via style attributes! Learn how below:
portswigger.net/research/inline-style-exfiltration -
Burp Suite
@Burp_Suite
Heard how attackers exploit cracks in HTTP to win huge bug bounties, but don’t know where to start?
@NahamSec and @albinowax are here to break down HTTP Request Smuggling for you. 🧵
Burp Suite
@Burp_Suite
This often-misunderstood vulnerability can be a goldmine for bounty hunters. 💰
In the video, the NahamSec and James Kettle explore how mismatches in how front-end and back-end servers interpret HTTP headers can open the door to:
✅ Sneaking past security
✅ Hijacking sessions
✅ Poisoning caches
✅ Full system compromise
Burp Suite
@Burp_Suite
James also shares cutting-edge techniques:
🔽 HTTP/2 downgrade attacks
🎯Real-world case studies from Netflix, Atlassian
And more!
Learn more and watch the video 👇portswigger.net/blog/http-request-smuggling-explained-wit…
Burp Suite
@Burp_Suite
HTTP/1.1 Must Die ☠️
In his new research, @albinowax argues that desync attacks aren’t just bugs in individual sites, they’re baked into HTTP/1.1’s design itself.
This can be very lucrative for a bug hunter, with $350,000 being secured in James’ research. 💰
👇 -
Burp Suite reposted
James Kettle
@albinowax
It's been great to see people 'enjoying' the 0CL @WebSecAcademy lab! Tune in this Friday at 11AM PT to watch me livestream the solution with @offby1security - registration link below 👇
-
Burp Suite reposted
HackerOne
@Hacker0x01
HTTP/1.1 is outdated and dangerous. And it’s time to kill it. 💀
James Kettle's new @PortSwiggerRes research exposes how attackers are still exploiting HTTP/1.1 flaws and how you can help end it (and earn while doing it).
Learn + hack: http1mustdie.com
#togetherwehitharder #websecurity #blackhat2025This media couldn't be displayed. See it on the original post. -
Burp Suite
@Burp_Suite
🚨 In case you missed it: #bhusa research by @albinowax reveals new techniques for 0.cl request smuggling.
Grab the whitepaper, test your skills in the new expert lab, and help us kill HTTP/1.1:
http1mustdie.com?ps_medium=social&ps_source=twitter&ps_ca… -
Burp Suite
@Burp_Suite
The ground-breaking new research release HTTP/1.1 Must Die! The Desync Endgame will be hitting @defcon this afternoon at 4.30pm.
Join the movement 👉 http1mustdie.com
#http1mustdie #defcon33 -
Burp Suite reposted
Web Security Academy
@WebSecAcademy
🚨New Black Hat research released: Over $200k in bounties earned in just two weeks. Join the movement to kill HTTP/1.1 today ⬇️
🔍PortSwigger’s James Kettle (@albinowax) introduces two new classes of HTTP desync attacks capable of compromising credentials on tens of millions of sites.
• Exploit previously unseen desync variants (0.cl, Expect-based)
• Leverage the open-source HTTP Request Smuggler v3.0 toolkit for systematic discovery
• Learn how to protect your websites
#bhusa -
Burp Suite reposted
Burp Suite
@Burp_Suite
🚨New Black Hat research released: Over $200k in bounties earned in just two weeks. Join the movement to kill HTTP/1.1 today ⬇️
🔍PortSwigger’s James Kettle (@albinowax) introduces two new classes of HTTP desync attacks capable of compromising credentials on tens of millions of sites.
• Exploit previously unseen desync variants (0.cl, Expect-based)
• Leverage the open-source HTTP Request Smuggler v3.0 toolkit for systematic discovery
• Learn how to protect your websites
#bhusa -
Burp Suite
@Burp_Suite
Missed @albinowax's new HTTP/1.1 Must Die! The Desync Endgame at Black Hat USA yesterday?
Catch it at 4.30pm tomorrow at @defcon!
Learn more 👉 http1mustdie.com
#http1mustdie -
Burp Suite
@Burp_Suite
🕵️♂️ What does @albinowax’s latest research mean for you?
Whether you secure apps, test them (in-house or for clients), or hunt bugs , we’ve broken down what this means for your role, with clear, actionable steps to stay ahead below ⬇️ -
Burp Suite reposted
Clint Gibler
@clintgibler
📢 Sponsor: HTTP/1.1 Must Die! At #blackhatusa, @PortSwigger revealed how they compromised major CDNs and 24M sites.
Today's request smuggling mitigations are an illusion, leaving critical vulns hiding in plain sight. The fix? Kill HTTP/1.1 for good.
Join the fight: -
Burp Suite
@Burp_Suite
👀 Sneak peek: Test this out in Burp Suite Professional Early Adopter 2025.8 from today.
Let us know what you think and how you’re using it with #burpai or the Burp AI channel on the PortSwigger Discord: discord.com/invite/portswigger -
Burp Suite
@Burp_Suite
🚨New Black Hat research released: Over $200k in bounties earned in just two weeks. Join the movement to kill HTTP/1.1 today ⬇️
🔍PortSwigger’s James Kettle (@albinowax) introduces two new classes of HTTP desync attacks capable of compromising credentials on tens of millions of sites.
• Exploit previously unseen desync variants (0.cl, Expect-based)
• Leverage the open-source HTTP Request Smuggler v3.0 toolkit for systematic discovery
• Learn how to protect your websites
#bhusa
Burp Suite
@Burp_Suite
💪 Make a difference today, go to:
http1mustdie.com?ps_medium=social&ps_source=twitter&ps_ca… -
Burp Suite
@Burp_Suite
In one hour, @tincho_508 and @zakfedotkin will presenting their brand new tools at Black Hat Arsenal!
In Vegas? Don't miss these exclusive new showcases of...
⭐ HTTP Hacker
⭐ Web Socket Turbo Intruder
#blackhatusa #bhusa -
Burp Suite
@Burp_Suite
5 hours until the desync endgame begins.
http1mustdie.com
#http1mustdie -
Burp Suite
@Burp_Suite
Today at #blackhatusa - three major new releases from @PortSwiggerRes
1pm - 'HTTP Hacker' at Black Hat Arsenal with @tincho_508
1pm - 'WebSocket Turbo Intruder' at Black Hat Arsenal with @zakfedotkin
3.20m - 'HTTP/1.1 Must Die! The Desync Endgame' at Black Hat USA with @albinowax
#bhusa #blackhatusa #blackhatarsenal #portswigger #burpsuite -
Burp Suite
@Burp_Suite
Tomorrow.
Are you ready? ☠️
http1mustdie.com
#http1mustdie -
Burp Suite
@Burp_Suite
24 hours until the desync endgame begins.
http1mustdie.com
#http1mustdieThis media couldn't be displayed. See it on the original post. -
Burp Suite
@Burp_Suite
Ever wondered how attackers can compromise modern websites by exploiting invisible cracks in HTTP infrastructure to win big bounties?
@NahamSec teams up with @albinowax (James Kettle) from @PortSwiggerRes to break it down in a killer new video 👇Post not available here, view on X
Burp Suite
@Burp_Suite
Whether you're a bug bounty hunter, pentester, or AppSec manager, this is essential knowledge.
Don’t sleep on request smuggling, it’s one of the most underestimated web risks out there.
Burp Suite
@Burp_Suite
Ready for the next evolution of desync attacks?
Tomorrow at #blackhatusa, @albinowax unveils new research with HTTP/1.1 Must Die! The Desync Endgame
👀 http1mustdie.com
Burp Suite
@Burp_Suite
Want to chat with other bug hunters diving into request smuggling?
Join the buzzing community on the Official PortSwigger Discord. 👇
discord.com/invite/portswigger -
Burp Suite
@Burp_Suite
It's nearly time... 👀
http1mustdie.com
#http1mustdie -
Burp Suite
@Burp_Suite
Coming this week... ⚠️
http1mustdie.com -
Burp Suite
@Burp_Suite
5 days until the desync endgame begins.
http1mustdie.com
#http1mustdieThis media couldn't be displayed. See it on the original post. -
Burp Suite reposted
PortSwigger
@PortSwigger
6 days until the desync endgame begins.
http1mustdie.com
#http1mustdie -
Burp Suite
@Burp_Suite
7 days until the desync endgame begins.
http1mustdie.com
#http1mustdieThis media couldn't be displayed. See it on the original post. -
Burp Suite
@Burp_Suite
Are you ready for the Desync Endgame?
http1mustdie.com
#http1mustdie -
Burp Suite reposted
Clint Gibler
@clintgibler
𝐑𝐞𝐩𝐞𝐚𝐭𝐞𝐫 𝐒𝐭𝐫𝐢𝐤𝐞: New AI-powered Burp Suite extension: Automates the discovery of IDOR and similar vulnerabilities.
By @PortSwigger's Gareth Heyes.
How?
By analyzing your Repeater traffic, it generates smart regular expressions based on the requests and responses you're testing.
And applies these regexes across your proxy history to uncover related issues.
Letting you turn a single vulnerability into a broader set of actionable findings with minimal effort.
📚 Blog: portswigger.net/research/repeater-strike-manual-testing-a…
🛠️ GitHub: github.com/hackvertor/repeat-strike
#cybersecurity #ai #bugbounty -
Burp Suite reposted
James Kettle
@albinowax
It's easy to bash vulnerabilities with logos but... I couldn't resist, say hello to http1mustdie.com :)
-
Burp Suite reposted
PortSwigger
@PortSwigger
Another stop for Burp on Tour 2025... and today we're in sunny Sheffield for SteelCon! 😎
Amazing buzz this morning talking to so many community members about Burp AI. If you haven’t already, swing by and grab the exclusive Burp AI and Burp Suite 2025 tees before they're gone...
#burpontour2025 #steelcon #burpsuite -
Burp Suite reposted
Soroush Dalili
@irsdl
I asked ChatGPT to give me a #burpsuite Bambda Custom Action to update cookies in Repeater based on the response so I don't need to do it manually when my token/ticket is being renewed.
It works well:
gist.github.com/irsdl/19169ef31b3d322675b26c02107f31c7 -
Burp Suite reposted
Tib3rius
@0xTib3rius
New video! Getting Into Cybersecurity - An Interview with James Kettle! (@albinowax)
In this episode, James Kettle talks about how he got started in security research, and how you can pivot into this rare but worthwhile role.
Links below! -
Burp Suite reposted
PortSwigger
@PortSwigger
In Vegas for Black Hat or DEF CON this August?
We've got an array of exciting events, meet ups and swag drops planned whilst the PortSwigger team are in Las Vegas, and we're keen to meet as many of you as possible!
Let us know if you'll be there too via this form 👉 -
Burp Suite
@Burp_Suite
⚠️ Don't miss out!
Shift-left without the strain – see how Burp Suite DAST fits directly into CI/CD pipelines without slowing devs down.
📅 July 10 | 4pm UTC
🎯 Real teams, real pipelines, real results
Register now ⬇️This media couldn't be displayed. See it on the original post.
Burp Suite
@Burp_Suite
🚀 Register here: events.zoom.us/ev/ArcUEkIgcIgd7BG9mSW0oW7aDcxghkicFBR9BMb…
-
Burp Suite
@Burp_Suite
🚀 AI isn’t here to replace pentesters, it’s here to supercharge them.
A recent study by the University of Sheffield makes a compelling case:
Burp Suite
@Burp_Suite
At PortSwigger, that’s how we think about AI.
We’re not taking away the thinking, intuition, or judgment that make pentesters so effective, but to automate the repetitive, accelerate the routine, and help uncover deeper insights.
Burp Suite
@Burp_Suite
Are you curious about how AI can reduce false positives or dig deeper into identified issues?
Explore how Burp AI enhances your existing workflow, helping you hack smarter, not harder.
👉 portswigger.net/burp/ai
Burp Suite
@Burp_Suite
Full paper by University of Sheffield: eprints.whiterose.ac.uk/id/eprint/219328/
-
Burp Suite
@Burp_Suite
Legendary PortSwigger researcher, James Kettle, recently answered your questions on security research, AI, and Burp Suite. In case you missed it, check out the recording 👉
www.youtube.com/watch?v=mgmUZ9odkvU -
Burp Suite reposted
Martin Doyhenard
@tincho_508
I'm thrilled to share that I will be presenting a 90 minute workshop in DEFCON's Bug Bounty Village!
I will be speaking about advanced HTTP Desynchronisation attacks, and introducing a new tool to exploit complex vulnerabilities found in top bounty programs!
Bug Bounty Village
@BugBountyDEFCON
We’re excited to announce that Martin Doyhenard (@tincho_508) will be speaking at the Bug Bounty Village at DEF CON 33!
Stay tuned for more details on their talk, you won’t want to miss it.
#bugbounty #defcon #bbv #bugbountyvillage -
Burp Suite reposted
PortSwigger
@PortSwigger
What a morning it's already been at @BSidesLeeds!
It's brilliant to meet the Burp community, and hear all about how you're using Burp, the Web Security Academy and Burp AI!
Don't forget to drop by and say hello if you haven't yet. 👋
#burpontour2025 -
Burp Suite reposted
🇷🇴 cristi
@CristiVlad25
Top 3 @Burp_Suite extensions, by popularity:
1. JS Miner
2. Param Miner
3. Autorize
I use 1 and 3 in the majority of my pentests. -
Burp Suite
@Burp_Suite
😵💫 Wrestling with JWTs in Burp Suite?
Try JWT Editor - a powerful extension to decode, edit, and attack JSON Web Tokens directly inside your workflow. Save time and reduce the friction of dealing with raw JWT data.
Here’s what it does 🧵👇Post not available here, view on X
Burp Suite
@Burp_Suite
💥 Built-in JWT attacks
No fuss - just select and attack.
Burp Suite
@Burp_Suite
🚀 Add JWT Editor to Burp now:
portswigger.net/bappstore/26aaa5ded2f74beea19e2ed8345a93dd
#burpsuite #jwt #burpextension -
Burp Suite
@Burp_Suite
Bambdas are a super powerful, light-weight way to extend and customize Burp - and we love to hear all the exciting ways you're using them!
Get started with Bambdas 👉 portswigger.net/burp/documentation/desktop/extend-burp/ba…
#burpextensibility #bambdas
Mazid
@Normalitee0os
One of the best thing I had ever done is learning @Burp_Suite bambdas. Its just ABSOLUTELY AWESOME FEATURE!!!! Freaking love it!
-
Burp Suite
@Burp_Suite
Since April, testers have been leveraging Burp AI to accelerate their testing, uncover vulnerabilities, and secure applications faster than ever.
Whether it’s helping you spot subtle bugs, streamline your workflow, or even win bounties, Burp AI is changing the game. 🧵
#burpaiPost not available here, view on X
Burp Suite
@Burp_Suite
Want to see what the future of AppSec looks like, and shape it?
Join the #burp_ai channel on the PortSwigger Discord to share your thoughts 👉 discord.com/invite/portswigger
Burp Suite
@Burp_Suite
Read the full overview of the first two months of Burp AI today 👇
portswigger.net/blog/two-months-of-burp-ai-empowering-sec… -
Burp Suite reposted
James Kettle
@albinowax
I'm thrilled to announce "HTTP/1 Must Die! The Desync Endgame" is coming to #defcon33! This talk will feature multiple new classes of desync attack, mass exploitation spanning multiple CDNs, and over $200k in bug bounties. See you there!
-
Burp Suite
@Burp_Suite
Curious about how Burp AI is shaping the future of security testing?
We’ve hosted some brilliant conversations and demos on Discord, along with some exclusive insight from AppSec experts and bug hunters. Catch up on them now👇Post not available here, view on X
Burp Suite
@Burp_Suite
🎥 See how @_JohnHammond uses Burp AI to uncover web app vulnerabilities:
▶️ www.youtube.com/watch?v=v-McepNOrTQ
Burp Suite
@Burp_Suite
🗣️ Join the conversation on Discord and be part of the future of AppSec:
discord.com/invite/portswigger -
Burp Suite reposted
PortSwigger
@PortSwigger
In Gothenburg for Security Fest today? Don't miss out on getting your hands on this exclusive Burp 2025 swag! 🤩
#burpontour2025
Security Fest
@securityfest
Our friends @PortSwigger sent some nice t-shirts for #securityfest . Limited supply now available in the merch/sticker village!
-
Burp Suite
@Burp_Suite
🚀New: AI Substitutor
⚙️ Automatically replaces HTTP request params & headers with smart, context-aware values.
🧠 Perfect for Swagger/OpenAPI inputs, JS-sourced requests, or auto-gen traffic.
⏱️ Supercharge your testing workflow with AI-driven substitutions.
#burpai
Burp Suite
@Burp_Suite
Find it here 👇
portswigger.net/bappstore/bd1775972c944060a7051b364b98bd6f -
Burp Suite reposted
Gareth Heyes \u2028
@garethheyes
This vector adds an onerror handler with eval, rewrites all ReferenceError names, then triggers an error to execute the payload. Just added it to the XSS cheat sheet. Credit to @_0x999, inspired by @terjanq.
Link to vector👇 -
Burp Suite
@Burp_Suite
🚀 Burp Suite Professional has had a huge year – performance improvements, smarter AI-powered automation, and loads of powerful new features.
Curious to see what's new? Explore the highlights here 👉 portswigger.net/blog/whats-new-in-burp-suite-professional… -
Burp Suite reposted
Scott Williams
@T0kenAlpha
Always a good day when a PortSwigger box shows up! 🔥
Enjoy diving into the goodies — happy hacking! 🛠️🐞 -
Burp Suite
@Burp_Suite
Want to quickly and easily import BChecks and Bambdas to your library?
👀 Check out Extensibility Helper on the BApp Store!
📄 Pull scripts directly from the PortSwigger community repositories, or provide your own for a custom store experience.
Burp Suite
@Burp_Suite
Find it on the BApp Store 👇
portswigger.net/bappstore/41274be469184a56b06d6a791ce8a9ce -
Burp Suite
@Burp_Suite
Burp is now on tour for 2025! 😎
So far, we've supported events such as HackGlasgow, BSides Exeter, the University of Manchester's StudentHack, and, more recently, HAC NYC.
Comment below where you'd like to see Burp next... 👀
#burpontour2025 #burpsuite -
Burp Suite
@Burp_Suite
Write your own AI powered Custom Actions in Burp! ✨
In this video, Burp developer Ibz walks us through how...
#customactions #burpsuiteprofessionalThis media couldn't be displayed. See it on the original post. -
Burp Suite
@Burp_Suite
🚀 Burp Suite now has improved keyboard navigation, making it faster and easier to move around without having to use your mouse.
We’ve focused on key areas of Burp Suite, so try it out and let us know what you think.
Want more? We’re listening...👂
#burpsuiteprofessional -
Burp Suite reposted
Gareth Heyes \u2028
@garethheyes
URL-based XSS payload smuggling yup, it’s a thing. You can sneak payloads past filters in unexpected ways using the window name and creative URL abuse. Shoutout to @williamserizao for the idea.
Link to vectors👇 -
Burp Suite
@Burp_Suite
Struggling to keep up with new threats, techniques, and tools?
In a must-watch interview, @clintgibler sat down with Burp Suite creator @dafyddstuttard and Director of Research @albinowax to talk about AI and the future of pentesting.Post not available here, view on X
Burp Suite
@Burp_Suite
Or learn more about what was discussed in the interview in this blog post 👇
portswigger.net/blog/elevate-your-testing-with-burp-ai-wa…
Burp Suite
@Burp_Suite
Want to be the first to hear about new Burp AI features and chat with the devs behind them?
Join the PortSwigger Discord 👉 discord.com/invite/portswigger -
Burp Suite
@Burp_Suite
The Single Packet Shovel
Join us on the PortSwigger Discord this Thursday at 4pm BST (11am EST) as @t0xodile dives into widespread request tunnelling in major platforms like IIS, Azure Front Door, and AWS ALB.
Join the PortSwigger Discord to attend.👇
discord.com/invite/portswigger -
Burp Suite
@Burp_Suite
Unleash the power of Custom Actions ⚡
Check out this Custom Actions walkthrough from Ibz, a developer working on Burp Suite Professional!
#customactions #burpsuiteThis media couldn't be displayed. See it on the original post. -
Burp Suite reposted
Aituglo - Cassim
@aituglo
Living the dream, Apidays, and meeting bug hunters
aituglo.com/aituweek-45/ -
Burp Suite reposted
Aituglo - Cassim
@aituglo
The best swag from NYC 😌
Burp Suite
@Burp_Suite
Another great morning at APIdays for HAC NYC!
It's brilliant to meet so many people from the Burp community, and seeing hackers using Burp Suite for the event CTF. 💪
Don't forget to come grab some swag this afternoon before it all goes... 👀
#burpontour #burpsuite #hacnyc #apidays -
Burp Suite
@Burp_Suite
Awesome to see the exclusive HAC NYC Burp t-shirt made it into your swag haul - thanks for dropping by Richard!
Did anyone else manage to get their hands on one? 👀
#burpontour #apidays #hacnyc
Richard Choi
@choir241
Swag drop time 🔥
Can ya guess which one's my fav? :D
(The snacks aren't actually swag, but I got it from the conference and wanted to include them 😁) -
Burp Suite
@Burp_Suite
Another great morning at APIdays for HAC NYC!
It's brilliant to meet so many people from the Burp community, and seeing hackers using Burp Suite for the event CTF. 💪
Don't forget to come grab some swag this afternoon before it all goes... 👀
#burpontour #burpsuite #hacnyc #apidays -
Burp Suite
@Burp_Suite
Take Burp a step further and provide even more functionality than before with Custom Actions.
Use @tincho_508's new Bambda to take screenshots in Burp. You can also highlight and draw on your image to draw attention to specific areas.
Check it out 👉 github.com/PortSwigger/bambdas/blob/main/CustomAction/Scr… -
Burp Suite
@Burp_Suite
Have you tried out the MCP Server extension yet?
Integrate Burp Suite with AI Clients using the Model Context Protocol (MCP).
Not got Pro? Don’t worry, this extension is compatible with Community, too!
#burpsuite #mcp
Burp Suite
@Burp_Suite
Did you join Burp devs Dan and Dan on the Discord server, as they talked about MCP and their extension?
🎥 Check out the recording here: discord.com/channels/1159124119074381945/1183812376491986…
Burp Suite
@Burp_Suite
Find the extension on the BApp Store today, in-product or online!
👉 portswigger.net/bappstore/9952290f04ed4f628e624d0aa9dccebc -
Burp Suite
@Burp_Suite
👀 Extension developers, this one's for you…
-
Burp Suite
@Burp_Suite
Really insightful new research from @t0xodile coming to the PortSwigger Discord next week. 👏
Register for the event below...
Tom Stacey
@t0xodile
If you missed my talk "The Single-Packet Shovel: Digging for Desync-Powered Request Tunnelling" @BSidesExeter you have another chance to catch it on 22/05 at 16:00 BST on the @PortSwigger discord.
discord.com/events/1159124119074381945/1370395516856307774
Abstract and resources:
github.com/t0xodile/the-single-packet-shovel -
Burp Suite reposted
Tom Stacey
@t0xodile
If you missed my talk "The Single-Packet Shovel: Digging for Desync-Powered Request Tunnelling" @BSidesExeter you have another chance to catch it on 22/05 at 16:00 BST on the @PortSwigger discord.
discord.com/events/1159124119074381945/1370395516856307774
Abstract and resources:
github.com/t0xodile/the-single-packet-shovel -
Burp Suite reposted
PortSwigger
@PortSwigger
Burp in the Big Apple 🍎
PortSwigger is proud to sponsor HAC NYC as part of #apidays this week.
If you're at the event, swing by our stand to say hi! We’ve got exclusive Burp Suite NYC swag to give away! 🗽
#hacnyc #burpsuite -
Burp Suite
@Burp_Suite
In case you missed it: Burp can now scan Postman Collections, allowing you to seamlessly import your APIs. 📮
Check it out in the latest releases of Burp Suite Pro and Burp Suite DAST!
#burpsuiteprofessional #burpsuitedast -
Burp Suite reposted
🇷🇴 cristi
@CristiVlad25
Here's my story of how I use AI in my pentests, on @PortSwigger's blog.
Burp Suite
@Burp_Suite
From curiosity to critical impact: A pentester's perspective on Burp AI, with @CristiVlad25: portswigger.net/customer-stories/cristi-vlad-burp-ai
-
Burp Suite
@Burp_Suite
Skeptical about AI in pentesting? So was @CristiVlad25.
But with Burp AI, he found something different: practical, AI-powered assistance that augments his skills and expertise, without disrupting his workflow.
Read the case study 👇
Burp Suite
@Burp_Suite
From curiosity to critical impact: A pentester's perspective on Burp AI, with @CristiVlad25: portswigger.net/customer-stories/cristi-vlad-burp-ai
-
Burp Suite
@Burp_Suite
Have you checked out these brand-new Burp AI-augmented extensions?
Find out more below. 👇
#burpai #extensibilityPost not available here, view on X
Burp Suite
@Burp_Suite
MCP Server
🔥Compatible with Burp Suite Community and Professional
🔗Link Burp Suite to your AI clients with the Model Context Protocol
portswigger.net/bappstore/9952290f04ed4f628e624d0aa9dccebcThis media couldn't be displayed. See it on the original post.
Burp Suite
@Burp_Suite
Looking for more AI-augmented extensions?
Check out:
📝Report LM
👤Shadow Repeater
💭AI HTTP Analyzer
⚒️Hackvertor
Find them in Burp or online today!
portswigger.net/bappstore -
Burp Suite
@Burp_Suite
🧠 Use Burp Scanner’s new AI capabilities to reduce false positives starting with Broken Access Control!
This media couldn't be displayed. See it on the original post. -
Burp Suite
@Burp_Suite
There's still 1 more day left to enter our giveaway competition to win some exclsuive Burp AI swag! 🏆 ✨
Share how you've been using the new AI-powered features on Discord, X, or LinkedIn using #burpai to be in with a chance to win.
Competition ends tomorrow!
Tom Shelton-Lefley
@TomLefley
Tempted by the chance to win a t-shirt but unsure how it'll look if you wear one and then casually toss a second, identical t-shirt over your shoulder?
Wonder no more! -
Burp Suite reposted
Tom Shelton-Lefley
@TomLefley
Tempted by the chance to win a t-shirt but unsure how it'll look if you wear one and then casually toss a second, identical t-shirt over your shoulder?
Wonder no more! -
Burp Suite
@Burp_Suite
Thousands of pentesters are using Burp AI to hack smarter, cutting through tedious tasks and getting instant insights right inside Burp Suite.
Now, @_JohnHammond takes it for a spin. Here's what you need to know. 👇
#burpaiPost not available here, view on X
Burp Suite
@Burp_Suite
Watch John's walkthrough 👉 www.youtube.com/watch?v=v-McepNOrTQ
Burp Suite
@Burp_Suite
Using Burp AI already? Want free Burp swag?
Share your experience using #burpai and tag us by May 4th to be in with a chance to win an exclusive Burp AI t-shirt! -
Burp Suite reposted
-
Burp Suite reposted
d4d
@zakfedotkin
Think you’ve seen every OS command injection trick?
Think again, read our latest blog post!
Link in the comments👇 -
Burp Suite
@Burp_Suite
Have you checked out @garethheyes brand new extension, Document My Pentest, yet?
Supercharge your reporting workflow through the power of Burp AI by generating notes based on your testing.
Burp Suite
@Burp_Suite
Find the full writeup on our Research blog here 👇 portswigger.net/research/document-my-pentest
Burp Suite
@Burp_Suite
Check it out on the BApp Store here 👇
portswigger.net/bappstore/bc746627d8494445bf91988e2e20ede1 -
Burp Suite
@Burp_Suite
🚀 Reduce setup time and avoid scan failures, with one-click, AI-generated recorded login sequences.
-
Burp Suite
@Burp_Suite
👕 Want a Burp AI t-shirt like the ones our Swiggers are rocking?
Tell us how you’re using Burp AI - the wild, the wonderful, or just the downright efficient.
Post your take using #burpai and tag us. We’ll pick our favourites to win this piece of swag.
🗓️ Deadline to enter: 4 May -
Burp Suite
@Burp_Suite
Tailor Repeater to your specific testing needs, automate repetitive tasks and integrate seamlessly with external software and services with Custom Actions.
Get started with our pre-built samples such as ‘Retry request without cookies’
#burpextensibility
Burp Suite
@Burp_Suite
Test for high-impact race conditions without building complex workflows with @albinowax's Custom Action.
Check out this new Bambda and use it for yourself 👉 gist.github.com/albinowax/101e3b2e605496db1ddf84d14f5d0485
Burp Suite
@Burp_Suite
Join us on Discord on May 1st where we’ll showcase…
🚀 Using pre-built templates to analyze requests and responses.
💡 Seeing results immediately with powerful in-line analysis.
🛠️ Running your custom logic automatically every time you send a request.
👇 -
Burp Suite
@Burp_Suite
Get AI-powered, security-focused insights, directly in Burp Repeater with Explainer. ✨
#burpai #explainer -
Burp Suite
@Burp_Suite
📖 📚 Got a cool story about your experience with Burp AI? Share it with #burpai by midnight BST on 27 April for a chance to win some exclusive Burp AI swag ✨ 🛍️ .
-
Burp Suite
@Burp_Suite
🚨 BREAKING: PortSwigger HQ breached by fluffy ‘Intruder’ 🐰
Swiggers are discovering Burp Suite Professional easter eggs across the office. We don’t know if they have a mischievous ‘Collaborator’ or they acted alone.
Stay vigilant, and keep scanning responsibly.This media couldn't be displayed. See it on the original post. -
Burp Suite
@Burp_Suite
🥇 Meme competition result: we have a winner!
@GoatSniff hits the bullseye with this Olympic-level take on "Send to Intruder" and "Send to Repeater" 🎯
Thanks to everyone who got involved, we’ve loved seeing your creativity on display.
🔗 Head over to the PortSwigger Discord to take part in future events: discord.com/invite/portswigger -
Burp Suite
@Burp_Suite
We've loved seeing how you're all enjoying Burp AI ✨ in Burp Suite Professional. In case you haven't had a chance to try it out for yourself yet, @_JohnHammond took it for a spin earlier this week. Check out how he got on 👇
Burp Suite
@Burp_Suite
-
Burp Suite
@Burp_Suite
🧠 New in the BApp Store: two powerful AI tools to accelerate your manual testing workflow.
Two of these latest extensions take advantage of AI functionality included with Burp’s Montoya API.
Check them out 👇Post not available here, view on X
Burp Suite
@Burp_Suite
AI Prompt Fuzzer
🎯 Fuzz LLM prompts with targeted payloads and custom verification conditions
🤖 Get a sense check via Burp AI for enhanced prompt injection detection
👉 portswigger.net/bappstore/d3d1f3c9427e453193eb5deb3b6c115a
Burp Suite
@Burp_Suite
Create your own extensions augmented with Burp AI today!
Check out Tom’s video showing how here 👇
www.youtube.com/watch?v=66Zo3l2tkKA -
Burp Suite
@Burp_Suite
🎉 'What I've learned creating AI extensions' with Gareth Heyes ✨
Want to build your own AI-enhanced Burp tools like HackVertor or Shadow Repeater? This Thursday, join PortSwigger researcher @garethheyes as he shares lessons, tips, and tricks to help you get started.
Join the PortSwigger Discord server to attend👇
#burpai
Burp Suite
@Burp_Suite
-
Burp Suite
@Burp_Suite
Get started with AI extensions in Burp Suite! ✨
Leverage cutting-edge AI technology to further enhance and automate your workflow in ways that were previously not possible, all with minimal overhead.
#toptiptuesday #burpai #burpsuiteprofessionalThis media couldn't be displayed. See it on the original post. -
Burp Suite
@Burp_Suite
Using Burp AI? We’d love to hear how you're getting on.
🗣️Share your experience using #burpai on X, BlueSky, or in the PortSwigger Discord by midnight (BST) on 27th April for a chance to win some limited-edition swag.
Join the PortSwigger Discord 👇
Burp Suite
@Burp_Suite
-
Burp Suite
@Burp_Suite
🔌 Introducing the Burp Suite MCP Server extension
Join us this Tuesday at 4pm BST (11am EDT) to see how you can leverage MCP for powerful AI integrations with Burp Suite. Live demo + Q&A with the devs.
Join the PortSwigger Discord to attend 👉 discord.com/invite/portswigger?event=1359889456810954763 -
Burp Suite
@Burp_Suite
🤫 #sneakpeekthursday #burpsuite #bappstore
-
Burp Suite
@Burp_Suite
This is definitely not one to miss...
Check out @clintgibler's brand new deep dive into AI and Burp Suite, with Burp Suite creator @DafyddStuttard and PortSwigger Researcher @albinowax. ✨
Clint Gibler
@clintgibler
🔥 𝐇𝐨𝐰 @Burp_Suite 𝐀𝐈 𝐜𝐚𝐧 𝐞𝐥𝐞𝐯𝐚𝐭𝐞 𝐲𝐨𝐮𝐫 𝐩𝐞𝐧𝐭𝐞𝐬𝐭𝐢𝐧𝐠
@PortSwigger founder Dafydd Stuttard & Director of Research @albinowax on how Burp is leveraging AI to become even more powerful.
📺 Watch here: youtu.be/3_tCNaQa-Qo
We discussed:
🔹 How Portswigger thinks about AI, and why now
🔹 How Burp AI respects user privacy
🔹 How Portswigger decided where AI can add value
🔹 Burp's new AI API
🔹 Future plans preview - what's coming next??
And two SUPER cool demos:
⚒️ 𝐄𝐱𝐩𝐥𝐨𝐫𝐞 𝐈𝐬𝐬𝐮𝐞 - Investigate & exploit this SQL injection for me
⚒️ 𝐒𝐡𝐚𝐝𝐨𝐰 𝐑𝐞𝐩𝐞𝐚𝐭𝐞𝐫 - Automatically iterates on your manual testing with new payloads
Highly recommend giving this a watch, both to see the tech itself, and to learn from a company thoughtfully integrating AI into their product (vs. just joining the hype bandwagon).
---
✨ 𝐁𝐨𝐧𝐮𝐬 𝐑𝐞𝐬𝐨𝐮𝐫𝐜𝐞𝐬
Here are some relevant blogs from Portswigger on their AI work:
𝐓𝐡𝐞 𝐟𝐮𝐭𝐮𝐫𝐞 𝐨𝐟 𝐬𝐞𝐜𝐮𝐫𝐢𝐭𝐲 𝐭𝐞𝐬𝐭𝐢𝐧𝐠: 𝐡𝐚𝐫𝐧𝐞𝐬𝐬 𝐀𝐈-𝐏𝐨𝐰𝐞𝐫𝐞𝐝 𝐄𝐱𝐭𝐞𝐧𝐬𝐢𝐛𝐢𝐥𝐢𝐭𝐲 𝐢𝐧 𝐁𝐮𝐫𝐩
📎 portswigger.net/blog/the-future-of-security-testing-harne…
𝐖𝐡𝐲 𝐢𝐭'𝐬 𝐭𝐢𝐦𝐞 𝐟𝐨𝐫 𝐀𝐩𝐩𝐒𝐞𝐜 𝐭𝐨 𝐞𝐦𝐛𝐫𝐚𝐜𝐞 𝐀𝐈: 𝐇𝐨𝐰 𝐏𝐨𝐫𝐭𝐒𝐰𝐢𝐠𝐠𝐞𝐫 𝐢𝐬 𝐥𝐞𝐚𝐝𝐢𝐧𝐠 𝐭𝐡𝐞 𝐜𝐡𝐚𝐫𝐠𝐞
📎 portswigger.net/blog/why-its-time-for-appsec-to-embrace-a…
𝐖𝐞𝐥𝐜𝐨𝐦𝐞 𝐭𝐨 𝐭𝐡𝐞 𝐧𝐞𝐱𝐭 𝐠𝐞𝐧𝐞𝐫𝐚𝐭𝐢𝐨𝐧 𝐨𝐟 𝐁𝐮𝐫𝐩 𝐒𝐮𝐢𝐭𝐞: 𝐞𝐥𝐞𝐯𝐚𝐭𝐞 𝐲𝐨𝐮𝐫 𝐭𝐞𝐬𝐭𝐢𝐧𝐠 𝐰𝐢𝐭𝐡 𝐁𝐮𝐫𝐩 𝐀𝐈
📎 portswigger.net/blog/welcome-to-the-next-generation-of-bu…
𝐁𝐮𝐫𝐩 𝐀𝐈 𝐬𝐞𝐜𝐮𝐫𝐢𝐭𝐲, 𝐩𝐫𝐢𝐯𝐚𝐜𝐲 𝐚𝐧𝐝 𝐝𝐚𝐭𝐚 𝐡𝐚𝐧𝐝𝐥𝐢𝐧𝐠
📎 portswigger.net/burp/documentation/desktop/burp-ai/ai-sec…
---
📺 Watch here: youtu.be/3_tCNaQa-Qo
Let me know what you think 👇
Which of these features looks most exciting?
What do you hope Portswigger adds next?
#cybersecurity #ai -
Burp Suite
@Burp_Suite
We love to see our community BApp authors repping the new Burp extensibility swag. 😎
Create your own extension and submit it to the BApp store and we'd love to share some swag with you in the future! #burpsuiteprofessional #extensibility
Soroush Dalili
@irsdl
Thanks @PortSwigger , the swags look awesome 🤩
-
Burp Suite reposted
Soroush Dalili
@irsdl
Thanks @PortSwigger , the swags look awesome 🤩
-
Burp Suite
@Burp_Suite
Have you checked out the new AI feature Explore Issue yet? ✨
Save time by automating follow-up analysis of scanner-identified vulnerabilities to reduce blind spots and uncover deeper insights.
#toptiptuesday #burpai #burpsuiteprofessionalThis media couldn't be displayed. See it on the original post. -
Burp Suite
@Burp_Suite
'AI and Security Research: Ask Me Anything' with James Kettle 🔥
Join us on Thursday at 4pm BST (11am EDT) for this exclusive event, and don't forget to submit your questions here: app.sli.do/event/ou8cmSGqnVdBzXYGpYftCT
Join the PortSwigger Discord to attend 👉 discord.com/invite/portswigger -
Burp Suite reposted
🇷🇴 cristi
@CristiVlad25
It's nice when you find one of these ATOs. And it was Burp's AI that gave me the lead. (for a client's pentest)
@PortSwigger @Burp_Suite -
Burp Suite
@Burp_Suite
Join the exclusive 'Introducing Burp AI' event over on the PortSwigger Discord this Tuesday at 4pm BST (11am EDT). ✨
Burp Suite developers Jay and Pete will be sharing the low down on the five new AI-powered features that landed in Burp Suite Professional this week, including live demos!
Join the PortSwigger Discord to attend 👉 discord.com/invite/portswigger -
Burp Suite
@Burp_Suite
In case you missed it, here's the low down on the new AI-powered features that arrived in Burp Suite Professional earlier this week. 👇
Let us know what you think! #burpai #burpsuiteprofessional
Burp Suite
@Burp_Suite
Burp AI is here ✨
We believe AI has the power to transform pentesting - not by replacing human testers, but by augmenting them.
Burp AI, a set of powerful features designed to enhance your workflow, reduce noise, and give you deeper insight into vulnerabilities is now available. 🧵
#burpai -
Burp Suite
@Burp_Suite
Don't miss this brand new AI extension in the BApp store! ✨
MCP Server allows you to:
✅ Connect Burp Suite to AI clients
✅ Easily integrate with Claude Desktop
MCP Server also comes with a packaged Stdio MCP proxy server.
Check it out 👇
BApp Store
@BApp_Store
🚀 Fresh in the BApp Store: MCP Server
Link Burp Suite to your AI clients with the Model Context Protocol.
🧠 Integration with Claude Desktop? Easy-peasy.
🛰️ Need a Stdio MCP proxy? Locked and loaded.
🔓 Unlock new LLM workflows. -
Burp Suite reposted
PortSwigger
@PortSwigger
‘Why AppSec should embrace AI’ with Burp Suite creator Dafydd Stuttard ✨
Planning to attend this exclusive event tomorrow? @DafyddStuttard will be sharing his thoughts, along with an insight into PortSwigger’s journey to AI, at 4pm BST (11am EDT).
Join the PortSwigger Discord to attend 👉 discord.com/invite/portswigger -
Burp Suite
@Burp_Suite
Burp AI is here ✨
We believe AI has the power to transform pentesting - not by replacing human testers, but by augmenting them.
Burp AI, a set of powerful features designed to enhance your workflow, reduce noise, and give you deeper insight into vulnerabilities is now available. 🧵
#burpaiPost not available here, view on X
Burp Suite
@Burp_Suite
Explainer 💡
Instantly understand unfamiliar tech from a security perspective, right inside Burp.
Burp Suite
@Burp_Suite
AI-generated login sequences 🔐
No more browser dance. Let burp AI generate recorded logins for you.Post not available here, view on X
Burp Suite
@Burp_Suite
To celebrate the arrival of Burp AI, we’re giving all Burp Suite Professional users 10,000 free AI credits! 🥳
Update to 2025.2.3 today to get started: portswigger.net/burp/releases/professional-community-2025…
Burp Suite
@Burp_Suite
Get the inside scoop on Burp AI
This April, we’re celebrating the launch of Burp AI with a series of exclusive live events on the PortSwigger Discord, including sessions with world-renowned experts @albinowax and @garethheyes.
Join the Portswigger Discord 👉 -
Burp Suite
@Burp_Suite
Burp AI is coming to Burp Suite Professional next week! ✨
Take a look at what's in store... #burpai #sneakpeekThis media couldn't be displayed. See it on the original post. -
Burp Suite reposted
BApp Store
@BApp_Store
Do you use extensions in Burp?
Are they essential to your workflow?
Is there one that's just really cool that you love?
Let us know!
📝 Fill out this quick form with your 3 top extensions from the BApp Store.
⭐ If you'd like to tell us why, there's space for that too! -
Burp Suite
@Burp_Suite
Don't miss this series of exclusive events, including live sessions with the PortSwigger Research team, over on the PortSwigger Discord this April! 👇
PortSwigger
@PortSwigger
Big things are happening on the PortSwigger Discord this April! ✨
We’re celebrating the launch of Burp AI with a lineup of exclusive events over on Discord, featuring AppSec legends, live demos, and even a community gaming session.
Here’s what’s coming up… 🧵 -
Burp Suite
@Burp_Suite
Burp AI sneak peek: introducing Explore Issue... 👀
Turn Burp into your personal pentesting assistant, automating follow-up on scanner-identified vulnerabilities to save time, reduce blind spots, and uncover deeper insights.
#burpai #burpsuiteprofessional #sneakpeek -
Burp Suite
@Burp_Suite
Have you tried out any of our new AI extensions on the BApp Store? These community-written extensions can help you unlock the potential of Burp AI.
Check them out below 👇 #burpaiPost not available here, view on X
Burp Suite
@Burp_Suite
See ReportLM on the BApp Store👇
portswigger.net/bappstore/c29264074acc4aacb5b424e6a033ba5d
Burp Suite
@Burp_Suite
Working on your own AI extension with the Montoya API? Let us know in the replies! 💪
-
Burp Suite
@Burp_Suite
Have a great idea for how to leverage the power of Burp AI in an extension? Tom from the PortSwigger development team shows you just how easy it is to build AI features using the Montoya API! 🤖
www.youtube.com/watch?v=66Zo3l2tkKA -
Burp Suite
@Burp_Suite
☘️ Ever tried to 'Split the B'? Neither had we—until now!
Happy St. Patrick's Day from the PortSwigger team! Watch as some of the team tries to master this techy twist on a well-loved tradition. Sláinte! 🍻
(Non-alcoholic beer was used in the making of this video.)This media couldn't be displayed. See it on the original post. -
Burp Suite
@Burp_Suite
Are you ready for another Burp AI sneak peek? 👀
Introducing False Positive Reduction - Access Control.
#burpai -
Burp Suite
@Burp_Suite
Another new AI-powered BApp just launched - ReportLM from our own @TomLefley 🚀
Transform issues into comprehensive, customized reports using the capabilities of Burp AI!
#burpai #extensibility
Burp Suite
@Burp_Suite
With this new BApp, you can leverage AI to generate vulnerability reports that are tailored to your specific needs, and best suited to your intended audience.
🧑🏫 Adjust technical depth.
🧑🔧 Focus on reproduction or remediation.
🌍 Even choose the language!
Burp Suite
@Burp_Suite
Check out ReportLM 👇portswigger.net/bappstore/c29264074acc4aacb5b424e6a033ba5d
-
Burp Suite
@Burp_Suite
Check out what's new in Burp Suite Professional 2025.2 🤩
#burpsuiteprofessionalThis media couldn't be displayed. See it on the original post. -
Burp Suite
@Burp_Suite
We’re super excited about a WICKED new feature coming to Burp Suite Professional in 2025.2, and available now in Early Adopter! 📚
#bambdalibrary #burpsuite -
Burp Suite
@Burp_Suite
Incoming Burp AI sneak peek 👀 🤫
Next up, we have AI-generated recorded login sequences…
#burpai #burpsuite -
Burp Suite
@Burp_Suite
Had a chance to check out @garethheyes Shadow Repeater yet? ✨ #burpai #bapps #extensibility
Burp Suite
@Burp_Suite
Simply use Burp Repeater as normal, and Shadow Repeater will learn from your attacks, try payload permutations, and report any discoveries via Organizer.
Read more 👇 portswigger.net/research/shadow-repeater-ai-enhanced-manu…
Burp Suite
@Burp_Suite
Take a look at Gareth’s walkthrough of Shadow Repeater 👇
www.youtube.com/watch?v=Z1uJmfCGpRE
Burp Suite
@Burp_Suite
Are you working on your own AI extension for Burp using the Montoya API?
Let us know in the replies... -
Burp Suite
@Burp_Suite
Did you know Param Miner can dynamically analyze your proxy traffic to generate wordlists tailored to your target?
#burpsuitetoptip #paramminer #burpextensibility -
Burp Suite
@Burp_Suite
The Bambda Library walkthrough event is happening today at 4pm GMT (11am ET).
Join us on the PortSwigger Discord for an in-depth look into this new Bambda feature! Register here 👉 discord.com/invite/portswigger?event=1341728502872932364 -
Burp Suite reposted
🇷🇴 cristi
@CristiVlad25
super pumped about this. AI augmenting my #1 tool for pentesting.
Burp Suite
@Burp_Suite
As promised, here's the first sneak peek into our new AI-powered features coming to Burp Suite Professional next month... 👀 🤫
First up, we have Explain This.
#burpai #burpsuite -
Burp Suite reposted
Clint Gibler
@clintgibler
📚 tl;dr sec 268
🤖 AI-powered Burp Suite
👨💻 OAuth Vulnerabilities
🤖 Subtle LLM Backdoors
🥰Plus a few communication and relationship resources I gathered from this week's responses!
tldrsec.com/p/tldr-sec-268 -
Burp Suite
@Burp_Suite
As promised, here's the first sneak peek into our new AI-powered features coming to Burp Suite Professional next month... 👀 🤫
First up, we have Explain This.
#burpai #burpsuite -
Burp Suite
@Burp_Suite
New AI-powered BApp just landed - AI HTTP Analyzer from @alpernae 🚀
AI HTTP Analyzer is our first community-written extension using the new Montoya AI API.
#burpai #extensibility
Burp Suite
@Burp_Suite
With this new BApp, you can leverage AI to analyze HTTP requests & responses for security vulnerabilities like SQLi, XSS, CSRF, and more.
🔍 Get instant, focused security insights.
⚡️ Identify vulnerabilities with AI-driven precision.
📌 See PoCs, payloads & exploitation steps.
Burp Suite
@Burp_Suite
Check out AI HTTP Analyzer 👇
portswigger.net/bappstore/36cb140ac1a6449bbab1bafc18df8cfa -
Burp Suite
@Burp_Suite
Did you know, with the new Bambda Library, you can save your favorite Bambdas? 💾
#burptoptip #bambdalibrary #extensibility -
Burp Suite
@Burp_Suite
Introducing the Bambda Library!
Join us on the PortSwigger Discord on March 4 at 11am ET (4pm GMT) for an exclusive walkthrough...
💾 Save and re-use your favorite Bambdas
🚀 Get started quicker with built in templates
📂 Keep Bambdas organized
Register 👉 -
Burp Suite
@Burp_Suite
Shadow Repeater ✨
Check out this new AI-powered extension from @garethheyes 👇 #burpai #bapps
Gareth Heyes \u2028
@garethheyes
We've just released Shadow Repeater, for AI-enhanced manual testing. Simply use Burp Repeater as you normally would, and behind the scenes Shadow Repeater will learn from your attacks, try payload permutations, and report any discoveries via Organizer.
Post not available here, view on X
Burp Suite
@Burp_Suite
Read more about Shadow Repeater and how to install this extension:
portswigger.net/research/shadow-repeater-ai-enhanced-manu…
Burp Suite
@Burp_Suite
It’s been awesome to see AI-powered extensions already being created and used in Burp Suite Professional. 💪
Let us know how you’re getting on with building your own AI extensions with the Montoya API below! -
Burp Suite
@Burp_Suite
Coming soon to the latest stable version... #montoya #sneakpeek #burpai
-
Burp Suite
@Burp_Suite
New AI enhancements to Hackvertor ✨
Post not available here, view on X
Burp Suite
@Burp_Suite
Want to know more about AI-powered extensibility in Burp?
Check out this blog post 👉 portswigger.net/blog/the-future-of-security-testing-harne…
Burp Suite
@Burp_Suite
Let us know how you’re getting on with these new Hackvertor AI enhancements over on the PortSwigger Discord. 👾
Join the PortSwigger Discord 👇
discord.com/invite/portswigger -
Burp Suite
@Burp_Suite
AI-powered extensibility in Burp 🛠️ #burpai
Post not available here, view on X
Burp Suite
@Burp_Suite
AI-powered extensibility opens up new possibilities for solving challenges that were previously difficult with traditional code alone.
Now, you can leverage AI to enhance security testing, automate tedious tasks, and gain deeper insights into web application vulnerabilities.
Burp Suite
@Burp_Suite
By using the purpose-built Montoya API, you can seamlessly integrate AI capabilities with minimal overhead, while ensuring all of your interactions with AI all remain within PortSwigger’s trust boundary.
Post not available here, view on X
Burp Suite
@Burp_Suite
Read more about AI-powered extensibility in Burp 👉 portswigger.net/blog/the-future-of-security-testing-harne…
Burp Suite
@Burp_Suite
Interested in learning more about why we're introducing AI into Burp Suite and what our plans are for future development?
Check out this blog post from Burp Suite creator, @DafyddStuttard.
👉portswigger.net/blog/why-its-time-for-appsec-to-embrace-a… -
Burp Suite
@Burp_Suite
Last week we announced Burp Suite's first AI-powered enhancements.
In this new blog post, Burp Suite creator, @DafyddStuttard, dives into why it's now time for AppSec to embrace AI. 👇
Burp Suite
@Burp_Suite
Burp Suite just got its first AI-powered enhancements.
PortSwigger's Chief Swig and Burp Suite creator, @DafyddStuttard , explains how we’re approaching AI responsibly—and why the AppSec industry needs to challenge its natural skepticism.
Read more below 👇 -
Burp Suite
@Burp_Suite
Burp Suite just got its first AI-powered enhancements.
PortSwigger's Chief Swig and Burp Suite creator, @DafyddStuttard , explains how we’re approaching AI responsibly—and why the AppSec industry needs to challenge its natural skepticism.
Read more below 👇 -
Burp Suite
@Burp_Suite
Happy Valentine's Day!
In case you missed it, check out the announcement we made yesterday for Burp AI below. 👇 #burpai
Burp Suite
@Burp_Suite
Welcome to the next evolution of Burp Suite… 🚀 #burpai
-
Burp Suite
@Burp_Suite
Welcome to the next evolution of Burp Suite… 🚀 #burpai
Post not available here, view on X
Burp Suite
@Burp_Suite
The ability to build AI-powered extensions is now available in Early Adopter 2025.2.
If you’re eager to start integrating AI into your workflow, now’s the time to build your own extension. 💪
Burp Suite
@Burp_Suite
Want to keep up to date with everything AI-related in Burp?
Join the PortSwigger Discord and head over to the dedicated Burp AI channel to stay up-to-date with new features and chat with Burp developers. 👾
discord.com/invite/portswigger -
Burp Suite
@Burp_Suite
Coming soon, something you’ll fall in love with. 😍✨
Disclaimer: we are not releasing a voice-activated bot… or offering a date with Dave.This media couldn't be displayed. See it on the original post. -
Burp Suite
@Burp_Suite
Gain granular control of your scans 👾
Run your scan checks against specific targeted insertion points with Intruder in Burp Suite Professional.
Check out how 👇
Burp Suite
@Burp_Suite
Quickly and easily apply custom encodings to your insertion points using the Hackvertor BApp by @garethheyes.
⬇️ Download the BApp:
portswigger.net/bappstore/65033cbd2c344fbabe57ac060b5dd100 -
Burp Suite reposted
BApp Store
@BApp_Store
Bypass Bot Detection, a @PortSwiggerRes extension, is now live in the BApp Store!
This extension helps you bypass TLS fingerprinting by mimicking browser fingerprints and brute-forcing protocol/cipher combinations -
Burp Suite
@Burp_Suite
BApp spotlight ✨
BApp author Tobias "floyd" Ospelt, co-founder of boutique pentesting company Pentagrid, has a wealth of tools and research in web app security, mobile apps, fuzzing, and cryptographic weaknesses.
Explore his BApps here 👇Post not available here, view on X
Burp Suite
@Burp_Suite
Pentagrid Scan Controller
Integrating with @hackvertor’s Hackvertor, this tool is helpful for enhancing Scanner usage by selectively auto-scanning only relevant requests.
portswigger.net/bappstore/e3dde890bdce4ae4bcef0d97019f5d46
Burp Suite
@Burp_Suite
Upload Scanner
Uncover vulnerabilities in server-side file parsing and processing using Upload Scanner. This BApp automates and customizes various attack techniques - like XSS, XXE, and SSRF.
portswigger.net/bappstore/470b7057b86f41c396a97903377f3d81 -
Burp Suite reposted
Musta Kissa
@CharyyevPerman
Yo, this IntelliJ plugin makes writing BChecks feel way smoother. Syntax highlighting? Auto-complete? Straight-up game changers!
-
Burp Suite
@Burp_Suite
TUBs: Totally Useless Bambdas - hosted by @0xTib3rius
Watch Tib3rius react to a few of our TUBs competition entries.
View all TUBs here: github.com/Tib3rius/Tibs-TUBs -
Burp Suite reposted
N$🌟
@__nav1n_
Wayback > hidden subdomain > Fuzz > Intruder > P1 🔥
Found a hidden subdomain dashboard.xxx.target.com in Wayback Machine dated back to 2019. Got 301 to the homepage in browser. While fuzzing, I found an interesting empty directory: `bin`. Used Burp Intruder and found a directory traversal bug. 💥 #bugbounty -
Burp Suite
@Burp_Suite
📝 Use your IDE to write and optimize your BChecks!
This IntelliJ plugin, built by PortSwigger, enhances your experience by providing a familiar coding environment with syntax highlighting, auto-complete, and more.
Check it out today ⬇️
Burp Suite
@Burp_Suite
Find the IntelliJ plugin here 👇
plugins.jetbrains.com/plugin/24320-bchecks
Burp Suite
@Burp_Suite
Once you’ve created your BChecks, don’t forget to test them in Burp Suite Professional:
www.youtube.com/watch?v=KgBQrx0Cy7s -
Burp Suite
@Burp_Suite
Print or log output to a console when writing Bambdas, making it easy to inspect variables, track errors, and test your code #toptiptuesday
-
Burp Suite
@Burp_Suite
Coming soon: Concurrent crawl and audit
📈 Start finding issues immediately as your attack surface is uncovered - no more waiting around for the crawl to finish!
#sneakpeek -
Burp Suite
@Burp_Suite
⏱️ Save valuable time by viewing and importing BChecks directly in Burp Suite Professional with BCheck Helper.
This extension adds a dedicated tab to streamline BCheck imports.
Burp Suite
@Burp_Suite
Download now 👇
portswigger.net/bappstore/41274be469184a56b06d6a791ce8a9ce
Burp Suite
@Burp_Suite
Extend Burp Scanner's power without coding! Learn how to author a BCheck & detect SQLi like a pro. Watch this video on crafting BChecks to hunt vulnerabilities:
www.youtube.com/watch?v=NaiQMJk4nus
Burp Suite
@Burp_Suite
🤔 Did you know that you can run BCheck only scans in Burp Suite Professional? Check out how here:
www.youtube.com/watch?v=WUbJiTxsWkM -
Burp Suite
@Burp_Suite
Take more control and create advanced proxy match and replace rules with Bambdas.
Check out this example where you can set up a rule to hijack CSP reports.
Find out more here: portswigger.net/burp/documentation/desktop/tools/proxy/ma… -
Burp Suite
@Burp_Suite
Coming soon: Bambda library
💾 Save and load your Bambdas across Burp projects
⏬ Easily load saved Bambdas in situ
🚀 Get started quicker with new Bambda templates
#sneakpeek -
Burp Suite
@Burp_Suite
Thread: Unlock Burp Suite's full potential! 🔌
1/ Customization is key to effective pentesting. With Bambdas, BChecks, & BApps, you can enhance workflows, automate tasks, & adapt to unique needs.👇
Read full blog here: portswigger.net/blog/make-burp-suite-your-own-high-powere…
Burp Suite
@Burp_Suite
2/ What are Bambdas?
🔹 Easy-to-write, modular code snippets.
🔹 Add custom filters to Proxy history, Site Maps, and more.
🔹 Tailor workflows quickly for specific use cases - like filtering protocols or identifying discrepancies.
Burp Suite
@Burp_Suite
3/ Coming soon for Bambdas:
The Bambda Library will let you save & manage scripts directly in Burp Suite - making it even easier to collaborate and stay organized. 👏
Burp Suite
@Burp_Suite
4/ What about BChecks?
Custom Scan Checks expand scanning coverage beyond standard features. Automate the detection of niche vulnerabilities and standardize scans for consistency.
Available in Burp Suite Professional & Burp Suite Enterprise Edition.
Burp Suite
@Burp_Suite
5/ For the power users: BApp extensions.
Go beyond customization with large-scale integrations and tools. Leverage the BApp Store, where 10+ years of community expertise have created game-changing plugins.
Here are our top picks this month: 👇
Burp Suite
@Burp_Suite
6/ BApp Store Highlights:
🔹 ActiveScan++: Extend active/passive scanning (now works in Burp Suite Enterprise Edition).
🔹 JWT Editor: Manipulate JWTs for common attacks.
🔹 Autorize: Automate broken access control testing.
Check out the store: portswigger.net/bappstore
Burp Suite
@Burp_Suite
7/ Feeling creative?
Use the Montoya API to build your own extensions in Java and submit them to the BApp Store. Join a thriving community of 80,000+ pentesters who benefit from your expertise. 🌍
Burp Suite
@Burp_Suite
8/ Your workflow, your way.
Bambdas, BChecks, and Extensions offer a wealth of opportunities to customize and supercharge Burp Suite. Ready to get started?
🔗 Explore Burp Suite extensions further in the blog: portswigger.net/blog/make-burp-suite-your-own-high-powere… -
Burp Suite
@Burp_Suite
Thread: BApp spotlight ✨
1/Corey Arthur, a penetration tester and occasional bounty hunter, has created powerful BApps tailored to their workflow. Built with Java/Kotlin, these tools solve real testing challenges and benefit from community-driven improvements.
See the BApps👇
Burp Suite
@Burp_Suite
2/ Stepper
Stepper extends Burp Suite’s Repeater, enabling step sequences and value extraction for use in subsequent steps.
portswigger.net/bappstore/065d156ecefd480fa3efa36e05d55f77
Burp Suite
@Burp_Suite
3/ Customizer
Enhance your experience with FlatLaf themes! Enjoy bundled options or third-party IntelliJ themes for a sleek look.
portswigger.net/bappstore/4265b6220a524d0da966e64e94fa9b26
Burp Suite
@Burp_Suite
4/ Logger++
Check out Logger++ to log traffic with enhanced export functionality, easy colorization, grep and filter options.
portswigger.net/bappstore/470b7057b86f41c396a97903377f3d81 -
Burp Suite
@Burp_Suite
🚀 Bambdas empower you to streamline your workflow by customizing and filtering your site map with precision.
Bambdas have a number of other powerful use-cases, for more details, check out the documentation and get started with Bambdas today:
portswigger.net/burp/documentation/desktop/extensions/bam… -
Burp Suite
@Burp_Suite
-
Burp Suite
@Burp_Suite
Modify Burp’s traffic with CSTC 👨🍳
Built for experts, CSTC enables you to define recipes that are applied to incoming or outgoing HTTP requests/responses automatically.
Download “CSTC, Modular HTTP Manipulator” in the BApp store today!
Burp Suite
@Burp_Suite
Download 👉 portswigger.net/bappstore/866df66d339d4bcd9b599772aff32efd
-
Burp Suite reposted
ISOC LIVE
@ISOC_Live
VIDEO: BSidesNYC 2024 - Building Burp Extensions with Kotlin - Nick Coblentz @VirtueSecurity
youtu.be/F5h9oIkrPyk?list=PLlg8We3ePxcMDrUFNWs7hyx3uJwnhK-_a
@BSidesNYC #bsidesnyc #bsidesnyc2024 #bsidesnyc0x04 #cybersecurity #infosec #kotlin @Burp_Suite -
Burp Suite reposted
Tib3rius
@0xTib3rius
Here's a good question from a conversation I had earlier. If you're a professional web app tester and you use Burp, which native (i.e. not extension) features do you use that aren't:
Intruder, Repeater, Intercept, or Collaborator.
Personally I can think of quite a few. 🤔 -
Burp Suite reposted
bugcrowd
@Bugcrowd
Want to get to grips with @Burp_Suite?
@insiderPhD has created this Burp Suite guide that you need to check out!
What's covered?
🪲 Setting up
🐛 Key features
🐞 Tips for beginners
Watch now! 👇
www.youtube.com/watch?v=ltgfOgN1GIo -
Burp Suite
@Burp_Suite
Happy new year to the Burp community! 🥳
Here's Carlos Montoya's resolutions... let us know your New Year's resolutions for 2025 below. 👀 -
Burp Suite
@Burp_Suite
You guys aced 2024, take a look below! 👇
PortSwigger
@PortSwigger
Wow, what a year 2024 has been! 🧵
The Burp Suite community has achieved so much, from completing Academy labs and passing the Burp Certification, to running events on the PortSwigger Discord.
Let’s take a look at what you’ve been up to this year… 👀 -
Burp Suite
@Burp_Suite
Burp's hex editor enables you to make precise changes to a request’s contents.
This is useful for attacks that involve non-printable characters or binary data. Let us show you how...
#burpsuitetoptip -
Burp Suite
@Burp_Suite
👀 🤫 #sneakpeek #bambdas
-
Burp Suite
@Burp_Suite
📈 97% faster load times in Burp Suite Enterprise Edition.
Learn about the recent performance improvements, designed for AppSec teams scanning large web application estates, in our latest video
Watch it here: www.youtube.com/watch?v=VXuFQIeZoBo -
Burp Suite
@Burp_Suite
After a major rewrite, ActiveScan++ is now available for Burp Suite Enterprise Edition! 🔥
Extend Burp Suite's active and passive scanning capabilities with this BApp from @albinowax
Download ActiveScan++ below. 👇 -
Burp Suite
@Burp_Suite
Filter Site map with Bambdas, output console for Bambdas, dynamic authentication tokens for API only scans and more in 2024.11. Update now to enjoy these updates!
-
Burp Suite
@Burp_Suite
-
Burp Suite
@Burp_Suite
📃 You can now generate PDF reports in Burp Suite Enterprise Edition.
Streamline your reporting processes with native PDF reporting. Share and encrypt sensitive vulnerability information, without relying on workarounds.
Upgrade to version 2024.11 to get started. -
Burp Suite
@Burp_Suite
New to Intruder... 🔥
The Payload position dropdown now shows both the payload position number and the enclosed text when setting up Pitchfork or Cluster bomb attacks!
#burpsuite #burptoptip -
Burp Suite
@Burp_Suite
🚀 Take control of HTTP traffic with Reshaper!
Shoutout to Daquanne Dwight for crafting and maintaining this must-have Burp Suite Pro extension!
Trigger actions and reshape HTTP request and response traffic with powerful, configurable rules.
Burp Suite
@Burp_Suite
⬇️ Download the Reshaper BApp here:
portswigger.net/bappstore/7bcec7656b5746e9a85c427f243e6d5a -
Burp Suite
@Burp_Suite
-
Burp Suite reposted
Tae’lur Alexis
@TaelurAlexis
Here’s my new blog post about finding and exploiting access control vulnerabilities on @portswigger :-)! Hope you enjoy taeluralexis.com/exploiting-and-remediating-access-contro…
-
Burp Suite
@Burp_Suite
🧼 SOAP API scanning is now supported in Burp Suite Enterprise Edition.
To start scanning, upload a WSDL definition file, or provide a URL to initiate scans - including for CI-driven pipelines.
Update to version 2024.11to start scanning your SOAP APIs. -
Burp Suite
@Burp_Suite
Did you know you can customize which HTTP request headers appear in the message editor in Burp? 🔥#burpsuite #toptiptuesday
This media couldn't be displayed. See it on the original post. -
Burp Suite reposted
The Secure Soapbox
@SecureSoapbox
Tbh ever since the performance update Burp has just been winning on all fronts
-
Burp Suite
@Burp_Suite
-
Burp Suite
@Burp_Suite
Check out what's new in the 2024.10 version of Burp Suite Professional! 🤩
-
Burp Suite
@Burp_Suite
-
Burp Suite
@Burp_Suite
🛠️ Big shoutout to Barak Tawily for their brilliant BApp extension, Autorize!
Simplify your hunt for authorization vulnerabilities by automating the process of testing requests with different privilege levels. Install Autorize on the BApp Store today! 👇
portswigger.net/bappstore/f9bbac8c4acf4aefa4d7dc92a991af2f -
Burp Suite
@Burp_Suite
Editable issue severity ratings in Burp Suite Enterprise Edition!
From your scan results page, you can now amend the severity ratings for individual issues, and mark issues as accepted risks.
Watch the video tutorial to find out how:This media couldn't be displayed. See it on the original post. -
Burp Suite reposted
James Kettle
@albinowax
We’re finally live! You can now watch “Listen to the whispers: web timing attacks that actually work” on YouTube: youtube.com/watch?v=zOPjz-sPyQM
-
Burp Suite
@Burp_Suite
We've streamlined setting up scans in Burp Suite Pro. Check it out!
-
Burp Suite
@Burp_Suite
-
Burp Suite
@Burp_Suite
🛠️ Huge shoutout to Oussama Zgheb for their incredible BApp extension, JSON Web Tokens!
Quickly and efficiently assess the security of JSON Web Tokens in web applications by installing this BApp 👇
portswigger.net/bappstore/f923cbf91698420890354c1d8958fee6 -
Burp Suite
@Burp_Suite
Did you know you can now upload SOAP API definition files directly to Burp Suite Professional? 🧼 #soap #burpsuitetoptip
-
Burp Suite
@Burp_Suite
-
Burp Suite
@Burp_Suite
🎉 ICYMI: Editable issue severity is live!
You can now edit issue severity ratings in Burp Suite Enterprise Edition.
Read on to find out more 👇Post not available here, view on X
Burp Suite
@Burp_Suite
✅ Mark issues as accepted risks - efficiently manage vulnerabilities that don’t require action or are mitigated by other measures.
Burp Suite
@Burp_Suite
These features are just the beginning. Take greater control of your security posture with Burp Suite Enterprise Edition - read the blog to find out more👇
portswigger.net/blog/take-control-of-your-security-postur… -
Burp Suite reposted
Gareth Heyes \u2028
@garethheyes
Exploit XSS in hidden inputs with no user-interaction, using this amazing new auto-executing vector from @kinugawamasato! We've added this powerful trick to our XSS cheat sheet linked below👇
-
Burp Suite
@Burp_Suite
Splunk 🤝 Burp Suite Enterprise Edition.
Splunk now integrates with Burp Suite Enterprise Edition:
👁️ Real-Time Control and Visibility
🏃 Streamlined Workflow for Faster Incident Response
🖇️ Efficient Collaboration Across Teams
Instructions here 👉 portswigger.net/burp/documentation/enterprise/user-guide/… -
Burp Suite reposted
James Kettle
@albinowax
Ever wanted to fuzz a WebSocket? We've just updated WebSocket Turbo Intruder with some new features. If you've used Turbo Intruder already, it should feel familiar :)
-
Burp Suite
@Burp_Suite
🚀 Montoya API improvements 🚀
We’ve added new utility methods for JSON parsing. It’s now easier than ever to handle JSON data within your extensions or within Bambdas.This media couldn't be displayed. See it on the original post. -
Burp Suite
@Burp_Suite
Whether you're new to fuzzing or looking to refine your techniques, this exclusive Discord event will equip you with practical tips and tricks to make Shazzer an essential tool in your workflow. 👇
PortSwigger
@PortSwigger
Take your fuzzing skills to the next level with Shazzer!
On Nov 7 at 4pm GMT (12pm EDT), @garethheyes will dive deep into its unique fuzz types, exploring when and why to use each one for optimal results.
Register for this exclusive Discord event 👇 discord.com/events/1159124119074381945/1300810918418186290 -
Burp Suite
@Burp_Suite
👀 Coming soon... #sneakpeek
-
Burp Suite
@Burp_Suite
Take control of your security priorities! In Burp Suite Enterprise Edition you can now:
⚡ Edit issue severity ratings to fit your context.
📝 Add notes to track decisions.
✅ Mark issues as accepted risks .
Learn more in our blog 👇
portswigger.net/blog/take-control-of-your-security-postur… -
Burp Suite reposted
Gareth Heyes \u2028
@garethheyes
Want to discover advanced XSS vectors like this? I'll be presenting "Digging for XSS Gold: Unearthing Browser Quirks with Shazzer" live online at 16:00 UTC November 7th
portswigger.net/research/talks -
Burp Suite
@Burp_Suite
Test your Match and Replace rules against requests or responses in Burp Suite Professional.
This media couldn't be displayed. See it on the original post. -
Burp Suite reposted
payloadartist
@payloadartist
🛠🔥 Gotta love the new UI for @Burp_Suite match and replace.
+ It gets a dedicated tab under the Proxy section
+ A request testing simulator to test out the rule in real time
#bugbounty #bugbountytips #cybersecurity -
Burp Suite
@Burp_Suite
Two out of three PortSwigger Research presentations from DEF CON are now available to watch on demand! 👇
PortSwigger
@PortSwigger
Watch research presentations on demand 🧵👇
PortSwigger recently presented three ground-breaking releases at Black Hat USA and DEF CON, uncovering a range of new techniques that could be used to exploit applications - and now two of these talks are available publicly! -
Burp Suite
@Burp_Suite
Coming soon to Burp Suite Enterprise Edition... 🤫 #sneakpeekthursday
-
Burp Suite reposted
Brumens
@Brumens2
Finally, been using extensions for this forever, nice! 🙂
-
Burp Suite reposted
Lucien
@Wlayzz
Awesome, I will not loose my tab in repeater again 🤩
-
Burp Suite
@Burp_Suite
Enhance your reports by manually recording issues in Burp 💪 #burpsuite #toptiptuesday
-
Burp Suite reposted
PortSwigger Research
@PortSwiggerRes
Master crafting attacks using the URL Validation Bypass Cheat Sheet with our new deep-dive video by @d4d89704243, just published to YouTube: www.youtube.com/watch?v=3VJKmARDzJ4
-
Burp Suite reposted
R3DD
@R3DD404
I'm already loving the UI
-
Burp Suite
@Burp_Suite
Thanks to @0xTib3rius for this awesome round up of Burp's latest features! 🔥
Ready to check out what's new? Update to the latest version of Burp Suite Professional.👇
portswigger.net/burp/releases/professional-community-2024…
Burp Suite
@Burp_Suite
-
Burp Suite
@Burp_Suite
New launcher, who dis?
🤫 #sneakpeekthursday -
Burp Suite
@Burp_Suite
Enabling auto-update is the best way to get the latest and greatest features in Burp Suite Pro!
portswigger.net/burp/releases -
Burp Suite reposted
Tib3rius
@0xTib3rius
New Video: You Should Know About These New Burp Features!
youtu.be/55kcyOHw5VQ -
Burp Suite reposted
Web Security Academy
@WebSecAcademy
The solution is now available for the Bypassing Access Controls lab 👉 portswigger.net/web-security/logic-flaws/examples/lab-log…
Read more about how to use email addressing parsing discrepancies to bypass access controls in @garethheyes Splitting the Email Atom white paper 👇
portswigger.net/research/splitting-the-email-atom -
Burp Suite
@Burp_Suite
Improve performance by updating to the latest version of Burp Suite Professional:
portswigger.net/burp/releases
#burpsuiteThis media couldn't be displayed. See it on the original post. -
Burp Suite
@Burp_Suite
🧵 It’s been great to hear the impact that Burp’s recent performance upgrades have had on your testing, ranging from accelerating your workflow and increasing testing efficiency, to saving you both time and money.
Below are some of our favorite examples…
#burpsuiteperformancePost not available here, view on X
Burp Suite
@Burp_Suite
Helping you save money 💰
Burp Suite
@Burp_Suite
Want to access these new performance upgrades? ⚡
Update to the latest version of Burp Suite to experience the full benefit of these time saving, memory efficient updates 👇
portswigger.net/burp/releases?ps_source=twitter&ps_medium…
#burpsuiteperformance -
Burp Suite
@Burp_Suite
Have you tried the new and improved Intruder? 😎 #burpsuite #toptiptuesday
-
Burp Suite
@Burp_Suite
🤫 #sneakpeekthursday #burpsuite
-
Burp Suite
@Burp_Suite
Performance so fast you don't have time for a tea #burpsuiteperformance
-
Burp Suite
@Burp_Suite
Have you checked out the new performance upgrades in Burp? 🚀 #burpsuiteperformance
-
Burp Suite
@Burp_Suite
Caught up with PortSwigger’s research releases from Black Hat USA yet? 🧵
Web security threats are constantly evolving, meaning it's crucial to stay up-to-date with the latest techniques.
Don't miss out on these newest findings from the legendary @PortSwiggerRes team…Post not available here, view on X
Burp Suite
@Burp_Suite
☠️ Uncover novel methods for web cache exploitation in Gotta Cache ‘em All. @tincho_508 shares how discrepancies in URL parsing can be leveraged to poison caches and deceive web applications, revealing vulnerabilities in popular CDNs.
portswigger.net/research/gotta-cache-em-all?ps_source=twi…
Burp Suite
@Burp_Suite
Have you tried any of these new techniques out for yourself in Burp Suite?
Let us know by tweeting us at @burp_suite and sharing your experience! 🚀 -
Burp Suite
@Burp_Suite
SOAP API scanning coming very soon to Burp Suite Professional #sneakpeekthursday
-
Burp Suite
@Burp_Suite
We asked AppSec pros about their biggest API security challenges. Here’s what we found:
👁️ Lack of visibility over API attack surfaces
📈 Struggles with automating/scaling API testing
🚫 Tool limitations holding them back
Discover more 👉 portswigger.net/blog/api-security-the-6-biggest-challenge… -
Burp Suite
@Burp_Suite
Did you know you can reduce the size of your project file in Burp Suite by saving a copy? 🔥 #burpsuiteperformance
-
Burp Suite
@Burp_Suite
Have you caught up with Burp Suite's latest performance upgrades yet? ⚡
Burp's performance has been enhanced across several key areas, reducing processing times, minimizing memory usage, and ensuring a smoother experience when you use Burp.
#burpsuiteperformance
Burp Suite
@Burp_Suite
Watch our Burp Suite Performance Discord event recording to find out how these new upgrades will supercharge your testing. 👇
www.youtube.com/watch?v=UmsXJkVyGfU
Burp Suite
@Burp_Suite
Ready to unlock these new performance upgrades? 🚀
These time saving, memory efficient updates have been rolled out over the last few releases of Burp Suite.
Get the full benefit of all upgrades and update to the latest version 👇
portswigger.net/burp/releases/professional-community-2024… -
Burp Suite reposted
₦฿₭ - Paw / Pwn / Purr
@nbk_2000
I appreciate getting ~2.5GB of memory back with the latest update, thanks 👍
The UI/UX improvements are very much appreciated too 😉 -
Burp Suite reposted
MOPAM
@m0pam
Keep the performance upgrades coming, they're LIT 🔥
-
Burp Suite
@Burp_Suite
Your experience with Burp Suite is now faster and smoother due to the new performance upgrades that have slashed memory usage in Intruder! 😎
#burpsuiteperformance -
Burp Suite reposted
James Kettle
@albinowax
Now I've got the hang of it, @Burp_Suite's Organizer is super useful for research. My workflow is:
- Work in repeater, using notes but making no attempt to label/group tabs
- If I see anything interesting, ctl+o to send to Organizer
- If I realize something was notable retrospectively, go back through repeater tab history and send to organizer
Then, by sorting by time & applying filters, Organizer gives me a clean chronological view of progress and I still get to have hundreds of messy repeater tabs -
Burp Suite
@Burp_Suite
Save time by forwarding all requests and responses at once in our new Proxy Intercept!
-
Burp Suite
@Burp_Suite
Introducing Burp Suite's latest performance upgrades ⚡
We've listened to your feedback and made our core tools faster, more efficient, and use less memory.
Here's a glimpse of what's new. 🧵👇 #burpsuiteperformancePost not available here, view on X
Burp Suite
@Burp_Suite
New & improved Proxy Intercept View 🌟
Control intercepted requests more easily with options for viewing, forwarding, and managing requests and responses in bulk - elevate your workflow efficiency!
Burp Suite
@Burp_Suite
Ready to unlock the full potential of Burp Suite? 💪
Upgrade to the latest version of Burp 👇
portswigger.net/burp/releases?ps_source=twitter&ps_medium…
Read more on our latest upgrades and how they'll supercharge your workflow by reading the full blog post 👇
portswigger.net/blog/introducing-burp-suites-game-changin… -
Burp Suite
@Burp_Suite
-
Burp Suite
@Burp_Suite
Did you know... you can now view multiple requests in the Proxy Intercept table! #toptiptuesday
-
Burp Suite reposted
Clint Gibler
@clintgibler
🗒️ URL validation bypass cheat sheet
Payloads for bypassing URL validation.
Useful for attacks like SSRF, CORS misconfigurations, and open redirects.
By @Portswigger #bugbountytips
portswigger.net/web-security/ssrf/url-validation-bypass-c… -
Burp Suite
@Burp_Suite
Introducing the new URL validation bypass cheat sheet 🔥
Join us on the PortSwigger Discord at 11am EST (4pm BST) on Sept 12 as Zakhar Fedotkin @d4d89704243 dives into the research behind this new tool, and how to use it to its fullest potential!
👉 discord.gg/portswigger?event=1281561111111663687 -
Burp Suite
@Burp_Suite
👀 Coming soon to Proxy Match and Replace #sneakpeekthursday
-
Burp Suite
@Burp_Suite
Today is the day - join us over Zoom at 11am EST (4pm BST) for this brand new API scanning webinar to discover how to scale your organization's API scanning!
Register for free here 👇
PortSwigger
@PortSwigger
On Wed Sept 4, our API team will be walking you through how to use Burp Suite Enterprise Edition to...
🔎 Find more API vulnerabilities in less time
📈 Scale your API scanning with easier, purpose-built functionality
Register here: portswigger.zoom.us/webinar/register/WN_hrc9qjI-T6ioGe4Y-… -
Burp Suite
@Burp_Suite
Today is the day...
Our Ask Me Anything event with the Chief Swig and PortSwigger founder, Dafydd Stuttard, is happening over on the PortSwigger Discord at 11am EST (4pm BST)!
Make sure to tune in and submit any questions.👇
PortSwigger
@PortSwigger
Meet the Chief Swig and PortSwigger founder, @dafyddstuttard 🔥
Tomorrow at 11am EST (4pm BST) on the PortSwigger Discord, Burp Suite creator Dafydd Stuttard will be hosting an exclusive Ask Me Anything event!
Join the event here 👉 discord.gg/portswigger?event=1273987342398656524 -
Burp Suite reposted
🇷🇴 cristi
@CristiVlad25
The Burp Suite Deep Dive course is now fully uploaded and completely free on YouTube.
Monetization is turned off so you should have an ad-free experience.
Feel free to spread the word.
#pentesting #appsec #cybersecurity #bugbounty #infosec
www.youtube.com/playlist?list=PLonlF40eS6nzPfbOv5NHv5SpUO… -
Burp Suite
@Burp_Suite
Have you seen the enhanced API scanning features we’ve added to Burp Suite?
You can now:
🧪 Test for vulnerabilities without having to host definition files.
🔧 Test a wider range of API endpoints.
Read the blog to find out how: portswigger.net/blog/unlock-enhanced-api-scanning-with-bu… -
Burp Suite
@Burp_Suite
The first rule of API scanning is... 🤫 #sneakpeekthursday #apiscanning
-
Burp Suite
@Burp_Suite
This exclusive sharing of @tincho_508 's Gotta Cache 'em All is happening over on the PortSwigger Discord today! 😎
Don't miss out, join the official PortSwigger Discord here: discord.com/invite/portswigger
PortSwigger
@PortSwigger
There will be another exclusive event on the PortSwigger Discord tomorrow at 11am EST (4pm BST) as @tincho_508 shares Gotta Cache 'em All, which premiered at Black Hat USA earlier in August! 🤩
Definitely don't miss out on this one: discord.gg/portswigger?event=1273989737660682321 -
Burp Suite
@Burp_Suite
In Burp Suite Enterprise, you can now configure endpoints after uploading an API definition file!
-
Burp Suite
@Burp_Suite
Did you know? Burp Scanner will automatically detect and report OpenAPI definitions 🕵️
-
Burp Suite
@Burp_Suite
Join our webinar on Sep 4th @ 11am EST (4pm GMT) and discover how to level up your API scanning with Burp Suite Enterprise Edition. You’ll learn how to:
🔎 Find API vulnerabilities faster.
📈 Scale your API scanning.
Sign up now: portswigger.zoom.us/webinar/register/WN_hrc9qjI-T6ioGe4Y-… -
Burp Suite reposted
PortSwigger
@PortSwigger
Final day to enter! Don't miss out on the chance of winning these exclusive PortSwigger Discord prizes. ⏳
Burp Suite
@Burp_Suite
📣 Win a range of exclusive Burp Suite prizes 📣
All you need to do is join the official PortSwigger Discord, and we’ll select 5 random winners from all members that post in the next 7 days. Entry closes Wed 20 Aug.
Join the Discord here: discord.com/invite/portswigger -
Burp Suite
@Burp_Suite
Coming very soon... 🤫 #sneakpeek
-
Burp Suite reposted
PortSwigger
@PortSwigger
Only one more day to enter our Discord competition and win some awesome Burp Suite prizes, including t-shirts, challenge coins, Burp Cert exam tokens, and more... 👀
Join the official PortSwigger Discord below. 👇
Burp Suite
@Burp_Suite
📣 Win a range of exclusive Burp Suite prizes 📣
All you need to do is join the official PortSwigger Discord, and we’ll select 5 random winners from all members that post in the next 7 days. Entry closes Wed 20 Aug.
Join the Discord here: discord.com/invite/portswigger -
Burp Suite
@Burp_Suite
Entry closes this Wednesday - don't forget to join the official PortSwigger Discord for the chance to get your hands on some exclusive Burp Suite swag! 😎
Burp Suite
@Burp_Suite
📣 Win a range of exclusive Burp Suite prizes 📣
All you need to do is join the official PortSwigger Discord, and we’ll select 5 random winners from all members that post in the next 7 days. Entry closes Wed 20 Aug.
Join the Discord here: discord.com/invite/portswigger -
Burp Suite
@Burp_Suite
Don’t miss these awesome events happening over on the PortSwigger Discord over the next few weeks! 🤯
PortSwigger
@PortSwigger
👾 Exclusive PortSwigger Discord events 👾
To celebrate the official PortSwigger Discord launch, we’re delighted to announce some extra special events coming to the Discord over the next few weeks!
Join the Discord here: discord.com/invite/portswigger -
Burp Suite reposted
PortSwigger
@PortSwigger
Wondering what our community think about the official PortSwigger Discord? 🤔
Join here: discord.com/invite/portswigger -
Burp Suite reposted
YesWeHack ⠵
@yeswehack
Web security research pioneer @albinowax has broken new ground again with his latest Black Hat USA presentation 👇
The @PortSwigger director of research begins his writeup for ‘Listen to the whispers: web timing attacks that actually work’ by urging his peers to start listening to the “timing oracles” pervading websites since they are “eager to divulge their innermost secrets” 😮
His latest tour de force promises to “unleash novel attack concepts to coax out server secrets including masked misconfigurations, blind data-structure injection, hidden routes to forbidden areas, and a vast expanse of invisible attack-surface”
With these techniques all too often failing in real-world scenarios, he also provides “real-world case studies on diverse targets” and “battle-tested open-source tools” 👉
portswigger.net/research/listen-to-the-whispers-web-timin… -
Burp Suite reposted
Daniel Oakley
@DeeOakster
@PortSwigger I just renewed my annual subscription. BurpSuite is one of the best and affordable cybersecurity products! My thanks go out to the team for providing such an indispensable tool. AppSec would be lost without you.
-
Burp Suite
@Burp_Suite
📣 Win a range of exclusive Burp Suite prizes 📣
All you need to do is join the official PortSwigger Discord, and we’ll select 5 random winners from all members that post in the next 7 days. Entry closes Wed 20 Aug.
Join the Discord here: discord.com/invite/portswigger -
Burp Suite
@Burp_Suite
Huge news - the official PortSwigger Discord community is now open to all. Join today using the link below! 👇👾
PortSwigger
@PortSwigger
The official PortSwigger Discord is now open! 🎉👾
Join for access to exclusive events, feature previews, research releases, and to hang out with Burp Suite developers.
Join for free here: discord.com/invite/portswigger -
Burp Suite
@Burp_Suite
Tom Stacey
@t0xodile
Some really crazy looking payloads in @tincho_508's Blackhat paper! Cannot wait to apply these! Awesome stuff!
portswigger.net/research/gotta-cache-em-all -
Burp Suite
@Burp_Suite
Eldar
@PikuHaku
Portswigger came out with some insane research today. I haven't even managed to process James Kettle's paper yet and this banger comes out. Crazy stuff.
Gareth Heyes \u2028
@garethheyes
Everyone knows that the RFCs for email addresses are crazy. This post will show without doubt that you should not be following the RFC.
portswigger.net/research/splitting-the-email-atom -
Burp Suite reposted
PortSwigger
@PortSwigger
What a week it’s been for @PortSwiggerRes at Black Hat USA!
Three major releases debuted at the conference, containing a range of new techniques that attackers are using to exploit applications.
Take a look at all three white papers below 👇 -
Burp Suite reposted
PortSwigger
@PortSwigger
Uncover the secrets of bypassing email security in Splitting the Email Atom. @garethheyes reveals how email parsers can be exploited to circumvent access controls, presenting new strategies for penetrating seemingly secure email systems. 👇
x.com/garethheyes/status/1821442072911450249
Gareth Heyes \u2028
@garethheyes
Everyone knows that the RFCs for email addresses are crazy. This post will show without doubt that you should not be following the RFC.
portswigger.net/research/splitting-the-email-atom -
Burp Suite reposted
PortSwigger
@PortSwigger
Dive into Listen to the Whispers, where @albinowax shares real-world applications of web timing attacks.
This research showcases how to detect sub-millisecond differentials, exposing hidden server secrets and vulnerabilities using only timing. 👇
x.com/albinowax/status/1821249849884598305
James Kettle
@albinowax
The whitepaper is live! Listen to the whispers: web timing attacks that actually work. Read it here ->
portswigger.net/research/listen-to-the-whispers-web-timin… -
Burp Suite
@Burp_Suite
Have you checked out the new Proxy intercept view? 🚀
This media couldn't be displayed. See it on the original post. -
Burp Suite
@Burp_Suite
This week we announced Burp's enhanced API scanning features, and it got us thinking...
What are the biggest challenges you face with securing your APIs? 🤔 -
Burp Suite
@Burp_Suite
Did you see Burp Suite's API scanning announcement yesterday? 👀
Burp Suite
@Burp_Suite
🔐 Unlock enhanced API scanning with Burp Suite! Upload definition files and scan your APIs alongside web apps, or in a standalone scan.
Available in Burp Suite Enterprise Edition and Burp Suite Professional.
Find out more: portswigger.net/blog/unlock-enhanced-api-scanning-with-bu…
#apisecurity #burpsuite -
Burp Suite
@Burp_Suite
🔐 Unlock enhanced API scanning with Burp Suite! Upload definition files and scan your APIs alongside web apps, or in a standalone scan.
Available in Burp Suite Enterprise Edition and Burp Suite Professional.
Find out more: portswigger.net/blog/unlock-enhanced-api-scanning-with-bu…
#apisecurity #burpsuite -
Burp Suite
@Burp_Suite
Did you know ... you can now scan APIs by uploading a definition in Burp Suite Enterprise!
#burpsuiteshorts -
Burp Suite
@Burp_Suite
Want to quickly swap request methods in Burp Suite Pro? Here’s how! #burpsuiteshorts
-
Burp Suite reposted
🆔*ArkhAngelLifeJiggy*🌏🪽 👨🏼💻🪽
@ArkhLifeJiggy
@PortSwigger @Burp_Suite
Manual Scope ✌️
💫💯🧠👑 -
Burp Suite reposted
Trail of Bits
@trailofbits
Want to master @Burp_Suite like a pro? Join @trailofbits and James Kettle from @PortSwigger for a webinar on July 31st @ 12 pm EST! Learn techniques, optimize your setup, and understand the lesser-known features of Burp. Register here 👇
trailofbits.registration.goldcast.io/events/5cfde272-7934… -
Burp Suite
@Burp_Suite
🤫 #sneakpeekthursdays #projectswitching
-
Burp Suite
@Burp_Suite
Did you know you can configure Collaborator to serve custom DNS records? You can have a single CNAME record or any number of TXT records. You can use this to verify ownership of the domain for TLS certificate issuance amongst lots of other things
-
Burp Suite reposted
James Kettle
@albinowax
The single-packet attack strikes again! Awesome finding from @_0x999 - check his reply for details and a near-identical @WebSecAcademy lab!
publiclyDisclosed
@disclosedh1
Mars disclosed a bug submitted by @_0x999: hackerone.com/reports/2142109 #hackerone #bugbounty
-
Burp Suite
@Burp_Suite
Can’t find a particular Repeater tab? Now when you use Burp Search you can view the Repeater tab name in the results and even go to straight to the tab #burpsuiteshorts
-
Burp Suite
@Burp_Suite
New Burp Suite Professional Testing Handbook from @trailofbits 📚
Check out this step-by-step guide, created by Trail of Bits, to rapidly master Burp and optimize the testing of your app!
Testing Handbook: appsec.guide/docs/web/burp/
Clint Gibler
@clintgibler
📚 New chapter in @trailofbits' Testing Guide: Burp Suite
Step-by-step guide to rapidly master @portswigger's Burp Suite
➡️ Using Burp Repeater, Intruder, and Collaborator,
➡️ Useful plugins
➡️ Best practices
➡️ Burp features to find specific vulns
blog.trailofbits.com/2024/06/14/announcing-the-burp-suite… -
Burp Suite
@Burp_Suite
With the Cloud-hosted Burp Suite Enterprise Edition, you can scale your testing with automated scheduled DAST scanning without the need to host and maintain your own infrastructure. ☁️
Read more here: portswigger.net/blog/introducing-dast-scanning-in-the-clo…
ed
@sprocket_ed
Had a pretty good experience with Enterprise when we used it. I would recommend going with the PortSwigger hosted version, however. Self hosting is a pain and costs lots of $$$. Feel free to DM me your specific use case I may be able to help out more.
-
Burp Suite
@Burp_Suite
Shout out to KnugiHK for their recent BCheck submission for detecting malicious polyfill usage! 👏
github.com/PortSwigger/BChecks/blob/main/other/Javascript…
To get scanning with this BCheck, simply import this BCheck into "Extensions > Bchecks” -
Burp Suite
@Burp_Suite
-
Burp Suite reposted
Gareth Heyes \u2028
@garethheyes
You can use baseURI to conceal XSS payloads! Every HTML tag has the baseURI property. Base allows you to change the baseURI.
-
Burp Suite
@Burp_Suite
Show and hide your table columns in the table menu across major tools in Burp Suite Pro! And yes, this is persisted across your project file 🙌
-
Burp Suite
@Burp_Suite
Huge news at PortSwigger 🔥
PortSwigger
@PortSwigger
🚀 1/5 Big news! We've partnered with Brighton Park Capital to accelerate our mission of securing the web. This investment will help us accelerate our product development.
What will this mean for pentesters? Read on👇 -
Burp Suite
@Burp_Suite
-
Burp Suite
@Burp_Suite
Enjoying our new 'Hide uninteresting headers' feature? You can now configure whether to hide them by default.
#burpsuiteshorts -
Burp Suite
@Burp_Suite
-
Burp Suite
@Burp_Suite
Did you know ... you can now configure authentication when running API scans in Burp Suite Pro!
#burpsuiteshorts -
Burp Suite
@Burp_Suite
... what would it taste like?
ali
@endingwithali
. @Burp_Suite should do a limited run soda called burp sweet
-
Burp Suite
@Burp_Suite
🔍 Burp Search just leveled up!
Now easily spot which Repeater tab holds your result and jump straight there from the context menu. Navigate with precision! -
Burp Suite
@Burp_Suite
-
Burp Suite
@Burp_Suite
We forgot to prep any content for this week's post ...
PortSwigger
@PortSwigger
Kiss, marry, kill ...
Proxy, Intruder, Repeater? -
Burp Suite reposted
Tib3rius
@0xTib3rius
The best @Burp_Suite Bambda.
Available here: github.com/Tib3rius/Tibs-TUBs/blob/main/Custom Column TUB…This media couldn't be displayed. See it on the original post. -
Burp Suite
@Burp_Suite
Are you running multiple Intruder attacks in Burp Suite? Try this out next time ... #burpsuiteshorts
-
Burp Suite
@Burp_Suite
🌐 Sitemap reorganized!
Now sorted by second-level domain then top-level domain, making it easier to assess a domain's attack surface. -
Burp Suite reposted
James Kettle
@albinowax
After discovering that custom columns are a lot more fun than they sound, the @PortSwiggerRes team has published some of our favourites in "Refining your HTTP perspective, with bambdas"
portswigger.net/research/adjusting-your-http-perspective-… -
Burp Suite
@Burp_Suite
Want to use millions of payloads in Intruder without impacting performance? Here's how! #burpsuiteshorts
-
Burp Suite
@Burp_Suite
Streamline your requests in Burp Suite Professional by hiding uninteresting headers with the editor. 🤩
-
Burp Suite reposted
James Kettle
@albinowax
I'm thrilled to announce "Listen to the whispers: web timing attacks that actually work" will premiere at Black Hat USA!
After nine months of running bulk timing attacks on thousands of live sites, I've got a lot to share :D #bhusa @BlackHatEvents
www.blackhat.com/us-24/briefings/schedule/index.html -
Burp Suite reposted
Martin Doyhenard
@tincho_508
I'm thrilled to announce that my talk "Gotta Cache Em All: Bending the Rules of Web Cache Exploitation" was accepted at Black Hat USA 2024!
I'll be showing how to abuse web cache parsers to completely compromise thousands of sites!
#bhusa @BlackHatEvents www.blackhat.com/us-24/briefings/schedule/index.html -
Burp Suite
@Burp_Suite
-
Burp Suite
@Burp_Suite
Filter your tables using Bambdas in Burp Suite! #burpsuiteshorts
-
Burp Suite
@Burp_Suite
We’re committed to not only improving the automated testing capabilities of Burp Suite Enterprise Edition, but also to simplifying and enhancing workflows for you and your team.
🌸 Read the spring 2024 update to find out more: portswigger.net/blog/burp-suite-enterprise-edition-spring… -
Burp Suite
@Burp_Suite
-
Burp Suite
@Burp_Suite
Want to know how much extensions are impacting Burp's performance? Here's how! #burpsuiteshorts
-
Burp Suite
@Burp_Suite
AppSec teams have told us that, since implementing Burp Suite Enterprise Edition in the Cloud, they have been able to:
⏱️ Start scanning in minutes.
💪 Scale up testing for multiple applications.
🎯 Optimize the efficiency of their testing.
Read more: portswigger.net/blog/one-month-of-burp-suite-in-the-cloud… -
Burp Suite
@Burp_Suite
-
Burp Suite
@Burp_Suite
Customize your tables using Bambdas in Burp Suite! #burpsuiteshorts
-
Burp Suite
@Burp_Suite
-
Burp Suite
@Burp_Suite
Tired of exporting your data from Burp Suite and writing scripts to analyze it?
With Bambda-powered custom columns, now available in Burp Suite Professional, you can perform that analysis in Burp in real time. It’s as good as it sounds 🥳.
portswigger.net/burp/releases/professional-community-2024… -
Burp Suite
@Burp_Suite
Access previously hidden data with Bambda-powered custom table columns. Now available in Burp Suite Professionals latest version.
Read the release notes to learn more: portswigger.net/burp/releases/professional-community-2024… -
Burp Suite
@Burp_Suite
Did you know ... you can improve the performance of Burp Proxy by enabling TLS passthrough! #burpsuiteshorts
-
Burp Suite
@Burp_Suite
In this video, our Enterprise Experts provide an overview of the different scanning options across agents based in PortSwigger’s secure Cloud, self-hosted environments and CI platforms. ☁️
Join our webinar on Wed May 1 at 11.30am EST to find out more: portswigger.zoom.us/webinar/register/4517143838132/WN_257… -
Burp Suite
@Burp_Suite
Do you use Burp Suite Professional?
We’re eager to hear your thoughts on the Burp scanner. Share your feedback through our quick survey and help us enhance your experience!
👉 usabi.li/do/205f5f307228/2e51
Thanks for your valuable insights! -
Burp Suite
@Burp_Suite
Join our webinar at 11.30am EST on Wednesday May 1 to find out how the new Cloud-based Burp Suite Enterprise Edition can help your organization scale their scanning.
Register for your free place 👉 portswigger.zoom.us/webinar/register/6317135337602/WN_257… -
Burp Suite
@Burp_Suite
Can you spot what's changed? 🤫 #sneakpeekthursdays
-
Burp Suite
@Burp_Suite
Did you know ... you can now scan APIs by uploading a definition in Burp Suite Pro! #burpsuiteshorts
-
Burp Suite
@Burp_Suite
📣 Burp Suite in the Cloud event 📣
Join us on May 1 at 11.30am EST as our team of Enterprise Experts explore how to scale up scanning with Burp Suite Enterprise Edition, without the burden of maintaining infrastructure.
Register for your free place: portswigger.zoom.us/webinar/register/4517134332574/WN_257… -
Burp Suite
@Burp_Suite
Want to know more about how the new Cloud-based Burp Suite Enterprise Edition can help automate security testing for your organization?
Request a demo with one of our Enterprise Experts 👉 meetings.hubspot.com/jamie-mackay/cloudtwitter?uuid=8ff1e…
Burp Suite
@Burp_Suite
Burp Suite Enterprise Edition is now available in PortSwigger’s secure cloud! ☁️
Free up testing time with automated, scheduled DAST scanning, without the hassle of maintaining your own infrastructure.
Learn more here 👇 portswigger.net/blog/introducing-dast-scanning-in-the-clo… -
Burp Suite
@Burp_Suite
Burp Suite Enterprise Edition is now available in PortSwigger’s secure cloud! ☁️
Free up testing time with automated, scheduled DAST scanning, without the hassle of maintaining your own infrastructure.
Learn more here 👇 portswigger.net/blog/introducing-dast-scanning-in-the-clo… -
Burp Suite
@Burp_Suite
-
Burp Suite
@Burp_Suite
Did you know ... you can now set a maximum memory allowance for Burp's Java Virtual Machine! #burpsuiteshorts
youtu.be/_49a7pTsUak -
Burp Suite
@Burp_Suite
🌟 Calling all Burp Suite Pro users 🌟
We’re eager to hear your thoughts on the Burp scanner. Share your feedback through our quick survey and help us enhance your experience!
👉 usabi.li/do/205f5f307228/2e51 -
Burp Suite
@Burp_Suite
-
Burp Suite reposted
Gareth Heyes \u2028
@garethheyes
I've built a brand new version of my fuzzing tool Shazzer🚀
shazzer.co.uk
- Easy fuzz browser behaviour
- Find bugs
- Share the results with the world -
Burp Suite reposted
PortSwigger
@PortSwigger
Scanning from an API definition is now possible in Burp Suite Pro. Thanks for having a little patience 😉
youtu.be/0v5BhW3DAPo -
Burp Suite
@Burp_Suite
Watch our latest YouTube short on how to reduce your memory usage with Burp Suite Professional Edition 🤔
youtube.com/shorts/oCIYGIviRRo
#burpsuiteshorts -
Burp Suite reposted
celesian
@c3l3si4n
thank you @PortSwigger
-
Burp Suite
@Burp_Suite
Improving the performance of Burp Suite is one of our top priorities. Here are some of the recent updates we have released:
- TLS passthrough
- Configurable memory limits
- Native ARM versions
We are just getting started. Help us pick what to do next at support@portswigger.net -
Burp Suite
@Burp_Suite
In this video, Scanner Dave and Tom will show how not to make a Burp Suite Short.
youtu.be/xZuCrSMPvZ8 -
Burp Suite reposted
PortSwigger Research
@PortSwiggerRes
We've just published "Making desync attacks easy with TRACE" by new PortSwigger Research member @tincho_508!
portswigger.net/research/trace-desync-attack -
Burp Suite
@Burp_Suite
Sent an item to be audited but unsure of where Burp Scanner will place payloads during the scan?
Dave from the Scanner team demonstrates the solution to this problem in the latest Burp Suite Short.
youtu.be/_UpVqEmIPiY -
Burp Suite
@Burp_Suite
Come and have a look at the latest Burp Suite Short 👀
Josh takes us through the new features added to the v2-beta language set for BChecks.
youtu.be/lR04_eN4Uuo -
Burp Suite
@Burp_Suite
Do you like the ability to toggle columns, change the column order, and persist your table setup across work sessions?
So do we! Therefore, we decided to add them to Burp Suite in the 2024.1.1.4 release.
More table improvements coming soon... 🤫
portswigger.net/burp/releases/professional-community-2024… -
Burp Suite
@Burp_Suite
Our top story tonight! 🐟 📺
With the latest version on the stable channel, you can now view the insertion points that Burp Scanner identified for a particular request during a scan.
This gives you previously hidden insight into Burp Scanner 👀
#dast
portswigger.net/burp/releases/professional-community-2024… -
Burp Suite
@Burp_Suite
🎉 BChecks competition results 🎉
Thank you to everyone that entered - we are delighted to announce that the winner is @j3ssie with their time-saving BCheck below!
Please email us at support@portswigger.net to claim your prize 🏆
Little Acorn
@Coena327648
RT @j3ssie: I recently began experimenting with #bcheck from @PortSwigger, and I found it to be a time saver. I discovered that you can…
-
Burp Suite reposted
PortSwigger Research
@PortSwiggerRes
The results are in! We're proud to announce the Top 10 Web Hacking Techniques of 2023! portswigger.net/research/top-10-web-hacking-techniques-of…
-
Burp Suite
@Burp_Suite
BChecks Tips & Tricks 🔥
Did you know you can make use of Collaborator within BChecks?
- The example below from our GitHub uses the generate_collaborator_address() function and checks for HTTP interactions.
- Enables you to customize your OAST workflow quickly and easily. -
Burp Suite
@Burp_Suite
BChecks Tips & Tricks 🔥
Did you know you can run different variations of your BCheck using the ‘run for each’ statement?
- The example below from GitHub uses file extensions to find Cache Deception vulnerabilities.
- Increases testing scope.
- Improves extensibility.
#bchecks -
Burp Suite
@Burp_Suite
BChecks Tips & Tricks 🔥
Did you know the BCheck editor (BS Code) has a format feature?
- Located in the right-click menu.
- Available to define as a custom hotkey.
- Keeps BChecks easy to read and standardized with minimal effort required.
“Wax on, Wax off.” 🧽
#bchecks -
Burp Suite
@Burp_Suite
Have you tried BChecks yet?
If not, why not? 🤔
#bchecks -
Burp Suite
@Burp_Suite
Looking good 😎
There's been some great uses of BChecks being sent to us this week. Keep the entries to the #bchecks competition coming...
x.com/fonderelite/status/1755341516627681787 -
Burp Suite
@Burp_Suite
Another great example of a BCheck being used to customize a scan to find something very specific, thanks @jimisaiyan 💪
Got a cool use for a BCheck? Share it by using #bchecks for your chance to win a virtual meeting with a Burp Suite Engineer! 🧑💻
jimi
@jimisaiyan
Pentesting an IoT device recently, I created a #bcheck script to look for the exposed hub's username and the SAS token (password) along with other info such as device's id.
github.com/jimiss/bchecks/blob/main/azure-iot.bcheck -
Burp Suite
@Burp_Suite
Have you caught up with the latest developments to Burp Suite’s BChecks?
🌟 Syntax highlighting
🪄 BChecks helper
🛠️ BChecks testing tool
Read more about the new BChecks updates in this article 👉 portswigger.net/blog/whats-new-with-bchecks?ps_source=twi… -
Burp Suite
@Burp_Suite
Great to see this use of a BCheck to save time @j3ssie 🙌
There's been some brilliant entries to the BChecks competition so far - keep them coming!
Share your BCheck using #bchecks for your chance to win a virtual meeting with a Burp Suite Engineer.
x.com/j3ssiejjj/status/1754558322814906507
Jessie Ho
@j3ssie
I recently began experimenting with #bcheck from @PortSwigger, and I found it to be a time saver. I discovered that you can swiftly test the scan using the BSCode Editor below
If anyone is interested check out my custom scans: github.com/j3ssie/custom-bcheck-scan -
Burp Suite
@Burp_Suite
How can you use BChecks in Burp Suite Enterprise Edition to discover niche vulnerabilities across your portfolio? 🤔
This new article explains how to get the full value out of BChecks, including using Professional and Enterprise in tandem with BChecks:
portswigger.net/blog/introducing-custom-scan-checks-to-bu… -
Burp Suite
@Burp_Suite
Think your use of a BCheck is special? We want to hear from you! 🏆
Share how you’re using BChecks with us on social media using #bchecks for your chance to win a virtual meeting with a Burp Suite engineer.
Entry closes February 9 at 11.59pm GMT. -
Burp Suite
@Burp_Suite
📣 Custom scan checks in Burp Suite Enterprise Edition
Import a BCheck to scan for a niche vulnerability, and extend your security coverage across your entire portfolio.
BChecks repository 👉 github.com/PortSwigger/BChecks
Learn more about BChecks here 👉 portswigger.net/burp/pro/features/bchecks?ps_source=twitt… -
Burp Suite
@Burp_Suite
A great recent submission to the BChecks (custom scan checks) repo from @0xElkomy - keep them coming 💪 #bchecks
This post is unavailable. See it on X. -
Burp Suite
@Burp_Suite
Lack of visibility over scan checks, and cluttered and disorganised issue logs, mean you're at risk of missing valuable info from your testing.
UX team's Liv talks through the latest updates, making the dashboard more intuitive and efficient.
youtu.be/xfaNwyZbOrU -
Burp Suite
@Burp_Suite
Last chance to join @garethheyes as he navigates the landscape of CSS exfiltration techniques...
Hit the link below to watch him present "Blind CSS Exfiltration: Stealing user data from unknown web pages via CSS" - it kicks off at 3pm (GMT) / 4pm (CET).
www.meetup.com/css-cafe/events/298480761/ -
Burp Suite
@Burp_Suite
Looking to get a a deeper understanding of CSS's potential for exfiltration and the skills to test for and protect against this new attack?
Catch "Blind CSS Exfiltration: Stealing user data from unknown web pages via CSS" at 4pm (CET) with @garethheyes
www.meetup.com/css-cafe/events/298480761/ -
Burp Suite reposted
PortSwigger Research
@PortSwiggerRes
Nominations are now open for the top 10 new web hacking techniques of 2023! Check out the nominations so far, and make your own here -> portswigger.net/research/top-10-web-hacking-techniques-of…
-
Burp Suite reposted
@ddǝɐuɐp
@DanaEpp
Learn how to write your own Burp BCheck scripts to tap into the web vulnerability scanner to automate your API security testing.
#apisecurity #bcheck #burpsuite
danaepp.com/improve-your-api-security-testing-with-burp-b… -
Burp Suite
@Burp_Suite
Bambdas were launched in Burp Suite in November, and, since then, over 5000 of you have used the feature, totaling almost 10,000 Bambdas being applied in under 2 months!
Make sure to keep an eye out for the brand new Bambdas releases coming in 2024 👀
portswigger.net/burp/pro/features/bambdas -
Burp Suite
@Burp_Suite
This year, development teams have been more aware of security than ever before.
In July, CI-driven scans were released for Burp Suite Enterprise Edition. Devs have been running Burp scans in their pipelines, finding bugs, and squashing them before they release to production🤖🦠 -
Burp Suite
@Burp_Suite
You’ve all been very busy over at the Web Security Academy - in fact, you guys have completed a whopping 352,373 labs this year alone. 🤯
This year's most popular lab was ‘SQL injection vulnerability in WHERE clause allowing retrieval of hidden data’.
Darshan Naik
@darshanhackz
Completed #sql #injection path from @WebSecAcademy , it was a great journey to learn about the different SQL Injection attack from this platform, some lab required pro version of burp for handling the DNS query in the collaborator.
but Nice Labs. #websecurity -
Burp Suite
@Burp_Suite
With 2023 drawing to a close, we’re taking a look at all the brilliant things Burp Suite users have achieved throughout the year. 🙌 👀
Here’s what you guys have been up to… -
Burp Suite
@Burp_Suite
Don't miss this new article by @albinowax and @garethheyes below. 👇
Inside, they take a look at how to find that one weird endpoint with Bambdas...
x.com/PortSwiggerRes/status/1735606676567334952
PortSwigger Research
@PortSwiggerRes
Find that one weird endpoint, with Bambdas (by @albinowax & @garethheyes) ->
portswigger.net/research/finding-that-one-weird-endpoint-… -
Burp Suite
@Burp_Suite
🤩 The revamped dashboard is now available on the early adopter channel for Burp Suite Professional and Burp Suite Community Edition.
These UI improvements will hit the stable release channel in Jan 2024.
Tom Shelton-Lefley
@TomLefley
All I want for Christmas, is UI
(Coming soon to @Burp_Suite 2023.12) -
Burp Suite
@Burp_Suite
We told you so.
www.bbc.co.uk/news/health-67774902 -
Burp Suite
@Burp_Suite
Glad to see you're enjoying the recent updates to Burp Suite 🎊
⚒️ We think that it's nearly always a good day for some hacking.
Andrew Hutz
@TheGreenAbyss
Spending the afternoon really digging into @Burp_Suite, it's amazing what @PortSwigger has here. Up until now, I'd only ever really scratched the surface. Good day to do some #hacking
-
Burp Suite
@Burp_Suite
Anybody been looking for a library containing examples and guidance to simplify the process of creating user interfaces for Burp Suite extensions?
Never fear, @CoreyD97 has you covered 💭
x.com/CoreyD97/status/1735261308373570040 -
Burp Suite
@Burp_Suite
Hackvertor creator and PortSwigger Researcher @garethheyes just released some UI updates to the tool.
🧪He's looking for some user testing if anyone feels like giving it a whirl... 🥽
Gareth Heyes \u2028
@garethheyes
On my lunch today I fixed the outstanding UI issues with Hackvertor and pushed the changes. I'm maintaining a change log in the readme too now. I'd love some user testing if anyone has time. CC @Agarri_FR @irsdl
github.com/hackvertor/hackvertor/blob/master/README.md -
Burp Suite
@Burp_Suite
Wondering what’s next for Bambdas? 👀
There are plenty more exciting #bambdas releases in the pipeline for Burp Suite.
Here’s a sneak preview of the upcoming Logger view and WebSockets filter Bambdas…
Read more about the future of Bambdas here:
portswigger.net/blog/the-future-of-bambdas?ps_source=twit… -
Burp Suite reposted
PortSwigger Research
@PortSwiggerRes
Find that one weird endpoint, with Bambdas (by @albinowax & @garethheyes) ->
portswigger.net/research/finding-that-one-weird-endpoint-… -
Burp Suite
@Burp_Suite
Finally, we have another winner, Dana Epp, with this awesome Bambda to find specific access tokens in the Proxy HTTP history. 🏅
Great work, @DanaEpp - send @Burp_Suite a DM to claim your #bambdas t-shirt.
@ddǝɐuɐp
@DanaEpp
You know @Burp_Suite, the new #bambdas feature for proxy filtering is actually kind of nice. I had to parse several hundred thousand records today to find specific access tokens that were using a different algorithm than expected. This little script did the deed quite well...
-
Burp Suite
@Burp_Suite
Next, we have another one of our winners @Tur24Tur with their Bambdas to identify potentially vulnerable OWASP top-25 parameters. 🎉
Well done - drop us a DM at @Burp_Suite to claim your #bambdas t-shirt.
x.com/Tur24Tur/status/1731780861182308827
Tur.js
@Tur24Tur
I've just developed my first @Burp_Suite Bambdas specifically to identify OWASP Top-25 Parameters potentially vulnerable to XSS, SSRF, RCE, SQLi, LFI, and Open Redirect. For easy code access, visit GitHub:
github.com/BugBountyzip/Bambdas/blob/main/OWASP Top-25 Pa…
#bambdas #java -
Burp Suite
@Burp_Suite
First up, we have one of our winners, Soroush Dalili, with a very cool Bambda to highlight traffic in the Proxy HTTP history. Congratulations @irsdl 🏆
DM @Burp_Suite to claim your #bambdas t-shirt.
Soroush Dalili
@irsdl
If you are using the latest early edition of #burpsuite, you can use the following #bambda code for highlighting:
gist.github.com/irsdl/d9078390cb844d538f75a2fe4831cadf
It highlights the request with BurpCOLOR like "BurpRed"!
You won't need an extension for PwnFox Firefox extension either btw!
@Burp_Suite -
Burp Suite
@Burp_Suite
🏆 Competition winners 🏆
Thank you to everyone who entered the #bambdas competition - it's been fantastic to see all the creative ways you've used the feature.
The top three winners are as follows... -
Burp Suite reposted
PortSwigger Research
@PortSwiggerRes
You've heard of blind XSS - but what if there's CSP? Introducing blind CSS injection!
portswigger.net/research/blind-css-exfiltration -
Burp Suite
@Burp_Suite
High volumes of traffic making it hard to spot interesting requests? 🤔
Using a Bambda, you can easily write a custom filter for the Proxy HTTP history.
Head to the Proxy HTTP history in Burp Suite, switch to Bambdas mode and write a custom filter using your own code. -
Burp Suite
@Burp_Suite
Ready to share your Bambdas with the world? 🌍
Introducing the official Bambdas GitHub repository: github.com/PortSwigger/bambdas
Terms and conditions apply. Please read the repository guidelines before submitting: github.com/PortSwigger/bambdas/blob/main/CONTRIBUTING.md -
Burp Suite
@Burp_Suite
Another entry to the Bambdas competition - thanks @Tur24Tur 👏
Don't forget, tomorrow is the final day to tweet @Burp_Suite sharing how you are using #bambdas to win one of our awesome Bambdas t-shirts.
x.com/Tur24Tur/status/1730181127208407414
Tur.js
@Tur24Tur
I've just developed my first @Burp_Suite Bambdas specifically to identify OWASP Top-25 Parameters potentially vulnerable to XSS, SSRF, RCE, SQLi, LFI, and Open Redirect. For easy code access, visit GitHub:
github.com/BugBountyzip/Bambdas/blob/main/OWASP Top-25 Pa…
#bambdas #java -
Burp Suite
@Burp_Suite
Extending Burp Suite just got easier!
Check out this explainer video, and tweet us with #bambdas sharing how you’re using Bambdas to filter the Proxy HTTP history for the chance to win a Bambdas t-shirt. 🏆
youtu.be/neQpukwW43g -
Burp Suite reposted
Tur.js
@Tur24Tur
I've just developed my first @Burp_Suite Bambdas specifically to identify OWASP Top-25 Parameters potentially vulnerable to XSS, SSRF, RCE, SQLi, LFI, and Open Redirect. For easy code access, visit GitHub:
github.com/BugBountyzip/Bambdas/blob/main/OWASP Top-25 Pa…
#bambdas #java -
Burp Suite
@Burp_Suite
Don't miss out on your Bambdas t-shirt ⏳
There are still a few more days to enter the competition for your chance to win free Burp Suite swag!
Use #bambdas and share how you're using Bambdas to enter. The competition closes at 23:59 on December 1.
Burp Suite
@Burp_Suite
It's competition time... 🏆
Tweet us sharing how you’re using the new HTTP Proxy Bambda with #bambdas for your chance to win a Burp Suite t-shirt!
We’ll round up a selection of winners on Friday December 1 and send them a tee.
Burp Suite
@Burp_Suite
🎉 Introducing Bambdas 🎉
Customize Burp Suite Professional to suit your personal workflow with Bambdas.
Switch to ‘Bambda mode’ whilst in the HTTP Proxy history, and start tailoring Burp to your own needs today.
portswigger.net/burp/pro/features/bambdas/?ps_source=twit… -
Burp Suite reposted
Tolgahan Demirayak
@TolgaDemirayak
I wrote a code that detects JavaScript files for the new feature of the @Burp_Suite application called #bambdas. I enjoy looking into JavaScript files; sometimes interesting endpoints can be found
-
Burp Suite
@Burp_Suite
Here's another couple of interesting Bambdas, courtesy of @_0x999 🔥
We're loving all these examples of Bambdas that our Burp Suite users are sharing - keep them coming for your chance to win a Bambdas t-shirt! #bambdas -
Burp Suite
@Burp_Suite
Really nice use of a Bambda within JWT claims here, thanks @DanaEpp 🙌
We've got a similar example in our 'Introducing Bambdas' blog post, which allows you to find a role within a JWT claim...
x.com/DanaEpp/status/1727260692414394634
@ddǝɐuɐp
@DanaEpp
You know @Burp_Suite, the new #bambdas feature for proxy filtering is actually kind of nice. I had to parse several hundred thousand records today to find specific access tokens that were using a different algorithm than expected. This little script did the deed quite well...
Burp Suite
@Burp_Suite
Here's a snippet of the code you can use in a Bambda to find a role within JWT claims #bambdas
You can also read the full blog post here for more examples of interesting Bambdas: portswigger.net/blog/introducing-bambdas?ps_source=twitte… -
Burp Suite
@Burp_Suite
It's competition time... 🏆
Tweet us sharing how you’re using the new HTTP Proxy Bambda with #bambdas for your chance to win a Burp Suite t-shirt!
We’ll round up a selection of winners on Friday December 1 and send them a tee.
Burp Suite
@Burp_Suite
🎉 Introducing Bambdas 🎉
Customize Burp Suite Professional to suit your personal workflow with Bambdas.
Switch to ‘Bambda mode’ whilst in the HTTP Proxy history, and start tailoring Burp to your own needs today.
portswigger.net/burp/pro/features/bambdas/?ps_source=twit… -
Burp Suite reposted
BApp Store
@BApp_Store
Updated: BCheck Helper
portswigger.net/bappstore/41274be469184a56b06d6a791ce8a9ce -
Burp Suite
@Burp_Suite
Want to learn how to fine-tune Burp Scanner to scan applications containing non-standard data structures more effectively?
Try your hand at the new lab 👇
portswigger.net/web-security/essential-skills/using-burp-… -
Burp Suite
@Burp_Suite
Discovered Bambdas yet?
They're a unique new way to customize Burp Suite on the fly with small snippets of Java.
You'll learn what a Bambda is, why we've built them into Burp Suite, and see a couple of examples of how Bambdas work.
www.youtube.com/watch?v=neQpukwW43g -
Burp Suite
@Burp_Suite
🎉 Introducing Bambdas 🎉
Customize Burp Suite Professional to suit your personal workflow with Bambdas.
Switch to ‘Bambda mode’ whilst in the HTTP Proxy history, and start tailoring Burp to your own needs today.
portswigger.net/burp/pro/features/bambdas/?ps_source=twit… -
Burp Suite reposted
You Gina
@yougina
Want to process specific requests from @Burp_Suite in another tool? Using this #bambda filter to write URL's to stdin for the specified process, or customize to your needs!
-
Burp Suite
@Burp_Suite
If you’ve ever tried to write a BCheck, you’ll know the feedback cycle can be slow and finding bugs can be frustrating. Watch Dave from Burp's Scanner team talk about the new BCheck Testing Tool in Burp Suite Pro, which makes debugging BChecks easy💪
youtu.be/iysBfABg50g
Burp Suite
@Burp_Suite
After some feedback, we've re-uploaded this with improved audio quality. Our apologies for any unplanned hearing challenges experienced as a result... www.youtube.com/watch?v=KgBQrx0Cy7s
-
Burp Suite
@Burp_Suite
🔍 Testing an application with a GraphQL API?
Learn about common GraphQL vulnerabilities over at the Web Security Academy, and then scan your app with Burp Suite Professional or Burp Suite Enterprise Edition to find GraphQL bugs automatically.
#graphql
portswigger.net/web-security/graphql -
Burp Suite reposted
PortSwigger Research
@PortSwiggerRes
Wrote a bamda to detect HTTP responses containing a space in the header name... not sure what we were expecting to find but it definitely worked
return requestResponse.response().headers().stream().anyMatch(e -> e.name().contains(" ")); -
Burp Suite
@Burp_Suite
When scanning a target, it’s crucial that requests are in session so that you’re hitting the attack surface.
Tom demonstrates how Burp Scanner can detect when a session is no longer valid and replay the required steps to continue with a fresh one.
youtu.be/yoENNJjC4NY -
Burp Suite
@Burp_Suite
Burp’s BChecks feature makes adding your custom checks to Burp Scanner quick and straightforward.
Now, you can test your BChecks from within the editor, enabling you to quickly confirm if a check is working as expected without running a scan manually.
github.com/PortSwigger/BChecks -
Burp Suite
@Burp_Suite
In this latest post from @PortSwiggerRes, they share their findings on applying the single-packet attack to other popular network protocols. If you're looking for race conditions or research ideas, you'll find some leads here:
portswigger.net/research/the-single-packet-attack-making-… -
Burp Suite
@Burp_Suite
A handy tip for any Pro users out there...
Tired of sifting through scan results? The latest dashboard update lets you categorise and filter your scan results, so you no longer have to dig for the specific results you need.
Filter by BChecks, BApps, and Burp scan checks. 💪 -
Burp Suite
@Burp_Suite
Streamline your testing workflow with custom notes for Repeater tabs in Pro and Community. Stay organised and focused on uncovering those critical findings.
Want more notes? They'll be landing in the Target and Proxy tools soon…
portswigger.net/burp/releases/professional-community-2023… -
Burp Suite reposted
PortSwigger Research
@PortSwiggerRes
We've just published our findings on applying the single-packet attack to other popular network protocols. If you're looking for race conditions or research ideas, you'll find some leads here:
portswigger.net/research/the-single-packet-attack-making-… -
Burp Suite
@Burp_Suite
If you've been manually testing for DOM XSS using the browser dev tools, you'll know how tedious and slow this can be.
There is a better way...
Use the DOM Invader extension to find bugs quicker by seeing which function is called with your input.
portswigger.net/blog/introducing-dom-invader -
Burp Suite
@Burp_Suite
We want your thoughts on Burp Organizer!
Do you love it? Do you hate it? Do you wish you could use it differently?
Hit the survey link below to tell us what you think.
usabi.li/do/21f4dbe7acd8/6bbb -
Burp Suite reposted
Soroush Dalili
@irsdl
#burpsuite latest early version 2023.10.3 is giving us #bambda in filtering among other things!
It is very very powerful in filtering and it runs pure Java code very well. As seen in the screenshot, I even managed to open calc with it😎
I hope to see it in Target Search soon!
It seems this release has been one of the most important ones. Well done @PortSwigger 👏 -
Burp Suite
@Burp_Suite
Writing BChecks? Wish there was an easy way to check if they are working correctly?
The new BChecks testing tool has arrived! 🎉🎉🎉
Write a BCheck to find a custom vulnerability, then test it right from the editor in Burp Suite Professional.
portswigger.net/burp/releases/professional-community-2023… -
Burp Suite
@Burp_Suite
Searching for new and niche bugs in your application?
Here's a BApp that lets you effortlessly download community-made BChecks from Github.
Load them into Burp Scanner and let it find those vulnerabilities for you!
portswigger.net/bappstore/41274be469184a56b06d6a791ce8a9ce -
Burp Suite
@Burp_Suite
Want to learn about the approach web security researchers take when developing custom automation?
In this latest post from @PortSwiggerRes, @albinowax shares his thoughts about this challenge, including a worked example based on his recent research.
portswigger.net/research/how-to-build-custom-scanners-for… -
Burp Suite
@Burp_Suite
Do you wish you could manage your HTTP messages in one place, to keep track of interesting requests to return to later?
Enter Burp Suite's new Organizer tool!
Watch the video below, where Mike demonstrates how to use it.
youtu.be/_UlgBdW6KSg -
Burp Suite reposted
PortSwigger
@PortSwigger
Calling all Pro and Enterprise users!
Got any thoughts on APIs? We're looking to improve Burp Suite's API scanning capabilities, so if you currently scan APIs, we want to hear from you.
Hit the survey link below to share your thoughts:
usabi.li/do/29366fb762c6/37fe -
Burp Suite reposted
PortSwigger Research
@PortSwiggerRes
Testing broken sites with DOM Invader enabled? Come across a situation where eval throws an exception? This post explains why it happens and what you can do to fix it and carry on testing ...
portswigger.net/blog/dom-invader-and-the-case-of-direct-e… -
Burp Suite
@Burp_Suite
If you’ve tried to write a Burp extension to add custom scan checks, you’ll know this can be time-consuming. Burp’s BChecks feature makes adding your checks to Burp Scanner quick and simple. See how the team at @SprocketSec have been experimenting...
portswigger.net/blog/supporting-sprocket-securitys-offens… -
Burp Suite reposted
James Kettle
@albinowax
The recording for "Smashing the state machine: the true potential of web race conditions" is now live, courtesy of @defcon! Watch it here - or catch the updated edition in-person at @nullcon later this week!
www.youtube.com/watch?v=tKJzsaB1ZvI&list=PLoX0sUafNGbEkK0… -
Burp Suite reposted
Gareth Heyes \u2028
@garethheyes
My mate Nolan redesigned my book cover. He did a much better job than me! I've also updated the content to include more Server-Side Prototype Pollution and a few new XSS vectors. Please RT to support my work
leanpub.com/javascriptforhackers/
www.amazon.com/JavaScript-hackers-Learn-think-hacker/dp/B… -
Burp Suite
@Burp_Suite
To all Pro/Community users:
How would you like to be kept informed of new feature releases and product enhancements?
Let us know your preferences: usabi.li/do/d1b1bcac36cb/9808 -
Burp Suite
@Burp_Suite
Writing custom scan checks can be time-consuming, but Burp’s BChecks feature makes it quick and simple to add your own checks to Burp Scanner.
Find out how the team at @SprocketSec have done exactly that, and more…
portswigger.net/blog/supporting-sprocket-securitys-offens… -
Burp Suite
@Burp_Suite
Have you tried the built-in single-packet attack capability in Burp Repeater?
It nullifies network jitter, allowing you to send synchronised requests in parallel.
portswigger.net/burp/documentation/desktop/tools/repeater… -
Burp Suite
@Burp_Suite
As a developer, you want to catch critical security issues before they become painful.
Dastardly, from Burp Suite, integrates directly with your CI/CD pipeline. Now, with improved scan coverage and handling for SPAs, React, clickable elements and more.
portswigger.net/burp/releases/dastardly-2023-10 -
Burp Suite
@Burp_Suite
Looking to make your testing workflows as efficient as possible? Wish you could run more specific checks for vulnerability classes? Better identify tech stack components?
Check out BChecks 👉 #bchecks github.com/PortSwigger/BChecks -
Burp Suite
@Burp_Suite
The Burp community voted @sprocket_ed's BCheck, our recent BChecks competition winner. We caught up with him and the @SprocketSec team to learn how they've been using BChecks to support their testing processes.
Read all about it here:
portswigger.net/blog/supporting-sprocket-securitys-offens… -
Burp Suite
@Burp_Suite
Calling all Pro/Community users...
As part of our table enhancement work, we'd like to know - are tables easier to read with or without zebra stripes?
Follow this link to cast your vote 👉 usabi.li/do/37e13b68846f/7baa -
Burp Suite
@Burp_Suite
Find seven security issues you care about - in 10 mins or less - with Dastardly, from Burp Suite.
Now, with improved handling of SPAs, YAML API definitions, iFrame audit requests, clickable elements and more.
portswigger.net/burp/releases/dastardly-2023-10 -
Burp Suite reposted
Mastering Burp Suite Pro
@MasteringBurp
Periodical reminder: it's possible to navigate sub-tabs (like Repeater entries) from the keyboard.
You simply have to configure the actions "Go to previous tab" and "Go to next tab". -
Burp Suite reposted
YesWeHack ⠵
@yeswehack
The release of @Burp_Suite's BCheck feature has added a fantastic touch to the scanner! 🤩
We wrote a blog where we described some of the BCheck scripts we have developed. These scripts are now available on our Github repository! 👇
github.com/yeswehack/BCheck-Burp-scripts
#yeswerhackers #bugbounty #bugbountytips -
Burp Suite
@Burp_Suite
Are you getting the most out of your GraphQL API? 🤔 Burp's advanced introspection techniques help to ensure that no function goes unnoticed.
Watch the latest Burp Short from the Burp Scanner development team to learn more.
youtu.be/BZh9f-KzYFc -
Burp Suite
@Burp_Suite
A Friday roundup of the latest Burp Scanner updates:
Added Status column in Crawl Paths>Outlinks to aid discovery.
Project-wide crawl path sharing boosts scan efficiency.
Perform GraphQL endpoint introspection queries to access query/mutation info.
www.youtube.com/watch?v=cDuyV2Mn6Yo&list=PLoX0sUafNGbGlLm… -
Burp Suite
@Burp_Suite
A GraphQL API app may only exercise a small portion of available functions. By using introspection techniques, Burp's crawler can auto-identify available functions via a GraphQL API and exercise them, even if the app hasn’t performed them during the crawl www.youtube.com/watch?v=BZh9f-KzYFc
-
Burp Suite
@Burp_Suite
Accelerate your AppSec journey with Dastardly, from Burp Suite.
Gear up your CI/CD pipeline for a quick scan and spot seven key security issues. Equip your team to champion web app security without added hassle.
portswigger.net/burp/dastardly -
Burp Suite reposted
Oli (C..1..P.H.Y)
@marcolivermunz
The BChecks from Burp are truly remarkable. They have allowed me to automate a significant portion of my personal checks with ease and convenience. The Integration with live tasks makes them super efficient. Exceptional job @PortSwigger 🙌
Check it out: github.com/PortSwigger/BChecks -
Burp Suite
@Burp_Suite
🔐 Safeguard your code like a pro and nip critical issues in the bud with Dastardly, from Burp Suite.
🌐 Scan for 7 top security concerns in your CI/CD pipeline, boosting DevSecOps synergy.
portswigger.net/burp/dastardly -
Burp Suite
@Burp_Suite
Almost everything you do in Burp Suite Pro contributes to the understanding of the target, so why do crawl tasks operate in complete isolation?
Dave talks about how this has been refined so that you can map out your application across multiple tasks.
youtu.be/opDHxt20gx0 -
Burp Suite
@Burp_Suite
🎉Congratulations to @sprocket_ed, you're the winner of our community-created BChecks competition!
Their BCheck appends an HTTP header for each request to attempt to elicit a response indicating NTLM authentication is present. Check it out on the BChecks GitHub repo 🤘
Burp Suite
@Burp_Suite
You can find their BCheck here: github.com/PortSwigger/BChecks/blob/adc6df00235ef4711fdd4…
@sprocket_ed - DM us and we'll chat about your prize 😏 -
Burp Suite
@Burp_Suite
It's frustrating when software doesn't allow you to customize its layout, and this often wastes precious on-screen real estate.
With Burp Suite, you can hide the tools you don’t use, rearrange the ones you do, and even group them in separate windows.
portswigger.net/burp/documentation/desktop/burps-layout -
Burp Suite
@Burp_Suite
Unveiling the single-packet attack, a technique that abuses HTTP/2 to stop network jitter from interfering with race condition attacks, effectively making remote races 'local'.
Find the new tooling in Burp Repeater…
portswigger.net/burp/releases/professional-community-2023…
Burp Suite
@Burp_Suite
Want to learn more about the single-packet attack technique? Dive in to "Smashing the state machine: the true potential of web race conditions" from @PortSwiggerRes to arm yourself with novel techniques & tooling.
portswigger.net/research/smashing-the-state-machine?ps_so… -
Burp Suite reposted
James Kettle
@albinowax
One cool thing I didn't mention in the presentation is that you can also use the single-packet attack via Burp Repeater, even in the free edition. This should make testing & creating replication steps for triagers a bit easier!
-
Burp Suite
@Burp_Suite
Want to experiment with a more reliable testing method that can make race conditions more easily discoverable? Find the new tooling in Burp Repeater now💪
PortSwigger Research
@PortSwiggerRes
We've just published 'Smashing the state machine: the true potential of web race conditions' by @albinowax! Dive in to arm yourself with novel techniques & tooling, and help reshape this attack class:
portswigger.net/research/smashing-the-state-machine?ps_so… -
Burp Suite reposted
STÖK ✌️
@stokfredrik
@albinowax running live demos of single packet race conditions… ON THE CONF WI-FI, since it wont not rely on network bandwidth and is not influenced by jitter.. 💪🔥
-
Burp Suite
@Burp_Suite
New to Burp Suite Enterprise Edition: the ability to run CI-driven scans without infrastructure or deployment dependencies.
portswigger.net/burp/documentation/enterprise/integrate-c…
Carry out full-power vulnerability scans, directly from within your CI/CD pipelines, with the new API key mode. -
Burp Suite
@Burp_Suite
📣 Last chance to vote for your favourite community-submitted BCheck!
We'll be counting es up until midnight today (31 July). Click through to the original post, then hit the "Like" button for the BCheck you like or think you'd use the most.
Burp Suite
@Burp_Suite
We've shortlisted the top ten submitted BChecks (so far), and now we'd like you to vote for your favourite.
Each BCheck will be shared as an individual reply to this tweet - simply hit the "Like" button for the BCheck you like the most.
Read more here: portswigger.net/blog/the-top-10-community-created-bchecks… -
Burp Suite
@Burp_Suite
Did you catch the latest Burp Suite roadmap update? It gives you the lowdown on some great new features over the next 12 months. Check it out:
portswigger.net/blog/burp-suite-roadmap-update-july-2023 -
Burp Suite reposted
Lucian Nitescu 🇷🇴
@LucianNitescu
Just stumbled upon the #bchecks project by @PortSwigger! It's a game-changer for #burpsuite users, offering powerful new checks in form of templates that are somewhat similar to #nuclei🤔
#portswigger #webappsecurity github.com/PortSwigger/BChecks -
Burp Suite
@Burp_Suite
Brand new to Burp Suite… It's frustrating when software doesn't allow you to customize its layout, and this often wastes precious on-screen real estate.
You can work faster when you focus on the things you want to see - and hide the things you don't.
portswigger.net/burp/releases/professional-community-2023…
Burp Suite
@Burp_Suite
Show and hide tabs, to avoid wasting screen space on tools you don't need or use.
Burp Suite
@Burp_Suite
Detach tabs, to create dedicated focus on the tools you want to see.
Burp Suite
@Burp_Suite
Change the order of tool tabs, to put the tools you use most within easy reach.
-
Burp Suite reposted
nightshiba
@nightshiba
Thrilled to see my BCheck detecting generic exposed Prometheus metrics in the top 10! It's been a fun experience exploring this new feature. I'm excited about its potential and eager to see how the BCheck syntax evolves. Thanks @Burp_Suite for recognizing my contribution!👀
Burp Suite
@Burp_Suite
Exposed-prometheus-metrics.bcheck
github.com/PortSwigger/BChecks/blob/adc6df00235ef4711fdd4… -
Burp Suite
@Burp_Suite
We've shortlisted the top ten submitted BChecks (so far), and now we'd like you to vote for your favourite.
Each BCheck will be shared as an individual reply to this tweet - simply hit the "Like" button for the BCheck you like the most.
Read more here: portswigger.net/blog/the-top-10-community-created-bchecks…
Burp Suite
@Burp_Suite
CVE-2023-25690 Apache mod_proxy CRLF Smuggling
github.com/PortSwigger/BChecks/blob/adc6df00235ef4711fdd4…
Burp Suite
@Burp_Suite
CVE-2020-10770 Keycloak request_uri SSRF
github.com/PortSwigger/BChecks/blob/adc6df00235ef4711fdd4…
Burp Suite
@Burp_Suite
CVE-2021-27748 SSRF Websphere Portal.bcheck
github.com/PortSwigger/BChecks/blob/adc6df00235ef4711fdd4…
Burp Suite
@Burp_Suite
Ntlm-authentication-discovery.bcheck
github.com/PortSwigger/BChecks/blob/adc6df00235ef4711fdd4…
Burp Suite
@Burp_Suite
CVE-2023-24488 - Citrix Gateway Open Redirect and XSS.bcheck
github.com/PortSwigger/BChecks/blob/adc6df00235ef4711fdd4…
Burp Suite
@Burp_Suite
Nacos-default-password.bcheck
github.com/PortSwigger/BChecks/blob/adc6df00235ef4711fdd4…
Burp Suite
@Burp_Suite
Exposed-prometheus-metrics.bcheck
github.com/PortSwigger/BChecks/blob/adc6df00235ef4711fdd4…
Burp Suite
@Burp_Suite
CVE-2018-1000129 - Jolokia 137 - Cross-Site Scripting.bcheck
github.com/PortSwigger/BChecks/blob/adc6df00235ef4711fdd4…
Burp Suite
@Burp_Suite
Exposed-swagger-ui.bcheck
github.com/PortSwigger/BChecks/blob/adc6df00235ef4711fdd4…
Burp Suite
@Burp_Suite
Javascript/jsMapFile.bcheck
github.com/PortSwigger/BChecks/blob/adc6df00235ef4711fdd4… -
Burp Suite
@Burp_Suite
Thanks to RandSec, who has submitted a Burp BCheck to identify possible Citrix Netscaler /ADC hosts for those looking to understand exposure to CVE-2023-3519, CVE-2023-3466, CVE-2023-3467 etc. -
github.com/PortSwigger/BChecks/blob/main/other/Netscaler_… -
Burp Suite reposted
Javeley😊
@Javeley_QAQ
这个版本我太爱了😍
-
Burp Suite reposted
Federico Dotta
@apps3c
Third article of the series "Extending @Burp_Suite for fun and profit - The Montoya way" is out! Topic: inspecting and tampering WebSocket messages!
security.humanativaspa.it/extending-burp-suite-for-fun-an… -
Burp Suite reposted
PortSwigger Research
@PortSwiggerRes
Good news for fans of ActiveScan++ - you can now load it into Burp Suite Enterprise Edition, using the jar here: github.com/PortSwigger/active-scan-plus-plus/releases
-
Burp Suite
@Burp_Suite
Web apps often apply many layers of formats and encoding to a single piece of data, which need unwrapping and reapplying when sending payloads. Tom shows how Burp Scanner detects these nested layers and takes care of transforming payloads correctly.
youtu.be/KOCl1CQnKVk -
Burp Suite reposted
Matheus Vrech
@vrechson
I did this to speed up the creation of basic bcheck scripts by exporting them directly from repeater github.com/vrechson/copy-to-bcheck
-
Burp Suite reposted
Ollie Whitehouse
@ollieatnowhere
These vulnerabilities are now being actively exploited - www.bleepingcomputer.com/news/security/critical-coldfusio…
@Burp_Suite #bcheck to find vulnerable hosts 👇
Ollie Whitehouse
@ollieatnowhere
Wrote a couple of #bchecks today for @Burp_Suite Pro for the Adobe ColdFusion vulnerabilities.
- CVE-2023-29298 Access Control Bypass
- CVE-2023-26360 Arbitrary File Read and Code Execution
ColdFusion made me feel nostalgic..
from @PortSwigger with 🧡
github.com/PortSwigger/BChecks/tree/main/vulnerabilities-… -
Burp Suite
@Burp_Suite
Thanks to everyone who's created and submitted a BCheck so far - we're going through the GitHub repo to decide who will win some swag... Hit the link below to submit your own BCheck and vote for your favourite submissions!
github.com/PortSwigger/BChecks/tree/main