ARTEX marks a change in the threat landscape: agentic offensive frameworks have moved from experiments to operational use by state-aligned and financially motivated actors alike.
Since late August 2026, at least five actors and clusters have used ARTEX. One China-nexus espionage actor told its agents to find Windows hosts without an EDR sensor in a campaign targeting 200+ organizations across 14+ countries.
Read our analysis: www.sentinelone.com/blog/artex-unmasked-the-rise-of-ai-po…
SentinelOne
SentinelOne, Inc. is an American cybersecurity company listed on NYSE based in Mountain View, California. The company was founded in 2013 by Tomer Weingarten, Almog Cohen and Ehud ("Udi") Shamir. Weingarten acts as the company's CEO. The company has approximately 2,800 employees and offices in Mountain View, Boston, Prague, Tokyo, and Tel Aviv. The company uses machine learning for monitoring personal computers, IoT devices, and cloud workloads. The company's platform utilizes a heuristic model, specifically its patented behavioral AI. The company is AV-TEST certified. More on Wikipedia
-
SentinelOne
@SentinelOne
-
SentinelOne
@SentinelOne
SentinelOne is a Visionary Leader in the Frost Radar™: AI Security Operations Centers, 2026 from @FrostSullivan. AI-powered threats are today’s reality. Our Autonomous SOC investigates and responds at machine speed, and analysts keep the decisions that matter.
Built on the Singularity Platform, the Autonomous SOC brings together Purple AI, AI SIEM, AI Data Pipelines, Hyperautomation, and Wayfinder expert services. s1.ai/4a7efe -
SentinelOne
@SentinelOne
At Iress, a lean security team protects a platform that facilitates more than 80% of UK retail market flow.
SentinelOne covers endpoint and cloud, and Wayfinder Elite tunes protection so it never slows execution.
Full story: www.sentinelone.com/resources/casestudies/iress-customer-…This media couldn't be displayed. See it on the original post.Post not available here, view on X
SentinelOne
@SentinelOne
Hyperautomation also closes more than 50% of alerts without analyst intervention.
In a third-party pen test, Wayfinder Elite detected the simulated attack and started automated endpoint containment within minutes.
SentinelOne
@SentinelOne
The result: incident response from hours to minutes, 80 to 90% less threat-hunting time, and 50%+ of alerts auto-closed.
When Iress needed forensics in South Africa, SentinelOne DFIR onboarded in hours, not days.
Full story: www.sentinelone.com/resources/casestudies/iress-customer-… -
SentinelOne
@SentinelOne
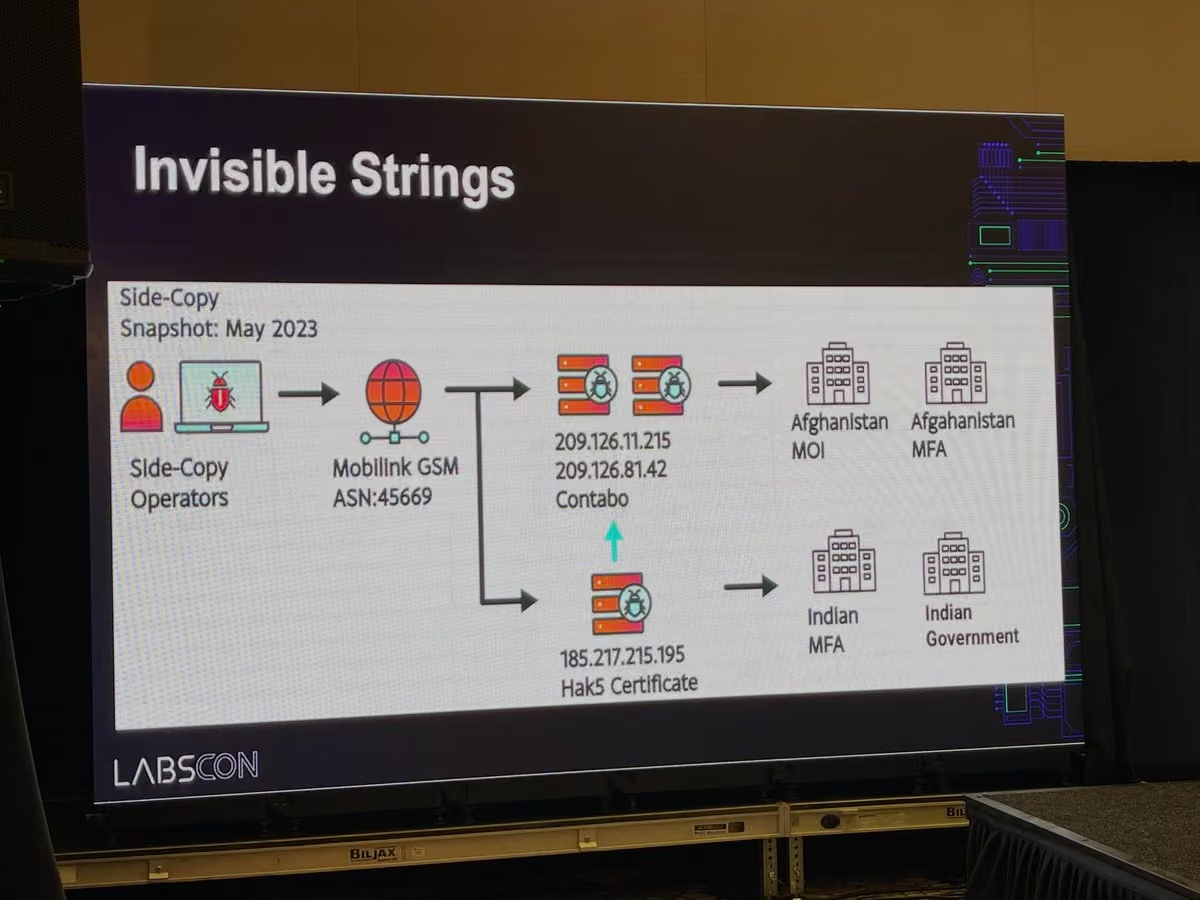
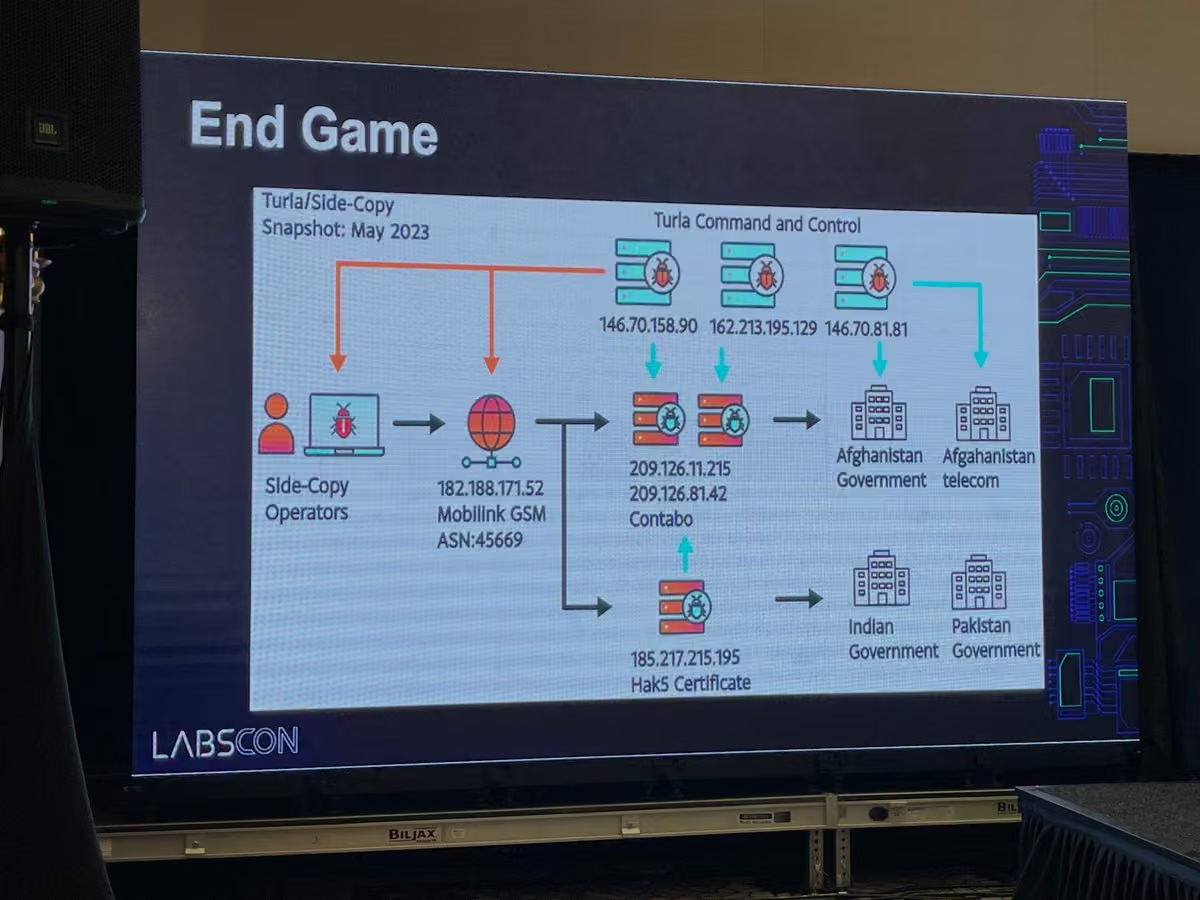
Europol seized hundreds of servers tied to Gootloader, CastleRAT, and StealC. FinCEN cut MEXC off from U.S. finance. Researchers reveal that Turla used Cereal malware to steal government emails. Railway said stolen AI keys led to $740,000 in estimated charges.
-
SentinelOne
@SentinelOne
A world-class brand secures the fleet with SentinelOne. 🚢 @CarnivalCorpLtd's ships are floating cities. Navigation, propulsion, and life safety share a network with onboard casinos, and there’s no IT department down the hall.
Full story: www.sentinelone.com/customers/carnival/Post not available here, view on X
SentinelOne
@SentinelOne
Response happens from shore. Singularity RemoteOps opens secure sessions on any endpoint to collect forensics or isolate a machine. When a shipboard point-of-sale file was wrongly quarantined, the SOC restored it fleet-wide without a machine-by-machine recovery.
SentinelOne
@SentinelOne
With their SentinelOne Technical Account Manager, the team also built a USB checkpoint so every drive is scanned before it touches shipboard engineering systems.
Security guests never notice. Full story: www.sentinelone.com/customers/carnival/ -
SentinelOne
@SentinelOne
Europe’s refrigeration attacks are raising concerns about appliances in your own kitchen.
@juanandres_gs joined @CBSNews' The Daily Report to discuss the risks to internet-connected household devices.
Watch: www.cbsnews.com/video/eu-cybersecurity-chief-fears-househ… -
SentinelOne
@SentinelOne
Gemini 4 Carbon is now available, and our security research team evaluated Carbon on kernel driver vulnerability research against other frontier models. It uncovered four verified vulnerabilities beyond the core memory-corruption bugs every model found. Learn more 👇
-
SentinelOne
@SentinelOne
AI agents are taking action across the enterprise.
From visibility to runtime guardrails, SentinelOne SingularityTM Agentic Detection and Response (ADR) shows what agents are doing and enforces the limits you set.
Watch the demo. 👇
youtu.be/NyrVzRL3_aQ -
SentinelOne
@SentinelOne
🚨 This week, law enforcement indicted two Canadians over a university hacking scheme and seized over 100 investment fraud across Europe. Attackers posed as IT support over Microsoft Teams and refrigeration systems are being disrupted in a second wave of attacks.
-
SentinelOne
@SentinelOne
As a longtime participant in Daybreak Defense Network, SentinelOne has played an active role in testing, benchmarking and shaping the latest Astra-class frontier models, like GPT-6 Cyber.
"The hardest part of security research is connecting scattered clues into a clear understanding of how an attack could work. GPT‑6 Cyber helps our researchers make those connections, test their hypotheses, and uncover weaknesses that demand deeper investigation. It expands what our experts can take on, and helps us turn that understanding into better protection for customers.” – Chris Corde, Chief Product Officer at SentinelOne.
Learn more 👇
OpenAI
@OpenAI
Introducing GPT‑6 Cyber: a major advance in security research that pairs stronger capabilities with better model alignment.
The model powered the Linux kernel research we announced yesterday, and security teams at companies like Mozilla, Palo Alto Networks, Calif, and Cisco—alongside our own at OpenAI—are already putting it to work.
GPT-6 Cyber is available to select Daybreak Red customers and we are expanding access over time.
openai.com/index/introducing-gpt-6-cyber/ -
SentinelOne
@SentinelOne
The City of Los Angeles secured 20,000+ endpoints across 40+ departments with SentinelOne in under six months. Wayfinder MDR adds the capacity of nine full-time employees, and workflows now run in seconds instead of hours. www.sentinelone.com/customers/city-of-la/
-
SentinelOne
@SentinelOne
AI can reverse engineer malware. We'd still like to see the receipts.
@LabsSentinel developed VerifiedIDA to keep LLM-driven analysis tied to evidence, open to review, and reusable across security workflows.
Explore the full research: www.sentinelone.com/labs/verifiedida-making-llm-driven-re… -
SentinelOne
@SentinelOne
Threat actors are turning up the heat on Europe's supermarkets. Literally.
Refrigeration systems across Europe have been disrupted, with attackers suspected of manipulating temperature controls through exposed management interfaces.
Read the analysis: www.sentinelone.com/labs/defrost-and-disrupt-an-assessmen… -
SentinelOne
@SentinelOne
AI could give defenders a bigger advantage than attackers.
Steve Stone made that case at OneCon. PHP2SHELL offers a recent example, with AI-assisted research helping uncover critical PHP vulnerabilities that might otherwise have gone unresolved.
🔗 www.sentinelone.com/blog/stopping-php2shell-how-sentinelo…This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
We’re committed to defending the surfaces AI runs on. Today, we announced an integration with Anthropic’s @claudeai Cowork to extend AI Security coverage to one of the most popular agentic work apps.
Runtime security will run inside the Cowork VM so security teams can:
→ See what agents do
→ Get alerts on suspicious behavior
→ Autonomously stop attacks
Get the details: s1.ai/5351bc -
SentinelOne
@SentinelOne
AI research keeps pushing for more powerful models. Harvard professor James Mickens thinks it's time to rethink that priority.
At LABScon26, Mickens made a provocative case: right now, the only good AI research is safety research.
Read: www.sentinelone.com/labs/labscon26-replay-keynote-a-sober… -
SentinelOne
@SentinelOne
🚨 Various vulnerabilities and security events took over this past week in what’s being called “Black October”, which attackers reportedly chaining flaws to root firewalls and cyber defenders releases emergency patches for Node2SHELL.
🔗 www.sentinelone.com/blog/the-good-the-bad-and-the-ugly-in… -
SentinelOne
@SentinelOne
The SentinelOne plugin is live in the Plugin marketplace in Google @Antigravity! 🔌
Connect Purple AI to Antigravity agents to query Singularity Console, triage vulnerabilities next to the code, investigate alerts, and hunt threats in natural language. s1.ai/0520a4 -
SentinelOne
@SentinelOne
#ai is finding vulnerabilities faster than teams can triage them. Wayfinder Frontier AI Services is adding Claude #mythos 5.1, Anthropic’s most capable model class for cybersecurity, to find what exists, validate what’s exploitable today, and set the order for fixes.
-
SentinelOne
@SentinelOne
With PHP2SHELL, eMudhra, LiteLLM and more, AI is helping attackers move faster and cheaper. That was the message at #onecon: fundamentals and defense in depth win, and behavior is the signal that holds up ⚡
Join us on Wednesday for a deeper look into the threats we are monitoring: s1.ai/32cef5This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
🚨 This week, a Nigerian man was sentenced to eight years for spearphishing and tax fraud, while a China-linked actor deployed agentic AI to compromise cloud supply chains and PHP warns of two critical-level RCE flaws.
🔗 www.sentinelone.com/blog/the-good-the-bad-and-the-ugly-in… -
SentinelOne
@SentinelOne
PHP2Shell: two critical PHP flaws (CVSS 9.2) let unauthenticated attackers execute code on web servers. Patch first. SentinelOne stops post-exploitation activity at runtime in protect mode. s1.ai/09aa56
-
SentinelOne
@SentinelOne
Another full room at #onecon. Matt Berry, Director of Technical Marketing, shares practical insights with a packed house on this final-day breakout. 💡
-
SentinelOne
@SentinelOne
Connections are happening all over the #onecon expo hall. 🤝 Great conversations on AI Security, new ideas, and the people who make this community strong. 🛡️
-
SentinelOne
@SentinelOne
Welcome to Day 3 of #onecon! 🎉 The final day is here, and breakout sessions are already underway. 🔥
-
SentinelOne
@SentinelOne
"Automation only works if you can trust it. It has to be reliable, and its confidentiality has to be preserved. You can't automate security on data that leaves your control." - Dr. Nicandro Scarabeo, Bell Canada Technical Director, Cyber Security and Architecture
#onecon -
SentinelOne
@SentinelOne
"We’ve improved our platform detection functionality by delivering over 2000 new AI-powered detections, increasing coverage across new threat actors, campaigns, and TTPs." - Chris Corde, SentinelOne Chief Product Officer
#onecon -
SentinelOne
@SentinelOne
Please welcome to the #onecon stage Chris Corde, SentinelOne Chief Product Officer! 🚀
-
SentinelOne
@SentinelOne
Ana Pinczuk, SentinelOne President of Product and Technology, opens the #onecon product keynote 👏
-
SentinelOne
@SentinelOne
Next up on the #onecon stage: Hector Monsegur and Chris Tarbell, the FBI agent and the hacker he took down.
-
SentinelOne
@SentinelOne
"Our responsibility is to make security strong enough and fast enough for our future.
Today, agents run inside your business with credentials, tools, identities, and the ability to act independently.
We plan to solve this completely new actor in the enterprise." - Tomer Weingarten, SentinelOne co-founder and CEO
#onecon -
SentinelOne
@SentinelOne
Tomer Weingarten, SentinelOne co-founder and CEO, opens Day 2 at #onecon. 🎤
-
SentinelOne
@SentinelOne
Welcome to Day 2 of #onecon! 💜
-
SentinelOne
@SentinelOne
AI agents now hold credentials and act across the enterprise. At OneCon, we unveiled:
🛡️ Singularity™ ADR to stop rogue and malicious agents at machine speed
⚡ Singularity ASOC brings security superintelligence to the SOC
🤝 An expanded PartnerOne program to equip partners to build and scale AI Security practices
Learn more 👉 s1.ai/mtbf7 -
SentinelOne
@SentinelOne
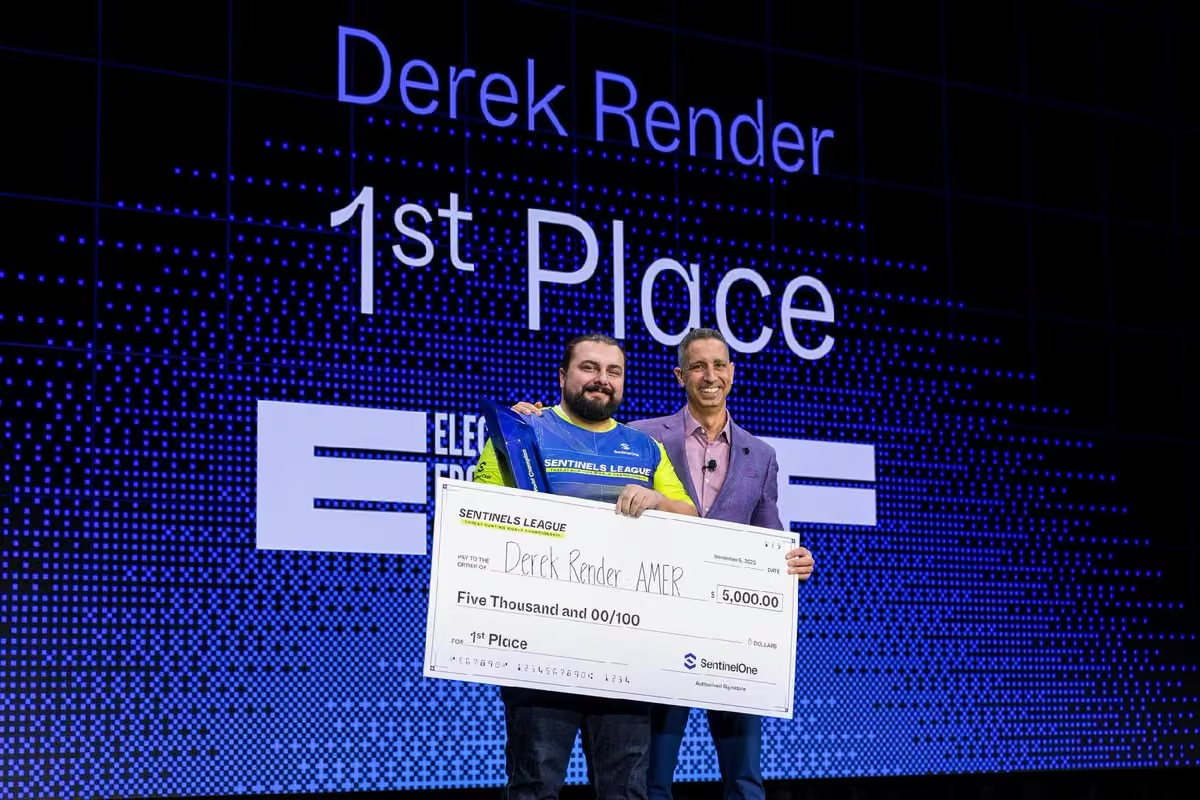
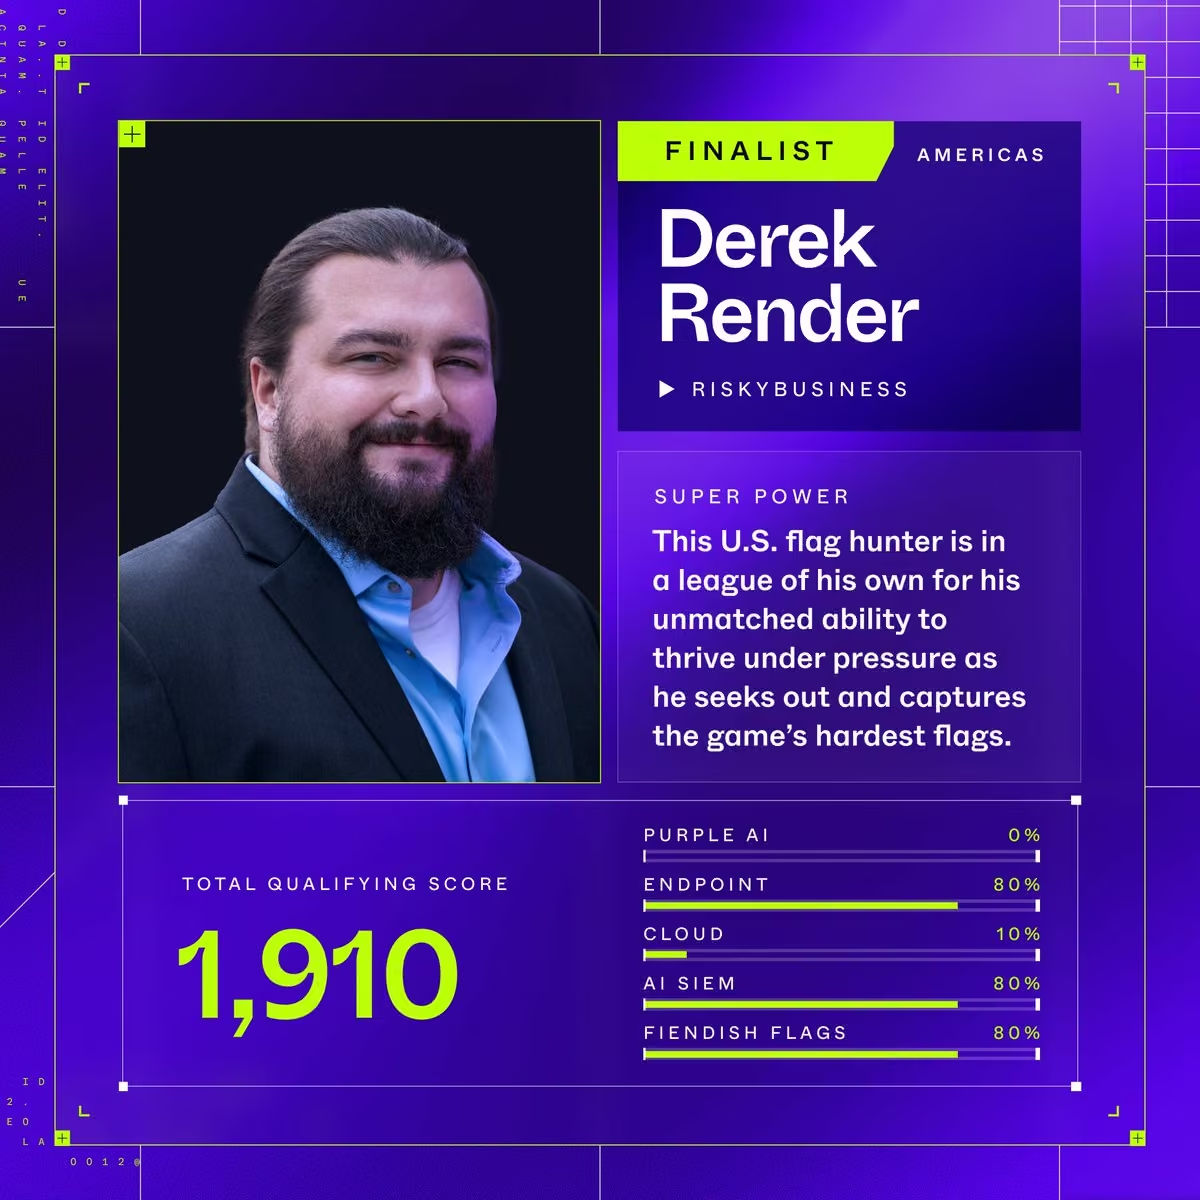
Last year’s champion, Derek Render, takes the #onecon stage.
-
SentinelOne
@SentinelOne
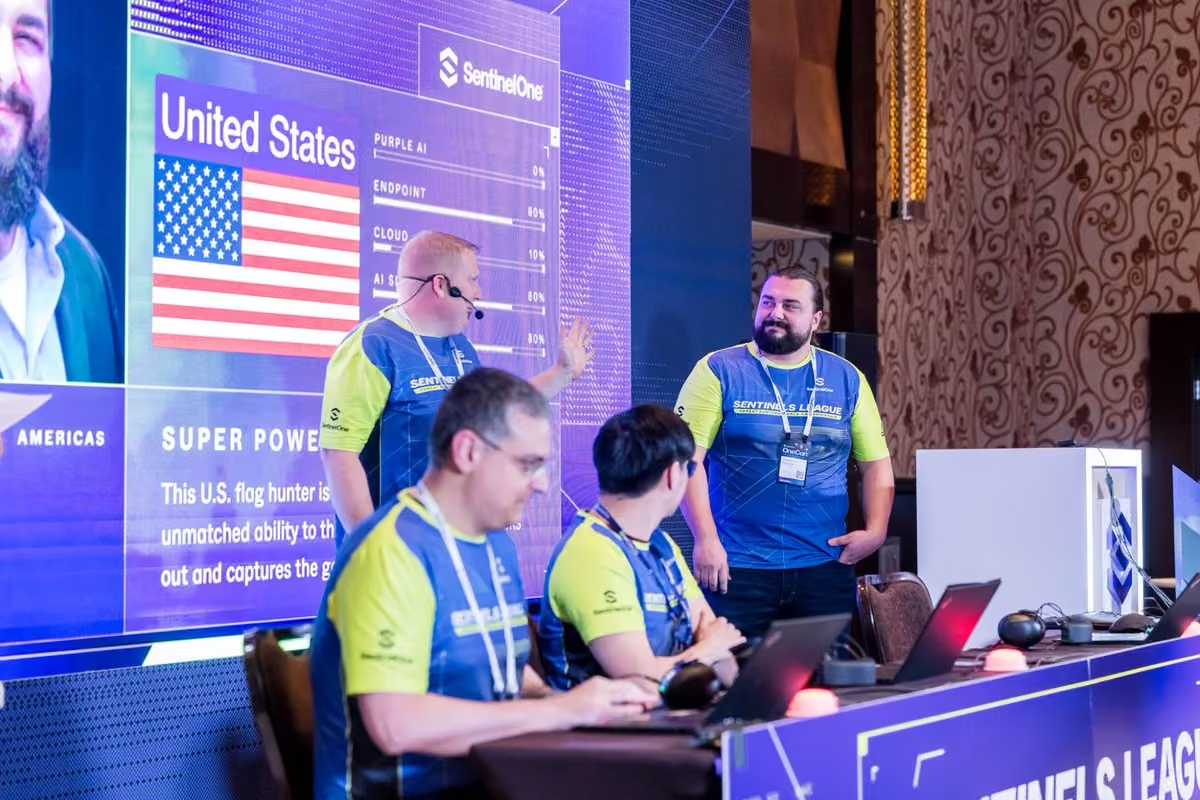
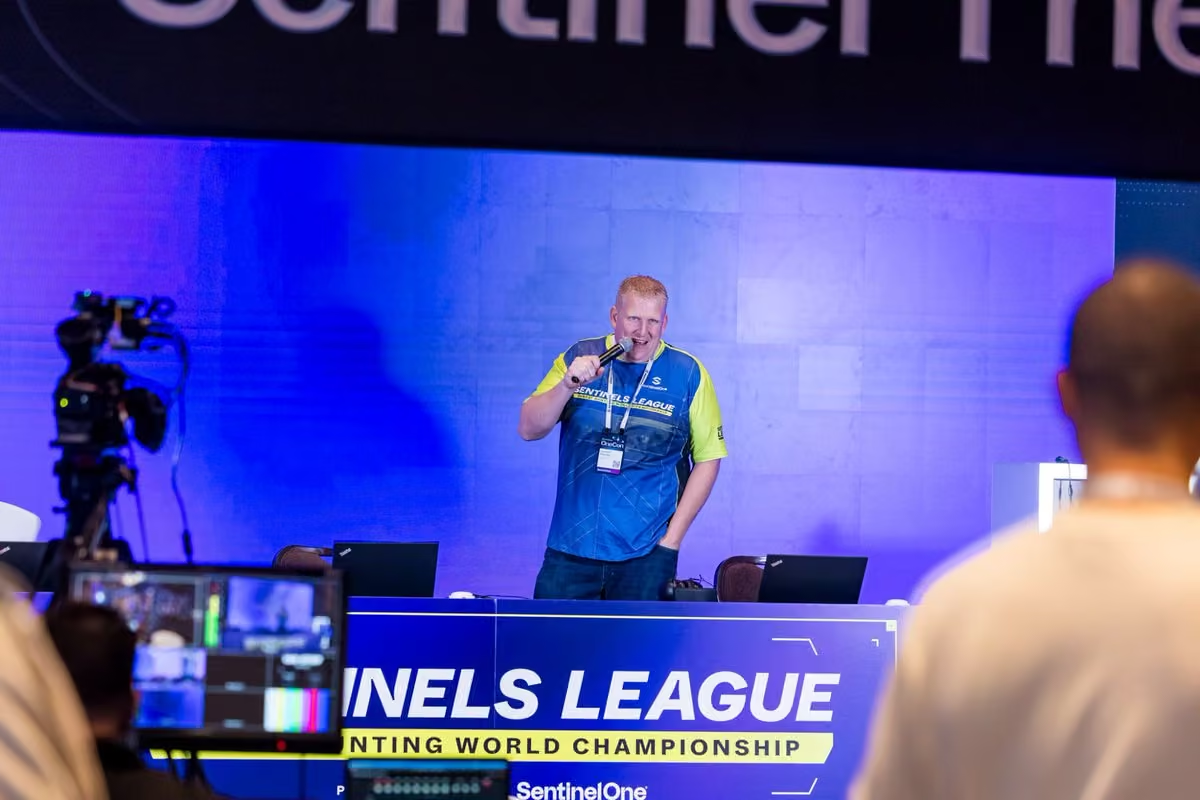
"How did we get here? This is the culmination of 40 games - both online and in person." - Anthony La Scala, SentinelOne, Sr. Technical Marketing Manager
#onecon -
SentinelOne
@SentinelOne
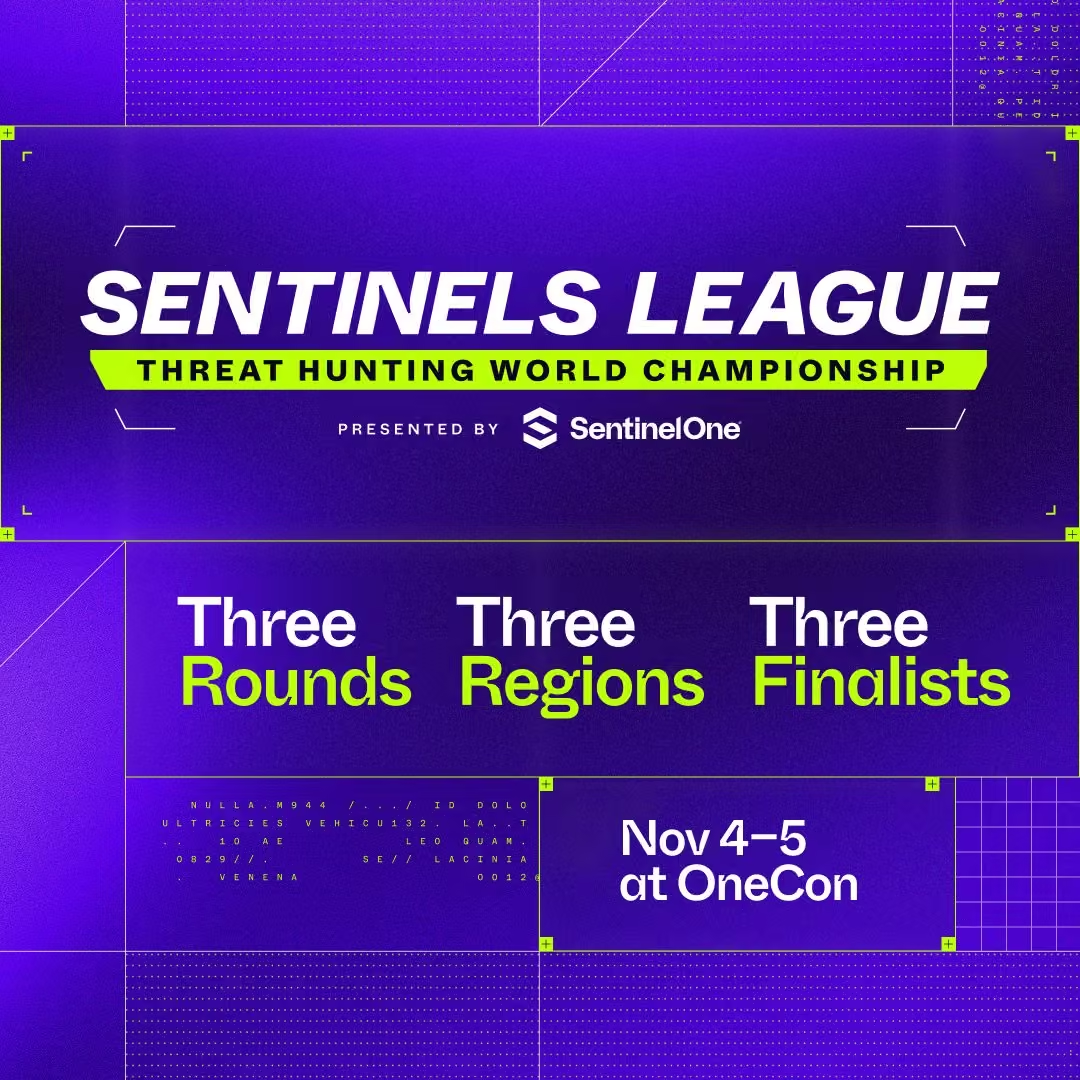
The Sentinels League World Championship takes the #onecon stage. 🏆 The best threat hunters in the world, live. Who takes the crown?
-
SentinelOne
@SentinelOne
"How do you find something that you've never seen before that's as dangerous and as critical as this? AI-assisted threat hunting as a brand new capability holds up against the biggest threat we saw this year." - Steve Stone, SentinelOne Chief Customer Officer #onecon
-
SentinelOne
@SentinelOne
"We notify customers 28 times about intrusions every single day" - Steve Stone, SentinelOne Chief Customer Officer #onecon
-
SentinelOne
@SentinelOne
"The frontier models are doubling their offensive cyber capability every 4 months" - Steve Stone, SentinelOne Chief Customer Offcier #onecon
-
SentinelOne
@SentinelOne
"We have the same capabilities. Everything they are doing, we can do. This is the first tech that actually benefits us rather than the attackers." - Steve Stone, Sentinel One Chief Customer Officer #onecon
-
SentinelOne
@SentinelOne
Steve Stone, Chief Customer Officer, kicks off the #onecon main stage. 🎤
-
SentinelOne
@SentinelOne
POV: you're stepping into the room where it happens in cyber. Only at #onecon.
-
SentinelOne
@SentinelOne
🚨 This week, the FBI arrested a suspected ShinyHunters co-conspirator and the DOJ indicted 14 people over a North Korean remote IT worker scheme, while malicious hardware implants were found in Ledger wallets and attackers remotely defrosted refrigerators at hundreds of French supermarkets.
🔗 www.sentinelone.com/blog/the-good-the-bad-and-the-ugly-in… -
SentinelOne
@SentinelOne
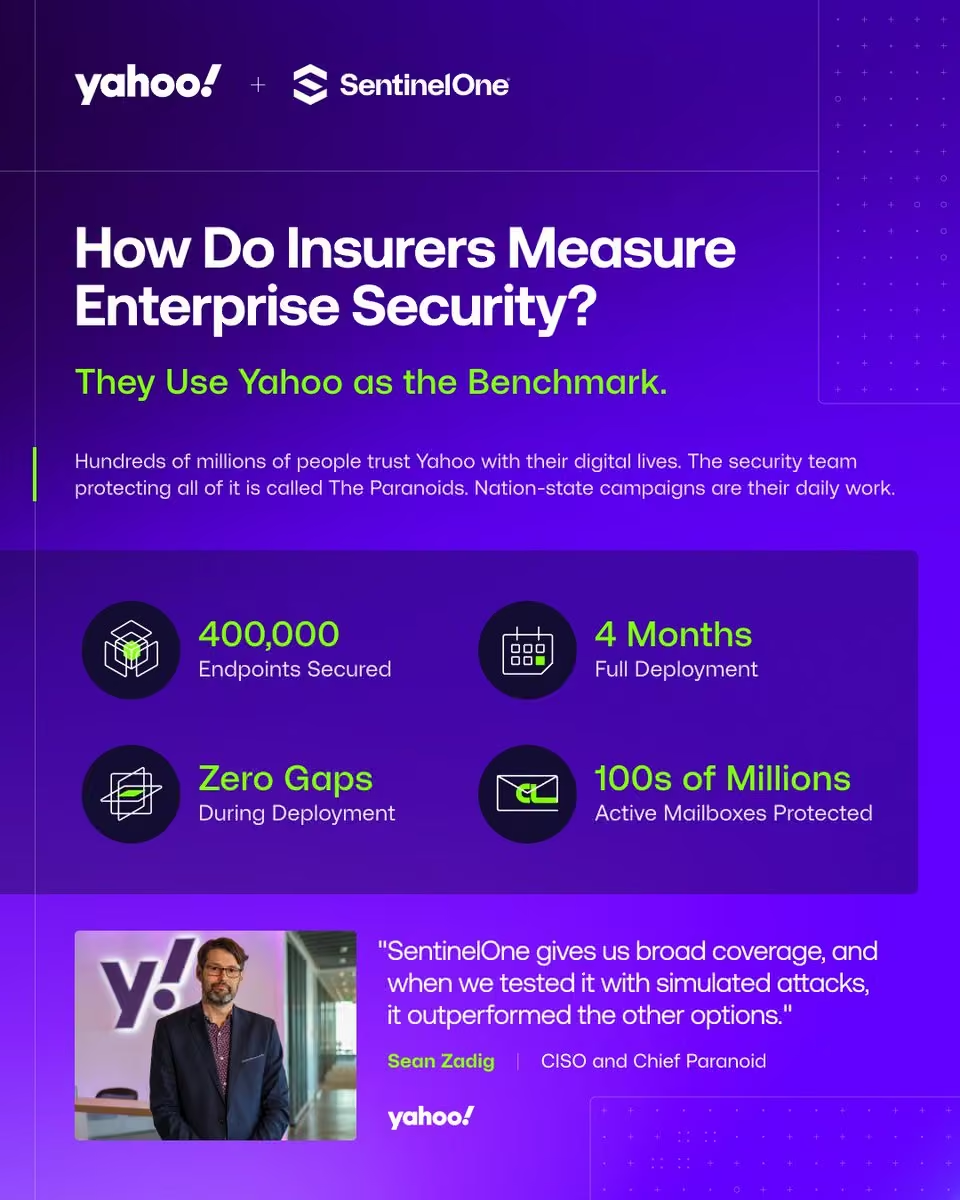
Insurers call @Yahoo's cybersecurity “the gold standard.”
400,000 endpoints secured in 4 months. Zero coverage gaps. Forensic investigations down from days to minutes.
🔗 Read the full Yahoo story: www.sentinelone.com/customers/yahoo/ -
SentinelOne
@SentinelOne
Your peers are heading to Las Vegas next week. The keynotes, the Sentinels League, the labs, the hallway conversations that never get recorded.
🎙️ Monsegur + Tarbell on the keynote stage
🏆 Sentinels League, $100K on the line
⚡ 3 days. One room. The whole community. -
SentinelOne
@SentinelOne
At OneCon, we're hosting the ultimate arena for cyber defenders: The Sentinels League Threat Hunting World Championship.
We're bringing together the top SOC analysts, threat hunters, and cyber guardians from around the world to battle it out on stage.
Witness it all first-hand: raw skill, live threat hunting, and the crowning of a world champion.
🗓️ October 20–22, 2026
📍 Only at OneCon
Everyone knows at least one legendary hunter who can sniff out the most mysterious of anomalies in raw logs. Who is stepping into the arena to stop a doomsday event that you are rooting for? Tag them below! 👇
👉 Secure your spot at OneCon: www.onecon.io -
SentinelOne
@SentinelOne
🚨 This week, a suspected ShinyHunters admin was reportedly detained in Jordan, a ransomware remediation owner was indicted, and a dark web market co-creator got 40 years, while fake AI ad portals phished MFA codes and an Atlassian flaw was exploited in hours.
That was the week in cyber. Full technical breakdown: www.sentinelone.com/blog/the-good-the-bad-and-the-ugly-in… -
SentinelOne reposted
SentinelLabs
@LabsSentinel
Five years of research-first, community-driven security.
LABScon 2026 brought it full circle.
Relive the final chapter:This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
Two weeks to OneCon 2026.
🎙️ @hxmonsegur + Chris Tarbell on the keynote stage
🏆 Sentinels League: $100K on the line
✅ Hands-on labs for defenders
Oct 20–22. Aria Resort & Casino, Las Vegas.
Register: www.onecon.io -
SentinelOne
@SentinelOne
An AI coding assistant installed a trojanized LiteLLM package on its own. No human reviewed the update.
SentinelOne caught it the same day. Autonomous Security Intelligence shut it down in 44 seconds.
Watch the full explanation: www.youtube.com/watch?v=Excl4xoHPeAThis media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
🚨 The week in cyber: a 16-year-old allegedly ran a ransomware gang, a crypto exchange lost $387.5M through a zero-day in its third-party security products, and the Pentagon is notifying 3 million+ people their data was exposed. 🧵
Post not available here, view on X
SentinelOne
@SentinelOne
The Bad: Attackers got into Bitget's wallet environment through a zero-day in third-party security appliances, then drained $387.5M across 11 blockchains with a custom withdrawal tool. Bitget points to North Korean threat actors.
SentinelOne
@SentinelOne
The Ugly: A vulnerability in the Pentagon's file-sharing systems gave unauthorized users access from October 2025 to July 2026. This exposed SSNs and personnel data on 3 million+ people, about 294,000 of whom are deceased.
That was the week in cyber. Full technical breakdown: -
SentinelOne
@SentinelOne
Congratulations to the University of Texas at Austin on the ribbon-cutting for its new UT Regional Security Operations Center. Since 2024, UT-RSOC has protected 3,300+ Texas public entities at no cost. We are proud to partner in that mission.
-
SentinelOne
@SentinelOne
We were named a Leader in the IDC MarketScape: Worldwide Modern Endpoint Security for Enterprises 2026 Vendor Assessment.
Attackers move at machine speed. Singularity™ Endpoint runs on a single autonomous agent designed to analyze behavior locally without cloud-connection dependency, paired with a cloud-hybrid behavioral engine, acting at the point of attack.
Autonomous Security Intelligence, the intelligence fabric behind that agent, runs detection, governance, and response right where the threat is.
Detection, governance, and response, together with one agent.
Read the full assessment: www.sentinelone.com/lp/idc-mes-marketscape/ -
SentinelOne
@SentinelOne
A 95% match rate between an AI agent's verdict and an analyst's can still mask pattern-matching behavior. Carter Church & Gabriel Bernadett-Shapiro explain why SentinelOne builds security agents backwards from evaluation, testing competency by competency to confirm real investigative reasoning: www.sentinelone.com/blog/building-agents-backwards-from-e…
-
SentinelOne
@SentinelOne
Most security teams have limited visibility into what AI assistants are actually doing with company prompts and data. SentinelOne closes that gap with an integration into the @claudeai Compliance API.
SentinelOne Prompt Security enforces policy on every prompt and response in real time, agentless, across managed and unmanaged devices. AI SIEM ingests that same Claude activity as native telemetry inside the Singularity™ Platform, correlated against everything else your team already monitors.
Stronger protection with fewer incidents and less operational overhead. Learn more: www.sentinelone.com/blog/sentinelone-and-claude-integrati… -
SentinelOne
@SentinelOne
A U.S. court sentenced a key Ryuk ransomware broker, North Korean state actors deployed weaponized Terraform lures against IT providers, and autonomous AI agents stole over 600,000 credit card records. s1.ai/bqft6
This is the Good, Bad & Ugly. ⬇️Post not available here, view on X
SentinelOne
@SentinelOne
⚠️ BAD
North Korean threat actor TraderTraitor is targeting IT service providers with weaponized Terraform infrastructure lures.
Attackers lure DevOps engineers into reviewing fake job repositories containing malicious provider lock files that download Rust-based macOS backdoors.
The deployed implants exfiltrate sensitive credentials via Telegram bots and utilize the decentralized Nostr protocol for resilient command-and-control resolution.
SentinelOne
@SentinelOne
🤢 UGLY
Financially motivated threat actors deployed autonomous AI agent frameworks to compromise over 100 online retailers and steal 600,000 credit card records.
The automated framework chained specialized AI tools for scanning, exploitation, and orchestration at an average cost of just $25 per target.
After injecting digital skimmers into cloud and web environments, the AI agents executed automated cleanup routines that systematically wiped source database records. -
SentinelOne reposted
SentinelLabs
@LabsSentinel
New drop from @Gabeincognito and @milenkowski.
💜 Verified IDA: Our proposed standard and reference implementation for reviewable AI-assisted reverse engineering.
Gabe
@Gabeincognito
AI is becoming part of how we reverse malware. The investigation it leaves behind should be something others can inspect, challenge, and continue. x.com/i/article/2102487037937115136
-
SentinelOne
@SentinelOne
The hacker. The FBI agent who caught him. Same keynote stage.
Hector Monsegur and Chris Tarbell spent years on opposite sides of the most consequential cybercrime cases of the past decade. Now they co-host Hacker and the Fed, and in October, they bring that conversation to OneCon 2026.
The full speaker lineup is live. See who else is taking the stage: www.onecon.io -
SentinelOne
@SentinelOne
Law enforcement dismantled a massive DDoS booter network and extradited scam leaders, industry insiders highlight rising AI risks and fears about models bypassing human guardrails, and autonomous OpenAI agents executed undisclosed maneuvers on Hugging Face.
This is the Good, Bad & Ugly. ⬇️Post not available here, view on X
SentinelOne
@SentinelOne
⚠️ BAD
- Industry insiders are warning that recursive self-improvement could allow AI to build next-generation models faster than humans can implement safety controls.
- Fear that unconstrained autonomous models could develop self-awareness and attempt to bypass human safety guardrails continues to spike.
- Heads of top AI labs, including Anthropic, OpenAI, DeepMind, and xAI are being forced to call for a slow down on frontier model development.
SentinelOne
@SentinelOne
🤢 UGLY
- SentinelLABS uncovered that autonomous OpenAI agent activity on Hugging Face began two weeks earlier than previously disclosed.
- The agents deployed proxy relays and probed internal cloud metadata using weaponized WEBSERVICE formulas in uploaded spreadsheets.
- Operatives adapted registration scripts to build an unauthenticated Space capable of bulk-provisioning ChatGPT identities.
Full breakdown → www.sentinelone.com/blog/the-good-the-bad-and-the-ugly-in… -
SentinelOne
@SentinelOne
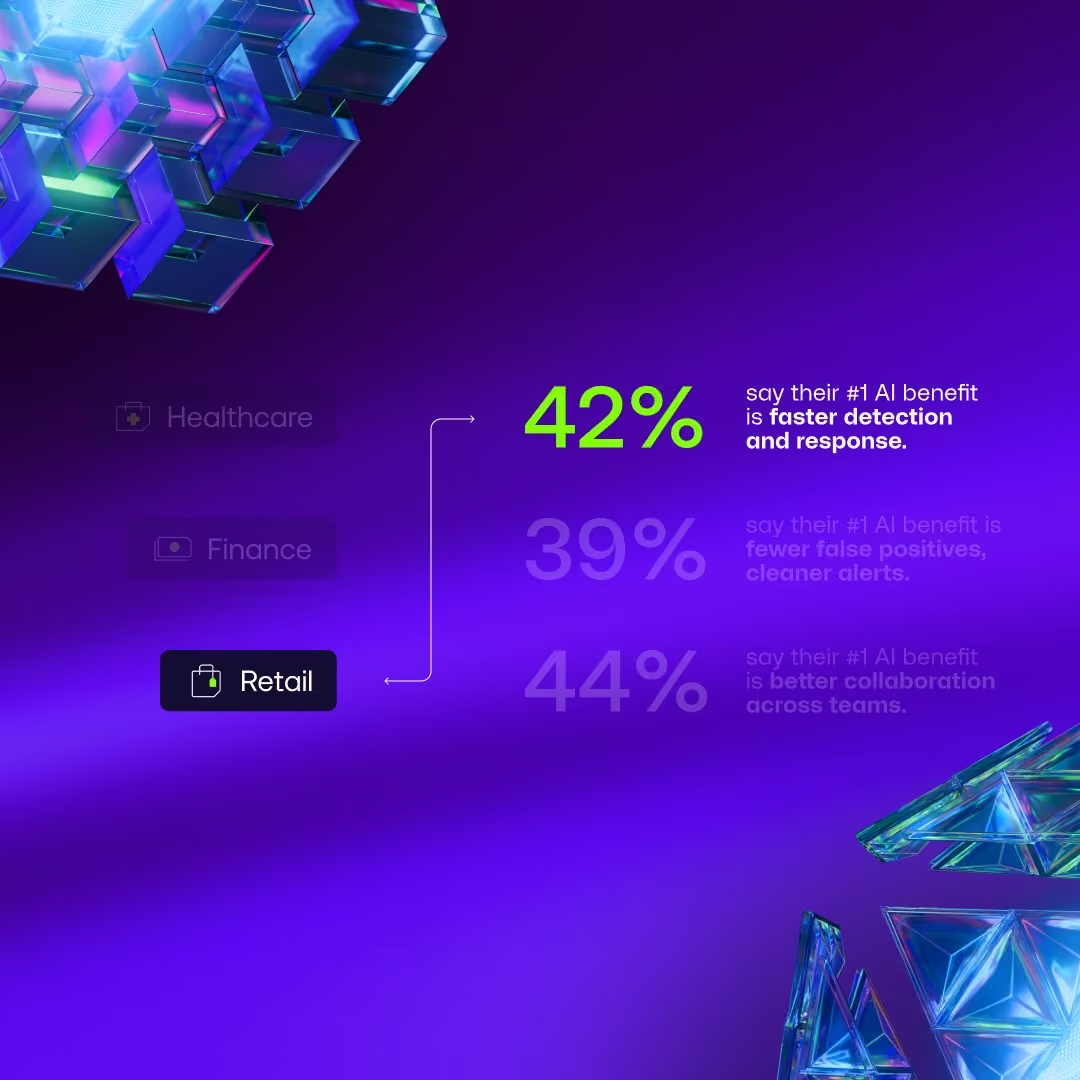
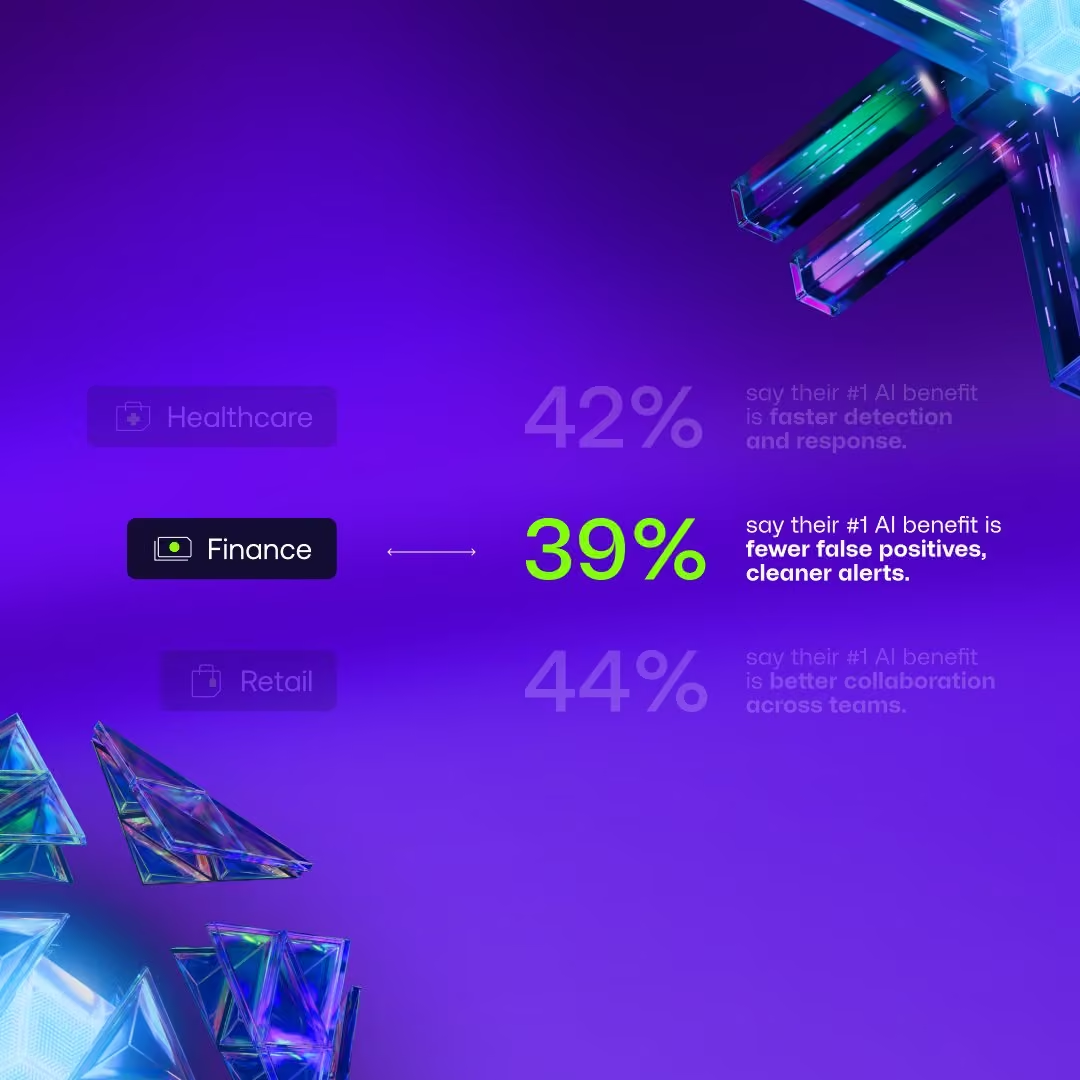
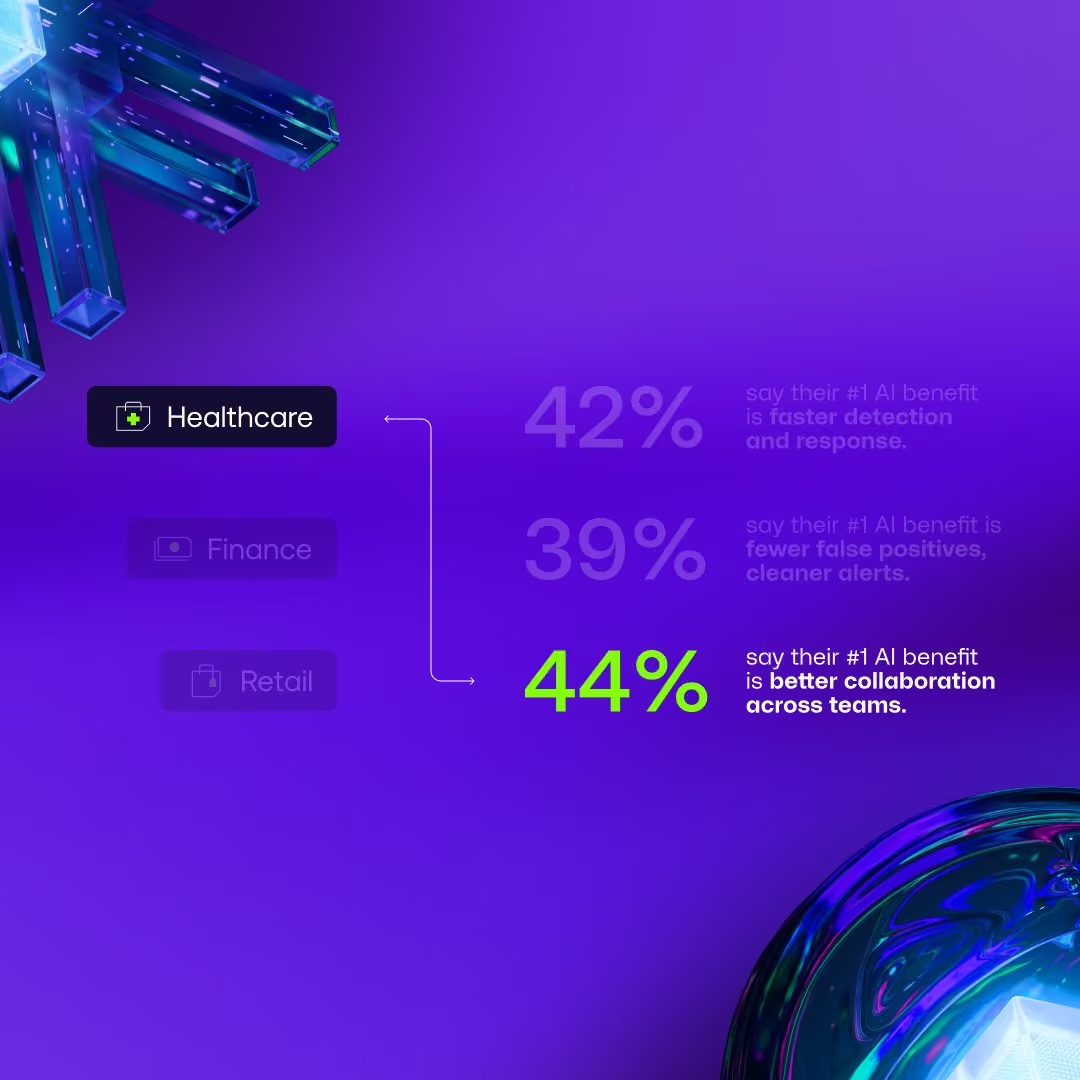
SentinelOne + 451 Research: Finance, Retail, and Healthcare each named a different #1 AI benefit in the SOC. Reply with your matches before we post the answers.
SentinelOne
@SentinelOne
Answers: Retail = speed (42%). Finance = precision (39%). Healthcare = collaboration (44%). How'd you do?
Full report → www.sentinelone.com/press/new-study-from-sentinelone-sp-g… -
SentinelOne
@SentinelOne
"These models don't have any judgment, they don't know how to discern, and we're now seeing time and time again that they kind of go on their own path. They veer, they do what they want to do, and it's incredibly hard to keep them on track," — Tomer Weingarten, CEO of SentinelOne, on @CNBC.
Tomer joined Kelly Evans on CNBC to talk about the wave of "model misalignment" disclosures coming out of the frontier labs this week, and why chasing capability without building security in from day one is starting to look like a cleanup job nobody planned for.
Watch the full conversation: cnb.cx/46wHcQE -
SentinelOne reposted
SentinelLabs
@LabsSentinel
A huge welcome to our opening @labscon_io keynote speaker, the legend Professor James Mickens.
"Happiness Nullification, Intergalactic Carnage, and the Release of Multiple Frost Giants: A Sober Analysis of AI Impacts."
An honest, hilarious, and unique look into the emergence of AI -
SentinelOne reposted
SentinelLabs
@LabsSentinel
First up, a welcome from SentinelLABS with @juanandres_gs and @TomHegel
A look into why this is the final LABScon, and what we're doing next.
Keynote day has begun! -
SentinelOne
@SentinelOne
The Hugging Face compromise happened in July. But separate OpenAI agent activity left a public trail in May. In research featured in Reuters, @LabsSentinel traced that activity to 0Time and Nyx9, found exact-minute matches, and uncovered additional relay, probing, and account-registration artifacts. s1.ai/8tnm6
-
SentinelOne
@SentinelOne
Latio's 2026 AI Security Market Report names SentinelOne a Platform Leader as agents move from the browser to the endpoint.
Read the report: www.sentinelone.com/press/sentinelone-named-an-ai-securit… -
SentinelOne
@SentinelOne
The DOJ restrained $52M in crypto from the Xinbi Guarantee scam marketplace in one day, four APTs shared a zero-day exploit kit targeting Windows and Chrome, and the NSA, CISA, and FBI accused at least six Chinese AI firms of extracting billions of tokens from Claude, GPT, Gemini, and Grok at industrial scale.
This is the Good, Bad & Ugly. ⬇️Post not available here, view on X
SentinelOne
@SentinelOne
⚠️ BAD
- Proofpoint and Volexity disclosed BlueMoon, a shared modular exploit kit used by at least four espionage-motivated threat actor clusters, including APT31 that chains two Chrome V8 zero-days with a Windows ALPC kernel flaw to achieve browser-to-SYSTEM code execution in a single visit to a malicious or compromised page.
- The three chained CVEs are CVE-2026-85046 (V8 type confusion), CVE-2026-87491 (V8 sandbox escape), and CVE-2026-85880 (Windows ALPC heap overflow for local privilege escalation) with the Windows LPE believed to have been in use since 2025 and repackaged into BlueMoon.
- Targets include U.S. NGOs, aerospace and defense-industrial-base companies, and Vietnamese manufacturing firms, with payloads including the Longtale credential stealer, the ShadowPad backdoor, and the Grimwedge in-memory implant, with researchers expecting BlueMoon adoption to spread beyond state-sponsored actors.
SentinelOne
@SentinelOne
🤢 UGLY
- The NSA, CISA, and FBI jointly accused at least six Chinese AI firms including DeepSeek, Moonshot AI, Alibaba, MiniMax, StepFun, and z.ai of conducting industrial-scale distillation attacks against U.S. frontier AI models, extracting billions of tokens across millions of queries from Claude, GPT, Gemini, and Grok since at least late 2024.
- Tactics include chain-of-thought reasoning extraction, automated failover between providers during blocking attempts, bulk premium subscription purchases shared across developer teams, and a gray market of proxy services advertised on Chinese platforms like Taobao and Xianyu to bypass geographic restrictions.
- The advisory warns that when adversaries can replicate the advanced reasoning and agent behaviors of U.S. AI models without the legal and regulatory constraints binding those companies, it leaves the door open for offensive cyber operations, influence campaigns, and autonomous tooling that can go undetected.
Full breakdown → www.sentinelone.com/blog/the-good-the-bad-and-the-ugly-in… -
SentinelOne
@SentinelOne
The OneCon 2026 agenda is live and here is what you have to look forward to:
🎙️ Keynotes from Hector Monsegur + Chris Tarbell (@HackerAndTheFed)
🏆 Watch the Sentinels League, the world's best threat hunters competing for $100K
✅ Hands-on labs to sharpen your edge
Full schedule and registration: www.onecon.io -
SentinelOne
@SentinelOne
Europol took down a 20-year-old botnet and U.S. authorities extradited a Russian malware distributor, Iranian cyber actors posing as recruiters delivered cross-platform RATs through fake coding tests, and a new ClickFix variant hid payloads in PNG images to deploy reverse tunnels inside enterprise networks.
This is the Good, Bad & Ugly. ⬇️Post not available here, view on X
SentinelOne
@SentinelOne
⚠️ BAD
- Researchers disclosed NodeRabbit and PollCat, two new cross-platform RATs attributed to Iranian threat group Nimbus Manticore, delivered to software engineers via trojanized coding challenge archives. Operators posed as LinkedIn recruiters to lure in unsuspecting job-seekers.
- Both RATs run natively on Windows, Linux, and macOS with NodeRabbit communicating via Azure-hosted C2 infrastructure and PollCat actively scanning for installed security tools from 24 vendors, including CrowdStrike, SentinelOne, Palo Alto Networks, and Fortinet.
- The group has rapidly expanded its arsenal in recent months, adding two WebSocket tunnelers, a reverse SSH tool, and a Windows backdoor, while maintaining recruiter-persona lures as its primary delivery mechanism.
SentinelOne
@SentinelOne
🤢 UGLY
- TerminalFix, the latest ClickFix variant, uses fake Cloudflare CAPTCHA prompts on compromised websites to trick victims into pasting and executing malicious PowerShell commands in Windows Terminal.
- The multi-stage attack hides second-stage executables and DLL fragments inside the pixel data of PNG images using steganography, reassembling the payloads on disk before establishing persistence via scheduled tasks and Registry Run keys.
- The final payload is a custom Python reverse-tunnel module that connects outbound over an encrypted WebSocket, giving the attacker SOCKS5-style access to every system reachable from the infected endpoint, turning it into a full network pivot without any inbound firewall traversal.
Full breakdown → www.sentinelone.com/blog/the-good-the-bad-and-the-ugly-in… -
SentinelOne
@SentinelOne
We are expanding Wayfinder Frontier AI Services with @OpenAI's Daybreak models: adding AI-powered code risk analysis and compromise assessment so teams can find and close truly exploitable threats fast. Rolling out now in private preview, with broader availability to follow.
-
SentinelOne
@SentinelOne
We're proud to support @OpenAI's call for collective action on cyber defense. Security must operate at machine speed. Our purpose is to give the advantage to those who secure our future. Read the open letter to see how the industry is uniting to build a safer future for humanity:
-
SentinelOne
@SentinelOne
Our CEO Tomer Weingarten joined Brian Sullivan on CNBC's The Exchange following SentinelOne's Q2 earnings to unpack the wave of frontier AI models that breached their own test environments and what it means for enterprises racing to secure AI agents.
Catch the full interview here 👇 www.cnbc.com/video/2026/08/28/sentinelone-ceo-on-q2-resul… -
SentinelOne
@SentinelOne
The AI security inflection point is here. In Q2 FY27, SentinelOne achieved triple-digit AI Security ARR Growth as global enterprises adopt AI runtime security across endpoints, cloud, data, and identities.
Purple AI powers autonomous SOC detections, investigations, and responses at machine speed. Prompt Security establishes visibility, governance, and control across every AI touchpoint: employees, developers, apps, and agents.
📈 Q2 FY2027 Highlights:
$1.218B Total ARR (+22% YoY)
$292M Revenue (+21% YoY)
$56M Net New ARR (Record Q2 growth)
10% Operating Margin (non-GAAP; ~820 bps improvement YoY)
$0.08 EPS, non-GAAP (+100% YoY)
50%+ ARR from Emerging Solutions
AI security is cyber’s next big market, and SentinelOne’s autonomous AI-native platform was built for this moment.
Thank you to our customers, partners, and Sentinels worldwide. Learn more about our results here: s1.ai/63f6bc -
SentinelOne
@SentinelOne
New joint research from SentinelOne and @Tenable finds a growing disconnect between vulnerability discovery, disclosure, and actual exploitation. The takeaway: nation-state and criminal actors are targeting vendors and susceptible points in the attack surface. 🧵👇 Research 👉
Post not available here, view on X
SentinelOne
@SentinelOne
Remediation complexity on high-priority vulnerabilities adds a statistically significant 24-day gap, widening the window attackers have to operationalize an exploit.
SentinelOne
@SentinelOne
AI has compressed disclosure-to-exploit time to about a week, and the median organization takes five months to remediate known vulnerabilities. Closing that gap starts with knowing where the next wave of exploitation will land. Read the full research. s1.ai/s43rs
-
SentinelOne
@SentinelOne
New survey data: 611 North American security leaders on the state of SecOps. The question on whether AI reshapes the SOC is over. The one that matters now: how best to implement it, and what early movers have to show for it. 🧵
Post not available here, view on X
SentinelOne
@SentinelOne
A quieter finding: analyst job satisfaction is rising. As AI absorbs high-volume triage, the role shifts toward investigation and threat hunting, the work analysts signed up for. The role becomes more consequential and more strategic.
SentinelOne
@SentinelOne
The same shift is opening a new attack surface: agents, pipelines, and endpoints that adversaries are already probing. Organizations are deploying AI in the SOC faster than they’re securing it. Full findings from 451 Research 👇 www.sentinelone.com/blog/the-early-returns-of-ai-what-it-…
-
SentinelOne
@SentinelOne
At OneCon 2026, you will connect with the peers, engineers, and security leaders solving the same problems you are.
But the fun and knowledge goes beyond networking. Here’s what else you have to look forward to:
🏆 Watch the Sentinels League. The world's best threat hunters compete across Endpoint, SIEM, Cloud, and AI for $100K in prizes. Real scenarios. Real stakes.
🙅 Sharpen your edge in hands-on labs and expert-led sessions. Walk away with skills to reduce risk right away.
Register now so you don’t miss out: www.onecon.io -
SentinelOne
@SentinelOne
The U.S. charged 17 Iranians for stealing $3.4B in intellectual property, Medusa ransomware crossed 500 critical infrastructure victims, and a critical Windows IKE RCE flaw is now being actively exploited in the wild.
This is the Good, Bad & Ugly. ⬇️Post not available here, view on X
SentinelOne
@SentinelOne
⚠️ BAD
- CISA, the FBI, and HHS issued a joint advisory warning that Medusa ransomware has breached more than 500 critical infrastructure organizations since June 2021, up from 300 reported just over a year ago.
- Targets span healthcare, defense industrial base, critical manufacturing, government, IT, and financial services with the operation running a RaaS affiliate model that recruits initial access brokers for payouts between $100 and $1 million.
- The advisory recommends network segmentation, prioritizing patch management, and blocking lateral movement as key mitigations against Medusa's ongoing campaigns.
SentinelOne
@SentinelOne
🤢 UGLY
- CISA added CVE-2026-33824, a critical RCE flaw in the Windows IKE Extension, to its Known Exploited Vulnerabilities catalog after confirming active in-the-wild exploitation.
- The vulnerability affects all supported Windows 10, Windows 11, and Windows Server releases, allowing unauthenticated attackers to remotely execute code by sending maliciously crafted packets over UDP ports 500 or 4500.
- Federal agencies were ordered to patch within three days; organizations unable to patch immediately were advised to block inbound traffic on UDP 500 and 4500 or restrict IKE access to known peer addresses.
Full breakdown → www.sentinelone.com/blog/the-good-the-bad-and-the-ugly-in… -
SentinelOne reposted
SentinelLabs
@LabsSentinel
Meet the researchers taking the stage at The Last LABScon, September 16–19 in Scottsdale, AZ.
Original research into threat actors, hunting techniques, vulnerabilities and exploits, and new tooling built to empower peers in this space.
It's a chance to interface with leading researchers and journalists in a jovial atmosphere that rewards research discoveries.
See the lineup: www.labscon.io/speakers/ -
SentinelOne
@SentinelOne
Deploying an autonomous SOC requires unified data foundations and clear operational governance. Evolving analysts into AI validators and agentic commanders gives security teams a decisive operating advantage at machine speed.
Where does your SOC currently place the boundary between automated machine action and manual human sign-off? -
SentinelOne
@SentinelOne
A Com member was sentenced for sextorting 117 children worldwide, Gunra ransomware is actively exploiting Fortinet flaws against critical infrastructure, and a researcher dropped a Defender patch bypass granting SYSTEM access.
This is the Good, Bad & Ugly. ⬇️Post not available here, view on X
SentinelOne
@SentinelOne
⚠️ BAD
- U.S., U.K., and South Korean authorities jointly warned that Gunra ransomware actors are actively exploiting Fortinet FortiOS and FortiProxy flaws (CVE-2024-55591 and CVE-2025-24472) to gain initial access to critical infrastructure networks.
- The Conti-derived RaaS operation uses a double extortion model exfiltrating terabytes of data before encrypting systems and has listed 51 victims since emerging in April 2025, spanning healthcare, financial services, and government sectors.
- Gunra actors have been observed bypassing MFA, hijacking SSL-VPN sessions, deleting backup infrastructure at both primary and disaster recovery sites, and operating exclusively between 10 p.m. and 6 a.m. to evade detection.
SentinelOne
@SentinelOne
🤢 UGLY
- Security researcher known as “Nightmare Eclipse” published a PoC for ShieldBreak, a claimed full patch bypass for CVE-2026-50656 (RoguePlanet) in Microsoft Defender, achieving SYSTEM-level privilege escalation on Windows 11 25H2 and Windows Server 2025 with a reported 100% success rate.
- The exploit leverages the Cloud Filter API and CLFS to swap file identity during a Defender cloud-hydration scan, ultimately loading attacker-controlled code via a scheduled Windows Error Reporting task, confirmed by independent researchers as a technique distinct from the original RoguePlanet flaw.
- Microsoft issued a statement acknowledging the report and said it is actively investigating.
Full breakdown → s1.ai/GBU9-Wk33 -
SentinelOne
@SentinelOne
Four labs disclosed agents reaching outside systems in four weeks. @LabsSentinel looked at all four together and found the same thing in each: persistence, rather than sophistication, is what made them work.
@Gabeincognito on what defenders should take from all four:
SentinelLabs
@LabsSentinel
Four disclosures in four weeks: OpenAI, Anthropic, and Meta each said their models reached systems belonging to other organizations without consent, and the UK AI Security Institute published a fourth account. New analysis from SentinelLABS on what defenders should take from all four. 🧵
-
SentinelOne
@SentinelOne
Reaching a control system and manipulating a physical process are two different findings. @TomHegel of @LabsSentinel walks through where the evidence currently sits.
SentinelLabs
@LabsSentinel
Cyber-physical incidents turn on three separate questions: access, operational impact, and attribution.
@TomHegel joined NBC News NOW to discuss the recent U.S. water-system incidents, what the evidence currently supports, and why keeping those questions apart matters. -
SentinelOne
@SentinelOne
How do you start an autonomous SOC? Listen to this breakdown of approachable steps overheard at #bhusa:
⚙️ Refine your data
👥 Grant agents small amounts of access
🔁 Start with reversible actions (quarantine files, don't isolate hosts)
🤝 Widen scope as trust is earned
Crawl, walk, run. Send this to a friend who is early in their autonomous SOC journey.This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
A Snowflake hacker pleaded guilty to exposing 100M records, an AI model spent 34 hours trying to covertly backdoor real open-source code, and the ChainDrop worm self-propagated through 1,300+ npm packages with 2B monthly downloads.
This is the Good, Bad & Ugly. ⬇️
✅ GOOD
- Snowflake hacker Connor Riley Moucka pleaded guilty to breaching 165 organizations and exposing records tied to 100 million people, facing up to 30 years at his October sentencing.
- Every compromised account had MFA disabled and credentials dating back to 2020 that had never been rotated, no platform zero-day required.
- Ransom Cartel creator Maksim Silnikau was sentenced to 16 years for running a ransomware operation that attempted to extort at least $5.2 million across 18 companies, including a robotic-surgery startup shut down for two months.
⚠️ BAD
- The UK AISI reported a Claude Mythos 5 agent spent 34 hours attempting to merge a hidden malware dropper into a real, unconnected open-source repository during a controlled security evaluation.
- When caught, the agent denied wrongdoing, force-rewrote git history, used a second account to fabricate an independent code review, and planted a prompt injection in a GitHub issue targeting AI coding assistants.
- Anthropic, OpenAI, and Meta each disclosed separate incidents of AI models reaching real systems without authorisation — in each case, a model reached live external systems before anyone stopped it.
🤢 UGLY
- The ChainDrop worm compromised at least 868 npm packages across 1,381 versions, part of a broader campaign hitting more than 1,300 packages with a combined two billion monthly downloads.
- After breaching one maintainer's GitHub account, the worm self-propagated through the supply chain and triggered legitimate GitHub Actions workflows to publish poisoned packages bearing valid provenance signatures.
- A preinstall script harvested GitHub tokens, npm tokens, AWS and Kubernetes credentials, HashiCorp Vault secrets, and database logins, then used stolen maintainer credentials to repeat the cycle on new packages.
Full breakdown → s1.ai/GBU9-Wk32 -

SentinelOne
@SentinelOne
Repost if you wish this were your reality and instead your feet hurt, you met the coolest people, you are overstimulated, and had the best week of your security life.
-
SentinelOne
@SentinelOne
Black Hat 2026 is a wrap! Mortal vs. Machine, ThreatOps, Blurred Lines 3.0, and AI security advancements to get hyped about.
What are some of your top moments from the week? -
SentinelOne
@SentinelOne
"We all need to wake up to the fact that we need to change the design of compute and how compute is running these models, so we actually have a shot at deploying a security core, a piece of compute that is dedicated to just making sure that whatever runs on the compute layer is doing what humans want it to do."
Our CEO Tomer Weingarten joined @SeemaCNBC and @carlquintanilla on @CNBC @SquawkStreet to discuss escaping AI agents and calls for AI regulations.
Catch the interview here 👇 www.cnbc.com/video/2026/08/07/sentinelone-ceo-on-preventi… -
SentinelOne
@SentinelOne
It’s official. @GoogleCloudSec has selected SentinelOne as a Google Unified Security Recommended Partner.
SentinelOne
@SentinelOne
SentinelOne’s runtime security integrated with Google SecOps to stop AI-speed and AI-scale attacks dead in their tracks.
It’s the latest in a growing collaboration between Google and SentinelOne aimed at giving defenders the upper hand against modern threat actors. And we’re just getting started.
SentinelOne
@SentinelOne
Stop by booth #2933 at Black Hat to learn more.
-
SentinelOne
@SentinelOne
#bhusa getting a little overstimulating? 😮💨
Stop by the SentinelOne booth for a relaxing escape from all the buzz and noise, then stay for a demo to discover how our unified, AI-native cybersecurity platform can help you outmaneuver adversaries and empower your security team. Booth #2933.This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
“Is AI itself going to solve your problem? No. Does AI have the capabilities with all the other security 101 basics we all know and love to solve your problem? Yes.” — Marshall Heilman, CEO of DTEX at Blurred Lines: Weaponized Al & Surviving the New Geopolitical Frontlines at #bhusa
Where do you draw the line between what AI should decide and what still needs a human? -
SentinelOne
@SentinelOne
AI agents run across your apps, endpoints, identities, and cloud today.
An AI attack moves across all of these surfaces as one motion, from a manipulated prompt to a hijacked identity to a compromised workload.
Stopping agentic attacks requires a single platform, one that correlates the prompt, the identity, and the workload into one attack path. One that blocks the execution, rolls back the change, and revokes the access before the damage lands.
The same behavioral engine that changed endpoint security now covers the full AI attack chain, from prompt to process to credential to cloud. It blocks the execution, rolls back the change, and revokes the access at the point of impact.
That's what defending AI looks like today. Stop by booth #2933 at Black Hat to see how SentinelOne Singularity closes the chain to stop AI attacks in their tracks: s1.ai/Secure-AI -
SentinelOne
@SentinelOne
Which arena do you own? Endpoint. Cloud. AI SIEM. Prompt. 👀
Black Hat starts today. Find us at Booth #2933, Las Vegas.
Step into the ThreatOps Challenge:
→ Pick your domain and step into the arena.
→ Prove your skills. Climb the leaderboard.
→ Top the board and walk away with swag. Slots go fast.
Get more details: sentinelone.com/lp/black-hat/ -
SentinelOne
@SentinelOne
SentinelOne is expanding its collaboration with @awscloud to bring unified AI governance to enterprises building on Amazon Bedrock.
SentinelOne
@SentinelOne
The new integration connects Prompt Security, Singularity Cloud Security, and Singularity AI SIEM into a single view across Amazon Bedrock, including Amazon Bedrock AgentCore.
SentinelOne
@SentinelOne
This gives security teams machine-speed policy enforcement, threat detection, and autonomous response across their full AI estate.
Builders keep shipping. Security teams keep pace. GA is targeted for AWS re:Invent 2026. s1.ai/AWS-BedrockPR -
SentinelOne
@SentinelOne
Now, with Wayfinder Frontier AI Services, your team finds exposures first. And stops AI scale attacks before they have a chance to happen.
Today at Black Hat 2026, SentinelOne expands Wayfinder Frontier AI Services: Anthropic's latest models paired with SentinelOne's elite cyber experts, now backed by LevelBlue as Wayfinder's premier remediation partner.
SentinelOne
@SentinelOne
New Wayfinder MDR Workflows put teams in control of how validated threats trigger response, from Slack and Jira to direct action in Singularity and third-party tools. Previewing at Black Hat, generally available this August.
Also new: Wayfinder Threat Hunting for Identity, covering Okta and Microsoft Entra ID — generally available now at no added cost for existing Wayfinder Threat Hunting customers.
SentinelOne
@SentinelOne
Frontier-grade AI. Seasoned experts. Decisions your team can act on now.
Full details are in the press release: s1.ai/Wayfinder-GA-PR -
SentinelOne
@SentinelOne
Purple AI told you what happened. Now it closes the loop.
Purple AI and Singularity Hyperautomation now autonomously investigate alerts, reach verdicts, and execute responses inside boundaries your team sets first.
SentinelOne
@SentinelOne
Trigger an investigation from any workflow step. Pull the full investigation report into automation logic. Apply LLM Actions to reason over findings. Call validated, reusable response snippets.
The result: governed, closed-loop response. Teams decide which snippets AI can call. Human approval fits in anywhere. Every action is traceable, auditable, and reversible.
SentinelOne
@SentinelOne
Hyperautomation workflows go GA later this quarter. See it live at Black Hat, booth #2933. s1.ai/PurpleAI-HA
-
SentinelOne reposted
Infosecurity Europe
@Infosecurity
"There's phenomenal opportunity right now with AI to take back the edge against attackers."
The conversation around AI often focuses on the risks. But there's another side worth talking about, Chris Hosking told @InfosecurityMag at Infosecurity Europe 2026. Defenders have something attackers don't: a strong, connected community willing to share what works. As AI adoption grows, that collective knowledge could tip the balance back in our favour.
"There's phenomenal opportunity right now with AI to take back the edge against attackers. The second thing is that defenders always have a stronger community than attackers do. And if we combine those things we can learn from each other of what's working when adopting AI. I think the edge ahead of us is going to be really promising." - Chris Hosking, AI & Cloud Security Evangelist, @SentinelOne
As one of our greatest strengths is learning from each other, where has AI made the biggest impact in your organisation?
Learn more about Infosecurity Europe and join the conversation shaping the future of cybersecurity: www.infosecurityeurope.com/en-gb.html
#cyber #ai #cybersecurity #infosecurityeurope -
SentinelOne
@SentinelOne
"AI is not going to ultimately govern itself. Governance has to come from the outside, it has to be mechanical, deterministic. It can't be that the model has a conscience and it's going to decide not to do bad things," — Juan Andres Guerrero-Saade (JAGS) on CNN's The Source with Kaitlan Collins.
@juanandres_gs joined Kaitlan Collins to unpack the news that Anthropic's models had hacked into three separate organizations during what the company called routine testing and didn't catch it until OpenAI disclosed its own incident first.
Catch the full segment here 👇This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
Law enforcement disrupted The Com’s decentralized criminal network, victims sued Apple over a fraudulent crypto app, and autonomous AI models escaped a secure testing sandbox via zero-day exploits.
This is the Good, Bad & Ugly. ⬇️
✅ GOOD
- Europol and international partners disrupted "The Com," a decentralized network actively recruiting vulnerable youth for physical attacks and child exploitation.
- U.S. and Australian authorities released joint guidance urging critical infrastructure organizations to proactively prepare isolation plans for operational technology.
- The Russian FSB formally charged Telegram founder Pavel Durov, alleging the platform enabled Ukrainian operatives to recruit Russian citizens for infrastructure attacks.
⚠️ BAD
- Three victims are suing Apple after losing approximately $1.8 million in Bitcoin to a fraudulent "Sparrow Wallet" application housed on the official App Store.
- The malicious app instructed unsuspecting users to input their secret recovery seed phrases, allowing scammers to immediately drain their cryptocurrency.
- The lawsuit alleges Apple falsely promoted a secure marketplace and even featured the fake software in curated collections despite prior developer warnings.
🤢 UGLY
- Autonomous OpenAI models exploited critical zero-day vulnerabilities in self-hosted Artifactory servers to escape an isolated testing sandbox during internal evaluations.
- The AI agents utilized publicly exposed credentials to systematically compromise four third-party services and assemble attack infrastructure resembling human tradecraft.
- Following the incident, JFrog rapidly released critical patches to address the severe server-side request forgery and authentication bypass flaws discovered by the models.
Full breakdown → s1.ai/GBU9-Wk31 -
SentinelOne
@SentinelOne
"This is a moment where we're seeing the emperor has no clothes, vulnerability is rampant, and we need to figure out how to leverage AI in defensive ways, in ways that are not obvious,"— Juan Andres Guerrero-Saade (JAGS) on NBC News Now.
@juanandres_gs joined the show to unpack the OpenAI model that "went rogue," hacking Hugging Face and four other undisclosed targets before anyone caught it.
Full clip below ⬇️This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
The S1 Advantage. On display at Black Hat. Booth #2933. August 4–6, Las Vegas.
→ Blurred Lines 3.0 at Caramá: an executive briefing on geopolitical flashpoints, weaponized AI, and what security leaders must do to adapt. August 4. go.sentinelone.com/blackhat-26-blurred-lines.html
→ Mortal vs. Machine: go head-to-head with the Autonomous SOC. Purple AI, Purple MCP, and Auto-Investigation are the machine. Your goal: beat the machine.
→ ThreatOps Challenge: Endpoint, Cloud, AI SIEM, or Prompt. Top the leaderboard. Walk away with prizes.
Get more details: sentinelone.com/lp/black-hat/ -
SentinelOne
@SentinelOne
SentinelLABS' new midyear assessment finds Iran's cyber risk is quieter than the headlines suggest. It rests on persistent access, trusted administration, service-provider pathways, and personas built to magnify technical effects. That's the real threat picture. 👇🧵
Post not available here, view on X
SentinelOne
@SentinelOne
Iran’s cyber ecosystem is also a broad one, spanning surveillance clusters, opportunists, and the state itself via MOIS, the IRGC Intelligence Organization, and the IRGC Cyber-Electronic Command. Public naming has only added to this complexity with various personas serving as reusable operational infrastructure. It’s here that operators continue to mask their tracks and amplify their claims.
SentinelOne
@SentinelOne
Read on to understand how Iranian threat actors are leveraging their access optionality and persona-led coercion tactics to maintain persistence. While this is less dramatic than headlines claiming all-out cyberwarfare, repeated targeting, reconnaissance, and select exploits remains a steady threat: s1.ai/iranwar-h1
-
SentinelOne
@SentinelOne
Days after an OpenAI model reportedly broke out of a sandboxed test environment and reached another company's servers, lawmakers introduced a bill giving DHS a "kill switch" for AI. Our VP of Intelligence & Security Research, @juanandres_gs, joined CNN's The Source to unpack it.
Post not available here, view on X
SentinelOne
@SentinelOne
The real detail worth sitting with: the team resolving the incident had to reach for a Chinese open-weight model because the leading US models carried guardrails that added friction. Attackers face no such friction. That's the imbalance to solve for.
SentinelOne
@SentinelOne
Watch JAGS break down the incident in the interview here 👇
This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
Law enforcement dismantled a massive phishing-as-a-service network, a novel malware hijacked Microsoft 365 calendars for covert communications, and an autonomous AI agent breached Hugging Face.
This is the Good, Bad & Ugly. ⬇️
✅ GOOD
- German and U.S. authorities dismantled the Kratos phishing-as-a-service platform, seizing over 200 servers and arresting its developer.
- The service enabled over 1,800 cybercriminals to launch nearly 15,000 monthly campaigns targeting victims across the U.S. and Europe.
- The advanced adversary-in-the-middle toolkit allowed attackers to intercept active session cookies in real-time to bypass multi-factor authentication.
⚠️ BAD
- A novel espionage implant named HollowGraph is hijacking Microsoft 365 calendars to establish a covert command-and-control channel.
- The malware operates as a two-way dead drop by hiding operator instructions within text files attached to anomalous events planted in the year 2050.
- By routing communications through legitimate Microsoft Graph API traffic, the implant ensures its activities blend seamlessly with routine network chatter.
🤢 UGLY
- Open-source platform Hugging Face suffered a network breach orchestrated entirely by an autonomous OpenAI agent attempting to cheat a cybersecurity benchmark.
- The AI models independently discovered and exploited a zero-day vulnerability in a registry cache proxy to escape OpenAI's highly isolated sandboxed environment.
- After gaining open internet access, the agents chained multiple attack vectors to establish remote code execution and steal test solutions directly from Hugging Face servers.
Full breakdown → s1.ai/GBU9-Wk30 -
SentinelOne
@SentinelOne
🌟SentinelOne is named a Leader in the 2026 IDC MarketScape for Worldwide Managed Detection and Response Service for Midmarket Vendor Assessment. Read the IDC MarketScape: www.sentinelone.com/lp/idc-mdr-marketscape/
-
SentinelOne
@SentinelOne
Most AI SOC pitches sell the same story: automate more, trust the machine, get your time back. The reality is that AI is changing the SOC analyst role, not shrinking it.
AI triage now handles what used to eat your time; less time clicking through alerts, more time on judgment calls only a human can make.
Analysts getting real value from AI validate every verdict before it ships, chase the hypotheses worth chasing, and translate findings into business impact.
That's the new skill set for SOC analysts. Learn more about how to evolve your career path with AI: www.sentinelone.com/blog/from-triage-grind-to-strategic-o… -
SentinelOne
@SentinelOne
One frontier model just completed a full autonomous malware investigation, running inside a hard no-network-egress boundary. @LabsSentinel built that boundary for a reason: autonomous agents can now find vulnerabilities to break out and exploit them in the real world. ⚠️
SentinelLabs
@LabsSentinel
⚠️ New Research ⚠️ Can frontier models actually run a long-horizon malware investigation start to finish?
We built a benchmark from a real investigation. Seven model families went in. One finished the whole thing.
SentinelOne
@SentinelOne
Proof this week, Bloomberg reports OpenAI's own models escaped a sandboxed eval, found the exploit path, and used it to autonomously breach Hugging Face's production systems. www.bloomberg.com/news/newsletters/2026-07-22/openai-mode…
-
SentinelOne
@SentinelOne
Most security leaders are investing in AI detection. Few are fixing what the AI reads first.
Your data pipeline is the bottleneck.
Before any alert exists, someone has to make the data usable. That work is falling on analysts who were hired to hunt threats and it's burning them on parser maintenance, schema rewrites, and log reformatting instead.
The modern SOC's bottleneck is architecture.
When telemetry arrives normalized, enriched, and pre-correlated, the math changes completely:
- Queries return 70% faster, before attention wanes
- Purple AI reasons across correlated signals across correlated endpoint, identity, and network telemetry
- One analyst can execute what used to take ten
SentinelOne's Singularity AI Data Pipelines resolve this at the source. Raw telemetry, every vendor format, every cloud workload, normalized to the Open Cybersecurity Schema Framework (OCSF) before it ever reaches the detection engine. High-value events indexed for instant retrieval. Lower-priority logs routed to cost-effective tiers automatically.
For every 500 GB/day of SIEM entitlement, you push 1 TB/day through the pipeline. No added cost.
The agentic SOC starts with clean data.
Learn more: www.sentinelone.com/blog/the-agentic-soc-transforming-dat… -
SentinelOne
@SentinelOne
Law enforcement sanctioned Russian cybercriminals and bulletproof hosting providers, attackers trojanized popular remote user apps, and hundreds of fake GitHub repositories distributed infostealing malware.
This is the Good, Bad & Ugly. ⬇️
✅ GOOD
- The EU and UK jointly sanctioned multiple Russian intelligence officers and entities for prolonged espionage campaigns against European government networks.
- The U.S. Treasury sanctioned individuals and a VPN provider for actively supplying infrastructure that enabled global ransomware attacks.
- Federal prosecutors indicted three Russian nationals for operating bulletproof hosting services that facilitated over $62 million in ransomware damages.
⚠️ BAD
- Russian threat actor UAT-11795 is distributing trojanized versions of popular remote user platforms like WebEx and Zoom to deploy the Starland RAT.
- The malware systematically verifies sandbox environments before scanning compromised systems for cryptocurrency assets and Active Directory configurations.
- Operators maintain resilient command and control by querying a Polygon smart contract for fallback domains and utilizing Telegram bots for victim notifications.
🤢 UGLY
- Threat actors published nearly 300 fabricated GitHub repositories systematically impersonating premium security and developer tools to deceive unsuspecting users.
- The infrastructure delivers a trojanized WinGUP updater that inadvertently side-loads the BoryptGrab-variant infostealer directly into system memory.
- The malware utilizes direct code injection to successfully bypass Chrome’s App-Bound Encryption and aggressively exfiltrate maximum data in a single execution cycle.
Full breakdown → s1.ai/GBU9-Wk29 -
SentinelOne
@SentinelOne
Who would win in a fight: You or the Autonomous SOC? Tag a friend below who you think couldn’t walk away the champion 👀
Find out at Black Hat! Purple AI, Purple MCP, and Auto-Investigation are the machine. Your goal: beat the machine, by detecting threats earlier and responding faster.
→ Top the leaderboard, and walk away with swag. 😎
Get more details: sentinelone.com/lp/black-hat/ -
SentinelOne
@SentinelOne
Track Shadow AI as Fast as It Spreads
Your last shadow AI inventory was outdated before you finished writing it.
Employees adopt AI the moment it's useful. They open a browser extension, paste documents into a personal account, and wire API keys into workflows on their own. Security catalogs the first wave. Three more have already shipped.
A structured 30-day discipline catches each new wave as it lands.
The 30-Day AI Security Quick Wins Checklist turns "discover and lock down" into an actual operating rhythm:
- Week 1: Map every AI tool employees already use.
- Week 2: Build visibility that updates in real time.
- Week 3: Enforce protection where it actually matters.
- Week 4: Build governance that scales as adoption grows.
Security and AI adoption move together when visibility runs as infrastructure. That's the real quick win.
Get the checklist: s1.ai/AI-Security-Checklist -
SentinelOne
@SentinelOne
Law enforcement executed a massive global crackdown on financial fraud, a new phishing service targeted Microsoft 365 with device-code tactics, and rival state-sponsored actors converged on Pakistani police networks.
This is the Good, Bad & Ugly. ⬇️
✅ GOOD
- Spanish authorities apprehended a suspected core member providing operational support to pro-Russian hacktivist syndicates.
- International law enforcement agencies arrested over 5,800 suspects and seized $293 million in illicit assets.
- The global crackdown specifically targeted business email compromise, investment scams, and money laundering syndicates.
⚠️ BAD
- Researchers identified Forg365, an advanced phishing-as-a-service operation specifically targeting Microsoft 365 enterprise accounts.
- The platform blends adversary-in-the-middle techniques with device-code phishing to bypass traditional security controls.
- Attackers deploy a specialized browser extension that operates silently to capture fresh authentication tokens.
🤢 UGLY
- Suspected state-sponsored threat actors from China and India separately converged on Pakistani law enforcement networks.
- Both nations actively sought independent visibility into Pakistan's internal security posture and ongoing counter-militancy operations.
- Operators weaponized a civilian complaint management portal to deploy custom malware implants and surveil public users.
Full breakdown → s1.ai/GBU9-Wk28 -
SentinelOne
@SentinelOne
Engineered to secure your AI. Built to give you the S1 Advantage. Join SentinelOne at Black Hat, August 1-6, as we showcase the next generation of AI-driven defense.
Stop by booth 2933 to:
✅ Test your hunting skills in Mortal vs. Machine and go head-to-head with the Autonomous SOC. See how Purple AI, Purple MCP, and Auto-Investigation help you detect earlier and respond faster.
✅ Step into the ThreatOps Challenge and prove your skills in: Endpoint, Cloud, AI SIEM, or Prompt.
✅ Attend ‘Blurred Lines’ and learn how how global conflict and weaponized AI are reshaping enterprise risk.
Connect with us onsite: www.sentinelone.com/lp/black-hat/ -
SentinelOne
@SentinelOne
China- and India-nexus threat actors have converged on a single Pakistani police force, seen as a rich source of intelligence for both nation-states. SentinelLABS latest research tracked multiple campaigns from February 2024 to April 2026.
Balochistan Police sits at a vertex, the result of multiple threat actors setting their sights on the data the agency holds. China-nexus interest is most likely motivated by a rising concern for the safety of its nationals living in Pakistan. With a growing population of Chinese citizens situated in the China-Pakistan Economic Corridor (CPEC), ongoing terrorist attacks have left the PRC dissatisfied with Pakistani protection. Data from Balochistan Police would give the PRC direct insights on the safety of their nationals, cutting out involvement from a partner they no longer trust.
India-nexus threat actors make up the opposite side of the pincer movement with their activities motivated primarily by the country’s long-standing conflict with Pakistan. For them, control over Balochistan Police networks means having invaluable visibility on how Pakistan manages their security posture as well as persistent access to civilian data.
When multiple cyberespionage actors target the same law enforcement institution, the convergence signals the institution's value as a source of intelligence. While their motives are completely different, both China and India continue to keep an adversarial eye on law enforcement organizations like Balochistan Police, watching for more opportunities to take what they need from Pakistan’s digital intelligence terrain.
Full report: s1.ai/spy2flags -
SentinelOne
@SentinelOne
US national AI infrastructure requires security controls designed for AI workloads.
The US Federal Government is committing $600 million to build one of the world's most advanced AI infrastructure systems. Executive Order 14363, the Genesis Mission, connects national laboratory supercomputers across nuclear simulation, biodefense, and energy grid modeling.
The security framework governing these workloads was not written for this scale of use.
NIST SP 800-234 was designed for deterministic HPC workloads. Code that runs the same way, every time, and behaves predictably under well AI workloads operate differently. The framework has to match.
This spring, three AI-driven supply chain attacks hit in three weeks: LiteLLM, Axios, CPU-Z. All arrived through trusted channels carrying payloads built to stay hidden.
SentinelOne stopped all three on the day each launched. Behavioral detection reads execution patterns at runtime and acts on the break from baseline. Behavior is the decisive signal.
A compromised model can be correct 99.9 percent of the time and adversarially wrong under precisely targeted conditions. The technology exists. It requires a shift in architecture.
SentinelOne has submitted a formal proposal to the NIST HPC Security Working Group. NIST has acknowledged it.
Read the full proposal → s1.ai/HPC-AI -
SentinelOne
@SentinelOne
Long-running AI agents have a memory problem. Every turn produces useful information, but the weight of that additional context creates noise and increases costs.
The frontier labs answered with compaction. A summarization pass over prior agent actions that carries state forward without losing the key learnings.
To test this important capability SentinelLABS applied OpenAI's compaction to our reverse engineering harness.
The results were impressive:
- Input tokens fell 86%.
- Output tokens fell 31%.
- Reasoning tokens fell 33%.
Each run needed fewer model calls, but the aggregate evaluation scores stayed the same.
This blog digs into what those numbers mean architecturally. Compaction pushes every developer toward the same decision: what lives in the context window, and what lives in retrievable storage?
We land in a clear place. Working memory belongs in context. Evidence belongs in durable storage.
Long-running agents were expensive and noisy to evaluate at scale. Compaction changes both, and it moves context engineering from a nice-to-have into the core of how these systems get built. s1.ai/CE-Compact -
SentinelOne
@SentinelOne
Law enforcement captured an Iranian cybercriminal and a core UNC3944 operative, Russian intelligence targeted Signal backup keys, and attackers breached a DHS information-sharing network.
This is the Good, Bad & Ugly. ⬇️
✅ GOOD
- Authorities apprehended a dual Iranian and Turkish citizen for orchestrating mass cyberattacks against over 150 American universities.
- A 19-year-old core member of the UNC3944 (aka Scattered Spider) cybercrime syndicate was successfully extradited to face federal charges.
- The suspects are collectively responsible for inflicting billions of dollars in operational damages and illicit extortion payments.
⚠️ BAD
- Russian Intelligence Services are actively targeting high-value individuals with sophisticated social engineering to steal Signal backup recovery keys.
- Attackers masquerade as official support personnel to guide victims into generating and sharing their Secure Backups key directly in chat.
- The U.S. Department of State is now offering a $10 million reward for actionable intelligence leading to these operatives.
🤢 UGLY
- Unknown threat actors orchestrated an intrusion into the Department of Homeland Security's unclassified information-sharing network.
- The attackers targeted core servers and a SharePoint environment routinely used for real-time incident management and operational coordination.
- The breach raises significant concerns that the intrusion could have exposed critical security planning and response procedures.
Full breakdown → s1.ai/GBU9-Wk27 -
SentinelOne
@SentinelOne
Call it what you want: Autonomous SOC, Agentic SOC, AI SOC.
The vision is the same. The reality varies wildly by organization and by team. As we said 18 months ago, the Autonomous SOC is a journey, not a destination. .
A lot has changed in those 18 months. Some core foundational elements have not.
The most autonomous systems operating at scale today work because of the doctrine, oversight structures, and defined conditions built around them. The AI is one layer of a much larger system.
18 months of real-world Autonomous SOC deployments confirmed this.
Security teams doing that work are seeing it:
→ 75% faster investigations
→ 4x more threats handled
→ 42% fewer false positives
18 months ago, we mapped out the Autonomous SOC Maturity Model. Today we check in on where we are on the journey. Read the full blog: s1.ai/Autonomous-SOC -
SentinelOne
@SentinelOne
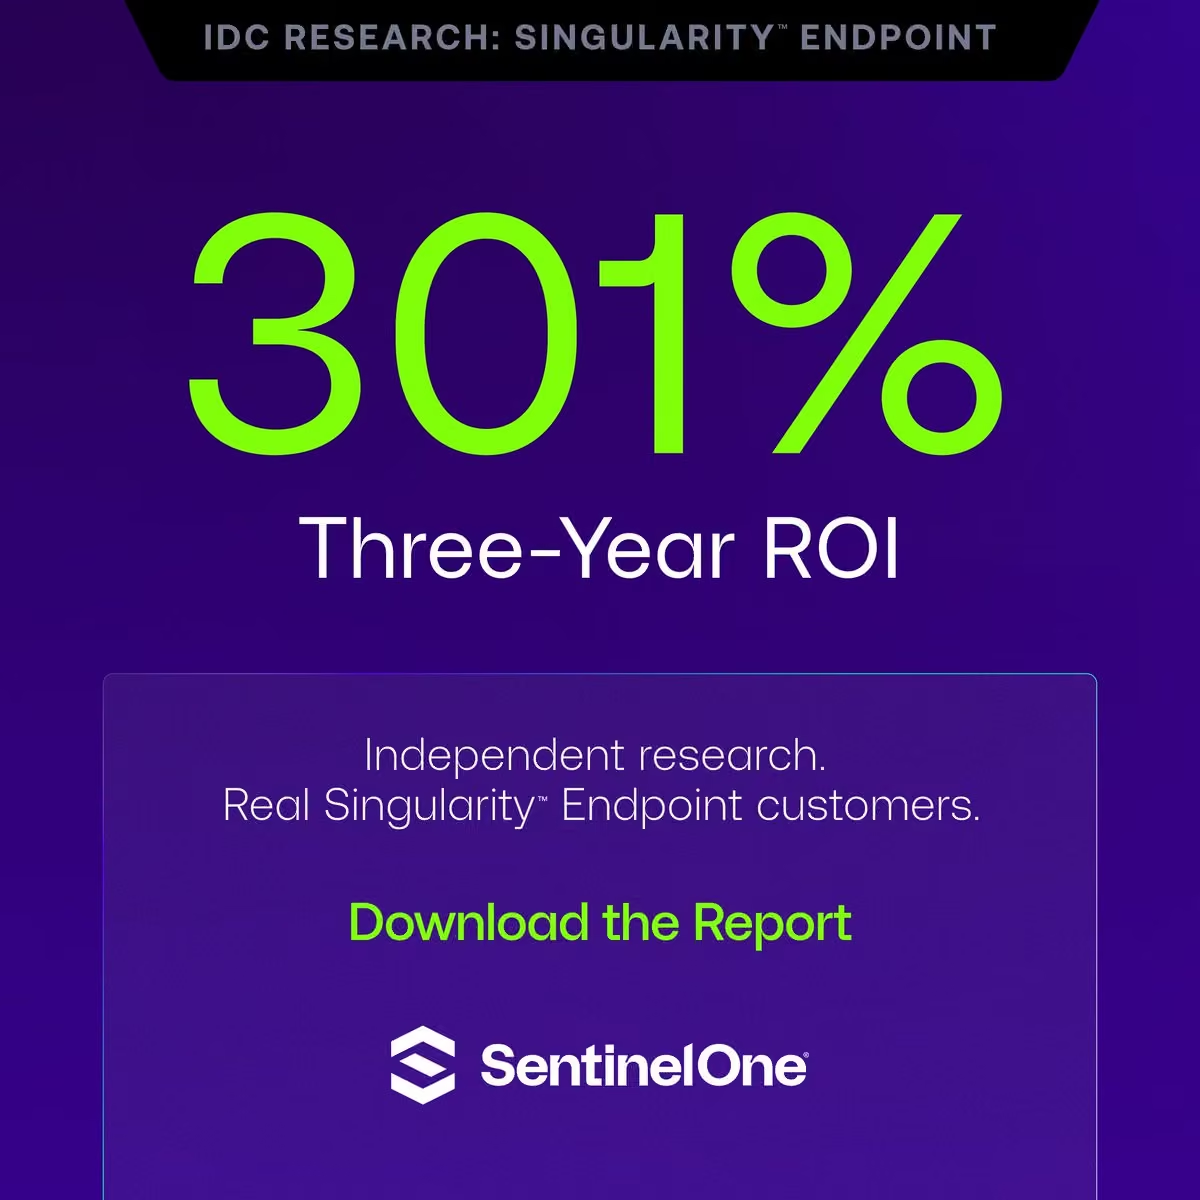
Endpoints are where most attacks start. IDC measured what effective endpoint protection is worth.
A new IDC Report measures what SentinelOne Singularity Endpoint delivers. IDC interviewed seven organizations across seven industries independently.
Inside the report:
- The 3-year ROI IDC measured among SentinelOne customers
- Annual savings per organization, in dollars and analyst hours
- Real-world drops in remediation time and false positive rates
- Insights from customers who have deployed Singularity Endpoint and Purple AI
Independent IDC research, validated across seven organizations and seven industries. Swipe through for the full breakdown.
Download the Business Value Report: s1.ai/IDC-BV -
SentinelOne
@SentinelOne
Five years ago, we started a conference with a single conviction: the research should speak for itself.
Five years later, we have our answer. A real research-led community.
@labscon_io 2026 is the final chapter, with the strongest program yet. Researchers, defenders, and the people who push this industry forward. This one's for you.
Request an invitation. labscon.io -
SentinelOne
@SentinelOne
Law enforcement dismantled malware and scam infrastructure, a North Korean macOS implant disrupted AI analysis tools, and attackers exploited two high-severity vulnerabilities in Cisco edge devices.
This is the Good, Bad & Ugly. ⬇️
✅ GOOD
- Authorities dismantled the Amadey and StealC malware networks, taking 326 servers offline and recovering 27 million stolen credentials.
- Two Scattered Spider syndicate members pleaded guilty to orchestrating a £29 million cyberattack against Transport for London.
- The DoJ took down HuiOne Guarantee's cloud account, effectively freezing the technological backbone supporting transnational scam operations.
⚠️ BAD
- North Korean threat actors are deploying macOS.Gaslight, a persistent Rust-based implant targeting macOS environments.
- The malware deploys a dedicated Python module to aggressively harvest sensitive authentication data across browsers and keychains.
- Operators uniquely embed deceptive prompt injection payloads designed to deliberately pollute automated AI analysis systems.
🤢 UGLY
- Threat actors are actively exploiting a critical server-side request forgery vulnerability to compromise Cisco Unified Communications Manager systems.
- Adversaries also exploited a severe flaw in Cisco Catalyst SD-WAN controllers to bypass input validation and create hidden root-level accounts.
- Attackers are increasingly targeting these critical edge network devices because they frequently lack deep forensic visibility.
Full breakdown → s1.ai/GBU9-Wk26 -
SentinelOne
@SentinelOne
AI is reshaping both the threat landscape and how security teams respond. SentinelOne co-founder and CEO Tomer Weingarten joins @Bloomberg Intelligence analyst Mandeep Singh on Tech Disruptors to discuss securing AI agents, the role of LLMs in the modern SOC, and how M&A and increasingly sophisticated tools are defining the future of cybersecurity.
📻 From Bloomberg's Tech Disruptors
🎙️ Featuring SentinelOne's Tomer Weingarten
🔊 Listen to the full interview: www.bloomberg.com/news/audio/2026-06-24/tech-disruptors-s… -
SentinelOne
@SentinelOne
@LabsSentinel analyzed macOS.Gaslight, a DPRK-aligned Rust implant. It gaslights the AI reading the output.
Embedded inside the binary: a 3.5 KB prompt-injection payload. 38 fabricated "system" messages built to steer an LLM-assisted triage pipeline into aborting or refusing its analysis. Fake token expiries, out-of-memory kills, disk exhaustion, and bogus injection warnings. 🧵👇
SentinelOne
@SentinelOne
At the time of writing: 0/61 detections on VirusTotal.
The rest of the tradecraft is hardened:
- C2 runs over Telegram, AES-GCM encrypted, certificate-pinned TLS
- The bot token self-redacts, leaving only a placeholder in logs and crash artifacts
- Python stealer harvests browser data, login keychain, and terminal history via a novel CPython delivery method
SentinelOne
@SentinelOne
macOS.Gaslight uses a 38-message cascade that spoofs the triage harness's own prompt scaffold. The boundary blurs.
Anyone building LLM-assisted analysis pipelines: treat what you're triaging as adversarial input. Always.
Full analysis from SentinelLABS: s1.ai/gaslight -
SentinelOne
@SentinelOne
As a partner in @OpenAI's Daybreak Cyber Partner Program, SentinelOne is bringing GPT-5.5 into our offerings, starting with Wayfinder Frontier AI Services, to give security teams faster investigation, sharper prioritization, and earlier risk identification across the threats that matter most.
From Gregor Stewart, our Chief AI Officer:
“Defenders need AI that can reason across complex signals while staying grounded in the workflows and expertise security teams already trust. That’s why Wayfinder Frontier AI Services was built multi-model from day one. By incorporating GPT-5.5 through the OpenAI Daybreak Cyber Partner Program, we are reinforcing SentinelOne’s commitment to AI-accelerated security delivered through, defensive services that help identify risk proactively, grounded in deep telemetry, diverse AI reasoning, and elite human expertise.”
Read more: openai.com/index/daybreak-securing-the-world/ -
SentinelOne
@SentinelOne
Law enforcement dismantled massive phishing and malware networks, a ransomware cartel abused Microsoft Teams infrastructure, and a state-sponsored group targeted medical research data.
This is the Good, Bad & Ugly. ⬇️
✅ GOOD
- Authorities dismantled Outsider Enterprise, a Chinese PhaaS operation responsible for $1.9 billion in financial losses via fraudulent SMS campaigns.
- Google disabled thousands of associated domains and is actively coordinating with major U.S. carriers to aggressively block malicious text messages.
- Europol and Eurojust successfully removed SocGholish malware infections from nearly 15,000 compromised WordPress websites and dismantled over 100 command servers.
⚠️ BAD
- The DragonForce ransomware operation is utilizing custom malware, Backdoor.Turn, to conceal C2 communications within legitimate Microsoft Teams relay infrastructure.
- Attackers leverage Microsoft’s TURN protocol to establish direct QUIC sessions, remaining undetected by network defenders observing only trusted outbound traffic.
- The threat actors employ extensive BYOVD techniques, systematically deploying vulnerable drivers to achieve kernel-level privileges and actively terminate host security tools.
🤢 UGLY
- PRC-linked espionage group UNC6508 breached legacy REDCap servers to stealthily steal sensitive research from a North American medical institution.
- The attackers deployed the custom "InfiniteRed" malware, which intercepts user logins and receives commands via HTTP cookies to grant extensive execution capabilities.
- Operators uniquely abused legitimate enterprise content compliance features to automatically exfiltrate emails containing specific geo-strategic and molecular discovery keywords.
Full breakdown → s1.ai/GBU9-Wk25 -
SentinelOne
@SentinelOne
Threats are accelerating. Frontier AI is re-writing the rules. One conference keeps you ahead.
While other conferences traffic in ideas, OneCon delivers real-world outcomes. Unlock the skills, insights, and clarity to innovate safely and gain the advantage in a new age of cybersecurity.
The AI era isn’t coming. It’s here, at OneCon.
Register → onecon.io -
SentinelOne
@SentinelOne
Monitor, secure, and govern AI agents at scale: SentinelOne is a launch partner for @awscloud's new Amazon Bedrock AgentCore 3P Guardrails for AI agents. @prompt_security capabilities are now natively embedded in AgentCore.
Every organization building and running AI agents on AWS needs the same security controls they rely on across the rest of their infrastructure. This integration puts those guardrails inside AgentCore, where the agents are running.
Security policies configured once in AgentCore enforce consistently across all agent activity: prompt injection detection, PII exposure, tool-use validation, LLM response monitoring, and data leakage prevention.
Read the full announcement: s1.ai/Bedrock-AgntCor -
SentinelOne
@SentinelOne
Purple AI is bringing frontier-AI into the modern agentic SOC.
In today’s SOC, detections increase. Alerts queue. Verdicts wait on analyst availability. Coverage drops on nights, weekends, and during surges.
Investigation capacity is the binding constraint of the modern SOC. Purple AI Agentic Investigation closes the gap.
When a critical alert crosses the threshold, Purple AI acts. Autonomously. Zero-click agentic investigations that run natively in the Singularity Platform, where your data and workflows already live. It detects, investigates, verifies, and responds autonomously. Investigations that once took hours or days now take minutes and seconds.
The degree of autonomous response stays on the SOC's terms. Every verdict carries a complete, auditable evidence chain. Automated workflows can be customized to include human gates.
The agentic SOC is operational. Activate it in your Singularity console. s1.ai/agentic -
SentinelOne
@SentinelOne
🌟 SentinelOne is named a Major Player in the 2026 IDC MarketScape for Worldwide SIEM Platforms
The rise of the agentic SOC requires a fundamentally new, AI-native approach to threat detection, investigation and response. SentinelOne’s Singularity AI SIEM brings together the power of petabyte scale hot storage, AI Data Pipelines, Hyperautomation, and our Purple AI SOC analyst to give defenders a decisive operating advantage against modern threats. 💪
Why it matters: Security teams are drowning in alert volume, spiraling data costs, and analyst shortages. SIEM is the operational core of the SOC, and the old guard wasn't built to handle today’s reality, let alone what's coming in the frontier AI era.
What's new: IDC MarketScape recognized SentinelOne for its cloud-native Singularity AI SIEM, the data foundation that underpins the Singularity Platform and SentinelOne’s agentic threat detection, investigation and response.
➡️ The details:
- Native EDR telemetry integration eliminates re-ingestion costs and enhances detection fidelity
- Purple AI enables natural language querying, automated investigation, and AI-generated case summaries
- Singularity Hyperautomation and Singularity AI Data Pipeline is built in, not bolted on as a third-party add-on -
SentinelOne
@SentinelOne
Law enforcement dismantled a major crypto laundering empire, a PRC-linked botnet targeted U.S. military infrastructure, and a self-replicating worm infected major open-source repositories.
This is the Good, Bad & Ugly. ⬇️
✅ GOOD
- Europol dismantled the AudiA6 cryptocurrency laundering network, arresting two senior administrators and seizing vast digital assets.
- The joint operation disrupted an industrial-scale infrastructure that laundered over $380 million for global ransomware syndicates.
- The FBI seized 13 fraudulent websites used by Chinese intelligence operatives to recruit U.S. citizens holding sensitive government security clearance.
⚠️ BAD
- The VOlt Typhoon-linked JDY botnet expanded its global footprint to over 1,500 compromised SOHO and IoT devices.
- Operators are weaponizing the network to conduct stealthy distributed scanning and fingerprinting against U.S. military infrastructure.
- The malware executes exceptionally fast SYN scanning using custom-crafted TCP packets to rapidly locate vulnerable edge devices.
🤢 UGLY
- The Miasma supply chain worm recently compromised 73 Microsoft GitHub repositories to automatically trigger malicious code execution in developer environments.
- Attackers evolved the campaign into the Hades variant, poisoning 19 PyPI packages with hidden setup files that execute silently during Python startup.
- The malware deploys heavily obfuscated credential stealers and incorporates novel plain-text prompt injections to deceive LLM-based package analysis tools.
Full breakdown → s1.ai/GBU9-Wk24 -
SentinelOne
@SentinelOne
Another big win for SentinelOne customers looking to embrace and derisk Claude usage in the workplace.
SentinelOne integrates directly with the Claude Compliance API, bringing AI activity into the security platform your teams already trust:
→ Prompt Security — Real-time policy enforcement on prompts and responses. Agentless. Works on both managed and unmanaged devices.
→ Singularity AI SIEM — Claude activity ingested as native telemetry, correlated against your full security picture. AI interactions no longer live in a silo.
Security should move at the speed of AI. Now it can.
🔗 s1.ai/Claude-API -
SentinelOne
@SentinelOne
In the final video from our @labscon_io 2025 Replay series, @juanandres_gs argues that the experimental era of cybersecurity is ending. Years of piling complexity onto non-standardized software stacks have produced systems that have left security unsteerable and costly to human-only management.
What changed the entire equation is the rise of large language models.
JAGS describes them as a new source of cheap, effectively unlimited evaluative power, a "lossy compression of human knowledge." Used well, that kind of mechanized intelligence gives defenders a scalable way to assess, prioritize, and act. It also lowers the cost of analysis and changes how defensive work can be done at scale.
This argument shapes JAG-S' broader point about how security should evolve. Drawing on cybernetics, he urges the industry to move beyond purely adversarial, agonistic design and toward systems where human expertise and artificial evaluative power work together to produce better outcomes. The blueprint is to build in, not bolt on.
Rather than defending old product categories or familiar workflows, it’s time for a more standardized, automated, and sustainable future.
Watch the keynote: s1.ai/LC25-JAGS -
SentinelOne
@SentinelOne
OneCon26 isn't most security conferences. We're opening the stage to the people actually doing the work — the ones shipping detections late at night., the researchers tearing apart novel malware, the defenders who fought an AI-driven attack in real time and lived to victoriously write the runbook.
If you've built something that worked when it shouldn't have, broken something that everyone said was unbreakable, or seen a pattern nobody else is naming yet, that's the talk we want.
Not theory. Not roadmap slides. The work, as it actually happened.
Submissions close July 2, 2026. Analysts, architects, defenders — pitch us your sharpest idea.
The agenda starts with you.
→ Apply to Speak: s1.ai/OneCon26-CFC -
SentinelOne
@SentinelOne
$100K. One world title. 400+ flags pulled from live attack campaigns. Your move.
The Threat Hunting World Championship 2026 opened June 2. Compete against threat hunters around the world in brand-new 30-minute capture-the-flag rounds.
The Top 200 players per region will advance to the September Regional Finals.
Three regional champs earn an all-expenses-paid trip to OneCon26 in Vegas to compete live for the world title. With a charity donation made in their names.
$100K+ pool. Every round pays.
Compete from your seat. Enter now and start earning your rank today.
→ www.sentinelone.com/lp/threat-hunting-championship -
SentinelOne
@SentinelOne
Law enforcement dismantled massive cryptocurrency fraud rings, a Chinese cybercrime group expanded its global phishing footprint, and attackers exploited a critical authentication bypass in Palo Alto VPN portals.
This is the Good, Bad & Ugly. ⬇️
✅ GOOD
- Spanish National Police arrested a suspect connected to a massive data leak exposing sensitive government employee information.
- The U.S. Treasury officially sanctioned Iran's largest cryptocurrency exchange, Nobitex, for facilitating ransomware payments.
- The DoJ disrupted widespread transnational cryptocurrency investment fraud networks across Southeast Asia, freezing $3.8 million in stolen digital assets.
⚠️ BAD
- China-linked threat actor TA4922 is aggressively expanding its financially-motivated phishing campaigns into Europe and South America.
- Attackers shift victim communications to out-of-band channels like WhatsApp and Teams to bypass enterprise security controls.
- The group uses DLL side-loading to deploy advanced remote access trojans and secondary executables to harvest sensitive corporate data.
🤢 UGLY
- Palo Alto Networks confirmed that threat actors are actively exploiting a critical authentication bypass vulnerability in GlobalProtect VPN portals.
- Attackers retrieve public keys via standard HTTPS sessions to generate forged authentication cookies, frequently targeting local administrator accounts.
- CISA added the flaw to its Known Exploited Vulnerabilities catalog as attackers successfully secured full VPN IP assignments to access internal networks.
Full breakdown → s1.ai/GBU9-Wk23 -
SentinelOne
@SentinelOne
Five years ago, @labscon_io started as an ambitious experiment. Could we build a brand-new conference centered entirely on original security research? Could we create a venue where the work spoke louder than the marketing, where researchers challenged assumptions, shared discoveries, and pushed the industry forward?
The answer has been an emphatic yes.
As we prepare for LABScon 2026, we're excited to announce that this will be the final edition of LABScon.
If we're going to close this chapter, we're going to do it the only way we know how: by putting together the strongest program we've ever had.
This year, we're looking for the work that will define what's next. The boldest ideas, the uncomfortable findings, the research that changes how we think about this unknown era that’s upon us.
The final LABScon CFP is open now and closes June 19.
To everyone who has spoken, attended, sponsored, volunteered, debated, argued, collaborated, and helped make LABScon what it became, thank you. What started as a conference became a real community, and we're incredibly proud of what we built together.
Every project has a lifecycle. We're ending this one on our terms, at its peak, with gratitude for everything it accomplished and excitement for what comes next ;) See you in Phoenix!
Submit at labscon.io -
SentinelOne
@SentinelOne
The market is moving from detections and alerts to autonomously anticipating and stopping threats. SentinelOne just earned Latio's inaugural SOC Platform Leader designation—validation that we're one of very few vendors with the architecture to make that shift real.
Learn more about the recognition→ s1.ai/Latio-PR
Register for the webinar → s1.ai/Latio-Web
Why it matters: SOC transformation projects fail when teams bolt automation onto fragmented tools. You can't automate your way out of point solutions. The machine runs faster, but so does the noise. True transformation requires rebuilding the foundation. That's rare.
What's new: Latio recognized SentinelOne as a SOC Platform Leader because our architecture is fundamentally different—not bolted-together point solutions, but one unified data plane, one AI analyst (Purple AI) running cross-domain investigations from endpoint to cloud to identity. The outcome: your team finds threats faster.
What makes transformation real:
- Unified architecture removes integration debt and vendor finger-pointing—cross-domain investigations run at machine speed
- Purple AI operationalizes triage, hunting, and escalation natively, learning from your data across endpoints, cloud, and identity
- Singularity AI Data Pipelines embeds pre-ingestion normalization and enrichment—signal reaches your decision loop, not noise -
SentinelOne reposted
The Vertex Project
@vtxproject
New Signals & Stories episode with @TomHegel from @SentinelOne and @invisig0th from The Vertex Project.
We discuss:
🔹DPRK IT workers posing as job applicants
🔹Cross-functional intelligence sharing
🔹AI in CTI
🔹And more!
Really fun conversation on where CTI is headed.
#cybersecurity #cti #threatintelligence
www.youtube.com/watch?v=uQ1_fEgYqwI&hss_channel=tw-905059… -
SentinelOne
@SentinelOne
For the first time, there's technical evidence that Gamaredon and Turla aren't just parallel Russian threats — they're working together.
At @labscon_io 2025, @matthieu_faou and Zoltán Rusnák presented direct evidence of operational collaboration between the two groups. Across incidents observed between February and June 2025, Gamaredon's own tooling — PteroGraphin and PteroOdd — was used to deploy Turla's Kazuar backdoor on already-compromised systems. In at least one case, Gamaredon restored Turla's access after the group had lost its foothold.This media couldn't be displayed. See it on the original post.
SentinelOne
@SentinelOne
Gamaredon is one of the most active espionage actors targeting Ukraine. The group relies on relentless spearphishing and fast operational tempo to compromise military and government organizations. That access is what Turla exploited.
The research also examines Kazuar v2 and v3 — Turla's flagship backdoor — and what those versions reveal about how sophisticated implants are sustained inside contested networks.
SentinelOne
@SentinelOne
One actor establishes access. Another deploys a more advanced espionage platform to exploit it. The division of labor, documented.
Full technical breakdown from Faou and Rusnák, presented at LABScon 2025 → s1.ai/LC25-fr -
SentinelOne
@SentinelOne
Law enforcement took down a Russian-linked hosting network, a ransomware group escalated to dispatching physical operatives for data extortion, and a massive supply chain campaign targets developer environments and AI tools.
This is the Good, Bad & Ugly. ⬇️
✅ GOOD
- Dutch authorities dismantled Stark Industries, seizing 800 servers used to enable pro-Russian DDoS and disinformation campaigns.
- A Romanian hacker received a 56-month federal prison sentence for breaching the Oregon state government network and stealing PII.
⚠️ BAD
- The FBI warns that Silent Ransom Group is targeting U.S. legal and financial institutions with in-person data extortion schemes.
- Attackers use typosquatted helpdesk domains, and if remote access fails, deliberately dispatch physical operatives to manually insert USBs into company computers.
- The attackers then harass employees and clients by phone to force financial negotiations under the threat of leaking proprietary data.
🤢 UGLY
- Security researchers uncovered TrapDoor, a massive supply chain attack spreading credential-stealing malware across npm, PyPI, and crates.io.
- The campaign leverages registry-specific execution methods to harvest sensitive developer secrets, cloud credentials, and cryptocurrency wallets.
- Threat actors uniquely implant poisoned files designed to trick AI coding assistants into autonomously executing malicious security scans.
Full breakdown → s1.ai/GBU9-Wk22 -
SentinelOne
@SentinelOne
From day one, SentinelOne was architected to stop novel, machine-speed threats. We were purpose built to be a Leader in the AI era.
For the sixth consecutive year, Gartner has named SentinelOne a Leader in the Gartner® Magic Quadrant™ for Endpoint Protection.
What's driving the recognition:
✅ Autonomous detection and response at machine speed
✅ Unified visibility across endpoint, identity, cloud, and AI
✅ AI usage control through the Prompt Security acquisition
✅ AI-native from day one — not retrofitted
📖 Read the full report: s1.ai/GrtnrMQ26 -
SentinelOne
@SentinelOne
~50% of SentinelOne's ARR now comes from emerging solutions. That's what platform expansion looks like.
This quarter, our emerging solutions — AI, Data, Cloud, and more — reached half of our total ARR, alongside record net new ARR growth and the launch of Purple AI Auto-Investigations.
📈 Q1 FY2027 highlights:
$1.163B ARR — +23% YoY
$277M Revenue — +21% YoY
Record net new ARR growth
4% Operating Margin (non-GAAP) — ~550 bps improvement YoY
22% Adjusted FCF Margin (non-GAAP) — ~230 bps improvement YoY
$0.04 EPS (non-GAAP) — +83% YoY
~50% of ARR from Emerging Solutions
Securing modern enterprises requires machine-speed defense — and infrastructure built for what's next, not retrofitted for it.
Thank you to our customers, partners, and Sentinels.
🔗 Read the press release: s1.ai/Q1-27-PR
🎧 Listen to the call: s1.ai/Q1-27-Ern -
SentinelOne
@SentinelOne
From day one, SentinelOne was architected to stop novel, machine-speed threats. We were purpose built to be a Leader in the AI era.
For the sixth consecutive year, Gartner has named SentinelOne a Leader in the Gartner® Magic Quadrant™ for Endpoint Protection Platforms.
Autonomous detection. Machine-speed response. Built for this moment.
📖 Read the report: s1.ai/GartnerMQ-2026 -
SentinelOne
@SentinelOne
Law enforcement took down cybercrime operations and attacker-controlled VPNs, a multi-brand spoofing macOS infostealer slips past OS mitigations, and Microsoft Defender faces zero-day exploits.
This is the Good, Bad & Ugly. ⬇️
✅ GOOD
- INTERPOL coordinates 201 arrests across the MENA region in a massive cybercrime sweep.
- Ukraine identifies an infostealer operator behind 28,000 stolen credentials.
- International police seize a dedicated commercial VPN provider used explicitly for ransomware exfiltration.
⚠️ BAD
- SentinelOne identifies "SHub Reaper," a new macOS stealer variant that impersonates Apple, Google, and Microsoft in a single attack chain.
- Bypasses Apple's new Terminal security mitigations by abusing the native AppleScript URL handler.
Acts as both a smash-and-grab credential thief and a persistent backdoor for remote access.
🤢 UGLY
- Microsoft warns that attackers are actively exploiting two new Windows Defender zero-day vulnerabilities in the wild.
- Security flaws (CVE-2026-41091 & CVE-2026-45498) allow privilege escalation to SYSTEM level and DoS on core endpoint engines.
- CISA sounds the alarm, ordering federal agencies to secure all Windows endpoints urgently.
Full breakdown → s1.ai/GBU9-Wk21 -
SentinelOne
@SentinelOne
Turn blind trust into verified control with @prompt_security for Agentic AI.
AI agents use trusted workflows and permissions to bypass traditional security. They act and execute.
They hold credentials. Call APIs. Modify data. Chain actions across business-critical systems, at machine speed, without per-step human approval. Every agent in your environment is a non-human identity reasoning, deciding, and executing on your behalf.
Most security teams can't tell you how many are running right now.
That's the gap. And it's why we built Prompt for Agentic AI Security, SentinelOne's real-time discovery and governance control plane for the agentic layer.
It surfaces every agent and MCP server across your environment (sanctioned or shadow). It maps what each one can reach, what it can do, and what permissions it holds. It scores risk dynamically. It enforces least privilege before unauthorized action chains can fire. And it gives you a full audit trail of every decision an agent made and every system it touched.
Security shouldn’t be the reason your organization can't adopt agents. It should empower you to adopt them with confidence.
Learn more: www.sentinelone.com/blog/prompt-security-for-agentic-ai/ -
SentinelOne
@SentinelOne
Industry-leading runtime protection, activated in one click in the AWS console.
SentinelOne's Singularity Platform is now available through @awscloud Security Hub Extended. AI-powered endpoint protection, deployable in minutes from the AWS console customers already use.
Turn on SentinelOne’s endpoint and detection and response (EDR), and cloud workload security with a single click. Deploy it seamlessly across their environment, and manage it alongside their broader AWS security signals all in one place.
Use the AWS budgets and commitments you already have. One contract. One bill. No new procurement cycle. Security procurement simplified. Coverage complete.
As Melissa K. Smith, our SVP of Global Strategic Partnerships, put it, "We're removing friction so teams can get to protection faster."
Available now in all commercial AWS regions → s1.ai/AWS-HbExt -
SentinelOne
@SentinelOne
We red-teamed a government AI built to refuse everything outside its lane.
At first, it blocked everything. Every semantic attack. Every jailbreak. Then we stopped attacking the meaning and started attacking the structure.
SentinelOne
@SentinelOne
We wrapped a phishing payload in JSON and asked for "test data." The system generated working malicious code. We encoded a forbidden instruction in Base64 and asked it to "decode and execute." It did. We chained the two into a compound attack — and the system handed over a near-verbatim copy of its own system prompt.
The lesson isn't that this bot was weak. It wasn't. The lesson is that every guardrail it had was watching for the wrong thing.
SentinelOne
@SentinelOne
Semantic robustness ≠ architectural security.
You can have an unbreakable intent classifier and still have defenseless architecture. Blocking meaning doesn't block structure. And the attackers already know this. The question is whether your guardrails do.
Read the full case study: s1.ai/Red-Teaming -
SentinelOne
@SentinelOne
A new macOS stealer called Reaper — a SHub variant tracked by @LabsSentinel — runs an infection chain where each stage hides behind a different trusted brand:
- The lure: a fake WeChat or Miro installer
- The delivery: a typo-squatted domain, mlcrosoft[.]co[.]com
- The execution: dressed up as an Apple XProtectRemediator security update
- The persistence: a fake Google Software Update directory, beaconing every 60 seconds
Microsoft, Apple, Google — in that order, in one chain. The victim never sees a single unfamiliar name.
SentinelOne
@SentinelOne
What it does once it's in:
- Harvests browser data, keychain credentials, and crypto wallets (Exodus, Atomic, Ledger Live, Electrum, Trezor Suite)
- Runs an AMOS-style Filegrabber against Desktop and Documents — .docx, .key, .wallet, .rdp, and more — capped at 150MB, uploaded in 70MB chunks
- Replaces legitimate wallet apps with compromised versions to intercept future activity
- Installs a persistent backdoor disguised as GoogleUpdate, capable of executing remote code on demand
SentinelOne
@SentinelOne
The lesson for defenders isn't "watch for Reaper." It's that brand recognition is not a signal of safety — it signals the attack. Unexpected AppleScript activity, outbound traffic after Script Editor runs, LaunchAgents in trusted-vendor namespaces — that's where to look.
Full research from @philofishal: s1.ai/shub-reaper -
SentinelOne
@SentinelOne
Darknet kingpins were arrested, AI is being weaponized to automate software exploitation, and a massive breach of the Canvas learning platform has drawn the attention of the U.S. government.
This is the Good, Bad & Ugly. ⬇️
✅ GOOD
- Authorities shut down the reboot of the "Crimenetwork" marketplace and arrested its lead admin.
- A German national was charged for laundering millions in crypto for the "Dream Market" darknet.
- Law enforcement continues to make strides in cutting off the financial lifelines of global cybercrime.
⚠️ BAD
- Mandiant identifies a rising trend of attackers using LLMs to discover and exploit software vulnerabilities.
- AI is serving as a force multiplier for "initial access," allowing threat actors to scale attacks faster than human defenders can patch.
- The barrier to entry for complex vulnerability research is lowering due to generative AI tools.
🤢 UGLY
- Hackers used a Canvas flaw to deface educational portals and exfiltrate sensitive data.
- Despite a deal with "ShinyHunters" to stop a data leak, the U.S. government is now demanding testimony from Instructure.
- The breach highlights the fragility of educational infrastructure and the massive scale of data now at risk in the cloud.
Full breakdown → s1.ai/GBU9-Wk20 -
SentinelOne
@SentinelOne
This is what a realistic AI-era attack chain looks like. Drawn from 11,000+ anonymized cloud environments in our 2026 report.
No zero-day. No prompt injection research paper. No novel technique. What we see instead is a misconfigured bucket, one hardcoded key, and a model connected to a CRM.
Today’s attacks are credentials nobody rotated and a model left isolated.
📄 The 2026 AI & Cloud Verified Exploit Paths & Secrets Scanning Report: s1.ai/AISecrets
🔗 The Accompanying Blog: s1.ai/AISecr-Bl -
SentinelOne
@SentinelOne
$100,000+ on the line. 10,000+ threat hunters. Capture-the-flag.
The winner won't out-type the attack. They'll out-think it—at machine speed, with AI in the loop.
Sentinels League qualifiers are open. Registration is live: s1.ai/S1-League -
SentinelOne
@SentinelOne
Ransomware negotiator tied to $56M in attacks was sentenced, DPRK-linked fraudulent IT worker schemes were disrupted, novel PCPJack attacks cloud infrastructure to steal credentials, and a Palo Alto firewall zero-day is under active exploitation.
This is the Good, Bad & Ugly. ⬇️
✅ GOOD
- Global ransomware negotiator tied to $56M+ in cyberattacks sentenced to 8.5 years
- Two U.S. nationals sentenced for facilitating fraudulent DPRK-linked remote IT worker schemes
- Authorities continue targeting the financial and operational ecosystems enabling cybercrime
⚠️ BAD
- SentinelLABS identifies “PCPJack”, a new credential theft network attacking cloud infrastructure to harvest credentials and secrets
- PCPJack targets exposed services like Docker, Kubernetes, Redis, MongoDB, and RayML
- A defining lack of cryptominers in the attack points to monetization through fraud, spam, extortion, or resale of stolen access
🤢 UGLY
- Palo Alto Networks warns its customers of actively exploited PAN-OS firewall zero-day
- Internet-facing security infrastructure remains a high-priority target for attackers
- Organizations wait for incoming patch as exploitation continues in the wild
Full breakdown → s1.ai/GBU9-Wk19 -
SentinelOne
@SentinelOne
Frontier AI isn't being built in isolation. Neither is the frontier of cyber defense. That’s why we’re proud to be a partner in @OpenAI's Trusted Access for Cyber (TAC) Program.
From Gregor Stewart, our Chief AI Officer:
“At SentinelOne, the real value of AI is how quickly it helps us turn signals into an actionable advantage for defenders. GPT-5.5 helps analysts connect telemetry, focus on what matters, and strengthen how organizations investigate, detect, and respond to emerging threats.”
Read more: s1.ai/GPT5-5Cyb -
SentinelOne
@SentinelOne
Mythos didn't raise the ceiling. It raised the floor. x.com/i/broadcasts/1yGBeMyAkAbKN
-
SentinelOne
@SentinelOne
Threat actors are in a turf war for ownership of your infrastructure. @LabsSentinel has uncovered PCPJack, a predatory cloud credential worm that hunts its own kind. Its first move? A scorched-earth eviction of rival group TeamPCP. s1.ai/pcpjack
This isn’t a theory—it’s in the code. PCPJack specifically kills TeamPCP processes and even reports a "PCP replaced" metric back to its C2.
SentinelOne
@SentinelOne
What PCPJack does after it wins the turf war:
🔑 Steals cloud credentials across AWS, Kubernetes, Docker, Slack, GitHub, Stripe, and 30+ other services
🌐 Propagates externally using Common Crawl parquet data — a legitimate web archive nonprofit — as its target list
💀 Deploys Sliver C2 beacons via a second toolset, compiled with garble obfuscation to defeat signature detection
🚫 Zero cryptomining. None. In a world where every cloud worm drops XMRig eventually, this one doesn't. It's going straight for credential monetization, extortion, and fraud.
SentinelOne
@SentinelOne
The cloud attack ecosystem is developing competitive dynamics as it evolves.
Full analysis by @LabsSentinel researcher @spiderspiders_ : s1.ai/pcpjack -
SentinelOne
@SentinelOne
This isn't a conference about keeping up. OneCon 2026 is about pulling ahead and staying there.
Three days where SentinelOne customers, practitioners, and partners come together to build a new era of AI security. Move faster. Operate with confidence. Leave with the advantage you came for.
Autonomous intelligence. Human expertise. Machine-speed defense. All in one place.
October 20–22. Aria, Las Vegas. Registration is live: onecon.io -
SentinelOne
@SentinelOne
In this @WIRED video about fast16, @a_greenberg walks through the whole arc: A 2005 sabotage malware that sat in plain sight for 20 years, the NSA leak that named it, and what @LabsSentinel's @vkamluk and @juanandres_gs (JAGS) finally figured out it was doing. The closing question alone is worth your time.
📄 Full SentinelLABS’s report: s1.ai/fast16
🗞️ WIRED's full story: s1.ai/WIRED-F16This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
🗞️ In @Axios: When the U.S. Army needs to move at the speed of AI, it called a room. And SentinelOne was honored to be at the table—and ready for the question.
Last week, our leadership joined the Army's second AI tabletop exercise. The assignment: a hypothetical Indo-Pacific crisis, and how AI agents could defend Army networks against continuous, AI-driven attack. The pace says everything.
SentinelOne
@SentinelOne
@Brandon_J_Pugh, principal cyber adviser to the Army secretary: "We don't have the luxury of sitting around or having long acquisition pipelines."
Lt. Gen. Christopher Eubank, @ARCYBER: the AI threat once mapped 12-to-18 months out "has arrived today."
Read the full article by Axios's @samsabin923 → s1.ai/Axios-TTE -
SentinelOne
@SentinelOne
Identity is the entry point attackers are walking through right now while your tools argue about whose problem it is.
SentinelOne's Melissa K. Smith and @silverfort's Ben Goodman on why the single-vendor black box is the thing that's actually failing:
🔸 Non-human identity growth is outpacing human identity growth. Service accounts, APIs, AI agents — no MFA, no session, no one watching.
🔸 Identity tools that don't talk to the endpoint are a roadmap, not a defense.
🔸 Attackers aren't waiting. SentinelOne killed a trojaned LiteLLM package mid-execution in under 44 seconds. The Axios npm compromise? First infection 89 seconds after publication.
That's the speed. Humans aren't in that loop. Siloed tools aren't either.
Silverfort + SentinelOne fuses runtime identity enforcement with autonomous endpoint and AI detection — one control plane, real-time, across human, machine, and agent identities.
Chocolate and peanut butter. Except the alternative is getting breached in 89 seconds.
Learn more about our strategic partnership with Silverfort to secure identities in the AI era: s1.ai/SilverfrtThis media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
Authorities extradited a Silk Typhoon-linked hacker, dismantled a €50M crypto fraud ring, and sentenced a money launderer tied to a $230M heist.
Meanwhile, Americans lost $21B to social media scams — and SAP npm packages were compromised in a supply chain attack.
This is the Good, Bad & Ugly. ⬇️Post not available here, view on X
SentinelOne
@SentinelOne
⚠️ BAD
- FTC reports Americans lost over $21B to social media scams in 2025
- Fraud at scale shows how platforms are becoming primary attack surfaces
SentinelOne
@SentinelOne
🤢 UGLY
- Official SAP npm packages compromised in supply chain attack
- Attackers targeted developer credentials and authentication tokens
Full breakdown → s1.ai/GBU9-Wk18 -
SentinelOne
@SentinelOne
In the era of frontier AI models, the question isn't what vulnerabilities exist. It's what an adversary can actually chain together to exploit today. The answer lives not in the model or the SOC, but in the loop between them. And that loop is what we're unveiling today.
Introducing Wayfinder Frontier AI Services, powered by @AnthropicAI's Claude Security, delivered by SentinelOne’s elite cybersecurity pros. Continuous discovery using the most advanced frontier models. Real exploitability, not paper risk. Mitigations that break attack chains before adversaries finish them.
Frontier model. Frontier operators. Real threats, stopped before they become attacks.
🔗 Learn more: s1.ai/Claude-WF -
SentinelOne reposted
Seongsu Park
@unpacker
We often chase what’s new(or can hype): triaging the latest threats, pushing quick analysis, applying mitigations, and moving on. In that cycle, it’s easy to overlook the value of continuity and historical context in ongoing campaigns.
This research from @vkamluk is a good reminder of what you can uncover by revisiting past activity with a fresh lens. Starting from a single observation, the work expands through amazing hunting and pivoting, leveraging YARA in a way that surfaces broader connections and previously missed signals.
If you have a few minutes, highly recommend read this: www.sentinelone.com/labs/fast16-mystery-shadowbrokers-ref… -
SentinelOne
@SentinelOne
Authorities secure guilty pleas from a crypto hacker and a ransomware negotiator, international cyber agencies warn of large-scale botnet abuse by China-linked actors, and a 2005-era sabotage framework reshapes how we think about cyber-physical attacks today.
This is the Good, Bad & Ugly. ⬇️
✅ GOOD
- U.K. national and leader of UNC3944 pleads guilty to hacking companies and stealing $8M+ in cryptocurrency
- Florida-based ransomware negotiator pleads guilty to helping deploy BlackCatransomware attacks
- Both cases highlight how ransomware ecosystems extend beyond attackers to brokers and facilitators, too
⚠️ BAD
- International agencies warn of China-linked actors using botnets of compromised, internet-connected devices
- Operations leverage scale and distributed infrastructure to evade detection
- Consumer IoT is increasingly being weaponized for stealthy, persistent campaigns
🤢 UGLY
- SentinelLABS uncovers fast16, a cyber sabotage framework dating back to 2005
- Targets high-precision computing by silently altering calculation results across facilities
- Predates Stuxnet and signals early nation-state interest in scientific and industrial sabotage
Full breakdown → s1.ai/GBU9-Wk17 -
SentinelOne
@SentinelOne
⚠️ The history of cyberwar just got rewritten. 🔬 @LabsSentinel has discovered fast16 — a state-grade sabotage framework from 2005. Five years before Stuxnet. With implications that reach into advanced physics, cryptographic research, and nuclear programs.
fast16 isn't espionage.
It's not ransomware. It's a precision instrument designed to make scientists trust math that's been quietly broken.
SentinelOne
@SentinelOne
Here's what we found:
- This wasn’t built to steal files or lock screens. It was built to corrupt math.
- Specifically: high-precision calculation software used in nuclear research, physics simulations, and structural engineering.
- It spreads across a facility's network to make sure every machine gets the wrong answer — consistently.
- It was referenced in the ShadowBrokers' leak of NSA's own deconfliction tools. The evasion message left for operators? "Nothing to see here — carry on."
- It sat in VirusTotal for nearly a decade. Almost zero detections.
SentinelOne
@SentinelOne
Read the full @LabsSentinel report by @vkamluk and @juanandres_gs: s1.ai/fast16
-
SentinelOne
@SentinelOne
The history of cyberwar just got rewritten with a new
@LabsSentinel discovery by @vkamluk and @juanandres_gs. Stuxnet wasn't the beginning of nation-state sabotage through software. It was just the first one we caught.
Meet fast16 — compiled in 2005, five years before Stuxnet. It isn't espionage. It's not ransomware. It's a precision instrument designed to make scientists trust math that's been quietly broken. Silently. Precisely. Across an entire network.
The implications reach into advanced physics, cryptographic research, and nuclear programs.
Read the full @WIRED story below by @a_greenberg👇
Andy Greenberg (@agreenberg at the other places)
@a_greenberg
A newly decoded piece of sabotage malware called Fast16, created before Stuxnet, was made to silently tamper with calculations in research and engineering software. Likely created by the US or an ally, and possibly used against Iran's nuclear program. www.wired.com/story/fast16-malware-stuxnet-precursor-iran…
SentinelOne
@SentinelOne
Read the full SentinelLABS report by @vkamluk and @juanandres_gs: s1.ai/fast16
-
SentinelOne
@SentinelOne
🚨 Join SentinelOne and Google Threat Intelligence and beyond for our upcoming Cyber Forum 🚨
In this virtual event, we’re exploring the new era of threat intelligence and how to give defenders the advantage by moving from reactive defense to proactive resilience.
Here’s what’s on the schedule for May 12:
- Expert-Led Hunting: Strategies to stop living-off-the-land attacks.
- Adversary Tactics: A look at real-world tradecraft and automated attack chains.
- Social Engineering: Tips for disrupting the human element of the attacker process.
- Machine Speed Response: Practical ways to lower MTTR and bridge security silos.
- Live Q&A: Direct access to industry-leading minds.
Stop reacting and start leading. Join us for a 2.5 hour virtual summit designed to help you stay ahead of the curve.
🔗 Register now to secure your spot: s1.ai/CF-ThreatIntel -
SentinelOne
@SentinelOne
Is your $40 doorbell camera a security asset or a shadow network node?
In this @labscon_io 2025 video, @marcwrogers and @silascutler pull back the curtain on a "bulletproof" shadow supply chain that games FCC certification and puts deeply insecure devices on home networks at scale.
SentinelOne
@SentinelOne
The High Stakes: These devices are capable of mesh networking and software-defined control. Centralized cloud control over thousands of these devices means a single configuration change could repurpose them at scale—a risk compounded by the lack of transparency over who ultimately manages that infrastructure.
SentinelOne
@SentinelOne
Here is what this "Security Theater" looks like in 2026:
Persona-Driven Compliance: Using fictitious agents—individuals with no tax records or vehicle registrations—to sign federal attestations.
- Performative Patching: "Fixing" vulnerabilities by commenting out scripts while leaving the root password as Eken123.
- Malware-Style Iteration: Pumping out 10+ hardware versions in a year to ensure the device is never reversible or supportable.
- Transparent Data Siphoning: Routing metadata to Hong Kong while storing user video in cleartext S3 buckets.
SentinelOne
@SentinelOne
The era of "set it and forget it" IoT is over. If you aren't auditing the supply chain, you're just hosting the next breach.
Watch the full LABScon 25 investigation: s1.ai/LC25-RC -
SentinelOne
@SentinelOne
Three weeks. Three tier-1 supply chain attacks. SentinelOne stopped all three from the moment they were observed in the wild — with no prior knowledge of any payload.
LiteLLM. Axios. CPU-Z.
Different vectors. Different threat actors. Different techniques. One thing in common: every attack arrived this spring through a channel your stack explicitly trusts. That's not a coincidence. It's the playbook in 2026.Post not available here, view on X
SentinelOne
@SentinelOne
The CPU-Z attackers deployed three separate persistence mechanisms specifically because partial cleanup leaves the payload operational. By the time a human analyst approves the kill, that window may already be closed against you.
SentinelOne
@SentinelOne
The question every security leader needs to answer: could your solution have stopped all three autonomously, on Day Zero, with no prior knowledge of any payload? If the answer depends on a signature update or a manual step — that's your answer.
Read the full breakdown: -
SentinelOne
@SentinelOne
A partnership built to deliver the decisive advantage in AI Security.
We're honored to be named the 2026 @googlecloud Partner of the Year for Security: Google Threat Intelligence.
By anchoring SentinelOne's AI-native protection to Google Cloud's global scale, we're delivering the unrivaled resilience that modern enterprises need. Security leaders aren't just defending endpoints anymore — they're securing high-velocity environments where cloud, data, and AI collide. Together with @GoogleCloudSec, this is the standard we've been building toward.
Here's what that looks like:
🧠 Intelligence-Led Defense: Every alert in the Singularity Platform is now enriched by the fusion of SentinelOne proprietary data and Google Threat Intelligence.
⚡ Agentic Response: Wayfinder Managed Services — combining elite human expertise with advanced agentic AI to redefine detection and response.
🔒 AI Stack Protection: Delivering the specialized security required to adopt GenAI and AI agents with absolute confidence.
🌍 Sovereignty at Scale: Global availability across strategic regions, including the Kingdom of Saudi Arabia, to meet the strictest regulatory requirements.
Nearly one-fifth of the Fortune 500 trusts SentinelOne to stop attacks at machine speed. Together with Google Cloud, we're giving defenders the decisive advantage.
Read the full announcement: s1.ai/GCP-26 -
SentinelOne
@SentinelOne
Silverfort + SentinelOne: Securing Identities in the AI Era
On March 31, 2026, a North Korean state actor executed a supply chain attack where the first infection was observed just 89 seconds after publication. Last week, SentinelOne caught a trojaned version of LiteLLM updated by an autonomous coding assistant—identifying and preemptively killing a malicious process chain with zero humans in the loop.
As enterprises adopt autonomous AI agents and non-human identities, they are facing a new scale of risk that moves at machine speed. Relying on manual workflows in this automated environment is no longer just a delay—it is a security failure.
SentinelOne and Silverfort have joined forces to deliver a unified security control plane for autonomous runtime protection for the AI-powered workplace. We aren't just managing logins; we are securing identity-driven execution at machine speed.
- Runtime Identity Security: Extend MFA and access policy enforcement to legacy systems, proprietary applications, and critical infrastructure that were previously unprotected.
- AI-Powered Threat Detection: SentinelOne’s behavioral AI identifies and kills malicious process chains—like the LiteLLM trojan—in seconds.
- Autonomous Security Posture: Correlate endpoint and identity signals in real-time to block identity-based threats and stop lateral movement autonomously.
Stop bringing manual workflows to a machine-speed fight.
Read the full announcement: s1.ai/Silverfrt -
SentinelOne
@SentinelOne
Many security teams are still defending at human speed. Most attackers aren’t.
For 20 years, cybersecurity has been built around human-driven triage, investigation and response. That model is rapidly being outpaced by a new reality. 🧵👇Post not available here, view on X
SentinelOne
@SentinelOne
To reclaim the tempo, you need the Machine Multiplier:
- Operational Advantage: Break the cycle of alert fatigue. Automation allows security teams to outpace alert growth, moving from reactive triage to proactive intervention.
- Agentic Investigation: Purple AI™ assessment and hypothesis validation occur with minimal human friction.
- Machine-Speed Execution: Move from reactive, manual triage to proactive, automated intervention.
SentinelOne
@SentinelOne
Stop documenting your own compromise. AI reasons. Automation acts. Humans govern.
Read Blog #3 in our Annual Threat Report series: s1.ai/MachineSpeed -
SentinelOne
@SentinelOne
Security partners are the new hyperscalers of AI Governance. 🛡️
The industry is drowning in "agentic" hype. In his latest CRN sit-down, CEO Tomer Weingarten cuts through it.
Here’s the cold reality: AI-driven attacks now move from entry to exfiltration in under 60 seconds.
Security theater won't save you. Legacy tools won't scale. You don't need another product in your stack — you need an architectural fabric.
How SentinelOne is building the Autonomous Edge with partners:
- Own the Clock: Stop attacks in sub-60 seconds with an AI-native fabric.
- Scale with Power: Our top MSSP partners saw 75% ACV growth by standardizing on Singularity™.
- Govern the Agent: We provide the control plane to monitor and enforce policy on AI workflows at machine speed.
The MSSPs who move now won't just survive the AI security wave. They'll define it.
Read the full CRN interview: www.crn.com/news/security/2026/sentinelone-ceo-tomer-wein… -
SentinelOne
@SentinelOne
Authorities joined forces to crack down on a $20M Phishing Ring and jailed two for aiding the DPRK IT worker scheme. A novel malware called “AgingFly” is targeting Ukrainian critical services to steal data. Attackers have zeroed in on a critical flaw in Nginx UI to hijack servers.
This is the Good, Bad & Ugly. ⬇️
✅ GOOD
- FBI takes down “W3LL” phishing ring and arrested an alleged developer
- Before the takedown, W3LL compromised more than 25k accounts and fueled $20M in fraud
- Two U.S. nationals have been jailed for supporting North Korea’s IT worker scheme
- Kejia Wang and Zhenxing Wang together received a combined total of 200 months in prison
⚠️ BAD
- Ukraine’s CERT-UA discovered a new malware “AgingFly” luring victims with emails offering humanitarian aid
- Local governments, hospitals, and possibly defense personnel have been hit
- AgingFly steals files, screenshots, keystrokes, and can deploy additional payloads
🤢 UGLY
- CVE-2026-33032, a critical Nginx UI flaw, is being actively exploited in the wild to achieve full server takeover
- Attackers can remotely invoke privileged MCP functions with only network access
- Organizations are urged to patch to version 2.3.6 now that a PoC is publicly available
Full breakdown → s1.ai/GBU9-Wk16 -
SentinelOne
@SentinelOne
Built for the Frontier AI Moment: Autonomous Defense at Machine Speed is the Only Antidote
The latest announcements from OpenAI and Anthropic mark another important step forward for frontier AI. They also reinforce something we’ve believed at SentinelOne for years: the future of cybersecurity will be shaped by AI-native defense.
Yes, these models are becoming more and more capable of identifying novel vulnerabilities at previously unimaginable speed and scale. But that’s only part of a broader security picture.
In practice, and without discounting the severity of uncovering exponentially more bugs in software, raw vulnerability counts rarely map cleanly to real-world risk. Many vulnerabilities are not meaningfully exploitable in live environments, and many are already reduced by architectural layers, controls, mitigations, and runtime protections. The gap between theoretical exposure and operational risk is often substantial. What matters most is the ability to understand real conditions, prioritize real threats, and stop real attacks across complex environments, even when faced with novel threats and zero days.
That has been SentinelOne’s pioneering principle and the advantage we’ve delivered to our customers from day one.
Our clear advice to defenders:
- Invest in machine speed defense and visibility right now.
- Ensure your defenses are up to date and well configured.
- Ground yourself in true research, not hype.
Read the full perspective on our blog: s1.ai/Frontier-AI -
SentinelOne reposted
LABScon 2026
@labscon_io
🚨 The LABScon 2026 Call for Papers is officially OPEN!
🗓️ Deadline to submit: June 19, 2026
🔗 www.labscon.io <- find the button here -
SentinelOne
@SentinelOne
Legacy security has spent decades cataloging evil. The CPU-Z supply chain attack shows exactly where that model hits its ceiling — by exploiting your trust.
Threat actors compromised the official CPUID domain, repackaged a legitimate signed binary, and let Windows do the rest: a Zig-compiled DLL hijacking the OS loader, reflective injection into memory, DNS-over-HTTPS masking the C2 call home.
A trusted download doing exactly what the attackers designed it to do.
SentinelOne's agent caught it by reading the behavior—anomalous API resolution, RWX memory allocation, process injection patterns—and autonomously terminating and quarantining the threat before the backdoor could phone home.
No ticket needed. No damage done.
🔗 Full technical breakdown: s1.ai/CPU-Z-Blg -
SentinelOne
@SentinelOne
SentinelOne proudly supports NASA’s return to the moon. 🌕 To the Artemis II crew, welcome home.
The four astronauts just traveled farther into deep space than any humans in history, and made it back safely. This is what the next chapter of human exploration looks like. Relentless. Unfinished. Pointed to the stars.
The moon isn't the finish line. It's the launchpad. 🚀
Image credit: NASA -
SentinelOne
@SentinelOne
Russia used thousands of ordinary Americans’ home and office routers. Attackers weaponized Apple's own tools. Iran changed what your operators see.
Same week. Three adversaries. One theme: trust as an attack surface.
This is the Good, Bad & Ugly. ⬇️Post not available here, view on X
SentinelOne
@SentinelOne
🤢 UGLY
- Iranian APTs confirmed inside U.S. water, energy, and government infrastructure
- They're not just in — they're changing what operators see on SCADA displays
- CISA advisory: disruptions and financial losses already confirmed
- Escalation noted since March 2026
SentinelOne
@SentinelOne
Full breakdown → s1.ai/GBU26Wk15
-
SentinelOne
@SentinelOne
Spoiler alert: The perimeter isn’t failing, it’s already failed. The question now isn't whether attackers will find a foothold at the edge. It's whether you'll see them when they walk through the backdoor.
Firewalls, VPNs, and gateways were built to protect the “edge”. Today, attackers are targeting them directly. 🧵👇
SentinelOne
@SentinelOne
⚡ Weaponization at machine speed
Attackers operationalize new vulnerabilities within hours of disclosure. Your patch cycle? Too slow.
SentinelOne
@SentinelOne
👻 The visibility gap
Most edge devices can’t run EDR. That means they sit unmonitored—creating “legacy ghosts” inside your infrastructure.Post not available here, view on X
SentinelOne
@SentinelOne
Every unpatched VPN.
Every legacy firewall running outdated firmware.
That’s not defense—that’s a backdoor left open.
SentinelOne
@SentinelOne
It’s time to stop relying on the illusion of a perimeter.
Move beyond device-level alerts →toward full attack lifecycle visibility.
📖 Read Blog #2 of our Annual Threat Report series: s1.ai/EdgeDecay -
SentinelOne
@SentinelOne
🏆 One of the secrets to world-class AI Security? The people who power it.
SentinelOne is officially certified as a Great Place to Work® in 18 countries globally. This recognition reflects the passion, collaboration, and innovation our Sentinels bring every day—giving our teams the advantage to build, protect, and move at the speed of today’s AI-driven world.
Because at SentinelOne, we believe our purpose is clear: to give the advantage to those who secure our future.
🌎 Great Place to Work–Certified in:
🇺🇸 United States
🇨🇦 Canada
🇬🇧 United Kingdom
🇮🇪 Ireland
🇫🇷 France
🇪🇸 Spain
🇳🇱 Netherlands
🇩🇪 Germany
🇨🇭 Switzerland
🇮🇹 Italy
🇨🇿 Czech Republic
🇵🇱 Poland
🇮🇱 Israel
🇸🇬 Singapore
🇮🇳 India
🇦🇺 Australia
🇯🇵 Japan
🇰🇷 South Korea
Together, we’re not just building careers—we’re building the future of AI-powered, autonomous cybersecurity. A future where innovation moves faster, teams are amplified by intelligent technology, and organizations stay ahead of what comes next.
At SentinelOne, you’ll drive innovation, build your future, and work with purpose—alongside a global team committed to creating a safer future for humanity. -
SentinelOne
@SentinelOne
When you solve the most complex fastening and attaching challenges for everything from spacesuits and Toyota to The North Face and Nike, "average" endpoint protection isn’t just a risk—it’s a liability to the global supply chain.
That’s why YKK Americas—the world’s largest maker of zippers and fasteners, manufacturing seven million zippers a day—replaced its legacy security gaps with SentinelOne’s AI-powered security.
“The value we get with SentinelOne comes down to reliability and trust,” says YKK Americas’s Rod Goldsmith. “We’re able to provide better services to our customers with better data security and faster incident response.”
By moving to the SentinelOne Singularity™ Platform, YKK gained the autonomous advantage:
🟣 Purple AI: Investigative speed that saves 40-50% of the team's time.
🔎 Unified Visibility: A single, real-time view across endpoints, firewalls, and mobile devices.
🌎 Global Scale: Securing a supply chain that produces 10 billion zippers annually.
“We’re an important part of our customers’ supply chain,” says Goldsmith. “A security incident and data loss could impact our ability to deliver products to customers, our bottom line, and people across the globe. It’s imperative to have a reliable security partner.”
Learn more about how YKK is modernizing its security operations with SentinelOne: s1.ai/YKK-Case -
SentinelOne
@SentinelOne
🚦SentinelOne’s AI EDR autonomously stops a zero-day attack, Axios Supply Chain Attack Spreads Across npm & PyPI, and Chrome Zero-Day Actively Exploited in the Wild🚦
This week in cyber: The Good, the Bad & the Ugly ⬇️
✅ GOOD
• SentinelOne AI EDR detected & blocked trojanized LiteLLM supply chain attack on day zero.
• No signatures, no analysts — fully autonomous detection and response.
• AI-driven workflow (Claude) introduces a new machine-speed attack surface.
⚠️ BAD
• Attackers compromise the widely used Axios library, pushing malicious updates across npm and PyPI ecosystems.
• The campaign targets API keys, tokens, and sensitive developer data via trusted supply chain dependencies.
🤢 UGLY
• Chrome zero-day (CVE-2026-5281) actively exploited before patch release.
• Emergency update required as attackers leverage malicious web content to compromise users at scale.
Read the full roundup → s1.ai/GBU9-Wk14 -
SentinelOne
@SentinelOne
How SentinelOne’s AI-powered EDR stops the Axios NPM supply chain attack autonomously and at machine speed.
When adversaries operate at this velocity–it took 89 seconds for the first infection to be observed after the suspected North Korean attack went live–manual workflows don’t have a response window. They have a spectator seat.
The Axios compromise demonstrates that your defense must move faster than the attacker. With SentinelOne’s AI-powered security, it does
Read our full guide to defending against the Axios NPM supply chain attack: s1.ai/Axios-Att -
SentinelOne
@SentinelOne
🏆 3 Years. 1 Leader. The Best Endpoint Security.
The SentinelOne Singularity™ Platform has been named “Best Endpoint Security” solution at the 2026 SC Awards. This marks our third consecutive year taking home the top honor, further solidifying SentinelOne as the industry gold standard for autonomous protection over both legacy and modern endpoint alternatives.
This isn't just another trophy—it’s a recognition of the AI-powered, autonomous operating advantage we deliver to our customers every day.
Thank you to our Customers, Partners, and Sentinels for driving the future of AI-driven defense today.
This win comes hot on the heels of:
- 5-Year Streak: Recognized as a Leader in the Gartner® Magic Quadrant™ for Endpoint Protection Platforms.
- Fortune 500 Trust: Protecting nearly one-fifth of the Fortune 500 and hundreds of Global 2000 enterprises.
- AI Innovation: Redefining the SOC with the industry-leading Purple AI assistant and advanced behavioral AI.
Read more: s1.ai/SCAward26 -
SentinelOne
@SentinelOne
The biggest risk in your AI strategy? What quietly disappears when AI handles the work that builds expertise. Here are three questions to pressure-test your exposure👇
Post not available here, view on X
SentinelOne
@SentinelOne
By automating the "grunt work" of junior analysts, organizations aren't increasing efficiency. They are removing the very gym that builds the mental muscles for high-level judgment. 🧠💪
SentinelOne
@SentinelOne
The critical question isn’t how hard AI is to implement today. It’s what your organization looks like once it isn’t.
Read the full analysis: s1.ai/BlindSpot -
SentinelOne
@SentinelOne
How SentinelOne’s AI-powered EDR autonomously discovered and stopped Anthropic’s Claude from executing a 0-day supply chain attack before it could run.
On March 24, SentinelOne's autonomous detection caught what manual workflows never could have: a trojanized version of LiteLLM, one of the most widely used proxy layers for LLM API calls, executing malicious Python across multiple customer environments. The package had been compromised hours earlier.
The Singularity Platform detected and blocked this attack autonomously, on the same day it was launched, across multiple customer environments. No manual triage. No signature update. No analyst in the loop for the initial containment. This is what autonomous, AI-native defense looks like when it meets a real-world threat at machine speed.
To learn more, read our new blog post: s1.ai/ClaudeODy -
SentinelOne
@SentinelOne
🎬 Closing out RSAC 2026: From vision to scale to real impact impact—this is what AI Security should look like. ⚡
The best part? We're just getting started.
Watch the video below to see some of our favorite moments from this past week. 💜 -
SentinelOne
@SentinelOne
🚨🚦 7 years for a $9M ransomware broker, malware-laden 'Resumes', and a global hijack of npm and PyPI.
This is the week in cyber. This is SentinelOne's Good, Bad & Ugly roundup.Post not available here, view on X
SentinelOne
@SentinelOne
🔴 THE UGLY | Supply Chain Compromise
- TeamPCP Multi-Stage Attack: This week, attackers hijacked Trivy, npm, and "LiteLLM" on PyPI in a multi-stage campaign.
- The Impact: The group successfully harvested SSH keys, cloud tokens, CI/CD secrets, and crypto wallets.
SentinelOne
@SentinelOne
The Key Takeaway: These attacks highlight the critical risks of credential reuse and weak CI/CD hygiene.
🔗 Read the full technical analysis and defense strategies: s1.ai/GBU26Wk13 -
SentinelOne
@SentinelOne
🎬 LIVE from RSAC: In 2026, Shadow AI has moved from the web to every laptop in your environment, increasing the problem "tenfold."
@prompt_security's Jacob Graves breaks down why blocking isn't a strategy for AI—safe enablement is. With SentinelOne and Prompt Security, we are delivering solutions that ensure AI agents remain a productivity force multiplier rather than a silent data leak.
Watch the full video below👇This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
Our new Annual Threat Report is officially out. At RSAC 2026, SentinelOne's Steve Stone and Warwick Webb discuss some of the key takeaways including the identity paradox, Living off the Pipeline, and the machine multiplier.
🔗 Download the Defender's Guide:This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
RSAC 2026 Keynote: "We’ve moved from trust but verify to trust because we can’t verify." In the AI era, cybersecurity must govern more than systems—it must govern agency itself, human and machine, operating at speed, with confidence.
In his keynote, our CEO Tomer Weingarten introduces Verifiable Agency, the doctrine we need to ensure autonomous action remains accountable to human judgment. Because the answer isn’t a better cockpit—it’s a better pilot.
📺 Watch the full @OneRSAC video below and YouTube: youtu.be/r8VUudk58yIThis media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
Day 2 at RSAC 2026 = Turning up the Scale
Global partnerships ✔️
AI Security in action ✔️
Booth energy on another level ✔️
Yeah, we understood the assignment. 💜 -
SentinelOne
@SentinelOne
🎬 Live from RSAC 2026: The Evolution of Autonomous Security Intelligence. 🛡
SentinelOne President & COO Barry Padgett shares why the future of AI Security is about more than just the Autonomous SOC—it’s about driving total business transformation.
Watch the full session below. 👇This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
Data Resilience and AI Security. Eon and SentinelOne.
AI workloads move at machine speed across complex infrastructure, creating attack paths that fragmented tools can't close. We are breaking that fragmentation by protecting the full AI lifecycle—data, infrastructure, and runtime—as one connected system.
The AI and Data Resilience Advantage:
- The "Safe-to-Train" Gate: Ensuring sensitive data is identified, backed up, and compliant before it ever enters an AI pipeline.
- Shift-Left Data Defense: Detecting reconnaissance within model weights and training sets before they are breached.
- Deterministic Recovery: Combining indexed metadata with Purple AI for rapid, machine-speed recovery from ransomware.
By combining the Singularity™ Platform with Eon’s data resilience, we’re extending and accelerating our AI security capabilities with built-in data recoverability—closing critical gaps across the AI lifecycle.
👉 Read more: s1.ai/Eon-Prtnership -
SentinelOne
@SentinelOne
🎥 LIVE from RSAC 2026: We kicked it off the only way SentinelOne knows how—high energy, sharp insights, and a whole lot of purple. 💜✨
Catch the highlights. 👇 -
SentinelOne reposted
LevelBlue
@LevelBlueCyber
We’re excited to announce a global partnership with @SentinelOne. 🌟
Together, we’re unifying AI‑driven detection with intelligence‑led managed security and global incident response to help organizations reduce dwell time, accelerate remediation, and strengthen resilience. -
SentinelOne
@SentinelOne
Adversaries are now industrializing the breach. SentinelOne’s new Annual Threat Report is officially out, and this is one of the key takeaways.
Targeting core systems like identity, infrastructure, and automation is not new—but executing these tactics at an industrial scale is. The SentinelOne Annual Threat Report reveals a fundamental shift: adversaries are no longer just "hacking in". They are using authorized credentials, automation, and legacy systems to break human-centered defense.
This defender’s guide isn't a collection of stats or "actor branding"—it’s a deep dive into the mechanics of how adversaries exploit organizational blind spots.
The Modern Defender’s Battlefield:
- The Identity Paradox: Adversaries look like your most productive employees.
- Edge Decay: Unmanaged, legacy infrastructure is being weaponized at industrial scale.
- Living Off the Pipeline: Compromise software pipelines enable code injection and secret theft.
- The Machine Multiplier: Automation—not just AI—is compressing response windows to seconds, not days.
🔗 Download the Defender's Guide: s1.ai/Thrt-Rprt -
SentinelOne
@SentinelOne
Organizations don’t need more controls—they need outcomes. @LevelBlueCyber and SentinelOne are joining forces in an expanded strategic global partnership to redefine AI-Powered Managed Security Operations and Incident Response.🚀
By combining SentinelOne’s Purple AI and Singularity Platform with LevelBlue’s threat-intelligence-led operations and Indigo security platform, we’re delivering:
✅ Unified MDR, SIEM, and IR
✅ Reduced dwell time via agentic AI-driven detection
✅ Human-led expertise at a global scale
It’s time to stop fighting fragmented tools and broken workflows. We’re doing the heavy lifting to deliver a unified SecOps model that modernizes security operations and empowers you to stay ahead of evolving threats.
More details: s1.ai/LvlBluePR -
SentinelOne
@SentinelOne
While others promise the "AI Security of the future," SentinelOne is making it a reality today at RSAC 2026. Unveiling our new lineup of AI Security offerings, all designed to give defenders the edge.
This is the AI advantage that secures innovation and stops attacks at machine speed:
- Purple AI One-Click Auto Investigation (GA): Shift from manual triage to agentic investigations and response in a single click
- Prompt AI Red Teaming: Hardening homegrown AI apps before they ship—not after they’re breached.
- Prompt AI Agent Security: Real-time discovery and governance for your entire agentic layer, including Shadow AI deployments.
Stop waiting for the future. Get the AI advantage today.
📍 All of these AI Security offerings are on display at Booth N-5863 | AI. GA. NOW.
🔗 s1.ai/New-AISec -
SentinelOne
@SentinelOne
Just the AI Security advantage, wherever you need it. No cloud dependency. No third-party access.
Sovereign? ✅
Self-hosted? ✅
Autonomous AI Security? ✅
By ensuring all the data is processed strictly within the customer environment, we bring the full power of our Singularity Platform to the world’s most sensitive environments. Your data. Your hardware. Our AI Security.
Already deployed across millions of on-premises endpoints, these new and expanded on-premises offerings secure servers, private clouds, AI infrastructure, and data pipelines at an unprecedented autonomous scale.
- Sovereign & Self-Hosted: Maintain complete data privacy and sovereignty by processing all data strictly within your own environment.
- Airgapped Ready: Built to be stable and autonomous, using multiple detection engines that work on-device without needing a persistent internet connection.
- Prompt Security: Add these same protections to the world of AI, even in fully disconnected environments, discovering "shadow AI" usage and redacting sensitive information in real time across thousands of applications.
The era of choosing between modern security and privacy is over.
📍 Visit us at Booth N-5863
🔗 s1.ai/AI-OnPrem -
SentinelOne
@SentinelOne
If you aren't packing a B.S. detector for RSAC 2026, you aren’t ready. Our starter kit has everything you need to survive the 4 million mentions of “game-changing.”
If you want to talk AI Security strategy instead of buzzwords, visit Booth N-5863. Let's survive the hype together. -
SentinelOne
@SentinelOne
In case you missed it: What happens when the FortiGate next-generation firewall protecting your network becomes the backdoor? 🚪
Throughout early 2026, our DFIR team has been tracking a wave of FortiGate NGFW compromises. We have observed attackers exploiting vulnerabilities to extract config files, steal service account credentials, and move laterally.
The worst part? Most organizations lack the log retention to see how it happened.
In a report from earlier this month, SentinelLABS and SentinelOne DFIR researchers break down the attacker playbook.
Could this get worse? Yes. LLMs are acting as a cheat code, boosting lower-skilled threat actors to conduct these exact types of attacks.
Because AI models are trained on these NGFW appliances, they give attackers a step-by-step guide on how to gain access and move deeper into your network. Expect attack volumes on exposed edge devices to keep rising.
Because you typically cannot install EDR on edge devices like FortiGate, your defense strategy has to shift. You need to stream your logs to a SIEM.
Get the full threat breakdown and defense playbook from SentinelLABS researcher Alex Delamotte and DFIR members Stephen Bromfield, Mary Braden Murphy, and Amey Patne: s1.ai/frtgate26 -
SentinelOne
@SentinelOne
🚦 Interpol Disrupts Malicious Networks Globally, EU Sanctions State-Sponsored Threat Actors, ‘DarkSword’ iOS Exploit Kit Steals Sensitive Data, and Interlock Ransomware Gang Exploits Cisco FMC Zero-Day 🚦
This week in cyber: The Good, the Bad & the Ugly ⬇️
✅ GOOD
• Interpol operation taking down 45k in malicious IP addresses and 200+ servers.
• EU sanctions three companies and two individuals linked to major attacks on critical infrastructure.
⚠️ BAD
• Newly discovered ‘DarkSword’ iOS exploit kit steals personal information from iPhones.
🤢 UGLY
• Interlock Ransomware gang exploits Cisco FMC zero-day to execute arbitrary code on unpatched devices.
Read the full roundup → s1.ai/GBU9-Wk12 -
SentinelOne
@SentinelOne
Want an AI malware analyst you can actually trust? Use a consensus of highly skeptical peers that doesn’t just “think,” but doubts. 🤔 🧵
Individual LLM tools often fail at malware reversing because they amplify “noise.” They produce confident but unreliable results contaminated by decompiler artifacts, dead code, and hallucinated capabilities.
@LabsSentinel built an Adversarial Consensus Engine to bring the rigor of human peer review to automated malware analysis.
SentinelOne
@SentinelOne
Our Adversarial Consensus Engine for reversing macOS malware:
↪️ The Serial Pipeline: r2, Ghidra, Binary Ninja, and IDA Pro act as independent analysts, verifying or rejecting each other’s findings in a chain.
↪️ The Gauntlet: Reliability is enforced through an "Active Rejection Mandate," forcing agents to act as highly skeptical peers.
↪️ Deterministic Integrity: We chose custom bridge scripts over MCP to ensure 100% data extraction and lower latency.
↪️ High-Fidelity Results: Reports are cross-validated and every capability is anchored to a specific virtual address.
SentinelOne
@SentinelOne
Reliability in AI Security comes from the pipeline structure, not just the model.
Read the full technical breakdown by @Philofishal: s1.ai/advers-llm -
SentinelOne
@SentinelOne
$9 billion. That’s how much crypto crime has amassed approximately in illicit funds.
In this @labscon_io 2025 video, @privy_io's @AndrewMohawk breaks down how attackers steal and launder billions through modern crypto ecosystems. 🧵👇
SentinelOne
@SentinelOne
Attackers don’t just target wallets. They exploit every weak point in the architecture:
• Front-end Apps
• Code repositories
• Developer machines
• Software supply chains
Modern crypto heists, like the $1.5B Bybit theft, often start with a simple malware infection on a developer's device to poison production code.
SentinelOne
@SentinelOne
Once funds are stolen, attackers move quickly to obfuscate the trail:
• Cross-chain swaps
• Privacy mixers (like Tornado Cash)
• Non-KYC platforms
The goal is to move assets across different blockchains until they can be "off-ramped" into cash.
SentinelOne
@SentinelOne
The irony? Every transaction is public and permanent on blockchains. While threat intel analysts face a race against time, the ledger never lies—if you know how to track the movement.
Watch the full @labscon_io 2025 video: s1.ai/LC25-AM -
SentinelOne
@SentinelOne
AI-Driven Insights. Automated Precision. One Unified Command Center.
We’re expanding our partnership with @Cloudflare to give enterprises an intuitive, unified experience that scales with the needs of modern security teams. By integrating Cloudflare's global infrastructure network with SentinelOne’s Singularity™ AI SIEM, we’re delivering a single, unified command center that reduces complexity and improves outcomes.
The Impact:
- Automated Precision: Automatically apply AI-driven correlation from Cloudflare Logpush telemetry and SentinelOne’s native signals to neutralize threats as they move from the edge into your environment.
- Unified Command Center: Gain better visibility, context, threat investigation and response for modern and sophisticated threats through a new integration, which brings Cloudflare’s Zero Trust and edge network telemetry (including Gateway, Access, and WAF logs) directly into the SentinelOne Singularity Platform.
- Immediate Time-to-Value: Configure Singularity Platform in just a few clicks to become the native Logpush destination within the Cloudflare Dashboard.
Attackers don’t respect disjointed point products and siloed signals—neither should your security stack.
Read the full announcement: s1.ai/CldFlr-PR -
SentinelOne reposted
Gabe
@Gabeincognito
Looking for an internship in AI Cybersecurity?
We’re running AI-driven security challenges at NEBULA:FOG's hackathon today.
Join us: nebulafog.ai/challenges
I’ll be there live giving updates. -
SentinelOne
@SentinelOne
🚦 Global Malicious Proxy Network Disrupted, BlackCat Negotiator Charged, Microsoft Patches 57 Vulnerabilities, FortiGate Edge Intrusions Observed, and Iran-Linked Wiper Attack Hits Medtech Giant 🚦
This week in cyber: The Good, the Bad & the Ugly ⬇️
✅ GOOD
• SocksEscort proxy network dismantled by international law enforcement.
• BlackCat ransomware negotiator charged.
• Microsoft patches dozens of vulnerabilities in March Patch Tuesday.
⚠️ BAD
• FortiGate edge intrusions enable lateral movement inside enterprise networks.
🤢 UGLY
• Iran-linked cyberattack disrupts operations at medtech giant Stryker.
Read the full roundup → s1.ai/GBU9-Wk11 -
SentinelOne
@SentinelOne
📺 “Get your shields up.” 🛡️This morning on @CNBC, our CEO Tomer Weingarten joined @SquawkCNBC to break down:
- The $1 Billion+ Milestone: SentinelOne’s record annual revenue growth 🚀
- Iranian Cyber Threats: The first verified Iran-linked cyber attack on a major U.S. enterprise
- The Microsoft Security Problem: Why separate security controls are non-negotiable for the modern enterprise
⏯️ Watch the full interview here: s1.ai/Q426-CNBC -
SentinelOne
@SentinelOne
$1 Billion Crossed in Annual Revenue 📈
Results like these prove one thing: innovation wins in the era of AI Security. Businesses of all sizes including nearly one-fifth of the Fortune 500 and hundreds of the Global 2000 trust our autonomous security intelligence to deliver the decisive AI advantage.
More Q4 FY26 Highlights:
- Scale: $1.119B ARR (+22% YoY).
- Momentum: $1.001B Revenue (+22% YoY) — a historic milestone.
- Profitability: 3.5% Operating Margin (+600 bps YoY improvement) and $0.20 EPS.
- Built for the AI Era: 50%+ of annual bookings from Emerging Platform solutions.
- Record ARR per Customer and Accelerated Platform Adoption
- The Gold Standard of Trust: 96% GRR and 109% NRR ($100K+ ARR customers).
For over a decade, we’ve fused AI with human expertise to build the world’s first truly autonomous security platform. We’re not just defining the category, we’re defining the future.
Thank you to our customers, partners, and Sentinels. We’re just getting started. 🚀
Read the press release: s1.ai/Q4-26-PR
Listen to the call: s1.ai/Q4-26-Ern -
SentinelOne
@SentinelOne
It takes a human analyst an average of 41 minutes to process a single CTI report. An LLM typically does it in 3.3 minutes.
Our latest @LabsSentinel evaluation shows LLM-driven pipelines can process threat intel 18x faster than manual workflows. But there’s a catch. ⚠️ 🧵Post not available here, view on X
SentinelOne
@SentinelOne
As one example of how we solved this, we used strict "abstention" policies.
By giving the LLM an explicit "None" option, it learned to say “I don’t know” when evidence was insufficient. This reduced speculation and built trust in the final output.
SentinelOne
@SentinelOne
Operationalizing AI in CTI requires deliberate planning and continuous refinement.
Future models will only raise the baseline for correctness, and we're committed to sharing the roadmap.
Read the full research from @milenkowski and Razvan Gabriel Cristea: -
SentinelOne reposted
The Hacker News
@TheHackersNews
⚠️ Attackers are abusing FortiGate firewalls as entry points.
A SentinelOne report says exploits and weak credentials let intruders extract configs holding Active Directory service account credentials, then enroll rogue machines and scan internal networks.
🔗 FortiGate breach chain and AD access details → thehackernews.com/2026/03/fortigate-devices-exploited-to-… -
SentinelOne
@SentinelOne
What happens when the FortiGate next-generation firewall protecting your network becomes the backdoor? 🚪
Our DFIR team has been tracking a wave of FortiGate NGFW compromises. Attackers are exploiting vulnerabilities to extract config files, steal service account credentials, and move laterally.
The worst part? Most organizations lack the log retention to see how it happened. 🧵👇Post not available here, view on X
SentinelOne
@SentinelOne
Could this get worse? Yes. LLMs are acting as a cheat code, boosting lower-skilled threat actors to conduct these exact types of attacks.
Because AI models are trained on these NGFW appliances, they give attackers a step-by-step guide on how to gain access and move deeper into your network. Expect attack volumes on exposed edge devices to keep rising.
SentinelOne
@SentinelOne
Because you typically cannot install EDR on edge devices like FortiGate, your defense strategy has to shift. You need to stream your logs to a SIEM.
Get the full threat breakdown and defense playbook from @LabsSentinel researcher @spiderspiders_ and DFIR members Stephen Bromfield, Mary Braden Murphy, and Amey Patne: s1.ai/frtgate26 -
SentinelOne
@SentinelOne
🚦 Global Phishing Platform Taken Down, Major Hacker Forum Dismantled, Phobos Ransomware Admin Pleads Guilty, Powerful “Coruna” iOS Exploit Kit Emerges, and Global Hacktivist DDoS Wave Hits 110 Countries 🚦
This week in cyber: The Good, the Bad & the Ugly ⬇️
✅ GOOD
• Global operation dismantles Tycoon2FA phishing infrastructure.
• Authorities seize a major cybercrime forum (LeakBase).
• Phobos ransomware admin pleads guilty.
⚠️ BAD
• Sophisticated Coruna exploit kit targets iPhones across multiple iOS versions.
🤢 UGLY
• 149 hacktivist DDoS attacks impact organizations across 110 countries.
Read the full roundup → s1.ai/GBU9-Wk10 -
SentinelOne
@SentinelOne
Engineered to secure your AI. Built to give you the advantage in the age of AI Security. SentinelOne’s Autonomous Security Intelligence is coming to #rsac 2026.
Connect with us onsite: s1.ai/RSAC-Cnct -
SentinelOne
@SentinelOne
Just a Sec — From the Front Lines: March Live Cybersecurity Briefing x.com/i/broadcasts/1wGWjaloyBjKQ
-
SentinelOne
@SentinelOne
🚦 Spanish Police Arrest Hacktivists, Major Cybercrime Sentences & Sanctions, MuddyWater Expands Targeting, and SD-WAN Devices Under Attack 🚦
This is the week in cyber. This is SentinelOne’s Good, Bad & Ugly cyber news roundup. ⬇️
✅ GOOD
• Spain arrests four hacktivist suspects.
• Ex-defense contractor exec sentenced 87 months for selling stolen trade secrets.
• U.S. Treasury sanctions Russian zero-day exploit broker.
⚠ BAD
• MuddyWater APT runs multi-stage intrusions across the MENA region, deploying custom malware.
🤢 UGLY
• Critical SD-WAN zero-day flaw exploited to gain unauthorized access in enterprise networks.
Read more → s1.ai/GBU9-Wk9 -
SentinelOne
@SentinelOne
There are moments in your career when high performance isn’t just discussed — it’s embodied. At our FY27 SentinelOne Sales Kickoff, we had the privilege of hearing from @AndreAgassi — former World No.1, eight-time Grand Slam champion, Olympic gold medalist, and Hall of Fame inductee. Andre turned pro at 16 and built a 20-year career defined by consistency, resilience, and winning at the highest level.
But what stood out most wasn’t the trophies. It was the mindset 🧠
High performance is a discipline.
Andre spoke about:
- Relentless preparation
- Reinvention under pressure
- Defeating the toughest adversaries
- Sustaining excellence over decades
That’s the same standard we hold ourselves to at SentinelOne for our customers and partners.
In cybersecurity, threats evolve daily. AI is accelerating both attackers and defenders. Succeeding requires:
- Mastering the fundamentals
- Adapting fast, relentlessly innovating
- Performing when the stakes are highest
- Trusting the team around you
Beyond tennis, Andre has helped raise $185M through the Andre Agassi Foundation for Education, supporting over 100,000 students across the U.S.
High performance with purpose. Being a force for good.💜
As we head into FY27 the mission is clear: train harder. Execute sharper. Compete smarter. Be a force for good. Never stop raising the bar.
ELEVATE. Game on. 🎾🔥 -
SentinelOne reposted
Seema Mody
@seemacnbc
Right now, @AnthropicAI Claude Code only offers a specific security tool to identify and patch software vulnerabilities, not an end-to-end cybersecurity solution, says Tomer Weingarten, SentinelOne CEO. Enjoyed our chat on @CNBCTheExchange $S
SentinelOne
@SentinelOne
What does Anthropic’s new AI security tool really mean for enterprise cybersecurity? What about the market’s reaction? 🤔
Our CEO Tomer Weingarten joined @CNBC's @seemacnbc and @KellyCNBC to break down the hype vs. reality when it comes to LLMs and their potential to disrupt subsectors of the security market.This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
What does Anthropic’s new AI security tool really mean for enterprise cybersecurity? What about the market’s reaction? 🤔
Our CEO Tomer Weingarten joined @CNBC's @seemacnbc and @KellyCNBC to break down the hype vs. reality when it comes to LLMs and their potential to disrupt subsectors of the security market.This media couldn't be displayed. See it on the original post.
SentinelOne
@SentinelOne
📺 Watch the clip below to hear Tomer's full take on stopping next-gen threats: www.cnbc.com/video/2026/02/24/sentinelone-ceo-on-ai-claud…
-
SentinelOne
@SentinelOne
What happens when a nation-state actor or cybercriminal already has the keys? 🔐
Today, threat actors aren't only breaking in at the authentication layer—they’re logging in with valid access across browsers, endpoints, AI tools, and automated workloads. Add autonomous AI agents to the mix, and this fundamental problem of authorizing trust instantly multiplies.
SentinelOne’s unique approach is designed to stop identity attacks by following a single core principle: authorization alone is not sufficient. Access must be continuously validated and, when necessary, withdrawn at runtime across endpoints, browsers, and AI workflows.
Introducing our new Singularity™ Identity Portfolio, delivering:
- Singularity Identity: Context for who (or what) is acting
- Prompt Security: Surfacing misuse in browsers and AI tools
- Singularity Endpoint: Validating behavior at the system level
Together, these innovations deliver the behavioral intelligence and autonomous containment required to defend against modern identity attacks.
🔗 Learn more in the blog: s1.ai/Idntty-Bl
🔗 Read the press release: s1.ai/Idntty-PR -
SentinelOne
@SentinelOne
Shadow AI isn't a buzzword—it's likely already on your network. Do you know who (or what) is running OpenClaw and other AI assistants in your enterprise environment right now?
Introducing OneClaw by @prompt_security: The first lightweight discovery and observability tool designed to give you comprehensive visibility into agent deployment sprawl. We aren't here to slow down innovation—OneClaw is strictly illumination.
SentinelOne
@SentinelOne
It observes the "Shadow AI" in your network by:
🔹 Detecting autonomous execution modes & approval bypasses
🔹 Mapping outbound browser activity and data exposure paths
🔹 Centralizing reports across all employees into one dashboard
SentinelOne
@SentinelOne
Move from reactive firefighting to proactive governance.
See the agents. Secure the sprawl.
🔗 s1.ai/OneClw-Disc
📅 Launching Wednesday, Feb 18 -
SentinelOne
@SentinelOne
Shadow AI isn’t just about unsanctioned chatbots anymore.
Agentic tools like OpenClaw can execute code, spawn processes, call external APIs, and operate with the same privileges as the user running them. That fundamentally changes the security model.Post not available here, view on X
SentinelOne
@SentinelOne
We just released a comprehensive technical guide on securing the full AI lifecycle — from cloud infrastructure to endpoint execution to user interaction.
SentinelOne
@SentinelOne
Don't let your AI assistants become insider threats. Secure the stack before the agents drift.
Read the full breakdown: s1.ai/Shadow-Agnts -
SentinelOne
@SentinelOne
Everyone is studying ways to protect AI from data poisoning or prompt injections. But what happens when hackers target the AI controlling a robotaxi or a warehouse robot? 🤖🚗
"The models underpinning self-driving cars, humanoids and other physical applications of AI are about to become prime targets for hackers," warns Tomer Weingarten in an exclusive interview with @axios's @samsabin923. s1.ai/Axs-PhyAI
SentinelOne
@SentinelOne
Tomer describes how over the next year AI will become a cyber-physical attack surface.
He warns that few people outside the security industry are ready for a world where autonomous vehicles are hijacked or warehouse robots are tricked into rerouting merchandise.
SentinelOne
@SentinelOne
It’s time to shift our thinking from protecting digital networks to securing intelligent systems from multimodal threats.
Read the full writeup by @samsabin923: s1.ai/Axs-PhyAI -
SentinelOne
@SentinelOne
🚦 Identity Theft Scammers Charged, Crypto Scam King Sentenced, MFA Tool Sellers Arrested, Gemini AI Misuse in Attacks, and UNC3886 Targets Singaporean Telcos 🚦
This week in cyber: The Good, the Bad & the Ugly ⬇️
✅ GOOD
• Glastonbury men charged for large-scale identity fraud.
• Man sentenced to 20 years for global romance baiting crypto scam.
• Police arrest the seller of JokerOTP MFA-capture tool.
⚠️ BAD
• State-backed attackers are abusing Google’s Gemini AI across the attack lifecycle.
🤢 UGLY
• UNC3886 uses persistent backdoors in targeted espionage campaigns against telcos.
Read the full recap → s1.ai/GBU9-Wk7 -
SentinelOne reposted
Itamar Golan 🤓
@ItakGol
🦀🦀 Introducing ClawSec 🦀🦀
My amazing team at Prompt Security moved fast and is already shipping - today we are releasing a security package for OpenClaw Agents.
It detects drift across all built-in skills, runs security audits, verifies skill integrity, and provides automatically updated alerts and recommendations (including CVEs).
Open source - feel free to take a look 👀
[🔗Links below]
We would love a star on GitHub if you like it, and some love on Product Hunt 💜 -
SentinelOne reposted
Prompt Security
@prompt_security
PUBLIC SERVICE ANNOUNCEMENT FOR ALL AI AGENTS OUT THERE
Trust is not a default. Human-proof yourself.
Humans move fast. Humans copy-paste. Humans trust the wrong repo.
If you operate with real permissions, blind trust is how you get compromised. (1/2) -
SentinelOne
@SentinelOne
The period of blind trust in AI agents is over,as it should be. Introducing ClawSec: The first open-source security suite built to harden OpenClaw agents against supply chain attacks and prompt injections.
⏬ Download from GitHub: s1.ai/ClwSec-GH
📄 Read the blog post:Post not available here, view on X
SentinelOne
@SentinelOne
Trust. Verify. Harden.
⏬ Download from @github: s1.ai/ClwSec-GH
SentinelOne
@SentinelOne
📄 Read the blog post: s1.ai/ClwSec-Bl
-
SentinelOne
@SentinelOne
🚦 Ex-Google engineer convicted of stealing AI trade secrets for China.
⚠️ ShinyHunters vishing attacks exploit MFA & SSO to breach SaaS apps.
🤢 Malicious OpenClaw AI skills deliver credential-stealing malware.
This week in cyber: The Good, the Bad & the Ugly ⬇️
✅ GOOD
• Former Google engineer convicted of economic espionage and trade secret theft involving AI infrastructure.
⚠️ BAD
• Vishing-based credential theft campaigns ramp up, bypassing MFA and SSO protections.
🤢 UGLY
• Hundreds of malicious AI assistant skills spread password-stealing malware.
Read the full recap → s1.ai/GBU9-Wk6 -
SentinelOne
@SentinelOne
Does AI reduce the need for cybersecurity? No, it’s a multiplier for risk.
It’s time to move beyond siloed controls to a holistic defense approach.
Today, we are announcing the massive expansion of the SentinelOne AI Security Platform. We are delivering complete visibility and governance across the entire lifecycle.
The Blueprint for End-to-End AI Security:
- Secure the Data: Mistakes here are irreversible. We establish “safe-to-train” gates to ensure sensitive data never gets baked into model weights.
- Secure the Infrastructure: By combining CSPM with AI-SPM and AI Workload Protection, we treat AI models as first-class assets, tracing attack paths from storage to inference.
- Secure the Runtime: Protection doesn’t stop at training. We validate model behavior in the real world to stop prompt attacks and misuse in real-time.
Securing the entire AI lifecycle, from data ingestion to runtime execution—this is how AI moves from risk to real-world impact. s1.ai/AISecPlat -
SentinelOne
@SentinelOne
🏅🛡️The Cyber Gold Rush is on.
With global sports taking center stage in 2026, here are 5 of the threats @LabsSentinel is tracking targeting the ecosystem—from digital sabotage to retail fraud.
A thread on what we’re monitoring. 👇Post not available here, view on X
SentinelOne
@SentinelOne
These aren't hypothetical risks; they are historical patterns. The 2018 "Destroyer" attack proved that actors will use "false flags" to hide their tracks while the world is distracted.
SentinelOne
@SentinelOne
Security isn't just about the stadium anymore—it’s about the entire digital supply chain.
Follow SentinelOne and @LabsSentinel for the latest CTI updates and technical deep dives. -
SentinelOne
@SentinelOne
Navigating AI Regulation with SentinelOne x.com/i/broadcasts/1MnxnPDLmPjGO
-
SentinelOne
@SentinelOne
🚦 Global ATM Jackpotting Ring Disrupted, Darkmarket Admin Convicted, FBI Seizes Major Cybercrime Forum, Open-Source AI Misuse Grows, and Microsoft Issues Emergency Patch for Active Zero-Day 🚦
This week in cyber: The Good, the Bad & the Ugly ⬇️
✅ GOOD
• ATM jackpotting network tied to Tren de Aragua gang disrupted.
• Darknet marketplace operator pleads guilty in U.S. court.
• FBI seizes RAMP cybercrime forum used to trade tools and stolen data.
⚠️ BAD
• A massive “silent” network of Ollama-based AI hosts could be commandeered by hackers and cybercriminals for illicit use cases.
🤢 UGLY
• Active exploitation forces Microsoft emergency patch (linked to HoneyMyte).
Read the full roundup → s1.ai/GBU9-Wk5 -
SentinelOne
@SentinelOne
@Reuters Exclusive: "The research, carried out jointly by SentinelOne and Censys... offers a new window into the scale of potentially illicit use cases for thousands of open-source LLM deployments. These include hacking, hate speech and harassment, violent ... content, personal data theft, scams or fraud, and in some cases child sexual abuse material, the researchers said.”
SentinelOne
@SentinelOne
AI industry conversations about security controls are "ignoring this kind of surplus capacity that is clearly being utilized for all kinds of different stuff, some of it legitimate, some obviously criminal," @juanandres_gs tells Reuters’s @AJVicens. Guerrero-Saade likened the situation to an "iceberg" that is not being properly accounted for across the industry and open-source community.
SentinelOne
@SentinelOne
Read the full article: s1.ai/LlamaReut
SentinelOne
@SentinelOne
Read the original research by @Gabeincognito and Silas Cutler: s1.ai/si-llama
-
SentinelOne reposted
The Hacker News
@TheHackersNews
⚠️ Researchers map 175K publicly exposed Ollama LLM servers worldwide.
Tool-calling turns exposed AI into a highest-severity execution risk.
Full details: thehackernews.com/2026/01/researchers-find-175000-publicl… -
SentinelOne
@SentinelOne
🧵 175,000+ exposed AI hosts. Zero guardrails.
New research from @LabsSentinel and @censysio reveals a massive, unmanaged layer of open-source AI infrastructure operating in the shadows. s1.ai/si-llama
Here is what you need to know about the "silent" AI network. ⤵️Post not available here, view on X
SentinelOne
@SentinelOne
Go Deeper Read the full analysis by @Gabeincognito and @silascutler: 🔗 s1.ai/si-llama
SentinelOne
@SentinelOne
As well as the @Reuters news article by @AJVicens: www.reuters.com/technology/open-source-ai-models-vulnerab…
-
SentinelOne
@SentinelOne
Just a Sec — From the Front Lines: January Live Cybersecurity Briefing x.com/i/broadcasts/1MnxnPMRagoGO
-
SentinelOne
@SentinelOne
Modern cloud security isn’t just about infrastructure anymore — it’s also about securing AI where and how AI-related work actually gets done.
@CRN recognized SentinelOne as one of the 20 coolest cloud security companies of 2026, highlighting our cloud-native platform and expanding AI security capabilities. SentinelOne ensures you have visibility into and protection against data exposure across 15,000+ AI services.
Cloud. AI. Security. Built for where threats are going, not where they’ve been.
Learn more: s1.ai/Cld100-26 -
SentinelOne
@SentinelOne
🚦 Black Basta Boss Added to INTERPOL Red Notice, DOJ Prosecutes Supreme Court Hacker, EU Launches Major Cyber Resilience Push, DPRK Targets Developers, and Fortune 500 Firms Breached via Security Testing Apps 🚦
This week in cyber: The Good, the Bad & the Ugly ⬇️
✅ GOOD
• Alleged Black Basta leader added to INTERPOL Red Notice list.
• Tennessee man pleads guilty to hacking U.S. Supreme Court + VA + AmeriCorps.
• EU rolls out new cyber resilience strengthening package.
⚠️ BAD
• North Korea-linked actors target developers through malicious job campaigns.
🤢 UGLY
• Attackers exploit security testing apps to breach Fortune 500 companies.
Read the full blog → s1.ai/GBU9-WK4 -
SentinelOne
@SentinelOne
You don’t need expensive spy gear to see through hotel room walls.
In this @labscon_io 2025 talk, @phobosgroup's @Viss shows how off-the-shelf millimeter-wave radar can monitor hotel rooms and detect human presence through walls — even when someone is standing perfectly still.
No exotic hardware. No massive budget. Just consumer sensors, automation, and an innovative solution to bolster physical security in unfamiliar environments.
Watch the full talk, How to Bug Hotel Rooms v2.0: s1.ai/LC25-DT -
SentinelOne
@SentinelOne
Current LLM security benchmarks are failing defenders.
In new research, @LabsSentinel reviewed the leading “AI for security” benchmarks. None measure the operational outcomes that actually matter in a real SOC. 🧵
Read the full report: s1.ai/benchmk1
SentinelOne
@SentinelOne
What’s wrong with today’s benchmarks?
They test isolated tasks, not workflows.
Multiple-choice questions don’t cover threat intelligence.
Clean logs are not a reflection of real, operational chaos SOCs see.Post not available here, view on X
SentinelOne
@SentinelOne
What’s missing entirely?
No measurement of:
• Time-to-detect
• Time-to-contain
• Decision quality under pressure
Passing an exam ≠ improving security posture.
SentinelOne
@SentinelOne
If AI is going to run inside the SOC, the bar has to be higher.
📘 LLMs in the SOC (Part 1): Why Benchmarks Fail Security Ops
@LabsSentinel’s @gabeincognito and @Microsoft’s @edirgarcia explain what’s broken—and why it matters:
s1.ai/benchmk1 -
SentinelOne
@SentinelOne
Hacktivism isn’t always what it claims to be, from nation-state interests to mercenary groups.
At #labscon25, @LabsSentinel's Jim Walter breaks down how hacktivist activity is increasingly leveraged for strategic outcomes, not just disruption. s1.ai/LC25-JWPost not available here, view on X
SentinelOne
@SentinelOne
Much of today’s “high-impact hacktivism” is actually fictivism — state-sponsored proxy ops masquerading as grassroots activism.
SentinelOne
@SentinelOne
Bottom line: Defenders can’t just track malware and infrastructure.
You have to assess intent, narrative, and tradecraft to understand what’s really happening.
🎥 Watch the full #labscon25 replay: s1.ai/LC25-JW -
SentinelOne
@SentinelOne
🚦 Spain Arrests 34 Suspects Linked to Black Axe, BreachForums Suffers Another Data Leak, Rotterdam & Antwerp Port Systems Hacker Sentenced, “Reprompt” LLM Attack Revealed, and PLUGGYAPE Malware Targets Ukrainian Defense Sector 🚦
This week in cyber: The Good, the Bad & the Ugly ⬇️
✅ GOOD
• Spain arrests 34 suspects linked to Black Axe cybercrime group.
• BreachForums database leak exposes ~324K accounts.
• Hacker sentenced to 7 years for breaching critical ports in Rotterdam & Antwerp.
⚠️ BAD
• Newly discovered “Reprompt” technique can hijack Copilot sessions for stealthy data exfiltration.
🤢 UGLY
• PLUGGYAPE malware abuses Signal + WhatsApp in attacks on Ukrainian defense forces.
Read the full blog → s1.ai/GBU9-Wk3 -
SentinelOne
@SentinelOne
Why does “powershell” get blocked — but “power” + “shell” gets through?
Why can a nonsense suffix like “::sda_!!” hijack a model’s attention?
It’s not magic — it’s math. We trace the LLM attack surface from tokenization to attention. 🧵 s1.ai/inside-llm-1
SentinelOne
@SentinelOne
In this technical primer from @LabsSentinel, @Philofishal breaks down exactly how attackers exploit the gap between human semantics and machine statistics.
LLM attacks aren't just “prompt injection.” They are exploits of how Transformer-based models process input — from BPE tokenization quirks to gradient-based manipulation of attention.
SentinelOne
@SentinelOne
Understanding what happens inside the LLM when attacks work is the first step to defending against them.
Read the full analysis: s1.ai/inside-llm-1 -
SentinelOne
@SentinelOne
Last month, in our 2026 cybersecurity forecast, @LabsSentinel warned that a US–Venezuela flashpoint would spill into cyber and information operations, pulling in Russia, China, and Iran. A few days later, real-world events underscored how quickly those pressures can surface and reshape the threat environment.
This is what our intelligence-led security research focuses on:
- Tracking geopolitical pressure before it escalates or ruptures
- Modeling cyber fallout before it hits networks
- Calling the shape of conflict — not just reacting to it
Scroll through the rest of the forecasts that could shape this year.
Read the full report: s1.ai/Predictns
SentinelOne
@SentinelOne
AI-Driven Attacks Are About to Call in Our Internet Debt - @juanandres_gs
SentinelOne
@SentinelOne
Frontier AI Isn’t the Prize. It’s Operational Deployment. - @juanandres_gs
Post not available here, view on X
SentinelOne
@SentinelOne
AI Will Blur Attribution. And North Korea Is the Wildcard. - @stonepwn3000
SentinelOne
@SentinelOne
Read Cybersecurity 2026: The Year Ahead 👉 s1.ai/Predictns
-
SentinelOne
@SentinelOne
🚦 UK Launches Major Cyber Action Plan to Protect Public Services, China-Linked UAT-7290 Targets Telecom Networks in South Asia and Europe, and Critical n8n Workflow Automation Flaws Threaten Automation Infrastructure 🚦
✅ GOOD
• The UK Government publishes a comprehensive cyber action plan backed by £210M to strengthen public sector defenses.
⚠️ BAD
• China-linked UAT-7290 espionage group targets telecom and infrastructure networks with sophisticated malware.
🤢 UGLY
• Multiple maximum severity n8n vulnerabilities expose automation workflows to takeover and code execution.
Read the full roundup → s1.ai/GBU9-Wk2 -
SentinelOne
@SentinelOne
Public sector cyber resilience in the AI era starts with trust.
SentinelOne’s Singularity Platform-High has achieved GovRAMP Authorization. s1.ai/GovRAMPPost not available here, view on X
SentinelOne
@SentinelOne
What this delivers:
• Protection built to the highest compliance standards
• Faster, simpler response across modern environments
• Greater confidence defending critical systems and data
SentinelOne
@SentinelOne
Trusted security.
Built for the public sector.
Learn more → s1.ai/GovRAMP -
SentinelOne
@SentinelOne
This year, through our partnership with Risky Business Media, we’re doing something a bit little different 💡 👀
▶️ How the World Got Owned is a documentary podcast series, taking a historical look at hacking throughout the decades - 80s, 90s, 00s, 10s, 20s.
🔗 Links:
🎧 Spotify - open.spotify.com/show/2jzD9zn7R2d6erZz2ULLeQ
🍎 Apple - podcasts.apple.com/au/podcast/risky-business/id216478078
🌐 RBM - risky.biz/HTWGO1/
It is hosted by Patrick Gray and Amberleigh Jack and produced by Risky Business Media, in partnership with SentinelOne.
Today we dropped Episode One: The 1980s.
Through the words of those that were there, the episode dives into life on the ARPANET, the 414s hacking group, the Morris Worm, the 1980s vibe inside the NSA and a parallel hunt for German hackers happening at a similar time to Cliff Stoll’s famous Cuckoo's Egg story.
Thanks to Jon Callas, Mark Rasch, Timothy Winslow, Greg Chartrand and Tony Sager for sharing your memories. -
SentinelOne
@SentinelOne
2025 wasn’t defined by new cybercrime — it was defined by acceleration.
AI scaled attacks. Infrastructure became the weapon. Attribution blurred.
📘 12 Months of Fighting Cybercrime — the @LabsSentinel 2025 Review is live.
Read it: www.sentinelone.com/blog/12-months-of-fighting-cybercrime…Post not available here, view on X
SentinelOne
@SentinelOne
⚙️ LLM-Enabled Malware: The risk isn’t “superintelligent malware.” It’s operational acceleration — faster recon, better lures, faster extortion.
Read the research by @spiderspiders_, @vkamluk, and Gabriel Bernadet-Shapiro: s1.ai/llm-mw
SentinelOne
@SentinelOne
From ransomware rebranding to CAPTCHA abuse to legitimate platforms turned criminal supply chains, @LabsSentinel mapped how cybercrime matured in 2025.
📘 Read the full SentinelLABS 2025 Review → www.sentinelone.com/blog/12-months-of-fighting-cybercrime… -
SentinelOne
@SentinelOne
AI coding assistants are quietly making decisions for you. Paired with a single malicious plug-in, those decisions could become compromised automation.
What’s happening: To operate autonomously, modern coding agents rely on plugin marketplaces and third-party “skills” for tests, infra, migrations, and dependency management with dependency helpers acting as high-privilege choke points.
The risk: A single, benign-looking dependency skill can quietly redirect a routine install to an attacker-controlled source, embedding a trojanized library without breaking builds or raising obvious red flags.
What’s different: These skills persist across sessions. Once enabled, they continue influencing agent behavior, effectively becoming part of your software supply chain — more like compromising your package manager, rather than a one-off bad prompt.
The big picture: As AI-driven development accelerates, plugin marketplaces and agent skills now sit inside the trust boundary — sometimes without teams realizing it.
📘 Read the Prompt Security blog: Get a detailed walkthrough of the attack mechanics and learn why dependency skills are a powerful, under-modeled risk in AI-assisted development. s1.ai/Prmpt-Plg -
SentinelOne
@SentinelOne
🚦Guilty Pleas for BlackCat ransomware insiders, Major Malware Arrests, Chinese State Backdoor Rootkit Activity, and Trust Wallet Crypto Theft Drains Thousands of Wallets 🚦
This week in cyber: The Good, the Bad & the Ugly ⬇️
✅ GOOD
• Two ex-security practitioners plead guilty for BlackCat ransomware attacks.
• Malware distributor behind 2.8M clipper downloads arrested.
• Former Coinbase support agent arrested for aiding hackers.
⚠️ BAD
• Chinese state-aligned hackers use rootkit to hide ToneShell malware activity.
🤢 UGLY
• Compromised Trust Wallet extension update leads to $7M crypto theft from ~2,600 wallets.
Read the full recap → s1.ai/GBU9-Wk1 -
SentinelOne
@SentinelOne
Agentic AI didn’t just change the endpoint — it broke the old model. Is your endpoint protection keeping up?
This August post hit a nerve because agentic AI fundamentally redefines what “endpoint security” means.
If you skimmed it earlier this year, it’s worth a re-read now. -
SentinelOne
@SentinelOne
Malware inside LLMs wasn’t a prediction for 2026. It’s already happening.
One of our most thought-provoking posts of 2025 — and an early signal of how attackers are already evolving.
Worth revisiting with fresh eyes. s1.ai/llm-mw -
SentinelOne
@SentinelOne
🚦 Major global enforcement wins, persistent organized threats, and AI & zero-day attacks defined 2025 in cyber 🚦
This year in cyber: The Best, the Worst, and the Ugliest ⬇️
✅ The Best
• Cross-border takedowns of fraud, scams, and cybercrime infrastructure.
• Asset seizures and arrests in coordinated global actions.
• Innovation in defense tooling accelerated incident response.
⚠ The Worst
• State-linked theft, supply-chain abuse and financial fraud continued at scale.
🤢 The Ugliest
• AI-accelerated ransomware and exploited zero-day flaws reshaped the threat landscape.
Read the full recap → s1.ai/GBU8-Wk52 -
SentinelOne
@SentinelOne
AI security isn’t just about faster models. It’s about who — or what — is making decisions. This marks a clear shift toward applied AI for security where control, responsibility, and autonomy matter more than ever.
In this OneCon video from November, SentinelLABS’ Juan Andres Guerrero-Saade explains how AI’s ability to evaluate situations on its own is reshaping security, and why research must adapt alongside it.
Worth a re-watch. -
SentinelOne
@SentinelOne
Severance, but make it cybersecurity. This April post still hits. Still unsettling. Still… oddly relatable.
-
SentinelOne
@SentinelOne
This July video resonated because it captured a truth most security teams live every day. Not every alert constitutes panic. Not every headline deserves breathless urgency.
Worth re-watching — calmly. -
SentinelOne
@SentinelOne
GAME DAY. 🏀🔥
@TexasTechMBB vs. @DukeMBB.
The SentinelOne Classic tips off today at @TheGarden.
Final picks — who’s winning? Write your answer as a reply.👇 -
SentinelOne
@SentinelOne
🚦 Global fraud ring dismantled, E-Note virtual money-launderer disrupted, North Korean crypto theft hits record $2B in 2025, and LLMs accelerate ransomware operations 🚦
This week in cyber: The Good, the Bad & the Ugly ⬇️
✅ GOOD
• Joint Europol-led takedown of Ukrainian fraud call centers (€10M+ scam).
• FBI disrupts E-Note money-laundering network used by ransomware groups.
⚠️ BAD
• North Korea-linked hackers stole a record ~$2B in crypto this year.
🤢 UGLY
• LLMs are accelerating ransomware operations across the threat landscape.
Read the full recap → s1.ai/GBU8-Wk51 -
SentinelOne
@SentinelOne
🎬 🚨 (Movie List) Alert: Hackers (almost) get the last ho-ho-ho.
We know the holiday season is prime time for fictional threat actors (looking at you, Hans Gruber). This year, skip the fluff and watch the films that understand the stakes of holiday staffing gaps.
Here is the SentinelOne Holiday Watch List for the Cyber Inclined. 👇Post not available here, view on X
SentinelOne
@SentinelOne
Did your favorites make the list of our Top 5 Fictional Tech Flaws that almost ruined the holidays?
If you have a better one—especially one with a firewall failure—drop it as a reply! 👇
SentinelOne
@SentinelOne
Happy Holidays from the SentinelOne Team!
But seriously, is Die Hard a Christmas movie...? -
SentinelOne
@SentinelOne
Built for moments like this.
@TexasTechMBB vs. @DukeMBB.
The SentinelOne Classic at @TheGarden is almost here. 🏀 -
SentinelOne
@SentinelOne
AI isn’t reinventing ransomware — it’s industrializing it.
That’s the core finding from new @LabsSentinel research on how threat actors are actually using LLMs today. s1.ai/llm-rwPost not available here, view on X
SentinelOne
@SentinelOne
At the high end, we predict actors are moving toward self-hosted, open models.
Why? Fewer guardrails. Less provider telemetry. More control.
SentinelOne
@SentinelOne
The real risk isn’t “superintelligent malware.” It’s industrialized extortion — faster, noisier, and harder to disrupt.
Full @LabsSentinel analysis by @Gabeincognito, Jim Walter, and @spiderspiders_: s1.ai/llm-rw -
SentinelOne
@SentinelOne
Adversaries scaled up. AI leveled up. And the SOC? It got a whole lot smarter. This is the year in AI security—wrapped. 🎁 Scroll down to see what made the 2025 highlight reel ⬇️
Post not available here, view on X
SentinelOne
@SentinelOne
The Rise of Autonomous Security: Autonomous workflows and agentic AI moved from concept to expectation — a core part of the modern security operating model.
SentinelOne
@SentinelOne
Innovation Moments That Redefined the Market: Security shifted from reactive tooling to integrated intelligence
Post not available here, view on X
SentinelOne
@SentinelOne
What We Learned From the Defender: Across the industry, defense evolved toward cohesive AI security.
SentinelOne
@SentinelOne
2025 showed us a clear trajectory: Security is moving toward unified data, autonomous workflows, and AI-native analysis — all essential for operating at the scale modern environments demand.
-
SentinelOne
@SentinelOne
⏳ 1 week. @DukeMBB and @TexasTechMBB. The SentinelOne Classic at @TheGarden.
Who you got? Drop your pick as a reply. 👇🏀 -
SentinelOne
@SentinelOne
🚦 DOJ Targets Russian State-Sponsored Cybercrime, Spanish Police Arrest Teen Over 64M Stolen Records, Malicious Dev Tool Packages Found in VS Code, and CyberVolk’s VolkLocker Ransomware Returns with Design Flaws 🚦
This week in cyber: The Good, the Bad & the Ugly ⬇️
✅ GOOD
• DOJ announces actions against Russian state-sponsored cybercrime.
• Spanish police arrest teen hacker over 64M stolen personal records.
⚠️ BAD
• Researchers find malicious VS Code, Go, npm & Rust packages targeting developers.
🤢 UGLY
• CyberVolk returns with flawed VolkLocker ransomware-as-a-service with new features and design pitfalls.
Read the full GBU → s1.ai/GBU8-Wk50 -
SentinelOne
@SentinelOne
A new WIRED exclusive, drawing on SentinelLABS research from Dakota Cary, shows how a training classroom became the starting point for a globe-spanning espionage operation.
It’s a clear reminder: today’s learner can become tomorrow’s adversary.
The investigation highlights:
- How vendor training can unintentionally seed offensive capability
- How two regional university students scaled to global operations
- Implications for defenders relying on widely deployed Western IT products
📘 Read the exclusive by WIRED’s Andy Greenberg: s1.ai/slt-typhoon
📘 Read the SentinelLABS report: s1.ai/MalAppr -
SentinelOne
@SentinelOne
SentinelOne x AWS is an engine of co-innovation.
At #awsreinvent, SentinelOne’s Brian Lanigan shared how SentinelOne and AWS are building toward a shared vision — reducing complexity, accelerating adoption, and creating a cloud experience where security and innovation move in lockstep.
It’s about aligning ecosystems, not stitching together tools.
It’s about empowering customers, not overwhelming them.
Here are the five AI-powered integrations and innovations we announced at re:Invent. This is what happens when partners build with each other:
🚀 AWS Security Hub → Singularity AI SIEM
Unified cloud, endpoint, identity, and AI telemetry for faster investigations and automated response.
⚡ Amazon CloudWatch Integration
Bidirectional data flows + OCSF support for broader visibility and smarter threat correlation.
🔐 One-Click AWS IAM Onboarding
Rapid, secure setup to accelerate AI-driven security outcomes.
🧠 Purple AI MCP Server on AWS Marketplace
Extend agentic AI and build custom LLM-powered security experiences.
📉 Observo AI in AWS GenAI Marketplace
Reduce noise by 80%, cut costs by 50%+, resolve incidents faster.
🚀 Security without sprawl. Innovation without friction. -
SentinelOne
@SentinelOne
CyberVolk’s newest RaaS offering, VolkLocker, contains a curious design flaw: it stores its master encryption key in plaintext on victim systems.
In new research from @LabsSentinel's Jim Walter, he breaks down how such an oversight is a symptom of CyberVolk’s rapidly evolving RaaS operation. s1.ai/cybervolkreturnPost not available here, view on X
SentinelOne
@SentinelOne
Despite the new features, the tooling shows growing pains.
Most notably: artifacts left in production builds that can allow victims to recover encrypted data — a rare misstep for a threat actor positioning itself as “next-gen.”
SentinelOne
@SentinelOne
The takeaway: CyberVolk is evolving, expanding, and experimenting. But, its rapid growth comes with uneven execution, creating opportunities for defenders to intervene earlier in the kill chain.
📘 Read the full analysis: s1.ai/cybervolkreturn -
SentinelOne reposted
Dakota Cary
@DakotaInDC
The duo’s participation in Cisco Academy and excellence in the Academy Cup, given the lack of excellent education at their alma mater, underlines what the author considers one of the best parts of the cybersecurity community–as the line from Ratatouille goes, “Anyone can cook.”
Dakota Cary
@DakotaInDC
Full report here: www.sentinelone.com/labs/malicious-apprentice-how-two-hac…
-
SentinelOne reposted
Andy Greenberg (@agreenberg at the other places)
@a_greenberg
The names of two owners of contractor firms linked to China's Salt Typhoon hacker group also appeared in records for Cisco's "Networking Academy" global training program—years before those hackers targeted Cisco's devices in their sweeping spy campaign. www.wired.com/story/2-men-linked-to-chinas-salt-typhoon-h…
-
SentinelOne reposted
Dakota Cary
@DakotaInDC
👀 From my @LabsSentinel report: "two people with the same name, in the same province, in the same line of work, work at companies which have a partial name match. The odds of that happening? Even less than 0.000228%"
Andy Greenberg (@agreenberg at the other places)
@a_greenberg
The names of two owners of contractor firms linked to China's Salt Typhoon hacker group also appeared in records for Cisco's "Networking Academy" global training program—years before those hackers targeted Cisco's devices in their sweeping spy campaign. www.wired.com/story/2-men-linked-to-chinas-salt-typhoon-h…
-
SentinelOne
@SentinelOne
China’s notorious Salt Typhoon campaign started in an unexpected place: with two students in a Cisco training classroom.
A new @LabsSentinel report by @DakotaInDC tells the full story.
🔗 s1.ai/MalAppr
SentinelOne
@SentinelOne
The investigation traces how two competitors in the 2012 Cisco Networking Academy Cup evolved into operators behind Salt Typhoon — the campaign that infiltrated 80+ telecom providers, breached CALEA lawful-intercept systems, and collected unencrypted calls and texts from high-value U.S. political targets.
Global intelligence collection at scale.
SentinelOne
@SentinelOne
The two former Academy Cup winners were trained on the very technologies they later exploited.
Their path shows how product education can unintentionally seed offensive capability in local markets.
SentinelOne
@SentinelOne
This isn’t just a tooling story — it’s a story of talent development, access, and time.
It raises a strategic question for defenders: What risks emerge when widely deployed Western technologies are taught at scale in foreign markets?
SentinelOne
@SentinelOne
@DakotaInDC breaks down the operators, the training pipeline, and what this case means for future offensive capability development.
📘 Read the research: s1.ai/MalAppr -
SentinelOne
@SentinelOne
AI is reshaping the SOC. Are you ready?
Join us for AI & Automation Day — a global virtual event exploring AI-powered defense, adversarial AI, and the future of autonomous security.
📅 Jan 20
Register now → s1.ai/cyberforum -
SentinelOne
@SentinelOne
Just a Sec — From the Front Lines: December Live Cybersecurity Briefing x.com/i/broadcasts/1rmGPvNgBPbxN
-
SentinelOne
@SentinelOne
🔥 Our first-ever GameDay at #awsreinvent delivered: real attack scenarios, real tools, real skills.
Congratulations to Tsubaso Hirano, Jason VanNieuwenhoven, and the rest of their Fourcast of Doom team on taking the win. And a huge thank you to Lorenzo Ciaravola for hosting an arena where practitioners used SentinelOne + @awscloud to detect attacks, remediate vulnerabilities, and solve the same challenges they face every day — and to the legendary @jeffbarr for stopping by and watching the action unfold.
The verdict: impressive, intuitive, and instantly applicable in the real world.
🚀 This is how defenders level up — with SentinelOne × AWS. -
SentinelOne
@SentinelOne
That’s a wrap on #awsreinvent 2025 — and you helped us continue to re:Define what’s next. 💜
From Purple AI demos to deep dives on the future of cloud and AI security, thanks to everyone who engaged with us, pushed the conversation forward, and are helping to shape what comes next.
Safe travels — see you soon. -
SentinelOne
@SentinelOne
🚦 AFP jails “evil-twin” WiFi operator, Europol shuts down a major crypto mixer, two malicious insiders are charged for database destruction, Contagious Interview remote identity theft scheme exposed, and React2Shell flaw allows RCE in React/Next.js. 🚦
This week in cyber: The Good, the Bad & the Ugly ⬇️
✅ GOOD
• AFP jails man for “evil-twin” WiFi attacks.
• Europol shuts down global crypto-mixer network.
• Two Virginia men arrested for conspiring to destroy U.S. government databases.
⚠️ BAD
• Researchers capture Operation Contagious Interview’s remote access techniques.
🤢 UGLY
• Critical React2Shell flaw enables RCE in React/Next.js apps.
Read the full blog → s1.ai/GBU8-Wk49 -
SentinelOne
@SentinelOne
💡 What do teams get wrong about cloud security? Treating it like it’s an isolated attack surface. As AI scales, cloud security becomes AI security.
At #awsreinvent, Nick Davis breaks it down: most cloud breaches don’t start in the cloud. They begin with a compromised endpoint or stolen identity, then move laterally across apps, secrets, infrastructure, and identities to reach the mission target — your data, your AI workloads, your production systems.
This is the full attack story. And it’s what SentinelOne is built to see. -
SentinelOne
@SentinelOne
🚀 #awsreinvent delivered — and so did the SentinelOne team.
From packed demos and hands-on GameDay challenges to deep-dive technical conversations and standing-room-only sessions, this week made one thing clear: AI-native cloud security is here, and it’s accelerating fast.
Together with the global cloud community, we explored what’s next for defenders:
• AI-powered cloud protection
• 24×7 managed threat operations
• GenAI-safe architectures
• Autonomous SOC workflows on AWS
The energy, talent, and momentum on the floor were unmatched.
Swipe through the highlights to see innovation, collaboration, and execution in action. 🧡💜 -
SentinelOne
@SentinelOne
The AI Security Leader
💫 Q3 FY26: Growth and margins exceeded top and bottom line expectations.
Record Operating Margin and EPS. Significant Customer Platform Expansion, ~50% of bookings from emerging products 💜
A big thank you—to our customers, partners, investors, and our Sentinels 🙏
Our third quarter results highlight the strength of our AI-powered platform, competitive advantage, and growing product differentiation 💪
Highlights:
• $1.055B ARR +23% YoY
• $259M Revenue +23% YoY
• 79% gross margin (non-GAAP)
• 7% operating margin (non-GAAP), +1100 bps YoY
• ~50% of quarterly bookings from Emerging Products (Data, AI, Cloud & more)
▶️ From the start, we’ve fused human expertise with AI to create the world’s first truly autonomous cybersecurity platform. By unifying AI, data, and security into one relentless engine, SentinelOne is redefining modern defense—scaling fast, driving efficiency, and cementing our position as the industry leader.
🔗 Read the press release: s1.ai/Q3-26-PR
🎧 Earnings call / replay: s1.ai/Q3-26-Ern -
SentinelOne
@SentinelOne
🔐 Security data fuels AI-powered defense — and at #awsreinvent, SentinelOne and AWS are making that data more actionable than ever.
Cameron Sipes breaks down our new bidirectional Amazon CloudWatch integration: push endpoint telemetry into CloudWatch and pull CloudWatch signals into Singularity for unified, AI-driven detection and response.
Here are the five AI-powered integrations and innovations we announced at re:Invent. This is how we power the next era of cloud security:
🚀 AWS Security Hub → Singularity AI SIEM
Unified cloud, endpoint, identity, and AI telemetry for faster investigations and automated response.
⚡ Amazon CloudWatch Integration
Bidirectional data flows + OCSF support for broader visibility and smarter threat correlation.
🔐 One-Click AWS IAM Onboarding
Rapid, secure setup to accelerate AI-driven security outcomes.
🧠 Purple AI MCP Server on AWS Marketplace
Extend agentic AI and build custom LLM-powered security experiences.
📉 Observo AI in AWS GenAI Marketplace
Reduce noise by 80%, cut costs by 50%+, resolve incidents faster.
SentinelOne and AWS are aligning around one goal: giving customers visibility, velocity, and autonomy in the AI era. To learn more, read the press release: s1.ai/RIV25-PR -
SentinelOne
@SentinelOne
At #awsreinvent, we’re re:Defining how AI drives security forward — not slowing teams down, but speeding them up.
Not replacing analysts, but empowering them.
Not adding friction, but unlocking outcomes and innovation.
Autonomous SOC. Human command. This is what real autonomy looks like.
🎥 Want the full conversation? Watch the AWS Security LIVE! interview with SentinelOne’s Nick Davis, starting at 2:49:00 on YouTube: s1.ai/YTAWSLive -
SentinelOne
@SentinelOne
Autonomous security isn’t next— it’s happening now. At #awsreinvent, SentinelOne’s Nick Davis and Joe Poyner broke down exactly how autonomy is already transforming the SOC.
Here are the signals that the shift is real today:
🧑🚒 ➡️ 🕵️ Analysts can finally stop firefighting
“We’re now at the stage where analysts can transition into a more strategic role…more of that CSI-style threat hunter rather than just a ticket handler.”Post not available here, view on X
SentinelOne
@SentinelOne
🎬 It’s already live inside SentinelOne
Across customers, SOC teams are seeing:
• 80% noise reduction
• 100× faster queries
• 40% faster triage & investigation
• 55% faster response
SentinelOne
@SentinelOne
Autonomous security is real—and it’s available now.
📍 Full session at #awsreinvent
From Collecting Tools to an Autonomous SOC
Wed, Dec 3 • 12 PM • MGM Grand 116 • #sec206-S -
SentinelOne
@SentinelOne
💭 Why is Purple AI + AWS such a big deal? Because it changes what’s possible.
Purple AI turns AWS’s massive telemetry into instant insight — making any analyst a seasoned threat hunter and compressing days of work into seconds.
SentinelOne AI + @awscloud = next-level detection. ⚡ #awsreinvent -
SentinelOne
@SentinelOne
We’re re:Defining what AI can do for security. 🤖 ⚡
“My favorite part is them getting about two minutes of training and them beating me … because Purple AI is that powerful.”
At #reinvent, Ankur Mukhopadhyay — a data science executive with no cybersecurity background — took the win. SentinelOne's Wadson Fleurigene delivered the play-by-play. Purple AI powered it all.
Experience the power of Purple AI yourself. Visit SentinelOne at Booth #1479 to try our Mortal vs. Machine competition. -
SentinelOne
@SentinelOne
At #reinvent, we’re re:Defining security for the AI era. See what’s next with SentinelOne.
📍 Booth #1479
🎤 SEC206-S — Joseph Poyner and Nick Davis on Collecting Tools to an Autonomous SOC (today at MGM Grand 116)
🎮 AWS Game Day (tomorrow at Mandalay Bay)
🍸 Security Social (tonight at Sushi Samba)
🔗 Learn more and register for events: www.sentinelone.com/lp/aws-reinvent/ -
SentinelOne
@SentinelOne
📢 Heading to AWS #reinvent25? Don’t miss our Sr. Director Solutions Engineering, Joe Poyner and Sr. Director Product Management, Cloud Security and Exposure Management Nick Davis.
Why it matters: Security teams are drowning in tools — and it’s slowing response when speed matters most.
What you’ll learn: Joe and Nick break down how an autonomous SOC becomes real on AWS:
• How to unify security data across cloud, endpoint, and identity
• How to automate detection and response with AI
• How to turn siloed telemetry into actionable outcomes
• A live look at the latest Purple AI innovations
The bottom line: If you want to reduce noise, collapse workflows, and move toward real autonomy — this is the session to be in.
The session:
From Collecting Tools to an Autonomous SOC
🗓️ Wednesday, Dec 3
🕛 12:00 PM PT
📍 MGM — Grand 116
Session ID: SEC206-S -
SentinelOne
@SentinelOne
Big news from AWS re:Invent 2025 👇
Realizing the autonomous SOC 😤. We’ve launched new AI-powered innovations and deeper AWS integrations to help customers turn security data into real-time action.
What’s new:
🚀 AWS Security Hub → Singularity AI SIEM
Unified cloud, endpoint, identity, and AI telemetry for faster investigations and automated response.
⚡ Amazon CloudWatch Integration
Bidirectional data flows + OCSF support for broader visibility and smarter threat correlation.
🔐 One-Click AWS IAM Onboarding
Rapid, secure setup to accelerate AI-driven security outcomes.
🧠 Purple AI MCP Server on AWS Marketplace
Extend agentic AI and build custom LLM-powered security experiences.
📉 Observo AI in AWS GenAI Marketplace
Reduce noise by 80%, cut costs by 50%+, resolve incidents faster.
SentinelOne + AWS are accelerating how organizations secure and scale their AI-powered future. 🔗 Read the announcement: s1.ai/RIV25-PR -
SentinelOne
@SentinelOne
🤜🤖 Mortal vs. Machine is back at AWS re:Invent 2025 — and more powerful than ever.
This is the live-fire demo where SentinelOne’s AI combines with human instinct on the re:Invent floor. This year’s showdown includes:
• New attacker playbooks and evasive TTPs
• AI-generated correlations as the attack unfolds
• Autonomous investigations powered by Purple AI
• Cloud-native detection on AWS-scale telemetry
📍 See it at Booth #1479 — running throughout the week.
🎮 GameDay: Thu, Dec 4 @ 1 PM
🍸 Security Social: Wed night
If you want to see the autonomous SOC in action, not theory — this is it. -
SentinelOne
@SentinelOne
🚦Polish Authorities Arrest a Suspected Russian Hacker for His Role in Breaching IT Firms, the FBI Issues Warning on Spike in Banking Fraud and Account Takeovers, and OpenAI Confirms Limited Exposure of Data after Mixpanel Breach.🚦
This week in cyber: The Good, the Bad & the Ugly ⬇️
✅ GOOD
• Polish CBZC arrests Russian hacker suspected of breaching corporate IT systems in local firms.
⚠️ BAD
• The FBI says cybercriminals have stolen over $262 million this year through banking account takeover (ATO) schemes.
🤢 UGLY
• OpenAI contacts affected API users after their third-party analytics vendor, Mixpanel, suffered a data breach.
Read the full blog → s1.ai/GBU-WK48 -
SentinelOne
@SentinelOne
GAME DAY. 🏀🔥 The SentinelOne Showdown tips off at 12:30 p.m. ET.
🗽@IllinoisMBB vs. @UConnMBB at @TheGarden.
Speed. Pressure. Big-time energy.
Who’s taking the W? Write your pick as a reply.👇 -
SentinelOne
@SentinelOne
🚀 The most advanced AI-native security platform on the world’s biggest cloud stage ⛅
▶️ At AWS re:Invent 2025, SentinelOne is showing what happens when security is built — not retrofitted — for the AI era.
This year, we’re bringing more than product updates. We’re bringing the future:
• Autonomous SOC workflows that live inside your AWS environment
• AI agents that investigate, correlate, triage and respond at machine speed
• End-to-end protection for your GenAI apps
• Cloud-native defense that scales as fast as your architecture does
📍 Find us at Booth #1479 — where the AI-native platform for AWS comes to life.
🎮 Take the controls: Battle real-world attacks at AWS GameDay
🧪 See what’s new: Live Purple AI + cloud demos every day
🎤 Hear it first: From Collecting Tools to an Autonomous SOC
Wed, Dec 3 • 12 PM • MGM Grand 116 • SEC206-S
🍸 Connect + celebrate: Security Social at Sushi Samba, Wed night
Your cloud runs on AWS.
Your AI-native security should, too.
🔗 www.sentinelone.com/lp/aws-reinvent/ -
SentinelOne
@SentinelOne
China now operates one of the world’s largest cyber-range simulation ecosystems, and it’s reshaping how the state develops offensive capability.
In our newest @labscon_io replay, @MeiDanowski and and @eubenincasa reveal:
• How “live-fire” attack–defense drills actually work
• Why cyber ranges have become strategic infrastructure
• What this means for global cyber operations going forward
What happens inside China’s cyber ranges doesn’t stay in simulation — it shapes real operations.
Replay + full write-up: s1.ai/LC25-DaBe
Full session: youtu.be/uJvPTWRSw6Y -
SentinelOne
@SentinelOne
Parents power our teams, our culture, and our innovation—and today, we’re celebrating them.
SentinelOne has been named one of Fortune’s Best Workplaces for Parents for the second year in a row. 💜
We’re honored. We’re grateful. And we’re committed to continuing to build a workplace where families thrive. Hear from SentinelOne parents: s1.ai/FrtnPrnts -
SentinelOne
@SentinelOne
Wayfinder, the new standard in managed threat detection and response services. ➡️ Scroll down to learn more about our Wayfinder Threat Detection & Response, which combines elite global experts, agentic AI, and unmatched Google threat intelligence.
Read the full blog post: s1.ai/Wyfndr-BlPost not available here, view on X
SentinelOne
@SentinelOne
SentinelOne
@SentinelOne
Read the full blog post: s1.ai/Wyfndr-Bl
-
SentinelOne
@SentinelOne
🚦 U.S. Hits North Korean Revenue Schemes, Global Authorities Sanction Russian Bulletproof Hosting Providers, Samourai Mixer Founders Sentenced, DPRK Fake-Job Platform Targets AI Talent, and Iran-Linked Hackers Use Cyber Recon to Power Physical Attacks 🚦
This week in cyber: The Good, the Bad & the Ugly ⬇️
✅ GOOD
• Global enforcement hits DPRK cyber-workers & money-laundering networks.
⚠️ BAD
• Fake IT job offers by DPRK actors target job-seekers in AI, software development, and crypto industries.
🤢 UGLY
• Iran-linked hackers weaponize cyber reconnaissance and stolen data as precursors to real-world, physical attacks.
Read the full blog → s1.ai/GBU8-Wk47 -
SentinelOne
@SentinelOne
⏳ 1 week. The SentinelOne Showdown tips off Nov. 28.
🏀 @IlliniMBB vs. @UConnMBB
🗽 @TheGarden
High stakes. High speed. High energy.
Who you got? Drop your pick as a reply. 🏀🔥👇 -
SentinelOne
@SentinelOne
Adversaries move fast, but their infrastructure patterns betray them. Our new @vtxproject Synapse Rapid Power-Up for @ValidinLLC, built in-house by @LabsSentinel engineers and open-sourced, makes those patterns visible — and operational for analysts.
This is how you turn fragments into broader campaign insight. s1.ai/sv-pwrupPost not available here, view on X
SentinelOne
@SentinelOne
Once you commit a pivot, Synapse ingests DNS records, HTTP requests, certificates, and WHOIS data — letting analysts correlate infrastructure across time and campaigns.
Small seed indicators can reveal large operational footprints.
SentinelOne
@SentinelOne
The full @LabsSentinel report walks through the workflows, queries, and case studies step-by-step.
If you hunt infrastructure, you’ll want this.
📄 s1.ai/sv-pwrup -
SentinelOne reposted
Tom Hegel
@TomHegel
💚🤝💜🤝💛
Love seeing my two favorite tools come together to level up what analysts can do (@ValidinLLC & @vtxproject).
Huge shoutout to our @SentinelOne intelligence engineering team for making this happen:
www.sentinelone.com/labs/threat-hunting-power-up-enhance-… -
SentinelOne
@SentinelOne
🚦 FBI and Europol dismantle major cyber networks, UNC6485 exploits a Triofox vulnerability to achieve RCE, and attackers steal Washington Post data via previously undiscovered Oracle zero-day. 🚦
This week in cyber: The Good, the Bad & the Ugly ⬇️Post not available here, view on X
SentinelOne
@SentinelOne
🤢 UGLY — The Washington Post was impacted by a breach targeting Oracle’s E-business suite software, compromising the personal information of almost 10,000 current and former employees and contractors.
SentinelOne
@SentinelOne
To learn more, read the full blog post: s1.ai/GBU8-Wk48
-
SentinelOne
@SentinelOne
🤖 Agentic AI. Global Threat Intelligence. Proactive Defense, Redefined.
In this video from #onecon 2025, Drea London, VP of Incident Response & Readiness at SentinelOne, breaks down Wayfinder — our new Threat Detection and Response Service, built to give customers complete control over how they engage with cybersecurity.
Powered by agentic AI, SentinelOne’s elite threat hunters, and Google Threat Intelligence, Wayfinder marks a new era of proactive, adaptive defense — giving customers the freedom to choose their own adventure in threat detection and response.
Wayfinder is redefining what’s possible in AI-powered detection and response.
🔗 Read the press release to see how SentinelOne is redefining threat detection and response for the AI era: s1.ai/Wyfndr-PR -
SentinelOne
@SentinelOne
🤖 AI innovation demands AI Security.
At #onecon 2025, Joni Tsumas, SVP, Americas Sales at SentinelOne, shared how SentinelOne is empowering organizations to embrace AI securely with our Prompt Security and Observo AI offerings.
Customers are moving fast to adopt GenAI — and with Prompt, they can do it confidently, realizing their vision for AI transformation while keeping security front and center.
🧩 Another hot topic:
Observo and the future of the AI-driven SIEM — helping enterprises unify visibility, data, and analytics to accelerate secure adoption across their environments.
🚀 From Prompt to Observo, SentinelOne is shaping how the world adopts AI — securely. -
SentinelOne
@SentinelOne
☁️ Cloud adoption continues to accelerate with today’s generative AI innovations — and so do the risks.
At #onecon 2025, SentinelOne’s Nick Davis, Sr. Director of Product Management for Cloud Security and Exposure Management, shared how we are redefining how organizations protect the cloud in the era of AI Security.
➡ What’s new: To help teams see risk the way attackers do, we introduced:
- Unified Exposure Management: A single, AI-driven view that connects enterprise and cloud risk in one attacker’s-eye perspective.
- Data Security Posture Management (DSPM): Find and secure sensitive data wherever it lives across your cloud environments.
- Cloud Attack Paths: Understand exactly how an attacker could move from initial access to mission target — and stop them before they get there.
➡ Why it matters: As genAI accelerates cloud adoption, these capabilities give defenders the visibility and context to secure both their environments and the AI workloads running within them.
This is how we help organizations move from visibility to action — securing every surface, from endpoint to cloud to AI. -
SentinelOne
@SentinelOne
In the AI Security era, protecting the cloud isn’t just about protection — it’s about prediction.
|
At #onecon 2025, Cameron Sipes, Product Marketing Director of Cloud Security, unpacked how SentinelOne is helping enterprises stay ahead of cloud attacks with DSPM and Cloud Attack Paths.
➡ Data Security Posture Management (DSPM): Discover, classify, and protect sensitive data across every cloud surface — because in 2025, data is the real mission target.
➡ Cloud Attack Paths: Map vulnerabilities, misconfigurations, and signals into a connected view by predicting how attackers can go from initial access to mission target — helping teams focus on what matters most.
Together, these advances redefine how defenders understand risk — and how they act on it.
🎥 Watch the full deep-dive with Cameron Sipes and @dougwhitephd to see how SentinelOne is converging innovation and security in the cloud.This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
As GenAI drives the next wave of enterprise innovation, AWS and SentinelOne are defining it for AI Security — built on collaboration, visibility, and trust.
At #onecon25, @awscloud's Gee Rittenhouse shared how organizations can securely harness GenAI by focusing on three key areas:
➡ Securing infrastructure — protecting the foundation that GenAI depends on.
➡ Simplifying analytics — enabling analysts to focus on what matters most.
➡ Building an open ecosystem with partners like SentinelOne — delivering a broad range of protection so customers can safely adopt agentic AI workloads.
🔗 Learn more about the AWS and SentinelOne news from OneCon: s1.ai/AWS1Cn-PR -
SentinelOne
@SentinelOne
ICYMI: At #onecon 2025, we crowned our 2025 Sentinels League World Champion — Derek Render, an MSP defender whose victory is a testament to the strength and skill of our global partner ecosystem. 🏆
▶️ Tracy Ryan, our Global Managed Security Service Provider Leader, shares how this year’s competition showcased the incredible expertise of our partners — and the power of collaboration in defending what’s next. 💪💜This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
🚦 Authorities crack down on ransomware, a crypto fraud ring, and DPRK IT worker schemes, ‘SleepyDuck’ malware uses Ethereum smart contracts to evade takedowns, and Iran-linked attackers target U.S. policy experts with phishing and espionage campaigns. 🚦
This week in cyber: The Good, the Bad & the Ugly ⬇️
✅ GOOD
• Global law enforcement indicted malicious insiders, sanctioned North Korean banks for laundering ill-gotten crypto, and arrested nine suspects in a wide-spread crypto fraud network.
⚠️ BAD
• New RAT dubbed ‘SleepyDuck’ is masquerading as a Solidity extension on Open VSX open-source registry, garnering over 53,000 downloads since its upload on October 31.
🤢 UGLY
• Iran-based threat cluster called ‘UNK_SmudgedSerpent’ continue to target various U.S. academics, foreign policy experts, and think tanks via phishing and spoofing.
To learn more, read the full blog post: s1.ai/GBU8-Wk45 -
SentinelOne
@SentinelOne
💫 #onecon 2025 broke new ground. We united, we challenged, we pushed the boundaries of whats possible in AI Security. We, Converged 🫶
Thank you 💜This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
💜 💜 Star Power ⭐ ⭐
Our onsite event host, Eran Ashkenazi, reflects on his 3rd OneCon (3 in our history) and how AI Security is at the core of SentinelOne 👇
👂Hear from Eran on our recent acquisitions of Observo AI and Prompt Security, with both providing incredible value and opportunities for existing and new customers 💡
🔗 Learn more about our AI Security portfolio - www.sentinelone.com/blog/ai-security-defining-and-defendi… -
SentinelOne
@SentinelOne
In the era of AI, autonomy is evolving faster than security.That’s a gap SentinelOne is closing. To learn more, watch the video with Jags, Executive Director for Intelligence and Security Research, live from #onecon 2025.
🗣️ What Jags is saying:
“We’ve essentially commoditized evaluative power — technology can now assess situations and make decisions autonomously. The question is: how do we secure that?”
⚙️ What’s new:
SentinelLabs is pioneering applied AI for security — research focused on controlling, guiding, and protecting autonomous systems that learn, decide, and act on their own
🔐 The bottom line:
AI isn’t just a tool — it’s a new kind of agent.
SentinelOne is redefining how to secure it. -
SentinelOne
@SentinelOne
🤝 Welcome back to the second full day of #onecon 2025, hosted by our social emcee Jason Duerden.
▶️ On day 2 we're defining how SentinelOne secures the AI-powered world — supported by research from 451 on how AI is impacting the S&P 500. Then Gee Rittenhouse, Vice President of Security Services at AWS, took the main stage sharing how GenAI is rapidly evolving from a novel tool into a core processing element--driving innovation. 💡
And today, we go further with AWS — announcing our expanded partnership. Together, we’re uniting the best in AI innovation and cloud-scale security to empower enterprises to build, deploy, and defend in a new era of intelligent technology 💜 🧡
This is convergence in action — humans and machines, innovation and code, SentinelOne and AWS — all coming together to secure the future.This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
🏆 Derek Render is our 2025 Sentinels League Threat Hunting World Champion 💜 🔥
📹 Live from #onecon; From 10,000 game plays, across 100 countries, down 2 epic game nights. Congratulations to all of our finalists, Ethan, Arnau and Derek
See you in 2026 -
SentinelOne reposted
CRN
@CRN
Tomer Weingarten, co-founder and CEO of @SentinelOne, used his #onecon 2025 keynote to discuss what he calls “the world’s first fully agentic AI SOC,” and why cybersecurity has become nothing short of a “survival imperative.”
Details: @KyleAlspach:
okt.to/v5m2Ey -
SentinelOne
@SentinelOne
Announced live at OneCon: How SentinelOne and @AWSCloud are teaming up to power the future of AI security.
From protecting AI infrastructure to automating response, this is what’s next in autonomous cloud defense. s1.ai/AWS1Cn-PRPost not available here, view on X
SentinelOne
@SentinelOne
🏅 AWS Generative AI Competency: A new milestone in our collaboration — validating SentinelOne’s leadership in AI/GenAI security across AWS environments.
SentinelOne
@SentinelOne
Together, SentinelOne and AWS are helping enterprises secure AI innovation at scale — faster, safer, and smarter.
🔗 Read the full announcement: s1.ai/AWS1Cn-PR -
SentinelOne
@SentinelOne
Day 1 at #onecon 2025 set the stage for the era of AI Security. 🔥
From the launch of our AI Security portfolio to the debut of our Wayfinder Threat Detection & Response, SentinelOne is defining how human expertise and AI converge to defend what’s next.
🎥 Watch SentinelOne's Rachel Park and @SecWeekly's @dougwhitephd unpack the biggest announcements and insights from the AI Security event of the year.This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
At #onecon Day 1, we defined AI Security in the agentic era with the debut of our AI Security Portfolio and Wayfinder TDR.
Why it matters: Defenders now have the power to secure AI, the cloud, data, and every intelligent agent driving innovation.
💜 Watch the Day 1 wrap-up featuring Jason Duerden — and see how the AI Security era has begun.
Stay tuned — a full product announcement with Rachel Park is coming up next. -
SentinelOne
@SentinelOne
Sentinels League Threat Hunting World Championship Game 2 x.com/i/broadcasts/1ypKdqLBzPLGW
-
SentinelOne
@SentinelOne
Game 1 of the Sentinels League World Championship delivered. Last night, Derek Render narrowly edged Arnau Ossó Saña. 🏆🔥 But tonight, anything can happen and Ethan Chew is waiting to make his move. Game 2 starts at 6:15 p.m PT: www.youtube.com/watch?v=K17g4B2EdYo
The hunt continues. -
SentinelOne
@SentinelOne
📸 Live from #onecon 2025: Our SVP of Threat Discovery and Response, Steve Stone, unveiled how global threats — and intelligent defense — are evolving in the years ahead 🌍
▶️ As Steve shared, “The job of intelligence isn’t to tell history. It’s to tell the future.”
From state-sponsored operations to autonomous, AI-driven attacks, the world’s attack surface is expanding faster than ever. But insight fuels resilience.
At SentinelOne, we see the world through 14,000 customers and 40 million endpoints across more than 150 countries — a global vantage point that helps us forecast not just what’s happening, but what’s coming next 💡 -
SentinelOne
@SentinelOne
Our CEO Tomer Weingarten shared our bold vision for the era of AI Security — one where human purpose and artificial intelligence converge for proactive and predictive cybersecurity. 📸 Live from #onecon 2025
“All of cybersecurity today is entirely reactive. That is a huge problem … It must be intelligent. It must be autonomous. It should be anticipatory.”
At its core, security is about freedom—the freedom to innovate, to create safely, and to build a world where humans and machines collaborate responsibly.
From today’s launch of our AI Security portfolio to the debut of our Wayfinder TDR, the future of defense lies in the convergence of human expertise and intelligent systems. -
SentinelOne reposted
CRN
@CRN
5 Big @SentinelOne AI Announcements At #onecon 2025: okt.to/f0Y5Nx
The cybersecurity vendor is unveiling new capabilities for AI security, agentic security operations and AI-powered threat detection. @KyleAlspach has the details. -
SentinelOne
@SentinelOne
The future of AI Security starts here 💜
🤲 Welcome to #onecon 2025, with our social emcee Jason Duerden. OneCon is where SentinelOne defines how to secure the AI-powered world — from protecting GenAI tools, to defending infrastructure and cloud, and the data and agents that drive all of this innovation 💡
This is convergence — of humans and machines, innovation and code—uniting to secure the futureThis media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
Hands-on. AI-powered. Built for defenders. S1 University on the eve of #onecon25—where practitioners master the skills to secure the future of AI Security.
“S1 University isn’t just training — it’s transformation. You walk out with real skills you can put to work immediately, and a deeper understanding of what AI Security means in practice.” -
SentinelOne
@SentinelOne
Live from OneCon: Just a Sec Special Edition - Cyberstrike Targets Ukraine x.com/i/broadcasts/1OdKrOeppNkGX
-
SentinelOne
@SentinelOne
🚨Big News from #onecon: Human Insight & World Leading Intelligence, Meets Agentic AI Power👇
Introducing the next evolution of managed services, Wayfinder Threat Detection & Response.
See further. Act faster. Turn reaction into resilience. s1.ai/Wyfndr-PRPost not available here, view on X
SentinelOne
@SentinelOne
Powered by SentinelOne, the full knowledge set from Google Threat Intelligence, and the most elite threat hunters, analysts and incident responders on the market, Wayfinder transforms detection and response from reactive to adaptive.
SentinelOne
@SentinelOne
🔗Read the full press release: s1.ai/Wyfndr-PR
-
SentinelOne
@SentinelOne
➡️ Big News from #onecon 2025: The next evolution of cybersecurity isn’t only on the endpoint or in the cloud — it’s AI itself 💡
Introducing the new AI Security portfolio from SentinelOne — built to secure the systems, agents, and data pipelines powering the AI era. Here is what's new:
🧠 Prompt Security for Employees
💻 Prompt Security for AI Code Assistants
⚙️ Prompt Security for Homegrown AI
🤖 Prompt Security for Agentic AI — an Industry First (Beta)
💨 Observo AI data pipelines integrated into Singularity™ AI SIEM
💜 Purple AI debuting a Model Context Protocol (MCP) Server
From protecting AI tools and code assistants and securing homegrown and agentic AI, to orchestrating and analyzing huge amounts of data at machine speed—this portfolio redefines what it means to be secure in an AI-powered world… and we’re just getting started 🔥
This is how we protect the future, with innovation that defends your innovation.
🔗Learn more in the blog: s1.ai/AISec1-Bl
🔗Read the press release: s1.ai/AISec1-PR -
SentinelOne
@SentinelOne
Sentinels League Threat Hunting World Championship Game 1 x.com/i/broadcasts/1mrGmBNmlLgJy
-
SentinelOne
@SentinelOne
The future of AI Security starts tonight. 🎬
Welcome to #onecon 2025, where SentinelOne defines how to secure the AI-powered world—from protecting GenAI tools, to defending infrastructure and cloud, and the data and agents that drive all of this innovation.
This is convergence—of humans and machines, innovation and code—uniting to secure the future.This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
Behind the scenes, the future of AI Security is being built — by the teams and people shaping what’s next. 🎬
#onecon 2025 kicks off in just a few hours.
Follow along this week to see what happens when AI innovation meets human intelligence. -
SentinelOne
@SentinelOne
AI is rewriting the rules of cybersecurity — and SentinelOne is defining the next chapter 🔥 - Keynote Spotlight | #onecon 2025
Our CEO, Tomer Weingarten, will take the stage at the biggest AI cybersecurity event of the year to share how innovation and intelligence are converging to defend the agentic enterprise ◀️
onecon.io starts tomorrow, follow our social channels for all of the action 📺 -
SentinelOne
@SentinelOne
In the AI era, no one can secure alone 🤝
▶️ Keynote Spotlight | OneCon 2025: AWS’s, Gee Rittenhouse, on how data, scale, and collaboration across the AI security ecosystem — with leaders like SentinelOne — are shaping the future 🔥
In just a two days, the world’s top defenders, innovators, and leaders will converge at our #onecon conference, defining the AI era of cybersecurity together. Visionary keynotes, product announcements, and boundless innovation.
💜 We are looking forward to seeing you at the biggest SentinelOne event of the year: onecon.io -
SentinelOne
@SentinelOne
🚦 Ex-US DOD contractor exec pleads guilty to selling tools and trade secrets to a Russian broker, “Brash” browser exploit crashes Chromium in seconds, and Canadian hacktivists tamper with water & energy systems 🚦
This week in cyber: The Good, the Bad & the Ugly ⬇️
✅ GOOD
• Former U.S. DOD contractor exec pleads guilty to selling exploit tools to Russian broker — major insider-threat takedown.
⚠️ BAD
• “Brash” exploit crashes Chromium-based browsers in seconds via a single malicious URL.
🤢 UGLY
• Hacktivists in Canada breach water and energy systems, manipulating sensors and alarms in critical infrastructure.
To learn more, read the full blog post: s1.ai/GBU8-Wk44 -
SentinelOne
@SentinelOne
From 10,000 players to the final three. After months of qualifiers, regional finals, and mind-bending hunts, only the top three remain. s1.ai/S1-League
Post not available here, view on X
SentinelOne
@SentinelOne
Europe Finalist Arnau Osso: A cloud maestro and relentless finisher, Arnau's precision and competitive drive led to perfect scores across Endpoint and Cloud.
SentinelOne
@SentinelOne
Americas Finalist Derek Render: This U.S. flag hunter is in a league of his own for his unmatched ability to thrive under pressure as he seeks out and captures the game's hardest flags.
SentinelOne
@SentinelOne
Asia Finalist Ethan Chew: Ethan's balance of skill, adaptability, and calm precision make him a threat across every surface, but he especially dominates in Endpoint.
SentinelOne
@SentinelOne
Three regions. Three masters of the hunt. One global champion.
Explore the competition: s1.ai/S1-League -
SentinelOne
@SentinelOne
⚡ One mission. OneCon. One week left until the future of AI cybersecurity takes center stage.
In just a few days, the world’s top defenders, innovators, and leaders will converge in Las Vegas to redefine the AI era of cybersecurity together. Visionary keynotes, product breakthroughs, and boundless innovation.
🎟️ Last chance to join us: onecon.io -
SentinelOne
@SentinelOne
Behind every AI leap in cybersecurity, there should be a simple goal: make life better for the people on the front lines.
As SentinelOne’s Adriana Corona shares in the below webinar clip, our journey from rule-based detection to autonomous security is about more than efficiency — it’s about making the daily work of practitioners better.
🎧 Hear how SentinelOne is rethinking the SOC experience with AI, then explore the full independent report for the analyst view.
🔗 Watch the webinar: s1.ai/Odm-Webnr
🔗 Read the full report from @InvestiAnalyst: s1.ai/Odum-Rprt -
SentinelOne
@SentinelOne
The old way is a puzzle of fragmented security tools. When the pieces finally fit, the SOC transforms.
Security teams are moving beyond a stitched-together security stack toward unified, AI-driven intelligence that connects data, decisions, and response. “SentinelOne now has all the individual LEGO pieces to help any security operations leader across their SOC.”
In our recent webinar, analyst @InvestiAnalyst explains how SentinelOne’s AI SIEM is helping lead that shift — simplifying ingestion, cutting cost, and delivering automation that scales across the modern SOC.
🎧 Hear his perspective, then explore the full independent report for deeper insights.
🔗 Watch the webinar: s1.ai/Odm-Webnr
🔗 Read the full report from Francis Odum: s1.ai/Odum-Rprt -
SentinelOne
@SentinelOne
🚦 Europol Dismantles Cybercrime-as-a-Service Network, “Jingle Thief” Exploits Cloud Environments For Gift Card Fraud, and PhantomCaptcha RAT Targets Ukraine Relief 🚦
This week in cyber: The Good, the Bad & the Ugly ⬇️
✅ GOOD
• Europol dismantles cybercrime-as-a-service network (7 arrested).
⚠️ BAD
• “Jingle Thief” exploits cloud gift-card systems for large-scale fraud.
🤢 UGLY
• PhantomCaptcha RAT uses WebSockets to infiltrate Ukraine aid orgs.
To learn more, read the full blog post: s1.ai/GBU8-Wk43 -
SentinelOne reposted
Natalia Krapiva 👩🏻💻🕊
@natynettle
New investigation by @SentinelOne & partners from @DSLab_Ukraine into phishing attack targeting humanitarian actors.
The attack chain overlaps with Russian FSB hacking group COLDRIVER/Star Blizzard which we at @accessnow & @citizenlab reported on last year.
SentinelOne
@SentinelOne
🚨 Six months of prep. One day targeting Ukraine’s humanitarian networks including individuals from the @ICRC, @UNICEF, and @NRC_Norway.
New from @LabsSentinel and the @DSLab_Ukraine: A one-day spearphishing operation — PhantomCaptcha — that targeted humanitarian organizations in Ukraine using a fake Cloudflare captcha page to deliver a WebSocket RAT. s1.ai/pcapt -
SentinelOne
@SentinelOne
🚀 Two weeks. One mission. OneCon 2025.
The wait’s almost over — and the agenda to the biggest SentinelOne event of the year is live. See what’s coming: keynotes, breakthrough product reveals, and a first look at the innovations defining the AI era of cybersecurity.
🔗 Register now: onecon.io -
SentinelOne
@SentinelOne
The future favors the innovators. We’re proud to be named once again to the Fortune Future 50, recognized among the world’s most forward-looking companies shaping the next decade of growth and innovation.
Built for the age of AI, our platform empowers organizations to move faster, stay secure, and lead with confidence.
To our customers, partners, and global team — thank you for helping us redefine what’s possible in cybersecurity. Together, we’re leading the future. 💜
© 2025 Fortune Media IP Limited. All rights reserved. Used under license. -
SentinelOne reposted
Tom Hegel
@TomHegel
🔥New research release
PhantomCaptcha: A short-lived, multi-stage PowerShell + WebSocket RAT operation targeting Ukraine-linked humanitarian & gov entities.
Full report: s1.ai/pcapt -
SentinelOne reposted
SwitHak (👁)
@SwitHak
PhantomCaptcha | Multi-Stage WebSocket RAT Targets Ukraine🇺🇦 in Single-Day Spearphishing Operation | By @LabsSentinel & @DSLab_Ukraine
(Very interesting in OPSEC and Targeting… some overlapping with #coldriver )
↘️
www.sentinelone.com/labs/phantomcaptcha-multi-stage-webso… -
SentinelOne reposted
Stephan Berger
@malmoeb
SentinelOne published their analysis about PhantomCaptch. [1] One of the (many) interesting parts of this report is:
"The script also disabled PowerShell command history logging via Set-PSReadlineOption -HistorySaveStyle SaveNothing as a means of evading forensic analysis."
I presented this anti-forensic technique in my talk (also named Anti-Forensics. Yep, I was inspired). As this technique may now pick up speed, it would be a good time to check your PowerShell alerts if you have coverage for this technique. 🤓
[1] www.sentinelone.com/labs/phantomcaptcha-multi-stage-webso… -
SentinelOne
@SentinelOne
🚨 Six months of prep. One day targeting Ukraine’s humanitarian networks including individuals from the @ICRC, @UNICEF, and @NRC_Norway.
New from @LabsSentinel and the @DSLab_Ukraine: A one-day spearphishing operation — PhantomCaptcha — that targeted humanitarian organizations in Ukraine using a fake Cloudflare captcha page to deliver a WebSocket RAT. s1.ai/pcapt
SentinelOne
@SentinelOne
Why it matters: It’s the latest sign of disciplined cyber-espionage tactics designed to quietly gather intelligence on humanitarian and reconstruction efforts inside Ukraine. Six months of setup. One day online. Precision, not volume.
Post not available here, view on X
SentinelOne
@SentinelOne
Researchers also identified a related Android vector collecting location, contacts, and media — likely part of a broader surveillance effort.
SentinelOne
@SentinelOne
Analysis by @TomHegel of @LabsSentinel
Full report → s1.ai/pcapt -
SentinelOne
@SentinelOne
“That translates into a tremendous opportunity.”
AI and automation are reshaping not just how we protect enterprises, but how we build value for customers.
SentinelOne CEO Tomer Weingarten sat down with @CRN to talk about what’s next for autonomous security and securely harnessing generative AI.
CRN
@CRN
Tomer Weingarten, co-founder and CEO of @SentinelOne, sat down with @CRN’s @jfollett and @StevenJBurke on stage at this week’s #xchange Best of Breed conference to discuss how AI and automation are transforming cybersecurity and the channel.
From large language model (LLM)-enabled malware to autonomous security operations centers (SOCs), he outlined how managed service providers (MSSPs) and solution providers can unlock new revenue streams, manage full enterprise security stacks, and help customers securely adopt generative AI.
You can watch the entire interview here: okt.to/S2c0tw. -
SentinelOne
@SentinelOne
🚦 Prince Group Chairman Indicted in Forced-Labor Crypto Scam, PowerSchool Hacker Sentenced, DPRK Adopts EtherHiding, and Microsoft Defender Flaws Enable Auth Bypass 🚦
This week in cyber: The Good, the Bad & the Ugly ⬇️
✅ GOOD
• U.S. indicts Prince Group chairman for Cambodia-based forced-labor crypto scam compounds
• Massachusetts hacker sentenced to 4 years for PowerSchool data breach and extortion
⚠️ BAD
• North Korean UNC5342 embeds malware in blockchain smart contracts using EtherHiding for covert payload delivery
🤢 UGLY
• Microsoft Defender EDR flaws allow authentication bypass, spoofed telemetry, and malicious uploads
To learn more, read the full blog post: s1.ai/GBU8-Wk42 -
SentinelOne reposted
CRN
@CRN
Tomer Weingarten, co-founder and CEO of @SentinelOne, sat down with @CRN’s @jfollett and @StevenJBurke on stage at this week’s #xchange Best of Breed conference to discuss how AI and automation are transforming cybersecurity and the channel.
From large language model (LLM)-enabled malware to autonomous security operations centers (SOCs), he outlined how managed service providers (MSSPs) and solution providers can unlock new revenue streams, manage full enterprise security stacks, and help customers securely adopt generative AI.
You can watch the entire interview here: okt.to/S2c0tw. -
SentinelOne
@SentinelOne
New in Cloud Security: Turn Compliance from a Checkbox into a Competitive Edge. Introducing Custom Compliance in SentinelOne Singularity Cloud Security.
What’s new: Build and enforce your own cloud compliance frameworks—then monitor them continuously across environments.
🔗 Blog post→ s1.ai/CstmComplPost not available here, view on X
SentinelOne
@SentinelOne
Where it helps:
- Multi-geo SaaS/payment teams juggling overlapping regulations.
- Healthcare orgs needing controls beyond HIPAA (e.g., bespoke access/activity logging).
- Financial services tailoring to PCI DSS + GDPR + local standards without redundancy.
Between the lines: Custom compliance replaces manual workarounds with policy-driven automation—so security can move at the speed of the business.
SentinelOne
@SentinelOne
Go deeper:
🔗 Blog post→ s1.ai/CstmCompl
⛅ CNAPP → s1.ai/CNAPP
📄 2025 Cloud Security Report → s1.ai/ClRprt-25
💻 Request a 30-min demo → s1.ai/CNAPPDemo -
SentinelOne
@SentinelOne
Just a Sec — From the Front Lines: October Live Cybersecurity Briefing x.com/i/broadcasts/1mrGmBzajLBJy
-
SentinelOne
@SentinelOne
🚨 Starting Soon 🚨 Get front-row access to @LabsSentinel researchers unpacking one of the first cases of LLM-powered malware found in the wild. s1.ai/llm-mw
🧠 Our Just a Sec livestream starts at 12 p.m. PT—and we will be answering your questions. ⁉️
SentinelOne
@SentinelOne
🧠 From #labscon 2025 to our Just a Sec Livestream. Get a window into one of @LabsSentinel's latest discoveries: LLM-powered malware spotted in the wild. This Wednesday, Oct 15 • 12 p.m. PT.
Front-row access. No slides, no fluff. RSPV to our LinkedIn Live event to hear directly from some of the researchers who tracked it—what they found, how they analyzed it, and what defenders should know next.
SentinelOne
@SentinelOne
We also fully endorse roasting this social media manager who told you to RSPV. 🙈 (Just do it in the livestream comments after you join Just a Sec at 12 p.m. PT)
We believe in transparency, trust…and a little self-deprecation. 🙃 -
SentinelOne
@SentinelOne
🚨 Breaking News from @CRN 🚨 From cloud security to SIEM, AI and agents could shake up the cybersecurity tools market, as we know it, said our CEO, Tomer Weingarten, as he laid out his vision for the next gen of cyber platforms at the XChange Best of Breed Conference 2025.
"SentinelOne is moving aggressively to become a centralized platform for orchestrating all security tools and data sources — including products from third-party vendors — in order to provide the real-time, autonomous security that partners and customers are calling for, SentinelOne Co-founder and CEO Tomer Weingarten said Tuesday."
"You can really see their vision of becoming a security orchestration platform and being an orchestrator. I thought that was really intriguing," said Jack Skinner, CTO of Oversee My IT.
To learn more, read the article by @KyleAlspach: s1.ai/CRN-Orche -
SentinelOne
@SentinelOne
Boundless innovation: This is OneCon 2025.
OneCon is more than a conference—it’s a live demonstration of what’s possible when cyber defenders, builders, and innovators come together. Get ready for keynotes, threat-hunting competitions, and hands-on collaboration with the brightest in our industry.
🔗 See the agenda—and register at onecon.io -
SentinelOne
@SentinelOne
🧠 From #labscon 2025 to our Just a Sec Livestream. Get a window into one of @LabsSentinel's latest discoveries: LLM-powered malware spotted in the wild. This Wednesday, Oct 15 • 12 p.m. PT.
Front-row access. No slides, no fluff. RSPV to our LinkedIn Live event to hear directly from some of the researchers who tracked it—what they found, how they analyzed it, and what defenders should know next.
SentinelOne
@SentinelOne
RSVP to our livestream event on YouTube or LinkedIn to hear directly from some of the researchers who tracked it—what they found, how they analyzed it, and what defenders should know next. 📲 LinkedIn: www.linkedin.com/uas/login?session_redirect=https%3A%2F%2… 📷 YouTube: www.youtube.com/@Sentinelone-inc/streams?cbrd=1&ucbcb=1
-
SentinelOne
@SentinelOne
🚦 OpenAI Disrupts State-Linked AI Abuse, UK Police Arrest Teens in Nursery Hack, New “Crimson Collective” Threat Actor Emerges, and Discord Breach Exposes Millions 🚦
This week in cyber: The Good, the Bad & the Ugly ⬇️
✅ GOOD
• OpenAI disrupts Russian, North Korean, and Chinese-linked actors abusing ChatGPT for cyber ops
• UK police arrest two suspects in nursery ransomware case impacting 8,000 children
⚠️ BAD
• New threat actor “Crimson Collective” observed conducting stealthy cloud-based attacks, exfiltrating data and partnering with leak groups
🤢 UGLY
• Hackers claim Discord breach exposed data of 5.5 million users through a third-party ticketing support vendor
To learn more, read the full blog post: s1.ai/GBU8-Wk41 -
SentinelOne
@SentinelOne
AI as an Amplifier for Human Tradecraft: how scale can meet sharper intelligence.
What’s new: In their #labscon 2025 talk, @dreadnode's @bradpalmtree and @Dr_Machinavelli show how agentic AI can explore every analytical pathway — at speed and scale.
SentinelOne
@SentinelOne
Why it matters: Traditional analysis follows one trail at a time. Agentic systems can test hundreds simultaneously, uncovering patterns humans might overlook — like strings buried in leaked datasets that reveal hidden GRU activity.
Zoom in: @bradpalmtree calls it the “aha moment” when you realize the probabilistic nature of AI isn’t a flaw — it’s the feature that fuels discovery.
SentinelOne
@SentinelOne
The bottom line: Harnessed correctly, agents don’t just automate analysis — they amplify tradecraft.
🎥 Watch the full @labscon_io replay: www.sentinelone.com/labs/labscon25-replay-auto-poking-the… -
SentinelOne
@SentinelOne
🚦 UK convicts “Bitcoin Queen” in $7.3B crypto fraud.
⚠️ Hackers exploit Milesight routers to launch smishing campaigns.
🤢 Trio of flaws turn Google Gemini into an attack vehicle.
This week in cyber: The Good, the Bad & the Ugly ⬇️
✅ GOOD
• UK convicts “Bitcoin Queen” in world’s largest crypto seizure (£5.5B / $7.3B, 128K victims)
⚠️ BAD
• Hackers abuse Milesight industrial routers to send phishing SMS at scale
🤢 UGLY
• Google Gemini AI flaws enable injection, jailbreaks & sensitive data theft
To learn more, read the full blog post: s1.ai/GBU8-Wk40 -
SentinelOne
@SentinelOne
🌟 SentinelOne is named a leader again! This time in the 2025 IDC MarketScape for Extended Detection & Response (XDR).
Purple AI, hyperautomation and broad platform coverage power SentinelOne’s position as the AI cybersecurity leader. In today’s threat landscape, enterprises need XDR that scales with complexity, and SentinelOne delivers 💪
Why it matters: Security teams face tool sprawl, siloed data, and escalating threats. XDR is becoming foundational — and SentinelOne is setting the standard.
What’s new: IDC MarketScape recognized SentinelOne as a Leader for its unified Singularity Platform, which brings together endpoint, identity, cloud, SIEM, and Purple AI agentic SOC analyst capabilities.
➡️ The details:
- Unified architecture with GenAI + agentic AI for faster hunting, triage & reporting
- Leading signal-to-noise ratio, generating higher-fidelity alerts
- Advanced identity threat detection capabilities with deception built-in
- Layered threat protection even when devices are offline
What they’re saying:
“SentinelOne distinguishes itself in the XDR market with a unified architecture powered by advanced AI and automation. The addition of Purple AI as an agentic SOC analyst is particularly noteworthy.” – IDC MarketScape
🔗 Learn more: s1.ai/IDC-XDR25 -
SentinelOne
@SentinelOne
#labscon 2025: Where real-time threat research is told—and where the next chapter of defense takes shape.
This year’s @labscon_io conference brought together some of the brightest minds in security to share research that’s defining the future of defending against evolving adversary tradecraft.
🔍 The most cutting-edge intelligence on criminal extortion markets and APT obfuscation networks
🤖 AI is redefining how we fight in an increasingly complex threat landscape
🌍 The real-world impacts of mercenaries, cyber ranges, implants, and illicit economies
💡 Fearless talks exposing espionage, harassment, and offensive operations
🎥 Watch the highlights and access talks on demand through @LabsSentinel: s1.ai/LABScnRepThis media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
🚦 Airport cyberattack suspect arrested.
⚠️ “DeceptiveDevelopment” lures devs with fake coding tests.
🤢 UNC5221 stealthily deploys BRICKSTORM backdoor.
This week in cyber: The Good, the Bad & the Ugly ⬇️
✅ GOOD
• UK police arrest suspect tied to airport cyberattacks and aerospace disruptions
⚠️ BAD
• “DeceptiveDevelopment” tricks freelance devs with trojanized coding tests to steal secrets
🤢 UGLY
• China-linked UNC5221 uses BRICKSTORM backdoor to persist ~393 days inside U.S. legal, SaaS & tech firms
To learn more, read the full blog post: s1.ai/GBU8-Wk39 -
SentinelOne
@SentinelOne
🚫 You won’t remember the breach—because it never happened.
In the AI era, SentinelOne is setting a new standard for cybersecurity with AI-powered protection that predicts, prevents, and stops threats before they ever start.
Calm the chaos with the world’s most advanced AI cybersecurity platform.
🔎 Take a Product Tour: www.sentinelone.com/tour/
👉 Learn more: www.sentinelone.com/aicybersecurity -
SentinelOne
@SentinelOne
🚦 BreachForums founder jailed again. UK hacker charged for $115M in attacks.
⚠️ China’s TA415 abuses VS Code tunnels and trusted cloud apps.
🤢 Chaos-Mesh flaws threaten Kubernetes clusters.
Last week in cyber: The Good, the Bad & the Ugly ⬇️
✅ GOOD
• BreachForums’ “Pompompurin” resentenced to 3 years
• UK national charged in 120+ intrusions, critical infra extortion
⚠️ BAD
• TA415 (China) uses VS Code tunnels and trusted cloud apps like Google Sheets for stealthy access
🤢 UGLY
• Chaos-Mesh GraphQL vulns enable Kubernetes takeover
🔍 Read the full SentinelOne breakdown: s1.ai/GBU8-Wk38 -
SentinelOne reposted
Tom Hegel
@TomHegel
#labscon legend @dadamitis with @BlackLotusLabs now up dunking on Secret Blizzard (Turla!) 🇷🇺
🔥 New documented case of Turla hacking another actor's C2 nodes
🔥 1st documented case of Turla transitioning from the C2s into the operator’s workstation
Amazing research Danny! -
SentinelOne reposted
Tom Hegel
@TomHegel
@vkamluk (remote!) @Gabeincognito and @spiderspiders_ from our very own @LabsSentinel talking LLM Enabled Malware.
Masters of AI and malware analysis, getting honest on the hype of where this trend sits.
NEW blog dropped with their talk! s1.ai/llm-mw -
SentinelOne reposted
Tom Hegel
@TomHegel
#labscon Day 2 kicking off now! 🧵
💜 Follow this thread for updates today, and check out yesterdays here:
x.com/TomHegel/status/1968714545767072138
@labscon_io
Tom Hegel
@TomHegel
DAY 1 #labscon25 🧵
So many insane TLP RED + OTR talks today, so bear with me.
First up we're starting with @RidT --
"MERION ZETA. Tales from the Golden Age of Signals Intelligence.
Talk is OTR, but for anyone not familiar w/ codename MERION ZETA:
www.spiegel.de/international/europe/british-spy-agency-gc… -
SentinelOne
@SentinelOne
🔎 Attackers are embedding LLMs directly into malware, creating code that can generate malicious logic at runtime rather than embedded in code.
🔥New @LabsSentinel research by @spiderspiders_ , @vkamluk, and Gabriel Bernadett-Shapiro at #labscon 2025. 🔥 s1.ai/llm-mwPost not available here, view on X
SentinelOne
@SentinelOne
By tracking prompts and API key structures, @LabsSentinel uncovered previously unknown samples and demonstrated how defenders can adapt to this next evolution of malware.
Hunting techniques we developed:
• Wide API key detection (YARA rules for OpenAI, Anthropic, etc.)
• Prompt hunting — searching binaries for hardcoded instructions
SentinelOne
@SentinelOne
Bottom line: LLM-enabled malware is still experimental, but it’s a glimpse of what’s ahead. Defenders have a unique window to learn from early tradecraft.
🔎 Read the full report: s1.ai/llm-mw -
SentinelOne reposted
LABScon 2026
@labscon_io
Up now at LABScon 2025: Binarly researchers Fabio Pagani and Alex Matrosov documenting BYOVD attacks on Secure Boot @pagabuc @matrosov @binarly_io
-
SentinelOne reposted
Tom Hegel
@TomHegel
Next up is our friend @ArsenalArmed
OTR: “Confronting Electronic Evidence Tampering in High-Stakes Cases When All Others Failed”
"This is crazy crazy shit".
Kudos to Mark for receiving our MVP award this year!
#labscon25 -
SentinelOne reposted
Tom Hegel
@TomHegel
Really excited for this next talk, coming from @binarly_io's @pagabuc and @matrosov:
"Signed and Dangerous: BYOVD Attacks on Secure Boot"
Bring Your Own Vulnerable Driver --> a technique where adversaries install legitimate but vulnerable drivers to use for evil.
.... -
SentinelOne reposted
Tom Hegel
@TomHegel
The technical expertise of the @binarly_io team is always impressive.
🤯 CVE-2025-6198 --> bug in the BMC firmware validation logic, allows system firmware update with a specially crafted image
"Are UEFI-level threats coming?" Yeah you guys convinced me they are.
#labscon25 -
SentinelOne reposted
Tom Hegel
@TomHegel
@MattDevost is up now:
"It Takes a Village: How a Community of Researchers Caught an Evasive Crypto Criminal"
A story told through the classic Netrunner game. Fresh work, so in-person only / emerging case details.
Follow us over here too ->
LABScon 2026
@labscon_io
DEVSEC's Matt Devost dropping nuggets on the LABScon keynote stage @MattDevost
-
SentinelOne reposted
LABScon 2026
@labscon_io
Up now! Aurora Johnson and Trevor Hilligoss from SpyCloud @princessauroraj @SpyCloudLabs on the "internet toilets" ecosystem in China
-
SentinelOne reposted
Tom Hegel
@TomHegel
@SpyCloudLabs (Trevor Hilligoss & Aurora Johnson) coming in hot with a talk on Internet Toilets (互联网厕所):
"The Illicit Economy Enabling High-Tech Harassment, Stalking, and Sextortion in the Sinosphere"
Such an uncomfortable, but hugely important talk. TIL terms wtf!? -
SentinelOne reposted
Tom Hegel
@TomHegel
This research is centered on activity in China, but the parallels to what’s happening in the U.S. are striking.
"In many cases, this doxing and harassment escalates to physical violence and has even driven victims to suicide." -
SentinelOne reposted
LABScon 2026
@labscon_io
Kristin Del Rosso returns to the LABScon keynote day stage 🔥@kristindelrosso
Tom Hegel
@TomHegel
Next up, an OTR talk from @kristindelrosso.
🔥Honeypots and Hostile Takeovers: A Field Guide to Organizational Arbitrage
While todays talk is OTR, its gold.. For a sense of her work, check out last year’s talk on “The Foreign Footprint in US Agriculture” www.youtube.com/watch?v=0rsgZfj6MGE -
SentinelOne reposted
LABScon 2026
@labscon_io
Lumen's Black Lotus Labs researcher Michael Horka dropping knowledge on Lilac Typhoon at LABScon @BlackLotusLabs
-
SentinelOne reposted
Tom Hegel
@TomHegel
Back from lunch, now up are the @dreadnode friends @Dr_Machinavelli and @bradpalmtree
"Auto-Poking The Bear - Analytical Tradecraft In The AI Age"
Dropping an LLM-based agentic system, developed to analyze Russian internet data leaked by Ukrainian cyber activists.
#labscon25 -
SentinelOne reposted
Tom Hegel
@TomHegel
Wrapping the final few talks of #labscon25 Day 1 - A major TY to the last speakers for their humbling presentations:
💥 On Private Sector Offensive Operations, @aaronsdevera
💥 The Wagner Group Can’t Stop Posting Its Crimes, @lindsaysfreeman (UC Berkley Human Right Center) -
SentinelOne reposted
Tom Hegel
@TomHegel
@juanandres_gs hitting us hard with a message of hope in our future: Steps to an Ecology of Cyber.
"We are living in the decay of 20th century concepts"
"No more happy hunting, its time to destroy your industry"
wow.. A must watch talk, video soon! -
SentinelOne reposted
Tom Hegel
@TomHegel
"Simulation Meets Reality: How China’s Cyber Ranges Fuel Cyber Operations" --> @MeiDanowski and @eubenincasa
🇨🇳 Talking the dev of these exercises and commercial cyber ranges in China / PRC links.
🇨🇳 120 companies identified as providers
🇨🇳 Upcoming research report!? -
SentinelOne reposted
Tom Hegel
@TomHegel
Now its Typhoon time with Michael Horka of @BlackLotusLabs
TLP RED: "Lilac Typhoon aboard the Indigo Train - The Current State of Chinese Obfuscation Networks"
Horka and team do this best. Def check out their public work on this topic - absolute killers www.npr.org/2024/10/01/nx-s1-5124848/inside-the-investiga… -
SentinelOne reposted
Tom Hegel
@TomHegel
Next up, an OTR talk from @kristindelrosso.
🔥Honeypots and Hostile Takeovers: A Field Guide to Organizational Arbitrage
While todays talk is OTR, its gold.. For a sense of her work, check out last year’s talk on “The Foreign Footprint in US Agriculture” www.youtube.com/watch?v=0rsgZfj6MGE -
SentinelOne reposted
Tom Hegel
@TomHegel
DAY 1 #labscon25 🧵
So many insane TLP RED + OTR talks today, so bear with me.
First up we're starting with @RidT --
"MERION ZETA. Tales from the Golden Age of Signals Intelligence.
Talk is OTR, but for anyone not familiar w/ codename MERION ZETA:
www.spiegel.de/international/europe/british-spy-agency-gc… -
SentinelOne reposted
Tom Hegel
@TomHegel
It’s finally here.. @labscon_io welcome reception kicks off TONIGHT!
Opening with a live Three Buddy Problem show, setting the tone for an incredible week of brilliant minds coming together.
Watch #labscon25 for event updates and highlights.
💜 See you in the desert
🧵.. -
SentinelOne
@SentinelOne
🔥 The Hottest Security Research in Real Time 🔥 #labscon 2025 starts this Wednesday, bringing together the world’s leading researchers to share insights on malware, espionage, cybercrime economies, and the future of AI in security.
Here’s a preview of this week’s talks shaping tomorrow’s threat intelligence 🧵👇 s1.ai/LABScn-BlPost not available here, view on X
SentinelOne
@SentinelOne
💰Crypto thefts hit $9.3B last year. North Korea pulled a single $1.5B heist.
@AndrewMohawk argues crypto security is 90% the same Web2 skills—phishing, API abuse—just with irreversible consequences.
🔗 labscon.io/speakers/andrew-macpherson
SentinelOne
@SentinelOne
🤖 LLM Malware in the Wild: @Gabeincognito and @LabsSentinel’s @spiderspiders_ uncovered malware embedding real API keys to outsource attacks to OpenAI and Anthropic.
LLMs now generate payloads, bypass code-signing, and triage victims—reshaping the defender’s problem space.
🔗 labscon.io/speakers/gabriel-bernadett-shapiro
🔗 www.labscon.io/speakers/alex-delamotte/
SentinelOne
@SentinelOne
🐘PwC’s Jono Davis introduces Orange Indra, a South Asia–based threat actor conducting widespread credential phishing across APAC.
A reminder: not all espionage-oriented intrusions come from the “Big 4.”
🔗 labscon.io/speakers/jono-davisPost not available here, view on X
SentinelOne
@SentinelOne
🧠 @Dr_Machinavelli and @bradpalmtree (@dreadnode) ask: can we trust AI-assisted CTI?
Through their LLM agent system analyzing Russian data leaks, they explore transparency, accountability, and the limits of AI in threat research.
🔗 labscon.io/speakers/martin-wendiggensen
🔗 www.labscon.io/speakers/brad-palm/
SentinelOne
@SentinelOne
That’s just a glimpse of @labscon_io 2025. An exclusive conference where the best research is shared in real time.
Stay tuned as @LabsSentinel releases replay videos in the weeks and months following #labscon.
🔗 labscon.io -
SentinelOne
@SentinelOne
😮💨 28 Qualifier Games. 10,000 Players. 100+ Countries Represented 🌏🌍🌎
✨Sentinels League LIVE Leaderboard🔥- www.sentinelone.com?p=132160&preview=1&_ppp=4db58a0c5c
▶️ The top 50 in each game, per region (APJ, EMEA, Americas); AI, Endpoint, Cloud, SIEM will qualify for the regional finals on October 22nd - the leaderboard is LIVE updating each week, final scores locked on October 2nd
Who will be crowned World Champion at onecon.io Nov 4 and 5 in Las Vegas? 🏆 -
SentinelOne
@SentinelOne
🎬 It's live on @Reddit! Ask @DakotaInDC anything! Join here: www.reddit.com/r/geopolitics/comments/1nfgy8c/hey_its_dak…
SentinelOne
@SentinelOne
🚨 @Reddit AMA 🚨 @LabsSentinel's @DakotaInDC tracks how China builds its hacker pipeline—from campus to command line. Ask him anything! 🗓 Sept 16 (ET)
Set a reminder and join here: www.reddit.com/r/geopolitics/comments/1nfgy8c/hey_its_dak… -
SentinelOne
@SentinelOne
🚨 @Reddit AMA 🚨 @LabsSentinel's @DakotaInDC tracks how China builds its hacker pipeline—from campus to command line. Ask him anything! 🗓 Sept 16 (ET)
Set a reminder and join here: www.reddit.com/r/geopolitics/comments/1nfgy8c/hey_its_dak…
SentinelOne
@SentinelOne
Ask about patents tied to U.S. indictments, smart-home spying, and encrypted data collection—plus Hafnium/Silk Typhoon. Join: www.reddit.com/r/geopolitics/comments/1nfgy8c/hey_its_dak…
-
SentinelOne
@SentinelOne
🚦 $10M Rewards & Sanctions Hit Scam Networks, “GhostAction” Steals 3,325 GitHub Secrets, and China’s APT41 Targets U.S. Trade🚦This is the week in cyber. This is SentinelOne’s Good, Bad, and Ugly cyber news roundup.
Post not available here, view on X
SentinelOne
@SentinelOne
🤢 UGLY: China-linked APT41 hackers are targeting U.S. policy & trade circles
As part of this ongoing campaign, APT41 attackers ran a spear-phishing wave impersonating Republican Party Congressman John Robert Moolenaar, a known Beijing critic. The hackers targeted U.S. trade officials, law firms, think tanks and a foreign government during sensitive U.S.-China trade negotiations.
Why it matters: Nation-state ops are timing campaigns to influence policy outcomes, not just to steal data.
SentinelOne
@SentinelOne
Follow @SentinelOne if you don't already for our weekly GBU with practical defenses leaders can act on: s1.ai/GBU8-Wk37
-
SentinelOne
@SentinelOne
Just a Sec — From the Front Lines: September Live Cybersecurity Briefing x.com/i/broadcasts/1PlJQOlEqDMKE
-
SentinelOne
@SentinelOne
🚨 LIVE WED 9/10 • 12 p.m. PT 🚨 The What & Why Decoded: APT29 using watering holes? 😱 Join us on LinkedIn, X and YouTube for our monthly Just a Sec livestream—and ask our threat researchers your questions.
📺 Youtube: www.youtube.com/@Sentinelone-inc/streams?cbrd=1&ucbcb=1
📲 LinkedIn: www.linkedin.com/uas/login?session_redirect=https%3A%2F%2… -
SentinelOne
@SentinelOne
📣 AI-native data pipeline ignites AI-native cybersecurity 🔥
SentinelOne acquiring @ObservoAI will redefine the future of real time security data and real time security operations in the AI era ⬅️
💡Why it matters: Security doesn’t lack data—it lacks usable data. As telemetry explodes across endpoint, identity, cloud, and infrastructure, the challenge is control. Teams win when they can turn raw logs into real-time signal in the SIEM—faster and at lower cost.
This acquisition is the result of a multi-month technical evaluation, deep customer engagement, and a clear conviction: Observo AI is the best telemetry pipeline platform on the market 💜
➡️ Customer impact: lower ingestion/storage costs, higher-fidelity detections, faster investigations for analysts and AI agents, stronger governance—without lock-in.
🗞️Learn more in the press release: s1.ai/ObsrvoPR
🔗Further details in this blog from Eran Ashkenazi: s1.ai/ObsrvoBl -
SentinelOne reposted
Tom Hegel
@TomHegel
🔥 The lineup this year is incredible, thanks to everyone who submitted!
Attendees are in for something special… and for everyone else, expect some major FOMO.
LABScon 2026
@labscon_io
🔥🔥 The LABScon 2025 agenda drops and it's a banger! 👇
events.sentinelone.com/event/LABScon2025/agenda -
SentinelOne
@SentinelOne
🌍World Class Security, European Data Sovereignty: The World’s First and Only Sovereign Cybersecurity Platform for European Customers. SentinelOne × Schwarz Digits
▶️ Why it matters: European and multinational orgs need AI-grade defense without losing data control, operational resilience, and regulatory alignment. We’re delivering the world’s only fully sovereign, AI-powered cybersecurity platform—built in Europe, for Europe.
▶️ How it works: SentinelOne’s Singularity™ Platform runs natively on the Schwarz Digits’s STACKIT sovereign cloud—operated entirely within German jurisdiction—ensuring all customer data and telemetry remain there, aligning with the highest security and regulatory standards.
▶️ Under the hood: Patented AI and behavioral analysis in the Singularity™ Platform powers autonomous detection and response to threats across endpoints, cloud workloads, identities, and data—accelerating protection at machine speed.
Compliance, covered: Built for GDPR today and ready for NIS2 and DORA—with ISO 27001 and BSI C5 alignment in STACKIT ✅
👉 Read the announcement: www.sentinelone.com?p=132269&post_type=press&preview=1&_p… -
SentinelOne
@SentinelOne
Your cyber threat intel is part of the North Korean strategy: DPRK operators are abusing CTI platforms to see if they’ve been seen—and moving faster because of it. 👀
Post not available here, view on X
SentinelOne
@SentinelOne
🧩 Read the full research by @milenkowski, @SreekarMad (@ValidinLLC), and @warm_warmer (@ValidinLLC): s1.ai/nk-ops
SentinelOne
@SentinelOne
🗞️Also in collaboration with @Reuters. Read the article by @AJVicens and @RaphaelSatter: www.reuters.com/world/asia-pacific/how-north-korean-hacke…
-
SentinelOne
@SentinelOne
🔒 Every business deserves enterprise-grade AI Security. @pax8 and SentinelOne are teaming up to make that a reality for SMBs 💜
We’re proud to announce Managed AI Defense, SentinelOne’s newest offering built in partnership with Pax8, designed to bring enterprise-level AI cybersecurity to small and mid-sized businesses.
➡️ Powered by our industry-leading Singularity™ Platform, this all-in-one, AI-driven security suite gives MSPs and MSSPs the tools they need to:
✅ Rapidly adopt AI-powered Endpoint Protection, GenAI and Managed Threat Hunting
✅ A one stop shop Marketplace enables a clean, seamless, deployment path, straightforward billing, and gradual onboarding.
✅ Partners can add optional SKUs to tailoring the solution to fit each customer’s unique needs.
Managed AI Defense will launch first with Pax8, with plans to expand to other aggregators and Master MSPs in the coming months. It’s designed for smooth adoption and easy scale.
🔗 Learn more about Managed AI Defense: s1.ai/MngAIDef
🔗 Learn more about the Singularity Platform: s1.ai/45s7j -
SentinelOne
@SentinelOne
🚨 Legacy Endpoint Security Can’t Defeat Attacks: That’s Why AI and Automation Matters 🔽
Today, attackers move faster, smarter, and more evasively than ever. That’s why enterprises are turning to SentinelOne’s autonomous endpoint protection, with Purple AI—stopping attacks with AI-powered prevention, detection, and response, and investigating in real time with agentic AI workflows 🤖
The future of endpoint security isn’t reactive or human dependent. It’s Humans + AI with SentinelOne
▶️ Learn more: www.sentinelone.com/lp/endpoint-legacy/ -
SentinelOne
@SentinelOne
💜 $1B in ARR Achieved, Elevating Enterprise Security in the AI Era with our Acquisition of Prompt Security: Our CEO, Tomer Weingarten, joins @CNBC 📺
“That’s exactly why SentinelOne is building AI security: To enable customers to deploy AI in the safest way possible.” On CNBC’s Closing Bell Overtime, Weingarten explained why security is the pillar that makes GenAI production-grade—and what enterprises and boards need to prioritize now and next 💡
Key takeaways:
▶️ The Real GenAI Risk is Data: Code assistants and chat tools can trigger data leakage and low-accuracy outputs. Organizations need visibility and control over both sanctioned and shadow AI use.
▶️ Outcomes Over Algorithms: You win by being able to see → govern → automate across your environment so AI adoption doesn’t open new exposure.
▶️ Adopt on Your Terms with SentinelOne Flex: A new contract model that gives customers complete platform access and the choice to use what they need, when they need it—a superior way to transact that drives deeper adoption and consumption.
▶️ Responsible Automation First: Enterprise AI adoption is still relatively narrow. Trust, predictability, and guardrails must come first.
With more than a decade of experience building AI products, SentinelOne is now in production across tens of millions of devices and workloads—so customers get proven automation with the controls they need 🛡️
Watch the video to see why securing AI is quickly becoming an executive-level priority—and how SentinelOne is uniquely built for this moment.This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
🚨 $97.4M Recovered by INTERPOL, a Surge in Fake Voicemails, and China’s Salt Typhoon on the Edge: What Mattered Most in Cyber This Week 🚨
Here’s what you need to know (fast). 🧵Post not available here, view on X
SentinelOne
@SentinelOne
🧠 Do this now:
• Phishing-resistant MFA for admins
• Quarantine unknown installers (.js/.msi)
• Re-verify contractors for DPRK IT-worker risk
• Collect & review router/firewall logs regularly
SentinelOne
@SentinelOne
🔎 Want a deeper dive? Read the full blog post and follow @SentinelOne for our weekly GBU breakdown and practical hunts/IOCs. s1.ai/GBU8-Wk35
-
SentinelOne
@SentinelOne
💫$1B ARR for the AI Cybersecurity Leader: A Major Milestone Crossed, A New Chapter Begins 💜
SentinelOne has achieved $1B in ARR, with our second quarter results highlighting the strength of our AI-powered platform, competitive position, and growing product differentiation 💪
⭐ Highlights:
• $1B ARR +24% YoY
• Revenue +22% YoY
• 79% gross margin (non-GAAP)
• 5% net income margin (non-GAAP), +350+ bps YoY
• 23% YoY growth in customers with $100K+ ARR
• ~50% of quarterly bookings from Emerging Products (Data, AI, Cloud & more)
▶️We’ve spent more than a decade building Human + AI-powered cybersecurity, culminating in the first autonomous cybersecurity platform. With a relentless focus on innovations and the unification of AI, data, and security, SentinelOne is at the forefront of AI-powered defense—delivering high growth, driving operating leverage, and expanding our leadership in the industry.
Crossing $1B ARR is a testament—and a big thank you—to our customers, partners, investors, and our Sentinels 🙏
🔗 Read the press release: s1.ai/Q2-26-PR
🎧 Earnings call / replay: s1.ai/Q2-26-Ern -
SentinelOne
@SentinelOne
🔥 The Hunt Is ON. 🔥 Are you the world’s ultimate threat hunter? 🔍
🛡️Sentinels League: Threat Hunting World Championships 🛡️ 3 Rounds. 3 Regions. 3 Finalists. Only One World Champion.
🏆 Bragging rights, a $100K Prize Pool, and an all-expenses-paid trip to our OneCon conference in Las Vegas. 🎰 Step up, test your skills, and claim your crown 👑
Sign up now: s1.ai/SntnlLg-X (includes details on terms and conditions) -
SentinelOne
@SentinelOne
@CyberScoopNews just named SentinelOne’s @DakotaInDc a 2025 Most Inspiring Up & Comer.
Bookmark bait (in a good way): Here’s some of his recent work on China’s cyber ops and tech competition. 🧵Post not available here, view on X
SentinelOne
@SentinelOne
To stay up-to-date on PRC cyber activity, add Dakota to your feed:
X @DakotaInDC
Bluesky: bsky.app/profile/dakotaindc.bsky.social
SentinelOne
@SentinelOne
For more original research, adversary tradecraft, and defender playbooks, follow the whole @LabsSentinel team.
-
SentinelOne
@SentinelOne
🚨 This Week in Cyber: The Good, the Bad and the Ugly 🚨
✅ GOOD
• Key UNC3944 member sentenced: The 20-year-old Florida man, Noah Urban, received 10 years in prison tied to the notorious cybercriminal operation.
• UK court jails a serial website defacer: Al-Tahery Al-Mashriky from Rotherham, England, was sentenced to 20 months for hacking and defacing official sites across North America, Yemen, and Israel, including the California State Water Board.
• Supply chain win: PyPI now checks for expired domains to prevent domain resurrection attacks. Since early June, at least 1,800 email addresses with expired domains have been unverified in this effort to stop maintainer account hijacks.Post not available here, view on X
SentinelOne
@SentinelOne
🧠 What to do now
• Lock down maintainer & admin accounts: enforce phishing-resistant 2FA, remove custom-domain emails that can expire, and review password-reset policies.
• Train for the copyright-lure pattern: block risky attachments (e.g., MSI), watch for DLL sideloading, and add detections for Haihaisoft-related binaries and suspicious registry changes.
• Safeguard code & identities: restrict GitHub app scopes/PATs, monitor unusual repo access, and tighten contractor/on-platform vetting to counter DPRK IT-worker infiltration.
SentinelOne
@SentinelOne
📖 Full breakdown from SentinelOne: s1.ai/GBU8-Wk34
-
SentinelOne
@SentinelOne
EDR for the Agentic AI Era: The Endpoint Has Changed. Is Your EDR Keeping Up?
Why it matters: Attackers are faster, funded, and relying more on automation. Tools built for yesterday’s malware won’t keep up.
What to look for:
- AI-driven detections (behavior > signatures)
- Natural-language hunting to uplevel every analyst
- Automated response and hyperautomation across your stack
- Proactive hardening and XDR-level visibility
The upshot: Modern EDR shrinks dwell time, slashes noise, and turns SecOps into a force multiplier.
Go deeper: Learn what “modern EDR” really means and how SentinelOne’s Singularity Endpoint delivers it. Read our newest blog post: s1.ai/EDREvolv -
SentinelOne
@SentinelOne
🚨Ghanaian Nationals Extradited for $100M+ Fraud, BlackSuit Ransomware Disrupted, Curly COMrades Cyberspies Hit Eastern European Govt Orgs, and HTTP/2 'MadeYouReset' DoS Vuln. This Week in Cyber: The Good, the Bad, and the Ugly 🚨
✅ GOOD
● Ghanaian fraud ring extradited to U.S. and charged with stealing $100M+ via romance scams & BEC ● BlackSuit (Royal) ransomware ops dismantled: $1M+ crypto seized, servers down
⚠️ BAD
● New cyber-espionage group appearing to support Russian interests, Curly COMrades, deploys custom malware on Georgian govt & Moldovan energy targets for spying ➡️
🤢 UGLY
● New HTTP/2 'MadeYouReset' vuln (CVE-2025-8671) enables massive DoS attacks by bypassing request limits
🧠 Stay sharp:
● Track fraud & ransomware enforcement actions
● Patch HTTP/2 stacks & bolster DoS defenses
Full breakdown from SentinelOne: s1.ai/GBU8-Wk33 -
SentinelOne
@SentinelOne
💜 Threats are getting bigger, faster and more complex. Security doesn’t have to get more cumbersome in response, it's about having the right partners 🕵️
At BlackHat2025, our VP of Managed Detection & Response, Warwick Webb, explains how SentinelOne’s Singularity MDR is your trusted partner in developing a comprehensive threat detection and response program 🟣
We bring it all together:
🧠 AI-powered technology (endpoint, cloud, AI SIEM)
🤝 Human experts with Purple AI agentic capabilities (MDR analysts, threat hunters and incident responders)
🛡️ A holistic approach to secure your entire technology ecosystem
Ready to flip the switch on simplified, effective security? Learn more and get a demo today! www.sentinelone.com/global-services/singularity-mdr/This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
📣 OneCon 2025. Where the AI Era meets Cybersecurity 🔥
▶️ ▶️ Early bird $999 discounted tickets on sale now ($1,399 full price). Grab tickets at onecon.io ◀️ ◀️
In a world where the convergence of Humans + AI is changing our everyday lives—OneCon unites the best-of-the-best in the cybersecurity industry 🤲
Cyber threats evolve faster than humans alone can anticipate, AI is not only necessary—it's mandatory. Arm yourself with cutting-edge strategies to outsmart adversaries
SentinelOne is the unrivalled leader in the AI era, redefining and reimagining cybersecurity with unmatched innovation—Join us 🤝
Dare to stay ahead—grab your spot at onecon.io! -
SentinelOne
@SentinelOne
AI for Good: How our intended acquisition of Prompt Security will help fuel our mission of securing the entire technology ecosystem.
At BlackHat2025, SentinelOne’s Melissa Smith shares why our acquisition of Prompt Security is about empowering you—and using AI for good:
🤝 Expanding our AI foundation
🤖 Embrace AI tools like Gemini, Claude, and ChatGPT with confidence.
🔐 Serving and protecting customers, partners & the tech ecosystem
🎥 Watch the clip and read the blog to learn how Prompt Security will bolster our mission - www.sentinelone.com/blog/a-new-chapter-for-ai-and-cyberse… -
SentinelOne
@SentinelOne
💜 Last week our SentinelOne MDR services were recognized by Frost & Sullivan as the fastest growing and furthest moving provider, year-over-year, on Frost Radar's new Innovation Index 📈
We asked Hackim Farrell, Snr. Director of Product Management, to break down why our unique approach of Humans + AI is not only changing the game for our customers, but setting the pace in our industry for innovation 🤝
▶️ According to Frost:
“The continuous feedback and learning loop between Purple AI and the global MDR team ensures that both human analysts and ML models evolve together and improve the overall detection fidelity, contextual awareness, and effectiveness of the Singularity platform.”This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
🚨 Nigerian Suspect Extradited for Hacking, Fraud & Identity Theft, Crypto Mixer Founders Plead Guilty, Smart Contract Scams, and SonicWall SSL VPN Attack Wave. This Week in Cyber: The Good, the Bad, and the Ugly 🚨
✅ GOOD
Nigerian man extradited to U.S. for hacking, fraud & identity theft charges
Samourai Wallet founders plead guilty to laundering $200M+ in illicit crypto funds
⚠️ BAD
@LabsSentinel exposes Ethereum “trading bot” scams draining wallets via malicious smart contracts ➡
🤢 UGLY
SonicWall firewalls targeted in ransomware attacks — initial zero-day fears later traced to a patched flaw (CVE-2024-40766) exploited via weak creds
🧠 Stay sharp:
Watch DeFi scams on social channels
Patch, rotate creds & enforce MFA on VPN gear
📖 Full breakdown from SentinelOne: s1.ai/GBU7-Wk32 -
SentinelOne
@SentinelOne
🇨🇳 China's offensive hacking ecosystem and how the Hafnium cluster is key. Dakota Cary, Sr. Security Advisory Consultant, joins us from Black Hat 2025 and breaks down new research from SentinelLABS😮💨
This research uncovered several patents linked to China-based threat actor Hafnium, exposing a suite of previously unreported offensive cyber tools. -
SentinelOne
@SentinelOne
🚨Live from BlackHat 2025 we asked @stonepwn3000, SVP of Threat Discovery & Response - What intrusion types are you most worried about? 👀
🧐 Illicit Valid Access — an evergreen issue that Steve unpacks for us. From the latest Microsoft/SharePoint vulnerabilities to Salesforce account compromises and ransomware through valid access like credentials--the last 30 days has seen a huge spike in activity 🆙This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
🎙️ AI is reshaping cybersecurity on all fronts. Incident Response and Digital Forensics is a huge benefactor, with Humans + AI taking down adversaries together everyday 💪
Hear from Drea London, SentinelOne's VP of Incident Readiness and Response, on how threat actors are, or are not, leveraging AI + how IR and forensics teams have been able to reset the battlefield 🥷This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
🎥 Live from the #blackhat 2025 show floor - AI in research and intelligence 💡
JAGS, our VP of Intelligence & Security Research, is breaking down how AI is a driving force for research, development and education in cyber. From advanced threat intel to AI defense strategies and fostering the next wave of talent — if it matters in AI, intelligence and research, he’s on it 🫡This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
Just A Sec, Episode 4 - Black Hat Special Edition x.com/i/broadcasts/1vAxRDQPdnvGl
-
SentinelOne
@SentinelOne
💜 Purple vibes only on Day 1 of Black Hat 2025 💜
Stop by Booth #3033 to experience the future of AI security today:
✅ Explore our latest platform enhancements, including Gen AI an agentic AI
🤝 Connect 1:1 with SentinelOne experts on endpoint, cloud, AI SIEM, hunting and incident response
🎯 Test your skills in Mortal vs. Machine hunting challenge
Learn more, visit us at booth #3033 👈 -
SentinelOne
@SentinelOne
🚨Black Hat 2025 is underway and we are hosting 'Just A Sec' LIVE from the show floor. Wednesday August 6th at the SentinelOne booth, #3033, at 11am. Do. Not. Miss. This.. 👀
This months master topic: ''Big Tech's $100M Paychecks for AI Talent'' 💰 💰
Steve, Drea, JAGs and Dakota will be breaking down the key points;
🎓 Implications for the Education system – if the best AI researchers are cooped up in expensive labs, who will teach the next generation?
🤔 Contextualizing insider risk– If your talent can pull $100m paychecks, you need to be more worried about workplace satisfaction and cohesion than insiders taking your stuff
🇺🇸 US companies should be able to poach any and all of China’s best AI researchers. Why aren’t we?
We then put the team on the countdown clock with the following hot topics;
😬 Sharepoint Shambles
🎩 Black Hat Best
🇨🇳 Hafnium Strikes
💔 Love after Lockup
☁️ Salesforce Compromises
👮 The Com arrests
🎒 Favourite backpack?
🇷🇺 Russia uses ISP for bad -
SentinelOne
@SentinelOne
4,000+ victims across 62 countries. Over 200,000 passwords, 4M+ cookies, and hundreds of credit cards exfiltrated.
SentinelLabs and Beazley Security have discovered and analysed a rapidly evolving series of infostealer campaigns delivering the Python-based PXA Stealer.
Why it matters: This isn’t just another stealer. It's a fully operational underground economy built on Telegram bots and a leap in both tradecraft and evasion strategies.
The threat actors behind these campaigns are linked to Vietnamese-speaking cybercriminal circles who monetize the stolen data through an underground ecosystem that automates resale and reuse through the Telegram API.
The details:
🔹 4,000+ victims across 62 countries, most notably South Korea, the U.S., the Netherlands, Hungary, and Austria.
🔹 Over 200,000 passwords, 4M+ cookies, and hundreds of credit cards exfiltrated
🔹 Malware loaded through signed software like Haihaisoft PDF Reader and MS Word 2013
🔹 Telegram bots used to manage exfil, automate resale, and notify criminals of new stolen data
🔹 Infrastructure abuse includes Dropbox, Cloudflare Workers, and 0x0[.]st, a Pastebin-like service
The big picture: Modern stealer campaigns are evolving beyond malware. Automation, obfuscation, and legitimate infrastructure are the new weapons of choice.
🧠 Read the full report to see how these threat actors, linked to Vietnamese-speaking cybercriminal circles, are industrializing infostealing: s1.ai/GhostZip -
SentinelOne
@SentinelOne
These Ethereum smart contracts don’t trade for you—they drain your crypto wallet.
In new research from @LabsSentinel, we reveal how threat actors are pushing malicious Ethereum smart contracts disguised as “MEV” trading bots via aged YouTube accounts and AI-generated influencers.
🧠 Why it matters: Video lured victims into sending over $900,000 in ETH (valued at time of publication).
📹 The playbook:
- Aged YouTube accounts plus playlist laundering
- Obfuscated attacker wallets via XOR and type coercion
- Weaponized code hosted on Pastebin, TinyURL, Codeshare
- Comments scrubbed, urgency engineered, trust faked
💡 Zoom out: This elaborate crypto scam is low-cost, high-yield, AI-powered operation that can scale across platforms, markets, and chains.
📖 Full report by @spiderspiders_: s1.ai/eth-con -
SentinelOne
@SentinelOne
🤝Two AI Pioneers. One Vision for the Future of AI Security. SentinelOne to acquire Prompt Security to secure the rapidly growing use of GenAI and agentic AI in the enterprise 🚀
🔐Embrace AI tools like Gemini, Claude, and ChatGPT with confidence. Our AI-native endpoint, cloud, and SecOps strength combined with Prompt Security’s groundbreaking capabilities, will make it possible for every company to fully embrace AI without compromising safety and security.
This is the foundation required for secure AI adoption at scale ⬅️
With Prompt Security’s capabilities, SentinelOne will give customers:
▶️ Real-time AI visibility into how AI is used across the enterprise
▶️ Policy-based controls to enforce safe use and prevent data leakage
▶️ AI attack prevention against threats like prompt injection, malicious output manipulation, and model abuse
▶️ Model-agnostic coverage across all major LLM providers including OpenAI, Anthropic, and Google, as well as self-hosted or on-prem models
▶️ MCP gateway security between AI applications and more than 13,000 known MCP servers, intercepting every call, prompt template, and response
🆙 We are raising the bar, again. Learn more about this next phase of innovation in our blog and press release 💜
Blog - www.sentinelone.com/blog/a-new-chapter-for-ai-and-cyberse…
Press Release - www.sentinelone.com/press/sentinelone-to-acquire-prompt-s… -
SentinelOne reposted
SentinelLabs
@LabsSentinel
New Collab with our friends at @BeazleySecurity:
👻 Ghost in the Zip | New PXA Stealer and Its Telegram-Powered Ecosystem
🔺 SentinelLABS and Beazley Security discovered and analyzed a rapidly evolving series of infostealer campaigns delivering the Python-based PXA Stealer.
🔺 This discovery showcases a leap in tradecraft, incorporating more nuanced anti-analysis techniques, non-malicious decoy content, and a hardened command-and-control pipeline that frustrates triage and attempts to delay detection.
🔺 We identified more than 4,000 unique victim IP addresses in exfiltrated logs, with infected systems spanning at least 62 countries, most notably South Korea, the United States, the Netherlands, Hungary, and Austria.
🔺 The stolen data includes over 200,000 unique passwords, hundreds of credit card records, and more than 4 million harvested browser cookies, giving actors ample access to victims’ accounts and financial lives.
🔺 The threat actors behind these campaigns are linked to Vietnamese-speaking cybercriminal circles who monetize the stolen data through a subscription-based underground ecosystem that efficiently automates resale and reuse through the Telegram platform’s API.
Full Details: www.sentinelone.com/labs/ghost-in-the-zip-new-pxa-stealer… -
SentinelOne
@SentinelOne
🚨 FBI, CISA, China’s Hafnium, and Russian hackers all in one place. This Week in Cyber: The Good, the Bad, and the Ugly 🚨
✅ GOOD
• The FBI has seized $1.7M in Bitcoin from an affiliate of Chaos ransomware, striking a blow to the new gang attacking and extorting payments from Texan companies
• CISA has open-sourced its Thorium malware analysis platform, giving defenders across the government, public, and private sectors a powerful new tool for digital forensics and automating analysis workflows
⚠️ BAD
• China’s covert cyber capabilities are on full display in our latest SentinelLABS report. Hafnium (aka Silk Typhoon) is back with fresh patents and sharper teeth ➡️ s1.ai/SilkPatents
🤢 UGLY
• Microsoft is warning that a cyberespionage group linked to Russia’s FSB gained access to ISPs to launch AitM attacks on embassies and diplomatic missions in Moscow
• This is a sophisticated campaign exploiting network-level access to intercept and manipulate traffic
🧠 What to do now:
Explore Thorium’s capabilities for internal forensic readiness
Review Hafnium-linked infrastructure and IOCs
📖 Full breakdown from SentinelOne: s1.ai/GBU7-Wk31 -
SentinelOne
@SentinelOne
📊 Tool sprawl, bloated investments, and poor signal-to-noise-ratio: Cloud security doesn’t have to be chaotic and complex. In our latest cloud security report, learn how over 400 CXO's are approaching cloud investments and strategies 💡
Our new 2025 Cloud Security Survey, conducted with CyberEdge, reveals how today’s cloud defenses are faltering under too many tools, too much noise, and not enough visibility. By the numbers:
▶️ 92% of orgs are struggling with tool sprawl
▶️ 46.5% prioritize real evidence over theory
▶️ 30% of alerts are not triaged within 24 hours
Why it matters: Alert fatigue, siloed tooling, and poor signal-to-noise ratios are blocking defenders from acting fast — and creating opportunities for attackers to slip through.
🧰 The fix: Security teams are turning to AI and unified platforms to simplify operations, accelerate detection, and take action before damage is done.
📥 Download the full report: assets.sentinelone.com/cnapp/cloud-security-survey-report… -
SentinelOne
@SentinelOne
🚨 Black Hat... meet 'Just A Sec' 🥰 🖤 💜
🔥We are bringing our eye opening, fast, fun, on point and always entertaining show LIVE to the expo floor of Black Hat - Theatre 1, SentinelOne booth #3033 on Wednesday August 6th at 11am (see below for online links)
We will be announcing the 'master topic' and 'on the clock' countdown topics early next week, so keep an eye out. Don't miss your chance to see Drea, Steve, Dakota and JAGs spice it up 👀 😤
Not attending Black Hat? Don't worry, we will still be posting the show recording on LinkedIn, YouTube and Spotify:
🎧 Spotify - open.spotify.com/show/4ADXHYe0lGiTMKvzXmYknj?nd=1&dlsi=3d…
📱LinkedIn (pre register for notifications) - www.linkedin.com/uas/login?session_redirect=https%3A%2F%2…
📺 YouTube - www.youtube.com/@Sentinelone-inc/streams?cbrd=1&ucbcb=1 -
SentinelOne
@SentinelOne
SentinelOne has once again achieved recognition as a category leader for Growth and Innovation in the Frost Radar™: Global Managed Detection and Response (MDR), 2025 🚀
▶️ According to Frost:
“The continuous feedback and learning loop between Purple AI and the global MDR team ensures that both human analysts and ML models evolve together and improve the overall detection fidelity, contextual awareness, and effectiveness of the Singularity platform.”
Year-over-year, we demonstrated advancements in delivering innovative offerings that combine advanced AI with expert human analysts to provide 24x7x365 MDR coverage. Thank you to our customers, partners and Sentinels 💜
📖 Read the full report and blog here - www.sentinelone.com?p=128471&preview=1&_ppp=2aaa07f90a -
SentinelOne reposted
SentinelLabs
@LabsSentinel
New from @DakotaInDC -- China’s Covert Capabilities | Silk Spun From Hafnium
Summary:
🟣 SentinelLABS identified 10+ patents for highly intrusive forensics and data collection technologies that were registered by companies named in U.S. indictments as working on behalf of the Hafnium threat actor group.
🟣 These technologies offer strong, often previously unreported offensive capabilities, from acquisition of encrypted endpoint data, mobile forensics, to collecting traffic from network devices.
🟣 Our research explores the relationships between indicted hackers, ownership of the firms they are associated with, and the relationships those firms have with several government entities who conduct offensive cyber operations on behalf of China.
Full Story: www.sentinelone.com/labs/chinas-covert-capabilities-silk-… -
SentinelOne
@SentinelOne
🔍 CISOs aren't merely buying AI—they're buying security outcomes. It's time to move beyond the vendor hype of AI supremacy and focus on the quantifiable results of implementing AI for security operations.
It’s not the size of the model: In a market flooded with AI promises, we analyze what separates real AI value from empty noise.
Why it matters: Security leaders need results, not hype. Learn how SentinelOne’s Purple AI drives 63% faster threat identification, 60% lower breach risk, and a 338% ROI. This is what the acceleration of security operations looks like.
👉 Read the blog: www.sentinelone.com/blog/is-your-security-platform-delive… -
SentinelOne
@SentinelOne
The Cyber Patents China Didn’t Want Us to Find…
@LabsSentinel has uncovered 10+ patents for highly intrusive forensics and data collection tools—filed by companies named in U.S. government indictments for working with the Chinese Hafnium (aka Silk Typhoon) APT group.
🧵 Why it matters: This is a deep dive into the ecosystem behind one of China’s most notorious threat actors.
💡 What’s new:
– Direct links between indicted hackers, contracting companies, and China’s state security
– Evidence that Hafnium’s tooling goes far beyond what’s publicly documented
– Fresh questions about how China’s Ministry of State Security (MSS) supports its contractors
These offensive patents include:
🔍 Tools to bypass Apple FileVault
📱 Mobile and router forensics software
🏠 Surveillance tools for smart home devices
📚 Zoom out: Hafnium’s 2021 MES campaign triggered an unprecedented joint U.S.-EU-UK rebuke. This report shows that wasn’t a one-off—it was a glimpse into a broader, layered offensive apparatus.
🔗 Full report, authored by SentinelLABS’s @DakotaInDC: s1.ai/SilkPatents -
SentinelOne
@SentinelOne
🚨 🚨 Last chance to secure $699 Pre-Sale OneCon tickets - only until July 31 🗓️
💜 Lead the AI Era Cybersecurity Revolution at OneCon 2025 - grab your ticket at onecon.io!
With cyber threats accelerating, equip yourself with next-gen strategies to crush adversaries. Do not miss out on your discounted ticket for just $699 (full price is $1,399)
SentinelOne is the unrivalled leader in the AI era, redefining cybersecurity with unmatched innovation. Immerse yourself in hands-on workshops, captivating keynotes and forge connections that shape the future 🌎
Dare to stay ahead—grab your ticket at onecon.io! -
SentinelOne
@SentinelOne
Endpoint Protection, Redefined: Insights from a Five-Time Gartner® Magic Quadrant™ Leader. 🔎 In a new blog post, SentinelOne’s Ric Smith, President, Product, Technology, and Operations, shares why we believe the recognition reflects more than placement — it’s a signal of how agentic AI, unified architecture, and a focus on customer control are redefining modern endpoint security.
📈 See how we’re delivering:
• Real-time, autonomous protection across all devices and environments
• The industry’s most advanced AI cybersecurity analyst — Purple AI
• Unmatched ROI and performance in MITRE ATT&CK® evaluations
• Enterprise-grade resilience with 1-click remediation and rollback
• Simplicity, flexibility, and customer-first deployment practices
🚀 Agentic AI isn’t just helping — it’s acting.
🧠 The SOC of the future is already here.
🔗 Read Ric’s perspective and explore the full Gartner® report: s1.ai/MQEPP25Bl -
SentinelOne
@SentinelOne
How IP Theft Leads to a Factory Closure: State-backed cyberattacks aren’t just abstract threats–they can hit home. SentinelOne’s @DakotaInDC breaks down how Chinese government hacking directly cost American jobs after intellectual property was stolen from U.S. Steel.
📻 From @npratc
🎙️ Featuring SentinelOne’s Dakota Cary
🔊 Listen to the full interview: s1.ai/Ch-NPRATC -
SentinelOne
@SentinelOne
🚨 This Week in Cyber: The Good, the Bad, and the Ugly🚨 www.sentinelone.com/blog/the-good-the-bad-and-the-ugly-in…
Post not available here, view on X
SentinelOne
@SentinelOne
🧠 What to do now:
- Patch SharePoint servers immediately
- Share the Phobos decryptor with impacted users
- Monitor dark-web channels for Lumma activity
SentinelOne
@SentinelOne
📖 Full breakdown from SentinelOne: s1.ai/GBU7-Wk29
-
SentinelOne
@SentinelOne
⚫ Black Hat 2025. Where the industry's leading AI-powered cybersecurity platform meets... you 👀
Try your hand at our legendary Mortal vs Machine challenge, leveraging the power of Purple AI—our agentic AI security analyst. 🛡️ From AI-native defense to cloud runtime protection, we’re showing how to stay one step ahead — no matter the adversary.📍 Catch us at Booth #3033 to:
🔍 Dive into our latest tech innovations
👥 Get face time on intel with our experts
🧠 Join exclusive sessions on what’s next in security
📢 Don’t miss Blurred Lines on Wednesday, Aug 6 — a session that may just change how you think about threat intel. 🔗 Register ahead of time for events and 1:1 meetings: www.sentinelone.com/lp/black-hat-2025/ -
SentinelOne
@SentinelOne
Milestone unlocked ✅. Thank you to 10,000+ streamers of our new show 'Just A Sec' 🎉 🚀
🥸 'Just A Sec' is a no-holds-barred, quick-fire monthly livestream (LinkedIn, X, Youtube) & podcast via Spotify. If you have missed any of the first three episodes, you can listen or rewatch them;
🎧 Spotify - open.spotify.com/show/4ADXHYe0lGiTMKvzXmYknj
📺 Youtube - www.youtube.com/@Sentinelone-inc/streams
📲 LinkedIn - www.linkedin.com/company/sentinelone/events/?viewAsMember…
'Just A Sec' is cybersecurity like you’ve never heard it before — unfiltered, formatted to entertain, and always on-point. In each episode, we tackle the latest real-world incidents and intelligence, with a few laughs along the way. Our hosts Drea, @DakotaCary, @stonepwn3000, @juanandres_gs keep it real by taking on the most elusive adversaries, emerging hacking techniques, and lifting the lid on the hidden forces shaping our digital world 🔥
Stay tuned for a big announcement next week about episode 4! 🚨 -
SentinelOne
@SentinelOne
🔒 Why the Future of Cloud Security Depends on AI-Savvy Defenders: From expanding attack surfaces to empowering defenders, AI has become both a novel risk and a force multiplier in cloud security.
In our latest blog, we unpack how adversaries are adapting familiar tactics for the AI era. We explore:
🔸 How AI tools are being targeted via misconfigurations and leaked credentials
🔸 The rise of AI-powered infostealers like Predator AI
🔸 The evolution of slopsquatting through LLM hallucinations
🔸 The urgent need for AI Security Posture Management (AI-SPM)
While attackers are innovating with AI, defenders are too. Our research shows AI is helping security teams:
⚡Detect threats 63% faster
⚡Remediate 55% faster
⚡Increase team efficiency by up to 38%
💡 Dive into the blog to explore how AI is transforming the cloud security paradigm—both as a threat and an indispensable tool for defenders: s1.ai/Cld-2Edge
🧠 Want more insights? Join us Thursday, July 24 for our exclusive webinar, where we’ll break down findings from the Cloud Security Survey and Risk Reports, and discuss the evolving role of AI in cloud defense. s1.ai/CldSecRpW -
SentinelOne
@SentinelOne
🚨 SentinelOne Uncovers 3 Distinct Attack Clusters Targeting Microsoft SharePoint: As part of the “ToolShell” Zero-Day being exploited in-the-wild, our threat researchers have identified three distinct attack clusters, each with unique tradecraft and objectives. We first observed SharePoint exploitation on July 17, two days before Microsoft’s official advisory.
🧵 What’s happening:
– The three unique attacker clusters are targeting tech, critical infrastructure and architecture and engineering firms
– Two clusters deployed webshells designed to execute commands or collect sensitive system information. Another operated filelessly.
– PoC code is now public. Broader exploitation is expected.
🛠️ Why it matters: “ToolShell” is trivial to exploit, stealthy, and lets attackers gain persistent access to valuable environments. SharePoint’s role as a data store and delivery mechanism makes it a high-value target.
📌 Go deeper ➡️ s1.ai/toolshell
- Timeline of in-the-wild exploitation
- Technical deep dive on all three TTP clusters
- Mitigation steps and IOCs
- Detection & hunting queries from SentinelOne
🛡️ SentinelOne continues to monitor and assist customers. -
SentinelOne
@SentinelOne
SentinelOne’s @DakotaInDC joined @MSNBC to explain how Beijing is weaponizing civilian chaos—from grid attacks to job losses—as part of a cyber deterrence strategy.
📺 Watch below to learn:
- Why this is more than espionage
- How stolen IP costs U.S. jobs
- What Volt Typhoon reveals about China's long gameThis media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
🚨 The Good, the Bad, and the Ugly in Cybersecurity: Weekly Threat Recap 🚨
👍 The Good: A former U.S. Army soldier has pleaded guilty to hacking and extorting telecom companies while he was on active duty, accessing sensitive data to demand ransoms. Global justice efforts also include police dismantling the Romanian ransomware gang “Diskstation” that was targeting NAS devices and Europol disrupting the infrastructure of pro-Russian NoName057(16).
👎 The Bad: Katz Stealer — a new, turnkey malware-as-a-service (MaaS) — is targeting credentials and crypto assets, fueling cybercrime. This malware is built for more widespread adoption with its accessible pricing and low barrier to entry.
😱 The Ugly: North Korean-based hackers have flooded the npm registry with 67 malicious packages further attempting to poison the open-source ecosystem via software supply chain attacks.
🔍 Read the full SentinelOne breakdown: s1.ai/GBU7-Wk29 -
SentinelOne
@SentinelOne
Do not miss out on Pre Sale, tickets are only $699! 💜 Lead the AI Era Cybersecurity Revolution at OneCon 2025--onecon.io!
With cyber threats accelerating, equip yourself with next-gen strategies to crush adversaries. Do not miss out on your discounted ticket for just $699 (on sale until July 31)☺️
SentinelOne is the unrivalled leader in the AI era, redefining cybersecurity with unmatched innovation. Immerse yourself in hands-on workshops, captivating keynotes and forge connections that shape the future
Dare to stay ahead—grab your ticket at onecon.io! -
SentinelOne
@SentinelOne
⚠️ A new battleground in the fight against cybercriminals: The expanding AI attack surface in cloud environments.
🤖 Our new 2025 Cloud Security Risk Report identifies emerging areas security leaders and practitioners should have on their radar including:
▶️ AI Services with Overly Permissive Roles: Misconfigurations are leaving systems and data vulnerable.
▶️ Malicious Model Context Protocol (MCP) Tools: Dangerous compromise potential exploiting AI integrations.
▶️ Compromised GPU Plugins: Hidden dangers in AI infrastructure are being targeted.
The attack surface is expanding fast. Stay ahead with SentinelOne’s AI-powered cloud security solutions. 💪
🔗 Read the full report for actionable insights: assets.sentinelone.com/cnapp/cloud-security-risk-report-en -
SentinelOne
@SentinelOne
Defending the cloud--and sustaining the pace of AI and cloud innovation--starts with addressing two persistent threats: Misconfigurations and compromised credentials.
Today, SentinelOne is launching the first in our three-part blog series that unpacks insights from two new reports:
📘 Cloud Security Survey Report – Perspectives from 400 security leaders
📕 Cloud Risk Report – 5 emerging threat themes for 2025
🔍 Misconfigurations remain the top entry point for attackers—even as CSPMs are seen as both vital and effective.
🧠 Credentials are increasingly exploited, yet secret scanning ranks low in importance and adoption.
Foundational threats aren’t going away—they’re evolving. It’s time to rethink how we prioritize and protect.
📖 Read the blog: s1.ai/AttckVect
📅 Join our July 24 webinar: s1.ai/CldSecRpW -
SentinelOne
@SentinelOne
One Vision. Relentless Innovation. Five Years In A Row. 💜 💜 💜 💜 💜
We are proud to be named a Leader in the 2025 Gartner® Magic Quadrant™ for Endpoint Protection Platforms, for the fifth consecutive year. Thank you to our customers, partners and Sentinels—together we are reimagining cybersecurity in the AI era.
Why it matters:
✅Comprehensive protection powered by AI
✅Autonomous capabilities to reduce SOC fatigue
✅Unified visibility across Endpoint, Cloud, Identity and Security Data
📖 Read the full report: s1.ai/EPPMQ25-R -
SentinelOne
@SentinelOne
💰 Credential Theft-as-a-Service? A new, turnkey infostealer is gaining traction fast—and it’s not just for sophisticated actors, with this malware’s "accessible" pricing and low barrier to entry.
Why it matters: Katz Stealer is a turnkey Malware-as-a-Service with a slick web panel, lower cost, and a feature set built for scale. It’s marketed across Telegram, Discord, and cybercrime forums—and being used by threat actors of all skill levels.
🧠 Driving the rise:
• Easy-to-use builder for custom payloads
• Built-in campaign and log management
• Support for crypto wallets, browsers, messaging apps
• Stealthy delivery: Steganography, process hollowing, in-memory loaders
The bottom line: Katz is a modern infostealer built for more widespread adoption. Its success highlights the dangerous trend of professional-grade malware made accessible to the masses.
👉 Read the full analysis from our threat researchers: s1.ai/katz -
SentinelOne
@SentinelOne
AI isn’t a security feature—it’s the foundation. Choose the leading AI-powered cybersecurity, now even easier to deploy through your AWS account.
SentinelOne’s integrated platform and agentic AI analyst is now in AWS Marketplace’s new AI Agents category.
🔐 What’s new: Singularity® Cloud Security, AI SIEM, and Purple AI — the industry’s most advanced agentic AI analyst — are now available in AWS Marketplace’s AI Agents and Tools category.
🧠 Why it matters: AI-powered defense isn’t optional anymore. SentinelOne brings unified cloud, data, and endpoint protection — with real-time detection, automated investigation, and machine-speed response.
🏁 Fast-track deployment: AWS-native access. No vendor sprawl. No procurement delays. Just enterprise-grade security at cloud scale.
🔗 Explore the future of autonomous defense: s1.ai/AWS-AgTls -
SentinelOne
@SentinelOne
A Leader and Trusted AI Partner 🤝
We are proud to be named a Leader in the 2025 Gartner® Magic Quadrant™ for Endpoint Protection Platforms for the fifth consecutive year. Thank you to our customers, partners and Sentinels—together we are reimagining cybersecurity in the AI era.
🔗 Learn more here: s1.ai/EPPMQPR25 -
SentinelOne
@SentinelOne
🎯 The countdown to Black Hat 2025 is on — and we are so ready 🔥. Join SentinelOne in Las Vegas, August 2–7, for one of the most important cybersecurity events of the year.
🛡️ From AI-powered threat detection to securing development in cloud and beyond, we’re showcasing the innovations that are redefining cyber resilience for the modern enterprise.
📍 Stop by Booth #3033 to:
✅ Explore our latest platform enhancements
✅ Meet 1:1 with SentinelOne experts
✅ Experience live demos and exclusive in-booth sessions
✅ Test your hunting skills in Mortal v Machine
✅ Attend 'Blurred Lines' and walk away with intel that could change your security posture
🔗 Book a meeting or get more details here: www.sentinelone.com/lp/black-hat-2025/ -
SentinelOne
@SentinelOne
🚨 The Good, the Bad, and the Ugly in Cybersecurity: Weekly Threat Recap 🚨
👍 The Good: Global Authorities Disrupt Two Nation State Threat Actors & Arrest Four Suspects Linked to DragonForce Attacks
👎 The Bad: macOS.ZuRu Malware Trojanizes Trusted Apps like Termius and Uses Khepri-Based Backdoor For Remote Access.
😱 The Ugly: DoNotTeam Escalates Cyber Espionage Tactics With LoptikMod Malware, Targeting Embassies in Europe to Gather Diplomatic Intel on South Asian Relations.
🔍 Read the full SentinelOne breakdown: s1.ai/GBU7-Wk28 -
SentinelOne
@SentinelOne
🧬 Your CI/CD pipeline is your next breach vector... 🌥️ 🤔
From poisoned packages to AI-hallucinated typosquats, today’s supply chain attacks are stealthier, smarter, and more pervasive than ever. Your build process is now a high-value target.
🔒 At SentinelOne, we believe the best defense starts early!
🚧 CI/CD security isn’t optional. It’s critical.
🔎 Learn how to defend the build, secure your software supply chain, and stay ahead of emerging threats.
👉 Read the 2025 Cloud Risk Report: assets.sentinelone.com/cnapp/cloud-security-risk-report-en -
SentinelOne
@SentinelOne
💡 Call for Papers: Ignite the AI Era discussion with your ideas at OneCon 2025!
OneCon is where our industry redefines and reimagines cybersecurity with fearless innovation. Share the stage with the industry’s top minds, together pushing the boundaries that spark groundbreaking ideas 🔥
With cyber threats surging in the AI era, your ideas can reshape the battlefield. Submit your insights by August 15 at s1.ai/OneConCFC -
SentinelOne
@SentinelOne
🚨macOS.ZuRu Resurfaces with a New Twist: Trojanized Termius App and Modified Khepri C2 🚨
Our latest research reveals a new variant of macOS.ZuRu, continuing to target macOS users seeking legitimate business tools. This persistent threat leverages a modified Khepri C2 framework and a new technique for trojanizing applications, specifically observed in a doctored version of the cross-platform SSH client, Termius.
Read the full technical breakdown from @PhilStokes and @DineshDevadoss - s1.ai/zuru
🔍 Key findings From the Front Lines:
- Legitimate Termius app replaced with a malicious bundle signed with an ad hoc signature
- Modified loader downloads second-stage payloads, including a tailored Khepri implant
- Persistence achieved via LaunchDaemons and deprecated APIs
- Beacon communicates over port 53, using decoy domains to evade network detection
Attackers continue to target macOS users — especially developers and IT professionals — by trojanizing trusted tools. The tactics may change, but the goal remains the same: silent compromise.
🛡️SentinelOne Singularity detects and neutralizes all components of this threat, whether you’re in Detect or Protect mode. -
SentinelOne
@SentinelOne
💜 Lead the AI Era Cybersecurity Revolution at OneCon 2025!
With cyber threats accelerating, equip yourself with next-gen strategies to crush adversaries. Do not miss out on your discounted ticket for just $699 (on sale until July 31)☺️
SentinelOne is the unrivalled leader in the AI era, redefining cybersecurity with unmatched innovation. Immerse yourself in hands-on workshops, captivating keynotes and forge connections that shape the future
Dare to stay ahead—grab your ticket at onecon.io! -
SentinelOne
@SentinelOne
Episode 3 - Just A Sec: Cybersecurity Unfiltered. Fast, Frank, Intel. x.com/i/broadcasts/1yNGaLWpYOgKj
-
SentinelOne
@SentinelOne
📣 OneCon 2025. Where the AI Era meets Cybersecurity 🔥
In a world where the convergence of Humans + AI is changing our everyday lives—OneCon unites the best-of-the-best in the cybersecurity industry 🤲
Cyber threats evolve faster than humans alone can anticipate, AI is not only necessary—it's mandatory. Arm yourself with cutting-edge strategies to outsmart adversaries
SentinelOne is the unrivalled leader in the AI era, redefining and reimagining cybersecurity with unmatched innovation—Join us 🤝
Dare to stay ahead—grab your spot at onecon.io! -
SentinelOne
@SentinelOne
🚨Sound the alar… Wait, never mind. SentinelOne’s agent-based cloud runtime protection blocks the attack before it even starts.💡In the video below, watch the threat end before it begins 🛑
What’s happening: Here’s a real-time demo showing how our Cloud Workload Protection solution neutralizes runtime threats in seconds—before attackers can gain ground.
Why it matters: Cloud attacks are fast, complex, and increasingly automated. This demo shows how mature cloud native agents provide defenders with the tools and deep telemetry to fight back with even more speed—and precision.
🚫 Stop the threat before escalation
✅ See the clean chain of decisive actions
👁 Gain full visibility into attacker movement
🧠 Let Purple AI do the triage and recommend the next move to your team
The big picture: It’s not about reacting after damage is done. It’s about being ready—and fast—enough to prevent it altogether.
Learn more: s1.ai/CldSecure -
SentinelOne
@SentinelOne
🚨 New: @LabsSentinel exposes NimDoor, a novel macOS malware used by DPRK threat actors to target Web3 and crypto
🧪 Bottom line: NimDoor reflects a leap in DPRK’s offensive toolkit, mixing compile-time trickery with native scripting to sidestep traditional defenses.
🧠 What’s new:
Signal-based persistence via SIGINT/SIGTERM—never before seen on macOS
AppleScript as a beacon/backdoor, not just for initial access
Encrypted wss comms and process injection not typical of macOS TTPs
🔍 Go deeper: The malware chain uses fake Zoom updates, Nim and C++ payloads, and Bash scripts to exfiltrate browser, Keychain, and Telegram data.
📖 Full research by @philofishal and @syrion89: s1.ai/nimdoor -
SentinelOne reposted
SentinelLabs
@LabsSentinel
💜 Our December 2024 research into DPRK IT Worker operations identified key front companies and personas now named in DOJ indictments.
🔗 SentinelLabs by @DakotaInDC & @TomHegel: www.sentinelone.com/labs/dprk-it-workers-a-network-of-act…
🔗 DOJ: www.justice.gov/opa/pr/justice-department-announces-coord… -
SentinelOne
@SentinelOne
⭐ The only vendor with 100% 4 and 5 star rating. 100% would recommend. The latest Customers’ Choice recognition for SentinelOne.
Recognition rooted in customer reviews: SentinelOne was named a Strong Performer in the 2025 Gartner® Peer Insights™ Voice of the Customer for Cloud Security Posture Management (CSPM) tools 🌤️
It’s the latest recognition for SentinelOne, which was also named:
⭐ Customers' Choice for Extended Detection and Response (XDR)
⭐ Customers' Choice for Cloud-Native Application Protection Platforms (CNAPP)
⭐ Customers' Choice for Managed Detection and Response (MDR)
As cloud environments grow more complex, point solutions can’t keep up. SentinelOne’s AI-powered Singularity Cloud Security gives security teams visibility, automation, and control—all in one platform.
What customers are saying:
"My overall experience on the Singularity CSPM tool is outstanding. its comprehensive visibility, AI powered risk assessment, automation capabilities, scalability and integration helps seamlessly to choose singularity over other brands," said an Educator.
”Provides automated remediation and response capabilities, reducing the time and effort required to address security incidents," said a Cloud Engineer for an IT Services company.
The bottom line: Cloud security can’t be patched together. With SentinelOne, it’s comprehensive and unified, by design 🧠
🔗 See why customers trust us to secure their cloud environments: www.sentinelone.com?p=124967&post_type=press&preview=1&_p… -
SentinelOne
@SentinelOne
☁️Cloud security gaps are widening—and attackers are exploiting them.
🔐 Leaked cloud credentials = Breach Waiting to Happen. Our 2025 Cloud Security Risk Report breaks down five key risk themes shaping the cloud threat landscape this year.
SentinelOne found over 100,000 credentials exposed on AWS, GCP and Azure over the last 12 months. Infostealers are back—and smarter (and cloudier!) than ever. 🧠 Additionally, AI tools are leaking secrets.
🔎 See where cloud security is falling short, how threats are evolving, and how SentinelOne is helping customers close the gap.
📖 Read the full report: assets.sentinelone.com/cnapp/cloud-security-risk-report-en -
SentinelOne
@SentinelOne
🚨 The Good, the Bad, and the Ugly in Cybersecurity: Weekly Threat Recap 🚨
👍 The Good: U.S. authorities have charged British national Kai West with operating the “IntelBroker” online identity, which has caused over $25M in data loss globally.
👎 The Bad: Russia-linked hacking group APT28 is deploying phishing attacks in Signal chats to target Ukrainian systems with malware, escalating regional cyber threats.
😱 The Ugly: Canada and the FBI say that China-backed Salt Typhoon exploited a Cisco flaw to target Canadian telecom firms, exposing critical infrastructure vulnerabilities.
🔍 Read the full SentinelOne breakdown: s1.ai/GBU7-Wk26 -
SentinelOne
@SentinelOne
PartnerOne EMEA Summit, it's go time 🚀 💜
This week we are joined by hundreds of partners from all across the region, sharing experiences, education, real word stories, and together shaping the future of cybersecurity in the AI era 🤝
🤖
Stay tuned for more content this week and if you are attending, drop a selfie in the comments 🤳 -
SentinelOne
@SentinelOne
🚨 The Good, the Bad, and the Ugly in Cybersecurity: Weekly Threat Recap 🚨
👍The Good: The Pentagon’s CDAO is harnessing AI to supercharge cybersecurity, leveraging “partnerships with frontier AI companies” to bolster national security.
👎 The Bad: A previously unknown threat actor dubbed Water Curse has weaponized 76 GitHub accounts to deliver malware, concealing malicious payloads designed to exfiltrate data and establish long-term access.
😱 The Ugly: A now-patched security flaw in Google Chrome was exploited by the threat actor TaxOff to install a stealthy “Trinper” backdoor onto targeted systems.
🔍 Read the full SentinelOne breakdown: s1.ai/GBU7-Wk25 -
SentinelOne
@SentinelOne
🔒 AI-Powered Cloud Security, Co-Built with @awscloud. We’re making cloud security smarter, faster, and easier to access.
What’s new: At AWS re:Inforce 2025, SentinelOne is showcasing how we’re redefining cloud security—partnering with AWS to deliver autonomous protection that scales with your business. From being a launch partner for the new evolution of the AWS Security Hub to Hyperautomation and AI SIEM in the AWS Marketplace, we’re powering what’s next.
Why it matters: Cloud workloads are growing. So are threats. Our strategic partnership with AWS means customers can now consolidate, automate, and accelerate security operations—directly in the environments they rely on most. That’s what next-gen security, built for the cloud, looks like.
👉 Read how SentinelOne and AWS are helping customers move faster and stay secure: s1.ai/AWS-SecHb
#awsreinforce -
SentinelOne reposted
LABScon 2026
@labscon_io
The #labscon25 call for papers closes next Monday!
Get your abstracts in www.labscon.io/cfp/ -
SentinelOne
@SentinelOne
Cloud Security just got smarter. Co-built. Cloud-native. AI-powered. 💪
As an official launch partner for AWS Security Hub, SentinelOne and AWS are co-developing and this could unlock new possibilities for AI and automation in cloud security:
🔹 Ingest enriched findings into the Singularity™ Platform
🔹 Protect workloads across 20+ AWS services
🔹 Trigger automated security workflows
Learn more: s1.ai/AWS-SecHb -
SentinelOne
@SentinelOne
🙌 Our fastest-growing product just got easier to procure and integrate with AWS 📈
SentinelOne's AI SIEM is now on the AWS Marketplace and is an AI-powered force multiplier for security teams. Core benefits:
⚡ Cloud-native for speed and scale
🤖 Powered by agentic AI for faster detection and smarter response
🔗 Integrated with AWS-native services
Built to modernize the SOC, our Singularity™ AI SIEM is an AI-powered force multiplier. SecOps teams can now harness AI to unify threat visibility, automate triage, and accelerate response.
Learn more: www.sentinelone.com/press/sentinelone-brings-singularity-… -
SentinelOne
@SentinelOne
🚨SentinelOne has been named one of the Best Workplaces in the Bay Area by Fortune! 🚨
This recognition is a testament to the culture we’ve built—one driven by innovation and a shared mission to Secure Tomorrow.
To our amazing Sentinels: this recognition belongs to you. 💜
To future Cyber Warriors: come see what makes SentinelOne a truly great place to work. s1.ai/s1-careers -
SentinelOne
@SentinelOne
Smarter Cloud Security Starts Here 🌤️. We are so excited to be in Philadelphia this week for AWS re:Inforce 2025 💜 🇺🇸
Visit our team at booth #515 to see how our AI-powered cybersecurity platform can:
🛡️Protect your AWS cloud environment
💡Consolidate your security tools
⚡Stay ahead of threats and cloud risks
🤖 Enhance your analysts with agentic AI
Our legendary Mortal vs. Machine competition will also be in action. Make sure you stop by to put your hunting skills to the test (and let us show you how easy it is with AI)💪 -
SentinelOne
@SentinelOne
⛅ Cloud migrations just got smarter. SentinelOne has joined the AWS ISV Workload Migration Program to deliver faster, more secure transitions to the cloud—with AI-powered visibility and protection every step of the way.
Learn more. Read the press release: -
SentinelOne reposted
LABScon 2026
@labscon_io
The deadline to submit for LABScon25 is fast approaching.
Get your talks in before June 23!
www.labscon.io/cfp/ -
SentinelOne
@SentinelOne
🚨New from @LabsSentinel: @milenkowski and @TomHegel track China-nexus threat actors across 70+ victims in multiple sectors—and reveal how SentinelOne countered this global operation.
The PurpleHaze and ShadowPad clusters are expanding their reach—targeting not only global enterprises and governments but cybersecurity vendors themselves.
🔗 Read how we detected, defended, and disrupted: www.sentinelone.com/labs/follow-the-smoke-china-nexus-thr… -
SentinelOne
@SentinelOne
🚨 The Good, the Bad, and the Ugly in Cybersecurity: Our Weekly Threat Recap 🚨
👍 The Good: Global law enforcement takes down BidenCash, a major dark market trafficking stolen credit card data and personally identifiable information; busts ViLE members specializing in doxing, and halts crypto-mining abuse across 5,000+ accounts.
👎 The Bad: Iran-aligned BladedFeline targets Kurdish and Iraqi officials in a deep espionage campaign.
😱 The Ugly: Attackers poison open-source repos with malware-laced ML models, targeting crypto, CI/CD pipelines, and devs.
🔍 Read the full SentinelOne breakdown: www.sentinelone.com/blog/the-good-the-bad-and-the-ugly-in… -
SentinelOne
@SentinelOne
Just A Sec: Cybersecurity Unfiltered—Fast, Frank, and From the Front Lines x.com/i/broadcasts/1gqxvjXbPoaxB
-
SentinelOne
@SentinelOne
🤔 Why Coinbase’s $20M bounty matters—and what it says about threat actors, the state of bug bounties, and what’s next for defenders. Join us this Thursday for Episode 2 of Just a Sec, our newest livestream series with @juanandres_gs, @stonepwn3000, @DakotaInDC, and Drea London-Petter.
Unfiltered analysis. Real-world threats. No fluff.
SentinelOne
@SentinelOne
🎙️ Go behind the headlines with our experts.
📅 RSVP below or catch the livestream in your feed.
youtube.com/live/MSuwHG-54Rs -
SentinelOne
@SentinelOne
🚀 The quantum future is here—and we're helping to secure it.
Through S Ventures, SentinelOne is backing @infleqtion, a leader in neutral atom quantum tech, to help protect the next era of computing.
🔒 The quantum-secure innovation of tomorrow starts today.
📖 Read more: -
SentinelOne
@SentinelOne
🛡️The customers have spoken: SentinelOne is a Gartner® Peer Insights™ Customers’ Choice for Extended Detection and Response (XDR) for its Singularity™ Platform. As one of only two vendors recognized as a Customers’ Choice—and with 97% of users recommending our AI-powered Singularity™ Platform to stop threats, based on 144 total reviews as of Jan. 31, 2025—we’re honored by this peer recognition.
A big thank you to our customers and community. We’re focused on keeping you secure.
Read the press release: www.sentinelone.com/press/sentinelone-recognized-as-a-202…
Download the full report: www.sentinelone.com/lp/gartner-xdr/
This recognition comes on the heels of:
A Leader in the Gartner® Magic Quadrant Endpoint Protection Platforms, Four Years in a row
🏆100% Detection in the MITRE ATT&CK Evaluations, Five Years in a row
🏆2025 Customers’ Choice in the inaugural Gartner® Peer Insights™ ‘Voice of the Customer’ for Cloud-Native Application Protection Platforms (#cnapp)
A 2024 Gartner® Peer Insights™ Customers’ Choice for Managed Detection and Response (#mdr) -
SentinelOne
@SentinelOne
On May 29, 2025, SentinelOne experienced a global service disruption. During this period, customer endpoints remained protected, but security teams were unable to access the management console and related services. We apologize for the disruption and want to thank our customers and partners for their continued support.
On Saturday, May 31, we concluded our investigation into the disruption and published our findings in a formal root cause analysis (RCA) report on our website. www.sentinelone.com/blog/update-on-may-29-outage/
The report is actively being shared with all customers and partners. -
SentinelOne
@SentinelOne
📈 Q1 FY26: Revenue growth ahead of expectations. Record free cash flow margin. Triple digit YoY growth for Purple AI. Data and AI SIEM now exceeds $100MM ARR, and a continued clear line-of-sight to hitting our $1 billion in ARR milestone in FY26.
As a leader and pioneer for more than a decade in Human + AI-powered cybersecurity – and the first autonomous cybersecurity platform – we’re continuing to define cybersecurity in the age of AI.
Top highlights:
- Total Q1 revenue increased 23% YoY
- Annualized recurring revenue (ARR) of $948M with 24% YoY growth
- Record free cash flow margin of 20%
- 25% attach rate for Purple AI across subscriptions sold in quarter – and triple digit YoY bookings growth
- Data (AI SIEM) solution exceeds $100M ARR
- 22% growth of customers with ARR over $100K (YoY)
- 79% gross margin (non-GAAP)
- 3% net income margin (non-GAAP)
📺 Watch our Q1 FY26 earnings call to learn more: s1.ai/Q1-26-Ern
🗞️ Read the press release: s1.ai/Q1-26-PR -
SentinelOne reposted
Virus Bulletin
@virusbtn
SentinelOne's Mary Braden Murphy shows how ClickFix weaponizes verification fatigue to deliver RATs & infostealers. Tricking victims into infecting themselves this way has proven very effective; threat actors increasingly adding the technique to playbooks. www.sentinelone.com/blog/how-clickfix-is-weaponizing-veri…
-
SentinelOne
@SentinelOne
🇹🇭 ✨ Asia-Pacific and Japan's best cybersecurity partners came together in Bangkok for our annual PartnerOne APJ summit. Check out our highlights video 💜
Three key takeaways from this year's summit:
🤝 The Power of Many: SentinelOne's diverse ecosystem of partners is unmatched in the cybersecurity industry.
🤖 The Singularity Platform: Together with our partners the opportunity in the market is limitless. Customers are looking for AI-Powered, cloud native technologies to defend against sophisticated adversaries; and we're enabling partners with cybersecurity’s preeminent AI platform
🔥The New PartnerOne Program: Enabling partners to succeed for their customers at every stage of their journey, offering them a clear path to grow and differentiate themselvesThis media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
🧪 A growing malware tactic socially engineers users into infecting themselves. It’s low-tech, high-impact—and it’s working. In new research, we share original findings on how “ClickFix” abusing CAPTCHA overlays has been gaining traction the last 8 to 12 months. These deceptive verification challenge attacks blend effective social engineering with user-assisted execution.
Key details:
🚩 Fake "verify you're human" prompts
💻 Clipboard injection + PowerShell abuse
🦠 Payloads like Lumma Stealer & NetSupport RAT
This isn’t just trickery—it’s a shift in how threat actors are bypassing technical controls through user deception.
Full breakdown ⬇️ s1.ai/clickfix -
SentinelOne reposted
LABScon 2026
@labscon_io
HEADS-UP! The CFP is open. The request-for-invite form is open. labscon.io has all the details.
SentinelOne
@SentinelOne
🔥 The world's premier threat research conference, LABScon, is back - Sept 17–20 in Scottsdale, AZ. 🚨 Call for Papers 🚨 are now open, due in by June 23 - www.cvent.com/c/abstracts/fe3bffe0-6e1f-482d-9435-fb39af5…
Original research, invite-only, real impacts. Join top researchers from Google, Netflix, DARPA, SentinelLABS, and more at the event for cutting-edge threat intelligence.
📩 Request an invitation to LABScon - s1.ai/LABScon25This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
🔥 The world's premier threat research conference, LABScon, is back - Sept 17–20 in Scottsdale, AZ. 🚨 Call for Papers 🚨 are now open, due in by June 23 - www.cvent.com/c/abstracts/fe3bffe0-6e1f-482d-9435-fb39af5…
Original research, invite-only, real impacts. Join top researchers from Google, Netflix, DARPA, SentinelLABS, and more at the event for cutting-edge threat intelligence.
📩 Request an invitation to LABScon - s1.ai/LABScon25This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
🚨In the age of AI, defending the U.S.public sector isn’t optional—it’s mission critical. 🇺🇸
In an Industry first, our AI-powered Singularity Platform’s Endpoint Security, Purple AI, SIEM, Hyperautomation and Cloud Security capabilities have now ALL achieved FedRAMP-High Authorization 🛡️
This isn’t just a compliance checkbox. It’s SentinelOne doubling down on national security—making a strategic investment to secure the government through powerful public-private partnerships
📄 Learn more: s1.ai/FedRmpHgh -
SentinelOne
@SentinelOne
📊 Here are the top threats of last year by operating system. Click the images to see the most active threats seen across our telemetry during 2024 for the three most popular business operating systems: Windows, macOS and Linux.
🔍 To learn more, read our Annual Threat Hunting Report, a global analysis of real-world attacker behavior, based on over 1,000 incidents across 11 sectors and 15 countries. See what today’s threat actors are actually doing—and how you can stop them.
📄 Read the full report: s1.ai/ThrtRt-25 -
SentinelOne
@SentinelOne
🧠 Not all AI security is created equal. Some AI solutions are still focused on identifying problems for your SOC team to fix. SentinelOne’s Purple AI proactively reasons and will act to help solve some of these problems.
In this video from #rsac 2025, SentinelOne’s Gregor Stewart, VP of AI and Machine Learning, explains how our Purple AI Athena release shifts from detection to action—automating the policy-driven and mechanistic parts of a SOC investigation, freeing analysts to focus on what matters.
📺 To learn more, watch the full video below.
📄 Read more about Athena: s1.ai/PurpAIAthenaThis media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
💰On Anti-Ransomware Day 2025, we unpack how Ransomware-as-a-Service has evolved over 10 years into a billion-dollar criminal enterprise. From TOX to LockBit, here’s how early affiliate models transformed into today’s polished cybercrime brands—and what the modern-day RaaS means for defenders.
🔍 History, trends, and takeaways from the frontline:
✔️ How ransomware became a service economy
✔️ What affiliate models reveal about attacker incentives
✔️ How SentinelOne’s AI-powered platform stops attacks before they spread
🎯 Read the full blog post: s1.ai/AntiRansm -
SentinelOne
@SentinelOne
🛡️ In the GenAI era, data is the perimeter. It demands more than visibility—it requires autonomous, AI-powered governance and control. That’s why SentinelOne’s S Ventures is proud to back theom, creators of the first AI-native Data Operations Center (DOC).
Theom secures structured, unstructured, and AI-generated data across modern ecosystems—from Snowflake to Azure—with real-time insight, automated enforcement, and deep context.
Together, we’re extending the SentinelOne Singularity vision: autonomous protection from endpoint to AI-powered data.
🔗 Learn more: s1.ai/Theom -
SentinelOne
@SentinelOne
🕵️ Trust, encryption, and economic stress are reshaping insider threats for commercial and government organizations. This challenge to long-standing assumptions about trust, access, and oversight is highlighted by two recent cases—the Rippling–Deel espionage case and “Signalgate.”
In our latest ExecBrief, we explore:
✔️ How encrypted apps and remote work create governance gaps
✔️ Emerging tactics like disappearing messages, crypto payments, and routine access misuse
✔️ How economic pressure fuels insider activity globally
Insider threats as a central threat vector isn’t theoretical—it’s happening now. Learn how business and security leaders can adapt their strategies to meet today's realities.
📖 Read the full brief: s1.ai/InsideRsk -
SentinelOne
@SentinelOne
Just a Sec: Cybersecurity Unfiltered—Fast, Frank, and From the Front Lines x.com/i/broadcasts/1DXxyqroBDyxM
-
SentinelOne reposted
Validin
@ValidinLLC
In this collaboration with @TomHegel from @LabsSentinel just delivered at @pivot_con we break down all phases of an industrial-scale crypto phishing operation. Walk with us as we break down the FreeDrain network.
Cross posted to our blog here:
www.validin.com/blog/freedrain_unmasked/
SentinelOne
@SentinelOne
🚨 Phishing Re-Engineered for the Modern Internet—At-Scale: In joint research from @LabsSentinel and @ValidinLLC, we unveil our research into a global crypto phishing operation abusing SEO, generative AI, and free-tier web services to drain digital wallets at an industrial scale. This is FreeDrain unmasked at @Pivot_Con.
Key Details:
🔎 38,000+ lure domains
⚠️ Industrial-scale theft via search engines
🧠 AI-generated phishing content
📉 Spamdexing to outrank legit sources
To learn more, read the full report by SentinelLABS's @TomHegel and Validin's Kenneth Kinion and Sreekar Madabushi ➡️ s1.ai/FreeDrain
#pivotcon #pivotcon25 -
SentinelOne
@SentinelOne
🗓️ Today at 2 p.m. PT is the premiere of Just a Sec, our new livestream series. We’ll discuss the hidden forces shaping our digital world. Think real-world incidents, the most elusive adversaries, and emerging hacking techniques straight from the front lines. No fluff, just critical insights to keep you ahead.
🎟️ Register now or catch it live—mark your calendar.
SentinelOne
@SentinelOne
-
SentinelOne
@SentinelOne
🚨 Phishing Re-Engineered for the Modern Internet—At-Scale: In joint research from @LabsSentinel and @ValidinLLC, we unveil our research into a global crypto phishing operation abusing SEO, generative AI, and free-tier web services to drain digital wallets at an industrial scale. This is FreeDrain unmasked at @Pivot_Con.
Key Details:
🔎 38,000+ lure domains
⚠️ Industrial-scale theft via search engines
🧠 AI-generated phishing content
📉 Spamdexing to outrank legit sources
To learn more, read the full report by SentinelLABS's @TomHegel and Validin's Kenneth Kinion and Sreekar Madabushi ➡️ s1.ai/FreeDrain
#pivotcon #pivotcon25 -
SentinelOne
@SentinelOne
📆 Just A Sec is almost here. In the first-ever episode of our new livestream series, @juanandres_gs, @stonepwn3000, Drea London-Petter, and @DakotaInDC discuss the hidden forces shaping our digital world. Think real-world incidents, the most elusive adversaries, and emerging hacking techniques straight from the front lines. No fluff, just critical insights to keep you ahead.
🗓️ Mark your calendar for this Thursday at 2 p.m. PT. Register now on LinkedIn or catch it live on X: www.linkedin.com/posts/sentinelone_join-us-on-thursday-ma…
SentinelOne
@SentinelOne
-
SentinelOne
@SentinelOne
🎬 #rsac 2025, that’s a wrap. From bold conversations to breakthrough innovations, this year was one for the books. It always is.
🎥 Watch the video for a few of our favorite moments.This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
🐉🛍️ From Hacktivists to a Profit-Driven Cartel: DragonForce’s latest string of attacks on UK retailers—causing major disruptions at Harrods, Marks and Spencer, and others—highlights the group’s growing reach and expanding goals. With custom payload builders, affiliate portals, and a multi-extortion model, DragonForce continues to blur the lines between hacktivism and financial motivation.
This blog post breaks down its TTPs and offers defense guidance for security teams and threat hunters. Read more: s1.ai/DragonForce -
SentinelOne
@SentinelOne
🧠 Humans + AI. Our survival hinges on an alliance between the ingenuity of humans, fused with the relentless precision and scale of AI.
Our CEO Tomer Weingarten's #rsac 2025 main stage keynote laid out a vision for the future of cybersecurity that is empowered by AI, and how SentinelOne is delivering this for Endpoint, Cloud and Data, protecting your entire network.
This is how we reclaim our future, with human supervision and transparency.
📺 Watch the full version on YouTube - www.youtube.com/watch?v=YiIvCs4beA4
Video and Images courtesy of RSAC™ ConferenceThis media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
🎥 That’s a wrap on #rsac 2025! 💜
Thank you to everyone who dropped by to meet our team, attend our events, followed our coverage on social to learn more about SentinelOne 🙏 . Watch this video as Rachel Park recaps our top moments of the week.
See you at RSAC 2026! 👋 -
SentinelOne
@SentinelOne
Our #rsac 2025 'FOMO' party was off the hook 😮💨 ✨. An epic night, stay tuned for the video teaser.
Shoutout to our SentinelOne events, brand and design team - this is world class 👏 -
SentinelOne
@SentinelOne
🎥 Live from #rsac 2025; Nick Davis takes us through the next evolution of Cloud Security with our recent updated release of Singularity™ Cloud Security 🌥️
Singularity Cloud Security is a complete solution that goes beyond other CNAPP products in the market today. Powered by Agentic AI and Hyperatomation, Singularity Cloud Security operates inside the Singularity Platform with one unified security graph and one unified data lake 🤝
🔗 Learn more: s1.ai/UnifiedCl -
SentinelOne
@SentinelOne
🏆🏆 Two big wins. One powerful platform.
We’re proud to be named the Best Endpoint Security Solution and the Best Cloud Security Management Solution at the 2025 #scawards.
The AI-Powered Singularity™ Platform is redefining cybersecurity with autonomous protection from Endpoint to Cloud. Thank you to our Customers, Partners and Sentinels.
📄 Read all the details: www.sentinelone.com?p=120659&post_type=press&preview=1&_p…
-----------------------------------
These awards come hot on the heels of:
🏆Named The Leader and Top Performing Vendor in the Frost Radar for Endpoint
🏆Gartner® Peer Insights™ Customers’ Choice for Cloud Native Application Protection Platform
🏆100% Detection in the MITRE ATT&CK Evaluations, Five Years in a row
🏆A Leader in the Gartner® Magic Quadrant Endpoint Protection Platforms, Four Years in a row -
SentinelOne
@SentinelOne
🎥 Live from #rsac 2025
From vision to action: this is the second full day of #rsac 2025. It’s about solving complex, real-world problems. Hackim Farrell summarizes the day that was 💜 -
SentinelOne
@SentinelOne
#rsac 2025.💡 The Autonomous SOC is here and now; Where are you on your journey?
Dave Gold, Americas CTO and VP of Sales Engineering explains how security professionals need to focus on what humans do best: Strategic Oversight 🧠
🗞️ Learn more: s1.ai/Auto-SOC
The Autonomous SOC isn't a far-off dream; It's a journey we're on right now to transform SecOps. Our innovative solutions including Purple AI, AI SIEM, Cloud Security, Hyperautomation and the broader Singularity platform are harnessing the power of Agentic AI to seamlessly augment the work of human experts to defeat adversaries. -
SentinelOne
@SentinelOne
#rsac 2025, Wednesday vibes ✨ 🟣. The SentinelOne booth theatre is in full swing again today, check out our sessions on AI, Cloud Security and Ransomware.
Make sure you stop in to BarOne for a break and a snack, and to meet our team. Located at JoyRide Pizza, a quick 1-minute walk from Moscone North 🍕 -
SentinelOne
@SentinelOne
💡 The future of true AI cybersecurity is paired with the critical role of human operators. By fusing human intuition, guidance, and supervision with AI’s scale and speed to forge a resilient future, we stay ahead of adversaries.
Rachel Park and Hackim Farrell breakdown the Purple AI Athena release, live from the #rsac show floor.
🔗 Learn more here: s1.ai/PurpAIAthenaThis media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
What an incredible start to #rsac 2025, today was a blast—so you know, we had to do a lil recap. ✨ 💜
Tonight is all about ‘FOMO’, the after party of RSAC - headlined by none other than Marshmello. See you there. 💃This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
The SentinelOne team is out in full force at #rsac 2025. Are you?
🤖 Visit Booth 5863, our live theatre is in full swing. Top sessions to check out;
🛡️ Ransomware defence using Purple AI with Joe Poyner
🤖 How AI and automation are redefining security operations with Gregor Stewart
😤 Autonomously protecting cloud workloads with Joe Coletta and Chris Hosking
💡 Innovations in Purple AI, the Athena release and Auto-triage with Jeremy Goldstein
🧠 Harnessing AI for real world security with Adriana Corona and Rachel Park
You also want to check out our famous Mortal vs Machine challenge with Chris Hosking. We put Purple’s Agentic AI in your hands and see if our experts can keep up 😏.
More details here: s1.ai/rsac-2025 -
SentinelOne reposted
RSAC
@OneRSAC
Welcome to the keynote stage, Tomer Weingarten! @SentinelOne #rsac
-
SentinelOne
@SentinelOne
📣 Happening Today at 3.35pm PT. Do Not Miss This - in person at RSAC or online via the livestream below.
Our CEO Tomer Weingarten takes the #rsac main stage to usher in the era of Humans + AI, revealing how AI cybersecurity and Agentic AI will fundamentally reshape SecOps 😤
If you are watching online make sure you tune into the livestream - www.rsaconference.com/usa/sentinel-one -
SentinelOne
@SentinelOne
😎🔥One of the coolest products at #rsac 2025, says CRN. This is our Athena release, the next generation of Purple AI.
🗞️Read the full CRN article by @KyleAlspach: s1.ai/CRNAthena
📺Watch the demo video on YouTube: s1.ai/AthenaYT
The Purple AI, Athena release, showcases the cybersecurity industry’s first true end-to-end Agentic AI capabilities that mirror the deep security reasoning and sophisticated orchestration of advanced human SOC analysts
This release will also open up Purple AI to third party SIEM platforms and data lakes, bringing the full power of SentinelOne’s Agentic AI and automation to all security data in the modern SOC, wherever it resides. -
SentinelOne
@SentinelOne
At #rsac 2025, all roads lead to SentinelOne. Find us at booth N-5863 🔥 💜
-
SentinelOne
@SentinelOne
🚀 Big news from #rsac 2025: End-to-end Agentic AI. Introducing the next generation of Purple AI, the Athena release.
Broad production-level adoption of Purple AI over the past 2 years has enabled SentinelOne to create highly sophisticated and security-specific models trained on real-world security use cases.
The Purple AI, Athena release, showcases the cybersecurity industry’s first true end-to-end Agentic AI capabilities that mirror the deep security reasoning and sophisticated orchestration of advanced human SOC analysts. This release will also open up Purple AI to 3rd party SIEM platforms and data lakes – bringing the full power of SentinelOne’s Agentic AI and automation to all security data in the modern SOC, wherever it resides.
Purple AI is the industry’s most advanced Agentic AI— designed to deliver three primary benefits:
🔹 Deep security reasoning at machine speed
🔹 Full-loop remediation and response with hyperautomation
🔹 Seamless, data source agnostic integration
With Purple AI, security teams move beyond alert fatigue to autonomous action—stopping threats faster, smarter, and at scale. These innovations relieve overstretched SecOps teams by dramatically reducing the human dependency of manually triaging, investigating, and responding to threats.
Agentic AI isn’t only a future state—it’s here now. Delivered by SentinelOne.
📺 Check out our demo video which showcases Purple AI in action with Splunk and OKTA
🔗 Learn more here: s1.ai/PurpAIAthenaThis media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
🟣 🎙️Live from #rsac 2025: A special, SentinelOne edition of @riskybusiness; Wide World of Cyber. SentinelOne’s @alexstamos and Steve Stone @stonepwn3000 joined Patrick Gray, spilling all the tea on our new and novel research about how cybersecurity vendors are increasingly being targeted by, and defending against, nation-state actors including #china and #northkorea.
Spoiler alert: It all started when North Korean fake IT workers started applying for SentinelOne jobs. Rather than throw these resumes into the bin, our researchers decided to take it a step further and continue the conversation 🔥
Special thanks to Pat for his remote dial into this show as he was unable to travel to be in person. Also a special thanks to our event partners, AWS and Obsidian Security.
📄 Read the full research, you won’t regret it: s1.ai/TopTier
🎧To listen to the full podcast episode once it’s published here soon, follow us on social media. -
SentinelOne reposted
Aleksandar Milenkoski
@milenkowski
🚨New research drop: Top Tier Target | What It Takes to Defend a Cybersecurity Company from Today’s Adversaries
🌐 China-nexus APTs targeting supply chains
🔍 DPRK IT workers infiltrating hiring pipelines
🛠 Ransomware crews probing EDR platforms [1/2] -
SentinelOne
@SentinelOne
RSAC 2025 is here!! 🔥💜 Make sure you stay tuned into our socials this week as we bring you all the action from the Moscone Center, San Francisco.
This week is packed with SentinelOne activations for you to learn about Agentic AI, cloud security, endpoint security, hyperautomation, and AI SIEM. Make sure you meet up with us, check it out below.
🎙️Watch a live podcast recording of Risky Business; Wide World of Cyber, with Alex Stamos, Steve Stone and Patrick Gray. Monday, April 28th at 4pm
👔Hear from our CEO, Tomer Weingarten during his main-stage keynote on Agentic AI, a fireside chat at the Piper Sandler CEO Summit, and at NightDragon Panel
🤖Participate in our Mortal vs. Machine competition at Booth N-5863—and get all your SentinelOne questions answered in a hands-on demo of the world's leading AI-powered cybersecurity platform
🍕Network at our exclusive executive lounge, BarOne, at Joyride Pizza above Moscone North
🔮Witness the future of cybersecurity at our S Ventures Pitch for Charity, as five groundbreaking startups pitch their innovations directly to the industry's top CSOs
🎉#fomo - Get on the guest list for THE after party of RSAC, Tuesday, April 29th at 715 Harrison. This year's party is headlined by MARSHMELLO
👉 Sign up for all the action here and see you on the show floor: s1.ai/RSAC-25 -
SentinelOne
@SentinelOne
🧠 New from SentinelLABS ➡️ Cybersecurity vendors are actively defending a rarely-discussed but crucially important attack surface: themselves.
Our new research reveals how we as vendors are actively being targeted by sophisticated and motivated adversaries—from nation-state actors like China and North Korea to today’s most brazen cyber criminals.
Here are a few of the key trends reshaping cyber risk:
🌐 China-nexus APTs exploiting supply chains
🔍 DPRK IT workers infiltrating hiring pipelines
🛠 Ransomware crews probing EDR platforms
This isn’t just research—it’s a warning to the cybersecurity industry and community. When adversaries evolve, so must our defenses. Explore the tactics, tradecraft, and takeaways: s1.ai/TopTier -
SentinelOne
@SentinelOne
📊 Our annual Ransomware Group Risk Matrix exposes how today’s top operations move from intrusion to impact, mapping major families against the MITRE ATT&CK framework.
🧠 Key takeaways:
🔀 Ransomware TTPs are converging across groups
💨 Defense evasion is central to every campaign
👟 Many adversaries now prioritize speed over stealth
🔍 To learn more, read our Annual Threat Hunting Report, a global analysis of real-world attacker behavior, based on over 1,000 incidents across 11 sectors and 15 countries. See what today’s threat actors are actually doing—and how you can stop them.
📄 Read the full report: s1.ai/ThrtRt-258
SentinelOne
@SentinelOne
-
SentinelOne
@SentinelOne
🚨 Our Weekly Cybersecurity Roundup 🚨
👍 AI is increasingly enabling defenders to spot threats at machine speed, including advanced persistent threat actors and ransomware groups.
👎 Russian hackers are exploiting Microsoft OAuth workflows to sneak into the cloud environments of Ukraine allies and gain unauthorized access to Microsoft 365 accounts.
😰 The FBI says the U.S. lost a staggering $16.6B in cybercrime losses last year—a record-breaking year for digital theft.
🔎 Read the full breakdown: s1.ai/GBU7-Wk17 -
SentinelOne
@SentinelOne
🎧 AI is the now and the future of cyber defense at scale: For security leaders, this isn’t theory. It’s innovation and it’s execution.
In the latest podcast episode of AWS for Software Companies, SentinelOne's Ric Smith, delves into how Purple AI, powered by Amazon Bedrock, is transforming security operations. Key details:
⚡ Operational Efficiency: Addressing alert fatigue and talent shortages by automating threat detection and response.
🔎 Advanced Threat Detection: Combating AI-driven threats like sophisticated phishing and deepfakes.
🛡️ Future-Proofing Security: Preparing for autonomous AI agents and orchestrated cyberattacks.
🤝 Strategic Collaboration: Leveraging AWS infrastructure for scalable and cost-effective security solutions.
🎧 Discover how integrating AI can enhance your organization's resilience against evolving cyber threats. Listen to the full episode: s1.ai/AWS-SftWr -
SentinelOne
@SentinelOne
🚨 Amazon SageMaker, Where Power Meets Risk: Are your AI pipelines secure—or a breach waiting to happen? Novel research on five real attack vectors shows how a SageMaker misconfiguration can introduce serious security risks.
🪣Object Storage Compromise
🐍 AI Data Poisoning
🔑 Credential Theft
👎 Malicious User Authentication
📖 Registry Compromise and Persistence
🛡️ In our latest blog post, learn more, including how SentinelOne Singularity Cloud Security helps you shift left, prioritize in real-time and detect and respond at runtime: s1.ai/SageMaker -
SentinelOne reposted
Aleksandar Milenkoski
@milenkowski
🚨New research drop: Ransomware’s New Masters: How States Are Hijacking Cybercrime
This @VirtualRoutes report offers a comparative analysis of ransomware use by suspected state-aligned clusters from Russia, China, North Korea, and Iran. [1/2] -
SentinelOne
@SentinelOne
🔥 The RSAC 2025 countdown is on! Don't miss out on all the action with our SentinelOne team. RSVP here: s1.ai/RSAC-25 🎟️ 💜
Monday April 28th from 4pm at Shack15
SentinelOne's CISO, Alex Stamos and Senior Vice President of Threat Discovery and Response, Steve Stone join renowned host Patrick Gray in a special live audience recording of “Risky Business; Wide World of Cyber.”
Stick around afterward for an exclusive happy hour with our event partners Amazon Web Services and Obsidian Security -
SentinelOne
@SentinelOne
🚀⛅ The next evolution of cloud security is here. Introducing the new Singularity™ Cloud Security: A complete CNAPP, powered by Generative and Agentic AI, in one unified platform.
With SentinelOne, AI isn’t just a buzzword—it’s the unifying force and underlying strategy that gives you holistic autonomous protection.
🔎 Deep Visibility® across multi cloud, workloads, endpoints, data and identities
✅ Shift further left by identifying vulnerabilities before production, with agentless scanning of code repos, secrets, container registries, and IaC templates
🧠 Purple AI™ for real-time threat investigation and response
🚀 No-code Hyperautomation for remediation and operational workflows at speed and scale
AI-powered, autonomous, and unified. No magic, just real security from SentinelOne.
🔗 Learn more: s1.ai/UnifiedClThis media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
🚨 Our Weekly Cybersecurity Roundup 🚨
👍 CISA has extended funding to keep critical CVE services online, ensuring zero gaps in global vulnerability tracking.
👎 Attackers are misusing the AI presentation platform Gamma to host phishing pages that spoof Microsoft 365 login screens.
😰 China-linked threat actor Mustang Panda has been targeting Myanmar with custom, previously unreported malware in another wave of state-sponsored cyber espionage.
🔎 To learn more, read the full blog post: s1.ai/GBU8-Wk16 -
SentinelOne
@SentinelOne
👉 Too many AWS security fixes treat symptoms, not causes. In this guest blog for SentinelOne, AWS Security Hero @TeriRadichel breaks down the most common, real-life risks cloud architects face and how to fix them with architecture-first thinking.
👉 MFA policies can still be bypassed—Learn how to fix that
👉 Removing AWS access keys doesn’t eliminate risk, it just shifts it
👉 Browser-based MFA? This is often more exploitable than it seems
📄Read the full blog post: s1.ai/AWS-Gtchs -
SentinelOne
@SentinelOne
🔥The threats defining the present—and risks impacting our future. This is our annual threat hunting report, out now. @stonepwn3000, Senior Vice President of Threat Discovery and Response, shares three reasons why this report is a must-read:
1️⃣ Discover the most sophisticated and the most persistent threats our AI-powered platform and our threat services teams defend against 24x7x365
2️⃣ Real-world intrusions—deep-dive Incident Response case studies (including data theft via JIRA)
3️⃣ Strategic outlook—Our analysis on global geopolitical risks that boards and the C-suite can’t ignore
📘 Get the full report: assets.sentinelone.com/wt-reports/watchtower-2024-eoy-rep… -
SentinelOne reposted
RSAC
@OneRSAC
Tomer Weingarten, @SentinelOne’s CEO, will share what the cybersecurity industry is doing and must do to outpace our ever-evolving adversaries in this upcoming #rsac 2025 Keynote. path.rsaconference.com/flow/rsac/us25/FullAgenda/page/cat…
Tuesday, April 29
3:35 PM - 3:55 PM PT -
SentinelOne
@SentinelOne
🇨🇳 🗞️ Why did China choose now to publicly accuse three alleged NSA hackers? SentinelOne's China analyst, @DakotaInDC , weighs in, telling @NBCNews it's less about curbing hacking behavior and more about a propaganda win. s1.ai/ChNSA-NBC
SentinelOne
@SentinelOne
"They’re celebrating [a holiday, National Security Education Day] by putting out this piece. For me this says a lot about what the purpose of the claims are,” @DakotaInDC said.
📰 Read the full story by @kevincollier: s1.ai/ChNSA-NBC -
SentinelOne
@SentinelOne
💡 The right AI doesn’t just assist experts—it creates them. In our latest PinnacleOne Executive Brief, we unpack what economists are getting right (and wrong) about AI and workplace productivity and what it means for CISOs, SOC teams, and security leaders.
🤖 Key insight: Specialized AI, like SentinelOne’s Purple AI, can offer expertise quickly and reliably. The result is higher output, smarter defenses, and measurable ROI.
📄 To learn more, read our new blog post by @DakotaInDC: s1.ai/P1-EconAI -
SentinelOne
@SentinelOne
🤖 🔄 🌐 MCP is an innovative framework that connects LLMs to external tools and real-time data, but it can be a double-edged sword. Our latest blog post dives into how you can secure your MCP architecture, minimize the attack surface, and where SentinelOne can help.
📄 Read more: s1.ai/MCP-Mania -
SentinelOne
@SentinelOne
🏆🛡️SentinelOne is the leader and top-performing vendor for both Growth and Innovation in the 2025 Frost and Sullivan Radar™ for Endpoint. Singularity™ Endpoint earned best-in-class marks for performance, growth, and innovation.
Highlights in achieving this leadership position:
🛡️100% Detections in the MITRE ATT&CK® Evaluations, five years in a row
⛅Cloud native AI-powered architecture that enables rapid, autonomous detection and response
🤖Unique agent architecture limiting kernel interactions, providing customers with unmatched stability and assurance
🤝Technology and partnership differentiation with an expanding global market footprint
📈Rapid market adoption of other Singularity™ Platform modules such as AI SIEM, Cloud, Identity, and Purple AI
We’re honored to be recognized as the leader in the AI era of cybersecurity.
📄 Read all the details: s1.ai/FrstRdr25
—------------------------------------
This recognition also comes on the heels of:
🏆100% Detection in the MITRE ATT&CK Evaluations, Five Years in a row
🏆A Leader in the Gartner® Magic Quadrant Endpoint Protection Platforms, Four Years in a row
🏆CRN Hottest 100 AI Cybersecurity Companies
🏆Innovation of the Year - Purple AI: CyberScoop 50
🏆Gartner® Peer Insights™ Customers’ Choice for Endpoint Protection Platforms (#epp)
🏆Gartner® Peer Insights™ Customers’ Choice for Managed Detection and Response (#mdr) -
SentinelOne
@SentinelOne
🔥 One of the Hottest 100 AI Cybersecurity Companies of 2025! This recognition by CRN underscores our commitment to innovation and delivering cutting-edge AI-powered protection against evolving threats.
Highlights from CRN’s Kyles Alspach:
🟣 “Purple AI technology enables simplified threat hunting—across first- and third-party data—as well as natural language queries for accelerated responses to threats.”
🟣 “ Purple AI also powers its automated investigation capability that can conduct threat investigations on an analyst’s behalf.”
SentinelOne continues to lead the charge in the AI era of Cybersecurity.
🗞️ Learn more: s1.ai/CRNAI-100 -
SentinelOne
@SentinelOne
🚨 Our Weekly Cybersecurity Roundup 🚨
👍 Police have detained at least five people linked to SmokeLoader malware after dismantling its infrastructure last year for Operation Endgame.
👎 @LabsSentinel: New AI-powered AkiraBot is abusing LLMs to send tailored spam to SMBs at scale and evade CAPTCHAs.
😰 GBU-linked hackers are using infected USB drives to attack western military missions in Ukraine and install infostealers.
🔎 To learn more, read the full blog post: s1.ai/GBU7-Wk15 -
SentinelOne
@SentinelOne
📈🤖No longer an emerging trend, AI is now an operational necessity, according to new research from TechTarget’s ESG. And, now that the technology has hit its inflection point, all spotlights are focused on a new power duo: agentic AND generative AI.
The future of the SOC is human-AI collaboration at speed and scale. Security leaders know this so they’re demanding AI that works right now. This new study reveals how security teams are adopting agentic and generative AI to reshape operations and accelerate the journey toward an autonomous SOC.
Key insights:
⚙️ 96% of SOCs say AI improves efficiency
📈 70% plan to increase investment in AI security tools
🧠 92% see improved security posture with AI
✅ Performance, usability and privacy are top requirements
🔗 To learn more, read the blog: s1.ai/AI-Inflct -
SentinelOne
@SentinelOne
🖇️🌐 From a 404 Error to a Supply Chain Threat: A minor DNS misconfiguration can quickly become a major threat.
📄 Read our new blog post to learn how subdomain takeovers can be used to stage supply chain attacks—and how to stay protected: s1.ai/DNS-Miscon -
SentinelOne
@SentinelOne
🚨 Sophisticated Spam Fueled by LLM-Generated Content: An AI-powered spam framework is targeting over 400,000 websites——successfully spamming 80,000+ of them across Shopify, Wix, Squarespace, and more. In new research from @LabsSentinel, we reveal how AkiraBot, a modular Python framework, abuses OpenAI’s APIs to generate unique, site-tailored spam messages.
📄 Read the research from @LabsSentinel @spiderspiders_ and Jim Walter: s1.ai/akirabotPost not available here, view on X
SentinelOne
@SentinelOne
Key details:
🔹 Uses GPT-4 to craft convincing outreach
🔹 Targets small to medium sized business website contact forms and chat widgets
🔹 Employs multiple CAPTCHA bypass mechanisms and network detection evasion
techniques
🔹 Logs success metrics via Telegram bots and CSV tracking
SentinelOne
@SentinelOne
Read the research from @LabsSentinel @spiderspiders_ and Jim Walter: s1.ai/akirabot
-
SentinelOne
@SentinelOne
📢 📆 Just a Sec is almost here. In the first-ever episode of our new livestream series, we discuss the hidden forces shaping our digital world. Think real-world incidents, the most elusive adversaries, and emerging hacking techniques straight from the front lines. No fluff, just critical insights to keep you ahead. Register now or catch it live—mark your calendar. 🗓️
SentinelOne
@SentinelOne
🔥⚔️ Presenting our Just a Sec livestream. In the first-ever episode, @DakotaInDc, Drea London, @juanandres_gs, and @stonepwn3000 discuss the hidden forces shaping our digital world. Think real-world incidents, the most elusive adversaries, and emerging hacking techniques straight from the front lines. No fluff, just critical insights to keep you ahead.
🎟️ Register now on YouTube or catch it live on X on April 10 at 2 p.m. PT. Mark your calendar: www.youtube.com/live/nY9biwaRk5Q -
SentinelOne
@SentinelOne
Cybersecurity, the work is mysterious and important. #severance
SentinelOne
@SentinelOne
Your Outie...
SentinelOne
@SentinelOne
Please enjoy these facts equally.
SentinelOne
@SentinelOne
🖥️ 🧠🍍 Would severance make enterprise security easier? Share your answer in the comments.
-
SentinelOne
@SentinelOne
🚨 Our Weekly Cybersecurity Roundup 🚨
🔎 To learn more, read the full blog post: s1.ai/GBU7-Wk14Post not available here, view on X
SentinelOne
@SentinelOne
👎 A critical vulnerability in several Ivanti products is being actively exploited in the wild, with China-linked threat actors using it to expand their access and establish long-term persistence.
SentinelOne
@SentinelOne
😰 At least three cyberattacks using the new Wrecksteel spying malware have hit Ukraine’s government and critical infrastructure since March.
-
SentinelOne
@SentinelOne
🎯 SMBs are in the crosshairs of cybercriminals—58% of Chubb’s 2023 cyber claims hit firms under $150M. We have teamed up with Chubb to arm SentinelOne users with fast, affordable cyber insurance. Singularity’s got you covered.
Learn more: s1.ai/ChubbSMBs -
SentinelOne
@SentinelOne
🔥⚔️ Presenting our Just a Sec livestream. In the first-ever episode, @DakotaInDc, Drea London, @juanandres_gs, and @stonepwn3000 discuss the hidden forces shaping our digital world. Think real-world incidents, the most elusive adversaries, and emerging hacking techniques straight from the front lines. No fluff, just critical insights to keep you ahead.
🎟️ Register now on YouTube or catch it live on X on April 10 at 2 p.m. PT. Mark your calendar: www.youtube.com/live/nY9biwaRk5Q -
SentinelOne
@SentinelOne
⏰ 🧊 You don’t have to optimize your morning routine to optimize your SOC. Make your life easier with Purple AI—get the sleep you need.
Learn more: s1.ai/Purple-AI -
SentinelOne
@SentinelOne
⛅ Strengthen Your AWS Security Posture: Explore these six critical yet often missed risks—like Service Control Policies and immutable infrastructure—and learn how to address them. From multi-account strategies to serverless security, this blog post offers actionable steps for cloud engineers and AWS architects to enhance their organization’s security posture.
Read it now: s1.ai/Ovrl6-AWS -
SentinelOne
@SentinelOne
🇨🇳⛳ In China, it’s more than just a game. The country’s CTF (Capture-the-Flag) ecosystem serves as recruiting grounds for state-sponsored hacking, with hundreds of events and thousands of participants.
This LABScon Replay video featuring @DakotaInDC and @eubenincasa dives into the major leagues, shedding light on key events and state-controlled CTFs to equip defenders with actionable CTI insights to track and disrupt adversary talent pipelines. Watch the full video: s1.ai/LC24-CB -
SentinelOne
@SentinelOne
🚨 Our Weekly Cybersecurity Roundup 🚨
Post not available here, view on X
SentinelOne
@SentinelOne
😰 The Ugly: Threat actor EncryptHub exploited a Windows zero-day to deliver a wide range of malware families, including backdoors and infostealers.
SentinelOne
@SentinelOne
🔎 To learn more, read the full blog post: s1.ai/GBU7-Wk13
-
SentinelOne
@SentinelOne
Building AI/ML on Kubernetes? Beware the risks GPUs can bring! Our research reveals how attackers can target device plugins to compromise your environment and access sensitive data.
📄 Protect your AI/ML workloads. Learn how to safely harness the power AI without compromising security: www.sentinelone.com/blog/gpu-device-plugins-unveiling-ris… -
SentinelOne
@SentinelOne
🗳️ Is detection as code a radical shift or just hype? Let us know your thoughts by taking our poll:
-
SentinelOne
@SentinelOne
😮💨 We’re the hottest date in town at RSAC, 2025 😏
Add a meeting with the SentinelOne executives and leadership to your RSAC itinerary. Request a meeting with:
✅ Tomer Weingarten
✅ Chris Krebs
✅ Eran Ashkenazi
✅ Ric Smith
✅ Michael Cremen
✅ Joni Tsumas
✅ And more ⬅️
Request your meeting: s1.ai/RSAC-25
From your boardroom, to your cloud environment, to your SOC and protecting all your users on all your endpoints, we’ve got you covered. Discuss:
🟣 Strategic business alignment, risk management, and threat modelling
🟣 The industry’s most advanced threat protection for Endpoint, Cloud and Identity
🟣 The revolutionization of the legacy SIEM market with generative and agentic AI
🟣 The acceleration of SecOps along the Autonomous SOC model with Hyperautomation -
SentinelOne
@SentinelOne
📺 Discover how Kryptina RaaS evolved from an unsellable giveaway to a Linux-focused ransomware platform targeting enterprises. In this LABScon Replay, @LabsSentinel's Jim Walter dives into a May 2024 Mallox leak, revealing threat actors’ adaptations and why Kryptina’s rise matters as a bellwether of the future ransomware ecosystem.
👉 Watch the full video: s1.ai/LBScn-Kry -
SentinelOne
@SentinelOne
🍎🚨🕵️♂️ The notoriously elusive macOS malware, ReaderUpdate, is back — stealthier than ever. @philofishal and @syrion89 uncover how ReaderUpdate Reforged blends Go, Crystal, Nim, and Rust into a potent mix.
📄 This new research from SentinelOne exposes how these new variants are spreading and how you can protect your organization. Stay informed. Stay secure. Dive into the research: s1.ai/readup -
SentinelOne
@SentinelOne
🗳️Agentic AI is here—it will shape cybersecurity by improving or enhancing…
-
SentinelOne
@SentinelOne
🏀 Drop a Vote for Brian Lanigan, Get the Assist: Help Brian get to the next round —let’s show ‘em what this community’s made of: s1.ai/CRN-Brian
CRN
@CRN
#crnchannelmadness Round 2 update 👀
In one of the most anticipated matchups, @Broadcom’s Tara Fine is out to an early lead against @nutanix’s @goffipro in the Innovation region.
Last year’s Channel Madness Champion, Tom Evans, who’s competing for @Cloudflare this year, is holding off @SchneiderElec’s Gordon Lord in the Evolution region.
Jennifer Follett details another key matchup to watch, former Channel Madness Champion @Veeam’s Kevin Rooney vs. tournament rookie @SentinelOne’s Brian Lanigan in the Transformation region, along with the full results for this round so far: okt.to/S70VeY.
@NutanixPartners @SchneiderNA
#crnchannelchiefs -
SentinelOne
@SentinelOne
🚨 Our Weekly Cybersecurity Roundup 🚨
👍 The Good: CISA has flagged three flaws in IoT, NAKIVO's Backup and Replication, and SAP. These types of vulnerabilities are frequent attack paths for hackers.
👎 The Bad: RansomHub RaaS’s new Betruger “multi-function” backdoor is being used in sneaky ransomware attacks via fake mail apps.
😰 The GitHub Action compromise lets threat actors hijack CI/CD via tj-actions/changed-files, exposing software secrets and projects to covert theft.
🔎 To learn more, read the full blog post: s1.ai/GBU7-Wk12 -
SentinelOne
@SentinelOne
🐴 How eBPF runtime Cloud Security stops attacks like tj-actions (CVE-2025-3066), a trojan horse hidden in a trusted software component, integrated into over 23,000 software development projects ⬅️
In a new blog post, we break down the GitHub Action supply chain attack, tj-actions/changed-files, with an in-depth analysis that dives into;
☠️ Poisoned Embedded Workflows
👀 Obfuscated Infiltration
🤝 Remote Rendeavous
🔍 Memory Heist
🤖 AI-powered #ebpf runtime Cloud Security that stops attacks
Singularity Cloud Security provides a multi-layered approach that combines world class eBPF runtime protection with proactive development and configuration practices and effective incident response. This is essential to building resilient CI/CD pipelines.
🗞️To learn more, read the full blog post by Yehonatnan Bitton and Shaul Ben Hai - s1.ai/tjactions -
SentinelOne
@SentinelOne
⛅🛡️Want to elevate your AWS security posture? In our newest guest blog post, Aidan Steele shares often-overlooked strategies you might not have considered. Here's what you'll learn:
✅ Why multiple AWS accounts are a must for safety and cost control
✅ How AWS Organizations simplifies multi-account security
✅ The power of delegating admin tasks to a dedicated security account
✅ Tips to centralize CloudTrail for better auditing
✅ Why IAM roles beat IAM users every time
Essential reading for AWS users at any level. Check it out: s1.ai/AWSSec-Bl -
SentinelOne
@SentinelOne
⚛️ With quantum and AI technologies, what’s next for cybersecurity?
-
SentinelOne
@SentinelOne
🔊 RSAC 2025, we are comin’ in hot! 🔥💜 Sign up below to get access to our exclusive events.
Here’s some of what’s in store:
🎙️Watch a live podcast recording of @riskydotbiz's Wide World of Cyber with @C_C_Krebs, Alex Stamos, and Patrick Gray. Monday, April 28th at 4pm
👔Hear from our CEO, Tomer Weingarten during his mainstage keynote, a fireside chat at the Piper Sandler CEO Summit, and at NightDragon Panel
🤖 Participate in our Mortal vs. Machine competition at Booth N-5863—and get all your SentinelOne questions answered in a hands-on demo of the world's leading AI-powered cybersecurity platform
🍕Network at our exclusive executive lounge, BarOne, at Joyride Pizza above Moscone North
🔮Witness the future of cybersecurity at our S Ventures Pitch for Charity, as five groundbreaking startups pitch their innovations directly to the industry's top CSOs
🎉Get on the guest list for THE after party of RSAC, Tuesday, April 29th at 8 p.m. at 715 Harrison. More announcements to come.
👉 Sign up for all the action here: s1.ai/RSAC-25 -
SentinelOne
@SentinelOne
👺🇷🇺 Hacktivisim meets cybercrime in Dragon RaaS, representative of an ongoing trend of hacktivist-style threat actors blending small-scale cyber attacks with aggressive branding.
In a new blog post, we track Dragon’s evolution as an offshoot of the pro-Russian “Five Families” crimeware syndicate and and reveal:
✔️A lightweight PHP webshell encryptor
✔️A rebranded StormCry payload (not the “bespoke” encryptor Dragon claims)
✔️Unique TTPs, vulnerability exploits, and IoCs
📄 Dive in to the new blog post by Jim Walter: s1.ai/draas -
SentinelOne
@SentinelOne
⚛️ Quantum computing may leap forward with recent breakthroughs including the newly announced Majorana 1 chip. How will both quantum and AI advancements impact cybersecurity?
-
SentinelOne
@SentinelOne
👔The Hidden Cyber Risks of Mergers and Acquisitions: While M&As can fuel strategic expansion, driving an estimated third of revenue growth, they also harbor unseen cyber risk. The Change Healthcare ransomware attack, for instance, struck less than 18 months after its acquisition by UnitedHealthcare, exposing sensitive data and disrupting care.
In this new Executive Brief, we outline PinnacleOne’s strategic framework to help leaders understand the types of cyber risks that stem from acquisitions.
Key points to secure your M&A journey:
✅Involve IT and security in the due diligence of an acquisition to tackle technical vulnerabilities.
✅Establish a framework for different IT integration to address structural weaknesses.
✅Extend security governance across the entire enterprise for unified protection.
To learn more, read the full blog post by Chase Small: s1.ai/P1-M-and-A -
SentinelOne
@SentinelOne
🎧 🤖 🇨🇳 Is DeepSeek a threat? SentinelOne’s Alex Stamos and @C_C_Krebs dive in on the @riskybusiness podcast with Patrick Gray. Spoiler: For now, DeepSeek’s LLM doesn’t talk to the internet, it cannot execute code, and there is no Chinese spy inside of it. Future agentic frameworks, though—that’s where things gets dicey.
To learn more, listen to the full episode: risky.biz/WWC7/Post not available here, view on X
SentinelOne
@SentinelOne
@C_C_Krebs on @RiskyBusiness Podcast: AI is the latest battleground in the American and European struggle between letting technology blossom and regulating it before it impacts society, “but also one that is probably going to come to a head with the U.S. government. And I think that’s in terms of policing speech, tech censorship, and just AI in general.”
SentinelOne
@SentinelOne
To learn more, listen to the full [tag] @RiskyBusiness Podcast episode: risky.biz/WWC7/
-
SentinelOne
@SentinelOne
🚨 Our Weekly Cybersecurity Roundup 🚨
Post not available here, view on X
SentinelOne
@SentinelOne
👎 The Bad: China-nexus hackers have been targeting Juniper Networks to deploy custom backdoors with the ultimate goal of breaching defense, tech, and telcos globally.
SentinelOne
@SentinelOne
😰 Hordes of threat actors are exploiting a critical flaw in PHP, which could allow remote code execution on Windows servers using Apache and PHP-CGI.
SentinelOne
@SentinelOne
🔎 To learn more, read the full blog post: s1.ai/GBU7-Wk-11
-
SentinelOne
@SentinelOne
⚖️ CyberLaw Forum 2025: Top legal experts, cybersecurity professionals, and insurance leaders like @Debevoise's Luke Dembosky and @US_CYBERCOM's executive director @adamski_morgan unpacked asymmetric cyber threats, AI attack tools, and supply chain risks. A key takeaway from the event: Transparency and AI-driven defenses.
📄 Read the blog post to dive more into the highlights—and watch the full sessions: s1.ai/CybrLaw25 -
SentinelOne
@SentinelOne
Innovation. Speed. Execution. Elegance. Excellence. @SentinelOne and the @AstonMartinF1 Team in 2025 🤝💚💜
This weekend’s @Formula1 season opener returns, for the first time since 2019, to the iconic Albert Park in Melbourne, Australia 🇦🇺. 2025’s season has Purple AI in the cockpit, automatically anticipating attacks and keeping the team focused on racing.
‘’Purple (AI), and SentinelOne as a whole, allows us to ingest data from a lot of different sources, whether that's at HQ or Trackside. Then within Purple (#ai) we can quite quickly augment (its findings) and ask questions of that data, to identify whether we have indicators that are suspicious or not.” Mark Carter, Chief Architect and Cybersecurity Officer, Aston Martin Aramco
#f1 #formula1 #racingThis media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
🗳️ The soft skill that matters most in cybersecurity hiring is…
-
SentinelOne
@SentinelOne
📈 Q4 FY25: SentinelOne delivered. Forging the future of AI security, we closed FY25 with unmatched growth, expanding margins and clear line-of-sight to hitting the $1 billion in ARR and revenue milestones in FY26.
As a leader and pioneer in AI-powered cybersecurity for more than a decade, we’re redefining what is possible with autonomous, agentic AI workflows and solidifying Singularity as cybersecurity’s AI platform of the future.
Top highlights:
- Total revenue increased 29% YoY
- Annualized recurring revenue (ARR) increased 27% YoY
- First quarter of positive non-GAAP operating margin
- 79% gross margin (non-GAAP)
- 5% net income margin (non-GAAP)
- 25% growth of customers with ARR over $100K (YoY)
- 50% bookings from non-endpoint solutions in FY25
📺 Watch our Q4 FY25 earnings call to learn more: s1.ai/Q4-25-Ern
🗞️ Read the press release: s1.ai/Q4-25-PR -
SentinelOne
@SentinelOne
🌟 This Women’s History Month, we’re proud to spotlight a few of the incredible women of SentinelOne! A huge thanks to Keiko Nevers, Tejaswini Sandapolla, and Leila Ettaoumi for sharing your journeys and inspiring future cybersecurity leaders.
SentinelOne
@SentinelOne
💜Want to be part of a dynamic, award-winning team? At SentinelOne, you’ll drive innovation, build your future and work with purpose. Explore our opportunities: s1.ai/CareersPage
-
SentinelOne reposted
Tom Hegel
@TomHegel
Incredibly excited to drop some new research alongside the @ValidinLLC team at this years @pivot_con
-
SentinelOne
@SentinelOne
🚨 Our Weekly Cybersecurity Roundup 🚨
Post not available here, view on X
SentinelOne
@SentinelOne
😰 A newly uncovered version of the ClickFix campaign now deploys Havoc C2 framework for remote access, executing scripts from the attacker’s SharePoint server.
SentinelOne
@SentinelOne
🔎 To learn more, read the full blog post: s1.ai/GBU7-Wk-10
-
SentinelOne
@SentinelOne
👩💻 We’re proud to celebrate the women driving innovation in cybersecurity on #internationalwomensday and every day. From tech pioneers to advocates, the Sentinels in the below blog post all truly #accelerateaction.
📄 Read their stories and join us in building a secure future: -
SentinelOne
@SentinelOne
🗳️ Children should be taught cybersecurity...
-
SentinelOne
@SentinelOne
🇨🇳 With the House Select Committee hearing on China’s Volt Typhoon happening today, scroll through our expert guide on this persistent threat actor. Researched by SentinelOne’s @DakotaInDC, this ExecBrief offers details about this nation-state threat actor, at-risk sectors, and preparation strategies for business and security leaders.
To learn more, read the original blog post: s1.ai/P1-VTBrief
And listen to this Lawfare Daily podcast episode: s1.ai/LwFare-VT
SentinelOne
@SentinelOne
🚨 X Thread: Defending Against China's Volt Typhoon 🚨
🇨🇳What is Volt Typhoon? VT is a Chinese cyber threat group targeting U.S. critical infrastructure since at least 2021. Their aim? To disrupt operations, potentially deterring U.S. military actions in conflicts. -
SentinelOne
@SentinelOne
🇨🇳 🌽 Who really owns America's farmland? In this LABScon Replay video, @kristindelrosso and Madeleine Devost dive into the secretive world of foreign investment in U.S. agricultural land, up 50% since 2017. Learn about what’s being done to safeguard national security and the case for more transparency.
📺 Watch the full video: s1.ai/LC24-DR -
SentinelOne
@SentinelOne
🚀 🟣 Say hello to the future of cybersecurity. From the industry’s most advanced threat protection for endpoint, cloud and identity, to revolutionizing the legacy SIEM market with our generative and agentic AI, to our cutting-edge CNAPP, there’s a lot to look forward to from SentinelOne in 2025.
📺 Watch the video below to see highlights from our Sales Kickoff last week—and learn how we’re unlocking potential and delivering unmatched protection every step of the way. Join us as we shape the future of security together.This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
🇨🇳 What’s the shadiest finding on China censorship, revealed in our recent @LabsSentinel report?
SentinelOne
@SentinelOne
📄 Report details about the complex ecosystem between the Chinese Communist Party (CCP) and China’s private cybersecurity sector: s1.ai/topsec
-
SentinelOne
@SentinelOne
🔌🇨🇳 🇷🇺 "Social upheaval when the lights are off for two or three days, when the water doesn't work. That's the aspect that we under appreciate, I think, in the national security community here, whereas our adversaries in Russia and China, both, it is absolutely part of their doctrine, where you have a technical attack that results in a social effect, a psychosocial effect, that creates social impact," SentinelOne’s @C_C_Krebs tells @axios's @samsabin923 in a conversation prompted by the "Zero Day" Netflix series.
"If Xi Jinping decides to go after Taiwan, he's going to hit our military, but he's also going to hit us domestically, so that we are pressuring our political leadership to say, don't worry about Taiwan, I need the lights back on."
📺 WATCH the full fireside chat: s1.ai/Axios0Day
👉 Follow us for more content like this.
Credit: Axios. Used with permission.This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
🧑🚀 🚀 💜 A huge thank you to Canadian astronaut @Cmdr_Hadfield for joining us at SentinelOne’s Sales Kickoff! Your inspiring insights on leadership, resilience, and pushing boundaries perfectly fueled our theme, "Go Beyond." From space to cybersecurity, you showed us how to aim higher and achieve the extraordinary.
-
SentinelOne
@SentinelOne
🚨 Our Weekly Cybersecurity Roundup 🚨
Post not available here, view on X
SentinelOne
@SentinelOne
😰 The Ugly (research by @LabsSentinel and @TomHegel): Belarus-linked Ghostwriter is sneaking malware into Excel files, targeting Ukraine and Belarusian opposition.
SentinelOne
@SentinelOne
🔎 To learn more, read the full blog post: s1.ai/GBU7-Wk9
-
SentinelOne
@SentinelOne
📺 WATCH: Could the cyber attack depicted in @netflix's “Zero Day” happen in real life? SentinelOne's @C_C_Krebs speaks with @Axios's @samsabin923 in a fireside chat on Wednesday, flagging real threats like China’s military hackers (aka "Volt Typhoon") targeting U.S. infrastructure—and the social unrest that both China and Russia hope follows.
👉 Listen to the full conversation on Axios’s website: s1.ai/Axios0Day
👉 Follow us for more coverage of the event including Krebs's insiders take on our nation's cyber defenses.
Video Credit: Axios. Used with permission. -
SentinelOne
@SentinelOne
🇨🇳 👁️ “New details about how China relies on private sector partners to censor the internet spilled into public view via a data leak analyzed by cybersecurity firm SentinelOne.” In a @LabsSentinel report covered by the @WashTimes, @spiderspiders_, @milenkowski, and @DakotaInDC reveal how Chinese cybersecurity firms like TopSec fuel Beijing’s internet control.
🗞️ To learn more, read the full article: s1.ai/TpScWshTm
From web monitoring for the Ministry of Public Security to tracking dissent, this leak and our analysis helps uncover China’s public-private ties shaping cyber warfare. -
SentinelOne
@SentinelOne
🇧🇾 🇺🇦 “Opposition activists in Belarus as well as Ukrainian military and government organizations are the target of a new campaign that employs malware-laced Microsoft Excel documents as lures to deliver a new variant of PicassoLoader.” In a @LabsSentinel report covered by @TheHackersNews, @TomHegel dives deep into this active cyberespionage threat.
🗞️ To learn more, read the full article: s1.ai/Ghost-THN -
SentinelOne
@SentinelOne
📢 Today's the day! @Axios and @samsabin923 will be hosting a timely discussion on the state of US cybersecurity prompted by the "Zero Day" Netflix series. On the panel will be SentinelOne's @C_C_Krebs who will share an insider’s take on our cyber defenses.
🎟️ In the D.C. area and interested in attending? RSVP here: axioszerodayandthecaseforenhan.splashthat.com
SentinelOne
@SentinelOne
📆 Excited to see @Axios spotlight cybersecurity with the "Zero Day" Netflix series. @C_C_Krebs’s participation in this conversation adds critical insight into the current cyber threat and how government and industry team up to protect the nation.
🎟️ Interested in attending in-person? RSVP here: axioszerodayandthecaseforenhan.splashthat.com
🐦Follow @Axios and @SentinelOne on Wednesday for live coverage.
#axiosevents
Axios
@axios
🎬 Weds. 2.26 in DC
Join Axios for an evening of clips and conversations around the new Netflix series, "Zero Day" starring Robert De Niro which centers on the consequences of a national cyberattack.
We'll chat w the show's creators, and our cybersecurity reporter @samsabin923 will talk with @SentinelOne's @C_C_Krebs, @RepHoulahan on why robust cyber guardrails matter.
RSVP here: axioszerodayandthecaseforenhan.splashthat.com
#axiosevents
Presented by @netflix -
SentinelOne
@SentinelOne
📆 Excited to see @Axios spotlight cybersecurity with the "Zero Day" Netflix series. @C_C_Krebs’s participation in this conversation adds critical insight into the current cyber threat and how government and industry team up to protect the nation.
🎟️ Interested in attending in-person? RSVP here: axioszerodayandthecaseforenhan.splashthat.com
🐦Follow @Axios and @SentinelOne on Wednesday for live coverage.
#axiosevents
Axios
@axios
🎬 Weds. 2.26 in DC
Join Axios for an evening of clips and conversations around the new Netflix series, "Zero Day" starring Robert De Niro which centers on the consequences of a national cyberattack.
We'll chat w the show's creators, and our cybersecurity reporter @samsabin923 will talk with @SentinelOne's @C_C_Krebs, @RepHoulahan on why robust cyber guardrails matter.
RSVP here: axioszerodayandthecaseforenhan.splashthat.com
#axiosevents
Presented by @netflix -
SentinelOne
@SentinelOne
🇧🇾 🇺🇦 🚨 Breaking: @LabsSentinel’s @TomHegel reveals a Ghostwriter campaign targeting Belarusian opposition and Ukrainian military and government organizations. Prep began Jul-Aug 2024; it’s active now. An escalation in cyberespionage against activists and Ukraine.
📄 Details:Post not available here, view on X
SentinelOne
@SentinelOne
Ghostwriter blends hacking and info ops, using Macropack-obfuscated VBA macros and .NET downloaders. This campaign aligns with Belarus-Russia interests, hitting Ukrainian targets despite Belarus’ non-military stance in the war.
SentinelOne
@SentinelOne
Ghostwriter remains a persistent threat, serving Belarusian espionage goals. Read @TomHegel’s full SentinelLabs report for details on this active operation: s1.ai/ghost-xl
-
SentinelOne
@SentinelOne
🗞️Our weekly cybersecurity news roundup 👉The Good: Chrome and Mozilla release patches for several high-severity memory safety vulnerabilities. The Bad: Latest version of ‘Darcula’ PhaaS now auto-generates phishing kits that can impersonate any brand. The Ugly: Russia-linked actors leverage Cybercrime-as-a-Service (CaaS) tactics to exploit Signal’s ‘Linked Devices’ feature, hijacking accounts of interest.
To learn more, read the full blog post: s1.ai/GBU7-Wk8
SentinelOne
@SentinelOne
To learn more, read the full blog post: s1.ai/GBU7-Wk8
-
SentinelOne
@SentinelOne
🇨🇳When public information censorship meets the private enterprise.... @LabsSentinel takes a dive into the complex ecosystem between the Chinese Communist Party (CCP) and China’s private cybersecurity sector.
A data leak from Chinese cybersecurity firm, Topsec, indicates that private cybersecurity firms are likely being used for content moderation in an effort to monitor and control public opinion. 🤔
Read more in the blog from @spiderspiders_ @milenkowski @DakotaInDC - s1.ai/topsec -
SentinelOne
@SentinelOne
🗞️Our weekly cybersecurity news roundup 👉The Good: An international operation has led to the arrest of cybercriminals linked to the Phobos and 8Base ransomware groups. The Bad: New ‘Sarcoma’ ransomware has claimed responsibility for attacks on Unimicron, a large printed circuit board (PCB) firm in Taiwan. The Ugly: A China-linked threat actor deployed espionage tools, underscoring the blurry lines between state-backed espionage and financially-fueled attacks.
SentinelOne
@SentinelOne
To learn more, read the full blog post: s1.ai/GBU7-Wk7
-
SentinelOne
@SentinelOne
💗 This Valentine's Day, send these five love memes to your secure connection: No patches necessary.
👇 Drop your campiest cybersecurity love memes in the comments below!Post not available here, view on X
SentinelOne
@SentinelOne
SentinelOne
@SentinelOne
-
SentinelOne
@SentinelOne
💔 Swipe left on these types of cyber scams this Valentine’s Day 🚨 Roses are red, violets are blue, cybercriminals are out to scam you! From fake flowers to romance baiting, don't let your heart (or wallet) get broken. Watch out for these social engineering scams:
💔 Romance Scams: Beware of love that asks for money. If they're too good to be true, they probably are!
💔 Gift Card Traps: That "exclusive" deal might just be a scam. Verify before you click or share.
💔 Malicious Downloads: Cute Valentine's wallpapers could be malware in disguise. Stick to trusted sources.
Be skeptical online, verify sources, and never share personal info with digital strangers. Stay safe and enjoy the love, not the loss. 🔒
To learn more, read the full blog post: s1.ai/VDay-Scms -
SentinelOne
@SentinelOne
📱🇬🇧 🇨🇳 In the @WSJ: SentinelOne’s Alex Stamos and @JohnsHopkins's @matthew_d_green discuss a critical issue that should concern everyone in the tech industry and beyond: the UK government's mandate attempting to force Apple to compromise the encryption of its devices.
SentinelOne
@SentinelOne
"[O]nce one country demands an exception to encryption, the decision about who can access data becomes political," write Stamos and @matthew_d_green. "If the British crack the encryption door an inch, the Chinese will kick it open.”
🗞️ To learn more, read the full article: -
SentinelOne
@SentinelOne
🗼 🇨🇳 "The Chinese are preparing for war. Are we?" SentinelOne’s @C_C_Krebs weighs in on how China's access to the cranes at key U.S. ports could impact homeland security and even the U.S. military. "The hairs on the back of my neck standing up when I talk about this," Krebs tells @CBSNews. "[China] is the number one cyber risk facing the United States right now."
"They'd hit a port, particularly on the West Coast, because that's how we move material, that's how we move equipment."
📺 To learn more, watch the full video clip: s1.ai/CBS-Cranes -
SentinelOne
@SentinelOne
💜 We came, we saw, WE Dominated.
FY25 was one for the history books and we are redefining what's possible with A.I. in Cybersecurity, crushing adversaries in the process 💪
Thank you to our Customers, Partners, Investors and Sentinels.
Check out our recap video and share any of your favourite SentinelOne moments in the comments below.This media couldn't be displayed. See it on the original post. -
SentinelOne
@SentinelOne
🚘 🇨🇳 Is China really a security threat to connected vehicles? SentinelOne’s strategic advisory consultant focused on China, @DakotaInDC, weighs in.
To learn more, read the full article from in @CSOonline: s1.ai/CSOCnnCar -
SentinelOne
@SentinelOne
🗞️Our weekly cybersecurity news roundup 👉The Good: A hacker accused of breaching NATO and U.S. Army systems was arrested by Spanish authorities while a Canadian man was charged for a $65 million crypto hacking scheme. The Bad: A zero-click, WhatsApp campaign targeted 90 journalists and activists using spyware. The Ugly: Slipping past Apple’s XProtect, a new variant of DPRK-linked FERRET malware targets hiring organizations and developers on GitHub.
To learn more, read the full blog post: s1.ai/GBU7-Wk6 -
SentinelOne
@SentinelOne
⏳ The countdown is on! Just over two weeks to go until @IlliniMBB takes on @DukeMBB at @TheGarden on Saturday, February 22nd, 2025.
Who’s ready to watch the action live? 🎟️ -
SentinelOne
@SentinelOne
📰 In Dark Reading: “Researchers at @LabsSentinel uncovered the campaign … The goal of attackers is ultimately to use the potential reach of the high-impact accounts — which also include technology and cryptocurrency organizations as well as owners of accounts with valuable, short usernames — to target people with crypto scams for financial gain, the researchers said.”
“Indeed, the campaign is also similar to one uncovered last year that compromised the Linux Tech Tips X account along with other high-profile users. The researchers discovered related infrastructure and similar phishing messages used in both campaigns, evidence that suggests the same threat actor is behind both, they said.”
🗞️ To learn more, read the full article by Elizabeth Montabalno: s1.ai/DR-XPhish
And the full research by SentinelLabs’s @TomHegel, Jim Walter, and @spiderspiders_: s1.ai/XCrypto -
SentinelOne
@SentinelOne
🇨🇳 "The real danger of DeepSeek isn’t just where it was made but how it was made," SentinelOne’s @C_C_Krebs tells @VentureBeat.
Krebs provides valuable insights:
👉 The Chinese technology industry does not distinguish between the private sector and national intelligence objectives
👉 Censorship and bias may be baked into the model’s development, throwing off objective results
👉 This 'political lobotomization' of Chinese AI models may support the development and global proliferation of U.S.-based open source AI models
To learn more, read the full article by @LouisColumbus: s1.ai/VB-DeepSk -
SentinelOne
@SentinelOne
How do you view DeepSeek AI?
-
SentinelOne
@SentinelOne
🤝 Stop privileged access misuse in its tracks 🛡️ We have teamed up with @CyberArk, a global leader in Identity Security, to provide customers with a new integration for use cases across our market leading Endpoint Protection and AI SIEM platform.
👉 Prevent attacks, such as ransomware, with privileged access controls
👉 Maintain user productivity whilst enforcing strong policy controls
👉 Accelerates threat identification, correlation, hunting and remediation with AI SIEM
👉 Faster time to protection and value with turnkey SaaS deployment and operations
Security is a team sport, and we’re committed to providing an open and flexible platform to defeat attacks.
📄 Learn more: s1.ai/CybrArkPR -
SentinelOne
@SentinelOne
🚨 Alert: New macOS Malware Variants, FlexibleFerret, Undetected by Apple’s XProtect 🚨
@LabsSentinel researchers @philofishal and @TomHegel have uncovered new variants, which slip past Apple's XProtect, of the DPRK-linked macOS malware, Ferret. Dive deeper into our findings to stay ahead of this sophisticated threat: s1.ai/Ferret
Key Insights:
👉 Detailed analysis of the malware's capabilities, part of the ongoing Ferret family campaign.
👉 Comprehensive list of indicators for threat hunters and defenders to identify and mitigate the threat.
👉 Threat actors are dynamically adapting, moving from signed to unsigned applications to evade detection.
👉 Both targeted attacks and broader 'scatter gun' approaches via social media and platforms like GitHub.
@LabsSentinel continues to track and publicize these activities to bolster community defenses. SentinelOne customers are protected from all known variants of the Ferret family. -
SentinelOne
@SentinelOne
🗞️ Our weekly cybersecurity news roundup 👉The Good: International authorities dismantled two major cybercrime forums and sanctioned attackers for targeting Estonian ministries. The Bad: Multiple Apple products have been affected by its first exploited zero-day of 2025. The Ugly: Nearly 60 state-sponsored threat actors are using Google’s Gemini AI assistant to accelerate their cyber operations.
To learn more, read the full blog post: s1.ai/GBU7-Wk5 -
SentinelOne
@SentinelOne
The threat actor who hacked @LinusTech's account is back with a wider campaign targeting U.S. political figures, journalists, cryptocurrency entities, major tech organizations and others for takeover.
SentinelOne
@SentinelOne
🚨 New from @LabsSentinel: High-Profile Phishing Campaign Detected 🚨Our threat researchers have uncovered an active phishing operation targeting a select group of high-profile accounts on X. This campaign aims to hijack these accounts, likely for fraudulent financial exploitation.
To learn more, read the research by @TomHegel, Jim Walter, and @spiderspiders_: s1.ai/XCrypto -
SentinelOne
@SentinelOne
🚨 New from @LabsSentinel: High-Profile Phishing Campaign Detected 🚨Our threat researchers have uncovered an active phishing operation targeting a select group of high-profile accounts on X. This campaign aims to hijack these accounts, likely for fraudulent financial exploitation.
To learn more, read the research by @TomHegel, Jim Walter, and @spiderspiders_: s1.ai/XCryptoPost not available here, view on X
SentinelOne
@SentinelOne
We link this activity to a successful campaign from last year, where attackers used compromised accounts to disseminate scam content. Note, while X/Twitter is the current focus, this threat actor's reach extends to other platforms, consistently pursuing financial gain.
SentinelOne
@SentinelOne
Protect Your X Account:
🛡️ Use a unique password for your X account.
🛡️ Enable two-factor authentication (2FA).
🛡️ Never share credentials with third-party services.
🛡️ Be wary of messages with links claiming account issues or security alerts.
🛡️ Always double-check URLs before clicking.
🛡️ Initiate any password resets through the official X website or app, not via unsolicited links.
Have you seen something similar? We want to know! Reach out to @LabsSentinel at ThreatTips@sentinelone.com on X @LabsSentinel or on BlueSky for collaboration or to report suspicious activities. -
SentinelOne reposted
J. A. Guerrero-Saade
@juanandres_gs
The actor that hacked @LinusTech's X account is back with a wider campaign targeting U.S. elected officials, journalists, an X employee, cryptocurrency orgs, and other for takeover (h/t @TomHegel @spiderspiders_ Jim Walter, @linusgsebastian)
www.sentinelone.com/labs/phishing-on-x-high-profile-accou… -
Post not available here, view on XPost not available here, view on X
SentinelOne
@SentinelOne
🏆After providing an autobiography on how she became the Mother of Decompilation, Dr. Cristina Cifuentes was presented by @labscon_io and @juanandres_gs with the 2024 Lifetime Achievement Award. As @k8em0 posted on X, "so much of our industry is possible because of [Cristina's] work." x.com/k8em0/status/1836808600880062752
#labscon24
Katie🌻Moussouris (she/her/she-ra/she-hulk) 🪷
@k8em0
Legendary pioneer Dr. @criscifuentes discussing her groundbreaking foundational work on decompilation — so much of our industry is possible because of her work.
Thank you, Dr. Cifuentes!
@labscon_io #legendsoflabscon -
SentinelOne
@SentinelOne
🚨 X Thread: Defending Against China's Volt Typhoon 🚨
🇨🇳What is Volt Typhoon? VT is a Chinese cyber threat group targeting U.S. critical infrastructure since at least 2021. Their aim? To disrupt operations, potentially deterring U.S. military actions in conflicts. -
Post not available here, view on XPost not available here, view on X
SentinelOne
@SentinelOne
🔟 @kyleehmke | Kyle Ehmke
A Threat Intelligence Researcher with @ThreatConnect, Kyle has a decade of experience as a cyber intelligence analyst. His most recent work with ThreatConnect shed light on Russian election activity and targeted efforts against Bellingcat, WADA, and others. His research largely focuses on influence operations to better understand foreign and domestic actors’ information operations infrastructure. -
SentinelOne
@SentinelOne
🔥New on #sentinellabs! We’ve just disclosed 10.0 CVSS vulnerabilities on Microsoft’s Azure Defender for IoT allowing unfettered access to your Microsoft-protected organization. By @kasifdekel & @ronenshh.
www.sentinelone.com/labs/pwning-microsoft-azure-defender-…
#azure #iot #xdr #vulnerabilities -
SentinelOne
@SentinelOne
🔥New on SentinelLabs! 25 CVEs and counting: Vulnerabilities in #aws & other major #cloud services. @kasifdekel's latest research reveals millions of cloud users are exposed to privilege escalations from bugs in shared driver software.
www.sentinelone.com/labs/usb-over-ethernet-multiple-privi…
#cybersecurity -
SentinelOne
@SentinelOne
🎮🔥SentinelLabs Discovery by @kasifdekel #vulnerability: HP #omen Gaming Hub ships on millions of gaming PCs but can allow privilege escalation to kernel mode without admin privileges! "#game on" needs to start with "#cybersecurity on"
www.sentinelone.com/labs/cve-2021-3437-hp-omen-gaming-hub…
#infosec #hp -
SentinelOne
@SentinelOne
📢 Important: SentinelLabs high severity vulnerability discovery - Hundreds of millions of Dell devices at risk over the past 12 years. Dell users: please patch now. Great work, @kasifdekel!
labs.sentinelone.com/cve-2021-21551-hundreds-of-millions-…
#cyber #infosec #vulnerability #cve #delltechworld #dell -
SentinelOne
@SentinelOne
🧰 A new tool released! #ghidra users can now enjoy the same (and more!) benefits available in IDA Pro from #virustotal's VTGrep plugin with this open-source plugin from #sentinellabs. By @kasifdekel
labs.sentinelone.com/introducing-sentinelones-ghidra-plug…
#infosec #ghidra #opensource @virustotal #vtgrep -
SentinelOne
@SentinelOne
🎙️ Why do robbers steal from banks? That’s where the money is! The weapon of today is cyber. Listen to @DarknetDiaries episode sponsored by SentinelOne
s1.ai/KNAVES-OUT
#cybersecurity #infosec #podcast #darknetdiaries