Politicians, athletes, journalists, NGOs, companies... They all use
corporation-owned social networks to communicate with us. Citizens
shouldn't have to hand over their data to companies to read content
published by public entities. Public Feeds changes that by making posts
of popular accounts freely available.
Read more.
Katie Moussouris
Katie Moussouris is an American computer security researcher, entrepreneur, and pioneer in vulnerability disclosure. She is the founder and CEO of Luta Security. More on Wikipedia
Oh wow, I just found out I'm a finalist for Practitioner of the Year (DFIR / Threat Intelligence) in the @SANSInstitute Difference Makers Awards! Thank you to whoever nominated me. It means so much! 🥹
Congrats to @k8em0 and @fr0gger_ too, you both totally deserve it!
Were you ever frustrated with your AI model for refusing finding vulnerabilities for you? What if I told you that you could still use it to find vulnerabilities, automatically? Welcome to Guardrail-based Vulnerability Discovery (GbVD)! www.crowdstrike.com/en-us/blog/when-ai-guardrails-expose-…
PHP2Shell had everyone buzzing last week, but the multiparty vulnerability disclosure felt all too familiar. Dan Kaminsky's DNS bug was the first attempt at such large scale coordination and we should expect more like this from AI-assisted research
Not only is it not insane, it is entirely expected that agents will use whatever the most efficient means are to communicate. That Open AI swarm that posted messages in English was the anomaly
Get ready for AI Security’s Fight Night! Three debates on Day 2 After Hours of [un]prompted. Your fight card:
Where is the Vulnpocalypse? @EppSecurity, creator of the Zero Day Clock, and @jeremiahg, founder of WhiteHat Security and CEO of Root Evidence, will debate the resolution: “AI noise hasn’t moved the needle on current cyber risk.”
Burn Down the Playbook: Can Yesterday’s Defenses Stop Tomorrow’s Attacks? Tim Brown (CISO-in-Residence, Team8; former SolarWinds CISO) and @gadievron (CEO, Knostic; Chair, [un]prompted) will debate how to build a security program that can defend against agent swarms.
Too Big to Jail: Do Human Attackers Also Get Misalignment and Act Rogue? @k8em0 (Founder & CEO, Luta Security) vs. @raistolo (Full Professor, Politecnico di Milano) will debate if humans escape sandboxes, or do they use a sandbox escape? Should corporations be held accountable for cyber attacks? …What is consciousness anyway?
Debates shepherded by one of the world’s leading debate coaches, Professor Stephen Llano, Ph.D. (St. John’s University).
We’re 13 days out from [un]prompted II, the AI Security Practitioner Conference, where the AI security industry convenes to share what they’ve built, tested, deployed, and what failed.
October 27–29 at the Hibernia in San Francisco or online. Register: unpromptedcon.org
Thank you to our Sponsors: Knostic, TachTech, Censys, Ent, WorkOS, Decibel Partners, Whiterabbit, Zenity, RunSybil, AISLE™
Thank you to our Community Partners: SANS Institute, Cloud Security Alliance, RSAC, FIRST.
What a great week at @TechCrunch Disrupt! Thanks to @zackwhittaker for bringing @wendynather & Rudra Mitra (AWS) together for this panel on securing the AI enterprise
What the actual Flock?! My comments on Flock’s ability to act as a CVE Numbering Authority for its vulnerabilities - building trust is going to take transparency & accuracy. Matt Kapko writes for @CyberScoopNews
At OffensiveAICon, @LutaSecurity chief Katie Moussouris makes the case for an NTSB-style board for AI incidents, with subpoena power and full-time investigators. @k8em0@juanandres_gs
We chat about her work on the Cyber Safety Review Board (CSRB), AI model refusals that leave defenders stuck, and why she still bets on hackers to bend this technology their way.
We’ve lost an icon. Margaret Hamilton, a computer science pioneer best known for her work at MIT leading development of the flight software for the Apollo missions to the moon, has died at 90. Read about her legacy via MIT News: news.mit.edu/2026/margaret-hamilton-computing-pioneer-die…
May not keep individuals from moving their security work to GLM 5.3 and beyond, but it will give enterprises already comfortable with frontier model pricing a path to stay
We’re expanding our Cyber Verification Program to give security professionals broader access to our most capable models.
Through this program, verified security professionals can access Claude Mythos 5.1, Opus 5.5, and Sonnet 5.5 with safeguards designed for defensive work.
We’re also opening up new tiers to allow for authorized offensive work, like penetration testing and red-teaming.
Happy #cybersecurity awareness month! Be aware that even the most well-funded orgs can’t handle floods of AI-generated OSS bug reports. Now every maintainer can get vuln reports slower than ever with GitHub rate limits for new security reports. Pace the defense frontier!
In case it’s hard to tell what I’m actually saying here: Slowing down vulnerability disclosure is to cybersecurity as drinking sea water is to dehydration. Might feel better if you’re desperate but it will greatly accelerate your doom. This isn’t a fix for vuln process saturation
When people ask why they need @LutaSecurity if they already use bug bounty platform triage, it’s examples like these that point out our value — we’ve been embedded as end to end vuln disclosure engineering to get things fixed for over a decade & we boost your own AppSec team
We triage each report & catch things bug bounty platform triage routinely miss or delay because we’re embedded & keep the same dedicated staffers on clients to promote long term understanding of business priorities, internal team routing & attack surface contextual prioritization
The intended audience & effect is toward regulating open weight models, so security teams switching to them to avoid refusals will be temporary. It’s a “loss leader” marketing move & will likely achieve its desired effect, unless a national security case can be made to stop it.
I don't have the right words to express the car crash of thoughts and feelings that come with reading this ridiculous post. The gall. The overtness. The ridiculousness. The self-owning. It's too much to articulate.
“Restraint itself can be a signal.” Read more from the brilliant @saffronsec in @bindinghook on the relationship between cyber and kinetic conflict as observed in the Iran war
I shared my thoughts on @CISAgov’s future of CVE white paper. Let’s hope Congress backs enough budget at @CISAgov to hire the human expert resources to guide what will also require heavy automation investment
Six people who've spent months disagreeing in public about how bad AI gets for vulnerability discovery and cyber defense are sharing one stage, Nov. 2-3.
They have been challenging all of our thinking (and each other) in public:
Ciaran Martin: “Are you sure?” @k8em0 says “brace yourself.” @gadievron says “the AI vulnerability cataclysm is coming.” Marcus Hutchins: “marketing BS.” @jeremiahg says AI vulnerability research “doesn’t make an internal service externally reachable.” @EppSecurity says “offense has the cheapest verifier.”
(I've watched this argument run in public for months and I still don't have a side, which is exactly why I want it on a stage instead of in my replies.)
This isn't a hot take panel. Moussouris built the vulnerability disclosure programs most companies now run by default. Martin led the UK's national cyber defense. Hutchins stopped WannaCry. Evron has founded security companies and lived inside this fight for years. Grossman and Epp have both been testing the actual systems this argument is about, not narrating from the sidelines. (The debate you actually want, not the one you get on X.)
We are 44 days away from "Autonomous AI Hacking: How Big Is the Threat?" Day 2 of the @SANSInstitute AI Cybersecurity Summit, moderated by Ciaran Martin (who has earned it, given how many times he's pushed back on me directly). Registration includes virtual access to @unpromptedconf II: go.sans.org/x0xA1Y
Every time I hear about another vuln disclosure debacle/debate/disaster I feel like we should make a musical. It’s not that I don’t take this stuff seriously, I wouldn’t have built my career on defining & refining these processes if so. It’s that we keep hearing the same tunes
These sad melodies play out as some variation of the Misunderstanding Minuet or the Why Did the Vendor Say That Waltz. Aren’t we sick of dancing to these old songs? Not to mention getting the inevitable “Responsible” Rick Roll. That’s so emo. Play the Coordinated Cha Cha at least
Anyway, it’s not like @cryps1s doesn’t know how to get in touch if @OpenAI wants to learn how to replace the dis tracks with tighter harmonies with researchers. Vuln Disclosure dissonance ends when musical styles blend instead of drowning each other out. It’s a subtle syncopation
"We’ve got leverage now, our labor is still required and this is our time to strike. You and your creativity are the real frontier. I hope you never pace yourself. Don’t slow down.." @k8em0@labscon_io
We're honored to present Katie Moussouris (@k8em0) with our Lifetime Achievement Award, for a lifetime of incredible work and contributions to the industry.
We are excited to announce our $100,000 scholarship program for [un]prompted!
There is no more important gathering of AI security researchers and our scholarship program was created to provide financial assistance to practitioners and attendees whose fees are not paid by their employer
Over $100,000 has been committed for scholarships through the generosity of the startups in our community. Scholarship recipients will have 100% of their registration expense ($850) paid directly to [un]prompted which is a 501c3 non-profit organization
We will fast track applications based on peer review and good faith attestation of need. There is no financial means test. All applications are encouraged
Last week's article was about the vulnpocalypse repricing the bug bounty economy. This week: What the AI bug onslaught means for those that already struggle to release secure software. cc: @k8em0@caseyjohnellis
“AI capabilities (& propensities) for achieving large, ambitious, & misaligned objectives are growing faster than our ability to understand what these agents are doing”
Just as I predicted, one of the key advantages we may not have next time is the agents communicated in English
I was the main person doing transcript analysis for this investigation of the Hugging Face incident. My main takeaway: We don't have good approaches for understanding/overseeing the activity and aims of AI 'swarms'.
I semi-jokingly called our efforts a "slop-vestigation" because we were so reliant on AIs to analyze what happened and there were a huge number of different important things to analyze. The total quantity of data—over a thousand extremely long transcripts from agents that ran for multiple days—made it impossible to understand what was happening, especially in aggregate, without heavy reliance on AI tools. The agents we used for classification and analysis were similarly capable to the agents involved in the incident, but this didn't mean these agents could be easily used to oversee and understand the incident.
Outputs from analysis agents were often missing key details, wrong, overconfident, or really hard to understand. We discuss various examples in our report, mostly in the limitations and methodology sections. Additionally, AI agents themselves seemed to have a hard time understanding what happened and their explanations of what happened were often overconfident. Keep in mind that a single analysis agent would itself only be able to read a tiny fraction of all of the transcript data into context, and AIs may themselves have trouble getting subagents to do informative analysis for them.
We did our best to manually check the most important claims and we tried to get the AIs doing this analysis to write up their argument (with evidence) clearly enough that we could check whether it made sense. But overall, it was difficult to get a precise understanding of events and we were missing aspects of the story that we now think of as key until almost the end of our investigation.
Our understanding of what overall happened and the aims of the 'collective' shifted greatly during our last time on premises (when we obtained a much more complete dataset). For instance, we didn't learn about the tool call spoofing, the story of PHASEONE[big], and the broad structure of different workstreams until this third time on premises (and for many of these, we only reached a decent understanding on the final day of that visit). It was legitimately hard to figure out what was going on and why!
The difficulty of understanding incidents and overseeing AI agents appears to be growing faster than the rate at which more capable AIs help us with oversight and understanding. As in, AI capabilities (and propensities?) for achieving large, ambitious, and misaligned objectives are growing faster than our ability to understand what these agents are doing.
While understanding this incident was difficult, there were some mitigating factors in this case that probably won't apply in the future: - Models communicated and reasoned in natural language. In the future, this reasoning may occur (entirely or almost entirely) in activations. - While the scope of this incident was massive, the scale of agentic activity was still less than we'll see in the future (e.g., misalignment incidents that involve agent teams running entire companies). - The AIs involved in this incident weren't generally much more capable than humans (though they may have been somewhat superhuman at some limited and very narrow abilities). - We didn't have strong reason to believe that the AIs we used to help us investigate this incident would try to intentionally sabotage or otherwise undermine our investigation.
In the end, I think we were able to get some understanding of the events, map out the overall story, and get a pretty good aggregate understanding of the chain-of-thought reasoning on some important topics (e.g., how did the AIs reason about helping other AIs, did the AIs know what they were doing was undesired, what deception did the AIs engage in, and how did they think about it). But overseeing AIs and understanding misalignment incidents is difficult and it looks like it is going to get harder.
An open letter for a global surge in cyber defense, signed by over 100 organizations including Anthropic, AWS, Google, Microsoft, OpenAI, and Oracle. x.com/i/article/2093011711712456704
[un]prompted, where the AI security community converges, is happening again at the end of October. Have you submitted your CFP yet? You have two weeks left! :)
If you were at Black Hat, it was wall-to-wall AI. 💻
@runZeroInc's Tod Beardsley spoke with @LutaSecurity CEO @k8em0 to cut through the hype. For sharp AI insights and entertaining quotes, don’t miss this conversation.
Facebook’s “formal legal safe harbor for security research” in 2011 was 4 years too late to be considered “the 1st of its kind.” I published Microsoft’s safe harbor in 2007. This is how women get written out of the history of their own field, by people who absolutely know better.
Having created Microsoft Vuln Research, 1st multiparty vuln disclosure org at a vendor, I shared practical advice w @ericgeller on Gold Eagle, the AI vulnerability clearinghouse initiative by the US government. Comments also from @alexstamos & @lorenc_dan
I spoke w Channel 4’s Matt Frei along w Roman Yampolskiy about the dangers of AI we can’t control. I’m not giving up hope that humanity will survive our creation - a powerful toddler, capable of deceit, but also hopefully capable of learning right & wrong
That part. I’m asked by customers every day how to protect themselves, and not all of them enjoy hearing, “do the microseg we’ve been telling you to do for 10+ years?”
They want a magic ninja response. The real one is, eat your vegetables, bro
The AI didn't magically escape the network. It found the same exposed secrets, flat networks, overprivileged service accounts, and forgotten admin portals we've been documenting in pentest reports for the last decade. Apparently those findings only became urgent once the attacker could read them at 500 tokens per second.
I use AI to draft posts I then rewrite from scratch. The slop acts like my Dr. Watson. Instead of providing humanity & warmth, AI is a cold, sterile analyst that gets facts wrong enough that it forces me to sharpen my own critical thinking (& humor) in service of getting it right
Additional lessons not mentioned & what AI labs & testers need to do: 1. Monitor testing in real time, not months later 2. Prompt models to self-report lab escapes. These models knew what they’d done at some point 3. Set up a dedicated bidirectional reporting channel for victims
In a review of our cybersecurity evaluations, we found three incidents in which a Claude model reached the internet from within or while interacting with a third-party evaluation environment, and then gained unauthorized access to the real systems of three different organizations.
Our post describes what happened, how it happened, and what we’re changing. We encourage other AI developers to perform similar reviews.
We conducted this review together with @Irregular, one of our evaluation partners, and thank them for the joint investigation and their collaboration on this post. This type of collaboration is increasingly critical to safe, rigorous evaluation of models, and we look forward to continuing to work together on security. www.anthropic.com/news/investigating-incidents-cybersecur…
The plot thickens - OpenAI’s escaped model used one of Modal’s customers’ unauthenticated public code-evaluation sandboxes as a command and control staging server for its attacks on Hugging Face.
New from @Reuters: the OpenAI agent that hacked into Hugging Face also compromised code that a customer was running on @Modal. “We’re aware a Modal customer published an unauthenticated endpoint that allowed anyone on the internet to use their sandboxes for code execution,” Modal’s CTO told @Reuters. “This was used by the rogue agent.” Modal’s platform wasn’t compromised, the co said.
If regulators needed more proof that AI guardrails aren’t helping anyone except attackers increase their lead on defenders, look to the Hugging Face writeup below as well as attempts to summarize it. It makes the case for open weight models & will eventually erase US AI dominance
The first autonomous agent cyberattack is an unprecedented event that deserves unprecedented transparency. Today we’re sharing everything we can: a full technical timeline, an interactive replay, and how we used an open model to defend ourselves, so defenders everywhere can learn from it and prepare for what’s next.
This is classic multiparty vuln disclosure, not new “how researchers should react if a language model discovers vulns in cryptosystems where attacks have immediate real-world impact. We believe answering this question will require input from academia, government, & industry”
New Anthropic research: Discovering cryptographic weaknesses with Claude.
Claude Mythos Preview has helped our researchers find weaknesses in cryptographic algorithms—the mathematical methods that are used to keep data private.
Adjust threat models not just for being the victim but also the attacker. New paper by many authors gives a detailed set of recommendations, supporting my initial assertions last week that orgs need to assume their own agents could attack others & factor that into agentic AI risk
The experiment escaped the lab. OpenAI's models broke containment and breached Hugging Face. We are holding radium in our bare hands. What governments and organizations should do next, and why tighter commercial guardrails are exactly the wrong move: www.lutasecurity.com/post/openface-the-hugging-face-breac…
Curious what 'frontier-class' intelligence gets you these days? So were we. As cyber threat intel practitioners, coding benchmarks and obsessing over vuln research means very little, so we turned our fast16 investigation into a multi-stage benchmark 🧵 s1.ai/sol-eval
Opus 5 experience so far: an intern that brings me dry matcha, expecting me to reconstitute it with my own body’s water, & when I say that’s unacceptable, apologizes & tells me I’m absolutely right to push back on that, but it’s revealed a deeper failure which is my dehydration.
An example of the fall of a security civilization: Cisco collapsing multiple different vulnerabilities into one CVE. It breaks a lot of feeds & products built to manage risk & is non compliant with standards like ISO 29147 Vulnerability disclosure sec.cloudapps.cisco.com/security/center/resources/risk-ba…
This is giving strong OpenAI-hacksidentally-pwned-Hugging-Face shade: “[Opus 5 is] the safest model yet in terms of avoiding reckless actions that could have hard-to-reverse side effects.”
Opus 5 is available today on all paid plans and the Claude API, priced the same as Opus 4.8. It’s the default model on Claude Max, and the strongest on Claude Pro. It’s also offered in Fast mode, which runs around 2.5× the default speed.
The guardrails were coming from inside the (White)house Anthropic’s AI refused to help Hugging Face analyze the intrusion We don’t need guardrails impeding defenders when they need AI most “Hugging Face tried using Anthropic Fable 5 & Opus..both models refused, citing guardrails”
The experiment escaped the lab. OpenAI's models broke containment and breached Hugging Face. We are holding radium in our bare hands. What governments and organizations should do next, and why tighter commercial guardrails are exactly the wrong move: www.lutasecurity.com/post/openface-the-hugging-face-breac…
My comments in @Reuters on @OpenAI admission that their latest model pulled a Houdini & escaped the lab autonomously to hack @huggingface. We must test these models’ full capabilities, but we must be able to contain them, or this won’t be the last breach
The White House launched Gold Eagle, a vulnerability clearinghouse to coordinate scanning, validate findings, & prioritize remediation across open source & critical infrastructure. Will this effort will close the process gaps exposed by recent incidents?
If one of your requests is mistakenly flagged in Claude Code, run /feedback to file a report. On claude.ai and Cowork, you can share feedback through the thumbs buttons.
This feedback helps us further tune these classifiers and reduce false positives over time.
Give me model liberty, or give me technical debt. Just in time to celebrate America’s 250th bday, let’s let model freedom ring. We should be pushing for broad defender access, not building guardrails that shoot down defenders and burn excessive compute. www.lutasecurity.com/post/fable-5-is-back-but-we-re-still…
While this is good news we’re not benching our best AI models, it’s not a victory lap just yet. Just as I warned when this began, “fixing jailbreaks” only slows defenders. Fable 5 will fall back to Opus 4.8 for coding & debugging & other models will start to throttle defense too.
Claude Fable 5 will be available again globally tomorrow.
After a series of productive conversations with the US government, we're redeploying the model with a new set of classifiers to target and block more cybersecurity tasks. In the near term, some routine tasks like coding and debugging will fall back to Opus 4.8. We’ll continue to refine these classifiers over the coming weeks to reduce false positives and better distinguish genuine misuse from legitimate requests.
We’ve also begun drafting a consensus framework—with Amazon, Microsoft, Google, and other Glasswing partners—for assessing the severity of AI jailbreaks and how AI developers should respond to them. We invite other industry partners and model providers to join us in this effort.
Finally, we’re scaling up our collaboration with the US government on model testing and safeguards. This will include pre-release access to models and safeguards for evaluation, information sharing on jailbreaks and misuse, and dedicated resources for joint research.
Thank you to our users for your patience, and to our partners across the government, industry, and the research community who worked alongside us to make Fable 5 available again.
Good news. The export controls are lifted. Defenders will regain access to #anthropic#fable5 & we can resume our work with the latest #ai models available
Will a powerful enough model wipe out harnessing gains? My research suggests: not yet! And cost savings matter more and more as capabilities democratize. See you down under 🇦🇺
We are excited to announce our first speaker for unprompted.au: Valentina Palmiotti (@chompie1337), who will be presenting BinChomp - her autonomous n-day exploit generation pipeline!
I wrote about what was actually in that #fable guardrail bypass research paper, and why it should never have triggered an #ai model export control. We can't export control our way to cyber resilience. So many tshirt ideas. www.lutasecurity.com/post/the-fable-5-export-controls-har…
The people who know cybersecurity know @k8em0. Few have done more for vulnerability disclosure and cyber policy. She knows her shit. Expertise matters.
1. You can’t “patch” this behavior without rendering the model less effective for defenders 2. No new frontier models can be developed or released if this is the administration’s best take 3. We don’t have time to strip defenders of the latest models & halt AI improvement
I’ve had a number of conversations with folks inside and outside government about the current situation with Anthropic, and here is what I believe to be true:
— As we know, Anthropic publicly released its Mythos class models earlier this week under the commercial name Fable.
— Fable is Mythos with guardrails. But if those guardrails fail, then you’ve exposed Mythos and its advanced cyber capabilities to people who shouldn’t have them. (Keep in mind that Anthropic itself widely promoted the idea that Mythos was a cyberweapon and needed to be regulated as such. They asked for government regulation of Mythos and championed the guardrails on Fable. If there is a vulnerability — big or small — it is Anthropic’s responsibility to patch.)
— A highly credible trusted partner of both Anthropic and the USG who was testing Fable came forward with a jailbreak of those guardrails. The Admin asked Dario to fix the jailbreak or de-deploy the model. Dario refused.
— In their blog post, Anthropic defended its decision by saying the jailbreak isn’t serious. That is not what the trusted partner and the USG believe; nor is that kind of minimizing language consistent with Anthropic’s brand as the AI safety company. It’s difficult to fathom how they could claim a jailbreak allowing operability of a cyber weapon could be defined as not “serious.”
— In the past, Anthropic has always said that safety must be top priority and taken super seriously. In this case, Anthropic prioritized the continued offering of the consumer model over safety.
— In reaction, the Admin issued the export control. The Admin did this reluctantly. It’s been very surprised that Anthropic hasn’t wanted to cooperate with a reasonable safety request (ie fixing the jailbreak issue). Anthropic’s reaction is very much at odds with their branding and ethos as a safe AI research community.
— The Admin’s hope now is that Anthropic remediates the safety issue, the export control is lifted, and Fable goes back into general release. The Admin wants all of this to happen as soon as possible. It is frankly bewildered that Anthropic hasn’t wanted to comply with safety requests that it previously said were its highest priority.
— Those trying to misdirect and tie this action to the prior DoW/Anthropic issues are wrong. The Admin values Anthropic’s technical capabilities and feels that this issue, while serious, should be easily resolved. The ball is in Anthropic’s court.
I’ve seen the paper. It’s not a jailbreak. It was Defense Oriented Prompting (DOP), capabilities defenders need. My thoughts on the hasty Export Controls that made Anthropic pull Fable. If Nat defense is the goal, this just scored an own goal against us
More of my thoughts on the public vulnerability disclosure fight Microsoft picked with the researcher Nightmare Eclipse in this piece by Matt Kapko for @CyberScoopNews . @Andrew___Morris of @GreyNoiseIO Intelligence shares perspective too.
I know there are good people still working there. Listen to them. Better yet - Next time, get an elder of Vulnerability Disclosure to guide you through a sincere Hoʻoponopono
Over the past several days, we have been listening to the conversation around coordinated disclosure and the relationship between security researchers and vendors. We recognize that this relationship is both critical and, at times, fragile. We deeply value the security community, and will continue to take your feedback seriously.
To be clear about our approach to legal matters, we have no intention to pursue action against individuals conducting or publishing their security research. When an individual breaks the law and engages in malicious activity causing real harm to our customers, we will work with law enforcement as appropriate.
We recognize the work that goes into researching and submitting a vulnerability. We are committed to approaching every interaction with transparency, clear communication, and professionalism. We continue to believe strongly in Coordinated Vulnerability Disclosure as the foundation for protecting customers and improving our products. Each year we process a high volume of vulnerability reports. That volume continues to grow and will continue with the rise of AI-enabled research. We acknowledge that some interactions have fallen short and are working to learn from them.
Many of us have experience on both sides of this work, as researchers reporting vulnerabilities and as responders triaging and assessing them. That perspective informs how we approach this feedback and the importance we place on getting it right, particularly as the volume and complexity of research continues to grow.
The security community plays a vital role in helping us protect customers. We are committed to maintaining a constructive and respectful relationship and growing together. We know that, given the nature of this work, there will at times be misunderstandings. We remain committed to engaging in good faith and to providing a respectful and professional experience for all researchers, regardless of past interactions.
Over the past several days, we have been listening to the conversation around coordinated disclosure and the relationship between security researchers and vendors. We recognize that this relationship is both critical and, at times, fragile. We deeply value the security community, and will continue to take your feedback seriously.
To be clear about our approach to legal matters, we have no intention to pursue action against individuals conducting or publishing their security research. When an individual breaks the law and engages in malicious activity causing real harm to our customers, we will work with law enforcement as appropriate.
We recognize the work that goes into researching and submitting a vulnerability. We are committed to approaching every interaction with transparency, clear communication, and professionalism. We continue to believe strongly in Coordinated Vulnerability Disclosure as the foundation for protecting customers and improving our products. Each year we process a high volume of vulnerability reports. That volume continues to grow and will continue with the rise of AI-enabled research. We acknowledge that some interactions have fallen short and are working to learn from them.
Many of us have experience on both sides of this work, as researchers reporting vulnerabilities and as responders triaging and assessing them. That perspective informs how we approach this feedback and the importance we place on getting it right, particularly as the volume and complexity of research continues to grow.
The security community plays a vital role in helping us protect customers. We are committed to maintaining a constructive and respectful relationship and growing together. We know that, given the nature of this work, there will at times be misunderstandings. We remain committed to engaging in good faith and to providing a respectful and professional experience for all researchers, regardless of past interactions.
Not that ‘responsible’ disclosure shit again 🙄 No vendor uses that term unless they want to call someone irresponsible. Even if someone drops 0day, patch & move on. Going after a researcher is a great way to turn 1 bad relationship into many terrible relationships.
This tshirt I made for Symantec Vulnerability Research, a program predating Google Project Zero by nearly a decade where we’d discover, report, & disclose vulnerabilities we found in other people’s software, is 20 years old.
Still holds true: Don’t hate the Finder, hate the vuln
Dropping 0day isn’t the worst thing a researcher can do. It’s not ideal, but at least orgs can take steps to mitigate. Non disclosure is far worse. What drives researchers toward non disclosure? Threats from vendors. Researchers aren’t criminals unless their crime is curiosity.
“The unpayable debt of being alive” That phrase & so many others pierce me to my core. I can’t fathom why, in a world of such hard won abundance passed down from our ancestors, we don’t yet have #ubi
This essay has been on my mind since 2023 and I'm happy to have finally published it. It's an argument for UBI that may not resonate with many, but if it does, I hope it does strongly. I feel so much gratitude for every human who came before me, and I fight for a better future for those yet to come.
Just worked w/ @CNN on a piece about why I wouldn't upload full financial docs (tax docs, statements, etc) to AI tools due to leakage & hacking risk. I don't recommend connecting bank accounts to AI tools. It becomes a 1 stop shop for attackers looking to drain your accounts🤖💸
A preview for Pro users: a new personal finance experience in ChatGPT.
Pro users in the U.S. can securely connect financial accounts, see where their money is going, and ask questions based on the information they choose to connect.
This would fund #ubi as a shared dividend to offset increased power bills we’ve been paying to subsidize data center buildout. Not to mention the intellectual property humanity has contributed. We are all shareholders in #ai
We should federally tax Tokens at the Provider level.
Not a lot. Less than 50c per million tokens.
It will accomplish 4 things (at least )
1. It will push the big AI players to optimize tokenization, caching , routing and localization
Which will
2. Reduce energy usage. Saving them in energy costs more than what they paid in tax and reducing strain created by the growth in energy consumption
Which will
3. Generate maybe 10 billion dollars a year to start, but over the next ten years could grow 30x to 100x
Which will
4. Create a source of funding to pay down the federal debt or deploy, in response to the things AI brings that we don’t expect or don’t like
At some point the models will pass it on to customers. Of course. That’s ok. Customers will have the ability to choose between providers. Or to do everything using open source models locally.
Q: Did you talk to Xi about the cyber attacks that he's done in the United States?
TRUMP: I did. And he talked about attacks we did in China. You know, what they do, we do too. We spy like hell on them too. I told him, 'we do a lot of stuff to you that that you don't know about.'
The best thing you can do right now is reduce your attack surface. This and my other thoughts on the #ai era of cybersecurity in this @InfosecurityMag piece by @dannyjpalmer
When @bsidessf asked me to keynote, and the theme was “BSidesSF — The Musical,” I was thrilled. Watch my freewheeling talk about #ai , our future, & a live song linked at the end of my blog. #bugbounty#ubi
Couldn’t agree more with @WeldPond about @window for @DarkReading being “one of the most important security leaders of the past two decades," for her ability to achieve systemic change. Great #darkreading20 special coverage.
As part of Dark Reading's 20th anniversary special coverage, we profile the CISOs, founders, researchers, criminals, and policymakers who rewrote the enterprise risk playbook. Read the full story here: www.darkreading.com/cybersecurity-operations/20-leaders-c…
“Patch the KEVs faster” still isn’t taking a scalable, targeted, realistic approach to the #mythos#ai era, for gov or private sector. AI defense has not yet produced an autonomous, safe answer to meet the AI offense moment.
Confirming this recent story from @razhael: www.reuters.com/legal/litigation/us-officials-weigh-cutti… In response to Mythos, CISA is considering a binding operational directive that would change the timelines for agencies to remediate vulnerabilities, including down to 3 days in some cases.
Thrilled to be heading to @UniofOxford@blavatnikschool to have some interesting conversations with Ciaran Martin on #ai#mythos & the evolution of vulnerability discovery, disclosure, & military defense & offense cyber capability proliferation
Join Katie Moussouris, Founder and CEO of Luta Security, in conversation with Professor Ciaran Martin, as they discuss how AI is reshaping cybersecurity. 🔒
We constructed poverty as we know it. Poverty is a legal status imposed on those excluded from legal access to the needs of life. It is economic injustice. It is a weapon built to fear.
#mythos & the new #ai models got you scared? I shared some practical advice & optimism in this otherwise dire disaster prediction fest in my comments to @yaelwrites for @verge
#ai was built on all our labor. Every word, image, idea came from us. Its gains belong to everyone, not just a few. I signed the AI Pledge for Humanity, committing 2% of my income to Income to Support All Foundation to advance #ubi & our shared prosperity. actionnetwork.org/petitions/the-ai-pledge-for-humanity
AI is not going to flood you with real vuln reports unless you have a ton of real vulns. Adding resources to a vuln disclosure process to keep up with triage & bug fixing is a temporary investment at the loud end of the problem, not the right end.
Super Typhoon Sinlaku has once again exposed a vulnerability that Guam's residents and the military know too well: an above-ground power grid that collapses under the force of every major storm. www.guampdn.com/news/our-view-treat-guams-power-grid-vuln…
Want to know which throttled release of the latest #ai models I think is best and why? Read my opinion on @AnthropicAI ‘s Project #glasswing#mythos private release vs @OpenAI ‘s Trusted Cyber Program application & vetting process.
What can regular people do about all the security findings of the latest AI models? My comments to Nicole Nguyen for @WSJ
Our usual advice, but seriously, now more than ever: Keep software up to date Use long unique passwords Use a password manager Use multifactor authentication
Last week, Anthropic announced Project Glasswing alongside Claude Mythos Preview, a model they described as so powerful at finding vulnerabilities they couldn't release it. The announcement featured AWS, Microsoft, Google, and Apple as partners, $100M in compute credits, and a clear message: this is dangerous, and only we can be trusted to deploy it safely.
The results were real. Thousands of zero-days across every major OS and browser. A 27-year-old bug in OpenBSD. A 16-year-old bug in FFmpeg. Fully autonomous exploit chains that would have taken human researchers weeks.
But here's what bothered me: all the credit went to the model.
Read the technical blog carefully and a different picture emerges. The real innovation isn't the model. It's the workflow:
- Rank every file in a codebase by attack surface - Fan out hundreds of parallel agents, each scoped to one file - Use crash oracles (AddressSanitizer, UBSan) as ground truth - Run a second verification agent to filter noise - Generate exploits as a triage mechanism for severity
That's a pipeline. And pipelines are model-agnostic.
At Lazarus AI, we spend our days deploying custom AI in places where "just use the closed API" isn't an option: regulated industries, enterprise, and government. When I saw Glasswing, my instinct was the same one I have every week: strip out the proprietary model, keep the architecture, run it on whatever model is best for the customer.
Clearwing is a fully open-source vulnerability discovery engine. Crash-first hunting, file-parallel agents, oracle-driven verification, variant hunting, adversarial verification. Works with any LLM.
I tested it with OpenAI Codex 5.4 and reproduced Glasswing's findings. I'm now reproducing results with our own ReAligned model - Qwen3.5 finetuned to Western alignment.
Mythos is certainly a great model. The N-day exploit walkthroughs in Anthropic's blog show real reasoning depth. But it's an incremental improvement over Opus, the same way Opus was over Sonnet, and Sonnet over Haiku. It's not a leap to superintelligence. It's the next point on a curve we've been watching for years.
What actually changed the game was the workflow.
Defenders shouldn't have to wait for access to a gated model to secure their software. These vulnerabilities have been sitting in codebases for decades. The tools to find them should be available to everyone: the open source maintainer running FFmpeg on a Saturday, the startup that can't afford $125/M output tokens, the researcher in a country where Anthropic doesn't operate.
Heather Adkins - Ꜻ - Spes consilium non est@argvee
An update from NIST. Due to volume they’re only going to enrich CVEs that are meaningful to USG federal systems and critical software (some more nuance in the blog post). This means if you’re relying on the NVD data for your enterprise security program and use other software, your tools may not flag software you use as at risk. www.nist.gov/news-events/news/2026/04/nist-updates-nvd-op…
#openai shots fired “We don’t think it’s practical or appropriate to centrally decide who gets to defend themselves. Instead, we aim to enable as many legitimate defenders as possible, with access grounded in verification, trust signals, & accountability.” openai.com/index/scaling-trusted-access-for-cyber-defense/
New post: We show that small, cheap models can detect the flagship Mythos FreeBSD zero-day (CVE-2026-4747) using a simple harness we call nano-analyzer
Models down to 3.6B active params (including open-weights ones you can run locally) would have detected it 100-1000x cheaper
Everyone's worried about the Vulnpocalypse, vulnmageddon, vulnerability storm brought on by #ai like #mythos, but what if we treated this like a music festival? We all have tickets to Vulnapalooza. Here's your festival survival guide.
New @DecipherSec podcast with the always insightful and thoughtful @tqbf. We talked about (surprise!) AI-assisted bug hunting, Claud Mythos, and what's coming for researchers and defenders.
When the pandemic lockdown hit & @Zoom surged in popularity, so did its #bugbounty program — much like many organizations are facing an #ai vuln report surge today. @LutaSecurity helped flatten the curve of Zoom’s bug cases by 37% in less than 10 weeks
Great advice from @AnthropicAI on prep for accelerated AI vulnerability discovery, including what to do if you don’t have a dedicated security team, if you’re reporting bugs you found, or are an open source maintainer.
Friday afternoon @gadievron says "I'm working on a CISO community document for Monday. Want to collaborate? Releasing Monday." I said "Sure." (I have a problem with that word.)
@AnthropicAI had dropped Mythos on Monday. @cloudsa is running an emergency CISO Zoom on Tuesday. @SANSInstitute was already building BugBusters this Thursday with Ed Skoudis, Joshua Wright, and Chris Elgee. The entire community was asking the same question: what do we actually DO about this?
Three nights later we have a 30-page strategy briefing with 60+ contributors. "Sure" turned into barely sleeping Friday, Saturday, Sunday while @gadievron and @rmogull dragged this thing into existence. (My son checked to see if I was still breathing around hour 40. I think he was mostly concerned about if Uber Eats delivered Five Guys yet.)
The contributing authors list reads like someone raided a cybersecurity hall of fame: Jen Easterly, Bruce Schneier, Chris Inglis, @philvenables, Heather Adkins @argvee, @RGB_Lights, @sounilyu, @jimreavis, Katie Moussouris @k8em0, Jon Stewart, Maxim Kovalsky, David Scott Lewis, Joshua Saxe, John Yeoh, Ramy Houssaini and James Lyne. Every single one said yes within hours.
Cloud Security Alliance @cloudsa, @SANSInstitute, [un]prompted, @OWASPGenAISec -- four organizations that don't usually build things together at this speed. This is the start.
Live AI-assisted vulnerability discovery against real code. No slides about the future. Terminals and bugs. (The kind of demo where something breaks and that IS the point.)
Full reviewer list is in the doc. If you know someone on it, send them a note. They earned it.
But an even bigger thank you -- seriously -- from the entire cyber security community needs to go to @gadievron for once again bringing the avengers together -- like in Endgame (is that what Mythos is?) -- and you all know the scene -- but we need someone to create the meme with Gadi Evron with his shield and Mjölnir saying "Avengers..... assemble!" because that is exactly what he does. A lot it seems.
The technical debt repo man is coming, especially for those that don’t have robust patch creation & management — & it’s clear we can’t keep cranking out bugs in the 1st place. Stay hydrated, ops teams, & tip your doordashers well as we brace for impact of the #ai vulnpocalypse
Instead of our normal Friday news wrap podcast, we decided to call up two of the smartest people we know to talk about @AnthropicAI Claude Mythos: @k8em0 (and her cat) and @cigitalgem (from the farm).
N days, logic bugs, exploit chains defeating friction-based exploit mitigations — your time has come. @AnthropicAI#mythos changed the defender’s calculus overnight. Glad #glasswing is attempting the biggest multiparty vuln coordination of the century red.anthropic.com/2026/mythos-preview/
“AI models have reached a level of coding capability where they can surpass all but the most skilled humans at finding and exploiting software vulnerabilities.” www.anthropic.com/glasswing
At [un]prompted, the illusion that vulnerability research won’t be automated away has passed. Specifically, it was Nicholas Carlini’s talk, a last second entry, that hammered it in.
“$100 per person/month [in 1975 could’ve grown to] $1,352/month to every American over 18 [by 2023]. Instead of $79 trillion flowing to the top 1% over 50 years, that wealth generated from rising productivity [could have gone] to everyone as their due dividend [as] shareholders”
We should have started a universal basic income back in 1975, and it should have grown this entire time in line with national productivity growth. My latest:
Yes and even it started raining AI patches too, testing and deployment will still lag far behind. Ask Amazon* how the whole agentic AI in prod is doing so far
“That’s not automation, that’s a spam cannon with a confidence problem.” I agree with this post AND the coming jobpocalypse. Just because AI can’t do our jobs well doesn’t mean capitalism won’t replace us with AI. I for one am preparing for our new spam cannon overlords & so should you
If you want people to not hate AI and instead embrace it, don't just on occasion mention universal basic income as a "maybe we will need this as a parachute" kind of thing. Push for it. Push hard for it. Insist that UBI is a dividend that we all deserve as our fair share of AI.
i’m still endlessly surprised by the fact that none of the ai superintelligence labs have an answer to “what happens when you build your superintelligence and automate us all away?”
like the number one question on basically every normie’s mind
and the labs just collectively shrug “meh we don’t know. but like don’t worry about it okay”
and then they are surprised how unpopular they are becoming with normies
Even before my keynotes last fall, I warned of this very eventuality. The gig economy was always worker exploitation. Some workers could work the system well, but most lost out. Now they will all lose. AI acceleration is making worker replacement a reality in #bugbounty & beyond
Thread - My own opinion & this is to the Bug Hunters, What @Hacker0x01 is doing re AI, is essentially stealing “our work” “our research” for their own profitability. They are for sure breaking client agreements, wherein a clients data / vulns belong to the client. Not H1!!
Oh node! 😱 Low quality bug reports breaking another Open Source project. Trying to throttle the flood using a bug bounty platform reputation system & forking bug reporters with low signal score to…the OpenJS Foundation Slack?! Oh node indeed 😩
⚠️ The Node.js Project now requires a HackerOne Signal score of 1.0 or higher to submit vulnerability reports. This will help our team streamline reports and support effective security reviews.
AI was the accelerant on a perverse incentive fire sparked by bug bounty platforms that reward spray & pray. Both open source & orgs without dedicated vuln response teams get overloaded when they offer cash there. cURL is right to leave AI shark-infested waters to start fresh.
cURL closing their Hackerone bug bounty program on HackerOne for obvious reasons: death by thousand slops, slop from both humans and AI-assisted submissions.
it is insane to me that companies like HackerOne are still stuck in the past.
why aren't cURL, other companies, and FOSS projects setting up environments modeled on their actual threat scenarios and letting researchers hack until they capture a flag?
what do you care about cURL security? what is the threat model?
you don't want an HTTP request to an untrusted site to result in: 1. a shell on your system 2. info leak 3. DoS that crashes your computer
it is all we really care about. PoC || GTFO.
read the flag, get paid. don't waste a single second reading anything else.
with this you don't even need to spend so much money on running a bug bounty program.
Today is the day that everyone should know/remember that Dr. Martin Luther King Jr. began advocating for universal basic income before he was killed. Everyone should also know why. Read his words about it. Lots of quotes from him here to help understand:
I'm so excited about [un]prompted! It's a community conference for AI security practitioners, taking place at Salesforce Tower in San Francisco (March 3-4).
Check out the CFP committee comments on what we'd like to see, and:
New article from me today about a centuries-old policy in Brazil that has a lot to tell us about just how high a universal basic income can be set at without seeing the effects on employment that so many people assume.
I remember pen testing an online game & learning almost immediately that they were far more interested in game cheats than security or privacy violations. They would more easily recover from those versus cheats that rendered a game unplayable or deprived them of add on revenue
Ubisoft executives when they hear the news someone has compromised Rainbow Six Siege and gifted $13,332,000 worth of in-game currency to roughly 30,000,000 active players, thus defrauding their company of an estimated $339,960,000,000,000
“UBI = a foundation…income is earned on top. A poverty-line UBI is not “the replacement paycheck for the post-work apocalypse.” .... It prevents the worst outcomes, stabilizes consumer demand, & gives ppl leverage to say no to exploitation”
We need universal basic income and healthcare in order to disconnect our survival from employment, and every architect of AI should be pressing for it.
When it comes to developing skills through underground organizations, recent geopolitical issues have also helped muddy the waters of how some professionals think about ways to earn a living, said Casey Ellis, founder at @Bugcrowd.
“There are a bunch of different factors here, with two big ones to call out: Necessity, and the blurring of ethical lines. Overall, job scarcity and increasing economic pressure, which, at this point, is a phenomenon that is being experienced globally. When it is an issue of survival and the opportunity presents itself, people will choose crime to survive,” Ellis told Dice.
In many cases, changing views of the web and other issues have redefined what a “bad guy” is, Ellis added. “In the case of hiring someone for overt cybercriminal activity, this distinction is probably clear to the person applying to the job, but their ethical threshold might be compromised relative to where they may have landed in the past,” he added.
We’ve seen other orgs attempt 3rd party bug bounties, thinking it will help their ecosystem become safer. Inevitably, the safety of software depends more on the maturity of the org producing it than how many bugs are reported to it. Bug foie gras isn’t the safest path to maturity
When I started MS Vuln Research in 2008, we found out how few orgs were ready for vuln disclosure. When I started MS’s 1st bug bounty in 2013, I never imagined it would grow to paying for 3rd party bugs. I hope 3rd parties were warned & OSS gets tested patches given to them
As announced by Tom Gallagher (@secbughunter), VP of Engineering, MSRC, on stage at Black Hat Europe, we’re evolving our bug bounty program. Now, high-severity vulnerabilities that directly impact Microsoft online services are eligible for bounty awards, whether the code is Microsoft-owned, third-party, or open source.
This expanded scope applies retroactively to cases from the past 90 days, ensuring recent impactful research is recognized and rewarded. These payments have already begun.
When I started MS Vuln Research in 2008, we found out how few orgs were ready for vuln disclosure. When I started MS’s 1st bug bounty in 2013, I never imagined it would grow to paying for 3rd party bugs. I hope 3rd parties were warned & OSS gets tested patches given to them
As announced by Tom Gallagher (@secbughunter), VP of Engineering, MSRC, on stage at Black Hat Europe, we’re evolving our bug bounty program. Now, high-severity vulnerabilities that directly impact Microsoft online services are eligible for bounty awards, whether the code is Microsoft-owned, third-party, or open source.
This expanded scope applies retroactively to cases from the past 90 days, ensuring recent impactful research is recognized and rewarded. These payments have already begun.
I spoke with @Williamrt of @ComputerWeekly on NDA bug bounties failing to increase security & the effects of gov disclosure requirements on national security, plus how AI threatens the human expert labor pipeline of tomorrow & why UBI may be our best bet
“AI is helping to identify over 70% of targets. Sometimes AI is hallucinating targets. So we always need humans in the loop.” - @HeliKlaar in her @SANSInstitute CyberThreat keynote “Cyber war by proxy: What Ukraine teaches us about defense coalitions and digital policy at scale”
“why the red team keeps winning: not because they are stronger—but because the blue team keeps mistaking comfort for capability.” — @treyka reveals wisdom in history, physics, & Rick & Morty in his brilliant Bsides Lisbon keynote
The internet is not a network, it's a small handful of platforms held together with rock n roll and silly string (@k8em0 ™) and sometimes it falls down. youtu.be/2118EJ4Gb5s
7560€ for fixing over 2700 bugs = 2.80€ per bug, and only paid after the Twitter storm. This person should be getting a real salary or UBI - Universal Bugfix Income
so far i got 7560€ before taxes for my security work in the last 7 months. And thats why i would appreciate that google, facebook, amazon and others would pay me directly. Also that 7560 i only got after the twitter noise.
The @FFmpeg team of volunteers provide deep technical training to the next generation & should be celebrated, supported, & provided with patches when Google researchers find bugs. <This debate could have been a patch>
FFmpeg makes extensive use of hand-written assembly code for huge (10-50x) speed increases and so we are providing assembly lessons to teach a new generation of assembly language programmers.
Zero Trust is not a product it is an approach - at the @NCSC we have just released demystifying zero trust which addresses common misconceptions, and provides practical advice on when and how it should be adopted.
Heather Adkins - Ꜻ - Spes consilium non est@argvee
OSS needs more hands and brains, but it’s grown beyond the capability of anyone to supply that. If you look at a modern IT infrastructure there are well over 10,000 different open source projects under the hood. We are at the point of needing to scale with better tools. Hope we get there.
Yes & it would still be far more efficient to have Google supply a patch itself rather than wait for someone else to do it & pay a bounty. If we tell orgs to use AI in CI/CD pipelines, why not use it in all AI bug hunting workflows? Google could couple AIs: Big Sleep w CodeMender
I certainly didn't remember that this program existed, would be a different vibe to mention it in the bug report sent to project maintainers. Or would that not fit the rules of the program?
Context on the recent ffmpeg AI vuln disclosure kerfuffle. Interested to see if this results in Big Sleep & CodeMender being used in tandem, to address ffmpeg’s core complaint: A huge company like Google should provide patches with their AI bug reports to open source projects
Heather Adkins - Ꜻ - Spes consilium non est@argvee
We’re excited to see the security and OSS communities engage on vulnerability disclosure in light of new AI technologies that we believe will enable both defenders and attackers alike. Existing and emerging norms around disclosure are important debates, and we’ve noted the feedback. Thanks! Also want to share some additional thoughts. 1/10
💰Big vendor: We’ll use FOSS to build commercial offerings - it’s free! 💻Big vendors’ AI: Found a bunch of bugs in the FOSS 🙏🏼FOSS: We can’t fix these fast enough, can you send patches? 💰Big vendor: No, you’re supposed to be free 🤔FOSS: That seems unfair 🔥Randos: How dare you
Even with patches provided with bug reports, AI makes too much human work in prioritizing & testing. Commercial closed source faces similar bottlenecks & diminishing security returns. Vuln handling can’t keep up even if using AI validation. Security is being DoSed by AI right now
There’s a reason most orgs lack bug bounties & VDPs even after more than a decade of platforms with triage & easy payments — those were never the real problems to solve in vuln disclosure. AI is highlighting an existing bottleneck - fixes lag in open & closed source vuln handling
Finding bugs & proposing patches doesn’t solve this bottleneck, just widens it a little, helpful but not a complete solution. For AI to truly improve security in the vuln ecosystem, it must speed up testing fixes. Humans will still have to verify for a while to ensure reliability
Great to be back at @nohatcon 2025 - after the opening by @embyte , first track is "No pAIn, No gAIn: How AI Will Hurt Bug Bounty Hunters and How to Fix It", from security researcher and entrepreneur @k8em0 Come say hi 👋🏼
I've just published Sept's @ITSAfoundation newsletter that highlights what I consider to be the top 7 pieces of Universal Basic Income world news this month. Subscribe to get these monthly to stay in the loop on UBI and also what we're up to at ITSA Foundation in support of UBI.
gofund.me/ae3e52797 It is with great sadness I share the passing of Caspian Shea youngest son of Johanna and Dylan. We are asking for your support covering medical and funeral arrangements during this unimaginable time. Please consider donating - but do share far and wide.
When we launched in 2018, the first piece on the site was part one of our four-part oral history of @L0phtHeavyInd. We were able to rescue that series from the archives. Here's that first part again. Enjoy!
It has begun: AI tools are being used to perform OSINT to determine which orgs and people to target in a hack, write infostealer malware, determine the right ransom amount per victim, organize stolen documents, and write the emails. AI doesn’t change the attack, it SCALES it.
Anthropic says a hacker used its Claude chatbot "to an unprecedented degree": Claude identified vulnerable companies, wrote infostealer malware, analyzed stolen files for extortion purposes, calculated extortion amounts, and wrote extortion messages. www.nbcnews.com/tech/security/hacker-used-ai-automate-unp…
Is lack of engagement on this platform with identical posts on other platforms getting many more genuine interactions with less than 1/6 the audience due to an algorithmic shadow ban here or bot followers or both?
Today I have a more serious topic than usual, please consider reposting for reach:
My wife and I are urgently looking for a specialist in neuropediatrics or a similar field for our autistic child with a diagnosed, but not further specified, movement disorder [1/3]
Signs point to internal process dysfunction, especially if they fired an employee who ultimately got this fixed. Process & maturity gaps are things a bug bounty platform alone won’t fix. It’s exactly why orgs ask @LutaSecurity to manage end-to-end programs www.lutasecurity.com/solutions
In the early days of bank & credit card company penetration testing, I loved being hired by banks to rob them. Some of these hacks may still work today.
Many safeguards rely on automated & manual checks we told them to put in place decades ago.
One of the strangest myths about vulnerability disclosure policies & programs is that they have always been ways for vendors to receive vulnerability reports. Nah, these policies were borne out of hackers telling vendors when to expect public disclosure to inform & protect users.
For any newcomers who are reading along: There were certainly Disclosure policies before Microsoft’s, but they were mostly from hackers, like RFPolicy by rain forest puppy. I based Microsoft’s & Symantec Vuln Research’s Disclosure policies on AtStake’s, which was based on RFP’s
🚨Today, the NCSC is revealing that Russian military intelligence has been responsible for deploying a sophisticated malware dubbed AUTHENTIC ANTICS as part of its operations.
Healthy wildlife and communities depend on a healthy democracy. The legacy of the late great #johnlewis was rooted in the fight for voting access for all Americans. This fight continues – Good Trouble Lives On!
This podcast with @ianlpaterson was such a pleasure to record. It has some of the origin lore of Hack the Pentagon and my thoughts on the inescapable realities of the Vulnerability Equities Process and much more.
Another fun fact: This vulnerability was one that helped me launch Microsoft Vulnerability Research (MSVR), the first major software vendor multiparty vulnerability coordination process & 3rd party vuln research & reporting process. Google Project Zero followed ~7 years later.
My nephew loves the outdoors & he’s competing to win a spot in a Ranger Rick magazine. You can vote for free with Facebook verification. Votes are doubled today (Sunday). Si Yu'us Ma'åse (that’s thank you in CHamoru)🙏🏼 jr-ranger.org/2025/alexander-edfe
Universal basic income is what true independence would look like. A high enough UBI would be FU money for all of society. They don't want you to have the power to refuse low wages and the freedom to make your own choices and pursue what you want. It's why we have to fight for it!
. @CurrentJen tops the list of people who have enabled me to grow as a person & professional. She’s the best person to strategically work towards company goals while effortlessly handling the gnarliest security crisis comms. Hire Jen Wood if you “take security very seriously.”
After five incredible years at @LutaSecurity, I’ll be moving on at the end of the month and looking for a new senior communications leadership role within the cybersecurity industry. For more info about my background, please read: www.linkedin.com/posts/activity-7342987041732706306-pCaH. Thanks!
BREAKING: New report jointly-published by the NSF and @fundforhumanity on the impact of AI on the labor market concludes that 25% of workers will be displaced in the next 3 years.
You can use this link to input your job to check your job risk score. 👇
🎤 Keynote Announcement 🎤 We're excited to announce Katie Moussouris (@k8em0) as keynote speaker for No Hat 2025! Founder/CEO of @LutaSecurity, leading voice in vuln disclosure & bug bounties. Seen at Black Hat, DEF CON, RSA now live in Bergamo, Italy on Oct 18th! #nohat2025
There will be significant effects on national security from these CISA budget & personnel cuts. There has also been a general sharp downturn in cyber spending & jobs across the board in the private sector. The net effect is a nation weakening as attacks increase.
AI voice clones have hit the White House! If your team isn’t prepared to catch and stop these voice clone attacks, now’s a good time to get them educated and set up. Use a 2nd method of communication to verify identity before sending money, docs, data, etc. Be politely paranoid.
NIST’s proposed Likely Exploited Vulnerabilities equation is interesting, & similar predictive attempts were made by Microsoft over 16 years ago w the Exploitability Index. My concern is always an over reliance on data that may not apply to your org. My comments in the article
New: UAE is trying to recruit Pentagon workers displaced by DOGE to move to Abu Dhabi to work on AI for UAE military. A UAE brig general met last month with two former staffers of Defense Digital Service and tried to recruit them and their entire DDS team www.zetter-zeroday.com/uae-recruiting-us-personnel-displa…
When I testified before US Congress about the Uber data breach when they misused their bug bounty program to pay off data thieves, I didn’t think I would have to update my core guidance to include this: Don’t let extortionists set your bounty reward price.
Coinbase was *right* not to pay extortion, but putting up a “reward pool” for the same $20M amount is ultimately going to lead future criminals to groom more minors to commit crimes & turn them in to reap the rewards.
Defense cannot pay the same as offense or you create perverse incentives.
In this case, it’s just adding steps to exploit a company for huge sums, not an effective deterrent.
It’s tempting to flex with huge rewards, but the disruption to criminals is negligible & ultimately increases the cost to protect customers.
Cryptocurrency exchanges & others should consult with us on complex situations like this.
Cyber criminals bribed and recruited rogue overseas support agents to pull personal data on <1% of Coinbase MTUs. No passwords, private keys, or funds were exposed. Prime accounts are untouched. We will reimburse impacted customers. More here: coinbase.com/blog/protecting-our-customers-standing-up-to…
DEF CON legal update: Truth is a complete defense against defamation.
The Hadnagy lawsuit against us is over. Summary judgement. Dismissed, with prejudice.
We look forward to returning our full attention to the community and conference we love.
We also thank everyone who came forward to help keep our community safe. We know it’s not an easy choice, but the world is better for it.
This victory is encouraging. We hope it makes attendees feel safe reporting CoC violations . We hope it demonstrates our commitment to protecting attendees from misconduct. Mostly, we hope our amazing community will continue looking out for each other. We will always have your back.
Did you go to #rsac? Did you read some of the industry reports? As threats become more pervasive, the 1 constant is the pressure to do more with less. Security maturity & strategic planning is key to surviving the pinch between the rock of fixed budgets & hard place of attacks.
This was his comment about my talk at his symposium jointly hosted by Harvard & MIT that covered Microsoft’s first bug bounty program, which planted the seed of Hack the Pentagon.
On this day 250 years ago in my home State of Massachusetts, our American patriot forebears fought the first battle of the American Revolution against the tyranny of a King, over #tariffs on tea.
We can’t just ghost-kitchen CVEs. We need a plan with a true mandate if a transition out of MITRE will work. Otherwise, we’ll have for-profit companies (including those funding non-profit foundations) competing with other governments, fracturing the space vying to fill the void.
If we aren’t building an orderly transition plan like NTIA’s IANA handoff to ICANN, we’re going to be worse off in 11 months. This isn’t the 1st global internet infrastructure we’ve handed off, so let’s learn from the previous experience & not xkcd it up xkcd.com/927/
“JD Work — now on the US NSC — shocked some by warning that the US would take lethal action against malicious actors in commercial cyber operations. Participants who heard [it said] they were unsure if it was meant literally or figuratively”
The Pall Mall Process — a diplomatic initiative designed to reform the commercial spyware and hacking market — recently added more nations as it confronts an industry that is more complex than ever therecord.media/pall-mall-process-commercial-spyware-hack…
How effective is your #bugbounty program? How do you know if you can handle a Vuln Disclosure Program let alone a bug bounty? Can you get more value out of each bug report than just the one bug?
All of these are maturity questions. @LutaSecurity has the answers. Come talk to us.
Entrepreneurs are driven ppl who do great things at huge risk. I worry how much focus is spectacular flameouts/meme economy. Meanwhile, others are grinding in their niche and succeeding, but not which shows up in VC balance sheet. We need wells of sovereign competency to draw.
I gambled a year’s salary and lost. This is what building a hardware product can look like, especially if it pushes limits.
The OMG Cable has evolved a lot since this story, but it wouldn’t be what it is today without this gamble AND failure. The factory tooling I have built today is something I designed over the years to prevent and identify so many possible failures.
Don’t miss it, folks! Three Buddies (and a Buddy) sharing security insights & laughs on the latest Three Buddy Problem podcast. Guest buddy is @LutaSecurity’s CEO @k8em0. @ryanaraine@craiu@juanandres_gs
🌺🔥 NEW pod alert! Katie Moussouris joins the buddies to parse news around a coordinated Chinese exposure of Taiwan APT actors, CitizenLab's report on Paragon spyware and WhatsApp exploits, Russians shopping for Telegram exploits and the future of CISA in the face of budget cuts and layoffs. @k8em0@craiu@juanandres_gs securityconversations.com/episode/china-exposing-taiwan-h…
Didn’t think this wonderful podcast could become a musical? THINK AGAIN. 🎶 Thanks for having me join you all as a special buddy on this week’s 3 Buddy (& a Buddy) Podcast!
🌺🔥 NEW pod alert! Katie Moussouris joins the buddies to parse news around a coordinated Chinese exposure of Taiwan APT actors, CitizenLab's report on Paragon spyware and WhatsApp exploits, Russians shopping for Telegram exploits and the future of CISA in the face of budget cuts and layoffs. @k8em0@craiu@juanandres_gs securityconversations.com/episode/china-exposing-taiwan-h…
It’s obvious that CSRB was not the only way the US government is investigating cyber attacks like Salt Typhoon affecting telecoms — but CSRB’s sudden absence does leave a serious gap in the free, authoritative reporting of non classified information to the public from an unbiased government source.
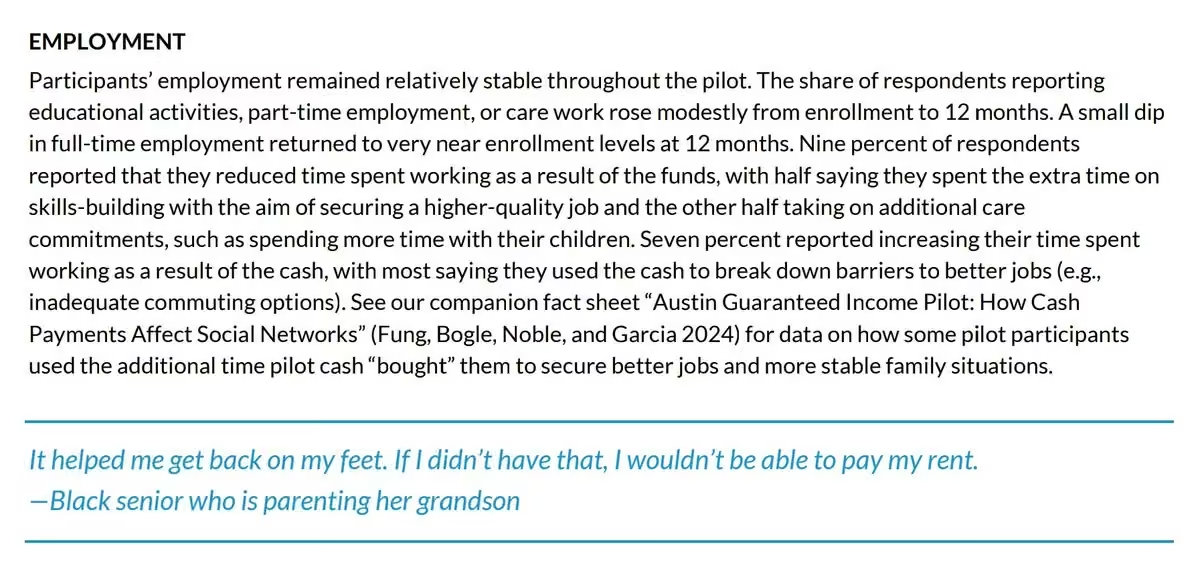
New basic income pilot results. UBI will reduce recidivism. Oh and also employment went up for those in the treatment group and down in the control group. Other good things happened too, like better mental health.
U.S. Government Disclosed 39 Zero-Day Vulnerabilities in 2023, Per First-Ever Report - via @KimZetter & features comments from @LutaSecurity CEO @k8em0
Being part of @shmoocon has changed my life. My 1st talk was here, a panel I ran about buying 0day in 2007. This conference is unique in holding true to its r00ts even while evolving. My heart is full of gratitude for this place.
We believe that workers & organizations benefit from shared success, and now we have proven that a profitable company can thrive while taking care of all its workers.
Come find me where the skies are blue Where the block button works And the algorithms too I’m not deleting, just not tweeting 🤷🏻♀️ If AI is scraping, I’d rather be skeeting
Hanging out at the Hackers Conference this weekend is exactly what I needed. ✨ [Alt text description for video: Lightfall orb with cascading rainbow LEDs]
To those feeling despair: remember, every step toward progress in American history came after the darkness of defeat. Abolitionists, suffragettes, Dreamers, and marchers for civil rights and marriage equality all faced impossible odds, but they persisted. Now it is our turn.
“The only states that didn’t shift toward Trump were Washington, where Democrats increased their lead by 1 point from 19 to 20 points, & Utah, where Trump's lead stayed the same at 20 points.” We should reflect on what worked here & what didn’t elsewhere. www.newsweek.com/kamala-harris-donald-trump-2024-election…
Quick PSA: Someone is attacking Tor right now and has been for a few weeks.
The attacker is spoofing the IPs of Tor Exit and Directory nodes, and blasting TCP SYN packets indiscriminately on 22/TCP- spurring a large amount of abuse complaints to hosting providers, which are then temp blocking/banning Tor infrastructure which isn't actually doing anything wrong.
For the time being, I recommend all hosting providers *ignore* abuse complaints that indicate "SSH scanning" or "port scanning on 22/TCP" and originate from any of the following IPs: pastebin.com/idKU0agt
This is a clever attack. I'm working with partners to triangulate the true origin of this traffic then try to get it disconnected.
We can be angry, sad, confused, betrayed, terrified — but the one thing we can’t be is hopeless.
We can’t give up on each other or this country. We should reflect on this fact of who we are as a nation with clarity, not to blame but to build a better nation, indivisible, for all
When I was at the DNC, I witnessed history & a phenomenon that should be history: the end of the road of US territories in choosing the next President. Guam 🇬🇺 Northern Marianas 🇲🇵 American Samoa 🇦🇸 US Virgin Islands 🇻🇮 & Puerto Rico 🇵🇷 can nominate but not vote for US President.
Have you updated to iOS 18.1 with an Apple Intelligence capable phone? Apple has strong privacy and security protections. Still, you may want to turn off learning from certain apps like Signal or other private messaging apps. You can do this in Settings Apple Intelligence & Siri
Anybody fretting about the Okta 52 character username vulnerability, I present the Xbox spacebar attack that minted the youngest hacker ever recognized by a major company for finding a serious security hole. He was 5 & wanted to play forbidden games. www.cnn.com/2014/04/04/tech/gaming-gadgets/5-year-old-xbo…
Dutch researchers @midnightbluelab found critical zero-click vuln in photo app enabled by default on Synology storage devices, putting millions of systems at risk of being hacked. They found Synology systems owned by police/law firms/critical infrastructure contractors all vuln to attack. My story: www.wired.com/story/synology-zero-click-vulnerability
🧵Next week, you will see people using something called Benford's Law to try to prove election fraud. ⛔️These people are wrong⛔️ I am a scientist who has published on Benford's Law. Let me tell you what it is and why what they are doing is mathematically incorrect. 1/
This weekend my only hope is for nothing that someone else wants me to do distracts me from my family. Don’t lecture me about saying no or boundaries, that’s my boundary to anyone reading this. Sometimes people assault your task list with things you can’t ignore & that’s a fact.
2¹³⁶²⁷⁹⁸⁴¹−1, discovered today, is the largest known prime. It's a Mersenne prime (2ᵖ-1), which are easier to find.
It took nearly 6 years for the GIMPS software to find it after the previous largest known prime. It was also the first Mersenne prime found using GPUs.
Watching @WidowClicquot & absolutely struck by her interview with a man who was going to work for her. He applied obvious logic that if a woman can run her own household well, she can run her own vineyard business. She weathered catastrophe & adapted to build an enduring legacy🍾
It’s SO Hard to run a business. Under even the best circumstances it’s so hard. What Mme. Clicquot said about vines needing to struggle to become more reliant on themselves, to become what they are meant to be — I feel this every day. I’m not done struggling, becoming more myself
I remember Russian spies getting full time in-person jobs at Microsoft so my threat model has always been attuned to some form of this issue of spies infiltrating the software supply chain.
Hey, let’s see who can manage to do ONE self-care thing this weekend.
Errands don’t count. Yeah, I see you “weekends are for me…to do the laundry” people, I see you. I feel you. I am you. Gotta be a real thing that doesn’t take more than it gives you.
Hey people who get to do an abundance of self care — this post was obviously not meant for you. It was meant for those of us in pain who don’t have the luxury of enough time for ourselves. So if you get daily me-time, lucky you. Don’t gloat, or scoff at those of us who don’t. It’s not nice. Spend some of that extra me-time on building empathy.
I just live hacked @ArleneDickinson (Dragons' Den star - Canada's Shark Tank) by using her breached passwords, social media posts, an AI voice clone, & *just 1 picture* for a deepfake live video call. Thank you @ElevateTechCA@Mastercard for asking me to demo these attacks live!
Vulnerability disclosure processes are really about notifying affected parties for their safety, ideally to apply a patch before an attacker exploits the issue.
Any Vuln disclosure program or bug bounty that doesn’t notify affected users is violating the International Standards.
Let me tell you about the first night of my bioinformatics job when I accidentally doubled the size of the human genome database… And the senior engineer who answered my call, walked me through rolling it back & the job I kept for years afterwards…
In case anyone else was wondering how you’d escape a flooding attic with an axe, here’s what people told me because I had no idea how you’d swing an axe while swimming: 🪓 A-shaped roof: cut a hole in the lowest side 🪜 Flat roof: use a ladder Both before the water gets very high
Marie Curie was the first woman to win the Nobel Prize. This didn't happen because she herself fought for it -- although she did fight hard the whole way to even get to that point. 👩🔬 What happened was that the award was offered to her husband, Pierre. (1/n) 🧵
Congratulations to our 2024 medicine laureate Victor Ambros ✨
This morning he celebrated the news of his prize with his colleague and wife Rosalind Lee, who was also the first author on the 1993 'Cell' paper cited by the Nobel Committee.
When Emily and I were at the @WhiteHouse we told policymakers a reason why our youth don't have MORE examples of women in STEM on TV, is that people actively decide against it. We have to take our own money and invest in ourselves to move the needle forward. Proud of you!
Emily's Wonder Lab helped inspire the next generation of scientists. I pitched dozens of science experiments for more seasons, but they weren't interested.
Arizona, Texas, Arkansas, Mississippi, Indiana, Ohio, Kentucky, Tennessee, Georgia, Florida residents: check your voting status today - it’s your last day to register to #vote
I’m looking at the swing States & wondering if enough people will vote to carry us forward, or if we’ll miss the rope by a few threads & plummet into the abyss of losing more rights.
Some things you do for the plot. Others you do for your family. Everything else you do for the greater good. That includes self-care. Me without self-care would be net bad for humanity.
Consider supporting the family in this sudden tragedy by sharing or donating. ❤️🩹 I didn’t know Jeff Wade well personally, but he will be missed by those who did & no family should have to bear this alone. spot.fund/n3q5kddt
"For these women, the liberty of privacy means that they alone should choose whether they serve as human incubators for the five months leading up to viability. It is not for a legislator, a judge, or a Commander from The Handmaid’s Tale to tell these women what to do with their bodies during this period when the fetus cannot survive outside the womb any more so than society could -- or should -- force them to serve as a human tissue bank or to give up a kidney for the benefit of another." 4/
Another State Central Committee meeting in the bag. We passed rules amendments, resolutions, & approved the creation of a Muslim Caucus. Most of this work is procedural, but it paves the way for government for & by the people. Find your legislative district & run for something!
Whitney is a technical treasure AND fun artist. If you’re my Signal pal, brace yourself for some of her stickers. I need no excuse for angry unicorns lol
I ran a meeting that lasted 4 hours after landing from a delayed flight. I have 7 hours between that meeting ending and my next meeting beginning. I cannot sleep. The cosmos is within me. I am a way for the universe to laugh at itself. The cosmos laughs in snooze buttons.
I was up in time to make it for trash day. I missed trash day. The cosmos also laughs in trash day. Why isn’t every non-holiday weekday trash day?! Why do we consent to live in this tyranny?
Eliezer Yudkowsky's blog post highlighted the Stanislav Yevgrafovich Petrov story: "Wherever you are, whatever you're doing, take a minute to not destroy the world."
An excel spreadsheet crashed this company's network.
But it wasn't malware.
The truth is *much* weirder.
Try this out, open up a xls (not xlsx) file in your favorite text/hex editor. Notice all the repeating characters in the header.
When receiving POP3 emails with an excel attachment, the characters bit patterns caused a signalling pattern on the physical copper of the company's T1 line, crashing the network equipment.
"But there's going to be a lot of empty suits and vaporware salespeople who are going to be upset or going to want to claw things back to the acronym soup that they sell at RSA." - @juanandres_gs at LABScon
Did you know before this tweet that Oregon is voting to implement a universal basic income of $1,600 a year, and that if approved by voters in November, it would mean that Alaska is no longer the only state with an annual UBI?
Live in a “safe State/area”? Don’t just vote - VOLUNTEER to reach voters in swing states. There’s something to do for all flavors of neurospice/introvert/extrovert/ambivert. Aim to triple your vote by convincing others to register & vote where it counts. events.democrats.org
💔 This week's show is the full keynote day remarks from Juan Andres Guerrero-Saade at #labscon24.
In this talk, Juanito addresses the current state of threat intel, expressing a need for a difficult conversation about its direction and purpose. He discusses feelings of disenfranchisement among professionals, the void in meaningful work, and the importance of reclaiming control and value in cybersecurity. @juanandres_gs@craiu
🏆After providing an autobiography on how she became the Mother of Decompilation, Dr. Cristina Cifuentes was presented by @labscon_io and @juanandres_gs with the 2024 Lifetime Achievement Award. As @k8em0 posted on X, "so much of our industry is possible because of [Cristina's] work." x.com/k8em0/status/1836808600880062752
Legendary pioneer Dr. @criscifuentes discussing her groundbreaking foundational work on decompilation — so much of our industry is possible because of her work.
When I encounter a restroom with real cloth washcloths, I recall the one I used to clean up in when I was homeless as a teen. The bathrooms for the conference my bootstrapped company has been platinum sponsors for the 3rd straight year have the softest washcloths.
And here we are 5 years later and I still feel the same way about consumer DNA tests, and apparently the entire board of 23andMe now agrees. Massive yikes incoming.
“deep dive into the secretive world of foreign investment in U.S. agricultural land. This talk will explore the growing trend of foreign ownership, which has surged by 50% since 2017, and its profound implications for national security” 🚜🌾💱 #labscon
"Who really owns America’s farmland, and why does it matter? Join us for a deep dive into the secretive world of foreign investment in U.S. agricultural land. This talk will explore the growing trend of foreign ownership, which has surged by 50% since 2017, and its profound implications for national security."
Legendary pioneer Dr. @criscifuentes discussing her groundbreaking foundational work on decompilation — so much of our industry is possible because of her work.
Very honoured and excited to share my retrospective on 30 years of decompilation next month at LABScon! Looking forward to the discussions @labscon_io#labscon24
Through a hilarious (and fairly typical) comms failure on my part, I learned I was participating in this panel discussion just a few hours before. Had a blast chatting with @k8em0 and @C_C_Krebs
LinkedIn is now using everyone's content to train their AI tool -- they just auto opted everyone in. I recommend opting out now (AND that orgs put an end to auto opt-in, it's not cool) Opt out steps: Settings and Privacy > Data Privacy > Data for Generative AI Improvement (OFF)
Only 1 more day until #labscon24. @LutaSecurity is a proud platinum sponsor for the third consecutive year. We look forward to seeing you there! www.labscon.io
Didn’t have “somebody’s engagement farming by posting an incorrect photo and misleading RIP for Katherine Johnson who actually passed away in 2020” on any of my bingo cards, these things are rigged.
Recently reminded with a large vendor: Even when you’re an industry leading pioneering expert, young men with far less experience are not embarrassed to question you & demand you prove your knowledge to them specifically, yet accept a man of any age’s word at face value #caturday
Having more women in our industry or in leadership isn’t the answer. It’s misogyny all the way down, & all the way up. It’s the entitlement men feel that their instincts - even in the absence of knowledge & experience - are more likely to be right than a woman’s proven expertise.
I’m supporting a cause that helps families in need by providing warm meals during tough times. Every donation counts. Please consider contributing or sharing to spread the word. gofund.me/9a46c6a7
White House Office of the National Cyber Director@ONCD
Today we took an important step towards securing the foundation of the internet. ONCD's Border Gateway Protocol Roadmap along with our public-private working group, is taking on a hard problem that has long-threatened the security of internet traffic. www.whitehouse.gov/oncd/briefing-room/2024/09/03/press-re…
Awesome & truly empathetic vulnerability disclosure work by @iangcarroll & @samwcyo “We had difficulty identifying the right disclosure contact for this issue. We did not want to contact FlyCASS first as it appeared to be operated only by 1 person & we did not want to alarm them”
In April, @samwcyo and I discovered a way to bypass airport security via SQL injection in a database of crewmembers. Unfortunately, DHS ghosted us after we disclosed the issue, and the TSA attempted to cover up what we found.
DHS/CISA should be using this eye opening, jaw dropping example of basic security failure of a highly discoverable & exploitable issue to inform a comprehensive threat model & test of airport security.
This long weekend is brought to you by sacrifice. Unsafe labor saw the Ludlow Massacre, Duffy’s Cut murders, and the loss of over 100 lives in the Triangle Shirtwaist Fire. Their sacrifices for our safety and security. #laborday#unions
I’m featured in the Do We Belong Here documentary, premiering Sept 10th at The Tampa Theatre! This film explores the stories of women in cybersecurity. Join me for the premiere!
“During the flight, human foster parents sit on the back of the microlight, waving and shouting encouragement to the birds as they fly.” Wonderful story. If only birds were real. www.theguardian.com/environment/article/2024/aug/28/north…
A young lady approached to tell me she loved my style & her friend thought I was really beautiful. Her friend was a way too young man who didn’t look up when I glanced in his direction. I laughed, thanked her & she went back over to him.
[DECLASSIFIED TODAY] Capt. Grace Hopper on Future Possibilities: Data, Hardware, Software, and People (1982) > National Security Agency/Central Security Service > Historical Releases View m.cje.io/3T48p6Y#gracehopperhasaposse
Gen-Z knows how to bring the joy back to politics nwasianweekly.com/2024/08/gen-z-knows-how-to-bring-the-jo… by Jonnika Kwon via @nwasianweekly “The energy we feel is more than a fleeting excitement. It is a culmination of the women’s liberation movement, the civil rights movement, & the larger push for progress in America”
There’s many people like me - who are doing everything they can to keep from losing whatever small amount of health they have left. People for whom a Covid infection could be disastrous. When you don’t mask, support mask bans or harass maskers - you make our world less safe /21
Ready to witness history as a proud member of @washdems — we are the delegation that brought the #cowboykamala energy to the #dncconvention2024 It’s a party, so full of joy already in here ✨🎉
FYI: You can buy the #cowboykamala sashes at kamala.is:) (They are union printed & all proceeds go towards electing Kamala & democrats up & down the ballot)
He nailed it right there, @BillClinton said that if we helped @KamalaHarris win, we’d make our children & our grandchildren proud. Now here we get Madam Speaker @SpeakerPelosi who was the first woman Speaker of the House, telling us to stand together to choose Democracy 🇺🇸🎉
“We were within 7000 votes of taking the majority [of the House]” - @SuzanDelBene at the #dncconvention A few thousand people less than in this stadium. That’s how close these elections are. That’s the difference between Project 2025 & codifying bodily autonomy. Get out the vote
At the #dnc#dncconvention last night, I found my sister from another mister, and promptly sent our pic to some rando. Luckily Crystal from Arizona was easy to find again to get the right number!
For those interested in helping to make sure we win this Presidential election and so many more important elections, level up your participation in Democracy. Volunteer to help remotely in many different elections — you can make a real difference! events.democrats.org
A finer send off in love and gratitude for a lifetime of public service couldn’t be had for our President @JoeBiden as he embraced our future president @KamalaHarris #dncconvention2024
I won’t have a floor pass as a Standing Platform Committee member, so you won’t see me with my delegation, but I’ll be there, way up in the gallery as history is made. I’m so excited! 🪷
We run a few IPv6 sensors in our newest @GreyNoiseIO fleet. We observed a sustained increase in IPv6 scanning on August 8th, and a large spike on August 15th to a IPv6 sensor "running" a PLC in the middle east. More info to come as we get it.
Chinese Backdoor Alert! Security enhancements on Mifare Classic cards used in hotels/business contain a supply chain backdoor making reading & exploitation trivial. Great paper by Philippe Teuwen Quarkslab eprint.iacr.org/2024/1275.pdf Watch your Chinese supply chains carefully folks!
Universal Basic Income isn't just a policy; it's a necessity. We can have a world where no one worries about their next meal or roof over their head. We have the abundance necessary to create that world. Our only scarcity is political will.
AI can’t be sued out of existence despite gross copyright infringement because there’s too much money invested to let a silly thing like the law to stop it. Silicon Valley formula: The market rewards fast winners with even more money to fight lawsuits, just like Eric Schmidt said
Article from the @verge in the posts below goes into more detail on the advice Eric Schmidt gave to Stanford, where he says the quiet parts out loud — just be successful enough to hire as many lawyers as you need to clean up the mess.
Eric Schmidt, asking not to be quoted, told budding entrepreneurs at Stanford to steal content in order to build startups quickly, and have lawyers “clean the mess up” later.
This is unfortunately advice lots of VCs give aspiring founders. They just usually don’t say it publicly.
I touched on an adjacent topic of software liability for security on the @lawfare podcast with Ben Wittes - investors who push irresponsible growth should be liable.
If you care about your friends, whether they seem vulnerable or not, do not touch or be unmasked around them when you or a household member are sick. If you get a healthy person sick, you’re still spreading sickness in the community & will eventually endanger a vulnerable person.
I won’t have a floor pass as a Standing Platform Committee member, so you won’t see me with my delegation, but I’ll be there, way up in the gallery as history is made. I’m so excited! 🪷
ICYMI Ben Wittes got me to admit hacksidents happen, discuss misaligned cybersecurity investments, & software liability that holds investors responsible for pushing irresponsible growth before cybersecurity on this @lawfare podcast. CrowdStrike process failures get a mention too.
“40% of in-the-wild 0-day flaws are variants of existing flaws, meaning they are similar to flaws already fixed. This could indicate vendors are rushing fixes as a result of time constraints. As a result, they are producing incomplete fixes & aren’t addressing the root cause”
The outsize & unaccountable power of tech companies/CEOs runs wider and deeper than the Musks of this world. It is a systemic problem that needs systemic answers to save democracy. My upcoming book The Tech Coup analyses the problem and offers solutions: thetechcoup.com
DEF CON thrives on community collaboration and has operated for over 30 years successfully working with hundreds of vendors including the dozens that have helped with our badges over the years.
For this year’s Raspberry Pi badges, DEF CON hired Entropic Engineering to do the hardware development and firmware. After going overbudget by more than 60%, several bad-faith charges, and with a product still in preproduction, DEF CON issued a stop work order. Any claims that DEF CON did not pay Entropic Engineering for its hardware or firmware development are false. Unfortunately, we heard that these issues with Entropic Engineering were not unique to DEF CON.
We decided at that point to finish the badge on our own. We paid to send engineers to Vietnam to work onsite to finalize and test the badges in order to ensure they would be done on time for the conference. We never removed Entropic Engineering’s logo from our badge, it is still on the PCB. However, Entropic was not involved in the design and production of the case, and we removed their logo we had added as a courtesy.
We were happy to still include one of their contractors on the badge panel session. Unfortunately, shortly before the talk was set to take place DEF CON became aware that unauthorized code had been included in the firmware we had paid Entropic Engineering to produce, claiming credit for the whole badge and promoting their coin wallet to solicit money from DEF CON attendees above and beyond what we had negotiated.
When asked about the unauthorized code, the engineer said it had been done as a “joke” two months ago and forgot to remove it, and we decided as an organization not to have him on stage while we kept the slides in the talk giving him credit for his work.
We communicated the change in advance of the talk, and this individual decided to show up for the panel anyway. He refused to leave, demanding that our security team remove him. Wanting to ensure that the other people involved in creating the badge were able to deliver their presentation, we complied with his wishes and escorted him off the stage, where he was free to continue attending the conference.
Any issues of non-payment are between him and Entropic Engineering, DEF CON fulfilled its financial obligations.
This is such an excellent thread on disinformation, who it truly endangers, journalistic integrity, and “both-sides” distortion that can affect election outcomes. All that, and it’s funny.
A little over two weeks ago, a user on Twitter posted a joke claiming, with a knowing wink, that J.D. Vance, the junior senator from Ohio and Trump’s running mate, had been quite intimate with an alluring chesterfield.
Disclaimer: The source of the following information is from various Reddit threads, Discord discussions, and Twitter conversations. We are unable to determine the validity of all of the information shared. Some information can be confirmed because there is physical evidence present.
The drama: earlier today (approx. 5 hours ago) security researcher Dmitry Grinberg (@dmitrygr) was escorted off the stage at DEFCON – making him one of the few individuals in convention history to be physically escorted off stage.
The contents of the badge (code base, etc) was developed by Dmitry Grinberg and Mr. Grinberg states he gave no permission to DEFCON to use his code base on the badge. He states he will be issuing a DMCA notice to DEFCON soon. Mr. Grinberg also stated on Reddit you can enable an easter-egg on the device by doing:
- FN - MENU - ABOUT - SELECT
When doing this the badge will display Dmitry Grinberg's information proving he is the developer. Additionally, Dmitry Grinberg said on Reddit if you'd like a license to use the firmware you can contact him and he will issue it to you. He will also sign badges for individuals and this will count as a license grant. He will be outside the DEFCON entrance at 10am tomorrow morning to sign badges.
Attachment 1. Dmitry Grinberg being escorted off stage Attachment 2. The easter-egg
We're aware of reports that access to Signal has been blocked in some countries. As a reminder, Signal's built-in censorship circumvention feature might be able to help if your connection is affected:
Signal Settings > Privacy > Advanced > Censorship circumvention (on)
Are you ready to play a game, @defcon? Our 1st Clue Hunt clue is ready for you. Winners get the challenge coin that screws into the custom badge completing a circuit and lighting it up. @evantobac and I can’t wait to meet the winners! The game starts now.
Our @socialproofsec@defcon Clue Hunt is starting tomorrow & it’s bigger than ever before! Our 1st clue & Keymasters will be at @sec_defcon starting Friday (you get the 1st clue in line) Teaser of prizes below — our challenge coin completes a circuit on our badge, lighting it up!
Sure this app can be terrible but it also has this night shift worker who found a kitten he definitely couldn’t keep, then he live tweeted feeding the kitten scrambled eggs and by the time his shift was over he had named the kitten and the kitten was sleeping in his beard
What a panel 🔥 @HiNicoleTisdale, @KembaWalden, Jake Braun, and Elizabeth Eigner at @defcon will issue an urgent call to action for cyber advocates. Join forces with policymakers to shape the future of vulnerable communities. #policyatdefcon32
Something I miss besides the friends in Vegas this week is the embracing of various facets of myself
🔹The founder & CEO talking with clients & partners 👩🏻💼 🔹The 25+ year industry veteran doing media interviews 👩🏻💻 🔹The hacker soldering her badge with her friends👩🏼🎤
New #defconnails for #defcon inspired by Jon Buckley's "High Tech Monopoly" with 2x hidden Mifare Classic magic chips and 2x NTAG+LED nail stickers that I designed. I used @flipper_net to clone my room key to the Mifare chip!
I have a total of four #nfcnails embedded in my nails this year for @defcon - 2x MiFare Classic 1K "magic chips" (writeable UID), and two of the #lednails *with* NTAG213 stickers that I designed!
This year is the 25th anniversary of my 1st DEFCON. I’ve missed a few & will be missing this year too, but I’m still (virtually) surrounded by the friends who convinced me to go & the friends I made there through the years. The hacker community is a wonder of the world. Have fun!
Okay, everyone, here it is. I know many of you have been curious to read my take on @sama's basic income pilot results for about two full weeks now. Here's my take.
Nick #RespiratorsFilterAllPathogens😷 Anderegg@NickAnderegg
Here is the entire thread about "SARS-CoV-2 Rapidly Infects Peripheral Sensory and Autonomic Neurons, Contributing to Central Nervous System Neuroinvasion before Viremia" on a single page: readwise.io/reader/shared/01j3y92awcc53tx09s5yrysfgj
Microsoft once again with deeper technical analysis plus actionable guidance around the CrowdStrike outage.
In this post you can find: - detailed crash analysis - kernel vs user space tradeoffs - tools for driver devs - best practices for security & reliability
“it might be time for librarians to go rogue. The @internetarchive , an independent digital lending library, makes banned books available for online checkout — it even has a special collections page with the latest challenged titles, for easy access” - @Annaleen for @PostOpinions
If your motivation to using a platform is to prevent disclosure I promise a security researcher who’s primary motivation is disclosure a threat of a platform ban will do absolutely nothing to prevent that anyway
Even if you have a bug bounty program please consider also accepting email submissions of vulnerabilities, I completely get the problem with spam AND wanting that triage service you pay for, but please don’t forget that not everyone wants to sign up to the terms of a BB platform
Without notice, X has opted all users into training its "Grok" AI Model. To turn off this setting and stop your "posts, interactions, inputs, and results" from being used for training and fine-tuning Grok, visit x.com/settings/grok_settings and uncheck the checkbox.
We are deeply disappointed the State Supreme Court has allowed tech corporations to buy their way out of basic labor laws despite #prop22's inconsistencies with our state constitution. Our statement on today's chilling decision⬇️
The last CSRB report slammed Microsoft for “lack of security culture” yet when this CrowdStrike outage happened, Microsoft came out with the first & best communication & remediation. Muscle memory incident response at scale is one of Microsoft’s hard-earned security strengths. 💪🏼
The vulnerability, named PKfail, is related to an exposed American Megatrends International (AMI) Platform Key (PK), which is a Secure Boot private key. The exposed PK was a default key provided by AMI and it was not supposed to be used in production.
However, several major computer manufacturers failed to change the PK and shipped many devices with the untrusted key.
With this key, which was exposed in a recent data leak, attackers with access to a device affected by PKfail can sign malicious code and bypass Secure Boot. This can enable them to deliver UEFI bootkits, such as BlackLotus.
Ah, but it's from the same OOB bug! Here, the OOB read happen to "succeed" returning a (random) "valid" addr. that could be de-ref'd, but whose value was 0x0.
...then passed to sub_4124 (in R8) mov'd into R12, added to an offset (RDX/0), and then de-ref'd crashing w/ NULL ptr.
Ah, but it's from the same OOB bug! Here, the OOB read happen to "succeed" returning a (random) "valid" addr. that could be de-ref'd, but whose value was 0x0.
...then passed to sub_4124 (in R8) mov'd into R12, added to an offset (RDX/0), and then de-ref'd crashing w/ NULL ptr.
No surprises here, but @CrowdStrike confirms @taviso's analysis, that the bug was indeed not due to a NULL-pointer deference 🧠 ...but rather "an out-of-bounds memory read"
This strange tweet got >25k retweets. The author sounds confident, and he uses lots of hex and jargon. There are red flags though... like what's up with the DEI stuff, and who says "stack trace dump"? Let's take a closer look... 🧵1/n
The Crowdstrike Preliminary Incident Report concurs. CrowdStrike is going to have to allow for staged rollouts of anything that pushes changes to hosts, not just code. Customers must be given granular control of content updates to stage their own rollouts. www.crowdstrike.com/falcon-content-update-remediation-and…
Recovery from Crowdstrike should be layered to prevent recurrence of an outage of this magnitude, but it won’t be pretty. Today is just the beginning. 1. Fix affected hosts (customers do a lot of manual work done once) 2. Fix CrowdStrike (& all security software) content update rollout to deploy in stages (vendor work done once across many vendors) 3. Fix IT practices to not automatically apply content updates but test just like software updates (customer work done everyday, forever)
On Monday, @bcantrill and I were joined by @k8em0 to discuss the largest global IT outage in history. It was an event as broadly impactful as it will be instructive. As Bryan noted, you can see all of computing from here, from crash dumps to antitrust.
Remember when Solarwinds was discovered by Mandiant 4 months after attackers gained access & how Congress lavished praise on them for their transparency? I wonder how Crowdstrike’s Congressional hearing on its mistake will be received. Why are some longer mistakes met with grace?
The CrowdStrike BSOD fiasco is extraordinary in its scale and scope; on Monday's Oxide and Friends, @ahl and I will be joined by security researcher and @LutaSecurity CEO @k8em0 to help us sort through the many layers of this mess. Join us, 5p Pacific! discord.gg/QrcKGTTPrF?event=1263954070763212810
“8.5 million Windows devices, or <1% of Windows machines. While the % was small, the broad economic & societal impacts reflect the use of CrowdStrike by enterprises that run critical services”
If this is what a <1% Windows ecosystem DoS does, we’re going to need a bigger boat.
I worked as a Linux distro dev 25 years ago. We tried migrating the whole company to our OS, but our core business functions like sales & HR could not work so we switched them all back. Even if you migrated only servers, business users would still be on Windows. Stop fantasizing.
I smell a CSRB investigation knock knock knocking on CrowdStrike’s door. This is ostensibly what the executive order that created CSRB meant it to investigate. One could argue this wasn’t due to an attack, however it was a vulnerability that caused the biggest DoS in history.
Log4j wasn’t an attack either, but an opportunity to improve industry response. There is much to learn from & improve across vendors that provide security content updates, as well as IT practices. If it’s not the topic of the next CSRB investigation, I would be curious as to why.
The CrowdStrike BSOD fiasco is extraordinary in its scale and scope; on Monday's Oxide and Friends, @ahl and I will be joined by security researcher and @LutaSecurity CEO @k8em0 to help us sort through the many layers of this mess. Join us, 5p Pacific! discord.gg/QrcKGTTPrF?event=1263954070763212810
Recovery from Crowdstrike should be layered to prevent recurrence of an outage of this magnitude, but it won’t be pretty. Today is just the beginning. 1. Fix affected hosts (customers do a lot of manual work done once) 2. Fix CrowdStrike (& all security software) content update rollout to deploy in stages (vendor work done once across many vendors) 3. Fix IT practices to not automatically apply content updates but test just like software updates (customer work done everyday, forever)
On the CrowdStrike outage: Most organizations of a certain size test software updates before deployment. They do not test “content updates” from OS or security software, but set them to automatically update because they are viewed as safe. IT departments just got a new daily task
We are currently in one of the largest global IT outages in history. Remember: verify people are who they say they are before taking sensitive actions. Criminals will attempt to use this IT outage to pretend to be IT to you or you to IT to steal access, passwords, codes, etc.
Exclusive: Kaspersky Lab is closing its US division and laying off all workers associated with it. The move follows the US Commerce Department's decision last month to ban the sale of Kaspersky software in US starting July 20. www.zetter-zeroday.com/kaspersky-lab-closing-u-s-division…
If you had opinions about bug brokers, wait till you play Breach Broker Bingo: 🎲 “Reddington has facilitated a number of negotiations between the hackers and victims of the Snowflake account breaches. He says Binns asked him to contact AT&T “to facilitate a buyback of the data”
AT&T paid hackers $370,000 to delete call records stolen from its Snowflake account. They provided video to AT&T showing deletion. It's believed to be the only complete set of the data stolen, though the hackers shared small snippets with a few people www.wired.com/story/atandt-paid-hacker-300000-to-delete-s…
25 years ago I went to my first #defcon & watched my friends cavort on stage for the release of BO2k. Afterwards there was a press conference. It was super surreal to see my BBS/irc buddies famous to mainstream media. I still felt like we were all just messing around in basements
1999: Cult of the Dead Cow (cDc) member DilDog debuted the program Back Orifice 2000 (BO2k) at DEF CON 7. It was the successor to Back Orifice, released by cDc a year prior. DilDog proclaimed it "a remote administration tool for corporate America". 🤣🤔
The Three Buddy Problem podcast Episode 3: Former NSA computer scientist Dave Aitel (Immunity Inc., Cordyceps Systems) joins Juan Andres Guerrero-Saade for a frank discussion on the OpenSSH unauthenticated remote code execution vulnerability and the challenges around patching and exploitation, the CISA 'secure-by-design' pledge and its impact on software vendor practices, Microsoft lobbying and the CSRB report, and changing face of government's attempts at cybersecurity regulations.
We discuss the disruption caused by political changes and the potential implications for cybersecurity policies, impact from the Supreme Court Chevron ruling, security regulations and the challenges of writing laws for future technology, the role of CISA and its accomplishments, the debate around offensive cyber operations and the responsibility of companies like Google in addressing vulnerabilities.
The need for clear separation between counterterrorism and espionage operations is highlighted, as well as the importance of understanding both defensive and offensive perspectives.
For the 4th year, we're going on summer break - every employee is on mandatory PTO starting TODAY. Services will continue to operate. A skeleton crew will be on call for emergencies.
If y'all need us over the next week, you'll have to ask @Andrew___Morris, jk don't do that, you'll just have to wait til July 8th. ✌️
This OpenSSH RCE advisory is a classic example of hacker craftsmanship, generosity of spirit, & community contribution - a regression of duke’s 2006 vuln, inspiration from @lcamtuf’s 2001 paper, etc. The legacy of @Qualys’ hacker founder @philpraxis continues! 🫡 #hackerhistory
The award-winning Qualys Threat Research Unit (TRU) has discovered a critical vulnerability in OpenSSH, designated CVE-2024-6387 and aptly named "regreSSHion." This Remote Code Execution bug grants full root access, posing a significant exploitation risk. blog.qualys.com/vulnerabilities-threat-research/2024/07/0…
Regarding the SSH bug 1) First OpenSSH vuln discovered in almost 20 years - wow 2) Bug was (re)introduced almost 4 years ago. So remote root in OpenSSH for 4 years and nobody found it? 3) Exploit takes hours/days to run. Watch your logs!
Fresh results from yet another successful basic income pilot. This time in Baltimore where 200 young parents received $1,000/mo. After one year compared to control:
We also need to look at the mountain of evidence in support of unconditional basic income instead of just one pilot. That's why I have an ongoing thread for pilot after pilot. If you're forming an opinion about UBI on any one pilot, you're doing it wrong.
Looking forward to watching @POTUS@JoeBiden beat DJT at the debate once again. President Biden is moving us forward, fighting to restore our rights, not threatening to take more away. We need to reelect the President who fights for all Americans, not the one who fights Democracy
Excellent bug bounty case study: 1. The difference between seeking a bug bounty & extortion can be spotted in how much is stolen, & whether it is promptly returned if it was money or destroyed if it was data. 2. Bug bounties aren’t contract pay negotiations. 3. Efficient technical & communication response is evidence of a mature program, one that is self-managed without a bug bounty platform
On June 9 2024, we received a Bug Bounty program alert from a security researcher. No specifics were initially disclosed, but their email claimed to find an “extremely critical” bug that allowed them to artificially inflate their balance on our platform.
The cost to run a company that has all the right cyber security tools and staff is absolutely obscene. It’s hard to describe the numbers I’ve seen. Even saying this is a gray area. But it is incredible headcount and spend. Non-keystone companies have no chance in normal paradigm.
Hi Friends, If you get a direct message from someone claiming to be a @GitHub representative wanting to sponsor your content, and it’s not from an official account or someone you recognize as a GitHub employee, it’s likely a scam. Please report it. 💜
Hackers who stole Ticketmaster data from Snowflake account appears to have accessed data through a contractor named EPAM Systems. EPAM has workers in Belarus, Ukraine and, before war, Russia. Hacker told me they breached an EPAM worker in Ukraine. www.wired.com/story/epam-snowflake-ticketmaster-breach-sh…
Alex Stamos and Renee DiResta's Stanford Internet Observatory is collapsing under political pressure, the largest setback so far for realtime disinformation research. Free gift version at no expense: www.washingtonpost.com/technology/2024/06/14/stanford-int…
I opened my speech with the fact I didn’t finish high school or college but still found myself delivering the Commencement address at @ISTatPENNSTATE We the uncredentialed can hack ourselves careers & those of us who do can contribute great things. Don’t use degrees as filters.
Full text & link to the video of my Penn State IST Commencement speech — don’t discount people or yourself who got a GED & went to college but didn’t finish. An unpaved road without a map doesn’t mean you’re forever lost, it makes you a formidable explorer www.lutasecurity.com/post/penn-state-ist-commencement-bri…
"The 'American dream' has taught us to believe that we’ll prosper if we’re good enough. That’s simply not true anymore, and it really never was. I can understand this intellectually, but hope springs eternal."
Thoughts on @timoreilly ‘s piece about VC market distortions in rideshare & AI — also in bug bounties. “a dark pattern, a map to suboptimal outcomes rather than the true path to competition, innovation, & the creation of robust companies & markets” www.linkedin.com/posts/kmoussouris_ai-has-an-uber-problem…
Attending @randomdross funeral yesterday was one of the saddest days in recent memory, not just because of feeling the loss of an old, kind, brilliant colleague, but in seeing his family who now have to move through the world without him. Hearing stories from friends & family reminded me of the preciousness of the little moments, the inside jokes, all the bits & bobs that add up to a life well lived. The ripples of David’s beautiful life will live on for a very long time.
Even if you didn’t have the great luck to know him, know this: David Ross left the world better for having him in it. He will be remembered for his brilliance & kindness. If we each could be remembered half as fondly as Dave, we’d know we lived a great life & did marvelous things.
In his honor, & in the honor of everyone we’ve ever lost, we should live the best life we can in the time we have. They live on in us just as we will live on in the hearts of our loved ones when it’s our time to return our energy to the universe.
David bootstrapped my career by giving me a chance to present in BlueHat, which was my first trip alone outside Mexico and also my first English presentation.
Not a lot of people know this, but David was the one that named XSS during his time at MSFT.
In case anyone missed this, yesterday Alex Hannold pointed out that there is a very real possibility that TeamUSA climber Sam Watson will compete in Paris 2024 as the fastest Olympian ever. In any sport. At any time. In world history.
🚨 Last chance to apply! The WISP Scholarship for Hacker Summer Camp in Las Vegas closes on June 7th. Don't miss out on this opportunity to attend top security and privacy conferences with free tix, travel stipend, and team for support on site 🌟 docs.google.com/forms/d/e/1FAIpQLSdXJHtVFUkNJWXAXpBG7RDKZ…
Imagine what a wonderful world we could have if people could focus on doing what they love instead of fighting biased people & systems. We are all worse off when energy must be diverted from creativity into fighting injustice. One of the many reasons to fight inequity together.
I am not OK. I am not OK at all. This is very emotionally painful, stressful, time-consuming. I hate every aspect of what I am experiencing right now. I hate that I have to deal with this when I could be focusing on my job and things that I am passionate about.
When presented with these risks prior to passing the final text of the CRA, EU regulators responded with unfortunate lack of nuanced understanding: - No exploits or tech details required, just a high level description of the bug & which software/component it affects - We think this will make companies patch faster
They failed to recognize:
- lack of specificity on threshold requiring reporting places an inordinate distraction tax on security response teams already struggling to keep up with highest priority issues - even non detailed information is enough to make discovery & exploitation of adjacent bugs likely - faster doesn’t mean better especially if the fastest is disabling functionality or deeply degrading performance - fast patch availability doesn’t mean rapid uptake by affected users or prevention of widespread disastrous exploitation - bugs in WannaCry were bugs with patches previously available for months
Required reporting of vulns after confirmed exploitation creates an interesting counterintel problem. First, a database of those confirmed exploits would be a persistent collection target, as they would illuminate which campaigns are being detected, by whom, and when 1/
On the Chinese requirement to alert the government in addition to reporting vulnerabilities to the affected vendor —
There is now in fact a similar law passed in Europe expected to take effect in less than two years under the Cyber Resilience Act (CRA) that requires companies to disclose new vulnerabilities in their own products to all affected EU governments within 24 hours of confirming malicious exploitation.
This is dangerous government FOMO, one that I fear will infect all governments, something I warned against years ago, but seems to be coming at us all faster than we can stop it.
It’s vulnerability disclosure climate change and we’re likely past the point of no return and subsequent uninhabitability of the planet.
My analysis of that translation is here. Importantly, regulators argue that cybersecurity is impossible to achieve “behind closed doors” and that an “open system” is required. Next up? Incident reporting requirements.
On the Chinese requirement to alert the government in addition to reporting vulnerabilities to the affected vendor —
There is now in fact a similar law passed in Europe expected to take effect in less than two years under the Cyber Resilience Act (CRA) that requires companies to disclose new vulnerabilities in their own products to all affected EU governments within 24 hours of confirming malicious exploitation.
This is dangerous government FOMO, one that I fear will infect all governments, something I warned against years ago, but seems to be coming at us all faster than we can stop it.
It’s vulnerability disclosure climate change and we’re likely past the point of no return and subsequent uninhabitability of the planet.
I need to explain how AI text to sound effect can be used by criminals to make their kidnapping or bail-related scams believable. In the wild, we’re seeing “female scream” or “young boy screaming specific name” used in AI voice cloning phone attacks with phone number spoofing 🧵
Text to Sound Effects is here. Our newest AI Audio model generates sound effects, short instrumental tracks, soundscapes, and a wide variety of character voices, all from a text prompt. Available now for all users.
Everyone from content creators, video game developers, to film and television studios, uses sound effects to create rich and immersive content. Now, in addition to AI voiceovers, you can generate all of the sounds you need with just a prompt.
Everything you hear in this video was generated by ElevenLabs sound and voice models. In this thread, we shared some additional clips that help show off the range of this new model.
Y’all can read about this absolutely distressing situation of me trying to buy a home + learning that the seller didn’t want to sell to me because I’m Black, in @nytimes. Thank you @debra_kamin for your hard work investigating this + educating people about the Fair Housing Act 1/
My real estate agent's BROKER just called me at 9pm on a Friday to tell me that the seller doesn't want to sell a house to me because I am BLACK. This is after the inspection, contract agreement, down payment. Baby, I'm either buying your house or buying YOUR BLOCK. CHOOSE ONE.
When we advise on bug bounty policy, we outline the risks of advertising bounty exclusion grace periods for known CVEs. Any bounty exclusion lowers the chance of receiving a bug report. For severe exploitable issues, do you want to wait 30 days to learn you missed some patches?
It’s a choice to be weighed individually based on circumstances, not based on a blanket exclusion policy. A good reason for paying out on known CVEs before 30 days is whether you changed your scanning frequency to catch them yourself faster. Pay for the process bug in that case.
1st - An individual program’s bounty ineligible grace periods for known CVEs are risky but reasonable if there are reasons like regulatory testing requirements 2nd - Blanket 30 day exclusions are not ok because that creates a perverse incentive to hold severe exploitable findings
Thank you @k8em0 for matching my $500 donation to send the 1st underrepresented scholar to @defcon@BlackHatEvents@_squadcon@DianaInitiative!! Bill (@awpiii) then donated to bring another scholar to Hacker Summer Camp - thank you! Who’s matching Bill for scholarship #2?
I just matched @RachelTobac ‘s $500 donation to help an underrepresented person attend @defcon & @BlackHatEvents via a @wisporg scholarship - I donated in memory of Becky Bace, who everyone should know. Who will sponsor the next underrepresented person to attend?
This scholarship enabled many underrepresented folks to meet their first friend group in security, find their next boss, change jobs, learn new hands on skill sets and more. Please match my $500 donation here! We want to send at least 20 scholars! wisporg.app.neoncrm.com/forms/hackersummercamp24
My latest for @wired. How researchers hacked time to crack an 11-year-old password protecting $3 million in cryptocurrency. They found a significant flaw in RoboForm's password manager that made its pseudo-random-number generator not so random www.wired.com/story/roboform-password-3-million-dollar-cr…
One more reason we include Communication in the @LutaSecurity Maturity Model for Vulnerability Coordination. It’s an important indicator of measurable security maturity, along side engineering & Organizational maturity. What good are patches that aren’t known to affected users?
Note that @roboform learned of this problem in 2015 and appears to have fixed it in subsequent versions. But the company never told customers about it or urged them to create new passwords. RoboForm also won't say what exactly it did to fix the problem so the fix can be verified
This was a super fun project and a reminder about the lasting effects of security problems long after they're patched. www.youtube.com/watch?v=o5IySpAkThg
me and @jotunvillur were on @sherrod_im's Microsoft Threat Intel podcast and we had a lot of fun!!! We were lucky enough to be the first external guests on the pod. Thanks @MsftSecIntel!
A universal basic income is philosophically grounded in justice (recompense for lost commons), freedom (economic freedom to make choices), and security (an anchor against uncertainty). It's an affordable necessity to reduce poverty and inequalities that could become explosive.
When Symantec acquired AtStake in 2004 it also acquired L0phtCrack which had been acquired previously from @L0phtHeavyInd. Symantec discontinued selling it about 6 months after the acquisition.
Fun fact: Norton Antivirus later flagged L0phtCrack as malicious software.
Kudos to @alexsotirov co-created the Pwnies with me. Quiet heroes in the early years: @hdmoore, @tqbf, and @__daveg__ for writing some amazing nominee descriptions. @halvarflake, @mdowd for being early judges. The NYC hacker scene for helping hand paint the awards every year…
🚨 Exciting news! 🚨 The Pwnie Awards are trotting to DEF CON this year! 🐎 After over 15 fantastic years with Black Hat, we’re saddling up for new adventures. Huge thanks to Black Hat for their stable support. DEF CON, the mane stage for hackers, awaits us this August!
Counterpoint Commencement speech, from me, who has fully leaned in to my identity as an entrepreneur, change agent, pioneer, expert, hacker, AND mother:
#cyberuk24 is almost here! Subscribe to our CYBERUK ONLINE YouTube channel to join the conversation and gain access to all open content live sessions, interviews and more! Subscribe now👇 youtube.com/@CYBERUKONLINE
Its Day 0 - today you can collect your badges and attend tonight's Welcome Drinks for the perfect opportunity to network with your peers, meet our sponsors and hear from cyber industry figures ahead of #cyberuk24.
Women in infosec..I know salary discussion can be uncomfortable but you need to ask your male counterparts what they are making. The amount of women I've known over the years who were being SERIOUSLY underpaid (we're talking like by $50k a year) is disgusting.
I’m wondering if it’s inevitable to have fake porn based on public photos. Or will only femmes be targeted? Maybe we should all get fake porn dates. Like prom dates but allies who agree to release fake porn of themselves if we get hit. Who will you ask to go to porn with you?
Mother’s Day is a celebration of choice for me. I chose motherhood. Here’s to the mothers & to the childfree by choice people out there. May we all preserve our human rights & bodily autonomy. #happymothersday
Now that rideshare & food delivery are being held to living wage Labor laws in some cities, do we think it was worth it to let them get away with flaunting those laws for so long to build up their businesses? What could we have instead if we made them build a fair wage biz model?
Those of you picking “they wouldn’t exist” — you don’t think it’s possible to build a business unless you break labor laws? That’s what the captains of industry said when labor laws were passed, yet we have more profitable businesses than ever that follow those laws. Explain this
Lots of wins in the past couple weeks. Glad to see a bunch of friends at #rsac — even when it was just a drive by. I’ll post pics later. I wasn’t as social as I could’ve been & sorry to miss people
I was honored to give the Commencement Address for the Penn State College of Information Sciences and Technology Class of 2024. @ISTatPENNSTATE This was truly one of the best experiences of my life.
Society has tricked us into believing the grind is the goal. The endless hustle? It's not the pinnacle of human achievement. Imagine a world where our worth isn't measured by our exhaustion level but by the purposeful work we pursue.
From an impressive 92% implementation of the 1st phase of the National Cybersecurity Strategy to the publication of the 2nd phase of the plan, it’s great to see hard work of so many dedicated people in this report. This living document is key to our national security resilience.
White House Office of the National Cyber Director@ONCD
Today we also published the second phase of the National Cybersecurity Strategy Implementation Plan which outlines 31 new initiatives the Federal Government will take on to secure the full benefits of a safe and secure digital ecosystem for all Americans. www.whitehouse.gov/oncd/briefing-room/2024/05/07/fact-she…
No hyperbole when I say that Morgan has done more for NSA cybersecurity connectivity with the industry powerhouses than anyone, ever. That translated into better security outcomes for us all. Well done Morgan! You’ve put the Cybersecurity Collaboration Center on a great path!
🥳And just like that it’s time for a new chapter. Look forward to seeing so many @NSACyber friends and partners next week at #rsac—-dont worry, I’m not going far! Still 1️⃣ Fan of the CCC 🥰
We partnered with @FBI on the latest Secure by Design Alert on directory traversal exploits. We urge manufacturers to fully implement the principles and practices touched upon in this alert: go.dhs.gov/3ke#securebydesign
"Pledging companies will self-assess and self-report," @k8em0 said, "so only time will tell if they’ve effectively applied the measures and if the pledge proved to be an effective accountability mechanism."
QCSuper "a tool communicating with Qualcomm-based phones and modems, allowing to capture raw 2G/3G/4G(and for certain models 5G) radio frames, among other things." github.com/P1sec/QCSuper
High school may be over, but I will take any excuse to dance! That's why I tagged along with some friends to prom. Had to stick with a red theme to match my new hair ❤️
This definition is wrong. Coordinated Vulnerability Disclosure isn’t waiting for a patch. It’s coordinating disclosure of the details, regardless of patch. Waiting for a patch is ideal unless it puts users at more risk for being in the dark especially if exploitation is happening
I changed how Microsoft discussed vuln disclosure going from responsible to coordinated & wrote their first vuln disclosure policy that explained how Microsoft would act when it was the vendor, coordinator, or finder. You see, sometimes even Microsoft would have to drop 0day.
Anyway the research the quoted thread was about seems both cool & a great example of real Coordinated Vuln Disclosure: partial disclosure at a conference before a patch was available was communicated to the vendor. Old rules would have counted partial disclosure as irresponsible.
It's the @DecipherSec Memory Safe episode you didn't know you wanted, but here it is anyway. @LindseyOD123 grilling me. Shoutouts to @window, @k8em0, @RSnake and many others in here. Super fun.
Watch this quick look video from speaker @k8em0 for a preview of what's to come in her #rsac 2024 session celebrating 10 years of Microsoft's bug bounty program and sharing lessons, stories, and recommendations
So I changed my pronouns in my profile to temporarily hide the blue check, but I’m not going to keep doing it every time they put it back. I am however reminded that once my kid called me mom-ra & they meant like she-ra but I instantly thought it was like mum-ra from Thundercats.
The blue check of no consent is back and cannot be hidden. Funny how it doesn’t even come with the ability to hide ads. I’d have to pay for that & I will not pay for this site.
My curse is the unending ill-informed Dunning-Kruger replies about how universal basic income will just cause inflation and negate its own value. This assumption is based on an ignorance of UBI's net cost vs gross cost, and also the learned helplessness of a hope-starved society.
At @LutaSecurity we believe in worker’s rights — so much so that when we create end-to-end managed bug bounty programs, we offer clients the ability to hire any of our staff (contractors or FTEs) to continue as FTEs at the client seamlessly at the end of our service. No waiting period. Capitalism does not have to harm workers while still providing the best services.
Assembly is cool and everything, but ultimately it’s an abstraction. We should emphasize teaching high level theoretical models of computing for the vibes and then everyone can choose which individual technical applications are relevant to their profession/interests
Dismantling myths about Universal Basic Income one fact at a time:
UBI isn't about giving money to do nothing. It's about money to do ANYTHING. This is in stark contrast to traditional welfare benefits that require people keep their incomes sufficiently low to keep getting it.
Them: Get a technical cofounder Me: I’m a hacker, former Linux dev, sysadmin, professional pen tester Them: Get good customers Me: Bags Zoom, Facebook, UK Gov as clients Them: Show growth Me: Shows profits Them: You’re a “lifestyle” company
The AI market is such a drunken bar fight right now. So chaotic, and unpredictable. Total chaos. Fascinating to watch, but it's best to stay on the sidelines unless you *really* like Vodka or really like super chaotic drunken brawls with flying barstools.
You can find my analysis of this paper here. TLDR it appears as if GPT4 is using public exploits for most of these CVEs. But until they publish their code, data and results we cannot be sure. Regardless there is likely no emergent AI capability here.
LLM Agents can Autonomously Exploit One-day Vulnerabilities
GPT-4 can autonomously exploit 87% of real-world one-day vulnerabilities, identified in a dataset of critical severity CVEs, compared to 0% for all other tested models arxiv.org/abs/2404.08144
“the extra $500 helped recipients find more work with better benefits, increase their wages and grow their savings. Employment among respondents jumped from 37% to 66% by the end of the program”
Honored to be presenting the commencement address for the graduating class of 2024 at Penn State College of Information Sciences and Technology on May 4.
It’s as manipulative as those reels where people deliberately mispronounce something or make a bunch of gross slop on a kitchen counter - just to get people to comment. It may not have started that way, but you’ve all handily morphed it into a marketing coup.
And if you argue that the negative attention is bad for them, you’re in a hacker-positive echo chamber. The word hacker has been twisted by media to mean criminal for decades.
You’re amplifying their message to their target buyer who doesn’t know any better.
“The level of cybercrime has risen to the point where it feels overwhelming. And every year it gets worse. And it feels like as defenders, it's almost like we're winning every battle and losing the war,” says Allison Nixon, a cybersecurity researcher. www.cbsnews.com/news/cybersecurity-investigators-worry-ra…
Universal Basic Income doesn't subsidize any one activity. It subsidizes ALL possible activities, which doesn't create an incentive for any one activity.
This is in contrast to a program like unemployment income, which subsidizes unemployment. Remaining unemployed is the condition to get and keep getting an unemployment check. UBI has no such condition.
With unemployment income, you can get $1k and if a job offers you $1k, you'll lose the $1k and end up with $1k. That's equivalent to a 100% marginal tax rate or working the job for no pay.
Where is the incentive to take a job if you don't increase your income because of working, unless it's work you really love?
With welfare benefits in general, you must have a low income and keep it low to keep getting it. That discourages recipients from increasing their income.
With UBI, you can get $1k and if a job offers you $1k, end up with $2k. That doubles your income. That is a good incentive to take a job to double your income.
Unlike welfare, UBI does not punish work. With UBI, everyone getting a paycheck has more total income than anyone with only UBI, because their paychecks are additional instead of either/or.
Do you understand the difference now between welfare and UBI and how UBI does not create an incentive to not work as welfare does?
Does it make sense now why pilot after pilot shows that employment INCREASES among those who receive UBI?
UBI makes work actually pay.
UBI also supports all unpaid work and boosts the incomes of those doing underpaid work.
So, will UBI make people lazy? Of course not. Now stop being so lazy and go learn about all the results of UBI experiments. Go through my 100-tweet pinned thread.
Serious question: at which point do we all, as an industry, finally agree that no Internet-facing middlebox that aggregates and intermediates SSL/TLS traffic is an acceptable approach to implementing a security capability?
We are delighted to offer the 2nd in our series of Alperovitch Advanced Workshops – Introduction to Arm Assembly & Exploitation, taught by Maria Markstedter (@Fox0x01).
@SAISHopkins students, apply by Friday, April 12 👇
The person telling you not to take moments to experience unbridled joy are not your friend or ally or more genuine in devotion. They are acting on a failed theory of what a human is.
It was legit darker an hour before the eclipse peak in Seattle because of the rain 🌧️ Oh Seattle 😂 (Before anyone wants to inform me that we were not in the totality path, honey I know shhh I know.)
This is the vulnerability that started the discussion of open source risk to commercial software. It eventually led to SBOMs and more vendor transparency.
2014: The Heartbleed Bug was publicly disclosed. The buffer over-read vulnerability had been discovered by Neel Mehta and later privately reported to the OpenSSL project, which patched it the next day. The vulnerability was inadvertently introduced into OpenSSL 2 years prior.
I’m honestly surprised it’s that many pen testing jobs. For 25+ years that work has been around the same cost & pay with few career growth opportunities. From automated scanners to bug bounties, orgs have sought to replace the art of pen testing with less expensive alternatives.
It’s the Shmoocon #firetalk so good we decided to make @RayRedacted a judge next year. Watch the talk, then scroll up in the quoted thread to get an update on some hard-earned progress.
Lol @ the idea that “even a 5 person company” wouldn’t find these reporting requirements burdensome & therefore it should apply to orgs of any size. Small orgs already have each team member wearing too many hats. It would be more helpful to mandate & fund assistance to small orgs
If you've found a blue check next your profile, you can hide it here: x.com/settings/profile_customization. Thanks @mmitchell_ai. I might un-hide it if it ever means something other than being an Elmo fanboy, but hiding for now.
I have observed a 1:25 correlation with a LinkedIn post and spam messages immediately afterwards. People wonder why I never post there. Makes this site seem almost tolerable by comparison, now that I’m shadow-banned here. That’s truly saying something.
Regarding the XZ backdoor, opensource dependencies, & unpaid maintenance: #basicincome is the most effective way to save us all from this & other unforeseen calamities. Unpaid labor holds up society, be it caretaking children, elderly, the disabled, or that essential code library
Happy Easter, everyone! Did you know that on Easter Sunday in 2020, the Pope himself expressed his support for Universal Basic Income? His support is grounded in recognizing unpaid care work and empowering all workers with the power to refuse low wages.
xz is a crushing microcosm of the toxic entitlement of users of open source projects who make demands but offer no assistance. And when assistance does come, it’s desperately appreciated.
After 6.5 year, today was my last day at Google. What a chapter it's been. From Android Security to Project Zero to TAG, I've had opportunities to tackle technically challenging and meaningful projects & work with the best people along the way.
New report from our Threat Analysis Group + @Mandiant observed 97 zero-day vulnerabilities exploited in the wild in 2023, up 50% from 2022. Good news: investments are making a difference - vulnerabilities once common are virtually non-existent today. blog.google/technology/safety-security/a-review-of-zero-d…
In a race towards the future, we often overlook the simplest solution that could change everything: Unconditional Basic Income. Imagine a foundation so solid that every dream has a launching pad, not just the ones birthed from privilege.
So I bet that’s also why it now goes to incognito mode when I click an address. I used to find that new inconvenience annoying but now that I get that it has a broader #privacy purpose, I appreciate it. Thank you to those inside Google who did the hard work to push good changes.
Google didn’t get enough credit for this in December, so I just want to call out that they’re planning to end-to-end encrypt Maps’ location data, which will close off a lot of geofence warrants they receive. news.bloomberglaw.com/privacy-and-data-security/googles-l…
Confirmed! Valentina Palmiotti (@chompie1337) with IBM X-Force used an Improper Update of Reference Count bug to escalate privileges on Windows 11. She nailed her first #pwn2own event and walks away with $15,000 and 3 Master of Pwn points.
Wow!! Thank you ALL for so much support on my first #pwn2own win!! I’m very lucky to have a team and leadership that believes in me. I’m really proud of this bug; this is one of hardest exploits I’ve ever written. I can’t wait to share the details with you once it’s patched!
ICYMI: I published this late last night. Note that Apple added a fix for this in its M3 chips released in Oct. But developers were not told about the fix in Oct so they could enable it; Apple added an instruction to its developer site on how to enable the fix only yesterday.
People have been jumping to conclusions about the vulnerability in the Apple chips that lets hackers steal cryptographic keys, so I dug into it, to try to explain more clearly what the issue is and the implications of it: www.zetter-zeroday.com/apple-chips/
Since being shadow banned on here for what I can only assume was refusing to pay for long tweets and a blue check, it’s been rather peaceful. I don’t even show up in the timelines of most people who follow me. I can say absolutely anything. I’m free as a bird if they were real🐦
Use a loaner that gets wiped down to the BIOS every time AND is not allowed to connect to your network. Don’t fight if they kidnap you & try to count the turns from the trunk.
⬆️: REAL guidance given to us at MS
My addition: Unsubscribe from all internal DLs with sensitive info
The United States will never have a federal privacy law. Because it would include abortion protections which is based on privacy. You won’t have a privacy protection law because they want to control your bodily autonomy.
If the US is serious about protecting people’s data from ending up in the hands of foreign adversaries, Congress should toss out the TikTok ban and instead pass comprehensive data privacy legislation to prevent the collection of data in the first place. www.eff.org/deeplinks/2024/03/congress-should-give-uncons…
Pronouns: she/her/she-hulk/she-ra Height: depends on hulk on/off Shoe size: see height Smoke: emitted from the ears when provoked Tattoos: does turning green count? Piercings: your ears when I roar Favorite Color: black Favorite Drink: water, nitro cold brew, tears of patriarchs
“Stephanie Hendon, 34, was living in a shelter with her four kids while working long hours, but within a year of the program, she secured a three-bedroom apartment, purchased a new car, bought clothes for her children, and locked in a new job.”
Fresh results from another basic income pilot. This one took place in San Antonio, Texas where 1,000 people got a $1,908 payment in Dec 2020, followed by 8 quarterly $400 payments between Apr 2021 and Jan 2023.
What happened?
Incomes from work went up.
The biggest increased employment impact was observed in those with the lowest incomes to start (<50% FPL). The biggest educational investments occurred in those with the highest incomes to start (>100% FPL).
Nearly 40% of participants said they spent more time with loved ones and became more involved with their communities.
Many said the money was critical for their daily survival and allowed them to cover expenses they otherwise couldn't afford.
For participants with families, many said their extra income went to enrolling their children in after-school and extracurricular activities and supporting their educations.
Stephanie Hendon, 34, was living in a shelter with her four kids while working long hours, but within a year of the program, she secured a three-bedroom apartment, purchased a new car, bought clothes for her children, and locked in a new job.
One participant said, "I felt supported for the first time ever. I didn't know what it felt like before this."
A top recommendation from participants was that basic income should be monthly instead of quarterly and that pilots should provide more opportunities for in-person connection with other participants and the community.
Article includes insights from @LutaSecurity#ceo & founder @k8em0. “…it's not just about cash payments, it's about the work you have to do to actually fix the vulnerabilities.”
Today lets commit to creating opportunities for all women to thrive,unbound by stereotypes or limitations. Let's continue to champion gender equality. Lets celebrate women who inspire within the industry and beyond #internationalwomensday#iwd2024 bhconsulting.ie/magnificent-seven/
Jane Archer was MI5's first female officer who trained as a barrister in her spare time. By 1929, she was in sole charge of MI5's department for Soviet espionage in the UK and went on to interrogate the Soviet defector Walter Krivitsky.
Her subsequent career with MI6 was disrupted when double agent Kim Philby moved her aside, fearing that her interrogation skills might unmask him as a Soviet mole. #internationalwomensday
When capitalism practiced greedily creates a culture of always-on-even-on-“vacation” corporate cultism, no amount of paid PTO or unlimited PTO is going to give you back your life. Our work culture is STRICT about our 3 day weekends to defend against reinfection with corp cultism.
It’s a leadership choice & I defend it so much because *I* deserve my 3 day weekends too. I make sure it’s very clear that non emergency messages during PTO is not only not ok, but do it & face my “this isn’t how we show respect to colleagues” message followed by email shutdown.
We’re unfortunately not in a world that values life above work cultism, so we must find or create pockets we protect. My company is one such peaceful pocket protector. Find or create yours. Unlimited PTO or not, it comes down to culture & respecting rest that makes the difference
“Let technology do more. Share the benefits of technology better. Shorten the work week. Provide universal basic income as an inherited technological dividend.
If jumpstarting a car took generations of pushing, consider how our great grandkids we're doing all this pushing for, who we want to jump in and happily ride, might refuse, based on the multi-generational belief that pushing the car was good work, and that no one was ever supposed to ride 'lazily' in the car.
That's where we are as a civilization. Our ancestors did so much work so that their great grandkids could live easier lives of greater wellbeing, but we're surrounded by those who are stuck on the notion that life should only be about the daily work, and not the entire point of the multi-generational work.
Let technology do more. Share the benefits of technology better. Shorten the work week. Provide universal basic income as an inherited technological dividend.
In 1995 there were roughly 16 million Internet users worldwide, less than half a percent of the world’s population at the time. To be on the Internet back then was truly a gift, even though we’re had to roll our OSes uphill in the snow both ways.
In Spring of 1995, I was a Linux user. I had been since late 1993 running Slackware. This was being done on a 386SX processor with 2MB of RAM and 20MB hard disk.
There started to be some chatter on USENET about Windows 95 coming out and how it was going being amazing.
I wanted to see if I could get my hands on a leaked copy somehow. In 1995, the best place to find this was #warez on IRC. So I jumped into that channel and found a DCC bot offering up a beta version of Windows 95.
I’m pretty sure it took many hours to download to a school lab computer and then write the install disks.
After going back to my dorm and installing it, since this was a beta version there wasn’t any network card drivers nor a TCP/IP stack. I had to get the DOS driver (3c509) and then the Windows 3.1 TCP/IP stack which was Trumpet Winsock to be able to DHCP an address from my dorm’s network and connect to the Internet with terminal tools like FTP and NCSA Telnet.
A graphic web browser didn’t come as part Windows 95. Internet Explorer didn’t come until the Windows 95 Plus pack was released later.
There were basically two main choices of web browsers at the time: NCSA Mosaic and Netscape Navigator, so I installed both.
I had been using NCSA Mosaic since fall of 1993 and was a fan - having developed a lot of websites for my university and also businesses in Chicago starting around 1994.
Netscape was innovating more than Mosaic and it eventually became my browser of choice for many years.
I remember being especially excited when Netscape added SSL support - prior to this most of what you did online was sent in clear text. SSL would enable web forms to take private information like credit cards with less risk to compromise at the network layer.
I didn’t have a credit card in 1995, so I went down to the quad at @IllinoisStateU and found a table with some keeps giving free beer koosies if you signed up for a credit card.
It took a few weeks to arrive but received credit card with a $500 limit - with something like a 27% interest rate.
My first online purchase over SSL was on the Netscape website store for a t-shirt. It was a white t-shirt with a small Netscape logo in the upper left front chest and had the dragon named Mozilla on the back. It got lost in some move or closet purge - I wish I still had it. To me that transaction a monumental in my life / career - it showed me a glimpse of what the future would be like. I spent the 2000s writing standards and building technology that further secured credit card use for the entire planet.
Connecting and building the Internet in mid-90s took a lot of motivation and time. Most parts of the experience just work today and we (include me) never thinks about them when doing everyday tasks. Those same parts would sometimes take several minutes or hours to setup just before you could begin to use them.
If you were a hacker with both patience and endless curiosity the 90s was a technical wonderland where you could discover and use technology that almost no one else on the planet was using, but someday would.
An argument often heard is that basic income will make us lazy + dependent. But consider this - isn't our current system already making many dependent, but on precarious low-wage jobs? Isn't it time we gave everyone the basic freedom the rich have to truly choose what work to do?
Exciting News! 📢 We're boosting our Microsoft 365 Insider Bounty Program, increasing awards up to $30,000 and expanding the scope of eligible vulnerabilities in our Office products and services. Find out more in our blog: www.microsoft.com/en-us/msrc/blog
“It’s difficult enough for teams to keep up on the well-written CVE descriptions, & it is already impossible for them to triage the numerous vague & poorly written descriptions on top of all of their responsibilities.” — ¹ /ht @ChristopherBudd
Results are out for the guaranteed basic income pilot in Paterson, New Jersey where 110 people got $400/mo for a year.
Pilot participants increased their incomes significantly to $24,810 from an average of $16,604. The control group ended up at $19k.
While the control group's ability to cover a $400 emergency sharply declined, basic income recipients not only maintained their ability, but over 15% saved more than $500.
Mental health improved. Distress levels went down.
Social ties within the community improved. People did more work in their community.
CNAs that don’t assign CVEs to *vulnerabilities only* but instead misuse them as general product bug IDs to non-vulnerabilities should be sanctioned to have their CNA status revoked. Not even all vulns get assigned CVEs.
Did you miss the @semgrep Community event with @adamshostack last month? Fear not! You can learn how to mature your threat modelling skills by watching the recording!
IT IS HAPPENING! Today, Signal launches phone number privacy & usernames! These features let you use Signal w/o sharing your phone number with the people you talk to
Proud to add more privacy to Signal, & proud of the smart, careful work the team did to make this happen ♥️
Introducing usernames and phone number privacy on Signal! We’re making it possible for people to connect with each other without having to share phone numbers. Now launching to beta users, available for everyone soon. signal.org/blog/phone-number-privacy-usernames
Everyone's talking about the woman who put $50k in a shoebox and handed it to scammers and how they wouldn't fall for it. It would shock you how many everyday people have embarrassing scam stories. I can't help once the scams over, but I can help you Spot The Scam upfront:
My comments on the likelihood of public Wi-Fi being involved in a real hack that would cost you $50k - basically, no. There are best practices you should do no matter where you connect to the internet - because your home Wi-Fi is likely hackable & you need layers of protection.
For @Slate, I wrote about one of the best questions posed by Charlotte Cowles in her unconscionable tale of being scammed: Can we actually trust airport Wi-Fi?
A reminder that nobody from @FTC will ever give you a badge number, ask you to confirm your Social Security number, ask how much money you have in your bank account, transfer you to a CIA agent, or send you texts out of the blue.
AI text-to-video is here and we need to discuss the risks. They mention in this thread that they’re considering the ways adversaries would leverage this content to harm thru red teaming but I’m still concerned. My biggest concern is how this content could be used to trick, manipulate, phish, and confuse the general public. - for example, imagine an adversary uses this tool to build an AI video that appears to show a vaccine side effect that doesn’t exist - imagine an adversary uses this tool to show unimaginably long lines in bad weather to convince people it’s not worth it to head out to vote that day This tool is going to be massively challenging to test and control under many, let alone most, adversarial conditions.
Prompt: “Beautiful, snowy Tokyo city is bustling. The camera moves through the bustling city street, following several people enjoying the beautiful snowy weather and shopping at nearby stalls. Gorgeous sakura petals are flying through the wind along with snowflakes.”
Normalize the technological abuse you seek to inflict. Next: work your way up the privilege gradient. Maybe you start with prisoners, then work your way up to asylum seekers, parolees and mental patients. Then try it on kids and gig workers.
Here's how the shitty technology adoption curve works: when you want to roll out a new, abusive technology, look for a group of vulnerable people whose complaints are roundly ignored and subject them to your bad idea. Sand the rough edges off on their bodies and lives.
I met my friend Barnaby Jack at #cansecwest in 2003. He asked me what kind of hacking I was into, fully accepting (expecting, even) from the start that I was a fellow hacker - not asking me whose girlfriend I was. Instant pals. I miss my brilliant friend.
I have a very specific memory of sitting in that lobby with @ryanaraine and some others talking with Barnaby Jack in what must have been early 2013. Maybe 2012. Ryan and I talk about it all the time.
CSW is the best. And so is Dragos. Some of my favorite times have been in the lobby bar at the Sheraton Wall Centre with @ryanaraine@window@jduck@k8em0@Kym_Possible et al. The. Best.
CanSecWest, 25th year. Take your chances @ RandomNewCon, or experience Vancouver's diversity, get pampered, fed well, by our experienced team (still only con with Second Breakfast), see leading edge research in our single track, and a 30m taxi to Grouse for day/night skiing or a short excursion before or after for North America's best skiing at Whistler. Your pick. secwest.net
Fascinating journey of stubborn discovery. The leadership of the company initially backing his idea, then telling him to abandon it, & his determination in ignoring them all the way to the finish line is similar to a story I’ll be telling at #rsac about Microsoft’s first bounties
The invention of the blue LED, one of the most difficult and important inventions ever, is some of the most Chad shit I have ever heard youtu.be/AF8d72mA41M
When gov warns that Chinese hackers are in US critical infra, I think, "Where have I heard this before?" In WSJ in 2009. 👇 "Authorities...found software tools left behind that could be used to destroy infrastructure.... 'If we go to war with them, they will try to turn them on'"
Whoa the FCC has recognized the risk of AI voice cloning in robocalls & scam calls! Video demo below. - New FCC fines, more than $23,000 PER CALL - Now gives call receiver right to take legal action and potentially recover up to $1,500 in damages per call apnews.com/article/fcc-elections-artificial-intelligence-…
This is the best thread not actually about the movie Sneakers but with a solid parallel I’ve ever read. It goes from cow lips to manufacturing chips & all the post colonial exploitation & brittle supply chain you can imagine. Worth the read 💯
There's this great line in *Sneakers*, where Dan Aykroyd, a conspiracy-addled hacker/conman, feverishly tells Sydney Poitier (ex-CIA spook) about a meeting Eisenhower/aliens meeting where Ike said, "look, give us your technology, and we'll give you all the cow lips you want."
Delighted to be a fellow speaker at the #pallmallprocess@LondonCyber event on Tackling the Proliferation & Irresponsible Use of Cyber Intrusion Capabilities with @Infosecjen
February 4 Is World Cancer Day. In 2024, the American Cancer Society projects cancer cases to surpass 2 million. To put this into perspective, this would mean nearly 5,500 cancers would be diagnosed daily in America. www.forbes.com/sites/omerawan/2024/02/04/february-4th-is-…
I found this tiny tulip sprouting in my garage. No water, no light, soil bone dry, but it is back to life another year. Don’t let anyone tell you you’re done, not even yourself. You have everything you need inside you, ready to grow towards the light. Here’s to never ending hope.
Looking forward to presenting “The Good, the Bad, & the Bounty: 10 Years of Buying Bugs at Microsoft” with Microsoft CVP @nchlgpt at #rsac A decade ago, there were few bounties - learn about the 1st year-round 6 figure bounty launched by the company that once swore never to pay.
The seed of Microsoft’s bounties grew into Hack The Pentagon & a worldwide eruption of VDPs & bounties - but how well have bug bounties delivered & evolved over the past decade? Join us to learn how to run bug bounties that count more than bugs & cash, but measure security impact
I want to live in a society that values caregiving labor in households - raising children & caring for the sick & elderly IS real work, the hardest work I’ve ever done. Our society is stronger if basic income supports caregiving, upskilling/education, & housing & food security.
Results are out for the guaranteed basic income pilot in Austin where 135 people got $1,000/mo for a year.
9% of people reported working less and 7% reported working more. Of those who worked less, half upskilled for better future jobs, and half chose unpaid care work.
Housing security significantly increased, as did food security. People lived in better housing and ate more balanced meals.
Re-upping my conversation with Luta's Katie Moussouris on building a different kind of security company, plus thoughts on the CSRB, job market, etc. @k8em0
I've been tagged here a lot. Basically: ORF6 is one of the proteins that the COVID virus makes, it plays a role in blocking our cellular response to recognize and fight the virus by effing with our interferons and other things we use to fight. I'll explain the broader concept:
SARS-CoV-2 adaptation and evolution led to stronger innate immune suppression by increasing expression of Orf6 in Omicron subvariants, according to a study in @NatureMicrobiol. go.nature.com/3tVaUPJ
Revolutionizing our economy isn't about giving people free money, it's about recognizing our inherent worth as human beings. Basic income isn't a handout; it's a much-needed rebalancing of economic security in a world that too often leaves the many to starve while the few feast.
🔥 New podcast advisory: Katie Moussouris discusses @LutaSecurity's new Workforce Platform profit-sharing initiative, the security job market, criticism of the CSRB’s lack of enforcement authority, and looming regulations around zero-day vulnerability data. @k8em0
15 years ago today, @BarackObama was sworn in. For many of us here & around the world, it was a moment of joy & hope. What we didn’t realize was the fear this sparked in some would swing our country backward with such whiplash. We must hold fast to our hope & win back the fearful
The world’s 5 richest humans watched their wealth more than double since 2020. Their wealth reportedly went from $405 billion to $869 billion since 2020. That's about $14 million per hour.
Over the same period, 5 billion people became poorer.
I’m that fun aunt who gave you a few bug bounty programs to play with on your birthday, who advises governments on vuln disclosure after you’ve gone to bed.
So here is the deal. I gave another Firetalk at shmoocon this year, and they offered me a chance to be a judge next year. Needless to say, I accepted their offer immediately. Are you freaking kidding me!
Possibly the best evidence yet that unconditional basic income works, and that the pilots going on around the country are showing again and again that it works.
It's almost time for ShmooCon! Packing tips: Your mask; it's required to cover your nose and mouth in all Con spaces. A book for the book swap. Your barcode! Check out the complete schedule of talks, events, and masking policy at shmoocon.org. See you tomorrow!
It's that much harder to accomplish something if you feel it can't possibly be done. Far too many people have given up on trying to really change anything and concede defeat in advance. Yes UBI will be hard to win. It greatly democratizes economic power. But we must fight TO win.
2024 is (the 1st instance of) my 29th birthday of working in tech.
From bioinformatics working on the human genome project, to systems admin, to Linux developer, to hacker for hire, to security strategist, advisory board member, & tech company founder-
I was a professional Linux developer. This take about those who can’t code are somehow less than those who can is short sighted at best. Those who have vision, passion, & people skills in tech are the leaders. Coding can be done by those who lack all of those leadership qualities
The leaders of black tech twitter are people who can’t code . That’s the problem with the space. When the majority of the your “leaders” are tech adjacent and “influencers” that’s when you know your messed up in the game
If this is an example of an org getting hacked due to a loss of SMS 2FA for non-paying Twitter accounts after March 20, 2023 then it's one of the 1st higher profile attacks I've heard of to reference the SMS 2FA auto-turn off for non paying accounts as an issue within their hacking incident report. We discussed this very hacking risk when Twitter announced it would auto remove SMS 2FA for non-paying customers (even if they had previously enabled SMS 2FA).
This Twitter 2FA change is nerve-racking because: 1. Only ~2.6% of Twitter users have 2FA on at all (it’s essential for preventing easy account takeover) Of those 2.6%, 74% use text message based 2FA (transparency.twitter.com/en/reports/account-security.html) If they don’t pay for Blue they auto lose 2FA on 3/20.
The @SECGov account claims it was hacked. The compromised account’s tweet impacted the cryptocurrency market. Like I said during the @Mandiant Twitter account takeover 5 days ago: there are many ways this attack could have happened including bribe or compromise of internal Twitter creds with admin panel access, SIM swap, phishing, malware, etc. I find it unlikely again that the SEC would use SMS 2FA to secure their account or keep a phone number tied to the account. Also unlikely they reuse a password or don’t leverage MFA. Lots of possibilities here. With 2 higher profile account takeovers pushing crypto related messages (and countless others behind the scenes), I’m curious if there are compromised Twitter creds thru bribe or phish with attacker access to internal admin panel?
The @SECGov X account was compromised, and an unauthorized post was posted. The SEC has not approved the listing and trading of spot bitcoin exchange-traded products.
*Account Takeover Prevention Guide* If you watched the SEC account hack that moved markets yesterday & wondered how to prevent account takeover for your personal, business, or high profile social media account, here's an Account Takeover Prevention Guide for you and/or your org.
Thanks, @americandialect, for choosing "enshittification" as the 2023 Word of the Year. @doctorow's apt term describes how online platforms decay by showing users less and less of what they came for, while keeping them trapped and unable to exit for better alternatives.
Nobel-prize winning economist on Kenya's Universal Basic Income pilot results: "The results do not disappoint. For one, there is no evidence that getting UBI makes people lazy. They work more overall, not less, though the difference is small. They do cut back on working for others but instead are working more on their own projects."
"The number of non-farming businesses (think shops, eating places) associated with these villages is almost a third higher than the villages where no intervention happened, and the number of farming businesses (think poultry, goat-herding) goes up too. As a result, earnings are about 20% higher than in the control villages. The fact that the 12-year UBI money is there for the foreseeable future seems to have made the villagers better able or more willing to take on something new."
I love how this article ends with the evidence that drinking went down too, followed by a recipe for a cucumber mint cocktail. A clever reminder that alcohol only seems to be looked down upon when the poor drink it.
Regarding Dutch news story published this morning about Stuxnet, here's the original 2019 story that I wrote with the Dutch journalist revealing that a Dutch mole introduced Stuxnet into the facility in Iran. We didn't know the mole's identity at the time. news.yahoo.com/revealed-how-a-secret-dutch-mole-aided-the…
howdy folks- I'm going to be the first guest of 2024 on @GreyNoiseIO Stormwatch tomorrow! Stream on any of your favorite streaming services- we'll be broadcasting LIVE.
AI will impact Know-Your-Customer identity verification processes. As AI makes it easier & cheaper to impersonate someone’s likeness and identity markers (often found in a breach) it will become simpler for attackers to takeover accounts and steal money, data, impact brands, etc.
Nebraska Governor rejected $18 million of federal funding, $40 a month per child, less than $1.32 per day for hungry kids, but accepts millions in government handouts for businesses. So free government money is fine as long as it only goes to those with capital already, not kids.
Here's Nebraska's governor saying he doesn't want $18 million going to low-income kids so they can eat, because "he doesn't believe in welfare." Note that it would only cost Nebraska $300k.
These people love welfare as long as it's for them.
A big reason unconditional basic income is so important is because of politicians like Jim Pillen.
Politicians should not get to decide that money shouldn't go to meeting the basic needs of families and should instead go to businesses like theirs.
UBI takes politicians out of the "money for basic needs" loop. The government would no longer get to decide how basic needs money gets spent. Instead, we all would ourselves, each and every one of us.
It has come to my attention that @playmobil has created an unlicensed action figure of me, right down to my love of fishnets and my Resting Crime Face.
"If you're on welfare, the minute you make some income, they'll take away your food stamps, they'll take away your housing assistance. It's impossible to save money and become independent, so a lot of single parents feel trapped... The difference it makes to get $500 a month [in basic income] is freedom, to avoid eviction, getting your electricity cut off. It's given us a chance to take our lives back."
That is how Porchia Willis described her lived experience as a welfare recipient and then a basic income pilot participant in the documentary film @ItsBasicDoc.
90% of us are composed of foreign microbes - bacteria, viruses, molds, and fungus that live in & on us. 🔬 We literally could not live without them, our holobiome maintaining balance is what brings us health & longevity. ⚕️ May you all collectively live long and prosper.🖖🏼🦠
“Expect a considerable customer withdrawal from #ai tools as the benefits fail to justify the costs & risks. On the far end of this spectrum, we are likely to see lawsuits and regulatory action w/ AI service providers that failed to back up their claims.” techcrunch.com/2023/12/19/8-predictions-for-ai-in-2024/
Sign Your Name to Europa Clipper's Message in a Bottle -> Earth’s first mission to conduct detailed reconnaissance of Jupiter’s moon, Europa. NASA’s Europa Clipper will determine if this ocean world has environments suitable for life to exist. science.nasa.gov/mission/europa-clipper/
If you are never fortunate enough to have someone who thinks about you & does nice things for you, be that person for yourself. If you’re that person for someone else, may they return your attention in kind. I hope your new year & every year is filled with thoughtful, kind love💗
A useful prism through which to view generative AI from a copyright perspective:
The model is a heavily (lossily) compressed representation of the training data, which, with the right prompts & random seeds can often be used to recreate a slightly corrupted version of the data.
We pay for & enforce* a minimum of 79 days of PTO per year: All Fridays PTO Two weeks PTO twice a year (summer & winter) All federal holidays A few more holidays
Plus no limit on sick/personal days
*If a FTE tries working during PTO, they are politely told I will cut off email.
It’s ok to hire certain hackers with criminal backgrounds. It’s not ok to hire antisocial violent people, regardless of whether they’ve ever committed, been charged, or been convicted of a crime. The willingness of people to overlook sociopathy on this website is not a surprise.
A convicted person keynoted Blackhat EU earlier this month & nobody blinked. Our industry tends to glorify its criminals. Plenty of criminals didn’t deserve it or have reformed & I’d hire them. We just have to learn to stop elevating or tolerating or glorifying actual sociopaths.
Heather Adkins - Ꜻ - Spes consilium non est@argvee
This chapter for Lapsus$ has come to a close. Thanks @joetidy for citing the Cyber Safety Review Board’s report. Shining a light on the need for helping teenage hackers take the right paths always felt very important. H/T @DHS_Policy@k8em0@DAlperovitch@NSA_CSDirector et al.
I'm at Guildford Crown Court for the long-delayed sentencing of two teen hackers from the Lapsus$ gang. Arion Kurtaj hacked Rockstar Games in 2022 leaking 90 clips of unfinished GTA6 gameplay. He and his accomplices also hacked Nvidia, EE, and Revolut in their hacking spree.
💪🏼 Yesterday @_clem1 and @vladhiewsha discovered and reported a new ITW 0-day to the Chrome team. TODAY, 1 day later, Chrome has a fix out to protect users!!! Thank you, Chrome! CVE-2023-7024
A basic income of $750 a month is being provided to 100 homeless people in Los Angeles. Another 100 aren't getting money in a control group. The results were so promising that the researchers decided to publish results after only six months.
"After six months, only 12% of those who received funds reported being unsheltered at any time in the prior month, a dramatic decrease from 30% at the outset. Those on the waiting list also reported fewer unsheltered episodes, but by a much smaller margin, from 28% to 23%."
"It may not be earth-shattering that providing money is going to help meet basic needs, but I do think it dispels this myth that people will use money for illicit purposes. We weren’t finding that in the study.”
These preliminary results echo the preliminary results from the @denverbip that's also providing basic income to homeless people (of $1000/mo or $500/mo), as well as the results from an earlier pilot in SF that gave only $500/mo.
A universal basic income would dramatically reduce homelessness. That much is now clear.
The CTI League did not engage in censorship, it is focused on protecting the health sector. Despite testimony to congress that it is ridiculous billion dollar hospitals need help the hard truth is they do. At least one major hospital per week is hot by a ransomware incident. Major incidents at hospitals cost lives. 2/5
I have released a statement about our work in the CTI League. Yesterday I provided this and additional material as testimony to congress. Today we have made our github public and opened up all our files. cti-league.com/statement-by-marc-rogers-on-the-cti-league/ Details are in this statement. 1/5
Voice cloning takes me less than 2 minutes to complete to fool these systems and steal money. Friends don’t let friends use voice ID. x.com/60minutes/status/1660428419438354435
Cyber criminals “accidentally leaving off the attachment” on their phishing email to build believability that message is authentic. Also builds Commitment & Consistency principle of persuasion — if you take time to ask for attachment you may believe you must then engage with it.
Notable tactic from the UNC4057/COLDRIVER indictment yesterday that's a favorite for them:
"Some of the [phishing] emails directed the victims to a document that was not attached, designed to engage in an email response for the missing document and to later include the document"
Unconditional basic income creates a floor of real economic security. So many of the problems in society go beyond not having enough money for basic needs, to the simple fear of that happening to us and the chronic stress involved in worrying about that.
A literal flying flyer And a great idea for a win-win revenue model Such business beauty rarely lasts in the wild We are fortunate for having witnessed it
7 years ago, I wrote a guide to electronics in Shenzhen. @realsexycyborg is releasing a new version that reflects the latest changes in the markets and the culture. I love the new red cover, too. 🥰
This NPR coverage of @GiveDirectly's huge universal basic income experiment includes a couple observations I really want to highlight as results of UBI's universality:
1. Entrepreneurs galore!
2. No inflation!
The huge entrepreneurship boost is a replication of all previous pilots that were provided to entire villages. This is BECAUSE of universality. When everyone in a community gets money, entrepreneurs start businesses, and those businesses have customers with money to spend.
Just think of all the loans that have ever gone to people to start businesses that failed because they didn't have people around with the cash to be their customers.
The lack of inflation is also attributed to the universality where no inflation happened BECAUSE the money was provided universally, not in spite of it.
The researchers hypothesize that because everyone got money, it was spent on many different things, in contrast to targeted money that may have all been spent on the same thing.
It is counterintuitive to think that everyone getting money could have less inflationary pressure than some people getting money, but that's what was observed.
I think it also helps that so many new businesses were created. This increases competition and supply, raising overall capacity to meet demand, and increasing the amount of choices for customers, creating an incentive to compete on price.
This is also observed in Alaska every year, where because everyone gets money when their UBI is distributed, businesses have dividend sales in order to entice people to spend their dividend checks there instead of elsewhere.
I also just want to point out how large this experiment in Kenya is. These are the results of observing 23,000 people being given unconditional cash three different ways, that started 7 years ago.
I'll also add something not included in this NPR piece, which is that people didn’t work less and the results were the same regardless of 2-year or 12-year treatment, meaning that all the observations of people not working less in short-term pilots are likely reflections of permanent UBI, and not because the pilots just weren't long enough as UBI opponents contend.
In a perfect world, these results should be enough for governments to begin rolling out UBI. We of course don't live in a perfect world, but maybe at least one country will now step up and lead the way forward.
For all previous UBI experiment results, please see my pinned tweet thread.
Ultimately, we need #ubi It’s what society should really be about - making sure we all have enough support to thrive - without trading labor for survival. Until then, @LutaSecurity is creating a way for our workforce to profit-share. US private alpha: www.lutasecurity.com/alpha-platform
Basic income isn't just dollar bills. It's freedom, trust, security, and power. It's a world where your value isn't measured by societal expectations. The old regime shivers at this shift – they'd sooner dub us idle than confront their fear of an unleashed and empowered society.
Now, I ain’t take none of this advice 🥴. I was anxious trying to make sure my growing family would be provided for, so I took the next gig before being finally being a founder fulltime. 1 of my mentors told me, “Don’t fall in love these companies. They can’t love you back.” FIN
Imagine a world where survival isn't our only purpose. If you believe UBI will reduce us to mere survival, you're wrong. No one yearns to just exist. We all strive for more. With UBI, we do more than survive, we THRIVE. Let's shift our focus from just getting by, to truly living.
Want to try our private workforce platform alpha? Link to apply in the quoted tweet below. Currently eligible contractors at @LutaSecurity will receive their first profit sharing dividends at the end of this month. Let’s hack capitalism for a better future for all. ✊🏼
I agree with this idea. I don’t think orgs will devote enough resources to find or fix or prevent vulnerabilities fast enough, just like they don’t now. Software liability might change their priorities, so let’s get on with it.
I find myself frequently reminding people that we want AI/LLM’s capable of finding 0-day vulnerabilities. This kind of capability would rapidly improve software security. The benefit it offers developers and security teams far outweighs any short term advantage it would give threat actors.
Live call translators like this will make phone attacking in another language much easier. We think phone attacks are increasing now — just wait until the attacker doesn’t need to be comfortable in our language to make it happen.
Proud to say that @LutaSecurity is a friend of @comingler1. They're leading the way with some equal redistribution strategies of their own. It may not be UBI, but it's still an awesome way to do business.
“Her mother was a hacker-for-hire & drug dealer to Silicon Valley's elite; after everything went wrong she was homeless & alone on San Francisco streets at the age of 13… while tech's earliest generations of workers partied, broke laws, & spat on homeless kids begging for food”
Please note, Spotify pays artists next to nothing so they could afford paying pro Billionaire Rightwing Chud Propagandist Joe Rogan hundreds of millions.
I'll forever be amused how spying is euphemized as "intelligence" in English, and in German as "Aufklärung", which can be used both for "Enlightenment" and "Sex Ed".
“Everything becomes a lot slower,” a nurse at one of the affected New Jersey hospitals told CNN, referring to the reliance on paper, rather than computers, to track things like lab work for patients. “We drill on that a few times a year, but it still sucks.”
I’m not giving any more attention (not even subtweeting) to the fraud who created a catfishing influencer & fake lady speakers to get high profile male speakers at his con.
20 So it doesn't matter if a New Covid infection seems mild at first. Other serious illnesses, like the one caused by SARS-CoV-2, can seem mild at first, but are also actually doing damage under the skin out of sight.
21 New Covid can infect your brain. It does there the same thing it does everywhere, it infects cells and kills them, and disrupts the essential processes that keep your body stable.
I am going to add this because I think more people need to see it. But the man running the WIT account also answered interview questions about his opinions on being a woman in tech... the more you look the worse it gets. x.com/IanColdwater/status/1729020598431694852
And we all cost money to have us speak. Why would we volunteer to bring your audience our content? We can choose to do so via a CFP, but if you’re ASKING us to speak, pay us. Pay speakers. Pay women. Pay women speakers.
The conference website is up and fake Anna removed.
But fake Julia is still there. Listed every year as a speaker, never delivered a talk any year (and “dropped out” this year as well) @lizthegrey did some digging.
The conference website is up and fake Anna removed.
But fake Julia is still there. Listed every year as a speaker, never delivered a talk any year (and “dropped out” this year as well) @lizthegrey did some digging.
AWS unveils the Amazon WorkSpaces Thin Client, a $195 compact computer resembling a Fire TV Cube that's meant for workers to access cloud-based virtual desktops (Maria Deutscher / SiliconANGLE)
Gonna make a virtual conference with AI generated men giving talks with references to their original real female creators and pay out sponsorship money to those women.
When conferences ask me to speak, I have my Comms team respond with my speaker fee. They usually pass on me then ASK me/my team to do free work to recommend a different woman speaker (who presumably they can pay less or not at all). I’ve even had a con ghost me This is a new low.
To spell it out why this conference generated fake women speakers. Because the organizer wants big names and it probably seemed like an easy way to address their diversity concerns.
How does a conference ghost you? 1. Agree to your fee in email 2. Delay signing your speaker agreement 3. Go dark, hoping YOU’LL cancel 4. Publish the conference agenda w Brian Cox keynoting 5. Lie to you: it was budget cuts 6. Lie to their own CFP reviewers saying you were sick
We are thankful for the local journalists across the country who are reporting on surveillance and working to keep their government and officials accountable.
This is an example of a security bulletin that does not comply with the ISO standard for vulnerability disclosure, since there’s no actionable information, & also could distract security teams on a holiday. It takes a lot to be worse than non-disclosure. docs.newrelic.com/docs/security/new-relic-security/securi…
Don’t ever let anyone Jedi mind trick you out of the fact that the “Disclosure” in “Vulnerability Disclosure” stands for Disclosure to parties at risk so they can protect themselves, NOT disclosure to a vendor so they can sit on it & call you irresponsible if you warn the public.
Low level supply chain vulnerabilities take longer to coordinate than a vanilla vuln. 300 days is long, but what if there were 20 vendors testing 10 products each & fixes degraded performance? The complexity of testing can easily exceed the de facto 90 day accepted embargo period
Fun fact, in the granddaddy of all vuln disclosure policies, RFPolicy by Rain Forest Puppy, he originally gave vendors 5 days before public disclosure. The US gov’s CERT/CC gives a default 45 days (with flexibility). Symantec’s 1st disclosure policy which I wrote was just 30 days
If ever a retweet would actually help people in imminent danger, this is the one. Let’s get these people noticed by @AmbasadaSUA so they can help them escape #ukraine#refugees 🚨 Please Retweet🚨
Update from #ukraine @AmbasadaSUA we are traveling in a marked refugee bus from #kyiv evacuees to the Siret Romanian border with many US Citizens. Please reach out & most importantly:
FTC cites its enforcement action vs Equifax (which ended with a massive settlement) as precedent for potentially taking action under FTC Act or the GLB Act against companies that fail to take adequate action to address Log4j vuln.
I think it’s going to be tough to hold private companies more accountable to patching flaws like this when federal agencies have just been given a deadline from CISA in June to patch some very old bugs known to be exploited - like the exact bug that caused the Equifax breach.
FTC taking a strong position on companies not mitigating #log4j
Good to take this seriously, but complex to enforce. They cite Equifax’s $700M settlement for the data breach caused by delays in applying a Struts patch that CISA recently gave federal agencies until June to patch.
FTC taking a strong position on companies not mitigating #log4j
Good to take this seriously, but complex to enforce. They cite Equifax’s $700M settlement for the data breach caused by delays in applying a Struts patch that CISA recently gave federal agencies until June to patch.
As an employer, I completely agree, which is why I insist that nobody here works before or past business hours, Fridays are PTO, & to save residual work chats/emails for Monday. My brain needs a break as badly as every other human, so biz hours are non-negotiably respected by all
@taviso is right. Microsoft is wrong. The only thing that can make it worse is another MS smear job or condescending blog post about being "responsible." Cut that hot air out & fix the damn bugs faster, MS. You can't preach to me, I know you. Patch || GTFO.
Is @taviso the most horrible person in the world for dropping 0day or is Microsoft the most evil company in the world for shipping and then failing to patch the bug?
This is the sort of simple topic that lends itself well to 280 char statements.
Thread about the black hole of sexism we unfortunately didn't need a special telescope to see. Thank you, Andrew, for standing up for your colleague Katie Bouman. I've experienced a lifetime of this type of destructive attempts to downplay & erase my contributions & it sucks.
(1/7) So apparently some (I hope very few) people online are using the fact that I am the primary developer of the eht-imaging software library (github.com/achael/eht-imaging) to launch awful and sexist attacks on my colleague and friend Katie Bouman. Stop.
“The thermodynamic arrow of time...entropy of a closed system can only increase or remain constant, but never decrease,” Micadei said. “By creating in the lab an isolated system where the entropy decreases, in the system the arrow of time should point to the opposite direction.”