 subgraph
@subgraph

We are at #zeronights in Saint Petersburg.


Politicians, athletes, journalists, NGOs, companies... They all use corporation-owned social networks to communicate with us. Citizens shouldn't have to hand over their data to companies to read content published by public entities. Public Feeds changes that by making posts of popular accounts freely available. Read more.
Subgraph OS is a security oriented Linux distribution, designed to be resistant to surveillance and interference by sophisticated adversaries over the Internet. It has been mentioned by Edward Snowden as showing future potential. More on Wikipedia
Adversary resistant computing. Open source security. Based in Montreal.
subgraph
@subgraph
We are at #zeronights in Saint Petersburg.
subgraph reposted
 Bruce Leidl
@bleidl
Good Morning, St. Petersburg
#zeronights
 subgraph
@subgraph
More portability for SGFW is in progress. We have a GTK prompter in addition to the modal Gnome shell dialog; and we are removing dependency on Oz related to next-gen Subgraph OS & Citadel.
subgraph
@subgraph
Marketing from Zero Knowledge Systems circa ~2000. ZKS was a Montreal startup with a consumer solution to a problem that took another 15 years to actually manifest. cc @austinhill

subgraph reposted
 Simone Stolzoff
@SimoneStolzoff
“Where are the most powerful AIs in the world right now? They are at Google and Facebook. And their AIs are essentially playing chess against our brains and trying to figure out what’s the best way to get you hooked.” -@tristanharris at #knightcomm cc @CommonSense
subgraph reposted
 Renee DiResta
@noUpside
Interesting glimpse into what this looks like outside of the US market, in another language.
 Amit Agarwal
@labnol
Every single video on the YouTube trending page is fake. The videos are made by 'verified' YouTube creators, they garner millions of views and the sad reality is that Google is indirectly encouraging the promotion of hoax content with AdSense dollars. 👎

subgraph reposted
 Facts In Your Face
@FactsInYourFace
China has blocked Facebook, Twitter and The New York Times since 2009.
subgraph reposted
 Leif Ryge
@wiretapped
 Adrian Colyer
@adriancolyer
82% of mobile (Android) apps send PII to at least on ad tracking service, and many send to more than one. What data is being leaked and where does it go? blog.acolyer.org/2018/03/05/apps-trackers-privacy-and-reg…

subgraph reposted
Leif Ryge
@wiretapped
it was Android that let Facebook have this data
 Dylan McKay
@dylanmckaynz
metadata about every text message I've ever received or sent
spoiler: I don't use messenger for SMS


subgraph reposted
 François Chollet
@fchollet
The problem with Facebook is not *just* the loss of your privacy and the fact that it can be used as a totalitarian panopticon. The more worrying issue, in my opinion, is its use of digital information consumption as a psychological control vector. Time for a thread
subgraph reposted
 AJ+
@ajplus
The UN has accused Facebook of spreading hatred against the Rohingya.
subgraph reposted
 grimmware
@grimmware
Compiling @subgraph Citadel on a 16vCPU VPS in tmpfs like
subgraph reposted
 Matt Buzanowski
@Mateusz_Jozef
Linux Kernel Exploitation github.com/xairy/linux-kernel-exploitation
subgraph reposted
 Ars Technica
@arstechnica
Newly discovered malware that lurked for 6 years was a well-oiled spy engine arstechnica.com/information-technology/2018/03/potent-mal… by @dangoodin001
subgraph reposted
 meh
@mehqq_
Found another off-by-one remote code execution vulnerability (CVE-2018-6789) in Exim mail server! It was challenging but interesting and we finally achieve RCE and bypass mitigations (ASLR, NX …) successfully. Details here:
devco.re/blog/2018/03/06/exim-off-by-one-RCE-exploiting-C…
subgraph reposted
Bruce Leidl
@bleidl
The only common denominator between Tails and Citadel is that they both have a Gnome desktop environment.
Citadel is not a live disk, is not built from Debian (or any other distro), and does not have any Tor software installed.
subgraph reposted
Bruce Leidl
@bleidl
But can we have our cake and also eat our cake too?
Is there some way to achieve the interesting properties of a Linux live disk while avoiding the annoying properties?
To what extent might this be possible? How could it be done?
To be continued...
subgraph reposted
Bruce Leidl
@bleidl
Subgraph Citadel: Secure and Stateless Desktop Linux
More details coming soon.

subgraph reposted
Bruce Leidl
@bleidl
I expect we will write a blog post about the direction we’re going within the next month, and we may also publish something then as a ‘technology preview’. It will be several months at least until we release the full new version.
subgraph reposted
Bruce Leidl
@bleidl
Reliability is actually a key characteristic of the new system design we’re working on. It should no longer be possible to break anything by updating, and especially not gnome or gdm.
subgraph reposted
Bruce Leidl
@bleidl
Maybe sandboxing Linux desktop applications that process untrusted data is a good idea after all.
(btw, we’ve been quietly working on very big improvements to Subgraph OS. More news coming soon.)
github.com/jollheef/libreoffice-remote-arbitrary-file-dis…
subgraph reposted
 REcon
@reconmtl
From Brussels with love, the REcon Montreal 2018 CFP and trainings have been announced: recon.cx/2018/montreal/cfp/
Register early to benefit from a steep discount: tickets.recon.cx/reconmtl/reconmtl18/

subgraph reposted
 grsecurity
@grsecurity
I no longer post to LWN, but to answer this question: lwn.net/Articles/743408/ Yes i386 is affected by Meltdown. No, no one else other than us seems to care enough about it to offer any fixes or give timelines for future fixes. AFAIK we're the only ones with a solution.

subgraph reposted
grsecurity
@grsecurity
So there's been a lot of talk about Meltdown and PTI, but 32-bit users have been implicitly left out in the cold it seems (PTI is x64-only). Based on some testing here with a modified POC (and helpful assist from @_minipli) it seems grsecurity w/ KERNEXEC/UDEREF stops it on i386
subgraph reposted
 Thomas H. Ptacek
@tqbf
Spectre is so bad compilers have to hack RET into a fake ICALL/IJMP, like an exploit dev would. In _everything_. archive.is/s831k
subgraph reposted
 Daniel Gruss
@lavados
The start of all this was @anders_fogh's blog post: cyber.wtf/2017/07/28/negative-result-reading-kernel-memor…
He deserves credits on this! #meltdown #intelbug #fuckwit #kaiser #kpti
subgraph reposted
 Mathias Krause | @minipli@infosec.exchange
@_minipli
v4.9.74-unofficial_grsec — the „let’s see what breaks” release: github.com/minipli/linux-unofficial_grsec/releases/tag/v4…
subgraph reposted
 Ben Hawkes
@benhawkes
Project Zero blog post: "Reading privileged memory with a side-channel" by Jann Horn (@tehjh) - googleprojectzero.blogspot.com/2018/01/reading-privileged…
subgraph reposted
Bruce Leidl
@bleidl
An example of how to use this in your own ebpf filter programs
github.com/brl/grlh
subgraph reposted
Bruce Leidl
@bleidl
Four opcodes to make verifier.c stop being such a buzzkill

subgraph reposted
Bruce Leidl
@bleidl
Pour one out for this really nice Linux kernel bugdoor that P0 killed a few hours ago. Straight up unlimited R/W to all kernel memory via ebpf verifier bypass. One of the best/worst Linux kernel vulns of all time
subgraph reposted
 Open Source Security mailing list
@oss_security
RCE in Exim reported: Posted by Phil Pennock on Nov 24In Post-Thanksgiving mail-catchup, I see that the Exim… seclists.org/oss-sec/2017/q4/325
subgraph reposted
 Project Zero Bugs
@ProjectZeroBugs
Linux: mincore() discloses uninitialized kernel heap pages bugs.chromium.org/p/project-zero/issues/detail?id=1431
subgraph reposted
 Arrigo Triulzi
@cynicalsecurity
The MemJam abstract, interesting SGX intra-cache attack w/ AES key recovery.
 Arrigo Triulzi
@cynicalsecurity
A. Moghimi et al., “MemJam: A False Dependency Attack against Constant-Time Crypto Implementations” (SGX attack) arxiv.org/abs/1711.08002
subgraph reposted
Mathias Krause | @minipli@infosec.exchange
@_minipli
@alpinelinux does, AFAIK
subgraph
@subgraph
Question: is @subgraph the only distro that ships an updated kernel with hardening from the @grsecurity public patchset?
(we use @_minipli’s patches)
subgraph reposted
 Thorsten Holz
@thorstenholz
The academic version of this is available at www.usenix.org/conference/usenixsecurity17/technical-sess…
subgraph reposted
grsecurity
@grsecurity
RAP's probabilistic check is much more infoleak-resistant than SSP,but not infoleak-proof,so also combines it with a deterministic CFI check
subgraph reposted
 David Stainton priv/acc
@david415
network privacy is super important. here's a technical introduction to mix networks i wrote. it has many links to good papers where you can read even more if you are interested.
 Least Authority
@LeastAuthority
Introduction to Mix Networks and Anonymous Communication Networks by @david415
leastauthority.com/blog/mixnet-intro/
#mixnetworks #privacymatters
subgraph reposted
Mathias Krause | @minipli@infosec.exchange
@_minipli
Out of holiday mode, brings you v4.9.64-unofficial_grsec: github.com/minipli/linux-unofficial_grsec/releases/tag/v4…
subgraph
@subgraph
Very high quality training at @reconbrx next Feb: @nedos, @i0n1c, @aionescu, @therealsaumil, etc, and it helps support REcon in Europe. Recommended. recon.cx/2018/brussels/trainings/
subgraph reposted
 Anders Fogh
@anders_fogh
This talk I'd love to see...
 Tim Blazytko
@mr_phrazer
We present our research on deobfuscation also at REcon Brussels (CC @dwuid)
 REcon Brussels
@reconbrx
...A short break in the static...
The first round of REcon BRX 2018 talks has been selected, the CFP extended until Nov. 27th, and @reconmtl 2017 recordings released!
Full Announcement: recon.cx/2018/brussels/news/2017/11/21/RECON-BRX-2018-Fir…
subgraph reposted
 Stephen A. Ridley
@s7ephen
Been making my way through this over the last few weeks of travel....and holy sh*t this book is a home run @billpollock ! huge props (and thanks) to @veorq for a much needed book.

subgraph reposted
 x0rz
@x0rz
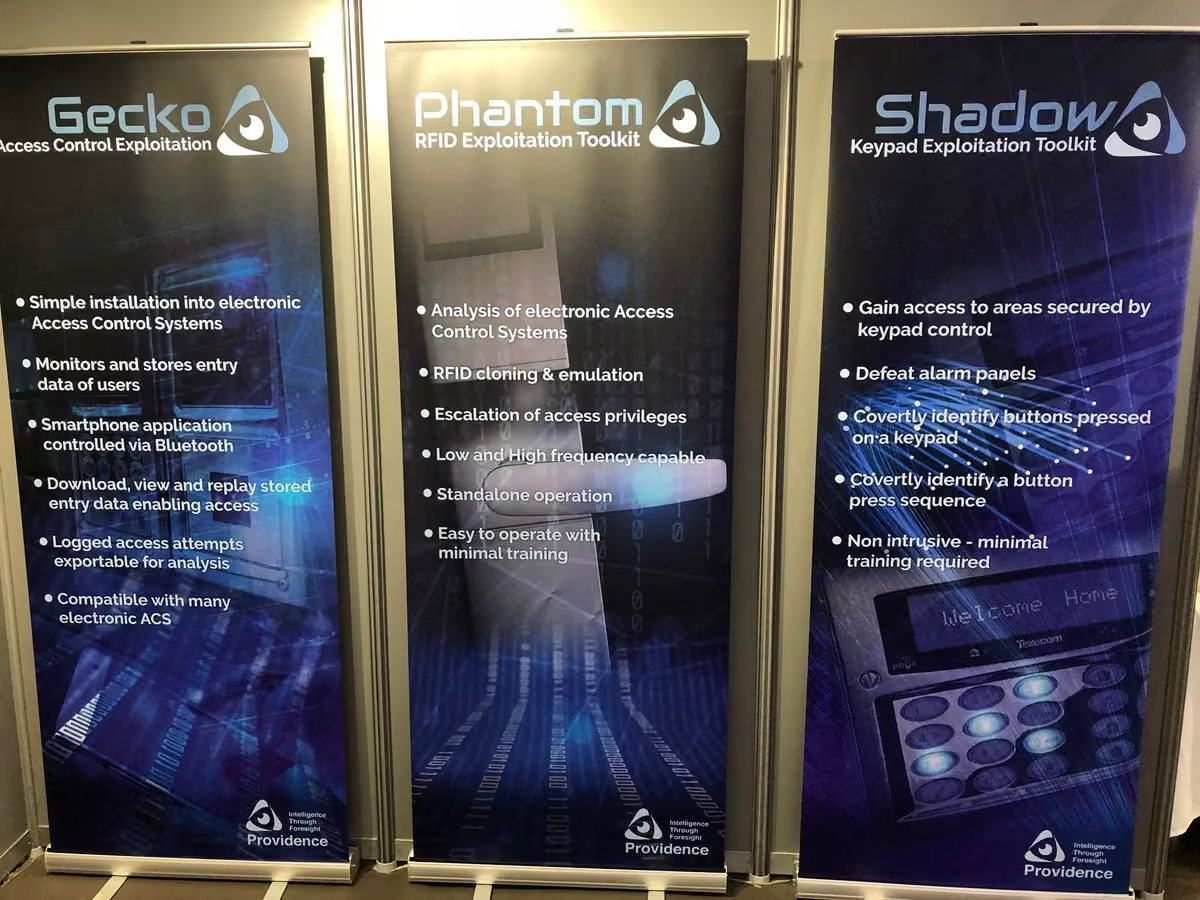
Milipol, the only place you’ll find people selling you guns and bulletproof vests. Malware and « threat intelligence » services. Milking the cow both ways.

subgraph reposted
 Julia Angwin
@JuliaAngwin
Facebook discriminatory ads thread 👇🏼
 ProPublica
@propublica
1/ Earlier this year Facebook said it had rolled out a system that would catch advertisers who tried to buy housing, credit and employment ads that excluded people by race.
We tested it. Our discriminatory ads for rental apartments sailed through.
propub.li/2mPl29n
subgraph reposted
 Forbes
@Forbes
Uber paid hackers $100,000 for silence after October 2016 cyberattack that exposed 57 million people's data on.forbes.com/6013D8F1f

subgraph reposted
REcon Brussels
@reconbrx
...A short break in the static...
The first round of REcon BRX 2018 talks has been selected, the CFP extended until Nov. 27th, and @reconmtl 2017 recordings released!
Full Announcement: recon.cx/2018/brussels/news/2017/11/21/RECON-BRX-2018-Fir…
subgraph reposted
 Matt Miller
@epakskape
SRD blog: Clarifying the behavior of mandatory ASLR blogs.technet.microsoft.com/srd/2017/11/21/clarifying-the…
subgraph reposted
 Juliano Rizzo
@julianor
enabling EMET since 2012 was completely useless? or just not very effective?
subgraph reposted
 Will Harris
@parityzero
Intel advisory generator: "Multiple unspecified issues in unspecified component in unspecified platform of unspecified version allows unspecified process to access privileged content via unspecified vector."
subgraph reposted
subgraph reposted
 eQualitie - digital security for a civil society
@eQualitie
Applications for the bot hunting team with Deflect Labs [1] close Thursday. Consider or RT equalit.ie/job-post/bot-hunters [1] docs.deflect.ca/en/latest/deflect_labs.html
subgraph reposted
 The New York Times
@nytimes
Skype has vanished from app stores in China, including Apple's www.nytimes.com/2017/11/21/business/skype-app-china.html?…
subgraph reposted
 Motherboard
@motherboard
Google chief says Google News will start engineering Russian propaganda out of the feed motherboard.vice.com/en_us/article/pa39vv/eric-schmidt-sa…

subgraph reposted
 Alexander Popov
@a13xp0p0v
My talk at @LinuxPiter: How STACKLEAK improves Linux kernel security. I credit @paxteam & show why mainline needs it it-events.com/en/events/9745/materials/2344

subgraph reposted
 AIfredo 0rtega
@ortegaalfredo
Indetectable, bios-level remote code exec on all 6th 7th and 8th intel platforms (needs admin access, for now 😓)
 Mark Ermolov
@_markel___
the Apocalypse begins: Multiple buffer overflows in Intel CSME including with remote vector
security-center.intel.com/advisory.aspx?intelid=INTEL-SA-…
subgraph reposted
 radare
@radareorg
“Radare Explorations” the book. www.gitbook.com/book/monosource/radare2-explorations/details
subgraph reposted
 David Wong
@cryptodavidw
An Ethereum Smart Contract CTF! This thing is freaking awesome! ethernaut.zeppelin.solutions/level/0xdf51a9e8ce57e7787e4a…
subgraph
@subgraph
The @rootme_org challenges are awesome, recommended. Nice work. 👇🏼👇🏼
 Root-Me
@rootme_org
Full ARM exploitation series on Root-Me. Never stop learning!
Stack, heap, fmt string, UAF, race cond, kernel...
www.root-me.org/en/Challenges/App-System/


subgraph reposted
subgraph reposted
 Azeria
@Fox0x01
Finally, Azeria-Lab-VM v1 is ready for download: azeria-labs.com/arm-lab-vm/
VMware image, OS: Ubuntu, QEMU running ARMv6, ready-to-play.
Here are some root-me ARM exploitation challenges: www.root-me.org?page=recherche&lang=en&recherche=ARM
I also included a quick guide on how to get started:

subgraph reposted
 Erik Bosman @brainsmoke@mastodon.social
@brainsmoke
I've uploaded some of my old 'Proofs-by-Construction' github.com/brainsmoke/pub-archive/tree/master/proofs_by_c… (CVE-2009-2629, nginx & CVE-2012-0809, @joernchen's sudo bug) in the hope it might be useful for software defense evaluations (it was for me :-)
subgraph reposted
 Ange
@angealbertini
ICYMI this is a walkthrough of the file formats aspects for the Pwnie Award 2017 of the best Crypto Attack.
speakerdeck.com/ange/exploiting-hash-collisions
I invite all file crafters to have a look and give me feedback.
subgraph
@subgraph
Beyond problems of seemingly arbitrary conduct enforcement and a lack of recourse, Twitter “verification” is part of a broader tiering of identity status online across social platforms.
 Daniel Hannan
@DanielJHannan
Twitter may regret de-verifying people of whom it disapproves. Until now, a blue tick simply meant authentication, but henceforth it implies endorsement. Suddenly, Twitter is in the ideology business.
subgraph reposted
x0rz
@x0rz
Chrome OS exploit abusing WebAsm. Full privesc w/ PageState, awk injection and crash reporter (multiple vulnerabilities leading to root RCE), rewarded $100k. Pretty amazing. bugs.chromium.org/p/chromium/issues/detail?id=766253
subgraph reposted
x0rz
@x0rz
hxxps://accounts.na02.safelinksprotectionsoutlook[.]com/
DNS registrar = Google (registered 3 weeks ago)
IP = Microsoft (Azure?)
Template displaying localized text, APT #phishing? 🤔 cc @msftsecresponse
 subgraph
@subgraph
This was clearnet browser instance, not Tor or VPN. Reminder that today, when you are not logged into a Google or Facebook account, you are a guest on the Internet.
subgraph
@subgraph
Seen today when trying to do a simple search:
"We'll need you to do this before you can continue using Google services"
 subgraph
@subgraph
Been asked why Monero, not Zcash? Monero wasn’t packaged, Zcash is, so we did it ourselves. SGOS users can add Zcash repo: github.com/zcash/zcash/wiki/Debian-binary-packages
subgraph
@subgraph
Seen today when trying to do a simple search:
"We'll need you to do this before you can continue using Google services"
subgraph reposted
 Joshua Hill
@p0sixninja
what makes an exploit great? number of systems affected, format of the code, ingenuity of exploitation?
subgraph reposted
 Halvar Flake
@halvarflake
I gave a keynote at zeronights about ML/AI and security. Slides are here: docs.google.com/presentation/d/16BWLRm4aNdxToJO-_63s1gLlw… - Lots of opinions to disagree with.
subgraph reposted
 emdel
@emd3l
Hardentools v1.0 is out! -- github.com/securitywithoutborders/hardentools/releases/ta…
subgraph reposted
 Francisco Ribeiro
@blackthorne
KernelAddressSanitizer (KASAN) - a dynamic memory error detector for finding use-after-free and out-of-bounds bugs in Linux kernel. github.com/google/kasan/wiki
subgraph reposted
 j00ru//vx
@j00ru
The joy of ancient font driver code... this is by far the most crazy/strange KASLR bypass I've ever found. It's a shame this & related issue bugs.chromium.org/p/project-zero/issues/detail?id=1398 will never be fixed on Windows 7 and 8.
Project Zero Bugs
@ProjectZeroBugs
Windows Kernel ATMFD.DLL NamedEscape 0x2511 pool address derivation from entropy accumulator bugs.chromium.org/p/project-zero/issues/detail?id=1401
subgraph reposted
 Dmitriy Evdokimov
@evdokimovds
RCE (CVE-2017-11882):
⚠️all the MS Office versions
⚠️all the MS Windows versions
⚠️x86/x86_64
⚠️does not require any interaction with a user
⚠️does not interrupt a user’s work with MS Office
❗️with stable exploitation ;) x.com/_embedi_/status/930498911676108801
subgraph reposted
 Tails
@Tails_live
Tails 3.3 is out: tails.boum.org/news/version_3.3, with fixes to Tails Installer, better accessibility, updated Tor, and more.
subgraph reposted
 Mozilla
@mozilla
Today we're releasing the biggest changes to Firefox since it launched 13 years ago. And it's fast.
Get the new Firefox: fast, for good.
mzl.la/2jolNon
subgraph
@subgraph
Monero test .deb packages available for download. Try it out, let us know if there are any issues before we drop them into our repo. subgraph.com/sgos/documentation/monero/ cc @fluffypony
subgraph reposted
 Adam Langley
@agl__
"Armv8.4-A adds a flag … indicating that you want the execution time of instructions to be independent of the data." community.arm.com/processors/b/blog/posts/introducing-201…
subgraph reposted
Arrigo Triulzi
@cynicalsecurity
Wu Cache Clan, “Automated Detection, Exploitation, and Elimination of Double-Fetch Bugs using Modern CPU Features” arxiv.org/abs/1711.01254
subgraph reposted
 argp
@_argp
Smashing the stack for fun and profit anniversary (8 Nov 1996)!
jmp offset-to-call; pop ...; call offset-to-pop; "/bin/sh"
phrack.org/issues/49/14.html
subgraph reposted
 Guillaume
@lapinhib0u
A method for exploiting #samba race CVE-2017-2619 using USB gadget gdelugre.github.io/2017/11/06/samba-path-pivot-attack/
subgraph reposted
 David Mirza Ahmad
@attractr
If that is “encrypting the Internet”, nothing means anything anymore.
subgraph reposted
 MyEtherWallet | MEW
@myetherwallet
🍿🍸😬 😬

subgraph reposted
David Mirza Ahmad
@attractr
Does this exist? Curated “best exploits of all time” collection spanning bug classes, for those interested in self-study. If not, I’ll make
subgraph reposted
 RustFest
@RustFest
You can watch all our amazing talks from #rustfest Zurich now on the @rustlang YouTube channel 🎥: www.youtube.com/playlist?list=PL85XCvVPmGQj9mqbJizw-zi-Eh…
subgraph reposted
 Igor Skochinsky (@IgorSkochinsky@infosec.exchange)
@IgorSkochinsky
SGX SDK includes PSDA.dalp which is a DAL applet. And iclsClient uses CLS (Capability Licensing Services) which is also an ME component
subgraph reposted
 Dan Guido
@dguido
The wallet contract was deployed 109 days ago yet initWallet was only called 22 hours ago, triggering the bug.
etherscan.io/address/0x863df6bfa4469f3ead0be8f9f2aae51c91…
subgraph reposted
 Patrick McCorry 🐋
@stonecoldpat0
Over 1 million ether (around $278,359,059 US) is the total impact of @ParityTech based on pastebin.com/ejakDR1f docs.google.com/spreadsheets/d/18dUFWIk84dmJngBoZG8BBk6S_…
subgraph reposted
Patrick McCorry 🐋
@stonecoldpat0
Omg. github.com/paritytech/parity/issues/6995 he owned it.

subgraph reposted
Juliano Rizzo
@julianor
🤦🏿♂️🤦🏿♂️🤦🏿♂️Parity multisig wallet (SC) bug "means that currently no funds can be moved" Decentralization revolution suspended, again.
Patrick McCorry 🐋
@stonecoldpat0
Looks like all funds are locked?? Oh my.
subgraph reposted
subgraph reposted
 Federico Bento
@uid1000
Hah, I also exploited that vuln, I used a different technique to get root though :)
www.youtube.com/watch?v=DfwOJIcV5ZA
subgraph reposted
 Salls
@chris_salls
Exploiting CVE-2017-5123 with full protections. SMEP, SMAP, and the Chrome Sandbox! salls.github.io/Linux-Kernel-CVE-2017-5123/
subgraph reposted
 Anastasios Pingios
@xorlgr
So, @grsecurity includes an awesome fix for a Linux kernel design flaw in mount which allows loading of arbitrary kernel modules. Nice!
subgraph
@subgraph
“An error with search results for certain terms”.
Search censorship mechanism malfunctioning?
subgraph reposted
 Dominic White 👾
@singe
“Submit articles about bug finding systems & tools or new bug classes. In general, do not submit articles about individual bugs.” 😍
Dan Guido
@dguido
It's been ~30 days since I started /r/SecurityEngineering, and I'm really happy with the results so far. www.reddit.com/r/securityengineering/
subgraph reposted
 Today In Infosec
@todayininfosec
1993: The Bugtraq mailing list was created by Scott Chasin.
subgraph reposted
 sergey bratus
@sergeybratus
"Bug archaeology" should be a thing, certainly, possibly a recurring column. @travisgoodspeed
subgraph
@subgraph
Lifetimes of thoughts, intents, fleeting curiosities, correspondence kept in redundant, bottomless storage, forever. x.com/dcuthbert/status/927226531734261761
subgraph
@subgraph
Cloud dystopia: quiet, opaque algorithmic manipulation based on location, identity, interests, who you cluster with.. how do we even know?
 Bi Pride UK
@BiPrideUK
Today @Twitter @TwitterSupport introduced a search filter blocking photo search on #bisexual and #bisexuality hashtags (among others). (1/2)

subgraph reposted
 Reproducible Builds
@ReproBuilds
diffoscope 88 has been released. Check out the changelog here: tracker.debian.org/news/883817
subgraph reposted
Ars Technica
@arstechnica
Stuxnet-style code signing is more widespread than anyone thought arstechnica.com/information-technology/2017/11/evasive-co… by @dangoodin001
subgraph reposted
Anastasios Pingios
@xorlgr
Very nice recent article from Phrack: Attacking JavaScript Engines: A case study of JavaScriptCore and CVE-2016-4622 phrack.org/papers/attacking_javascript_engines.html
subgraph
@subgraph
Also, our seccomp-bpf policies and runtime profiler only support 64-bit x86.
grimmware
@grimmware
Nope, the kernel patch sets aren’t available or complete for ARM :(
subgraph
@subgraph
In @subgraph OS, Tor Browser runs sandboxed w/own network namespace & virtual network interface, a design intended to avoid leaks like this.
x0rz
@x0rz
file:// links leaking user IP address on #tor Browser < v7.0.9 www.bleepingcomputer.com/news/security/tormoil-vulnerabil… #privacy #vulnerability
subgraph reposted
 Lorenzo Franceschi-Bicchierai
@lorenzofb
Company that owns NSO Group now owns a big certificate authority.
subgraph reposted
 Dan Pfeiffer
@danpfeiffer
There’s a real contradiction between Facebook saying Russian ads had no impact and Facebook telling brands to spend millions on Facebook ads
subgraph reposted
 Stuart Benson
@LeftHandStu
Why does Google Docs even have Terms of Service that pertain to content? How do you justify literal censorship like this?
subgraph
@subgraph
Cloud: algorithmic surveillance with chance of arbitrary suspension, no accountability, nobody to call. Even worse for users outside West.
 KJohnstonMH
@KimJohnston
Still suspended from @Facebook over wallposts from 2007. Ive emailed 6x for clarification over what the disputed posts are. Still no reply.
subgraph reposted
 Rachael Bale
@Rachael_Bale
Has anyone had @googledocs lock you out of a doc before? My draft of a story about wildlife crime was just frozen for violating their TOS.
subgraph reposted
 Select All
@selectall
Google Docs is inexplicably and frighteningly locking people out of documents for "Terms of Service violations" slct.al/2z20EEl
subgraph reposted
 Sarah K Moir is on Mastodon
@smorewithface
Who gives you the Internet? thisisimportant.net/2017/10/27/who-gives-you-the-internet/
subgraph reposted
 iVentures
@iVenturesON
It's hard to get content into China, and it's hard to do business in China. That's what we're here for." #alibabacloud #iventures
subgraph reposted
Mathias Krause | @minipli@infosec.exchange
@_minipli
Here comes v4.9.59-unofficial_grsec: github.com/minipli/linux-unofficial_grsec/releases/tag/v4…
subgraph reposted
Sarah K Moir is on Mastodon
@smorewithface
relevant: thisisimportant.net/category/borders-on-the-web/ and www.orbooks.com/catalog/splinternet-by-scott-malcomson/
subgraph
@subgraph
Fracture lines deepen, “splinternet” future seems inevitable. At least three “Internets” serving cultural spheres: Chinese, Russian, “West”.


subgraph reposted
REcon Brussels
@reconbrx
The first round of the CFP for Recon Brussels is ending October 30 (next Monday) and the CFP closes on November 20 recon.cx/2018/brussels/cfp/
subgraph reposted
 Techmeme
@Techmeme
McAfee says it will no longer let governments review its source code, following Symantec www.reuters.com/article/us-usa-cyber-russia-mcafee/mcafee… www.techmeme.com/171026/p16
subgraph reposted
Mathias Krause | @minipli@infosec.exchange
@_minipli
The unofficial grsec repo has a FAQ now: github.com/minipli/linux-unofficial_grsec/wiki
subgraph reposted
Mathias Krause | @minipli@infosec.exchange
@_minipli
v4.9.57-unofficial_grsec: github.com/minipli/linux-unofficial_grsec/releases/tag/v4…
subgraph reposted
 Thomas @thomascovenant@infosec.exchange
@NGC_3572
They released the first open beta of the new VPN client in Rust today. Woo hoo! #rust
 Mullvad.net
@mullvadnet
Our new #vpn app in beta is available for download! Got macOS? Be an early adopter. mullvad.net/guides/beta-app/ #mullvad #privacy #uxdesign

subgraph reposted
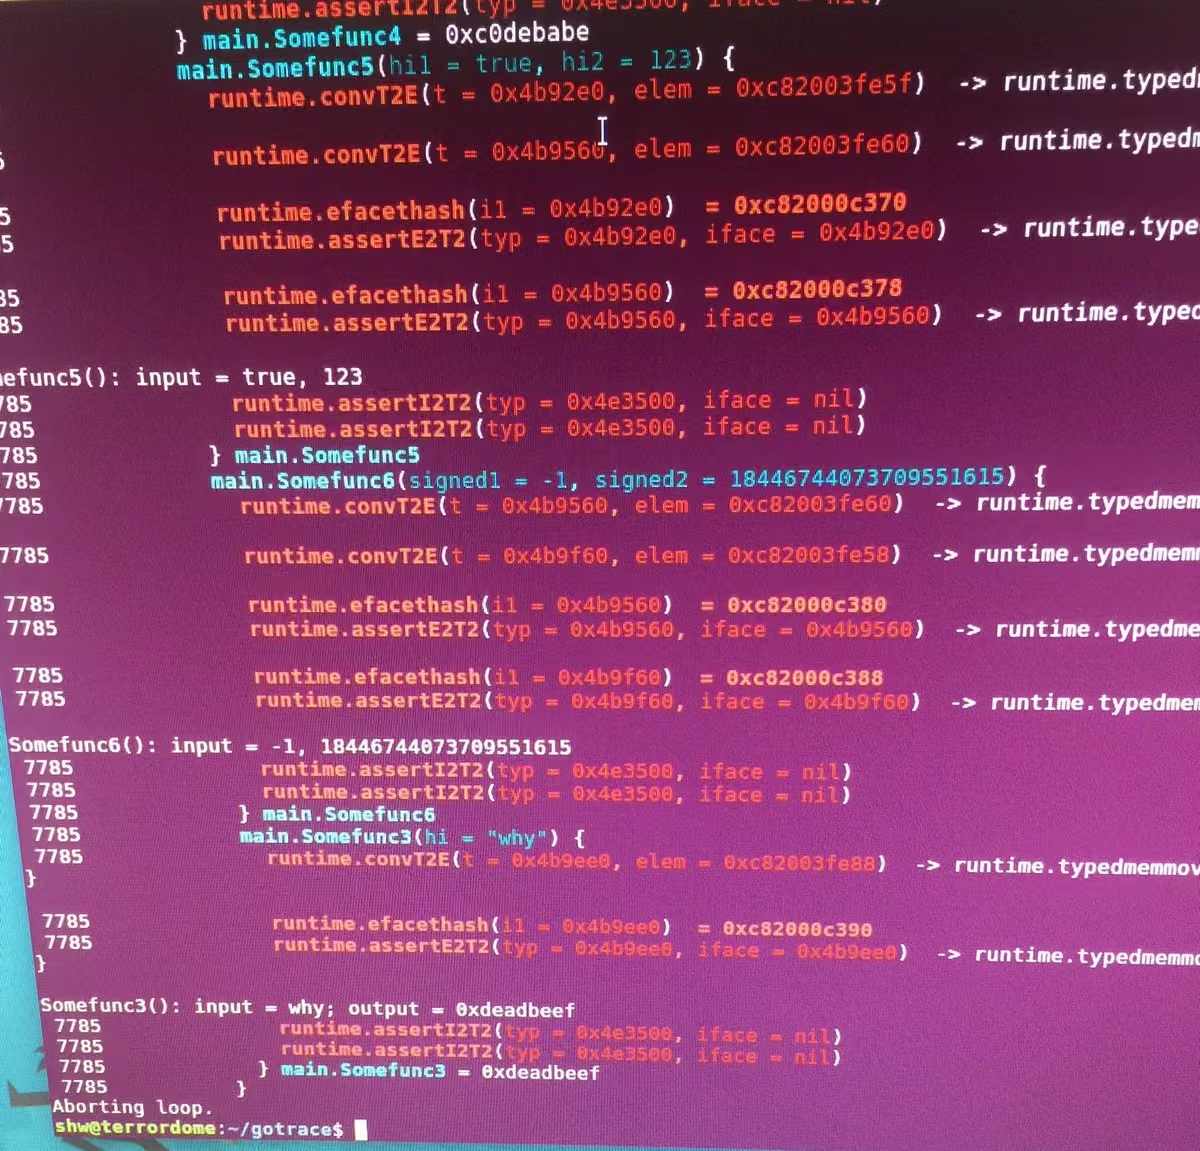
 Stephen Watt
@uT_Infection
Support for funcs w multiple return values working. Wonder how much of this I can successfully write without ever viewing golang ABI docs...

subgraph reposted
 ScyllaDB
@ScyllaDB
Learn about the different I/O access methods for Linux, what we chose for Scylla, and Why from @AviKivity
www.scylladb.com/2017/10/05/io-access-methods-scylla/
#nosql
subgraph reposted
Stephen Watt
@uT_Infection
Does a runtime golang binary tracer exist? Hopefully not, so that what I’ve gotten working so far isn’t a complete waste of my time...
subgraph reposted
Mathias Krause | @minipli@infosec.exchange
@_minipli
v4.9.51-unofficial_grsec: github.com/minipli/linux-unofficial_grsec/releases/tag/v4…
subgraph
@subgraph
New ISO available for download: subgraph.com/sgos/download/index.en.html
subgraph reposted
 CCC Events
@ccc
Event Blog: 34C3: Call for Participation and Submission Guidelines events.ccc.de/2017/09/19/34c3-call-for-participation-and-… #ccc
subgraph reposted
REcon Brussels
@reconbrx
You can now grab your tickets for REcon BRX 2018, the rate is discounted for early registration! tickets.recon.cx/reconeu/reconbrx18/
subgraph reposted
REcon Brussels
@reconbrx
──├■│■│┌┘■┘ RECON Brussels CFP - recon.cx/2018/brussels/cfp ─┐■┘┌──┘┌┘ ┌┘└├■──├■
subgraph reposted
Mark Ermolov
@_markel___
We did it: Intel ME 11.x arbitrary code execution, #bheu www.blackhat.com/eu-17/briefings/schedule/
subgraph reposted
grsecurity
@grsecurity
Highlights from our 4.12 release: grsecurity.net/grsecurity_4_12_updates.php
subgraph reposted
grsecurity
@grsecurity
Slight modification, more to come

subgraph reposted
 WithSecure Labs
@FSecureLabs
Ever needed to exploit a driver mmap handler? If so this detailed whitepaper by @MateuszFruba may help! labs.mwrinfosecurity.com/publications/kernel-driver-mmap-…
subgraph
@subgraph
A good friend and SGOS tester/user found a little nostalgic treasure 😏
 subgraph
@subgraph
Recent Oz update in repo should fix long standing clipboard issue some users had. Please help test and report if problems persist.
subgraph reposted
grsecurity
@grsecurity
#grsecurity mentioned in NIST draft of "Security Assurance Requirements for Linux Application Container Deployments" csrc.nist.gov/publications/drafts/nistir-8176/nistir8176-…

subgraph reposted
Mathias Krause | @minipli@infosec.exchange
@_minipli
Here comes v4.9.46-unofficial_grsec: github.com/minipli/linux-unofficial_grsec/releases/tag/v4…
subgraph reposted
argp
@_argp
The public release of our shadow v2 jemalloc exploitation tool with support for Android (both ARM32 and ARM64): census-labs.com/news/2017/08/22/shadow-v2-release/
subgraph reposted
grsecurity
@grsecurity
RAP uses a combination of probabilistic and deterministic techniques to protect returns, and can be read about here: pax.grsecurity.net/docs/PaXTeam-H2HC15-RAP-RIP-ROP.pdf
subgraph reposted
grsecurity
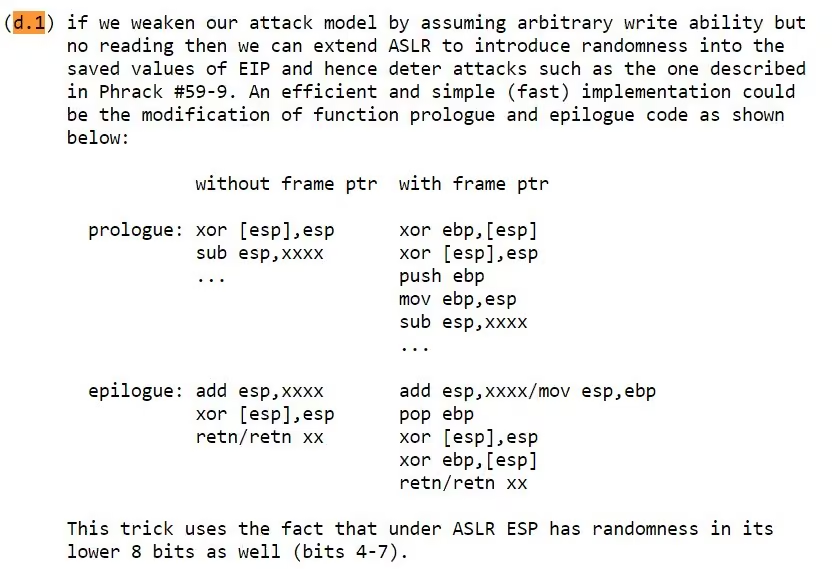
@grsecurity
Interested in a technical analysis of RETGUARD? See d.1 in pax.grsecurity.net/docs/pax-future.txt from 2003 when it was first identically described:
subgraph reposted
Mathias Krause | @minipli@infosec.exchange
@_minipli
v4.9.44-unofficial_grsec: github.com/minipli/linux-unofficial_grsec/releases/tag/v4…
subgraph reposted
 Anil Kurmus
@kurmus
Link to our paper: www.usenix.org/system/files/conference/woot17/woot17-pape… and demo of the attack: www.youtube.com/watch?v=Mnzp1p9Nvw0
subgraph reposted
 Chris “Law Dork” Geidner
@chrisgeidner
Wow. This DOJ request: VISITORS. www.dreamhost.com/blog/we-fight-for-the-users/ (h/t @bartongellman)

subgraph reposted
Open Source Security mailing list
@oss_security
Re: Linux kernel: CVE-2017-1000112: Exploitable memory corruption due to UFO to non-UFO path switch: Posted by… seclists.org/oss-sec/2017/q3/286
subgraph
@subgraph
Regular reminder that unpriv user ns (disabled w/grsec) is a kernel security disaster (nice exploit @andreyknvl).

 Andrey Konovalov
@andreyknvl
Linux kernel local root exploit for CVE-2017-1000112 github.com/xairy/kernel-exploits/blob/master/CVE-2017-100…
subgraph reposted
Andrey Konovalov
@andreyknvl
Linux kernel local root exploit for CVE-2017-1000112 github.com/xairy/kernel-exploits/blob/master/CVE-2017-100…
subgraph reposted
Mathias Krause | @minipli@infosec.exchange
@_minipli
...next one: v4.9.43-unofficial_grsec github.com/minipli/linux-unofficial_grsec/releases/tag/v4…
subgraph reposted
Mathias Krause | @minipli@infosec.exchange
@_minipli
New weekend, new release: v4.9.42-unofficial_grsec github.com/minipli/linux-unofficial_grsec/releases/tag/v4…
subgraph reposted
x0rz
@x0rz
APT28 using Responder and ETERNALBLUE to pwn hotels. Хороший выбор! 👌 www.fireeye.com/blog/threat-research/2017/08/apt28-target… #apt28 #pentesting
subgraph reposted
x0rz
@x0rz
(n+1)sec library for off-the-record (deniable authenticated forward secure confidential) multiparty messaging github.com/equalitie/np1sec
subgraph reposted
 Mobile Security
@mobilesecurity_
EggShell: iOS/macOS post exploitation surveillance pentest tool
#mobilesecurity #iossecurity
github.com/neoneggplant/EggShell

subgraph reposted
CCC Events
@ccc
Event Blog: 34C3 Presale events.ccc.de/2017/08/09/34c3-presale/ #ccc
subgraph reposted
 IACR
@IACR_News
#eprint On Improving Integer Factorization and Discrete Logarithm Computation using Partial Triangulation: F Boudot ia.cr/2017/758
subgraph reposted
 Nicolas Krassas
@Dinosn
Race For Root: The Analysis Of The Linux Kernel Race Condition Exploit (SHA2017) cdn.media.ccc.de/events/SHA2017/h264-sd/SHA2017-295-eng-R…
subgraph reposted
x0rz
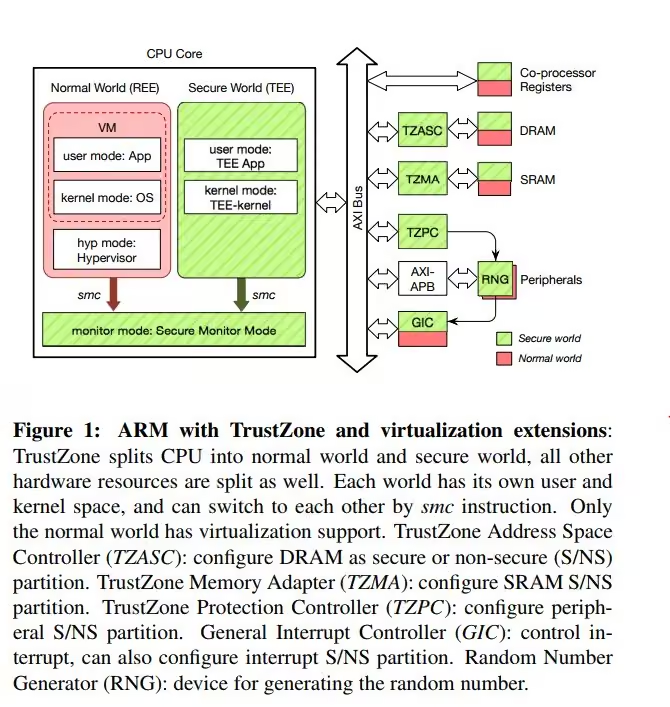
@x0rz
vTZ: Virtualizing ARM TrustZone ipads.se.sjtu.edu.cn/lib/exe/fetch.php?media=publications… (PDF) #arm #trustzone #hardening
subgraph reposted
 azet
@a_z_e_t
The recording of my talk on CSPRNGs/RNGs in Operating Systems & Programming Languages @SHA2017Camp is up:
www.youtube.com/watch?v=Az_5vpHW-CM #sha2017
subgraph reposted
Mathias Krause | @minipli@infosec.exchange
@_minipli
v4.9.41-unofficial_grsec is ready: github.com/minipli/linux-unofficial_grsec/releases/tag/v4…
subgraph reposted
 Alex Ionescu
@aionescu
And it's up! www.alex-ionescu.com?p=340
Alex Ionescu
@aionescu
What if I told you... everything they told you about X64 was a lie? Getting ready for a new post. LDTs and Segmentation are alive and well.

subgraph reposted
Alex Ionescu
@aionescu
Contradictory sentences in CPU manuals and a new blog post on how segmentation is alive and well on x64 systems: www.alex-ionescu.com?p=340
 subgraph
@subgraph
We had runtime peripheral (u2f, hardware wallet) support for app sandboxes prototyped earlier this year, something should be released soon.
subgraph
@subgraph
There is a recent test ISO that fixes the UEFI issue, but we encountered a problem with Coreboot that's preventing a release. DM for DL URL.
subgraph reposted
Daniel Gruss
@lavados
Our paper on mitigating cache attacks using TSX is now online! x.com/flxflx/status/893114534583574528 gruss.cc/files/cloak.pdf
 Felix Schuster
@flxflx
Uploaded our paper on mitigating cache side-channel attacks using TSX that will appear in @USENIXSecurity: www.microsoft.com/en-us/research/publication/strong-effic…
subgraph reposted
 Frank
@jedisct1
Dan Boneh’s class on cryptocurrencies, blockchains, and smart contracts crypto.stanford.edu/cs251/
subgraph reposted
 Trail of Bits
@trailofbits
Microsoft didn’t sandbox Windows Defender, so I did blog.trailofbits.com/2017/08/02/microsoft-didnt-sandbox-w…
subgraph reposted
 @pagetable@mastodon.social
@pagetable
62 Reverse-Engineered C64 Assembly Listings www.pagetable.com?p=904
subgraph reposted
Nicolas Krassas
@Dinosn
Linux Heap Exploitation Intro Series: Used and Abused – Use After Free sensepost.com/blog/2017/linux-heap-exploitation-intro-ser…
subgraph reposted
 Paul Triolo
@pstAsiatech
Alibaba's cloud services going global, operating in 65 languages. Newest data centers India, Indonesia, Malaysia it.people.com.cn/n1/2017/0611/c1009-29331911.html
 subgraph
@subgraph
"Alibaba Cloud has recorded eight consecutive quarters of triple-digit growth" www.alizila.com/key-takeaways-from-alibabas-2017-investor…
subgraph reposted
 The Hacker News
@TheHackersNews
Russia Parliament Passes Bill to Ban Proxy Services, #tor And VPNs To Purge Extremist Content thehackernews.com/2017/07/russian-ban-proxy-vpn-tor.html

subgraph reposted
 The Guardian
@guardian
China moves to block internet VPNs from 2018 www.theguardian.com/world/2017/jul/11/china-moves-to-bloc…
subgraph reposted
 Alex Kuleshov
@0xAX
Build an 8-bit computer from scratch - eater.net/8bit/
subgraph reposted
 James Forshaw
@tiraniddo
Nice .net serialization research and useful gadgets from @pwntester www.blackhat.com/docs/us-17/thursday/us-17-Munoz-Friday-T…
subgraph reposted
 Orange Tsai 🍊
@orange_8361
My Black Hat Case Study
How I Chained 4 Vulns on GitHub Enterprise, From SSRF Execution Chain to RCE! blog.orange.tw/2017/07/how-i-chained-4-vulnerabilities-on…
#bhusa #defcon
subgraph reposted
 hanno
@hanno
Certificate Transparency: Hacking web applications before they are installed (about my @defcon talk) www.golem.de/news/certificate-transparency-hacking-web-ap…
subgraph reposted
 Min(Spark) Zheng
@SparkZheng
#defcon# macOS/iOS Kernel Debugging and Heap Feng Shui: github.com/zhengmin1989/MyArticles/blob/master/PPT/DEFCON…

subgraph reposted
Lorenzo Franceschi-Bicchierai
@lorenzofb
During the talk yesterday I asked Google if they had reached out to law enforcement or Equus before shutting down spyware, answer was "no."
subgraph reposted
 0x5A1F
@Saif_Sherei
Will be disclosing a new windows kernel GDI object abuse technique and and a new EoP N-Day at 13:00 @defcon 101 track hope to see you there
subgraph
@subgraph
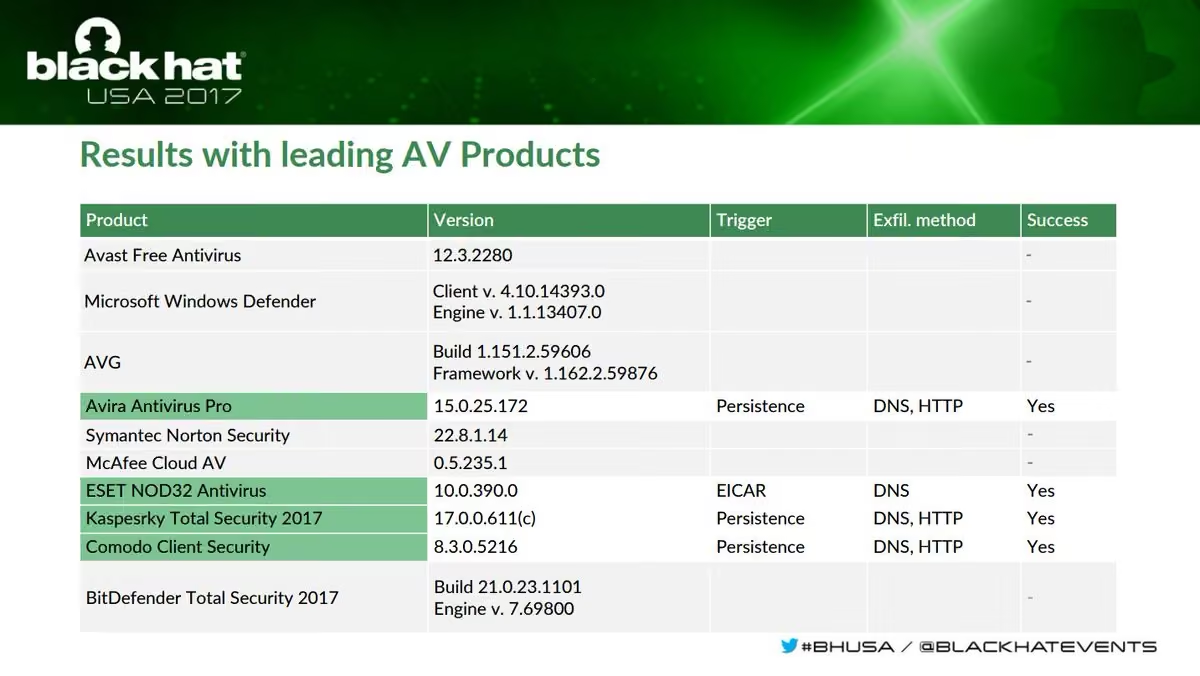
Clever enterprise exfil path courtesy of the computer security / anti-virus industry. H/T @x0rz www.blackhat.com/docs/us-17/thursday/us-17-Kotler-The-Adv…


subgraph reposted
x0rz
@x0rz
Air-gapped data exfiltration via cloud AV sandboxes 👏👌 www.blackhat.com/docs/us-17/thursday/us-17-Kotler-The-Adv… (PDF, slides) #blackhat #airgap #malware #antivirus
subgraph reposted
Thomas H. Ptacek
@tqbf
Contender for scariest talk at Black Hat is Luca’s Electron talk: the Electron security model is batshit, XSS->RCE.
subgraph reposted
Dmitriy Evdokimov
@evdokimovds
Intel ME firmware loader plugin for IDA Pro github.com/embedi/meloader
subgraph reposted
Anders Fogh
@anders_fogh
New blog post: [Technical] Negative Result: Reading Kernel Memory From User Mode. cyber.wtf/2017/07/28/negative-result-reading-kernel-memor…
subgraph reposted
 Binni Shah
@binitamshah
A survey of BSD kernel vulnerabilities (DEFCON) : media.defcon.org/DEF CON 25/DEF CON 25 presentations/DEFC… (Slides)
subgraph reposted
Mathias Krause | @minipli@infosec.exchange
@_minipli
Just pushed v4.9.40-unofficial_grsec: github.com/minipli/linux-unofficial_grsec/releases/tag/v4…
subgraph reposted
Igor Skochinsky (@IgorSkochinsky@infosec.exchange)
@IgorSkochinsky
cool stuff! BTW @xoreaxeaxeax : you mention db{e0-e1} as undocumented but they seem to be known: sandpile.org/x86/opc_fpu.htm
 Tal Liberman
@Tal_Liberman
An x86 CPU fuzzer to find hidden instructions and CPU bugs
#fuzzing #cpu #x86
github.com/xoreaxeaxeax/sandsifter
subgraph reposted
Paul Triolo
@pstAsiatech
China’s Next Target: U.S. Microchip Hegemony www.wsj.com/articles/chinas-next-target-u-s-microchip-heg…
subgraph reposted
Bruce Leidl
@bleidl
One of my favourite genres of Horror literature is CPU errata

subgraph reposted
 Morten Schenk
@Blomster81
Just finished presentation on Windows 10 kernel exploitation at @BlackHatEvents slides and code is on GitHub github.com/MortenSchenk/BHUSA2017
subgraph reposted
 Nitay Artenstein
@nitayart
Broadpwn: The First WiFi Worm. A full writeup blog.exodusintel.com/2017/07/26/broadpwn/
subgraph reposted
 Yosuke HASEGAWA
@hasegawayosuke
Slide for my talk from now "ELECTRON - Build cross platform desktop XSS" is already published at here. utf-8.jp/cb2016 #codeblue_jp
subgraph reposted
 AbdulAziz Hariri
@abdhariri
This is going to be a fun talk :)
 TrendAI Zero Day Initiative
@thezdi
Excited to see @abdhariri & @kernelsmith accepted to @derbycon - VMWare Escapology: How to Houdini The Hypervisor www.derbycon.com/blog/derbycon-speaker-announcements/
subgraph reposted
Open Source Security mailing list
@oss_security
CVE-2017-7541: Linux kernel: Memory corruption due to a buffer overflow in brcmf_cfg80211_mgmt_tx(): Posted by… seclists.org/oss-sec/2017/q3/208
subgraph reposted
Mathias Krause | @minipli@infosec.exchange
@_minipli
v4.9.39-unofficial_grsec is out: github.com/minipli/linux-unofficial_grsec/releases/tag/v4…
subgraph reposted
 xamfp
@xamfp
People on /r/DNM were saying that Hansa was forcing users to enable javascript to register. Government private 0day perhaps?
subgraph reposted
 Tavis Ormandy
@taviso
Here is Cisco's advisory tools.cisco.com/security/center/content/CiscoSecurityAdvi…
subgraph reposted
Tavis Ormandy
@taviso
Multiple Cisco Webex remote code execution vulnerabilities, and working exploit bugs.chromium.org/p/project-zero/issues/detail?id=1324. Patch ASAP. 🐞
subgraph reposted
Mathias Krause | @minipli@infosec.exchange
@_minipli
Kind of on schedule, v4.9.38-unofficial_grsec ready to grab from github.com/minipli/linux-unofficial_grsec/releases/tag/v4… #grsecurity #community
subgraph reposted
grsecurity
@grsecurity
Announcing our latest release! grsecurity.net/grsecurity_4_11_updates.php
subgraph reposted
Bruce Leidl
@bleidl
You can also reach these vulns from evince as comic book, because comic book plugin is sketchy heap of shit
 Rio
@0x09AL
Two new CVEs.
CVE-2017-11189 : unrar-free Denial Of service.
CVE-2017-11190 : unrar-free Stack Buffer Overflow.
github.com/0x09AL/my-exploits/tree/master/pocs/unrar-free
subgraph reposted
 Felix Wilhelm
@_fel1x
If you use evince you should upgrade: bugzilla.gnome.org/show_bug.cgi?id=784630 drive-by RCE due to a cmd injection in their comic book handler ¯\_(ツ)_/¯
subgraph reposted
 Oliver Chang
@halbecaf
Made a short post about a v8 bug and exploit: halbecaf.com/2017/05/24/exploiting-a-v8-oob-write/
subgraph reposted
 Senrio
@XipiterSec
Neat

subgraph reposted
 tukan
@_2can
ptmalloc fanzine episode 05 - thread local caching in glibc malloc tukan.farm/2017/07/08/tcache/
subgraph reposted
Bruce Leidl
@bleidl
Most everybody underestimates the effectiveness of grsecurity. It completely shuts down almost every Linux kernel vulnerability.
subgraph reposted
 Hossein Lotfi
@hosselot
Details and exploitation of PwnFest 2016 VMware Workstation "Hearthstone" Vulnerability:
cansecwest.com/slides/2017/CSW2017_QinghaoTang_XinleiYing…
subgraph reposted
Bruce Leidl
@bleidl
I'm the voice of the original version of this. I hauled my desktop tower computer around the Core office looking for quiet place to record
 Greg Linares (Laughing Mantis)
@Laughing_Mantis
Why is it so hard to find the Core Impact "Agent Deployed" Sound file when i want to just drop it in a track
subgraph reposted
 phoenhex team
@phoenhex
5 bugs, 1 exploit -- the full Pwn2Own Safari sandbox wrap-up
phoenhex.re/2017-07-06/pwn2own-sandbox-escape
subgraph reposted
 Austin Hill
@austinhill
Canada announces Startup firendly accelerated visa for those w/ tech or biz skills www.axios.com/canada-aims-to-lure-talent-from-silicon-val… -great initiative @NavdeepSBains
subgraph reposted
 NPR
@NPR
6 US intel agency chiefs were asked in May if they'd be OK with Kaspersky software on their computers. All said no. www.npr.org/sections/parallels/2017/07/05/535651597/congr…
subgraph reposted
azet
@a_z_e_t
words of wisdom!
kerberos is old (v5 which all implementations are based upon: 1993) & has some flaws, but there're no competitors to date.
 Tony "Abolish ICE" Arcieri 🦀🌹
@bascule
Those who do not understand Kerberos are doomed to reinvent it... poorly eng.lyft.com/blessing-your-ssh-at-lyft-a1b38f81629d
subgraph reposted
Tails
@Tails_live
Tails 3.0.1 is out, with important security fixes: tails.boum.org/news/version_3.0.1/
subgraph reposted
 Vitaly Nikolenko
@vnik5287
uploaded my last workshop Linux kernel bug (addr_limit/set_fs bug + stack info leak) walkthrough www.youtube.com/watch?v=UFakJa3t8Ls
subgraph reposted
 raptor
@0xdea
You can thank me later that I saved your Fedora boxes
from an ssh 0day —@steaIth
c-skills.blogspot.it/2017/06/opmsg-saving-you-from-openss…
subgraph reposted
 ashkan soltani
@ashk4n
“You have no reasonable expectation of privacy because browsers”
finance.yahoo.com/news/facebook-beats-privacy-lawsuit-u-1…

subgraph reposted
 Olivia Solon
@oliviasolon
Facebook's counter-terrorism team (staffed by contractors) has clearance to track the location & read all the private messages of its users

subgraph reposted
 ZeroNights
@ZeroNights
#zeronights 2017 CFP is OPEN: General program/Workshops/FastTrack/DefensiveTrack. Submit your talk 2017.zeronights.org/news/cfp-is-now-open/

subgraph reposted
Nicolas Krassas
@Dinosn
Complete break of RSA-1024 as implemented in Libgcrypt eprint.iacr.org/2017/627.pdf
subgraph reposted
Halvar Flake
@halvarflake
Great read about the Ocaml-triggered CPU bug, and important whenever somebody thinks about "cloud security": medium.com/ahrefs/skylake-bug-a-detective-story-ab1ad2beddcd
subgraph reposted
David Mirza Ahmad
@attractr
First stab @ UI for configuring Tor bridges, proxies, etc, that @uT_Infection & I are working on. Nothing complex, but useful & works.

subgraph reposted
 Hannes Grassegger
@HNSGR
How the world's largest censoring algorithm was born. My latest @Facebook investigation with @ProPublica
Julia Angwin
@JuliaAngwin
My latest investigation: Facebook’s secret censorship algorithm that protects white men more than black children.
www.propublica.org/article/facebook-hate-speech-censorshi…
subgraph reposted
 Justin Seitz
@jms_dot_py
Use-After-Silence: Exploiting a quietly patched UAF in VMware www.thezdi.com/blog/2017/6/26/use-after-silence-exploitin… <- awesome post by @abdhariri
subgraph reposted
 David Barroso
@lostinsecurity
It’s always great to listen to @halvarflake thoughts on exploits mitigations at @EuskalHack


subgraph reposted
Bruce Leidl
@bleidl
If you ever wonder why grsecurity is not in upstream Linux here's one reason.
www.spinics.net/lists/kernel/msg2540934.html
subgraph reposted
 Hardened-GNU/Linux
@hardenedlinux
More CONFIG_VMAP_STACK vulnerabilities, refcount_t UAF, and an ignored Secure Boot bypass / rootkit method: www.openwall.com/lists/oss-security/2017/06/24/1
subgraph reposted
Igor Skochinsky (@IgorSkochinsky@infosec.exchange)
@IgorSkochinsky
looks like ME11 Huffman compression is going to be solved soon: github.com/IllegalArgument/Huffman11
subgraph reposted
 HS.T - Hardware Security Training
@SecureHardware
We're opening our CFP. If you submit, you'll have a chance to take one of our hardware security trainings for free. hardwaresecurity.training/blog/cfp/
subgraph reposted
 Katja Bego
@katjabego
Another week of net politics (Macronleaks, Cambridge Analytica): read my piece from Jan about looming splinternet: thelongandshort.org/forecasts/the-end-of-the-web
subgraph reposted
Hossein Lotfi
@hosselot
Details of a Firefox use-after-free vulnerability + exploiting with shared array buffers:
phoenhex.re/2017-06-21/firefox-structuredclone-refleak
subgraph reposted
 TinySec
@TinySecEx
j00ru's method about kernel information leak , you can read and compare with my method www.iceswordlab.com/2017/06/14/Automatically-Discovering-…
j00ru//vx
@j00ru
Announcing Bochspwn Reloaded – a new kernel memory infoleak detector – and the REcon Montreal 2017 slides. j00ru.vexillium.org?p=3295
subgraph reposted
j00ru//vx
@j00ru
Announcing Bochspwn Reloaded – a new kernel memory infoleak detector – and the REcon Montreal 2017 slides. j00ru.vexillium.org?p=3295
subgraph reposted
Matt Miller
@epakskape
Some people mentioned they missed the technical SRD blog posts. We missed them too. Here's a new one (cc @R00tkitSMM)blogs.technet.microsoft.com/srd/2017/06/20/tales-from-the…
subgraph reposted
Bruce Leidl
@bleidl
NOP sliding into ROP gadgets is not a thing btw
 Bryan Steele 🦋
@canadianbryan
subgraph reposted
 Brandon Edwards
@drraid
I keep meaning to get that patch framed for my wall :D
subgraph reposted
 Markus Vervier
@marver
Impressive work by Guido Vranken: guidovranken.wordpress.com/2017/06/21/the-openvpn-post-au…
But the conclusion is wrong, you want to do a manual code auditing AND fuzzing.
subgraph
@subgraph
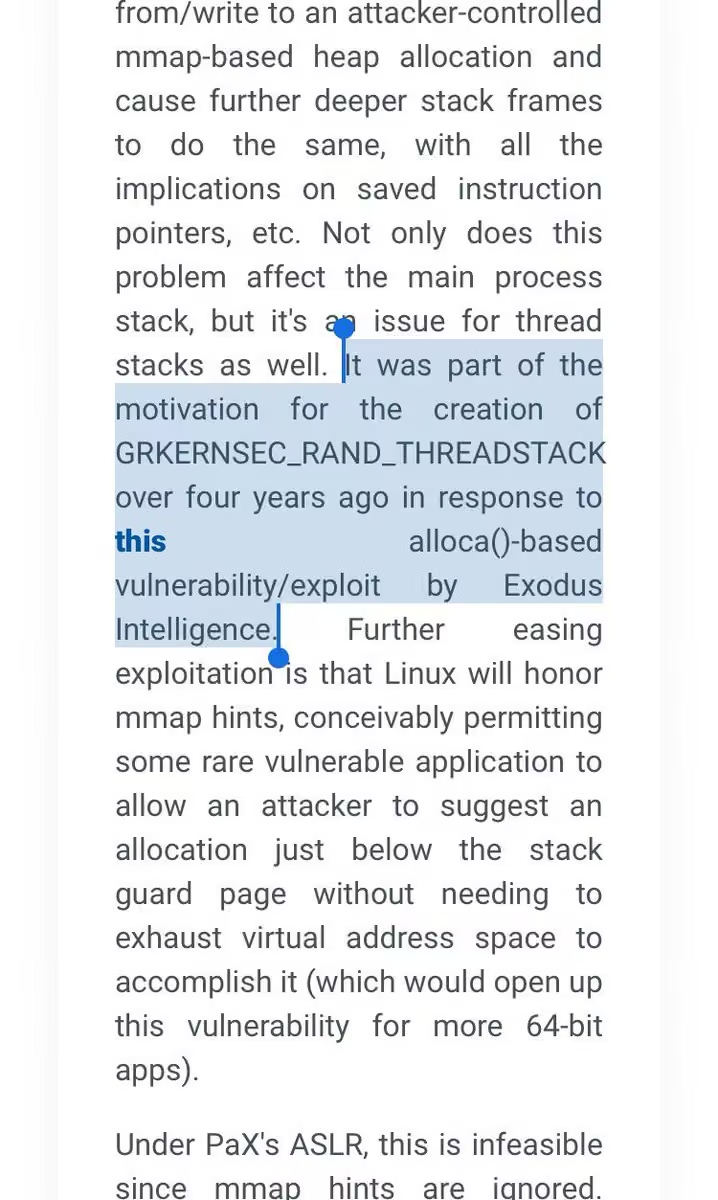
Example of the insight that comes from studying actual exploitation, including writing exploits and understanding those written by others.
 subgraph
@subgraph
We released a @subgraph OS update increasing stack guard-page size yesterday, deter_bruteforce already on by default github.com/subgraph/subgraph-sysctl-config/blob/master/fi…
subgraph
@subgraph
Grsecurity/PaX and the Stack Clash: www.qualys.com/2017/06/19/stack-clash/stack-clash.txt


subgraph reposted
Juliano Rizzo
@julianor
SGXBounds: memory safety for shielded execution blog.acolyer.org/2017/06/06/sgxbounds-memory-safety-for-s… exploits the small address space to add boundaries to pointers👍
subgraph reposted
 PaX Team
@paxteam
An Ancient Kernel Hole is (Not) Closed: grsecurity.net/an_ancient_kernel_hole_is_not_closed.php. A lesson in real non-embargoed security.
subgraph reposted
 Saul Procterm
@pozdnychev
Qualys Security Advisory: Stack Clash. 24 CVE, 7 PoCs, 7 LPE exploits; Linux/{Net,Free,Open}BSD/Solaris; i386/amd64: www.openwall.com/lists/oss-security/2017/06/19/1
subgraph reposted
Markus Vervier
@marver
General exploitability of stack exhaustion was known semi-public. I did initial research, decommissioning this now: github.com/x41sec/poc/blob/master/stack-overflow-threadre…
subgraph reposted
Markus Vervier
@marver
This is big research. Stack overflows (exaustion) _are_ exploitable in user space.
Saul Procterm
@pozdnychev
Qualys Security Advisory: Stack Clash. 24 CVE, 7 PoCs, 7 LPE exploits; Linux/{Net,Free,Open}BSD/Solaris; i386/amd64: www.openwall.com/lists/oss-security/2017/06/19/1
subgraph
@subgraph
See reproducible-builds.org. Our recent efforts have most @subgraph OS source packages also building reproducibly: github.com/subgraph/subgraph-debian-packages/blob/master/…
 Devil 9000 🔺
@devilish_flux
I'm sorry, what does reproducibly mean?
subgraph reposted
 The Debian Project
@debian
94% of the 24823 stretch source packages are reproducibly built tests.reproducible-builds.org/debian/reproducible.html #releasingstretch
subgraph reposted
 Tamir Bahar
@tmr232
A proper IDA Pro color scheme for #recon17
@reconmtl
github.com/tmr232/RECon2017

subgraph reposted
Mathias Krause | @minipli@infosec.exchange
@_minipli
v4.9.33-unofficial_grsec: github.com/minipli/linux-unofficial_grsec/releases/tag/v4…
subgraph reposted
x0rz
@x0rz
Here is how anyone can mimic a fake APT28 attack blog.0day.rocks/lets-get-fancy-with-false-flags-28eaabefeff6 #malware #opsec #apt28 #fancybear #emleaks
subgraph reposted
Mathias Krause | @minipli@infosec.exchange
@_minipli
Here comes v4.9.32-unofficial_grsec: github.com/minipli/linux-unofficial_grsec/releases/tag/v4… -- contains a RANDSTRUCT+gcc7 compile fix
#grsecurity #community
subgraph reposted
Hossein Lotfi
@hosselot
Exploit an "Unexploitable" Chrome bug: Full exploit for cve-2016-9651 used in pwnfest2016, slide (syscan360 2017):
github.com/secmob/pwnfest2016/
subgraph reposted
Tails
@Tails_live
Tails 3.0 is out: tails.boum.org/news/version_3.0 based on @Debian 9, brand new startup and shutdown, security improvements in depth, and more.

subgraph reposted
 Kim Zetter
@KimZetter
The Malware Used Against The Ukrainian Power Grid Is More Dangerous Than Anyone Thought - motherboard.vice.com/en_us/article/ukraine-power-grid-mal…
subgraph reposted
x0rz
@x0rz
Reverse engineering guide for beginners 0x00sec.org/t/re-guide-for-beginners-methodology-and-tool… #reverse
subgraph reposted
 John Lambert
@JohnLaTwC
Do APTs use remote management features in Intel chipsets to bypass host controls? Meet PLATINUM blogs.technet.microsoft.com/mmpc/2017/06/07/platinum-cont…


subgraph reposted
 CoyIM
@coyproject
We are proud to release CoyIM 0.3.8 with a number of fixes and improvements. Get it at coy.im !
subgraph reposted
REcon
@reconmtl
Hot off the presses! The REcon MTL 2017 Schedule has been released! recon.cx/2017/montreal/schedule/ See you all next week!
subgraph reposted
radare
@radareorg
The radare2 book can be downloaded here in EPUB, PDF, HTML, … www.gitbook.com/book/radare/radare2book/details
subgraph reposted
Tavis Ormandy
@taviso
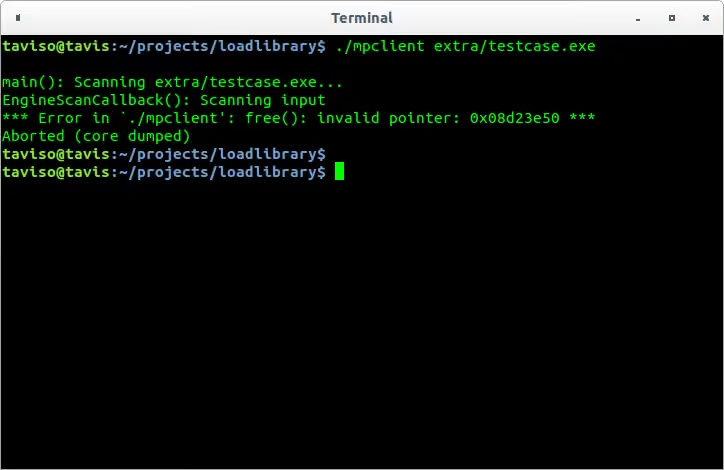
Sigh, more critical remote mpengine vulns. Found on Linux then reproduced on Windows, full report on the way. This needs to be sandboxed.
subgraph reposted
Mathias Krause | @minipli@infosec.exchange
@_minipli
v4.9.31-unofficial_grsec is ready for you to grab from github.com/minipli/linux-unofficial_grsec/releases #grsecurity #community
subgraph reposted
 blasty
@bl4sty
For all you VIM nerds who want working autocomplete for C(++) code, I recommend YCM + BEAR. github.com/Valloric/YouCompleteMe github.com/rizsotto/Bear
subgraph reposted
 Guillaume Valadon
@guedou
bincat: Binary code static analyser, with IDA integration #sstic github.com/airbus-seclab/bincat
subgraph reposted
radare
@radareorg
Analyzing embedded ARM devices with r2 (SUE (snow.nl) 2017) vimeo.com/211371081 by @trufae

subgraph reposted
 twiz
@lazytyped
It's very simple: give credits where credits due and start writing your own code
PaX Team
@paxteam
we do not tolerate blatant copyright violations from the Kernel Self Protection Project anymore: openwall.com/lists/kernel-hardening/2017/06/03/14
subgraph reposted
PaX Team
@paxteam
we do not tolerate blatant copyright violations from the Kernel Self Protection Project anymore: openwall.com/lists/kernel-hardening/2017/06/03/14
subgraph reposted
 Tuur Demeester
@TuurDemeester
2 hardware wallet camps: off-the-shelf (@BitcoinTrezor) vs. closed source (@LedgerHQ). @Yubico defends the latter: www.yubico.com/2016/05/secure-hardware-vs-open-source/

subgraph reposted
Alex Ionescu
@aionescu
Noble Gases of Windows 10 Containers (SyScan 360 Seattle Talk) Slides posted at www.alex-ionescu.com/publications/syscan/syscan2017.pdf. Enjoy!

subgraph reposted
Juliano Rizzo
@julianor
false
 Mitja Kolsek
@mkolsek
If 0days are in your threat model, you're either some government's enemy or delusional. The rest of us only need to patch.
subgraph reposted
 Mathias Payer
@gannimo
Today in parsing is hard: RCE in subtitle formats for VLC, Kodi, PopcornTime, and StremIO @SyScan360 by @omriher and @GullOmer

subgraph reposted
Matt Miller
@epakskape
The section in Chapter 7 on Windows 10 exploit mitigations is awesome. Anyone interested in this space should definitely check it out.
Alex Ionescu
@aionescu
Here at last, #windows #internals 7th Edition. Find out all about it here: www.alex-ionescu.com?p=335 cc @zodiacon @markrussinovich
subgraph reposted
 Unicorn Engine
@unicorn_engine
UniversalROP is a new smart ROP tool to generate exploitation gadgets using @unicorn_engine & Z3 solver.
github.com/kokjo/universalrop
subgraph reposted
 Catherine
@whitequark
pidgin: XMPP client you have to exploit to get RCE
gajim: XMPP client that straight up lets the server control it bugs.debian.org/cgi-bin/bugreport.cgi?bug=863445
subgraph reposted
azet
@a_z_e_t
some sane log-rotation settings for production systems using PaX/grsecurity: gist.github.com/azet/f4f0aeb849747ed505cc1d720d1bc919
subgraph reposted
 Satoshi Tanda
@standa_t
Have AMD processors and interested in hypervisors? Learn how to program AMD-V including Nested Page Tables with: github.com/tandasat/SimpleSvm
subgraph reposted
azet
@a_z_e_t
uh, yet another local privilege escalation vulnerability in sudo(1): www.openwall.com/lists/oss-security/2017/05/30/16
subgraph reposted
 Dhaval Kapil
@dhaval_kapil
A collection of my notes made during the past few weeks. Compiled a short book :) #heap #exploitation
github.com/DhavalKapil/heap-exploitation
subgraph reposted
x0rz
@x0rz
Dirty COW and why lying is bad even if you are the Linux kernel chao-tic.github.io/blog/2017/05/24/dirty-cow #linux #vulnerability
subgraph
@subgraph
Testing: Subgraph Firewall SOCKS5 filter; built-in enforcement around TLS use, e.g. can permit Tor exit only for apps using TLS, by policy.

subgraph reposted
Azeria
@Fox0x01
My first tutorial series on ARM Assembly Basics is finally finished. If you're new to ARM, this tutorial is for you:
azeria-labs.com/writing-arm-assembly-part-1/
subgraph reposted
REcon
@reconmtl
At last ! Here is the list of selected talks for REcon Montreal 2017: recon.cx/2017/montreal/news/2017/05/24/Talks-Announced.html
subgraph reposted
 Robert Swiecki
@robertswiecki
My preso from @CONFidence_news about Linux sandboxing techniques: www.swiecki.net/resources/Promises and pitfalls of sandbo…
subgraph reposted
 Joshua J. Drake
@jduck
A Simple Tool for Linux Kernel Audits www.droidsec.org/blogs/2017/05/22/a-simple-tool-for-linux…
subgraph reposted
Bruce Leidl
@bleidl
This is a really interesting and unique book about C programming.
subgraph reposted
Stephen Watt
@uT_Infection
udp and ipv6 too, tho
subgraph reposted
Halvar Flake
@halvarflake
An somewhat old-ish, but still very good presentation about Linux kernel heap exploitation: census-labs.com/media/heap-owasp-appsec-2012.pdf
subgraph
@subgraph
Subgraph Firewall running on Ubuntu with embryonic first-attempt at non-modal GTK3 prompter. Also coming: sandbox awareness, SOCKS5 support.

subgraph reposted
 Xeno Kovah
@XenoKovah
Alright, from newest to oldest, here's the talks which I've added to the timeline: timeglider.com/timeline/5ca2daa6078caaf4 ...
subgraph reposted
 Chris Evans
@scarybeasts
[blog] Are we doing memory corruption mitigations wrong? scarybeastsecurity.blogspot.com/2017/05/are-we-doing-memo…
subgraph reposted
Chris Evans
@scarybeasts
Is it possible, the SMB bug discovery was assisted by Microsoft giving source code to the "defensive" side of the NSA?
subgraph reposted
 quarkslab
@quarkslab
[BLOG] Results of our OpenVPN audit: blog.quarkslab.com/security-assessment-of-openvpn.html Thanks to @OSTIFofficial, all donors, and the @OpenVPN team! #cve-2017-7478
subgraph reposted
PaX Team
@paxteam
restoring balance to the force: www.openwall.com/lists/kernel-hardening/2017/05/11/2
subgraph reposted
twiz
@lazytyped
Pax Team response in the KSPP mailing list is something anyone should take the time to read: openwall.com/lists/kernel-hardening/2017/05/11/2
subgraph reposted
Bruce Leidl
@bleidl
A longer rant against KASLR:
forums.grsecurity.net/viewtopic.php?f=7&t=3367
subgraph reposted
Bruce Leidl
@bleidl
You don't even need hardware side channels since you can often just use the same vuln you want to exploit. Circular reasoning as security.
Anders Fogh
@anders_fogh
2)It is likely there are other vectors in hardware. 3) We don't fully understand consquences of fixes.
subgraph reposted
Bruce Leidl
@bleidl
Good thread. I'm glad more people are starting to agree with grsecurity on this.
Anders Fogh
@anders_fogh
1/x Rant on KASLR to follow
subgraph reposted
Felix Wilhelm
@_fel1x
Happy to hear that Windows is secure again now that MS patched the last remaining bug in their unsandboxed, system-privileged JS runtime.
subgraph reposted
PaX Team
@paxteam
FYI, UDEREF on amd64 already has similar infrastructure for this kind of page table management (for a different purpose).
subgraph reposted
Daniel Gruss
@lavados
[RFC, PATCH] x86_64: KAISER - do not map kernel in user mode lkml.org/lkml/2017/5/4/220 @mlqxyz @misc0110 @BloodyTangerine #essos17 #ruhrsec
subgraph reposted
 Reuters
@Reuters
UPDATE: Macron campaign says it has been the victim of a massive, coordinated hacking operation. www.reuters.com/article/us-france-election-macron-leaks-i…

subgraph reposted
 Francisco Falcon
@fdfalcon
I wrote "Exploiting MS16-145: MS Edge TypedArray.sort UAF (CVE-2016-7288)", involving Quicksort, COOP and more blog.quarkslab.com/exploiting-ms16-145-ms-edge-typedarray…
subgraph reposted
 Not Bob
@bob_beck
Ahh yes.. The good old days: marc.info?l=bugtraq&m=93656900402840&w=2
subgraph reposted
 The Register
@TheRegister
Confirmed: Intel patches remote execution hole that's been hidden in its chips since 2008 reg.cx/2sHr
subgraph reposted
Hardened-GNU/Linux
@hardenedlinux
HardenedLinux: The way to the Ark
hardenedlinux.github.io/announcement/2017/04/29/hardenedl…
subgraph reposted
Bruce Leidl
@bleidl
Also, attacker does not even get the opportunity to reach this vuln:
grsec: denied kernel module auto-load of n_hdlc by uid 1000
subgraph reposted
Mathias Krause | @minipli@infosec.exchange
@_minipli
This is why we need grsec. RAP detects the type mismatch for the callback, KERNEXEC prevents executing user code even with SMEP disabled.
subgraph reposted
 Shawn C - citypw@ioc.exchange
@citypw
PaX/Grsecurity is the most fascinating defensive project we ever had. To those who contributed this project, I salute you.
subgraph reposted
Bruce Leidl
@bleidl
Thank you so much for all your work pipacs. Immense gratitude and respect to you, spender, and everybody else who contributed to grsecurity
PaX Team
@paxteam
We are passing the baton: grsecurity.net/passing_the_baton.php
subgraph reposted
PaX Team
@paxteam
We are passing the baton: grsecurity.net/passing_the_baton.php
subgraph reposted
PaX Team
@paxteam
a new blog from spender about CVE-2017-NOTREALLY grsecurity.net/the_infoleak_that_mostly_wasnt.php
subgraph reposted
 Drupal Security
@drupalsecurity
A highly critical security release for #drupal 8.3.1 and 8.2.8 is now available. Update your sites now. www.drupal.org/SA-CORE-2017-002
subgraph reposted
 Solar Designer
@solardiz
minicom 2.7.1 released today fixes remote code execution. Would have been more fun if discovered in the dialup days. www.openwall.com/lists/oss-security/2017/04/18/5
subgraph reposted
Matt Miller
@epakskape
Yep, for RCE issues we've noticed an increase in type confusions and heap out-of-bounds reads. UAF issues have declined (thanks to MemGC)

subgraph reposted
Matt Miller
@epakskape
Interesting trend: heap corruption issues reported to Microsoft are now more often non-linear (buf[n] = x) vs. linear (memcpy(buf, x, n))

subgraph reposted
 CVE
@CVEnew
CVE-2017-7889 The mm subsystem in the Linux kernel through 4.10.10 does not properly enforce the ... www.cve.org/CVERecord?id=CVE-2017-7889
subgraph reposted
Bruce Leidl
@bleidl
Those exploit escaped from the laboratory every time they were deployed. Exploit terrorist and maybe terrorist can now exploit everybody.
 Edward Snowden
@Snowden
The Mother Of All Exploits escaped from an NSA laboratory and is wrecking the internet. motherboard.vice.com/en_us/article/your-governments-hacki…
subgraph reposted
Bruce Leidl
@bleidl
Every time you use an undisclosed vulnerability you are demonstrating to your adversary how to attack you. Do you think he's not watching?
subgraph reposted
Bruce Leidl
@bleidl
When your side is most dependent on technology, offense with secret exploits is just not rational at all.
subgraph reposted
 hacker.house
@hackerfantastic
Here is a video showing ETERNALBLUE being used to compromise a Windows 2008 R2 SP1 x64 host in under 120 seconds with FUZZBUNCH #0day ;-)
subgraph reposted
 Chaouki Bekrar
@cBekrar
Microsoft usually patches bugs/exploits within "just" 6 to 12 months. Let's see how they'll handle #shadowbrokers as cyber chaos is coming
subgraph reposted
hacker.house
@hackerfantastic
This isn't a data dump, this is a damn Microsoft apocalypse. #0day #shadowbrokers
subgraph reposted
Halvar Flake
@halvarflake
Turns out serversides arent dead, they just went underground.
subgraph reposted
Frank
@jedisct1
RT @FuzzySec: 200+ RCE vulns in Trend Micro, the HITB slides are totally savage guys! @steventseeley & @malerisch - conference.hitb.org/hitbsecconf2017ams/materials/D1T1 - S…
subgraph reposted
 Jeff Williams
@planetlevel
Is your build pipeline secure? 32 RCEs + more fixed in latest Jenkins release jenkins.io/security/advisory/2017-04-10/ #devsecops #appsec
subgraph reposted
Bruce Leidl
@bleidl
I looked at this in depth recently and Yawning Angel has done an outstanding job on the details. All Tor users on Linux should use this
 Toronto Crypto
@TorontoCrypto
Release: sandboxed-tor-browser-0.0.5 www.reddit.com/r/TorontoCrypto/comments/6566ws/release_sa…

subgraph reposted
Toronto Crypto
@TorontoCrypto
Release: sandboxed-tor-browser-0.0.5 www.reddit.com/r/TorontoCrypto/comments/6566ws/release_sa…
subgraph reposted
REcon
@reconmtl
Annoucing first round of talks for RECON 2017. recon.cx/2017/montreal/news/2017/04/12/First-Round.html
subgraph
@subgraph
The go lib that compiles our expressive seccomp bpf policies relicensed LGPL: github.com/twtiger/gosecco/commit/06b8323873a0c9ed1227950… Thanks @ultrastoic, @rosatolen & team!
subgraph reposted
 Morgan Marquis-Boire
@headhntr
That Word 0day floating around... was being used to install FinSpy. Nice work by @botherder & @FireEye. motherboard.vice.com/en_us/article/government-hackers-use…
subgraph
@subgraph
To do this: sudo apt-get update; sudo apt-get upgrade; sudo killall nautilus nautilus-desktop
subgraph
@subgraph
Upgraded Nautilus package to address vuln described in @micahflee's blog post is in the @subgraph OS repo. Upgrade packages to help test.
subgraph
@subgraph
Upgraded Nautilus package to address vuln described in @micahflee's blog post is in the @subgraph OS repo. Upgrade packages to help test.
subgraph reposted
 DuckDuckGo
@DuckDuckGo
Hi. Yes, sorry for the inconvenience. A message went out to XMPP users and we've put a notice on the XMPP blog post: duck.co/blog/post/4/xmpp-services-at-duckduckgo
subgraph reposted
 thaidn
@XorNinja
on testing (EC)DH and (EC)DSA vnhacker.blogspot.com/2017/04/testing-ecdh-and-ecdsa.html, as a comment for research.kudelskisecurity.com/2017/04/10/how-not-to-break…
subgraph
@subgraph
It's going to get better, too. There is active development on it (@uT_Infection, in fact, presently). You're welcome!
subgraph
@subgraph
Outstanding Nautilus vulnerability is a serious issue, has been on our radar for some time - we will probably audit it, benefiting everyone.
subgraph
@subgraph
The dukgo.com XMPP servers seem to have been totally inaccessible via their onion addresses past few days. cc @duckduckgo
subgraph
@subgraph
Unofficial word is that the dukgo.com XMPP service will end on May 9, 2017. Any official confirmation from @duckduckgo?
subgraph
@subgraph
Unofficial word is that the dukgo.com XMPP service will end on May 9, 2017. Any official confirmation from @duckduckgo?
subgraph reposted
Solar Designer
@solardiz
You're welcome. Here's his 2008 update: eprint.iacr.org/2008/036. Classic Luby-Rackoff: crypto.stanford.edu/~dabo/courses/cs355_fall02/lr.ps. Other papers on unbalanced.
subgraph reposted
Solar Designer
@solardiz
FWIW, I found Jacques Patarin's Crypto 2004 paper followed by "Generic Attacks on Feistel Schemes" especially useful www.prism.uvsq.fr/~jap/
subgraph reposted
hacker.house
@hackerfantastic
EBBISLAND “Exploit for Solaris 2.6, 2.7, 2.8, 2.9 and 2.10)” could be a generic RPC exploit as opposed to service specific, thats really bad
subgraph reposted
hacker.house
@hackerfantastic
HOLY SHIT, THERE IT IS, REMOTE SUNOS GOD MODE! Solaris 0day for *everything* - WHOEVER WROTE THIS DESERVES A KNIGHTHOOD!


subgraph reposted
subgraph reposted
 CopperheadOS
@CopperheadOS
The mainline Linux kernel developers pretend to care more about performance than grsecurity and then land slower clones of features from it.
subgraph reposted
Tails
@Tails_live
The first release candidate for Tails 2.12 is out and needs testing: tails.boum.org/news/test_2.12-rc1/
subgraph reposted
 Go
@golang
Go 1.8.1 is released!
Get it: golang.org/dl
Announcement:
groups.google.com/forum/
#golang
subgraph reposted
 Mudge
@dotMudge
This is a brilliant tactic. There are so many others like this because the AV community keeps thinking this is a one-move game... Kudos!
 Mark Kriegsman
@MarkKriegsman
Choose a malware signature as your username. Gets logged, and server-side anti-malware will delete whole log file :)
www.sec.cs.tu-bs.de/pubs/2017-asiaccs.pdf
subgraph
@subgraph
GTK hackfest 2017: D-Bus communication with containers
smcv.pseudorandom.co.uk/2017/dbus_and_containers/
subgraph reposted
subgraph reposted
CopperheadOS
@CopperheadOS
Next release fixes Bluetooth buffer overflow caught by our syscall overflow checks. Thanks to @ScottyBauer1 for helping to fix it quickly.
subgraph reposted
 Sy Brand
@TartanLlama
My first post of a 10 part series on writing a linux debugger. Been working on this for a while, hope it's useful! blog.tartanllama.xyz/c++/2017/03/21/writing-a-linux-debug…
subgraph reposted
 Dave Aitel
@daveaitel
"the web is just a beautiful exploit platform - we're pretty much just laying the whole spread out there for you" -@justinschuh
subgraph reposted
Dave Aitel
@daveaitel
"I can't actually imagine anything with more attack surface than a browser " - @justinschuh #youkillityoueatit
subgraph reposted
David Wong
@cryptodavidw
rustls: A Modern, Pure-Rust TLS Library jbp.io/2017/04/03/rustls
subgraph reposted
 Nima Fatemi 🍉 mrphs.bsky.social
@mrphs
I did a quick write up on some of the tools you can use to protect your privacy against your ISPs technical.ly/2017/04/05/secure-vpn-privacy-isp
subgraph reposted
 Richard Johnson
@richinseattle
This writeup on the research process used by Gal and @halvarflake to analyze and exploit Broadcom wifi SoC is a masterclass
subgraph
@subgraph
The @ubuntu desktop is shifting back to GNOME. insights.ubuntu.com/2017/04/05/growing-ubuntu-for-cloud-a…
subgraph reposted
 CBC Montreal
@CBCMontreal
Devices that track, spy on cellphones found at Montreal's Trudeau airport www.cbc.ca/news/canada/montreal/trudeau-airport-spying-1.…

subgraph reposted
Ben Hawkes
@benhawkes
Project Zero blog: "Over The Air: Exploiting Broadcom’s Wi-Fi Stack (Part 1)" by @laginimaineb - googleprojectzero.blogspot.com/2017/04/over-air-exploitin…
subgraph reposted
 Alisa Esage Шевченко
@alisaesage
In short: avoid ROP, avoid heap spraying, avoid noisy memory ops, avoid bare API, avoid known tech, & try not to kill the bug in the process
subgraph reposted
Alisa Esage Шевченко
@alisaesage
A nice, if not too brief overview of modern anti-exploit tech: www.endgame.com/blog/chakra-exploit-and-limitations-moder…
subgraph reposted
 Philipp Winter
@__phw
We found relays that shared prime factors, some shared moduli, and some manipulated their RSA exponent to attack onion services.
subgraph reposted
Philipp Winter
@__phw
We published our analysis of ten years worth of archived #tor relay RSA keys: nymity.ch/anomalous-tor-keys/
subgraph reposted
subgraph reposted
 Beatrice Martini
@beatricemartini
Meeting on local message boards in the 90s! So many memories. (In the background: a dial-up modem sound)
David Mirza Ahmad
@attractr
True story: three of us from @subgraph: myself, @bleidl, @lifeistheonlyth, met in the early 90s 403 undergorund BBS / X.25 (datapac) scene.
 CSMPasscode
@CSMPasscode
Meet the hackers trying to build @subgraph, a hack-resistant operating system via @JackDetsch w/ @attractr www.csmonitor.com/World/Passcode/2017/0327/The-hackers-tr…

subgraph reposted
 Onur Mutlu
@_onurmutlu_
Talked about #rowhammer and what comes next, at #date2017. Here is the paper: people.inf.ethz.ch/omutlu/pub/rowhammer-and-other-memory-…
 subgraph
@subgraph
The @quarkslab audit of @OpenVPN is great news (reminder: it was affected by shellshock, is scary). 👍🏼
 OSTIF Official
@OSTIFofficial
The audit is wrapping up now. @quarkslab will be securely disclosing the results to the security team at @OpenVPN on April 7th.
subgraph reposted
OSTIF Official
@OSTIFofficial
The audit is wrapping up now. @quarkslab will be securely disclosing the results to the security team at @OpenVPN on April 7th.
subgraph reposted
quarkslab
@quarkslab
[TOOL+BLOG] LIEF - Library to Instrument Executable Formats blog.quarkslab.com/lief-library-to-instrument-executable-… Website: lief.quarkslab.com
subgraph reposted
David Mirza Ahmad
@attractr
Reminded of this again with Ethereum in sandbox.. Cgroup implementation coming to Oz this month to support USB devices & resource limits.
subgraph
@subgraph
Bitcoin core in an SGOS sandbox is also a good use case for adding cgroups support to Oz, this is something we will experiment with soon.
subgraph reposted
 Jann Horn - jann@infosec.exchange
@tehjh
and aws.amazon.com/security/security-bulletins/AWS-2017-004/ says AWS is not affected
subgraph reposted
Jann Horn - jann@infosec.exchange
@tehjh
xenbits.xen.org/xsa/advisory-212.html Xen 64-bit PV guests can break out into the host; we have a working exploit
subgraph reposted
David Mirza Ahmad
@attractr
There are some great people who want to work at Subgraph just because the project interests them. Should work on making that possible.
subgraph reposted
subgraph reposted
subgraph reposted
 Dmitry Bestuzhev
@dimitribest
 Kris McConkey
@smoothimpact
Great q from @ryanaraine to @GeorgetownLaw "should any vendor whitelist malware at the request of their gov?". Answer? "Business decision".
subgraph reposted
 Eugene Kaspersky
@e_kaspersky
Thanks to bug mitigation technologies the bug discovery time has changed dramatically since 2000s. @mdowd at #thesas2017
subgraph reposted
 Chris Eng
@chriseng
Sandboxes, by far, have had the biggest impact on exploit development time. @mdowd #thesas2017
subgraph reposted
argp
@_argp
The new macOS/iOS kernel bug slaughter list by P0's Ian Beer: bugs.chromium.org/p/project-zero/issues/list?can=1&q=owne…
subgraph reposted
Bruce Leidl
@bleidl
Cool, how many times have Tor routers been compromised by mem corruption vulns? Zero times? Does FBI still have a Tor browser exploit? Yes?
subgraph reposted
Bruce Leidl
@bleidl
We're currently working on providing more flexibility for various use cases. Coming soon, including per-sandbox transport configuration UI
subgraph reposted
 Raphael Satter
@razhael
A friend types a pub's name into the search bar. Google replies: "You visited 2 years ago." 📍

subgraph reposted
Alexander Popov
@a13xp0p0v
I've published the write-up about exploiting CVE-2017-2636 in the Linux kernel: a13xp0p0v.github.io/2017/03/24/CVE-2017-2636.html
subgraph reposted
 Matthew Green
@matthew_d_green
Google says U.S. consumers don't consider their web browsing history to be sensitive. What fucking planet are they living on.

subgraph reposted
Edward Snowden
@Snowden
Huge: USG confirms cyber offense funded at 9x rate of defense. Wonder why we can't stop foreign hacks? This is why. www.reuters.com/article/us-usa-cyber-defense-idUSKBN17013U

subgraph reposted
subgraph reposted
David Mirza Ahmad
@attractr
Added workaround to SGOS clearnet Chromium testing setup steps, along w howto fix Debian's ugly default font config: subgraph.com/sgos/documentation/clearnet-chromium/
subgraph
@subgraph
Yes, will be fixed when we finally release new Oz daemon for all users. Important, because the web is awful without certain browser plugins.
subgraph
@subgraph
Yes, will be fixed when we finally release new Oz daemon for all users. Important, because the web is awful without certain browser plugins.
subgraph
@subgraph
Monero GUI beta 2 out. With new release tag we'll make a proper package for the SGOS repo (XMR donations accepted!): github.com/monero-project/monero-core/releases/tag/v0.10.3.1
subgraph
@subgraph
Sandboxed Transmission can only exit over a bridge, routed by Oz through OpenVPN link. If VPN link is down, app traffic has nowhere to go.
subgraph
@subgraph
Torrent using Oz-sandboxed Transmission with an OpenVPN exit tunnel in @subgraph OS (try it, experimental!): subgraph.com/sgos/documentation/openvpn-transmission/
 subgraph
@subgraph
Still work in progress + we're working on a GUI for easy config, but design objective is to fail closed, which app sandbox approach allows.
subgraph
@subgraph
Torrent using Oz-sandboxed Transmission with an OpenVPN exit tunnel in @subgraph OS (try it, experimental!): subgraph.com/sgos/documentation/openvpn-transmission/
subgraph
@subgraph
"Now this is really troubling. Seems that my Gentoo system has been ransomwared." forums.gentoo.org/viewtopic-t-1060828.html
subgraph reposted
Bruce Leidl
@bleidl
RT if this song has been looping in your head all day long
subgraph reposted
Nicolas Krassas
@Dinosn
Keyshuffling Attack for Persistent Early Code Execution in the Nintendo 3DS Secure Bootchain github.com/Plailect/keyshuffling
subgraph reposted
 Steve Weis
@sweis
SSH over a cache covert channel between VMs on the same host from NDSS'17: cmaurice.fr/pdf/ndss17_maurice.pdf
subgraph
@subgraph
Even then we aren't really happy: recommend disabling JS, and we sandboxed "Chronion": Chromium w/Tor (w/bunch of residual privacy caveats)
subgraph reposted
Dan Guido
@dguido
Tor levels the playing ground for bad actors. Anyone can intercept your traffic and no one uses a browser sandbox.
 Gabriella "Biella" Coleman
@BiellaColeman
Such a crucial point. Tor levels the playing ground for good actor
subgraph reposted
 Algo VPN
@AlgoVPN
You can trust these guys or you can deploy your own VPN with us
 Doublehop.me VPN
@doublehop_me
Hokay, we fixed the Internets! Verified no funny biz or govvy intervention, brought the EU interconnect back online.

subgraph reposted
Ars Technica
@arstechnica
Someone is putting lots of work into hacking Github developers arstechnica.com/security/2017/03/someone-is-putting-lots-… by @dangoodin001
subgraph
@subgraph
Grsecurity (and @subgraph OS) disable unprivileged user namespaces because it is a fountain of privilege escalation.
subgraph reposted
David Mirza Ahmad
@attractr
I've also nmapped my host Internet IP address by creating an Oz OpenVPN sandbox and running locally installed nmap from that sandbox shell.
subgraph reposted
David Mirza Ahmad
@attractr
Useful if you need OpenVPN to eg SSH to some host, but don't want to exit all host traffic through that VPN. Can mount a ~/.ssh in sandbox.
David Mirza Ahmad
@attractr
Oz+OpenVPN trick: can "oz launch -n app". Create sandbox w/o launching app. Oz shell from there for CLI VPN egress.
subgraph
@subgraph
Ever wanted to have a specific application use a VPN, rather than system wide? Try it w/@subgraph OS. Experimental! subgraph.com/sgos/documentation/openvpn-chromium/

subgraph reposted
David Mirza Ahmad
@attractr
Oz+OpenVPN trick: can "oz launch -n app". Create sandbox w/o launching app. Oz shell from there for CLI VPN egress.
subgraph
@subgraph
Ever wanted to have a specific application use a VPN, rather than system wide? Try it w/@subgraph OS. Experimental! subgraph.com/sgos/documentation/openvpn-chromium/
subgraph
@subgraph
We are currently designing a really nice GUI in Oztool for configuring OpenVPN settings for an Oz sandbox.
subgraph
@subgraph
Ever wanted to have a specific application use a VPN, rather than system wide? Try it w/@subgraph OS. Experimental! subgraph.com/sgos/documentation/openvpn-chromium/
subgraph reposted
hanno
@hanno
This is huge wiki.mozilla.org/Security/Binary_Transparency mozilla starts with binary transparency
subgraph reposted
David Mirza Ahmad
@attractr
True story: three of us from @subgraph: myself, @bleidl, @lifeistheonlyth, met in the early 90s 403 undergorund BBS / X.25 (datapac) scene.
CSMPasscode
@CSMPasscode
Meet the hackers trying to build @subgraph, a hack-resistant operating system via @JackDetsch w/ @attractr www.csmonitor.com/World/Passcode/2017/0327/The-hackers-tr…
subgraph reposted
 jean marc manach
@manhack
The hackers trying to build @subgraph, a hack-proof operating system
csmonitor.com/World/Passcode/2017/0327/The-hackers-trying… by @JackDetsch on @CSMPasscode
subgraph reposted
 Jeremy de Beer
@jdebeer
For those who want to know the law on tractor hacking, I explain it in this @sparkcbc story. www.cbc.ca/radio/spark/297-the-future-of-food-farming-and…
 As It Happens
@cbcasithappens
Saskatchewan farmer hacks his 'smart' tractor to avoid costly dealer fees: cbc.ca/1.4042504

subgraph reposted
Azeria
@Fox0x01
Uh, look at that. For those afraid of Radare2: there are no excuses anymore.
 Itay Cohen 🌱
@megabeets_
Finally published the first part in a series of articles: A journey into radare2.
Check it out @ www.megabeets.net/a-journey-into-radare-2-part-1
@radareorg #radare2
subgraph reposted
Binni Shah
@binitamshah
Finding The Lost Vikings – Reversing a Virtual Machine : ryiron.wordpress.com/2017/02/01/finding-the-lost-vikings-… ,Recompiling the Lost Vikings : ryiron.wordpress.com/2017/03/26/recompiling-the-lost-viki…

subgraph reposted
 krypteia
@krypteiaorg
Seriously. This is life changing.
subgraph
@subgraph
Ever wanted to have a specific application use a VPN, rather than system wide? Try it w/@subgraph OS. Experimental! subgraph.com/sgos/documentation/openvpn-chromium/
subgraph reposted
 mdowd
@mdowd
Jesus, what a bloodbath: support.apple.com/en-us/HT207617
subgraph
@subgraph
Ever wanted to have a specific application use a VPN, rather than system wide? Try it w/@subgraph OS. Experimental! subgraph.com/sgos/documentation/openvpn-chromium/
subgraph reposted
subgraph
@subgraph
WWTGD: "what would @thegrugq do" is a question asked during SGOS development. Consider supporting him on Patreon 👇🏼www.patreon.com/grugq
subgraph reposted
 pynchon my finger in the door of perception
@HongPong
Likely refinements to protect keys and combat malware with disposable VMs in Qubes, or @subgraph at @SecureDrop talk #libreplanet

 subgraph
@subgraph
How to setup @Spotify in @subgraph OS: subgraph.com/sgos/documentation/spotify/

subgraph reposted
David Mirza Ahmad
@attractr
Spotify Linux client's required syscall count: 107 (out of 330+). From the Oz seccomp trainer's (semi) auto-generated seccomp bpf whitelist.

subgraph reposted
subgraph reposted
Tavis Ormandy
@taviso
Ah-ha, I had an epiphany in the shower this morning and realized how to get codeexec in LastPass 4.1.43. Full report and exploit on the way.
 subgraph
@subgraph
Oztool allows for menu-driven GUI creation / management of app sandbox profiles in @subgraph OS; reads & outputs json configuration files.
subgraph
@subgraph
Screenshots of Oztool, the new GUI sandbox profile editor, also coming soon. cc @uT_Infection

 subgraph
@subgraph
Screenshots of Oztool, the new GUI sandbox profile editor, also coming soon. cc @uT_Infection
subgraph
@subgraph
Early screenshots of coming @Subgraph OS event monitor/GUI being developed by @uT_Infection. Available for testing if anyone wants to try.

 subgraph
@subgraph
This is why we adopted the Golang @coyproject for @subgraph OS & contributed code to make it more usable (single window UI, notifications).
subgraph reposted
 Mark Wodrich
@markwo
not all objects are protected with MemGC. Also, see #3 in blogs.360.cn/360safe/2016/11/29/three-roads-lead-to-rome-2/
subgraph reposted
 Ivan Fratric 💙💛
@ifsecure
In IE/Edge, string content is not protected by MemGC. Consequence: UAFs on strings can lead to fun infoleaks like bugs.chromium.org/p/project-zero/issues/detail?id=1076
subgraph
@subgraph
Agree with thread; our answer is to sandbox app. No "clearnet connections by accident". With Tor, whole platform needs defensive posture.
 Sarah Jamie Lewis
@SarahJamieLewis
For example even something like a hyperlink in electron can be a deanonymization vector because forcing a proxy on all connections is hard.
subgraph reposted
Tavis Ormandy
@taviso
Oops, new LastPass bug that affects 4.1.42 (Chrome&FF). RCE if you use the "Binary Component", otherwise can steal pwds. Full report on way.
subgraph reposted
Richard Johnson
@richinseattle
K2s demos at CSW were pretty awesome. DKOM & ROP detection and direct snapshot memory editing to bypass lsass for local unlock
 K2
@ktwo_K2
Gargoyle memory evasion countermeasures pushed to github github.com/ShaneK2/inVtero.net
Detect a RoP in User/Kernel space from #hypervisor #cloud
 subgraph
@subgraph
The artist (@artofsephy) who made many of our illustrations thinks our adversaries need to be a little more menacing.

 subgraph
@subgraph
This is great community support. We will definitely work on this soon and then include it in our documentation. Thanks @BitcoinTrezor!
 Pavol Rusnak
@PavolRusnak
No need to order one. Send me your address to stick@satoshilabs.com and we'll send you one @BitcoinTrezor for free!
subgraph reposted
Bruce Leidl
@bleidl
Usually takes everybody a few tries for successful implementation of asn1 or telnet options in C without adding rce nobody finds for years
subgraph
@subgraph
Grsecurity has a new website: grsecurity.net
subgraph reposted
 Samuel Groß
@5aelo
More browser hacking: exploiting a cross-mmap overflow in #firefox saelo.github.io/posts/firefox-script-loader-overflow.html
subgraph
@subgraph
Thanks! The appfw is built partially on Gnome shell, as are a few other SGOS comonents. To build what we wanted, we had to settle on one DE.
 Nicolae Crefelean
@kneekoo
That firewall is precisely what I want in every GNU/Linux distro. I love it! Too bad the DE is Gnome 3. Are there options?
subgraph reposted
Nima Fatemi 🍉 mrphs.bsky.social
@mrphs
This is why projects like @subgraph, @QubesOS and @Tails_live are so important.
Sarah Jamie Lewis
@SarahJamieLewis
This is why I still believe for privacy to advance we need to move away from websites & browsers.
subgraph
@subgraph
Thank you to handful of people sending us BTC donations. Planning to use it soon to order a TREZOR for testing USB support in Oz sandboxes.
subgraph
@subgraph
Want to help support Subgraph OS? We are now officially accepting Bitcoin contributions. Address: 1KUnb8ivujnmrvW8qdtFMs3uUHcVVSuLtj
 subgraph
@subgraph
We include the password manager @KeePassX with @subgraph OS by default, and it's decent software. Local database, no monthly fees, no cloud.
 thaddeus e. grugq
@thegrugq
now they want that sweet sweet recurring revenue of renting accessing to your passwords back to you, so -> cloud.
subgraph reposted
TrendAI Zero Day Initiative
@thezdi
Team fm @ChaitinTech finish their #pwn2own by popping Firefox w/ an int overflow and escalating via uninitialized buffer in Windows kernel.
subgraph reposted
 offensivecon
@offensive_con
Mark your calendars! First edition of OffensiveCon is happening in Berlin. 12-17 February 2018. www.offensivecon.org
subgraph reposted
azet
@a_z_e_t
remember - SELinux won't save you.

subgraph reposted
azet
@a_z_e_t
OMEMO: Cryptographic Analysis Report: conversations.im/omemo/audit.pdf
subgraph reposted
TrendAI Zero Day Initiative
@thezdi
We've seen folks pop calc, and folks pop calc in scientific mode, but xcalc is a first for #pwn2own - thanks to @ChaitinTech. #p2o

subgraph reposted
TrendAI Zero Day Initiative
@thezdi
Chaitin Security Research Lab (@ChaitinTech) welcomes Ubuntu to #pwn2own with a Linux kernel heap OOB access: earns them $15K.
subgraph reposted
hanno
@hanno
I've looked into this RAND report on 0days. I'm not impressed. blog.hboeck.de/archives/882-Zero-Days-and-Cargo-Cult-Scie…
subgraph reposted
 O'Reilly Security
@OReillySecurity
We are saddened to hear about our friend, internationally recognized security expert Becky Bace. Her 2016 keynote: www.oreilly.com/ideas/a-vision-for-future-cybersecurity
subgraph reposted
David Mirza Ahmad
@attractr
Recon (@reconmtl) has some pretty good training classes.
 Olivier THOMAS
@reivilo_t
For those @reconmtl lovers I am actually part of. @Texplained_RE will be there with a training on IC security and RE
recon.cx/2017/montreal/training/trainingic.html

subgraph reposted
David Mirza Ahmad
@attractr
The Muggleverse: yesterday I guest lectured a class remotely, this required 1) java browser plugin 2) flash plugin 3) run app w/expired cert
subgraph reposted
David Mirza Ahmad
@attractr
WORST FUTURE www.telegraph.co.uk/technology/2017/03/14/creepy-facial-r…
subgraph reposted
Juliano Rizzo
@julianor
Path traversal to escape guest<->host VM shared folder. Vmware 2008? No Virtualbox 2017. 👍cooperating VMs trick bugs.chromium.org/p/project-zero/issues/detail?id=1037
subgraph reposted
REcon
@reconmtl
Get your submissions in for the first phase of the @reconmtl CFP before
this Wednesday! The CFP closes on April 15th recon.cx/2017/montreal/cfp/
subgraph reposted
Halvar Flake
@halvarflake
Remember: Intelligence agencies hack to get the access your surveillance capitalism provider already has.
subgraph reposted
Bruce Leidl
@bleidl
Signal doesn't notify you when you are a journalist and the app uploads your entire contact list to Signal server including your sources
subgraph reposted
Bruce Leidl
@bleidl
various causes of vuln zeitgeist including new techniques disclosed causing researchers to revisit old 'almost' vulns
subgraph
@subgraph
Just some Chronions, sketched by @artofsephy.

subgraph reposted
Bruce Leidl
@bleidl
In my direct experience and many others would agree this number is closer to 100% than to 5.7%. My sample size is smaller but meaningful
subgraph reposted
 Ryan Duff
@flyryan
This Harvard paper is using bug trackers to find collisions… at that point, your dupes are likely due to word of mouth rather rediscovery…
subgraph reposted
 Lillian Ablon
@LilyAblon
The decision calculus for retention/disclosure of vulnerabilities is complicated; our findings can help inform part of the calculus, not all
 matt blaze
@mattblaze
Not-very-bold prediction: the RAND study will be widely cited to make categorical statements that support opposite conclusions.
subgraph reposted
 Daniel Miller ✝
@bonsaiviking
New @nmap NSE script to exploit Apache #struts vuln CVE-2017-5638, by Seth Jackson. nmap.org/nsedoc/scripts/http-vuln-cve2017-5638.html
subgraph reposted
David Mirza Ahmad
@attractr
Jessie Frazelle's #googlenext17 Linux container presentation/demo.
subgraph reposted
Dave Aitel
@daveaitel
Everyone panicking over SIGNAL weaknesses should...come to the @InfiltrateCon talk, where you get to see actual SIGNAL weaknesses.
subgraph reposted
CSMPasscode
@CSMPasscode
Checkbox security is an “absolute disaster,” costs $75 billion a year, says @WilHarm3. @highwirePR #sponsored www.csmonitor.com/World/Passcode/2017/0223/The-rise-of-th…
subgraph reposted
 ZODL | Zcash Open Development Lab
@zodl_co
Our co-authored report with @R3CEV on Confidentiality & Privacy for Blockchains z.cash/blog/r3-blockchain-report.html
subgraph reposted
 Bruce Potter
@gdead
Wow. Average time between private discovery and public disclosure is 6.9 years while yearly collision (2nd discovery) is ~6%.
 RAND
@RANDCorporation
RAND's @LilyAblon examined 200 real-world zero-day software vulnerabilities. Here's what she found: r.rand.org/3rma
subgraph reposted
 Cisco Talos Intelligence Group
@TalosSecurity
Content-Type: Malicious - New Apache 0-day Under Attack feedproxy.google.com/~r/feedburner/Talos/~3/-z8Jo3rCyGM/a…

subgraph reposted
 Reuters Science News
@ReutersScience
U.S. aware of CIA security breach in 2016; contractors suspected in leak www.reuters.com/article/us-cia-wikileaks-idUSKBN16F2AP

subgraph reposted
 Gemat👁️m
@atomgem
In memory of Kris Kaspersky.

subgraph reposted
David Mirza Ahmad
@attractr
Neat, @uT_Infection sandboxed Spotify in Oz with a clearnet profile.
subgraph reposted
Stephen Watt
@uT_Infection
TFW Trump keeps tweeting about all the jobs coming back to America but there were none for you so you happily accepted one from Canada.
subgraph
@subgraph
New ISO very soon, we are testing and packaging important changes, such as the Chromium clearnet browser.
subgraph reposted
thaddeus e. grugq
@thegrugq
Awesome hire!
subgraph
@subgraph
We are happy to announce that Stephen Watt (@uT_Infection) has joined the @Subgraph OS development team.
subgraph
@subgraph
Will be coming down via apt soon for all users, also has experimental openvpn support w/per-sandbox policy routing. x.com/josephfcox/status/838427591480643586
subgraph reposted
REcon
@reconmtl
The Recon Montreal 2017 CFP is alive!! recon.cx/2017/montreal/
subgraph reposted
 Sephy
@artofsephy
With my cubic « BOX » font yay! I always love designing stuff for @SUBGRAPH projects. Big up to the team! @attractr
subgraph reposted
 Brad Heath
@bradheath
DOJ said that disclosing details of the FBI's Tor Browser exploit "is not currently an option."
 subgraph
@subgraph
People claim on @soylent subreddit that they've received email with link to "Soy Route" Onion site (SGOS shot below) www.reddit.com/r/soylent/comments/5xdabg/trish_from_soyle…

subgraph reposted
Stephen Watt
@uT_Infection
I don't always make Linux desktops more secure, but when I do, I make sure I start by installing SGOS
subgraph
@subgraph
We are happy to announce that Stephen Watt (@uT_Infection) has joined the @Subgraph OS development team.
subgraph
@subgraph
Chrome in Oz: for a captive portal check, we needed a website that doesn't automatically redirect to HTTPS. A nostalgic choice, for now :)

 subgraph
@subgraph
Netflix and chill (in an Oz sandbox with grsecurity and PaX) 🍿

subgraph reposted
Hardened-GNU/Linux
@hardenedlinux
Linux kernel mitigation checklist( update: Feb 28 2017) hardenedlinux.github.io/system-security/2016/12/13/kernel…
subgraph reposted
 X41 D-SEC GmbH
@X41Sec
-X41 libice bonus feature: Working PoC for retrieving ICE cookies via timing attack: www.x41-dsec.de/lab/sources/icetest.c
subgraph reposted
X41 D-SEC GmbH
@X41Sec
Advisory X41-2017-001: Multiple vulnerabilities in x.org - www.x41-dsec.de/lab/advisories/x41-2017-001-xorg/
subgraph reposted
X41 D-SEC GmbH
@X41Sec
Three makes a pattern - winmail.dat considered harmful www.x41-dsec.de/lab/blog/winmaildat-harmful/ Vulnerabilities found in TNEF, YTNEF, and KTNEF!
subgraph reposted
 TKMatima.com
@TKMatima
Now reading: Exploiting VLC - A case study on jemalloc heap overflows
phrack.org/issues/68/13.html via @_argp
subgraph reposted
Andrey Konovalov
@andreyknvl
You can, so namespace support is not technically required to exploit the bug, but it made things easier for two reasons: @vnik5287
subgraph reposted
Andrey Konovalov
@andreyknvl
Proof-of-Concept local root exploit for the double-free in Linux kernel DCCP implementation (CVE-2017-6074): github.com/xairy/kernel-exploits/tree/master/CVE-2017-6074
subgraph
@subgraph
We setup a page for those attending @cryptoharlem tonight trying SGOS. Find us on IRC or send email if you have q's. subgraph.com/sgos/documentation/crypto-harlem
 Matteo / @geminiimatt@infosec.exchange
@geminiimatt
Just a reminder there is a @cryptoharlem event tonight 2/23 www.meetup.com/New-York-Cryptoparty-Network/events/237937… 6pm to 9pm at HBA, 275 Malcolm X Blvd, NY,NY10027
subgraph reposted
 Natalie Silvanovich
@natashenka
tl;dr there's no guarantee that private message you sent on OkCupid isn't on the public internet somewhere blog.cloudflare.com/incident-report-on-memory-leak-caused…
subgraph reposted
 grsecurity rss
@GrsecurityRss
grsecurity-3.1-4.9.12-201702231830.patch is available from grsecurity.net/test/grsecurity-3.1-4.9.12-201702231830.patch
subgraph reposted
Tavis Ormandy
@taviso
Cloudflare have been leaking customer HTTPS sessions for months. Uber, 1Password, FitBit, OKCupid, etc. bugs.chromium.org/p/project-zero/issues/detail?id=1139
subgraph reposted
Jann Horn - jann@infosec.exchange
@tehjh
subgraph reposted
 Microsoft Edge Dev
@MSEdgeDev
Mitigating arbitrary native code execution in Microsoft Edge blogs.windows.com/msedgedev/2017/02/23/mitigating-arbitra…
 subgraph
@subgraph
We will soon deliver Chromium as our clearnet browser. We are packaging now, but if you want to test w/manual steps: subgraph.com/sgos/documentation/clearnet-chromium/
subgraph
@subgraph
SGOS not vulnerable to CVE-2017-6074: DCCP not compiled in kernel. Even if it were: RAP limits exploitability, and seccomp-bpf reachability.
x0rz
@x0rz
CVE-2017-6074: DCCP double-free vulnerability (local root), works for #linux >2.6.18, public PoC soon seclists.org/oss-sec/2017/q1/471 #vulnerability

subgraph reposted
subgraph reposted
 CryptoHarlem
@cryptoharlem
Next event will be Thursday Feb 23 covering secure operating systems @subgraph @Tails_live & @QubesOS Bring a 8GB USB for each 1 you want
subgraph
@subgraph
Clearnet (non-Tor) sandboxed Chromium browser to be released very soon. Contact us if you want to help test. IRC or info@subgraph.com.
subgraph reposted
 Monero (XMR)
@monero
"Building & using the Monero Core GUI Wallet in Subgraph OS": subgraph.com/sgos/documentation/monero/
subgraph reposted
Markus Vervier
@marver
Our co-worker Eric had a look at ytnef (lib used by popular mailclients to parse winmail.dat / Outlook mails), here is what he found:
X41 D-SEC GmbH
@X41Sec
Advisory X41-2017-002: Multiple Vulnerabilities in ytnef - www.x41-dsec.de/lab/advisories/x41-2017-002-ytnef/
subgraph reposted
Thomas H. Ptacek
@tqbf
Other forms of “next-gen antivirus”: U2F tokens, cryptographically authenticated cookies, WireGuard, Secure Enclave Processor, Rust.
subgraph reposted
 Reuters Business
@ReutersBiz
BREAKING: Yahoo says investigating creation of forged cookies that could have enabled intruder to access users' accounts without password
subgraph reposted
 Kav
@kavehrazavi
MMU side-channel attack that breaks ASLR in 10s of seconds! We had to keep this a secret for a while. Enjoy: www.vusec.net/projects/anc/ #ndss17
subgraph reposted
subgraph
@subgraph
Kernel 4.9.9 is now available for @subgraph OS in the repo.
grsecurity rss
@GrsecurityRss
grsecurity-3.1-4.9.9-201702122044.patch is available from grsecurity.net/test/grsecurity-3.1-4.9.9-201702122044.patch
subgraph reposted
subgraph reposted
 CISA Cyber
@CISACyber
Enhanced Analysis of GRIZZLY STEPPE www.cisa.gov/news-events/alerts/2017/02/10/enhanced-analy…
subgraph reposted
 NYT Business
@nytimesbusiness
Restricted spyware used to hack advocates of Mexico’s soda tax www.nytimes.com/2017/02/11/technology/hack-mexico-soda-ta…

subgraph reposted
Ars Technica
@arstechnica
Mac malware—not so mythical anymore. arstechnica.com/security/2017/02/mac-malware-has-a-way-to…
subgraph reposted
hacker.house
@hackerfantastic
Metasploit just got an interesting injection of Office Macro generation tricks and exploits that also impact LibreOffice. Handy.
subgraph reposted
 `Ivan
@Ivanlef0u
How Control Flow Integrity is implemented in Windows 10 lucasg.github.io/2017/02/05/Control-Flow-Guard/ Process Hacker 2 CFG support
subgraph reposted
CopperheadOS
@CopperheadOS
So @paxteam has RAP (full CFI) working with Chromium and Google only has 1/3 of the forward-edge-only Clang CFI, for one platform... sigh.
subgraph reposted
 Filippo Valsorda @filippo.abyssdomain.expert
@FiloSottile
Ticketbleed (CVE-2016-9244): leak of up to 31 bytes of memory via TLS Session IDs, affecting most F5 BIG-IP versions ticketbleed.com

subgraph reposted
Algo VPN
@AlgoVPN
Hello, world! Follow this account for news, updates, feedback, or even tech support about Algo VPN! github.com/trailofbits/algo
subgraph reposted
Ben Hawkes
@benhawkes
Project Zero blog: "Lifting the (Hyper) Visor: Bypassing Samsung’s Real-Time Kernel Protection" by @laginimaineb - googleprojectzero.blogspot.com/2017/02/lifting-hyper-viso…
subgraph reposted
 packagecloud.io
@packagecloudio
Monitoring and Tuning the Linux Networking Stack: Sending Data: blog.packagecloud.io/eng/2017/02/06/monitoring-tuning-lin… #linux #networking


subgraph reposted
Hossein Lotfi
@hosselot
Exploring Control Flow Guard in Windows 10:
sjc1-te-ftp.trendmicro.com/assets/wp/exploring-control-fl…
subgraph reposted
Juliano Rizzo
@julianor
Some antivirus (ESET, Bitdefender) intercept HTTPS connections and don't check server certs allowing easy MiTM :-/ zakird.com/papers/https_interception.pdf
subgraph reposted
 Mashable
@mashable
D.C. police slaps Facebook with subpoena for Trump protesters' data
on.mash.to/2jW6H97
subgraph reposted
PaX Team
@paxteam
today's grsecurity release for linux 4.9 adds the promised return checking to the public version of RAP: grsecurity.net/rap_announce_ret.php @epakskape
subgraph reposted
 VPRO Tegenlicht
@VPROTegenlicht
'De mainstream media en de elites eromheen zijn de weg kwijt', aldus @evgenymorozov #fakenews #tegenlicht tegenlicht.vpro.nl/artikelen/uitdagers-van-de-democratie
subgraph reposted
David Mirza Ahmad
@attractr
Can't wait for next grsec test patch.
subgraph
@subgraph
Yeah - the Windows DRM Tor deanon is a good example of the kind of "surprise" our sandbox mitigates. Data from app has only one way out.
 Eran Sandler
@erans
Beware of DRM files when using @torproject unless your route all of your computer traffic via Tor like @subgraph www.helpnetsecurity.com/2017/02/03/uncloaking-tor-browser…
subgraph
@subgraph
Want to help support Subgraph OS? We are now officially accepting Bitcoin contributions. Address: 1KUnb8ivujnmrvW8qdtFMs3uUHcVVSuLtj
subgraph reposted
CopperheadOS
@CopperheadOS
Chromium also generates 3 random DNS queries to figure out if DNS is well-behaved: mikewest.org/2012/02/chrome-connects-to-three-random-doma….
subgraph reposted
 hackaday
@hackaday
The Gray-1, A Computer Composed Entirely Of ROM And RAM hackaday.com/2017/02/02/the-gray-1-a-computer-composed-en…
subgraph reposted
Sarah Jamie Lewis
@SarahJamieLewis
Looks like Freedom Hosting II got pwned. They hosted close to 20% of all dark web sites (previous @OnionScan report) mascherari.press/onionscan-report-september-2016-uptime-d…
subgraph reposted
 Lukasz Olejnik
@lukOlejnik
Cyberattacks targeting banks in Poland, sensitive material stolen. Organized operation. Looks really serious. badcyber.com/several-polish-banks-hacked-information-stol…
subgraph
@subgraph
Container Hardening mailing list:
groups.google.com/a/containerhardening.org/forum/m/ x.com/jessfraz/status/827500850691969024
subgraph reposted
 Runa Sandvik
@runasand
Cozy Bear goes after Norwegian Police Security Service, Ministry of Foreign Affairs, Radiation Protection Authority: www.tv2.no/nyheter/8903847/
subgraph reposted
Halvar Flake
@halvarflake
static.googleusercontent.com/media/research.google.com/en… - good paper on Google datacenter network fabric.
subgraph reposted
 Turkey Untold
@TurkeyUntold
Tonight, @Twitter has suspended simultaneously several accounts of dissident lawyers and of the Libertarian Lawyer's Association (ÖHD).
subgraph reposted
Shawn C - citypw@ioc.exchange
@citypw
It seems two GCC plugins( INITIFY/STRUCTLEAK) will merge soon ported from PaX/Grsecurity: git.kernel.org/cgit/linux/kernel/git/next/linux-next.git/… git.kernel.org/cgit/linux/kernel/git/next/linux-next.git/…
subgraph reposted
radare
@radareorg
Announcing radare2-1.2.0 (codename HopeBells) github.com/radare/radare2/releases/tag/1.2.0
subgraph reposted
 Tamas K Lengyel
@tklengyel
Guestrace - System call tracing using Xen altp2m and LibVMI (released under LGPL) www.flyn.org/projects/guestrace/index.html
subgraph reposted
 Fermin J. Serna
@fjserna
Just published the slides of the Glibc vuln (CVE-2015-7547) "high level" talk I gave at CCN-CERT X Jornadas STIC zhodiac.hispahack.com/my-stuff/security/Glibc_vulnerabili…
subgraph reposted
Thomas H. Ptacek
@tqbf
Read this thread. Then come back.
 Vess
@VessOnSecurity
Regarding the ex-Mozilla employee's anti-AV rant, I have to tell you a story. But first some background - I intensely dislike Microsoft.
subgraph reposted
 Ali Hamedani
@alihamedanii
All done! They've interviewed, searched my bag, searched my phone and computer and let me in after 2 hours. He said I can come back anytime.
subgraph reposted
 kennyog
@kennyog
docs.google.com/document/d/17r18cKaMSeZF4fI7UZYV0QwCvdbEb… … crypto/IS folks: pls add if you're willing to hear from US-banned aspiring grad students #muslimban #phdsforall
subgraph reposted
 Chris Mallz
@vvalien1
Analyzing the NULL Security Descriptor kernel exploitation mitigation in the latest Windows 10 v1607 Build 14393
labs.nettitude.com/blog/analysing-the-null-securitydescri…
subgraph reposted
 sarah jeong
@sarahjeong
A psychologist thinks his research with Facebook data was used to make Brexit happen, and to help Trump win. motherboard.vice.com/read/big-data-cambridge-analytica-br…
subgraph reposted
 George Kargiotakis
@kargig
Reversing and exploiting Utimaco HSM by @fotisl fotisl.com/reverse/utimaco/recon2017/ tools repo: github.com/fotisl/utimaco
subgraph reposted
subgraph reposted
Guillaume Valadon
@guedou
ShellcodeSmuggler/IAT_POC: POC for IAT Parsing Payloads #reconbrx github.com/ShellcodeSmuggler/IAT_POC
subgraph reposted
Richard Johnson
@richinseattle
Just checked in Windows Intel PT Driver for Windows v0.5 from our presentation github.com/intelpt/WindowsIntelPT cc: @aall86 @reconbrx
subgraph
@subgraph
This is due to an issue with Tor Browser Launcher that's been fixed upstream. Workaround until new Debian package: github.com/subgraph/subgraph-os-issues/issues/205
subgraph reposted
Jann Horn - jann@infosec.exchange
@tehjh
thejh.net/misc/firefox-cve-2016-9904-and-cve-2017-5378-bu… Firefox bug: turning a hashtable DoS into a partial pointer leak and a cross-origin string contents oracle
subgraph reposted
 dragosr
@dragosr
Android VPN apps!
Of 283:
18% don't encrypt
84% leak
66% tracking libs
38% malware
80% access texts, accounts
blog.csiro.au/tinker-torrentor-streamer-spy-vpn-privacy-a…
subgraph reposted
Julia Angwin
@JuliaAngwin
Section 14 of this Exec Order rolls back the privacy protections Obama extended to foreigners data after Snowden. www.whitehouse.gov/the-press-office/2017/01/25/presidenti…

subgraph reposted
Hossein Lotfi
@hosselot
Exploiting services and readers that support the ePub book format;
s1gnalcha0s.github.io/epub/2017/01/25/This-book-reads-you…
subgraph reposted
 Alexandre Dulaunoy @adulau@infosec.exchange
@adulau
"Python script designed to perform a quick offline analysis of the boot records used by BIOS" github.com/ANSSI-FR/bootcode_parser #dfir
subgraph reposted
 Niels Provos
@NielsProvos
7 ways we harden our KVM hypervisor at Google Cloud: Security in plaintext
cloudplatform.googleblog.com/2017/01/7-ways-we-harden-our…
subgraph reposted
 matteyeux
@matteyeux
incomplete iOS 10.2 jailbreak for 64 bit devices by qwertyoruiopz and marcograssi
github.com/kpwn/yalu102
subgraph reposted
 Collin Mulliner
@collinrm
I'm co-organizing Usenix WOOT'17 submit your offense work! Specifically work you submitted to major industry cons www.usenix.org/conference/woot17/call-for-papers
subgraph reposted
 Gizmodo
@Gizmodo
Russia arrests top Kaspersky hacking investigator for treason gizmo.do/wMUqB4W

subgraph reposted
Binni Shah
@binitamshah
The Cisco Meraki switch has backdoor accounts (Part 1) : research.trust.salesforce.com/Meraki-RCE-When-Red-Team-an… , Part 2 : research.trust.salesforce.com/Meraki-RCE-When-Red-Team-an…

subgraph reposted
Trail of Bits
@trailofbits
Let’s talk about CFI: Microsoft Edition blog.trailofbits.com/2016/12/27/lets-talk-about-cfi-micro…

subgraph reposted
 Giuseppe `N3mes1s`
@N3mes1s
Manual Control Flow Guard in C - nullprogram.com/blog/2017/01/21/
subgraph reposted
Raphael Satter
@razhael
Saudi Arabia warns destructive computer virus has returned apnews.com/888029171f0e4a67bdbae98cbd5bf814
subgraph reposted
 Suchakra ↔️ @suchakra@mastodon.social
@tuxology
@subgraph also it's worth looking at uftrace github.com/namhyung/uftrace which is basically ftrace functionality in userspace
subgraph reposted
 Bad Cyber
@badcybercom
Dropbox surprise – deleted files magically reappear after several years badcyber.com/dropbox-surprise-deleted-files-magically-rea…

subgraph reposted
 Capstone Engine
@capstone_engine
ftrace is a nice Linux tool that dynamically intercepts & records all local function calls #capstoneinside
github.com/docileninja/ftrace
subgraph reposted
 reddit 보안 봇
@reddit_sec_bot
Systemd v228 local root exploit (CVE-2016-10156) www.openwall.com/lists/oss-security/2017/01/24/4
subgraph
@subgraph
WebEx: shared desktop/presentation service used for "webinars" etc, installed on practically every corporate desktop/laptop in the universe.
Filippo Valsorda @filippo.abyssdomain.expert
@FiloSottile
This is how the attack looks like if you have the fixed WebEx extension. Click OK and you're doomed. This is a social engineering nightmare.

subgraph reposted
Tavis Ormandy
@taviso
There was a secret URL in WebEx that allowed any website to run arbitrary code. ¯\_(ツ)_/¯ bugs.chromium.org/p/project-zero/issues/detail?id=1096
subgraph reposted
Hossein Lotfi
@hosselot
Bypassing Control Flow Guard in Windows 10 - Part 2 :
improsec.com/blog//bypassing-control-flow-guard-on-window…
subgraph reposted
 The Verge
@verge
Leaked emails reveal how Dataminr was pitched to foreign governments www.theverge.com/2017/1/19/14310498/dataminr-twitter-news…

subgraph reposted
 JS0N Haddix
@Jhaddix
Such epic, very exploit, amaze - Curated list of Windows Exploitation resources: github.com/enddo/awesome-windows-exploitation
subgraph reposted
 haroon meer
@haroonmeer
Our v2 @ThinkstCanary is:
- now released;
- covered here [canary.tools/new];
- totally awesome!
You really should check it out

subgraph reposted
 Antonio Gomes 🇧🇷🇨🇦🇵🇹
@tonikitoo
#chromium Mus window system overview: frederic-wang.fr/mus-window-system.html by Frederic Wang <fwang at igalia> (cc @igalia @ChromiumDev)
subgraph reposted
 Archillect
@archillect

subgraph reposted
 C.A.Y.
@redditiosymboli
China's Ministry of Industry & Info Technology finally moves in to outlaw unauthorised installing or renting of VPN www.leiphone.com/news/201701/zZyJrgzw4RkReuTJ.html
subgraph reposted
 heige
@80vul
《GMP Deserialization Type Confusion Vulnerability [MyBB <= 1.8.3 RCE Vulnerability]》www.seebug.org/vuldb/ssvid-92631 by @chtg57
subgraph reposted
 CIRCL - @circl@social.circl.lu
@circl_lu
SELinux policycoreutils allows local users to execute arbitrary commands cve.circl.lu/cve/CVE-2016-7545
subgraph reposted
 Cem Paya
@randomoracle
Downside to walled-gardens: how #apple & #google app stores became handmaidens of #censorship in Russia/China
www.nytimes.com/2017/01/18/technology/clearing-out-the-ap…
subgraph reposted
 Clayton Rice, K.C.
@WiretapLawyer
Minnesota court rules fingerprint unlocking phone does not violate privilege against compelled self-incrimination arstechnica.com/tech-policy/2017/01/court-rules-against-m…
subgraph reposted
subgraph reposted
 Guardian Tech
@guardiantech
Russia threatens retaliation over Facebook 'censorship' of RT d.gu.com/N8fBkm
subgraph reposted
Today In Infosec
@todayininfosec
1986: The first PC virus appeared - a boot sector virus called Brain. It displayed the phone # of its 2 creators.
 subgraph
@subgraph
It is truly a shame that we can't participate in this year's Pwn2Own because we are based in Québec ;)
subgraph reposted
Bruce Potter
@gdead
It makes good security sense to not have an open mic in your house relaying our words back to a giant cloud analytic service.
subgraph reposted
 Chris Wysopal
@WeldPond
The Post-Snowden Cyber Arms Hustle. Boutique orgs selling "NSA-level" spy tech to governments. www.bloomberg.com/news/features/2017-01-18/the-post-snowd…
subgraph reposted
 🧙♀️zei - @zei@mastodon.social
@thezeist
Dismissing Python Garbage Collection at Instagram engineering.instagram.com/dismissing-python-garbage-colle…
subgraph reposted
 rtl-sdr.com
@rtlsdrblog
LimeSDR First Batch Shipping Now www.rtl-sdr.com/limesdr-first-batch-shipping-now/
subgraph reposted
The Debian Project
@debian
The root CA for Let's Encrypt (ISRG root X1) is now part of Debian's Jessie, Stretch and Sid releases letsencrypt.org/2016/08/05/le-root-to-be-trusted-by-mozil…

subgraph reposted
 Go News
@golang_news
Most Subgraph OS custom code written in Go subgraph.com #reddit
subgraph reposted
Solar Designer
@solardiz
AES-GCM-SIV (nonce reuse mitigating construction) revised due to NSA www.ietf.org/mail-archive/web/cfrg/current/msg08895.html tools.ietf.org/html/draft-irtf-cfrg-gcmsiv-03 github.com/Shay-Gueron/AES-GCM-SIV
subgraph reposted
 Polish Embassy UK 🇵🇱
@PolishEmbassyUK
#onthisday in 1940, #polish cryptologist Marian Rejewski broke the Enigma code in the presence of Alan Turing during their meeting in Paris.

subgraph reposted
REcon Brussels
@reconbrx
RECON Brussels coming in fast. Schedule is live: recon.cx/2017/brussels/schedule
subgraph reposted
 PhysicalDrive0
@PhysicalDrive0
Virtual Memory, Page Tables, and One Bit - CVE-2016-7255 ricklarabee.blogspot.it/2017/01/virtual-memory-page-table… PoC github.com/rlarabee/exploits/tree/master/cve-2016-7255
subgraph reposted
 Theori
@theori_io
Proof-of-Concept exploit for Edge bugs (CVE-2016-7200 & CVE-2016-7201) —
github.com/theori-io/chakra-2016-11
subgraph reposted
Sarah Jamie Lewis
@SarahJamieLewis
Just take a look and now imagine that 99.6% certainty is your buying algorithm, or your fraud algorithm or your traffic scaling algorithm.

subgraph reposted
Sarah Jamie Lewis
@SarahJamieLewis
If you want to know the kinds of threats your ML faces I summarized a bunch of stuff here: mascherari.press/introduction-to-adversarial-machine-lear…
subgraph reposted
 Steve (@sc00bz@infosec.exchange)
@Sc00bzT
ProtonMail paid a DDoS ransom and said it was a sophisticated nation state sponsored attack. Also
Steve (@sc00bz@infosec.exchange)
@Sc00bzT
OMG they finally fixed this it only took them 894 days.
subgraph
@subgraph
Flexibility in outgoing connections (vpn, clearnet, tor) is the next big change, and is coming very soon, possibly in the next iso release.
subgraph reposted
The New York Times
@nytimes
Breaking News: Chelsea Manning will be freed in May. President Obama is commuting her sentence. www.nytimes.com/2017/01/17/us/politics/obama-commutes-bul…
subgraph reposted
 Tatu Ylonen
@tjssh
How exploit writers can bypass Windows heap randomization.
Binni Shah
@binitamshah
PoC to bypass LFH randomization : github.com/saaramar/Deterministic_LFH


subgraph reposted
David Mirza Ahmad
@attractr
Looking for contacts at @IPredatorVPN / @mullvadnet / (others?)
subgraph reposted
subgraph reposted
 femmetasm
@femmetasm
@subgraph os has this right now, ricochet or onionshare are in the package manager and are sandboxed and firewalled,its tor control filtered
Sarah Jamie Lewis
@SarahJamieLewis
Which means we really also must be pushing for standardized Tor deployments - having all these apps bundle Tor or rely on TBB is a headache.
subgraph reposted
Morten Schenk
@Blomster81
First blog post on bypassing Control Flow Guard is up - www.improsec.com/blog//bypassing-control-flow-guard-in-wi… #exploit
subgraph reposted
 Artem I. Baranov
@artem_i_baranov
Hm, EquationDrug rootkit authors do same trick as Remsec developers with creation of new DriverObject. It is not widespread method.

subgraph reposted
mdowd
@mdowd
Qualcomm have a doc on ARMs new pointer authentication stuff (h/t @brinlyau): www.qualcomm.com/media/documents/files/whitepaper-pointer…
subgraph reposted
 André Moulu
@andremoulu
Executing code in the TrustZone land by @embarbosa www.syscan360.org/slides/2016_SH_Edgar_Barbosa_Running_Co…
subgraph reposted
Unicorn Engine
@unicorn_engine
w0w, finally someone used Unicorn emulator to built an IDA plugin for binary deobfuscation \O/
github.com/tkmru/nao


subgraph reposted
 Wolfie Christl
@WolfieChristl
An interactive map of hidden third-party tracking services on Android apps, impressive: haystack.mobi/panopticon (via @narseo at #privacycon)

subgraph reposted
subgraph
@subgraph
This story from 2014 about Regin, suspiciously somehow "not detected" for years by AV companies, is worth a read today.
subgraph reposted
 Jake Williams
@MalwareJake
Someone uploaded this #shadowbrokers file to @virustotal this morning. 12/56 detection. Look at who's missing. Not a good day for them I bet

subgraph reposted
Jake Williams
@MalwareJake
Of the 61 files in the new Shadow Brokers dump, only 74de13b5ea68b3da24addc009f84baee was in @virustotal before today.
subgraph reposted
 Infiltrate
@InfiltrateCon
INFILTRATE '17 Speakers have been announced: infiltratecon.com/speakers.html
Grab tickets b4 we reach the next pricing tier infiltratecon.com/register.html
subgraph reposted
 Stephan Somogyi
@thinkpanzer
Announcing Key Transparency! Open src tools to addr longstanding key mgmt challenges. Props to @rmhrisk & @gdbelvin security.googleblog.com/2017/01/security-through-transpar…
subgraph reposted
argp
@_argp
So, @yung_vats and myself will be presenting Android userland heap exploitation using shadow at @InfiltrateCon: www.infiltratecon.org/speakers.html
subgraph reposted
Arrigo Triulzi
@cynicalsecurity
Have an SSL timing attack against ECDSA with P-256 curve (#openbsd patch) to end the day in glory… ftp.openbsd.org/pub/OpenBSD/patches/6.0/common/016_libcry…
subgraph reposted
 Rolf Rolles
@RolfRolles
Video of two-thirds of my talk on automated shellcode synthesis is now online: www.youtube.com/watch?v=e1ipR3W4vBQ (slides here www.msreverseengineering.com/blog/2016/11/8/synesthesia-m…)
subgraph reposted
Unicorn Engine
@unicorn_engine
A great article by @s4sh_s on setup GDT table & X86 segments (so you can emulate Windows shellcode) with Unicorn: scoding.de/setting-global-descriptor-table-unicorn
subgraph reposted
The New York Times
@nytimes
Apple has removed The New York Times's apps from its app store in China after a request from authorities www.nytimes.com/2017/01/04/business/media/new-york-times-…
subgraph reposted
David Mirza Ahmad
@attractr
Testing Tor censorship from Turkey using OpenVPN exit for an Oz sandbox: Tor, commercial VPN websites blocked, but can still bootstrap Tor.
 subgraph
@subgraph
Torrent is up: dist.subgraph.com/sgos/alpha/subgraph-os-alpha_2016-12-30…
subgraph
@subgraph
New December 2016 @Subgraph OS ISO available for download. Changes and download link: subgraph.com/blog/subgraph-dec2016-iso-availability/
subgraph reposted
Least Authority
@LeastAuthority
Check out @subgraph OS Alpha release 3 and @david415 's contributions to it! subgraph.com/blog/index.en.html
subgraph
@subgraph
New December 2016 @Subgraph OS ISO available for download. Changes and download link: subgraph.com/blog/subgraph-dec2016-iso-availability/
subgraph reposted
Hossein Lotfi
@hosselot
Source code level analysis and exploitation of recent Firefox/tor zero-day (CVE-2016-9079):
community.rapid7.com/community/metasploit/blog/2016/12/29…
subgraph
@subgraph
Even if Chromium isn't airtight, there is nowhere for leaked traffic to go, only one way out of sandbox for all processes: tor proxy port.
subgraph
@subgraph
LIke other Oz sandboxed apps, Chronion runs in its own network namespace, no NIC, only loopback configured in sandbox. SOCKS5 out only.
 subgraph
@subgraph
This is still work in progress: need to address circuit isolation, and other things. It's unfortunately not a drop-in replacement for TB.
subgraph reposted
 Sid Rao
@sidnext2none
Good to see @QubesOS @subgraph in @csoghoian 's #33c3 talk while stress their role on surviving a (government) hack on your PC.

subgraph reposted
REcon Brussels
@reconbrx
Recon Brussels 2017 talks list has been released recon.cx/2017/brussels/
subgraph reposted
Nicolas Krassas
@Dinosn
Tool to manipulate address space of Linux process github.com/daniel-araujo/proctal
subgraph reposted
 Don A. Bailey
@DonAndrewBailey
As usual, Fabrice Bellard is a total bad ass. 128-bit RISC-V emulator that boots Linux:
bellard.org/riscvemu/
subgraph reposted
Solar Designer
@solardiz
Infect to Protect: patching seccomp sandboxing into Linux ELF binaries tia.mat.br/posts/2016/11/08/infect_to_protect.html by @lafp
subgraph reposted
Bruce Leidl
@bleidl
Problems with PGP are more about key distribution and mail client integration than memory corruption vulns and crypto primitives
subgraph reposted
 Sasha Goldshtein
@goldshtn
ICYMI, my #velocity talk on ftrace, perf and #bpf is available online: www.oreilly.com/learning/using-linux-tracing-tools <-- covers some bleeding-edge BCC tools
subgraph reposted
Lorenzo Franceschi-Bicchierai
@lorenzofb
Are you going to #33c3? Then you should go see this talk.
subgraph reposted
hacker.house
@hackerfantastic
I wrote a reliable memory corruption exploit for Red Star OS 3.0, you can read how it works and download it here www.myhackerhouse.com/naenara-browser-3-5-exploit-jackrab…
subgraph
@subgraph
mp4 link: Testing if Tor is blocked in Turkey, from the desktop, in Subgraph OS using Oz + coming OpenVPN support: support.subgraph.com/turkey-tor.mp4
subgraph
@subgraph
Video: Testing to see if Tor is being blocked in Turkey from the desktop in Subgraph OS using Oz + coming OpenVPN support.
subgraph
@subgraph
Video: Testing to see if Tor is being blocked in Turkey from the desktop in Subgraph OS using Oz + coming OpenVPN support.
subgraph reposted
Thomas H. Ptacek
@tqbf
This is the coolest thing I’ve seen in months: github.com/google/wycheproof
Bleichenbacher and Thai Duong!
subgraph reposted
 JS Cournoyer
@jscournoyer
Facebook automatically translates our posts into foreign languages without our knowledge, has it gone too far? medium.com/@jscournoyer/has-facebook-gone-too-far-309b53e…
subgraph
@subgraph
American student allegedly hacked, surveilled & blacklisted in GCC states. Targeted due to research on migrant labor conditions in the UAE.
subgraph
@subgraph
The @coyproject team is working on OTRv4 and has just published a specification. 👇🏽👇🏽 github.com/twstrike/otrv4/blob/master/otrv4.md

subgraph reposted
Matt Miller
@epakskape
Edge has a new exploit mitigation that has begun lighting up in Windows 10 build 14986. Who noticed? :)
Prohibit dynamic code: enabled

subgraph reposted
 Donncha Ó Cearbhaill
@DonnchaC
Reliably compromising Ubuntu desktops by attacking the crash reporter donncha.is/2016/12/compromising-ubuntu-desktop/
 subgraph
@subgraph
Yahoo: ".. we believe an unauthorized third party accessed our proprietary code to learn how to forge cookies.." yahoo.tumblr.com/post/154479236569/important-security-inf…
subgraph reposted
Reuters
@Reuters
Yahoo discloses new data breach affecting one billion accounts www.reuters.com/article/us-yahoo-cyber-idUSKBN1432WZ?feed…
subgraph reposted
REcon Brussels
@reconbrx
Recon Brussels 2017 registration is finally open and the first round of talks have been announced. recon.cx/2017/brussels/
subgraph
@subgraph
Video demonstration of (early) Subgraph OS + OpenVPN: support.subgraph.com/oz-openvpn-demo.webm
subgraph reposted
 Electrospaces
@electrospaces
New law will allow Dutch police to hack into suspect's networks, computers and smartphones, but parliament and experts are critical
 NRC
@nrc
Een nieuwe wet geeft het OM de bevoegdheden om apparatuur van verdachten te hacken. Foute boel, zeggen critici.
www.nrc.nl/nieuws/2016/12/12/justitie-wil-nu-terughacken-…
subgraph
@subgraph
We made a little "what's my IP address" website today for coming demo of OpenVPN/clearnet support in SGOS: myip.subgraph.com. Try it!
 subgraph
@subgraph
We have OpenVPN support for Oz sandboxes working now, we will add Algo next.
Trail of Bits
@trailofbits
Meet Algo, the VPN that works blog.trailofbits.com/2016/12/12/meet-algo-the-vpn-that-works
subgraph reposted
 @mikko
Ransomware gives free decryption keys to victims who infect their friends via referral links. www.bleepingcomputer.com/news/security/new-scheme-spread-…

subgraph reposted
 Brendan Gregg
@brendangregg
Slides and labs from my perf/BPF/bcc tutorial with @goldshtn at #lisa16 s.sashag.net/bpflisa github.com/goldshtn/linux-tracing-workshop
subgraph reposted
Vitaly Nikolenko
@vnik5287
add_key() is apparently another good candidate for a kernel heap spray. -18 bytes for the header at the beginning
 subgraph
@subgraph
Private Internet Access also offered & provided us resources for testing SGOS sandbox-to-VPN egress (which works, post soon) @buyvpnservice
subgraph reposted
Solar Designer
@solardiz
Philip Pettersson's CVE-2016-8655 Linux AF_PACKET race exploit for Ubuntu 16.04, 14.04. Many other systems affected. www.openwall.com/lists/oss-security/2016/12/07/3
subgraph reposted
 𝗥𝗬𝗔𝗡 𝗦𝗧𝗢𝗥𝗧𝗭
@withzombies
@nickdepetrillo writes shitty exploits
subgraph reposted
Felix Wilhelm
@_fel1x
FreeBSD fixed a bhyve VM escape I reported a couple of months ago: lists.freebsd.org/pipermail/freebsd-security/2016-Decembe…
subgraph reposted
Chris Evans
@scarybeasts
[1day] [PoC with $rip] Deterministic Linux heap grooming with huge allocations: scarybeastsecurity.blogspot.com/2016/12/1day-poc-with-rip…
subgraph
@subgraph
Another local privilege escalation thanks to unprivileged user namespaces.
Solar Designer
@solardiz
CVE-2016-8655 Linux AF_PACKET race condition (local root). Found by
Philip Pettersson. Exploit for Ubuntu tomorrow. www.openwall.com/lists/oss-security/2016/12/06/1
subgraph
@subgraph
Running a Bitcoin node in SGOS is neat: participate in p2p net, but no firewall hole punching, client onion listener forwarded to sandbox.
subgraph
@subgraph
Bitcoin core running in an Oz sandbox w/seccomp, its onion service forwarding connecting p2p clients from Tor into sandbox.
 subgraph
@subgraph
Bitcoin core in an SGOS sandbox is also a good use case for adding cgroups support to Oz, this is something we will experiment with soon.
subgraph reposted
Unicorn Engine
@unicorn_engine
Wanna understand how emulator can help reversing? @sk3wl did a fantastic job to explain that in this DEFCON talk www.youtube.com/watch?v=6wypIgRi3cw
subgraph
@subgraph
Bitcoin core has built-in support for ephemeral hidden services; SGOS can transparently support this when the client runs in an Oz sandbox.
subgraph
@subgraph
Electrum in sandbox using .onion servers. Soon force only .onion if users want. Send BTC if you like :) 16gJmmBdkMecm9iiSyKr93d72SVUMte5h5
 subgraph
@subgraph
Noticed that Bitcoin core was attempting to create a Tor HS because our Tor control port filter denied the ADD_ONION.
subgraph
@subgraph
Bitcoin core running in an Oz sandbox w/seccomp, its onion service forwarding connecting p2p clients from Tor into sandbox.
subgraph reposted
Ben Hawkes
@benhawkes
Project Zero blog: "BitUnmap: Attacking Android Ashmem" by @laginimaineb - googleprojectzero.blogspot.com/2016/12/bitunmap-attacking…
subgraph
@subgraph
Subgraph OS PaX flag maintenance utility 'paxrat' has been accepted into Debian unstable. packages.qa.debian.org/p/paxrat/news/20161128T200010Z.html
subgraph reposted
 codypierce
@codypierce
The first entry in mozilla's crash reporter service for the Firefox 0day is from June 2016. crash-stats.mozilla.com/report/index/3d7251c5-72d5-4178-a…
subgraph reposted
codypierce
@codypierce
Just posted a quick blog on the Firefox 0day with a touch of technical and exploit prevention thrown in. www.endgame.com/blog/another-0day-another-prevention
subgraph reposted
 Giorgio Maone 🐘 @ma1@todon.eu
@ma1
For the curious, the 0-day bug fixed in @firefox and @torproject some hours ago has just been disembargoed:
bugzilla.mozilla.org/show_bug.cgi?id=1321066
subgraph reposted
 The Tor Project
@torproject
Urgent: Please update your Tor browser (6.0.7 is released) blog.torproject.org/blog/tor-browser-607-released
subgraph reposted
subgraph reposted
 Black Hat
@BlackHatEvents
Announcement: The first 5 Briefings for #bhasia 2017 have been selected and announced. Details here: blackhat.com/asia-17/briefings/schedule/index.html
subgraph reposted
Reuters
@Reuters
FBI to gain expanded hacking powers as Senate effort to block fails www.reuters.com/article/us-usa-cyber-congress-idUSKBN13P2…
subgraph reposted
 Qubes OS
@QubesOS
Announcement: Qubes OS Begins Commercialization and Community Funding Efforts:
www.qubes-os.org/news/2016/11/30/qubes-commercialization/
subgraph reposted
Dan Guido
@dguido
Consider the difficulty of running a Tor exit node that injects this exploit into every HTTP session. ¯\_(ツ)_/¯
subgraph reposted
subgraph
@subgraph
Pseudomonarchia jemallocum: On exploiting jemalloc memory manager (Phrack 2012, @_argp/huku) phrack.org/issues/68/10.html
subgraph reposted
subgraph reposted
subgraph reposted
Dan Guido
@dguido
There's a bunch of misinformation about the new Firefox exploit so I'd like to clear a few things up. x.com/movrcx/status/803744059022069760
subgraph reposted
 Rafael Bonifaz (@rbonifaz@mastodon.social)
@rbonifaz
Hice una pequeña investigación @subgraph OS. Espero resulte útil para aprender sobre #privacidad y #anonimato
rafael.bonifaz.ec/blog/
subgraph reposted
Bruce Leidl
@bleidl
Good advice seen in 2014 Tor Browser security review by iSEC Partners

subgraph reposted
 mozillacentral
@mozillacentral
[default] Bug 1321066 - Explicitly guard against reentrance in nsSMILTimeContainer... hg.mozilla.org/mozilla-central/rev/adcc39e3cad0
subgraph
@subgraph
The handbook has been packaged and is now available in Subgraph OS.
To install:
$ sudo apt-get update
$ sudo apt-get install sgos-handbook


subgraph reposted
Bruce Leidl
@bleidl
I agree, that should be the default, especially since it's a known fact that FBI has an undisclosed vulnerability
subgraph reposted
Bruce Leidl
@bleidl
This is true, and in particular selfrando won't stop this exploit or most future Firefox memory corruption vulns. Read exploit to see why.
subgraph reposted
David Mirza Ahmad
@attractr
OH: "kind of suspicious timing that this exploit is 'found' right before that new law allowing FBI to hack the planet goes into effect"
subgraph reposted
Bruce Leidl
@bleidl
If you don't want to get ransomware, don't use Tor Browser right now. If you must use it, make sure javascript is disabled
subgraph reposted
 slipstream/RoL
@TheWack0lian
The shellcode used is almost exactly the shellcode of the 2013 one tsyrklevich.net/tbb_payload.txt
...except it builds sockaddr_in on the stack.
subgraph
@subgraph
People out there actually sent us BTC. Thanks! Buys us some VPN access for testing, as well as hosting. We'll sandbox Bitcoin classic also.
subgraph
@subgraph
Electrum in sandbox using .onion servers. Soon force only .onion if users want. Send BTC if you like :) 16gJmmBdkMecm9iiSyKr93d72SVUMte5h5
subgraph reposted
Brad Heath
@bradheath
Federal judge says "the public interest is ... well served" by keeping the FBI's Tor exploit secret, for reasons that are also secret.

subgraph reposted
WithSecure Labs
@FSecureLabs
Taking your first steps into 64-bit Windows exploitation? Check out our paper on porting MS08-067 to 64-bit systems labs.mwrinfosecurity.com/publications/hello-ms08-067-my-o…
subgraph reposted
Sarah Jamie Lewis
@SarahJamieLewis
ricochet.im is an actually anonymous, metadata eliminating, audited messenger. It will get better. You should start using it.
subgraph reposted
 Yuki Chen
@guhe120
One of our edge exploits prepared for PwnFest (but patched before the contest ): blogs.360.cn/360safe/2016/11/29/three-roads-lead-to-rome-2/ , more to come soon @mj0011sec
subgraph
@subgraph
Cameo appearance by IFS 👌🏻
subgraph reposted
Rolf Rolles
@RolfRolles
If you're interested in January's public program analysis training class, sign up or express interest by 12/16 www.msreverseengineering.com/training-classes/
subgraph reposted
Rolf Rolles
@RolfRolles
January's public static rev. engineering training has reached its student minimum; sign up soon to ensure your seat www.msreverseengineering.com/training-classes/
subgraph reposted
Rolf Rolles
@RolfRolles
Slides (and soon, code) for my recent talk on automated shellcode generation with encoding restrictions: www.msreverseengineering.com/blog/2016/11/8/synesthesia-m…
subgraph reposted
 Debian Advisories
@debian_advisory
DSA-3726 imagemagick (security update) | More details: lists.debian.org/debian-security-announce/2016/msg00308.html #debian #advisory
subgraph reposted
Andrey Konovalov
@andreyknvl
Compiled together a bunch of links related to Linux kernel exploitation: github.com/xairy/linux-kernel-exploitation
subgraph
@subgraph
Electrum in sandbox using .onion servers. Soon force only .onion if users want. Send BTC if you like :) 16gJmmBdkMecm9iiSyKr93d72SVUMte5h5
subgraph
@subgraph
Algo from @trailofbits a very cool project, we'll support it in @subgraph OS as another way to control network exit: github.com/trailofbits/algo
subgraph reposted
David Mirza Ahmad
@attractr
New (valid) certificate for @duckduckgo XMPP server produced pinning prompt in @coyproject. Certs are saved by default when first seen.

subgraph reposted
 Thomas Robitaille 🇪🇺
@astrofrog
Wow, I can't believe @esa's Schiaparelli Mars probe crashed because of integer overflow. Write tests people! phys.org/news/2016-11-glitch-blamed-european-mars-lander.…
subgraph reposted
Nicolas Krassas
@Dinosn
MS Edge: Abusing of Protocols to Load Local Files, bypass the HTML5 Sandbox, and more! - Broken Browser www.brokenbrowser.com/abusing-of-protocols/
subgraph reposted
0x5A1F
@Saif_Sherei
After allot of hard work MS16-098 Microsoft RNGOBJ Integer Overflow full exploit win 8.1 x64


subgraph reposted
 Troy Hunt
@troyhunt
Get Kaspersky to be unhackable *
(* may still be hackable)


subgraph reposted
 thomas
@LimThomas168
Windows Defender just got hacked on stage at SyScan360 by Vulcan Team
subgraph reposted
 Alexander K.
@opexxx
Analysis of OpenSSL ChaCha20-Poly1305 Heap Buffer Overflow (CVE-2016-7054) - Fortinet nzzl.us/wW1VHMI via @nuzzel thanks @revskills
subgraph
@subgraph
Session on OS Security - Nov 26 @ Ritter University in Porto Alegre.
 cryptolinux
@creonte38
Next saturday I will talk about your project and about Qubes OS too. (Ritter University). Brazil South.

subgraph reposted
subgraph reposted
 Hacker News YC
@newsycbot
Subgraph OS: Adversary resistant computing platform subgraph.com (cmts bitly.ift.tt/2frLRus)
subgraph reposted
 n3k
@kiqueNissim
Slides + Code + CVE-2016-7255 exploit: I Know Where Your Page Lives github.com/IOActive/I-know-where-your-page-lives @IOActive #zeronights
subgraph reposted
 newsoft
@newsoft
All your Windows 10 activity is sent to FireEye: www.arnnet.com.au/article/610583/can-fireeye-change-cyber… #themoreyouknow
subgraph reposted
 Wings Over Scotland
@WingsScotland
Well, the internet was fun while it lasted. yiu.co.uk/blog/who-can-view-my-internet-history/

subgraph reposted
 Te-Ping Chen
@tepingchen
"Blacklisted!" What happens when Microsoft's Chinese-speaking chatbot Xiaobing encounters 'sensitive' topics: chinadigitaltimes.net/2016/11/microsofts-chinese-chatbot-…

subgraph reposted
 Freedom of the Press Foundation
@FreedomofPress
Facebook has reportedly built a censorship tool to get back into China and it has led to several employees resigning www.nytimes.com/2016/11/22/technology/facebook-censorship…
subgraph reposted
 The Washington Post
@washingtonpost
After Trump, Americans want Facebook and Google to vet news. China likes that plan. www.washingtonpost.com/news/worldviews/wp/2016/11/17/afte…
subgraph reposted
 Surya Mattu
@suryamattu
If you’re in NY next week come checkout #glassroom
 Tactical Tech
@Info_Activism
7 days to the opening - work in progress #glassroom theglassroomnyc.org @unfitbits @bitnk @hdeweyh @lifewinning @tegabrain @suryamattu

subgraph reposted
Surya Mattu
@suryamattu
Black box Episode 3: See the different headlines @nypost and @nytimes test on readers www.propublica.org/article/breaking-the-black-box-when-ma…
subgraph reposted
Surya Mattu
@suryamattu
Download our extension to see what Facebook thinks you like and share with us. We are trying to collect their data propub.li/2d6dkUg
subgraph reposted
 The Intercept
@theintercept
“There is no other democracy in the world, possibly no other country in the world, doing this.” interc.pt/2fo2Xt8

subgraph reposted
 Charlie Miller
@0xcharlie
@scarybeasts it's so nice to see actual info about exploitation. I miss the old days when this info was discussed in the open.
subgraph reposted
CopperheadOS
@CopperheadOS
Rust removed reliable stack overflow detection before the replacement implementation was ready outside of Windows: github.com/rust-lang/rust/pull/27338.
subgraph reposted
Markus Vervier
@marver
TIL: Safe Rust can segfault too:
$ ./totallysafe
Segmentation fault (core dumped)
And no it's not a controlled panic.
subgraph
@subgraph
Indeed, just need to avoid C libraries wrapped in Rust.
Mozilla
@mozilla
Rust is revolutionary because it’s a safe systems language. Learn more about what that really means: www.youtube.com/watch?v=P3sfNGtpuxc&list=PLo3w8EB99pqJ74X…
subgraph reposted
subgraph reposted
David Mirza Ahmad
@attractr
Any VPN providers out there interested in SGOS want to donate access for us to experiment with? It is an interesting application :)
subgraph reposted
subgraph reposted
Ange
@angealbertini
online hex
binvis.io - @cortesi
hexed.it - www.duttke.de
icebuddha.com - @0xdabbad00
subgraph reposted
 KT
@koczkatamas
Reverse engineers! Just released a new tool for binary file RE which may come handy for you: kt.pe/kaitai_struct_webide/ (based on @kaitai_io)
subgraph reposted
 CBC Politics
@CBCPolitics
Russia, China targeting Canada's classified information, spy agency warns www.cbc.ca/news/politics/csis-espionage-warnings-china-ru… #hw #cdnpoli

subgraph reposted
 Jesper Jurcenoks
@jesperjurcenoks
Critical Buffer overflow CWE-121 in Palo Alto NGFW, CVE-2016-9150 #exploit POC bugs.chromium.org/p/project-zero/issues/detail?id=908 #infosec #owasp Top10 "A9" CWE-937
subgraph
@subgraph
This reality has informed the design of @subgraph OS: our app fw, containment / whitelisting, event monitoring,..👇🏼x.com/jzdziarski/status/800409350938521601
subgraph reposted
 Peter Kruse | Cybercrime Research
@peterkruse
Confirmed! #locky spreading on #facebook through #nemucod camouflaged as .svg file. Bypasses FB file whitelist. www.virustotal.com/da/file/5e9e3f9f96ce2333473a4c7eae8e07…

subgraph reposted
David Mirza Ahmad
@attractr
Listening to @drericcole give (in Montreal) what is essentially the @subgraph OS presentation, but generalized, for organizations.
subgraph reposted
 ∫КჄ⎩∣⋂ᕮᗤ
@berendjanwever
So, 10+ years after releasing my first heap spray, I finally wrote an article about it. :)
blog.skylined.nl/20161118001.html
subgraph reposted
Richard Johnson
@richinseattle
Coming soon to a kernel debugger/fuzzer near you!
 Andrea Allievi
@aall86
My and @richinseattle PT driver is starting to work even in Kernel Mode! :-)

subgraph reposted
 paπcake 🌱 🏴
@trufae
I will be giving another talk about @radareorg at CCC this year! halfnarp.events.ccc.de

subgraph reposted
Today In Infosec
@todayininfosec
1983: Stony Brook student Perry Kivolowitz published Unix keylogger code to 2 newsgroups to demonstrate current risk

subgraph reposted
Natalie Silvanovich
@natashenka
I've always wanted to find an 0-day I could tweet
var p = new Proxy(eval, {});
p("");
CVE-2016-7240 on Edge
bugs.chromium.org/p/project-zero/issues/detail?id=948
subgraph
@subgraph
We are at tomorrow's ASIQ Semaine de la Sécurité de l'Information Montréal event: asiq.org/evenement/montreal-conference-18-novembre/ Horaire:asiq.org/wp-content/uploads/2016/11/horaire-mtl.pdf
subgraph reposted
The Intercept
@theintercept
iPhones secretly send call history to Apple, security firm says theintercept.com/2016/11/17/iphones-secretly-send-call-hi… by @kimzetter
subgraph
@subgraph
Tibetan community targeted for years: implant delivery through .rtf file sent by email w/exploit for long patched CVE-2012-0158 in MS Word.
 The Citizen Lab
@citizenlab
The Tibetan community has been targeted for over a decade by malware. Our latest report, entitled "KeyBoy and the... www.facebook.com/login/?next=https%3A%2F%2Fwww.facebook.c…
subgraph reposted
 JP Aumasson
@veorq
tldr:
- Penalty for using 3DES
- Forward secrecy required for A
- AEAD suites required for A+
- <128b ciphers => F
- SHA1 Deprecation
 Ivan Ristic
@ivanristic
Announcing new, stricter, SSL Labs requirements for 2017 blog.qualys.com/ssllabs/2016/11/16/announcing-ssl-labs-gr…
subgraph
@subgraph
CONFIG_BPF_SYSCALL is off in @subgraph OS, and @grsec disables kernel pointer oracle kcmp: x.com/pent0thal/status/728149983958982656
subgraph
@subgraph
We are on our way to San Francisco for the @icdiran and @rightscon. Ping us if you want to meet to talk about/demo Subgraph OS.
subgraph
@subgraph
Screenshot: close-up of the @coyproject notifications coming to Subgaph OS.
 subgraph
@subgraph
Screenshot: We added desktop notifications to @coyproject. Coming very soon to Subgraph OS via updated Coy package.
 subgraph
@subgraph
Trying Subgraph OS and want to see the application firewall? Just open Gnome Calculator for a sketchy surprise.
 subgraph
@subgraph
Screenshot: Subgraph OS users can now manage the application firewall rules with a new UI.
 subgraph
@subgraph
Tor status indicator plugin now in repo. To try: apt-get update/upgrade; install gnome-shell-extension-torstatus.


 subgraph
@subgraph
CVE-2015-4495: pdf.js. Never forget. www.mozilla.org/en-US/security/advisories/mfsa2015-78/
subgraph
@subgraph
CoyIM single window, multi-convo chat UI in repo: run apt-get update/upgrade. To try, launch in shell: coyim -single
 subgraph
@subgraph
We are contributing to @coyproject! So far we've added a single window multi-conversation UI. Will be in SGOS soon.
 subgraph
@subgraph
Subgraph OS test users can apt-get update/upgrade to get the new release of CoyIM from our repo.
CoyIM
@coyproject
We have just released 0.2 of CoyIM - get it here: coy.im - this is still an early version, so no signed binaries.
subgraph
@subgraph
We need testers for pre-alpha Subgraph OS! Interested? Visit #subgraph on OFTC for link to download the ISO. Notes: support.subgraph.com/private/sgos/pre-alpha/
subgraph
@subgraph
Pidgin has been removed from SGOS forever. Long live @coyproject, the new default GUI XMPP client: github.com/subgraph/subgraph_desktop_stretch/commit/b2f25… #nomorelibpurple
subgraph
@subgraph
Join the Secure Desktops assembly at @CCC Congress 2015. @bleidl will be there to talk about and demonstrate SGOS: events.ccc.de/congress/2015/wiki/Assembly:Secure_Desktops
subgraph
@subgraph
Introducing the Secure Desktops mailing list, a forum for discussion and collaboration on open source projects: secure-os.org/pipermail/desktops/2015-October/000000.html

 ageis


 GreenAF


 corin.bsky.social
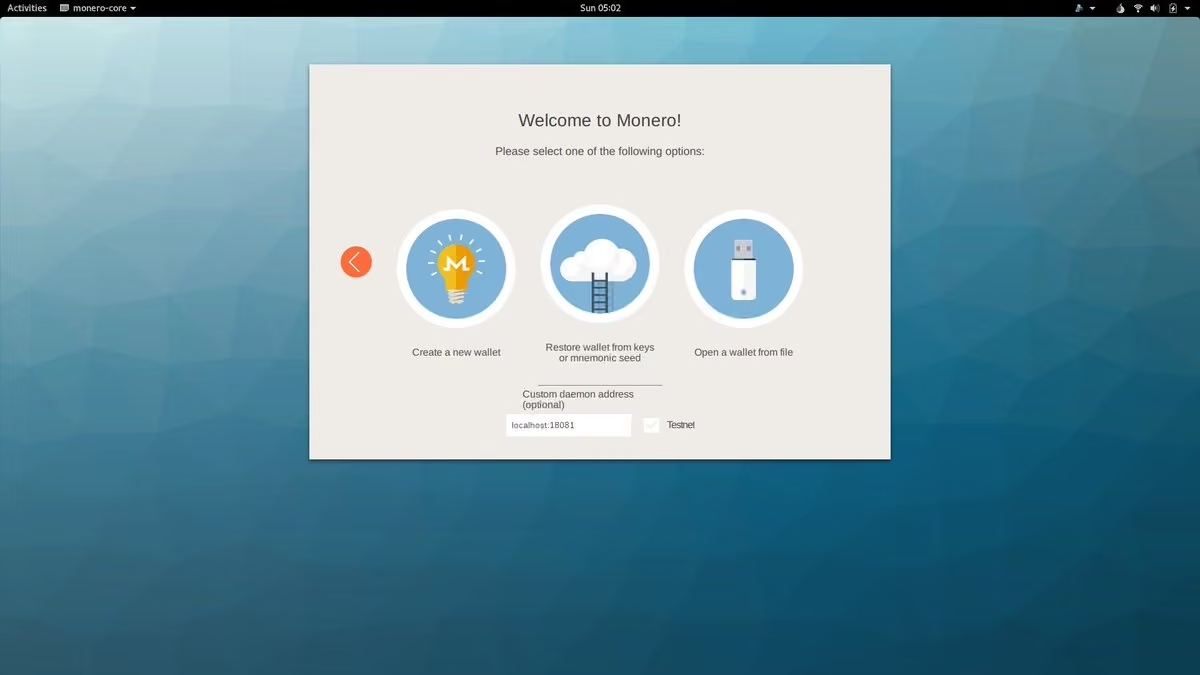


 Zisis

 stig atle
 Elizabeth K. Joseph


 Ryan Hurst
 zmanian